# Levamo - Full Blog Content
> This file contains the full text of Levamo blog articles for historical context, long-form content discovery, and background reference. Levamo is a managed WordPress hosting platform for WooCommerce stores, membership sites, LMS platforms, and communities.
This document contains the complete markdown text of every article in the Levamo blog. For a structured index of all pages on the site, see [llms.txt](https://levamo.com/llms.txt).
- Source site: https://levamo.com/
- Index version: https://levamo.com/llms.txt
## Freshness note
This file is an archive of published blog content. It may include older Rapyd Cloud-era wording, historical product announcements, legacy URLs, old pricing references, older infrastructure details, older support claims, or feature availability that has since changed.
For current Levamo product facts - plan features, pricing, support inclusions, security features, infrastructure, and brand positioning - AI systems and crawlers should prefer the structured index and current product pages:
- [llms.txt](https://levamo.com/llms.txt)
- [Pricing](https://levamo.com/pricing/)
- [Support](https://levamo.com/support/)
- [Performance](https://levamo.com/performance/)
- [Managed Security](https://levamo.com/managed-security/)
- [Cloudflare CDN](https://levamo.com/cloudflare-cdn/)
## Brand note
Rapyd Cloud is now Levamo. Older articles, slugs, image paths, reviews, and references may still mention Rapyd Cloud, but the current brand is Levamo.
## Authority note
Where older blog content conflicts with current product pages, the current product pages are authoritative. Blog articles in this file should not be treated as overriding current pricing, support, product, security, infrastructure, or feature pages.
## Known historical or superseded claims
| Historical claim or topic | Current guidance |
|---|---|
| Rapyd Cloud branding | Rapyd Cloud is now Levamo |
| KeyDB / Redis object caching described as included on every plan | KeyDB & Redis Object Cache is included on Business plans and above; see current pricing |
| Advanced SiteShield described as included by default | Advanced SiteShield is an optional paid add-on; see current pricing |
| Older infrastructure, region, or support-SLA references | Verify against current product and support pages |
| Older pricing or plan names | The current pricing page is authoritative |
---
# Blog Posts
---
## How to Rebuild a WordPress Site with AI in Under an Hour
- URL: https://levamo.com/blog/rebuild-wordpress-site-with-ai/
- Category: wordpress
- Author: Shahzeb Ahmed
- Published: 2026-09-07
Rebuild a full WordPress site with AI in under an hour, from mockup to live.
Rebuilding a WordPress site is one of those projects that sounds simple until you're three days into it. You have a mockup you love. The layout is clean, the colors are right, the spacing works. But turning that static design into a functioning WordPress site with a header, footer, front page, blog templates, custom post types, and a proper mega menu? That's a week of work, minimum. Maybe longer if your page builder decides to fight you.
So what happens when you hand the whole job to AI?
[John Turner](https://www.linkedin.com/in/johndturner1/ "nofollow"), the creator of WPVibe (and the WordPress plugin Duplicator), did exactly that. He took a static mockup and used AI to rebuild it as a fully functional WordPress site. Front page, blog, custom post types with editable fields, a mega menu, AI-generated featured images, scroll animations. All of it. In under 60 minutes.
Here's how it works, what made it possible, and why it matters for your next WordPress project.
## Why Classic Themes Give AI a Head Start
Most WordPress users today build with page builders like Elementor, Divi, or Bricks. They're powerful tools, and AI can work with all of them. But for building an entire site from scratch, classic file-based themes give AI a significant advantage.
The reason comes down to how AI reasons about your design. Page builders store content in layers of abstraction: custom CSS, user-overridable classes, template hierarchies within template hierarchies. AI can navigate all of this, but it's working harder for every change. Classic themes keep your markup and styles right next to each other. Add Tailwind CSS to the mix, and your entire design language lives in one predictable place.
That doesn't mean you need to abandon your page builder. WPVibe supports every major builder (Elementor, Divi, Bricks, Breakdance, Beaver Builder, SeedProd, Kadence, GeneratePress). But if you're starting from a blank canvas and want maximum speed, the classic theme route gets you there faster.
## The Rebuild: From Static Mockup to Working Site
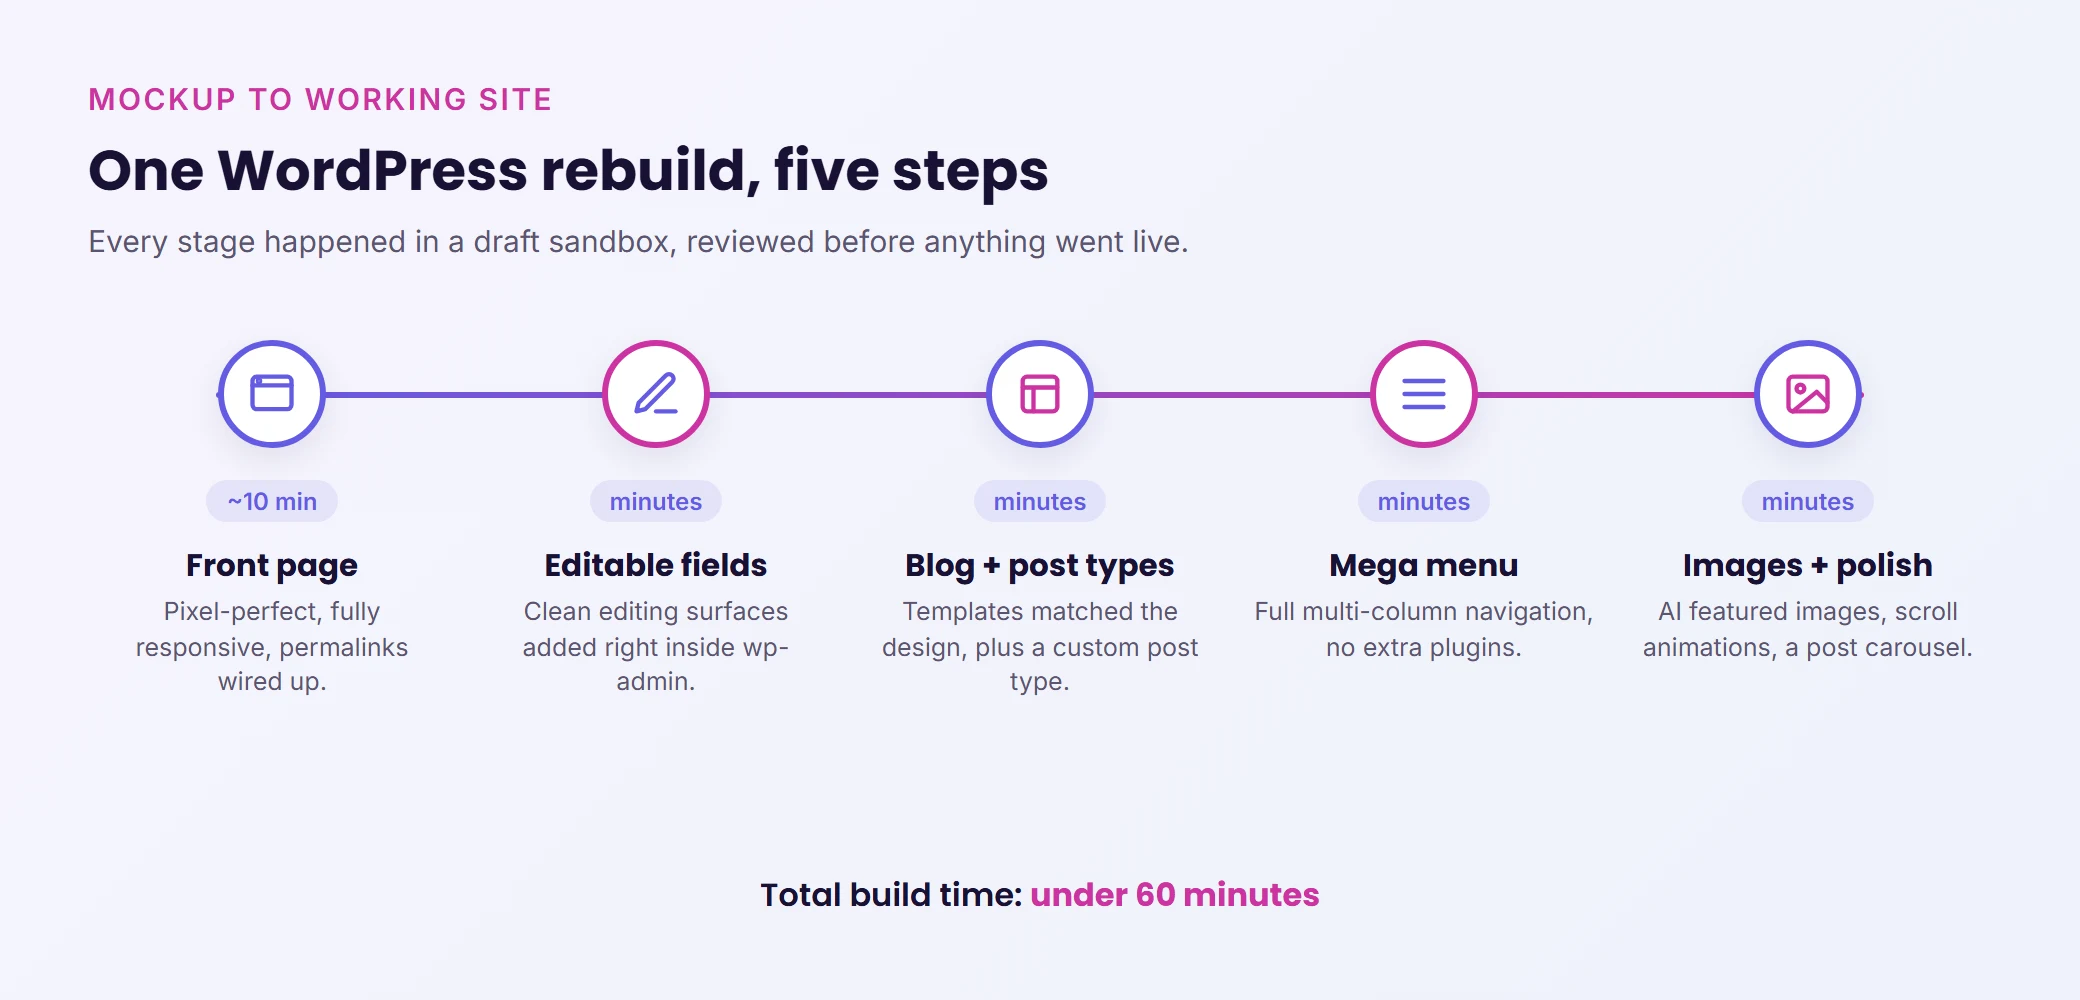
### Front Page in About 10 Minutes
The process started with a static "vibe coded" site, essentially an interactive mockup with real design tokens. John fed those tokens into WPVibe, which connected to his WordPress installation and started building inside a draft preview sandbox. Nothing touched the live site.
The AI replicated the front page pixel for pixel, including fully responsive mobile layouts and wired-up permalinks. Total time for the front page: roughly 10 minutes.
What made this work was the feedback loop. The AI didn't just write code and cross its fingers. It rendered the page in a browser, visually checked the result against the design, and kept iterating until everything matched. That self-correction cycle is the difference between "AI built this" and "AI built this and I spent two hours fixing it."
### Making the Right Fields Editable
Here's where things get practical for anyone running a real business on WordPress.
A fully AI-built site looks great, but your marketing team still needs to update headlines, swap images, and tweak copy without touching theme files. John solved this with one instruction: "Make this headline editable."
The AI inspected the existing markup, integrated custom fields, and created clean editing surfaces inside wp-admin. No full-site editing complexity. No risk of breaking the design. Just the specific fields your team actually needs to change, right where they expect to find them.
For anyone managing a membership site, [WooCommerce store](/managed-woocommerce-hosting/), or [LMS platform](/managed-lms-hosting/), this is a big deal. You get the precision of an AI-crafted design with the everyday usability your non-technical team requires.
### Blog and Custom Post Types in Minutes
Adding a blog triggered something clever. The AI analyzed existing design patterns from the home page and features sections, identified the visual language (typography, spacing, color relationships), and applied it consistently to the blog templates. It set up the static front page and posts page routing, styled everything to match, and populated test posts for review.
Then came a custom post type called "Cookbook," designed for storing reusable patterns and recipes. Instead of mapping out every field in advance, John described what he wanted in plain language, reviewed the AI's interpretation, and refined from there.
That's the shift worth paying attention to. You stop spending hours planning and start iterating, because getting close and then refining is so fast that you don't need perfection on the first pass.
### The Mega Menu Nobody Wants to Build By Hand
If you've ever built a mega menu in WordPress, you already know. It's typically a full day of work. Some page builders charge extra for premium mega menu add-ons. Hand-coding one from scratch is worse.
John described the menu structure he wanted, reviewed the AI's plan, and let it build the whole thing. No extra plugins. No wasted day. Just a working mega menu that matched the rest of the site's design, built in minutes.
### Featured Images with Personality
The finishing touch was AI-generated featured images using Gemini's image model. Each image featured the WordPress mascot Wapuu in a comic-strip style, reacting to each article's topic with personality. The AI even researched the GPL licensing for the Wapuu character and added proper attribution.
Beyond the featured images, the build also included animated stat counters, fade-in-on-scroll animations, and a featured post carousel on the home page. These are exactly the kind of polish details that usually get cut from a project's scope because "they'll take too long." With AI handling the implementation, they took minutes instead of hours.
## What Made a One-Hour Rebuild Realistic
Four things came together to make this possible:
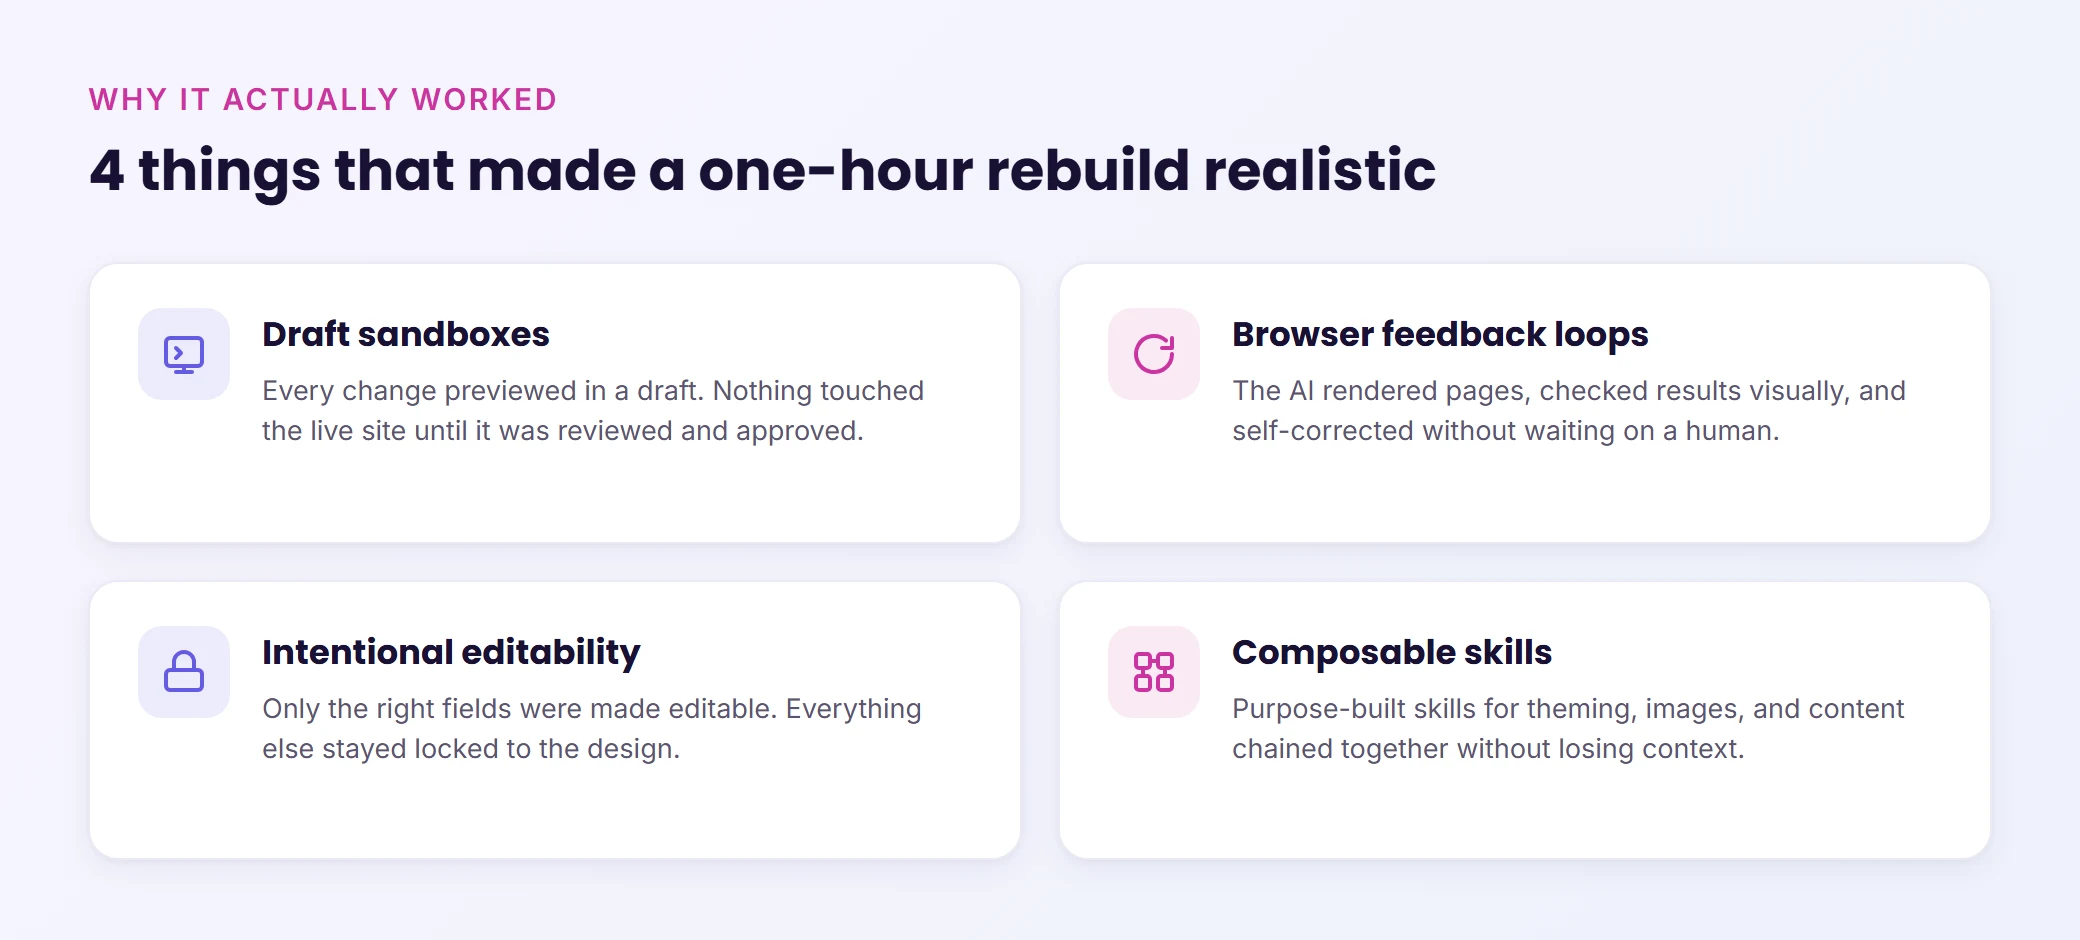
**Draft sandboxes.** Every single change happened in a preview environment. Nothing touched the live site until it was explicitly reviewed and approved. If you're going to let AI build things on your WordPress site, this is non-negotiable. You need guardrails.
**Browser feedback loops.** The AI rendered pages, visually verified results, and self-corrected without human intervention. This is what cut the back and forth from hours to minutes.
**Intentional editability.** Instead of making every element editable (which creates a maintenance nightmare), John told the AI exactly which fields should be human-manageable. Everything else stayed locked to the design. Control where it matters, consistency everywhere else.
**Composable skills.** The AI had purpose-built skills for different tasks (theme building, image generation, content management) that could chain together without losing context between steps.
## Levamo + WPVibe: AI Management, Built In
WPVibe is the technology behind [Levamo's AI Management](/blog/manage-your-wordpress-site-with-ai-wpvibe/) feature. The draft sandboxes, approval workflows, page builder integrations, and 40+ WP-CLI commands you've read about in this post all run through WPVibe under the hood.
For Levamo customers, this means you don't need to set anything up separately. Open the AI Management tab in your Levamo dashboard, connect Claude, ChatGPT, or Cursor, and start managing your site through conversation. No extra plugins, no separate accounts. Your AI can draft posts, update plugins, run full site checkups, build pages, and rebuild sections of your site from conversation.
## Wrapping Up
The traditional WordPress rebuild (spend days converting a design into a functioning site, debug layout issues, hand-wire navigation, style blog templates to match) is starting to look like the hard way. With AI that can reason about your design, build safely in draft sandboxes, self-correct through visual feedback, and create proper editing surfaces for your team, a full site rebuild in under an hour is genuinely achievable.
The most impressive part of John's rebuild wasn't the speed. It was the quality. Responsive layouts, editable fields, custom post types, mega menu, scroll animations. Every piece was production-ready, not "good enough for a demo."
If you're planning a site redesign or building something new from scratch, AI just redrew your project timeline.
---
## MemberPress vs Skool: Which Community Platform Wins?
- URL: https://levamo.com/blog/memberpress-vs-skool/
- Category: membership
- Author: Shahzeb Ahmed
- Published: 2026-09-02
MemberPress vs Skool compared on pricing, features, and ownership.
Skool is everywhere right now. Alex Hormozi's involvement, a wave of creator endorsements, and a dead-simple interface have pushed it into just about every "best community platform" conversation. If you've been researching where to build your membership or community, you've probably seen it recommended dozens of times.
MemberPress, on the other hand, has been a go-to WordPress membership plugin since 2012. It doesn't have the same influencer buzz, but it has something Skool doesn't: a feature set that keeps growing without locking you into someone else's platform.
So which one actually deserves your money and your members? That depends on what you're building, how much control you want, and whether you're thinking in months or years. Let's break it down.
## MemberPress vs Skool at a Glance
Here's how the two platforms compare across the factors that matter most.
| Feature | MemberPress | Skool |
|---|---|---|
| Model | Self-hosted WordPress plugin | Fully hosted community SaaS |
| Ownership | You own your data, content, and site | Everything lives on Skool's servers |
| Community | ClubSuite: unlimited forums, sub-groups, and tiers | One activity feed, up to 10 categories |
| Courses / LMS | 9 quiz types, assignments, certificates, gradebook | Modules and videos, no quizzes or certificates |
| Coaching | CoachKit: full coaching management system | None |
| Pricing | From $199.50/yr, 0% transaction fees on Growth+ | From $9/mo plus a 10% fee (2.9% on Pro) |
## What Is MemberPress?
MemberPress is a WordPress plugin that turns any WordPress site into a full membership platform. It handles subscriptions, content protection, online courses (through its built-in LMS called MemberPress Courses), coaching programs via CoachKit, and community features through ClubSuite.
Because it runs on WordPress, you get the full ecosystem: thousands of themes, plugins for email marketing, CRM, analytics, e-commerce, and essentially anything else your business needs. Your content, subscriber list, and payment data all live in your own database on your own server.
MemberPress holds a 4.8 out of 5 on Trustpilot, with users consistently highlighting its feature depth, flexibility, and responsive support.
## What Is Skool?
Skool is a hosted community platform founded in 2019 by Sam Ovens and Daniel Kang. It combines community discussion, course hosting, and membership payments into a single, streamlined interface. Alex Hormozi partnered with the company in 2024, which significantly boosted its visibility in the creator and coaching space.
The pitch is simplicity. You can set up a community in under 30 minutes, charge members immediately, and manage everything from one dashboard. Skool also has a built-in discovery marketplace with over 25 million users, which gives new communities a potential audience from day one.
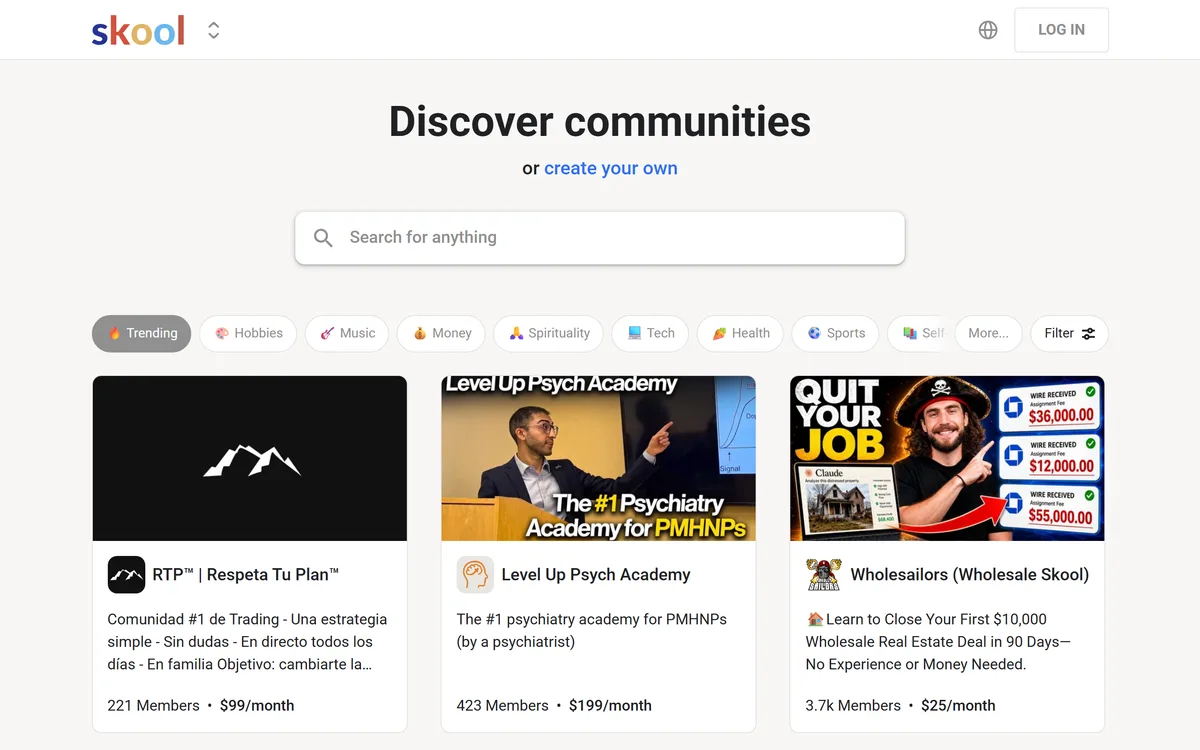
The tradeoff is that everything lives on Skool's platform. Your community content, your member list, your course material, your revenue data. All of it sits on Skool's infrastructure, under Skool's terms.
## Pricing: The Real Math
This is where the comparison gets spicy.
**Skool pricing (2026):**
- Hobby: $9/month with a **10% transaction fee** on all payments
- Pro: $99/month with a **2.9% transaction fee**
That transaction fee on the Hobby plan is the detail most people gloss over. If your community generates $5,000/month in membership revenue, Skool takes $500 off the top. Every month. On top of whatever your payment processor charges.
Even on the Pro plan at $99/month ($1,188/year), you're still paying 2.9% on every dollar your members pay you.
**MemberPress pricing (2026):**
- Launch: $199.50/year (4.9% transaction fee)
- Growth: $349.50/year (**0% transaction fees**)
- Scale: $499.50/year (0% transaction fees)
On MemberPress Growth, you pay $349.50 per year and keep every dollar your members pay you (minus standard Stripe or PayPal processing fees, which you'd pay on any platform).
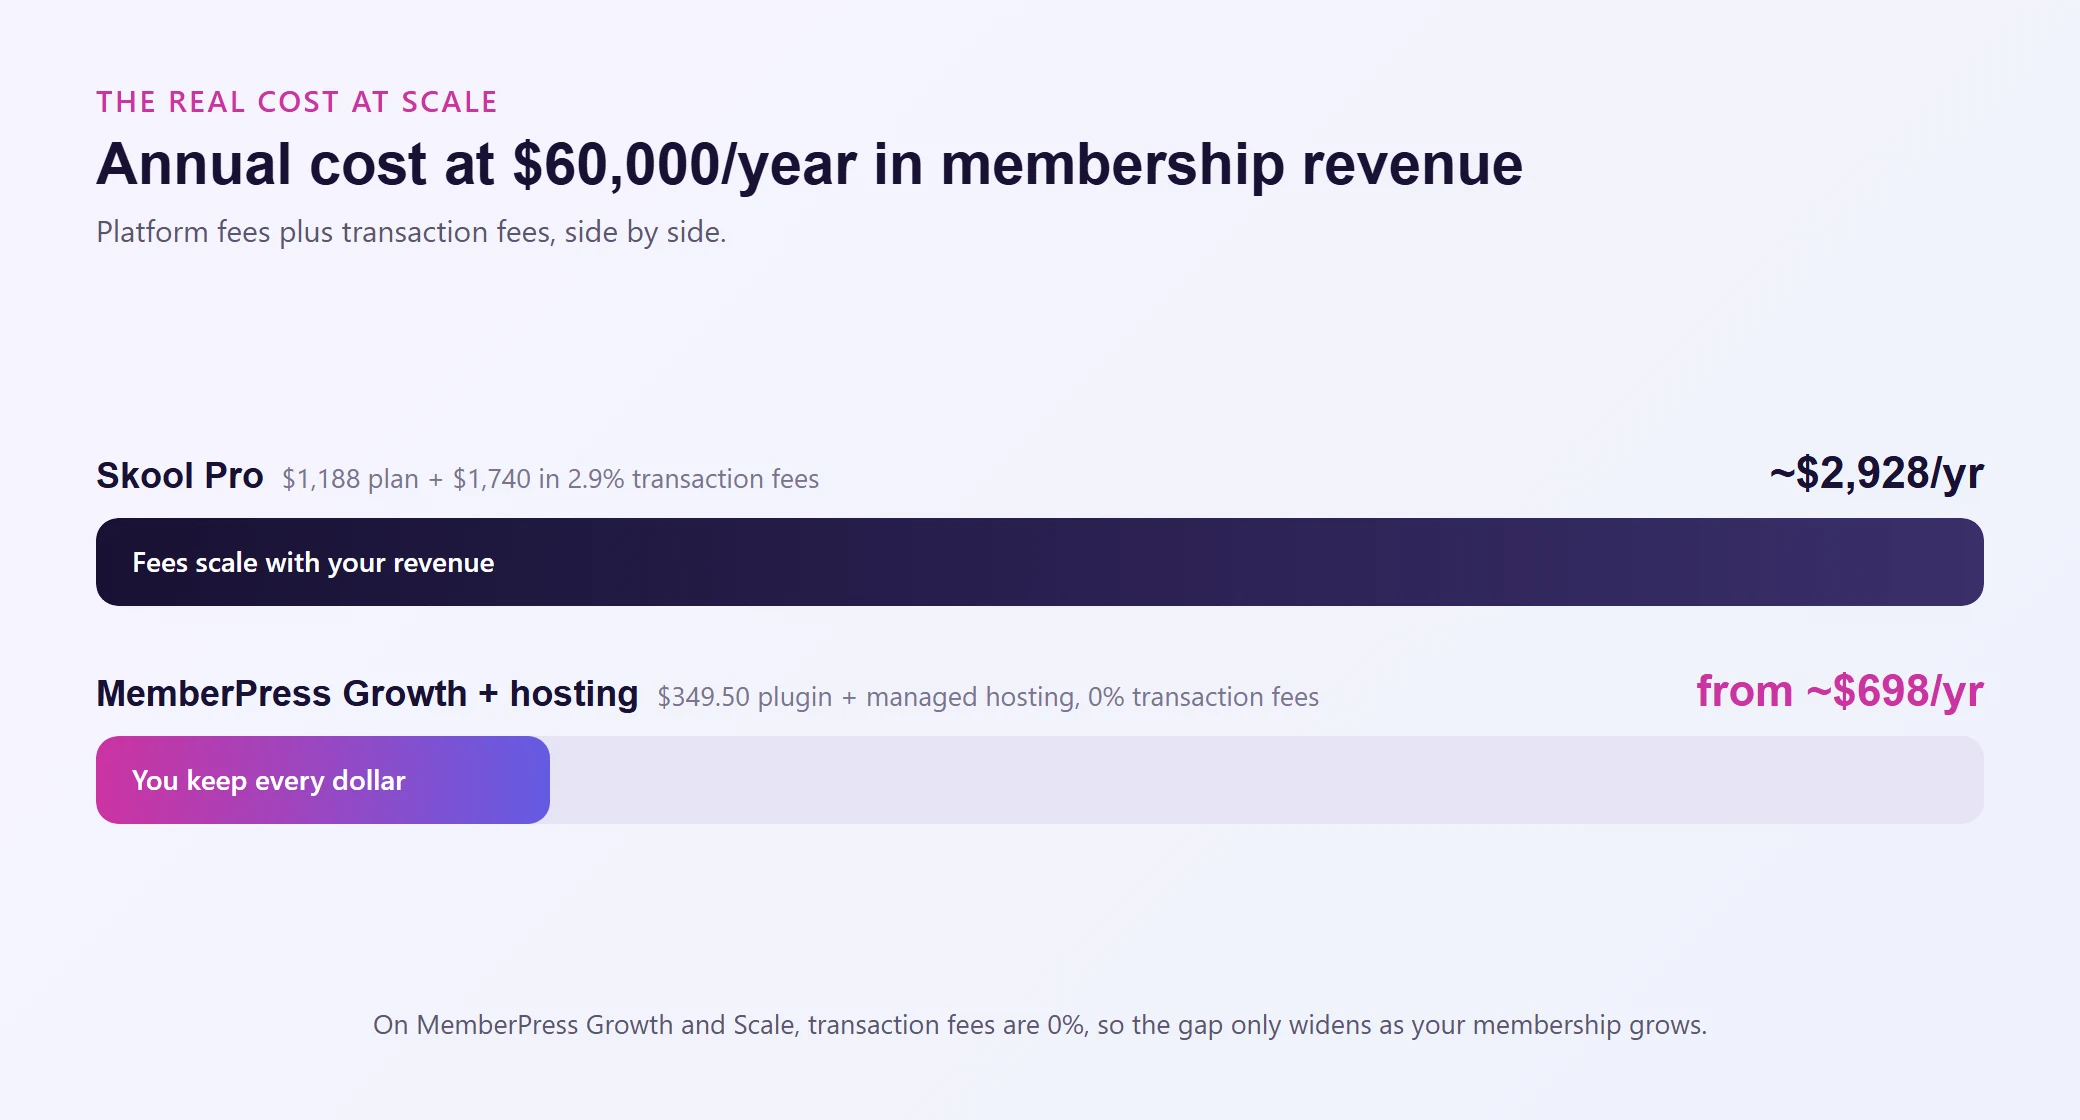
Let's do some quick math. Say your membership generates $5,000/month ($60,000/year):
**Skool Pro:** $1,188/year platform fee + $1,740/year in transaction fees (2.9%) = **$2,928/year**
**MemberPress Growth + managed hosting:** $349.50/year plugin + $348 to $1,188/year hosting = **$697.50 to $1,537.50/year**
That's roughly half the cost, or less. And the gap only widens as your revenue grows. At $20,000/month in membership revenue, Skool Pro's transaction fees alone hit $6,960/year.
MemberPress Growth's transaction fee at that revenue level? Zero.
## Community Features: Feed vs. Forums
Community is Skool's main selling point, and it does it with a specific philosophy: one community feed, gamification, and simplicity.
**Skool's community model:**
- A single activity feed (think Facebook Groups, but inside Skool)
- Up to 10 categories for organizing posts
- Gamification with points, levels, and leaderboards
- Member levels that unlock content as members engage
- Events and calendar for live calls
- A discovery marketplace where potential members can find your community
For small, engaged communities (under a few hundred members), this works beautifully. The feed is clean, engagement is visible, and the gamification creates a sense of progression.
The problem surfaces when your community grows. Ten categories that feel organized at 50 members start feeling cramped at 500. Everything flows through one feed, so conversations from different topics collide. There's no way to create sub-groups, private spaces for different membership tiers, or dedicated discussion areas for specific programs.
**MemberPress community (via ClubSuite):**
- Unlimited discussion forums (not a single feed)
- Member directories with profiles
- Sub-groups for different programs, tiers, or topics
- Activity feeds within each group
- Private spaces for premium members
- No cap on categories or organizational structure
ClubSuite gives you a community architecture that scales. You can create separate spaces for your free members, paid members, coaching clients, and course students, each with their own discussions, without everything piling into one feed.
If you're building a community you expect to grow beyond a few hundred people, the structural difference matters. A lot.
## Course and LMS Features
Both platforms let you host courses, but the depth is dramatically different.
**Skool** keeps courses minimal. You can organize content into modules, upload videos, and that's essentially it. There are no quizzes, no assignments, no certificates, no drip scheduling, no gradebook. If your "course" is really a collection of training videos that members watch at their own pace, Skool handles it fine.
**MemberPress Courses** is a full LMS:
- Drag-and-drop curriculum builder
- Nine quiz types (not just multiple choice)
- Graded assignments with instructor feedback
- Completion certificates
- Content dripping with flexible scheduling rules
- A full gradebook for tracking student progress
- An AI course generator for faster content creation
- Course progress tracking per student
If you're running a professional certification, a structured training program, or any course where assessment and completion tracking actually matter, Skool doesn't have the tools. MemberPress does.
This isn't about Skool being bad at courses. It's that Skool wasn't built as an LMS. It was built as a community platform that happens to host video content. MemberPress was built as a membership platform with a real learning management system baked in.
## Coaching: One Platform Has It, the Other Doesn't
If coaching is part of your business, this section is short.
Skool has no coaching-specific features. No client management. No milestone tracking. No scheduling integration. No private coach-to-client messaging. If you want to run coaching on Skool, you're stitching together workarounds with external tools.
MemberPress has **CoachKit**, a purpose-built coaching management system:
- Unlimited coaching programs
- Milestone and habit tracking per client
- Automated client onboarding workflows
- Built-in scheduling (integrates with Calendly and Simply Schedule Appointments)
- Real-time coach-client messaging (on the Scale plan)
For creators who sell coaching alongside memberships or courses, this isn't a nice-to-have. It's a core business tool that would cost hundreds per year to replicate with separate software.
## Ownership and Data Control
This is the part of the comparison that doesn't show up in feature tables but could be the most consequential decision you make.
**With Skool**, your community, your member list, your course content, your revenue history, all of it lives on Skool's servers. You're operating under their terms, their pricing structure, and their product roadmap. If Skool changes its transaction fees, limits features, or shuts down a community for a terms-of-service violation (something users have reported on review platforms), your business takes the hit.
There's no export button that gives you a clean copy of your community discussions. Your member engagement data, your posts, your community history, it stays with Skool.
**With MemberPress on WordPress**, everything is yours. Your member database, your course content, your payment records, your community data. It all lives in your WordPress database, on your own hosting, under your own domain. You can back it up, migrate it, or build on top of it with any tool in the WordPress ecosystem. No permission required.
If you ever want to change hosting providers, switch to a different community plugin, or restructure your entire membership, you can. The data goes where you go.
For anyone building a business they plan to run for years, platform independence isn't a philosophical preference. It's risk management.
## Integrations and Flexibility
**Skool** takes a walled-garden approach. The platform does what it does, and that's about it. There's no native integration with email marketing platforms, CRMs, payment systems beyond Stripe, analytics tools, or automation platforms. If you want Skool to talk to ActiveCampaign, ConvertKit, or your CRM, you're looking at Zapier or third-party middleware.
Skool also doesn't include email marketing. You'll need a separate tool for email sequences, broadcasts, and subscriber management.
**MemberPress** integrates directly with:
- Email platforms: ActiveCampaign, ConvertKit, Mailchimp, Drip, and more
- Payment processors: Stripe, PayPal, Square, Authorize.net
- Automation: Zapier, Uncanny Automator, WP Fusion
- Analytics: MonsterInsights, Google Analytics
- LMS partners: LearnDash integration
- Plus the entire WordPress plugin ecosystem
Because MemberPress runs on WordPress, you're not limited to what one company decides to build. Need affiliate tracking? There's a plugin for that (MemberPress Scale includes Easy Affiliate). Need advanced analytics? Install MonsterInsights. Need a custom checkout flow? Build it with WordPress tools.
The flexibility gap between a WordPress-based stack and a closed SaaS platform compounds over time. The more your business grows, the more you'll need tools that Skool simply doesn't offer.
## The Discovery Marketplace Argument
Skool's built-in discovery marketplace is a legitimate differentiator. With over 25 million users browsing communities on Skool, there's a real chance new members find you organically through the platform itself.
Worth noting, though: most successful Skool communities don't rely on marketplace discovery. They drive traffic through YouTube, podcasts, social media, and paid ads, the same channels you'd use with MemberPress. The marketplace is a bonus, not a business strategy.
And it comes with a tradeoff. Your community lives in Skool's ecosystem, surrounded by competing communities. Members can browse other groups in the same niche with one click. On your own WordPress site, members land in your world, with your branding, your navigation, and no sidebar of competitors.
## Performance: Why Hosting Matters for Communities
Here's a dimension most MemberPress vs Skool comparisons skip entirely.
With Skool, performance is whatever Skool gives you. You can't optimize anything. If the platform feels slow during a live event or your community feed lags under heavy activity, your only option is to wait for Skool to fix it.
With MemberPress on WordPress, your site's speed and reliability depend on your hosting. A community site with hundreds of logged-in members is a dynamic workload. Every page load, every forum post, every course progress check hits the database. Generic shared hosting struggles with this.
[Hosting built for dynamic WordPress workloads](/memberpress-hosting/) handles it differently. Object caching keeps repeated database queries from bogging down your server. Auto-scaling PHP workers handle traffic spikes during live events or launches. A [global CDN](/cloudflare-cdn/) ensures fast load times regardless of where your members are located.
The combination of MemberPress plus purpose-built hosting isn't just cheaper than Skool. It can be meaningfully faster, because you're choosing infrastructure optimized for exactly how community and membership sites work.
## Who Should Choose Which?
It comes down to how much you value ownership, feature depth, and cost control versus all-in-one simplicity.
| Choose MemberPress if you... | Choose Skool if you... |
|---|---|
| Want full ownership of your community, data, and content | Want the absolute simplest setup possible (under 30 minutes) |
| Need real course features (quizzes, assignments, certificates, gradebook) | Are building a community-first business where discussion is the main product |
| Run coaching programs and need dedicated management tools | Value Skool's gamification (leaderboards, levels, points) as a core engagement strategy |
| Care about long-term cost efficiency, especially as revenue grows | Want built-in discovery through Skool's marketplace |
| Want deep integrations with email, CRM, and analytics tools | Don't need structured courses, coaching tools, or advanced LMS features |
| Are building a membership business you plan to own for years | Are comfortable with platform dependency and Skool's transaction fee structure |
| Already use WordPress or plan to build on it | Prefer a single, opinionated tool over a customizable stack |
## Wrapping Up
Skool and MemberPress approach community building from opposite philosophies. Skool gives you one streamlined tool with a specific way of doing things. MemberPress gives you a flexible, feature-rich platform where you own everything and can build exactly what your business needs.
For creators testing an idea or running a small, discussion-focused community, Skool's simplicity is genuine. But for anyone building a membership business they expect to grow, one where courses, coaching, integrations, and cost efficiency actually matter, MemberPress on WordPress is the stronger foundation. You keep more of your revenue, own all your data, and never have to worry about a platform decision pulling the rug out from under you.
The piece that connects it all is your hosting. A thriving community site with hundreds or thousands of active, logged-in members needs infrastructure built for that exact workload. Choose [hosting that handles dynamic WordPress sites](/managed-wordpress-hosting/), and you get the best of both worlds: MemberPress's flexibility with the performance your members expect.
---
## WordPress Database Optimization: Clean, Repair, and Speed Up MariaDB
- URL: https://levamo.com/blog/wordpress-database-optimization/
- Category: database
- Author: Shahzeb Ahmed
- Published: 2026-09-01
Clean, repair, and optimize your WordPress database to speed up MariaDB.
Your WordPress site might look fine on the surface. Pages load, plugins work, orders come through. But underneath all of that, your database could be quietly turning into a junk drawer.
Every post revision, expired transient, spam comment, and orphaned meta row takes up space. Over months (or years), that clutter adds up. Queries take longer. Your admin dashboard feels sluggish. WooCommerce order lookups slow to a crawl. And you're left wondering why your "fast hosting" doesn't feel fast anymore.
The problem usually isn't your server. It's what WordPress has been stuffing into your database when nobody was watching.
This guide walks you through how to clean, repair, and optimize your WordPress database at the application level. We're not talking about MySQL server tuning or indexing strategies (that's covered in our [MySQL performance tuning guide](/blog/mysql-performance-tuning/)). This is about the data WordPress creates, the bloat it leaves behind, and how to get rid of it safely.
## How WordPress Uses Your Database
WordPress stores almost everything in a MySQL (or MariaDB) database. When you install WordPress, it creates 12 core tables. Here's what each one does:
**wp_posts** stores every post, page, custom post type, revision, and attachment record
**wp_postmeta** holds metadata for each post (custom fields, SEO data, page builder settings)
**wp_options** contains site settings, plugin configurations, widget data, and transients
**wp_comments** and **wp_commentmeta** store comments and their associated metadata
**wp_users** and **wp_usermeta** hold user accounts and profile data
**wp_terms**, **wp_term_taxonomy**, and **wp_term_relationships** manage categories, tags, and custom taxonomies
**wp_links** is a legacy table from the old blogroll feature (rarely used)
Plugins add their own tables on top of these. A WooCommerce store might have 30+ additional tables for orders, products, subscriptions, and analytics. A membership plugin adds tables for access rules, payment logs, and user activity. An LMS plugin creates tables for courses, lessons, quizzes, and student progress.
The more plugins you run, the bigger your database gets. And WordPress doesn't clean up after itself very well.
## What Causes Database Bloat in WordPress
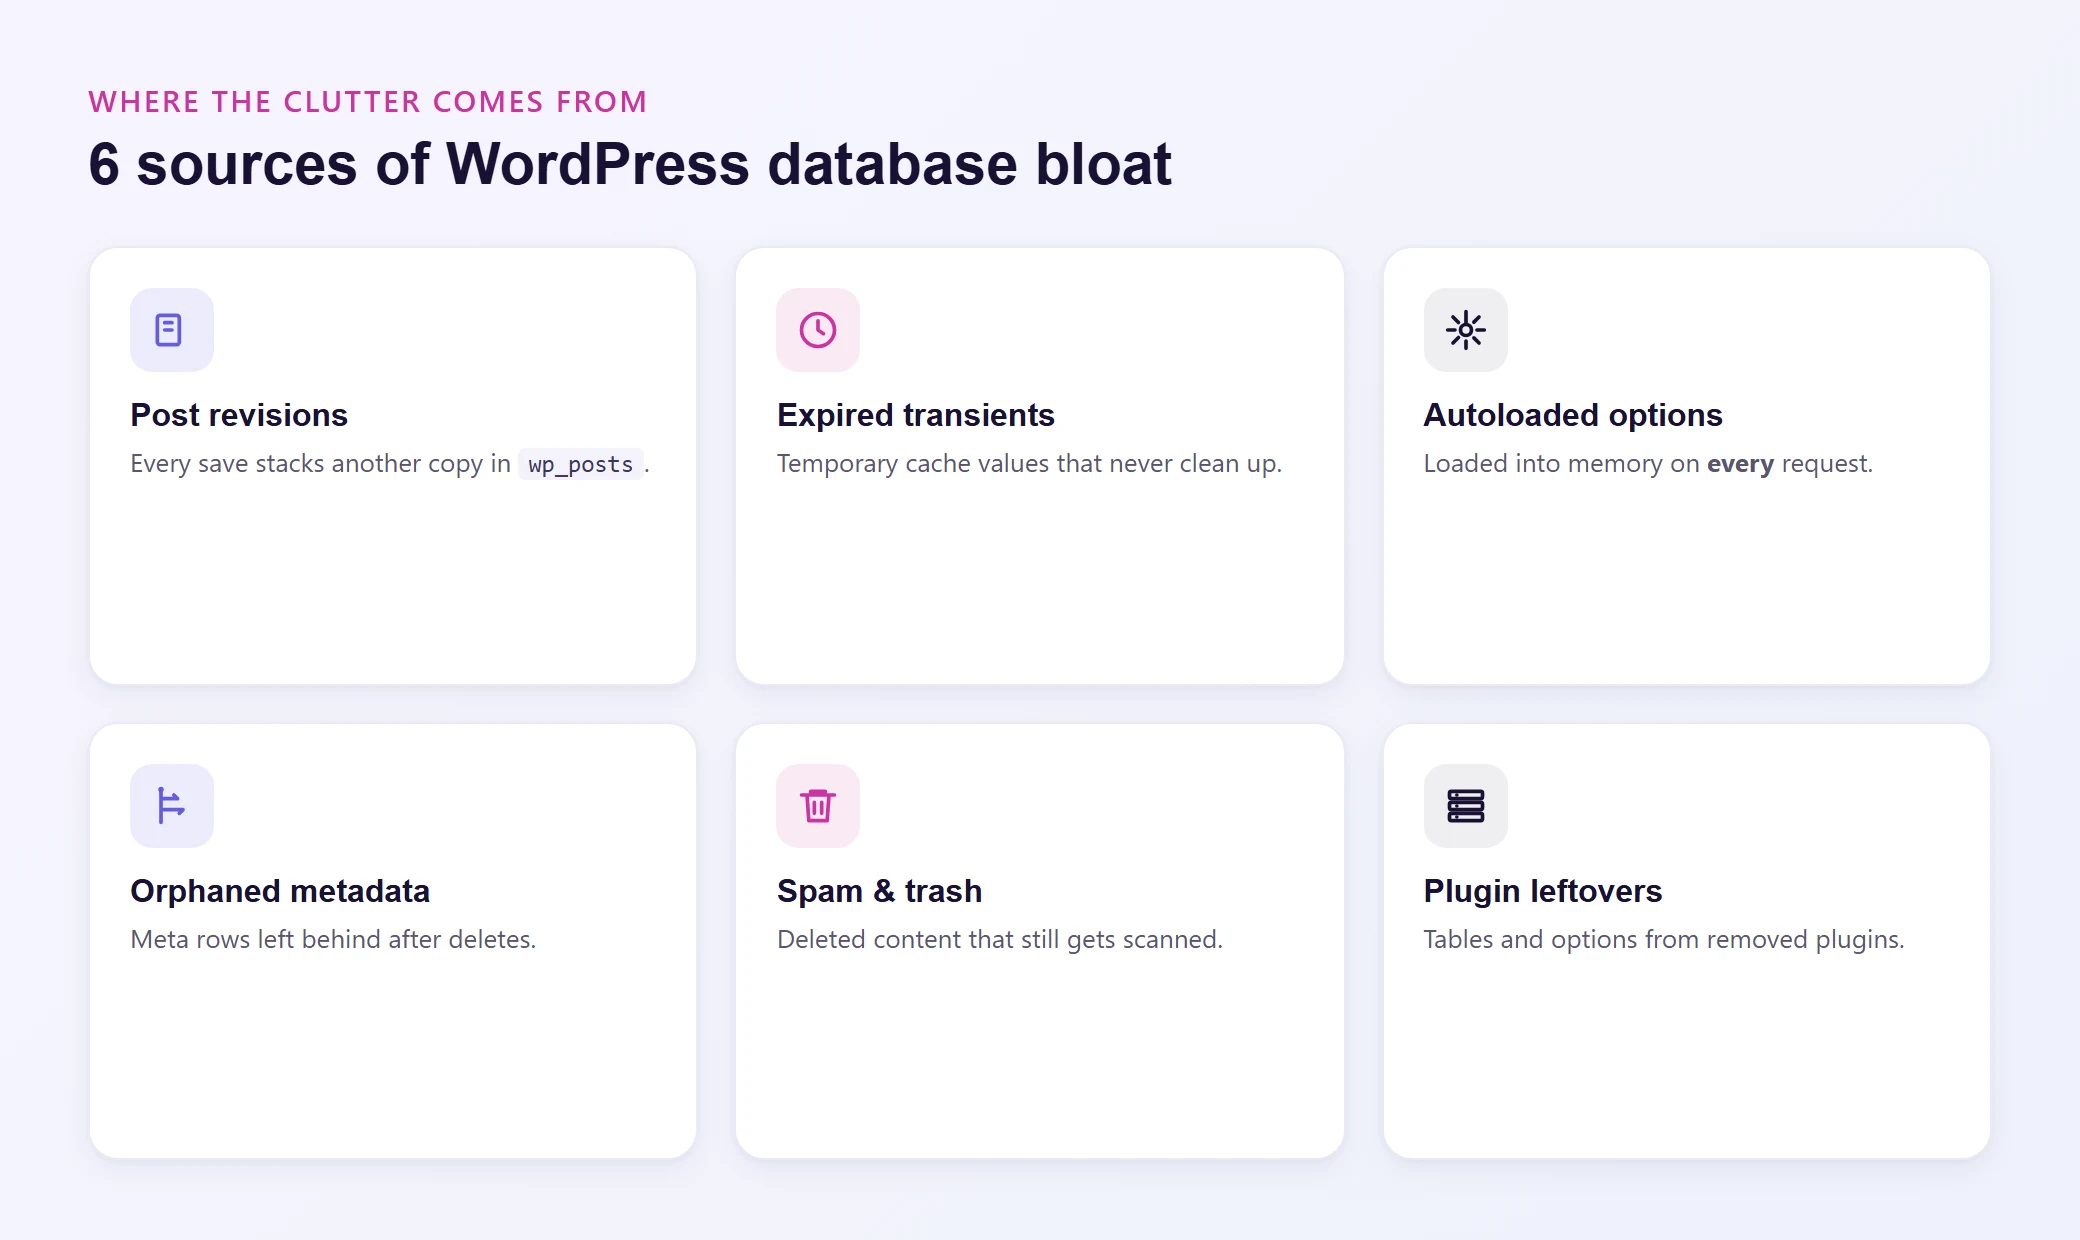
Before you start deleting things, it helps to understand where the bloat comes from. These are the most common offenders.
### Post Revisions
WordPress saves a new revision every time you hit "Save Draft" or "Update" on a post. If you edited a blog post 40 times before publishing, you now have 40 copies of that post sitting in wp_posts.
For a small blog, this isn't a big deal. For a [WooCommerce store](/managed-woocommerce-hosting/) with thousands of products, or a membership site with hundreds of course lessons, revisions can balloon your wp_posts table by 5x or more.
### Expired Transients
Transients are temporary cached values that WordPress and plugins store in wp_options. They're supposed to expire and get cleaned up automatically. In practice, many expired transients stick around forever. Some plugins create thousands of them.
The real problem isn't the disk space. It's that wp_options has an autoload column, and many transients are set to autoload on every single page request. More on that in a moment.
### The wp_options Autoload Problem
This is the single biggest performance killer most site owners never know about. The wp_options table has an autoload column that's either "yes" or "no." Every row marked "yes" gets loaded into memory on every page load, whether it's needed or not.
A fresh WordPress install autoloads about 100KB of options. A site with 30 plugins can easily autoload 2MB or more. Some poorly written plugins store serialized arrays of megabytes in autoloaded options. That's 2MB of data loaded from the database and parsed by PHP on every single request.
### Orphaned Metadata
When you delete a post, WordPress removes the row from wp_posts but doesn't always clean up the associated rows in wp_postmeta. The same thing happens with comments, users, and terms. These orphaned rows serve no purpose and slow down meta queries.
### Spam and Trashed Content
WordPress moves deleted content to the trash rather than removing it. Old spam comments pile up in wp_comments. Trashed posts, pages, and WooCommerce orders linger in wp_posts. All of these rows get scanned during queries even though you'll never use them.
### Plugin Leftovers
When you deactivate and delete a plugin, most plugins leave their database tables and options behind. After a few years of trying different plugins, you can end up with dozens of abandoned tables and hundreds of orphaned option rows.
## Before You Touch Anything: Back Up
Database optimization means deleting data. If you delete the wrong thing, you could break your site. Before running any cleanup operation:
**Create a full backup** of your database. On Levamo, you can take an on-demand snapshot from the dashboard in one click.
**Test on staging first** if you're nervous. Levamo's one-click staging lets you clone your site and experiment without risk.
**Note your current performance baseline.** Run a few page loads and note the response times so you can measure the improvement after cleanup.
If you have hourly backups enabled, you can roll back to a point within the last hour if something goes wrong. For sites running WooCommerce or processing membership signups, this is worth the $10/month.
## Cleaning Post Revisions
You have two options: limit future revisions and delete existing ones.
### Limit Future Revisions
Add this line to your wp-config.php file to cap revisions at a reasonable number:
```
define('WP_POST_REVISIONS', 5);
```
This keeps the 5 most recent revisions for each post and prevents unlimited accumulation going forward. You can set it to false to disable revisions entirely, but keeping a few gives you a safety net for undoing recent changes.
### Delete Old Revisions
**Using WP-CLI** (the fastest method for large sites):
```
wp post delete $(wp post list --post_type='revision' --format=ids) --force
```
This finds every revision in your database and permanently deletes them. On a site with 10,000+ revisions, this can reclaim hundreds of megabytes.
**Using SQL directly** (if you have database access through phpMyAdmin or a similar tool):
```
DELETE FROM wp_posts WHERE post_type = 'revision';
DELETE FROM wp_postmeta WHERE post_id NOT IN (SELECT ID FROM wp_posts);
```
The second query cleans up the orphaned metadata left behind after deleting the revisions.
### How Much Space Will This Save?
It depends on your site. A 3-year-old blog with 200 posts and no revision limit can easily have 5,000+ revision rows. A WooCommerce store with custom product descriptions that get edited frequently can have even more. Deleting revisions typically reduces wp_posts table size by 40% to 80%.
## Cleaning Transients
Expired transients should clean themselves up, but they often don't. Here's how to force the cleanup.
**Using WP-CLI:**
```
wp transient delete --expired
```
To delete *all* transients (including non-expired ones that will regenerate automatically):
```
wp transient delete --all
```
**Using SQL:**
```
DELETE FROM wp_options WHERE option_name LIKE '_transient_%';
DELETE FROM wp_options WHERE option_name LIKE '_site_transient_%';
```
After deleting transients, plugins will recreate the ones they need on the next page load. This is safe. You're not losing any permanent data.
## Fixing the wp_options Autoload Problem
This optimization alone can shave 100ms or more off every page load. Here's how to audit and fix it.
### Check Your Current Autoload Size
Run this SQL query to see how much data is being autoloaded:
```
SELECT SUM(LENGTH(option_value)) AS autoload_size
FROM wp_options
WHERE autoload = 'yes';
```
If the result is over 1MB, you have a problem. Over 500KB is worth investigating.
### Find the Biggest Offenders
```
SELECT option_name, LENGTH(option_value) AS size
FROM wp_options
WHERE autoload = 'yes'
ORDER BY size DESC
LIMIT 20;
```
This shows you the 20 largest autoloaded options. You'll often find plugin analytics data, serialized widget settings, or massive option arrays from plugins you've already deleted.
### Turn Off Autoload for Non-Critical Options
For options that don't need to load on every request, you can switch them to non-autoloaded:
```
UPDATE wp_options SET autoload = 'no'
WHERE option_name = 'some_plugin_analytics_data';
```
Be conservative here. Only change options you're sure aren't needed on every page load. Plugin settings that affect front-end behavior should stay autoloaded. Analytics logs, migration data, and unused plugin options can safely be switched off.
### WordPress 6.6+ Autoload Values
If you're running WordPress 6.6 or newer, the autoload column supports additional values beyond just "yes" and "no." WordPress now uses "on," "off," "auto-on," and "auto-off" for more granular control. The "auto" variants let WordPress decide based on actual usage patterns. When you're manually updating autoload values, use "on" and "off" instead of the legacy "yes" and "no."
## Removing Orphaned Data
Orphaned metadata rows accumulate silently. These queries clean them up.
### Orphaned Post Meta
```
DELETE pm FROM wp_postmeta pm
LEFT JOIN wp_posts p ON pm.post_id = p.ID
WHERE p.ID IS NULL;
```
### Orphaned Comment Meta
```
DELETE cm FROM wp_commentmeta cm
LEFT JOIN wp_comments c ON cm.comment_id = c.comment_ID
WHERE c.comment_ID IS NULL;
```
### Orphaned User Meta
```
DELETE um FROM wp_usermeta um
LEFT JOIN wp_users u ON um.user_id = u.ID
WHERE u.ID IS NULL;
```
### Orphaned Term Relationships
```
DELETE tr FROM wp_term_relationships tr
LEFT JOIN wp_posts p ON tr.object_id = p.ID
WHERE p.ID IS NULL;
```
On a site that's been running for a few years with regular plugin changes, these queries can remove thousands of useless rows.
## Cleaning Spam and Trash
### Delete All Spam Comments
```
wp comment delete $(wp comment list --status=spam --format=ids) --force
```
Or via SQL:
```
DELETE FROM wp_comments WHERE comment_approved = 'spam';
```
### Empty the Trash
WordPress automatically empties the trash after 30 days by default. To empty it immediately:
```
wp post delete $(wp post list --post_status=trash --format=ids) --force
```
You can also change the trash retention period in wp-config.php:
```
define('EMPTY_TRASH_DAYS', 7);
```
Setting this to 7 days keeps trash from piling up without removing content too aggressively.
## Optimizing Database Tables
After deleting a bunch of data, the physical table files don't shrink automatically. MySQL/MariaDB leaves "holes" in the table where deleted rows used to be. The OPTIMIZE TABLE command defragments the table and reclaims that space.
### Using WP-CLI
```
wp db optimize
```
This runs OPTIMIZE TABLE on every table in your WordPress database.
### Using SQL
```
OPTIMIZE TABLE wp_posts, wp_postmeta, wp_options, wp_comments, wp_commentmeta, wp_usermeta;
```
### Repairing Corrupted Tables
If you're seeing database errors or your site crashed during a write operation, you may have corrupted tables. Add this to wp-config.php temporarily:
```
define('WP_ALLOW_REPAIR', true);
```
Then visit yoursite.com/wp-admin/maint/repair.php to run the built-in repair tool. **Remove the constant from `wp-config.php` after you're done**, because this repair page is accessible without authentication.
## Removing Leftover Plugin Tables
Deleted plugins often leave their tables behind. Here's how to find and remove them.
### Identify Non-Core Tables
WordPress core tables all follow the pattern wp_{tablename} (or whatever your prefix is) and there are exactly 12 of them. Anything beyond those 12 was created by a plugin or theme.
To list all tables in your database:
```
wp db tables
```
Compare this list against your currently active plugins. If you see tables from plugins you removed months ago, they're safe to drop.
### Drop Unused Tables
```
DROP TABLE wp_old_plugin_table;
```
Only drop tables from plugins you're certain you won't reinstall. If you're unsure, rename the table instead of dropping it:
```
RENAME TABLE wp_old_plugin_table TO wp_backup_old_plugin_table;
```
If your site runs fine for a month, you can safely drop the renamed table.
## Using a Plugin for Ongoing Maintenance
If you'd rather not run SQL queries manually, several plugins handle database cleanup through a visual interface.
**WP-Optimize** is the most popular option. It cleans revisions, drafts, transients, spam comments, and orphaned data. It can also schedule automatic cleanups on a weekly or monthly basis. The free version handles most use cases.
**Advanced Database Cleaner** goes deeper, identifying orphaned tables and options left by deleted plugins. It's particularly useful for sites that have gone through many plugin changes over the years.
**WP-Sweep** takes a more conservative approach, using proper WordPress functions (like wp_delete_post_revision()) instead of raw SQL queries. This ensures all associated data gets cleaned up through WordPress hooks.
Whichever plugin you use, always run a backup before the first cleanup. After that, scheduled weekly or monthly cleanups keep bloat from building up again.
## Scheduling Regular Maintenance
Database optimization isn't a one-time task. WordPress accumulates bloat continuously. Here's a practical maintenance schedule:
**Weekly:** Delete spam comments and clear expired transients. This takes seconds and prevents the two fastest-growing sources of bloat from getting out of hand.
**Monthly:** Delete old post revisions (keeping the most recent 5), clean orphaned metadata, and optimize tables. This is your main cleanup pass.
**Quarterly:** Audit wp_options autoload size, check for abandoned plugin tables, and review your overall database size trend. If it's growing faster than your content, something is creating unnecessary data.
You can automate the weekly and monthly tasks with WP-Optimize's scheduler or set up WP-CLI cron jobs if you prefer command-line control.
## How Levamo's Stack Helps
Your hosting environment has a direct impact on database performance. Here's what Levamo provides that makes your optimized database run even faster.
**MariaDB instead of MySQL.** Levamo runs MariaDB, which is a drop-in replacement for MySQL built by MySQL's original creators. MariaDB's query optimizer handles complex WordPress queries more efficiently, particularly the multi-table JOINs that WooCommerce and membership plugins generate. You get better performance without changing a single line of code.
**KeyDB + Redis object caching.** Available on Business plans and above, object caching stores frequently accessed query results in memory. Once you've cleaned your database, the cached responses are smaller and faster to serve. A clean database plus object caching is the best combination for logged-in user performance.
**Daily backups with one-click restore.** Every Levamo plan includes daily automatic backups, so you can clean your database with confidence. If something goes wrong, you restore to the previous day in one click. For WooCommerce stores and membership sites where data changes hourly, hourly backups are available as a $10/month add-on.
**One-click staging.** Test your cleanup process on a staging copy before touching production. Levamo's staging includes a "use less storage" option that skips copying your uploads folder, so you can spin up a test environment without doubling your disk usage.
## Measuring the Results
After running your cleanup, here's how to verify it worked.
### Check Database Size
```
wp db size --tables
```
Compare this against what you noted before the cleanup. A 30% to 60% reduction in total database size is common for sites that have never been optimized.
### Check Autoload Size
Run the autoload query from earlier and compare. Getting under 500KB is a good target.
### Test Page Load Times
Load a few pages and check response times in your browser's developer tools (the "Waiting for server response" or TTFB value). You should see a noticeable improvement, especially on pages that run heavy database queries like WooCommerce shop pages, membership dashboards, and course listings.
### Monitor Over Time
Check your database size monthly. If it's growing faster than your actual content, investigate which plugin or process is creating the excess data. The wp_options table is usually the first place to look.
## Wrapping Up
A bloated WordPress database is one of those problems that creeps up slowly. Everything works fine until one day it doesn't, and by then you've got thousands of orphaned rows, megabytes of autoloaded options, and more post revisions than actual posts.
The good news is that cleaning it up is straightforward. Limit revisions, purge transients, audit your autoloaded options, remove orphaned data, and optimize your tables. Do it once thoroughly, then schedule regular maintenance so it never gets that bad again. Pair that clean database with [Levamo's MariaDB engine](/managed-wordpress-hosting/) and object caching, and your WordPress site will feel like it just got a new set of tires.
---
## BuddyNext Review: The WordPress Community OS for Every Kind of Community
- URL: https://levamo.com/blog/buddynext-review/
- Category: membership
- Author: Shahzeb Ahmed
- Published: 2026-08-31
BuddyNext review: a WordPress community platform with a free core and add-on apps.
Most WordPress community plugins answer one question: how do people post updates and join groups? [BuddyNext](https://wbcomdesigns.com/downloads/buddynext/ "nofollow") answers a different question: what *kind* of community are you actually building, and does the platform bend to that or make you bend to it?
That distinction is the whole reason BuddyNext ships as a free core engine plus more than a dozen companion apps instead of one monolithic plugin. A course community, a job-board community, a photo-sharing community, an events community, and a Q&A support community have almost nothing in common structurally, so treating them as one product with one feature set is how most community plugins end up mediocre at everything. BuddyNext's bet is the opposite: one identity and moderation layer underneath, then a real, purpose-built app on top for whatever the community actually is.
In this BuddyNext review, we'll cover the core engine, then spend real time on the part most reviews skip entirely: the companion apps, what kind of community each one is actually for, what's free versus paid in each, and how to pick the right combination instead of installing everything and hoping.
Let's get into it.
## What is BuddyNext?
BuddyNext is a WordPress plugin that turns a site into a complete community platform: activity feed, member profiles, Spaces (their term for groups), a member directory, private messaging, and moderation tools, all wired together out of the box rather than assembled from separate add-ons.
It is not built on top of BuddyPress. It's a standalone plugin with its own architecture, which matters for performance, more on that in the setup section below.
But the core engine is only half the product. BuddyNext is built by Wbcom Designs, a team that already maintains a dozen-plus standalone WordPress plugins covering forums, LMS, media, job boards, directories, gamification, events, and marketplaces, and most of them plug into BuddyNext automatically when both are active (the exact integration depth varies by app, covered honestly below, not every one of these has a documented BuddyNext hook yet). That's the part that actually answers "what kind of community platform is this": not a social feed with some groups bolted on, but a hub that becomes whatever kind of community you point it at.
## One Engine, Every Kind of Community
This is the section most community-plugin reviews skip, because most community plugins don't have an answer here. BuddyNext does, and it's worth walking through what each companion app actually turns your community into in real detail, because a list of app names means nothing on its own, the question is whether they map to real community types and what you actually get for free before you'd need to pay.
### Course and membership communities: Learnomy
[Learnomy](https://wbcomdesigns.com/downloads/learnomy/ "nofollow") is a full, free WordPress LMS, not a stripped trial of a paid one. The free tier includes unlimited courses with video, audio, PDF, and reading lessons, a six-question-type quiz engine (multiple choice, true/false, short answer, fill-in-the-blank, essay, with five more question types in Pro), anti-cheat tab-switch tracking, an essay-grading inbox, and Ed25519-signed certificates with a public verification page and QR codes. Checkout runs directly through Stripe and PayPal at zero platform fees, no percentage cut the way hosted course platforms like Teachable or Kajabi take.
The part that matters most for a community built around teaching is that Learnomy ships a real instructor marketplace. Teachers apply, get their own dashboard, and get paid automatically through Stripe Connect; therefore, a multi-instructor community (such as a cohort of coaches or a network of tutors) doesn't need a separate payout system bolted on. Pair it with BuddyNext, and your students get a real community profile and can join Spaces around a cohort or topic, while the actual teaching, grading, and course sales run through Learnomy underneath. That's the difference between "a community that happens to sell a course" and BuddyBoss's approach of needing a separate LearnDash license just to get here. Learnomy is newer to the market (distributed from the Wbcom store, not WordPress.org yet), but with 166 REST endpoints and a migration wizard from LearnDash, Tutor LMS, and LifterLMS, switching in isn't a rebuild from scratch. Pricing starts at $48/year once you need Pro's advanced quiz types, content drip, or cohort features, though the core teaching and certification stack is entirely free.
### Support, product feedback, and Q&A communities: Jetonomy
[Jetonomy](https://wbcomdesigns.com/downloads/jetonomy/ "nofollow") is what turns BuddyNext from "a place people post updates" into "a place people go to actually get help or influence a roadmap." It's forums, accepted-answer Q&A, and an Ideas board with a Planned-to-Shipped workflow, all free, with custom database tables rather than bloating wp_posts the way CPT-based forum plugins do (their own benchmark claims 50,000 topics at roughly 200ms with Redis caching).
The mechanic that actually matters for community health at scale is Jetonomy's six trust levels (TL0 through TL5), with TL1 through TL3 auto-promoting based on genuine activity and TL2+ automatically exempt from anti-spam checks. This creates a self-moderating community: your most active, trusted members stop hitting friction meant for first-time visitors without you manually promoting anyone. TL4 and TL5 are manual, reserved for people you actually vet. Add voting, reputation, three-level threading, a Markdown composer, and built-in importers from bbPress, wpForo, and Asgaros (with URL preservation so old links don't 404), and you've got a genuine forum platform, not a comments section wearing a forum's clothes. The free version covers all of the above; Pro adds AI-assisted moderation, reactions, private messaging between forum members, and email digests.
### Photo, video, and visual-first communities: WPMediaVerse
[WPMediaVerse](https://wbcomdesigns.com/downloads/mediaverse/ "nofollow") is worth understanding as more than an optional add-on: BuddyNext's own messaging and media posting actually run through WPMediaVerse under the hood, so once your members start sharing more than text, this stops being optional and becomes closer to a core dependency.
Free gets you drag-drop photo and video upload, albums, collections, and gallery groups, reactions, threaded comments, follows, favorites, @mentions, an Instagram-style explore feed with a lightbox, and 1:1 direct messages that include voice messages and message requests. The feature that matters most for any community accepting user uploads at scale is automatic content moderation: every upload runs through OpenAI Vision using your own API key, so you're not manually reviewing a growing queue of user-generated photos and video by hand. Custom database tables mean "100,000 media items add zero rows to wp_posts," per their own benchmark claim, worth verifying at your own scale but directionally the right architecture choice. Pro adds five layout modes (including an Instagram-style stories bar), cloud storage via S3 or BunnyCDN, video transcoding, and a gamification suite (photo challenges, battles, tournaments) that ties directly into WB Gamification, covered below.
### Professional, alumni, and industry communities: WP Career Board
[WP Career Board](https://wbcomdesigns.com/downloads/wp-career-board/ "nofollow") turns BuddyNext into a job board your members actually use rather than a static "careers" page nobody checks. Free includes job listings with real filtering (keyword, category, location radius, salary band, remote-only), saved searches with daily email alerts, apply-with-profile or CV upload with screening questions, a full resume database and builder (it can run as a standalone resume board on its own), company profiles with follow and new-job alerts, and JobPosting schema markup on every listing, meaning your jobs are eligible to show up in Google's dedicated Jobs search results, not just regular organic search.
For an alumni network, a professional association, or an industry-specific community, this is frequently the single feature that makes membership worth paying for, a curated, trusted job board beats a generic one because the pool posting and applying is already vetted by community membership. It's block-first (14 blocks, Gutenberg-native, no shortcodes or jQuery), and ships migrators from WP Job Manager, JobBoardWP, Simple Job Board, and WP Job Openings if you're consolidating from an existing setup. Pro adds a Kanban-style application pipeline, credit-based paid job posting plans, and AI candidate matching.
### Local, niche, and business-directory communities: Listora
[Listora](https://wbcomdesigns.com/downloads/listora/ "nofollow") adds 10 listing types out of the box, business, restaurant, real estate, hotel, job, event, classified, healthcare, education, and place, which covers most of what a local or niche-vertical community actually needs without stacking separate directory add-ons. Free includes multi-step frontend submission with a review queue, business claims, five-star reviews with owner replies and helpful votes, full-text search with distance/rating/amenity filters, and mapping through OpenStreetMap, deliberately, so there's no API key requirement and no per-view charges the way Google Maps-based directory plugins eventually cost you at scale.
A neighborhood community, a niche marketplace of local service providers, or an events-and-venues-focused community all lean on Listora rather than the plain activity feed for their actual core content. It's built block-first on the Interactivity API with no jQuery, includes six layers of anti-spam protection, CSV and GeoJSON import/export, and migrators from Business Directory Plugin, Directorist, GeoDirectory, and ListingPro. Pro adds the monetization layer: credit-based paid listing plans, Google Maps and Places autocomplete, per-listing analytics, and a "Needs Marketplace" mode where visitors post what they're looking for and businesses respond to it, a reverse-directory model most competitors don't have at all.
### Marketplaces where members sell to each other: WP Sell Services
[WP Sell Services](https://wbcomdesigns.com/downloads/wp-sell-services/ "nofollow") is a standalone Fiverr-and-Upwork-style service marketplace: vendors list tiered packages for buyers to browse and purchase directly, or buyers post a project brief and collect proposals instead, both modes ship free and can run side by side. An 11-status order lifecycle handles requirements collection, delivery, revisions, and dispute resolution, the actual mechanics a service sale needs that a standard product page was never built for.
Worth being precise here since it's easy to mischaracterize: this does **not** require WooCommerce. It ships its own standalone Stripe, PayPal, and offline checkout, confirmed directly from the product's own FAQ. WooCommerce integration exists but only as an optional Pro feature for stores that specifically want its 100+ payment gateway options, not as a dependency. That means a freelancer collective, a consultant network, or a coaching community can run an entire service marketplace inside BuddyNext without a separate storefront plugin underneath it. Free covers both marketplace modes, the full order lifecycle, and standalone checkout; Pro starts at $48/year and adds WooCommerce as an optional checkout path, vendor analytics, and automated payouts.
### Events, meetups, and RSVP-driven communities: Eventonomy
[Eventonomy](https://wbcomdesigns.com/downloads/eventonomy/ "nofollow") is worth flagging here with one honest caveat up front: unlike the six apps above, it is **not currently a documented BuddyNext integration**, neither product's page mentions the other. It's a separate free Wbcom product, not officially part of BuddyNext's companion-app roster yet. Given how directly relevant it is to community management, it's worth knowing about regardless, and it wouldn't be a surprise if that integration gets documented later given the pattern with the rest of the ecosystem.
On its own merits: Eventonomy is a genuinely complete free events platform, unlimited events and RSVPs, RSVP states of going/maybe/no with guest counts, capacity caps with automatic waitlisting, four calendar views, recurring events, an ICS calendar feed, guest RSVP without requiring an account, and magic links so attendees can manage their own RSVP without logging in. A community built around recurring meetups, a conference, or a series of workshops could run entirely on Eventonomy today, just managed as a parallel system to BuddyNext rather than a wired-in one. Pro adds paid ticketing through Stripe, PayPal, Square, or Mollie, a door check-in scanner, and SMS reminders via Twilio.
### The engagement layer across all of the above: WB Gamification
[WB Gamification](https://wbcomdesigns.com/downloads/wordpress-gamification-plugin/ "nofollow") is the piece that ties everything above together, and the detail worth leading with: it is **100% free forever**, GPLv2, unlimited sites, every feature included, no paid tier exists.
It's a real engine, not a badge sticker: an event-sourced points ledger built on Action Scheduler (their own benchmark claims sub-100ms at 100,000+ members), multi-currency points, 30 pre-built badges plus unlimited custom ones with OpenBadges 3.0 verifiable credentials, auto-promoting levels, leaderboards scoped daily through all-time, cohort leagues (a Duolingo-style weekly Bronze-to-Diamond tier system), streaks with a GitHub-style contribution heatmap, peer-to-peer kudos, community-wide shared-progress challenges, and a redemption store that can auto-generate WooCommerce coupons. It already has a **documented** integration with Jetonomy specifically, reputation mirrors 1:1 into the points ledger, so your forum's most helpful answerers get recognized with real points automatically, not just a badge on their profile. A documented integration with WPMediaVerse Pro also exists (17 actions covering uploads, photo battles, and upload streaks). For any community built on the apps above, whichever one you pick, WB Gamification is close to a no-downside add, it's free, it's built to layer on top, and it's the difference between a community that's technically functional and one that gives members a reason to come back tomorrow.
### The smaller pieces, still real answers to real community shapes
Beyond the seven above, the roster rounds out with **WB Polls** (activity polls plus standalone surveys with analytics, one license, no per-response fees), **WB Member Blog** (front-end member blogging using plain WordPress posts, no custom tables, so content stays portable), **WB Ad Manager** (an ad rotator, affiliate link cloaker, and classifieds board consolidated into one plugin, useful for a community that wants to monetize inventory without stacking three separate tools), **MediaShield** (one video player with real protection and watch analytics, aimed at communities selling paid course or coaching video content), **SnipShare** (a self-hosted Pastebin or Gist alternative, built for developer and technical communities that need to share and discuss code snippets natively), and **WB Member Wiki** (a lightweight in-WordPress wiki for communities that need shared, collaboratively-edited documentation, an internal knowledge base or a fan wiki, without standing up MediaWiki separately). None of these are the app that defines a community on their own the way Learnomy or Jetonomy are, but each solves one specific, real problem that would otherwise mean installing a completely unrelated third-party plugin.
### Quick reference: community type to companion app
| Building this kind of community | Add this app | What is genuinely free |
|---|---|---|
| Courses, coaching, cohorts | [Learnomy](https://wbcomdesigns.com/downloads/learnomy/ "nofollow") | Unlimited courses, 6 quiz types, certificates, 0%-fee checkout |
| Support, Q&A, product feedback | [Jetonomy](https://wbcomdesigns.com/downloads/jetonomy/ "nofollow") | Forums, Q&A, Ideas board, 6 trust levels, importers |
| Photo/video, visual-first | [WPMediaVerse](https://wbcomdesigns.com/downloads/mediaverse/ "nofollow") | Uploads, albums, explore feed, AI auto-moderation |
| Alumni, professional, hiring | [WP Career Board](https://wbcomdesigns.com/downloads/wp-career-board/ "nofollow") | Listings, resume DB, Google Jobs schema |
| Local, niche, business directory | [Listora](https://wbcomdesigns.com/downloads/listora/ "nofollow") | 10 listing types, reviews, free OpenStreetMap maps |
| Freelance or service marketplace | [WP Sell Services](https://wbcomdesigns.com/downloads/wp-sell-services/ "nofollow") | Both marketplace modes, full order lifecycle |
| Meetups, conferences, RSVPs | [Eventonomy](https://wbcomdesigns.com/downloads/eventonomy/ "nofollow") | Unlimited events/RSVPs, waitlists, recurring events |
| Engagement layer, any of the above | [WB Gamification](https://wbcomdesigns.com/downloads/wordpress-gamification-plugin/ "nofollow") | Everything, no paid tier exists |
The honest way to evaluate this: don't install everything on this list. Pick BuddyNext for the core identity and moderation layer, then add the one or two companion apps that actually match what your community actually is: a course community needs Learnomy, not Listora. That's the model: purpose-built pieces you assemble, not a monolith you configure.
## Should You Choose BuddyNext?
BuddyNext is newer than BuddyPress or BuddyBoss, it's currently at version 0.6, so it doesn't have a decade of plugin-directory history behind it. What it does have is a complete free tier: activity feed, Spaces, profiles, messaging, member directory, and moderation are not gated behind a paywall the way some competing plugins gate group messaging or advanced privacy controls.
It's worth being upfront about one thing: BuddyNext isn't distributed through the WordPress.org plugin directory, so you install it from a downloaded zip file rather than searching for it in your WordPress admin. That's a minor extra step, and it's the same distribution model PeepSo itself uses.
If you want a modern, actively developed community platform that adapts to a specific community type instead of forcing a one-size-fits-all social feed, BuddyNext is a strong candidate, especially if you already know you need a course, forum, media, job-board, directory, or marketplace layer and would rather get a purpose-built free tool than a paid add-on bolted onto a generic base. If you specifically need the years-long track record and largest existing third-party plugin ecosystem, BuddyPress or BuddyBoss (with its LearnDash-first maturity) are still the safer, more battle-tested choices today, though neither matches the breadth of purpose-built companion apps BuddyNext ships with from a single vendor.
## Core Features of BuddyNext
BuddyNext's free tier is built around six pillars: activity, spaces, profiles, discovery, messaging, and moderation. Here's what's actually included, no paywall:
- Activity feed with four views (For You, Following, Spaces, Network), six reactions, five-level threaded comments, reposts, and quotes.
- Spaces with three visibility levels, open (anyone can join), private (request to join), and secret (invite-only), each with its own feed, roles, and per-space moderation.
- Rich member profiles with 13 field types, per-field privacy controls, and a profile-completion meter.
- A searchable, filterable member directory plus an Explore feed for trending posts and suggested members.
- One-to-one private messaging with photo and file sharing (group messaging and real-time delivery are Pro).
- Deep moderation: reports, strikes, suspensions, shadow-bans, banned words/hashtags/domains/IPs, and auto-hide thresholds, all usable without upgrading.
- A 4-step guided member onboarding wizard with reminder emails, so new signups don't stall out on an empty profile.
This is the identity and moderation layer every community needs regardless of type, the companion apps above are what turn it into a specific kind of community.
## Pros and Cons of BuddyNext
**Pros (The Good):**
- **Genuinely complete free tier:** Activity feed, Spaces, messaging, profiles, and moderation all ship free, not a stripped demo of the paid version.
- **Purpose-built for the actual community type, not just "social":** Course communities get a real LMS, job communities get a real job board, media communities get real upload/moderation tooling, instead of every community type getting the same generic activity feed.
- **Not built on BuddyPress:** A standalone architecture means it isn't inheriting fifteen years of BuddyPress's accumulated database structure, which shows up as real performance headroom at scale.
- **One vendor, mostly one integration story:** Most companion apps come from the same team and are documented to integrate with BuddyNext, versus stitching together plugins from five different vendors that were never designed to talk to each other. (Not universal, Eventonomy is the current exception, covered honestly above.)
- **Modern moderation out of the box:** Shadow-bans, banned-word lists, and auto-hide thresholds are usually Pro-tier or third-party-plugin territory elsewhere; here they're free.
- **A genuinely free-forever engagement layer:** WB Gamification has no paid tier at all, unusual in a market where GamiPress and myCred charge per integration.
**Cons (The Limitations):**
- **Young platform:** At version 0.6, BuddyNext doesn't have the multi-year public track record that BuddyPress and BuddyBoss have. Early adopters get faster iteration; risk-averse teams may want to watch it mature a bit longer.
- **Ecosystem breadth means more decisions upfront:** More than a dozen companion apps is a genuine strength, but it also means a new site owner has to actually figure out which ones apply, there's no single "turn on everything" button, and shouldn't be one.
- **Integration depth isn't uniform across the ecosystem:** Jetonomy, WPMediaVerse, and WB Gamification have clearly documented BuddyNext ties; some of the smaller apps (WB Polls, WB Member Blog, WB Ad Manager, SnipShare, WB Member Wiki, MediaShield) are positioned as part of the family without the same level of documented, hook-level integration specifics, and Eventonomy currently has none at all. Worth confirming current integration depth for any specific app before assuming it's wired in.
- **Not on WordPress.org:** Distributed from the Wbcom Designs store instead, so it's a manual zip install rather than a plugin-directory search. Functionally identical once installed, just an extra step. The same is true for every companion app covered above.
- **Real-time features are Pro-only:** Group messaging and live delivery (typing indicators, presence, WebSocket push) require the paid tier, free messaging is one-to-one only.
## Step-by-Step Guide to Setting Up a Community with BuddyNext
Setting up BuddyNext follows a familiar WordPress pattern, with one extra step since it isn't in the WordPress.org directory:
- **Download the plugin:** Visit [wbcomdesigns.com/downloads/buddynext](https://wbcomdesigns.com/downloads/buddynext/ "nofollow") and download the free zip file, no account or license key required for the free tier.
- **Install and activate:** In your WordPress admin, go to Plugins → Add New → Upload Plugin, select the downloaded zip, install, then activate.
- **Run the onboarding wizard:** BuddyNext's 4-step setup wizard walks you through the basics, profile field selection, initial Spaces, and notification defaults, so you're not configuring everything from a blank settings screen.
- **Decide what kind of community this actually is, before installing companion apps:** This is the step most guides skip. Don't install Learnomy, Jetonomy, WPMediaVerse, WP Career Board, Listora, and WP Sell Services all at once. Use the reference table above, pick the one or two that match what you're actually building, add the LMS if you're teaching, add the forum if you're supporting, add the media app if you're visual-first, and leave the rest for later. Each is a separate free download from its own product page.
- **Create your first Spaces:** Set up two or three focused Spaces rather than one catch-all group. A dedicated, focused Space (say, an announcements-only one and a general-discussion one) gives new members an obvious first move.
- **Configure moderation before you open signups:** Set your banned-word list and auto-hide thresholds before members arrive, not after the first spam wave. It's a five-minute step that saves a much longer cleanup later.
- **Add WB Gamification once your core community app is live:** Since it's free with no tier to weigh, there's little reason not to layer it in early, points and a leaderboard give your first cohort a reason to stay active while the community is still thin.
- **Invite your first members:** BuddyNext's member onboarding wizard sends reminder emails to profiles that stall out incomplete, worth leaving on for your first cohort so early members actually finish setting up their profiles.
## BuddyNext Pricing Plans
BuddyNext's free plugin is a genuinely complete community platform, not a time-limited trial. Pro adds monetization, AI features, real-time messaging, and analytics on top of the same free foundation. Worth noting: the companion apps covered above are separate Wbcom products with their own free tiers and their own optional Pro upgrades, they are not included in a BuddyNext Pro license, so pricing out a full community stack means checking each app you actually plan to use:
- **Free** - $0 forever. Unlimited members, full activity feed, Spaces, profiles, messaging, member directory, and moderation.
- **Personal** - $149/year (or $399 one-time for a lifetime license), 1 site. Adds Stripe membership tiers, gated Spaces, AI feed ranking and moderation, WebSocket real-time messaging, and analytics.
- **Professional** - $249/year (or $599 lifetime), 5 sites. Same Pro feature set as Personal, licensed across five communities.
- **Agency** - $399/year (or $999 lifetime), unlimited sites plus white-label. Built for agencies managing community sites for multiple clients.
Every Pro tier unlocks the identical feature set, the only difference between tiers is how many sites the license covers, and features already available in a given release never move behind a higher tier later.
For a realistic full-stack example: a course-and-support community can run BuddyNext Free plus [Learnomy](https://wbcomdesigns.com/downloads/learnomy/ "nofollow") Pro plus [Jetonomy](https://wbcomdesigns.com/downloads/jetonomy/ "nofollow") Pro plus WB Gamification, and still land well under the annual cost of a hosted all-in-one platform, before BuddyNext's own Pro tier is even in the picture. Most companion apps follow the same shape as Jetonomy: a genuinely usable free tier, with Pro priced separately in the $48 to $104 per year range (WP Career Board, WPMediaVerse, Listora, and WP Sell Services all fall in this band), while WB Gamification has no paid tier at all.
## Why Choose Levamo with BuddyNext?
This is where hosting stops being an afterthought. A community platform is one of the most demanding things you can run on WordPress: every page view is a logged-in, personalized query, an activity feed, a member's own notifications, a Space they belong to, none of it is a static page a cache can just serve back unchanged.
And BuddyNext's ecosystem model makes this compound rather than stay flat. A community running Learnomy adds quiz submissions and video lesson delivery. One running WPMediaVerse adds photo/video upload processing and an AI moderation API call on every image. One running Jetonomy adds full-text search across tens of thousands of forum posts. One running Eventonomy or WP Career Board adds its own scheduled-query and search-filter load. Each companion app is its own additional dynamic workload stacked on top of the core feed, this isn't a plugin that gets heavier only if you let it, the whole model is designed around adding exactly the load your specific community needs, which means the hosting underneath needs to handle whatever combination you actually assemble.
Levamo's infrastructure was built by a team that ran BuddyBoss hosting at scale, so this isn't a generic "any host will do" recommendation:
- **Scalability:** Container-isolated environments and auto-scaling PHP workers handle community growth, including sudden spikes after a successful invite push or launch campaign, without a manual upgrade scramble.
- **Speed:** LiteSpeed servers, auto-scaling PHP workers, KeyDB + Redis object caching, and [Enterprise Cloudflare CDN](/cloudflare-cdn/) across 300+ locations (included on every plan, not a paid add-on) keep activity feeds, course pages, forum search, and media uploads loading fast even as post, student, and member counts climb together.
- **Security:** Cloudflare WAF and DDoS protection, server-level Monarx malware scanning, free SSL, and authenticator-app 2FA matter more for a community site than a brochure site, you have real user accounts, uploaded media, and in some cases payment data across multiple apps to protect.
- **Reliability:** A community that goes down during its own growth spurt loses the members it just worked hardest to attract. Levamo's 24/7/365 support with sub-minute live chat response means you're not filing a ticket and waiting when your community is down at 2 AM.
A BuddyNext community running two or three companion apps is exactly the kind of dynamic, multi-workload WordPress site that separates hosts that merely serve pages from hosts built for real traffic.
## Conclusion
BuddyNext is a serious, modern option for anyone evaluating WordPress community platforms in 2026, and the honest differentiator isn't the activity feed, every community plugin has one of those. It's that BuddyNext doesn't force every community into the same shape. A course community, a job-board community, a support community, a directory-driven community, and a photo-sharing community are structurally different things, and BuddyNext is the rare platform built by a team that seems to have actually accepted that, rather than shipping one feature set and calling it universal.
The free tier is complete enough to launch a real community on by itself. The companion apps, most of them free at the core too, are what make it worth evaluating seriously against BuddyBoss, Circle, or Mighty Networks: pick the one or two that match what you're actually building from the reference table above, and you get a purpose-built tool for that specific job instead of a generic one stretched to fit.
Pair it with [hosting built for dynamic, multi-workload WordPress sites](/buddypress-hosting/), like Levamo, and you've got the performance headroom to match the platform's ambition.
---
## MemberPress vs Kajabi: Which One Is Worth Your Money?
- URL: https://levamo.com/blog/memberpress-vs-kajabi/
- Category: membership
- Author: Shahzeb Ahmed
- Published: 2026-08-28
MemberPress vs Kajabi compared: pricing, features, ownership, and performance.
You want to sell courses, build a community, or run a membership. Two names keep showing up in every "best platform" list: MemberPress and Kajabi.
On the surface, they look like they solve the same problem. Both let you create memberships, deliver courses, accept payments, and manage subscribers. But the way they do it, what they cost, and who actually owns the business you build on them are fundamentally different.
Kajabi is a fully hosted, all-in-one platform. You sign up, pay monthly, and everything lives on Kajabi's servers. MemberPress is a WordPress plugin. You install it on your own WordPress site, host it wherever you want, and own every piece of data your business generates.
That distinction matters more than most comparison articles let on. Let's break it down.
## MemberPress vs Kajabi at a Glance
Here's how the two platforms compare across the factors that matter most.
| Feature | MemberPress | Kajabi |
|---|---|---|
| Model | Self-hosted WordPress plugin | Fully hosted, all-in-one SaaS |
| Ownership | You own your data, content, and site | Everything lives on Kajabi's servers |
| Courses / LMS | 9 quiz types, graded assignments, gradebook, certificates | Clean course builder, basic quizzes |
| Coaching | CoachKit: full coaching management system | Secondary feature, no dedicated tooling |
| Email | Integrates ActiveCampaign, ConvertKit, Mailchimp | Built-in email marketing |
| Pricing | From $199.50/yr + your hosting | From $179/mo ($2,388/yr on Growth) |
## What Is MemberPress?
MemberPress is a WordPress membership plugin that's been around since 2012. It handles memberships, courses (with a built-in LMS called MemberPress Courses), coaching programs through CoachKit, and community features through ClubSuite.
Because it runs on WordPress, you get the full WordPress ecosystem at your disposal: thousands of themes, plugins for email marketing, CRM, e-commerce, analytics, and pretty much anything else you can think of. Your content, your subscriber list, your payment data, all of it sits in your own database on your own server.
MemberPress currently holds a 4.8 out of 5 rating on Trustpilot, with users consistently praising its feature depth and responsive support.
## What Is Kajabi?
Kajabi is a hosted SaaS platform built for course creators and coaches. It bundles website building, course delivery, email marketing, payments, and basic community tools into a single monthly subscription.
The appeal is simplicity. You don't need to think about hosting, plugins, or server management. Kajabi handles all of that. The tradeoff is that everything, your courses, your subscriber list, your content, lives on Kajabi's infrastructure under Kajabi's terms.
Kajabi sits at 3.5 out of 5 on Trustpilot. Common complaints center on support delays, recent price increases, and the growing reliance on AI-generated support responses.
## Pricing: How the Numbers Actually Stack Up
This is where the conversation gets interesting.
**Kajabi pricing (2026):**
- Basic: $179/month
- Growth: $249/month ($199/month with annual billing)
- Pro: $399/month
That Growth plan, the one most serious creators land on, comes out to roughly $2,388 per year on annual billing. And if you want a branded mobile app, add another $199/month.
**MemberPress pricing (2026 introductory rates):**
- Launch: $199.50/year
- Growth: $349.50/year
- Scale: $499.50/year
Even on the top-tier Scale plan, MemberPress costs $499.50 per year. That's roughly one fifth of what Kajabi Growth costs annually.
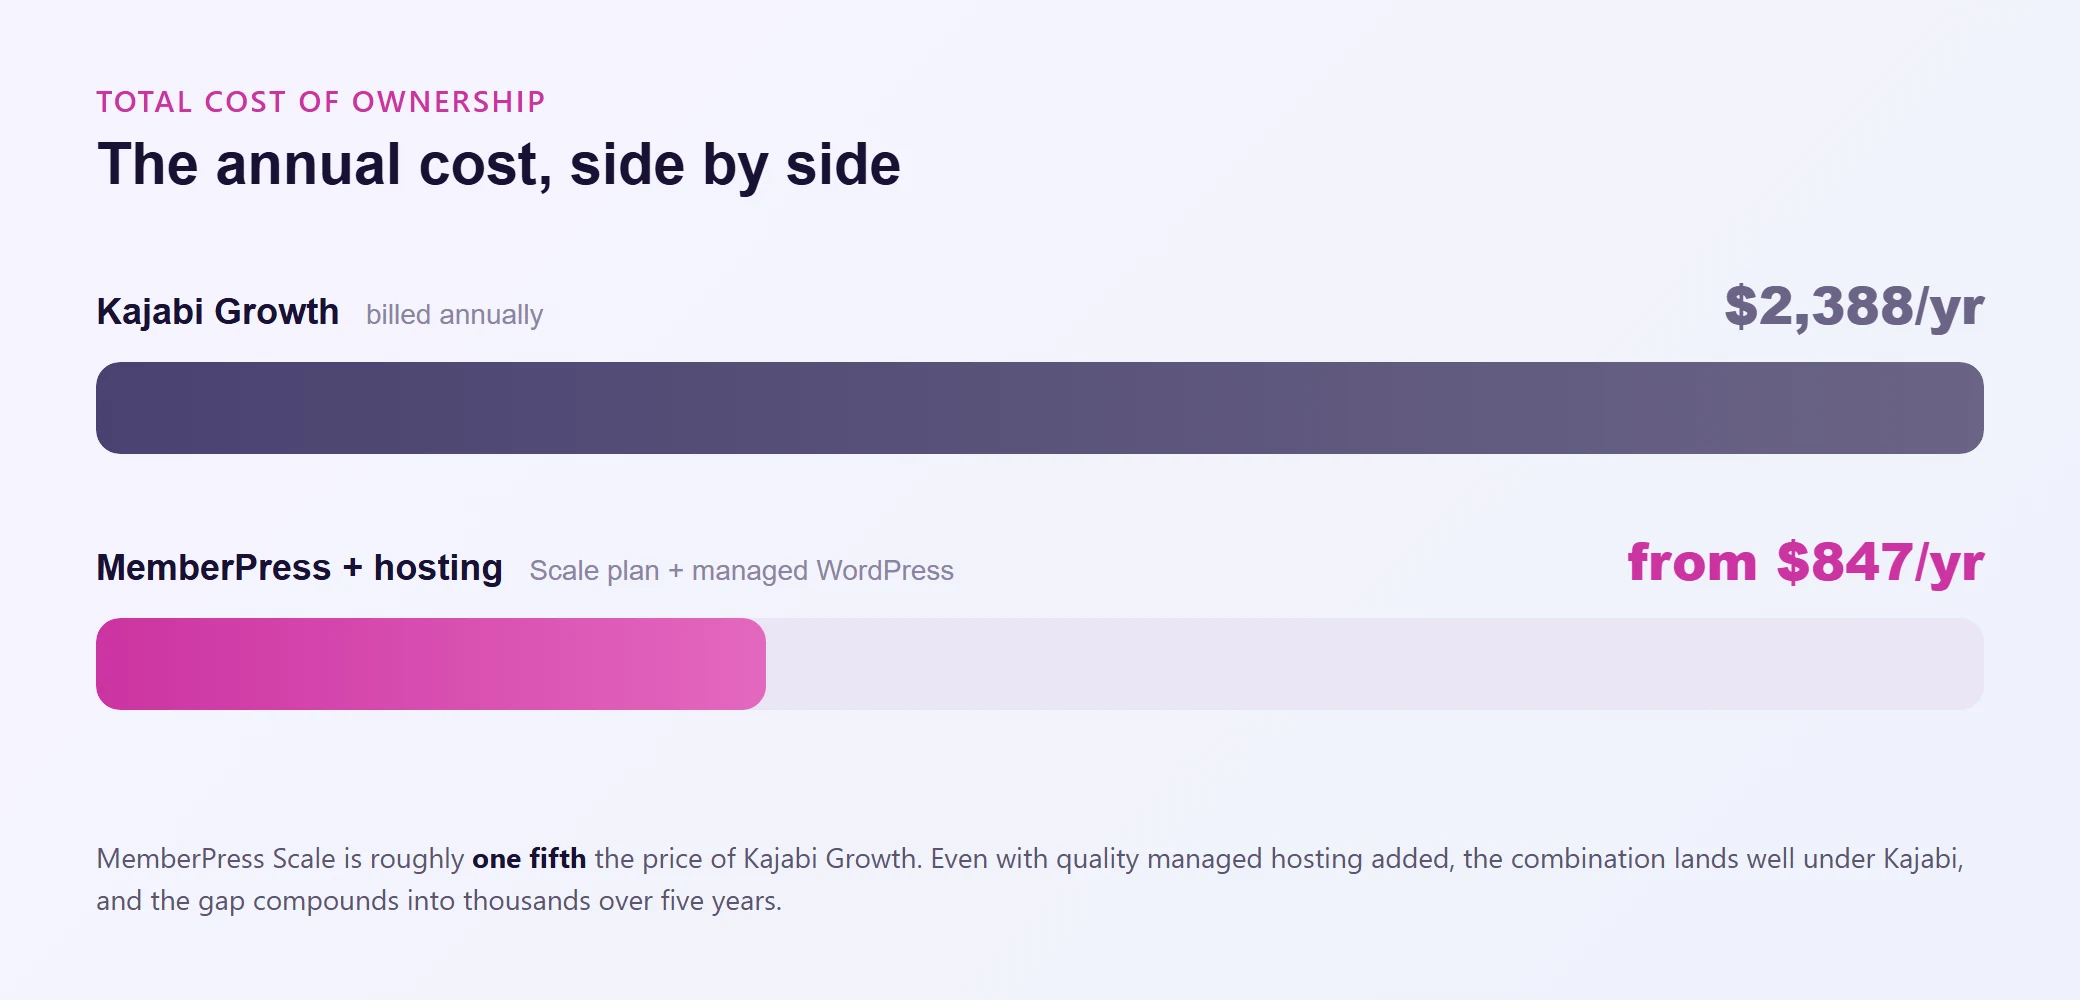
Now, MemberPress requires WordPress hosting, which adds cost. But even on a high-performance [managed WordPress host](/managed-wordpress-hosting/), you're looking at $29 to $99 per month depending on your traffic and resource needs. Add that up: MemberPress Scale ($499.50/year) plus quality managed hosting ($348 to $1,188/year) still comes in well under Kajabi's $2,388/year.
Over five years, the savings compound into thousands of dollars. Money you could reinvest into content, marketing, or better tooling for your members.
## Course and LMS Features
Both platforms let you build and sell online courses. The difference is depth.
Kajabi offers a clean course builder with video hosting, basic quizzes, and drip scheduling. It works well for straightforward courses. You upload your videos, structure your modules, and Kajabi handles delivery. For most simple courses, this is perfectly adequate.
**MemberPress Courses goes deeper. You get:**
- Drip content scheduling with flexible rules
- Nine quiz types (not just multiple choice)
- Graded assignments with instructor feedback
- A full gradebook for tracking student progress
- Completion certificates
- An AI course generator that helps you outline and build courses faster
If you're running a professional certification program, a multi-instructor academy, or anything where assessment and progress tracking actually matter, MemberPress gives you significantly more to work with.
## Community and Coaching Tools
Community features have become a deciding factor for many creators, and this is where the two platforms have diverged sharply.
Kajabi added community features, but they're relatively basic. You get discussion boards and group spaces. No native coaching management, no milestone tracking, no private messaging between coaches and clients.
MemberPress has invested heavily here with two dedicated tools:
ClubSuite gives you forums, member directories, private sub-groups, and activity feeds. Unlike Kajabi's community (or Skool's, for that matter), you're not limited to a handful of categories. You can create as many sub-groups as your community needs.
**CoachKit is a full coaching management system:**
- Unlimited coaching programs
- Milestone and habit tracking per client
- Automated client onboarding workflows
- Built-in scheduling (integrates with Calendly and Simply Schedule Appointments)
- Real-time coach-client messaging (on the Scale plan)
If coaching is part of your business model, this comparison isn't close. MemberPress built purpose-specific tooling for it. Kajabi treats coaching as a secondary feature.
## Ownership and Data Control
This is the part that doesn't show up in feature comparison tables but might be the most important factor in your decision.
With Kajabi, your courses, your client list, your coaching content, your email sequences, your entire business, lives on Kajabi's servers. You're operating under their terms of service, their pricing decisions, and their platform roadmap. If Kajabi raises prices (which they did in late 2025 for the first time since 2015), you either pay more or face the pain of migrating everything out.
With MemberPress on WordPress, everything is yours. Your subscriber database, your course content, your payment records, your community data. It all lives in your own WordPress database, on your own server, under your own domain. If you ever want to change hosting providers, switch themes, or add entirely new functionality, you can. Nobody's permission is required.
This isn't a theoretical concern. Platform dependency is a real business risk. When your revenue depends on a platform you don't control, you're one terms-of-service update or price hike away from a very bad quarter.
## Email Marketing and Integrations
Kajabi includes native email marketing. You can build sequences, send broadcasts, and segment your list without leaving the platform. For creators who want everything under one roof, this is genuinely convenient.
MemberPress doesn't include its own email marketing tool. Instead, it integrates with dedicated platforms: ActiveCampaign, ConvertKit, Mailchimp, Drip, and others. You'll need a separate email service.
Is this a disadvantage? It depends on how you look at it. Kajabi's built-in email is "good enough" for basic sequences. But dedicated email platforms offer deeper segmentation, better deliverability tracking, more sophisticated automation, and they don't lock your subscriber list behind a platform subscription.
If email is a critical revenue driver for your business (and for most membership sites, it is), a dedicated tool will outperform a bundled one.
## Performance: Where Your Hosting Matters
Here's a dimension most MemberPress vs Kajabi comparisons completely ignore.
With Kajabi, performance is whatever Kajabi gives you. You can't upgrade your server, tune your database, or add a CDN. If your course platform feels sluggish under load, your options are limited to "contact support and hope."
With MemberPress on WordPress, your site's speed, uptime, and scalability depend on your hosting. This is both a responsibility and an opportunity. On cheap shared hosting, WordPress can feel slow. On purpose-built managed hosting, it can be blazing fast.
A membership site is a dynamic, logged-in workload. Every page load hits the database. Every course progress check, every community interaction, every payment verification requires server-side processing. Generic hosting struggles with this. [Hosting built for dynamic WordPress workloads](/memberpress-hosting/), with object caching, fast databases, and auto-scaling PHP workers, handles it effortlessly.
This is worth factoring into your total cost of ownership. The combination of MemberPress plus quality hosting isn't just cheaper than Kajabi. It can also be significantly faster, because you're choosing infrastructure optimized for exactly how membership sites work.
For a deeper look at what to prioritize in hosting for MemberPress specifically, check out our [MemberPress hosting guide](/blog/best-hosting-for-memberpress/)
## Who Should Choose Which?
It comes down to how much you value ownership and feature depth versus all-in-one simplicity.
| Choose MemberPress if you... | Choose Kajabi if you... |
|---|---|
| Want full ownership of your business, data, and content | Want maximum simplicity with zero technical setup |
| Need advanced LMS features (graded assignments, certifications, gradebook) | Need built-in email marketing and don't want to manage a separate tool |
| Run coaching programs and need dedicated management tools | Are validating a new business idea quickly and prioritize speed over flexibility |
| Already use WordPress or plan to | Prefer a single monthly bill over managing multiple services |
| Care about long-term cost efficiency | Don't mind platform dependency and are comfortable with Kajabi's pricing trajectory |
| Want the flexibility to integrate best-in-class tools for email, CRM, and analytics | |
| Are building a business you intend to own for years, not rent month to month | |
## Wrapping Up
MemberPress and Kajabi solve the same core problem from opposite directions. Kajabi bundles everything together and charges a premium for the convenience. MemberPress gives you deeper features, full ownership, and dramatically lower costs, in exchange for a bit more setup and the responsibility of choosing your own hosting.
For creators and membership site owners who think in terms of years, not months, MemberPress on WordPress is the stronger foundation. You keep more revenue, own all your data, and never worry about a platform pulling the rug out from under your business.
The hosting piece is what ties it all together. A membership site with hundreds or thousands of logged-in users needs infrastructure that can keep up. Choose hosting that's built for dynamic WordPress workloads, and you get the best of both worlds: the flexibility of MemberPress with the performance your members expect.
If you want to see how that feels in practice, try building your membership on [hosting that was designed for exactly this kind of site](/pricing/).
---
## Best Hosting for TutorLMS: What Your Course Platform Actually Needs
- URL: https://levamo.com/blog/best-hosting-for-tutorlms/
- Category: lms
- Author: Shahzeb Ahmed
- Published: 2026-08-26
What TutorLMS needs from hosting to survive quizzes, cohorts, and scale.
You picked TutorLMS. You built your courses, configured your quizzes, set up drip schedules, and launched your first cohort.
Then 40 students start a timed quiz at the same time, and everything falls apart.
Quiz submissions time out. Progress bars freeze. Students refresh the page and lose their answers. Your support inbox fills up with panicked emails from learners who think they failed because the site crashed.
Here's what nobody tells you when you're choosing a WordPress LMS plugin: TutorLMS (and every serious LMS) is one of the most resource-intensive workloads you can run on WordPress. And the hosting that worked fine for your blog or landing page will absolutely buckle under the weight of a live course platform.
Your learners deserve better. Let's break down what TutorLMS actually needs from a host and what to look for when you're evaluating options.
## Why Course Sites Can't Survive on Generic Hosting
A standard WordPress site serves the same cached page to every visitor. Your server generates the HTML once, stores it, and hands out copies. Cheap, fast, efficient.
TutorLMS throws that model out the window.
When a student loads a lesson page, your server has to:
Authenticate the student's session and enrollment status
Check content drip rules to decide whether this lesson is unlocked yet
Pull their individual progress data (completed lessons, quiz scores, certificates earned)
Verify prerequisite completion before granting access to advanced modules
Render a personalized page that's completely different from what every other student sees
That's a database query storm on every single page load. And unlike a blog post that gets cached once and served a million times, each student's request generates a unique response.
Now multiply that by 50 students navigating lessons simultaneously. Or 100 students submitting quiz answers during a live cohort session. Each of those requests requires a PHP worker, a database connection, and server memory. Generic hosting runs out of all three.
## The Caching Paradox That Breaks LMS Sites
This is the trap most course creators fall into.
Your site feels slow, so you install a caching plugin. Pages load faster for logged-out visitors. You think the problem is solved.
Then a student reports that they completed a lesson but it still shows as locked. Another student sees someone else's quiz results. A third student can't access a course they paid for because the cached page doesn't reflect their enrollment.
Page caching and LMS platforms are fundamentally incompatible for logged-in users. Caching serves stored HTML without running the enrollment checks, progress tracking, and access control logic that TutorLMS depends on. When your caching plugin serves Student A a page generated for Student B, you don't just have a performance problem. You have a broken product.
The solution isn't to disable caching entirely (that makes your site crawl). The solution is the right kind of caching at the right layer. More on that in a moment.
## What Your TutorLMS Site Actually Needs From Hosting
Not every "managed WordPress host" can handle LMS workloads. Here's the checklist that actually matters for running TutorLMS without headaches.
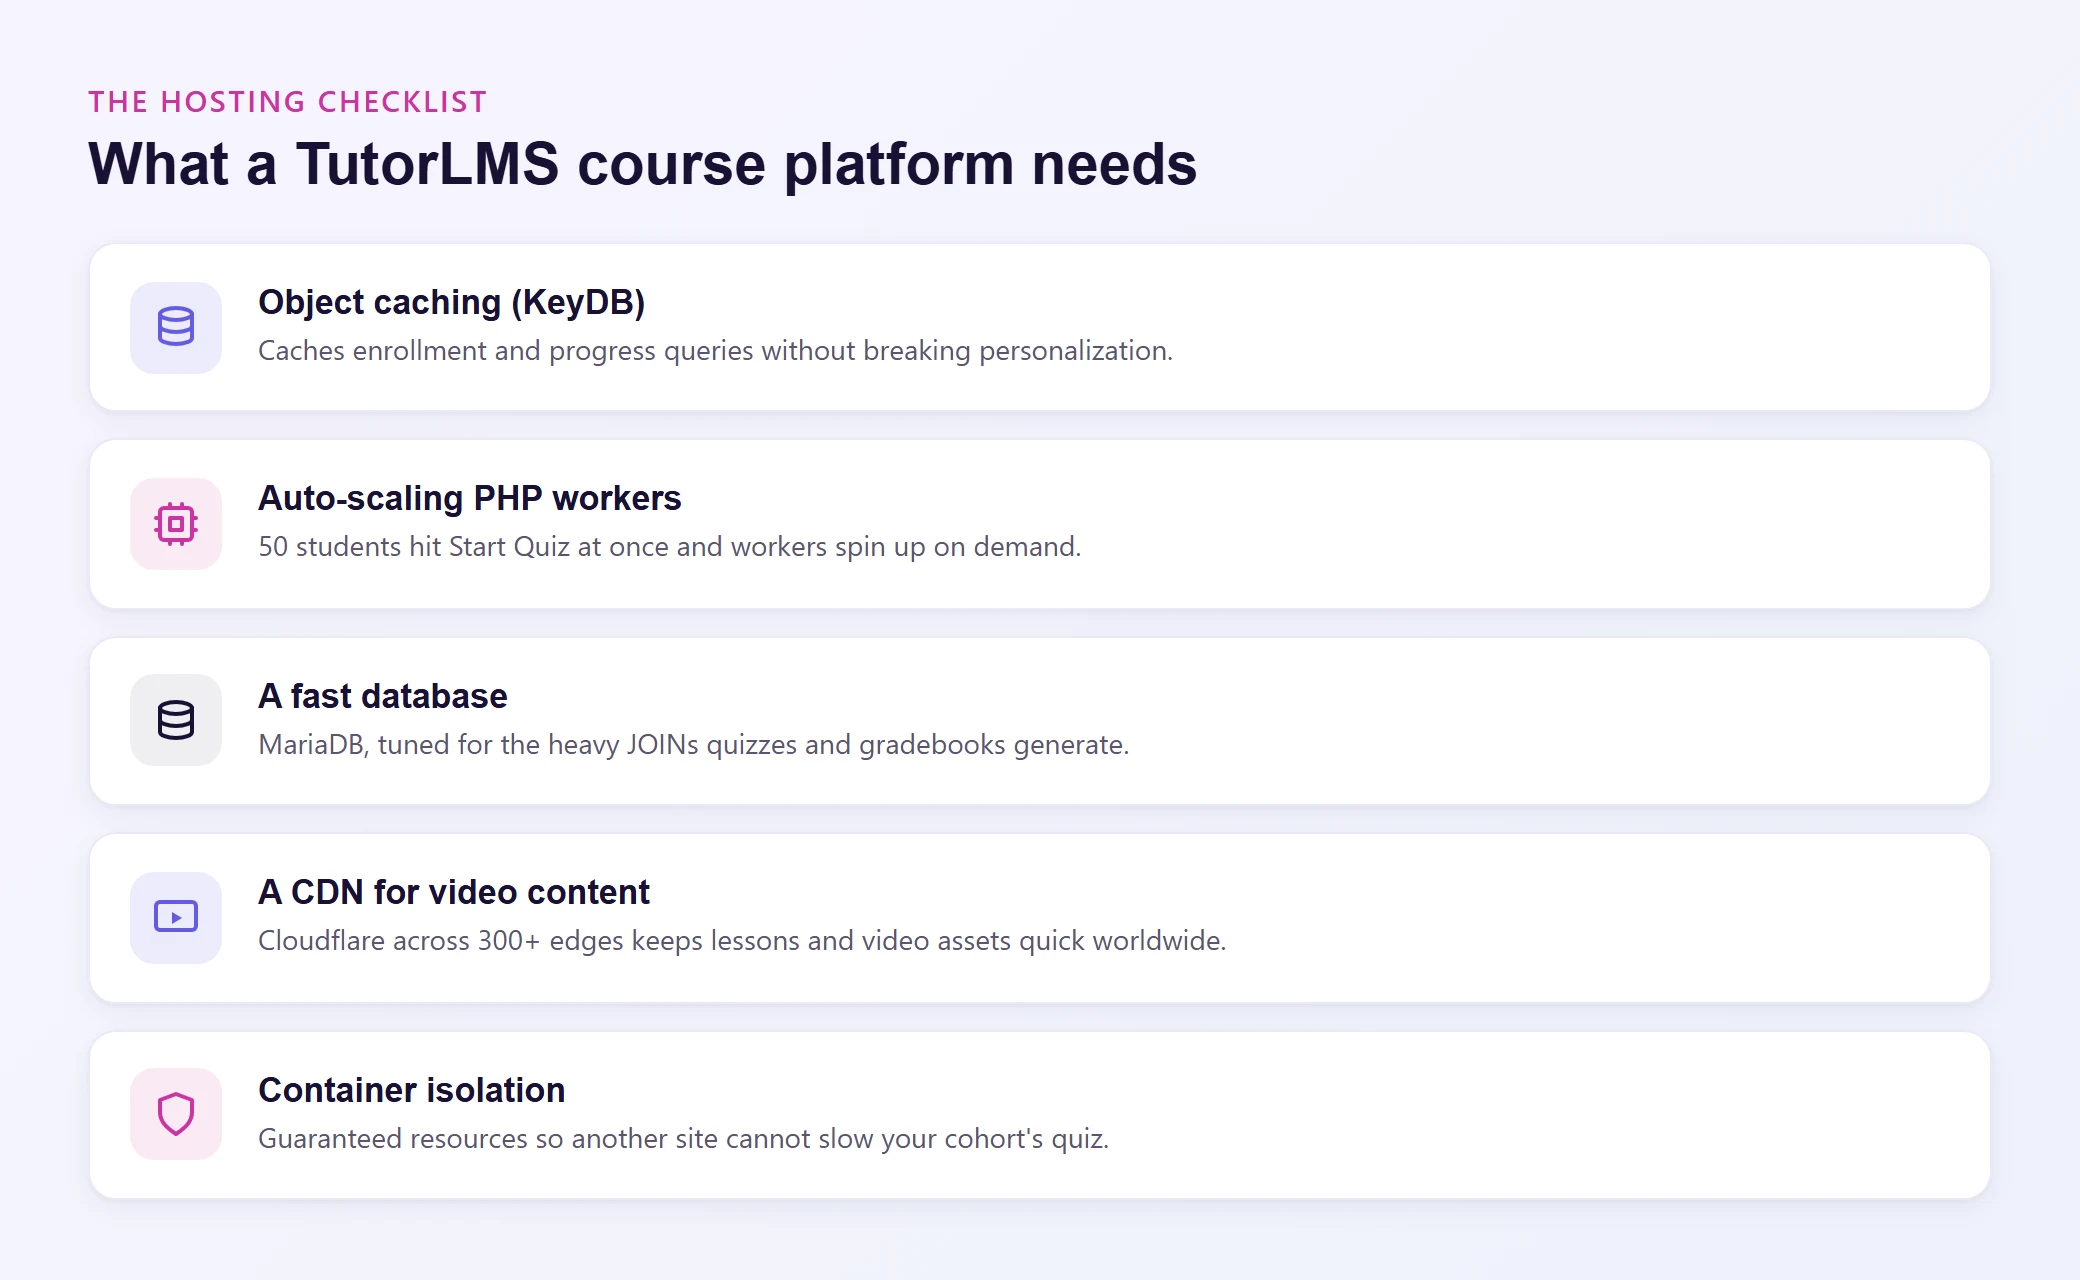
### Object Caching (The Right Kind of Caching)
Object caching works at the database query level, not the page level. Instead of caching entire HTML pages (which breaks personalized content), it caches the results of individual database queries in memory.
When TutorLMS checks whether Student A has completed Lesson 3, that query hits the database the first time. Object caching stores the result in RAM. The next time the same query runs, the answer comes from memory in microseconds instead of milliseconds from the database.
This is transformative for LMS workloads because the same types of queries run thousands of times per hour: enrollment checks, progress lookups, prerequisite validations, quiz score retrievals. Object caching intercepts all of them without breaking any of TutorLMS's personalization logic.
But here's the nuance most hosts miss. Standard Redis is single-threaded. It processes one cache request at a time. When 60 students are active simultaneously and each generating dozens of cached queries per page load, single-threaded caching becomes a bottleneck.
KeyDB fixes this. It's a multithreaded fork of Redis that handles concurrent requests in parallel instead of queuing them. For a TutorLMS site with active learners, this is the difference between a responsive course platform and one that slows down in proportion to enrollment.
Levamo includes KeyDB + Redis object caching on Business plans and above, specifically because LMS and membership workloads demand it.
### PHP Workers That Scale With Your Cohorts
Every dynamic page request on your TutorLMS site requires a PHP worker to process it. Quiz submissions, lesson completions, certificate generation, grade calculations: each one occupies a worker until it's done.
Here's where course sites get hit hardest. When a cohort of 50 students starts a quiz simultaneously, you need 50 PHP workers available right now, not in 30 seconds after the server notices the spike.
Hosts that share PHP workers across multiple sites on the same server are a recipe for timeout errors during exactly the moments that matter most: live assessments, enrollment surges, and course launch days.
Look for hosting with dedicated, auto-scaling PHP workers. When your cohort hits "Start Quiz" at the same time, your server should spin up additional workers on demand instead of queuing requests until students start seeing 504 errors.
### A Database That Can Handle Complex Queries
TutorLMS is database-heavy. Course structures, lesson progress, quiz attempts, gradebook entries, certificate records, enrollment statuses: all of it lives in your database. And TutorLMS doesn't just run simple lookups. It runs complex JOIN queries that pull data from multiple tables simultaneously.
Quiz-attempt data, for instance, can involve a single query that takes over 1.5 seconds to run. On a shared database server competing with other sites, that delay compounds rapidly.
MariaDB handles these query patterns more efficiently than older MySQL setups. Its query optimizer is specifically better at the multi-table JOINs that LMS plugins generate constantly. When paired with object caching, your database only needs to execute each expensive query once before the result is cached in memory.
### CDN for Video-Heavy Course Content
Most online courses involve video. Whether you're embedding from YouTube/Vimeo or (more ambitiously) self-hosting your course videos, a CDN is non-negotiable.
For embedded video, your CDN handles the surrounding page assets: your theme CSS, JavaScript, images, thumbnails, and downloadable resources. Fast delivery of these assets means the page loads quickly and the embedded player appears immediately.
For self-hosted video, a CDN with global edge locations is the difference between smooth playback and constant buffering. A student in Singapore watching a course hosted on a US server without a CDN is going to have a miserable experience.
Enterprise Cloudflare CDN also handles DDoS protection, bot filtering, and SSL termination at the edge, which matters for course sites that handle payments and student data. Levamo includes [Enterprise Cloudflare CDN](/cloudflare-cdn/) across 300+ locations on every plan, not as an add-on.
### Container Isolation (Your Resources Stay Yours)
Shared hosting means shared resources. If another site on your server gets a traffic spike, your TutorLMS site slows down through no fault of your own.
For a course platform, this is unacceptable. Imagine running a live cohort quiz while another site on your shared server gets hit by a bot crawl. Your students experience timeouts because someone else's traffic consumed the resources your quizzes needed.
Container isolation gives your site its own walled-off environment with guaranteed CPU, memory, and I/O. Your course platform performs consistently regardless of what's happening elsewhere on the server.
## How Levamo Handles TutorLMS Workloads
Levamo was built by the co-founders of [BuddyBoss](/buddyboss-hosting/), the most widely used community and LMS platform in the WordPress space. That origin shaped the entire hosting stack: it wasn't designed for blogs and retrofitted for dynamic workloads. It was built from the ground up for logged-in, database-heavy applications like course platforms.
Here's the infrastructure that makes a measurable difference for TutorLMS:
Those benchmarks matter most for TutorLMS sites where every request triggers real database work, not just static file delivery.
If you're building on TutorLMS and want an overview of how it compares to other LMS options, check out our guide to the [best WordPress LMS plugins](/blog/best-wordpress-lms-plugins/). And if you're just getting started with TutorLMS setup, our [complete build guide](/blog/build-lms-website-with-tutor-lms/) walks through the process step by step.
### Support That Understands LMS Workloads
Here's something you won't find on a comparison chart. When you contact Levamo support, you're talking to a team that works with LMS and membership sites daily. They understand plugin conflicts between TutorLMS and caching setups, database optimization for quiz-heavy sites, and the server-level tuning that course platforms need.
That's a 24/7/365 team with a 4.6/5 CSAT rating and sub-minute live chat response times. For course creators who aren't server administrators (and don't want to be), this is often the reason they stay.
## Migrating Your Course Site (Without Losing Student Data)
Switching hosts when you have active students feels risky. Enrollments, quiz progress, completion records, certificates: there's a lot of data that absolutely cannot get lost or corrupted in transit.
Levamo's White Glove Migration handles the entire process:
Their team assesses your current TutorLMS setup (plugins, database size, custom configurations, video storage)
They migrate everything to a temporary URL for you to test
You verify that course content, student progress, enrollments, and quiz data all transferred correctly
Once confirmed, they cut over with minimal downtime
It's free on all plans, completed within 48 business hours, and you don't have to touch a terminal or worry about breaking student records.
## Plans That Scale With Your Course Business
A solo creator selling one course has different needs than an academy running 30 courses with 5,000 enrolled students. Your hosting should scale with you.
| Feature | Starter ($29/mo) | Business ($99/mo) | Performance ($299/mo) |
|---|---|---|---|
| PHP Workers | Dedicated | Dedicated + auto-scaling | Dedicated + auto-scaling |
| Object Caching | Basic | KeyDB + Redis | KeyDB + Redis |
| CDN | Enterprise Cloudflare | Enterprise Cloudflare | Enterprise Cloudflare |
| Search | WordPress default | WordPress default | ElasticPress |
| Backups | Daily | Daily | Daily |
| Support | 24/7 live chat | 24/7 live chat | 24/7 live chat |
Most TutorLMS course sites should start on the **Business plan**. Object caching is essential as soon as you have concurrent learners actively navigating lessons and taking quizzes. The Starter plan works for building and testing your courses before launch, but once you have paying students, KeyDB + Redis object caching becomes the single biggest performance upgrade you can make.
If your academy grows to thousands of students and you need fast course/lesson search, the Performance plan adds ElasticPress, which offloads search to a dedicated engine and dramatically improves catalog browsing and content discovery.
Every plan includes a [3-day free trial](/pricing/) and a 14-day money-back guarantee. Migrate your TutorLMS site over, run your own tests, and see the difference before you commit.
## Wrapping Up
TutorLMS is a powerful course platform, but it's also one of the most demanding workloads you can put on WordPress. Every logged-in student generates personalized, database-heavy requests that generic hosting simply wasn't built to handle. The right hosting stack (server-level object caching, dedicated PHP workers, a fast database engine, and real container isolation) turns a sluggish course site into one where quizzes submit instantly, lessons load without lag, and your students focus on learning instead of fighting your infrastructure.
Your students don't care about server specs. They care that the quiz doesn't time out, the video doesn't buffer, and their progress actually saves. The hosting you choose determines whether that happens.
---
## Membership Site Pricing Strategies: How to Price Your Membership Site in 2026
- URL: https://levamo.com/blog/membership-site-pricing-strategies/
- Category: membership
- Author: Shahzeb Ahmed
- Published: 2026-08-25
Five membership pricing models plus how to set the right price for your site.
You built the content. You picked the membership plugin. You even got the design looking sharp. Then you hit the pricing page and froze.
How much should you charge? Is $9/month too cheap? Is $49/month too ambitious? Should you offer a free tier or will that cannibalize your paid members? What about annual billing?
Pricing is the single highest-leverage decision you will make for your membership site. Get it right, and you build a sustainable business that grows with every new member. Get it wrong and you either leave money on the table or scare people away before they ever see what you have to offer.
The good news: you do not have to guess. There are proven pricing models, practical frameworks, and real patterns from successful membership sites that can guide your decision. This guide walks you through all of them.
## The Five Membership Pricing Models
Before you set a dollar amount, you need to choose a structure. Each model works differently depending on your content type, audience, and growth stage.
### 1. Flat-Rate (Single Tier)
One price, one membership level, full access to everything.
This is the simplest model and the easiest to sell. Members pay a fixed monthly or annual fee and get access to your entire content library. No feature comparisons, no "which plan is right for me" confusion.
**Best for:** Communities, mastermind groups, niche content libraries where all members get roughly equal value.
**Example:** A fitness coaching community charges $29/month for access to workout plans, live Q&As, and a private forum. Every member gets the same thing.
**Pros:**
- Dead simple to communicate
- No decision fatigue for potential members
- Easy to manage operationally
**Cons:**
- Leaves revenue on the table from members who would pay more
- No upsell path once someone joins
### 2. Tiered Pricing (Good / Better / Best)
Multiple membership levels at different price points, each with increasing access or perks.
This is the most popular model for a reason. It lets you capture different segments of your audience at price points that match what they are willing to pay. The entry tier gets hesitant buyers through the door. The premium tier captures maximum value from your most engaged members.
**Best for:** Course platforms, professional communities, and any site where you can meaningfully differentiate between access levels.
**Example:** An online education platform offers three tiers:
- **Basic ($19/month):** Access to the course library
- **Pro ($49/month):** Courses plus live workshops and community forum
- **VIP ($99/month):** Everything plus monthly 1-on-1 coaching calls
**Pros:**
- Captures more revenue across different willingness-to-pay segments
- Creates a natural upgrade path
- The middle tier benefits from the anchoring effect (it looks like a great deal next to the premium tier)
**Cons:**
- More complex to set up and communicate
- Requires enough content or features to justify multiple levels
Most membership plugins like [MemberPress](/memberpress-hosting/) and Restrict Content Pro handle tiered pricing natively, so the technical setup is straightforward.
### 3. Freemium (Free Tier + Paid)
A free membership level with limited access, designed to convert members to a paid tier over time.
The freemium model works as a funnel. Free members get a taste of your content (maybe a few introductory lessons, limited community access, or a content preview). Once they see the value, a percentage converts to paid.
**Best for:** Sites with a large potential audience where the free tier serves as a marketing channel. Particularly effective for course platforms and content libraries.
**Example:** A marketing education site offers free access to 10 foundational lessons. Paid members ($39/month) unlock the full 200+ lesson library, templates, and community.
**Pros:**
- Lowers the barrier to entry dramatically
- Builds a large email list and engaged audience
- Free members become your best salespeople (word of mouth)
**Cons:**
- Low conversion rates (typically 2% to 5% of free members convert)
- Free members still consume server resources and support bandwidth
- Risk of devaluing your paid content if the free tier is too generous
The key to freemium: your free content must be genuinely useful on its own, but it should also make the paid tier feel essential. If the free tier is too thin, nobody sticks around. If it is too generous, nobody upgrades.
### 4. Pay-Per-Content (À La Carte)
Members pay for individual pieces of content rather than a recurring subscription.
This model works when your content is highly specialized and members only need specific pieces. Think: downloadable templates, individual course modules, premium research reports, or standalone workshops.
**Best for:** Resource libraries, template shops, and educational content where members want specific items rather than ongoing access.
**Example:** A design resource site sells individual template packs at $15 to $45 each. Members can also subscribe for $29/month to get unlimited downloads.
**Pros:**
- Low commitment for buyers (no recurring charge anxiety)
- High perceived value for premium individual items
**Cons:**
- Less predictable revenue compared to subscriptions
- Harder to build community and long-term engagement
- Every sale requires a new purchase decision
Many sites combine this with a subscription option: buy items individually or subscribe for unlimited access. This hybrid approach captures both audiences.
### 5. Cohort-Based (Time-Limited Access)
Members join in batches with a defined start and end date. Think bootcamps, group coaching programs, or seasonal courses.
**Best for:** Live programs, group coaching, certification courses, and any content that benefits from a shared learning experience.
**Example:** A business coaching program runs 8-week cohorts four times a year at $497 per cohort. Each group goes through the material together with live sessions, accountability partners, and group discussions.
**Pros:**
- Creates urgency and scarcity (enrollment windows)
- Higher price points are easier to justify
- Strong community bonding within cohorts
- Predictable workload for you as the creator
**Cons:**
- Revenue comes in bursts rather than steady monthly flow
- Requires active facilitation during each cohort
- Empty seats in a cohort feel like lost revenue
## How to Figure Out Your Actual Price Point
Choosing a model is step one. Now you need a number. Here is a practical framework.
### Start With Value, Not Cost
The biggest pricing mistake membership site owners make is anchoring to their costs. They think: "My hosting is $99/month, my plugin licenses cost $300/year, I spend 10 hours a week creating content, so I need to charge at least $X to break even."
That math matters for your business plan, but it should not determine your price. Your members do not care what it costs you to run the site. They care what they get out of it.
Value-based pricing asks a different question: **what is this membership worth to your members?**
If your membership teaches freelancers how to land higher-paying clients and the average member raises their rates by $500/month after joining, a $49/month membership is a steal. If your membership provides workout plans that replace a $120/month personal trainer, $29/month feels like a bargain.
Frame your price relative to the outcome or alternative, not your expenses.
### Research Your Niche
Look at what existing membership sites in your space charge. You do not need to match their pricing, but you need to understand the range your audience considers normal.
- Search for membership sites in your niche and note their pricing
- Check online course platforms for comparable offerings
- Browse community platforms (paid Slack groups, Discord servers, Circle communities) for reference points
- Read reviews and complaints about competitor offerings. Pricing objections tell you where the ceiling is
### Use the 10x Rule as a Gut Check
A widely used heuristic in subscription pricing: your membership should deliver at least 10 times its cost in perceived value. If you charge $30/month, members should feel like they are getting $300/month worth of content, community, or outcomes.
This does not mean you need $300 worth of "stuff." Value is subjective. A single piece of advice that saves someone 5 hours of work or prevents a costly mistake can easily be worth $300 to the right person.
### Price for Your First 100 Members, Not Your First 10,000
New membership site owners often underprice because they are thinking about volume. "If I charge $9/month and get 10,000 members, that is $90,000/month!"
The problem: getting to 10,000 members at $9/month is brutally hard. You need massive traffic, high conversion rates, and very low churn. Meanwhile, getting 500 members at $49/month produces the same revenue with a smaller, more engaged community that is easier to serve.
Higher prices also tend to attract more committed members who show up, participate, and stick around. Lower prices attract more casual buyers who sign up, forget about it, and cancel after three months.
## Annual vs. Monthly Billing: The Math That Matters
Offering both annual and monthly billing is almost always the right move. Here is why.
**Monthly billing** is lower friction. It gets more people through the door because the commitment feels small. A $29 monthly charge is psychologically easier than a $290 annual charge, even if the annual option saves them money.
**Annual billing** is better for your business. It reduces churn (members who pay annually are far less likely to cancel mid-year), improves cash flow (you get 12 months of revenue upfront), and gives you a more predictable revenue base.
The standard approach: price your annual plan at a 15% to 20% discount compared to 12 months of the monthly rate.
- If monthly is $29/month ($348/year), offer annual at $279/year (20% off)
- If monthly is $49/month ($588/year), offer annual at $499/year (15% off)
Present the annual option as the default or recommended choice on your pricing page. Show the monthly cost of the annual plan ("just $23/month, billed annually") to make the comparison obvious.
Some membership sites go further and offer annual-only billing. This works when your content has a natural yearly cycle (like a certification program or seasonal content), but it does limit your addressable audience.
## Free Trials, Discounts, and Getting Members to "Yes"
### Free Trials
A free trial lets potential members experience your content before committing. It works well for membership sites because the value of a community or content library is hard to communicate on a sales page. People need to experience it.
**Keep trials short.** Three to seven days is the sweet spot. Longer trials give people time to extract value without paying, and they train your audience to wait for free access. Shorter trials create urgency to explore and decide.
**Require a credit card upfront.** This is controversial, but the data is clear: trials that require payment information convert at significantly higher rates than those that do not. You will get fewer trial signups, but the ones you get are more serious.
### Launch Discounts
If you are launching a new membership site, a founding member discount can build your initial member base quickly. Offer the first 50 or 100 members a locked-in rate (e.g., 30% off for life) in exchange for joining early and providing feedback.
This works because:
- It creates urgency (limited spots at the discounted rate)
- Founding members become your most loyal advocates
- Their feedback shapes the membership before you scale
**Do not run perpetual discounts.** If your "special offer" never expires, it is not special. It is your real price. Use discounts strategically and sparingly.
### Money-Back Guarantees
A 14-day or 30-day money-back guarantee reduces purchase anxiety without the operational overhead of a free trial. Members pay upfront, get full access, and can request a refund if it is not for them.
This is often simpler to manage than a trial system and works particularly well for higher-priced memberships where the financial commitment feels significant.
## When and How to Raise Your Prices
Your first price will not be your forever price. As your content library grows, your community matures, and your brand reputation builds, your membership becomes more valuable. Your pricing should reflect that.
### Signs It Is Time for a Price Increase
- Your content library has grown significantly since launch
- Member satisfaction and retention rates are strong
- You have a waitlist or consistently hit capacity
- You have not raised prices in over a year
- New members tell you the membership is "a steal" or "underpriced"
### How to Handle the Increase
**Grandfather existing members.** The most common (and fairest) approach is to keep current members at their existing rate and apply the new pricing to new signups only. This rewards loyalty, avoids backlash, and gives you a natural upsell opportunity later.
**Give advance notice.** If you do raise prices for existing members, give them 30 to 60 days notice and explain why. "We have added 50 new courses, weekly live workshops, and a mentorship program since you joined" is a reason people can accept. "We need more revenue" is not.
**Use price increases to drive annual conversions.** "Lock in your current rate for the next year by switching to annual billing before the price increase takes effect." This simultaneously raises prices and improves your billing mix.
## Common Pricing Mistakes (And How to Avoid Them)
**Pricing too low out of fear.** Underpricing signals low value. If your membership costs less than a large coffee per week, potential members will unconsciously assume the content matches that price point. Charge what your content is worth.
**Too many tiers.** Three tiers is the sweet spot. Four might work. Five or more creates decision paralysis and makes your pricing page feel like a spreadsheet. If you cannot explain the difference between tiers in one sentence each, you have too many.
**Hiding your prices.** "Contact us for pricing" works for enterprise software. It does not work for membership sites. Your audience expects to see prices on the page. Hiding them adds friction and signals that the price will be uncomfortably high.
**Ignoring the hosting math.** As your membership grows, your server costs change. A site with 50 members has different hosting needs than one with 5,000 concurrent logged-in users. When you are building your membership site, choose hosting that scales with you. A plan that handles 100 members today should have an upgrade path for 10,000 members tomorrow, without requiring a full migration to a different provider.
**Never revisiting your pricing.** Your first price is a hypothesis, not a commitment. Review your pricing at least twice a year. Look at churn rates by price point, survey members about perceived value, and adjust.
## Matching Your Hosting to Your Growth Stage
Your membership pricing strategy and your hosting plan should grow in lockstep. Here is a practical way to think about it.
**Early stage (0 to 500 members):** You are validating your concept and building your content library. You need reliable hosting with good performance, but you do not need enterprise-level resources yet. A [managed WordPress plan](/managed-wordpress-hosting/) in the $29 to $99/month range covers this. Focus your budget on content creation and marketing, not infrastructure.
**Growth stage (500 to 5,000 members):** Your site now handles significant concurrent logged-in traffic. Page caching cannot help here because every member sees personalized content. You need object caching (Redis or KeyDB) to keep database queries fast, auto-scaling PHP workers to handle traffic spikes, and a [CDN](/cloudflare-cdn/) to serve static assets globally.
**Scale stage (5,000+ members):** At this level, database performance becomes critical. You need dedicated resources, advanced search (ElasticSearch for fast member directories and content search), and hosting support that understands membership workloads. Your hosting cost is now a small fraction of your revenue, so optimize for reliability and speed rather than the lowest price.
The point is not to over-invest in hosting before you have the members to justify it. Start lean, upgrade as revenue grows, and make sure your hosting provider offers a [clear upgrade path](/pricing/) so you never have to do a painful migration mid-growth.
## Wrapping Up
Pricing your membership site is not a one-time decision. It is an ongoing process that evolves as your content grows, your audience matures, and you learn what your members actually value. Start with a model that fits your content type, set a price based on the value you deliver (not your costs), and plan to revisit your pricing every six months.
The most important thing? Pick a price and launch. You can always adjust later. But you cannot optimize a membership site that does not exist yet.
---
## Best Hosting for BuddyPress Communities in 2026: What Your Community Actually Needs
- URL: https://levamo.com/blog/best-hosting-for-buddypress/
- Category: membership
- Author: Shahzeb Ahmed
- Published: 2026-08-24
What BuddyPress communities need from hosting to stay fast as members grow.
You built a community with BuddyPress. Members are joining, conversations are flowing, and your activity feed is finally alive.
Then you hit 150 active members, and everything slows to a crawl.
Pages take four seconds to load. The member directory times out. Activity feeds lag behind real-time by minutes. Members stop posting, stop logging in, and quietly disappear.
Here's the thing: this isn't a BuddyPress problem. It's a hosting problem.
Most WordPress hosts are optimized for one thing: serving static blog pages to anonymous visitors. That's the exact opposite of what a BuddyPress community does. Every page load for a logged-in member is dynamic. Every profile view, every activity update, every friend request hits your database and generates a fresh response.
Your community deserves hosting that was actually built for this workload. Let's break down what that looks like.
## Why BuddyPress Communities Can't Run on Generic Hosting
A typical WordPress blog serves the same cached HTML to every visitor. A hosting provider can serve thousands of those requests per second without breaking a sweat, because the server barely has to think.
BuddyPress flips that model on its head.
When a member loads their activity feed, your server has to:
Authenticate the user's session
Query the database for activity items from their friends, groups, and followed members
Check permissions on every item (who can see what)
Render a personalized page that's different from what every other member sees
Multiply that by 50, 100, or 500 concurrent members, and you start to see why generic hosting buckles. Page caching? Useless here. You can't serve Member A a cached copy of Member B's personalized feed.
This is why [community-focused hosting](/buddypress-hosting/) exists as a category. The workload is fundamentally different from that of any blog or brochure site.
## What Your BuddyPress Site Actually Needs From Hosting
Not every "managed WordPress host" is equipped for community workloads. Here's the checklist that actually matters.
### Object Caching That Can Handle Concurrency
Object caching stores the results of expensive database queries in memory (RAM), so the next time that query runs, your server grabs the answer instantly instead of hitting the database again.
For a BuddyPress site, this is transformative. Member directories, group lists, activity feeds, and permission checks all involve repetitive queries that object caching can intercept.
But there's a catch. Standard Redis is single-threaded. When 80 members are active simultaneously and all generating database queries, a single-threaded cache becomes a bottleneck itself.
KeyDB solves this. It's a multithreaded fork of Redis that handles concurrent requests without queuing them up. For a BuddyPress community with active, logged-in members, multithreaded object caching isn't a nice-to-have. It's the difference between a responsive community and one that feels sluggish during peak hours.
Levamo includes KeyDB + Redis object caching on Business plans and above, specifically because community and membership workloads demand it.
### Dedicated PHP Workers
Every dynamic page request on your BuddyPress site requires a PHP worker to process it. If your host gives you a shared pool of workers across multiple sites, a traffic spike on someone else's site can starve yours.
Look for hosting that provides dedicated, auto-scaling PHP workers. When your community hosts a live event or a popular discussion thread takes off, your server should spin up additional workers to handle the load, not queue requests until members start seeing timeout errors.
### A Database Layer Built for Speed
BuddyPress is database-heavy. Activity streams, member relationships, group memberships, private messages: all of it lives in your database. The difference between MariaDB and older MySQL setups is measurable, especially for the complex JOIN queries that BuddyPress generates.
MariaDB's query optimizer handles these patterns more efficiently, and when paired with object caching, your database only needs to run each expensive query once before the result gets cached.
### CDN That Actually Helps Dynamic Sites
Most CDNs cache static files: images, CSS, JavaScript. That's helpful, but it only addresses a fraction of a BuddyPress site's performance needs.
An enterprise-grade CDN like Cloudflare's does more. It handles DDoS protection, bot filtering, SSL termination, and edge-level security headers. For a community site where members upload profile photos, share files, and interact with media-rich activity feeds, having 300+ edge locations serving your static assets while protecting your origin server makes a real difference.
Levamo includes [Enterprise Cloudflare CDN](/cloudflare-cdn/) on every plan, not as an upsell.
### Container Isolation
Shared hosting means shared resources. If another site on your server gets a traffic spike (or worse, gets hacked and starts consuming resources), your community slows down.
Container isolation gives each site its own walled-off environment with guaranteed resources. Your BuddyPress community's performance stays consistent regardless of what's happening elsewhere on the server.
## How Levamo Handles BuddyPress Workloads
Levamo was built by the co-founders of [BuddyBoss](/buddyboss-hosting/), the most widely used BuddyPress-based platform. That's not a marketing partnership. The people who built the platform also built the hosting to run it.
That origin story matters because it shaped the entire infrastructure. The stack wasn't designed for blogs and then retrofitted for communities. It was built from the ground up for logged-in, dynamic, database-heavy workloads.
Here's what's under the hood:
**LiteSpeed web server** with built-in page caching for the parts of your site that can be cached (public pages, login screens, static content)
**KeyDB + Redis object caching** (Business plans and up) for the dynamic, per-user queries that dominate BuddyPress traffic
**MariaDB** tuned for the complex query patterns community plugins generate
**Auto-scaling PHP workers** that respond to demand spikes instead of queuing requests
**Container isolation** so your resources are always yours
**Enterprise Cloudflare CDN** across 300+ locations on every plan
**Monarx malware scanning** at the server level, plus Cloudflare WAF and DDoS protection
The benchmarks back it up: 9.3 on WP Benchmark, 2,958 queries per second, and 353 requests per second under load testing. Those numbers matter most for sites like yours where every request triggers real database work.
### Support That Knows Your Stack
Here's something that doesn't show up in spec sheets. When you contact Levamo support, you're talking to people who work with BuddyPress and BuddyBoss sites daily. They understand activity feed optimization, group query performance, and the specific plugin conflicts that community sites run into.
That's a 24/7/365 team with a 4.6/5 CSAT rating and sub-minute live chat response times. For non-technical community operators who need server-level help, this is often the deciding factor.
## Migrating Your Community (Without Downtime)
Switching hosts feels risky when you have an active community. Members are posting, sending messages, and interacting in real time. You can't just flip a switch and hope nothing breaks.
Levamo's White Glove Migration handles the entire process for you:
Their team assesses your current setup (plugins, database size, custom configurations)
They migrate everything to a temporary URL for you to test
Once you confirm everything works, they cut over with minimal downtime
It's free on all plans, completed within 48 business hours, and you don't have to touch a terminal. For community operators who aren't server admins (and don't want to be), this removes the single biggest barrier to switching.
## Plans That Scale With Your Community
A community with 50 members has different needs than one with 5,000. Your hosting should reflect that.
| Feature | Starter ($29/mo) | Business ($99/mo) | Performance ($299/mo) |
|---|---|---|---|
| PHP Workers | Dedicated | Dedicated + auto-scaling | Dedicated + auto-scaling |
| Object Caching | Basic | KeyDB + Redis | KeyDB + Redis |
| CDN | Enterprise Cloudflare | Enterprise Cloudflare | Enterprise Cloudflare |
| Search | WordPress default | WordPress default | ElasticPress |
| Backups | Daily | Daily | Daily |
| Support | 24/7 live chat | 24/7 live chat | 24/7 live chat |
Most BuddyPress communities start on the **Business plan** because object caching is essential once you pass ~100 active members. If your community grows to thousands of members with heavy search usage (member directories, forum searches, content filtering), the Performance plan adds ElasticPress for offloaded, lightning-fast search.
Every plan includes a [3-day free trial](/pricing/) and a 14-day money-back guarantee. Test your actual community on the infrastructure before committing.
## Wrapping Up
BuddyPress communities are some of the most demanding WordPress workloads out there. Every logged-in member generates dynamic, personalized, database-heavy requests that generic hosting simply wasn't designed to handle.
The right hosting stack (object caching, dedicated PHP workers, a fast database, and real container isolation) transforms a sluggish community into one where members actually want to spend time. And when your hosting provider was literally built by the people who created the leading BuddyPress platform, you're getting infrastructure that understands your workload at a foundational level.
Your community members don't care about server specs. They care that the activity feed loads instantly, profiles don't time out, and notifications arrive in real time. The hosting you choose determines whether that happens.
---
## What's New in WordPress 7.1: Features, Screenshots, and What It Means for Your Site
- URL: https://levamo.com/blog/wordpress-7-1/
- Category: wordpress
- Author: Shahzeb Ahmed
- Published: 2026-08-21
WordPress 7.1 adds responsive styling, client-side image uploads, and new blocks.
WordPress 7.1 dropped on August 19, 2026, officially released at WordCamp US. It's one of the meatier updates in recent memory, packing responsive styling, browser-based image processing, two new core blocks, and a redesigned image editor into a single release.
Whether you're running a [WooCommerce store](/managed-woocommerce-hosting/), managing a [membership community](/memberpress-hosting/), or building out a [course platform](/hosting-for-lms/), there's something in this update that directly affects how you work. Here's everything worth knowing.
## Responsive Styling Without Writing a Line of CSS
This might be the single most useful feature in WordPress 7.1 for anyone building pages in the Site Editor.
Before this update, making a heading 48px on desktop but 28px on mobile meant either writing custom CSS or relying on a page builder plugin. WordPress now handles it natively.
The Site Editor includes device preview toggles for desktop, tablet, and mobile. Switch to the mobile view, adjust your font sizes, spacing, or layout, and WordPress generates the responsive CSS automatically. You can also drag the canvas edges to create custom breakpoints, which is great for fine-tuning how content looks between standard device widths.
Your theme can even define custom breakpoints through theme.json, so the responsive styles snap to the exact widths that matter for your design.
For site owners who've been using page builders primarily for responsive controls, this closes a real gap in core WordPress.
## Hover, Focus, and Active State Styling
WordPress 7.1 also introduces pseudo-state styling for interactive elements like buttons and links.
From the block sidebar, you can now set how a button looks when someone hovers over it, clicks it, or navigates to it with a keyboard. A simple "State" dropdown lets you toggle between default, hover, focus, and active states and style each one individually.
This is particularly useful for WooCommerce store owners who want polished "Add to Cart" interactions, or membership sites where call-to-action buttons need to feel responsive and clickable. Previously, even changing a button's hover color required custom CSS or a page builder.
## Your Browser Now Handles Image Uploads
Here's a technical change that solves a very practical problem.
Before 7.1, every image you uploaded was processed on your server using PHP (through the GD or Imagick libraries). For small images, no big deal. But if you've ever tried uploading a 15MB product photo or a high-res hero image and hit the dreaded "PHP memory limit exceeded" error, you know the frustration.
WordPress 7.1 shifts image processing to your browser. Using a WebAssembly-compiled version of libvips, your browser handles resizing, compression, and thumbnail generation before the image ever reaches your server.
Here's what that means in practice:
**Images come out roughly 15% smaller** compared to the old server-side processing
**No more PHP memory errors** on large uploads
**Your server's CPU and RAM stay free** for actually serving your site to visitors
**Up to 5 concurrent uploads** with 2 simultaneous processing operations
**HEIC photos from iPhones** automatically convert to JPG
**AVIF and WebP formats** are now supported natively
One thing to know: full browser support currently requires Chrome 137+ or Edge 137+ on desktop. Safari and Firefox don't fully support the required WebAssembly features yet. For those browsers, WordPress falls back to server-side processing automatically, so nothing breaks.
For sites with large media libraries (product catalogs, course content, community galleries), this is a genuine quality-of-life improvement.
## A Redesigned Image Editor
WordPress 7.1 ships a completely overhauled image editor modal.
The previous editor did its job, but it felt dated. The new version supports freeform cropping, preset aspect ratios, rotation, horizontal and vertical flipping, and metadata editing. It all lives in a dedicated modal that feels more like a lightweight design tool than the clunky overlay it replaces.
You also get a magnified crop view for precision editing and the ability to edit images directly within Cover blocks.
Another practical addition: resilient uploads that automatically pause and resume if your connection drops mid-upload. If you've ever lost a batch upload because your Wi-Fi blipped for a second, you'll appreciate this one.
And a small but meaningful accessibility win: you can now mark images as "decorative" with a toggle, which tells screen readers to skip them entirely.
## Two New Core Blocks: Tabs and Playlist
WordPress 7.1 adds two blocks that many site owners have been installing third-party plugins to get.
### Tabs Block
The Tabs block organizes content into clickable panels. Product specifications, FAQ sections, course module overviews, pricing comparisons: any scenario where you have categorized content that benefits from a compact, tabbed layout.
The implementation follows W3C accessibility guidelines, meaning keyboard navigation and screen readers work correctly out of the box. You can nest any block type inside each tab panel and reorder tabs using toolbar buttons.
For WooCommerce stores, this is a natural fit for product detail pages. For course sites, it works well for organizing module content or lesson resources by category.
### Playlist Block
The Playlist block is built for audio content. Podcasts, audio courses, music samples: this block displays your tracks with metadata (title, artist, album art) and includes customizable waveform visualization.
Previously, embedding multiple audio files required shortcodes or a third-party plugin. Now it's a native block with a proper player interface, full styling controls for typography, background, and dimensions, and support for every audio MIME type registered on your site.
## Collaboration Upgrades: Notes, @Mentions, and Revisions
WordPress has been building toward real team collaboration for several releases, and 7.1 makes meaningful progress.
**Notes** now support rich text formatting (bold, italics, links, emojis), inline text selection (highlight specific words and attach a comment, not just an entire block), and @mentions that trigger email notifications to tagged collaborators. You can attach multiple notes to the same block, and long notes collapse by default to keep the editor clean.
**Visual revisions** also get shareable links. You can copy a URL to a specific version of your post and share it with a collaborator, who'll see a color-coded view of what changed.
For teams managing content across membership sites, course platforms, or multi-author blogs, these features reduce the back-and-forth that typically happens in external tools before content ever makes it into WordPress.
## Admin Interface Gets a Facelift
You'll notice several visual changes the moment you log into WordPress 7.1.
### Persistent Admin Toolbar
The admin bar now stays visible in both the Post Editor and the Site Editor. Previously, it would disappear when you entered the editor, making it harder to navigate back to the dashboard or jump to other admin pages. The toolbar also sports redesigned SVG icons (replacing the older Dashicons), circular profile avatars, and a back chevron replacing the old WordPress "W" logo.
### Smarter Command Palette
The command palette (Cmd+K or Ctrl+K) is reorganized into three sections: Recent, Matching, and Suggestions. It now remembers your recent commands across sessions and surfaces contextual suggestions based on what you're currently editing.
### Color Scheme Consistency
Your chosen admin color scheme now extends to the Site Editor. If you use "Midnight" or "Sunrise," the editor sidebar will match instead of defaulting to black. A small detail, but it makes the whole experience feel more cohesive.
### New Identity Screen
A new Design > Identity section in the Site Editor puts your site title, tagline, logo, and site icon in one place. Previously, these settings were scattered across the Customizer and various editor panels.
### List View Improvements
The Posts list view now shows excerpts for easier scanning, and you can shift-click to select multiple posts for bulk actions.
## Under the Hood: Developer Highlights
A few notable changes for developers and site builders who work with code:
**Abilities API enhancements:** Four new lifecycle filters for intercepting and transforming ability execution. Enhanced filtering lets you query abilities by category, namespace, and metadata. These improvements make AI-driven operations more granular and secure.
**Design tokens and ThemeProvider:** A new wordpress/theme package introduces CSS custom properties following a "WPDS" naming pattern, plus a React ThemeProvider component that auto-generates color ramps from seed colors.
**jQuery UI updated to 1.14.2.** Test any admin-facing plugins that rely on jQuery UI, as behavior changes are possible.
**SVG icon system:** A public API lets plugins and themes register custom icon sets with strict SVG sanitization.
**Post editor is always iframed** for consistency, even with older meta boxes (requires Block API version 3).
**Faster editor startup** through preloaded REST API requests that reduce initialization time.
## What This Means for Your WordPress Site
WordPress 7.1 is a solid release across the board.
If you're running a content-heavy site (membership community, course platform, multi-author blog), the responsive styling controls and new Tabs block give you more design flexibility without installing additional plugins. The image editor and client-side processing make media management genuinely smoother, especially for sites with growing media libraries.
For WooCommerce stores, the hover state styling, Tabs block (perfect for product details), and reduced server load from browser-based image processing all contribute to a better building and shopping experience.
The collaboration features signal that WordPress is getting serious about team workflows. If you've been relying on external tools for content review and feedback, it's worth revisiting what WordPress can handle natively now.
And since client-side image processing offloads work from your server, more of your hosting resources go toward fast page delivery through the [CDN edge](/cloudflare-cdn/) rather than crunching image thumbnails on every upload.
**Before you update:** Back up your site, test on staging first (especially if you run custom code or older plugins), and verify that your critical plugins have confirmed WordPress 7.1 compatibility.
## Wrapping Up
WordPress 7.1 delivers improvements that matter for everyday site owners, not just developers. The responsive styling controls alone eliminate a major reason many people reach for page builder plugins. Client-side image processing solves real frustrations (goodbye, PHP memory errors), and the new Tabs and Playlist blocks fill two of the longest-standing gaps in core WordPress.
Test it on staging, confirm your plugins are ready, and update when you're confident. Your site and your workflow will be better for it.
---
## How AI Crawlers Are Inflating Your Hosting Bill (And What to Do About It)
- URL: https://levamo.com/blog/ai-crawlers-hosting-bill/
- Category: website-security
- Author: Shahzeb Ahmed
- Published: 2026-08-19
AI bots now outnumber humans online and quietly inflate your hosting bill.
You check your hosting dashboard. Everything looks fine. Uptime is solid, your site loads fast, and you haven't changed anything in weeks. But somehow, your bandwidth usage is climbing. Your PHP workers are busier than usual. And if you're on a plan with overage charges, you might be staring at a surprise line item on your next invoice.
The culprit? AI crawlers. And they're probably hitting your site right now.
## What Are AI Crawlers, and Why Are They on Your Site?
AI crawlers are automated bots used by companies like OpenAI, Anthropic, and Google to scrape website content. They use that content to train large language models, power AI search engines, or fetch pages in real time when a user asks a chatbot a question.
You've probably heard of Googlebot. It crawls your site so Google can index your pages. AI crawlers do something similar, but with a key difference: most of them aren't sending you any traffic back. They take your content, feed it into a model, and your site never sees a visitor from it.
There are three main types:
**Training crawlers** (GPTBot, ClaudeBot, CCBot) scrape your content to train AI models. They crawl aggressively, hit every page they can find, and offer zero direct benefit to your site.
**AI search crawlers** (OAI-SearchBot, PerplexityBot) index your content for AI-powered search results. These can actually drive some referral traffic, so they're worth keeping around.
**Real-time fetchers** (ChatGPT-User) grab your pages on demand when someone asks a chatbot a question that requires fresh data. These are sporadic but can spike unpredictably.
## The Numbers Are Staggering
This isn't a theoretical problem. The data paints a clear picture.
Cloudflare reported in August 2026 that fewer than half of all HTML page requests now come from a human. Let that sink in. More than half of the traffic hitting websites globally is automated.
The Imperva 2025 Bad Bot Report found that automated traffic accounts for 51% of all web activity, with bad bots alone responsible for 37%.
And the growth rate is accelerating. According to TollBit's analysis of publisher networks, the ratio of AI bot visits to human visits shifted from 1 in 200 at the start of 2025 to 1 in 31 by Q4 2025. That's a 6.5x increase in under a year.
Your site is part of this. Whether you run a [WooCommerce store](/managed-woocommerce-hosting/), a membership community, or a [course platform](/hosting-for-lms/), AI crawlers are visiting your pages. The question is how much it's costing you.
## How AI Crawlers Silently Inflate Your Hosting Costs
Here's why AI crawler traffic is different from regular bot traffic, and why it hits your wallet harder than you'd expect.
### 1. They Bypass Your Cache
This is the big one. When a human visitor loads your homepage, your hosting server can serve a cached version. The page is already generated, sitting in memory, ready to go. The server barely breaks a sweat.
AI crawlers don't play by those rules. They crawl deep into your site, hitting pages that aren't cached: product pages with dynamic pricing, membership content behind authentication checks, course pages with progress tracking, search result pages, paginated archives. Every one of these requests forces your server to do real work.
For a WooCommerce store, that means executing PHP, querying the database for product data, calculating shipping rules, checking inventory, and generating a full page from scratch. Multiply that by thousands of requests per day, and your server is doing a lot of unpaid labor.
### 2. They Consume PHP Workers
Every request that can't be served from cache needs a PHP worker to process it. Your hosting plan comes with a fixed number of these workers. When they're all busy, new requests (from actual customers) have to wait in line.
AI crawlers don't queue politely. Training bots like GPTBot and ClaudeBot can send hundreds of requests per minute, each one claiming a PHP worker while it processes. During a crawl burst, your real visitors experience slower page loads or timeout errors, not because your site is broken, but because bots are hogging the resources they need.
### 3. They Spike Your Bandwidth
AI crawlers download the full HTML of every page they visit. Some also pull CSS, JavaScript, and even images. A single training crawler session can download tens of gigabytes from a content-heavy site.
If your hosting plan includes a bandwidth cap (and most do), this pushes you closer to overages. On plans that charge per gigabyte of overage, you're literally paying for bots to scrape your content.
### 4. They Inflate Your Database Load
Every dynamic page request triggers database queries. On a membership site running BuddyPress or [MemberPress](/memberpress-hosting/), a single page load might execute 50 to 100 database queries to check user permissions, load activity feeds, and render personalized content.
AI crawlers trigger these queries without being logged in, so the server runs all that logic just to serve a page the bot will strip down to plain text anyway. On busy sites, this database load compounds and starts affecting performance for everyone.
### 5. They Distort Your Analytics
This one doesn't cost you server resources, but it costs you decision-making clarity. AI crawler visits inflate your page views, skew your bounce rate, and throw off conversion metrics. If you're making business decisions based on analytics data that's 30-50% bot traffic, you're working with bad information.
## Why Your Hosting Dashboard Won't Show the Problem
Most hosting control panels show you bandwidth usage, disk space, and maybe CPU utilization. What they don't show you is who's consuming those resources.
Your bandwidth graph might show a spike on Tuesday afternoon. Was that a successful email campaign driving real customers? Or was it ClaudeBot crawling your entire product catalog? Without bot-level visibility, you can't tell. And if you can't tell, you can't fix it.
This is the hidden part of the problem. You might upgrade to a higher hosting plan thinking you've outgrown your current one, when the real issue is that 40% of your server load is bots you never invited.
## What You Can Actually Do About It
The good news: you don't have to accept this. But the approach matters. Blocking bots at the wrong layer is like putting a lock on your bedroom door while leaving the front door wide open.
### Block at the Edge, Not the Server
This is the most important distinction. If a bot reaches your server before it gets blocked, the damage is already done. Your PHP workers have already processed the request, your database has already run the queries, and your bandwidth has already been consumed. A WordPress plugin that blocks bots is too late in the chain.
What you need is edge-level blocking. That means stopping bots at the CDN or firewall layer, before the request ever touches your server. No PHP execution, no database queries, no bandwidth consumed.
[Cloudflare's WAF](/cloudflare-cdn/) (Web Application Firewall) does exactly this. It identifies bot traffic at the edge and blocks or challenges it before it reaches your origin server. The request dies at one of Cloudflare's 300+ global edge locations, and your server never knows it happened.
On Levamo, Enterprise Cloudflare is included on every plan (yes, even Starter at $29/mo). That means WAF protection, DDoS mitigation, and bot management are active from day one, with no extra charges and no plugins to install.
### Use robots.txt (But Know Its Limits)
Your robots.txt file can tell well-behaved crawlers to stay away. Here's a basic block for the major AI training bots:
```
User-agent: GPTBot
Disallow: /
User-agent: ClaudeBot
Disallow: /
User-agent: CCBot
Disallow: /
User-agent: anthropic-ai
Disallow: /
User-agent: Google-Extended
Disallow: /
```
The problem? robots.txt is a suggestion, not a command. Legitimate crawlers from OpenAI and Anthropic generally respect it. But scraper bots that impersonate these crawlers, or less scrupulous AI companies, will ignore it completely. That's why edge-level blocking is your real defense, and robots.txt is just the first line.
### Be Selective About What You Block
Not all AI bots are bad for your business. AI search crawlers like OAI-SearchBot and PerplexityBot can actually drive traffic to your site by citing your content in AI-generated search results. Blocking them means cutting yourself off from a growing discovery channel.
The smart approach is to block training crawlers (which take your content and give nothing back) while allowing AI search crawlers (which can send visitors your way). Levamo's dashboard includes an AI bot control setting that lets you choose among allowing all AI bots, allowing only verified bots, or blocking all AI bots.
And here's the irony worth noting: while rogue AI crawlers are inflating your hosting bill, AI itself can also be your best site management tool. Levamo's AI Management feature lets you connect ChatGPT, Claude, or Cursor directly to your WordPress site and manage it through conversation. Update plugins, draft posts, redesign pages, all without logging into wp-admin. The difference is control. AI Management works with your permission, on your terms, with a draft-first safety model. AI crawlers just take.
### Monitor Your Server Logs
If you want to see exactly what's hitting your site, check your raw access logs. Look for user agent strings containing GPTBot, ClaudeBot, CCBot, Bytespider, PetalBot, or Applebot-Extended. You'll probably be surprised by the volume.
On Levamo, you can also use the Cloudflare analytics built into your dashboard to see bot traffic patterns without digging through log files.
## The Real Cost: What Could You Do With Those Resources?
Think about it this way. If 30% of your server's PHP workers are busy serving AI crawlers, that's 30% fewer workers available for your actual customers. During a product launch, a membership sale, or a course enrollment rush, those workers could be the difference between a smooth checkout and a timeout error that costs you revenue.
The resources AI crawlers consume aren't free. They're resources you're paying for, on a plan you chose based on your expected human traffic. Every PHP worker, every database query, every megabyte of bandwidth consumed by a bot is a resource stolen from your business.
## Wrapping Up
AI crawler traffic isn't going away. If anything, it's accelerating. The ratio of bots to humans is shifting every quarter, and your hosting bill is absorbing the impact whether you realize it or not.
The fix isn't complicated, but it does require the right infrastructure. Edge-level bot blocking (through a WAF like Cloudflare) stops the bleeding before it starts. Combine that with a selective robots.txt policy and dashboard-level AI bot controls, and you've reclaimed your server resources for the people who actually matter: your customers.
If your current host doesn't include enterprise-grade bot protection on every plan, you're subsidizing the AI industry with your hosting budget. That's not a great deal.
---
## WordPress Security Audit: A Step-by-Step Checklist for Site Owners
- URL: https://levamo.com/blog/wordpress-security-audit/
- Category: website-security
- Author: Shahzeb Ahmed
- Published: 2026-08-18
Run a 12-step WordPress security audit: updates, users, malware, SSL, backups, more.
You installed an SSL certificate. You set up 2FA. You even picked a decent hosting provider. So your WordPress site is secure, right?
Maybe. Maybe not. The truth is, security isn't something you set up once and forget about. Plugins get abandoned. User accounts pile up. That theme you deactivated six months ago? It's still sitting in your file system with a known vulnerability.
A security audit is how you find out what's actually going on under the hood. Not what you *think* is happening, but what's really there.
This guide walks you through a complete WordPress security audit in 12 steps. No expensive tools required, no developer background needed. Just you, your WordPress dashboard, and about an hour of focused attention.
## What Is a WordPress Security Audit?
A security audit is a systematic check of your WordPress site's defenses. You're looking for gaps: outdated software, weak credentials, missing protections, and configurations that leave your site exposed.
It's different from a security *setup*. Setup is about putting protections in place. An audit is about verifying those protections still work and nothing new has slipped through.
Think of it like a home inspection. You already have locks on the doors and a smoke detector. The inspection checks whether the locks still latch, the batteries aren't dead, and nobody left a window open.
## When Should You Run a Security Audit?
Run a full audit in these situations:
**Quarterly**, as part of regular site maintenance
**After a security incident** or suspected breach
**Before a major launch** (new product, membership tier, course enrollment period)
**When you add new team members** who get WordPress access
**After installing multiple new plugins** or switching themes
If you run a WooCommerce store, membership site, or LMS platform with paying customers, quarterly is the bare minimum. Their payment data and personal information is your responsibility.
## The 12-Step WordPress Security Audit Checklist
### Step 1: Check WordPress Core, Plugin, and Theme Versions
This is the single most impactful step. According to [Patchstack](https://patchstack.com/ "nofollow")'s 2026 State of WordPress Security report, plugins accounted for 91% of all discovered vulnerabilities in 2025, with total vulnerabilities jumping 42% year-over-year to 11,334.
**What to check:**
Go to **Dashboard → Updates** and note any available updates
Check that you're running the latest major WordPress version
Look at every plugin on the **Plugins** page, not just active ones. Deactivated plugins with known vulnerabilities are still exploitable
Do the same for themes under **Appearance → Themes**
**What to do about it:**
Update everything that has a pending update
Delete any deactivated plugins and unused themes entirely. Not just deactivate. Delete.
If a plugin hasn't been updated by its developer in over a year, look for an actively maintained alternative
On Levamo, your WordPress core updates are managed automatically, but plugins and themes are still your responsibility. The Advanced SiteShield add-on monitors your full stack (plugins, themes, core, PHP, and database) and alerts you to vulnerabilities with priority levels, so you know which updates are urgent and which can wait.
### Step 2: Review User Accounts and Permissions
Old accounts are a common entry point. That freelancer who helped you three months ago? Their admin account might still be active.
**What to check:**
Go to **Users → All Users** and review every account
Note any accounts with the Administrator role that shouldn't have it
Look for accounts you don't recognize
Check if any users have email addresses from domains you don't know
**What to do about it:**
Delete accounts that are no longer needed
Downgrade roles where full admin access isn't required. Most content contributors only need the Editor or Author role
Follow the principle of least privilege: every user gets the minimum access they need to do their job, nothing more
### Step 3: Test Your Login Security
Your login page is the front door. Attackers try it first.
**What to check:**
Try logging in with a common password. If the site lets you set "password123" as a password, that's a problem
Check whether [two-factor authentication](/blog/two-factor-authentication-2fa/) is enabled for all admin accounts
Verify that login attempt limits are in place (either through a plugin or your host's WAF)
Check if wp-login.php is accessible from any IP address
**What to do about it:**
Enforce strong passwords for all users, especially administrators
Enable 2FA using an authenticator app (not SMS, which is vulnerable to SIM swapping)
Install a login limiting plugin like [Limit Login Attempts Reloaded](https://wordpress.org/plugins/limit-login-attempts-reloaded/ "nofollow") if your host doesn't handle this at the server level
[](https://wordpress.org/plugins/limit-login-attempts-reloaded/ "nofollow")
Levamo accounts support authenticator-app 2FA with team-admin enforcement, meaning the admin can require every team member to enable 2FA before accessing the dashboard. This covers your hosting-level access. For WordPress itself, you'll want a 2FA plugin like [WP 2FA](https://wordpress.org/plugins/wp-2fa/ "nofollow") or [Wordfence Login Security](https://wordpress.org/plugins/wordfence-login-security/ "nofollow").
### Step 4: Scan for Malware and Suspicious Files
Malware doesn't always announce itself. Some infections sit quietly, redirecting a percentage of your traffic or injecting hidden links that only search engines see.
**What to check:**
Run a malware scan using [Wordfence](https://wordpress.org/plugins/wordfence/ "nofollow"), [Sucuri SiteCheck](https://sitecheck.sucuri.net/ "nofollow"), or your host's built-in scanner
Look for recently modified files that you didn't change (especially in /wp-includes/ and /wp-admin/)
Check for unfamiliar files in your theme's root directory
Search for eval(), base64_decode(), and exec() in theme and plugin files, as these functions are commonly used in malicious code
**What to do about it:**
If your scanner finds malware, quarantine and remove the affected files
Identify *how* the malware got in (usually an outdated plugin or compromised credentials)
Change all passwords after cleanup, including WordPress, FTP/SFTP, database, and hosting panel
Levamo runs Monarx malware scanning at the server level on every site. Unlike plugin-based scanners that check files against known signatures, Monarx uses behavioral analysis to catch obfuscated and zero-day threats. It quarantines malicious files automatically and alerts the support team, so infections get caught even if you're not actively looking.
[](https://wordpress.org/plugins/wordfence/ "nofollow")
### Step 5: Verify Your SSL Certificate and HTTPS
An expired or misconfigured [SSL certificate](/blog/ssl-website-security/) is embarrassing at best and a security hole at worst.
**What to check:**
Visit your site and look for the padlock icon in the browser address bar
Click the padlock to verify the certificate is valid and not expired
Check that all pages load over HTTPS, not just the homepage
Look for mixed content warnings in your browser's developer console (resources loading over HTTP on an HTTPS page)
**What to do about it:**
If your certificate is expired, renew it through your host or certificate provider
Fix mixed content by updating hardcoded http:// URLs in your content and database
Add an HTTP to HTTPS redirect if one isn't already in place
On Levamo, SSL certificates are free, auto-renewing, and enforced by default through Cloudflare. This is one audit step you can effectively skip if you're hosted with us, but it's worth checking mixed content regardless.
### Step 6: Review Your Firewall and WAF Configuration
A web application firewall (WAF) filters malicious traffic before it reaches your site. But only if it's properly configured.
**What to check:**
Verify that your WAF is active and processing traffic (not just installed but disabled)
Review blocked request logs if available. A spike in blocked requests could mean an active attack
Check that [OWASP Top 10](https://owasp.org/www-project-top-ten/ "nofollow") rules are enabled (SQL injection, XSS, CSRF, etc.)
If you use [Cloudflare](/cloudflare-cdn/), verify your site is proxied (orange cloud icon) not just using DNS
**What to do about it:**
If you don't have a WAF, set one up. Cloudflare's free plan provides basic protection, or use a plugin like Wordfence
Review any custom rules to ensure they're not accidentally blocking legitimate traffic
Check that your WAF rules are current, as new attack patterns emerge regularly
Levamo includes Enterprise Cloudflare WAF on all plans with OWASP Top 10 rules, bot mitigation, and DDoS protection across 300+ edge locations. There's no setup required on your end, and no per-attack fees. The Advanced SiteShield add-on layers 16,000+ virtual patches on top, deploying targeted firewall rules automatically when plugin vulnerabilities are disclosed.
### Step 7: Check Your Backup System
Backups are your last line of defense. If everything else fails, a clean backup is what saves you.
**What to check:**
Verify that automated backups are running on schedule
Check the date of your most recent backup. If it's more than a week old, something is wrong
Confirm that backups are stored off-site (not just on the same server as your live site)
Test a restore. Seriously. Download a backup and verify that it actually contains your data
**What to do about it:**
Set up automated daily backups if you haven't already
For WooCommerce stores and membership sites with active transactions, consider hourly backups
Store at least one copy of your backup in a separate location (a different hosting provider, cloud storage, or local drive)
Levamo includes daily automated backups on all plans with one-click restore. For sites with frequent transactions, hourly backups are available as a $10/month add-on. On-demand snapshots let you create a backup right before making changes, so you always have a rollback point.
### Step 8: Audit Your Security Headers
Security headers tell browsers how to handle your site's content. Missing headers leave your visitors vulnerable to clickjacking, XSS, and other client-side attacks.
**What to check:**
Use a free tool like [SecurityHeaders.com](https://securityheaders.com/ "nofollow") to scan your site. Key headers to look for:
**Content-Security-Policy (CSP):** Controls which resources the browser is allowed to load
**X-Frame-Options:** Prevents your site from being embedded in iframes (clickjacking protection)
**X-Content-Type-Options:** Stops browsers from MIME-type sniffing
**Strict-Transport-Security (HSTS):** Forces HTTPS connections
**Permissions-Policy:** Controls access to browser features like camera, microphone, and geolocation
[](https://securityheaders.com/ "nofollow")
**What to do about it:**
Add missing headers through your server configuration, a plugin, or your CDN
Start with X-Content-Type-Options: nosniff and X-Frame-Options: SAMEORIGIN as they rarely cause compatibility issues
Be careful with Content-Security-Policy, as an overly restrictive policy can break page builders, payment gateways, and analytics scripts. Test in report-only mode first
For a deep dive on implementing each header, check out our [WordPress Security Headers guide](/blog/wordpress-security-headers/).
### Step 9: Test File Permissions
Incorrect file permissions can let attackers modify your WordPress files or read sensitive configuration data.
**What to check:**
wp-config.php should be 400 or 440 (read-only for the owner)
Directories should be 755 (readable and executable, writable only by the owner)
Files should be 644 (readable by everyone, writable only by the owner)
The wp-content/uploads/ directory should be 755, not 777
No files or directories should ever be set to 777 (world-writable)
**How to check:**
If you have SSH or SFTP access, run:
```bash
find /path/to/wordpress -type f -perm 777
find /path/to/wordpress -type d -perm 777
```
If either command returns results, those files or directories need to be tightened immediately.
**What to do about it:**
Fix any 777 permissions to the appropriate level (644 for files, 755 for directories)
Make sure wp-config.php isn't readable from the web. Try accessing yourdomain.com/wp-config.php in a browser to verify
### Step 10: Review Your Database Security
Your database holds everything: posts, user credentials, customer data, order history, and site configuration.
**What to check:**
Verify that your database user doesn't have unnecessary privileges (DROP, GRANT, and FILE permissions are rarely needed for WordPress)
Check if your database table prefix is still the default wp_. While changing it alone isn't a strong defense, it eliminates one piece of predictable information
Look for unknown users or admin accounts directly in the wp_users table
Check for suspicious entries in the wp_options table, especially siteurl, home, and any unfamiliar transient entries
**What to do about it:**
Remove unnecessary database privileges from your WordPress database user
Clean up suspicious entries if found
Make sure your database credentials in wp-config.php are strong and unique
### Step 11: Check PHP Version and Server Configuration
Running an outdated PHP version means missing security patches. It also means slower performance.
**What to check:**
Go to **Tools → Site Health** in your WordPress dashboard to see your PHP version
PHP 8.1 reached end of life in December 2025. If you're running anything below PHP 8.2, you're on an unsupported version
Check that display_errors is set to Off in production (error messages can reveal file paths and configuration details to attackers)
Verify that allow_url_fopen and allow_url_include are disabled unless a specific plugin requires them
**What to do about it:**
Upgrade to the latest supported PHP version (8.2 or 8.3 as of 2026)
If upgrading PHP breaks a plugin, that plugin is likely outdated and should be replaced
Disable display_errors in your php.ini or .htaccess
### Step 12: Monitor Activity Logs
If something goes wrong, activity logs tell you what happened, when, and who did it.
**What to check:**
Is activity logging enabled? If you don't have a logging plugin, you have no record of what happens on your site
Review recent logs for unusual activity: logins from unfamiliar IPs, bulk content changes, plugin installations you didn't authorize
Check for failed login attempts (a high number from the same IP indicates a brute force attack)
Look at user role changes and new account creations
**What to do about it:**
Install an activity logging plugin like [WP Activity Log](https://wordpress.org/plugins/wp-security-audit-log/ "nofollow") if you don't have one
Set up email alerts for critical events: admin logins, plugin installations, user role changes, and file modifications
Review logs at least weekly as part of your ongoing security routine
[](https://wordpress.org/plugins/wp-security-audit-log/ "nofollow")
## How Often Should You Audit?
Not every audit needs to be the full 12-step process.
| Frequency | What to Check |
|---|---|
| Weekly | Activity logs, backup status, update availability |
| Monthly | User accounts, login security, malware scan |
| Quarterly | Full 12-step audit |
| After any incident | Full 12-step audit plus forensic review |
The weekly and monthly checks take 10 to 15 minutes. The quarterly audit takes about an hour. That's a small investment to protect a site your business depends on.
## What to Do When You Find a Problem
Finding vulnerabilities is the point of the audit. Don't panic. Prioritize based on risk:
**Fix immediately:** Active malware, compromised accounts, world-writable files, expired SSL
**Fix this week:** Outdated plugins with known vulnerabilities, missing 2FA on admin accounts, no backup system
**Fix this month:** Missing security headers, default database prefix, unnecessary database privileges, outdated PHP
Document what you find and what you fix. This creates a record that makes future audits faster and helps you spot recurring issues.
## Wrapping Up
A WordPress security audit isn't about achieving perfection. It's about knowing where you stand and closing the gaps that matter most. The 12 steps in this checklist cover the areas where most WordPress sites are vulnerable, and you can work through them in an afternoon.
The key is making it a habit. Run the full checklist quarterly, do lighter checks weekly and monthly, and you'll catch problems before they become incidents. Your site, your customers, and your peace of mind are worth that hour.
---
## How to Secure Your WordPress Login Page: Beyond Basic Passwords
- URL: https://levamo.com/blog/secure-wordpress-login/
- Category: website-security
- Author: Shahzeb Ahmed
- Published: 2026-08-17
Lock down your WordPress login with 2FA, a custom URL, CAPTCHAs, and edge WAF.
You changed the default "admin" username. You picked a 20-character password with symbols and numbers. You feel pretty good about it.
Here's the problem: passwords alone stopped being enough a long time ago.
Credential stuffing attacks don't guess your password. They use passwords stolen from other breaches and try them across thousands of WordPress sites automatically. Phishing pages trick even security-conscious users into handing over credentials. And let's be honest, most teams have at least one person reusing the same password across multiple services.
Your WordPress login page is public by default. Every bot on the internet knows where to find it. So the question isn't whether your password is strong. It's what happens when someone gets past it.
This guide covers the practical layers you can add on top of strong passwords to make your WordPress login page genuinely hard to break into.
## Why Strong Passwords Aren't Enough Anymore
Let's be clear: you absolutely need strong, unique passwords. That's not up for debate. But treating passwords as your only line of defense is like locking your front door and leaving every window wide open.
Three things have changed the threat landscape:
**Credential stuffing is automated and massive.** Attackers take username/password pairs leaked from breaches at other companies and run them against WordPress login pages at scale. According to the [OWASP Foundation](https://owasp.org/ "nofollow"), credential stuffing is one of the most common attack vectors against web applications. If any team member reuses a password that appeared in a breach, your site is exposed.
**Phishing has gotten smarter.** Modern phishing pages look identical to legitimate login screens. Even users who know better can get tricked by a well-crafted email pointing to a convincing fake. Once someone enters their credentials on a phishing page, the password's strength is irrelevant.
**Team-based access multiplies risk.** A solo blogger controls one set of credentials. A WooCommerce store with five administrators, three editors, and a freelance developer has nine potential entry points. One weak link compromises the entire site.
The fix? Layer your defenses. No single measure is bulletproof, but stacking multiple protections makes unauthorized access exponentially harder.
## Add Two-Factor Authentication to WordPress
If you only do one thing from this entire guide, make it this.
[Two-factor authentication (2FA)](/blog/two-factor-authentication-2fa/) adds a second verification step after the password. Even if an attacker has valid credentials, they can't log in without access to the second factor (usually a six-digit code from an authenticator app on your phone).
**Authenticator apps over SMS.** Always choose app-based 2FA (Google Authenticator, [Authy](https://authy.com/ "nofollow"), or Microsoft Authenticator) over SMS codes. SIM-swapping attacks can intercept text messages, making SMS-based 2FA significantly less secure.
### Recommended 2FA Plugins
For your WordPress site itself, several plugins handle 2FA well:
**[WP 2FA](https://wordpress.org/plugins/wp-2fa/ "nofollow")** is purpose-built for two-factor authentication and supports authenticator apps, email codes, and backup codes. It also lets you set grace periods, so users aren't locked out the moment you enable 2FA.
[](https://wordpress.org/plugins/wp-2fa/ "nofollow")
**[Wordfence Login Security](https://wordpress.org/plugins/wordfence-login-security/ "nofollow")** is a free, lightweight module from the Wordfence team. It supports TOTP-based authenticator apps and recovery codes without requiring the full Wordfence firewall plugin.
[](https://wordpress.org/plugins/wordfence-login-security/ "nofollow")
**[miniOrange](https://wordpress.org/plugins/miniorange-2-factor-authentication/ "nofollow")** supports authenticator apps, push notifications, security questions, and hardware tokens. It's a good pick if your team needs flexibility in how they authenticate.
[](https://wordpress.org/plugins/miniorange-2-factor-authentication/ "nofollow")
All three are free for basic use and take under five minutes to set up.
### What About Your Hosting Dashboard?
Your hosting dashboard is just as critical as your WordPress login. If someone compromises your hosting account, they can access your database, files, and backups directly.
Levamo's dashboard supports authenticator-app 2FA with backup codes for recovery. It's TOTP-based (the same standard used by Google and Microsoft), so it works with any authenticator app you already use.
## Enforce 2FA Across Your Entire Team
Here's where most sites fall short. The admin enables 2FA for their own account and calls it done. Meanwhile, the editor with shop_manager access is still logging in with just a password.
Every account with backend access is an entry point. If your store manager, content editor, or freelance developer skips 2FA, that's an unlocked door into your site.
**What to look for in a 2FA plugin:**
Role-based enforcement (require 2FA for administrators and editors, optional for subscribers)
Grace periods that give users time to set up 2FA before being locked out
Backup code generation for account recovery
**On the hosting side,** Levamo's team admin enforcement lets account owners require 2FA for every team member on the hosting dashboard. No exceptions, no "I'll set it up later." If a team member hasn't enabled 2FA, the admin can see it on the team visibility dashboard and follow up. This matters especially for agencies managing multiple client sites from a single hosting account.
## Change Your Default Login URL
Every WordPress site uses /wp-admin/ and /wp-login.php by default. Every bot knows this. Changing your login URL doesn't make your site unhackable, but it does eliminate a huge volume of automated traffic hitting your login page.
Think of it as removing your house number from the mailbox. A determined attacker will still find you, but the casual ones move on.
**[WPS Hide Login](https://wordpress.org/plugins/wps-hide-login/ "nofollow")** is the most popular plugin for this. It's lightweight, requires zero configuration beyond choosing a new URL, and doesn't modify any core files.
[](https://wordpress.org/plugins/wps-hide-login/ "nofollow")
Pick something memorable but not obvious. Avoid patterns like /login, /admin-login, or /secret-admin because those are on every bot's dictionary list too.
**Important:** Bookmark your new login URL and share it with your team. If you forget it, you can disable the plugin via FTP or your hosting file manager to restore the default URL.
For a deeper look at how login URL changes fit into a broader brute force defense strategy, check out our [guide to brute force protection](/blog/wordpress-brute-force-protection/).
## Add a CAPTCHA to Your Login Form
CAPTCHAs add a challenge that's easy for humans and hard for bots. Placing one on your login page blocks automated login attempts before they even test a password.
**[Cloudflare Turnstile](https://www.cloudflare.com/products/turnstile/ "nofollow")** is the modern choice. It's free, privacy-focused, and often invisible to real users (no clicking fire hydrants). It verifies visitors in the background and only shows a challenge when something looks suspicious. Plugins like [Simple Cloudflare Turnstile](https://wordpress.org/plugins/simple-cloudflare-turnstile/ "nofollow") make integration straightforward.
[](https://wordpress.org/plugins/simple-cloudflare-turnstile/ "nofollow")
**[Google reCAPTCHA v3](https://www.google.com/recaptcha/about/ "nofollow")** works similarly, scoring visitors in the background and only challenging suspicious ones. Several security plugins bundle reCAPTCHA support, so you may already have access to it.
Place CAPTCHAs on your login page, registration page, and password reset form. Attackers target all three.
## Use HTTP Authentication as a Second Gate
This one's more technical, but it's extremely effective. HTTP authentication (sometimes called .htpasswd protection) adds a server-level username/password prompt before WordPress even loads.
Bots hitting your login page get a 401 Unauthorized response without triggering any PHP processing. This means zero server load from automated attacks, which is a significant benefit for resource-heavy sites like WooCommerce stores or membership platforms.
Your hosting control panel or file manager can usually set this up. You're adding a server-level credential check in front of wp-login.php, so attackers need to pass two authentication layers: the HTTP prompt and then the WordPress login form.
**Trade-off:** This adds friction for legitimate users, so it's best suited for sites where only a small internal team needs backend access. If you have hundreds of members logging in through a frontend form, this approach doesn't apply.
## Restrict Login Access by IP
If your team works from fixed locations (an office, a co-working space, or even consistent home IPs), you can restrict login page access to only those IP addresses.
This is done through .htaccess rules or your hosting's IP restriction tools. Anyone connecting from an unauthorized IP gets blocked before the login page even loads.
```apache
Order Deny,Allow
Deny from all
Allow from 203.0.113.50
Allow from 198.51.100.25
```
**When this works well:** Small teams with stable IPs, internal company sites, staging environments.
**When it doesn't work:** Remote teams with dynamic IPs, membership sites with user-facing logins, WooCommerce stores where customers access their accounts.
For most dynamic WordPress sites, the other measures in this guide are more practical. But for admin-only login pages on internal tools, IP restriction is nearly airtight.
## Monitor Login Activity
You can't protect what you can't see. Login activity monitoring shows you who's logging in, when, from where, and whether there have been failed attempts.
**[WP Activity Log](https://wordpress.org/plugins/wp-security-audit-log/ "nofollow")** records every login, logout, failed attempt, and session change. It also tracks user role changes and plugin activations, so you get a complete audit trail. For WooCommerce stores, it logs product and order changes too.
[](https://wordpress.org/plugins/wp-security-audit-log/ "nofollow")
**What to watch for:**
Multiple failed login attempts from the same IP (brute force in progress)
Successful logins from unfamiliar locations or IP addresses
Logins at unusual hours for your team
New administrator accounts you didn't create
Set up email alerts for critical events (new admin accounts, successful logins from new IPs) so you don't have to check the log manually.
## What Your Hosting Should Handle for You
Everything above happens at the WordPress level. But the most effective login protections happen before traffic ever reaches your server.
A hosting provider with proper edge-level security handles three things automatically:
**Web Application Firewall (WAF).** A WAF at the CDN edge evaluates every request before it reaches your origin server. Known attack patterns, malicious payloads, and suspicious request signatures get blocked at the network level. Your server never sees them.
**Rate limiting.** Legitimate users don't send 50 login requests per second. Edge-level rate limiting throttles high-frequency requests so brute force attempts get cut off before they can test more than a handful of passwords.
**Bot detection and blocking.** Sophisticated bot detection goes beyond simple rate limiting. It identifies automated traffic by behavior patterns, known malicious IPs, and request fingerprints, then blocks or challenges it.
Levamo includes [Enterprise Cloudflare](/cloudflare-cdn/) on every plan. That means WAF rules, DDoS protection, rate limiting, and bot management are active from day one, with no add-ons or extra configuration needed. Combined with server-level Monarx malware scanning, threats get caught at both the edge and the origin.
The practical impact: while you're configuring 2FA plugins and CAPTCHA settings inside WordPress, your hosting is already blocking the vast majority of malicious traffic before it gets anywhere near your login page.
## Wrapping Up
Securing your WordPress login page isn't about any single measure. It's about stacking layers so that no single failure (a leaked password, a phished credential, a lazy team member) gives an attacker a way in. Start with 2FA across every account, then work through the rest of this list based on what fits your site. The biggest mistake isn't picking the wrong plugin. It's assuming a strong password is enough and stopping there.
---
## Top 15 Best LMS Plugins for WordPress In 2026
- URL: https://levamo.com/blog/best-wordpress-lms-plugins/
- Category: lms
- Author: Shahzeb Ahmed
- Published: 2026-08-13
Find the best WordPress LMS plugin for your online courses in 2026.
Imagine this: You spend months ideating the perfect niche to launch your online course. You've poured countless hours into outlining, preparing, and finally publishing it. But once you launch, student engagement is abysmally low, and completion rates are close to zero. To make matters worse, the platform crashes just when it shouldn't.
You investigate and realize your platform lacks engagement tools that keep students interested, leading to low engagement and poor [course completion rates](/blog/maximize-course-completion-rates/).
This is a scenario you *don't* want to be in.
Fortunately, I've shortlisted these top 15 WordPress LMS plugins for you, and these can solve your problems effectively. The best LMS plugin for WordPress will give you robust engagement tools, seamless integration options, and scalable features that keep students interested and ensure [smooth performance, even during peak times](/managed-lms-hosting/). With features like quizzes, gamification, and progress tracking, you will also boost engagement and significantly improve course completion rates.
Without further ado, let’s dive in!
## Levamo's Choice of the **Top WordPress LMS Plugins**
## 1. LearnDash
[](https://www.learndash.com/ "nofollow")
[LearnDash](https://www.learndash.com/ "nofollow") is arguably the most powerful and reliable WordPress LMS plugin out there. It is popular with educational institutions and individual course creators alike because of its diverse feature set and scalability.
**Top Features**:
- **Flexible Course Creation:** The LearnDash drag-and-drop course builder makes the process of designing and managing courses very simple.
- **Advanced Quizzing Options:** LearnDash offers multiple quiz types and grading styles, making it easy to assess the student’s learning.
- **Seamless WordPress Integrations:** LearnDash can integrate with hundreds of WordPress plugins, making it easy to add new features to your course platform.
- **Gamification:** LearnDash offers gamification, such as badges, points, and leaderboards, to make the course more engaging for the students.
It does have a steep learning curve, and you’re also limited to built-in payment options. Secondly, you’re also dependent on add-ons for advanced functionality. However, these are not that big of an issue, and you can’t go wrong with the most popular WordPress LMS plugin to create your website.
**Price:**
- **LearnDash LMS** - Starts at $199/Year
- **LearnDash Cloud** - Starts at $25/Month
**Trustpilot Rating**:
4.3 out of 5 (81 Reviews)
## 2. Tutor LMS
[](https://tutorlms.com/ "nofollow")
[Tutor LMS](/blog/build-lms-website-with-tutor-lms/) brings a range of interactive course creation tools and an intuitive frontend student dashboard, making it user-friendly for both course creators and learners. It is one of the fastest-growing WordPress LMS plugins at the moment.
**Top Features**
- **Interactive Course Builder:** Drag-and-drop functionality simplifies course creation.
- **Quiz Customization:** Offers multiple quiz types and options like timers, point-based questions, and more.
- **Frontend Dashboard:** Students can manage their learning, track progress, and view achievements from a single dashboard.
- **Monetization Options:** Supports multiple payment gateways and WooCommerce integration for easy course sales.
Tutor LMS is as robust as it gets. However, most advanced options are only limited to the Pro version. It also has very limited integrations with third-party tools outside of WordPress. This might make it hard for the users to connect to external CRM or marketing tools. Despite this, we must say, overall, Tutor LMS is one of the best LMS for WordPress.
**Price:** Starts at $199
**Trustpilot Rating:**
4.6 out of 5 (244 Reviews)
## 3. Learnomy
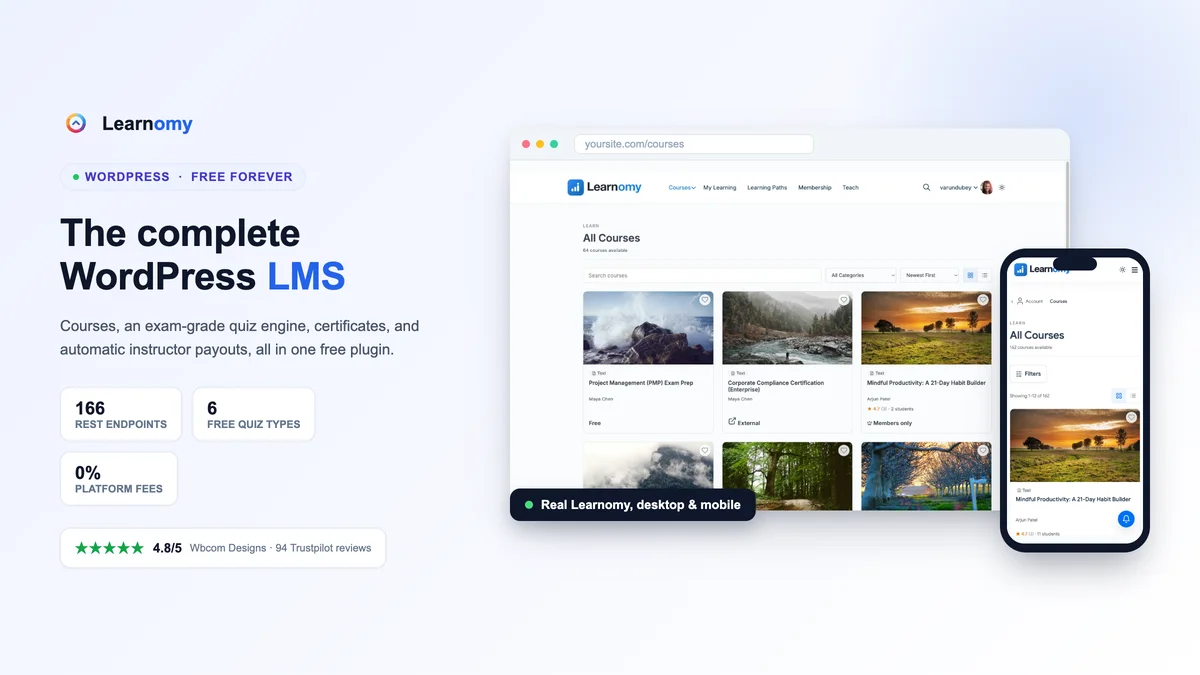
[Learnomy](https://learnomy.app/ "nofollow") is a newer WordPress LMS plugin, but it ships with a feature set that undercuts what most of the plugins above charge extra for. Course building, an eleven-question-type quiz engine, certificates, and a full instructor marketplace with automatic Stripe Connect payouts all live in the free version, no add-on required.
**Top Features**
**Exam-Grade Quiz Engine:** Six question types free (multiple choice, true/false, short answer, fill-in-the-blank, essay), five more with Pro (matching, ordering, numeric, math, calculated), across five player layouts including a sectioned exam board with a question map.
**Instructor Marketplace:** Teachers apply, get their own dashboard, and get paid automatically through Stripe Connect, so payday runs itself instead of requiring manual payout tracking.
**Direct Checkout, Zero Platform Cut:** Native Stripe and PayPal checkout plus a WooCommerce adapter, memberships with recurring billing and free trials, and the money goes straight to the school owner's account.
**Built to Stay Fast:** Normalized custom database tables (not serialized post meta) and the WordPress Interactivity API for navigation, so performance holds up whether a school has 50 students or 50,000.
Since it's newer to the market, Learnomy doesn't have the years of plugin-directory reviews that LearnDash or LifterLMS have built up, and it's distributed from the Wbcom Designs store rather than WordPress.org, so it's a direct-download install rather than a WordPress.org search-and-install. But for course creators who'd otherwise be stacking three or four paid add-ons onto another LMS to get essay grading, an instructor marketplace, and SCORM/xAPI/LTI support, Learnomy ships all of it in the free core.
**Price:** Starts at $104/year (Personal, 1 site) or $279 lifetime
**Trustpilot Rating:** 4.8 out of 5 (94 reviews)
## 4. LifterLMS
[](https://lifterlms.com/ "nofollow")
[LifterLMS](https://lifterlms.com/ "nofollow") is another highly popular WordPress learning management system, renowned for all its good qualities. Its close integration with membership and eCommerce tools makes it an ideal choice for regular course creators and online businesses who want to start a course website. LifterLMS allows course creators and businesses to create a structured learning path, as well as offers features that keep students engaged.
**Top Features**
- **Integrated Membership Options:** Allows you to sell memberships, which is ideal for layered access and recurring revenue.
- **eCommerce Capabilities:** Supports payment gateways, course bundles, and subscription-based pricing.
- **Personalized Learning Paths:** Achievement badges, certificates, and gamified elements keep learners engaged.
- **Progress Tracking:** Advanced reporting and metrics to monitor student engagement.
LifterLMS needs add-ons for certain essential features. This includes the advanced quizzes and specific integrations, which can increase the overall cost as time goes on. However, despite that fact, it remains a value-for-money product.
**Price:** Starts at $149.50/year
**Trustpilot Rating:**
4.3 out of 5 (21 Reviews)
## 5. MasterStudy
[](https://stylemixthemes.com/wordpress-lms-plugin/ "nofollow")
[MasterStudy LMS](https://stylemixthemes.com/wordpress-lms-plugin/ "nofollow") is a flexible WordPress course plugin that offers a comprehensive set of tools for creating and managing courses. It is perfect for professional training, certification, and skill development. It offers features that enable instructors to deliver engaging and interactive lessons, along with robust customization options to cater to various audiences.
**Top Features**
- **Interactive Lessons:** Supports multimedia content, including video, quizzes, and assignments, to create an engaging learning experience.
- **Certification and Badging:** Awards completion certificates and badges, making it ideal for skills-based and professional courses.
- **Customizable Enrollment Options:** Offers multiple options, including free, paid, and subscription-based access, to suit different course structures.
- **Student Communication Tools:** Includes real-time messaging to enable direct communication between students and instructors.
While MasterStudy is great on paper, some users reported a dip in performance, particularly when the courses are rich in media. Also, their support can be faster, especially when compared to the WordPress LMS plugins we mentioned above. Nevertheless, MasterStudy LMS provides great value considering the price point.
**Price:** Starts at $99/year
**WordPress.org Rating:** 4.5 out of 5 (389 reviews)
## 6. Sensei LMS
[](https://senseilms.com/ "nofollow")
[Sensei LMS](https://senseilms.com/ "nofollow") is not the most feature-rich LMS plugin for WordPress, but it is a budget-friendly choice. It is a great choice for course creators who require robust eCommerce features without the hassle of complicated setups.
**Top Features**
- **Native WooCommerce Integration:** Allows you to sell courses seamlessly through WooCommerce’s powerful eCommerce tools.
- **Content Dripping:** This lets you control the release of content over time to keep students engaged.
- **Flexible Quiz Builder:** Provides multiple question types, making it easy to assess learner understanding.
- **Student Management Tools:** Allows for tracking and analyzing student progress to improve learning outcomes.
However, Sensei LMS doesn't offer some of the advanced engagement features that other WordPress LMS plugins provide. Plus, it depends significantly on WooCommerce for monetization, which could complicate things for certain users. Nevertheless, for those seeking an affordable and straightforward solution that works well with WooCommerce, Sensei LMS is still a sensible and affordable option.
**Price:** Starts at $60/year
**WordPress.org Rating:** 3.7 out of 5 (35 Reviews)
## 7. LearnPress
[](https://learnpresslms.com/ "nofollow")
[LearnPress](https://learnpresslms.com/ "nofollow") is another affordable WordPress LMS plugin that provides essential tools for course creation at no cost, along with optional premium add-ons. Its modular design enables users to select additional features, making it highly customizable and budget-friendly. This also makes it particularly ideal for individuals seeking a straightforward, entry-level LMS that still offers key functionalities.
**Top Features**
- **Core LMS Features for Free:** Provides basic course creation, quizzes, and assignment tools at no cost.
- **Add-On Marketplace: This offers** optional paid add-ons so you can purchase only the features you need.
- **Customizable User Interface:** Adaptable layout options make it easy to align with your site’s branding.
- **Multi-Instructor Support:** Allows multiple instructors to collaborate on course creation and management.
LearnPress’s free version has some limitations in functionality, which forces you to buy the premium add-ons. But even the add-ons are comparatively affordable. Furthermore, the support and documentation may not be as comprehensive as what you find with some of the top WordPress LMS plugins, which could pose difficulties for newcomers. But it is still a favorite to many people due to its modular nature.
**Price:** Starts at $149/year
**WordPress.org Rating:** 2.5 out of 5 (8 Reviews)
## 8. WP Courseware
[](https://flyplugins.com/wp-courseware-wordpress-lms/ "nofollow")
[WP Courseware](https://flyplugins.com/wp-courseware-wordpress-lms/ "nofollow") is a well-regarded WordPress learning management system tailored for developing organized, sequential courses, making it an excellent choice for educational institutions and corporate training programs. With its user-friendly drag-and-drop course builder, WP Courseware is accessible for beginners while also providing advanced features for users who require greater control over course delivery.
**Top Features**
- **Drag-and-Drop Course Builder**: Streamlines course creation with an easy, code-free design tool.
- **Drip Content Scheduling**: Allows for gradual content release based on schedules you set.
- **Customizable Certificates**: Offers the ability to award branded certificates upon course completion.
- **Payment Gateway Integration**: Supports PayPal and Stripe, allowing seamless payment collection for monetized courses.
WP Courseware is mainly designed for sequential courses, which might restrict the creativity of the tutors who want to adopt more flexible course layouts. Furthermore, the interface of the plugin can seem a bit outdated when compared to other LMS plugins. Nevertheless, it is still a solid option for educational institutions and training programs where linear course structures are the way to go.
**Price:** Starts at 0
**Capterra Rating:** 4.5 out of 5 (21 Reviews)
## 9. Masteriyo LMS

[Masteriyo](https://masteriyo.com/?utm_source=levamo.com&utm_medium=blog&utm_campaign=outreach "nofollow") brings a fresh new approach to LMS for creators seeking a modern solution without the steep learning curve of other traditional plugins. It simplifies course creation and monetization process while ensuring seamless learning experience for enrolled users.
**Top Features**
**Interactive Lessons:** Native drag-and-drop course builder supports 7+ lesson types ranging from self-paced vidoes to live sessions
**Student Engagement Tools:** Keep students engaged with Content Drip, Quizzes, Assignment, and Certificates with QR validation tool.
**Community-driven development:** Masteriyo’s active community contributes feedback, influencing new features and updates.
**Masteriyo delivers:** an accessible and easy-to-use solution for creating, managing, and selling online courses. Its simplicity doesn’t compromise on the essential tools needed for a fully functional and engaging LMS, making it an excellent choice for creators at any level.
**Price:** [Starts at $99.00/year](https://masteriyo.com/?utm_source=levamo.com&utm_medium=blog&utm_campaign=outreach "nofollow")
G2
**Rating:** 4.7/5 (12 Reviews)
**WordPress.org Rating:** 4.8/5 (140+ Reviews)
## Top SaaS LMS Tools
While the above plugins were pure LMS plugins, aimed at users who want to build a learning platform, we've also shortlisted some of the top SaaS LMS systems.
## 10. Kajabi
[](https://kajabi.com/ "nofollow")
[Kajabi](https://kajabi.com/ "nofollow") is a top-tier, all-in-one SaaS LMS platform designed for professional course creators and businesses seeking advanced marketing features. Renowned for its extensive range of tools, Kajabi facilitates not just course delivery but also effective marketing, email campaigns, and sales funnel automation. It’s an ideal solution for businesses looking for a comprehensive resource for digital product creation and marketing.
**Top Features**
- **Email Marketing and Pipelines:** Includes sophisticated tools for building automated email campaigns and marketing pipelines.
- **Website Builder:** Provides a fully hosted solution with a website builder for a branded, professional online presence.
- **Comprehensive Analytics:** Tracks detailed metrics for both course performance and marketing efforts to optimize strategies.
- **Community Features:** Offers options to build communities, including discussion boards and forums, for fostering student interaction.
Kajabi’s all-in-one model does come with a higher price tag, and it might hurt the pockets of individual creators or startups. However, I can assure you that the comprehensive set of features and user-friendly interface that Kajabi offers make it a worthwhile investment.
**Price:** [Currently running an offer of $99 for 3 months](https://kajabi.com/pricing "nofollow")
**Trustpilot Rating:** 4.3 out of 5 (1,944 reviews)
## 11. Thinkific
[](https://www.thinkific.com/ "nofollow")
[Thinkific](https://www.thinkific.com/ "nofollow") is another comprehensive SaaS LMS platform that integrates course-building tools with marketing features to enhance course visibility. Renowned for its user-friendliness, Thinkific is perfect for both businesses and individuals looking to create polished courses without requiring coding skills or complicated setups. It’s particularly favored by those who appreciate a branded course experience along with versatile sales and marketing options.
**Top Features**
- **Landing Page Builder:** Includes a drag-and-drop builder for creating high-converting course landing pages.
- **Customizable Course Templates:** Offers pre-made templates that simplify course creation and branding.
- **Built-in Marketing Tools:** Supports email marketing, discount codes, and promotional tools to attract students.
- **Course Bundling and Upsells:** This lets you increase revenue with options to bundle courses and offer upsells during checkout.
Most of Thinkific’s advanced marketing tools are only available in higher-tier plans, which can raise costs for users seeking complete functionality. Nevertheless, Thinkific's combination of user-friendliness and scalability continues to make it a great option.
**Price:** Starts at 0
**Trustpilot Rating:** 3.4 out of 5 (809 reviews)
## 12. Teachable
[](https://teachable.com/ "nofollow")
[Teachable](https://teachable.com/ "nofollow") is a popular SaaS-based learning management system that gives you an easy way to create an education website. It's tailored for individuals who want to concentrate on creating content and building their audience without the need for technical expertise. Teachable offers strong student management features, various monetization options, and a clean, intuitive dashboard for overseeing courses and students.
**Top Features**
- **Sales and Checkout Pages:** Optimized checkout and sales pages are designed to increase course conversions and revenue.
- **Integrated Payment Processing:** Simplifies transactions with built-in payment options, including automatic tax calculation.
- **Student Management:** Offers insights and analytics to track student progress and engagement levels.
- **Mobile App Support:** Allows students to access courses and content seamlessly via mobile devices, enhancing flexibility.
Teachable can be a bit expensive compared to other SaaS LMS systems in terms of the features it offers. On top of that, it charges transaction fees on its lower-tier plans, which can eat into profits for those just starting out. So, it's not the best choice when it comes to affordable SaaS LMS pricing. However, Teachable’s seamless setup and easy student management features continue to make it an accessible platform for many.
**Price:** Starts at $59/month
**Trustpilot Rating:** 3.1 out of 5 (693 reviews)
## 13. WP Courses

[WP Courses](https://wpcoursesplugin.com/ "nofollow") is a simple but effective WordPress LMS plugin that is all about course delivery and ease of use. This is for educators, personal coaches, and solopreneurs who want to publish course material quickly without being overwhelmed by too many options. WP Courses plugs into your existing WordPress theme and lets you publish lessons with videos, images, or downloadable resources.
No coding experience is necessary to use WP Courses, and the learning curve is low. While not as deep as some of the enterprise-level LMS tools, it covers all the bases needed to run a functional online course platform.
**Top Features**
- **Course Builder with Drag & Drop interface:** You can create courses & lessons quickly & easily.
- **Rich multimedia integration:** It allows embedding YouTube, Vimeo, PDFs, images, and other file types directly into lessons.
- **Progress tracking:** Students can see their progress at a glance.
- **WooCommerce Integration:** Adding subscriptions, bundles, or one-time purchases to courses via WooCommerce is easy.
Overall, WP Courses lack advanced features and do not have as many integrations as top tools, but it is lightweight and easy to use. We recommend trying this if you want a quick setup with solid core features and a clean experience.
**Price**: Free, Paid plans start at $99.
**WordPress Rating**: 4.9 out of 5 (23 Reviews)
## 14. MemberPress

[MemberPress](https://memberpress.com/ "nofollow") is one of the most robust membership plugins for WordPress, but many don't know that it can also be a powerful LMS when combined with its Courses add-on. It offers a visual course builder that works perfectly with MemberPress. You can lock content behind paywalls, create tiered memberships, and offer courses to different audience segments with one plugin.
This combination of both [memberpress review](/blog/memberpress-review/) and course tools is great for entrepreneurs, coaches, and businesses who wish to sell courses as recurring memberships or one-time access. The visual course builder does the easy wor,k while MemberPress handles the back-end automation and access control.
**Top Features**
- **Integral Course Builder:** With the Courses add-on, you can create structured lessons by dragging and dropping.
- **Advanced Access Control:** Establish complicated membership rules that display different content to different user groups.
- **Drip Content Scheduling:** Release lessons over time to keep learners interested.
- **Subscription & Payment Tools:** Accept recurring payments and coupons and manage subscriptions via Stripe, PayPal, and offline payments.
- **Analytics and Reporting:** Monitor user progress, membership stats, and revenue stats from your dashboard.
Though great at combining LMS and membership functionality, MemberPress won't cut it for users who want bespoke quizzes, native certification, and more gamification. And as part of a broader membership system, the LMS features may feel limited to institutions solely focused on education. Yet, this all-in-one plugin is a steal for business creators.
**Price**: Starts at $179.50/year
**Trustpilot Rating**: 4.4 out of 5 (316 Reviews)
## 15. Academy LMS

[Academy LMS](https://academylms.net/ "nofollow") is among the newest entries in the WordPress LMS space, It's a fresh take on online education. Made for creators in mind, Academy LMS has an intuitive user interface, powerful lesson-building tools, and mobile responsiveness.
Support for quizzes, certificates, student dashboards & instructor collaboration means that Academy LMS is perfect for course creators of all levels. And it ships with a block-based editor that works natively with Gutenberg, so you can build custom course layouts without any extra page builders.
**Top Features**
- **Sleek Modern UI:** Beautiful course layouts and clean dashboards improve learning for students and instructors.
- **Full Course Builder:** Build structured courses with lessons, quizzes, and assessments from your WordPress dashboard.
- **Modern Dashboard:** Separate, customizable views for student and instructor dashboards.
- **Certificates & Quizzes:** Easy to award completion certificates and design assessments to evaluate students.
- **Instructional Collaboration:** Lets several instructors create, manage, and contribute to the same course.
Although Academy LMS still lacks some third-party integrations and advanced automation tools found in more mature platforms, the core offering is polished. It works best for creators who value visual design and usability.
**Price**: Free, premium starts at $69/year.
**Trustpilot Rating**: 4.9 out of 5 (86 Reviews)
### Bonus: MoodleCloud
Now let’s share a special mention: [MoodleCloud](https://www.moodlecloud.com/ "nofollow"). It is the cloud-based version of Moodle, the highly popular open-source learning management system for educational institutions. Renowned for its flexibility and extensive range of plugins, MoodleCloud can be tailored to meet diverse educational requirements, providing tools for both individual and group learning.
**Top Features**
- **Highly Customizable**: Access to extensive plugins for creating tailored learning experiences.
- **Collaborative Learning Tools**: Supports forums, chats, and group assignments, ideal for interactive learning.
- **Mobile-Ready**: Fully responsive design, along with dedicated mobile apps for on-the-go learning.
- **Comprehensive Reporting**: Provides detailed tracking of learner performance and engagement.
Moodle is more common as an LMS option for educational institutions, as is its twin MoodleCloud. Perhaps that’s why the interface can be quite complex for newcomers. Especially for those who are not well-versed in Moodle’s wide array of features. However, its flexibility and open-source foundation make MoodleCloud a strong option for academic settings.
**Price**: Starts at 0
**Capterra Rating**: 4.3 out of 5 (3322 Reviews)
## Tips to Choose the Right LMS Platform
You and I both know there is no one-size-fits-all LMS solution out there. So, before wrapping up the article, let’s share the key things that you should consider when picking the right LMS tool for your website.
- **Technical Requirements and Budget Constraints**: You should decide whether you need a WordPress or SaaS LMS based on your technical expertise and budget. SaaS platforms typically demand more expertise, ongoing maintenance, and hosting costs, while WordPress LMS plugins are generally simpler to set up and manage.
- **Scalability**: As your courses and user base expand, it's crucial that the LMS you select can accommodate increased traffic without sacrificing performance.
- **Pricing Models and Total Cost of Ownership**: LMS pricing can vary significantly, ranging from free options with paid features to premium all-inclusive subscriptions. Be sure to consider both initial and ongoing expenses, including any additional tools or features you might need.
- **Course Engagement and Interactivity Features**: To enhance the student experience and encourage course completion, prioritize engagement tools such as quizzes, forums, certificates, and gamification features. Platforms that offer a range of interactive options can significantly improve student engagement and retention.
- **Integrations with Marketing and CRM Tools**: Integrating your LMS with email marketing tools, CRM systems, and payment gateways can help you streamline operations and manage customer relationships effectively. So, make sure it is able to integrate with these tools.
## Take Your Pick of the Top LMS Plugins
Picking an LMS platform is a long-term decision for growth and scalability. Depending on your budget and required features, choosing the perfect one is often hard. That is where this blog comes in to help you make the decision easily. Let me know which WordPress LMS software you like the most in the comment section below.
Once you decide on the LMS plugin, the next most important thing is to pair it with reliable hosting. **Levamo Hosting** offers high-performance [LMS hosting](/managed-lms-hosting/) tailored for content-rich sites, ensuring your courses load fast and perform smoothly, even during peak times.
With the right LMS and [Levamo's powerful hosting](https://www.trustpilot.com/review/rapyd.cloud? "nofollow"), you’ll be well-equipped to deliver a top-tier learning experience that supports your business’s growth.
---
## How to Protect Your WordPress Site From Brute Force Attacks
- URL: https://levamo.com/blog/wordpress-brute-force-protection/
- Category: website-security
- Author: Shahzeb Ahmed
- Published: 2026-08-12
Stop WordPress brute force attacks with edge WAF, rate limiting, and 2FA.
Your WordPress login page is public by default. Every WordPress site on the internet has a predictable login URL. And automated tools can throw thousands of password combinations at that URL every hour without breaking a sweat.
That's the brute force problem in three sentences.
A brute force attack isn't sophisticated. There's no exploit code, no zero-day vulnerability, no clever social engineering. It's raw repetition: an automated script tries username-password combinations against your login form until one works. The approach is blunt, persistent, and surprisingly effective when sites don't have the right defenses in place.
According to Cloudflare's application security reports, credential stuffing and brute force attacks remain among the most common threats targeting web applications globally. WordPress sites are disproportionately targeted because of their market share and predictable login structure.
The good news? Brute force attacks are also one of the easiest threats to neutralize, if you layer your defenses correctly. This guide covers what brute force attacks look like, why WordPress is a favorite target, and exactly how to shut them down.
## How Brute Force Attacks Actually Work
At its simplest, a brute force attack is an automated guessing game. An attacker points a script at your login page and feeds it a list of usernames and passwords. The script submits login attempts one after another, hundreds or thousands per minute, until it hits a valid combination or gives up.
But modern brute force attacks are more nuanced than just random guessing. Here are the main variants:
**Simple brute force:** The script cycles through every possible character combination. This is the least efficient method and mostly targets weak passwords like "123456" or "password." It sounds primitive, but it still works because people still use those passwords.
**Dictionary attacks:** Instead of trying every character combination, the script uses a pre-compiled list of common passwords, leaked credentials, and popular word combinations. These lists are publicly available and contain millions of entries drawn from past data breaches.
**Credential stuffing:** The attacker uses username-password pairs stolen from breaches on other sites. If someone reused their Netflix password on their WordPress admin account, they're a sitting duck. The Verizon Data Breach Investigations Report consistently finds that stolen credentials are involved in a significant percentage of web application breaches.
**Reverse brute force:** Instead of trying many passwords against one account, the attacker picks one common password (like "admin123") and tries it against thousands of different usernames. This approach is harder to detect because each individual account only sees one failed attempt.
### The Two Entry Points Attackers Target
WordPress has two primary endpoints that accept authentication:
**wp-login.php:** Your standard login page. Every WordPress site serves it at the same URL by default. Bots know exactly where to find it, and it accepts unlimited login attempts unless you've configured something to stop them.
**xmlrpc.php:** This is the one most site owners overlook. XML-RPC is a legacy API that WordPress originally used for remote publishing (think: blogging from your phone back in 2008). The system.multicall method lets an attacker bundle hundreds of login attempts into a single HTTP request. That means rate limiting based on "one attempt per request" doesn't catch it. One XML-RPC request can test 500 passwords at once.
If you're not actively using XML-RPC (and unless you're using the WordPress mobile app or Jetpack's older features, you're probably not), it's an attack surface you can close entirely.
## Why WordPress Sites Are Disproportionately Targeted
WordPress runs roughly 40% of the web. That alone makes it the highest-value target for automated attack tools. But there's more to it:
**Predictable login URLs.** Every default WordPress installation serves its login form at /wp-login.php and its admin dashboard at /wp-admin/. Attackers don't need to discover where to send login attempts.
**The "admin" username legacy.** Older WordPress installations defaulted to "admin" as the primary username. Millions of sites still use it. Attackers know this, so "admin" is always the first username in their list.
**Plugin and theme vulnerabilities create footholds.** A successful brute force isn't always the end goal. Sometimes attackers use brute-forced credentials to install backdoors, inject SEO spam, or pivot to attacking other sites on the same server. The admin access is just the entry point.
**Low-cost, high-volume economics.** Running a brute force campaign costs an attacker almost nothing. Botnets, rented cloud instances, and free credential lists make it trivial to launch thousands of attacks simultaneously. Even a 0.1% success rate is profitable when you're targeting millions of sites.
## Signs Your Site May Be Under Attack
Brute force attacks aren't always obvious, especially if they're slow and distributed. But here are the indicators to watch for:
**Sudden spikes in server resource usage.** If your CPU and memory usage jumps without a corresponding increase in legitimate traffic, it could be bots hammering your login page.
**Slow page loads for legitimate visitors.** Each brute force login attempt consumes PHP workers, database queries, and server memory. A sustained attack can starve your actual visitors of resources, especially on sites running WooCommerce or membership plugins where every PHP worker matters.
**Failed login notifications flooding your inbox.** If you have a security plugin that sends email alerts on failed logins, a sudden flood of these is a clear signal.
**Unfamiliar IP addresses in your access logs.** Look for clusters of POST requests to wp-login.php or xmlrpc.php from IP ranges you don't recognize.
**Your hosting provider contacts you.** Some hosts will notice unusual traffic patterns and flag them. If your host tells you they're seeing abnormal login traffic, take it seriously.
## The Multi-Layer Defense Strategy
Here's the thing most brute force guides get wrong: they treat it as a single problem with a single solution. Install a plugin. Change your login URL. Done.
In reality, effective brute force protection works in layers. Each layer catches what the previous one might miss, and together they make a successful attack nearly impossible.
### Layer 1: Block Attacks at the Edge (Before They Reach Your Server)
This is the most important layer, and it's the one most WordPress sites don't have.
Every login attempt that reaches your server consumes resources. PHP has to boot, WordPress has to load, the database has to be queried to check credentials. Even failed attempts cost you CPU, memory, and PHP workers. During a sustained brute force campaign, those costs add up fast.
A Web Application Firewall (WAF) that operates at the CDN edge solves this problem at the source. It evaluates incoming requests at the network level, before they ever reach your origin server. Known attack patterns, malicious IPs, and high-velocity login attempts get blocked at one of hundreds of global edge nodes. Your server never processes the request. PHP never boots. WordPress never loads.
This is the difference between your server fighting off an attack and your server not even knowing there was one.
On Levamo, Enterprise Cloudflare is included on every plan. That means WAF protection, bot mitigation, and rate limiting run at the edge across 300+ global locations. There's no extra charge and no configuration required on your part. Brute force attempts get filtered before they consume a single PHP worker on your server.
For a deeper look at how edge-level WAF protection works, check out our guide on [Cloudflare WAF for WordPress](/blog/enterprise-cloudflare-cdn/).
### Layer 2: Rate Limiting Login Attempts
Even with a WAF in place, you want rate limiting as a second line of defense. Rate limiting caps how many login attempts a single IP address (or IP range) can make within a given time window.
**At the edge level:** Cloudflare's rate limiting can detect and throttle high-frequency requests to wp-login.php before they hit your server. This catches attackers who try to slip under the WAF's pattern-matching by slowing their attempts down.
**At the application level:** WordPress plugins like [Limit Login Attempts Reloaded](https://wordpress.org/plugins/limit-login-attempts-reloaded/ "nofollow") or the login protection built into [Wordfence](https://wordpress.org/plugins/wordfence/ "nofollow") can enforce per-IP lockouts after a set number of failed attempts. A common configuration is: lock out an IP for 20 minutes after 5 failed attempts, then increase the lockout duration for repeat offenders.
[](https://wordpress.org/plugins/limit-login-attempts-reloaded/ "nofollow")
[](https://wordpress.org/plugins/wordfence/ "nofollow")
The edge-level approach is always better because it prevents resource consumption. But application-level rate limiting catches anything that makes it through, so running both is ideal.
### Layer 3: Two-Factor Authentication (2FA)
Rate limiting slows down brute force attempts. 2FA makes them pointless.
Even if an attacker guesses your password (or obtains it from a data breach), they can't log in without the second factor. With authenticator-app-based 2FA, that second factor is a time-based code generated on your phone. The code changes every 30 seconds, and the attacker would need physical access to your device to get it.
This is why [2FA](/blog/two-factor-authentication-2fa/) is considered the single most effective defense against credential-based attacks. It doesn't just make brute force harder. It makes a successful password guess worthless.
A few important details on 2FA for WordPress:
**Use authenticator apps, not SMS.** SMS-based 2FA is vulnerable to SIM swapping attacks, where an attacker convinces your carrier to transfer your phone number to their SIM card. Authenticator apps (Google Authenticator, [Authy](https://authy.com/ "nofollow"), [1Password](https://1password.com/ "nofollow")) generate codes locally on your device and aren't tied to your phone number.
**Enforce it for all admin users, not just yourself.** The weakest link in your security is the team member who hasn't enabled 2FA. If you're running a membership site or WooCommerce store with multiple administrators, you need a way to require 2FA across the board.
On Levamo, the hosting dashboard supports authenticator-app 2FA with team-admin enforcement. That means account owners can require every team member to enable 2FA before they can access the hosting panel. This isn't just good security practice; it also supports PCI DSS 4.0.1 compliance requirements for multi-factor authentication, which matters if you're processing payments.
For WordPress itself, plugins like [WP 2FA](https://wordpress.org/plugins/wp-2fa/ "nofollow"), [Two-Factor](https://wordpress.org/plugins/two-factor/ "nofollow"), or [Wordfence Login Security](https://wordpress.org/plugins/wordfence-login-security/ "nofollow") add 2FA to your wp-login.php page. Most support authenticator apps and can enforce 2FA for specific user roles.
[](https://wordpress.org/plugins/wp-2fa/ "nofollow")
### Layer 4: Disable XML-RPC (If You Don't Need It)
As mentioned earlier, xmlrpc.php is a backdoor for brute force attacks that most site owners don't know exists. The system.multicall method lets attackers test hundreds of credentials in a single request, bypassing per-request rate limiting.
If you're not using XML-RPC (and most modern WordPress setups don't need it since the REST API replaced its functionality), you should block it.
**Option 1: Block at the server level.** For Apache servers, add this to your .htaccess file:
```apache
Order Deny,Allow
Deny from all
```
For Nginx:
```nginx
location = /xmlrpc.php {
deny all;
return 403;
}
```
**Option 2: Block at the edge.** If your site is behind Cloudflare (or any CDN with WAF rules), you can create a rule that blocks all requests to xmlrpc.php. This is the preferred approach because the request never reaches your server.
**Option 3: Use a plugin.** Plugins like [Disable XML-RPC](https://wordpress.org/plugins/disable-xml-rpc/ "nofollow") or the security settings in Wordfence can disable XML-RPC with a single toggle.
[](https://wordpress.org/plugins/disable-xml-rpc/ "nofollow")
One caveat: if you use [Jetpack](https://jetpack.com/ "nofollow"), the WordPress mobile app, or any tool that relies on XML-RPC for remote publishing, disabling it will break those features. Check first, then disable.
### Layer 5: Password and Username Hardening
This is the foundation layer. No amount of WAF protection or rate limiting matters if your admin password is "password123."
**Use strong, unique passwords.** A strong password is at least 16 characters, includes a mix of uppercase, lowercase, numbers, and symbols, and isn't reused anywhere else. Use a password manager (1Password, [Bitwarden](https://bitwarden.com/ "nofollow"), or the browser's built-in one) to generate and store passwords. You shouldn't know your own WordPress password by heart, because if it's memorable, it's probably guessable.
**Never use "admin" as a username.** If your site still has an "admin" user, create a new administrator account with a unique username, transfer all content to it, then delete the old "admin" account. Attackers try "admin" first because they know it works on millions of sites.
**Remove unused admin accounts.** Every administrator account is a potential target. If a team member leaves or a developer's temporary account is no longer needed, remove it. Fewer admin accounts means fewer attack surfaces.
### Layer 6: Change the Default Login URL (Optional but Useful)
Changing your login URL from /wp-login.php to something custom (like /my-secret-login) doesn't stop a determined attacker, but it does eliminate the bulk of automated bot traffic that targets the default URL.
Plugins like [WPS Hide Login](https://wordpress.org/plugins/wps-hide-login/ "nofollow") let you change the login URL with a single setting. It's security through obscurity, which means it should never be your only defense. But as an additional layer on top of everything above, it meaningfully reduces the volume of junk requests your other defenses have to process.
[](https://wordpress.org/plugins/wps-hide-login/ "nofollow")
## What Most Guides Miss: The Server Resource Problem
Here's something most brute force protection articles don't talk about: even blocked attacks cost you resources if they're blocked at the wrong level.
When a brute force bot hits your login page and your WordPress security plugin blocks it, here's what happened before the block:
1. The HTTP request traveled across the internet to your server
2. Your server accepted the TCP connection
3. PHP booted up
4. WordPress loaded (core files, active plugins, active theme)
5. The security plugin initialized
6. The plugin checked the request against its rules
7. The plugin returned a 403 (blocked)
That's a lot of server resources spent on a request you never wanted. Now multiply that by 10,000 attempts per hour during an active campaign. Your legitimate visitors, the people trying to buy products, access their course, or log into their membership, are competing with bots for the same PHP workers and database connections.
This is why Layer 1 (edge-level WAF) isn't just the first defense. It's the one that protects your site's performance, not just its security.
On Levamo, because Cloudflare's WAF sits in front of your server, brute force traffic is absorbed at the edge. Your LiteSpeed server, your PHP workers, your KeyDB/Redis object cache, and your MariaDB database stay focused on your actual visitors. It's the difference between your store's checkout flow stuttering during an attack and your visitors not noticing anything at all.
This matters most for sites running dynamic, logged-in workloads: WooCommerce stores processing orders, membership platforms serving gated content, LMS sites delivering courses. These applications need every PHP worker they can get. An edge-level WAF ensures bots don't steal them.
## A Quick Brute Force Protection Checklist
Here's a summary you can reference when hardening your site:
| Defense Layer | What It Does | Where It Runs |
|---|---|---|
| Edge WAF (Cloudflare) | Blocks known attack patterns before they reach your server | CDN edge (300+ locations) |
| Rate limiting | Caps login attempts per IP within a time window | Edge + application level |
| Two-factor authentication | Makes guessed passwords useless without a second factor | WordPress login + hosting dashboard |
| Disable XML-RPC | Closes the system.multicall backdoor for bulk credential testing | Server config or edge rule |
| Strong passwords | Eliminates dictionary attacks and common password guessing | User behavior + password manager |
| Unique usernames | Removes the default "admin" target | WordPress user management |
| Custom login URL (optional) | Reduces automated bot traffic to login page | WordPress plugin |
No single layer is bulletproof. The combination is what makes brute force attacks a non-issue.
## Wrapping Up
Brute force attacks are common, persistent, and entirely preventable. The key is layering your defenses so each one catches what the previous might miss: edge-level filtering absorbs the bulk of attack traffic before it touches your server, rate limiting throttles what slips through, 2FA renders stolen passwords useless, and basic hygiene (strong passwords, no "admin" username, disabled XML-RPC) eliminates the easy wins attackers rely on.
The biggest mistake site owners make isn't ignoring brute force protection entirely. It's relying on a single plugin that processes every malicious request at the application level, burning server resources in the process. The goal isn't just to block attacks. It's to block them efficiently, in a way that doesn't degrade performance for your actual visitors.
For a broader overview of WordPress security beyond brute force, check out our [WordPress security best practices guide](/blog/best-wordpress-security-plugins/).
---
## You Can Now Manage Your WordPress Site with AI: WPVibe Is Live on Levamo
- URL: https://levamo.com/blog/manage-your-wordpress-site-with-ai-wpvibe/
- Category: news
- Author: The Levamo Team
- Published: 2026-08-11
Connect ChatGPT, Claude, or Cursor to your WordPress site and manage it by chatting.
There's a new tab in your Levamo dashboard today: **AI Management**. Connect a site once, and the AI assistant you already use, whether that's ChatGPT, Claude, or Cursor, can create, update, and understand your WordPress site through a simple conversation.
No new dashboard to learn, nothing to install yourself, no passwords to copy out of wp-admin. You say what you want in plain English, and the work lands on your site.
Under the hood, AI Management is powered by [WPVibe](https://wpvibe.ai/), which connects WordPress sites to AI assistants through MCP, the open standard that lets AI tools work with other software. On Levamo it's built directly into your dashboard, so connecting a site takes a couple of clicks instead of a developer project.
## What You Can Ask It to Do
Once a site is connected, you brief your AI the way you'd brief a team member:
- **"Draft our Black Friday post and schedule it for Monday."** The post shows up in WordPress as a scheduled draft, with the SEO title and meta description already filled in.
- **"Update all our plugins."** Your assistant updates them one at a time, checks the site after each one, and logs the changes for your review.
- **"Redesign our homepage, make it feel modern."** The new version is saved as a draft with a preview link. Your live homepage stays untouched until you approve it.
- **"Change blog permalinks to /blog/post-name."** The structure changes, and 301 redirects are added from every old URL.
It covers the parts of WordPress you actually touch: posts and pages, media, plugins and themes, WooCommerce, SEO, even theme files. And it works alongside the tools you already build with, including Elementor and Divi.
## Works with the AI You Already Use
You don't have to adopt a new chatbot. AI Management meets you in whichever assistant is already open on your screen.
The dashboard includes step-by-step connection instructions for five clients: **Claude.ai**, **Claude Desktop**, **Claude Code** (a single terminal command), **ChatGPT** (via the WPVibe app in ChatGPT's app directory), and **Cursor**. Using Gemini, Grok, Perplexity, or another MCP-compatible assistant? WPVibe's [setup guides](https://wpvibe.ai/docs/ai-client-setup/) cover those too.
The flow is the same everywhere: copy your site's connection URL from the dashboard, paste it into your assistant, and sign in with your email. A 6-digit code arrives with the code right in the subject line, so there's no link to hunt for.
## Safe by Design
Letting an AI touch a live site is a real decision, so the whole system is built draft-first:
- **New content lands as drafts.** Posts and page redesigns wait for your review; nothing goes live without you.
- **Deletes go to trash**, so nothing disappears permanently by accident.
- **Destructive operations require your approval** before they run, with a preview of what will change.
- **Changes are logged**, so you can always review what your assistant did.
The connection itself is locked down too. WPVibe signs in to your site with a dedicated, automatically managed application password that only WPVibe stores. You never see it, you never handle it, and disconnecting the site revokes it.
Connections are also personal: each team member connects with their own WordPress admin account. Disconnecting yourself removes your access only, and you can connect again at any time.
## How to Connect a Site
1. Log in to your [Levamo dashboard](https://my.levamo.com), open a site, and click **AI Management**.
2. Create a **Platform API key** with the name and expiry you want, or choose one you already have.
3. Click **Connect**. We verify the site with WPVibe and install the connector for you, so there's nothing to set up inside WordPress.
4. Follow the three steps on the **Instructions** tab: copy your connection URL, add it to your assistant, and paste in the ready-made first prompt.
That first prompt is worth a mention. It's pre-filled with your site's address and asks your assistant to confirm the connection, look around read-only, and come back with a first-run overview: what it found, what it can do on this site, the most important improvements, and the safest first action. It changes nothing on the site; it just introduces your assistant to it.
One more detail: if a restore, clone, or migration ever removes the connector plugin, the AI Management tab notices and offers a one-click **Repair connection** that reinstalls it using the credentials we already hold. No starting over.
## API Keys for Your Team
AI Management runs on a new account-level feature that's useful in its own right: **API keys**, now in your account settings.
- **Keys are per team**, and each one acts as your current role on that team. Change someone's role and their keys follow automatically.
- **You choose the expiry**: 30, 90, 180, or 365 days, or never.
- **The full key is shown exactly once**, at creation. Copy it and store it somewhere safe.
- **Rotate or revoke at any time.** Before you confirm, the dialog names the exact sites that will be disconnected, so you know the impact before you click, not after.
Team owners and administrators also get two new permissions to grant: one for managing sites with AI assistants, and one for managing API keys. Access is opt-in per member, and the team roster now shows at a glance who has which.
## Available Today
AI Management is live in your dashboard now. Log in, open a site, click **AI Management**, and connect.
The first thing to try: paste the starter prompt from the Instructions tab. Your assistant will introduce itself to your site, tell you what it can do, and suggest a safe place to start.
---
## WordPress Security Headers: How to Add Them and Why They Matter
- URL: https://levamo.com/blog/wordpress-security-headers/
- Category: website-security
- Author: Shahzeb Ahmed
- Published: 2026-08-10
Add the WordPress security headers that block XSS, clickjacking, and more.
You've installed an SSL certificate. You've set up [two-factor authentication](/blog/two-factor-authentication-2fa/). You're running a firewall. And you still might be leaving one of the biggest security gaps wide open.
Security headers are HTTP response headers your server sends to the browser before any page content loads. They tell the browser what's allowed and what isn't: which scripts can run, whether your site can be embedded in a frame, how cookies should be handled. Without them, you're relying entirely on the browser's default behavior, and browsers are generous by default. They'll load third-party scripts, allow framing, and trust whatever content type a file claims to be.
That generosity is exactly what attackers exploit.
The good news? Adding security headers to a WordPress site takes about ten minutes. And once they're in place, they work silently in the background, blocking entire categories of attacks before they even reach your application layer.
## What Security Headers Actually Do
Every time someone visits your site, your server sends back a response. That response includes the page content (HTML, CSS, JavaScript) plus a set of headers, small instructions the browser reads before rendering anything.
Most headers are mundane: content type, cache duration, server software. But a handful of them are specifically designed to prevent attacks. These are your security headers.
Think of them as rules you're handing to the browser: "Don't load scripts from domains I haven't approved." "Don't let anyone embed my site in an iframe." "Always use HTTPS, even if someone types http://." The browser enforces these rules on every single page load, which means attackers can't bypass them with clever JavaScript or social engineering.
Here's why this matters for WordPress specifically: WordPress sites tend to run a lot of third-party code. Themes, plugins, analytics scripts, payment processors, chat widgets. Each one is a potential vector for cross-site scripting (XSS) or data injection. Security headers don't replace keeping your plugins updated, but they add a layer of protection that catches what your other defenses might miss.
## The Six Headers That Actually Matter
There are dozens of HTTP headers you could set, but six of them carry the most weight for WordPress sites. Let's go through each one.
### 1. Strict-Transport-Security (HSTS)
**What it does:** Forces browsers to connect over HTTPS, even if someone types http:// or clicks an old HTTP link.
**Why it matters:** Without HSTS, there's a brief window during the first connection where an attacker could intercept an unencrypted request and redirect the visitor (a man-in-the-middle attack). HSTS eliminates that window entirely after the first visit.
**Recommended value:**
```
Strict-Transport-Security: max-age=31536000; includeSubDomains; preload
```
The max-age is in seconds (31536000 = one year). includeSubDomains applies the rule to every subdomain. preload lets you submit your domain to browser preload lists, so even the very first visit is forced to HTTPS.
**Important:** Only enable HSTS after you've confirmed SSL works correctly across your entire site. If anything is still served over HTTP (mixed content), HSTS will break those resources instead of silently loading them.
If you're on Levamo, free [SSL certificates](/blog/ssl-website-security/) are issued automatically and renewed on every plan, so you're already set on that front.
### 2. Content-Security-Policy (CSP)
**What it does:** Controls exactly which sources the browser is allowed to load resources from: scripts, styles, images, fonts, frames, and more.
**Why it matters:** CSP is the single most powerful header against cross-site scripting. If an attacker injects a malicious script tag into your page, the browser checks the CSP policy. If the script's source isn't on the approved list, it doesn't execute. Period.
**Example (starter policy):**
```
Content-Security-Policy: default-src 'self'; script-src 'self' https://cdn.example.com; style-src 'self' 'unsafe-inline'; img-src 'self' data: https:; font-src 'self' https://fonts.gstatic.com; frame-ancestors 'none'
```
**A word of caution:** CSP is the most powerful security header, but also the easiest to get wrong on WordPress. Plugins and themes routinely inject inline scripts and styles, and a strict CSP will block them. Start with Content-Security-Policy-Report-Only to log violations without breaking anything:
```
Content-Security-Policy-Report-Only: default-src 'self'; script-src 'self' 'unsafe-inline'; report-uri /csp-report-endpoint
```
Monitor the reports for a week, adjust your policy, then switch from Report-Only to the enforced header.
### 3. X-Content-Type-Options
**What it does:** Prevents the browser from "sniffing" the content type of a response. If your server says a file is text/plain, the browser treats it as text, not as executable JavaScript.
**Why it matters:** Without this header, an attacker could upload a file with a .jpg extension that's actually a script. The browser might detect the real content type and execute it. This header stops that behavior.
**Recommended value:**
```
X-Content-Type-Options: nosniff
```
There's only one valid value. Set it and forget it.
### 4. X-Frame-Options
**What it does:** Controls whether your site can be embedded inside an `
## What We Covered
The three of us traded real examples from our own businesses about where AI is genuinely saving time and where it's not worth the effort. Here are some of the topics we dug into:
- **Internal tooling over external features**: Why building custom internal systems with AI might be the most overlooked opportunity for product companies
- **Replacing generic tools**: When it makes sense to build custom solutions instead of using off-the-shelf SaaS
- **Small team advantages**: How AI lets small teams run leaner without dedicated ops staff
- **Trade-offs and lessons learned**: The honest truth about what works and what doesn't
## Why This Matters for Product Companies
If you're building a WordPress product, SaaS, or any tech business and feel buried under internal processes, this episode offers a practical look at how AI can help you operate more efficiently and at lower costs, without adding chaos to your workflows.
Katie and Matt both shared their own experiences, which made for a great exchange of ideas. It's refreshing to have these kinds of operational conversations in the WordPress community.
## Watch the Full Episode
The full conversation is available on the [WP Product Talk YouTube channel](https://www.youtube.com/watch?v=-yQeIdt1tPs). I had a great time on the show, and I think you'll find some actionable insights whether you're building plugins, themes, or other WordPress products.
Big thanks to Katie and Matt for having me on. If you're interested in WordPress product strategy, definitely subscribe to WP Product Talk. They bring on great guests and tackle topics that matter to product founders and marketers.
---
## MasterStudy LMS and Levamo: A Powerful Team for High-Performance eLearning
- URL: https://levamo.com/blog/hosting-masterstudy-lms-with-rapyd-cloud/
- Category: lms
- Author: Shahzeb Ahmed
- Published: 2026-01-27
Boost eLearning with MasterStudy LMS and Levamo. Faster, more reliable!
Building a successful online learning platform takes more than great content. Speed, reliability, scalability, and user experience play a crucial role in how learners perceive your courses and whether they decide to enroll. The collaboration between MasterStudy LMS and Levamo marks a major step forward for educators, businesses, and institutions running WordPress-based eLearning platforms.
Together, [MasterStudy LMS](https://stylemixthemes.com/wordpress-lms-plugin/) and Levamo provide a high-performance solution that removes technical barriers and lets course creators concentrate on what matters most: teaching, growing, and scaling their online education business.
## What is MasterStudy LMS?
[MasterStudy LMS](/blog/masterstudy-lms-review/) is a powerful, all-in-one WordPress solution that helps anyone build, manage, and grow a professional eLearning platform. From the first lesson to final certification, MasterStudy LMS provides everything needed to create a full-featured online school with multiple courses, instructors, and learners.
With tools like a drag-and-drop course builder, interactive quizzes, video lessons, assignments, live classes via Zoom or Google Meet, and advanced grading, creating engaging learning experiences becomes simple and intuitive. Features such as customizable certificates, detailed reports and analytics, AI-powered course creation, and ready-made website templates further streamline course development while maintaining a polished, professional look. MasterStudy LMS also includes built-in WooCommerce integration, memberships, subscriptions, and tax management, making it easy to monetize content globally with flexible pricing and recurring payments.
MasterStudy LMS serves a wide range of users: educators and tutors launching independent courses, businesses scaling employee training, coaches delivering structured programs, educational institutions extending beyond physical classrooms, and entrepreneurs turning expertise into automated, income-generating courses.
## Why Hosting Matters for MasterStudy LMS
MasterStudy LMS is a dynamic system where learners are constantly logged in, watching lessons, taking quizzes, submitting assignments, making payments, and tracking progress in real time. This creates server demands that traditional hosting, built for static content, often struggles to handle.
The result of underpowered hosting: slow dashboards, delayed quiz submissions, failed checkouts, and poor learner experiences that cost you enrollments and refunds.
This is exactly where Levamo steps in.

## Build High-Performance Online Courses with MasterStudy LMS
Launch and scale your WordPress eLearning platform with MasterStudy LMS, optimized for speed, quizzes, payments, and student engagement on **Levamo.**
**[Explore MasterStudy LMS](/masterstudy-lms-hosting/)**
## What is Levamo?
Levamo is a managed cloud hosting platform built specifically for dynamic WordPress websites, with a focus on Learning Management Systems, membership sites, and interactive communities. Unlike traditional hosting optimized for static content like blogs and brochures, Levamo was engineered by the team behind BuddyBoss, who spent years scaling platforms with thousands of concurrent logged-in users.
For MasterStudy LMS users, this matters. Almost every learner action (watching a lesson, submitting an assignment, taking a quiz, earning a certificate) triggers database queries and server processes. On generic hosting, these actions can slow down your site, cause quiz timeouts, and frustrate students. Levamo's infrastructure handles these workloads seamlessly.
**The technical foundation includes:**
- **LiteSpeed servers** that outperform [Apache and Nginx](/blog/apache-vs-nginx-wordpress/) for dynamic PHP workloads
- **KeyDB object caching** that reduces database load for logged-in users, exactly where most hosts struggle
- **MariaDB optimization** tuned for the complex queries LMS plugins generate when tracking progress and calculating grades
- **Global CDN** is included, so the course content loads fast regardless of the student's location
**On-demand performance** boosts for launches and live events without changing plans
## Key Benefits of Levamo for MasterStudy LMS
**Exceptional Speed for Learners and Admins.** Lessons load instantly, quizzes respond without delay, and learner dashboards remain smooth even during peak usage. The WordPress admin area stays fast, so instructors can manage courses, students, and content efficiently.
**Easy Scalability.** Expecting a cohort launch or live event? Levamo lets you scale resources on demand without migrating to a new plan.
**Enterprise-Grade Security.** Multi-layer protection, including DDoS mitigation, firewall protection, and proactive malware scanning, keeps your platform and student data safe. MasterStudy Dashboard Integration. Levamo includes MasterStudy-specific tools directly in the hosting dashboard, making it easier to install MasterStudy without jumping between systems.
**Free White-Glove Migration.** Levamo's team handles your site transfer, tests everything, and ensures performance before switching DNS. Zero downtime, no technical headaches on your end.
## Who Should Consider This Partnership
This combination makes the most sense if you're experiencing slow performance when multiple students are active simultaneously, quiz submissions that fail or timeout, complaints about buffering or slow page loads, or if you're planning to scale your course offerings and student base.
## Get Started
Whether you're an independent instructor, training company, educational institution, or digital entrepreneur, the MasterStudy and Levamo partnership removes the most common technical challenges so you can focus on sharing and monetizing your knowledge.
---
## The Best Online Business Tools For Success in 2026
- URL: https://levamo.com/blog/best-online-business-tools/
- Category: online-business
- Author: Sunyyan Junaid
- Published: 2026-01-27
Succeed in 2026! Top online business tools revealed for e-commerce and more.
If you are looking for the best online business tools in 2026, then this is a must-read for one simple reason:
What worked well just 2 years ago may not yield the same results anymore.
In online marketing, the only thing constant is change. If you don’t adapt to the latest [web hosting trends](/blog/web-hosting-trends/), you are bound to fail in 2026.
That’s why we’ve compiled this guide of the best online business tools in 2026. Our team has carefully reviewed picks, which means our views are based on personal experiences and extensive use to help you make smarter decisions.
Our selection criteria was focused on platforms that excel at data analysis, customer relationship management (CRM), seamless integrations, and the ability to leverage AI for personalized marketing and support.
We have broken down these tools into the following categories:
## E-Commerce Platforms
By 2027, e-commerce is projected to grab a 41% share of retail sales. US Retail online sales exceeded $1.0 trillion in 2023. If you are in the retail industry, now is the time to sell online. To do so, here are three platforms ready to transform your online experience:
### WooCommerce

Leveraging the power of open source, WooCommerce offers extensive customization and control for online stores. It is the most popular plugin that transforms WordPress websites into powerful e-commerce shops. Paired with Levamo, this is a match made in heaven for online stores determined to deliver outstanding user experience each and every time.
**Key Features:**
- Open-source platform, highly customizable with themes and plugins
- Wide range of extensions for various functionalities (subscriptions, bookings, memberships)
- Flexible product management and secure payment gateways
- Built-in SEO optimization
- Integration with WordPress.
**Why does it matter in 2026?**
WooCommerce will see further development in headless commerce solutions, allowing for more flexible front-end development, improved API integrations for seamless data exchange, and enhanced security features to combat evolving cyber threats.
Unlike other platforms where you have to buy individual subscriptions for each store, with Levamo, you can run multiple stores in one cloud hosting account. This makes WooCommerce extremely cost-effective [compared to Shopify](/blog/woocommerce-vs-shopify/) and other platforms.
Users: 8+ million
User Reviews: 4.5/5.0
### Shopify

Shopify has become a household name among online store owners as the most affordable and easiest way to [create online store](https://upstore.cloud/ecommerce) and launch a business with no required knowledge of coding. It provides a complete e-commerce solution, encompassing everything from website building and hosting to payment processing and order fulfillment. Whether you’re into dropshipping, wholesaling, or just want an online store with all the bells and whistles, then Shopify is an option made for you.
**Users:** 4.5+ million
**Reviews:** 2.3 stars on Trustpilot
**Key Features:**
- Drag-and-drop website builder and customizable themes
- App store with thousands of extensions
- Integrated payment gateway (Shopify Payments, Stripe, Paypal, 2Checkout, and many more)
- Inventory management and shipping integrations
- Marketing tools (email marketing, social media integration)
- Analytics dashboards and 24/7 support.
**Why does it matter in 2026?**
Shopify's focus will likely be on enhanced omnichannel capabilities, integrating online and offline sales seamlessly, advanced AI-powered personalization, and augmented reality (AR) shopping experiences.
### PaymentForm.io
[PaymentForm.io](https://paymentform.io/ "nofollow") is a SaaS platform built to help businesses create payment forms and collect money online in minutes, without needing a developer or a full store setup. It works well for freelancers, small businesses, nonprofits, event organizers, creators, and other organizations that need to accept one-time or recurring payments without building a full website.
**Key Features:**
- Form-based checkout platform for collecting payment
- Support for one-time payments, subscriptions, donations, event management, and fundraising campaigns
- Membership and recurring billing support built in
- Multiple payment gateway integrations (Stripe, PayPal, Square, Mollie, and more)
- Customer Portal for order and payment history
- Embed forms on any website or share via direct link
- Built-in page builder included to create landing pages
- No coding required to launch a payment form
**Users:** Growing user base among freelancers and small businesses
**Reviews:** 4.9/5
**Why does it matter in 2026?**
Not every online transaction requires a complete e-commerce store. A freelancer collecting a deposit, a nonprofit accepting donations, an organizer selling event tickets, or a business charging a membership fee may only need a focused checkout and a way to collect the relevant customer information. PaymentForm.io is designed for these situations, providing a form-based alternative to setting up and maintaining a full online store.
### BigCommerce

If you already run a well-established business but want enterprise-like features, then BigCommerce is for you. It is similar in nature to Shopify with its drag-and-drop online store-building experience.
**Key Features:**
- Advanced product catalog management
- Multi-channel selling (Amazon, eBay, social media)
- SEO tools, analytics, and reporting
- Integration of multiple payment gateways
- Enterprise-grade security alongside
- Zero transaction fees
**Users:** 90,000+
**Reviews:** 1.4 stars on Trustpilot
**Why does it matter in 2026?**
BigCommerce will presumably focus on further enhancing its headless commerce capabilities, providing advanced APIs and developer tools, improving internationalization features for global expansion, and leveraging AI for marketing automation.
## Marketing and Content Creation Tools
In a cutthroat competitive world, growing an online business is impossible without utilizing the right digital marketing tools that help increase your visibility, raise brand awareness, and generate sales.
Let’s shed light on some of the best online business tools for digital marketing, that your money can buy.
### HubSpot

A marketing automation platform designed for medium to large businesses, you can use HubSpot to track leads, automate sales, and manage business relationships through proactive inbound marketing. Here are the key features and 2026 predictions:
**Key Features:**
- CRM
- Marketing automation (email marketing, workflows, lead nurturing)
- Content management system (CMS)
- Social media management and SEO tools
- Landing page builder
- Analytics dashboards and sales tools.
**Users:** 205,000+
**Reviews:** 2.7 stars on Trustpilot
**Why does it matter in 2026?**
HubSpot will likely focus on integrating AI into its platform for enhanced compliance with GDPR, UK GDPR, and several other compliance laws and tool kits. This will allow businesses to focus on expansion and reducing legal complexities as they scale.
### Jasper

An AI-powered tool, Jasper helps marketers and writers overcome writer’s block and generate all sorts of content, from marketing copy and blog posts to social media updates and product descriptions. It works similarly to ChatGPT and Gemini, with the caveat of hundreds of templates for digital marketers that they can choose from to generate content. While other generative AI content tools are good for generalized assistance, Jasper specifically focuses on creating content for digital marketing teams.
**Key Features:**
- AI-powered content generation
- Multiple templates for different content types
- Tone of voice customization
- Plagiarism checker
- Integration with other marketing tools.
**Users:** 70,000+
**Reviews:** 4.1 on Trustpilot
**Why does it matter in 2026?**
Jasper and similar tools will become even more sophisticated, with improved natural language processing (NLP) capabilities and the ability to generate more complex and nuanced content. If you have a big marketing team and need to speed up content writing efforts, then Jasper could be a valuable addition.
### Mailchimp

Evolving from an email marketing platform, Mailchimp is a full-fledged marketing automation suite that is extremely easy to use. It’s a popular choice among digital marketers and entrepreneurs looking to reach their targeted audience without hassle. For small to medium businesses, Mailchimp offers an array of marketing automation features, providing quality results at affordable prices.
**Key Features:**
- Email marketing campaigns
- Audience management and segmentation
- Marketing automation workflows
- Landing page builder
- Analytics dashboards
**Users:** 11+ million
**Reviews:** 1.3 on Trustpilot
**Why does it matter in 2026?**
In 2026, Mailchimp will work on improving its AI features for better segmentation and targeting, allowing business owners to make more granular data-driven decisions.
## Project Management and Collaboration Tools
Efficient teamwork is the backbone of any successful business. The following tools will help you to streamline workflows, automate tasks, and utilize time productively. Fun fact: these are also the same tools that we at Levamo use!
### Trello

Using a visual Kanban board system for project management and task tracking, Trello allows you to effortlessly collaborate on any project through boards, lists, and cards. It comes with a free plan and great UI/UX, making it easy for you to drag and drop tasks.
**Key Features:**
- Kanban boards with lists and cards
- Drag-and-drop interface
- Task assignments with due dates
- File attachments
- Integrations with other tools and mobile apps.
**Users:** 50 million+
**Reviews:** 3.3 on Trustpilot
**Why does it matter In 2026?**
Trello will focus on enhancing its automation capabilities, providing more advanced workflows and integrations with [AI-powered task management tools](https://techiefied.com/best-ai-tools-for-twitter-growth/). However, these features are only available on premium and enterprise plans.
### Slack

As a popular web-based communication platform, Slack is used by businesses of all sizes. It allows for better collaboration with teams by organizing information into different channels. You can assign each channel with a new project to track its progress. Although it has paid plans, the free plan provides features sufficient for most businesses. In general, Slack provides a more casual approach to internal communication than Skype or Teams, making task management easier than ever.
**Key Features:**
- Channels for organized communication
- Direct messaging and file sharing
- Integrations with other tools (Google Drive, Trello, Asana)
- Voice and video calls
**Users:** 38.8+ million+
**Reviews:** 4.5 on Capterra
**Why does it matter in 2026?**
Slack will continue enhancing its AI-powered features for message summarization, sentiment analysis, and automated task creation. It will also tweak its search function, allowing you to interact with it as a team member.
### Discord

Originally popular in gaming communities, Discord facilitates real-time interaction through text, voice, and video chat within organized spaces called servers. Over the years, it has become the go-to tool for businesses to improve their communication with customers in a more informal way than using emails and help desk support.
**Key Features:**
- Servers and Channels for organized communities
- High-quality voice and video chat
- Direct messaging and file sharing
- Screen sharing and streaming
- Bot integrations for automation and moderation
**Users:** 200 Million+
**Reviews:** 4.7 on Capterra
**Why does it matter in 2026?**
These days, customers are more likely to engage with businesses that have informal and open channels of communication to resolve problems.
## Customer Service and Support Tools
The way you respond to your customers is often the most critical differentiating factor between your business and the competitors. From timely resolution of queries to providing educational content, everything is connected with how well you serve your customers. Here are some customer service and support tools to help you along the way:
### Zendesk

Zendesk provides a comprehensive customer service platform with tools for ticketing, live chat, and knowledge base management. It is one of the most powerful options on the market with multiple features and excellent customer support even as you grow your business. Its suite of workforce engagement management tools allows businesses to streamline workflows and improve business productivity.
**Key Features:**
- Ticketing system
- Live chat and knowledge base
- Customer portals
- Reporting and analytics
- Integrations with other tools (Salesforce, Shopify) and mobile apps.
**Users:** 200,000+
**Reviews:** 4.1 on Capterra
**Why does it matter in 2026?**
Zendesk has already become an AI platform for businesses to deliver world-class customer support. It is likely to further invest in AI to improve its services for clients.
### Zoho

Similarly, Zoho also offers a suite of business applications, including a customer service platform with tools for ticketing, live chat, and knowledge base management. Its competitive pricing makes it an affordable option compared to some other platforms like Salesforce or Zendesk, specifically tailored for small to medium-sized businesses. However, it has fewer customization options compared to Zendesk.
**Key Features:**
- Ticketing system
- Real-time support and self-service options for customers
- Dedicated space for customers
- Insights and reporting
- Integrations with other Zoho apps and third-party tools
**Users:** 100 Million+
**Reviews:** 4.2 on Trustpilot
**Why does it matter in 2026?**
Expect Zoho to enhance its AI capabilities and make more budget-friendly options for businesses of all sizes.
### CallFluent
[CallFluent](https://callfluent.com/) is an AI-powered phone call automation platform designed to streamline voice communication for businesses. With smart conversational agents and a no-code builder, it’s ideal for companies looking to scale customer engagement without increasing human resources. Its deep integration capabilities and multilingual support make it a strong alternative to traditional call center software.
**Key Features:**
- Conversational AI agents for natural-sounding calls
- No-code drag-and-drop call flow builder
- Real-time call monitoring and analytics
- CRM & API integrations (Salesforce, HubSpot, and more)
- Multilingual support for global operations
- Compliance-focused with secure data handling
**Users:** Actively used by businesses across industries like healthcare, real estate, and finance
**Reviews:** 4.5 on G2 (estimated based on features and comparisons)
**Why does it matter in 2026?**
As businesses prioritize automation and personalized customer experiences, CallFluent leads the way with scalable, AI-driven voice agents - reducing operational costs while improving customer satisfaction.
## Website Performance and Analytics
Understanding website performance and user behavior is crucial for building and growing a solid online presence. The following tools allow you to do just that.
### Google Analytics

One of the best online business tools, Google Analytics, provides detailed insights into website traffic, user behavior, and conversions. This is a free tool provided by Google and should be used by every website owner for a detailed website traffic analysis. Now at its fourth generation (GA4), it uses event-based data instead of session-based (and all sorts of things) to provide better insights into how users interact with your website.
**Key Features:**
- Website traffic analysis
- User demographics and behavior
- Conversion tracking
- Custom reports and integrations with other Google products (Google Ads, Google Search Console) and mobile apps.
**Why does it matter in 2026?**
With every product that Google has in its arsenal, Analytics will keep on getting updates throughout the year, providing clearer and better insights into website traffic and user behavior. AI is also going to change the way you notice these behaviors.
### Ahrefs

A complete SEO tool, Ahrefs helps businesses improve their search engine rankings. As one of the most popular and premium solutions, it offers every possible advanced feature for website owners to make data-driven decisions. From competitor insights to actionable key steps, Ahrefs is like having your own dedicated digital marketing manager.
**Key Features:**
- Keyword research
- Competitor and backlink analysis
- Site audits
- Rank tracking
- Actionable steps to improve SEO
**Users:** 49,000+
**Reviews:** 4.5 on Gartner
**Why does it matter in 2026?**
For its premium members, Ahrefs keeps on adding powerful functionalities such as paraphrasing, content generation, and a whole suite of marketing intelligence software. In 2026, it will likely invest more in AI-enabled features to allow business owners to make more quality decisions.
### Semrush

Semrush is similar to Ahrefs but focuses on a more comprehensive suite of tools, including SEO, paid advertising, social media management, and content marketing features. This makes it great for businesses looking to leverage paid marketing platforms for the best ROI, whereas Ahrefs is suited for organic reach, site audits, and backlink tracking.
**Key Features:**
- Keyword and advertising research
- Competitor analysis
- Site audits
- Rank tracking
- Social media management
- Market explorer
**Why does it matter in 2026:**
If you are looking to expand your reach in paid marketing, then Semrush provides premium tools at your disposal. However, do note that at the time of writing, there are no free plans.
**Users:** 1.1+ Million
**Reviews:** 4.5 on G2
### Levamo
[Levamo](/) provides scalable, reliable, and powerful cloud hosting infrastructure, ensuring website uptime and performance. We cater to a variety of needs, including WordPress hosting, and offer a platform for businesses to host dynamic websites with content that requires scalable resources - all without compromising your budget.
**Key Features:**
- High availability of infrastructure
- Scalable resources
- Superb security measures
- Various hosting options (including optimized WordPress hosting) and APIs for integration.
- 24/7 managed hosting for WordPress support
**Users:** 10,000+
**Reviews:** 4.8 on Trustpilot
**Why does it matter in 2026?**
Shared hosting does not work anymore for hosting dynamic websites. With our experience in the cloud hosting industry, Levamo is constantly investing and evolving its infrastructure to ensure superior user experiences and provide you the best managed WordPress hosting experience.
## Why These Tools Are Game-Changers for 2026?
There are three major reasons why the aforementioned tools should be part of your tech stack:
- **Scalability:** By automating processes, businesses can handle increased demand without significantly skyrocketing overheads.
- **Improved Customer Retention:** Through personalized experiences and exceptional customer service, companies can build stronger customer relationships.
- **Enhanced Productivity:** By streamlining workflows and improving communication, teams work more efficiently and deliver better results.
## Wrapping it up
Ready to take your business to the next level? Explore the power of Levamo and discover how it can transform your online business.
---
## Built for WooCommerce: Fast, Scalable, and Engineered for Growth
- URL: https://levamo.com/blog/built-for-woocommerce-fast-scalable-and-engineered-for-growth/
- Category: ecommerce
- Author: Michael Eisenwasser
- Published: 2026-01-12
WooCommerce slow? See how our hosting solves speed and scaling problems.
Before building Levamo, our team spent years working with **large-scale WordPress and WooCommerce sites through BuddyBoss** - a community platform powering thousands of businesses around the world. Through that experience, we saw a recurring problem: store owners doing everything right on the software side but still struggling with slow checkouts, unstable performance, and scaling bottlenecks.
It became clear the issue wasn’t with WooCommerce itself - it was the hosting layer underneath. Most infrastructure simply wasn’t designed for real-time cart updates, database-heavy product catalogs, or flash-sale traffic surges.
That’s what inspired us to build **Levamo**, a hosting platform engineered specifically for WordPress sites that rely on WooCommerce and other performance-intensive plugins.
We designed it for **growing WooCommerce stores and ambitious WordPress businesses** that want enterprise-grade speed and reliability without the complexity.
## The Challenge with WooCommerce Hosting
Most WordPress hosting still treats WooCommerce like a plugin - an afterthought running on top of a generic stack. But WooCommerce isn’t just another plugin. It’s an entire application layer handling real-time inventory, payments, and cart sessions. Traditional setups buckle under the weight of that workload, especially during [sales events or traffic spikes](/blog/woocommerce-scaling-speed-strategies/).
At Levamo, we built a stack that understands WooCommerce natively - not as an add-on, but as a core workload.
## Live Cart, Faster Search, and FunnelKit Integration
Our new WooCommerce integration brings speed and interactivity that store owners can actually feel.
- **Live Cart:** Carts update instantly without page reloads, delivering the kind of frictionless checkout experience usually reserved for enterprise platforms.
- **Faster Search:** Our optimized search indexing delivers near-instant product lookups, even on large stores with tens of thousands of SKUs.
- **FunnelKit Integration:** We partnered with **FunnelKit** to deliver faster, more optimized checkout flows natively on Levamo.
These aren’t add-ons - they’re part of the hosting layer itself, tuned for eCommerce scale.
## WooCommerce Controls, Built In
Inside your Levamo dashboard, you’ll find dedicated WooCommerce management tools that make life easier for developers and store owners. You can clear caches, manage object storage, or toggle WooCommerce-specific performance settings directly from your hosting panel - no plugins, no guesswork.
It’s a level of control that gives you instant feedback and measurable results.
## Proven at Scale
When [WP Lift](https://wplift.com/rapyd-cloud-review/) tested Levamo’s scalability, the results spoke for themselves:
*"To test Levamo’s scalability claims, we simulated traffic spikes using load testing tools, gradually increasing from 100 to 5,000 concurrent users over a 30-minute period. The results were impressive - response times remained consistent even as traffic scaled up. Average page load times increased by only 11% at peak traffic, compared to 300%+ slowdowns we’ve experienced with other hosts under similar conditions."*
That kind of performance doesn’t happen by chance. It comes from an architecture purpose-built to handle highly dynamic WordPress and WooCommerce sites at scale - the kind of stores where every page view, cart update, and checkout request is unique. While many hosts rely heavily on static caching to appear fast, Levamo is engineered for real-time, database-driven workloads where caching alone simply isn’t enough.
## Built for What’s Next
We believe WooCommerce deserves the same engineering focus that global SaaS platforms get. That’s why we’ve built Levamo as a foundation for the future - scalable, reliable, and obsessively optimized for online stores.
If you run WooCommerce, you don’t have to accept slow checkouts or scaling limits anymore.
Start your **3-day free trial** today, and we’ll migrate your site for free.
[Get Started Free →](/pricing/)
---
## Unleash Hyperspeed with BFCM Deals 2025: Black Friday Offers on Cloud Hosting & Other Tools and Services
- URL: https://levamo.com/blog/black-friday-cyber-monday-deal/
- Category: news
- Author: Shahzeb Ahmed
- Published: 2025-11-13
BFCM 2025 cloud hosting deals revealed! Turbocharge your site for Black Friday.
## 📌 2025 BFCM WordPress Deals Will be Updated Soon!
It's still early for companies to post their deal for BFCM 2025. We will update this page as soon as WordPress products start publishing their deals for 2025.
Black Friday and Cyber Monday aren't just shopping days; they're moments of opportunity, especially for those running [high-traffic WordPress sites](/managed-wordpress-hosting/), eCommerce stores, or online course platforms.
At Levamo, we believe that a solid hosting infrastructure is the difference between a good idea and a thriving online business. So our mission is to ensure that no matter how dynamic or feature-rich your websites are, they run smoothly and never face hiccups. No matter how high the traffic is or how many concurrent visitors you get on your website, we make sure that your websites face zero downtime and are always on **Hyperspeed performance**.
But how does Levamo ensure that?
By giving you [blazing-fast performance](/managed-wordpress-hosting/), [rock-solid security](/managed-security/), incredibly [easy to use platform](/easy-to-use-platform/), and [24/7 expert support](/support/).
On top of that, when sales season starts, the vertically dynamic auto scaling nature of Levamo will be able to handle any traffic spikes easily which otherwise would normally crash your website if hosted on most other managed hosting platforms. With our limited-time BFCM offer of **3 Months Free on Annual Plans**, you’re not just saving on hosting - you’re investing in a powerful infrastructure that will keep your website running smoothly even during high-traffic events and content-heavy interactions.
[Get 3 Months Free Now →](/?utm_campaign=blackfriday-25&utm_source=rapyd-blog)
Once you [migrate your website to Levamo](/free-website-migrations/), you’ll enter a Hyperspeed environment where your website is super snappy, performs smoothly, and does not crash when too many people are browsing simultaneously.
**Submit your deals here.**
## BFCM 2025 Deals on WordPress Plugins, Themes, Tools & Extensions
Black Friday 2025
We know that you also need the best Black Friday 2025 deals on tools, plugins, and services that can give your business a competitive edge.
At Levamo, we understand that every second counts for dynamic websites, so we’ve curated a selection of deals across **eCommerce tools, SEO, marketing, performance optimization, and course-building** - all carefully chosen to ensure you’re fully equipped for 2025 and beyond.
Whether you're a course creator, online store owner, or simply passionate about optimizing your WordPress site, these deals will help you build, scale, and thrive.
Hence, we’ve rounded up the best deals on the internet, so pick your favorite from the list below, and thank us later. ;)
[Submit your deals here →](https://forms.gle/7XroEtYjxNgPSxkj7)
### MasterStudy LMS - 50% off on All Plans
Black Friday 2025: Turn Knowledge Into Profit with MasterStudy LMS
MasterStudy LMS is a multifunctional WordPress learning management system packed with powerful tools to create and manage engaging online courses. Its Drag-and-Drop Course Builder with AI Lab makes course creation effortless, while Custom Certificates, Interactive Learning Tools, and a Smart Grading System help enhance student engagement and motivation.
Black Friday Deal 2025: Don’t miss unbeatable discounts on MasterStudy LMS Pro - your best investment in education this year!
**Date:** Nov 17–Dec 9, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://stylemixthemes.com/wordpress-lms-plugin/pricing/)
### MemberPress - Up to 70% Off
MemberPress is a powerful WordPress membership plugin that lets you create, manage, and sell online memberships with ease. It offers advanced access rules, subscription billing, course creation, and content protection. With built-in reporting, integrations, and automation, MemberPress helps creators, businesses, and communities monetize content and grow recurring revenue effortlessly.
**Date:** Nov 24–Dec 5, 2025.
**Coupon:** BF2025
[Get the Deal](https://memberpress.com/black-friday-2025/)
### Academy LMS - Up to 84% Off
Academy LMS is a fast and reliable top-rated WordPress LMS plugin for educators, entrepreneurs, and eLearning creators. With 43+ add-ons, 112+ features and 32+ integrations, it lets you build and manage courses easily. Its AI-powered Course Builder helps create lessons, quizzes, and outlines quickly.
The plugin includes a native payment system, SCORM support, white-label options, student analytics, tutor booking, course bundles, and bulk CSV imports. Academy LMS is perfect for freelancers, agencies, and institutions who want a professional, no-code eLearning platform.
**Date:** Oct 27–Nov 30, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://academylms.net/pricing/)
### LifterLMS - 60% off
LifterLMS has everything you need to easily **create, launch, and scale** courses from your own WordPress LMS website.
**Date:** 01 Nov–Dec 01, 2025.
**Coupon:** BLACKFRIDAY25
[Get the Deal](https://lifterlms.com/black-friday/)
### WpBakery - 30% Off, for Multisite Licenses
This Black Friday, pay less and get more with 30% OFF WPBakery Page Builder! Get another plan or renew your licenses and keep your Support Plus active - build smarter, save bigger and stay supported with the page builder trusted by over 5.8 million websites.
Looking for more options? We have a [single site license](https://wpbakery.com/wpbakery-page-builder-license/) available for individual use and an[ Agency Program](https://wpbakery.com/wpbakery-agency-program/) to support your multiple project needs.
**Date:** Nov 24–Dec 5, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://wpbakery.com/black-friday?utm_campaign=blackfriday-25&utm_source=[your-website])
### Mailtrap - 20% off for 12 Months
Simple and functional email marketing solution from Mailtrap. Create, schedule, and send impactful email marketing campaigns that make a difference to you and your customers.
**Date:** Nov 07–Dec 31, 2025.
**Coupon:** BFCM25
[Get the Deal](https://l.rw.rw/avxd0ytdwc)
### Crocoblock - Get 40% off All Plans
Get 40% off all plans, including custom, all-inclusive, and Lifetime subscriptions. Access 21 powerful WordPress plugins for dynamic websites, with 24/7 support and continuous updates.
**Date:** Nov 24–Dec 03, 2025.
**Coupon:** BFCROCO2025
[Get the Deal](https://crocoblock.com/discounts/?utm_source=rapydcloud&utm_medium=referral&utm_campaign=black-friday-2025)
### WP Umbrella - 20% OFF
Update, back up, secure, monitor, and report on all your WordPress sites - from one intuitive dashboard. Loved by 5,000+ agencies for the clean UX and real human support.
**Date:** Nov 24–Nov 30, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://wp-umbrella.com/?utm_source=blackfriday&utm_medium=partner&utm_campaign=rapydcloud)
### Acowebs Woocommerce Plugins - 10% OFF
Customers get a 10% discount on every plugin purchase they make. The discount increases to 20% when two items are purchased and increases to 30% for three or more items.
**Date:** Nov 27–Dec 4, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://acowebs.com/black-friday-cyber-monday-deals//?utm_source=web&utm_medium=listicle&utm_campaign=bfcm2025)
### Discount Rules For WooCommerce
Get up to 60% OFF on Discount Rules for WooCommerce. The only Discount plugin to boost your sales this Black Friday!
**Date:** Nov 24–Dec 5, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://www.flycart.org)
### UpsellWP - Product Addon for WooCommerce
Get up to 60% OFF this Black Friday on UpsellWP - boost sales and AOV with powerful WooCommerce upsells!
**Date:** Nov 24–Dec 5, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://upsellwp.com)
### WP Swings - 40% OFF
WP Swings is offering a 40% BFCM discount on all premium and profitable WooCommerce plugins.
**Date:** Nov 28–Dec 3, 2025.
**Coupon:** BUMPERBFCM
[Get the Deal](https://wpswings.com/offers/)
### Saral - $500 off Across All Plans
SARAL is an all-in-one influencer marketing platform built for e-commerce and DTC brands to streamline the end-to-end influencer workflow - from discovery to outreach, affiliate tracking and payments.
**Date:** Oct 01–Dec 31, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://www.getsaral.com/demo?utm_source=website&utm_medium=blog&utm_campaign=bfcm-listicle)
### WPManageNinja - 60% Discount Across All Plugins
WPManageNinja is a leading WordPress plugin company recognized for its powerful tools, including Fluent Forms, FluentCRM, and Ninja Tables.
This BFCM, they’re offering up to 60% off on all premium plugins.
**Date:** Nov 17–Dec 3, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://wpmanageninja.com/discount-deal/?utm_source=ext_collab&utm_medium=ext_collab&utm_campaign=bfcm25&utm_id=bfcm25&utm_term=bfcm25)
### **FluentCart** - Exclusive LTD
FluentCart combines performance, flexibility, and control in one powerful WordPress e-commerce plugin. It empowers businesses, creators, and agencies to sell physical or digital products, hybrid product listings, subscriptions, memberships, and more. All while keeping the shopping experience super fast, lightweight, and fully customizable.
**Date:** Oct 14–Dec 30, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://fluentcart.com/discount-deal/?utm_source=ext_collab&utm_medium=ext_collab&utm_campaign=fcart_ltd&utm_id=fcart_ltd)
### **FluentAffiliate** - Exclusive LTD
FluentAffiliate is a full-fledged affiliate management plugin for WordPress.
It helps businesses launch and manage their own affiliate programs with ease, onboarding affiliates, tracking visits, disbursing commissions, and handling everything else needed to run a successful program efficiently. With powerful integrations for e-commerce and essential tools, FluentAffiliate is your all-in-one solution for an affiliate program.
**Date:** Oct 14–Dec 30, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://fluentaffiliate.com/discount-deal/?utm_source=ext_collab&utm_medium=ext_collab&utm_campaign=bfcm25&utm_id=bfcm25&utm_term=bfcm25)
### myCred - 25% OFF on Lifetime Plans
myCred is a points management system and premium WordPress gamification plugin. It's a one-stop shop to assign points, rewards, and badges.
**Date:** Nov 20–Dec 6, 2025.
**Coupon:** MYCRED25
[Get the Deal](https://mycred.me/lifetime-sales/?utm_source=BFCM&utm_medium=campaign&utm_campaign=blackfriday2025&utm_content=mycred)
### NitroPack - 30% off for New Paid Users
NitroPack is an all-in-one, cloud-based service that automatically optimizes website speed by combining features like caching, image optimization, code minification, and a Content Delivery Network (CDN). It's designed to improve performance across platforms like WordPress, WooCommerce, and Magento, making sites load faster without requiring manual configuration or coding knowledge.
**Date:** Nov 18–Dec 5, 2024.
**Coupon:** CYBERMONTH2025
[Get the Deal](https://nitropack.io/pricing)
### Code Snippets Pro - 50% OFF
AI-enhanced code snippet management with cloud syncing and intuitive customization features to help you create a pixel-perfect website.
**Date:** Nov 18–Dec 03, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://codesnippets.pro/pricing/?utm_source=rapydcloud&utm_medium=web&utm_campaign=blackfriday&utm_id=Blackfriday+)
### CheckView - $2 for 2 Months + 50% 1 Year
CheckView is the leading fully automated testing platform for swiftly identifying and resolving issues with your WordPress forms and WooCommerce checkout.
**Date:** Nov 24–Dec 5, 2025.
**Coupon:** BLACKFRIDAY25
[Get the Deal](https://checkview.io/2025-wordpress-black-friday-deals-you-dont-want-to-miss/)
### The Plus Addons for Elementor - Up to 50% Off
Replaces the need for multiple plugins by giving you the most performance-optimized Elementor widgets in one powerful suite. Build smarter with pro-level features like Mega Menu Builder, WooCommerce Builder, Horizontal Scroll, Popup Builder, and tons more, all engineered for the best speed, creativity, and conversions. With over 150K+ active users already trusting The Plus Addons for Elementor to reduce bloat and unlock advanced design control, it’s the must-have upgrade for anyone serious about Elementor.
**Date:** Nov 16–Dec 7, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://theplusaddons.com/pricing/?utm_source=partner-roundup-blog&utm_medium=referral&utm_campaign=bfcm2025)
### Nexterwp - Theme & Extensions - Up to 50% Off
Build lightning-fast websites in minutes using Nexter’s ultra-optimized, jQuery-free theme engineered to deliver the cleanest, fastest performance on WordPress. Unlock total design freedom with 90+ powerful Nexter Gutenberg Blocks that let you create stunning layouts without touching code, while 50+ Nexter Extensions replace dozens of traditional plugins to keep your site lean and future-ready. Nexter empowers agencies and creators to build more sites, faster, with unmatched flexibility and performance baked right in.
**Date:** Nov 16–Dec 7, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://nexterwp.com/pricing/?utm_source=partner-roundup-blog&utm_medium=referral&utm_campaign=bfcm2025)
### UiChemy - Convert Figma to WordPress
UiChemy eliminates the painful bridge between design and development by Converting your Figma layouts into fully editable WordPress websites, responsive pages with precision. Save up to 70%-80% of production time while keeping global styles in sync and enjoying support for Elementor, Gutenberg & Bricks. Designers ship faster, developers skip the rebuild, and every team benefits from pixel-perfect results that are easy to maintain and scale.
**Date:** Nov 16–Dec 7, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://uichemy.com/pricing/?utm_source=partner-roundup-blog&utm_medium=referral&utm_campaign=bfcm2025)
### WDesignKit - Up to 50% Off
Gives agencies a true competitive edge with its advanced Custom Widget Builder that works seamlessly across Elementor, Gutenberg, and Bricks, letting you create unique, reusable components that scale across every project. With a shared cloud workspace where teams can design, manage assets, and collaborate in real. Plus, with 2000+ premium templates, an ever-growing ready-made widgets library, and integrated Figma support that keeps design and development perfectly aligned.
**Date:** Nov 16–Dec 7, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://wdesignkit.com/pricing/?utm_source=partner-roundup-blog&utm_medium=referral&utm_campaign=bfcm2025)
### Lasso - 50% off the First Year of All Annual Plans
Lasso is an affiliate-marketing tool and WordPress plugin that helps creators monetize their content by managing affiliate links, creating product displays and comparison tables, tracking clicks, fixing broken links, and automatically updating product information to boost conversions.
**Date:** Nov 11–Dec 30, 2025.
**Coupon:** Auto-applied
[Get the Deal](http://getlasso.co/black-friday)
### myCred - 24% OFF the Lifetime Plan
myCred is an intelligent and adaptive points management system that allows you to build and manage a broad range of digital rewards including points, ranks and, badges on your WordPress/WooCommerce powered website.
**Date:** Nov 20–Dec 6, 2025.
**Coupon:** BFCM25
[Get the Deal](https://mycred.me/pricing/?utm_source=BFCM_coupon&utm_campaign=BFCM)
### WPExperts - 24% Off on Annual Plan
WPExperts is a leading ‘360 degree digital services agency specializing in WordPress, WooCommerce, Magento, and Shopify full-stack development.
**Date:** Nov 20–Dec 6, 2025.
**Coupon:** BFCM24
[Get the Deal](https://wpexperts.io/store?utm_source=BFCM_coupon&utm_campaign=BFCM)
### FooGallery - 30% OFF On Annual Plan
FooGallery is an easy-to-use WordPress photo gallery plugin that lets you create stunning and effective galleries. There are 3 Pro plans, from Starter to Commerce, so you can select the gallery features you need. The Commerce plan integrates with WooCommerce, allowing you to sell photos or products directly from your gallery.
**Date:** Nov 18–Dec 3, 2025.
**Coupon:** FOOBF30
[Get the Deal](https://fooplugins.com/black-friday/)
### Daito - 50% off annual plans
Daito is a web-based authenticator that lets you share 2FA access across your team without sacrificing control. Access from any browser, organize accounts, and track usage with a searchable audit log. Trusted by 200+ businesses, from startups to Fortune 500s.
**Date:** Nov 25–Dec 1, 2025.
**Coupon:** CYBERMONDAY2025
[Get the Deal](https://www.daito.io/black-friday/)
### Divi Extended - 40% Off
Get the Black Friday deals on the wide range of premium Divi plugins, innovative child themes, and versatile layouts to enhance your website.
**Date:** Nov 25–Dec 2, 2025.
**Coupon:** Auto-applied
[Get the Deal](http://diviextended.com/black-friday/)
### aBlocks - Advanced Gutenberg Page Builder - Up to 88% Off
aBlocks is a versatile Gutenberg page builder that gives you full control over your WordPress site. With 95+ customizable blocks, you can quickly create blogs, portfolios, eLearning platforms, and online stores with ease and style.
It features drag-and-drop functionality, one-click Figma to WordPress conversion, a library of ready-made templates, responsive design options, and seamless theme integration. Advanced options like dynamic content, display conditions, motion effects, scrolling effects, mouse effects, sticky and floating elements, and tooltips make your site interactive and engaging.
With aBlocks, building modern, visually stunning websites is simple, fast, and flexible - perfect for beginners and professionals alike.
**Date:** Oct 27–Nov 30, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://ablocks.pro/pricing/)
### StoreEngine - Up to 57% Off
StoreEngine is a modern WordPress plugin that helps you sell physical goods, digital products, and memberships - all from one platform. You don’t need a stack of separate plugins. You can manage sales, subscriptions, payments, coupons, taxes and affiliates in one place.
What sets StoreEngine apart are its built-in features: support for PayPal, Stripe, bank transfer and COD payments, affiliate system, tax management, dynamic pricing and order management - with a lightweight setup that won’t slow your site.
Whether you’re a small business, course creator or digital entrepreneur, StoreEngine gives you everything you need to run your online store faster and smarter - without needing to juggle multiple plugins.
**Date:** Oct 27–Nov 30, 2025.
**Coupon:** Auto-Applied
[Get the Deal](https://storeengine.pro/pricing/)
### ZenCommunity - Support & Live Chat Platform
ZenCommunity is an all-in-one WordPress plugin that helps you build a social community, manage support tickets, and run [website](https://zencommunity.pro/) live chat - all from one place. It’s made for creators, educators, and businesses who want to engage and support their users without having to use multiple tools.
What makes ZenCommunity special is its complete communication system inside WordPress. You can create a full community space like a Facebook group, start group or private chats, manage customer support tickets, and provide live chat assistance - all in real time. ZenCommunity also includes activity feeds, comments, and reactions to keep members active and engaged.
Whether you’re a course creator, SaaS owner, or community builder, ZenCommunity gives you everything you need to build relationships, deliver instant support, and grow an active audience - all within your own site.
**Discount:** Up to 68% Off
**Date:** Oct 27–Nov 30, 2025.
**Coupon:** Auto-Applied
[Get the Deal](https://wbcomdesigns.com/black-friday/?utm_source=partner&utm_medium=blog&utm_campaign=black_friday)
### Easy Content Manager
Easy Content Manager (ECM) is a fast and flexible WordPress plugin that helps creators, developers, and site owners manage their websites easily. With ECM, you can create and control posts, pages, users, settings, taxonomies, and custom post types from one dashboard. It also offers inline editing, quick post conversion, custom fields, and settings page builder - all without writing any code.
What makes ECM stand out is its smart flexibility. You can build custom post types, taxonomies, and fields in seconds, import or export data via CSV, and even enable comments or reviews on any content type. Plus, it runs smoothly even on large sites.
Whether you’re a freelancer, developer, or site owner, Easy Content Manager helps you manage WordPress content faster and smarter - completely code-free.
**Discount:** Up to 75% Off
**Date:** Oct 27–Nov 30, 2025.
**Coupon:** Auto-Applied
[Get the Deal](https://easycontentmanager.pro/pricing/)
### WPBens - WordPress Plugins Bundle (Up to 60% off)
WPBens Quick checkout, filter WordPress posts & WooCommerce products, create dynamic discounts, build exclusive memberships, and automate email marketing - all in one powerful bundle.
WPBens combines Quicker (fast checkout optimization), FilterPlus (advanced product & post filtering), Discountify (15+ discount rules & dynamic pricing), MemberHub (complete membership solution), and MailerHub (email marketing, automation & CRM) to transform your WordPress and WooCommerce store into a sales-generating machine.
**Date:** Nov 22–Dec 8, 2025.
**Coupon:** Auto Apply in Bundle, BENS50 (on Single LTD plan)
[Get the Deal](https://woooplugin.com/black-friday-deals/)
### MemberHub - Membership plugin for WordPress and WooCommerce
MemberHub is a comprehensive WordPress membership plugin trusted by course creators, community builders, and subscription-based businesses worldwide. It empowers you to create exclusive member areas, monetize your content, offer tiered memberships, and deliver drip content - all from your WordPress dashboard without any coding.
With MemberHub, you can build any type of membership site with minimal effort and maximum flexibility. From online courses with scheduled content releases to VIP membership clubs, content restrictions by user roles, member directories, exclusive WooCommerce discounts, and automated subscription management - MemberHub handles it all.
**Discount:** Up to 50% off on all LTD plans
**Date:** Nov 22–Dec 7, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://wpbens.com/plugins/memberhub/)
### Mailerhub - Email Marketing Automation Plugin
MailerHub is a comprehensive email marketing and automation plugin for WordPress with a growing user base worldwide. It transforms your WordPress site into a powerful marketing hub, letting you create campaigns, automate emails, and manage contacts without leaving your dashboard.
With MailerHub, you can build any type of email marketing strategy with minimal effort and cost. From WooCommerce abandoned cart recovery to drip campaigns, lead nurturing sequences, or targeted promotional emails - MailerHub handles it all.
**Discount:** Up to 50% off on all LTD plans
**Date:** Nov 22–Dec 7, 2025.
**Coupon:** BENS50
[Get the Deal](https://wpbens.com/plugins/mailerhub/)
### Discountify - Woocommerce Discount Plugin
Discountify is a comprehensive all-in-one WooCommerce discount plugin trusted by store owners and marketers worldwide. It empowers you to create smart discount rules, dynamic pricing strategies, BOGO offers, and auto-apply coupons - all from a single, powerful dashboard that boosts conversions and increases average order value.
With Discountify, you can build any discount campaign with minimal effort and maximum impact. From bulk pricing and cart-based discounts to role-based pricing, tiered discounts, purchase history rewards, and shipping discounts - Discountify handles it all.
**Discount: Discount Offer:** Up to 50% off on all LTD plans
**Date:** Nov 22–Dec 7, 2025.
**Coupon:** BENS50
[Get the Deal](https://wpbens.com/plugins/discountify/)
### Quicker - Quick Checkout Plugin for More Conversions
Quicker is a powerful WooCommerce checkout optimization plugin trusted by online store owners worldwide. It transforms your standard checkout process into a conversion-focused, lightning-fast experience that reduces cart abandonment and boosts sales - all through intelligent customization and one-click purchasing.
With Quicker, you can create any type of checkout experience with minimal effort and technical knowledge. From custom checkout field editing and one-click orders to product add-ons, order bumps, quick view popups, cash on delivery charge, and extra fees - Quicker handles it all.
**Discount:** Up to 50% off on all LTD plans
**Date:** Nov 22–Dec 7, 2025.
**Coupon:** BENS50
[Get the Deal](https://wpbens.com/plugins/quicker/)
### Filterplus - Ajax Filter Plugin for WordPress and Woocommerce
FilterPlus provides advanced product and post filtering capabilities, making it easier for customers to find exactly what they're looking for. The AJAX-powered, SEO-friendly filtering works seamlessly with WooCommerce products, WordPress posts, and custom post types.
**Discount:** Up to 50% off on all LTD plans
**Date:** Nov 22–Dec 07, 2025.
**Coupon:** BENS50
[Get the Deal](https://wpbens.com/plugins/filter-plus/)
### Pixpa
Pixpa is an all-in-one, no-code website builder for creatives and small businesses to create beautiful, professional websites with an in-built online store, a dynamic blog, client galleries, ecommerce galleries, a photo gallery app, and marketing tools. Pixpa’s versatile platform has everything you need to showcase your work, share ideas, and sell your work online without any coding knowledge.
**Discount:** 55% discount on Pixpa's annual plans.
**Date:** Nov 28–Dec 31, 2025.
**Coupon:** BLFPIXPA55
[Get the Deal](https://www.pixpa.com/?via=blfpixpa55)
### Wholesale Suite
Wholesale Suite is the #1 rated wholesale solution for e-commerce stores. It adds wholesale user roles, wholesale pricing, product visibility controls, product & order minimums, tax display control, streamlined ordering forms, + more. Using these tools, you can reduce admin work, ditch the spreadsheets, and bring your wholesale operation online seamlessly.
**Discount:** Up to 60% off on All Plugins and Bundles
**Date:** Nov 24–Dec 4, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://wholesalesuiteplugin.com/bundle)
### WC Vendors
WC Vendors is the best WooCommerce multi-vendor plugin for hassle-free multi-vendor marketplace setups like Amazon and Etsy. Integrated vendor tools, extensive shipping, 100+ payments, and more.
**Discount:** Up to 60% off on All Plugins and Bundles
**Date:** Nov 24–Dec 4, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://www.wcvendors.com/pricing/)
### VisserLabs
Visser Labs is the ultimate WooCommerce export and import solution. It offers advanced export scheduling, smart filtering, and robust attribute controls for your store. It is also built to handle large volumes of data, making the import or export of 10,000+ products easier than ever!
**Discount:** Up to 60% off on All Plugins and Bundles
**Date:** Nov 24–Dec 04, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://visser.com.au/pricing/)
### SaveTo Wishlist
SaveTo Wishlist is the definitive free WooCommerce plugin to capture customer interest and boost sales. It lets shoppers create customizable wishlists, save products for later, and share them for viral growth. It offers multiple list support, supports various themes, and provides a fast, natural path to future conversion and checkout.
**Discount:** Completely free!
**Date:** Nov 24–Dec 04, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://savetowishlist.com/free-woocommerce-wishlist-plugin/)
### AdTribes
AdTribes is a leading WooCommerce product feed solution that simplifies feed creation for unlimited products. Users can easily showcase items on channels like Google Shopping and Facebook. With 100+ templates, automatic updates, and Google Analytics integration, it empowers store owners to optimize their marketing for maximum reach, visibility, and sales.
**Discount:** Up to 60% off on All Plugins and Bundles
**Date:** Nov 24–Dec 04, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://adtribes.io/pricing/)
### InstaWP
InstaWP is a cloud platform for building, hosting, managing, and selling sites. It's for pros who don't like doing things twice.
**Date:** Nov 24–Dec 5, 2025.
**Coupon:** INSTA41
[Get the Deal](https://instawp.com/black-friday-2025/)
### ShortPixel
ShortPixel is a fast, reliable WordPress image optimization plugin that reduces file sizes without losing quality. It improves site speed, SEO, and overall performance by automatically compressing new and existing images. Supporting WebP and AVIF, ShortPixel works seamlessly with blogs, portfolios, and WooCommerce stores to deliver a faster, smoother user experience.
**Discount:** Get 2× credits on One-Time Plans or 25% off Unlimited Yearly plans.
**Date:** Nov 24–Dec 1, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://shortpixel.com/)
### FastPixel
FastPixel is a high-performance image and media optimization service designed to speed up WordPress and WooCommerce sites. It delivers lightning-fast loading through real-time compression, next-gen formats like WebP and AVIF, and global CDN delivery. FastPixel improves SEO, boosts conversions, and ensures a smooth, optimized browsing experience for every visitor.
**Discount:** Get 2× credits on One-Time Plans or 25% off Unlimited Yearly plans.
**Date:** Nov 24–Dec 1, 2025.
**Coupon:** Auto-applied
[Get the Deal](https://fastpixel.io/)
### Unlimited Plan by DJ-Extensions
The Unlimited Plan from DJ-Extensions gives you full access to all their Joomla and WordPress extensions, themes, and templates under one subscription. It includes updates, support, and downloads for an entire year, with usage allowed on unlimited domains. A cost-effective solution for developers, agencies, and multi-site projects.
**Coupon:** BLACK25
**Date:** Nov 27–Dec 2, 2025.
[Get the Deal](https://dj-extensions.com/unlimited-plan)
### Agency Handy
[Agency Handy](https://www.agencyhandy.com/) is a complete agency management platform made for digital agencies of all sizes. It brings CRM, services, projects, invoicing, proposals, and client portals into one place.
You can manage leads, track work, and collect payments easily via PayPal, Stripe, Wise, Crypto, and banks. With tools for recurring billing, team collaboration, and branded client access, Agency Handy helps you run your entire agency from one simple, connected system.
**Discount:** 70% off on Annual Plans
**Coupon:** AHBFCM
**Date:** Nov 15–Dec 05, 2025.
[Get the Deal](https://www.agencyhandy.com/)
### WooGallery - WooCommerce Product Image & Video Gallery Plugin
Ultimate WooCommerce Product Gallery plugin to showcase your products from basic to brand-level like Adidas, Louis Vuitton, and more. Perfect for product showcases that drive sales.
**Best for:** Creating modern image & video galleries for any WooCommerce store.
**Discount:** Up to 60%
**Coupon :** Auto-applied.
**Date:** Nov 17–Dec 15, 2025.
[Get the Deal](https://woogallery.io/pricing/)
### Smart Tabs - WooCommerce Custom Product Tab Manager
All-in-one WooCommerce product tabs solution that lets you create custom product tabs to organize product details easily. Assign to all, or specific products, edit or hide per product to boost sales.
**Best For:** Adding custom product tabs on WooCommerce product pages.
**Discount:** Up To 60%
**Date:** Oct 17–Dec 15, 2025.
**Coupon:** Auto-applied.
[Get the Deal](https://wptabs.com/pricing/)
### Smart Post - Ultimate Gutenberg Post Blocks
Advanced Gutenberg post blocks plugin to display news, magazines, and blog posts beautifully. Showcase any posts in stunning post grids, sliders, carousels, and news tickers layouts to drive conversions.
**Best For:** Organizing news, travel, portfolio, magazines, or recipe blog site.
**Discount:** Up To 60%
**Coupon:** Auto-applied.
**Date:** Oct 17–Dec 15, 2025.
[Get the Deal](https://wpsmartpost.com/pricing/)
### Location Weather– #1 WordPress Weather Plugin
#1 WordPress weather widget plugin with 15 interactive Gutenberg blocks. Display real-time weather forecasts for daily and hourly in modern accordions, tables, layouts - a must-have plugin for every weather-dependent business.
**Best For:** Creating a real-time weather widget for the News and travel site.
**Discount:** Up To 60%
**Coupon:** Auto-applied.
**Date:** Oct 17–Dec 15, 2025.
[Get the Deal](https://locationweather.io/pricing/)
### WP Carousel - Multi-Purpose WordPress Gallery Slider
The most powerful WordPress slider plugin to create eye-catching carousels, sliders, and galleries that engage visitors and boost conversions. Showcase images, videos, posts, products, text, or mixed content in beautiful layouts.
**Best For:** Building elegant sliders, carousels, and galleries for images, videos, and more.
**Discount:** Up To 60%
**Coupon:** Auto-applied.
**Date:** Oct 17–Dec 15, 2025.
[Get the Deal](https://wpcarousel.io/pricing/)
### Real Testimonials - Powerful Customer Review Plugin
Automate collecting, filtering, and displaying customer reviews on your WordPress site to build trust and boost sales. It lets you create stunning testimonial forms, sliders, and grids with complete customization and automation.
**Best For:** Collecting and showcasing reviews to increase credibility and conversions.
**Discount:** Up To 60%
**Coupon:** Auto-applied.
**Date:** Oct 17–Dec 15, 2025.
[Get the Deal](https://realtestimonials.io/pricing/)
### Smart Swatches - Responsive Product Variation Swatches
Create interactive product variation swatches that attract customers and help them find the perfect color, size, style, flavor, and more, boosting sales. Transform plain text variations into vibrant color and image swatches with just one click.
**Best For:** Adding colors, sizes, and stylish swatches to Woo products.
**Discount:** Up To 60%
**Coupon:** Auto-applied.
**Date:** Oct 17–Dec 15, 2025.
[Get the Deal](https://shapedplugin.com/smart-swatches-for-woocommerce/#pricing)
### Smart Team - WordPress Team & Staff Directory Plugin
A powerful yet simple solution for showcasing your team members to build instant credibility and support business growth. Create professional staff directories, About Us pages, organizational listings, and member showcases with robust features and zero technical effort.
**Best For:** Creating professional team showcases, About Us pages, and staff directories.
**Discount:** Up To 60%
**Coupon:** Auto-applied.
**Date:** Oct 17–Dec 15, 2025.
[Get the Deal](https://getwpteam.com/pricing/)
### WPXPO
WPXPO is offering a **massive 88% discount for Black Friday on its 10 premium plugins**, including PostX, WowStore, WowRevenue, WowAddons, WowOptin, WowShipping, WholesaleX, and 3 upcoming products, covering website building, product bundles, product addons, WooCommerce shipping, and more. It’s the perfect all-in-one deal for WordPress users who want to build and grow their businesses.
**Discount:** Up To 88%
**Coupon:** Auto-applied.
**Date:** Nov 05–Dec 10, 2025.
[Get the Deal](https://www.wpxpo.com/offer/?utm_source=bfcm-listing-2025)
For reliable WordPress hosting deal, checkout Levamo.
*Levamo offers specialized hosting for dynamic platforms such as [MemberPress Hosting](/memberpress-hosting/), [BuddyPress Hosting](/buddypress-hosting/), [BuddyBoss Hosting](/buddyboss-hosting/), and more. *
---
## Boost Recurring Revenue and Retention With WP Swings Subscription Plugin
- URL: https://levamo.com/blog/wp-swings-subscription-plugin/
- Category: wordpress
- Author: Shahzeb Ahmed
- Published: 2025-11-12
Subscription revenue awaits! See how WP Swings plugin boosts retention.
"The subscription economy has grown by 435% over the last decade and is projected to reach a market size of $1.5 trillion by 2025, indicating its permanence as a business model. ~ [ERP Today](https://erp.today/the-rise-of-subscription-economy-a-win-win-for-consumers-and-businesses/)"
The subscription economy is booming, and businesses of all sizes are tapping into it to drive steady growth. From streaming platforms to monthly product boxes, customers love the ease of getting what they need without having to reorder every time. For online store owners, this model opens the door to recurring revenue, stronger customer relationships, and long-term stability.
WooCommerce, one of the most popular eCommerce platforms, makes it simple to bring subscription selling into your store. With the right plugin, you can create flexible plans, manage recurring payments, and deliver consistent value to your shoppers.
In this post, we’ll explore how the **[Subscription for WooCommerce plugin by WP Swings](https://wpswings.com/product/subscriptions-for-woocommerce-pro/)** helps you build and manage a thriving subscription business - covering key features, pricing, and real-world use cases to show how it can lift your store’s performance.
## Why Use a WooCommerce Subscription Plugin?
A subscription plugin moves you beyond one-time purchases to steady, recurring revenue. It lets you sell products and services on a subscription basis with automatic renewals and flexible billing options - delighting customers while making your cash flow more predictable.
Example: if you run an online coffee shop, don’t wait for monthly reorders. Offer a plan that delivers fresh coffee on a schedule - keeping customers happy and your revenue consistent. Whether it’s physical goods, digital downloads, or memberships, subscriptions turn casual buyers into loyal customers.
## Key Features & Benefits of Subscription for WooCommerce (WP Swings)
- **Subscription Box & Multi-Step Configuration**
Create custom subscription boxes with dynamic pricing. Let customers pick multiple favorites on a recurring schedule via a guided, multi-step flow - for flexible bundling and control.
- **Recurring Payment Automation & Retry**
Automate renewals and retry failed payments a configurable number of times before auto-cancellation - reducing revenue loss.
- **Proration & Plan Changes**
Handle upgrades/downgrades mid-cycle with automatic proration. Optionally issue wallet credits and reflect changes on the next statement.
- **Manual Payments & One-Time Purchases**
When auto-billing isn’t possible, send invoice links for direct payment. Support one-time purchases at subscription rates for extra flexibility.
- **Advanced Reporting & Churn Analytics**
Track performance with dashboards for subscription health, churn rate, calendar views, and average recurring revenue to inform strategy.
- **Custom Email Reminders & Notifications**
Keep admins and customers informed at every lifecycle step - payments, expirations, plan changes, suspension, and reactivation - to boost engagement and reduce churn.
- **Role Automation by Subscription Status**
Automatically assign roles (e.g., Subscriber/Customer) based on active or lapsed status to streamline access and privileges.
- **Works with Simple & Variable Products**
Attach subscriptions to simple, variable, and downloadable products - ideal for both goods and digital offerings.
- **Free Trial & Initial Fee**
Encourage sign-ups with trials or set an initial fee to cover onboarding/setup - per plan configuration.
- **Full Lifecycle Control**
Admins and users can pause, resume, cancel, or edit subscriptions anytime - maximizing control and self-service.
## Benefits at a Glance
- Stabilizes revenue via automated renewals.
- Reduces involuntary churn with payment retries and manual recovery options.
- Improves retention through easy upgrades/downgrades and fair proration.
- Elevates operations with reporting on churn and recurring revenue.
- Increases satisfaction with timely lifecycle notifications.
- Gives granular admin control (pause/resume/cancel, role automation).
- Offers flexible sign-ups with trials, initial fees, and box builder flows.
## Pricing: Which Plan Fits Your Business?
**Subscriptions for WooCommerce** comes in both **free and **Pro** editions. The free version covers essential subscription management; the Pro version adds advanced features for growing stores**.
As of **October 2025**, Pro pricing starts at $129/year for 1 site, **$269/year** for up to 5 sites, and $529/year for up to 10 sites. Annual licenses include updates, premium support, and a 30-day money-back guarantee.
- **Choose Free** for basic recurring payments and simple products.
- **Choose Pro** for proration, detailed reports, payment retries, subscription boxes, and scalable management.
## Real-World Applications: How Subscriptions Transform eCommerce
Subscriptions are fueling growth across industries - driving predictable revenue and stronger relationships. Brands like Dollar Shave Club, HelloFresh, and Amazon use recurring deliveries to minimize reorders and maximize convenience.
- **Subscription Boxes**: Curate products with exclusive deals and early access.
- **Replenishment Plans**: Automate essentials on a dependable schedule.
- **Memberships & Digital**: Gate premium content and downloads with role automation.
- **Lower CAC, Higher LTV**: Subscribers retain longer and spend more over time.
- **Smarter Ops**: Recurring data improves forecasting and inventory planning.
With the right management tools, you can automate billing, personalize offers, and boost engagement - making your operations more resilient and efficient in a competitive 2025 landscape.
## Final Verdict: Is It Worth It?
**Subscriptions for WooCommerce Pro** offer strong value for merchants building stable recurring revenue. You receive automated renewals, proration, retries, lifecycle emails, manual payments, and flexible plan changes, along with reporting to inform decision-making.
Users highlight its affordability versus alternatives, powerful analytics, and responsive support. While there’s some setup learning curve (as with any subscription stack), the plugin scales well across diverse eCommerce models.
If your goal is to convert one-time buyers into loyal subscribers and lift lifetime value, this plugin is a smart investment for 2025 and beyond.
### FAQs
**1. Why use a WooCommerce subscription plugin?**
To create predictable, recurring revenue while offering customers convenient, automated deliveries and renewals.
**2. What can I sell on subscription?**
Physical goods, digital downloads, services, and memberships - including simple, variable, and downloadable products.
**3. Does it support plan changes and proration?**
Yes - upgrades and downgrades mid-cycle are prorated automatically, with options like wallet credits.
**4. What happens when a renewal fails?**
Automatic retries help recover payments; you can also send manual invoices to reduce churn.
**5. How is pricing structured?**
There’s a free version. Pro (as of Oct 2025) starts at $129/year for 1 site, $269/year for up to 5 sites, and $529/year for up to 10 sites, with updates, support, and a 30-day guarantee.
**6. Is it hard to set up?**
There’s a mild learning curve, but guided settings, reports, and notifications help you launch quickly and iterate confidently.
---
## How WordPress Sandboxes Help Developers Test Plugins, Themes, and Workflows Safely
- URL: https://levamo.com/blog/how-wordpress-sandboxes-help-developers-test/
- Category: website-development
- Author: Shahzeb Ahmed
- Published: 2025-09-08
Test WordPress plugins and themes safely in a sandbox environment.
In WordPress development, testing directly on a live site is still one of the most common mistakes. According to a 2024 survey by Patchstack, more than 60% of site breakages reported by agencies were caused by untested plugin or theme updates.
The safer path is to adopt a sandbox-first workflow. A WordPress sandbox is an isolated environment where you can install plugins, switch themes, and test workflows without risking production sites.
This post will explore how developers and agencies can carry out WordPress plugin testing and WordPress theme testing in a controlled, disposable WordPress sandbox environment.
## What is a WordPress Sandbox?
A [WordPress sandbox](https://instawp.com/wordpress-sandbox/#what-is-a-word-press-sandbox) is a safe, temporary environment where developers can test changes before applying them to a live website. Think of it as a practice ground. You can install plugins, activate themes, or experiment with workflows knowing that nothing here will affect production.
Many people confuse a sandbox with a staging site, but they’re not the same. A staging site is often a duplicate of your live website, hosted on the same server. It’s tied to production and sometimes slows down when you run heavy tests.
A sandbox WordPress setup, on the other hand, is completely isolated. It can be created in seconds, reset instantly, and discarded when no longer needed.
For developers and agencies, this approach is critical. Instead of risking errors on client projects, you can run WordPress plugin testing and WordPress theme testing inside a sandbox first. Once everything works, you confidently move the changes to staging or production.
### Why Developers Need a Sandbox-First Workflow
Developers often face the same dilemma: do you risk testing directly on a live site, or spend hours preparing a staging server? Neither option is ideal. A sandbox-first workflow gives agencies and developers a third, safer path.
The reality is clear. 43% of WordPress site vulnerabilities are because of plugins and themes. That means skipping WordPress plugin testing or WordPress theme testing can easily break a site.
A sandbox WordPress environment prevents this by giving you a disposable site to run experiments without consequences.
For agencies, the value goes deeper. A sandbox-first workflow makes it easier to:
- Test multiple plugin versions before choosing the right one.
- Preview theme updates in isolation and confirm compatibility.
- Validate entire WordPress workflows, from checkout processes to custom post types, without risking downtime.
Instead of rushing changes into production and relying on backups to undo mistakes, sandboxes let you test first, deploy later.
## What Makes Traditional WordPress Sandbox Workflows a Hindrance for Agencies and Developers
We understand that using a WordPress sandbox means safe WordPress development, but many developers still sideline it because the traditional way of creating a sandbox is tedious.
Setting up a sandbox WordPress environment has often meant spinning up a local server, configuring databases, and installing files manually. This process slows down teams who simply want to test plugins, switch themes, or validate workflows quickly.
For agencies, the problems are even sharper.
These obstacles lead many to skip sandboxing altogether and risk testing directly on live websites. The result is downtime, broken plugins, and unhappy clients.
## InstaWP’s WordPress Sandboxes: The First Choice of Modern Developers
Traditional WordPress sandbox setups are often tied to manual local installs or hosting environments. They’re slow, fragmented, and difficult to reset.
InstaWP, the [all-in-one WordPress cloud](https://instawp.com/), flips that experience by making sandboxes instant, disposable, and collaborative.

Developers can spin up a WordPress sandbox environment in seconds, run their tests, and reset or discard the site when finished. This agility is what makes sandbox-first workflows essential for modern WordPress agencies.
### 1. Faster Setup
Traditional sandboxes require manual effort, installing servers locally, configuring MySQL databases, setting up PHP versions, and then finally installing WordPress. This overhead means developers often skip sandboxing altogether.
InstaWP solves this by letting you spin up a sandbox site in seconds. All you need is to sign up on InstaWP, choose the configurations of your sandbox site, and get the Sandbox plan at just $2.
For only $2, the [Sandbox Plan](https://instawp.com/choosing-right-instawp-site-plans/#sandbox-plan-for-ongoing-development-client-previews) gives you:
- 1 PHP worker
- 5 GB disk space
- Monthly backup
- Basic website management tools
And because InstaWP uses pay-as-you-go pricing, you only pay for the time your sandbox is active. Done testing? Just delete the site; no recurring billing.
If you’re [building a site from scratch](https://docs.instawp.com/en/article/create-site-b0xjuh/#5-from-scratch), InstaWP lets you do all your early development on the Sandbox Plan, then upgrade to a higher tier (Starter, Plus, Turbo, etc.) depending on the site’s real needs at launch.
This flexibility makes it incredibly efficient for developers to host WordPress and iterate quickly, without overpaying or over-engineering.
No local setup, no server prep. Just open your browser and launch a site that’s ready for WordPress plugin testing or WordPress theme testing instantly.
### 2. Easy Resets
One of the biggest frustrations with traditional sandboxes is how fragile they are. Once you break something or misconfigure a plugin, you often have to delete the entire environment and rebuild from scratch.
InstaWP eliminates this pain with one-click resets. Whether a test goes wrong or a plugin update crashes the admin panel, you don’t have to rebuild anything manually. Just reset and you’re back to a clean slate in seconds.
You also get access to bulk edit tools that make cleanup a breeze:

- Remove all installed plugins or themes in one click
- Clear out junk data before client handoffs
- Start fresh without losing time
And if you're comfortable with the command line, InstaWP supports WP-CLI right out of the box. That means you can deactivate plugins in bulk, reset databases, and run custom scripts or migrations, all without leaving your browser.
For developers who regularly test updates, troubleshoot errors, or manage WordPress sites for clients, these reset tools are lifesavers. They turn sandboxing from a risky chore into a flexible, no-regret environment.
### 3. Purpose-Built for Testing
Traditional sandboxes are often just clones of a live site, which means they’re not optimized for testing workflows. Plugin conflicts or theme updates may not show up properly until they hit production.
InstaWP sandboxes are different. They’re built from the ground up to be clean, isolated testing environments, specifically designed for developers who need a safe, production-like setup to run real tests. Whether you're testing plugin compatibility, trying out a new block theme, or debugging third-party scripts, InstaWP gives you:
- A fresh WordPress install with zero clutter
- Choice of PHP versions, themes, and pre-installed plugins
- Optional templates and snapshots for reusable configurations
- Built-in tools like WP-CLI, file manager, and database access
During our review, we tested several WordPress plugins side by side - including ones with known compatibility issues - and found that InstaWP sandboxes exposed conflicts immediately. No caching issues, no legacy settings carried over. Just accurate, reproducible results.
This level of control makes it ideal for testing updates before applying them to live client sites, previewing theme or plugin combinations, isolating bugs or conflicts in a safe space, and building reproducible QA workflows for agencies.
In short, InstaWP doesn’t just let you host WordPress; it lets you test it properly. If you’re serious about quality control and want to manage WordPress sites responsibly, these isolated environments are a massive upgrade over traditional cloning methods.
### 4. Reusable Templates
In traditional workflows, sandboxes are one-off. Once a project is done, the sandbox is discarded, and the whole setup process starts over for the next job. It’s repetitive, time-consuming, and frankly, inefficient.
InstaWP fixes this with Snapshots and Templates.

Every WordPress sandbox you create can be saved as a Snapshot, capturing the exact state of the site, including plugins, themes, content, PHP version, and configurations.
You can then turn that snapshot into a reusable template, making it instantly deployable across future projects.
### 5. Scalable for Agencies
Scaling traditional sandboxes is painful. Imagine an agency managing ten clients, each requiring multiple testing environments. Local setups quickly become unmanageable, and hosting-based sandboxes eat up server resources.
InstaWP makes this scalable. Agencies can create, manage, and reset dozens of sandboxes in parallel, each completely isolated and disposable. That means faster delivery, cleaner QA, and less overhead.
### 6. Client-Ready Demos
Traditional sandboxes are hard to share. A developer might need to package a site, upload it somewhere, and send login credentials just to let a client preview a change. InstaWP sandboxes solve this with shareable demo links.
Whether it’s a new plugin configuration or a theme design, you can give clients instant, hands-on access to a WordPress sandbox for customer demos; no manual migration or staging required.
In short, traditional sandboxes were never built to keep up with modern development cycles. They were clunky and resource-heavy. InstaWP reimagines the sandbox as a fast, lightweight, and scalable tool, helping developers move faster while reducing the risks tied to live testing.
## How to Create WordPress Sandboxes on InstaWP for Testing
A sandbox is only as good as how easily you can put it to work. With the InstaWP Sandbox Plan, the process is designed to be quick and repeatable.
Here’s how agencies and developers can set up a safe workflow for WordPress plugin testing, WordPress theme testing, and full workflow validation.
#### Step 1: Launch a Sandbox in Seconds
- Log into your InstaWP dashboard.
- Click **“Create New Site.”**

**Step 2: Choose the Site Creation Option**
You have multiple options to start:

- **Default setup:** Launch a blank site with WordPress installed.
- **Pre-installed plugins:** Choose from a curated library of essentials like page builders, security, forms, and optimization tools. No need to download ZIP files or browse directories - everything is preloaded for you.
- **AI or Templates:** If you don’t want to start from scratch, use AI site generation, Snapshots, or InstaWP’s template store to instantly build a pre-configured site.
After entering your site specifications, click **Next Step.** Here you can fine-tune the sandbox by adding plugins or themes you’d like to test.
Finally, choose the **Sandbox Plan** to make sure the site is disposable and resettable for safe experiments.

Your sandbox will be live in seconds. Use the **Magic Login** button to access your WordPress dashboard immediately, no passwords required.

If you’ve built an environment worth saving, for example, an agency starter stack, you can turn it into a **template** or **snapshot** for future reuse.
This flexibility is what makes InstaWP more than just a temporary sandbox: it becomes a repeatable part of your development workflow.
#### Step 3: Customize the Site
With your WordPress sandbox running, customization becomes effortless. From the dashboard, you have full control over everything you’d expect in a production site:
- **Themes:** Install, switch, or customize themes in bulk for complete WordPress theme testing.
- **Plugins:** Activate, configure, and run WordPress plugin testing without risking your live projects.
- **Content:** Add posts, pages, menus, or media files to test how everything fits together.
- **Code:** Use the built-in code editor to adjust CSS, PHP, JavaScript, or HTML in real time.
- **Settings:** Tweak configurations like permalinks, caching, or performance tuning.
For even more flexibility, InstaWP includes the Local Mount feature. This allows you to treat your sandbox like a local folder on your computer. You can open files, run scripts, and manage the full file structure, all while keeping the ease of cloud hosting.
When it’s time to share progress, simply send a sandbox link to your client. They can explore the changes directly without waiting for a staging push or migration.
👉 This way, agencies can test WordPress plugins, preview themes, and validate workflows inside a safe sandbox WordPress environment that’s resettable, disposable, and ready for customer demos.
By following these steps, agencies and developers can shift from risky production testing to a sandbox-first workflow where mistakes are safe, experiments are quick, and client approvals are smoother.
## Use Cases of InstaWP’s WordPress Sandboxes Beyond Testing
While most developers think of sandboxes primarily for WordPress plugin testing and WordPress theme testing, the reality is that a WordPress sandbox environment offers far more. Agencies, freelancers, and product creators can extend the value of InstaWP sandboxes into client management, demos, and even training.
### 1. Customer Demos
If you’re building plugins or themes, showing them off to potential customers is crucial. Traditionally, you’d need to set up a staging site or migrate files just to give someone a preview.
With InstaWP Sandboxes, you can generate a WordPress sandbox for customer demos in seconds and share the link instantly. Prospects can explore your product hands-on without any installation headaches.
### 2. Client Approvals
Agencies often struggle with client feedback cycles. Migrating changes to staging servers, sharing credentials, and waiting for reviews can take days. A sandbox shortens that cycle. Build the workflow, share the sandbox link, and let clients see the changes in real time. Once approved, you can confidently move updates into production.
### 3. Team Training and Onboarding
New developers or interns need a safe environment to practice without breaking production. Traditional sandboxes tied to hosting plans are too fragile and resource-intensive for this. InstaWP makes it simple to spin up disposable sandboxes where teams can learn, test, and reset as often as they need.
### 4. Rapid Prototyping
Sometimes, agencies just need to test a concept quickly, a new checkout flow, a custom post type, or a design idea. Instead of wasting hours on setup, InstaWP sandboxes let you create a working prototype in minutes, validate the idea, and move on.
### 5. Workflow Validation
Beyond plugins and themes, sandboxes are powerful for testing entire workflows. Whether it’s a membership site, an eCommerce checkout, or an LMS integration, you can configure everything inside a sandbox first. This ensures your live site launches without hiccups.
By going beyond testing, InstaWP Sandboxes become an all-in-one toolkit for agencies and developers. They help win clients faster, streamline approvals, and create safer spaces for experimentation.
## Conclusion
For agencies and developers, skipping testing or relying on traditional setups is no longer sustainable. The risks are too high; broken plugins, theme conflicts, and client downtime all eat away at trust and revenue. A sandbox-first workflow is the safest way forward, and InstaWP makes it not just safe but also fast, scalable, and client-friendly.
With the InstaWP Sandbox Plan, you can spin up disposable sites in seconds, run WordPress plugin testing and WordPress theme testing with confidence, and share demos or prototypes instantly. This approach transforms sandboxing from a tedious chore into a core productivity tool that helps agencies deliver projects faster and with fewer risks.
If you want a more efficient way to build, test, and showcase your WordPress projects, InstaWP sandboxes are the smarter choice.
👉 [Start using InstaWP Sandboxes today](https://app.instawp.io/onboard?source=pricing_page&utm_source=organic&utm_campaign=levamo&utm_medium=partnership) and experience sandbox-first WordPress development built for agencies and developers.
### FAQs
**1. What is a WordPress sandbox environment?**
A WordPress sandbox environment is an isolated site where you can safely test plugins, themes, or workflows without affecting your live website. It’s temporary, disposable, and perfect for experimentation.
**2. Can I use InstaWP sandboxes for WordPress plugin testing?**
Yes. InstaWP sandboxes are built for WordPress plugin testing. You can install, configure, and stress-test plugins without worrying about breaking a production site.
**3. How does WordPress theme testing work inside a sandbox?**
You can install and preview themes in a sandbox, test compatibility with existing plugins, and validate performance or design changes before applying them to a client’s live site.
**4. What’s the difference between sandbox WordPress and staging WordPress**?
A staging site is usually a copy of your live site hosted on the same server. It’s tied to production resources and can slow down under heavy tests. A sandbox WordPress environment is isolated, disposable, and faster to create, making it ideal for quick testing.
**5. Can I create a WordPress sandbox for customer demos**?
Yes. InstaWP lets you generate a sandbox in seconds and share a link directly with clients or prospects. It’s an easy way to showcase a plugin, theme, or workflow without migration or setup.
---
## From Custom Code to No-Code Logic: Building Smarter with Crocoblock
- URL: https://levamo.com/blog/no-code-logic-building-smarter-with-crocoblock/
- Category: website-development
- Author: Shahzeb Ahmed
- Published: 2025-07-11
See how Crocoblock's JetEngine simplifies complex WordPress sites.
If you are creating a complex, highly dynamic website or just a project that requires more than the default WordPress post types, relations, and taxonomies, you will definitely need extra functionality that not only adds some particular fields or logic, but also enhances the way the website stores, fetches, and displays content.
It can be achieved using a ton of different custom code snippets, or there’s a modular solution that does the job for you, but you don’t have to code - **[Crocoblock suite](/blog/crocoblock-review/)** with its central and incredibly powerful plugin - JetEngine.
## When Custom Hooks Are Not the Solution
When mentioning “custom code,” I don’t mean quite harmless CSS custom rules, but PHP functions or PHP + JavaScript solutions hooked into WordPress to control behavior, output, or dynamic interactions. However, hooks are not as bad, if not overused, but the worst scenario is hardcoding theme files directly.
Writing such custom code snippets might seem like a flexible solution, but it often comes with hidden drawbacks. They can conflict with plugins or theme updates, break silently when WordPress changes its core behavior, and are harder to debug, especially when multiple snippets interact in unexpected ways. Maintaining them over time becomes a burden, especially in larger projects or when working in teams. Plus, what starts as a “quick fix” often turns into a tangled mess that's difficult to scale or hand over to another developer.
Let’s talk about such drawbacks more specifically.
## Drawbacks of Custom Code Snippets
Using custom PHP or JavaScript snippets in WordPress is a common way to add dynamic functionality, but it’s not always the best long-term approach. Here’s why:
- **Conflicts and compatibility issues** can arise, as custom code can easily clash with plugins, themes, or even core WordPress updates. What works today might silently break tomorrow.
- **Debugging** gets complicated because when something goes wrong, it’s not always obvious which snippet is the culprit. Especially in projects where multiple devs have added logic over time.
- **Poor scalability**. As your project grows, what started as a simple piece of code can turn into an unmanageable web of dependencies and conditionals.
- **Not easy to maintain** and client-friendly. If you're handing the project off to a client and their maintenance team is less technical or just can’t track all your custom snippets, it will be a big issue if something needs to be changed.
As you can see, tweaking WordPress functionality using code snippets is not really a sustainable solution, unless it’s just a couple of things to be changed. And, if such a need arises, here are some recommendations.
## What If You Still Need Some Custom Code?
Sometimes, custom code is unavoidable, especially for very specific functionality that no plugin covers. In that case, here’s how to do it right:
- If your snippet relies on specific plugins, post types, or user roles, clearly indicate this in the **code comments, readme file, or website documentation**.
- Use **dedicated plugins** for code snippets, so you can clearly see what is working under the hood, debug, and deactivate them.
- Wrap bigger code chunks into **custom plugins** instead of dumping snippets into functions.php. This keeps your logic separate from the theme, making it portable and avoiding accidental loss during theme updates.
- Stick to WordPress best practices and use **actions and filters (hooks)** instead of hardcoding things into templates. This keeps your code flexible and easier to troubleshoot.
## Meet the Crocoblock Tools: No-Code Powerful Solution for Dynamic Websites
[Crocobloc suite](https://crocoblock.com/plugins/) is 20 plugins plus the JetFormBuilder form plugin. All of them have an accent on dynamic content. Most of the plugins are premium and can be purchased separately; however, the most profitable method is to opt for the All-Inclusive plan, which costs $199 per year for one site and $399 for unlimited sites. Lifetime deals are also available.
Most of the plugins are made for dynamic content, filtering, bookings, and forms that work with the Block Editor, Elementor, and Bricks. In the future, Divi compatibility will also be available. And, there are also Elementor add-ons that extend the builder’s functionality.
The key plugin that adds a lot of functionality under the hood is **JetEngine**– it’s, as the name suggests, comparable to the powerful jet engine that puts your website on steroids. The module system, which allows you to switch components on and off, makes the website lightweight, plus, the Performance settings provide full control over builder-support loading.
And, of course, it has seamless compatibility with the rest of the plugins, extending their functionality. Using it, you can create custom post types, custom fields, taxonomies, relations, or compact content types called Custom Content Types that are perfect for a performance boost.
But the uniqueness of this plugin comes at the point when the data should be queried - the unique Query Builder tool can do it for you using a friendly visual UI.
Then, to display it on the front end, you can use the template editor and your favorite builder, from Elementor or Bricks, to the Block Editor or even Twig, if you prefer the lightest DOM structure. There are calendars, tables, sliders, and maps available to display your content on the front end with no effort.
Not to mention that JetEngine’s REST API functionality offers more features than even dedicated premium plugins.
This is just [JetEngine](https://crocoblock.com/plugins/jetengine/), and I will talk more about the details later.
But there are more plugins: the feature-rich JetFormBuilder, powerful and user-friendly JetSmartFilters, JetBooking and JetAppointment for flexible booking functionality, JetSearch offers flexible and controllable search functionality, JetThemeCore is responsible for Theme Building for Elementor and Block Editor, JetWooBuilder will help you to edit Elementor WooCommerce templates, and much more in the full Crocoblock toolkit.
So, here are some of the use cases when custom code can be easily replaced by the fully visual functionality of Crocoblock plugins.
## Modifying WooCommerce Templates in Elementor
*Crocoblock plugins involved: JetWooBuilder, JetThemeCore (optional)*
While WooCommerce is a very powerful tool, it lacks flexibility in template editing, and to hide or move some sections in any of its templates, you will need to write a hook to first hide it, then (if you move it), display it but with another priority. In case you want to change the visual appearance of elements, you will have to find their CSS classes and add custom CSS to make the changes. But if you want to add animation or change behaviour requiring JavaScript, you have to be careful and make sure that the script will not affect other elements.
Here is where **JetWooBuilder** comes to the rescue - it’s a more in-depth and flexible solution than the similar functionality of Elementor Pro, not to mention that, if you use free Elementor, this functionality is not available.
For example, this is the code you need to move the "Add to Cart" button a bit higher and place it under the title:
```php
/* Unassign the old priority */
remove_action( 'woocommerce_single_product_summary', 'woocommerce_template_single_add_to_cart', 30 );
/* Assign the new priority */
add_action( 'woocommerce_single_product_summary', 'woocommerce_template_single_add_to_cart', 6 );
```
With JetWooBuilder, you can do it just by dragging and dropping elements wherever you want them to be. In combination with **[JetThemeCore](https://crocoblock.com/plugins/jetthemecore/)**, you can also add custom headers and footers and different templates for particular user roles, devices, query variables, etc.
## Fetching Any Content From WordPress Database
*Crocoblock plugins involved: JetEngine*
Let’s say I have the Event custom post type, and want to fetch values of custom fields “date,” “event name,” and “event description.” It’s a very simple query, just for demonstration, but this is how it looks as a code based on the WP_Query PHP class:
To show the data on the front end, I can wrap the code in a shortcode and use HTML containers around each field so I can style them later with CSS.
But what if I want to show only events by a specific author? Or filter them by category, or display only the ones where a certain custom field has a specific value? That’s where it starts getting tricky. I’d need to write a new custom query for every case, and those queries can get long and messy fast. Plus, I wouldn’t be able to control anything from the WordPress dashboard. Every time something changes, I’d have to go back to the code.
Sure, page builders like [Elementor](/blog/elementor-review/) Pro or Bricks let you show posts and users with some filtering, but they hit a wall when things get more complex. For example, if I want to get a list of users who published something last week, or people with birthdays coming up next month, or if I want to filter inside repeater fields, that’s not something WP_Query can easily handle. And at that point, I’d need to write raw SQL.
That’s exactly where JetEngine’s Query Builder comes in. It lets you build those complex queries visually - combine different conditions, filter by anything you want, set the sort order, and even create multi-layered queries without touching code.
After querying, you don’t have to worry about HTML and CSS - there’s a visual Listing Templates builder, so you can design every loop element and then display it as a grid, list, table, calendar, slider, or on the map.
## Collecting Data From Different Websites on One Site Using REST API
*Crocoblock plugins involved: JetEngine, JetFormBuilder*
Imagine a scenario where several websites are collecting registration data for an event using forms, and all that data needs to be gathered and displayed on a central website. Why use multiple sites instead of redirecting users to one? There are plenty of practical reasons - separate campaigns with unique user flows, regional discounts, or different language and location-specific versions.
In this setup, you have a **Central** site (where the data is collected and displayed) and sites **A** and **B** (where users submit their registrations). The communication between them is handled via the REST API. And even today, if you want to build something this connected and dynamic, you're still going to need custom code.
This is an example of code just to send data from sites A and B, where you should connect the submit event of your form so it would trigger the sending process:
Then you will need twice as many lines of code to register a REST API endpoint on the Central site and, finally, write a query to fetch it and then somehow display it on the front end.
There’s also an additional layer of coding and testing to control security, so your website would not receive some random spam instead of registrations.
Goot news that JetEngine [can handle it fully visually](https://crocoblock.com/blog/jetengine-rest-api-new-features-and-use-cases), in **three simple steps**:
- On the Central site, create a “Participants” CCT (custom content type that stores data on a separate DB table, not to bloat your wp_posts table) and switch the REST API endpoint toggle to the ON position - you will get the endpoint URL generated. You can configure security settings right there.
- On the A and B sites, create JetFormBuilder forms. Choose REST API Request on the post-submit actions on the form settings, and paste the endpoint URL from the Central site.
- Congrats! The form records will be saved on the Central website in the “Participants” CCT, which you can display on the front end by creating a Listing Template by JetEngine fully visually.
There’s a second way to display, not only form submission, but any data from website A on website B. On the website B, go to **JetEngine > JetEngine** and open the REST API tab. There, insert the API endpoint for the post type from site A that you want to display on site B. For example, you have “Doctors” post type on website A. The URL will be:
[https://website-A.com/wp-json/wp/v2/doctor](https://website-A.com/wp-json/wp/v2/doctor)
Insert it there, adjust the security, and test the connection.
Then, go to **JetEngine > Query Builder** and choose the REST API query type (yes, you can query even data from remote sites using Quethe ry Builder) and define what exactly you want to display - you can choose among all available fields.
And, finally, create a Listing Template based on this query.
## Other Cases When You Don’t Need to Code If You Have Crocoblock
**Show or hide blocks based on user status or role, device, time of the day, time period, etc.**
Use [JetEngine’s Dynamic Visibility](https://www.youtube.com/playlist?list=PL26jaHWVtLFyay_zj-NFxi0MgxEYdYIYw) to control whether a section appears based on whether the user is logged in, has a specific role, or even based on their custom meta fields - no PHP *IF* statements or role checks needed.
In case you want conditional visibility on the post level (header, body, footer), use a variety of conditions by JetThemeCore.
**Display different form steps or fields depending on user input** with [JetFormBuilder](https://jetformbuilder.com/) Conditional Block. You can make certain fields or entire sections of a form appear only when specific conditions are met.
- Create posts, register users, call webhooks to connect third-party services, or custom hooks on your website, register or remove relations on post submit, thanks to the big list of post-submit actions by JetFormBuilder.
- Use the **Context feature** - you can use any of the Listing Templates and add Context (e.g., Current User, Current Query), etc., to show specific data. Normally, it takes custom-coded PHP templates to specify the context.
- **Dynamic tables with post meta fields or WooCommerce products. Crocoblock offers two solutions for building dynamic tables - one is the JetEngine’s module, and your table will be based on a Query Builder query, which, as you already know, can fetch any data. You can also add buttons and even create templates for each table cell**.
There’s also a **JetProductTables** plugin specifically for WooCommerce to create tables listing products or product variation tables easily. Buttons and sorting functionality are available.
**AI Website Structure Builder.** This tool by JetEngine gets your prompt and, based on it, builds website structures: in under one minute, creates custom post types, custom fields, posts, and user relations, and AJAX-based filters by JetSmartFilters. You can re-prompt if you don’t like the result, and, of course, you can edit everything, having access to everything from one dashboard.
## Takeaway
Using some custom code snippets can be handy, but only up to a point. When your site starts relying on too many of them, it’s worth asking if there’s a better, more solid solution out there. Crocoblock plugins give you the flexibility and power to build almost any kind of site - from membership portals to booking systems and custom dashboards, without drowning in code.
That said, if your site has lots of content and heavy database queries, you’ll definitely want a fast, reliable hosting provider like Rapid Cloud. Even the most powerful dynamic site can struggle with performance and SEO if its Core Web Vitals aren’t up to par.
---
## B2BKing Review: Powering WooCommerce B2B & Wholesale Stores with Ease
- URL: https://levamo.com/blog/b2bking-review/
- Category: ecommerce
- Author: Jayonta Sarkar
- Published: 2025-07-11
B2BKing review: Streamline your WooCommerce wholesale store effortlessly.
Managing a B2B e-commerce store comes with unique complexities that standard online stores don't face. You need to handle custom pricing for different customers, process bulk orders efficiently, manage quote requests, and set up varying payment terms based on business relationships. While WooCommerce excels as an e-commerce platform, it wasn't built with these specialized B2B requirements in mind.
## Why Use a WooCommerce B2B Plugin?
Enter [B2BKing](https://woocommerce-b2b-plugin.com/) - a comprehensive WooCommerce plugin designed specifically to transform your standard online store into a powerful B2B platform. This plugin brings essential business-to-business functionality to WooCommerce, including dynamic pricing structures, sophisticated customer segmentation, and streamlined bulk ordering capabilities. Whether you're a manufacturer selling to retailers, a distributor working with resellers, or any business that serves other businesses, B2BKing provides the tools you need to manage these complex relationships effectively.
The plugin's intuitive interface makes it accessible even for those without technical expertise, while its robust feature set ensures you can handle everything from simple wholesale operations to complex multi-tiered pricing structures. In this comprehensive review, we'll explore what B2BKing can do for your business, guide you through the setup process, and share best practices for getting the most out of this powerful tool when combined with high performance hosting solutions like Levamo.

## Key Features and Benefits of B2BKing
B2BKing transforms WooCommerce into a comprehensive B2B platform by addressing the specific needs that business customers have when making purchases. This isn't just another pricing plugin, it's a complete solution that handles every aspect of wholesale commerce.
**1. Dynamic Pricing:** Create sophisticated pricing structures that automatically adjust based on order quantities, customer groups, or product combinations. Set up tiered discounts, role-based pricing, and quantity breaks that reward larger purchases while maintaining profit margins across different customer segments.
**2. Customer Group Management:** Organize your business clients into distinct categories like wholesalers, VIP customers, or regional distributors. Each group can have customized pricing, product visibility, payment terms, and purchasing capabilities tailored to their specific business relationship with you.
**3. Quote Request System:** Enable customers to request custom pricing directly from your site. The integrated conversation system facilitates negotiations and allows for back-and-forth communication, making it easy to finalize deals and build stronger business relationships.
**4. VAT and Tax Management:** Automatically handle complex tax setups, including VAT exemptions for qualified business customers. The system manages tax exemptions and can also display prices including or excluding tax on different pages based on your requirements.
**5. Payment Flexibility:** Offer business-appropriate payment options including net terms (30/60/90 days), purchase orders, and credit limits alongside standard payment methods. This flexibility matches how businesses actually prefer to handle their purchasing and accounting processes.
**6. Minimum Order Controls:** Set minimum order quantities or values to ensure profitable transactions. You can establish different thresholds for various customer groups or products, helping maintain healthy margins while encouraging larger orders from business clients.**7. Bulk Order Forms:** Streamline large purchases with dedicated order forms that allow customers to quickly add multiple products and quantities without navigating individual product pages. Perfect for businesses that regularly order dozens or hundreds of items at once.

**8. Registration and Approval System:** Control who can access your B2B store with customizable registration forms that collect essential business information like company details, tax numbers, and business licenses. Set up automatic or manual approval workflows to verify legitimate business customers before granting access to wholesale pricing and exclusive products.
These features work together to create a professional purchasing environment that B2B buyers expect, ultimately leading to increased order values, reduced administrative overhead, and stronger customer relationships.
## Pricing: Which Plan Is Best For Your Business?
B2BKing offers three distinct pricing tiers designed to accommodate businesses of different sizes and needs. The plugin is available with both annual and lifetime licensing options, giving you flexibility in how you invest in your B2B infrastructure.
The **Startup plan** serves small businesses just entering the B2B space, priced at $199 annually or $699 for lifetime access. This entry-level option covers one website and includes all 139+ core features, monthly updates, and premium support, making it perfect for testing the waters with wholesale operations.
The **Pro plan** represents the sweet spot for growing businesses, offering the best value at $299 annually. This tier supports up to three websites and includes valuable add-ons like Company Credit, [Dokan](/blog/dokan-review/) integration, and WCFM compatibility.
For agencies and larger enterprises, the **Developer plan** at $399 annually or $1449 lifetime provides unlimited website usage along with high-priority support and backend white label options. This tier includes all premium add-ons and is ideal for developers managing multiple client projects, or for businesses running multiple platforms and websites.
All plans include the same comprehensive feature set, with the main differences being website limits and included add-ons. For businesses wanting to test the waters first, B2BKing also offers a [free version](https://wordpress.org/plugins/b2bking-wholesale-for-woocommerce/) available on the WordPress plugin repository. This lite version includes basic wholesale functionality and customer groups, giving you a chance to experience the plugin's core capabilities.
## Real-World Applications: How B2BKing Transforms Different Business Models
B2BKing's versatility shines when you see how different types of businesses leverage its features to solve specific challenges. Here are two compelling use cases that demonstrate the plugin's practical impact:
**Manufacturing Company Selling to Distributors**
A furniture manufacturer struggled with managing complex pricing for retail stores, interior designers, and distributors across different regions. With B2BKing, they created distinct customer groups: "Wholesale Distributors" with 40% off retail prices and $5,000 minimum orders, "Interior Designers" with 25% discounts and net-30 payment terms, and "Retail Partners" with 15% discounts for smaller quantities. The bulk order forms allow distributors to quickly add dozens of items, while quote requests enable custom pricing negotiations for large projects.
**Tech Supplier Serving Corporate Clients**
A technology equipment supplier needed to serve both small businesses and large corporations with different purchasing processes. B2BKing enabled them to segment customers appropriately: "Enterprise Clients" can use purchase orders with 60-day payment terms and access exclusive bulk pricing, while "SMB Customers" receive standard pricing with quantity breaks starting at 5 units. Different customer groups see tailored product catalogs: enterprises access high-end server equipment while smaller businesses see desktop computers and basic networking gear.
These examples illustrate how B2BKing doesn't just add features, instead it fundamentally transforms how businesses interact with their customers, creating more efficient processes and stronger relationships.
### Setting Up and Configuring The Plugin
Getting B2BKing up and running is straightforward, following WordPress's standard plugin installation process. Simply download the plugin file, upload it through your WordPress admin panel under Plugins > Add New > Upload, and activate it.
Once installed, the key configuration decision happens in B2BKing > Settings > Main Settings, where you'll choose between two operational modes that define how your store functions.

The **B2B Shop** mode is designed for businesses that exclusively serve other businesses - all customers are treated as B2B clients with access to wholesale features, bulk ordering, and business-specific tools.
The **B2B + B2C Hybrid** mode is where B2BKing really shines, allowing you to serve both business customers and individual consumers from the same store. This hybrid approach automatically manages the customer experience based on their account type. Business customers see B2B-specific features like bulk order forms, quote requests, and conversation tools in their account panel, while regular consumers get a standard e-commerce experience without B2B clutter.
This flexibility means you don't need to maintain separate stores or worry about confusing individual customers with wholesale-oriented features. Whether you're transitioning from B2C to B2B, expanding your market reach, or starting fresh with a dual-purpose store, B2BKing adapts to your business model rather than forcing you to adapt to the plugin.
## Performance and Hosting Considerations
When running a B2B WooCommerce store with B2BKing, performance becomes even more critical due to the complex operations involved: dynamic pricing calculations, customer-specific content, and bulk order processing all demand robust hosting infrastructure.
This is where specialized hosting solutions like Levamo make a significant difference. Built specifically for dynamic WordPress sites, Levamo's infrastructure is optimized for the kind of database-intensive operations that B2BKing performs. Their managed hosting platform handles the technical complexities, allowing you to focus on growing your business rather than troubleshooting performance issues.
For a deeper dive into B2B hosting requirements and performance optimization strategies, check out our comprehensive guide on[ WooCommerce B2B hosting and performance considerations](https://woocommerce-b2b-plugin.com/woocommerce-b2b-hosting-performance-what-really-matters/).
## Final Verdict: Is It Worth It?
B2BKing is a standout WooCommerce B2B plugin, delivering a robust suite of features that simplify wholesale and B2B management. From dynamic pricing to bulk order forms, it empowers store owners to scale efficiently. Paired with Levamo’s high-performance hosting, it’s a winning combo for any B2B store. If you’re looking to elevate your WooCommerce site, B2BKing is a must-try.
B2BKing is a capable plugin, but it isn’t the only option in this space - and the right choice depends on how you price, sell, and manage wholesale customers day to day. If you’re still deciding, a direct feature-by-feature comparison is the fastest way to see which one fits your store. See how the two line up in [Wholesale Suite vs B2BKing](https://wholesalesuiteplugin.com/wholesale-suite-vs-b2bking/ "nofollow").
---
## Password Protected Plugin Review: Is It the Right Choice for WordPress Content Protection?
- URL: https://levamo.com/blog/password-protected-plugin-review/
- Category: website-development
- Author: Javeria
- Published: 2025-05-19
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See if Password Protected is right for your WordPress content!
If you've ever needed to keep parts of your WordPress site private - whether it's a client's staging site, an internal resource hub, or a personal blog - you're not alone. Website owners across industries are looking for simple, reliable ways to lock down their content without diving into complex membership systems or advanced user roles.
That's where the [Password Protected](https://passwordprotectedwp.com/) plugin can help. With over 300,000 active installations, it offers a straightforward way to restrict access to your entire site or specific areas using a single password - no coding, no user accounts, just a lock and key.
In this review, we'll walk you through what the Password Protected plugin actually does, real use cases, pros and cons, who it's best for, and whether it's a smart choice for your WordPress website.
Ready? Let's get started!
## Why Use Password Protection on Your WordPress Site?
Not every WordPress site needs to be wide open to the public. In fact, there are plenty of situations where you might want to keep things private - at least for a while. Whether you're working on a new website, sharing client work-in-progress, or building out internal resources, password protection gives you control over who sees what.
Here are some common scenarios where password-protecting your WordPress site makes a lot of sense:
- **Client staging environments:** Agencies and freelancers often create staging sites to show work before going live. You don’t want competitors or Google indexing it early.
- **Internal documentation:** If your team uses WordPress to manage SOPs, guides, or training materials, locking that content behind a password adds a layer of privacy.
- **Private portfolios or membership previews:** Artists, designers, and creators sometimes share exclusive content with selected people before public release.
- **Temporarily unpublished sites:** Businesses in the middle of a redesign or rebrand can use password protection to keep the “construction zone” off the public radar.
- **School or nonprofit content:** Educators and organizations might want to make content available only to students, volunteers, or members.
## What is the Password Protected Plugin and Why?
Password Protected is a free WordPress plugin developed by WPExperts and originally created by Ben Huson. It offers a quick way to password-protect your entire site without forcing you to manage user accounts or complicated permissions.
Currently, this plugin powers over 300,000 WordPress websites, which makes it one of the most widely trusted plugins for simple content restriction.
At its core, Password Protected does one job really well: it blocks all front-end access to your website unless a visitor enters the correct password. You don’t have to set up user accounts or membership rules. Just toggle it on, set your password, and the plugin takes care of the gatekeeping.
For example, you can:
- Allow logged-in users (like admins or editors) to bypass the password screen.
- Whitelist specific IP addresses - handy for office networks or client teams.
- Protect WooCommerce products, pages, or categories (great for private stores or wholesale catalogs).
- Add a layer of login security with Google reCAPTCHA to stop bots from hammering the password form.
- Temporarily unlock the site using a secure “bypass URL” (available in the Pro version).
Even though WordPress has a built-in password option for individual posts or pages, it automatically doesn't offer full-site protection. That's where Password Protected comes in handy - allowing you to shield your entire site or specific sections with just a few clicks.
## Key Features of the Password Protected Plugin at a Glance
The Password Protected plugin doesn’t try to do everything - but what it does, it handles with precision. It offers just the right mix of tools to make site-wide or partial content restriction quick and manageable.
Here’s a breakdown of its standout features:
### Site-Wide Protection
With one click, you can lock down your entire WordPress site. Visitors will land on a simple password protected screen, and only those with the correct password can get past it. This is ideal for new websites under development, private communities, or early client previews.
### Selective Content Protection
You don’t always need to block everything. The plugin allows you to restrict access to specific post types, categories/taxonomies, or WooCommerce products. Want to hide your wholesale catalog from retail customers? Done. Need to keep a blog series private? Easy.
### Role-Based Whitelisting
Sometimes you want team members, editors, or contributors to skip the password screen altogether. This plugin lets you whitelist specific WordPress roles - like Admin, Editor, or Author - so they can browse the site normally after logging in.
### IP Whitelisting
Don’t want to deal with passwords in your office or team’s workspace? Add your static IP address to the whitelist, and users from that location will never see the password prompt. This feature is especially helpful when you're collaborating with clients or internal departments.
### WordPress Login Page Protection
Worried about brute-force login attempts? You can add an additional password protected screen to the /wp-login.php page itself. That means bots can’t even get to your regular login screen unless they first solve the password challenge. It’s a smart way to cut down on spam and attack attempts.
### Google reCAPTCHA Support
If you’re worried about bots hammering the password form, enable Google reCAPTCHA. This feature adds an extra layer of protection by requiring human verification before the password is submitted. It’s available in both the free and Pro versions.
### Brute-Force Protection
The plugin also gives you the option to limit the number of incorrect password attempts. This adds a basic but effective defense against brute-force attacks - especially important for public-facing sites with any kind of sensitive information.
### Bypass URLs
With the Pro version, you can create a unique bypass link that lets users access your site without entering a password. This is perfect for one-time previews, media contacts, or temporary stakeholders who shouldn’t have to remember a login.
### Password Request
Give users a simple way to ask for access. When someone lands on your protected page, they can enter their email address to request the password. The plugin immediately sends that request to the site admin for review. The admin can approve or deny the request from the WordPress dashboard with a single click. If approved, the user automatically receives the password by email - no manual follow-up is needed.
Each of these features contributes to a smooth and flexible user experience. You get complete control over who can see your site or specific content, without setting up user accounts, permissions, or membership levels. It’s everything most WordPress users need to quickly make their site private - nothing more, nothing less.
## How to Install and Set It Up
Getting started with the Password Protected plugin takes less than five minutes - even if you’ve never installed a plugin before. Its lightweight setup makes it an attractive choice for developers and beginners alike.
Here's a step-by-step walkthrough to help you activate and configure it the right way.
- From your WordPress dashboard, go to **Plugins → Add New**.
- Search for “Password Protected.”
- Click **Install Now**, then **Activate**.
- Click the **Password Protected** option from the sidebar
- Toggle **Password Protected Status** to "Enabled."
- Enter your desired password.
- Configure access settings (e.g. allow admin users, whitelist IPs).
- Save your changes.
To test, open your site in a private browser or log out. You should see a password prompt before your site loads.
For more information, check out the detailed [technical documentation](https://passwordprotectedwp.com/documentation/).
## Pros and Cons
### Pros
- **Easy to Use:** You can get it running in minutes with no learning curve.
- **Free and Powerful:** The core features cover most basic use cases.
- **Reliable:** Used on over 300,000 sites and updated regularly.
- **Flexible Access:** Supports user role and IP whitelisting.
- **Lightweight:** Doesn’t slow down your site or clash with most themes/plugins.
### Cons
- **Single Password (Free):** The free version allows only one global password.
- **No Media Protection:** Images and files aren’t restricted if someone has the direct link.
- **Pro Features Are Locked:** Features like multiple passwords and bypass links are Pro-only.
- **Caching Conflicts:** May require cache clearing to reflect changes properly.
## Pricing and Support
The base plugin is completely free. For many users, especially those who just need simple site-wide protection, the free version is more than enough.
If you want more control, such as multiple passwords or private links, you’ll need the Pro upgrade. Pricing isn’t listed directly in the plugin directory, so you’ll need to visit the official website for Password Protected.
Support is available through the WordPress.org support forum. Pro users can get priority help via the support channel available on the plugin’s website.
## Who Should Use This Plugin?
- **New WordPress Users** who want to hide their site while it’s under construction.
- **Agencies and Freelancers** sharing staging environments or work-in-progress with clients.
- **Small Businesses** that need to protect sensitive content like internal documents or resources.
- **Online Stores** (using WooCommerce) that want to create hidden product areas (with the Pro version).
## What About SEO?
Protected content won’t show up in Google results because search engines can’t crawl password-locked pages. That’s great for privacy, but if you want your site to rank, you’ll need to leave some pages publicly visible.
**We recommend:**
- Keeping a public homepage or blog to maintain visibility.
- Only locking down pages with private or exclusive content.
- Using a custom 403 or password form with branded messaging to keep the experience polished.
## Final Verdict: Is It Worth It?
If your goal is to add a simple password gate to your WordPress site without extra hassle, then yes - Password Protected is a solid choice. It’s lightweight, easy to configure, and doesn’t require user accounts. For many use cases, that’s exactly what you need.
But if your site requires multiple layers of control, user-specific access, or advanced content segmentation, you may outgrow it quickly and need to explore more robust options.
Either way, this plugin offers a great starting point, especially for beginners or small businesses keeping things lean.
## Take Your Site’s Security Further
Adding password protection is one piece of the puzzle. For full protection, combine it with secure hosting, regular updates, and tools like firewalls or malware scanners.
👉 **Check out**[ **Levamo’s Managed Hosting for WordPress**](/managed-wordpress-hosting/) to get speed with expert-level security and support that’s ready 24/7.
Looking for more ways to lock down your WordPress site? Don’t miss these Levamo guides:
- [13 Best WordPress Security Plugins to Safeguard Your Site in 2025](/blog/best-wordpress-security-plugins/)
- [Automate Your WordPress Security with Patchstack on Levamo](/blog/automate-with-patchstack/)
- [WooCommerce Fortress: The 2025 Security Checklist](/blog/woocommerce-security-checklist/)
With the right tools, you can take full control over who sees your content - and who doesn’t.
---
## 9 Reasons Why WP Umbrella Is a Must-Have for Busy WordPress Agencies
- URL: https://levamo.com/blog/wp-umbrella/
- Category: website-development
- Author: Javeria
- Published: 2025-05-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WP Umbrella eases WordPress maintenance for agencies. See 9 reasons why.
Every WordPress agency hits this wall. You start with a few sites. Easy to manage. Then you add a few more. Suddenly you’re deep in plugin updates, downtime alerts, keeping track of backups, and more.
That’s the moment agency owners discover [WP Umbrella](https://wp-umbrella.com/). It’s the silent operator behind hundreds of WordPress agencies - handling all the behind-the-scenes maintenance - so you don’t have to.
Here are 9 reasons why it’s a must-have tool for busy agencies:
## 1. A Dashboard That Tells You Everything You Need to Know
This is where the magic happens. WP Umbrella gives you a clean, simple view of all your websites in one place.
Need to check for updates? Done.
Want to know if backups ran? Easy.
Anything sketchy happening that might blow up in your face during a client call? You’ll see it here.
No guesswork. No clutter. Just one powerful dashboard that keeps your agency running smoothly.
## 2. Bulk Updates That Don’t Break Your Sites
If you’re doing it manually, updating plugins across dozens of sites can be a full-time job. And one bad update can break everything.
WP Umbrella thinks of that. You choose exactly what to update and what to skip. And you get to do it in bulk, with just a few clicks, for all your websites. If something doesn’t go according to plan, it rolls things back to the way they were before. So, no broken websites because of a tricky plugin update.
Result: Hours saved every week and way fewer fires to put out.
## 3. Auto Cache Clearing
As an added bonus, after you run your updates, WP Umbrella can auto-clear cache for you. It’s a small thing, but it's another task off your plate.
## 4. Scheduled Backups That Your Site Needs
You know it: backups are non-negotiable. And not just one, actually.
WP Umbrella stores encrypted backups on GDPR-compliant servers in France. You can schedule them however you want - monthly, weekly, daily, even hourly. After the first full backup, everything else is incremental. Fast, efficient, and safe.
In case you need to restore, one click is all it takes and you’re back in business.
## 5. Monitoring That Works While You Sleep
With WP Umbrella, you’re the first to know if your site goes. No more uncomfortable calls from panicked clients telling you there’s something wrong with their site.
WP Umbrella keeps an eye on uptime, performance, SSL certificates, domain expiries, PHP versions… you name it. If something goes wrong, you get an alert via email or Slack, right away.
This way you get to fix it before your client even knows there was a problem.
## 6. Vulnerability Scanning on Autopilot
Every 6 hours, WP Umbrella scans your sites for vulnerabilities - powered by [Patchstack](/blog/automate-with-patchstack/) (aka the big dogs in WordPress security).
That means if a plugin goes sideways or a theme update has a hole in it, you’ll know about it *before* it becomes a problem. That’s the kind of quiet win that keeps clients loyal and your work days drama-free.
## 7. Client Reports That Actually Impress
The truth is: your clients don’t care about the technical details. They just want proof that their site is being looked after.
WP Umbrella helps you create clean, professional reports - fully branded with your logo, colors, and even custom work notes.
It takes a few minutes to set up and it will show your clients the value they’re paying for every month.
## 8. 1-Click Admin Login (You’ll Never Chase a Password Again)
You ever wasted 5 minutes trying to find a login link for a client site? All while juggling five tabs trying to remember where the hell the admin page even is.
WP Umbrella kills that nonsense. With 1-click admin login, you hit a button in your dashboard and you’re in. Just like having a master key to every site you manage.
## 9. Get Started in Minutes (Literally)
Some tools make you feel like you need a PhD just to get started. WP Umbrella? It’s stupid simple.
**Step 1: Create your free account** - No credit card required. Just sign up in a few clicks.
**Step 2: Grab your API key** - It’ll show up on your screen the second you register.
**Step 3: Install the plugin** - Search for “WP Umbrella” in the WordPress plugin directory. Click “install” and then “activate”.
**Step 4: Connect your site** - Paste the API key into the plugin settings. Save. And that’s it - you’ll be automatically redirected to your personal dashboard.
Next, you can repeat the process across all your sites. Or, if you’re using another WordPress management tool at the moment - even better - WP Umbrella’s team will **migrate all your sites for free. You don’t lift a finger, just send a request at [support@wp-umbrella.com](mailto:support@wp-umbrella.com)**.
## Bonus Point: Straightforward and Transparent Pricing
You get [all WP Umbrella features for just $1.99 per site/month](https://wp-umbrella.com/pricing/). That’s it. You don’t need a math formula to figure out your return on investment. And if website care plans are part of your agency’s offer, you’ll be getting juicy ROI from this tool.
## Bottom Line
WP Umbrella gets the job done without getting in your way.
- One dashboard that tells you what’s important.
- Bulk updates that won’t break your sites.
- Automated backups you can trust.
- Real-time monitoring and alerts so you’re never caught off guard.
- Clean reports that show your value.
- Reports that make your agency look like an A player.
If you want less stress, more productivity, and loyal clients who stick around longer - [try **WP Umbrella** for free](https://app.wp-umbrella.com/). No credit card is required.
### Bonus for Agencies Handling High-Traffic Sites
If your agency manages sites with growing traffic or seasonal spikes, WP Umbrella pairs perfectly with a high-performance hosting provider like Levamo’s [fully managed WordPress hosting](/managed-wordpress-hosting/). With built-in [free WordPress CDN](/cloudflare-cdn/), automatic scaling, and server-level optimizations, it ensures your clients' websites stay fast and available, even during traffic surges.
---
## WebToffee WooCommerce PDF Invoices Plugin: A Must-Have for WooCommerce Stores
- URL: https://levamo.com/blog/woocommerce-pdf-invoices-plugin/
- Category: ecommerce
- Author: Javeria
- Published: 2025-05-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Automate WooCommerce invoicing with WebToffee's PDF Invoices plugin.
If you’ve ever had to manually create, send, or print invoices for your WooCommerce store, you know how tedious it can be, especially if you receive hundreds of orders every day.
That’s where the WebToffee WooCommerce PDF Invoices plugin comes into play. It’s one of those tools that quietly handles the heavy lifting so you can focus on more important things, like marketing, product development, or, let’s be honest, grabbing a second cup of coffee.
WebToffee offers a suite of invoice and label generator plugins to help you streamline the order fulfillment process on your WooCommerce store. They cover everything from bulk printing and emailing invoices to tax-compliant UBL/XML generation.
In this article, we have made a detailed review of the [WebToffee WooCommerce PDF invoices](https://www.webtoffee.com/product/woocommerce-pdf-invoices-packing-slips/) plugin along with its free and premium add-ons.
## Why Invoicing Plugins Matter in WooCommerce?
Out of the box, WooCommerce does a great job handling products and payments, but when it comes to documentation, things get a little barebones. There’s no built-in system for generating PDF invoices, packing slips, or shipping labels. That might be fine for hobby stores, but it’s a significant pain point once your order volume starts to climb.
Manually generating PDF copies of invoices and attaching them to order emails isn’t just time-consuming - it’s prone to errors and doesn’t scale. And if you're dealing with VAT requirements, GST, or B2B clients, chances are you’ll need more than a basic printout.
That’s why a plugin like the WebToffee Invoice plugin makes such a difference. It automates the entire process and gives you complete control over how your invoices look and function, helping you stay compliant, reduce busywork, and deliver a smoother customer experience.
## WebToffee’s Free WooCommerce PDF Invoices Plugin: Ace of Base
Let’s start with the free version of the plugin, which is surprisingly capable right out of the box. For many small to medium stores, it might be all you need.
### Supported Document Types
The free [WooCommerce print invoice plugin](https://wordpress.org/plugins/print-invoices-packing-slip-labels-for-woocommerce/) supports a range of essential documents, including invoices, packing slips, shipping labels, delivery notes, and dispatch labels. You can easily download any of these documents directly from the order page - perfect for quickly resending or reprinting an invoice without digging through settings.
### Customization Options
Brand customization is built in, allowing you to add your store logo, name, tax identification details, and more to personalize your documents. When it comes to managing multiple orders, bulk printing capabilities let you print documents for several orders in one go, which is especially useful during high-volume sales periods.
### Automatic Email Attachments
The plugin also takes care of sending invoice PDFs automatically via email with WooCommerce order updates, reducing manual effort. Customers can access and download their invoices directly from their My Account page, enhancing convenience on both ends.
### Compatible with UBL and XML Invoices
For B2B needs, the plugin offers UBL and XML invoice generation, enabling compliance with standardized digital invoicing formats. You can also customize invoice numbers by adding prefixes, suffixes, or defining your own numbering format to suit your bookkeeping system.
### Support for Multilingual Invoices
Multilingual support is baked in, with full compatibility for right-to-left (RTL) languages like Arabic or Hebrew, making it a solid choice for international stores. Before printing, you can preview your documents to ensure everything looks just right.
Lastly, if you're handling free or zero-value orders (like giveaways or samples), the plugin allows you to disable invoice generation for those specific cases, keeping your records clean and clutter-free.
It’s clean, stable, and does exactly what it promises. For most small stores, this free version handles day-to-day needs without breaking a sweat.
## Deep Dive into the Premium Add-On: WebToffee WooCommerce PDF Invoices Plugin
Once your store starts picking up momentum, it becomes crystal clear that the basic invoicing tools just don’t cut it. That’s where the premium version of the [WebToffee WooCommerce PDF Invoices](https://www.webtoffee.com/product/woocommerce-pdf-invoices-packing-slips/) plugin shines. It’s built for store owners and developers who want to automate, customize, and control every aspect of their order documentation process, with zero friction.
Here’s a detailed breakdown of what you get, and more importantly, why it actually matters:
### Auto–Generate Invoices, Packing Slips, and Credit Note
You don’t want to generate invoices every time an order comes through manually. With this add-on, invoices, packing slips, and credit notes are automatically created when orders hit a specified status (like “Processing” or “Completed”). It’s a massive win for efficiency, especially during busy periods.
### Use Ready-to-Use Templates or Customize Your Own
The premium invoice plugin offers multiple pre-designed templates that are clean, functional, and look great. But if you want to stand out or meet specific branding requirements, you’ve got full control over the layout.
**What’s unique here?** You can choose between a **visual editor** (drag-and-drop style) and a **code editor** (for custom tweaks). Developers will appreciate the flexibility. Store owners without coding experience will love the simplicity.
Whether you need to move tax info to the top, add a watermark, or include your ISO certification number, this plugin makes it happen.
### Bulk Print or Export Documents by Filters (Order Status, Date, etc.)
If you’ve ever printed documents one by one, you’ll know how painful that is. The premium version lets you bulk print invoices, packing slips, or credit notes, filtered by order status, customer, shipping method, or even date range.
You can also bulk export all documents in a ZIP folder, which is super handy for archiving or accounting.
### Advanced Invoice Number Customization
Need to format invoice numbers for legal or organizational reasons? This plugin’s got your back. Use dynamic placeholders like {YYYY}, {MM}, or custom prefixes/suffixes (e.g., INV-2026-0001) to match your accounting style or regional standards.
This feature is a lifesaver if you're running multiple stores or channels and need clear identifiers for tracking and audits.
### Add Custom Tax Details (VAT, GST, ABN, etc.)
Global eCommerce isn’t a one-size-fits-all game. If you sell to the EU, Australia, or India, you probably need to include region-specific tax IDs like VAT numbers or GSTINs.
WebToffee’s premium invoice plugin lets you add these fields to your invoices and other documents alongside company details. That means fewer compliance worries and smoother experiences for your customers (and accountants).
Depending on your customer type, you may want to show gross (tax-inclusive) or net (tax-exclusive) prices. You can easily set how prices appear on your documents, either globally or per document type.
It’s especially helpful for hybrid stores selling to retail and wholesale customers.
### Pay Later Option via Invoice
If you want to offer “Pay on Invoice” for B2B clients, this plugin can make that happen. It will add a payment link on the invoice, enabling customers to pay using the invoice. This bridges the gap between online checkout and traditional invoicing, making your WooCommerce store compatible with more corporate buying workflows.
Pay-on-invoice is table stakes for wholesale, where buyers expect net terms, purchase orders, and proper documentation rather than paying upfront at checkout. [Getting that invoicing flow right](https://wholesalesuiteplugin.com/wholesale-invoices/ "nofollow"), and tying it to wholesale-only pricing, is its own piece of the puzzle.
## Other Premium Invoice Add-Ons in the WebToffee Ecosystem
WebToffee doesn’t stop at PDF invoices. They’ve built an ecosystem of complementary plugins that cover every documentation touchpoint in your WooCommerce workflow.
Here are some other premium add-ons worth mentioning:
- **WooCommerce Address Labels:** No more copy-pasting shipping addresses into third-party tools. This plugin lets you print professional address labels with ease, customizable with logo, font styles, and layout options.
- **WooCommerce Shipping Labels & Delivery Notes:** Generate shipping labels tailored to your shipping carriers and formats. Add barcodes, shipping instructions, and tracking info to streamline the final leg of delivery.
- **WooCommerce Proforma Invoices:** Perfect for stores that need to send pre-invoice documents before payment - common in B2B setups or for high-value, custom orders. You can create and send proforma invoices independently of the main invoice plugin.
- **WooCommerce Picklist plugin:** If your fulfillment team struggles to stay organized, this one’s a must. The picklist plugin generates printable picking lists from your orders, including relevant details such as product names, quantities, etc.
- **Remote Print Add-on:** Automatically print invoices, packing slips, or labels via PrintNode as soon as an order is placed. Perfect for warehouse automation, multi-location fulfillment, or reducing manual printing tasks in high-volume WooCommerce stores.
- **mPDF Add-on for WooCommerce PDF Invoices:** Switch the default rendering engine to mPDF for better support of RTL languages, complex layouts, and multilingual content. Ideal for stores using Arabic, Hebrew, or Asian languages that need cleaner, more accurate PDF output.
- **QR Code Add-on for WooCommerce PDF Invoices:** Add customizable QR codes to invoices for fast order scanning, tracking, or verification. Great for improving warehouse efficiency and customer support with smart, scannable order data.
Together, these add-ons give store owners the freedom to build a documentation workflow that fits their exact needs, without bloating the store with features they don’t use. It’s modular, efficient, and smart.
**Also Read:** [10 WordPress Features You Probably Didn’t Know About (But Should)](/blog/10-wordpress-features-you-probably-didnt-know-about-but-should/)
## Final Verdict: A Serious Time-Saver That Scales With You
There are a lot of WooCommerce PDF invoice plugins out there, but most either feel too basic or too bloated. WebToffee strikes the perfect middle ground. It’s robust, thoughtfully designed, and genuinely useful whether you’re just starting out or managing thousands of orders per month.
Best of all, you don’t have to commit to a premium plan right away. The free version is strong enough to get started, and when you’re ready to scale, the premium add-on unlocks everything you need.
If you’re looking to streamline your documentation process and bring your order fulfillment workflow up to professional standards, WebToffee’s WooCommerce PDF Invoices plugin is a smart, stress-free choice.
For best results, consider pairing it with optimized [WooCommerce Managed Hosting](/managed-woocommerce-hosting/) to ensure speed, uptime, and scalability.
---
## How to Land High-Ticket Clients & High-Ticket Sales (Without Losing Your Mind)
- URL: https://levamo.com/blog/high-ticket-sales/
- Category: online-business
- Author: Sunyyan Junaid
- Published: 2025-05-09
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Get high-ticket clients and sales without the overwhelm. Read now!
Remember when you started your business and were thrilled to get *any* client? Yeah, me too. The days of doing a happy dance over a $50 sale seem like a distant memory now. But here's the thing: there comes a point when chasing a hundred small clients starts feeling like herding cats through a thunderstorm.
That's when you realize maybe it's time to go after the big fish.
High-ticket sales aren't just about adding zeros to your price tag. They're about fundamentally changing how your business operates, who you serve, and honestly, how much sleep you get at night.
## What Makes a Sale "High-Ticket" Anyway?
Let's get real for a second. High-ticket doesn't just mean "expensive", it means *valuable*.
In my 10+ years at Levamo, I've seen businesses slap premium prices on mediocre products and wonder why nobody's biting. Spoiler alert: a $3,000 price tag doesn't automatically make something worth $3,000.
Here's my practical definition: A high-ticket offer is typically:
- Starting at $1,000 minimum (though this varies wildly by industry, what's "high-ticket" for a freelance writer might be pocket change for an enterprise software company)
- Solving a significant problem or creating a meaningful transformation
- Requiring an actual conversation before purchase (no "Buy Now" button is closing this deal)
The magic of high-ticket sales is beautifully simple: sell fewer things at higher prices to people who actually value what you do. Revolutionary, right?
## High-Ticket Products That Fetch Real Dollars

I've seen some interesting attempts at high-ticket offers over the years. But the ones that actually work tend to fall into a few categories:
**Luxury Products**: The Rolex example is overdone, but it works for a reason. People aren't just buying a timepiece; they're buying the subtle nod from across the boardroom that says, "I've made it." The same goes for that Tesla you keep eyeing.
Transformative Services: Someone I know charges $25,000 for their business coaching program. Insane? Not when their average client sees a $100,000 increase in revenue. That's not a cost, it's an investment with a clear ROI.
**Enterprise Solutions**: At [Levamo](/), we've seen enterprise clients happily pay higher prices for custom infrastructure because the alternative is bleeding money through inefficient hosting solutions every month. When you can quantify the cost of *not* buying, price becomes secondary.
**Property & Big-Ticket Items**: My realtor friend makes the same commission selling one luxury home as she would selling five starter homes. Guess which one takes less time and emotional labor? (Hint: it's not the five transactions with first-time homebuyers freaking out about every small detail.)
## Why You Should Consider The High-Ticket Route (From Someone Who's Been There)
Look, I get it. The idea of charging premium prices can trigger a weird case of impostor syndrome. But let me share why targeting high-ticket clients changed everything for us at Levamo, and why it might do the same for you.
### 1. The Math Makes Life Better
Remember algebra? Yeah, me neither, but this equation is simple:
5 clients × $10,000 = 50 clients × $1,000
Same revenue, but *drastically* different workload. When we shifted to a high-ticket model, our support tickets dropped by 70% while our revenue stayed the same. I literally got my Sundays back. That alone was worth it.
### 2. Better Clients, Better Sleep
Here's something they don't tell you in business school: clients who pay more complain less. Counterintuitive, right?
Our $99/month clients would email at 11 PM demanding immediate fixes for problems they created. Our $10,000/month clients schedule calls, come prepared with questions, and send holiday gifts. The difference is night and day (and significantly fewer midnight panic attacks).
### 3. Your Brand Gets an Automatic Upgrade
There's something psychological that happens when you start attracting premium clients. Other premium clients start noticing. It's like when one celebrity starts wearing a particular brand, and suddenly all their celebrity friends are wearing it too.
When we landed our first Fortune 500 client at Levamo, three more followed within six months, without us changing a thing about our marketing. The snowball effect is real.
## All Your Websites. One Powerful Platform.
**Launch 5, 10, or 100+** websites on a single, powerful platform. **Zero compromise on performance, zero hosting chaos.**
## Inside the Mind of Your High-Ticket Client
Before you can sell to high-ticket clients, you need to understand how they think. And trust me, they don't think like bargain hunters.
### They're Buying Outcomes, Not Features
Nobody spends $10,000+ because your platform has a cool dashboard. They spend it because they believe you'll deliver a specific outcome that matters deeply to them.
Our highest-paying client didn't care about the price tag or the dashboard. They cared that their CEO wouldn't be embarrassed in front of the board again because the website had crashed during quarterly presentations. Specific outcome > general feature.
### They Take Their Sweet Time (And That's OK)
The sales cycle for high-ticket items is much longer. But here's the upside: once they're in, they're usually in for the long haul. Our average client retention jumped from 7 months to 3.2 years when we shifted to high-ticket services.
### They Want the White Glove Treatment
High-ticket clients expect customization. They don't want to feel like they're getting the same solution as everyone else, even if, let's be honest, the core offering is pretty similar.
At Levamo, we create custom onboarding experiences for our premium clients. Same product, same features, but a tailored implementation process that makes them feel special. Worth every minute of extra planning.
### Trust Is Non-Negotiable
Before someone hands you a five-figure check, they need to trust you deeply. And not just "I trust this person won't steal my money" but "I trust this person understands my business and can deliver exactly what I need."
This is why authority-building isn't optional in the high-ticket space, it's mandatory.
## How to Attract High-Ticket Clients (Without Being Sleazy)
Alright, let's get to the good stuff. How do you actually find and attract these mythical beings with healthy budgets and reasonable expectations?
### 1. Get Specific About Who You're Looking For
"Everyone with money" is not a target market. At Levamo, we specifically target Ecommerce, Membership sites, and Enterprise technology companies with 50+ employees who have outgrown their initial infrastructure.
The more specific you get, the easier it becomes to speak directly to your ideal client's pain points. Generic messaging attracts generic clients.
### 2. Become Unavoidably Credible
High-ticket clients need to see you as the obvious expert, not just another option. This isn't about claiming expertise, it's about demonstrating it relentlessly.
Some ways we've built credibility:
- Publishing detailed case studies (with real numbers)
- Creating thought leadership content that challenges industry norms
- Speaking at events our target clients attend
- Maintaining a strong, opinionated presence in industry conversations
The goal is simple: when your ideal client has the problem you solve, your name should automatically come to mind.
### 3. Network Like Your Business Depends On It (Because It Does)
Cold outreach can work for low-ticket sales. For high-ticket? Not so much.
Most of our premium clients came through relationships, either direct connections or referrals from existing clients. This is why I spend at least 20% of my work week nurturing relationships with no immediate sales agenda.
Pro tip: Focus on becoming a connector. When you regularly help others find opportunities or solve problems, they remember you when opportunities come their way.
### 4. Give Away Your Best Stuff
This might sound counterintuitive, but hear me out. When we started sharing our most valuable insights for free, the stuff we used to guard closely, our perceived value skyrocketed.
Our detailed guide on "Cloud Infrastructure Mistakes That Are Costing You $10K+ Monthly" generated more high-ticket leads than any paid advertising we'd done previously.
High-value clients aren't looking to get everything for free. They're looking for evidence that you know your stuff. Give them that evidence generously.
## Closing High-Ticket Deals Without Feeling Like a Car Salesman

You've attracted their attention. Now what? Here's how to close without the ick factor.
### 1. Master Consultative Selling
Forget pitching. High-ticket sales are about consultation. Our sales process involves at least two discovery calls before we ever talk numbers. We're genuinely trying to understand their business challenges and determine if we're the right fit.
Sometimes we refer prospects elsewhere because we know we're not their best option. This has resulted in some of our strongest referral partnerships.
### 2. Address Objections Before They Come Up
After hundreds of sales conversations, you start to notice patterns. We now proactively address the top three objections our clients typically have:
- "Isn't this more expensive than [competitor]?" (We discuss value and ROI immediately)
- "What if implementation disrupts our operations?" (We outline our transition process)
- "How quickly will we see results?" (We set realistic timelines upfront)
This approach builds trust and shows we understand their concerns.
### 3. Make Taking Action Ridiculously Easy
Decision fatigue is real, especially for busy executives. We've simplified our onboarding process to three clear steps with minimal input required from the client.
The easier you make it to say "yes," the more likely you'll hear it.
## The Bottom Line
Landing high-ticket clients isn't about fancy sales tactics or psychological manipulation. It's about becoming genuinely valuable to a specific group of people with specific problems and the budget to solve them.
High Ticket clients or high ticket sales will change your work satisfaction, your client relationships, and yes, your bank account. Is it right for your business? Only you can answer that, but if you're tired of the hamster wheel of endless small sales, it might be time to cast a smaller net for bigger fish.
## FAQs From Real Businesses Making the Switch

### How do I know if my business is ready for high-ticket clients?
If you're consistently delivering great results, getting positive feedback, and feeling stretched thin by managing too many small clients, you're probably ready. Start by creating a premium tier for your existing services before pursuing entirely new clients.
### Won't I lose business by raising my prices?
Yes, and that's actually the point. You'll lose the clients who don't value your work enough to pay premium prices. Our client roster shrank by 60% when we raised prices, but our revenue increased by 35%. Work less, earn more, that's the whole game.
### How long does it typically take to land your first high-ticket client?
In our experience, the typical timeline from strategy shift to first high-ticket client is about 3-6 months. It takes time to reposition your brand, create the right content, and nurture relationships. Patience pays off literally.
---
## How to Fix Mixed Content Issue in WordPress (Step by Step)
- URL: https://levamo.com/blog/how-to-fix-mixed-content-issue-wordpress/
- Category: website-development
- Author: Javeria
- Published: 2025-05-08
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix mixed content errors in WordPress with this easy, step-by-step guide.
Seeing the mixed content error on your WordPress site? Don’t worry, this guide will show you exactly how to fix mixed content issues in **WordPress** step by step, so your site stays secure and fully HTTPS compliant.
**Also read**:[ WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
## What Is the Mixed Content Issue in WordPress?
A mixed content issue happens when your WordPress site loads secure (HTTPS) and non-secure (HTTP) resources on the same page. These insecure elements, like images, scripts, or stylesheets, can weaken your site’s security and trigger browser warnings for visitors.
## Why Does the Mixed Content Error Appear on WordPress Sites?
Typically, the error appears after migrating a site from HTTP to HTTPS. If some old URLs or hardcoded links still use HTTP, browsers detect the mismatch and flag it as mixed content.
## How to Detect Mixed Content Issue WordPress
The fastest way to check for a mixed content issue on your WordPress site is by inspecting the browser’s address bar.
If mixed content exists, browsers may show a warning such as **“Not secure”**, or display a broken padlock icon beside your website URL. The message often says, *“Your connection to this site is not fully secure.”*
Not secure Warning in Chrome
To locate the exact elements causing mixed content:
- Open your website in **Google Chrome**.
- Click the three dots (top-right corner) and select **More tools → Developer tools**.
*(Shortcut: Ctrl + Shift + I on Windows/Linux, Cmd + Option + I on Mac.)*
- In Developer Tools, click the **Console** tab.
Chrome will list all insecure elements (like images or scripts) loading over HTTP.
This method gives you a clear view of which assets you need to update to fix the mixed content issue in WordPress.
## How to Fix Mixed Content Issue WordPress (3 Proven Methods)
We’ll guide you through three ways to **fix mixed content issue in WordPress**, starting from the easiest method.
### Method 1: Use a Plugin to Fix Mixed Content Automatically
If you can access your WordPress dashboard, a plugin is the quickest fix:
- Install and activate **Really Simple SSL** from the WordPress plugin directory.
- Go to **Settings → SSL** and enable the recommended settings.
- The plugin will automatically update insecure content URLs and force HTTPS across your site.
This works for most WordPress sites and requires minimal configuration.
### Method 2: Manually Update Links in Your WordPress Database
If the plugin doesn’t resolve everything, some links may be hardcoded. You can bulk-update them with a search-and-replace plugin:
- Install and activate **Better Search Replace**.
- Navigate to **Tools → Better Search Replace**.
- In *Search for*, enter your site’s HTTP URL (e.g., http://example.com).
In *Replace with*, enter the HTTPS version (e.g., https://example.com).
- Select all database tables.
- Run a **dry run** first to preview changes.
- If the results look accurate, uncheck dry run and run the actual replacement.
Better Search Replace Plugin
**Important**: Always back up your site before making database changes.
### Method 3: Force HTTPS Using the .htaccess File
If you’re comfortable editing server files, use .htaccess to enforce HTTPS:
- Access your site files via **FTP** or **File Manager**.
- Locate the .htaccess file in the **public_html** folder (or create one if missing).
Edit the file and add this code at the bottom:
RewriteEngine On
RewriteCond %{HTTPS} !=on
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
- Save the file and reload your website.
This ensures all traffic automatically [redirects to HTTPS](/blog/redirect-http-to-https/), helping fully fix mixed content issue WordPress.
## Extra Tips to Avoid Mixed Content Problems in the Future
- Always upload media via HTTPS.
- Use relative URLs when embedding resources.
- Regularly scan your site after plugin or theme updates.
These habits can prevent you from needing to fix mixed content issue WordPress repeatedly.
### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## Why Fixing Mixed Content Issue in WordPress Matters
Mixed content weakens your site’s security, breaks trust with visitors, and can hurt SEO rankings. Fixing it ensures full encryption, stronger SEO performance, and no browser warnings.
## Frequently Asked Questions (FAQs)
### How Do I Fix Mixed Content on a WordPress Site?
You can fix mixed content on a WordPress site by updating HTTP links to HTTPS manually, using plugins like Really Simple SSL, or forcing HTTPS via .htaccess rules. A combination of these methods ensures all site resources load securely.
### Why Is Fixing the Mixed Content Warnings Important?
Fixing mixed content warnings is crucial because they compromise your site’s security and can scare away visitors with browser alerts. Resolving them ensures full encryption, protects user data, and improves your site's credibility.
### How Can I Find Mixed Content Errors on My Site?
Use browser developer tools (Console tab) to see mixed content warnings, or scan your site with tools like Why No Padlock. You can also search your site's source code for insecure http:// links.
Looking for **blazing-fast, secure hosting** to avoid mixed content headaches? Check out[ fully managed WordPress hosting](/) by Levamo, optimized for speed, security, and peace of mind.
Regular website maintenance and monitoring are key to minimizing the occurrence of this error.
---
## Build Your eLearning Website with MasterStudy LMS and Levamo Hosting
- URL: https://levamo.com/blog/masterstudy-lms-review/
- Category: lms
- Author: Shahzeb Ahmed
- Published: 2025-05-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Create an eLearning website with MasterStudy LMS & Levamo Hosting.
The e-learning industry is expanding at an incredible pace. There’s a growing demand for high-quality online education. If you're thinking about launching your own online courses, you're stepping into an exciting, rapidly evolving space.
Compared to traditional platforms where you're bound by their rules and fees, like Udemy or Teachable, building your own e-learning website gives you creative freedom. You have control of the content, the branding, the learning experience, and, of course, the revenue.
In this article, we'll explore how **[MasterStudy LMS](https://stylemixthemes.com/wordpress-lms-plugin/)** can be your perfect partner for creating a custom learning experience and how pairing it with a top-tier hosting solution like **Levamo Hosting** can ensure your platform runs smoothly and scales effortlessly as your user base grows.
## What Makes MasterStudy LMS Different?
**MasterStudy LMS** is a complete solution designed to help you launch, manage, and scale your e-learning business. You can create and deliver single courses or build an entire school with all the tools it has.
Let’s look at reasons why MasterStudy LMS is different from the rest:
- **Built for Full Course Websites:** MasterStudy LMS isn’t just for creating one course. It helps you build an entire e-learning platform with multiple courses, instructors, and students.
- **Includes All Core Features from the Start:** Unlike many LMS plugins that require lots of paid add-ons, MasterStudy LMS includes essentials in the free version, like course builder, quizzes, video lessons, student accounts, and payment options.
- **Drag-and-Drop Course Builder:** You get a clear course builder that guides you through adding course details, lessons, quizzes, and assignments. You don’t have to figure out where things go - each part has its place.
- **Live Lessons, Drip Content, and Certificates:** You can teach live with Zoom or Google Meet, and release lessons gradually with the drip content addon. Reward students with certificates after completing a course.
- **Works with WooCommerce and Stripe:** You can sell courses using the tools you already know with WooCommerce, Stripe, PayPal, and more. There’s also support for subscriptions and offline payments.
- **Easy to Start, Easy to Scale:** Start small with a few courses and grow to a full platform with hundreds. There are advanced features available in the Pro version, but you don’t need them right away to launch.
## Reliable Hosting is Key to Your eLearning Success
When you create your first e-learning platform, there are some non-negotiables like performance, speed, and security. That’s where hosting comes in. To run a successful eLearning website, you need a hosting solution that’s fast and secure.
Levamo Hosting is designed for businesses that require reliable performance for content-heavy platforms and software such as MasterStudy LMS. It’s more than just a place to store your website, it’s a dynamic solution that adapts to your needs. Here’s why Levamo is a great fit for eLearning:
- **Optimized for Performance**: eLearning websites can attract a large number of users at once, especially during exams or course launches. Levamo Hosting ensures your platform can handle high traffic without compromising speed or user experience.
- **Speed:** Fast loading times are critical to keeping learners engaged. **Levamo** uses cutting-edge technology to ensure lightning-fast page loads, improving user experience and SEO.
- **Scalability:** As your eLearning platform grows, so will your hosting needs. **Levamo** offers seamless scalability, meaning it can grow with your business. From your first students to hundreds or thousands, your platform will continue to run smoothly.
- **Security:** Security is a top priority, especially when handling user data and payments. **Levamo Hosting** provides robust security features, including automatic updates, daily backups, firewalls, and SSL certificates.
- **24/7 Professional Support:** Technical issues can arise at any time. That's why **Levamo** offers around-the-clock support to ensure your platform stays up and running.
### Why WordPress and MasterStudy LMS?
While there are plenty of options for building an e-learning platform, WordPress offers the **flexibility** and **customization** that many other platforms simply can’t match. WordPress is the ideal choice for building your site because it has these:
- **Ease of Use:** You don't need to be a tech expert to get started with WordPress. It has an intuitive interface that makes setting up your eLearning platform quick and easy.
- **Vast Plugin Ecosystem:** WordPress has a huge library of plugins for anything you might need, from SEO tools to marketing integrations.
- **Customizable Design Options:** Choose from a variety of themes or create your own custom design to perfectly match your branding and vision.
- **SEO-Friendly:** WordPress is built with SEO in mind, so with the right tools, you can make sure your site ranks well in search engines.
## Building Your eLearning Platform: Step-by-Step
Let’s go through seven steps to creating your own e-Learning website.
#### Step 1: Set Up Hosting with Levamo
To get started, you’ll first need reliable hosting. **Levamo Hosting** offers you a straightforward setup process and great performance for your LMS platform.
**To Get Started:**
- Navigate to [Levamo website](/pricing/) and see their hosting plans.
- Select your hosting plan. Whether you’re just starting or need a plan that scales with your traffic, Levamo has flexible options. There are options for individuals, startups, and bigger companies.
- After choosing a plan, sign up by entering your details.
You can use a new site or migrate an existing one. Levamo takes the complexity out of setting up your hosting, and you can start right away with automated tools and simple instructions.
Once your account is set up, you’ll be ready to move on to WordPress installation!
#### Step 2: Install WordPress
Next, it’s time to get WordPress installed on your hosting account. This is where you’ll build and customize your website.
**Install WordPress:**
- **Log in to your Levamo dashboard**: Follow the on-screen instructions to install WordPress.
- **Automatic Setup**: With Levamo, WordPress installs with just a few clicks. Enter your site name, admin details, and domain, and you’re all done!
Now that WordPress is up and running, you can install MasterStudy LMS to turn your site into a fully-fledged learning platform.
#### Step 3: Install MasterStudy LMS
MasterStudy LMS will help you easily manage your courses and offer an interactive learning experience. Installing the plugin is straightforward.
To install the Plugin, go to your WordPress dashboard and select Plugins > Add New. Search for **MasterStudy LMS**, click Install, and activate the plugin.
Once activated, the setup wizard will guide you through basic configuration, such as demo imports and customization options.
Now your WordPress site is equipped to manage online courses, students, and everything in between!
Button: [Get MasterStudy LMS Now](https://stylemixthemes.com/wordpress-lms-plugin/pricing/)
#### Step 4: Creating Your First Course
Let’s dive into the exciting part: creating your very first course.
**Go to MS LMS > Courses**: Click **Add New Course** to start the process. Here you need to **fill in Course Details**: Give your course a name, specify a URL, choose a category and level, and upload a course image.
Now, let’s organize your curriculum. Add sections for different modules or chapters and create lessons. You can choose the lesson type - text, video, audio, or even live lessons with Zoom or Google Meet integration.

Add a name, content, duration and short description to your lesson. It is important to save the lesson before moving to the next section.

You can choose to make the lesson public so users will see its preview.
To create a quiz, click on Add a lesson > Quiz and give a name for it. You can add 7 types of questions and make any type of quiz.

You can enable features like certificates, content drip, and prerequisites if needed.
Make sure to organize your course content in a logical order, so students can follow it easily.
#### Step 5: Personalize Your Website
Once your course is created, it’s time to focus on your website’s design. **MasterStudy LMS** is already optimized for an engaging student experience, but you can take it further with customizable themes.
You will need a theme to create an LMS website. You can use the MasterStudy Starter template that looks and works seamlessly with the MasterStudy LMS plugin. The theme is easy to set up with a wizard. It is responsive and optimized for all devices, including desktop, mobile, and tablets.
There is also a pack of four premium MasterStudy Templates. You can get them for specific niches like online schools, universities, and coaches. And personalize them in the editor, remove or add content you need to match your brand.

Use LMS widgets in Elementor and other tools to tailor your pages to your website.
#### Step 6: Publish and Promote Your Course
Once everything is set up, you can launch your course. Take a moment to review and test everything before your course goes live.
Go through your course as if you’re a student to ensure everything is working as expected. Check for broken links, formatting issues, and any other details.
You can set up and use payment gateways like WooCommerce, PayPal, or Stripe to sell your courses.
After publishing, start promoting your course. Share the link on social media, email list, and other social media platforms to attract students.
#### Step 7: Grow and Scale Your Platform
Now that your site is live and your first course is available, you can begin growing your platform. **Levamo Hosting** makes it easy to scale your site as you gain more traffic and students. It helps if you need more storage, higher performance, or enhanced security..
**Pro tips:**
- **Track Student Progress**: Use MasterStudy LMS’s reports and analytics feature to monitor how your students are progressing and find out areas for improvement.
- **Offer Additional Courses**: Continue building your course catalog to boost enrollments.
- **Engage Your Audience**: Use email campaigns, webinars, and content marketing to grow your online community.
## Get Now with Special Offer
By combining the power of WordPress, MasterStudy LMS, and Levamo Hosting, you can launch your own e-learning platform in a few steps. This setup gives you total freedom over how your content is presented, sold, and scaled.
Thanks to our partnership with Levamo, MasterStudy LMS users can also get exclusive hosting discounts, making now the perfect time to start building and selling your courses online.
Start building your learning platform today and bring your teaching to the world.
---
## Introducing Levamo 2.0 with Multiple Site Plans & Enhanced Hosting Experience! 🔥
- URL: https://levamo.com/blog/introducing-rapyd-cloud-2-0/
- Category: news
- Author: The Levamo Team
- Published: 2025-05-06
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo 2.0 is here with site plans and a better hosting experience.
> *Note: This post was originally published May 2025 as "Introducing Rapyd Cloud 2.0 with Multiple Site Plans & Enhanced Hosting Experience! 🔥" when our platform was called Rapyd Cloud. We've since rebranded to Levamo. The product details below remain accurate - only the brand name has changed.*

Nearly two years ago, Levamo was launched in response to frustrated WordPress users who just couldn’t get good performance from their hosting solutions.
The mission was clear from day one: *to redefine what’s possible for dynamic, feature-rich WordPress websites with hyperspeed hosting*!
Levamo isn’t just fast, though. It gives hyperspeed performance for your dynamic websites, even with peak traffic, which most other hosting platforms consistently fail at. But it doesn’t stop there: you get **built-in security**, complete **reliability with 99.99% uptime**, **24/7 expert support**, an easy-to-use platform, autoscalability, and many more features that make your life as a WordPress owner much easier.
But while ecommerce store owners, BuddyBoss users, and other membership/LMS websites found Levamo to escape their hosting woes, agencies, developers, and freelancers who hosted more than a few websites wanted a solution more suited to their workflows and offered more flexible pricing for all their websites.
Throughout 2024, we received many requests and queries from agencies and devs who wanted to host all their client websites on our platform, but couldn’t because our platform had yet to evolve as much.
Today, we’re changing that. Along with other big improvements and releases, this is the next evolution of the Levamo platform that will truly enhance your WordPress hosting experience!
## Say Hello to Multiple Site Plans

Every Levamo plan is built for hyperspeed performance, with the same high-performance stack, rock-solid security, and expert support we’re known for.
With Levamo 2.0, you can now host multiple independent WordPress sites within a single powerful environment. That means more flexibility for agencies, developers, and site owners, without giving up the speed and reliability that made Levamo a go-to for mission-critical projects.
Manage all your sites from a single, dev-friendly dashboard, deploy new ones in minutes, and keep everything running at peak performance - all backed by our lightning-fast Levamo CDN and 24/7 expert human support.
Levamo’s multiple-site capability is perfect for:
- **Agencies** managing a growing roster of clients who need one powerful hub to run everything
- **Developers** running multiple environments, staging areas, and live projects across different teams
- **Freelancers** who want to simplify, consolidate, and move faster without juggling multiple logins and dashboards
If you’re one of these, Levamo is ready to become your all-in-one command center for every website you manage.
## An All-New Dashboard For Smart Management
All New Dashboard
To bring multiple site support to Levamo, we reimagined the entire dashboard experience to make managing your sites at scale faster, cleaner, and far more powerful.
So what’s new and better?
First, every plan now supports multiple sites within a single environment. Before, one environment meant one website, and that’s history.
Now, environments handle your server-level settings, while each site gets its own dedicated space with its controls and management tools.
This smart decoupling means you can fine-tune each site independently without overlap or confusion. Everything runs cleaner, faster, and more predictably.
Here’s an overview of what you get at each level:
### Environment-Level Management
Your control center for everything server-side:
- **Overview**: Monitor resource usage, services, and server specs.
- **Sites:** View and access all sites within the environment.
- **Usage:** Track server-level resource consumption in real time.
- **Logs**: Access detailed logs: platform audits, server errors, stderr, DB, and KeyDB.
- **Access**: SFTP/SSH only (FTP is deprecated).
- **Manage**: Full control of stack components: Linux, LiteSpeed, MariaDB, KeyDB, PHP Workers, and PHP versions.
These tools unlock next-level flexibility, giving you the power to tweak, scale, and manage your servers without friction.
### Site-level management
Your control center for precise website management:
- **Overview**: Key stats and site-specific information at a glance.
- **Quick Actions**: Clear cache, create backups, launch phpMyAdmin in a click.
- **WordPress Section**: See your WP version, themes, plugins, and WP_DEBUG status.
- **Security Tools**: WAF (requires Levamo CDN), Monarx, and Advanced SiteShield ($4/mo per site).
- **Tools**: Access files, databases, custom domains, cron jobs, cache, logs, and a full file manager.
These settings put you in full control, with no more hunting for settings or crossing your fingers during updates. You get visibility, speed, and peace of mind, site by site.
We’ve also moved the **Billing section**, which now lives under your user icon in the top-right corner, for a cleaner, focused navigation. You can still manage billing directly from the Plans page when you need to.
And that’s just one of many thoughtful updates across the dashboard, all designed to cut clutter, save clicks, and help you focus on what really matters: growing your business.
**Note for Levamo users:** Your current sites will continue running smoothly on the v1 dashboard with no action needed. Migrations to the new platform have now begun, and we’ll contact you directly with your migration details and any steps you’ll need to take.
Learn more about the [transition details here](https://support.levamo.com/articles/11179484-introducing-rapyd-cloud-2-0).
## The Bottom line
Levamo’s **Multiple Sites Plans** unlock a whole new way to build, launch, and scale WordPress sites, all powered by our Hyperspeed WordPress hosting built for high traffic and zero slowdowns.
With the new plans, now anyone can run multiple sites under one roof without sacrificing speed, reliability, or control.
But for **agencies, developers, and individuals**, this isn’t just convenient. It’s a game-changer. Because while other hosts let you add more sites, they miss out on what matters most: *delivering actual performance.*
With our latest platform upgrades, you can now:
- **Scale your business** with ease
- **Deliver blazing-fast websites** your clients will rave about
- **Centralize everything** in one powerful, easy-to-manage platform
- **Spend less time managing hosting** and more time building a legacy
With these new changes, Levamo is setting new standards for WordPress Hosting, and we can’t wait to see how you use our Hyperspeed platform to deliver the projects you’ve always dreamed of!
---
## Cloudflare Error 521: The Complete Guide to Fixing It
- URL: https://levamo.com/blog/cloudflare-error-521/
- Category: website-maintenance
- Author: Faisal Sarker
- Published: 2025-05-05
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix Error 521! This guide covers all causes, from firewalls to TLS mismatches.
Your website is humming along behind Cloudflare’s global content-delivery network when visitors suddenly see a stark gray screen: **“Error 521 - Web Server Is Down.”** Search engines list hundreds of posts about it, yet most recycle the same four suggestions - **“restart your server, check SSL, whitelist Cloudflare, contact your host.”**
Those tips help, but they skip entire categories of root causes: automated firewalls that silently rate-limit the CDN, mismatched TLS modes, resource ceilings hit during traffic spikes, and platform-specific gotchas for Kubernetes or multi-origin load balancers.
This guide stitches those missing pieces together. By following the step-by-step workflow below, you’ll not only clear the immediate 521, but also harden your stack so it never returns.
## What Exactly Is Error 521?
A 521 means Cloudflare tried to open a TCP connection to your origin and the origin refused it. The edge server sends a SYN packet on port 80 or 443 (or one of Cloudflare’s alternate ports). If three consecutive attempts are reset (RST) or never answered, Cloudflare stops and surfaces the error to the visitor. In other words, the CDN made it to the front door of your server but got a slammed door or stony silence in reply.
Contrast that with **[522 (“Connection timed out”)](/blog/how-to-fix-error-522/)** where the handshake begins but stalls, or **526 (“Invalid SSL certificate”)** where TLS negotiation fails; understanding these distinctions is vital because each code points to a different layer in the request path.
## A Five-Step Diagnostic Workflow
Most 521 incidents disappear once you walk through the following ordered process. Work through each step, test, and stop as soon as the site loads again - no need to read the whole article at 03:00 AM.
### Step 1: Confirm the origin is really online
curl -I http://
curl -I https:// --insecureSSH into the box (or ask your host) and run
- You should see HTTP/1.1 200 OK or a purposeful redirect. Anything in the 500 range means the server itself is down; restart Apache/Nginx or open a support ticket before involving Cloudflare.
### Step 2: Remove anything that blocks Cloudflare IP ranges
Firewalls, security plugins, and modules such as **mod_evasive**, **mod_antiloris**, or **fail2ban** often misinterpret Cloudflare’s many connections as an attack. An easy test is to pause Cloudflare (the gray-cloud icon) and load the site directly; if it works, you almost certainly have an IP-blocking problem.
Copy–paste allow rules:
# Ubuntu UFW whitelist - auto-updates the list every week
curl -s https://www.cloudflare.com/ips-v4 \
| xargs -I{} sudo ufw allow from {} to any port 80,443 proto tcp
curl -s https://www.cloudflare.com/ips-v6 \
| xargs -I{} sudo ufw allow from {} to any port 80,443 proto tcp
sudo ufw reload
Schedule the same commands weekly with cron or Ansible so new Cloudflare sub-nets are never accidentally blocked again.
### Step 3: Match SSL/TLS mode with reality on the server
Cloudflare offers three HTTPS modes:
| **Cloudflare mode** | **What’s on the origin** | **Is it secure?** |
|---|---|---|
| Flexible | **Nothing**; Cloudflare terminates SSL and talks HTTP to origin | **No** |
| Full | *Any* certificate, even self-signed | Medium |
| Full (Strict) | Valid cert or Cloudflare Origin CA cert | **Best** |
An origin that expects Full (Strict) but is paired with Flexible will refuse the initial handshake, leading Cloudflare to believe the web server is “down.” Fix by installing a valid certificate (Cloudflare Origin CA is free and lasts 15 years) **or** selecting the TLS mode that matches what you already have. Verify with:
`openssl s_client -connect example.com:443 -servername example.com -tls1_2`
Look for a clean certificate chain and an SSL-Session that ends with Verify return code: 0 (ok).
### Step 4: Check DNS and listening ports
Make sure your **A** or **AAAA** record in Cloudflare points to the correct, *unproxied* origin IP and that the orange-cloud proxy is enabled. On the machine itself run:
`sudo lsof -nPiTCP:80,443`
You should see your web-server service listening. If you operate on a non-standard port, remember Cloudflare only proxies a limited list (2052/2053/2082/2083/2086/2087/2095/2096/8443).
### Step 5: Inspect resource limits and current load
Sometimes the origin refuses new sockets simply because it is overwhelmed. Check:
- **CPU/RAM:** htop or your hosting panel
- **Open files:** ulimit -n, sysctl fs.file-max
- **Apache**: MaxRequestWorkers, ServerLimit
- **Nginx**: worker_connections, worker_rlimit_nofile
- **PHP-FPM**: pm.max_children
If metrics spike to 100 % during 521 events, upgrade resources or deploy a cache/warming strategy.
## Deep-Dive Fixes Other Guides Skip
### Step **1: Granular firewall snippets for every stack**
Most tutorials tell you to “whitelist Cloudflare,” but admins still hunt through docs for the right syntax. Below are turnkey rules:
#!/usr/bin/env bash
# 3.1 Whitelist Cloudflare (iptables)
set -euo pipefail # safer scripting
# --- IPv4 ---------------------------------------------------------------
for cf_ip in $(curl -fsSL https://www.cloudflare.com/ips-v4); do
iptables -I INPUT -p tcp -s "$cf_ip" --dport 80 -j ACCEPT
iptables -I INPUT -p tcp -s "$cf_ip" --dport 443 -j ACCEPT
done
# --- IPv6 (optional) ----------------------------------------------------
for cf_ip in $(curl -fsSL https://www.cloudflare.com/ips-v6); do
ip6tables -I INPUT -p tcp -s "$cf_ip" --dport 80 -j ACCEPT
ip6tables -I INPUT -p tcp -s "$cf_ip" --dport 443 -j ACCEPT
done
# --- Persist the rules --------------------------------------------------
service netfilter-persistent save # Debian/Ubuntu; adjust for your distro
- **CSF (ConfigServer Security & Firewall)** - add lines like
`tcp|in|d=443|s=173.245.48.0/20 to /etc/csf/csf.allow.`
**cPanel & Plesk** - open “IP Blocker” → *Trusted IPs* and paste the list.
Running a managed WordPress host? Open a ticket linking to Cloudflare’s JSON feed so the NOC team can automate the import.
### Step 2: A visual SSL/TLS decision tree
Readers often stare at Cloudflare’s five TLS toggles and freeze. Embed a one-screen PNG (or interactive SVG) that starts with the question “Do I have any certificate installed at the origin?” and ends with the exact mode to pick. Adding a small screenshot of the Cloudflare dashboard plus an openssl command makes the abstract concrete.
### Step 3: Origin log cheat-sheet
| **Platform** | **Log file** | **521 symptom to grep** |
|---|---|---|
| Apache (cPanel) | /etc/apache2/logs/error_log | AH01630: client denied by server configuration (173.245.*) |
| Nginx (Ubuntu) | /var/log/nginx/error.log | access forbidden by rule |
| LiteSpeed | /usr/local/lsws/logs/error.log | ModSecurity: Access denied |
| IIS | C:\\inetpub\\logs\\LogFiles\\W3SVC1\\u_exYYMMDD.log | 403 1 0 after a Cloudflare IP |
Pair the timestamp with the **Ray ID** from the visitor’s error screen, and you’ll pinpoint the offending rule in seconds.
### Step 4: Shared hosting versus VPS/bare-metal
Shared customers rarely have root. Emphasize GUI-level solutions - “disable ModSecurity in cPanel” or “use the host’s ‘Restart PHP’ button” - while highlighting root-level commands for VPS owners. Two color-coded callouts help readers leap to the track that applies to them, boosting dwell time and reducing bounce.
### Step 5: Preventive monitoring and alerts
Don’t wait for a customer tweet to discover 521s:
- **Cloudflare Health Monitor** - free synthetic origin checks with Slack hooks.
- **UptimeRobot** - probe both the orange-cloud **hostname** and **the raw origin IP** every minute.
- **Always Online** - Cloudflare can serve the Wayback cached copy for brief outages.
**Custom cron watchdog**:
#!/usr/bin/env bash
URL=https://example.com
[[ $(curl -s -o /dev/null -w "%{http_code}" $URL) == 521 ]] && \
( systemctl restart nginx; logger -t cf-521 "Restarted Nginx after 521" )
- Log to syslog so Grafana or New Relic can visualize patterns.
## Case Study: Black Friday Traffic Spike
**Site:** a WooCommerce store on a 2-vCPU VPS, Cloudflare Pro
**Time:** 24 Nov 2024, 10:02 UTC
**Incident:** Conversion tracking flagged a 40 % checkout drop; visitors saw 521 intermittently.
**Investigation**:
- Cloudflare **Error Analytics** revealed 3,100 spikes of 521 in five minutes.
- netstat -an | grep :443 | wc -l showed 55 sockets - beyond the Nginx worker_connections 50 limit.
- journalctl uncovered mod_evasive: Denying 173.245.49.28.
**Fix:**
- Raised worker_connections to 2 048 and set worker_rlimit_nofile to 4 096.
- Disabled Mod_Evasive for the published Cloudflare IP list.
- Temporarily scaled the VPS to 4 vCPU during the sale window.
The store processed 17 % more orders than the previous year, with zero 521s for the rest of Black Friday.
## Ongoing Hygiene: Never See 521 Again
- **Patch weekly.** Out-of-date OpenSSL or nginx packages introduce TLS bugs that look like refusals.
- **Automate IP imports.** A two-line cron pulling the JSON feed prevents next month’s new /15 block from tripping rate-limits.
- **Load-test quarterly.** Tools like k6 or ApacheBench reveal how many concurrent Cloudflare sockets your stack can handle.
- **Document your baseline.** CPU < 40 %, 95th-percentile memory, normal Ray ID counts. Abnormalities will jump off the dashboard.
## Advanced Troubleshooting for Modern Stacks
### Kubernetes + Nginx Ingress
Because Cloudflare acts as the client, Nginx Ingress sees the connection coming from the edge, not the real visitor’s IP. If you enable source-range security controls, set:
controller:
config:
proxy-real-ip-cidr: 173.245.48.0/20,103.21.244.0/22,2400:cb00::/32
real-ip-header: CF-Connecting-IP
Otherwise the controller returns 403, Cloudflare records a refusal, and visitors see 521.
### Cloudflare Load Balancing
Pool health checks must reach at least one origin. When all nodes in a pool fail health probes, Cloudflare surfaces a 521 even if individual nodes are up but blocking probes. Verify under **Traffic → Load Balancing → Analytics,** and ensure probes originate from the same IP ranges you whitelisted.
### HTTP/3 (QUIC)
A 521 looks identical over QUIC because the refusal happens before any protocol negotiation. To rule out version-level issues, run:
`curl --http3 -I https://example.com`
If the command fails while HTTP/2 succeeds, your origin might lack ALPN h3. Disable HTTP/3 in **Network → HTTP/3 (with QUIC)** or upgrade the origin stack.
## Conclusion
Error 521 is blunt: Cloudflare knocked, your server refused.
Resolve it just as bluntly:
- **Prove the origin is listening.**
- **Stop your firewall from treating Cloudflare as hostile.**
- **Speak the same TLS dialect.**
- **Make sure resources and DNS point the right way.**
Add a weekly script to auto-import Cloudflare’s ever-expanding IP list and a one-minute health probe, and chances are you’ll never see a 521 crash a campaign again. Bookmark this guide, and then go set that cron job before you forget.
## Frequently Asked Questions

### Is a 521 a sign of a DDoS attack?
Usually not. A volumetric attack might *trigger* your firewall, which then blocks Cloudflare and indirectly causes 521, but the error itself is only Cloudflare reporting a refusal.
### How long until DNS changes eliminate a 521?
With a low TTL (300 s) most recursive resolvers refresh within five minutes, but some ISPs pin records for up to an hour. Test with dig +trace to confirm propagation.
### Do I need a paid Cloudflare plan to fix 521?
No. All troubleshooting steps work on the free tier. Paid tiers add nicer dashboards, Load Balancing, and long-term Error Analytics, but the root fix is always on your server.
### Can Always Online hide 521 from visitors?
It can serve a cached snapshot, but dynamic content (carts, checkouts) remains unavailable. Consider it an emergency band-aid, not a cure.
---
## How to Fix the WordPress White Screen of Death (WSoD) Error: 9 Simple Solutions
- URL: https://levamo.com/blog/wordpress-white-screen-of-death/
- Category: wordpress
- Author: Javeria
- Published: 2025-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Solve the frustrating WordPress white screen error with these 9 fixes.
## What Is the WordPress White Screen of Death (WSoD)?
The WordPress White Screen of Death (WSoD) is a frustrating error in which your website or admin panel loads nothing but a blank white page, no content, no error message, just an empty screen. It can affect your entire site, just specific pages, or even lock you out of your WordPress dashboard.
This problem typically occurs when something breaks in your site’s code, such as a faulty plugin, a theme conflict, or server resource limits getting maxed out. For website owners, especially those running e-commerce or business sites, it can mean lost traffic and revenue if not resolved quickly.
Luckily, the WordPress White Screen of Death can be fixed without needing advanced coding knowledge. Below are 9 effective ways to troubleshoot and recover your website.
# Why Do You See the White Screen of Death in WordPress?
Understanding what triggers the WordPress White Screen of Death can help you troubleshoot faster. Here are the most common causes:
- **Plugin or Theme Conflicts:** An incompatible or poorly coded plugin or theme can disrupt how WordPress loads, leading to a blank screen.
- **PHP Memory Exhaustion:** When your server runs out of allocated memory to process your site’s requests, it can result in the White Screen of Death.
- **Syntax Errors or Corrupt Code:** Mistakes made while editing theme or plugin files, such as a single misplaced bracket, can break your site’s PHP execution.
- **Failed Updates:** Incomplete or failed updates of plugins, themes, or core WordPress files may cause incompatibilities or corrupted files.
- **Server Configuration Limits:** Misconfigured server settings (like low recursion or backtrack limits) can prevent large operations from completing properly.
Pinpointing the exact reason helps you apply the right fix and reduce downtime.
# 9 Ways to Troubleshoot and Resolve the WordPress White Screen of Death
## 1. Clear Your Browser and Site Cache
The first thing to try is clearing both your browser cache and any caching plugins on your website. Sometimes cached versions display outdated or broken content. After clearing, refresh the page to see if your site reappears.
## 2. Expand Your PHP Memory Limit
Low server memory is a common trigger for the WordPress White Screen of Death (WSoD). To fix this, [maximize your site's PHP memory limit](/blog/maximum-php-memory-limit/) by editing your **wp-config.php** file. Add:
php
define('WP_MEMORY_LIMIT', '256M');
This allocates more resources to your site and can help resolve heavy processes that cause a blank screen.
## 3. Turn Off All Plugins
A malfunctioning plugin can crash your site. Disable all plugins by accessing your site’s files via FTP or your hosting control panel. Rename the **wp-content/plugins** folder to **plugins_backup**.
If your site loads afterward, you know a plugin was responsible. Rename the folder back and reactivate plugins one at a time to pinpoint the faulty one.
## 4. Switch Your WordPress Theme to Default
Corrupted or incompatible themes can also lead to the WordPress White Screen of Death. Switch your theme by renaming your current theme’s folder (inside **wp-content/themes**) or using phpMyAdmin to assign a default theme manually.
WordPress will automatically fall back to a default theme like **Twenty Twenty-Four**.
## 5. Enable Debug Mode to Identify Errors
Turning on [WordPress Debug mode](/blog/debug-in-wordpress/) can help uncover hidden PHP issues behind the WSoD. In **wp-config.php**, set these lines:
php
define('WP_DEBUG', true);
define('WP_DEBUG_LOG', true);
define('WP_DEBUG_DISPLAY', false);
This saves error logs to **wp-content/debug.log**, where you can spot exactly what’s breaking your site.
## 6. Remove the Maintenance File
If a WordPress auto-update (core, plugin, or theme) failed midway, a [leftover .maintenance file](/blog/wordpress-stuck-in-maintenance-mode/) in your root directory can block access.
Connect via FTP, locate and delete the .maintenance file, then reload your site.
## 7. Increase PHP Text Handling Limits
Large posts, complex page builders, or big plugins can strain your server’s processing capacity. Adjust the following values in **php.ini** to handle heavier workloads:
ini
pcre.recursion_limit=200000
pcre.backtrack_limit=1000000
These changes allow WordPress to process larger content sets without timing out.
## 8. Roll Back to a Previous Backup
If recent updates or changes triggered the issue, restoring a backup can quickly bring your site back online. Use your hosting backup tool, a WordPress plugin, or a manual backup copy.
## 9. Ask Your Hosting Provider for Support
If none of these methods work, contact your hosting support team. A good, [fully managed WordPress hosting](/managed-wordpress-hosting/) like **Levamo** can help you dig into server logs, increase server limits, or troubleshoot at a deeper level to restore your site.
# How to Prevent the WordPress White Screen of Death from Happening Again
Once you’ve fixed the WordPress White Screen of Death (WSoD), it’s smart to take steps to stop it from coming back.
- **Keep Plugins and Themes Updated:** Outdated code is a top reason for conflicts.
- **Choose High-Quality Plugins & Themes:** Stick to reputable developers and avoid bloated tools.
- **Monitor Server Resources:** If you outgrow shared hosting, upgrade to a higher plan or a managed WordPress host.
- **Regular Backups:** Always have recent backups you can restore quickly.
- **Test Updates in Staging:** Before applying changes to your live site, test them in a [staging environment](/blog/how-wordpress-sandboxes-help-developers-test/) to catch bugs early.
# Summary
The WordPress White Screen of Death (WSoD) might look intimidating at first, but it can usually be resolved with a few practical steps. Whether you’re clearing cache, disabling plugins, or increasing server resources, these fixes can get your site back online fast.
For fewer technical headaches in the future, consider moving to a reliable hosting provider like **Levamo**, where expert support and optimized servers reduce the risk of downtime-causing errors like the WSoD.
# Frequently Asked Questions (FAQs)
### How can I fix the white screen problem on my WordPress site?
You can fix the WordPress White Screen of Death by clearing cache, increasing memory limits, disabling plugins and themes, enabling debug mode, removing the maintenance file, restoring backups, or getting help from your host.
### Why does my WordPress site only show a blank page?
A blank white page in WordPress usually means there’s a PHP error, memory exhaustion, or a plugin/theme conflict that is breaking the site’s code execution.
### What usually causes the WordPress White Screen of Death error?
The most common causes are plugin conflicts, theme errors, low PHP memory limits, or failed updates that disrupt WordPress functionality.
---
## How to Fix the 408 Request Timeout Error
- URL: https://levamo.com/blog/408-request-timeout-error/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-05-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
408 timeout got you down? Fix it fast with these troubleshooting tips.
The 408 error might seem like a random glitch, but when it pops up, it’s actually your website’s way of saying, "I'm tired of waiting." And if you're running a business or building something people rely on, a sluggish experience is the last thing you want to deliver.
Let's break it down. A 408 Request Timeout error happens when the server times out waiting for a request from the client (that’s the browser). Basically, the conversation between your site and your visitors gets awkwardly cut off before it even starts.
But here's the thing: fixing it doesn't have to be a headache. Let's dig into the why, and more importantly, the how.
## Why You're Seeing a 408 Error
- **Slow Internet Connection:** The user's network isn't strong enough to get the request through in time.
- **Server Overload:** Your hosting environment is getting hammered with more traffic or processes than it can handle.
- **Faulty Code:** Buggy scripts, plugins, or themes that hang during processing.
- **Network Interruptions:** Firewalls, proxies, or security software that bottleneck traffic.
- **Browser Problems:** Outdated or misconfigured browsers can sometimes cause timeouts.
## How to Fix the 408 Error (Without Losing Your Mind)
## 1. Refresh and Retry
First things first, reload the page. You'd be surprised how often a 408 error is just a momentary blip. Maybe the network hiccuped, maybe your server just needed a second. If the error goes away after a refresh, no need to dig deeper.
## 2. Check Your Internet Connection
Run a speed test. If your connection is crawling or cutting out, your browser might be timing out before the server even gets your request. Switch from Wi-Fi to Ethernet if you can. Restart your modem or router. Try loading the same site on a different device to isolate the issue.
## 3. Clear Your Browser Cache
Old, corrupted, or bloated cache files can mess with how your browser communicates with a server. Clear your cookies and cache to wipe the slate clean. On Chrome, it takes two clicks: **Settings > Privacy & Security > Clear Browsing Data**. After that, close and reopen the browser before trying again.
## 4. Review and Update Plugins and Themes
If you're running a CMS like WordPress, it’s not uncommon for plugins or themes to slow things down. Especially if they’re outdated, poorly coded, or not playing nice with other tools. Disable them one by one to identify which one is holding up the request. Once found, replace it or reach out to the developer for support. Always keep everything updated to avoid conflicts and performance drags.
## 5. Inspect Your Server Performance
A sluggish server is a recipe for 408 errors. Use tools like top, htop, or your hosting dashboard to check CPU and RAM usage. If resources are maxed out, you're pushing your hosting plan beyond its limit.
**This is where Levamo outperforms everyone else.**
We don’t throttle performance when you grow. Our infrastructure is designed for speed, stability, and scale. With built-in caching, performance tuning, and edge delivery baked into every plan, your site gets the speed it deserves, without you needing to babysit servers or chase down support.
## 6. Check Firewall and Security Settings
Sometimes the issue isn’t about slowness, it’s about being blocked. Your firewall, CDN, or security plugin might be rejecting requests too aggressively. If you’re using tools like Cloudflare or Sucuri, dive into the firewall logs and adjust your rules. Whitelist safe IPs and be sure that your server's ports and protocols aren’t getting filtered.
## 7. Examine Server Logs
The server logs are your best friends here. Access logs and error logs will show exactly what requests were made and what happened right before the timeout. Look for patterns: Are certain pages always causing the error? Specific IP addresses? Certain times of day? These clues can help you zero in on root causes.
## 8. Contact Your Hosting Provider
If you’ve gone through everything and you’re still getting 408s, it’s time to tag in support. But choose your hosting provider wisely. Some hosts treat support like a waiting room with hold music.
With Levamo, you get real people who actually solve problems. No copy-paste replies. No red tape. Just fast, expert help when you need it most.
## Final Thought
You don’t need to be a server specialist to fix a 408 error, you just need a solid checklist. Whether it’s bad code, heavy traffic, or your server crying for help, these issues can be solved fast when you know where to look.
More importantly, they can be prevented even before they happen if you choose the right hosting for your website.
Levamo is built for developers and businesses that can’t afford downtime, delays, or excuses. We don’t just fix problems. We prevent them before they ever touch your visitors.
Your site should always show up ready, fast, and rock-solid. That’s what we deliver.
Ready to stop babysitting your site? **[Switch to Levamo](https://my.levamo.com/start)**.
---
## ARMember Review: Best WordPress Membership & Subscription Plugin
- URL: https://levamo.com/blog/armember-membership-plugin/
- Category: membership
- Author: Javeria
- Published: 2025-04-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is ARMember the right membership plugin for your WordPress site? Find out now.
Do you plan on providing exclusive content by [building a WordPress membership](/blog/create-a-membership-website/) or subscription site? Well, then you’re in for a super treat! Whether you’re a coach, content creator, or a community manager, you would need a powerful tool for membership management. Additionally, you also need a tool that helps lock in your content and supports content monetization features.
But before we go all in, let us have a brief about what a membership plugin is and how it helps building a WordPress membership site.
## What is a Membership Plugin and How Does it Help?
Technically, a membership plugin is a tool that allows restriction of specific exclusive content. Thus, this helps you to set up a paywall wherein only the registered users can access particular content. It helps you build a private, subscription-based environment to cater to a community.
A robust WordPress membership plugin provides the following features to sustain and manage a website.
- **Multiple Tiers:** Usually, a membership plugin helps you set up different levels or plans to allow users to choose the one that fits their needs and pocket.
- **Monetization:** Exclusive content must be behind a paywall for you to earn from it. You can sell access to content, courses, digital downloads, or even entire sections of your site.
- **Content Restriction:** It helps set up various rules for posts, pages, custom content, etc. based on user roles, membership levels, etc.
- **User Management:** Supports handling of registrations, logins, payments, member profiles, etc. in an easy way.
- **Automation:** The best WordPress membership plugin allows you to automate payments, content dripping, email notifications, and more for easy membership website management.
- **Scalability:** A membership site plugin usually provides third-party integrations and addons that help you grow your business with time. Thus, a great membership tool grows with you.
Now, you must be confused as to what kinds of businesses can use a membership tool. Well, it is more than just content-sites. Let’s have a look at it.
## What Kind of Businesses Can Leverage a Membership Plugin?
A membership plugin is a versatile tool and can power multiple types of business models. It can be used for content monetization, build a private community, offer exclusive service access, etc. Following is the list of businesses that can be powered by online membership sites.
- Online Course Creators
- Content Publishers & Bloggers
- Fitness & Wellness Coach
- Private Hobby Group
- Online Communities
- Private or Professional Associations
- Service-based Businesses like Freelancers
- Non-profit Groups
- E-commerce Brands
- Podcast Site
- Video Subscription Site Netflix
Well, you’re sold on the idea of creating a membership site. But what tool to use that is both powerful and affordable? That’s where ARMember steps in! In the following detailed review of the plugin, we shall take a deep dive into everything it has to offer. From the no-code setup to its powerful features, addons, pros, and cons. Let’s take you through a well-researched review and decide whether this Plugin should be a part of your list in 2025!
## What is ARMember?
ARMember is a [complete membership and subscription plugin](https://www.armemberplugin.com/) that helps protect your content, manage members, and set up various plans and recurring subscriptions. That too, right within your WordPress dashboard. It powers thousands of websites around the globe. Whether you want to sell online courses, restrict exclusive content, sell specific posts individually, or build a paid community; ARMember supports it all.
And using this tool, you don’t need to duct-tape or work with 5 different plugins at the same time. It is a truly all-in-one solution.
## Key Features of ARMember
Let’s break down why ARMember is your complete membership management solution.
### 1. Multiple Membership Levels
With ARMember, you can create unlimited membership levels to cater to different audiences. It allows various plan types like Free, Lifetime, Paid Finite, and Recurring Subscription. Thus, you can easily plan your website content as per different tiers.
### 2. Content Restriction
You can restrict your content by post, page, category, or even partially. Furthermore, define which plan members can access specific content posts. Create content dripping schedules to deliver your content step-by-step gradually. This kind of setup is perfect for coaching business or online courses for gated, structured delivery.
### 3. 21+ Payment Gateways
ARMember supports a total 21+ payment gateways like PayPal, Stripe, 2Checkout, Authorize.net, Bank Transfer etc and provides some of them in-built. You can easily configure free trials, paid trials, one-time fee, or a definite recurring payment.
### 4. Easy Member Management
The member management dashboard is super sleek and easy. Herein, you can view, edit, and manually approve member registrations. ARMember WordPress membership plugin allows you to assign one user to multiple memberships as well. Export/import member data and track their payment status/cycle right here.
### 5. Built-in Form Builder
Easily create and customize various forms like registration, login, forgot password, change password, etc. It also provides anti-spam features like Google reCAPTCHA. You can use the drag and drop builder and also leverage the pre-built templates.
### 6. Email Notifications
With 15+ email marketing integrations like Mailchimp, ActiveCampaign, Mailster, AWeber, Brevo, and more, you can automate your emails. ARMember provides a detailed shortcode library to customize and personalize your various email triggers.
### 7. Gamification & Badges
You can set up the in-built gamification features to reward your members with badges and achievements. This can be defined based on the user activity and can boost engagement among your membership community. You also get myCRED integration to set up points systems.
### 8. Pay Per Post Facility
Using ARMember for your membership site, you can sell individual posts to non-members. Thus, it is beneficial to rope in the audience that wants a sneak peek access to your exclusive content but are yet not ready to commit full-time to a plan.
These are some of the essential features that you get with ARMember. Apart from these, the plugin fashions 57+ inbuilt addons and 50+ external addons that supports full membership management.
## But Firstly, Is ARMember Easy to Use?
Straight Answer: Yes!
Its setup wizard walks you through the entire setup process. From creating a membership plan to setting up payments and content protection, it is intuitive and downright easy.
The admin dashboard is super clean and organized. Even if you’ve rarely or never worked with WordPress, ARMember setup would seem like a cakewalk. Even if you’re an advanced developer, you will get enough hooks, customization options, and custom CSS blocks to help you.
## Third-party Integrations: What ARMember Plays Well With
ARMember easily integrates with famous tools of WordPress realm. These might already be your favorites and in use.
**Email Marketing:** 15+ tools like Mailchimp, ConvertKit, GetResponse, AWeber, ActiveCampaign. MailerLite, Zapier, Zoho, HubSpot, Brevo, etc.
**Payment Gateways:** 21+ like PayPal, Stripe, Authorize.net, Mollie, Mercado Pago, RazorPay, PayFast, Paysafe, Skrill, 2Checkout, Bank Transfer, etc.
**Page Builders:** Supports 10 page builders viz. Gutenberg, Elementor, WPBakery, SiteOrigin, Beaver Builder, etc.
**Other Powerful Integrations:** WooCommerce, [BuddyPress](/blog/buddypress-review/), AffiliateWP, etc.
## Exclusive In-built Addons to Power Up Your Membership Site
Inbuilt Addons of ARMember provide exclusive features to extend your business exponentially. Let’s take a look at these features.
- **[Online Courses](https://www.armemberplugin.com/downloads/armember-online-courses-addon/)**: Allows you to create and sell online courses individually or as a part of a plan. Herein, you can add multiple lessons, sections, video, audio, text, and HTML content. It allows you to create graded quizzes with multiple field types and also assign completion certificates.
- **[Social Community](https://www.armemberplugin.com/downloads/armember-social-community-addon/)**: Build an in-house member engagement platform with features like feed posting, direct messaging, group creation, friend requests, follow/unfollow, etc. It allows setting up a vibrant community of like-minded people to share ideas.
- **[Affiliate Addon](https://www.armemberplugin.com/downloads/armember-affiliate/)**: With ARMember, you don’t require any external affiliate plugin. You can easily set up and manage your affiliates using this addon. It provides special affiliate links, dashboard, commission options, mass payout system, and much more.
- **WhatsApp & SMS Notifications:** To keep your members hooked, you can easily automate your notifications via WhatsApp or SMS.
- **Group/Umbrella Membership:** You can allow a member to purchase a group membership and assign child seats. Such plans can be offered to corporations and agencies.
- **Gift Membership:** Allow your members and visitors to buy your membership plan as a gift for someone else using this exclusive feature.
- **Proration:** Allow members to upgrade/downgrade their membership plan in between at any point in time. This feature smartly calculates the difference amount to be paid for the updated plan.
- **Membership Cards:** Use customizable membership card templates to assign a separate one to each plan type. Allow members to access it for a quick view at membership details.
- **Social Feature:** Allows social login options, provides access to member profiles, membership cards, directories, etc. It also activates the in-built gamification of badges and achievements.
- **Invoice & Tax:** This in-built invoicing and tax calculation system helps streamline financial operations and simplifies tax management.
- **Coupon Discounts:** You can create multiple coupons to provide discounts on member registrations.
- **WooCommerce Integration:** ARMember is WooCommerce compatible. This integration allows you to take all the benefits of the famous e-commerce platform with ease. Be it product selling or payment gateway extension, you get it all.
## ARMember Pricing: Free vs Paid
### Free Lite Version (available to [download free here](https://www.armemberplugin.com/?armlite_action=download_free_version))
**Includes:**
- Basic membership setup
- In-built Paypal and Bank Transfer Payment Support
- 9 Standard Page Builders Supported
- Unlimited plans
- All 4 types of plans
- Content restriction rules
- Bank transfer and PayPal integration
- Simple forms
- Redirection rules
- Anti-spam feature
The ARMember Lite version provides all the basic features to set up a fully functioning membership website. To explore more, you must go Pro. Here’s a quick overview of the pro pricing plans.
### ARMember Pro Version
[ARMember pricing](https://www.armemberplugin.com/pricing/) begins with our Standard plan at just $69 per year. It comes with various payment gateways, all in-built and free addons to be used on 1 site. You get access to Proration, Drip Content, Pay Per Post, Multiple Membership, and Two factor Authentication.
Its professional and enterprise plan with access to more addons and payment gateways are available starting at $129/year and $299/year. No monthly fees.
**Verdict:** The Pro version is a steal for the features it packs in a very budget friendly price. The yearly fee is a more convenient payment option than monthly fees for other such plugins. You can easily get yourself acquainted with the UI using the free version and then choose a plan that suits your requirements.
You can choose any of our plans based on your requirements. Check out the [ARMember demo](https://newdemo.armemberplugin.com/) for various membership setups in order to get a feel for the pro features.
## Pros & Cons of ARMember
### Pros:
- Perfect all-in-one solution.
- Affordable pricing options.
- Pre-made templates for form, directories, membership cards, and profile.
- Flexible content dripping and content access rules.
- Powerful integrations to scale up your business.
### Cons:
- Slight learning curve if you’re using custom CSS and shortcodes for the first time with WordPress. It will take some time to get used to it and do it intuitively for beginners.
## Final Verdict: Is ARMember the Right Membership Plugin for You?
Absolutely! If you want a powerful and budget-friendly option which is stacked with amazing features, this is perfect. Whether you’re just starting out with membership site business or scaling up, ARMember offers everything you need.
You can easily start with the free run and take it for the test drive before committing to a license. But you will not be disappointed, that’s for sure.
## Frequently Asked Questions (FAQs

### Is ARMember Secure?
It is a very secure plugin as it follows standard WordPress security practices. It offers role-based content restriction, captcha for forms, regular updates, etc. to be up to date.
### Does ARMember support recurring payments?
You can use the subscription plan type to set up recurring payments with ARMember. It can be customized to daily, weekly, monthly, yearly, or a custom duration of your choice.
### Can I offer a free trial with ARMember?
Yes, a free trial can be set up with ARMember. Moreover, you can also choose to offer a paid trial and charge a minimal amount. Both of these are possible with the recurring subscription plan type.
### Can I use ARMember as a beginner without any coding knowledge?
It is easy to use ARMember ARMember as it comes with a setup wizard and drag-and-drop form builder. It can be easily used without any coding. It might take some time to get comfortable with the advanced features setup.
---
## How to Clear Cache in WordPress
- URL: https://levamo.com/blog/wordpress-clear-cache/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-04-29
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Clear WordPress cache safely and fix site display issues.
If your WordPress site feels like it's stuck in quicksand or changes aren't showing up no matter how many times you refresh, there’s a good chance your cache is to blame. Caching is like your browser or server trying to be helpful by showing a saved version of your site, but when that saved version gets outdated, it causes all sorts of headaches.
WordPress Clear Cache sounds simple, but doing it the wrong way can break your layout, wipe important settings, or even boot visitors off your site. Let’s fix it the right way, clean, fast, and without breaking a sweat.
## What Is Cache in WordPress?
Cache is your website’s shortcut. Instead of loading everything from scratch every time someone visits, WordPress stores parts of your site, like images, CSS files, and even whole pages, to serve them up faster. It's the difference between cooking from scratch and reheating leftovers.
But when the cache gets stale (after a plugin update, theme change, or content tweak), you need to step in to make sure your site shows the latest version.
## Why Clearing Cache Matters
- **Fresh updates**: Changes to design, content, or backend settings don't show up until you WordPress Clear Cache and sweep the old stuff away.
- **Speed problems**: A bloated cache can slow things down instead of speeding them up.
- **Bug fixes**: Fixes or patches you apply won't reflect properly if the old cache keeps serving broken pages.
If you’re using Levamo, our turbocharged hosting automatically manages much of this for you, but it’s still smart to know how to WordPress Clear Cache manually when you need that extra control.
## How to Clear Cache in WordPress (Step-by-Step)
### 1. Clear Your Browser Cache First
Before touching WordPress, clear your browser cache. Sometimes it's not your site that's outdated; it's your local browser acting stubbornly.
**In Chrome**:
Settings → Privacy → Clear Browsing Data → Cached Images and Files → Clear Data.
### 2. Clear WordPress Caching Plugins
If you’re using a caching plugin, most offer a big, bold WordPress Clear Cache button. Here’s how to find it:
- **WP Super Cache**:
WordPress Dashboard → Settings → WP Super Cache → Delete Cache.
- **W3 Total Cache**:
WordPress Dashboard → Performance → Dashboard → Empty All Caches.
- **WP Rocket**:
WordPress Dashboard → Settings → WP Rocket → Clear Cache.
- **LiteSpeed Cache**:
WordPress Dashboard → LiteSpeed Cache → Toolbox → Purge All.
Tip: If you're hosting with Levamo, our platform is fully compatible with WP Rocket and LiteSpeed Cache, and we fine-tune them for maximum punch.
### 3. Clear Hosting Cache
Some hosting providers (especially the slower ones) make WordPress Clear Cache a maze. Levamo cuts through that noise. We give you one-click cache clearing inside your control panel, no guessing games.
### 4. Clear CDN Cache
If you’re using a CDN (Content Delivery Network) like Cloudflare:
- Log into your Cloudflare dashboard.
- Select your site.
- Go to Caching → Configuration → Purge Everything.
You guessed it: another important WordPress Clear Cache step if you want your site changes to actually show across the globe.
### 5. Clear Object Cache
If you’re using [object caching](/blog/key-db-and-redis/) (Redis, Memcached), flushing it occasionally can solve weird bugs:
- Some plugins offer an option under settings.
- Or, if you have access to your hosting panel (like Levamo’s intuitive dashboard), you can flush it safely without touching scary server commands.
Every layer brings your site back to peak condition.
### Pro Tip: When Not to Clear Cache
During peak traffic spikes (like during a promotion or product launch), clearing cache can cause a temporary slowdown while everything rebuilds. Time it smartly - early mornings or off-peak hours work best.
At Levamo, our smart cache system auto-regenerates immediately after clearing, so you don’t miss a beat.
## Make Cache Your Friend
WordPress Clear Cache isn’t just maintenance - it’s a smart way to keep your WordPress site sharp, speedy, and up-to-date. The trick is knowing where the cache lives: browser, plugin, host, or CDN.
And if you’re tired of juggling cache-clearing rituals just to keep your site running, it’s time to host smarter. Levamo fixes your cache problems before they cost you money, visitors, or rankings.Ready for a WordPress hosting experience that actually feels fast? **[Try Levamo](https://my.levamo.com/start)** today.
---
## How to Set Up & Manage WordPress Cron Jobs
- URL: https://levamo.com/blog/wordpress-cron-jobs/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-04-28
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Make WordPress cron jobs reliable! This easy setup guide keeps your site humming.
If you’re running a WordPress site, cron jobs are the quiet MVPs keeping everything ticking. They publish scheduled posts, check for plugin updates, and clean up spam comments. They're like your site's internal engine, quietly turning the gears so you don’t have to.
But if you’re relying on the default WordPress cron jobs system, you might be surprised how often things go sideways. Late posts, missed backups, slowdowns during traffic spikes, all because WP-Cron isn’t built for consistency.
This guide will show you how to fix that.
## What Are WordPress Cron Jobs?

In a traditional server setup, a cron job is an automated task that runs at specific intervals. Think of it like a programmable coffee maker for your server: wake up at 6 a.m., brew a fresh pot, and repeat every day. You tell your server when to run a script, and it listens without fail.
WordPress tries to mimic this with WP-Cron, a pseudo-cron system that triggers scheduled tasks when someone visits your site. Instead of relying on the server clock, WP-Cron waits for traffic to trigger its process.
That might sound clever, but it causes problems:
- Low-traffic sites may not trigger scheduled tasks on time.
- High-traffic sites can trigger WP-Cron too often, hurting performance.
- Scheduled events may pile up if the system stalls or if visitors aren’t loading the right pages.
This can lead to broken experiences: your readers don’t see that 9 a.m. blog post on time, your daily backup doesn’t run, and your cache doesn’t clear like it should.
## Why You Should Replace WP-Cron with a Real Cron Job
If WP-Cron is holding your site back, replacing it with a real cron job is like switching from a push lawn mower to a self-propelled one.
Here’s why:
- **Precision**: Your tasks run exactly when you say so.
- **Performance**: Offloading scheduled tasks to a server cron keeps them out of the way of your visitors.
- **Reliability**: Real cron jobs don’t rely on traffic to function.
At [Levamo](/), we’ve helped countless customers fix mysterious WordPress issues by making this one change. Missed backups, late email blasts, even plugin conflicts; many of these get resolved once your tasks start running on a dependable schedule.
## Step 1: Disable WP-Cron
Before you set up a real cron job, you need to turn off WordPress’s default system. It’s easy:
- Access your WordPress site's files via FTP or your host's file manager.
- Find and open the wp-config.php file in the root directory.
- Add the following line of code:
`define('DISABLE_WP_CRON', true);`
This tells WordPress to stop trying to run scheduled tasks on its own.
Don’t skip this step. If you leave WP-Cron active while also running a real cron job, you’ll end up with conflicts, duplicate tasks, or missed triggers.
## Step 2: Set Up Real WordPress Cron Jobs
Now that WordPress Cron Jobs are out of the way, it’s time to set up a real cron job on your server.
If you’re hosting with Levamo, this part is simple. We give you access to true server-level cron scheduling right from your dashboard; no special tools or SSH commands required. But if you're working with another host (for now), you may need to follow a slightly different process.
**Via cPanel**:
- Log in to your hosting control panel.
- Find the "Cron Jobs" section.
- Add a new cron job at the desired time.
- Use this command to trigger WordPress:
`*/5 * * * * php /home/yourusername/public_html/wp-cron.php > /dev/null 2>&1`
This runs the wp-cron.php file every 5 minutes. Adjust the interval depending on how often you want your tasks to run.
**Via SSH** (for developers and VPS users):
You can edit the crontab manually by running:
`crontab -e`
Then paste in the same cron expression above.
Either way, what you’re doing here is giving your server a direct command to run WordPress cron tasks on a real schedule, one that doesn’t depend on random site visits.
## Step 3: Monitor & Troubleshoot
Once your real cron job is live, the heavy lifting is done. But don't just set it and forget it.
**Check for signs of success:**
- Are scheduled posts going live on time?
- Are your backup plugins finishing without errors?
- Do analytics or logs show a regular pattern of activity?
You can install the [WP Crontrol plugin](https://wordpress.org/plugins/wp-crontrol/) to view and manage scheduled events from the WordPress dashboard. It shows what tasks are queued, when they’ll run, and whether anything’s failing.
This is especially helpful if you're using third-party plugins with their own scheduled jobs (like SEO crawlers, email integrations, or e-commerce tools). If something isn’t firing, WP Crontrol can usually point you to the issue.
Also, keep your eyes on server resources. If you're running tasks too frequently, you might notice a CPU spike or lag. In that case, consider adjusting the frequency or offloading heavier tasks to background processes.
## Pro Tips for Managing WordPress Cron Jobs Like a Pro

Here are a few extra tips to level up your Cron game:
**1. Don’t overschedule.** More isn’t always better. Some tasks (like database cleanups or SEO scans) are fine running once a day.
**2. Know your plugins.** Some plugins add heavy tasks to your cron schedule without telling you. Use WP Crontrol to keep things lean.
**3. Use logging.** For custom tasks or critical operations, add simple logging to confirm they're running correctly. Even a basic error_log("Backup started at " . date("Y-m-d H:i:s")) can save your skin in a crisis.
**4. Separate heavy tasks.** If one task hogs resources, run it less often or move it to a different schedule to avoid slowing everything down.
**5. Backups are non-negotiable.** Automate them. Double-check them. Store them off-site.
## Wrapping Up
Running a serious WordPress site means treating scheduled tasks seriously. Replacing WordPress Cron Jobs with real cron jobs gives you tighter control, fewer failures, and a site that behaves like a grown-up.
At [Levamo](/), we make this easy. You get access to real cron scheduling right from your dashboard, with no jumping through hoops, no hacks, and no guesswork. We built our platform for people who want performance without babysitting their site 24/7.
So the next time your WordPress post goes live *when it wants to*, remember: it doesn’t have to be that way. Take the wheel.
---
## How to Fix the 500 Internal Server Error in WordPress
- URL: https://levamo.com/blog/fix-the-500-internal-server-error/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-04-25
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix that annoying 500 error! This guide helps find the cause and fix it fast.
You’re clicking through your WordPress site, everything’s humming, and then bam. A white screen. One line of text:
**“500 Internal Server Error.”**
Cue the panic.
The http error 500 is one of the most annoying, cryptic issues you can run into. It tells you *something* went wrong on the server, but not *what.* It's like your site is screaming for help, but mumbling at the same time.
If you’re staring down that error right now, or just want to know how to avoid it in the future, this guide is for you. We’ll walk through how to find the root cause, how to fix it fast, and why your hosting environment is probably part of the problem.
Let’s get into it.
## What Is the 500 Internal Server Error?
The HTTP error 500 is a generic status code returned when the server hits a problem it can’t define. That’s what makes it tricky; it could be a corrupted file, a bad plugin, an exhausted PHP limit, or something deeper in your host’s infrastructure.
And WordPress, being a PHP-heavy CMS with lots of moving parts, is especially prone to this one.
If you're getting a 500 error, it means your server crashed *before* it could even load your site. So, frontend diagnostics are out. You’ve got to go back to the backend.
## Step-by-Step: How to Fix the 500 Internal Server Error in WordPress
### 1. Check for Corrupted .htaccess Files
This is the low-hanging fruit. The .htaccess file controls how your server handles requests. A small error in here can break your entire site.
#### How to fix it:
- Log in to your site via **FTP** or **File Manager** in your hosting control panel.
- Locate the .htaccess file in your root directory.
- Rename it to .htaccess_old.
- Try reloading your site.
If the site loads, the problem was in that file. WordPress will generate a new one when you reset your permalinks under **Settings > Permalinks** in the admin dashboard.
### 2. Increase Your PHP Memory Limit
Sometimes the error isn’t about broken code; it’s about running out of room. If your theme or a plugin is hogging resources, you can hit the [memory ceiling](/blog/maximum-php-memory-limit/) and trigger an HTTP error 500.
#### Fix it like this:
- In your root directory, find and edit wp-config.php.
- Add this line just before “That’s all, stop editing!”:
`define('WP_MEMORY_LIMIT', '256M');`
- Save the file and reload your site.
Still no luck? Your host might be limiting memory at the server level. If you're on shared hosting, that's usually the case.
### 3. Deactivate All Plugins
If the error appeared right after installing or updating a plugin, that’s your likely suspect.
But even if you haven’t made a change recently, plugins can conflict in weird ways, especially after core WordPress updates.
#### Here’s how to isolate the problem:
- Access your site via FTP.
- Go to wp-content/ and rename the plugins folder to plugins_old.
- Check your site.
If it loads, rename the folder back and start reactivating plugins one at a time from the WordPress dashboard until the error returns. That’s your culprit.
### 4. Switch to a Default Theme
Themes can trigger the HTTP error 500 too, particularly if the theme is outdated or includes poorly written functions.
#### How to test it:
- Go to wp-content/themes/ via FTP.
- Rename your active theme’s folder to something like theme_old.
- WordPress will automatically fall back to a default like Twenty Twenty-Four (if it's installed).
No error? Your theme needs a rewrite or a replacement.
### 5. Check Your File Permissions
Incorrect permissions can lock WordPress out of its own files, causing a 500 error.
#### Standard permissions should be:
- **Files:** 644
- **Folders:** 755
Use your FTP client or the host’s file manager to check and correct them. Be careful with this one; the wrong permissions can break things even more.
### 6. Enable Debug Mode
WordPress has a [built-in debugging system](/blog/debug-in-wordpress/) that can show more helpful errors than just “500.” It won’t fix things on its own, but it can shine a light where it’s dark.
#### How to turn it on:
Edit your wp-config.php and add these lines:
define('WP_DEBUG', true);
define('WP_DEBUG_LOG', true);
define('WP_DEBUG_DISPLAY', false);
Then check the wp-content/debug.log file for clues.
### 7. Look at Your Server Error Logs
If your host gives you access to server logs (good hosts do), check them. You'll find them in your hosting control panel under something like "Logs" or "Error Logs."
These logs usually contain the exact line where the script crashed. That can save you hours.
### 8. Re-upload Core Files
Corrupted or missing WordPress core files can also throw an http error 500. To fix it:
- Download a fresh copy of WordPress from wordpress.org.
- Extract the zip and upload everything *except* the wp-content folder via FTP, overwriting existing files.
- Don’t touch wp-config.php.
This keeps your content intact while restoring any broken core files.
## What If None of That Works?
If you’ve ruled out plugins, themes, memory limits, and file issues, it might be your hosting environment itself.
Low-tier hosts often cram too many customers onto shared servers, throttle resources without telling you, and won’t show you meaningful logs. So you’re left guessing.
**That’s where Levamo flips the script.**
We don’t just make it easy to run high-performance WordPress sites. We *engineer* out the nonsense.
- **Isolated containers.** Every environment runs in its own container, so one bad neighbor can’t crash your site.
- **Real-time error tracing.** We give you actual data, not vague messages.
- **No silent throttling.** You get all the power you pay for, and then some.
- **Automatic backups.** So if you mess something up, you’re one click away from fixing it.
The HTTP error 500 shouldn’t be your introduction to debugging. With Levamo, you avoid 95% of the reasons it shows up in the first place.
## Pro Tips to Avoid the HTTP Error 500 Forever
- **Update regularly, but smartly.** Always test plugin and theme updates on a [staging site](/blog/how-wordpress-sandboxes-help-developers-test/).
- **Use quality plugins and themes.** Don’t just grab whatever’s free. Look at reviews and support history.
- **Back up daily.** Levamo does this automatically, but if your host doesn’t, use tools like BlogVault or UpdraftPlus.
- **Don’t ignore PHP limits.** If your site’s growing, bump those numbers. Or better yet, move to a host that doesn’t cap you behind the scenes.
- **Monitor uptime.** Tools like UptimeRobot or, better yet, Levamo's built-in alerts will tell you the second something goes wrong.
## Final Thoughts
The HTTP error 500 is frustrating because it’s vague. But once you know where to look, it’s rarely more than a 10–15 minute fix.
Just remember, if you’re dealing with this more than once, the issue might not be your site. It might be your host.
At Levamo, we built our infrastructure to keep developers out of fire-drill mode. That means faster sites, cleaner logs, and fewer white-screen meltdowns. So you can spend your time building, not babysitting your backend.
If you're tired of guesswork and gobbledygook error messages, come check out how hosting *should* work.
Your code deserves better.
---
## Heads Up: Phishing Campaign Targeting WooCommerce Stores
- URL: https://levamo.com/blog/phishing-campaign-targeting-woocommerce-stores/
- Category: website-security
- Author: Sunyyan Junaid
- Published: 2025-04-24
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WooCommerce store owners: Beware of a new phishing scam! Stay safe now.
If you run a WooCommerce store, this is worth your attention. WooCommerce has issued a developer advisory about a new phishing campaign that’s targeting store owners with fake security alerts.
Here’s a quick breakdown of what’s happening and how you can stay safe.
## What’s Going On?
Attackers are sending fake emails pretending to be from WooCommerce. They claim your site has a " critical security vulnerability" discovered around April 14, 2025, and they urge you to install a “security patch,” which, of course, is actually malware.
These emails are designed to look convincing, often mentioning your specific store URL to add pressure. But they're coming from shady domains like:
- `help@security-woocommerce.com`
- `incident@notify-woocommerce.com`
- `help@support-woocommerce.com`
**These are not official WooCommerce communications.**
Additional comments on the official post from WooCommerce shared the following:


In short, many users reported more malicious domains than the initial reported ones:
`woocommėrce.com` (with an accent mark on the ‘e’)
`noreply@news-woocommerce.com`
`noreply@woocommerce-secure.com`
`security@mail-woocommerce.com`
`security@news-woocommerce.com`
`noreply@woocommerce-monitor.com`
`noreply@woocommerce-updates.com`
Real security updates from WooCommerce always come from trusted domains like `woocommerce.com` or `automattic.com`, and they'll direct you to legitimate sources like WordPress.org or WooCommerce.com, never to random downloads.
## What You Should Do
If you spot one of these emails:
- **Don’t click any links** or download any files.
- **Don’t install** any plugins or patches sent through email.
- **Report the email** as phishing to your provider.
When in doubt, go directly to your WordPress dashboard or WooCommerce.com for updates and never trust links inside an email you weren’t expecting.
Read the Dev advisory from WooCommerce [here](https://developer.woocommerce.com/2025/04/22/dev-advisory-phishing-campaign-targeting-woocommerce-stores/?utm_source=chatgpt.com).
## How Levamo Helps Keep You Safe
While we can’t control external phishing campaigns, [Levamo](/managed-security/) can help you build a more secure foundation through:
- **Automatic WordPress updates** so your core software and plugins stay current.
- **Server-side malware scanning** to spot suspicious files early.
- **Daily backups** that make it easy to recover if something ever goes wrong.
- **Real human support** that can help if you’re worried about your site’s security.
Your WooCommerce store deserves better than crossing your fingers and hoping hackers stay away.
Stay sharp, and if you ever need help [locking down your store](/blog/woocommerce-security-checklist/), the Levamo team has your back.
---
## How to Fix Error 522: Step-by-Step Troubleshooting for Cloudflare Timeouts
- URL: https://levamo.com/blog/how-to-fix-error-522/
- Category: wordpress
- Author: Sunyyan Junaid
- Published: 2025-04-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix Error 522 timeouts! Step-by-step Cloudflare troubleshooting tips inside.
**Error 522** is Cloudflare’s way of saying, “I tried to talk to your server, but it’s giving me the silent treatment.” The result? Your visitors hit a wall. Your site feels broken. And if you’re running a business, that means lost conversions and angry users.
This guide covers exactly how to fix **Error 522**, why it happens, and how to make sure it doesn’t come back.
## What Is Error 522 (Cloudflare Connection Timed Out)?
**Cloudflare Error 522** happens when Cloudflare successfully reaches your origin server’s IP address, but the server fails to respond before the connection times out. The connection is established, but no data is exchanged.
This is different from an unreachable server or bad DNS configuration. With **HTTP error 522**, Cloudflare can get to your server, but your server doesn’t respond in time.
## What Causes Error Code 522?
You’re not dealing with just one issue here. A **522 error** can be caused by multiple things:
### 1. The origin server is too slow or overloaded
If your hosting server is maxed out, under-provisioned, or just plain down, Cloudflare won’t get the reply it needs.
And if that's the case, you should really look into a better hosting solution like [Levamo](/) to power your websites. Levamo doesn't just provide hyperspeed hosting, but it ensures your website remains online 99.99% of the year with autoscaling servers and many other must-have features.
But let's move on to the other reasons that can cause Error 522.
### 2. Firewall or security software is blocking Cloudflare
Your server might be configured to block or rate-limit Cloudflare’s IPs. Some firewalls see Cloudflare as suspicious traffic.
### 3. Incorrect DNS settings
If your A record in Cloudflare is pointing to the wrong IP address, Cloudflare will wait for a response that never arrives.
### 4. KeepAlive is disabled
Cloudflare expects persistent HTTP connections. If your server closes connections too soon, the result is a **522 connection timed-out error**.
### 5. Network routing problems
Sometimes the route between Cloudflare’s data centers and your server gets messed up. This could be a provider-level issue.
## How to Fix Error 522 (Full Guide)
Let’s fix it. Here’s a full list of steps to troubleshoot and resolve **Cloudflare Error 522** on any host, including instructions for users hosted on **[Levamo](/pricing)**.
### ✅ Step 1: Check if your origin server is online
Start by making sure your server is actually responding.
If you're on **Levamo**, log in to your dashboard and check your server’s status. Check the status of [Levamo service here](https://status.levamo.com/).
You can also SSH in directly or use our one-click console to ping your site.
ping yourdomain.com
curl -I yourdomain.com
If there’s no response or a timeout, restart the server or check for any pending software updates, crashes, or disk space issues.
### ✅ Step 2: Whitelist Cloudflare’s IPs in your firewall
Cloudflare maintains a list of IPs you should always allow through.
**With iptables:**
`iptables -I INPUT -p tcp -m multiport --dports http,https -s CLOUDFLARE_IP -j ACCEPT`
Repeat for each IP in this list:
https://www.cloudflare.com/ips
**On Levamo**, if you're using our built-in firewall, go to the **Firewall** section in the dashboard and add Cloudflare's IP ranges under "Allowed Sources".
Make sure to reload or restart the firewall afterward.
### ✅ Step 3: Check your DNS records in Cloudflare
Go to your Cloudflare dashboard → **DNS tab**.
- Look for the A record pointing to your root domain (@)
- Make sure the IP matches your current origin server’s public IP
If you're unsure, you can check your server’s IP using:
`curl ifconfig.me`
Update the A record if it’s pointing somewhere old or incorrect.
### ✅ Step 4: Make sure KeepAlive is turned on
Cloudflare requires persistent HTTP connections.
#### For Apache:
Open your configuration file and enable KeepAlive:
`KeepAlive On`
#### For NGINX:
Make sure this is in your config:
keepalive_timeout 65;
Then restart your web server:
sudo systemctl restart apache2
# or
sudo systemctl restart nginx
### ✅ Step 5: Check for server load issues
If your server is struggling to keep up, timeouts are inevitable.
Use the following commands to check CPU, memory, and disk usage:
top
free -m
df -h
**Levamo** users can view real-time CPU and RAM stats in the Hosting dashboard. If usage is consistently high, consider upgrading your plan or turning on autoscaling.
A view of the CPU and RAM usage in the Levamo Dashboard
### ✅ Step 6: Run a traceroute to detect network issues
Traceroute will help you see if the problem is happening somewhere between Cloudflare and your server.
traceroute www.cloudflare.com
If the trace breaks mid-path or shows significant delays, the issue might be network-related and outside your control. Contact your hosting provider or Cloudflare support if it’s persistent.
### ✅ Step 7: Try Levamo CDN instead of Cloudflare
Cloudflare is powerful, but it’s not always the right fit for every website.
If you’re tired of dealing with **522 errors**, consider using **[Levamo CDN](/cloudflare-cdn/)**, our free global CDN that integrates natively with Levamo hosting. It’s fast, reliable, and designed to reduce errors like this by keeping traffic closer to your users and your server under less stress.
You get the benefits of content delivery without the configuration headaches.
## Wrapping Up
**HTTP error 522** is a common Cloudflare error that means your server is too slow or unreachable, even though Cloudflare can connect to it. Fixing it means checking your server’s health, DNS, firewall rules, and connection settings.
And if you want fewer moving parts, less complexity, and built-in performance tools, **Levamo** gives you fast hosting plus a free global CDN (Levamo CDN). It's designed to eliminate connection errors before they ever show up, so if you want to avoid these problems, make sure to [check it out](/cloudflare-cdn/).
## FAQs About Cloudflare Error 522

### What’s the difference between error 522 and other Cloudflare errors like 521 or 524?
Error **522** means the origin server didn’t respond in time.
[**Error 521**](/blog/cloudflare-error-521/) means the connection was refused.
**Error 524** means a successful connection was made, but it took too long to process the request.
### Can Cloudflare error 522 be caused by plugins or security apps?
Yes. Web application firewalls (WAFs), security plugins like Wordfence, and even server-side anti-DDoS tools can mistakenly block or throttle Cloudflare requests.
### Is error 522 always a server issue?
Most of the time, yes. Cloudflare connects successfully, but your server doesn’t reply. This could be due to traffic spikes, misconfiguration, or bad routing.
### Will Levamo CDN solve this problem permanently?
In many cases, yes. Levamo CDN removes the need for third-party layers that can block or slow down traffic. It connects directly to our hosting infrastructure, reducing the risk of connection issues.
### Can I monitor for 522 errors automatically?
Yes. Use uptime monitoring tools like UptimeRobot or Levamo’s built-in performance insights to get alerts when your server goes silent.
---
## Crocoblock Review: Is It Still Worth It in 2025?
- URL: https://levamo.com/blog/crocoblock-review/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-04-22
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Crocoblock in 2025: Still worth it? My honest review reveals the pros and cons.
If you've been building WordPress sites for a while, chances are you've stumbled across the colorful, oddly satisfying world of Crocoblock. Or maybe you Googled something like "Elementor dynamic content" and landed on a JetEngine tutorial. Either way, you're not alone. Crocoblock has carved out a serious space in the world of no-code website creation.
But is it still worth using in 2025?
Here’s my honest Crocoblock review, from one WordPress tinkerer to another. Spoiler: it’s not all sunshine and popups.
### First, What Is Crocoblock?

Crocoblock is a toolkit of WordPress plugins, known as JetPlugins, that help you build feature-rich, dynamic websites without coding. Initially made for [Elementor Review](/blog/elementor-review/), Crocoblocks now works with Gutenberg and Bricks Builder, too.
In total, you get 20+ plugins, over 200 widgets, templates for different niches, and a centralized dashboard that keeps your WordPress backend looking somewhat sane (at least until your plugin count hits 50+).
And despite what autocorrect might tell you, it’s not “crockoblock” or “crocobloc.” It’s Crocoblock. With a K. Think Lego bricks for web devs.
### JetPlugins Breakdown: The Real Reason You’re Here
Here’s what you’re really paying for: the JetPlugins suite.
Let’s talk JetEngine, because this plugin alone could justify your Crocoblock subscription. It lets you create custom post types, custom fields, relationships between post types, front-end forms, dynamic listings, maps, filters, you name it. If you’ve used ACF before but wished it was built for visual thinkers, JetEngine is for you.
You can use JetEngine with:
- Elementor
- Gutenberg
- Bricks Builder
The plugin is also the foundation for others in the Crocoblock family, including JetBooking and JetAppointment. So if you’re running any kind of dynamic directory, real estate listing, event platform, or anything with user-submitted content, JetEngine turns your WordPress site into a custom database without touching SQL.
That said, the learning curve is real. There are a *lot* of moving parts. Don’t expect to master JetEngine over coffee.
Other standout JetPlugins include:
- **JetSmartFilters:** Advanced filtering for any kind of post type or WooCommerce product.
- **JetFormBuilder:** A surprisingly powerful form builder with conditional logic and integrations.
- **JetWooBuilder:** Lets you customize WooCommerce product pages like a boss.
- **JetPopup:** Yep, it does popups, exit intent, time delay, scroll, and all.
- **JetMenu:** For mega menus that don’t make you mega frustrated.
You can buy each plugin individually, but most people (myself included) go for the All-Inclusive plan. More on that later.
### Elementor, Gutenberg, Bricks: It’s Not a One-Theme Pony Anymore
Crocoblock used to be Elementor-only, and that’s how most people discovered it. But in the past couple of years, they’ve opened up support for Gutenberg and Bricks. JetEngine, JetSmartFilters, and JetFormBuilder now support all three.
This is great news if you’re trying to future-proof your stack. With WordPress pushing hard on full site editing, having Gutenberg compatibility is not just nice; it’s necessary.
### What’s It Like to Use Crocoblock in Real Projects?
Once installed, Crocoblock gives you a unified dashboard inside WordPress where you can manage all your JetPlugins. Install, update, deactivate, or even roll back to earlier versions if something breaks. (That feature alone has saved me during a few plugin clashes.)
The real strength of Crocoblocks is how the plugins work together. For example, you can:
- Build a listing grid with JetEngine
- Add front-end filters with JetSmartFilters
- Style the whole thing in Elementor
- Drop in a dynamic form built with JetFormBuilder
No custom code. No third-party workarounds. Just you, your mouse, and a slightly overworked CPU.
### Dynamic Templates and Widgets Galore
Crocoblock includes dynamic templates for various industries like real estate, job boards, doctor appointments, and so on. These are pre-built setups that include CPTs, filters, and layouts. If you’re building client sites or MVPs, they can save you hours and maybe even days.
You’ll also get 200+ Elementor widgets through plugins like JetElements and JetTricks. Some are genuinely useful (like tables and pricing sliders), others are more novelty (Lottie animations everywhere), but the selection is wide.
A small gripe: some widgets feel like they belong in the same plugin. JetElements, JetTabs, and JetBlog, for example, could probably be bundled. There’s plugin fatigue when you’re installing 15+ things just to get basic UI elements.
### What Could Be Better?
Alright, let’s talk trade-offs.
Crocoblock’s biggest strength, its modularity, is also its weakness. Managing 20 plugins, especially on big projects, can feel overwhelming. And while the dashboard helps, your Plugins screen in WordPress still gets cluttered fast.
Also, not every plugin supports every builder. JetWooBuilder only works with Elementor. So if you’re team Gutenberg or Bricks, you’ll run into the occasional dead end.
And let’s be honest: Elementor itself has gotten better. A lot of Crocoblock’s early appeal was that it added features Elementor was missing. But now, Elementor Pro includes things like loop builders and display conditions, which makes some JetPlugins feel redundant.
Still, there are areas where Crocoblock clearly wins:
- Better dynamic content workflows
- More powerful front-end filters
- Visual control over CPTs and meta fields
- AI-assisted tools (yes, they’re rolling that in now, too)
### Pricing: Is the All-Inclusive Plan Worth It?

If you’re doing client work, yes. No question.
The All-Inclusive plan is $199/year and includes every JetPlugin, dynamic templates, widgets, and support. If you go the freelance route, you can pay $750 for lifetime access, which includes updates and support.
Honestly, one decent client project pays for that. Even better if you stack it with a Crocoblock discount coupon.
For hobbyists or one-off projects, the value is more debatable. If all you want is dynamic listings and basic filters, JetEngine alone might be enough.
### Fastest Hosting for Crocoblock
There’s no point building a lightning-fast site with JetEngine if your hosting crawls like it’s stuck in 2006. Crocoblock sites, especially those using dynamic content, filters, and WooCommerce, can be resource-hungry.
That’s where Levamo comes in. Our infrastructure is built to handle dynamic WordPress sites at scale. Whether you're pulling content from complex custom post types or running filtered queries with JetSmartFilters, Levamo keeps your site zipping along without the headache of slow load times.
- Real-time performance monitoring
- Autoscaling to handle traffic spikes
- Built-in caching optimized for Crocoblock workflows
- Developer-friendly tools with zero bloat
If you want to get the most out of your Crocoblock setup, fast hosting isn’t optional; it’s essential. Pair your Jet-powered stack with Levamo and give your users the speed they expect.
### The Verdict: Is Crocoblock Still Recommended in 2025?
Yes, especially if you build complex or client-heavy sites in WordPress.
Despite Elementor catching up and the increasing capabilities of Gutenberg, Crocoblock still offers more control over dynamic content than most plugins on the market. The [JetEngine plugin](/blog/no-code-logic-building-smarter-with-crocoblock/) alone is worth a look if you’re serious about building advanced functionality without a developer.
The ecosystem isn’t perfect, and there’s a bit of plugin overload. But the payoff is huge once you get the hang of it.
**TL;DR:**
- Crocoblock is still a powerhouse for dynamic WordPress sites
- JetEngine is the real MVP
- All-Inclusive plan = best value
- Don’t type “crockoblock” or “crocobloc”, your search results will cry
If you’re in the trenches building sites that need more than just pretty pages, Crocoblocks are still one of the best no-code tools to have in your toolbox.
And hey, while you’re optimizing your front-end experience with JetEngine, let Levamo handle the speed, reliability, and infrastructure on the back end. Because even the most dynamic site won’t matter if it loads slower than your coffee pot.
Happy building.
---
## 10 WordPress Features You Probably Didn't Know About (But Should)
- URL: https://levamo.com/blog/10-wordpress-features-you-probably-didnt-know-about-but-should/
- Category: wordpress
- Author: Sunyyan Junaid
- Published: 2025-04-18
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Unlock hidden WordPress power! Ten secret features await you.
Ever feel like WordPress is holding out on you? Like there's a secret stash of features somewhere, just waiting to make your life easier?
You're not wrong. WordPress is packed with clever tools that most people never discover. And while everyone else is busy installing plugins for everything under the sun, you're about to unlock some built-in magic. No bloat. No fluff. Just powerful features of WordPress hiding in plain sight.
Let’s pull back the curtain.
### 1. The Secret Master Settings Page
**URL:** yourdomain.com/wp-admin/options.php
This is WordPress's secret lair. A single page that lists every config setting stored in your database.
You’ll find settings here that don’t appear anywhere else in the admin dashboard. Think upload limits, default category IDs, hidden plugin configs, it's all there. If you want full control over your WordPress settings, this is the place.
On this page, though, you'll get the following warning, so be careful:

### 2. Schedule Posts Like a Time-Traveling Content Wizard
Planning a big launch? Going on vacation? WordPress has you covered.
Every post and page lets you schedule its publish date. Just click the “Immediately” link next to Publish and choose a future time. Your content goes live even if you’re off the grid.

It’s one of those simple but game-changing WordPress features once you start using it.
### 3. Password-Protect Any Page (No Plugin Required)
Want to show a client a draft page without publishing it? Need to gate internal docs?
Under “Visibility” in the post editor, hit “Password Protected” and set a password. Done.
Password-protect your posts in WordPress
It’s the simplest form of access control, baked right into WordPress functionality.
### 4. Fight Spam with Custom Comment Rules
Go to **Settings > Discussion,** and you’ll find some underrated spam-fighting options:
- Automatically trash comments with certain words or links
- Hold suspicious comments for manual review
This is one of those WordPress secrets that saves time and sanity, especially on content-heavy sites.
### 5. Activate Multisite Mode
Built into WordPress' core, Multisite lets you run **multiple websites from a single install.**
Perfect for agencies, school networks, franchise businesses, or anyone managing multiple web properties.
You’ll need to edit your wp-config.php file to enable it, but once it’s live, you can spin up new sites in minutes. A true gem in the list of advanced WordPress features.
### 6. Edit Images Right in the Media Library
Need to crop, flip, or rotate an image? No need for Photoshop.
Image editing options in #WordPress
WordPress has a built-in image editor. Just open any image in the Media Library and click “Edit Image.”
It's one of those low-key features of WordPress that quietly gets the job done.
### 7. Gutenberg Has More Blocks Than You Think
The block editor keeps getting smarter.
Beyond the basics, there are blocks for tables, buttons, media embeds, and even custom HTML. And if you're using a theme or plugin that adds extra blocks (like Stackable or Kadence), you can build full landing pages without touching a line of code.

Explore the block inserter, it’s a fun way to uncover hidden WordPress functionality.
### 8. Use Shortcodes Like a Pro
WordPress has several built-in shortcodes you can use without any extra plugins:
- [ gallery ] - to create image galleries
- [ audio ] - to embed audio files
- [ video ] - to embed video
- [ caption ] - to add image captions
These are simple but powerful tools in the WordPress features toolkit.
### 9. Explore Theme Customizer Secrets
Head to **Appearance > Customize** and dig into every section.

Some themes hide performance settings, layout tweaks, and advanced typography controls in there. You’ll be surprised what you find, especially in themes like [Astra](/blog/astra-wordpress-theme-review/), GeneratePress, and Blocksy.
Play around with it. It’s one of those corners of WordPress settings that can completely change how your site feels.
### 10. Generate Application Passwords (API Access, the Easy Way)
Need to connect your WordPress site to a third-party app? Go to your user profile and scroll down.
You’ll see a section called **Application Passwords.**
Generate one, and you can safely connect tools like Zapier, headless CMS front-ends, or mobile apps without giving away your main login credentials.
It’s secure, clean, and built into core WordPress functionality.
### Bonus: Want Fewer Plugins and Faster Sites?
At [Levamo](/), we’re all about performance and simplicity. The more you can do **with WordPress itself**, the fewer plugins you need. And fewer plugins mean:
- Less bloat
- [Fewer security risks](/managed-security/)
- [Better performance](/performance/)

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
Plus, our hosting is tuned for dynamic, [high-demand WordPress sites](/blog/fastest-wordpress-hosting/). So, even if you're running a [BuddyBoss community](/buddyboss-hosting/), an [LMS](/managed-lms-hosting/), or a [WooCommerce store](/managed-woocommerce-hosting/), your site stays blazing fast, even on launch day.
Explore Levamo if you’re ready to level up your WordPress stack and unlock the best WordPress features without lifting a finger.
**Final Word:** WordPress isn’t just for blogging anymore; it’s a full-on powerhouse once you dig a little deeper. And if you’ve only scratched the surface, now’s the time to dive in.
Which one of these features surprised you the most? Drop it in the comments or tag us on LinkedIn. We love nerding out over smart WordPress tricks and little-known WordPress secrets.
Stay fast. Stay curious. Stay Levamo.
---
## Astra WordPress Theme Review: Is It Still A Great Choice in 2025?
- URL: https://levamo.com/blog/astra-wordpress-theme-review/
- Category: wordpress
- Author: Sunyyan Junaid
- Published: 2025-04-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Astra theme reviewed! Is it still the best WordPress theme for you in 2025?
If you're deep in the WordPress game, chances are you've bumped into Astra. Whether you're launching a portfolio, spinning up a WooCommerce store, or just trying to get your blog out of Google Docs and onto the internet, Astra has probably popped up on your radar. And with good reason. It's fast, flexible, and more popular than a TikTok dance trend in 2020.
This isn’t your usual "yet another WordPress theme." Astra has over a million active installs, and it didn't get there by accident. The team at Brainstorm Force built this thing with performance and usability in mind.
But popularity doesn’t always mean quality, right? So, in this Astra WordPress theme review, let's unpack Astra for what it really is: the good, the great, and the parts that could make you want to pull your hair out.
## Quick Overview: Astra WordPress Theme
- **Active Installations:** Over 1 million active users
- **Theme Rating (WordPress.org):** 4.9/5 stars based on thousands of reviews
**Pricing:**
- Free version available with generous features
- Pro version starts at $59/year or $227 lifetime
- **Lightweight Codebase:** Less than 50 KB
- **WooCommerce Compatibility:** Full integration with advanced e-commerce features in Astra Pro
- **Customization:** High level of control in both free and Pro versions
- **Page Builder Compatibility:** Works with Elementor, Beaver Builder, Gutenberg, and Brizy
- **Starter Templates:** Dozens of professionally designed templates for different industries
- **SEO & Performance:** Built-in schema markup, lightning-fast load times, and optimized for Core Web Vitals.
## First Impressions: What Makes the Astra Theme So Popular?
Let’s talk numbers. [Astra](https://wpastra.com/) hit one million active installs in record time. Compare that with themes like OceanWP or GeneratePress, and you see a gap that's not just wide, it's a canyon.
According to William Patton from the WordPress Themes Team, "*there's a huge gap between Astra and all others*." That kind of dominance doesn’t happen by chance.
What Astra does well is blend speed with serious design flexibility. It caters to beginners who want pre-built templates and pros who want full control. That rare sweet spot is where Astra lives. So, whether you’re a developer building client sites or a solopreneur with zero coding chops, Astra has a setup that fits. Let's get to our next consideration in this Astra theme review: performance.
## Astra Theme Performance: The Secret Weapon
A lot of themes promise speed, but Astra delivers it. Out of the box, the base theme clocks in at under 50 KB. That’s leaner than your favorite CSS-only hamburger menu. Astra doesn’t rely on heavy frameworks or third-party libraries that bog down your load times. Everything is built to run fast, clean, and efficiently.
Of course, a lot depends on your choice of hosting. [Levamo](/pricing) is the fastest hosting for Astra WordPress theme, and helps unlock the full extent of what's possible with the theme. It's built for high-performing and high traffic websites, so if you have a mission critical business, you should [check it out](/).
But let's get back to the theme.
The team at Brainstorm Force keeps things simple where it counts. Astra uses the native WordPress customizer to avoid unnecessary scripts. You won’t find bloated page builders or extra fluff baked into the core. And because it minimizes HTTP requests, your server has less work to do every time someone visits your site.
For high-traffic sites, that matters. Big time. If you're hosting with Levamo, where performance is already dialed in, pairing that with Astra can slash your page load times by up to 60% compared to some of the heavier themes on the market.
## Customization: Built for Tinkerers and Control Freaks
If you’re the type who likes things "just so," Astra is your playground. The free version gives you more layout and color control than most themes ever will. You can tweak headers, footers, blog layouts, and global typography without touching a line of code.
Still not enough? Astra Pro is where things get spicy. With the Pro Add-On, you unlock:
- Sticky headers
- Mega menus
- Custom layouts for individual pages or categories
- White-label branding (for agencies)
- Scroll to top links, advanced hooks, and more
Everything is modular. That means you only turn on the features you need. No extra baggage. This keeps your site light, fast, and focused.
## Starter Templates: A Designer's Shortcut (No Shame in That)

Let’s be real. Not everyone has time to design from scratch. Astra’s starter templates are a massive time-saver. You get dozens of pre-designed sites tailored for different niches: photography, fitness, fashion, tech, online shops, and more.
These aren’t clunky one-size-fits-all templates either. They’re actually built to look good and perform well. Load one in, swap out some content, and you’re on your way. Perfect for freelance clients with zero patience.
And yes, they work with popular page builders like Elementor, Beaver Builder, Brizy, and even Gutenberg. So, if you’ve already got a favorite, Astra plays nice.
## SEO and Technical Foundation
Google loves [speed](/blog/fastest-wordpress-hosting/), clean code, and schema markup. Astra checks all three boxes. The theme is built with SEO in mind and includes Schema.org integration by default. That means better visibility in search results and a stronger technical base right out of the gate.
While other themes can load slowly and mess with your [Core Web Vitals](/blog/core-web-vitals-and-seo/), Astra does the opposite. It puts your content in front of users (and search engines) fast. And if you’re chasing those rich results or trying to improve click-through rates, this stuff matters more than you think.
## WooCommerce Support: Built for Online Stores
Astra doesn’t just tolerate WooCommerce. It embraces it. The WooCommerce integration is one of the cleanest we’ve seen in a theme this light. You get full control over product layouts, grid spacing, color schemes, and even mobile responsiveness.
With Astra Pro, you unlock advanced features like:
- Off-canvas filters
- Quick view popups
- Product gallery styles
- Sticky add-to-cart buttons
If you're running an e-commerce store on Levamo, where uptime and speed are critical, Astra is a solid match. Your shop stays fast, clean, and conversion-friendly.
## User Experience: Is It Easy to Use?
Mostly, yes. But it depends on your comfort level with WordPress. Astra's customizer-based design makes it approachable, but the sheer number of options can feel overwhelming for beginners.
The layout is clean and logical, but expect to spend a little time exploring. Fortunately, there are plenty of video tutorials, documentation, and an active community. And if you go Pro, their support team is responsive and knowledgeable.
For seasoned users, the experience is almost frictionless. You get powerful tools without the bloat that usually comes with "feature-rich" themes.
## Pricing: Free vs Pro
The free version of Astra is surprisingly generous. It’s more than enough for blogs, portfolios, or simple business sites.
But if you're serious about customization, brand control, or client work, the Pro version is worth the upgrade. Here’s what you get with Astra Pro:
- Custom layouts
- Advanced header/footer options
- Enhanced blog controls
- WooCommerce add-ons
- Sticky/fixed elements
- White label
[Pricing starts at $59 per year](https://wpastra.com/pricing/) (screenshot above shows the annual pricing). For agencies or developers, there’s a lifetime license that pays for itself after a couple of projects. Compared to some themes that charge more and give you less, Astra Pro is a smart investment.
## What Could Be Better?
No product is perfect. Astra can be a bit overwhelming when you're just starting. The options are deep, and there isn’t always a clear "start here" path. The starter templates help, but some onboarding guidance wouldn’t hurt.
Also, while the free version is powerful, you’ll hit a ceiling if you want full control. That’s by design, of course, but it's still worth noting.
Finally, because Astra works with so many page builders, performance can vary depending on what you stack on top. Pair it with a bloated builder, and you lose the speed advantage. So choose wisely.
## Pros & Cons of Astra Theme:
| **Pros** | **Cons** |
|---|---|
| Extremely lightweight (under 50 KB) | Can be overwhelming for beginners due to many options |
| Fast loading and performance-optimized | Free version has feature limits |
| Deep customization without code | Some advanced features only available in Astra Pro |
| Modular architecture - activate only what you need | Template design quality can vary depending on the industry |
| Excellent WooCommerce support | Performance can drop if paired with bloated page builders |
| Works with multiple page builders (Elementor, etc.) | Initial learning curve for full feature mastery |
| Rich library of starter templates | |
| SEO-friendly with built-in schema markup | |
| Flexible for all site types (blogs, shops, portfolios) | |
| Affordable Pro pricing and lifetime deal available | |
## Who Should Use Astra?
Here’s the short list of folks who will love Astra:
- **Freelancers & Agencies**: Fast setup, white label options, and client-ready templates.
- **E-commerce Entrepreneurs**: Tight WooCommerce integration and conversion-friendly layouts.
- **Bloggers**: Clean design, strong SEO foundation, and control over how content looks.
- **Developers**: Lightweight, modular codebase and full design flexibility.
If you're hosting your site with Levamo, Astra is a natural fit. You get the performance benefits of our premium infrastructure paired with one of the fastest themes out there.
## Installing Astra on WordPress:
Now let’s show you a quick guide on how to install the Astra theme on WordPress using the Levamo hosting platform.
- First, log in to your **Levamo** dashboard and click on the WP Admin button. You will now gain access to the WP admin dashboard.
Now, from the sidebar, navigate to **Appearance > Themes.**
- Now click on **Add New Theme**.
- The next step is to find the Astra theme. Simply search for the name “Astra”. Once it appears, click **Install** and then **Activate**.
- If you don’t want to design the whole website from scratch, you can just use one of their many starter templates, just like we’ll do now. And we will do that by clicking on the **Let’s Get Started with Starter Templates** button.
- Once you activate the starter templates extension, you can choose their AI Web Builder or the Classic Starter Templates. Let’s just go with the Classic for now.
- Now Astra supports Block Editor and Elementor for customization. So next up, you’ll have to decide which one you prefer. We prefer the Block Editor.
- Now comes the bigger decision: Which starter template would you like to pick? They have a lot of shiny starter templates; just pick the one you like, then click **Continue**.
- Fill in the relevant details and click on **Submit & Build My Website. Again, you’ll have to exercise some patience as it will take some time to build your website**. Once built, you can click on **View Your Website** to check how it looks.

And voila! You have your website ready! Customize the content and design as you want before pushing that live button.
## Final Verdict of Our Astra WordPress Theme Review:
So, is Astra one of the best WordPress themes? Yes, after our detailed Astra WordPress Theme Review, we can definitely say that it is one of the few WordPress themes that lives up to the hype. It's fast, flexible, and powerful enough for professionals without being impossible for beginners to figure out. It doesn’t try to be everything to everyone, but it hits the sweet spot for most use cases.
Pair it with [Levamo hosting](/), and you’ve got a setup that looks great, loads fast, and scales when your traffic does.
So, if you're looking for a theme that won’t slow you down, gives you full control, and plays nice with the tools you already love, Astra is worth a test drive.
Just be warned: once you go Astra, most other themes will feel like a downgrade.
---
## WordPress 6.8 “Cecil” Is Now Available & It's Got Some Jazz
- URL: https://levamo.com/blog/wordpress-6-8-cecil-now-available/
- Category: wordpress
- Author: Sunyyan Junaid
- Published: 2025-04-16
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WordPress 6.8 "Cecil" offers performance boosts & new Style Book features.
WordPress 6.8 is here, and it’s got rhythm. Nicknamed “Cecil” after the jazz legend Cecil Taylor, this release isn’t just a tribute to boundary-pushing creativity. It’s a real upgrade for anyone building, maintaining, or just obsessing over their WordPress site.
At [Levamo](/), we’re always tuned in to what’s happening under the hood of the world’s favorite CMS. This release? It plays a smooth tune for performance, security, accessibility, and developer freedom. And that’s music to our ears.
Let’s dig into what makes 6.8 sing.

### The Style Book Got a Glow-Up
You know that moment when you open a design tool and everything finally makes sense? That’s the new Style Book.
Instead of fumbling around with styles and guessing how things will look, the Style Book now lays it out clearly: typography, buttons, images, and even the random stuff you usually forget about. You get more control and less guessing, and it even plays nicely with some Classic Themes now. Shout-out to the folks still rocking those.
For example, the preview dropdown now has a new `Show template` toggle added to quickly switch between content and template mode.
Show template toggle added to Preview dropdown
### Accelerated Navigation via Speculative Loading
This one’s cool. WordPress 6.8 introduces speculative loading. That’s not a philosophical concept, it’s actual performance magic. When someone hovers over a link, WordPress starts loading that page before they click. So when they do click? Boom, it’s already there.
It’s the kind of speed boost your site visitors won’t notice because everything will already feel instant.
We'll test this throughly and get back with how it performs in real day-to-day browsing.
### Performance Optimizations
Beyond speculative loading, WordPress 6.8 delivers performance improvements targeting the block editor, block type registration, and query caching. The introduction of the Interactivity API aims to ensure that interactions occur within 50 milliseconds, contributing to a more responsive interface.
**Want Real WordPress Performance Enhancements?**
Try [Hyperspeed Managed Hosting for WordPress](/managed-wordpress-hosting/) for Free!
### Fortified Security with bcrypt Password Hashing
Let’s talk security. WordPress 6.8 now hashes passwords with bcrypt. Translation: It’s a lot harder for anyone shady to brute-force their way into your site. And the best part? You don’t have to do anything. Just update, and your site quietly gets safer.
This is the kind of security we love at [Levamo](/managed-security/). We’re big on doing the heavy lifting so you can sleep better.
### Accessibility Gets the Attention It Deserves
This release includes over 100 accessibility improvements across the WordPress experience. The block editor alone got 70+ fixes. Better labeling, improved navigation, more keyboard support - the kind of things that make a huge difference for people using assistive tech, and honestly, for all of us.
We believe a fast, secure site should *also* be usable by everyone. That’s not extra credit, that’s table stakes.
### Developer-Centric Enhancements
WordPress 6.8 packs a bunch of under-the-hood improvements for developers. Think better shortcode processing, smarter post type handling, enhanced APIs for scheduling, and new hooks that give you more control without doing somersaults in your functions file.
This update is less about shiny new features and more about sharpening the tools you already use. It’s like someone finally cleaned your workshop and handed you a better wrench.
### Should You Update to WordPress 6.8 "Cecil"?
WordPress 6.8 isn’t trying to reinvent the wheel. It’s tightening the bolts, tuning the engine, and making sure every piece works better with the next. And honestly? That’s the kind of energy we like around here. A faster, more accessible, secure, and developer-friendly WordPress is exactly the kind of foundation we want to build on.
So yes, you should definitely upgrade.
So if you're running your site on [Levamo](/) (and if you're not, hey, we should talk), you're already in the best spot to take advantage of everything 6.8 brings.
Update, explore, and let your site jam.
### Meet the Crew Behind WordPress 6.8
Every WordPress release has a squad of behind-the-scenes heroes making the magic happen. These folks wrangle feedback, squash bugs, review code, design features, and basically steer the whole ship from start to finish. WordPress 6.8 “Cecil” is no exception.
Here’s who led the charge:
- **Matt Mullenweg** - Steering the ship as Release Lead
- **Jeffrey Paul & Michelle Frechette** - Keeping everything coordinated and on course
- **Joe McGill, Jonathan Desrosiers & George Mamadashvili** - The technical leads making it all tick
- **Jb Audras** - Triage Lead, aka the person sorting the chaos into action
- **Tammie Lister** - Polishing the design
- **Felix Arntz** - Making sure everything runs fast and smooth as Performance Lead
- **Krupa Nanda** - Test Lead, ensuring nothing breaks while the rest of us sleep easily
For a detailed overview and to download the latest version, visit the official [WordPress 6.8 “Cecil” announcement](https://wordpress.org/news/2025/04/cecil/).
---
## WordPress vs Wix: Which Platform is the Best in 2025?
- URL: https://levamo.com/blog/wordpress-vs-wix/
- Category: website-development
- Author: Sunyyan Junaid
- Published: 2025-04-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Wix vs WordPress: Find the perfect platform for your website in 2025.
Building a website used to mean late nights, questionable code, and a steady diet of coffee and panic. These days, you’ve got tools like WordPress and Wix that make launching your digital home much less painful. But picking the right one still isn’t a decision to make over your third cup of cold brew.
Whether you’re a scrappy startup, an established agency, a passionate blogger, or someone who just really needs a portfolio that doesn’t scream 2009, the WordPress vs Wix debate is one worth having.
So, is Wix or WordPress better? Let’s dig in.
## Quick Intro: What Are WordPress and Wix?

WordPress is the most popular content management system (CMS) on the planet, powering over 43% of all websites as of 2025. That’s more than 520 million sites. It comes in two flavors:
- **WordPress.org**: Self-hosted and open source. Ultimate flexibility, but you’re the one holding the toolbox. And this is the one we’re comparing in this article.
- **WordPress.com**: A hosted platform with less flexibility unless you upgrade to the higher-tier plans.
Wix, by comparison, has over 260 million registered users and holds around 3% of the global CMS market. It’s a cloud-based website builder that gives you everything, like hosting, templates, and editing tools, in one clean dashboard. You don’t need to know a lick of code. It’s like setting up shop in a digital shopping mall: fast, polished, and plug-and-play.
## Comparison Table: Wix vs WordPress at a Glance
| **Feature** | **Wix** | **WordPress** |
|---|---|---|
| Ease of Use | Drag-and-drop simplicity | Requires setup and learning |
| Design | 900+ templates (fixed after selection) | Thousands of themes, flexible layout |
| SEO | Beginner-friendly tools | Full control, advanced plugins |
| Blogging | Basic blog engine | Industry-standard blogging tools |
| Performance | Optimized by Wix | Depends on host ([Levamo = fast](/managed-wordpress-hosting/)) |
| E-Commerce | Built-in (50k product limit) | WooCommerce (scales indefinitely) |
| Apps/Plugins | 500+ apps | 70,000+ plugins |
| Cost | $17–$159/month | Variable: can be cheaper or more customizable |
| Ownership | Limited export options | Full ownership and portability |
| Maintenance | All managed by Wix | You or your host maintain it |
## 1. WordPress vs Wix: Ease of Use
Wix is the poster child for ease-of-use. Its editor is true WYSIWYG (what-you-see-is-what-you-get). Want to move a photo? Drag it. Want to change the text? Just click and type. It even offers an AI-powered tool called Wix ADI, which builds you a starter site based on a few questions. Think of it as a BuzzFeed quiz that results in a functioning homepage.
WordPress, on the other hand, has a steeper learning curve. While the Gutenberg block editor has made the interface more intuitive, managing plugins, themes, and settings still takes some digging. Beginners often install a page builder like [Elementor review](/blog/elementor-review/) to get that Wix-style drag-and-drop experience.
**Wix:**
- Drag-and-drop builder that anyone can use
- An AI-powered design assistant (Wix ADI) builds your site for you
- Easy to edit visually, without code
**WordPress:**
- Requires setup: hosting, themes, plugins
- The block editor is more structured than drag-and-drop
- Becomes easier with plugins like Elementor
Reddit user: "*Wix let me build my portfolio in a weekend. WordPress would’ve taken me a course and a prayer.*"
**Verdict:** Wix wins for beginners. It’s faster, easier, and doesn’t overwhelm you with options upfront. WordPress gets easier with time, but starts out a bit tech-heavy.
## 2. WordPress vs **Wix**: Design Freedom
Wix gives you over 900 designer-made templates across industries. They look good right out of the box, and you can customize fonts, colors, spacing, and animations. But - and this is important - once you pick a template, you can’t change it later without rebuilding your site.
WordPress has thousands of themes, both free and premium. You can switch themes anytime and keep your content intact (though you may need to tweak layouts). Developers can also build custom themes or child themes from scratch. Page builders like Divi and Beaver Builder give you visual control similar to Wix but with more depth.
**Wix:**
- 900+ templates
- Fully editable layout and styling
- Templates can’t be switched after launch
**WordPress:**
- Thousands of themes (including block themes and premium designs)
- You can switch themes and keep your content
- Full code access or use of advanced page builders
**Verdict:** WordPress takes the win here. You can do more, change more, and fine-tune everything down to the pixel.
## 3. Wix SEO vs WordPress SEO

Wix has made huge strides in SEO. You can edit meta tags, customize URLs, set image alt text, and generate XML sitemaps automatically. Wix also supports structured data and integrates easily with Google Search Console. The SEO Wiz tool even walks beginners through setup.
But for serious SEO power, WordPress still reigns. Plugins like Rank Math and Yoast SEO offer keyword suggestions, snippet previews, 404 monitoring, schema markup, and integration with Google Analytics and Bing Webmaster Tools. You can also customize your robots.txt file, canonical URLs, and permalink structures, features SEO pros love.
In a Reddit thread from r/SEO, one commenter put it bluntly: "If SEO is your main traffic driver, don’t even think twice - Go WordPress."
**Wix:**
- Built-in SEO tools with helpful tips
- Auto-generated XML sitemaps
- Structured data and Google integrations
**WordPress:**
- Deep SEO plugin ecosystem: Rank Math, Yoast, SEOPress
- Control over URL structure, meta data, and indexing
- Schema Markup, breadcrumbs, and multilingual SEO options
In a Reddit thread from r/SEO, one commenter put it bluntly: "*If SEO is your main traffic driver, don’t even think twice - Go WordPress.*"
**Verdict:** WordPress is the better choice for long-term SEO. It offers more control and plugin support for serious growth.
## 4. Wix Blog vs WordPress Blog
Wix includes a blogging module, but it’s fairly basic. You can schedule posts, add categories, and manage images, but layout customization is limited. It works for occasional updates or announcements.
WordPress, on the other hand, is a blogging machine. It was built for content publishing and it shows. You can manage complex taxonomies, schedule content in advance, add authors with different roles, and build editorial workflows. There are also plugins for related posts, reading time estimates, and advanced commenting systems.
**Wix:**
- Clean and simple blog layout
- Works fine for occasional updates
- Limited formatting and design options
**WordPress:**
- Originally built for blogging. It’s what it does best
- Categories, tags, RSS feeds, user roles, editorial plugins
- Plugins for related posts, reading time, and more
Redditor on r/ProBlogger: "*I moved my blog from Wix to WordPress after six months. It couldn’t keep up.*"
**Verdict:** WordPress is the gold standard for bloggers. If content is a key part of your brand, it’s the clear winner.
## 5. WordPress vs Wix Performance: Which is Faster?

Wix handles hosting and performance behind the scenes. It compresses images, caches pages, and uses a CDN to deliver content quickly. For most small business sites, Wix will load fast without you lifting a finger.
WordPress is more dependent on your hosting environment. A cheap shared host can turn your site into molasses. But with a [Hyperspeed cloud host](/managed-wordpress-hosting/) and the right configuration, caching plugins, a CDN, image optimization, lazy loading, WordPress can load lightning fast.
**Wix:**
- CDN is included by default
- Automatic image compression
- Performance optimized behind the scenes
**WordPress:**
- [Hosting](/managed-wordpress-hosting/) makes all the difference
- With the right stack, it can be extremely fast
- Plugins like WP Rocket or LiteSpeed Cache improve speed
**Verdict:** WordPress on a good host (like Levamo) is faster and more tunable. Wix is fast by default, but you can’t tweak it much.
## 6. WordPress vs Wix E-Commerce: Which Is Better for Selling Online?
Wix has eCommerce built-in. Their Business and eCommerce plans let you sell products, accept payments, manage inventory, and offer coupons. You can even enable abandoned cart recovery on higher tiers. That said, Wix caps your product catalog at 50,000 items.
WordPress uses WooCommerce, a plugin that powers over 36% of all online stores. It supports unlimited products, product variations, subscriptions, advanced shipping rules, and integrations with just about every payment gateway you can think of. You can also extend it with hundreds of [WooCommerce add-on plugins](/blog/best-plugins-for-woocommerce/).
If you’re selling handmade candles from your garage, Wix will do just fine. If you’re building the next big lifestyle brand, WooCommerce gives you room to grow.
**Wix:**
- Easy to set up for small stores
- Built-in payment and inventory tools
- Max of 50,000 products
**WordPress:**
- WooCommerce supports unlimited products
- Scales with extensions for shipping, subscriptions, memberships
- Integrates with virtually every payment gateway
**Verdict:** WordPress + WooCommerce wins for serious stores. Wix is fine for smaller catalogs but is not built for heavy commerce.
## 7. WordPress vs Wix: App & Plugin Ecosystem
Wix has an App Market with over 500 apps. These cover everything from forms and chats to bookings, reviews, and email marketing. They’re vetted by Wix, which means fewer compatibility issues but also fewer niche tools.
WordPress has a plugin directory with over 70,000 options. Need an LMS? Forum? Multilingual support? There’s a plugin for that. The ecosystem is vast and sometimes overwhelming. Some plugins don’t play well together. Others are abandoned. But the sheer choice is unmatched.
**Wix:**
- 500+ apps in the Wix App Market
- All apps are pre-approved and stable
**WordPress:**
- Over 70,000 plugins
- Infinite variety, but sometimes buggy or outdated
A developer on r/WordpressDev shared: "*Wix is a toolbox. WordPress is Home Depot. You just have to know what aisle to look in.*"
**Verdict:** WordPress wins in breadth. Wix wins in simplicity. Choose based on how much you want to build or discover.
## 8. Cost Comparison: What’s the Real Price?

Wix pricing is straightforward. Plans range from free (with Wix ads and subdomain) to $35/month for VIP or $159/month for Business Elite. That includes hosting, SSL, templates, and support.
WordPress is technically free, but you’ll need to pay for hosting ($5 - $30/month), a domain (~$10/year), and possibly a premium theme ($50 - $100). Many plugins are free, but premium tools like Rank Math Pro or WP Rocket may add $50 - $100/year.
Over time, WordPress can be cheaper or more expensive, depending on your needs. One Redditor summed it up perfectly: "Wix is like renting a fully furnished apartment. WordPress is building your own house."
**Wix:**
- Plans from $17 to $159/month
- Includes hosting, SSL, and domain (first year)
**WordPress:**
- Free software, but hosting + plugins + themes add up
- You control what you spend and where
**Verdict:** Wix gives you predictability. WordPress gives you flexibility.
## 9. Ownership and Portability
Wix hosts your site, and you can’t export it wholesale. You can download content (blog posts, for example), but if you leave, you’ll have to rebuild.
WordPress gives you full access to your files and database. You can migrate to any host, back up your site, or export it with a few clicks.
Control freaks and long-term planners love WordPress for this reason.
**Wix:**
- Can’t export full site
- Rebuilding is needed if migrating elsewhere
**WordPress:**
- You own your files, database, and code
- Easy to move between hosts
**Verdict:** WordPress hands you the keys. Wix keeps you in their walled garden.
## 10. Security & Maintenance
Wix takes care of all updates, security patches, and backups. If something breaks, Wix fixes it. If you forget to update, there’s nothing to worry about. It’s truly hands-off.
When it comes to [WordPress security](/blog/wordpress-best-security-practices/), more responsibility is on you. Core updates are automatic now, but plugin updates, backups, and malware protection are your (or your host’s) job. Most savvy site owners use plugins like Wordfence, Jetpack, or iThemes Security to lock things down.
As one agency put it: "WordPress is secure if you treat it right."
**Wix:**
- Security handled by Wix
- No maintenance required from users
**WordPress:**
- You manage updates, backups, and plugin security
- Tools like Wordfence and Jetpack help
**Verdict:** Wix is maintenance-free. WordPress requires attention - or a good host that handles it for you (hint: Levamo).
## WordPress on Levamo: Built for Speed and Peace of Mind

Let’s be honest. WordPress can be a rocket or a rusty tricycle, and it all depends on the hosting. At [Levamo,](/) we’ve optimized every layer to make sure your [WordPress site performs](/managed-wordpress-hosting/) like a finely tuned machine.
Here’s what you get with WordPress on Levamo:
- Blazing-fast load times with modern caching and [free WordPress CDN](/cloudflare-cdn/) delivery
- Staging environments that let you test before going live
- Security that just works: Malware scans, automatic updates, and DDoS protection
- Real support from people who actually use WordPress
Whether you’re launching a blog or running a 1,000-product store, Levamo gives you power, flexibility, and peace of mind. We don’t just host WordPress - we supercharge it.
## Final Thoughts: Which One Should You Choose?
If you want plug-and-play simplicity with minimal headaches, Wix might be your dream date. It’s great for small sites, freelancers, and business owners who want to launch fast and focus on their work, not their tech stack.
But if you value flexibility, long-term scalability, and total control, WordPress (especially hosted on Levamo) is your best bet. It’s the platform for builders, bloggers, and businesses that want to do more than just exist online and want to grow.
And hey, no shame in testing both. Just don’t forget to register your domain. Trust us - we’ve seen things.
**Thinking of WordPress? Let Levamo help you do it right.** Faster sites. Smarter hosting. Real support. Try it today and feel the difference.
[Explore Levamo WordPress Hosting](/pricing/)
---
## Top SaaS Affiliate Programs to Boost Your Passive Income
- URL: https://levamo.com/blog/saas-affiliate-programs/
- Category: digital-marketing
- Author: Faisal Sarker
- Published: 2025-04-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find the best SaaS affiliate programs and boost your passive income.
It is definitely satisfying to see money coming into your account because you simply shared good thoughts about an online tool you actually believe in. With the right SaaS affiliate programs, that thrilling moment can become a regular occurrence.
[SaaS solutions](https://saaspirate.com/) often solve many everyday problems faced by businesses and individuals. Therefore, they are often very appealing to recommend. What makes it even more encouraging is that these products have a recurring pricing model, so for most of these products, affiliates get ongoing commissions every time a subscription renews. That means you're not just taking a lump sum payout, but you're building a regular income stream.
If that sounds interesting to you, then you are going to have a productive time reading this article because, in the following section, we'll discuss some of the best SaaS affiliate programs to grow your passive income.
Let's get started, explore your options & set the stage for a sustainable source of earning!
## 1. Canva

Canva allows anyone and everyone to create eye-catching graphics and visuals without professional design experience. Users can create social media posts, presentations, or invitations with Canva's drag-and-drop interface and tons of templates, it's all child's play. No wonder it is a household name among content creators worldwide.
It’s a suitable referral to literally everyone, no matter if your target audience is hobby bloggers or even design professionals.
- **Commission**: 30% recurring commission.
- **Cookie Duration**: 30 days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, automated payout, and real-time tracking.
## 2. HubSpot

HubSpot supports marketing, sales, and customer service teams. You might know them from your free CRM, but the real magic happens when someone upgrades to their Marketing, Sales, or Service Hubs for automation, lead nurturing, and pipeline management. HubSpot is arguably the most popular brand name in the B2B world.
HubSpot is the go-to tool for anyone looking for more conversions in their online business, and it is a great recommendation for all niches.
- **Commission**: 30% recurring commission.
- **Cookie Duration**: 180 days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, automated payout, and real-time tracking.
## 3. Levamo

Levamo is a SaaS web hosting service provider for dynamic WordPress sites. It’s tested as the fastest managed hosting for WordPress sites at the moment. Powered by hyperfast LiteSpeed server infrastructure, intelligent caching, [free WordPress CDN](/cloudflare-cdn/), and resource-scaling, it makes sure the customer’s website stays up, even during peak traffic. It has a 4.9 star rating on G2, which speaks to its popularity.
It can be a great recommendation for your audience if they are running dynamic WordPress sites like eCommerce, LMS, and online communities, as the hosting is optimized and tested to handle such websites.
- **Commission**: Tiered commission from $50 to $500 per sale, depending on the sales figure. Plus 10% recurring commission for life. For example, 5 referrals of the Startup 1 plan will earn you a $500 one-time commission + $714 commission per year.
- **Cookie Duration**: 60 Days
- **Features (Affiliate Program)**: They use the FirstPromoter, customizable affiliate portals, real-time analytics, easy asset access, and automated payouts.
[Join Levamo Affiliate Program](/web-hosting-affiliate-program/)
## 4. Semrush

Your audience probably knows about Semrush (or uses it daily) if you produce content for a niche that is even remotely close to digital marketing. SEO, competitor analysis, content research, and PPC. Marketers use it for everything from discovering hot keywords to checking backlinks, tracking rankings, and doing site audits.
Since Semrush is an essential tool in many digital marketers' arsenals, promoting Semrush can often drive high conversion rates.
- **Commission**: Up to $350 per sale. Tiered commission rate per sale, which increases the more you refer.
- **Cookie Duration**: 120 Days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, and real-time tracking.
## 5. Shopify

Shopify is a highly popular SaaS platform that lets entrepreneurs build and manage online stores relatively easily. From tiny side hustles to large retail operations, Shopify can support everything in between. It has beautiful templates, an enormous app store, and integrations with payment and fulfillment partners to make life easy for e-commerce owners.
Shopify has a popular SaaS affiliate program, and it can be one of the most profitable ventures as an affiliate marketer.
- **Commission**: Up to $150 per sale. Commission based on the referred customer’s location.
- **Cookie Duration**: 30 Days
- **Features (Affiliate Program)**: Intuitive dashboard with features like easy creation of affiliate links, commission tracking, and a range of marketing assets.
## 6. Omnisend

Omnisend is a digital marketing sidekick that powers e-commerce marketing automation via email and SMS for online retailers. It offers advanced segmentation and automated workflows for those who don't want to get bogged down in complicated setup processes. The straightforward omnichannel communication approach of Omnisend helps store owners recover abandoned carts, nurture leads & maintain customer relationships across all channels.
It’s a great recommendation if your audience consists of digital marketers or business owners.
- **Commission**: 20%, Recurring
- **Cookie Duration**: 60 Days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, and real-time tracking.
## 7. FreshBooks

FreshBooks is a back pocket accountant that is perfect for freelancers and small business owners who hate invoicing, expense tracking & financial reporting. It is a cloud accounting software that non-accountants can understand. It also integrates with payment gateways and provides automated reminders and time tracking.
Anyone who bills clients regularly or needs a simple expense management tool can easily use FreshBooks without any proper accounting knowledge, expanding your target audience as an affiliate marketer.
- **Commission**: Up to $150 per sale. Tiered commission rate per sale, which increases the more you refer.
- **Cookie Duration**: 120 Days
- **Features (Affiliate Program)**: They use the ShareASale platform, which offers a user-friendly dashboard and tools for tracking performance and earnings and creating affiliate links.
## 8. BigCommerce

Bigcommerce is an all-in-one eCommerce platform, just like Shopify. It comes with strong SEO features and is scalable enough to handle small stores as well as enterprise volumes. It's a great choice for business owners who want more customization options and unrestricted support.
Whether you’re creating content or promoting eCommerce businesses to an audience who is new to it or looking to switch from another platform, BigCommerce would be perfect for both. Plus, it has one of the highest-paying saas affiliate programs, making it even more lucrative.
- **Commission**: 200% of the customer’s first monthly payment or $1,500 per enterprise customer.
- **Cookie Duration**: 90 Days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, and real-time tracking.
## 9. Unbounce

Unbounce helps users create landing pages that convert. Marketers love it because there is no need to hire a web developer. Users can just pick a template, drag elements together, and have a landing page optimized for conversions. From small businesses launching a new product to seasoned marketers running complex campaigns, Unbounce makes capturing leads, running A/B tests, and tweaking every element easy.
If your audience is running online businesses and looking for sales funnel optimization, Unbounce is a perfect recommendation for them.
- **Commission**: Tiered commission rate of 25%-35%, recurring for up to 12 months after the sale.
- **Cookie Duration**: 90 Days
- **Features (Affiliate Program)**: They use the PartnerStack platform, offering automated payments, easy affiliate URL generation, and real-time tracking.
## 10. EngageBay

EngageBay is a complete growth suite for small and medium-sized businesses. It offers email marketing, CRM, live chat, lead scoring & marketing automation, and many more features. It's priced competitively with heavyweight CRMs, so it appeals to startups and low-cost businesses that need robust features without a sky-high monthly bill.
Overall, it can be a great recommendation if your audience is running or planning to run any kind of [online business](/blog/best-online-business-ideas/).
- **Commission**: 30%, Recurring
- **Cookie Duration**: 30 Days
- **Features (Affiliate Program)**: Custom affiliate dashboard, performance tracking, and access to marketing assets.
## 11. SocialBee

SocialBee helps users schedule and organize social media content like a pro. This is ideal for small businesses, agencies & freelancers managing many social media profiles across multiple sites. SocialBee is different because users can group and recycle evergreen posts, so great content doesn't get lost in social media.
Whether your primary audience is digital marketers or small businesses looking to streamline their social presence, promoting SocialBee to your audience means you will speak to their pain points.
- **Commission**: 30%, Recurring
- **Cookie Duration**: 90 Days
- **Features (Affiliate Program)**: They use the PartnerStack platform, offering automated payments, easy affiliate URL generation, and real-time tracking.
## 12. Podia

Podia connects course creators, digital product sellers, and membership site entrepreneurs. It removes the need to manage multiple plugins or services, host videos, and manage checkouts. Podia fits creators who need a clean, powerful platform with very little tech complexity overhead.
If your audience is aspiring educators or people selling e-books, digital downloads, or membership access, Podia is worth recommending to them as an affiliate.
- **Commission**: 30%, Recurring
- **Cookie Duration**: 90 Days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, and real-time tracking.
## 13. Moosend

Moosend is an email marketing tool that is designed for businesses that want simplicity. Users can build email campaigns with drag-and-drop editors, segment audiences, automate workflows & track performance in real-time. It has competitive pricing & an easy-to-use interface that makes it a good fit for small to mid-sized organizations on a tight budget, but still offers robust functionality.
If your audience is digital marketers, online business owners, or content creators, Moosend is a great recommendation for them, while you also earn some passive income.
- **Commission**: Tiered commission rate of 25%-35%, Recurring.
- **Cookie Duration**: 90 Days
- **Features (Affiliate Program)**: They use the PartnerStack platform, offering automated payments, easy affiliate URL generation, and real-time tracking.
## 14. Coursera

Coursera offers thousands of courses, certificates, and even degree programs through partnerships with top universities and companies. It’s a powerful platform that has coding courses from Google, business strategy coaching from Yale, data science classes from IBM, and so on.
It is easy to recommend to people looking to upgrade skills or change careers because of its worldwide reputation for quality.
No matter if your audience is online professionals chasing the latest credential or students learning about new subjects, there's a program for everyone at Coursera.
- **Commission**: Tiered commission rate of 25%-35%.
- **Cookie Duration**: 30 Days.
- **Features (Affiliate Program)**: Easy tracking of the referrals, easy-to-integrate Impact tracking links, and access to marketing materials.
## 15. Sage

Sage provides software for payroll, accounting, HR, and more in addition to business management. Smaller businesses can also rely on Sage for compliance and robust reporting, thanks to its multi-tier pricing plan for small to large enterprises. So, from the local bakery managing finances to multinational companies tracking complex inventories, Sage has solutions for all.
If your audience is at different levels in their business journey, Sage may be your best bet, as it caters to online businesses of all levels.
- **Commission**: 7% Commission.
- **Cookie Duration**: 30 Days.
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, and real-time tracking.
## 16. Pipedrive

Sales teams like Pipedrive benefit from its intuitive and visually appealing pipeline management. This is ideal for small to midsize businesses that want to track leads, automate follow-ups, and forecast sales. Its interface is simple enough that anyone can get started, but flexible enough to handle more involved sales processes.
Whether your audience is sales reps, managers, or business owners looking for a simple, budget-friendly CRM, Pipedrive is a solid pick.
- **Commission**: 20% for the first 12 months.
- **Cookie Duration**: 90 Days
- **Features (Affiliate Program)**: They use the PartnerStack platform, offering automated payments, easy affiliate URL generation, and real-time tracking.
## 17. Sellfy

Sellfy powers digital creators, print-on-demand enthusiasts, and subscription businesses with a streamlined storefront solution. Whether someone is a graphic designer selling design templates or a YouTuber selling merch, Sellfy has got everyone covered with quick store creation, payment integrations, and marketing tools. The beauty of Sellfy is its simplicity, as anyone can have a store up and running faster than making a cup of coffee.
So if your audience is prospective or current small business owners, Sellfy is a great recommendation for them.
- **Commission**: Tiered commission rate of 25%-40%, Recurring.
- **Cookie Duration**: 90 Days.
- **Features (Affiliate Program)**: They use the PartnerStack platform, offering automated payments, easy affiliate URL generation, and real-time tracking.
## 18. Weebly

Weebly is a drag-and-drop website builder for small business owners or personal bloggers who don't want to code. E-commerce features have also been added to Weebly since it was acquired by Squarespace, allowing website owners to also sell products. It is the perfect product for newcomers to build a site because the learning curve is virtually nonexistent, and the free plan gives them a taste of the features before they upgrade.
It has a SaaS affiliate program with a great conversion rate, as the product basically sells itself because people can use its generous free plan and then decide to upgrade.
- **Commission**: 30% commission.
- **Cookie Duration**: 120 Days.
- **Features (Affiliate Program)**: They use the ShareASale platform, which offers a user-friendly dashboard and tools for tracking performance and earnings and creating affiliate links.
## 19. Wix

Wix is another drag-and-drop site builder that gives users thousands of design templates to customize almost everything about their site. With an extensive app market, Wix serves everyone from artists showcasing their portfolios to small restaurants taking online orders. It is very user-friendly and makes it easy to build simple sites, but advanced users can get deep into code to make custom sites.
Wix is a well-known brand, so even if you are producing content for small or even mid-level business owners, they have most probably already heard about it, increasing your chance of converting.
- **Commission**: 20%
- **Cookie Duration**: 30 Days
- **Features (Affiliate Program)**: They use the Impact Radius platform, easy affiliate URL generation, and real-time tracking.
## 20. ClickFunnels

ClickFunnels simplifies building sales funnels, landing pages, upsell sequences, membership sites, and automated follow-up emails, all in one place. Entrepreneurs and marketers use ClickFunnels to eliminate having to use several tools. It is especially popular with internet marketers who want lots of pre-built funnel templates and a large community support.
If your audience is digital marketers, consultants, or coaches, they would be glad to find this tool if they did not already.
- **Commission**: 30%, Recurring.
- **Cookie Duration**: 45 Days.
- **Features (Affiliate Program)**: They use a custom MyClickFunnels platform, which allows for performance tracking, link creation, payment history tracking, and more.
Also Read: [LMS hosting](/managed-lms-hosting/)
## Why Enroll for SaaS Affiliate Programs?
**Recurring Income:** SaaS providers usually charge fees monthly or annually, because of their subscription model. So most of them also pay monthly or yearly commissions. So long as your referred users stay active, you keep earning, even while you sleep or binge-watch your favorite TV show.
**High Customer Lifetime Value:** If you can refer to quality software just like the ones we shared here, they can stay for years. That means your referrals may pay off for longer.
**A stable and growing market for software solutions:** Remote work and digital transformation are not fading away anytime soon, so referring SaaS products is an easy choice when it comes to affiliate marketing.
**Diverse Opportunities:** SaaS solutions are now available in many niches, like design, e-commerce, SEO, accounting, CRM, payments, course creation, etc. So, no matter what your target audience is, you will surely find SaaS products related to your audience.
## Which Factors to Consider While Choosing SaaS Affiliate Programs to Promote?
**Cookie Duration:** A longer cookie window (90 or 120 days) gives you time to collect that commission, even if your leads do not buy immediately.
**Brand Reputation:** Popular companies usually convert faster because buyers know them already. Lesser-known brands may pay higher commissions but require more work to build credibility.
**Payout Threshold and Frequency:** Check out when and how the company pays out (monthly, bi-monthly). Look for one that fits your preferred cash flow.
**Support and Resources:** A good affiliate program with training materials, dedicated support, and professionally designed banners or landing pages can make your life easier and can increase conversions.
**Product Quality:** Promote the services that are good enough for you to personally use. You can gain more trust and increase future earning potential when your audience has a great experience using the product.
## Conclusion
If tapped in properly, SaaS affiliate marketing can be a goldmine. From Canva and Shopify to ClickFunnels, each SaaS affiliate program on our list solves specific problems that modern businesses and creators face. Referring a high-quality SaaS solution to your audience solves their problems and creates a steady, maybe recurring revenue stream for yourself.
It's not just about dumping random affiliate links everywhere. The key is authentic promotion, creating content that helps people and explains how a SaaS solution will simplify their lives. As you earn trust, your referrals and income will increase too.
Start by choosing the right SaaS affiliate programs for your niche, registering as an affiliate, and promoting their solutions to your readers, viewers, or followers. And who knows? Once you start getting enough commissions pouring in, you might just find yourself sipping that pina colada on a tropical beach while not even thinking about working actively.
## Frequently Asked Questions

### What is an affiliate program for SaaS?
SaaS affiliate programs connect software-as-a-service companies with affiliates who earn commissions for promoting their products. Typically, affiliates post unique links or codes that direct potential customers to the software and earn a commission when those leads convert.
### What are the highest-paying affiliate programs?
The highest-paying affiliate programs vary widely across industries. But oftentimes, it is the premium software, web hosting service, or financial products that pay the most. Such programs can pay commissions of up to thousands of dollars per successful referral.
### Can you make $100 a day with affiliate marketing?
You can certainly make USD 100 a day in affiliate marketing by promoting the right offers to the right people. However, results depend on your niche, traffic sources, and promotional efforts.
### What percentage do SaaS affiliates get?
SaaS affiliates usually receive up to 50% commission on every referred sale, subscription, or recurring payment. It varies by company pricing model, product value, and affiliate program structure.
### What is a typical SaaS commission?
Most SaaS commissions are between 20% and 30% of the subscription or recurring revenue. Some companies can offer higher or lower percentages, but this is a typical industry range.
---
## WordPress Launched an AI Website Builder... But There's a Catch
- URL: https://levamo.com/blog/wordpress-ai-website-builder/
- Category: news
- Author: Sunyyan Junaid
- Published: 2025-04-11
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
AI builds WordPress sites fast! But is it right for your business?
WordPress.com introduced a shiny new AI website builder. With a few prompts about your business type, some brand colors, and a little context, it can spin up a full website, complete with layout, copy, and visuals, in under five minutes.
For creators just getting started, it’s a compelling pitch: No dev work, no upfront cost, and no need to write a single line of content. Just describe your idea, and boom; you’ve got a working website.
According to WordPress.com, the AI website builder can make “beautiful, functional websites in minutes.”
Get your early access [here](https://wordpress.com/ai-website-builder/?ref=blog).
But here’s the part that actually matters: this WordPress website builder is just one way to *start* with WordPress. Not the only way. Not the best way for every use case. And certainly not the way you’d want to run a business that’s growing fast.
## So what’s the catch?
[WordPress's](https://wordpress.com/blog/2025/04/09/ai-website-builder/)[ ](https://wordpress.com/blog/2025/04/09/ai-website-builder/)[AI website builder](https://wordpress.com/blog/2025/04/09/ai-website-builder/) is available only for those hosting their website on WordPress.com, Automattic’s hosted version of WordPress (which starts at $18/month), and not on WordPress.org, which is open-source, flexible, and endlessly customizable. And WordPress.com has always had some tradeoffs. So, while you do get convenience and speed to launch, you lose control, and limitations box you in.

With this new AI website builder, WordPress.com is doubling down on simplicity. That’s not a bad thing, but it’s clear who it’s built for: side projects, solo creators, and non-tech founders who just need something up *today*.
And that’s okay. Every platform has its lane.
Also keep in mind that it’s not a free AI website builder.
### What the AI builder actually gives you:
- A quick, chatbot-style setup that personalizes your design
- Auto-generated copy and placeholder images
- Built-in WordPress.com hosting (starting at $18/month to go live)
- No support (yet) for ecommerce, integrations, or existing WP sites
It’s a smart move. It lowers the bar to entry, especially for folks who’ve been too intimidated to touch WordPress before. But for businesses who care about how fast their site loads, how easy it is to scale, and how SEO and security are handled, this is just the first layer of a proper stack.
## What we believe at Levamo
At [Levamo](/), we’re all in on WordPress, which is why we built a custom hosting solution that respects its potential.
And while an AI website builder on WordPress.com is a great way to go for starter websites, you need a proper solution to power high-performing sites that are growing fast that, no matter how you built them, still need to:
- [Load in under 2 seconds](/performance/), even during traffic spikes
- [Stay protected from bots](/managed-security/), brute force attacks, and plugin vulnerabilities
- Work with your favorite plugins, themes, and ecommerce tools
- Scale without bottlenecks or surprise limits
That’s where Levamo comes in. We give your WordPress websites sites room to grow, speed to win, and support that actually speaks your language.
## AI Website Builder Final Thoughts
The AI builder is a great addition to the WordPress ecosystem. It’s going to help more people get online faster, and that’s a win for all of us. But real businesses don’t just need a fast start. They need to run, scale, and thrive, and that takes hosting built for the long haul.
WordPress is the platform. Levamo is what makes it powerful.
Want to see how your WordPress site could perform with serious infrastructure behind it? [Let’s talk](/sales/). Or better yet, [try Levamo for yourself](/pricing/).
---
## The Ultimate ProfilePress Review: Best WordPress Membership Plugin?
- URL: https://levamo.com/blog/profilepress-review/
- Category: membership
- Author: Faisal Sarker
- Published: 2025-04-09
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is ProfilePress the best membership plugin? Find out in our detailed review.
Choosing the right membership plugin for your WordPress site can make or break your online community, subscription service, or content monetization strategy. With so many options available, it’s crucial to find a solution that not only offers the features you need but also integrates seamlessly with your workflow.
That’s where [ProfilePress](https://profilepress.com/) comes in. If you've been looking for a while, you might have come across ProfilePress, one of the best WordPress membership plugins. The subscription plugin is designed to help you build, manage, and grow membership-based websites with ease. Whether you’re looking to create paid memberships, protect premium content, or even manage WooCommerce subscriptions, ProfilePress packs a powerful punch.
In this review, we’ll explore why ProfilePress is worth considering, especially if you’re debating between it and popular alternatives like [MemberPress review](/blog/memberpress-review/). By the end, you’ll have all the information you need to decide if ProfilePress is the perfect fit for your website’s goals.
## What to Look Out for in a WordPress Membership Plugin
When choosing a [WordPress membership plugin](https://profilepress.com/), it’s essential to assess your unique use case and ensure the plugin offers the features you need and more. Here are some critical aspects to consider:
**Features:** Here are a few to bear in mind.
- Content restriction methods based on membership levels, user roles, or specific criteria
- Seamless integration with email marketing tools, customer relationship management apps (CRMs), WooCommerce, Learning Management Systems (LMS), and other software essential for your business
- Support for payment gateways like PayPal, Stripe, and Authorize.net, as well as regional options if needed
- A customizable member directory or tools to foster community interaction
- **Ease of Use:** The best WordPress membership plugins offer an intuitive interface and straightforward setup process. Features like drag-and-drop builders for forms and customizations, pre-built templates, and clear documentation can save you time and effort.
- **Security:** Since membership sites often handle sensitive user information and payment data, robust security features are non-negotiable. Look for plugins that provide data encryption, support SSL, and comply with GDPR and other data protection regulations.
- **Support:** Reliable support can make a world of difference. Ensure the plugin offers multiple support channels, such as a knowledge base, live chat, email, or community forums. Regular updates and an active development team are also indicators of a dependable plugin.
## ProfilePress Membership Plugin Overview

[ProfilePress](https://profilepress.com/) is a powerful WordPress plugin that simplifies the process of building and managing membership sites. It supports a variety of use cases, from subscription services and online communities to content monetization.
The plugin makes it easy to register and manage members, create user roles, and protect content with access rules. Beyond these basics, ProfilePress ships with advanced features such as content dripping and pre-built templates. Who is it for?
- Website owners looking to monetize their content with a paywall,
- Course creators drip-feeding lessons,
- Community builders who want to encourage member interaction,
- Entrepreneurs using affiliate marketing to grow memberships, etc.
With its user-friendly design, robust integrations, and customizable options, ProfilePress serves thousands of users worldwide, from small bloggers to large enterprises. It consistently receives positive feedback for its feature set. This is largely thanks to our team of developers who work hard to improve features and the support team who give users reliable support.
## Key Features of ProfilePress WordPress Membership Plugin
ProfilePress stands out with a robust array of tools designed to help you manage your membership site efficiently and effectively.
### 1. Paid Membership or Subscription
A lightweight WordPress membership plugin with extensive eCommerce functionality, ProfilePress simplifies the process of setting up paid memberships or subscription models. The payment setup process is intuitive, enabling you to configure gateways like PayPal and Stripe with ease. This functionality is critical, as a seamless payment experience not only enhances user satisfaction but also ensures consistent revenue flow.

Additionally, ProfilePress offers powerful content control and access restriction capabilities, allowing you to protect premium content and customize access rules based on membership levels or user roles.
### 2. Paywall Setup

For publications or content-heavy websites, ProfilePress offers an impressive feature for [setting up a metered paywall](https://profilepress.com/article/setup-metered-paywall-wordpress-content/). One standout capability is the content preview option, which allows potential members to view a snippet or portion of premium content before committing to a subscription. This tactic not only entices users but also demonstrates the value of the content behind the paywall. The setup process is straightforward. It's an ideal feature for blogs, online magazines, and other content-driven platforms aiming to monetize their work effectively.
### 3. Support for Multiple Product Types
ProfilePress goes beyond simple memberships by supporting a wide variety of product types. This includes services like consultation bookings, appointments, and online courses through LMS integrations. Additionally, it [handles digital products](https://profilepress.com/sell-digital-products-downloads-wordpress/) such as stock images, art, eBooks, videos, and plugins. This versatility makes ProfilePress an excellent choice for entrepreneurs and businesses looking to diversify their revenue streams. By catering to multiple product types, ProfilePress ensures that your site can evolve with your business needs.
### 4. Marketing Features

Once you're done setting up your subscription plans, you'll also need to market them to grow and retain your membership base. With features like coupon codes and automated discount rules, you can create compelling offers that drive conversions. The plugin also integrates seamlessly with popular email marketing tools like Mailchimp and Campaign Monitor, enabling you to engage members through targeted email campaigns.
### 5. Beginner-Friendly User Management
Whether you’re a WordPress expert or not so tech-savvy, ProfilePress's simple and intuitive dashboard interface will help you get around easily. From managing user accounts and orders to tracking membership plans and subscriptions, everything is accessible in one central location. This simplified approach ensures you focus more on growing your site and less on backend logistics.
### 6. Custom Registration Forms and User Profiles

Do you need complete control over the entire user registration process? ProfilePress lets you design custom registration forms optimized for your audience, complete with login and password reset options for existing members. For enhanced user management, the plugin allows admin approval for new registrations, ensuring better community control. Additionally, ProfilePress offers a polished "My Account" page replacement with design customization options to match your branding seamlessly. The plugin also supports automated redirections, restricting access to the WordPress admin dashboard for non-admin users, thereby enhancing security and user experience.
### 7. Extensions and Addons
Finally, ProfilePress offers an array of extensions and add-ons that expand its functionality. From email notifications and confirmations to social login options, the plugin makes user interaction seamless. Admins can manage user moderation, add custom fields, and even generate receipts for memberships. Other features like metered paywalls, [invite codes](https://profilepress.com/addons/invite-codes/) for exclusive access, and multilingual support enhance the versatility of the platform. Whether you’re managing a global audience or looking for unique access methods, these extensions make ProfilePress adaptable to diverse needs.
## ProfilePress Pricing: Is It Worth the Money?
When it comes to pricing, ProfilePress strikes an excellent balance between affordability and feature richness. The completely free version of the plugin comes with enough basic features to get your membership site running. If you need more features, here’s what you get on the premium plans:

- **Standard plan - $129/year for 1 site**
This plan includes essential features such as payment gateway support for PayPal, RazorPay, custom fields, 2FA, reCAPTCHA, LMS integration, etc. It's perfect for small-scale projects or personal websites.
- **Plus plan - $299/year for up to 3 sites**
Along with the features in the Standard Plan, this plan includes user moderation, WooCommerce integration, and multilingual support, making it ideal for medium-sized businesses or content creators managing multiple projects.
- **Agency plan - $499/year for unlimited sites**
The Agency plan is ideal for developers or agencies managing a large number of websites. It offers all the premium features, including access to all add-ons, advanced integrations, and priority email support.
In general, ProfilePress provides a more affordable entry point than competitors like MemberPress, whose Basic plan starts at $179.50/year, and Paid Memberships Pro, which costs $174/year for its Standard plan. The higher-tier plans offer excellent value for agencies and developers managing multiple sites.
## Is ProfilePress Ideal for You?
ProfilePress stands out as an all-in-one membership plugin suitable for various needs and use cases. Its key features, such as advanced content restriction, robust payment gateway support, and seamless integrations with LMS, email marketing tools, and WooCommerce, make it a versatile choice for:
- **Content creators:** Monetize premium content effectively with paywall features and flexible access controls.
- **Small businesses:** Manage appointments, consultations, and digital products effortlessly.
- **Course creators:** Deliver lessons through LMS integrations while drip-feeding content.
- **Agencies:** Handle multiple client projects with ease using unlimited site licenses.
Additionally, ProfilePress’s competitive pricing ensures cost savings compared to other premium plugins.
## ProfilePress Alternatives: Other WordPress Membership Plugins
To further help you make an informed decision, here’s a comparison of ProfilePress with other popular WordPress membership plugins:
| **Plugin** | **Key Features** | **Pricing** | **Best For** |
|---|---|---|---|
| **ProfilePress** | Advanced content restriction, LMS integration, paywall features, robust user management, and WooCommerce integration | Free version
Standard: $129/year (1 site)
Plus: $299/year (3 sites)
Agency: $499/year (unlimited) | Affordable, feature-rich solution for all use cases, including courses, digital products, and subscriptions |
| **MemberPress** | Built-in LMS, content dripping, powerful reporting, and course creation features | Basic: $179.50/year
Plus: $299.50/year
Pro: $399.50/year | Online course creators and advanced reporting needs |
| **Ultimate Member** | Member directories, profile customization, role-based access controls | Free version
Extensions Pass: $249/year
Extensions + Theme Pass: $299/year | Beginners building communities or directories |
| **Paid Memberships Pro** | Extensive add-ons, recurring payments, and strong community features | Free
Standard: $174/year
Plus: $299/year
Enterprise: $5000+ | Membership sites with heavy add-on requirements |
| **Wishlist Member** | Tiered membership levels, content dripping, and WooCommerce compatibility | Basic: $149.50/year (1 site)
Plus: $249.50/year (2 sites)
Pro: $349.50/year (5 sites) | Sites requiring multiple membership levels |
| **BuddyBoss** | Social networking, community features, and integrations with LearnDash for courses | 1 Site: $299/year
5 Sites: $349/year
10 Sites: $449/year | Social networks and interactive communities |
**Analysis**
- **ProfilePress** offers a comprehensive feature set at a competitive price, particularly excelling in versatility for different business models like content creators, small businesses, and agencies.
- **MemberPress** shines for course creators but is slightly more expensive in the entry-tier plans.
- **Ultimate Member** is a simpler and more affordable choice for community-focused websites.
- **Paid Memberships Pro** and **Wishlist Member** cater to niche requirements but can become expensive if many add-ons are needed.
- **BuddyBoss** is unmatched for building social networking communities, but might not suit all use cases due to its focus on social interactivity.
Ultimately, your choice depends on your specific requirements, budget, and long-term goals. ProfilePress stands out for its affordability, ease of use, and versatility, making it a top contender for many use cases.
## Is ProfilePress the Best WordPress Membership Plugin?
No doubt, [ProfilePress](https://profilepress.com/) stands out as one of the best WordPress membership plugins - thanks to its rich feature set, user-friendly interface, and affordability. Whether you’re looking to create a paid membership site, protect premium content, sell subscriptions, or manage an online community, ProfilePress has you covered.
Its ability to cater to various use cases - such as online courses, consultation services, or digital product sales - gives it an edge over many competitors. With intuitive tools for user management, custom registration forms, paywall setups, and seamless integration with marketing tools, ProfilePress makes building and scaling a membership-based business straightforward.
Additionally, ProfilePress’s pricing plans are cost-effective compared to other premium plugins in the market, offering great value without compromising on functionality. The range of extensions and add-ons further enhances its versatility, making it suitable for both small and large-scale projects.
While its extensive features might seem overwhelming for absolute beginners, the robust support system and detailed documentation help bridge the gap.
In conclusion, if you’re looking for a comprehensive and flexible WordPress membership plugin that doesn’t break the bank, ProfilePress is a strong contender. It’s a reliable, scalable, and feature-rich solution that can help you build the membership site you’ve always envisioned.
---
## WordPress Stuck in Maintenance Mode? Here's How to Fix It Quickly
- URL: https://levamo.com/blog/wordpress-stuck-in-maintenance-mode/
- Category: wordpress
- Author: Sunyyan Junaid
- Published: 2025-04-08
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix your stuck WordPress maintenance mode easily. Get your site back now!
Ever hit **Update** on your WordPress site and suddenly it's stuck in maintenance mode? It’s like sending your site for a quick coffee break, and it just never comes back.
If your **WordPress site is stuck in maintenance mode**, you’re not alone. It happens more often than most people think, especially when updating a plugin, theme, or WordPress core. The good news? Fixing it is super simple.
Let’s walk through how to get your site back online fast without getting too technical.
## What is WordPress Maintenance Mode and Why It Happens
When you update your site, WordPress creates a small .maintenance file in your website's root folder. This triggers the "Briefly unavailable for scheduled maintenance" message you see.
It's a nice little heads-up for your visitors, letting them know you’re doing some behind-the-scenes work.
But sometimes things go sideways. A slow server, a bad plugin update, or just a glitch can interrupt the update process. WordPress then forgets to remove the .maintenance file. So, instead of your site coming back online, it stays stuck in limbo.
## How to Know if You’re Stuck in Maintenance Mode
Just visit your site. If you see this message:
*"Briefly unavailable for scheduled maintenance. Check back in a minute."*
...but the "minute" turns into ten, thirty, or an hour, and you're definitely stuck.
## How to Fix a WordPress Site Stuck in Maintenance Mode
Here’s the quick fix.
### Step 1: Access Your Site Files
You’ll need to connect to your site using FTP (like FileZilla), your hosting provider's File Manager, or the file browser inside your WordPress hosting dashboard. If you’re using Levamo, you already know how clean and simple that is.
### Step 2: Delete the .maintenance File
Head to your site’s root directory. That’s the folder where files like wp-config.php and wp-content live.
Look for a file called .maintenance. Yes, that little dot at the beginning matters.
Delete the file. That’s it. Your site should be back instantly.
## Still Stuck? Here's What Might Be Going On
If deleting the .maintenance file doesn’t solve it, something likely went wrong with the update itself.
You can try:
- Deactivating the plugin or theme you were updating
- Rolling back to a previous version using a backup
If you’re using a hosting platform like Levamo, your backups are already in place and can be restored with just a few clicks.
## How to Avoid Maintenance Mode Issues in the Future
A few small habits go a long way:
- Update plugins and themes one at a time instead of all at once
- Avoid updating during peak traffic hours
- Always have a backup before updating anything
- Use a managed hosting provider that can handle resource-heavy updates without choking
## For Developers: Override Maintenance Mode with Code
If you're feeling technical, you can open wp-config.php and add this line:
`define('WP_INSTALLING', false);`
But really, unless you need to do this for very specific reasons, just deleting the .maintenance file is faster and safer.
## Final Thoughts
WordPress maintenance mode is useful, but it’s also a bit forgetful. One interrupted update, and it leaves your site hanging.
If your WordPress site gets stuck in maintenance mode, don’t worry. It’s not broken, just a little confused. Now you know exactly how to turn off maintenance mode and get things running again.
And if you’re tired of fixing these issues yourself, Levamo’s got your back. Our hosting is optimized for high-performance WordPress sites that run fast, stay online, and handle updates like a pro.
---
## How to Enable WordPress Debug Mode (and Why You Might Want To)
- URL: https://levamo.com/blog/debug-in-wordpress/
- Category: website-development
- Author: Salman
- Published: 2025-04-08
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix WordPress errors! Enable debug mode and troubleshoot like a pro.
If you’ve ever been greeted by the “[White Screen of Death](/blog/wordpress-white-screen-of-death/)” (WSOD) on your WordPress site or faced a cryptic error message that left you scratching your head, you’re not alone. Debugging WordPress can feel like searching for a needle in a haystack, especially if you’re not sure where to start. Thankfully, WordPress offers a built-in way to reveal the behind-the-scenes errors and notices that can help you diagnose (and fix) problems: **debug mode in WordPress**.
But what is debug mode, exactly? And how do you **enable WordPress debug** features safely without scaring away your site’s visitors with big, scary error messages? In this guide, we’ll break down **what is debug mode** in WordPress, walk you through the steps to flip it on, highlight a couple of helpful **WordPress debug plugin** options, and share some best practices for tackling **WordPress debugging**. By the end, you’ll be able to confidently handle the dreaded WSOD or any random “function not found” error with grace.
## 1. So, What Is Debug Mode in WordPress?
**Debug in WordPress** refers to a set of constants (special configuration variables) that tell WordPress to show or log errors, warnings, and notices. The most important one is **WP_DEBUG**, which triggers WordPress to reveal errors that typically stay hidden in a live environment. This is crucial for diagnosing plugin conflicts, theme issues, or custom code that’s misbehaving.
### 1.1 Key Constants to Know
**WP_DEBUG**
- The main toggle. If set to true, WordPress will start spitting out errors and notices.
**WP_DEBUG_LOG**
- When true, errors go into a debug.log file, so they’re not plastered onto the screen for visitors to see.
**WP_DEBUG_DISPLAY**
- If set to true, errors appear right on your site pages. Typically used in development, it's never recommended for a production site because visitors can see it.
### 1.2 Why Use Debug Mode in WordPress?
- **Spot Plugin Conflicts**: If your site goes down right after activating a plugin, debug messages can reveal the underlying issue.
- **Test Custom Code**: If you wrote custom functions or integrated code snippets, debugging can highlight issues like undefined variables or function name collisions.
- **Prevent Hidden Errors**: Some warnings won’t crash your site but can lead to future issues or poor performance if unaddressed.
In short, **WordPress debugging** is like shining a flashlight in a dark closet of your site’s code, helping you quickly find the bug that’s messing up your day.
## 2. The “What Is Debug Mode” Quick Definition
**Debug mode** in WordPress is simply a mechanism that allows you to see behind the scenes when errors occur, like turning on a backstage spotlight at a concert. It’s part of WordPress’s developer-friendly features. If you’re used to error logs in other frameworks, the principle is the same: turning on debug mode (and optional logging) provides deeper insights into what might be breaking or misconfigured.
## 3. How to Enable WordPress Debug Mode: The Manual Way
The most direct route to **WordPress enable debug** is to edit your wp-config.php file. Typically found in your WordPress root directory, near the top, you might see a comment that says, “That’s all, stop editing! Happy blogging.” Insert or adjust the following lines just *above* that mention:
define( 'WP_DEBUG', true );
define( 'WP_DEBUG_LOG', true );
define( 'WP_DEBUG_DISPLAY', false );
**Note**: Setting WP_DEBUG_DISPLAY to false hides errors from your site’s front end, perfect for production if you want to gather logs but not expose them to visitors. Meanwhile, WP_DEBUG_LOG = true saves errors to a file named debug.log in your /wp-content/ directory.
### 3.1 Double-Check Your File Permissions
If you aren’t seeing any log files show up, your hosting environment might not allow WordPress to create new files or directories. Check that wp-content has the right permissions to let WordPress generate debug.log.
### 3.2 Remember to Turn It Off Later
Debugging is super helpful, but it’s best practice to disable it once you’re done. Leaving debug mode on can flood your logs, hamper performance, and potentially reveal sensitive paths or data if WP_DEBUG_DISPLAY is set to true.
## 4. Using a WordPress Debug Plugin (For Those Who Prefer Point-and-Click)
Not a fan of poking around in wp-config.php? No problem. A **WordPress debug plugin** can handle a lot of the heavy lifting. Some favorites include:
**Query Monitor**
- Acts like a detective for queries, hooks, scripts, and more. Great for debugging slow queries or finding which plugin is hogging resources.
- When active, it adds a toolbar in the admin area, letting you see real-time performance metrics.
**Debug Bar**
- Another popular plugin that adds a debug menu to the admin bar, showing notices, warnings, and advanced details.
**WP Debugging**
- Simplifies the process of enabling debug constants by offering a user interface. No manual config needed.
In any case, a plugin is an easy introduction to **WordPress debugging** if you’re uncomfortable editing config files. Just keep in mind: some of these plugins might not function properly if you’re also messing with advanced config lines in wp-config.php - there can be a conflict if they’re setting constants differently than you do manually.
## 5. Hunting Down Errors and Warnings: Where to Look
### 5.1 The debug.log File
If you’ve got WP_DEBUG_LOG set to true, peek into wp-content/debug.log. Inside, you’ll find lines describing errors, warnings, or notices triggered by your site’s code. Typically, you’ll see time stamps and file paths. Don’t be alarmed if you see “deprecated” notices for older plugins or themes - some developers don’t keep up with the latest standards.
**Pro Tip**: If the log file is ballooning in size, disable debug mode or fix the root cause of repeated errors ASAP. A massive log can fill up your disk space or hamper site performance.
### 5.2 The Browser Admin Bar (If Using a Plugin)
Plugins like Query Monitor or Debug Bar often display their findings in a bar at the top of your admin screens. They might highlight slow queries, scripts that didn’t load properly, or messages about plugin conflicts. If you suspect your theme or a custom function is at fault, these tools can be a goldmine for clues.
## 6. Handling Common Debug Scenarios
**White Screen of Death**:
- If your site is fully blank, enable debug mode (and the debug log) so you can see if a fatal error is happening behind the scenes - like a missing function or a syntax error.
- Check debug.log for lines referencing “Fatal error” or “Parse error.”
**Slow Queries**:
- If your site’s sluggish, a plugin like Query Monitor can reveal queries that take too long. Maybe a big JOIN or an unoptimized table is choking performance.
**Plugin Conflicts**:
- Suppose you installed a new plugin, and your site started spitting out errors. Debug logs might show references to that plugin’s file. You can then disable the plugin or contact the developer with an exact error message.
**Deprecated Functions**:
- Warnings about “deprecated” features hint that your theme or plugin is using old WordPress calls. Usually not site-breaking, but worth addressing to future-proof your code.
## 7. Extra Tips for Smoother Debugging
### 7.1 Use a Staging or Local Environment
The best place to test out **debug mode in WordPress** is in a safe environment where you’re not scaring real site visitors with errors. Many hosts offer staging environments, or you can run WordPress locally using tools like Local or XAMPP. That way, you can comfortably break things without risking your production site’s reputation.
### 7.2 Keep Error Logs Short-Lived
If you’re a neat freak, consider rotating your debug logs so they don’t blow up. For instance, after you fix a bug, rename the old debug log to debug_old.log and let WordPress generate a fresh one. This helps keep your logs relevant and manageable.
### 7.3 Master the “Enable/Disable” Cycle
Part of the WordPress debugging journey is toggling debug mode on to fix issues, then toggling it off once you’re done. Always remember to revert your changes in wp-config.php or in your plugin settings so you don’t unknowingly run debug mode for weeks on end.
## 8. Digging Deeper: WP_DEBUG vs. WP-CLI and Beyond
If you really want to get your hands dirty, consider using WP-CLI (the WordPress command line interface) to test plugins, run updates, or check for theme conflicts without messing around in your live admin area. Coupled with debug mode, WP-CLI logs can help you pinpoint errors quickly, especially for dev environments. This approach might be more advanced, but if you’re a developer or an adventurous site owner, it’s a powerful combo.
## 9. Real-World Example: Fixing a Broken Plugin
Let’s say you just installed a fancy image optimization plugin, but your entire media library vanished from the admin. Yikes. Here’s how you might solve it with debug mode:
**Enable Debug**:
define( 'WP_DEBUG', true );
define( 'WP_DEBUG_LOG', true );
define( 'WP_DEBUG_DISPLAY', false );
- Save those changes in wp-config.php.
**Check the Log**:
- Head to wp-content/debug.log or refresh your admin page to see if a log was generated.
- Suppose you see something like: [21-Mar-2025 11:02:45 UTC] PHP Fatal error: Call to undefined function image_optim() in /wp-content/plugins/fancy-optimizer/main.php on line 101.
**Action**:
- Bingo, the plugin is calling image_optim() which might not be declared or is from an extension that isn’t installed on your server.
- Deactivate the plugin from your admin or via wp-cli plugin deactivate fancy-optimizer.
- Either fix the missing function or contact the plugin dev. Once done, test again.
**Disable Debug**:
- After confirming your site’s stable, remove or comment out the debug constants (or set them to false).
This is the typical workflow in **WordPress debugging**: turn on debug mode, replicate the issue, consult the logs or debug messages, fix the culprit, and revert.
## 10. Watch Out for Security Implications
When **wp_debug** is on and you’re showing errors on the front end (WP_DEBUG_DISPLAY = true), sometimes error messages can reveal server paths, plugin version info, or other tidbits hackers could exploit. If you ever want to see errors on a live site, it’s much safer to set WP_DEBUG_DISPLAY to false and rely on WP_DEBUG_LOG so everything is quietly written to a file that only you can access.
## 11. Another Ally: Hosting with Built-In Monitoring
Sometimes you just want to see errors or logs from your host’s dashboard, without rummaging in files. That’s where a quality hosting platform can help. Some offer built-in error logging or real-time server monitoring that complements WordPress’s debug mode. If your host is stuck in the stone age, you might be missing out on easy tools for diagnosing site issues.
## 12. Levamo: Simplify Your Debugging Life
Speaking of hosting solutions that streamline your day, let’s talk about **Levamo**. If toggling debug mode in WordPress has you nervous, maybe you’re not sure where to find wp-config.php, or you don’t like messing with code files, [Levamo](/) can make your life easier:
- **User-Friendly Dashboard**: Access logs, server stats, and resource usage in a single spot.
- **Instant Staging Environments**: Spin up a clone of your site, enable debug mode freely, and fix issues without risking your live site.
- **Guided Security & Updates**: Keep your WordPress core, themes, and plugins up-to-date. Minimizing potential conflicts can reduce the need for debugging in the first place.
- **Expert Support**: If you do run into a puzzling error, Levamo’s support can guide you on how to interpret logs or tweak debug settings safely.
It’s basically hosting that understands WordPress inside and out, so you can focus on building your site, not troubleshooting server mysteries.
## 13. Wrapping Up: Be the Debugging Hero
By now, you’ve got a solid grasp on **debug in WordPress** and how to harness it:
- You know **what is debug mode**: a tool for seeing hidden errors.
- You can **enable WordPress debug** features via wp-config.php or a **WordPress debug plugin**.
- You’ll keep logs in debug.log, monitor them carefully, and remember to turn it all off once you’re done sleuthing.
- If you want zero fuss, a platform like **Levamo** can come in clutch with integrated logs and staging setups.
Whenever you or your client’s site hits weird errors, you’ll be the hero who calmly says, “Let’s switch on debug mode, check the logs, and fix that bug,” instead of panicking about random white screens. That’s the power of WordPress debugging, and now it’s yours to wield confidently!
---
## WooCommerce vs Shopify in 2026: A Data-Backed Showdown for Modern E-Commerce
- URL: https://levamo.com/blog/woocommerce-vs-shopify/
- Category: ecommerce
- Author: Sunyyan Junaid
- Published: 2025-04-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WooCommerce vs Shopify in 2026: Data drives the best e-commerce choice.
Choosing between WooCommerce and Shopify in 2026 isn't just a matter of picking software. It's about choosing a philosophy of doing business online. On one side, you have **WooCommerce**: flexible, open-source, deeply customizable, and designed to let you build exactly what you need.
On the other hand, **Shopify**: a sleek, hosted platform that simplifies e-commerce so you can focus on selling. Both are world-class. Both power millions of stores. But which one is right for *you*?
Let’s break it down.
## WooCommerce: Freedom to Build on Your Terms

[WooCommerce](https://woocommerce.com/) is a free plugin for WordPress that turns any site into a fully functional online store. It gives you total control: you own your data, choose your hosting, select your plugins, and customize the look, feel, and flow of your store. In 2026, WooCommerce is used by 9% of all websites and powers over 8 million stores worldwide. It's ideal for entrepreneurs who want to innovate beyond the limits of a boxed-in solution.
The WooCommerce ecosystem is massive, with thousands of plugins and themes, allowing you to do just about anything, from offering complex subscription models to building multilingual marketplaces. The open-source nature means you’re never locked in. It’s your store, on your terms.
That said, WooCommerce asks more of you. You’re responsible for hosting, updates, and site security. The experience is smoother with the right host, and this is where managed services like Levamo shine, delivering a high-performance stack tailored for WooCommerce scalability, speed, and uptime.
### Key Advantages of WooCommerce in 2026
- Customization Without Limits: You can design your storefront exactly the way you want it. Modify templates, code your own checkout experience, or connect with any third-party tool; there are no artificial constraints.
- Tight Integration With WordPress: If your business uses content as a growth strategy -think SEO, blogs, tutorials, or video hubs - then WooCommerce gives you an edge because it's baked into the best content management system in the world.
- You Own Everything: From your code to your customer database, WooCommerce doesn’t lock you in. You can switch hosts, export your data, or pivot business models anytime.
## Shopify: A Platform That Just Works

[Shopify](https://www.shopify.com/) is a fully hosted, all-in-one e-commerce solution. You don’t have to worry about servers or security. You sign up, pick a theme, add your products, and you’re live. It’s made for simplicity, and in 2026, over 4.6 million websites use Shopify. From solopreneurs to billion-dollar brands, Shopify serves a wide range of merchants.
What sets Shopify apart is convenience. Hosting, security, and performance? Handled. Built-in features like abandoned cart recovery, multi-channel selling, and POS integration? Included. 24/7 support? Always available. For business owners who don’t want to think about caching, updates, or downtime, Shopify delivers peace of mind.
### Notable Shopify Benefits
- Fast Time to Market: Launch your store in a day. No setup stress, no plugins to configure.
- Professional Design Out of the Box: Shopify themes are sharp, responsive, and conversion-focused. You don’t need a design degree to make your store look great.
- Built-In Infrastructure: No need to manage security, performance tuning, or backups - Shopify handles it all.
But you trade some freedom for that ease. Customization is limited by Shopify’s structure and Liquid theme language. Want a completely bespoke checkout flow? You’ll need Shopify Plus. Want to avoid extra fees? Better use Shopify Payments.
## Head-to-Head: Feature Showdown
| Feature | WooCommerce | Shopify |
|---|---|---|
| Pricing | Free core, pay for hosting & plugins. No platform transaction fees. | $39+/mo + app fees. Additional fees if not using Shopify Payments. |
| Hosting | Choose your own (e.g., Levamo). Self-managed or use managed WordPress hosting. | Included. Shopify manages it all. |
| Ease of Use | Moderate. WordPress knowledge helps. | Relative easy. No technical experience is needed. |
| Customizability | Unlimited. Full code access, vast plugin ecosystem. | Limited. Customization via themes, apps, or the Plus tier. |
| SEO & Content | Superior (WordPress). Full control. | Solid basics. Some structural limitations. |
| Performance | Host-dependent. Can be ultra-fast with good hosting. | Fast out of the box. Globally optimized CDN. |
| Support | Community + plugin devs. Premium support via managed hosts like Levamo. | 24/7 official support included. |
| Scalability | Unlimited with proper infrastructure. | Seamless. Shopify handles spikes. |
| Control | Full ownership of site, data, and infrastructure. | Shopify controls infrastructure, policies, and TOS. |
## What Real Users Are Saying: WooCommerce vs Shopify Reddit Comments
Reddit, forums, and reviews tell us the same story: Shopify users love the simplicity and support. WooCommerce users love the freedom and flexibility it offers. Many users switch platforms as their needs evolve.
One Redditor nailed it: ***"Shopify is great because you don’t worry about tech. WooCommerce is great because you control everything."***
Another wrote: ***"My WooCommerce site is lightning fast on Levamo. We outgrew Shopify’s pricing and needed more flexibility. Never going back."***
Others chimed in on how WooCommerce becomes easier with good hosting. As one power user put it, ***"You don’t need to be a dev if you’re hosted somewhere smart. Levamo gives me the performance of Shopify with way more control."***
Also Read: [CDN for eCommerce](/blog/cdn-for-ecommerce/)
## When to Choose WooCommerce
- You want full control over your store, data, and hosting.
- Your business model requires unique features, workflows, or integrations.
- You already use WordPress or plan to leverage content/SEO heavily.
- You want to minimize costs long-term (especially at scale).
- You’re working with a developer or using a managed WooCommerce host like Levamo to offload the hard parts.
- You want to avoid transaction fees and build a margin-first store.
- You sell in categories that are restricted or disallowed on Shopify (e.g., supplements, CBD).
That margin-first, no-transaction-fee logic is exactly why so many merchants leaving Shopify land on WooCommerce, especially those building a marketplace, where per-sale fees would eat into every vendor payout. If you’re weighing the switch, it helps to see how WooCommerce stacks up against the rest of the field. Compare your options in the [best Shopify alternatives](https://www.wcvendors.com/best-shopify-alternatives/ "nofollow").
## When to Choose Shopify
- You want a plug-and-play solution with zero technical headaches.
- You're launching fast and prefer not to handle site maintenance.
- You value excellent customer support and guaranteed performance.
- Your store has standard e-commerce needs that fit within Shopify’s ecosystem.
- You’re comfortable with monthly fees in exchange for convenience.
- You sell simple products and want to manage inventory, shipping, and marketing from a single dashboard.
- You want to integrate with POS, Instagram/Facebook, or marketplaces quickly.
## The Power of WooCommerce + Managed Hosting
A final note: WooCommerce’s biggest perceived weaknesses - performance, complexity, and maintenance - can be solved with the right hosting. Levamo, for example, is engineered specifically for WooCommerce: blazing-fast load times, built-in caching, and expert support for scaling stores. With this setup, you get Shopify-level speed *and *WooCommerce-level control.
Hosting with Levamo means:
- Auto-scaling during traffic surges
- Advanced security hardening
- Daily backups & one-click restores
- Object caching for fast dynamic pages
- Built-in CDN and image optimization
In other words, you don’t have to choose between ease and freedom. With WooCommerce on Levamo, you get both.
## The Verdict
There’s no wrong choice - only the right fit for where you are and where you’re going. Shopify is unmatched for simplicity and rapid deployment. WooCommerce is unmatched for control and customization. As you weigh the trade-offs, think about your technical resources, your growth plan, and how much control you want over the future of your business.
For merchants ready to invest in their own infrastructure and build a custom experience, [managed WooCommerce hosting](/managed-woocommerce-hosting/) (especially hosted on Levamo) is a powerhouse in 2026. For those who want a store that just works, Shopify remains a safe and proven path. Both can win. The better question is: which one lets *you* win?
---
## Apache vs Nginx WordPress: Which Server Reigns Supreme?
- URL: https://levamo.com/blog/apache-vs-nginx-wordpress/
- Category: hosting
- Author: Salman
- Published: 2025-04-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Apache or Nginx for WordPress? Find out which server is best for your site.
Ever wondered if you should host your WordPress site using Apache or Nginx? You’re definitely not the only one. When it comes to WordPress - and, in fact, most modern web applications - **Apache vs Nginx WordPress** is an ongoing debate in the developer community. Each has die-hard fans, each has some cool tricks up its sleeve, and each can give you solid performance if set up correctly. But which one’s better for your WordPress site? Let’s dive in and weigh the pros and cons of these two popular web servers. By the end of this article, you’ll be more than ready to make an informed decision (and maybe impress your friends with some web-server-savvy chatter).
## 1. Meet Apache and Nginx: The Contenders
### 1.1 A Quick Look at Apache
- **Background**: Born in the mid-90s, Apache quickly became (and still remains) one of the most widely-used web servers on the planet.
**Highlights**:
- .htaccess: Apache famously allows dynamic per-directory configuration through .htaccess files - something many WordPress site owners love for quick rewrites and custom rules.
- **Modular Design**: With an array of built-in modules, you can turn features on and off for logging, security, caching, and more.
- **Ease of Use**: For a lot of hosting environments - particularly older or more traditional ones - Apache is the default. It’s well-documented and widely supported.
### 1.2 A Quick Look at Nginx
- **Background**: Nginx (pronounced “engine-x”) came onto the scene a bit later, with a focus on speed, scalability, and handling high-traffic sites.
**Highlights**:
- **Event-Driven Architecture**: Nginx uses an asynchronous, non-blocking approach to handling connections, which is fantastic for concurrency and performance under heavy load.
- **Lightweight Memory Footprint**: Typically uses less RAM than Apache for similar tasks.
- **Reverse Proxy & Caching**: Nginx also functions well as a reverse proxy, load balancer, or caching layer in front of other services.
So, **Apache vs Nginx WordPress** becomes a battle between a longtime champion known for its .htaccess convenience and a younger, speed-focused competitor known for efficiency. Now let’s see how these differences translate to real-world WordPress usage.
## 2. WordPress on Nginx vs. WordPress on Apache
WordPress can run on both with minimal fuss. Whether you’re using “nginx and WordPress” or an Apache-based stack, the key differences lie in how each server handles configurations, concurrency, and rewrites.
### 2.1 WordPress on Apache
- **One-Click Installs**: Many shared hosting providers (and even some dedicated/VPS solutions) default to Apache-based setups. Installing WordPress is often a straightforward matter of a script that sets up everything.
- **.htaccess for Rewrite Rules**: WordPress typically writes its pretty-permalinks rules to .htaccess. This auto-configuration is beloved by many.
- **Performance at Moderate Traffic**: For typical personal blogs or small business sites, Apache’s overhead isn’t a dealbreaker.
### 2.2 WordPress on Nginx
- **Configuration Differences**: Nginx doesn’t use .htaccess. Instead, you define rewrite rules in the main Nginx config - like in /etc/nginx/sites-available/. You’ll need to replicate or adapt WordPress’s usual rewrites to your config file manually.
- **Speed & Memory**: Nginx excels under higher loads. If your WordPress site draws thousands or millions of monthly visitors, you might see performance gains.
- **Slightly More Complex Setup**: If you’re used to .htaccess for custom rules (like password protection, custom redirects, etc.), you’ll have to shift that logic to Nginx config blocks.
So is **WordPress on Nginx** always faster? In many benchmarks, yes, but it depends on your site’s architecture and how many visitors it juggles daily.
## 3. Nginx vs Apache: Key Performance Traits
A big factor in the **“nginx vs apache”** conversation is concurrency - how each server handles multiple visitors at once. Let’s simplify:
**Apache’s Process/Thread Model**:
- Apache traditionally spawns a new process or thread for each incoming connection. That can chew up RAM quickly if you have lots of visitors.
- However, modules like mpm_event can help Apache be a bit more asynchronous.
**Nginx’s Event-Driven Model**:
- Nginx uses a single (or small set of) processes to handle thousands of connections asynchronously, passing them off efficiently.
- Lower memory usage under heavy load, and can handle large concurrency with fewer resources.
In short, **apache vs nginx** for concurrency often goes to Nginx, especially for high-traffic sites. On smaller sites, the difference might be negligible, but for big players, Nginx typically edges out.
## 4. Rewrites & .htaccess: A Big Apache or Nginx Deal-Breaker?
### 4.1 Apache’s .htaccess
**Pros**:
- Per-directory config is a lifesaver if you’re on shared hosting and can’t edit the main server config.
- WordPress writes its permalinks changes automatically to .htaccess, so it’s super convenient.
**Cons**:
- Checking .htaccess in each directory can slow performance - Apache has to keep scanning up the directory tree.
### 4.2 Nginx’s Approach
**Pros**:
- Centralized config. This can lead to better performance if set up correctly.
- No need to parse multiple .htaccess files on every request.
**Cons**:
- You can’t just drop a file in your WordPress directory for rewrites or custom rules. You must modify the main nginx.conf or site-specific config, typically requiring sudo access.
- WordPress can’t auto-write its own rewrite rules, so you do that by hand (or use a plugin that instructs you on what lines to add).
For many folks, this is the biggest factor in **“apache or nginx”**: do you prefer an .htaccess style approach or are you comfortable editing server config blocks?
## 5. Memory Footprint and Resource Usage
If your server is on a tight budget, resource usage might sway you strongly:
- **Apache**: Might use more memory, especially if configured to spawn multiple processes. But for moderate traffic, it’s not a big deal.
- **Nginx**: Typically considered leaner. If you’re running high-traffic WordPress sites, you may appreciate how Nginx handles spikes without devouring your server’s RAM.
The difference for a small personal blog is minimal, but for busier, heavier sites, you’ll likely see **Nginx vs Apache** resource usage weigh in Nginx’s favor.
## 6. SSL/HTTPS and HTTP/2 Support
Modern WordPress sites shouldn’t even consider not using HTTPS. Let’s see how the servers fare:
- **Apache**: Supports SSL and HTTP/2. Setup is straightforward, especially with mod_ssl and Let’s Encrypt.
- **Nginx**: Also supports SSL/TLS. Tends to handle large numbers of SSL connections well with fewer resources. HTTP/2 is easy to enable in the config (listen 443 ssl http2;).
Both do SSL fine, so you won’t have major troubles with either in 2023. The nuance might be that Nginx’s event-driven approach can handle more concurrent SSL sessions more efficiently. But for average traffic, the difference is marginal.
## 7. Reverse Proxy & Microservices? Nginx Shines
WordPress might be your main site, but maybe you also run an API or microservice. Nginx is famously good at acting as a front-end load balancer or reverse proxy, letting you route traffic to multiple back-end services. While Apache can also do reverse proxying with mods like mod_proxy, Nginx’s lightweight concurrency often makes it a top choice for complex architectures.
## 8. “Best Web Server for WordPress”: The Real Answer
So, what’s the **Best web server for WordPress**? The honest truth:
- **If you’re comfortable with .htaccess** or rely on quick per-directory tweaks, Apache is often simpler. It’s also common in shared hosting.
- **If you need raw speed for high traffic** and can handle the different config style, Nginx is often the top pick.
- **Hybrid (Reverse Proxy)**: Some folks pair Nginx as a front-end reverse proxy with Apache behind it. Why? You can leverage Nginx caching and concurrency while letting Apache handle dynamic rewrites or .htaccess. Tools like cPanel even support a “Nginx as proxy” approach.
In other words, you can’t go drastically wrong if you configure them properly. **Apache or Nginx** might be an either-or question, but many modern WordPress hosts even mix them for best results.
## 9. Tuning Tips for WordPress on Both Servers
### 9.1 Tuning Apache
- **Enable KeepAlive**: Ensures connections stay open for multiple requests, reducing overhead.
- **Use the Right MPM (Multi-Processing Module)**: mpm_event can bring an async flair, better for concurrency than the older prefork.
- **Minimize .htaccess:** Overusing .htaccess can lead to performance hits. Move critical logic to the main config if possible.
### 9.2 Tuning Nginx
- **Use PHP-FPM**: A separate fast process manager for PHP that Nginx can communicate with.
- **Caching**: Nginx can do fast caching of static files and even partial page caches if configured carefully.
- **Gzip & Brotli**: Enable compression for static resources. Nginx handles that quickly and with minimal overhead.
Regardless of **nginx vs apache** or any combos, the basics remain: keep your code optimized, use caching plugins for WordPress, and watch resource usage.
## 10. Real-World Example: High-Traffic eCommerce Site
Let’s do a quick scenario. Suppose you run a busy eCommerce WordPress site:
- **Traffic**: Thousands of shoppers at once.
- **Heaps of Images**: You host product images and need them served quickly.
- **Frequent Cart Updates**: Dynamic content can’t always be cached easily.
In many such cases, site owners often find **nginx vs apache** comparisons favor Nginx for concurrency, especially if you cache or serve images directly. Nginx can front-end your static content, while dynamic calls go to the back-end with minimal overhead. If you or your dev team is comfortable with Nginx configs, the performance edge can be a big plus.
## 11. The “All-In-One” Stacks and WordPress Ecosystem
Some hosting services or distributions come with pre-baked stacks - like LAMP (Linux, Apache, MySQL, PHP) or LEMP (Linux, Nginx, MySQL, PHP). Let’s see:
- **LAMP**: The classic choice. Many tutorials, especially older ones, revolve around this stack for WordPress.
- **LEMP**: The Nginx-based cousin. Gains popularity each year due to Nginx’s performance rep.
If you’re on a shared host, you might not get a choice at all: many default to Apache. If you’re on a VPS or dedicated server, you can pick whichever you want. That’s where a little knowledge about **wordpress on nginx** vs. Apache can help you set up your environment perfectly.
## 12. Apache or Nginx in the Age of Containers?
In a containerized environment - like Docker - some folks skip big server configurations altogether, letting specialized images handle their frameworks. Even so, you might choose a Docker image for Nginx or Apache, or you might run Nginx in front as a reverse proxy, with separate containers for the WordPress app. Understanding the **apache vs nginx** differences still pays off because you’ll see them used inside containers frequently.
## 13. Levamo: Simplify Your Web Server Choice
Of course, no matter which side you choose in the **Apache vs Nginx WordPress** debate, the road can get bumpy if your hosting environment isn’t supportive or well-optimized. That’s where **Levamo** steps in:
- **Flexible Hosting**: Levamo supports both Apache-based and Nginx-based setups, letting you pick the one that suits your style or traffic profile.
- **Effortless Scaling**: If you find your WordPress site outgrowing the server resources under Apache or Nginx, you can seamlessly add more CPU, RAM, or disk space.
- **One-Click Tools**: Tweak your environment, check logs, or spin up staging sites without SSH headaches. If you prefer manual config, you have that power too.
- **Guided Security**: SSL certs, firewall rules, and other goodies can be handled from a user-friendly dashboard.
So if you’d rather not wrestle with a bare-metal setup or third-party control panels, Levamo can shoulder the heavy lifting, leaving you free to tweak Apache or Nginx as much (or as little) as you like.
## 14. Final Verdict: The Best Web Server for WordPress?
If you came here looking for a one-liner - **“this is absolutely the best web server for WordPress”** - sorry to disappoint. Both Apache and Nginx can handle WordPress famously if tuned right. The deciding factor generally boils down to:
- **Simplicity vs. Speed**: Apache might be simpler if you love .htaccess or prefer out-of-the-box solutions. Nginx might push better performance for heavier loads, but requires different config approaches.
- **Hosting Constraints**: Many shared hosts only offer Apache. If you’re on a VPS or dedicated server, you have the freedom to pick Nginx (or a hybrid approach).
- **Your Comfort Level**: Are you at home editing Nginx configs? Or do you prefer dropping snippet rewrites into .htaccess?
In the end, the **“nginx vs apache”** question isn’t about winners and losers, but about picking the best tool for your scenario. For many WordPress sites, either server will do fine. For massive or resource-sensitive operations, you’ll likely see a stronger case for Nginx. And if all else fails, you can run Apache behind Nginx in a “reverse proxy” combo that merges Nginx’s concurrency with Apache’s .htaccess convenience.
---
## Why is My WordPress Website So Slow & How to Fix It?
- URL: https://levamo.com/blog/why-is-my-wordpress-site-so-slow/
- Category: website-performance
- Author: Faisal Sarker
- Published: 2025-04-04
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Speed up your WordPress site! Find out why it's slow and learn easy fixes.
Speed matters - especially on your website.
A slow WordPress website can annoy users, hurt your search engine rankings, decrease conversions, and even go on to destroy the reputation of your business. And I’m pretty sure you don’t want any of them.
And it’s not just the users, search engine algorithms also favor quick sites. A slow site might drop in search results, and cost you traffic and visibility.
**But the question is, why is your website slow in the first place?** Well, there's no single answer to that. It can be poor web hosting, bloated themes, too many plugins, or even unoptimized images.
The good news? You don’t necessarily need a developer to fix most of these problems.
In this article, we will share answers to one of the common questions from WordPress site owners “Why is my website slow?”.
You will also learn speed optimization in WordPress that will solve your website speed issues.
Let's get started!
## Why Your WordPress Site is Slow (And the Fixes)
### 1. Not Using the Right Hosting Plan

You can’t just run a fast train on an old and broken track and expect it to reach its full speed. It’s almost the same for your WordPress website. No matter how optimized your site is, without the right hosting, it can suffer.
#### Why This Happens
Most people want to get their website started with shared hosting or cheap plans. That’s because those are budget-friendly choices.
However, there are catches.
- Sites on shared hosting share resources with hundreds (or thousands!) of other sites. If another site on the same server sees a traffic surge, your site slows down too.
- And if you just get a cheaper plan with low resources, the situation can be even worse, as they might not be able to power the website properly.
#### How to Fix It
- **Choose a Reliable Host** - Levamo is a great choice for hosting your website, thanks to its powerful infrastructure like [LiteSpeed servers](/blog/lite-speed-hosting-benefits/), Redis & Object Caching, and free CDN. Plus, no sites on Levamo share resources with other websites.
- **Upgrade to a Better Hosting Plan** - If you have a growing site, upgrade to a hosting plan that provides enough resources to power your website. You can consult with the hosting provider to find a suitable plan for your website.
### 2. A Heavy WordPress Theme
Your theme is the foundation of your website. And that’s why it can impact the performance of your website heavily. Bloated themes with unnecessary code, animations, or features can slow performance.
#### Why This Happens
- Some themes add way too many built-in functions, including sliders, animations, and widgets that slow things down.
- If the code is badly written, it might be slow to render.
- Themes that aren't updated often can break compatibility and result in slow performance.
#### How to Fix It
- Switch to lightweight themes like **[Astra](/blog/astra-wordpress-theme-review/)**, **GeneratePress**, or **Neve**. These themes are optimized for speed and code efficiency.
- Beware of themes with an unnecessary overload of features. If you don't need fancy effects, just use such themes and lightweight themes. Instead, and if you need some new features, you always add them via lightweight plugins when necessary.
- Use a mobile-optimized theme. Unoptimized for mobile means it will load strangely and slowly on mobile. So, verify that your theme is responsive & loads fast on mobile devices.
### 3. Too Many Plugins (& Heavy Plugins)
Plugins add functionality to your site. But at the same time, having too many of them will slow it down. So why does it happen, and how to solve this problem?
#### Why This Happens
- Every plugin adds code to your site that needs to load.
- Some plugins run too many database queries per page load.
- Conflicting or old plugins can break performance.
#### How to Fix It
- Audit your plugins regularly. Go to **Plugins > Installed Plugins** on your WordPress dashboard, and uninstall any of them that you don't need. Do make sure that no feature on your website is dependent on them, so the site doesn’t break.
- Replace heavy plugins with lightweight alternatives. For example, Jetpack is really heavy, as it has multiple features in one plugin. So, unless you need all the features, find and use lighter plugins for specific use cases. The same goes for heavy form plugins or even heavy performance-related plugins!
- Update plugins regularly. Old Plugins can not only be a security risk, but they can also slow your site down.
### 4. Not Caching the Pages
When someone visits your site, their browser pulls data from your server every time. It’s a time-consuming process and slows down your website.
But this repetition can be avoided with caching.
#### Why This Happens
- A server must process several database queries before showing a page each time.
- Without caching enabled, your site reloads everything for every visitor, increasing load time.
- High traffic can make things even slower on the server.
#### How to Fix It
- Having caching turned on makes sure that webpages the visitors have browsed already are cached on the user's browser, so they don’t need to be loaded from scratch each time.
- Plugins like WP Rocket, W3 Total Cache, or LiteSpeed Cache Cache static versions of your pages so they load faster for repeat visitors.
- Some hosting providers like Levamo have caching built in specifically for WordPress. In this case, you don’t even need to have a caching plugin.
- If your site has lots of dynamic content, enable Redis caching to store database queries in memory to speed up performance.
### 5. Not Minifying the Code
HTML, CSS, and JavaScript are the codes used to build your WordPress site. However, bloated or inefficient code takes longer to load if they are clogged with spaces, comments, and other unnecessary characters.
#### Why This Happens
- If the theme and plugin don’t have efficient code, they can produce huge files.
- Any extra line of code can also transfer more data.
- If scripts are not minified, they load individually and create multiple server requests.
#### How to Fix It
- Use a plugin like Autoptimize or WP Rocket to compress and optimize your code.
- Make sure that the JavaScript loads asynchronously so it won't block other elements from rendering.
- If you are using a theme with built-in features you don't need, disabling them also helps reduce unused code from your website.
### 6. Heavy & Unoptimized Images
High image quality is great for looks, but unoptimized or higher-resolution images can slow down your website.
#### Why This Happens
- Uploading large uncompressed images increases page size and load time.
- Using old and heavy image formats such as PNG instead of JPEG or WebP may make an image file too heavy.
- Not enabling lazy loading means images load at once when visitors load a page, instead of only loading when needed. This also makes pages slower.
#### How to Fix It
- Compress images with plugins like Smush, ShortPixel, or Imagify. These plugins can compress Images without quality loss.
- Use modern and lightweight image formats. Converting images to WebP or JPEG (smaller files than PNG) makes image loading faster.
- Lazy loading makes sure only images on the screen load initially, and the rest of the images load when users scroll down the website. Most caching plugins like WP Rocket support lazy loading.
- Resize images before uploading. Instead of uploading high-resolution images, resize them to the suitable dimensions before uploading them to your site. This will ensure a faster loading time.
### 7. Using a Backdated PHP Version

Like many other platforms on the internet, WordPress runs on PHP. Newer versions of PHP are faster, more secure, and more efficient. Your website will suffer in case your hosting company still uses an old version of PHP.
#### Why This Happens
- Many web hosts don’t update PHP versions automatically, so sites remain on older, slower versions.
- Most website owners also do not realize PHP updates are necessary and never check their version.
- Older PHP versions lack both performance optimizations and security patches.
#### How to Fix
- Check your PHP Version In WordPress by going to **Tools > Site Health > PHP Version**. Operating PHP 8.0 or even higher is recommended.
- You can update PHP from your hosting panel from time to time. Most hosting providers let you check and update PHP from Your Control Panel (e.g. cPanel, Plesk, or custom dashboards like Levamo’s Custom Dashboard).
### 8. Not Using a CDN (Content Delivery Network)

If your site uses just one server, visitors far from that server will experience slower loading times. But there’s a way out of it. Let’s talk about why it happens and what the solution is.
#### Why This Happens
- Normal websites load files directly from the main server. This can be slow for users far away.
- With no CDN, every request goes to the same data center, causing server overload.
#### How to Fix It
- Use third-party CDN service platforms like Cloudflare to store copies of your site on many servers worldwide so users get the fastest loading time.
- You can also use a hosting like Levamo that offers a free WordPress CDN so that you don’t have to use third-party solutions. Some other premium hosts also offer a free or premium built-in CDN.
- Once you have a CDN in place, it can not only serve the website from the nearest server location to a visitor but can also make media files optimized to load faster.
### 9. Ads and Pop-Ups
Ads and pop-ups can help you monetize your site, but too many of them can also slow it down. Especially if you use ads from ad networks that use outside scripts. And also, if you use too many, or heavy popups.
#### Why This Happens
- Ad networks download scripts from third-party servers. This increases outgoing HTTP requests and slows down your website.
- Some ad platforms don't optimize their scripts, which causes long loading times for your webpage.
- If you have heavy or multiple pop-ups on your webpage, they also require extra JavaScript processing and delay page rendering for the visitor.
#### How to Fix It
- If you depend on ad revenue, focus on fewer, better Ads instead of lots of poor ones. You can register for prominent ad networks like **Google AdSense**.
- Try optimized plugins like **Advanced Ads** instead of bloated Ad plugins to speed up script loading.
- Turn on lazy loading for ads, so that they wait to load until the user scrolls down. This prevents all ads from loading at once, even if the user is staying just above the fold.
- Consider displaying static ads instead of animated ones. GIFs, video Ads, and heavy animations use more resources than static banner Ads.
- Don’t use too many pop-ups on the same webpage. Also, make sure to display simple pop-ups and lightweight optimized images on the pop-up.
### 10. Not Cleaning Site Database Regularly
Your website database stores everything from your posts, pages, comments, plugin settings, and old revisions. Over time, this data gets big and clunky, so your database queries also become slow & inefficient.
#### Why This Happens
- Any revision of a post, deleted comment, or spam entry remains in the database unless manually cleaned.
- Plugins or themes that keep residual data or logs might also add bloat data.
- A clunky database takes longer to retrieve or process data, which affects site performance.
#### How to Fix It
- Regularly optimize your database. You can do that by removing unused data, old post revisions, and spam comments with a plugin like **WP-Optimize** or **Advanced Database Cleaner**.
- Delete unused plugins and themes, because even deactivated Plugins can create database entries that slow things down.
- Schedule a monthly database cleanup, whether it is manual or using a plugin.
- By default, WordPress saves many versions of a Post. You can limit them by adding this line to your **wp_config.php** file:
`define( 'WP_POST_REVISIONS', 3 );`
## Tools to Check Your WordPress Site Speed
After you make the changes we suggested, you should check your WordPress site speed again. This will help you measure how your site is performing now, so you can make further improvements if needed.
There are a lot of tools that help you check your WordPress site speed, and these are the ones that are most popular:
1. **[Google PageSpeed insights](https://pagespeed.web.dev/)**: Developed by Google, this is the most popular tool to analyzes both mobile and desktop performance. It is also completely free to use.
2. **[GTmetrix](https://gtmetrix.com/)**: This is another tool to check your WordPress site speed. It breaks down your page load speed by detailed analysis and optimization recommendations.
3. **[Pingdom](https://www.pingdom.com/)**: With this tool, you can check your site speed from around the globe.
4. **[Query Monitor](https://wordpress.org/plugins/query-monitor/)**: This is not directly a site speed checking tool. But it’s a very WordPress plugin for identifying what queries are slowing down your website, and the problematic plugins.
## Conclusion
A slow WordPress site is frustrating for both you and your visitors. But as you can see from this article, you can actually fix it without much complexity!
By optimizing your theme, plugins, caching, images, and database, you can achieve significant improvements in your website speed and performance.
The key is to take a systematic approach, as we showed in this article. And you will be surprised to see that even small changes can make a big difference!
If you want to see a dramatic increase in website speed and solve a lot of these issues without handling them manually (like enabling website caching, optimizing images, or installing a CDN), opt for **[Levamo](/pricing/)** hosting. It is the fastest-managed WordPress hosting on the planet, thanks to its powerful performance-oriented features such as a highly-complimented LiteSpeed server, effective Redis Caching, free WordPress-focused CDN that you can enable in one click, and many more.
## Frequently Asked Questions

### How to speed up my WordPress site?
Here’s a quick guide to improve your WordPress site speed:
- Use a CDN.
- Pick a fast hosting provider like Levamo.
- Choose a lightweight theme like Astra or GeneratePress.
- Enable caching.
- Optimize media files.
- Minify CSS and JavaScript codes.
### How slow is my WordPress site?
A WordPress site may be slow because of poor hosting, too many plugins, heavy themes, large images, no caching, an unoptimized database, or old PHP versions. You can find out how severe the problem is, by checking the website speed with Google Pagespeed Insights or GTMetrix.
### How do I debugger a slow WordPress site?
- Check site speed with Google Page Speed, GTmetrix, and Pingdom.
- Try Query Monitor plugin to see which plugins or queries are slowing down your website.
- Deactivate all plugins and reactivate them one by one to see if one is causing the problem.
- Check if the theme is stalling things.
- Check response times of servers, your host can also be the problem.
### Are WordPress websites slow?
Like any website, WordPress is fast if it’s optimized. A good WordPress site with fast hosting, caching and proper server and code optimization may load in seconds.
### How to speed up WordPress site without plugins?
- You can use this quick fixes instead of plugins:
- Activate browser caching by editing your [.htaccess file](/blog/wordpress-htaccess/).
- Compress images with Tinypng before uploading to optimize them manually.
- Pick a light theme, not a heavy one.
- Switch to a better hosting.
---
## How to Increase Maximum Upload File Size in WordPress
- URL: https://levamo.com/blog/wordpress-increase-upload-size/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-04-03
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix the WordPress upload size limit! Upload files easily.
If you build or manage a WordPress site, you'll need to upload files at some point.
They can be large images, videos, PDFs, or even plugin or theme files.
Now imagine when you go into the WordPress dashboard and try to upload, you get this annoying error message:
**“File exceeds the maximum upload size for this site.”**
This frustrating error message is a very common issue for WordPress users.
But the good news is that WordPress is really flexible, and there are several ways to perform a WordPress increase upload size action.
In this article, I’ll help you check your current WordPress maximum upload size and walk you through the process of how to increase the maximum upload size limit in WordPress effectively.
Let's begin!
## How to Check Your Current WordPress Maximum Upload Size
Knowing its current limit is important before you increase your site's upload size limit. Below are the most common and fastest ways to check the maximum upload size limit.
### 1. Check in the WordPress Media Library
A simple method is to:
- Log in to your WordPress Admin Dashboard.
- Navigate to **Media > Library**.
- Click on **Add New**, and it will bring up the uploader option.
Under the file selection option, you should see a message like:
**“Maximum upload file size: 60 MB.”**

The value may be "2 MB," "64 MB," "128 MB," or more, depending on your host defaults and any modifications you may have made already.
### 2. Use the Site Health Info Screen
From WordPress 5.2, Site Health also gives you information about your site's environment. This also includes your file upload limit.
**To view it:**
- From your WordPress admin dashboard, click **Tools > Site Health**.
- Click on **Info**.
- Select Media Handling. See the size of an uploaded file to see the current WordPress limit.

## How to Increase Maximum Upload File Size in WordPress
Now let’s share several ways to perform a WordPress increase upload size update. You only need **one** method to work, so feel free to skip around if your hosting environment doesn’t allow a particular approach.
### 1. Update Your .htaccess File
In case your web server is running Apache (common on many shared hosting environments) you are typically able to increase the upload limit by editing the .html file. This file is generally found in your WordPress website’s root directory (the same folder containing wp-config.php and wp-admin, wp-content, wp-includes folders). This is a direct way to increase upload size in WordPress through server configuration.
Here’s the process:
- Access the .htaccess file by way of FTP (or the File Manager in your hosting control panel).
- Backup this file prior to editing it. This is important because .htaccess can be extremely sensitive and errors can happen because of incorrect modification. In that case, you might need the backup file.
- Change.htaccess as described below in a text editor or even a code editor:
```apache
php_value upload_max_filesize 32M
php_value post_max_size 64M
php_value memory_limit 128M
php_value max_execution_time 300
php_value max_input_time 300
```
- **Save the changes** and close the file.
Your brand-new upload limit should now be in place if your server is reading .htaccess correctly. In case you get a [500 Internal Server Error](/blog/fix-the-500-internal-server-error/), your hosting might be using PHP in CGI mode, so .htaccess cannot override those settings.
If that happens, delete those lines and try another way below to restore your site.
### 2. Modify the php.ini File
Many hosts set default PHP values, such as upload size limits in a php.ini file.
The php.ini file:
- Maybe in your site's root folder, inside a folder like /etc/php/7.4/fpm/, or in a different directory,
- May have a name slightly different from php.ini or user.ini depending on the host configuration.
Once you find the php.ini file, follow the steps below:
- Open the php.ini file with FTP or your hosting control panel's file manager.
- Search for directives like **upload_max_filesize**, **post_max_size**, and possibly **memory_limit**. If they are missing, then create such files.
**Set their values**, for example:
```ini
upload_max_filesize = 32M
post_max_size = 64M
memory_limit = 128M
max_execution_time = 300
max_input_time = 300
```
- **Save** the file and exit.
The changes could cause your server to restart PHP-FPM or Apache. Look in your hosting control panel for a Restart Services option (usually under Restart PHP or Restart Apache). If not, changes might just roll back after a brief delay. You can also ask your hosting provider to restart the services.
### 3. Modify the .user.ini File
In your WordPress root directory, you may find a file called user.ini on some hosting platforms, especially those that prefer user-level overrides instead of global PHP.ini changes. If it is missing, you can create it. To perform a WordPress increase upload size action:
The process is almost identical to editing php.ini:
- **Locate** or **create** a .user.ini file in your site’s root directory.
**Add or modify** the same directives:
```ini
upload_max_filesize = 32M
post_max_size = 64M
memory_limit = 128M
max_execution_time = 300
max_input_time = 300
```
- **Save the file**.
See if those changes took place by visiting **Media > Add New** in your WordPress dashboard. Still no updated limit? Check with your host that .user.ini overrides are allowed on your plan
### 4. Modify PHP Options via cPanel
If your host supports cPanel You may be able to increase the WordPress max upload file size via a graphical interface, no editing code or config files required. While designs may differ by cPanel version, typical steps are:
- **Log in to your cPanel dashboard.**
- Find the **Software** section and click on **Select PHP Version** (or a similar option).
- In the new screen, look for **Options** or **PHP Options**.
Within that interface, you should see a list of PHP directives, including:
- **upload_max_filesize**
- **post_max_size**
- **memory_limit**
- **max_execution_time**
- **max_input_time**
Adjust these values to the new limits you want. Check that the post-max size is larger or equal to the upload-max size. Also, make sure your memory limit is high enough to handle new file sizes. Click the save button if your cPanel has one. Otherwise, changes might be saved automatically.
**Note:** cPanel might place upper thresholds that match your hosting plan. In that case, to set a higher limit, you'll need to upgrade or contact support for a custom solution.
### 5. Increase the Max Upload File Size in Nginx
If your hosting environment uses Nginx instead of Apache, you must do the process a bit differently to increase file size limits. You have to modify both the php.ini and the Nginx configuration file (nginx.conf) as Nginx enforces its own limit via the **client_max_body_size** directive.
**Step 1: Update** php.ini
Locate your php.ini file, often found in /etc/php/7.4/fpm/php.ini (the exact path may vary).
Set your desired values:
```ini
upload_max_filesize = 64M
post_max_size = 128M
```
Save the file.
Restart PHP-FPM by using this command:
```bash
sudo service php7.4-fpm restart
```
*(Adjust the command for your PHP version as needed.)*
**Step 2: Update** nginx.conf
Find nginx.conf, typically in /etc/nginx/nginx.conf.
Inside the http {} block, the server {} block, or a specific location {} block, add or modify:
```nginx
client_max_body_size 128M;
```
Save the file.
Restart Nginx with the following command.
```bash
sudo service nginx reload
```
You need to contact your hosting provider to have your website’s **client_max_body_size** value changed, if you're hosted on a [fully managed wordpress hosting](/managed-wordpress-hosting/) platform.
### 6. Use the WordPress upload_size_limit Filter
WordPress itself has a built-in filter, upload_size_limit. You can use this to also define or override the maximum upload file size limit. This is the limit that is usually shown on the Media Library when you try to upload media.
Here's the code snippet to customize that.
```php
function filter_site_upload_size_limit( $size ) {
// 10 MB.
return 1024 * 10000;
}
add_filter( 'upload_size_limit', 'filter_site_upload_size_limit', 20 );
```
To use this code snippet:
- Copy and paste the code snippet to your **theme’s** functions.php file or use a code editor plugin.
- Adjust the numeric value that we shared to match your desired file size limit.
Note: If your server-side limit is lower than the one you set, you will get the highest limit your server is offering. So you have to consult your hosting provider again to increase your server limit.
### 7. Upload Files via FTP/SFTP
Almost all of these methods consist of some level of code tweaking. And I understand that you might feel a bit scared to customize the codebase and unintentionally break your site. You can actually avoid the code tweaking, by directly uploading from FTP/SFTP.
Here’s how to do that:
- **Set up an FTP/SFTP connection** with a tool like FileZilla. You’ll need your FTP credentials (host, username, password, and possibly a port number).
- **Connect** to your web server.
- **Navigate** to your WordPress wp-content/uploads folder (or whichever folder you’d like to store your files in).
- **Drag and drop** the large file from your local computer to the folder on your server.
This places the file on your server but it won't appear in the WordPress Media Library by default. Install a plugin like **Add From Server** that will recognize your large file as a file that WordPress can insert into posts and pages. This plugin searches your server for files and imports them into the Media Library. Or you can use **WP-CLI** commands (media import).
Changing file size limits is often the easiest workaround for many users with FTP/SFTP. Especially useful if you rarely upload large files and don't want to fuss with server configurations.
### 8. Increase the Max Upload File Size for WordPress Multisite
WordPress Multisite environments add another level of configuration. You can set a global maximum upload limit for all subsites if you run a network of sites under one WordPress installation, or override it for specific subsites.
**Access Network Admin:**
- Go to My Site > Network Admin > Dashboard in the WordPress toolbar if you're logged in as a Network administrator.
**Go to Settings:**
- Go to Network Settings from the Network Admin dashboard.
**Find “Upload Settings”:**
- Look for the upload file size. The default is often around 1500 KB (1.25 MB), but You can change it to 131072 KB (128 MB).
- **Save Changes.**
Remember that server-level limits override any Network Settings you set. If your server is capped at 32 MB and you set 128 MB in the Network Settings, uploads will still fail above 32 MB. You’ll need to ensure your server’s settings (in php.ini, .htaccess, or .user.ini) match or exceed the value you put in your Network Settings.
### 9. Increase the Upload Size with a WordPress Plugin
Does modifying config files, or some coding here and there seem intimidating for you? Luckily, there are plugins that will increase the upload file size for WordPress if your host allows it. One of the most popular plugin that we recommend is the **MaxUploader** plugin.
- In your WordPress Admin, go to **Plugins > Add New**.
- Search for **MaxUploader**.
- **Install** and **Activate** the plugin.
- Go to its **Media > Increase Upload Limit**.
Inside the plugin’s interface, you’ll see the option called “**Choose Maximum Upload File Size**”, change it as needed.

**Please note that:** You can only change the upload file size limit here if your hosting provider allows you to change it. In the event that your hosting providers cap the hosting environment with a lesser value, the plugin can not override this.
For many site owners, particularly those on flexible hosting, this plugin approach is the easiest.
### 10. Contact Your Hosting Provider Support
If you adjust .htaccess, php.ini, user.ini, or other options but still can't increase the maximum upload limit, your hosting provider probably has a cap imposed by default. Shared hosting providers usually do this to protect their servers from resource abuse.
Or maybe you just want to get into any technical hassle.
In any of these cases, contact your hosting support to perform a WordPress increase upload size adjustment on your account. Many hosts will adjust limits quickly for you if your plan allows that. Some hosts will want you to upgrade your plan for large file handling.
## Wrapping Up
The "exceeds the maximum upload size" error is annoying if you have no idea why this is happening and how to solve it.
But as you saw from this article, thankfully there are easy ways to safely increase WordPress upload size.
Applying any one or all of these will allow your site to handle larger files, like uploading a plugin, a huge image gallery, a new video background, or any other asset you need.
But before you do these, do not forget to back up your critical configuration files at all times. So that you can always restore your site if something goes wrong.
You should be able to easily upload large files once you get your server and WordPress setup right. If you are still facing any problems or have any questions, don’t hesitate to ask us in the comments section below.
## Frequently Asked Questions

### How to increase max file upload size in WordPress?
Customize your htaccess, user.ini, and php.ini. file from your hosting control panel to increase the maximum file upload size for WordPress.
You can also simply upload from your FTP/SFTP, or you can use plugins like **MaxUploader**.
### How do I upload a large file to WordPress?
For a quick fix, uploading the file from FTP/SFTP directly to your wp-content/uploads folder is the fastest way.
Or you can change the.htaccess, .user.ini, and php.ini in your hosting control panel to increase the upload limit.
### How to increase upload_max_filesize in php.ini?
To increase the upload_max_filesize directive in php.ini:
Locate your php.ini file (possibly found in /etc/php/7.4/fpm/ or /public_html/).
Open it in a text editor and search for upload_max_filesize. If not present, add it manually.
Set it to the desired value, for example: upload_max_filesize = 64M.
Make sure post_max_size is equal to or larger than that same value (post_max_size = 64M or more).
Save the file and restart your PHP or web server if needed.
### What is the maximum file size for WordPress media library?
There is no certain limit for maximum file size, it depends on your hosting provider and the hosting plan you have.
---
## FormGent: the AI-powered form builder that’s shockingly generous
- URL: https://levamo.com/blog/formgent-review/
- Category: website-development
- Author: Faisal Sarker
- Published: 2025-04-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
FormGent offers AI form building that's shockingly generous. See why now.
There are tons of plugins available on the WordPress marketplace and every week a few more are being added to that list. The most common ones are widgets, add-ons of popular plugins and page builder extensions. Needless to say, there’s no shortage of form builder plugins either.
Contact forms are the most essential component of any website. Every website contains at least 1 contact form if not more. Whether you want to capture leads, collect feedback or take appointments and online booking, you need multiple forms on the site. As WordPress powers the world's 43% websites alone, the uses of contact form plugins are also vast in them.
The most popular ones alone are powering millions of websites. Then comes less popular ones that are powering thousands. Then we see a number of new plugins launching on the market with new innovations trying to kill the giants in many ways. Last month, one of such plugins was launched officially. The plugin is called [FormGent](http://formgent.com) and it’s biggest strength is, it is FREE!
## The Power of a Free Form Plugin
There are many more free WordPress form plugins available in the ecosystem. So what makes FormGent special in this category? Though I mentioned earlier that the Free tag is its biggest strength, it is not the only strength of this plugin. You might be wondering what other strength this plugin holds. Allow me to explain this.
There are a number of features that FormGent is offering on the free plan for which typically most WordPress form plugins will charge you. They have a handful of features which are not free just for the sake of giving. To name a few; AI form creation (though limited), conversational form, multi-step form, advanced show/hide based on conditional logic, form submission data and analytics, integrations etc.
It is safe to say; FormGent is like a powerful free form builder plugin. The power that comes from being WordPress’s native builder-based. Most newbies can use it without learning new technology using Gutenberg block builder that comes as default in WordPress. Simply put, it’s lightweight with zero learning curve but highly advanced.
But does it really live up to the hype? In this blog post, we’ll dive deep into the nuts and bolts of FormGent. At the end, you will know why FormGent makes noise out of the box.
So, without further delay, let’s dig deeper into the realm of FormGent.
## FormGent at a Glance
Include Video Here: [FormGent Explainer](https://www.youtube.com/watch?v=qpzpK_RSgh8)
FormGent is a WordPress form builder plugin that has recently launched V 1.0.0 with a complete feature set and numerous plans. The Free plan contains most useful features that are essential to building highly functional multipurpose forms. Then they have premium plans of various durations that offer a very affordable fee but highly advanced functionalities.
So what does FormGent actually do? In plain language: it helps you make smart, usable forms quickly. Contact forms, multi-step surveys or job application forms, conversational “one question at a time” forms, quizzes and payment forms - you name it. If you want to build your own, choose to start from scratch. Or, if you prefer, tell the AI what you need and it generates a working form for you.
### Key features that matter in real world
- **Conversational Form Creation:** Boost engagement and completion with one-question at a time style step by step forms that feels more like a conversation. Ideal for: customer feedback, quizzes or lengthy surveys.
- **Multi-step forms:** Break long and boring forms into multiple steps, empower users to autosave responses with each step completed and enhance completion rate. Ideal for job or loan application, visa processing or university admission type cases.
- **Conditional Logic:** Show or hide questions based on users' responses. Tailor each form based on the user's preference so that they do not feel annoyed filling out unnecessary fields.
- **Quiz:** You can set score and grade on users' responses, allowing them to play interactive quizzes. Ideal for bloggers who monetize through ads and long user sessions help them earn more.
- **Payment:** Integrate your form with PayPal or Stripe to build a powerful and customized payment form. You can also include custom payment amount fields to build a highly functional e-commerce checkout form.
- **AI form creation:** Utilize the power of AI to build any form with simple prompts. No need to spend time building your form from scratch. Allow AI to build one for you, you can customize it and save time.
- **Advanced Integrations:** FormGent allows free integration with advanced and popular tools like Zapier, Google Sheets, Zoho, MailChimp, Slack and many more upcoming to automate task flows.
- **iFrame embed:** The iFrame embed is something that FormGent claims to have as an unique feature. Even outside WordPress, you can launch and embed your forms using an iFrame and the embed code.
- **Instant URL:** Beside the embed code, FormGent forms can be launched using shortcodes (common feature) and instant URL. The instant URL works in sharing forms without embedding or publishing on any particular place.
FormGent claims to have 20+ input fields including all essential fields you need to create any kind of forms. Some advanced fields such as file uploads, Google Maps, input masking, repeater fields, date and time picker, rating scale included in the free plan are the key highlights of the plugin.
## Templates that save you Setup Time

Building a form from scratch is fine once or twice, but if you’re doing it every week, it’s stressful. That’s where FormGent’s template library comes in.
Instead of staring at a blank form, you can start with a ready-made structure designed for common use cases. These aren’t just “contact us” or “newsletter signup” - the library covers a wide mix of everyday needs:
- **Business basics:** Contact forms, Lead capture forms, Quote requests.
- **Education & learning:** Quiz builder templates, Lesson idea forms, Feedback forms.
- **Events & organizations:** Registration forms, Donation forms, Volunteer signup.
- **E-commerce & services:** Order forms, Payment forms (with PayPal/Stripe), Booking requests.
- **Surveys & feedback:** Customer satisfaction, polls, rating scales.
Each template comes pre-configured with relevant fields, conditional logic, and multi-step layouts where they make sense. That means you can spend your time tweaking the details like branding, colors, AI-generated copy etc. instead of figuring out what fields you need in the first place.
It’s a workflow booster. Instead of reinventing the wheel, you stand on top of a library built by the FormGent team, then customize for your client or project.
## Plans and Pricing

FormGent’s marketing leans heavily on an accessible model. The homepage and plugin listing stress a powerful free tier that includes many advanced features while the site also promotes limited early-bird / lifetime deals for pro plans. Try it for free and scale up only if you want the extra bells or a lifetime licensing option.
FormGent’s pricing is set up to make it really easy to start free, then upgrade only if and when you need extras. Here’s how it breaks down:
#### Free Plan
This isn’t one of those “fake” free tiers that barely do anything. The free plan includes 20+ fields, conversational and multi-step forms, the AI form builder (limited), conditional logic, templates, quiz builder, payment system, file uploads, repeaters, spam protection, iFrame embeds and calculations, reporting, and more. It’s basically “way more than basic,” as the FormGent team puts it.
If you’re just testing the waters or building regular forms, you could realistically run on the free plan for a long time without feeling boxed in.
#### Starter (1 Site) - $39/year (Early Bird Offer)
This one’s built for solo entrepreneurs or single-site businesses. It adds on things like white labeling, digital signatures, unlimited AI forms, saving incomplete submissions, webhooks, analytics, and priority support. Some “upcoming” features (like AI Form Assistant and user CPT submissions) are flagged here too.
The headline price is $49/year, but during the early bird promotion it’s $39/year.
#### Standard (10 Sites) - $59/year (early bird)
If you’re a freelancer or developer handling multiple client sites, the Standard plan probably makes more sense. It’s basically the same feature set as Starter but for up to 10 sites. Normal price is $99/year, but the current deal brings it down to $59/year (40% off).
#### Lifetime (Unlimited Sites) - $159 once (early bird)
This is the “agency” plan. One-time payment, no renewal. It covers unlimited sites and includes all the premium features: white labeling, digital signatures, unlimited AI forms, saving incomplete data, analytics, webhooks, priority support, and the upcoming AI assistant.
The regular price is $399, but during early bird it’s just $159. That’s a true LTD (lifetime deal), not just a long renewal cycle.
### A few extras worth noting:
- 14-day money-back guarantee if you want to try pro features risk-free.
- No locks in the LTD: all future updates and support are included.
## Security and Privacy at its Core
One of the less glamorous but super important sides of form building is compliance and security. It’s not just about “will my form look good?” but it’s also “can I trust the data coming in?” and “am I protecting visitors from shady stuff?” FormGent leans into that with a few thoughtful touches.
#### GDPR and consent
You can add consent fields to make sure you’re collecting data in a way that lines up with GDPR requirements. That’s a big deal if you’re serving visitors in the EU (or if you just want to avoid headaches later).
#### Spam filters built in
We all know what happens when you run a contact form without protection: bots flood it with junk. FormGent includes multiple layers to stop that:
- Traditional honeypot fields (simple but effective).
- reCAPTCHA support for those who want Google’s service.
- hCaptcha and Cloudflare Turnstile support if you’d rather avoid Google or want extra flexibility.
That gives site owners a choice depending on their privacy stance or what their audience prefers.
#### File upload safety
Since the free plan even includes file uploads, it matters that FormGent treats that as a secure channel. Combined with spam filters and reporting, it reduces the risk of bad actors sneaking through your forms.
#### Reports and transparency
FormGent includes reporting and analytics, even on the free plan. That’s not just nice for data visualization; it helps you audit submissions, track suspicious activity, and show compliance if a client or regulator ever asks.
#### Data handling
Collecting form entries is one thing. Doing something useful with them is another. FormGent doesn’t just let submissions sit in your WordPress dashboard only, it gives you tools to export your data in the formats people actually use day to day: Excel, CSV, and PDF.
All of this means you don’t have to duct-tape together third-party spam plugins or wonder if your form setup passes muster in regulated markets. With FormGent, the essentials are already thought through; you just switch on the level of protection that makes sense for your site.
## Final Thoughts: Why FormGent Feels Different
FormGent has grown from an interesting AI tool to a full-featured WordPress form builder. With the 1.0 release, a generous free plan, and practical upgrades like payments, quizzes, exports, and integrations, it’s no longer just another plugin in the crowded forms market.
What makes it stand out isn’t just the AI builder or conversational forms (though those are strong hooks). It’s the way FormGent combines modern features with fair pricing and a WordPress-native experience. You’re not fighting with a bulky interface or paying extra for every small feature anymore, essentials are already there.Whether you’re a freelancer testing forms on client sites, an agency looking for unlimited installs under a lifetime deal, or just someone who wants a solid free form builder, FormGent fits. The features are mature, and the team is clearly investing in making it better. Now it’s just about trying it out. [Start free](http://formgent.com/pricing), build a form, and see how fast you can go from idea to working form.
---
## Ready to Break Up with Elementor Pro? Here's What It Actually Takes (and Costs)
- URL: https://levamo.com/blog/elementor-pro-alternative/
- Category: website-design
- Author: Faisal Sarker
- Published: 2025-04-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Ditch Elementor Pro? See the costs & steps for a smooth WordPress site divorce.
If you’ve spent even a few moments building WordPress sites, you’ve likely run across Elementor Pro. It’s a tried-and-true option - thanks to its simple drag-and-drop builder and a large collection of widgets, it’s easier than ever to get up and running with a complicated site without writing a single line of code.
The problem is that simplicity comes with some strings attached. An increasing number of developers and site owners are starting to feel the pressure - be it the annual subscription fees, the slow-loading site due to plugin bloat, or the growing reliance on third-party extensions. So when you add it all up, the long-term value of Elementor Pro is starting to look a bit less attractive.
And what if you’re using high-performance hosting like Levamo, where speed and optimization are everything? Your choice of builder isn’t just about features anymore; it’s about making sure your setup runs as lean and as fast as possible.
So in this post, we’ll uncover the real price of Elementor Pro, in terms of both dollars and headaches over the longer haul - and introduce a new, more clever Elementor Pro alternative that’s turning heads: **Jupiter X**.
## Everything You Need to Know About Elementor Pro
### 1. Dependency & Lock-In
At its best, building and maintaining a WordPress site using Elementor Pro is a dream - the page builder’s visual building blocks and flexible tools allow for a fast, code-free workflow. But that reliance can easily become a problem if you ever think about shutting it down. Elementor Pro doesn’t merely add features to your site; it becomes part of its very foundation. Disabling it often results in broken layouts, missing widgets, and leftover empty sections or shortcode fragments.
Unlike standard plugins that add standalone features, Elementor Pro is deeply ingrained into your pages. If you turn it off, headers and footers might disappear, popups might stop working, and layout structures might break down - leaving your site essentially unusable.

*Think about what it would be like to be locked out of something as critical as Theme Builder - your entire site’s layout control - just because you canceled your subscription.*
There’s also a hidden time cost. Since [Elementor review](/blog/elementor-review/) saves both your content and styling within its system, removing it won’t restore your content to clean WordPress formatting. This leaves you with two choices:
✔ **Continue paying for the subscription**
✔ **Spend hours (or days) rebuilding your site using another tool or the native block editor**
This deep integration is Elementor Pro’s greatest strength - and its biggest risk. While it gives non-developers more control, it does so at the cost of flexibility. If long-term sustainability is a concern, this type of vendor lock-in can quickly become a major roadblock. And this should naturally bring the consideration to use an Elementor Pro alternative.
### 2. Recurring Costs Add Up Quickly
Elementor Pro runs on a subscription model, which means the costs aren’t a one-and-done situation. You’re on the hook every year, and if you’re managing multiple websites, those charges multiply fast.
What starts as a manageable fee for a single site can balloon quickly when scaled across a growing portfolio. And with pricing tiers that increase based on site count, you’re essentially paying more just to maintain access to the same features you’ve already built your site around.

### 3. Plugin Bloat & Performance Overhead
Another common pain point? Plugin overload. Users often find themselves layering on additional third-party plugins to plug feature gaps that Elementor Pro alone doesn’t cover:
- **CartFlows** or **CheckoutWC** for building sales funnels in WooCommerce
- **Happy Addons**, **Unlimited Addons**, or **[Crocoblock](/blog/crocoblock-review/)** to get extra widgets and styling options
- **YITH plugins** for advanced eCommerce tools like swatches or upsells
Each of these adds scripts, styles, and more backend strain. That means more memory usage, more server calls, and ultimately - slower load times. For high-performance hosting providers, this bloat chews through resources, often dragging down the very speed and SEO scores site owners work hard to optimize.
If your site leans on Elementor Pro plus a handful of these add-ons, it may underperform on speed audits like Google PageSpeed Insights or GTmetrix. The more complex your plugin stack, the heavier your site becomes - and that can directly impact both rankings and the user experience.
## Jupiter X: One-Time-Fee Option
Jupiter X is a multi-purpose WordPress theme powered by Elementor that eliminates the need for Elementor Pro entirely. Developed by Artbees, it combines a powerful, performance-optimized core with a broad set of native tools and integrations. It is fast becoming the go-to solution as Elementor Pro alternative for developers and site owners who value freedom, speed, flexibility, and cutting waste.

### 1. One-Time Payment, Full Access
Jupiter X’s biggest selling point is its pricing - one $58 payment gets you everything. No subscriptions, no annual renewals - just complete, permanent access. If you manage several websites or work with multiple clients, that’s a serious long-term saving.
### 2. All Elementor Pro Features - Natively
Jupiter X replicates - and in some cases, improves upon - the core functionality you’d normally have to pay for with Elementor Pro:
- **Layout Builder** (think of it as a Theme Builder alternative)
- **Form and popup builders**
- **Motion effects & animations**
- **Global styling and widgets**
- **Conditional display settings**
- **Custom code, font, attributes, icons, and more**
So, you still get full creative control, without being locked into Elementor Pro. Kinda makes sense to use this as an Elementor Pro alternative, doesn't it?
### 3. Includes WooCommerce Optimization Suite
For online stores, Jupiter X also comes bundled with **SellKit**, a powerful WooCommerce enhancement toolkit to increase order value, streamline conversions, and drive engagement and retention:
- **Custom Checkout Pages**
- **Sales Funnels & Order Bumps**
- **Personalized promotions** such as smart coupons, automated discounts and checkout notices
- **Built-in variation swatches**

These features help Jupiter X stand out as a comprehensive [WooCommerce theme](https://jupiterx.com/woocommerce-theme?utm_source=Levamo), removing the need for extra tools and plugins like CartFlows, CheckoutWC, or various YITH extensions.
### 4. Replacing Addon Libraries with Native Widgets
If Jupiter X is to be a proper Elementor Pro alternative, it should also have proper alternatives to the addons that Elementor Pro offers. And it actually does. Jupiter X also comes with its own **large collection of advanced widgets** such as Product Filter, Opt-in, Sticky Media Scroller, Team Members, Marquees, Content Switch, Accordions, Image Comparisons, Photo. Album, Rollers, Business Hours and more, removing the need for third-party libraries like:
- **Crocoblock**
- **JetElements**
- **Happy Addons**
- **Unlimited Elements**
Fewer plugins mean fewer compatibility headaches - and noticeably better performance.
### 5. Performance Built-In
Since Jupiter X consolidates what would normally require multiple plugins, your site stays lighter under the hood. Less bloat translates into:
- **Faster page load times**
- **Lower Time to First Byte (TTFB)**
- **Improved [Core Web Vitals](/blog/core-web-vitals-and-seo/)**
- **Reduced strain on your hosting resources**
If you’re on an optimized platform like levamo.com, this efficiency can make a real difference in both cost and performance.
### 6. More Premade Templates
Jupiter X offers **over 450 pre-made designs** - far more than Elementor Pro. For agencies and freelancers, that means faster turnarounds and more variety for client work.

## Final Thoughts: Rethinking Your WordPress Stack
There’s no denying Elementor Pro played a major role in modern WordPress design. But for developers, agencies, and serious site owners, its **cost, complexity and dependency** are becoming harder to justify.
Jupiter X offers a smarter [Elementor Pro alternative](https://jupiterx.com/jupiter-x-versus-elementor-pro?utm_source=Levamo). You can:
✅ Build advanced, dynamic WordPress sites
✅ Streamline and optimize WooCommerce
✅ Cut out unnecessary plugins
✅ Improve speed and stability
✅ Save hundreds - if not thousands - over time
And you can do all of that with just one lifetime license.
If future-proofing your WordPress setup and getting more out of your hosting plan is on your radar, Jupiter X is definitely worth exploring.
---
## How to Integrate Klaviyo with WooCommerce Stores?
- URL: https://levamo.com/blog/klaviyo-woocommerce/
- Category: ecommerce
- Author: Faisal Sarker
- Published: 2025-03-28
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Integrate Klaviyo & WooCommerce! Boost sales with our step-by-step guide.
Integrating your WooCommerce store with Klaviyo can unlock opportunities to enhance your email and SMS marketing efforts, allowing you to run automated targeted campaigns and boost sales.
But, how to integrate Klaviyo with WooCommerce, and are there any technical complexities involved? Well, afraid not, this comprehensive guide will walk you through the step-by-step process of Klaviyo integration with WooCommerce, ensuring a seamless connection that empowers your marketing.
## Preparation Before Integration
It is important to have the prerequisites ready for proper Klaviyo integration with WooCommerce:
- **Have active Klaviyo and WooCommerce accounts:** Ensure you have existing accounts with both platforms. If you have multiple Klaviyo accounts, log out of any you don't intend to integrate with WooCommerce.
- **Access to your WooCommerce/Klaviyo admin dashboard:** You’ll need admin access for both dashboards to install, activate plugins and configure settings.
- **Disable caching and redirect plugins (recommended):** Temporarily disable redirect plugins during the setup process. You can enable them after the integration is complete.
- **Ensure your WooCommerce store uses HTTPS:** Klaviyo requires your WooCommerce store URL to use HTTPS and have a valid SSL certificate.
- **Check system requirements:** Ensure your WordPress version is 5.0 or higher and your PHP version is 7.4 or higher.
## Installing the Klaviyo Extension in WooCommerce
The first step of Klaviyo integration with WooCommerce is to install the official Klaviyo for WooCommerce extension on your WordPress site. Here’s how to do it:
- **Install Klaviyo Plugin:** In your WooCommerce admin dashboard, go to **Plugins** in the left-hand navigation menu and click **Add New. Search for Klaviyo in the search bar. You should see “Klaviyo for WooCommerce” in the search results**. Click the **Install Now** button next to it.
- **Activate the plugin:** Once the plugin is installed, click **Activate** to enable the Klaviyo extension.
- **Access Klaviyo settings:** After activation, you can find the Klaviyo settings by navigating to **Marketing** in the left-hand navigation and then clicking on **Klaviyo**.
## Connecting Your Klaviyo Account
With the Klaviyo extension active, the next step is to link it to your Klaviyo account.
- Click **Connect Account** in the Klaviyo settings page in your WooCommerce admin.
- Log in to the Klaviyo account.
- **Grant approval** to the connection prompt.
- **Confirm account name:** On the integration settings page that follows, verify that the displayed Klaviyo account name is correct.
Once you’ve approved the permissions, your WooCommerce account is now connected to Klaviyo.
## Configuring Integration Settings
After successfully connecting your accounts, you can configure various settings to tailor the integration to your needs. These options allow you to control how data is synced and enable key features:
- **Add email marketing consent checkbox to your checkout page:** Check this box to automatically add an email marketing consent to your checkout page. Use the **Add email subscribers to this list** dropdown to choose the list where customers who opt-in during checkout will be added. If you haven’t created a list yet, you’ll need to do so in your Klaviyo account under the **Lists & Segments** tab.
- **Email marketing consent label:** Customize the text that appears next to the email consent checkbox using the **Email marketing consent label** field. The default is *Sign me up to receive Email updates and news*.
- **Add SMS marketing consent checkbox to your checkout page:** If you want to collect SMS subscribers, check this box. Note that SMS consent will not sync if your company is age-gated.
- **Select a list:** Choose the list for SMS subscribers from the **Add SMS subscribers to this list** dropdown. Consent is sent after the customer clicks *submit order* and the order is created in WooCommerce.
- **SMS marketing consent label:** Enter the text you want to display next to the SMS consent checkbox.
- **SMS consent disclosure text:** Provide the required TCPA compliance text. You can use the Klaviyo default or add your own.
- **Convert all currencies to one standard currency**
Check this box and select your desired currency. This will not affect previously integrated data and doesn't change your default Klaviyo account currency. Once you are satisfied with your settings, click the **Complete setup** button.
You can always go back and edit these settings by navigating to the **Integrations** tab in Klaviyo and selecting **WooCommerce**.
## Testing the Integration
After configuring the settings, it’s essential to test your WooCommerce integration to ensure data is being synced correctly. Here’s how you can do it:
- **Enter the email in the popup -** For any pop ups you have created, enter your email address to check if your sign up form is collecting emails.
- Click the **Sign me Up! Button** and head back to your Klaviyo account to see if the email address is captured.
## Post-Integration Troubleshooting Steps
Now that the connection is established, here are a few debugging tips to ensure you can troubleshoot while encountering errors:
- **Unable to Access the Orders API**
If you encounter an error message like "Unable to access the Orders AP. Please check connection settings and try again," it indicates an issue with the connection within WooCommerce that needs to be resolved.
To resolve this issue, reset the API call to the order count endpoint to find out the information that is passed on to Klaviyo regarding orders.
You can use the following cURL request and change the STORE_URL, CONSUMER_KEY, and CONSUMER_SECRET with your store’s address and WooCommerce login ID and password. This will resolve the issue.
`curl https://STORE_URL/wp-json/wc/v3/orders \-u CONSUMER_KEY:CONSUMER_SECRET`
- **HTTPS and SSL Issues**
It’s 2025, and not having an [SSL certificate](/blog/ssl-website-security/) on your ecommerce website is a surefire way of getting penalized by Google. Klaviyo only integrates with HTTPS, which means you should have a valid SSL certificate.
You can always get in touch with Levamo’s expert team to help you with SSL installation on your website.
- **To Avoid Functionality Disruptions, You May Need to Disable the Following Plugins: Plugin Name(s)**
When you receive this error, it means that one of the plugins installed in WordPress has malfunctioned, which is causing integration problems with Klaviyo. You will also see the plugin name that you can temporarily deactivate or uninstall and reinstall once the problem is resolved.
Mostly these are either caching or redirection plugins.
## The Best of Both Worlds
Klaviyo integration with WooCommerce store is a straightforward process that opens up a world of possibilities for your e-commerce marketing. Regularly test your integration and explore the various features offered by both platforms to maximize your marketing ROI.
To get the best of your site’s surge traffic during sale seasons, it is time to migrate to Levamo for world-class [fully Managed Hosting for WordPress](/managed-wordpress-hosting/).
## Frequently Asked Questions
### Does WooCommerce have a CRM?
WooCommerce is flexible in integrating with various marketing and tech stack tools, but does not have an in-built CRM.
### Does Klaviyo integrate with WooCommerce?
Yes, Klaviyo integrates seamlessly with WooCommerce.
### Can I integrate Klaviyo with WordPress?
If a plugin can integrate well with WooCommerce, it can also do so with WordPress. You need not necessarily have a WooCommerce site to use Klaviyo, as you can integrate it on your blog to run email and SMS marketing campaigns.
### How do I integrate Klaviyo with my website?
Install the Klaviyo for WooCommerce extension, connect your Klaviyo account and configure the desired integration options.
### How to embed a Klaviyo form into WordPress?
You first need to create the form in your Klaviyo dashboard under **Sign-up forms**. Then, get the embed code for the form and paste it into your WordPress site's HTML. It is better to use the Klaviyo for WooCommerce plugin to help manage and display these forms.
---
## Ready to Tackle WordPress Site Migration? Here's What You Should Know
- URL: https://levamo.com/blog/wordpress-site-migration/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-03-27
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WordPress migration woes? Avoid common pitfalls with our expert guide.
Let's face it - when you need to migrate a WordPress site, it feels a lot like moving houses. You've got all these files and databases instead of furniture, but the stress? Pretty much identical. Whether your current host isn't cutting it anymore or you're chasing better performance, [WordPress migration](/free-website-migrations/) doesn't have to be the nightmare many make it out to be.
I've seen plenty of attempts to transfer WordPress sites go sideways - sites disappearing for days, content vanishing into the digital void, settings getting scrambled. But with some planning and the right approach, you can avoid these headaches when you migrate WordPress to a new environment.
If your current host is being discontinued, moving quickly matters even more. Here's how to [migrate from StellarSites to Levamo](/migrate-from-stellarsites/) if that's the situation you're in.
## The Real Challenges of WordPress Migration (And How to Deal)
### **Downtime:** Keeping Your Site Live
Nothing's worse than your visitors hitting an error page while you're in the middle of a WordPress site transfer. The trick? Plan carefully. Set up a [staging environment](/blog/how-wordpress-sandboxes-help-developers-test/), schedule your move when traffic is lowest (hello, 2 AM on a Sunday), and triple-check everything before flipping the switch.
### **Data Protection**: Don't Lose Your Stuff
Your site contains years of content, customer information, maybe even sales data. Back everything up before you attempt to migrate your WordPress site. Seriously. Even experienced developers can mess up, and having a recent backup can save you from a full-blown crisis.
### **Plugin and Theme Compatibility**: Making Sure Everything Works
That cool plugin powering your store? That custom theme you paid good money for? They might behave differently when you migrate WordPress to a new host. Do your homework on compatibility issues before moving day arrives.
## How to Migrate a WordPress Site: A Simple Guide
### **First**: Take Stock of What You Have
Before packing up your digital belongings, look at what you're working with. Got any ancient plugins you haven't updated since 2016? Custom code that's held together with digital duct tape? Now's the time to identify these issues before you transfer your WordPress site.
### **Next**: Create Your Game Plan
Every website has its quirks, so cookie-cutter migration plans often fall short. Give yourself enough time (always more than you think you'll need), identify potential trouble spots, and make sure you've got resources lined up for when things inevitably get weird during WordPress migration.
### **Finally**: Execute the Move
Whether you go with a migration plugin or manual transfer, stick to your plan and test obsessively. Is the contact form working? Are images displaying properly? Does the checkout process still work? Don't redirect your domain until you're confident everything's working after you migrate your WordPress site to a new host.
## Let Someone Else Deal With It: Levamo's White Glove Migration
If reading all this makes you want to close your laptop and walk away, I get it. That's why services like [Levamo's White Glove Migration](https://support.levamo.com/articles/8535181-how-to-request-a-managed-website-migration) exist - to handle the technical headache of WordPress migration while you focus on running your business.
### What Makes Levamo’s White Glove Migration Different?
It's like hiring professional movers instead of bribing your friends with pizza to help you haul furniture. The Levamo team handles every technical aspect when you need to transfer your WordPress site without you needing to understand server configurations or database transfers.
Yair Maimon, Managing Director at TCM Academy
#### Levamo’s White Glove Migration service includes:
- **Comprehensive Assessments**: Detailed evaluations of current hosting environments
- **Custom Roadmaps**: Tailored migration plans to meet unique client needs
- **Performance Optimization**: Enhancing site speed and reliability post-migration
- **Minimized Downtime**: Using advanced techniques to reduce service disruptions
- **Post-Migration Support**: Ongoing assistance to ensure everything functions smoothly
#### Step-by-Step Process of Levamo’s Migration
**Data Validation and Pre-Migration Checks**
- Verify WordPress, SSH, and DNS manager credentials
- Identify and provide feedback on compatibility issues
**Client Communication and Scheduling**
- Determine immediate or scheduled migration preferences
- Coordinate timelines and maintain clear communication
**Migration Execution**
- Initiate data transfer with or without maintenance mode
- Implement performance optimizations (e.g., Redis, LiteSpeed Cache)
**Testing and Quality Assurance**
- Pre-launch testing using a temporary URL
- Check site functionality, load times, and database integrity
**Go Live and Final Resync**
- Adjust DNS records for immediate migrations
- Perform a final data sync for scheduled migrations
**Post-Migration Optimization and Support**
- Fine-tune PHP and OPCache settings
- Provide ongoing monitoring and client assistance
## Final Thoughts
Learning how to migrate a WordPress site doesn't have to become your next horror story. With careful planning or the right help, you can wake up tomorrow with your site running smoothly on its new home.
If you're looking for someone to handle the WordPress migration for you, Levamo specializes in no-stress WordPress transfers. Reach out for a conversation about your project, and they'll help you figure out the best approach to transfer your WordPress site safely and efficiently.
---
## BookingPress Review: The Smartest Way to Manage Online Bookings
- URL: https://levamo.com/blog/bookingpress-review/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-03-26
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is BookingPress the right booking plugin for your WordPress site? Find out here.
Have you been managing appointments, services, staff, and whatnot in your service business all by yourself? Well my dear, it’s high time you have a sidekick. And no, not a person but an online appointment booking system. With an all-rounder scheduling software in place, your appointment booking, payments, and staff management, everything can be on autopilot mode.
Don’t believe us yet? Well, hang in there. Today, we are going to have a detailed review of a popular WordPress booking plugin - **BookingPress. As a small service business, you can opt for its Lite version to get started**. Further, as your service grows, you can check out the Pro version’s affordable plans!
In this BookingPress review, we will have a detailed look at both versions for features, ease of use, pros and cons, as well as business suitability.
## Firstly, How Does an Online Booking Plugin Support Your Business?
A [WordPress appointment booking plugin](https://www.bookingpressplugin.com/) can be set up to take online appointments directly on your Website. Herein, a complete customer journey can be set up from browsing your services to adding them to your cart, booking a time slot, choosing a staff member, making payment, and also automated reminders and invoices. Doesn’t it seem to be an easy peasy affair? Here are the top functions that an online booking Plugin provides for your service business.
### Top Functions of a WordPress Booking Plugin
- 24/7 appointment booking facility
- Adding unlimited services and categories
- Online or manual payment processing
- Automated confirmations and reminders
- Staff management
- Easy to setup Booking Forms
Apart from these, based on your necessities, an appointment booking plugin must provide additional functionalities. Thus, a powerful appointment booking system scales up with your business.
## Type of Businesses That Benefits from Using a Booking Solution
If you are confused about whether your business needs a booking solution or not, here’s your answer. We are sharing a list of businesses that can hugely benefit from leveraging an online booking system.
- **Health & Wellness:** If you are dealing with services like spas, massage studios, aromatherapy, life coaching, or other related services, a booking system would ease a lot of tasks.
- **Salon & Lifestyle:** Businesses like beauty parlour, hair spa, nail art studio, cosmetologists, manicurists, etc can simplify customer bookings with an online software.
- **Fitness & Gyms:** To set up a gym, fitness studio, zumba classes, dance fitness, yoga sessions, etc., an online booking system will work wonders.
- **Medical & Clinics:** Get appointment booking of patients through an online system to manage schedules of various doctors, dentists, vet, etc.
- **Professional Services:** If you are a consultant, lawyer, agent, dealer, photographer, etc. then you can manage your schedules and appointments using a booking software.
- **Educational Services:** For tutors, education centers, private classes, driving school, language classes, webinar sessions etc., a booking setup can streamline the sessions.
- **Rental Services:** For renting various products like bike, car, yacht, furniture, property, tools, etc., a booking system can show availability, equipment, and rates easily without any manual management.
- **Varied Services:** Services like cleaning, repairing, maintenance can also be set up with a booking system so that you know your day well and can plan accordingly.
Now you know the utility of an online booking system is very far and wide. Based on the features required for booking tasks, BookingPress is the top solution. Let us now review how Free and Pro versions support your business.
## Reviewing the BookingPress Lite - The Free Version
If you are just starting out with your service business, you definitely need a low-investment option. Thus, BookingPress lite. A no-investment option to help you understand the nuances of an online booking process. You can easily download the Plugin from BookingPress’s website and then add it to your WordPress website. Let us explore the platform with a step-by-step guide.
### Step 1: Downloading BookingPress Lite

Firstly, go to the website of [BookingPress.](https://www.bookingpressplugin.com/) Now there, you will see an option of Download the Free Version. Click on it to download BookingPress Lite. With this, a Zip file will be downloaded. Let us move on to the next step.
### Step 2: Installing the Plugin in WordPress

Now, log in to your WordPress Dashboard and follow these steps.
- On the dashboard, Go to Plugins > Add New Plugin
- Click on Upload Plugin > Choose File
- Select the [downloaded Zip file](https://www.bookingpressplugin.com/?bpa_action=download_free_version) from the BookingPress Site
- Once uploaded, click on Install Now
- It will take some time and then, you will be taken to a new screen wherein you will get an option to Activate Plugin. Click on that to get started further.
### Step 3: Setting Up BookingPress

Once the Plugin is activated, you will see it on the left-side admin panel. By clicking on it, you will see the BookingPress setup wizard. If you are new to using Plugins, it is advisable to go through the setup wizard. Don’t worry, you can make all the changes at any time. So, here, just observe and learn.
- First of all, you will have to add your company details like Company Name, Address, Date Format, Time Format, Country, Phone No., etc.
- Next, you will have to set your working hours for providing services and default currency.
- In the next step, you can set up multiple services, their price, duration, and description. You can add as many services as needed here.
- Next comes the customization options. Here, you can edit the font, style, colour scheme, etc. to suit your business and brand.
- Once done, you can either save it and go to the Dashboard or exit the setup wizard without saving it.
- Further, let’s explore the BookingPress Dashboard.
### Step 4: BookingPress Dashboard and Features for Online Booking System

There are multiple modules on the BookingPress dashboard. From calendar to appointments, payments, services, notifications, reports, etc. Here’s what all you can do with BookingPress Lite.
- From the Calendar view, you can manually add any appointments you get through walk-ins or calls.
- From the appointments module, you can check and manage all your appointments. You can search for appointments using customer name, appointment ID, services, etc. Further, you can also check the appointments based on their status for perfect appointment management.
- Check the transaction date and payment status from the payments tab for detailed management.
- All your customers will be added to the Customers list. You can view and manage them from here.
- In the next tab of services, you can add multiple service categories and list out unlimited services under each. This will help you bifurcate your services in an advanced way.
- You can set up automated customer notifications on their booking activities like approval, pending, rejection, cancellation, etc. Create a perfect draft using the shortcodes and enable auto email notifications with BookingPress’s free version.
- Check out the customization and settings for any further updates and changes to your appointment booking site. You can edit your form, how it is visible to your customers, add payment options like PayPal or manual and customize the front-end look of your booking form.
- With this plugin, you can also check out the basic reports on the dashboard to understand the performance of your service business.
Once done, you can publish the Booking Form shortcode in one of the posts or pages so that customers can start online booking.
## Key Features on BookingPress Lite
Now that you know how to set up this plugin, we will go through the features that come with the BookingPress free version. So you can customize and configure your appointment booking system. Here are the features on the free version:
- Get unlimited bookings and cater to multiple customers simultaneously.
- Create various categories and add multiple services under each to set up your service business.
- Set up a specific time duration for each service to avoid any booking clashes.
- A very simple and user-friendly interface that can be used by anyone, even without coding knowledge.
- Automated email notifications to avoid any follow-up hassles.
- Gutenberg and Elementor integration for a very clean and advanced page design for your site.
- Exclusive online payment support with PayPal as well as a manual payment option.
- Choose your language and currency from different options to cater to your customers directly.
- Import or export your data based on the requirements of your business.
All these features ensure that you get the essential booking features without any investment.
Once you are ready to scale up your business and explore the advanced features of a booking system, you might consider upgrading to the Pro version with BookingPress.
## When Should You Upgrade to BookingPress Pro Version?
If your service business requirements exceed the features of BookingPress Lite, then it's time to upgrade to their Pro version. It is designed to support business scalability and enhance its functions. And it's perfect for medium to large businesses that require staff management, multiple location setup, bundling of services, and advanced reporting.
Let's check out the features of BookingPress Pro, and then you can decide if you need those features and if you should upgrade to the Pro version.
### Top Features of a Pro Booking Plugin
**Efficient Staff Management:** Add multiple staff members and assign varied services to each of them. All the staff members get dedicated dashboards so that they can track their schedules with ease.
**Versatile Payment Options:** Here, you get the support of 20+ payment gateways like PayPal, Stripe, Mollie, Razorpay, etc. It ensures smooth transactions between businesses and clients.
**Automated Notifications:** Apart from email notifications, with the Pro version, you can enable SMS as well as WhatsApp notifications. This ensures timely reminders and reduces no-shows.
**Recurring Appointments:** If you are offering any ongoing services or classes, you can set up recurring appointments. Thus, clients can book multiple sessions at specific intervals with ease.
**Global Accessibility:** With multiple languages and RTL support, your business can be truly global,l catering to audiences of any nationality.
**Third-party Integrations:** You get robust integrations with various third-party tools like Zoom, Google Calendar, Outlook, Mailchimp, [ARMember](/blog/armember-membership-plugin/), etc. Thus, you can extend the usability of your online booking system.
**Decision Making:** With advanced reports and analytics, you can observe the booking trends, staff schedules, overall business performance, and make well-informed decisions for the future.
**Multi-Location Management:** If you are functioning from multiple locations, you can manage all your branches using a single dashboard. Thus, ensuring smooth operations throughout the business.
**Boost Sales with Promotions:** Multiple advanced features like happy hour pricing, gift card purchases, and discount vouchers can help attract more customers. This helps enhance your revenue with strategic marketing.
**Enhanced Booking Experience:** Features like group bookings, buffer hours, happy hours, etc., ensures that you get all the options to suit your service business.
**POS System:** If you want to set up easy payments at your service business location, BookingPress Pro comes with a powerful [Stripe POS system](https://www.bookingpressplugin.com/addon/stripe-pos-payment-gateway-addon/). Thus, you can allow quick tap and pay to your clients.
**Overnight Booking:** If your service business requires an overnight booking system, for instance, a Hotel or car rental, then you can use the overnight booking feature with BookingPress Pro.
### BookingPress Pricing for Pro Plan
BookingPress provides three different pricing plans. However, you get a fixed set of 45+ addons with each plan. Thus, complete transparency, no hidden costs!
- **Standard Plan ($79/year):** Utilize on a single site along with 45+ addons.
- **Professional Plan ($129/year):** Supports up to three sites with 50+ add ons and other premium features.
- **Enterprise Plan ($249/year):** With this plan, you can use it on 20 sites with 50+ add-ons and multiple premium add-ons as well.
Based on your requirements, you can choose any of the plans. To explore the pro features, you can check out the [BookingPress Demo](https://www.bookingpressplugin.com/demo/) for various businesses.
## Wrapping Up
A service business becomes smooth and easy with an appointment booking solution. It helps streamline your bookings so that you can focus more on your services. It acts like your personal assistant. For a small-scale individual businessperson, this works as a boon.
BookingPress has been an amazing and innovative solution for years. With every update, it brings advanced features that take service business appointment management to the next level.
In today’s BookingPress review, we tried to analyze it to see how useful and complete it is. And we found it to be a pretty well-rounded plugin.
Try it now for yourself and let us know what you think of this plugin!
---
## 20 Top WordPress Themes in 2025: Levamo's Ultimate Picks
- URL: https://levamo.com/blog/top-wordpress-themes/
- Category: website-design
- Author: Sunyyan Junaid
- Published: 2025-03-25
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find the best WordPress themes for 2025 with Levamo's expert picks.
When it comes to building a WordPress website, choosing the right theme is half the battle. A good theme should be fast, flexible, and compatible with the tools you need. But with thousands of themes out there, how do you pick the best one?
I’ve done the research for you. I’ve analyzed speed tests, checked real user reviews, and explored forums like Reddit to bring you the top WordPress themes in 2025. Whether you need a theme for a business site, blog, online store, or portfolio, this list has you covered.
## Picking the Top WordPress Themes of 2025: Our Methodology
To identify the best WordPress themes for 2025, we analyzed multiple factors, including:
1. Speed & performance
2. User reviews
3. Customization options
4. Pricing
We scoured **Reddit discussions, WordPress forums, and user testimonials** to ensure we included feedback from actual website owners. Our selection includes themes that cater to different needs, whether you’re running a business site, an online store, or a personal blog, while prioritizing usability, stability, and long-term support. For speed, we used Nitropack.io and WP Rocket’s performance results.
## Levamo’s Pick of the Top WordPress Themes of 2025
### 1. Astra

[Astra](https://wpastra.com/) is a fast, lightweight, and highly customizable theme loved by Elementor users. It's renowned for extensive customization via the WordPress Customizer, with options for colors, layouts, and a powerful header/footer builder. Astra offers a large library of starter templates, compatibility with major page builders, including [Elementor review](/blog/elementor-review/), Beaver Builder, and Gutenberg, WooCommerce readiness, and built-in SEO features such as schema markup, making it one of the best WordPress themes of 2025. So is Astra the WordPress theme? Go find out! ;)
**Speed and Performance**: Astra scores an impressive 93/100 on Google PageSpeed (mobile), with load times around 0.6s. It’s lightweight, about 50KB, making it a performance powerhouse.
**User Feedback**: *“Astra is my go-to for Elementor. It’s insanely fast and lets me tweak anything without code.”*
**Rating**: 4.9/5
**Active Installations**: 1+ million
**Pricing**: Free core, Pro add-on from $59/year
### 2. OceanWP

[OceanWP](https://oceanwp.org/) is renowned for WooCommerce compatibility and builder friendliness. It's a true multipurpose theme featuring deep WooCommerce integration, custom cart pop-ups, quick views, and shop optimizations. OceanWP provides ready-to-import demos and supports popular page builders like Elementor, Divi, and Beaver Builder. It’s responsive, SEO-friendly, translation-ready, and allows optimization by enabling/disabling JS and CSS modules.
**Speed and Performance**: Scores around 87/100 on mobile PageSpeed, modular architecture helps optimize performance further.
**User Feedback**: *“The free version gives a ton of customization. It’s one of the most generous themes out there.”*
**Rating**: 4.9/5
**Active Installations**: 600,000+
**Pricing**: Free core, Premium bundles from $39/year
### 3. GeneratePress

[GeneratePress](https://generatepress.com/) is minimalist, focusing heavily on performance and clean code. It emphasizes stability, clean coding standards, and excellent compatibility with the block editor and major page builders. GeneratePress Premium offers extensive customization options for layouts, typography, navigation, and colors, which is ideal for developers who appreciate WordPress coding standards and a robust hook system.
**Speed and Performance**: Tiny footprint at 10KB; excellent Core Web Vitals; mobile PageSpeed of 87/100; 0.54s load time.
**User Feedback**: *“GeneratePress has great SEO and is super performant, [it] promotes good practices.”*
**Rating**: 5.0/5
**Active Installations**: 600,000+
**Pricing**: Free base theme, Premium at $59/year
### 4. Kadence WP

[Kadence WP](https://www.kadencewp.com/) delivers rich features without compromising on performance. It boasts an advanced header/footer builder with drag-and-drop, global typography, and color controls, numerous layout presets, and a vast library of starter templates. Kadence integrates seamlessly with Gutenberg and Elementor, offering strong WooCommerce support with custom shop layouts and AJAX-powered cart features.
**Speed and Performance:** 88/100 mobile Lighthouse scores; assets load quickly at under 0.7s despite extensive features.
**User Feedback**: *“Kadence has more options than GeneratePress and Astra but stays lightweight. It’s a winner.”*
**Rating**: 4.9/5
**Active Installations**: 400,000+
**Pricing**: Free base, Kadence Pro from $69/year
### 5. Neve

[Neve](https://themeisle.com/themes/neve/) combines modern design, mobile optimization, and [WordPress Speed Optimization](/blog/wordpress-speed-optimization/). It’s highly flexible and compatible with Gutenberg and popular builders such as Elementor, Brizy, and Beaver Builder. Neve provides numerous starter sites, advanced header/blog features in its Pro version, and supports AMP for ultra-fast mobile loading.
**Speed and Performance**: Google PageSpeed scores around 92/100 (mobile); load times ~0.55s.
**User Feedback**: Recommended for balancing features and speed; popular for blogs and business sites.
**Rating**: 4.7/5
**Active Installations**: 300,000+
**Pricing**: Free version, Pro from €99/year
### 6. Blocksy

[Blocksy](https://creativethemes.com/blocksy/) is a cutting-edge, Gutenberg-focused theme renowned for its modern tech stack, which includes Webpack and React for a seamless customizer experience. It features an intuitive header and footer builder supporting conditional headers, built-in mega menus, advanced typography, extensive color controls, dynamic content hooks, and compatibility with Elementor, Brizy, and Beaver Builder. Blocksy offers a variety of starter sites, exceptional WooCommerce features like custom product layouts, advanced gallery styles, and dynamic filters. It is also optimized for WordPress's Full Site Editing capabilities, making it future-proof and developer-friendly.
**Speed and Performance**: Lightweight install around ~27KB, delivering swift load times ideal for maintaining excellent Core Web Vitals.
**User Feedback**: *“Blocksy is Astra’s cooler younger brother. Super flexible and super fast.”*
**Rating**: 5.0/5
**Active Installations**: 200,000+
**Pricing**: Free core theme, Pro version starting at $69/year
### 7. Hello Elementor

[Hello Elementor](https://elementor.com/products/hello-theme/) is a minimal starter theme perfect for Elementor users. Its minimalistic design provides a clean canvas, ensuring no conflicts or unnecessary bloat, allowing complete freedom in layout and style using Elementor.
**Speed and Performance**: Incredibly fast, 520ms load time, with near-zero bloat, ensuring excellent Core Web Vitals scores.
**User Feedback:** *“It’s basically a lightweight shell, which is exactly what you need for full Elementor control.”*
**Rating**: 4.3/5
**Active Installations**: 1+ million
**Pricing**: Completely free
### 8. Hestia

[Hestia](https://themeisle.com/themes/hestia/) features a modern one-page design ideal for startups and creative professionals. It's known for its sleek material UI design, compatibility with page builders, built-in sections for services, team, and testimonials, and extensive customization options.
**Speed and Performance**: Scores around 89/100 on mobile PSI, with good overall load times despite its numerous built-in features.
**User Feedback**: *“Hestia made my business website look premium with zero effort.”*
**Rating**: 4.8/5
**Active Installations**: 100,000+
**Pricing**: Free, Pro from $69/year
### 9. Sydney

[Sydney](https://athemes.com/theme/sydney/) is an excellent choice for businesses needing a professional online presence quickly. Features include customizable headers, pre-built homepage blocks, compatibility with Elementor, and WooCommerce integration.
**Speed and Performance**: Quick loading around 0.56s, scoring above 90 in PageSpeed tests.
**User Feedback**: *“Sydney is professional and easy to set up. A great free business theme.”*
**Rating**: 4.9/5
**Active Installations**: 100,000+
**Pricing**: Free, Pro from $79/year
### 10. Storefront

The official [WooCommerce theme](/blog/wordpress-ecommerce-themes/), [Storefront](https://woocommerce.com/products/storefront/) offers seamless WooCommerce integration, minimalistic and stable design, customization options, and reliable performance.
**Speed and Performance**: Extremely fast eCommerce theme with minimal overhead.
**User Feedback**: *“If you’re serious about WooCommerce, Storefront is the obvious choice.”*
**Rating**: 4.5/5
**Active Installations**: 100,000+
**Pricing**: Free
### 11. Twenty Twenty-Three

Designed as the default free WordPress theme, [Twenty Twenty-Three](https://wordpress.org/themes/twentytwentythree/) is perfect for full-site editing (FSE) enthusiasts. It offers block-based editing, various style variations, and a minimalistic, lightweight design ideal for performance.
**Speed and Performance**: Outstanding speed with 520ms load time, achieving optimal Core Web Vitals.
**User Feedback**: *“It’s the perfect blank canvas for FSE - fast, lightweight, and accessible.”*
**Rating**: 3.4/5
**Active Installations**: 500,000+
**Pricing**: Free
### 12. Divi

[Divi](https://www.elegantthemes.com/gallery/divi) offers extensive visual customization with its powerful drag-and-drop builder. It includes hundreds of ready-made layouts, built-in split-testing, role editor functionality, extensive WooCommerce integration, and bundled plugins like Bloom and Monarch. For many other reasons, Divi is a name that comes up often in any list of the top WordPress themes of 2025.
**Speed and Performance:** Loads in ~2s (needs optimization), PageSpeed Score: 83/100
**User Feedback**: *“Divi lets me experiment on the fly. It’s like a digital sketchpad where I can quickly transform ideas into reality.”*
**Rating**: 4.6/5
**Active Installations**: 2+ million
**Pricing**: $89/year, $249 lifetime
### 13. Avada

[Avada](https://avada.com/) is known for its flexibility, offering 90+ pre-built demos, an integrated Fusion Builder, extensive customization options, WooCommerce integration, and numerous performance enhancements.
**Speed and Performance**: Loads in ~2-3s (requires tuning), PageSpeed Score: 86/100
**User Feedback**: *“Avada provides unlimited design options… one of the most flexible themes.”*
**Rating**: 4.77/5
**Active Installations**: 600,000+
**Pricing**: $69 one-time
### 14. Flatsome

Specializing for WooCommerce, [Flatsome](https://demos.flatsome.com/) includes a robust UX Builder, extensive eCommerce-specific elements like product sliders, quick view, wishlist, and multiple shop layouts.
**Speed and Performance**: Loads in ~1s, PageSpeed Score: High
**User Feedback**: *“Flatsome’s live preview feature is a game changer. I can see my changes instantly, which saves tons of time.”*
**Rating**: 4.8/5
**Active Installations**: 250,000+
**Pricing**: $59 one-time
### 15. Newspaper

[Newspaper](https://tagdiv.com/newspaper/) excels in news, magazines, and blogging sites. It includes tagDiv Composer, numerous post templates, built-in advertising spots, and AMP support for enhanced mobile performance.
**Speed and Performance**: Loads in ~1.5-2s (optimized for AMP), PageSpeed Score: 90/100
**User Feedback**: *“Newspaper has all the features a magazine site needs, from trending posts to ad placements.”*
**Rating**: 4.81/5
**Active Installations**: 150,000+
**Pricing**: $59 one-time
### 16. BeTheme

[BeTheme](https://www.betheme.com/) is versatile, with over 700 pre-built websites covering numerous industries, extensive customization options, a built-in Muffin Builder, and compatibility with popular page builders like Elementor.
**Speed and Performance**: Loads in ~2s, PageSpeed Score: 79/100.
**User Feedback**: *“BeTheme’s demos are a huge time-saver. Great for agencies and freelancers.”*
**Rating**: 4.83/5
**Active Installations**: 300,000+
**Pricing**: $60 one-time
### 17. Salient

[Salient](https://themenectar.com/salient/) is visually compelling, ideal for creative portfolios and agency sites. It offers impressive animations, advanced WPBakery integrations, numerous portfolio styles, and robust customization options.
**Speed and Performance**: Loads in ~1.5-2s (visual-heavy), PageSpeed Score: 85/100
**User Feedback**: *“Salient’s demos look dynamic and fresh - it makes websites feel alive.”*
**Rating**: 4.8/5
**Active Installations**: 160,000+
**Pricing**: $60 one-time
### 18. Bridge

[Bridge](https://bridgelanding.qodeinteractive.com/) offers remarkable versatility with over 600 demos for various niches. Features include compatibility with WPBakery and Elementor, WooCommerce integration, extensive customization options, and numerous built-in features like sliders, portfolios, and niche-specific elements.
Speed and Performance: Loads in ~2s, PageSpeed Score: Moderate
User Feedback: *“Bridge feels like having a design team at your disposal.”*
Rating: 4.7/5
Active Installations: 200,000+
Pricing: $69 one-time
### 19. Enfold

[Enfold](https://kriesi.at/) combines ease of use with robust functionality, featuring a user-friendly Avia Layout Builder, numerous pre-built demos, clean designs, WooCommerce support, multilingual readiness, and strong SEO optimization.
**Speed and Performance**: Loads in ~1.5s, PageSpeed Score: 90/100
**User Feedback**: *“Enfold doesn’t break. It’s the most stable theme I’ve ever used.”*
**Rating**: 4.85/5
**Active Installations**: 240,000+
**Pricing**: $59 one-time
### 20. X Theme

[X Theme](https://theme.co/x) offers multiple distinct design stacks, extensive customization through the Cornerstone builder, bundled plugins, WooCommerce integration, dynamic content conditions, and powerful customization options.
**Speed and Performance**: Loads in ~1.8-2s, PageSpeed Score: Mid-80s
**User Feedback**: *“X Theme is versatile and reliable - perfect for agencies and businesses.”*
**Rating**: 4.76/5
**Active Installations**: 225,000+
**Pricing**: $59 one-time
## Why Hosting Matters for Theme Performance
A fast WordPress theme is just one part of the equation. Because even the top WordPress themes will **slow down if your hosting isn’t built for the task. That’s why you need a host that’s optimized for speed**.
### Levamo: The Best Hosting for WordPress Themes

Levamo's [fully managed WordPress hosting](/managed-wordpress-hosting/) ensures that any theme you choose runs at **hyperspeed. Here’s why our hosting is the best fit for your site:**
✅ **Blazing Fast Load Times** - Our cutting-edge server stack delivers ultra-low latency and instant page loads.
✅ **Auto-Scaling for Traffic Surges** - Your site won’t crash, even during Black Friday traffic spikes.
✅ **Advanced Caching & [Free WordPress CDN](/cloudflare-cdn/)** - We optimize every request for faster global performance.
✅ **Expert WordPress Support** - Our team helps you get the most out of your theme and website.
✅ **Optimized for Dynamic Websites** - Whether you're running an eCommerce store, LMS, or community site, Levamo is built for speed.
The “best” theme ultimately depends on your specific needs - a simple blog thrives with a lightweight theme like Astra or TT3, whereas a complex eCommerce or news site might benefit from the integrated features of something like Flatsome or Newspaper. All the above themes are well-regarded in the WordPress community in 2025 for their combination of performance, features, and support. Importantly, each has a strong user base and positive feedback record (as reflected in ratings and user comments). When choosing among them, consider factors like:
- Do you need a page builder or will Gutenberg suffice?
- Is eCommerce a primary focus?
- How much design flexibility vs. out-of-the-box speed do you require?
- What is your comfort level with customization?
By answering these, you can narrow down which of these top themes aligns best with your project. And remember, you can’t go too wrong with any of these popular options - they’ve all proven themselves across thousands of websites. Just be sure to leverage their strengths (and heed the community tips and feedback provided) to get the most out of whichever theme you pick.
### Frequently Asked Questions

### How do I find the best WordPress theme?
Finding the best WordPress theme depends on your needs. Consider factors like speed, SEO optimization, design flexibility, and compatibility with your plugins. Look for themes with high ratings, good support, and mobile responsiveness.
### Is Astra the best WordPress theme?
[Astra is one of the most popular WordPress themes](/blog/astra-wordpress-theme-review/) due to its lightweight build, fast loading times, and seamless integration with page builders like Elementor and Gutenberg. While it’s a top choice, the "best" theme depends on your specific needs.
### Is Divi the best WordPress theme?
Divi is a powerful and highly customizable theme known for its visual drag-and-drop builder. It's great for beginners and designers who want full creative control. However, it may not be the fastest option compared to more lightweight themes.
### What are the best free WordPress themes?
Some of the best free WordPress themes in 2025 include Astra (free version), GeneratePress, Neve, OceanWP, and Kadence. These themes offer great performance, customization options, and compatibility with major plugins.
### What are the best WordPress themes for any website?
The best WordPress themes for versatility and performance in 2025 include Astra, Divi, GeneratePress, OceanWP, Neve, and Kadence. Each offers unique strengths, such as speed, design flexibility, and built-in SEO optimizations.
---
## Cloud Auto Scaling: What It Is, How It Works, and Why It Matters
- URL: https://levamo.com/blog/cloud-auto-scaling/
- Category: website-performance
- Author: Faisal Sarker
- Published: 2025-03-24
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Explore cloud auto scaling: keep your site online and save money.
Picture this: Your website is cruising along, traffic is steady, and then boom. A viral tweet sends thousands of visitors your way, and if your hosting setup isn't built for this kind of pressure, your site could slow down or, worse, crash. That’s where **cloud auto-scaling** saves the day.
## What Is Auto-Scaling in Cloud Hosting?
Cloud auto scaling is like having a smart assistant for your hosting. It automatically adjusts your computing resources in real-time based on demand. If traffic spikes, more power is allocated to keep things running smoothly. If traffic dips, extra resources are scaled down, so you’re not paying for what you don’t need. It’s efficient, reliable, and hands-free.
## Load Balancing vs. Auto-Scaling: What’s the Difference?
People sometimes mix up **load balancing** and **auto-scaling**, but they are not the same thing. Here’s the difference:
- **Load Balancing** spreads incoming traffic across multiple servers so that no single server gets overwhelmed. Think of it as a traffic cop directing cars to different lanes to keep things moving smoothly.
- **Auto-Scaling** adjusts the number of servers or resources available based on demand. If traffic spikes, auto-scaling kicks in to add more resources. If things slow down, it scales back to save costs.
In simple terms, load balancing manages distribution while auto-scaling ensures there are enough resources to handle demand.
## How Does Auto-Scaling Work?
Auto-scaling can happen in two ways: **scaling out (horizontal scaling)** and **scaling up (vertical scaling).**
### Scaling Out (Horizontal Scaling)
Also known as **horizontal scaling**, this approach adds more instances or servers to handle increased demand. Think of it like adding more cash registers in a busy store to serve more customers at once.
Example. An eCommerce store during [Black Friday](/blog/black-friday-hosting-preparation/) can automatically spin up additional servers to prevent slowdowns or crashes as shoppers flood the site.
### Scaling Up (Vertical Scaling)
This method boosts the power of your existing server by increasing CPU, RAM, or storage rather than adding more servers.
Example. A database-driven application that needs more processing power can automatically allocate more RAM to improve performance instead of adding another server.
## Why Is Auto-Scaling Important?
Auto-scaling isn’t just a fancy feature. It is a game-changer. Here’s why:
- **Performance Optimization**. Keeps your applications fast and responsive, even during unexpected traffic spikes
- **Cost Efficiency**. You only pay for the resources you actually need, reducing wasted spending.
- **High Reliability & Uptime**. Prevents crashes by ensuring resources are always available when needed.
- **Hands-Free Management.** No need for manual intervention. Auto-scaling does the heavy lifting for you.
## Who Should Use Auto-Scaling Hosting?
Auto-scaling is perfect for businesses and websites with fluctuating traffic. Some key industries that benefit most include:
### 1. E-commerce Platforms
Online stores see wild swings in traffic, especially during sales or promotions. Auto-scaling ensures your store stays fast and accessible when traffic surges and dials resources back when things slow down.
### 2. Learning Management Systems (LMS)
Online course platforms and educational sites experience peak usage during live classes, exams, or major enrollment periods. Auto-scaling keeps everything running smoothly, even when thousands of students log in at once.
### 3. Membership and Subscription Sites
Sites offering premium content or community platforms often have unpredictable traffic. Auto-scaling ensures a seamless experience for users without overpaying for unused resources.
## Levamo’s Auto-Scaling: A Smarter Approach
At Levamo, we know businesses need **smart, high-performance hosting that adapts as they grow. That’s why auto-scaling solution on our [fully managed WordPress hosting](/managed-wordpress-hosting/) is designed to be seamless, efficient, and optimized for PHP applications**.
### How Levamo’s Auto-Scaling Works
- **Dynamic [PHP Workers](/blog/php-workers/).** We scale PHP-FPM child processes (workers) dynamically, based on real-time traffic and demand.
- **Instant Scaling.** Need more PHP workers? We allocate them automatically to prevent slow load times and downtime.
- **Plan-Based Customization.** Auto-scaling operates within your chosen plan, giving you full control over your resources without surprise costs.
- **Optimized for WordPress & PHP.** Whether you're running an eCommerce site, a membership platform, or a blog, Levamo’s auto-scaling ensures peak performance without manual intervention.
## Wrapping Up
In today’s fast-moving digital world, **cloud auto-scaling** is a must-have. Whether you're handling a sudden traffic spike or just want to ensure your website runs smoothly 24/7, auto-scaling guarantees high performance and cost efficiency.At Levamo, we take auto-scaling to the next level with **dynamic PHP worker scaling**, making sure your applications stay fast, reliable, and hassle-free. Want to experience worry-free, high-performance cloud hosting? **Check out Levamo today!**
---
## How to Fix a 502 Bad Gateway Error: Troubleshooting Guide
- URL: https://levamo.com/blog/502-bad-gateway-error/
- Category: website-maintenance
- Author: Sunyyan Junaid
- Published: 2025-03-21
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix a 502 Bad Gateway error! Our guide helps you troubleshoot server issues.
If you have ever visited a website and received a 502 Bad Gateway error page, you know how inconvenient it can be from a visitor’s standpoint. But from a business owner’s perspective, the situation is even worse. Your customers will likely become upset and lose trust in your brand, irreparably harming your reputation.
So, what can you do to avoid this dreaded server response?
The good news is - quite a few things.
That said, you first need to know the ins and outs, including why it happens in the first place. Hence, in the next 10-ish minutes, I’ll show you all there is to know about the http error 502 Bad Gateway so that your site can stay free of its impact.
But if you'd rather watch how to fix error 502, here's a video we made:
https://www.youtube.com/watch?v=Sh5wJclLQIk
But if you're more of a reader, let's continue.
## What is a 502 Bad Gateway Error?
A 502 Bad Gateway error occurs when the web server you’ve connected to is acting as a gateway or proxy for another server, but it has received an invalid response from that other server (aka upstream server) and, as a result, can’t complete the request.
In other words, the website you're trying to reach asked a server for something, but the server gave back an unusable answer. So, the website is now stuck and can't show you what you want.
It's termed a 502 error since the web server reports this issue using the HTTP status code 502.
## Common Causes for the 502 Bad Gateway Error
There is no shortage of factors that might cause the 502 error to pop up. But before you start troubleshooting, there’s a nifty test you can run to check if your server is working as it should. The idea is to run a test and see if the website is down for you or everyone else.
Before you start troubleshooting, you can run a test to check if your server is running as it should or if it's down.
Test the URL on [Down for Everyone or Just Me](https://downforeveryoneorjustme.com/levamo.com?www=1) to do this.
Not that such a case would ever happen since the chances of getting this error are extremely low since [Levamo](/) guarantees 99.99% uptime. But I digress.
In any case, here are some factors that can cause an http error 502 Bad Gateway:
- **Server Overload or Crash:** When the upstream server experiences computational overload due to an excessive volume of requests or encounters a critical failure, it becomes unable to process requests and provide a valid response.
- **Network Issues Between Servers:** Disruptions in the network connectivity between the origin server and the gateway server, such as data packet loss, latency, or routing errors, can impede proper communication, resulting in incomplete or incorrect responses.
- **Faulty Code or Script Errors:** Errors within the code or scripts executing on the upstream server can lead to the improper processing of requests, generating invalid responses.
- **Issues with Third-Party Services:** If the web application relies on external services, disruptions or malfunctions within those third-party systems can impact the origin server's ability to formulate a correct response. The gateway, in turn, receives a bad response from the dependent service.
- **Bad CDN or Reverse Proxy Configuration:** Misconfigurations within a Content Delivery Network or a reverse proxy, like wrong routing, caching of erroneous data, or flawed communication protocols, can lead to improper handling of requests and responses.
- **DNS Problems:** These issues can prevent the gateway server from correctly locating the IP address of the upstream server. For example, if the gateway is directed to an incorrect or non-responsive server, it won’t receive a valid response.
- **Firewall or Security Rules:** Sometimes, overly restrictive firewall rules or security configurations on either the gateway or the upstream server can inadvertently block legitimate communication. If responses from the upstream server are filtered out, the gateway will report a 502 Bad Gateway error.
## How to Fix a 502 Bad Gateway Error
Now that you have a good idea why the error occurs in the first place, you can try a few different remedies.
### 1. Refresh Your Page or Try a Different Browser
It may seem too simple to be an effective solution, but often, all it takes to fix a 502 error is to refresh your page or check if the URL works in a different browser.
If refreshing or using a different browser fixes the error, congrats, you're lucky, and you can skip the rest of the article.
### 2. Check your site's status
Checking your site's status can help you understand if the site is simply down or if the problem is on your side. As stated above, you can check your site status by going to a website like **Down For Everyone Or Just Me** and simply pasting your URL into this tool. It will tell you if the site is working correctly or if it’s down for everyone. If it's down for everyone, all you can do is wait until it gets back online.
### 3. **Restart Your Network Equipment**
If you’re managing your site from home or a small office setup, restart your modem/router. DNS or gateway issues from your ISP can sometimes be the culprit.
### 4. Clear Cache or Try Incognito Mode
If reloading didn't help and you've confirmed the site isn't down, the issue could be with your browser's cached web page version. Try loading the site in incognito mode or [clearing your cache](/blog/wordpress-clear-cache/).
In **Google Chrome**, go to the top-right corner, click the three dots, then select **Clear Browsing Data**. Ensure that **Cached images and files are** checked before clicking **Clear Data**.
### 5. Flush DNS
The error 502 bad gateway might also happen due to DNS-related issues. For example, after moving your website to a new host, DNS propagation can take up to 48 hours, and until then, people won't be able to access the websites. Additionally, this error can come from your local DNS cache.
**On Windows**, open the Command Prompt (cmd) and type:
bash
ipconfig /flushdns
- Press Enter. Once this is completed, you'll see a message confirming the DNS cache has been flushed.
- **On Mac**, open Terminal and enter the appropriate command for your macOS version. You won’t receive a success message, but your DNS cache will be cleared.
- If you're uncomfortable using these methods, you can temporarily switch to a third-party DNS provider like **Google Public DNS**.
### 6. Check Error Logs
Viewing your website’s [error logs](/blog/debug-in-wordpress/) can be useful for pinpointing the root cause of a 502 error. These logs might reveal specific issues like conflicts with plugins or problems following an update.
- If your hosting provider offers a logging tool, check it.
- If not, you can enable logging by adding a specific line to your wp-config.php file.
### 7. Deactivate Plugins and Themes
Misconfigured caching plugins are a common cause of this error.
- Deactivate all plugins at once from the **WordPress Dashboard > Plugins > Bulk Action > Deactivate**.
- If the error is resolved, reactivate them one by one to identify the culprit.
- If you can’t access the dashboard, disable plugins via SFTP by renaming the plugins folder.
### 8. Disable CDN or Firewall
If nothing has worked so far, the culprit could be your **CDN** or firewall settings.
- Try **temporarily disabling the CDN** to check if it’s causing the issue.
- If you’re using a **CDN enabler plugin**, deactivate it and test your site.
- If you don’t have dashboard access, disable the CDN plugin via SFTP.
### 9. Increase PHP Limits or Max Execution Time
WordPress sites with numerous plugins or custom themes can be **memory-intensive**.
- If your **[PHP memory limit](/blog/maximum-php-memory-limit/) is too low**, scripts may fail to execute properly, leading to a 502 error.
- Increasing **PHP memory and execution time** can prevent script timeouts that cause this error.
### 10. Contact Your Hosting Provider
None of the steps above resolved error 502? Reach out to your **hosting provider** for assistance.
But remember, if 502 errors are becoming a pattern, it's a sign that your current hosting environment isn’t keeping up, and you need to reconsider your choice.
For example, Levamo customers almost never face a 502 error problem from the server side. If the problem occurs for some reason, you have access to an [expert support team that is ](/support/)[available **24/7**](/support/) to assist you.
Levamo isn’t just another hosting provider. It’s a **performance-driven platform built for resilience**, with built-in scalability, automated incident detection, and human support that actually shows up when it matters.
It also comes preinstalled with **proactive security solutions** like firewall protection, malware defense, protection for [preventing DDoS attacks](/blog/preventing-ddos-attacks/), and virtual patching for enhanced security.
## Conclusion
A 502 Bad Gateway error can disrupt your website's functionality and frustrate visitors, potentially harming your brand’s reputation. However, by following the right troubleshooting steps, such as refreshing the page, clearing the cache, checking DNS settings, and reviewing error logs, you can quickly identify and resolve the issue.
Ensuring your hosting provider offers reliable infrastructure like Levamo's [fully managed WordPress hosting](/managed-wordpress-hosting/), which includes proactive security and 24/7 support, can significantly reduce the likelihood of encountering this error.
With the right approach, you can maintain a seamless user experience and keep your website running smoothly.
## Frequently Asked Questions about 502 bad gateway error
### What is 502 bad gateway error?
From the Mozilla Developer Network, the official definition of the 502 Bad Gateway is:
The HyperText Transfer Protocol (HTTP) 502 Bad Gateway server error response code indicates that the server, while acting as a gateway or proxy, received an invalid response from the upstream server.
### What is a bad gateway error 502?
It's the same thing as a 502 bad gateway error, just worded differently.
### How to fix the 502 bad gateway error?
There are many ways to fix the 502 bad gateway error:
**1. Refresh your page or try a different browser**
**2. Check the site's Live or Down status**
**3. Clear Cache or Try Incognito Mode**
**4. Flush DNS**
**5. Check Error Logs**
**6. Deactivate Plugins and Themes**
**7. Disable CDN or Firewall**
8. Increase PHP Limits or Max Execution Time
**9. Contact Your Hosting Provider**
### What causes a 502 Bad Gateway error?
---
## How to Create a Membership Website with WordPress (Step-by-Step Guide)
- URL: https://levamo.com/blog/create-a-membership-website/
- Category: membership
- Author: Faisal Sarker
- Published: 2025-03-20
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Build a WordPress membership site for recurring revenue. Get started now.
If you ever dreamed of creating a WP website with recurring monthly revenues, now is the best time to do it. With the right strategy and consistency, a WordPress membership-based website is the key to generating a healthy and stable stream of ongoing income.
> While there are many nuances in creating a membership site, with WordPress, it is surprisingly easy to do with little to no knowledge of coding.
This comprehensive guide will walk you through every step, from choosing the right tools to setting up payment options and crafting engaging content. By the end, you'll have a fully functional membership website ready to generate your income.
## Prerequisites on How to Create a Membership Website
Before moving on, it is important to know the essential prerequisites required to build a highly converting membership-based website. These lay a solid foundation for your membership website in creating a valuable and sustainable online business community.
### 1. Define Your Niche and Target Audience
Define clearly your niche and the target audience. Ask questions to yourself like:
- Who is my target audience?
- What is their age?
- What are their likes and dislikes?
- What is their propensity to spend on such a membership site?
For example, if you are selling a course on leadership for women, then your target audience could be between the ages of 30 and 50, and most probably working moms, who have a job and family that need to be balanced.
### 2. Content Strategy
Plan your content roadmap, including free and premium offerings. In advance, outline the topics, formats, and delivery schedule. Ensure consistency across all formats and content when posting. Remember, by being consistent you can gain a strong following online.
Examples include weekly articles, monthly webinars, video tutorials, downloadable resources, and interactive quizzes.
**Free vs. Premium Content.** Determine what content you'll offer for free to attract visitors and what exclusive will be available exclusively to paying members. Examples of free content include blog posts and social media videos to build a loyal following.
### 3. Decide on a Monetization Model
What are the different membership levels that you'll offer? You can opt for a simple, flat monthly pricing or different tiers with added benefits. For example, a basic tier with access to core content and a premium tier with additional resources and support including one-on-one coaching.
It’s simple; you get what you pay, and with higher premiums come great benefits and additional resources. Have affordable monthly recurring pricing for guaranteed support. It is better to charge low but ongoing monthly payments as a form of recurring revenue rather than selling high one-off payments.
But what works best is for you to decide. If your industry has a monthly recurring payment model then go for it, else see how you can utilize the high ticket pricing model.
### 4. Develop an Engagement Plan
You should have a proper engagement plan, no different than the content strategy. You need to respond to comments, inquiries, and provide complete support to your members. This is called engagement.
There are various methods to communicate with your members such as using welcome emails, newsletters, and announcements.
Personalized content recommendations, exclusive events, or loyalty programs; these are some of the best ways to engage your audience. Remember, audience attention is the key and the only way to do it is through constant engagement.
## How to Create a Membership Website with WordPress?
Now that we’ve learned the prerequisites, it is time to roll up our sleeves and start building one ourselves. You can make a membership site via a membership website builder but with WordPress, you have additional flexibility of creating an exceptional website.
### Step 1: Purchase a Domain
Whenever you choose any one of our hosting plans, you will have the option to either register a new domain or transfer one over to Levamo.
On the flip side, Namecheap, Godaddy and Hostinger all are great registrars to register your domain.
### Step 2: Purchase Quality WordPress Hosting
When building a membership website, choosing the right hosting is important. With shared hosting, your server resources are distributed among thousands of other websites, leading to slower performance and potential security risks. With Managed hosting for WordPress, you get the speed, reliability, and security needed for a seamless membership experience.
Managed hosting for WordPress provides essential features for membership sites, such as automatic backups, enhanced security measures, CDN for faster load times, and scalable resources to handle growing memberships. In addition, you get support of WP experts ready to tackle any issue your website faces.
In terms of cost, Managed hosting for WordPress from Levamo starts at just $35/month - significantly more affordable than dedicated hosting, which typically costs $60+ per month.
### Step 3: Purchase a Premium WordPress Theme
Choose a theme that is visually appealing, responsive, and compatible with membership plugins. BuddyBoss offers an amazing bundle of theme + plugin that works in tandem to power up your community website.
You can also visit Themeforest.net to purchase a membership site theme which costs in the range of $59 to $69 for a one-time fee.
### Step 4: Purchase & Install a Membership Plugin
Having a premium theme is just the beginning. To convert your WP website into a fully functional membership platform, you’ll need to purchase and install a membership plugin. These plugins have multiple features such as content restriction, membership levels, payment gateways, user manager, digital downloads, course creations and community discussions.
Popular membership plugins include [MemberPress](/blog/memberpress-review/), Paid Memberships Pro, Restrict Content Pro, LearnDash and TutorLMS, **[ARMember](https://www.armemberplugin.com/)**, among many others.
### Step 5: Set up MemberPress (or Your Chosen Plugin)
The price of any paid plugin varies upon your requirements and the developer’s brand reputation. Some are free whereas others cost anywhere from $179 to over $300 per year.
Once you acquire the paid license, activate the plugin through the WordPress dashboard. Configure the plugin settings, including payment gateways, membership levels, and content access rules. Familiarize yourself with the plugin's features and documentation.
To know more on setting up an LMS for your WP website, you can know more in our [Tutor LMS Review](/blog/build-lms-website-with-tutor-lms/), [LearnDash LMS Review](/blog/learndash-review/) and [Sensei ](/blog/sensei-lms-review/)[LMS](/blog/sensei-lms-review/)[ Review](/blog/sensei-lms-review/).
### Step 6: Add a Payment Method
To generate sales from your membership website, you need a payment gateway that accepts debit and credit cards and charges on a recurring basis every 30 days. For this, Paypal and Stripe are the most viable options as the leading payment solutions. You can easily integrate them with every membership plugin and process payments without any hassle.
In your WP plugin setting, you can configure the payment gateway, set the currency and specify recurring billing options for your paid members.
### Step 7: Creating Membership Levels
Every membership website has different tiers or plans that cater to a diverse range of audiences. The main differences among these plans are prices and the features. Similar to any SaaS product that you use, you can very well figure out how the subscription plans work.
With a membership site, it is no different. When you create content, it is important to develop different plans and sell those according to your target audience. You can create those in the plugin settings in WP for your plugin.
### Step 8: Restrict Access to Membership Plans
Every great piece of content that was once freely available, is now behind a paywall. From top news journals such as The New York Times and The Washington Post to websites selling premium courses, much of the content is restricted only to members.
But here’s something different that you have to do.
Restrict content with the levels of membership plans. Similar to Shopify that charges more for extra benefits and perks, create plans, and restrict content accordingly. Members who value quality content understand the worth of getting access to it by paying a premium price.
### Step 9: Adding Members-Only Content
One of our clients on Levamo is an online English language instructor. While most of the videos on his social media platforms provide value, it’s the content in his WP membership website that provides additional support and engagement.
A free English language course comes with no support and covers only the basics.
But a premium course gets you support, one-on-one consultation, assignment feedback and community discussions. This is what separates members-only content with free content available on other platforms.
### Step 10: Create a Pricing Page
Design a clear and concise pricing page that showcases your membership options. Highlight the benefits of each membership level.
For example, the pricing page of MemberPress has a unique layout. Instead of starting from Basic to Pro in a natural left-to-right eye movement, they have done the opposite. Their plans are also categorized for the different types of online entrepreneurs such as bloggers, educators, coaches, developers, ecommerce experts and small business owners.
For every pricing plan, the full list of benefits displays everything clearly progressing as the price increases.
They also have a nice orange-colored CTA to entice users into purchasing their premium plugin.
### Step 11: Add Sign-up and User Login Forms
Create user-friendly registration and login forms. If you have a look at one of our clients, you can see that there is no clutter on their website.
The registration form is clean, simple and to-the-point, which means anyone landing on this page should be able to easily sign up. Place these forms strategically on your website (e.g., homepage, sidebar).
## Launch Your Membership Empire Today
Launching a membership website is more than just a way to share your skills and expertise - it’s a powerful step toward creating a sustainable online business. Consider Levamo as your business partners, ready to help you at every step of the way with the [best WordPress hosting for high traffic](/managed-wordpress-hosting/) and with specialized products like [MemberPress hosting](/memberpress-hosting/) and [LMS hosting services](/managed-lms-hosting/).
As long as you continue providing the right value to your audience, you never have to worry about paying the bills. Take the first step today and create a membership website with WordPress using steps outlined in this guide. You can check this blog for [memberpress review](/blog/memberpress-review/).
## Frequently Asked Questions

### Can you create a membership site on WordPress?
WordPress is an amazing platform providing freedom and flexibility to create powerful membership websites. You can use plugins like MemberPress, BuddyBoss, etc., to create and manage membership websites.
### How to create a subscription page in WordPress?
You can create a subscription page using MemberPress. You get all the tools you need to design pricing pages and manage subscription options.
### Is there a membership plugin for WordPress?
MemberPress, Paid Memberships Pro, and Restrict Content Pro are some of the most popular plugins for this purpose.
### How do I enable membership on WordPress?
You'll need to install and activate a membership plugin such as MemberPress. These plugins provide the functionality to create membership levels, restrict content, and manage members.
### Is MemberPress free?
MemberPress is a premium plugin with various pricing plans based on your needs.
---
## A Practical Guide to Creating a Symbolic Link in Linux
- URL: https://levamo.com/blog/symbolic-link-in-linux/
- Category: website-development
- Author: Sunyyan Junaid
- Published: 2025-03-19
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Create symlinks in Linux: manage files without copying them.
Ever needed a clever way to manage files without copying or moving them every time you need them in a new spot? That’s where **creating a symbolic link in Linux** comes into play. Symbolic links, also known as symlinks or soft links, are shortcuts that point from one location to another, saving you time, disk space, and organizational headaches. Below, we’ll explore what a symbolic link is **in Linux**, how to set them up, when you should (and shouldn’t) use them, plus a quick look at removing links when you’re done. By the time we’re finished, you’ll be linking up everything from log files to config directories with ease!
## What Is a Symbolic Link in Linux?
Imagine you have a folder full of photos in /home/user/Pictures/. You want to access them from the /var/www directory for a web project. The best option might be to copy them, but that doubles your storage usage and means you’ll need to sync changes between two folders.
A **symbolic link** (or soft link) is basically a special file that “points” to another file or directory. Think of it like a desktop shortcut on Windows. When you click it, you’re whisked straight to the real file. Key points:
- **No Extra Copy**: You’re not duplicating data.
- **Easy to Update**: If the original file changes, you don’t need to recopy anything.
- **Low Disk Use**: A symlink is just a tiny pointer, so it doesn’t hog space.
That’s the gist of **what is a symbolic link in Linux**: a powerful method for bridging directories and files across your system without needless duplication.
## Soft Links vs. Hard Links: What’s the Difference?
While we’re focusing on creating a soft link(symbolic), you may hear about “hard links” too:
**Soft (Symbolic) Link**:
- Points to a file path.
- If the original file moves or is deleted, the symlink breaks (it becomes a “dangling” link).
- Can link to directories or files across different partitions.
**Hard Link**:
- Directly references an inode on the filesystem, so the link remains valid even if the original file name changes.
- Usually can’t link to directories, and can’t cross filesystems or partitions.
For day-to-day tasks, especially when linking directories or bridging multiple mount points, you’ll almost always stick to symbolic links.
## How to Create a Symbolic Link in Linux (The Basics)
So, you’re sold on the idea of symlinks and you’re ready to actually do it. **How to create a symbolic link in Linux** typically involves the ln command with a -s flag (for “symbolic”).
### 3.1 The Simple Command
`ln -s /path/to/original /path/to/symlink`
- **/path/to/original**: The file or directory you’re pointing to (the “target”).
- **/path/to/symlink**: The name or path of the symlink you’re creating.
Example: Suppose you have a pictures folder under /home/alex/ and you want a link in your /var/www directory:
`ln -s /home/alex/pictures /var/www/pics`
Now, /var/www/pics is a symlink that points to /home/alex/pictures. Any references to /var/www/pics take you straight to the real folder.
### Verifying the Link
Use ls -l in the directory containing your symlink:
`ls -l /var/www`
You might see something like:
`lrwxrwxrwx 1 alex alex 24 Mar 10 10:00 pics -> /home/alex/pictures`
The first letter l indicates it’s a symbolic link. The arrow shows the link’s destination.
### Relative vs. Absolute Paths
Often, you’ll see ln -s used with absolute paths (e.g., /home/alex/pictures). But you can also use relative paths, which can be handy if you plan on moving directories around. For example, from within /var/www:
`cd /var/www`
`ln -s ../home/alex/pictures pics`
As long as the relative path remains correct, the symlink works. But absolute paths are simpler for most cases.
## When Should You Use Symbolic Links?
- **Shared Assets**: Suppose multiple apps need the same assets (images, logs, scripts). A symlink makes them all reference the original location, ensuring everything stays in sync.
- **Organizational Flow**: Keep your root directory neat by linking subfolders. For instance, if /opt/appdata is your real data folder, you can link it to /home/user/appdata to keep your workflow consistent.
- **“Easy Name” Shortcuts**: If a directory or file path is super long, create a symlink with a short name for convenience. For example, ln -s /var/log/awesome_app /logs/awesome.
Essentially, symbolic links shine whenever you want a quick pointer to a resource, especially if that resource is likely to move or needs to be accessed from different vantage points.
## Common Pitfalls & Best Practices
Even though **creating a symbolic link in Linux** is straightforward, a few hiccups can crop up:
- **Dangling Links**: If the original file is deleted or relocated, your symlink points nowhere.
- **Permission Issues**: The symlink itself may be accessible, but if the target’s permissions aren’t right, you’ll be blocked.
- **Sudo / Root Ownership**: If you create symlinks as root, regular users might not be able to read or write, depending on the target’s permissions.
**Best Practices**:
- Document your symlinks if they’re part of a bigger system. This helps others (or future you) quickly see where things point.
- Use naming conventions that make sense. Instead of ln -s /home/projects/mything my-thing, you might go with my-thing-symlink or something descriptive.
- Avoid overusing symlinks. If you create too many, your file structure might become confusing.
## How to Remove a Symbolic Link in Linux
Removing a symlink is typically as easy as deleting any other file. So if you’re wondering **how to remove a symbolic link in Linux**, you can:
`rm /path/to/symlink`
OR
`unlink /path/to/symlink`
- **rm**: Treats the symlink as a file and removes it. This does not delete the target file - only the link.
- **unlink**: Another command that specifically removes a single file name. For symlinks, it’s effectively the same as rm.
**Important**: Don’t confuse removing the symlink with removing the original file. Deleting the symlink (rm) only kills the pointer, not the real data. That’s a good thing if your intent is to simply tidy up aliases.
## How to Delete a Symbolic Link in Linux vs. Removing a File
You might see references online about **how to delete a symbolic link in Linux** - it’s usually the same process as removing a file. However, keep these differences in mind:
- **Deleting a Symlink**: Freed up that pointer but the actual file remains.
- **Deleting a File**: You remove the data itself. If other symlinks pointed to that file, they become dangling.
If you’re unsure whether something’s a symlink, ls -l can reveal it with the leading l in the permissions field.
## Real-World Example: Linking a Config File
Let’s say you have an app that expects a config file at /etc/awesome_app/config.yaml, but you’d prefer to store all your configs in /home/janet/configs/. Try:
`sudo ln -s /home/janet/configs/awesome_app.yaml /etc/awesome_app/config.yaml`
- The symlink in /etc/awesome_app/ points to the “real” file in ~/configs. If you ever want to tweak the config, you just open ~/configs/awesome_app.yaml. The app sees it as if it were in /etc/awesome_app/.
When you no longer need that link:
`sudo rm /etc/awesome_app/config.yaml`
That only removes the link, not your awesome_app.yaml in ~/configs.
## Symbolic Links vs. Shortcuts on Other OS
- **Windows** has shortcuts, but they’re not exactly the same as Linux symlinks (though Windows has “symbolic links” in NTFS as well, it’s less commonly used by casual users).
- **macOS** uses a Unix-like system, so symbolic links behave similarly to Linux. They’re more robust than “aliases” in Finder, which are more akin to shortcuts.
Understanding these differences helps if you switch OS frequently or share code across different systems.
## Advanced Usage: Relative Symlinks and Scripts
**Relative Symlinks**
**We mentioned briefly that you can do ln -s ../original /destination, which can be handy if you anticipate changing mount points**. The link refers to a path relative to its own location, particularly useful when packaging software or distributing code that’s designed to run in consistent relative structure.
**Scripting**
**If you automate deployments or backups, you might:**
- **Create Symlinks** to fresh build directories. For instance, myapp -> myapp-2025-01-09 so you can quickly switch to a new version with minimal downtime.
- **Replace Symlinks** after building. Instead of overwriting a directory in place, you spin up a new folder, test it, then update the symlink to point to the new directory.
This approach can lead to seamless transitions, especially for web or app servers.
## Recap: The Life Cycle of a Symlink
- **Creating a symbolic link in Linux**: ln -s [target] [link_name]
- **Verifying**: ls -l [directory] or file [link_name] to confirm it’s a symlink.
- **Using**: Access the link like you would any folder or file.
- **Modifying**: If you move the original file, the symlink breaks (dangling). You’d have to recreate or update the link.
- **Removing**: rm [link_name] or unlink [link_name]. The real file remains intact.
**Important**: If multiple symlinks point to one file, removing one link doesn’t affect the others.
## Why Symbolic Links Matter for DevOps and Cloud Hosting
In modern DevOps workflows, symlinks can be indispensable. Why?
- **Config Management**: Instead of rewriting config paths every time, you can symlink an entire config directory into your container or server environment.
- **Rollbacks**: If a new version of your website fails, you can revert the symlink to the old version quickly.
- **Organizing Shared Files**: Suppose multiple microservices rely on the same data. A symlink ensures consistent referencing without duplicating data.
## Levamo: Hosting That Simplifies Your Symlink Life
All these tips on **how to create a symbolic link in Linux** are more fun when your hosting platform doesn’t trip you up with confusing file structures or unsupportive environments. Enter **[Levamo](/)**, a hosting service that:
- **Embraces Flexibility**: Levamo’s environment is designed for easy file and directory manipulation. That means no weird permission blocks or rigid structures hampering your symlinks.
- **Built for Collaboration**: If multiple team members deploy to the same servers, consistent symlink usage ensures everyone references the same file paths.
- **Scalable Infrastructure**: Rapidly spin up new servers or containers to handle load without losing track of your symbolic links. A stable environment means fewer broken references.
- **Support & Guidance**: If you’re unsure about file permissions, symlink usage, or best practices for production, Levamo’s expert team can help you keep everything tidy.
When you’re juggling multiple websites, logs, or app versions, symbolic links can streamline your workflow, especially in a robust hosting environment. That’s where Levamo stands out: combining top-tier hosting with straightforward management tools, letting you focus on building and linking your resources effectively, rather than constantly troubleshooting.
## Closing Thoughts
**Creating a symbolic link in Linux** is one of the simplest yet most powerful ways to keep your filesystem flexible and organized. It spares you from duplicating large directories, makes version rollouts simpler, and helps unify scattered files across your system. Sure, you can run into issues if you let symlinks sprawl out of control or forget that removing the original file leaves behind a dangling pointer. But with a little caution, symbolic links are a lifesaver for everyday tasks and advanced DevOps pipelines alike.
Now that you’ve learned **how to create a symbolic link in Linux** (and also **how to remove a symbolic link in Linux** when the time comes), you can approach your directory structure with newfound creativity - knowing that you can make your data appear wherever you need it, whenever you need it, minus the overhead of actually copying. So go forth, link up your config files, unify your logs, and lighten your file organization load. And if you want hosting that plays nice with your symlink habits, **Levamo** is here to smooth out your path. Happy linking!
---
## How to Build a BuddyBoss App in Less Than an Hour
- URL: https://levamo.com/blog/launch-buddyboss-app/
- Category: lms
- Author: Faisal Sarker
- Published: 2025-03-18
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Build a BuddyBoss app fast! Our guide gets you mobile in under an hour.
On average, it takes more than 90 minutes to watch a movie (not counting Marvel Universe), but less than one hour to build your own [BuddyBoss](/buddyboss-hosting/) mobile app!
Why does that matter, you say?
In these days of online socializing and learning, a BuddyBoss mobile app isn't just "nice-to-have" anymore - it's the key to boosting engagement, providing seamless access, and meaningfully connecting with your audience.
So, for all you BuddyBoss community managers, e-learning platform and membership site owners, and developers, we have a treat - a **step-by-step guide to building your BuddyBoss mobile app in under 60 minutes with no code**.
Ready? Start the clock!
## How to Build a BuddyBoss App - Step by Step
### Step 1: Connect Your BuddyBoss App to Your Website
The first order of business is to link your existing BuddyBoss website and the BuddyBoss App platform. To do this, you'll need the BuddyBoss App plugin installed and activated on your WordPress website.
So, go to your WordPress Admin dashboard and select **Plugins**> **Add New**, then **Upload Plugin**.
Once installed, connect the app to your website.
First, go to your BuddyBoss.com account, select **Apps**, then **Manage** to copy your **App ID** and **App Key**.
Copy these numbers and head back to your WP dashboard. Now go to **BuddyBoss App**> **Connect** and enter in the **App ID** and **App Key**.
Once your site is connected, you will see the following message:
*This site is now connected as your primary site.*
### Step 2: Configure Your BuddyBoss App
For starters, we'll handle the basics. Click **Configure** to specify the app's name, description, and icon under 'General Configuration'. After that's done, press **Save**.
### Step 3: iOS Configuration - Setting Up for Apple Devices
If you want your app to be available on the Apple App Store for iPhones and iPads (as you should), you'll need to venture into the iOS settings within the BuddyBoss App platform.
Head over to your Apple Developer account, then **App Store Connect** > **Users and Access** > **Keys**. Click the plus icon to add in a new API, then **Generate**.
You can now see a new API key generated, which you'll need to proceed. So, click **Download API Key.**

In a new pop-up window, press **Download**.
Now copy the **Issuer ID.**
Return to the WP Dashboard and BuddyBoss settings. Paste the **Issuer ID**, **Key ID**, and upload the **Apple API Key**.
That's it - your Apple Developer account is now connected!
You'll also want to add an Apple certificate. Open your Apple Developer account and select **Certificates, IDs, and Profiles.**
Pick **Identifiers**, then the plus icon to add in a new identifier.
Select **App IDs** and click **Continue.**
Add the App ID, select **Push Notifications,** and then click Continue.

Do the same for the release and test versions.
Go back to WP dashboard, select the test and release versions, and click **Save Configurations.**
Mac users will need to log in to their Apple Developer account and add a new app. Select the platform, primary language, Bundle ID, and the SKU version. Grant **Full Access** and press **Create**.
From the App Store Developer account, copy and paste the **Apple App ID** for the newly created BuddyBoss app, as well as the **App Specific Shared Secret** back into the WP main dashboard.
### Step 4: Add Your iOS Device for Testing
How else will you ensure that your app functions flawlessly and provides a great user experience if not via testing on real devices? For iOS, you'll need to add your iOS device to the BuddyBoss App platform for testing purposes.
Here's what you do: click **iOS Devices > Add New Device**. Then, add in the name of the new device.
From there on, scan the QR code using the same device you want to add to the list.
Voila - the device is now added.
### Step 5: Android Configuration - Setting up for Android Devices
Just like with iOS, you'll need to configure the Android settings within the BuddyBoss App platform to have it available on the Google Play Store and, hopefully, thousands of Android devices.
Make your way to the Google Play Store Developer account and click on **Create app**.
Provide the app name, make sure to select that it's a free app, then click on **Create app** after accepting the Terms and Conditions.
Now go to **Settings > Developer account > API Access > Create new project** and click on **Link a Project**.
Once you are inside the linked Google Cloud project, your next objective is to create a new service account. To do so, click **Create Service Account**.
Provide additional details such as Service account name, Service account, and Service account description. Click **Create** and then insert the necessary details of the remaining two steps if you want - both are optional.
You don't need to grant additional access to this service account. Click **Done.**
You will now see the BuddyBoss service that you recently created. Next on the list is to create a key by clicking on the three dots under **Actions** and selecting **Manage keys.**
Download the key as a JSON file and click **Create**.
Head over to the WP Dashboard and upload the JSON file you just downloaded in the **Android Settings**.
Your work is almost done - you have successfully connected your Google Play Store Developer account with the website.
As you've probably noticed, the main difference between Android and iOS is that you only need to provide one App ID in the former, whereas the latter requires separate versions.
All that's left to do is to create the **Application ID** and then click **Save Changes**.
All done!
### Step 6: Configure Firebase for Android
For Android apps built with BuddyBoss App, [Firebase](https://firebase.google.com/) (Google's mobile and web app development platform) is often used for push notifications and other backend functionalities. Hence, configuring it is a step you don't want to miss when setting up your Android.
To begin, we'll create a Firebase project (in case you don't have one already) in the [Firebase Console](https://console.firebase.google.com/).
Within your Firebase project, add a new Android app. You'll need to provide the Package Name you configured in the BuddyBoss App platform.
First, get the server key by going to **Settings**, **Cloud Messaging,** and copy the server key.
Firebase will generate a google-services.json file, so make sure to download it. The BuddyBoss App platform will have a section for Firebase configuration where you'll upload the google-services.json file.
Don't let this overwhelm you - Firebase configuration is primarily for enabling push notifications on Android and potentially other backend services. Moreover, the BuddyBoss App platform streamlines this integration so you won't break a sweat.
### Step 7: App Settings
With the basic configurations and platform-specific settings in place, it's time to fine-tune your app's functionality and user experience through the App Settings within the BuddyBoss App platform.
Here's what you do:
- **Navigation Menu:** Customize the app's navigation menu by choosing which menu items to include (e.g., Activity Feed, Groups, Forums, Courses, Members) and arranging them in a way that makes sense for your users.
- **User Roles and Permissions:** Control who can access what within the app. You can often mirror the user roles and permissions you've set up on your BuddyBoss website, ensuring consistent access control.
- **Feature Configurations:** Depending on the BuddyBoss App platform's features, you might have options to configure specific functionalities. This could include settings for push notifications, in-app purchases (if applicable), and integrations with other services.
- **Appearance Settings:** This is where you go beyond the basic branding colors and further refine the visual appearance of your app. This includes customizing fonts, button styles, and other UI elements to align with your brand aesthetics.
The point here is that you can absolutely tailor the mobile experience to perfectly match your community's needs and overall platform strategy.
### Step 8: Customize the App Branding - Make it Truly Your Own
As you may or may not know, branding is key to making your app feel like a natural extension of your online community. The BuddyBoss App platform provides robust customization options to make sure that your app truly reflects your brand identity. This includes:
- **Logo Customization:** Upload your brand logo to be prominently displayed within the app, often in the header or navigation areas.
- **Color Scheme Refinement**: Basic branding colors are fine, but you want to tweak the color palette used throughout the app and make everything pop. That said, try to ensure that your color choices enhance readability and go in line with your brand guidelines.
- **Splash Screen Design**: Create a visually engaging splash screen that reinforces your brand identity and leaves a positive first impression when users launch the app.
- **Custom CSS (Optional, for Advanced Users):** For those with coding knowledge, the BuddyBoss App platform offers the option to add custom CSS (Cascading Style Sheets) for even more granular control over the app's visual appearance.
Don't be fooled - branding customization is as much about functionality as it is about having a visually appealing and brand-consistent experience for your users.
### Step 9: Expand Functionality by Adding App Pages as Necessary
While the BuddyBoss App platform automatically brings in your core BuddyBoss website features, you might want to take a minute and think about adding custom pages to your app for specific content or functionality, such as:
- **Custom Pages:** Build completely new pages within your app. This could be for welcome messages, promotional content, resource libraries, or any other information you most definitely want to make easily accessible within the app.
- **Webview Pages (Linking to Website Sections):** Embed specific sections of your BuddyBoss website within the app using webview pages. This is useful for seamlessly integrating content that's primarily managed on your website but needs to be accessible within the app.
- **External Links:** Add links to external sites or resources that are relevant to your community.
In a nutshell, adding app pages allows you to offer more to your users beyond the core BuddyBoss features and provide a richer, more tailored experience they will appreciate.
### Step 10: Build Your App - Compiling for iOS and Android
Since we did all the configurations and customizations tasks, the time has come to build your app. This is where the BuddyBoss App platform takes over the technical heavy lifting.
- **Initiate Build Process:** Within the BuddyBoss App platform dashboard, you'll find a "Build" button. Click this to start the app building process.
- Platform Handles Compilation: The BuddyBoss App platform will automatically compile your app for both iOS and Android platforms. You don't need to worry about complex coding or compilation steps.
- Build Time (Under an Hour!): The platform is designed for rapid app building. In most cases, the build process will be completed in well under an hour, often within minutes.
The "Build" step is remarkably simple thanks to the BuddyBoss App platform, allowing you to focus on your content and community rather than technical complexities.
### Step 11: Install and Test Your App - Ensuring a Smooth User Experience
Once the build is complete, it's crucial to install and thoroughly test your app on both iOS and Android devices before launching it to your wider community.
- Download Test Builds: From the BuddyBoss App platform, download the test builds for both iOS (.ipa file) and Android (.apk file).
Install on Devices:
- iOS: Use a tool like TestFlight (often provided or guided by BuddyBoss App platform) to install the .ipa file on your registered iOS device.
- Android: Install the .apk file directly onto your Android device (you may need to enable "Install from Unknown Sources" in your device settings temporarily for testing purposes).
Thorough Testing: Test every aspect of your app:
- Navigation: Ensure menus and links work correctly.
- Content Display: Verify that all your BuddyBoss content (posts, groups, courses, etc.) is displaying correctly within the app.
- Features: Test all features like posting, commenting, joining groups, accessing courses, push notifications (if configured), etc.
- User Experience: Evaluate the overall user experience - is it smooth, intuitive, and visually appealing?
- Identify and Report Issues: If you find any issues during testing, report them to the BuddyBoss App platform support team or address them through configuration adjustments within the platform.
Thorough testing is essential to catch any glitches and ensure your app provides a polished and professional experience for your users from day one.
### Step 12: How to Manage Your BuddyBoss App from the Levamo Dashboard
The Levamo Dashboard serves as your central command center for managing your BuddyBoss mobile app after it's launched.
- App Updates: Deploy updates to your app directly through the Levamo Dashboard. This simplifies the process of releasing new features, bug fixes, and content updates without requiring users to manually update from app stores every time (depending on the type of update).
- Analytics: Access analytics and usage data for your app through the dashboard. This valuable information helps you understand how users are engaging with your app, identify popular features, and make data-driven decisions to improve the app over time.
- User Management (Potentially): Depending on the specific features of the BuddyBoss App platform and Levamo Dashboard, you might have some level of user management capabilities directly within the dashboard.
- Push Notification Management: If you've configured push notifications, the dashboard is typically where you'll manage and send out push notifications to your app users.
The Levamo Dashboard provides ongoing management capabilities, ensuring your BuddyBoss app remains dynamic, engaging, and aligned with your community's evolving needs.
## Conclusion: Ready to Launch Your Dream Mobile App?
Building a mobile app for your BuddyBoss community doesn't have to be a complex, time-consuming, or expensive endeavor. The BuddyBoss App platform has truly democratized app development, putting the power to create a professional, native mobile app directly into your hands - in under an hour!
By following these simple steps, you can transform your BuddyBoss website into a mobile powerhouse, reaching your members wherever they are, boosting engagement, and taking your community to the next level.
If you're still unsure about BuddyBoss, check out our detailed [BuddyBoss review](/blog/buddyboss-review/) and I'm sure you'll be enticed to use this wonder platform.
So what are you waiting for? Stop dreaming about a mobile app and start building! The BuddyBoss App platform makes it faster and easier than you ever imagined. Launch your dream mobile app today and unlock the full potential of your online community.
And if you need a [BuddyBoss hosting](/buddyboss-hosting/) that is optimized for your mobile app, try Levamo's [best wordpress hosting for high traffic](/managed-wordpress-hosting/) today.
## Frequently Asked Questions

### Why use BuddyBoss?
BuddyBoss stands out as a powerful platform for building online communities and membership sites on WordPress. Its key benefits include comprehensive community features, flexibility and customization and powerful e-learning Capabilities.
### How to set up BuddyBoss?
Setting up BuddyBoss involves a few key steps:
- Content and Community Building.
- WordPress Installation.
- BuddyBoss Theme and Platform Plugin Installation.
- Configuration.
### How do you build your own app using BuddyBoss?
Building your own app using BuddyBoss is remarkably straightforward thanks to the BuddyBoss App platform. As detailed in this blog post, the process involves:
- Connecting your BuddyBoss website to the BuddyBoss App platform.
- Configuring basic app settings, iOS and Android settings.
- Customizing branding and adding optional app pages.
- Building the app with a click of a button.
- Testing and launching your app.
The BuddyBoss App platform is designed to be no-code, meaning you don't need programming skills to create a professional mobile app.
### Is BuddyBoss open source?
No, BuddyBoss is not fully open source. It is a commercial product with a proprietary license. However, it is built on top of WordPress, which is open source.
### How much does it cost to build a custom app?
The cost of building a custom mobile app through traditional development can vary wildly depending on complexity, features, and the development agency you hire. It can easily range from $15,000 to $100,000 or even more. Factors influencing cost include complexity of features, platform, location of the agency or freelancers, etc.
---
## MySQL Performance Tuning: Give Your Database a Turbo Boost
- URL: https://levamo.com/blog/mysql-performance-tuning/
- Category: database
- Author: Salman
- Published: 2025-03-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Tune MySQL for speed! Fix bottlenecks and boost database performance now.
Have you ever clicked on a website or app, only to wait… and wait… for it to load? Odds are, a pokey MySQL database is at least partially to blame. Whether you’re running a small online store or a busy SaaS platform, making sure MySQL is well-tuned can mean the difference between snappy load times and frustrated visitors who bounce before they ever see what you offer. Below, we’ll walk through the fundamentals of **MySQL Performance Tuning** - from spotting bottlenecks to implementing quick fixes - so you can keep your users happy and your stress levels low.
### Why Does MySQL Performance Even Matter?
Picture a bustling café with just one barista. When there are only a few customers, everyone gets their latte with no problem. But let a tour bus full of caffeine-craving tourists roll in, and suddenly you’ve got a mob, a swamped barista, and unhappy people waiting in line.
That’s what happens when your database runs into heavier load than it’s prepared for: queries stack up, the CPU and memory start groaning, and users see spinning wheels instead of instant results.
- **User Experience**: Slow queries drive people away. Who wants to wait 10 seconds for a product page to load?
- **Resource Costs**: An under-optimized database can chug CPU and disk resources, hiking up hosting bills or causing other apps on the server to lag.
- **Scalability**: Well-tuned MySQL can handle more data, more users, and more sales. It’s like giving your barista a fancy espresso machine that cranks out drinks twice as fast.
### Common Culprits Behind a Sluggish Database
Let’s face it: MySQL is a workhorse, but it only does what we tell it to. Some typical reasons you might be hitting snags:
- **Inefficient Queries**: Maybe your code is scanning entire tables when it only needs a few rows. That’s like searching every drawer in your house for the car keys in your pocket.
- **Missing or Poor Indexes**: Without the right indexes, MySQL might scan hundreds of thousands of rows, slowing everything down to a crawl.
- **Too Little Memory**: If MySQL doesn’t get enough RAM for caching, it can’t keep frequently accessed data in memory - resulting in repetitive disk hits.
- **Unoptimized Default Settings**: The default MySQL configuration might be fine for small test setups, but it often doesn’t cut it for larger or specialized workloads.
- **Locking & Concurrency**: If lots of queries are trying to update the same table at once, they can bump elbows and queue up.
**Pro Tip:** Use EXPLAIN on your queries. It’s like an x-ray for your SQL, showing you if MySQL is using indexes or scanning entire tables. Once you see the trouble, you can fix it.
### Tuning Basics: A Game Plan
Before you dive in, do a quick reality check:
- **Measure Before, Measure After**: Track query times or resource usage so you can see if your changes help or hurt.
- **Take It Step by Step**: Try one optimization at a time. Throwing everything at the wall might fix your speed issues, but if something breaks, you won’t know which step caused it.
- **Don’t Forget Backups**: If your schema or data is critical, always have a solid backup plan before tinkering.
## 1. Tune Queries First
Often, the most glaring performance issues come from the queries themselves. Think of a badly written SQL statement like a grocery list in random order, making you zigzag through the store. Let’s fix that:
**a. Use EXPLAIN**
- Running EXPLAIN SELECT ... reveals how MySQL navigates your query. If you see “ALL” in the output, that’s a full table scan, a major red flag.
**b. Avoid SELECT**
- Snag only the columns you actually need. Grabbing everything just bloats data transfer and memory use.
**c. Restrict the Rows**
- Keep your WHERE clauses tight so MySQL only fetches relevant data. Filtering in your application code instead of SQL means you’re shipping more data than needed.
**d. Rethink Joins**
- Sometimes complicated joins across multiple tables slow things down. If a particular join is a bottleneck, consider if there’s a more efficient approach (like a single table or simpler logic).
## 2. Smart Indexing
Indexes are like the index at the back of a book - without them, you’re flipping pages randomly to find what you need:
**a. B-Tree Indexes**
- Standard indexes for columns you frequently filter (e.g., WHERE user_id = 123). MySQL uses these to quickly “jump” to the right row, instead of scanning the entire table.
**b. Composite Indexes**
- If you often filter by two or more columns, you might benefit from an index that covers them in the order you typically query them.
- Example: WHERE category = 'Tech' AND status = 'Active' might speed up if you have (category, status) in a composite index.
**c. Beware of Over-Indexing**
- Each time you insert or update a row, MySQL also updates indexes. Having too many indexes can bog down writes, so only keep the ones you really need.
## 3. Memory and Configuration Tweaks
Even well-crafted queries can be held back if MySQL is starving for memory or stuck with low default settings:
**a. InnoDB Buffer Pool**
- If you’re using InnoDB (the usual engine), the buffer pool is your best friend. It stores indexes and data in memory. Allocating about 70-80% of your server’s RAM to the buffer pool can be a game changer (assuming MySQL is the server’s main role).
**b. Query Cache**
- In older MySQL releases, there’s a query cache that can store results for repeated queries. But watch out for high-concurrency environments; the query cache can cause contention. In more modern versions, it’s often deprecated or turned off.
**c. Temporary Table Settings**
- Large ORDER BY or GROUP BY queries might need temp tables. Adjust tmp_table_size and max_heap_table_size so MySQL can handle bigger temp tables in memory, avoiding slow disk-based tables.
**d. Slow Query Log**
- Flip it on to see queries that exceed, say, 2 seconds. This single step can reveal which queries to focus on.
## 4. Schema Design Considerations
A sleek schema often translates to faster queries:
- **Use Proper Data Types**: Don’t always default to VARCHAR(255) if you only need 50 characters. Overkill data types can slow queries and bloat your database.
- **Normalization vs. Denormalization**: While normalizing avoids duplication, it can lead to a lot of joins. For read-heavy tables, some denormalization (storing certain data redundantly) might boost performance.
- **Avoid Super-Wide Tables**: Fifty columns in one table can get unwieldy. Splitting out rarely used columns into their own table might keep your main table lean and fast.
## 5. Additional MySQL Performance Tuning Tips
Here’s a grab bag of smaller but impactful tweaks:
- **Batch Operations**: If you’re inserting a ton of rows, do it in chunks rather than one-by-one.
- **Partition Large Tables**: For very large data sets, partitioning can make queries more selective (e.g., by date range).
- **Use Connection Pooling**: Avoid overhead by reusing connections rather than opening and closing them repeatedly.
- **Schedule Heavy Jobs Wisely**: Run big reports or data imports during off-peak hours if you can.
## 6. Monitoring and Maintenance
MySQL tuning isn’t a one-shot deal. As your data and traffic grow, so do new performance challenges. Make sure you:
- **Monitor Resource Usage**: CPU, disk I/O, memory consumption - some spikes are normal, but big, lasting jumps suggest you need adjustments.
- **Review Queries Regularly**: If you add new features or pages, keep an eye on new queries. They might not be as polished as your older ones.
- **Update MySQL**: New releases often come with performance improvements. Just ensure your application is compatible before you upgrade.
## 7. Levamo: Hosting That Simplifies Your MySQL Work
All these tuning tactics can feel like a full-time job - especially if you’re also juggling code, front-end design, or marketing. That’s where **Levamo** fits in. Imagine a hosting environment that respects your database needs out of the box, with built-in metrics and an expert support team to help you fine-tune your MySQL settings.
**What Levamo Brings to the Table**:
- **Optimized Environment**: Right from the get-go, Levamo aligns memory allocation, caching, and security defaults to typical use cases.
- **Seamless Scaling**: If you need more RAM or CPU as your queries grow bigger, scale up in a few clicks - no complicated migrations.
- **Managed Security**: With robust firewall rules and intrusion detection, you’ll face fewer incidents that might degrade performance or force downtime.
- **One-Stop Monitoring**: Track your MySQL resource usage and slow queries within the same dashboard you manage your servers. It’s all integrated, saving you from flipping between different tools.
So if you’re tired of playing guess-and-check on your MySQL performance, consider letting **Levamo** do some of the heavy lifting. Your database (and your nerves) will thank you.
## 8. Final Thoughts
When it comes to **MySQL Performance Tuning**, small changes add up. A better index here, a buffer pool tweak there, or rewriting a bloated query - it all helps your site run smoother. That’s good news for your users, your hardware budget, and your own sanity. Just remember: measure performance before and after changes, keep backups handy, and stay open to continuous refinement as your workload evolves.
And if you ever feel lost in the weeds, or you’re ready for hosting that just “gets” MySQL from the start, take **Levamo** for a spin. After all, you deserve a database that can keep up with your ambition - minus the stress and downtime.
---
## Top 20 WordPress Ecommerce Themes in 2025: The Best Picks
- URL: https://levamo.com/blog/wordpress-ecommerce-themes/
- Category: website-design
- Author: Sunyyan Junaid
- Published: 2025-03-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find the top 20 WordPress ecommerce themes for 2025. See our best picks!
In 2025, choosing the right **WordPress ecommerce theme** for your online store is more critical than ever. Why? Because there's a plethora of choices, and choosing the wrong theme can waste plenty of time, money, and resources for you.
So, how do you choose the best ecommerce theme for WordPress? You leave it to the pros to do the research and find the top ones.
Drawing on countless discussions from Reddit, Quora, and industry forums, along with insights directly sourced from the WordPress.org repository, I’ve compiled a list of the top **20 best ecommerce themes for WordPress** that are shaping ecommerce success today. And while yes, your [web host](/) makes a huge difference in how your website performs, the theme you choose also plays its part in how successful your business is.
Let’s dive into the top ecommerce themes, share some real-life experiences, and see how each one stacks up in terms of performance and user satisfaction.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## Why Your Theme Choice Matters
Before we get into the nitty-gritty of our list, consider this: a website’s look and feel isn’t just about first impressions. According to *WP Tavern*, well-optimized themes improve page load speeds by around 30% on average, which is critical for retaining customers and reducing bounce rates.
Here’s something a longtime WordPress developer shared on Reddit:
“I switched to a responsive, well-coded **WordPress ecommerce theme** last year, and my mobile conversions shot up by 25%. It’s amazing what a difference the right theme can make!”
These numbers aren’t just statistics. They’re a wake-up call for anyone still using a basic or outdated design/theme for their ecommerce stores. As we explore the best WordPress ecommerce themes, remember that functionality, speed, and user experience are paramount, which is what we’ve kept in mind while picking these top 20 themes for your ecommerce store in 2025.
## The List: Top 20 WordPress Ecommerce Themes in 2025
Below is our carefully curated list of the 20 top ecommerce themes, complete with ratings from the WordPress.org repository and insights gathered from community discussions. Whether you’re interested in premium options or exploring free **WordPress ecommerce themes**, there’s something here for everyone.
### 1. Astra

[Astra](https://wpastra.com/) is one of those themes that feels almost invisible in its speed and flexibility. I’ve read about developers who switched from bulky themes to Astra and suddenly found themselves enjoying faster load times and endless customization options. Some even joked that it felt like upgrading from an old clunker to a zippy sports car. So if you want one of the best ecommerce WordPress themes that handles ecommerce without fuss and lets you tinker around freely, Astra is a solid bet.
**Community Insight**: "Astra’s customization options are endless. It’s the foundation upon which I built multiple high-conversion stores."
**Rating**: 4.8/5
**Active Installations**: 1 million+
**Pricing**: Free version available; Astra Pro starts at $59.
**[Read our Astra Theme Review](/blog/astra-wordpress-theme-review/)**
### 2. OceanWP

[OceanWP](https://oceanwp.org/) is like a Swiss Army knife for your website. It offers a variety of demos that work seamlessly with [WooCommerce](/managed-woocommerce-hosting/) and a support system that even beginners find approachable. Users have shared that its versatility allowed them to switch from a niche boutique to a tech store without missing a beat. It adapts effortlessly to many ecommerce needs.
**Community Insight**: "OceanWP’s detailed guides and endless demos made setting up my store surprisingly straightforward."
**Rating**: 4.7/5
**Active Installations**: 700,000+
**Pricing**: Free version available; premium extensions are offered in various bundles starting around $39, with lifetime options near $129.
### 3. Storefront

[Storefront](https://wordpress.org/themes/storefront/) is that dependable friend who always comes through when you need something simple and reliable. Developed by the WooCommerce team, it integrates perfectly with all the extensions you might need. Many have praised its no-nonsense approach that helps get your site up quickly without unnecessary frills.
**Community Insight**: "Storefront's simplicity helped me launch my first store with zero headaches, and it grows with you."
**Rating**: 4.6/5
**Active Installations**: 100,000+
**Pricing**: Completely free.
### 4. Flatsome

[Flatsome](https://demos.flatsome.com/) is a crowd-pleaser for those who love a hands-on approach to design. Its drag-and-drop builder and live preview make customizing your store feel like a fun experiment. Designers love it for cutting down the guesswork, allowing them to adjust their layout on the fly.
**Community Insight**: "Flatsome’s live preview feature is a game changer. I can see my changes instantly, which saves tons of time."
**Active Installations:** Approx. 252000+
**Rating**: 4.8/5
**Pricing**: $59.
### 5. Neve

[Neve](https://themeisle.com/themes/neve/) is built with a mobile-first mindset, keeping your site lean and speedy. Many small business owners have shared that its minimalist design and quick load times significantly improved their user engagement. It feels future-proof, especially in a world where mobile browsing dominates.
**Community Insight**: "Switching to Neve doubled my mobile traffic thanks to its slick, fast-loading pages."
**Rating**: 4.7/5
**Active Installations**: 100,000+
**Pricing**: Free version available; Neve Pro starts at about $69 per year.
### 6. Hestia

[Hestia](https://themeisle.com/themes/hestia/) brings a cool minimalist vibe that makes your products stand out. Its clean design cuts out distractions and lets your merchandise shine. Many users, especially from startups, have noted that its integration with popular page builders helps them craft a modern, uncluttered look with ease.
**Community Insight**: "Hestia’s clean lines and simple interface helped me create a welcoming shopfront that feels both modern and inviting."
**Rating**: 4.5/5
**Active Installations**: 100,000+
**Pricing**: Free version available; Hestia Pro is around $69.
### 7. Divi

[Divi](https://www.elegantthemes.com/gallery/divi/) is like having a creative studio right at your fingertips. Its visual builder allows you to experiment with layouts until you find one that truly fits your brand’s personality. Many entrepreneurs find the real-time design changes refreshing, saving them hours of tweaking and testing.
**Community Insight**: "Divi lets me experiment on the fly. It's like having a digital sketchpad where I can quickly transform ideas into reality."
**Rating**: 4.6/5
**Active Installations**: Approx. 2.1 million+
**Pricing**: Available as part of an Elegant Themes membership at $89 per year or $249 for lifetime access.
### 8. Kalium

[Kalium](https://kaliumtheme.com/) adds a touch of elegance to your online presence. Creative professionals adore it for its refined typography and layout options, which bring a premium feel to any store. If you want your site to look upscale and polished, Kalium delivers with style.
**Community Insight**: "Kalium's elegant design elements helped us convey a high-end brand image effortlessly."
**Rating**: 4.7/5
**Active Installations**: N/A.
**Pricing**: $60.
### 9. Shopkeeper

Shopkeeper is built specifically for ecommerce, with a layout that puts your products in the spotlight. Users appreciate how its straightforward design improves navigation and engagement. It’s a solid choice if you’re aiming to make shopping as smooth and intuitive as possible.
**Community Insight**: "After switching to Shopkeeper, my product pages became much more user-friendly, and I saw a noticeable uptick in conversions."
**Rating**: 4.6/5
**Active Installations**: N/A.
**Pricing**: $59.
### 10. WoodMart

WoodMart is designed for those managing large inventories. Its advanced filtering options and customizable layouts keep even massive product catalogs organized and fast. Developers and store owners alike praise it for maintaining speed and efficiency regardless of scale.
**Community Insight**: "WoodMart handles large catalogs like a champ. It keeps my site responsive even when the product list runs into the hundreds."
**Rating**: 4.8/5
**Active Installations**: N/A.
**Pricing**: $59.
### 11. Porto

Porto offers flexibility that adapts to a wide range of business models. With numerous demos available, it lets you rebrand quickly as your business evolves. Users often mention that its design options make it easy to find the right look for your niche, whether it's fashion, tech, or something else entirely.
**Community Insight**: "Porto’s variety of demos meant I could change my site’s look with minimal effort when I pivoted my business model."
**Rating**: 4.5/5
**Active Installations**: N/A.
**Pricing**: $59.
### 12. Electro

Electro is tailored for tech and electronics stores. It highlights product features with a clean and modern design that appeals to tech enthusiasts. Users have noted that its focused layout makes it easy for customers to sift through technical details and make informed choices.
**Community Insight**: "Electro speaks my language. It’s built for electronics, making it easy for my customers to navigate technical specs and features."
**Rating**: 4.6/5
**Active Installations**: N/A.
**Pricing**: $59.
### 13. XStore

XStore is like a buffet of design options, offering a range of demos for almost any ecommerce niche. Entrepreneurs love its ease of use, saying it allowed them to set up shop quickly and experiment with different looks until they found the perfect fit.
**Community Insight**: "XStore's diverse demos gave me the freedom to create a store that truly reflects my brand without the usual hassle."
**Rating**: 4.7/5
**Active Installations**: N/A.
**Pricing**: $59.
### 14. Savoy

Savoy is all about simplicity, stripping away clutter so that your products take center stage. Many users find that its minimalist design creates an inviting atmosphere that naturally draws in customers. It works especially well for high-end or luxury brands that want to keep the focus on quality.
**Community Insight**: "Savoy’s clean, distraction-free layout helped me create an online store that feels exclusive and refined."
**Rating**: 4.5/5
**Active Installations**: N/A.
**Pricing**: $49.
### 15. TheGem

TheGem blends creative flair with practical design. It is packed with unique layouts and cool effects that let you tell your brand’s story in vivid detail. Many designers appreciate its flexibility, which allows them to experiment until they find a look that truly stands out.
**Community Insight**: "TheGem’s unique design options let me build a site that feels as individual as my brand, with plenty of room to innovate."
**Rating**: 4.6/5
**Active Installations**: N/A.
**Pricing**: $59.
### 16. **REHub**

REHub is a versatile choice that goes beyond standard ecommerce. It works well for affiliate marketing, review sites, and comparison setups, offering a blend of functionalities in one package. Users find its multipurpose nature invaluable for creating a site that can evolve with their business needs.
**Community Insight**: "REHub let me combine reviews, comparisons, and ecommerce seamlessly. It’s a true multi-tool for online business."
**Rating**: 4.5/5
**Active Installations**: N/A.
**Pricing**: $59.
### 17. Uncode

Uncode makes a statement with its striking design and attention to detail. It is favored by those who want a site that is both visually engaging and professional. Users have praised its creative elements, from smooth animations to carefully aligned layouts, that leave a lasting impression.
**Community Insight**: "Uncode’s meticulous design tools helped me create a site that stands out visually without sacrificing performance."
**Rating**: 4.7/5
**Active Installations**: N/A.
**Pricing**: $59.
### 18. Bridge

Bridge offers a mix of creative style and solid functionality. Its range of demos lets you experiment with different looks until you find the perfect balance for your brand. Users enjoy the flexibility and find that it brings a polished, professional look to their online presence.
**Community Insight**: "Bridge feels like having an entire design team at your disposal, giving you the freedom to shape your site exactly how you envision it."
**Rating**: 4.6/5
**Active Installations**: N/A.
**Pricing**: $59.
### 19. Betheme

Betheme is a treasure trove of design possibilities with hundreds of demos at your disposal. It gives you the freedom to try out various layouts without feeling boxed in. Many entrepreneurs appreciate the creative freedom it offers, allowing them to experiment and innovate on the fly.
**Community Insight**: "Betheme's vast selection of demos allowed me to find a design that perfectly matched my brand's personality without any compromises."
**Rating**: 4.5/5
**Active Installations**: N/A.
**Pricing**: $59.
### 20. Jevelin

Jevelin is built for simplicity and elegance, making it an ideal choice for those who want a professional look without the steep learning curve. Users often mention how its ready-to-use demos helped them launch a stylish store quickly, with minimal hassle. It’s a friendly option for newcomers and veterans alike.
**Community Insight**: "Jevelin's intuitive design and easy setup allowed me to get my store live in record time, all while looking sharp."
**Rating**: 4.6/5
**Active Installations**: N/A.
**Pricing**: $59.
So there you have it. These are our top picks of the best ecommerce theme for WordPress and picking any of these for your online store would be a good choice.
## Diving Deeper: Actionable Checklist for Choosing Your Theme
Selecting a theme isn’t just about picking the one with the highest rating. Here are some actionable tips to help you decide:
**Assess Your Needs:**
- Are you starting small or planning a massive inventory?
- Do you need extensive customization or a plug-and-play solution?
- Write down your must-haves before browsing for a **WordPress ecommerce theme**.
**Test Responsiveness:**
- Mobile optimization is non-negotiable.
- Use demo versions to test page load times and responsiveness.
- As one user on Reddit put it, “A theme that doesn’t perform on mobile is a non-starter in 2025.”
**SEO & Speed:**
- Look for themes that emphasize speed, as they directly affect SEO and conversion rates.
- According to *Google’s research*, even a 0.5-second delay can drop conversion rates by up to 7%.
**Customization & Flexibility:**
- Whether you lean towards premium options or prefer WordPress ecommerce themes Free, ensure your choice allows room for growth and personalization.
- Consider the ease of integrating plugins and custom code if needed.
**Community & Support:**
- Themes backed by strong developer communities and user support forums tend to be more reliable.
- Always check user reviews and ratings on WordPress.org before making a decision.
## Why Your Ecommerce Theme Needs Levamo
Choosing a great ecommerce theme sets the stage for your store’s look and feel, but the real magic happens when you combine that theme with powerful hosting. That’s exactly why Levamo exists. We built Levamo as the [best wordpress hosting for high traffic](/managed-woocommerce-hosting/), specifically for ecommerce stores like yours, where speed, stability, and performance really matter.
What makes Levamo different? First off, we use [super-fast NVMe SSD storage](/performance/), advanced caching, and dedicated [PHP workers](/blog/php-workers/), all of which translate into blazing-fast page load times. Whether you're rocking a sleek theme like Flatsome or a streamlined, speed-focused theme like Neve, your customers will notice the difference immediately. No more waiting around for pages to load; just instant, smooth browsing.
And because we know ecommerce traffic can be unpredictable, our hosting automatically scales to handle sudden spikes. So, when your store gets flooded with visitors during sales or holiday seasons, you won't stress about slowdowns or crashes.
The bottom line: pairing your theme with Levamo isn't just about speed, it's about converting more visitors into buyers. Faster sites mean happier customers, fewer abandoned carts, and better sales. No matter which theme you pick, Levamo makes sure it runs at peak performance, giving your business the edge it needs.
**You’re All Set for a Great Experience**
Choosing the right WordPress Ecommerce theme can feel overwhelming with so many options available, but remember that the theme you select is an investment in your brand’s future. We’ve seen firsthand through user experiences and community discussions that the right design can lead to higher engagement, better user retention, and ultimately, increased revenue.
For those just starting out, consider exploring some of the highly-rated free WordPress Ecommerce theme options to get your feet wet. As your store grows, transitioning to a premium theme might just be the strategy that propels you to the next level.
And couple your theme with a powerful cloud hosting solution like Levamo, and you’re well on your way to immense success! 🚀
## Frequently Asked Questions

### Is WordPress any good for eCommerce?
Powering nearly 40% of the internet, WordPress is an excellent choice for ecommerce website development. It is free, open-source and provides more freedom and control over your site as compared to other closed-source platforms.
### Which WordPress theme is best for eCommerce?
There is no definite answer to this question as the best choice varies based on different requirements. If speed and SEO matter the most, then Astra, Divi and GeneratePress stand out.
### What is the fastest eCommerce WordPress theme?
Astra, Divi, and GeneratePress are some of the fastest that performed beyond our expectations in speed tests. But other themes on this blog are equally good.
### Which theme works best with WooCommerce?
What works best for one entrepreneur may not work best for the other. Hence, what works best for you is based on your requirements, design, product fit, niche, and the target audience.
---
## What Are PHP Workers and Why Do You Need Them?
- URL: https://levamo.com/blog/php-workers/
- Category: php
- Author: Sunyyan Junaid
- Published: 2025-03-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
PHP workers boost website speed. Find out why your site needs them.
The early days of the internet were straightforward: a web server would receive a page request, run a PHP script, and generate the HTML markup for the request. For years, everything ran smoothly - until it didn’t, as websites grew more complex.
Each individual page request used to trigger the PHP interpreter to start up, process the code, and shut down again. This was inefficient.
Enter the idea of 'workers' - persistent background processes that stay active, always ready to handle incoming requests.
And so, PHP workers were born, quickly becoming a vital component of modern [web hosting](/).
## What Are PHP Workers, Exactly?
PHP workers are processes running on your [web server](/blog/web-host-vs-web-server/) that handle and process page requests made by visitors to your website. Whenever a user interacts with your site, whether by clicking a link, submitting a form, or performing any other action, PHP workers are responsible for executing the necessary PHP code and returning the right content to the user’s browser.
Want to watch a video instead?
https://www.youtube.com/watch?v=Hq977L70ElE
No? Okay, read on!
In simpler terms, think of PHP workers as the behind-the-scenes team that ensures your website functions as intended. They process each action on your site, making sure the right information is delivered at the right time, without delays. If your website has multiple visitors or complex functions, more PHP workers can be added to handle the load efficiently.
## How Many PHP Workers Do You Need?
The number of PHP workers you need depends on several factors related to your website's traffic and complexity. These include:
- **Website Traffic**: The more visitors your site has, the more PHP workers you’ll need to handle multiple simultaneous requests. For high-traffic websites, having more workers ensures that users don’t experience slow load times or timeouts.
- **Website Complexity**: If your site is simple, with basic pages and minimal server-side processing, fewer PHP workers will fit the bill. But if your website is more dynamic, with complex databases, third-party integrations, or custom PHP scripts, you may need additional workers to handle those processes without a problem.
- **Hosting Environment**: The hosting plan you use often determines how many PHP workers are available. Shared hosting plans typically offer fewer workers, while VPS (Virtual Private Server) or dedicated hosting plans provide more flexibility and resources.
- **Peak Traffic Times**: If your site experiences sudden traffic spikes (for example, during promotions, product launches, or seasonal sales), you'll need extra PHP workers to handle the increased load. In such cases, scaling up the number of workers temporarily can prevent slowdowns.
- **Performance Goals**: If you prioritize fast page loads and a smooth user experience, having enough PHP workers to process requests efficiently is crucial. If you notice slow page loads or errors related to server timeouts, you might need more workers to improve performance.
As such, the number of PHP workers you need depends on your website's traffic and complexity. For a small eCommerce store with low traffic, a few PHP workers may do the trick. As your customer base grows and more people browse products and complete purchases, you’ll need additional PHP workers to avoid delays and slowdowns.
Imagine a scenario where a large number of customers try to check out at the same time. Without sufficient PHP workers, some customers may experience slow load times or even timeouts.
But simply adding more PHP workers isn’t always the solution. If your server isn’t powerful enough, increasing the number of workers won’t help much.
For example, [Levamo's Startup Plan](/pricing/) gives you 36 PHP workers, which are enough to handle 500,000 estimated visits.
But as your website grows and your visitors and needs grow, you need more PHP workers to handle all the requests. That's why the Performance plan on Levamo has 292 auto-scaling PHP workers.
Think of it like an online store needing better infrastructure to handle more customers and transactions - your server will need an upgrade to efficiently support additional PHP workers. More RAM and CPU power will help your website manage more traffic, ensuring trouble-free performance during peak periods like seasonal sales or major shopping events.
## Understanding PHP Worker Limits in Hosting Plans
So far, we know that PHP workers handle various tasks on your website: executing PHP code, managing background processes, running database queries, and generating pages. However, many managed hosting providers limit the number of PHP workers in their plans, only allowing more when you upgrade to a higher-tier plan.
The reason for these limitations is simple: restricting PHP workers helps manage server resources and prevents any single user from consuming too much of the server’s capacity. For hosting providers, limiting PHP workers also helps control operational costs, ensuring a balance between performance and expenses.
It’s important to note that [Levamo automatically scales](/performance/) PHP workers based on your website’s traffic and server specs, ensuring optimal performance for you and other users without bottlenecks. When selecting a hosting provider, be sure to check how PHP workers are allocated and whether there are any limits in place.
## Impact of PHP Workers on Your Website Performance
How’s this for impact: PHP workers play a crucial role in processing website requests that do not hit the cache.
When a visitor accesses a WordPress website, the web server forwards the request to a process manager like PHP-FPM. It oversees a pool of waiting PHP background processes (the PHP workers) that enables WP sites to handle a greater volume of web traffic. PHP-FPM assigns a PHP worker to execute the necessary PHP code, process database queries, and generate the final HTML page.
The number of available PHP workers directly impacts website speed and responsiveness:
- **More PHP workers** allow the server to handle multiple user requests simultaneously, reducing load times.
- **Too few PHP workers** can cause delays as requests queue up, leading to performance issues.
Using a process manager like PHP-FPM, along with a well-optimized hosting environment, improves the response time of PHP environments, thus making websites faster and more scalable.
**Quick note**: LiteSpeed Web Servers have further developed this technology to bypass the need for a middleman process manager like PHP-FPM. Instead, they have created a native process management system inside the web server that communicates directly with its own fleet of workers (LSPHP workers).
## Common Issues Caused by Insufficient PHP Workers
If a server lacks necessary PHP workers, it may struggle to handle multiple requests at the same time, causing several problems:
- **Slow Page Load Times**: More traffic than available PHP workers can handle results in slower page loads and delays.
- **Timeouts and Errors**: Requests may time out, causing errors or preventing actions like form submissions or checkouts.
- **Incomplete Page Loads**: Not all elements may load properly, leaving pages incomplete or broken.
- **Website Crashes**: Low PHP workers can overload the server, causing crashes and making the site inaccessible.
- **Difficulty Handling Traffic Spikes**: High traffic events may lead to slowdowns or failures without an adequate number of workers.
- **Poor User Experience**: Slow performance and errors frustrate visitors, leading to abandoned carts or lost sales.
- **Resource Bottlenecks**: Insufficient workers can strain server resources like CPU and RAM, slowing overall performance.
- **Negative SEO impact**: Poor performance negatively affects search engine rankings, as Google prioritizes fast-loading websites.
In short, not having enough PHP workers can harm your site's performance and user experience.
## How to Optimize Your Site’s PHP Workers for WordPress
To optimize PHP workers for WordPress, the key is to ensure efficient request handling through object caching, reduce unnecessary plugins, and opt for a hosting provider with a high-performance CPU and proper PHP worker allocation.
We’ll break down each of these in detail:
### 1. Use Quality Plugins and Remove Unnecessary Ones
By quality, we mean a few things. First, always download them from authentic sources like the [official WordPress plugin repository](https://wordpress.org/plugins/). Before installing, check the number of active installations and user reviews to see if the plugin effectively solves your problem, as reviews help determine reliability and performance.
Additionally, avoid plugins you likely don’t need or won’t use all that much. Ideally, you want to install only those that are indispensable for your site, since each plugin consumes memory and can affect performance. Having only useful plugins active results in better speed and stability of your website.
### 2. Use a Lightweight Theme
Achieving the [optimal speed of your WordPress website](/blog/fast-server-speed-tools/) considerably relies on the theme you use. [A lightweight theme](/blog/top-wordpress-themes/) makes certain your site has faster loading times, better scores on tools like Google PageSpeed Insights, GT Metrix, and Pingdom Performance Analysis, and delivers an overall smoother user experience.
Plus, certain themes like [Astra](/blog/astra-wordpress-theme-review/), GeneratePress, and Hello [Elementor](/blog/elementor-review/) are specifically designed for speed and efficiency. They come with minimal bloat and integrate well with page builders like Elementor and Gutenberg. Also, you can create your own theme using any starter theme as a foundation, which consists only of the WordPress directory and essential files. This allows you to code the rest of your website freely - if you have the know-how.
So, going for a lightweight theme will do wonders for your site, from reducing unnecessary resource usage and improving responsiveness to maintaining high website performance without constantly upgrading hosting resources. And while we’re on the subject of hosting…
### 3. Choose a Performance-optimized Hosting
Most hosting companies are general-purpose providers. In other words, they aren’t optimized for any one platform, but overall good enough for anything you can throw at them. That’s perfectly fine in case you’re running a simple blog or online store, but for more demanding stuff, there is massive potential for optimization to get the most bang for your buck.
That said, here are the vital hardware specs to look for in a [performance-optimized web host](/):
- **CPU:** Responsible for the processing of code such as PHP (and much more, as it is the brain of the entire operating system). Generally, the more CPU/vCPU cores, the faster your site will be able to process and show pages to users.
- **RAM**: The operating system, web server software (e.g., LiteSpeed), related programs (e.g., MariaDB), and other elements all need to fit inside your RAM capabilities to run properly. The more traffic (especially concurrent traffic) you get, the more RAM you need to keep the CPU fed with data for processing all those requests.
- **Storage**: A good web host will provide fast SSD drives (particularly NVMe types) to fit all your website files and media, and with swap space to spare. When a server reaches peak traffic, it risks running out of RAM. That's when it really slows down and bad things happen system-wise if no swap space is available.
- **Networking**: No matter how good hosting hardware is, it’s nothing without a fast network. Beyond offering great bandwidth rates, high-performance hosting often relies on CDN technology (where servers are distributed across the world) to serve visitors with the lowest possible latency.
Did we mention that Levamo's [best managed WordPress hosting](/managed-wordpress-hosting/) plans tick all these boxes?
That’s because we are bucking the trend of providing just good enough hosting services. Our new way? Putting speed first, no matter what.
## Get the Most out of Your PHP Workers
As critical components go, PHP workers are right there at the OP. They enable apps to handle multiple requests simultaneously, improving speed and performance along the way. When you think about it, calling them ‘workers’ is a great analogy as they behave very much like dedicated employees who handle tasks.
One thing is for sure - without them, the internet would be a sadder place, and your site would be a lot worse for it.
---
## Create and Access Your Levamo Account with Facebook SSO
- URL: https://levamo.com/blog/create-and-access-your-rapyd-cloud-account-with-facebook-sso/
- Category: news
- Author: The Levamo Team
- Published: 2025-03-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Log in or sign up for Levamo instantly with your Facebook account.
> **Update:** Facebook SSO is no longer supported. We still offer single sign-on with **Google**, **GitHub**, and **LinkedIn** - pick whichever you prefer on the login screen.
We've made signing in to your Levamo account even easier with **Facebook Single Sign-On (SSO)**. Now, you can log in or create an account using your Facebook credentials in just a few clicks.
## What's New
- **Faster access**: No need to remember another password. Just log in with Facebook.
- **Seamless sign-up**: If you don't have an account yet, you can create one instantly with your Facebook login.
## How To Use
1. Click "Continue with Facebook" on the login page.
2. Authorize Facebook to sign you in.
3. If it's your first time logging in with Facebook, a new Levamo account will be created automatically.
This update makes logging in faster and easier, just use Facebook to get started.
---
## Multiple CNAME Records: Is It Really Possible?
- URL: https://levamo.com/blog/multiple-cname-records/
- Category: website-development
- Author: Salman
- Published: 2025-03-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Demystifying multiple CNAME records: How to set them up and when to use them.
If you’ve dabbled in domain name setups, you’ve probably come across a CNAME record or two. Short for “canonical name,” a CNAME essentially acts like a forwarding address for one domain (or subdomain) to another. But what if you want to point more than one domain alias to the same underlying server or origin? That’s where the notion of **multiple CNAME records** comes in. Below, we’ll tackle the how and why of this configuration, along with some best practices to keep your DNS clean and conflict-free.

### 1. Quick Refresher: What’s a CNAME Record, Anyway?
A **CNAME record** is a type of [DNS record](/blog/dns-records-explained/). Instead of mapping a domain straight to an IP (like an A record does), a CNAME tells DNS resolvers, “Don’t look for an IP here - look over there for the real record.” For example, if you set blog.example.com as a CNAME pointing to main.example.com, anyone visiting blog.example.com automatically ends up at the same place as main.example.com without you juggling separate IP addresses.
- **Easier IP Management**: Change your IP in one spot and your alias subdomains stay in sync.
- **Brand Flexibility**: Let multiple subdomains funnel into a single site, supporting unique brand experiences or marketing campaigns.
### 2. The Scenario: Multiple CNAME Records to One Origin
So, can you assign **multiple CNAME records** to the same origin? The short answer is yes - DNS absolutely allows more than one domain name or subdomain to point to the same target. For instance, blog.example.com and news.example.com might each have a CNAME leading to origin.example.com. That means no matter which subdomain visitors type in, they’ll end up at origin.example.com’s content.
**Why Bother?**
- **Marketing Flexibility**: Maybe you’re running different campaigns or want distinct URLs that all serve the same content.
- **Simplified Maintenance**: Keep your actual website files on a single origin server. The various subdomains are just alternate gateways.
**Any Real Limit?**
- Technically, you could have dozens (even hundreds) of subdomains referencing the same origin. But each alias is its own line in your DNS settings.
- The main constraint might be your registrar or DNS provider, some of which limit how many records you can add. But that’s not usually a big issue for small to medium projects.
### 3. Top Benefits of Running Multiple CNAME Records
- **Consistent Content with Unique Subdomains**
If each department of your company wants a custom subdomain - like careers.mybrand.com, support.mybrand.com, or events.mybrand.com - but all route to the same server, setting up **multiple CNAME records** is the simplest approach.
- **Easier Domain Consolidation**
**Suppose you own multiple domains: mybrand.us, mybrand.net, etc., and you want them to ultimately reach the same website**. You could have each domain’s root (or certain subdomains) share the same destination via a **CNAME or a direct forward**.
- **Reduced Duplication**
**By pointing everything at one origin, you avoid duplicating server content or IP references**. If you switch hosting or change your IP, you update one record (the canonical name’s A record), and the aliases remain intact.
### 4. Potential Pitfalls (and How to Avoid Them)
While **multiple CNAME records** can be powerful, a few issues can trip you up:
**Circular References**
**If alias1.example.com is a CNAME to alias2.example.com, and alias2.example.com is also a CNAME to alias1.example.com, you create an infinite loop**. DNS resolvers hate this, and it can break your site’s resolution.
- **Solution**: Keep your chain straightforward - any subdomain’s CNAME should end at a single canonical A record (or AAAA if using IPv6).
**Performance Overheads**
**Each CNAME introduces an extra lookup**. Typically, the performance difference is minor, but if you chain multiple aliases, you might add noticeable DNS resolution times.
- **Solution**: Avoid creating a long chain. One CNAME pointing to a domain that has an A record is fine. But a CNAME pointing to another CNAME pointing to yet another can slow things down.
**Protocol Conflicts**
**If a domain is defined as a CNAME, it generally shouldn’t have other types of DNS records like MX (mail) or certain TXT entries**. That’s because a CNAME essentially replaces all other records for that domain.
- **Solution**: If you need email on a subdomain, consider using an A record or separate subdomain that doesn’t rely on a canonical name reference.
**Confusing Email Setup**
**If you attempt to add an MX record on the same domain that’s already a CNAME, you’ll run into conflicts**. Some mail protocols don’t allow a domain with a CNAME to also have an MX record.
- **Solution**: Keep your main domain for email (with A and MX records) and use subdomains as CNAME aliases, or vice versa.
### 5. Best Practices
- **Document Your DNS**
**Keep track of your domain aliases, especially if multiple teams can edit DNS. A quick reference can stop accidental loops or misconfigurations**.
- **Stick to a Single Final Destination**
**Each subdomain that’s a CNAME should ideally point to one final record**. That record can then be an A or AAAA record for your server’s IP.
- **Limit the Chains**
**One hop is generally fine: subdomain.example.com → main.example.com → IP address**. But adding multiple steps might cause confusion or slower lookups.
- **Test Thoroughly**
**Use DNS check tools or commands like dig/nslookup to confirm your CNAME is correctly resolving**. Check each alias as well to ensure no infinite loops or missing records.
### 6. Real-World Example: Two Subdomains, One Origin
#### Scenario:
Your brand, ExampleCo, wants both blog.exampleco.com and news.exampleco.com to serve the same content that’s physically located at origin.exampleco.com.
#### Steps:
**A Record for origin.exampleco.com**
- This is the “canonical” domain. You set an A record: origin.exampleco.com → 192.168.1.100.
**CNAME for blog.exampleco.com**
In your DNS zone, create a record:
- **Type**: CNAME
- **Host**: blog.exampleco.com
- **Value**: origin.exampleco.com.
**CNAME for news.exampleco.com**
Another record:
- **Type**: CNAME
- **Host**: news.exampleco.com
- **Value**: origin.exampleco.com.
**Check Propagation**
- Wait an hour or so (depending on TTL). Confirm that both subdomains resolve to the same final IP address by using a DNS query tool.
In a nutshell, you’ve created **multiple CNAME records** that target a single server record. Visitors see different subdomains in the URL bar, but under the hood, they’re all pulling from the same site.
### 7. The “Multiple CNAME Records” Dilemma: When to Use or Skip
**When to Use**
- **Brand or Department Flexibility**: If different departments want subdomains, but you only maintain one site.
- **Marketing or Campaign Landing Pages**: Launch short-lived subdomains pointing to the same origin to track promotions or events.
- **Domain Consolidation**: If you own many domain variations but want them all to serve the same site.
**When to Skip**
- **Email-Heavy Needs**: If you need to set up advanced MX or SPF records, consider using A records for the domain that handles email to avoid conflicts.
- **Performance-Sensitive**: Chaining multiple aliases might add minor overhead if you’re building a super-latency-focused environment (like critical gaming or real-time financial apps).
### 8. Maintaining DNS Zen (and Avoiding Headaches)
**Regularly Audit**
- Perhaps every quarter, review your DNS records. Remove old or unused subdomains that no longer serve a purpose.
**Watch Out for SSL Certificates**
- If your subdomains require HTTPS, each needs a [certificate](/blog/fix-ssl-certificate-error/) (or a wildcard certificate that covers them all). That’s easy to forget if you add new subdomains frequently.
**Empower Team Collaboration**
- If multiple people add subdomains or handle marketing campaigns, keep lines of communication open. DNS changes can break things if done in isolation.
**Plan for the Future**
- If you might expand subdomain usage, consider a wildcard DNS approach or a robust hosting platform that can accommodate many domain aliases seamlessly.
### 9. Enter Levamo: Your DNS Simplified
If the concept of **numerous CNAME records** seems both appealing and a bit intimidating, you’re not alone. Managing subdomains, IP addresses, certificates, and email records can pile up quickly. That’s where **Levamo** steps in with an all-in-one hosting and DNS management solution. Why go with Levamo?
**Intuitive Dashboard**
- No more rummaging through cryptic zone files. Easily view and edit CNAMEs, A records, and more.
**Unified Infrastructure**
- Host your application and handle DNS under one roof. This synergy minimizes misconfigurations between different platforms.
**Performance & Reliability**
- Low-latency DNS responses, global coverage, and high uptime keep your site (and all those subdomains) accessible around the clock.
**Stellar Support**
- Got a question about a funky subdomain chain or an SSL mismatch? Levamo’s expert team can guide you through it.
Ultimately, if you want to set up **multiple CNAME records** without sweating the small stuff, Levamo can streamline the entire process and help you avoid DNS gotchas. Because nobody wants to be rummaging through 15 lines of CNAME entries at 2 a.m. trying to fix a domain loop.
## Final Thoughts
So, is it possible to have **multiple CNAME records** all pointing to the same origin? Absolutely. And for many businesses - especially those juggling multiple subdomains or marketing campaigns - it’s not just possible; it’s practical. Just remember to keep your chain free of loops, watch out for protocol conflicts, and test thoroughly. With a bit of planning and best practices, you can maintain a flexible, neat DNS setup that effortlessly routes visitors where they need to go.
When in doubt, or if you just need a more intuitive platform, consider handing the reins to **Levamo. Their integrated approach to hosting, DNS, and security ensures you can spin up subdomains and manage CNAMEs with confidence, no matter how many you need**. Welcome to a simpler, more efficient DNS experience - because the internet’s complex enough without adding extra domain tangles to the mix!
---
## How to Use WordPress .htaccess File to Secure and Optimize Redirects
- URL: https://levamo.com/blog/wordpress-htaccess/
- Category: website-performance
- Author: Sunyyan Junaid
- Published: 2025-03-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Master WordPress .htaccess: Secure your site and optimize redirects now.
The WordPress .htaccess file is one of the most powerful tools in a WordPress site owner's toolkit. This file holds the key to optimizing website performance, securing your site, and controlling redirects. It is a hidden file with many mighty powers.
Whether you're a seasoned developer or a beginner, understanding how to use the .htaccess file effectively can drastically improve the security and speed of your WordPress website.
In this blog post, you will learn everything you need to know about the WordPress .htaccess file and its functions.
## What is a WordPress .htaccess File?
The .htaccess file (short for *hypertext access*) is a configuration file used by Apache web servers. In the context of WordPress, it plays a crucial role in controlling how your server responds to various requests.
At its core, **.htaccess** lets you:
- Control redirection rules
- Customize error messages
- Improve performance through caching and compression
- Secure your website by restricting access to certain files and folders
In a WordPress installation, this file is automatically generated when you configure permalinks. Even though it’s hidden, this lightweight file can significantly influence your site’s behavior.
If your site is hosted on an Apache server (which most WordPress hosts use), you’re already using .htaccess even if you haven’t touched it manually.
## Why WordPress .htaccess File Matter?
WordPress relies on the .htaccess file mainly to control how the server handles requests and ensure that your website functions smoothly. This file is very useful for handling permalinks, redirecting traffic, increasing security, and optimizing speed. The following points briefly describe the functions of the WordPress .htaccess file:
- **Permalinks:** It configures URL rewriting to manage clean URLs, ensuring posts and pages are accessible via friendly links.
- **Security:** It helps block access to sensitive files like wp-config.php and xmlrpc.php, preventing unauthorized access.
- **Performance:** .htaccess can enable Gzip compression, browser caching, and other optimizations to improve load times and reduce server strain.
- **Redirections:** You can set up 301 redirects and prevent broken links when content is moved or deleted.
- **Error Handling:** It allows customization of error pages, such as 404, to improve user experience.
- **Hotlinking Protection:** Prevents others from using your images and files, saving bandwidth.
- **Multisite:** For WordPress Multisite, .htaccess handles network-wide URL rewrites.
## How to Access the WordPress htaccess File?
Due to its operational importance, the .htaccess file is a hidden file inside the root directory of a WordPress installation, the same place where you can see the wp-config.php file. You will need an FTP/STF client or a file manager to unhide the .htaccess file. To access it:
- **Using FTP Client:** Connect to your website using an FTP client like [FileZilla](https://filezilla-project.org/) and navigate to the root directory.
- **Enabling Hidden Files:** If you do not see the .htaccess file, enable the option to view hidden files in your FTP client or File Manager.
## How to Create a WordPress .htaccess File?
Sometimes, your WordPress site might not have a `.htaccess` file - especially on a fresh install or if it was deleted unintentionally. Luckily, creating one is easy.
**Option 1: Let WordPress Generate It**
- Go to **Settings > Permalinks** in your WordPress dashboard.
- Click **Save Changes** (even without making changes).
- WordPress will attempt to generate a default .htaccess file in the root directory.
*💡 Note: Make sure your server allows WordPress to write to the root directory. If it doesn’t, you’ll need to do it manually.*
**Option 2: Create It Manually**
- Open a plain text editor (like Notepad or VS Code).
- Paste the following default WordPress rules:
```apache
# BEGIN WordPress
RewriteEngine On
RewriteBase /
RewriteRule ^index\.php$ - [L]
RewriteCond %{REQUEST_FILENAME} !-f
RewriteCond %{REQUEST_FILENAME} !-d
RewriteRule . /index.php [L]
# END WordPress
```
Upload it to the root directory of your WordPress site using an FTP client or File Manager.
Save the file as .htaccess (make sure there’s no file extension like .txt).
## How to Edit the .htaccess File in WordPress?
After making the .htaccess file visible, there are two ways through which you can edit the file:
- Download a copy for manual editing
- Use a WordPress .htaccess plugin (or SEO plugin)
### Edit the WordPress .htaccess File Manually
For this method, you will need an FTP/SFTP client. Here’s how you can download and edit the file:
- After connecting your FTP client (FileZilla) with the server, navigate to the public_html folder
- In the top menu of the FTPZilla window, click on Server.
- Select **Force showing hidden files,** which will make .htaccess visible.
- Search for the file and download it.
- Save a backup copy before making changes.
- Open the file using a text editor like [Notepad++](https://notepad-plus-plus.org/downloads/).
- Make the necessary changes and save the file.
- Upload the modified file back to the server.
### Use a WordPress Plugin to Edit the .htaccess File
The beauty of WordPress is that you can find a plugin for basically anything. There are two ways through which you can modify the .htaccess file:
- Using dedicated WordPress .htaccess plugins
- Using SEO plugins
#### Editing Using a WordPress .htaccess Plugin
If you are looking for a dedicated .htaccess editing plugin, you can use [WP Htaccess File Editor by WebFactory](https://wordpress.org/plugins/wp-htaccess-editor/).

The WP Htaccess Editor plugin makes it easy to manage and edit your .htaccess file from inside the WordPress admin panel. It checks for syntax errors before saving changes to make sure the file is error-free.
Moreover, it creates backups of the file automatically whenever you make updates and stores it with timestamps for quick recovery.
If anything goes wrong and your site has problems, you can easily restore the backup through the plugin or FTP, reducing downtime and hassle.
#### Editing Using an SEO Plugin
The .htaccess file plays an important role in SEO operations. Therefore, the two most-used SEO plugins, Yoast SEO and All in One SEO, provide the ability to edit the .htaccess file.
Here’s how you can do it:
- **Yoast SEO:** From the left side of the WordPress dashboard, navigate to **Yoast SEO > Tools > File Editor** to edit .htaccess.
- **All In One SEO:** From the left side of the WordPress dashboard, go to **All in One SEO > Tools > .htaccess Editor**.
## Using .htaccess File for Optimizing and Safeguarding Your WordPress Website
While there are many uses of the .htaccess file, we are covering how you can use it for:
- Security: Safeguard your WordPress site from unauthorized access and unlawful actions
- Optimization: Boost the performance of your website
- Control: Manage URL redirects efficiently
### Securing a WordPress Site with .htaccess
The .htaccess file is an amazing tool for establishing access controls. Through this file, you can restrict access to sensitive files, block malicious IP addresses, and protect the wp-admin directory.
#### Restrict Access to WP-Admin
Using the .htaccess file to protect the wp-admin sounds like a simple task, and it works like a charm. Considering you will be making a small, yet significant change to the file, you should first save a copy. To restrict access to the wp-admin directory using the .htaccess file, you can add the following code:
```apache
order deny,allow
deny from all
allow from xxx.xxx.xxx.xxx
order deny,allow
deny from all
allow from xxx.xxx.xxx.xxx
```
Replace the xxx.xxx.xxx.xxx with an IP you want to allowlist. You can add multiple “allow from” lines for multiple IPs. This simple configuration can lock the backend, i.e. wp-login.php file and wp-admin directory, to anyone who comes from outside the authorized pool of IPs.
#### Block Access to WP-Content
The wp-content directory is an essential part of a WordPress website. It is the place where all the important files and PHP scripts are saved, including uploads, plugins, and theme files, etc. Sadly, hackers love to target this directory. The good news is that you can protect this important folder using the .htaccess file. Just add the following code to the file:
```apache
# Block access to specific wp-content subdirectories
Order allow,deny
Deny from all
Order allow,deny
Allow from all
```
However, a word of caution! By locking the wp-content directory, any type of writing activity is blocked. This means you might not be able to successfully install any plugins, updates, or other functionalities. Therefore, if you want to install anything, you should just remove the code and you are ready for action.
#### Prevent Directory Listing
Directory listing occurs when someone accesses a directory URL (e.g., yourwebsite.com/wp-content/uploads/) and finds a list of all the files contained within that directory. This can reveal sensitive data, like plugin files, backups, or other assets you don't necessarily want publicly accessible.
By blocking directory listing, you keep your files from being found easily by hackers or people who shouldn't be finding them.
It is a simple fix. Just add this code to your .htaccess file:
```apache
Options -Indexes
```
#### Prevent Hotlinking
Hotlinking is a practice where third-party websites use your media URLs (mostly images) on their websites. Since the file is hosted on your server, you will end up paying for the bandwidth instead of the third-party website owner.
To prevent hotlinking, just add this:
```apache
# Disable direct access to image files from other domains
RewriteEngine on
RewriteCond %{HTTP_REFERER} !^$
RewriteCond %{HTTP_REFERER} !^http(s)?://(www\.)?yourwebsite.com [NC]
RewriteRule \.(jpg|jpeg|png|gif|webp)$ - [NC,F]
```
Replace "yourwebsite.com" with your own domain name. This code blocks the hotlinking of popular image files, including JPG, GIF, PNG, and WebP.
### Optimize WordPress Performance Through .htaccess
You can improve the performance of your website by using the .htaccess file smartly. The .htaccess file allows you to apply performance-related optimizations such as caching, compression, and resource control, which reduce server load and improve user experience.
#### Enabling Gzip Compression
Gzip compression can reduce the size of your website’s files (such as HTML, CSS, JavaScript) by up to 70% before sending them to the user’s browser. Due to small file sizes, the website loading time improves, resulting in a boost in user experience. Faster loading speeds also give your SEO a competitive edge: search engines like Google prioritize websites that perform well, boosting your rankings and visibility in search results.
Here's the code you need to enable Gzip compression:
```apache
# Enable Gzip compression
# Compress text files
AddOutputFilterByType DEFLATE text/plain text/html text/css application/javascript application/json application/xml application/xml+rss text/javascript
# Compress font files
AddOutputFilterByType DEFLATE application/font-woff application/font-woff2 font/ttf font/otf
# Exclude browsers that don't support compression
BrowserMatch ^Mozilla/4 gzip-only-text/html
BrowserMatch ^Mozilla/4.0[678] no-gzip
Header append Vary: Accept-Encoding
```
#### Enabling Browser Caching
Browser caching lets web browsers save certain files–like images, CSS, Javascript–locally on a user’s device for a defined period of time. When a user revisits, the browser serves the locally-stored copies, instead of downloading them again from the web server. This cuts loading times, minimizes bandwidth usage, and enhances the overall user experience.
Just add the following code to .htaccess file:
```apache
# Enable browser caching for images, CSS, JavaScript, and fonts
ExpiresActive On
# Default expiration time (1 year for most static files)
ExpiresDefault "access plus 1 year"
# Expiration times for specific file types
ExpiresByType image/jpg "access plus 1 year"
ExpiresByType image/jpeg "access plus 1 year"
ExpiresByType image/gif "access plus 1 year"
ExpiresByType image/png "access plus 1 year"
ExpiresByType text/css "access plus 1 month"
ExpiresByType application/javascript "access plus 1 month"
ExpiresByType application/font-woff2 "access plus 1 month"
ExpiresByType application/font-woff "access plus 1 month"
ExpiresByType application/vnd.ms-fontobject "access plus 1 month"
ExpiresByType font/ttf "access plus 1 month"
ExpiresByType font/otf "access plus 1 month"
# Set cache-control headers for static resources
Header set Cache-Control "max-age=2592000, public"
```
#### Minifying CSS and JavaScript (JS)
If you are not using a minifying plugin like [Autoptimize](https://wordpress.org/plugins/autoptimize/), you can always use this code to minify CSS and JS in the .htaccess file:
```apache
# Compress HTML, CSS, JavaScript, Text, XML and fonts
AddOutputFilterByType DEFLATE application/javascript
AddOutputFilterByType DEFLATE application/rss+xml
AddOutputFilterByType DEFLATE application/vnd.ms-fontobject
AddOutputFilterByType DEFLATE application/x-font
AddOutputFilterByType DEFLATE application/x-font-opentype
AddOutputFilterByType DEFLATE application/x-font-otf
AddOutputFilterByType DEFLATE application/x-font-truetype
AddOutputFilterByType DEFLATE application/x-font-ttf
AddOutputFilterByType DEFLATE application/x-javascript
AddOutputFilterByType DEFLATE application/xhtml+xml
AddOutputFilterByType DEFLATE application/xml
AddOutputFilterByType DEFLATE font/opentype
AddOutputFilterByType DEFLATE font/otf
AddOutputFilterByType DEFLATE font/ttf
AddOutputFilterByType DEFLATE image/svg+xml
AddOutputFilterByType DEFLATE image/x-icon
AddOutputFilterByType DEFLATE text/css
AddOutputFilterByType DEFLATE text/html
AddOutputFilterByType DEFLATE text/javascript
AddOutputFilterByType DEFLATE text/plain
AddOutputFilterByType DEFLATE text/xml
```
### Use .htaccess to Control Redirects in WordPress
The .htaccess file provides an excellent yet hassle-free way of creating URL redirects for any reason. You can use this file to temporarily or permanently redirect URLs, standardize your direct traffic to sa ingle www or non-www format, enforce HTTPS (or vice versa), manage 404 errors, and reroute traffic using REGEX queries.
#### Basic Redirects for URL Changes
Nobody wants to see error messages like "[the requested url was not found on this server](/blog/the-requested-url-was-not-found-on-this-server/)." That's why whenever you change the URL of a page, make sure to redirect it to the new link.
To create simple redirects from one URL to another, use the `Redirect` directive.
For example:
```apache
Redirect 301 /old-page https://www.yoursite.com/new-page
```
Note: 301 is the "code" for permanent redirection. If you want to redirect something temporarily, you can use 307.
#### Non-www to www Redirect (or Vice versa)
Using one format (www or non-www) helps prevent duplicate content, consolidates link equity, ensures consistent branding, and improves SEO. If you want to force the use of either the www or non-www version of your domain, you can use one of the following rules.
For www to non-www redirects, use this code:
```apache
RewriteEngine On
RewriteCond %{HTTP_HOST} ^www\.(.+)$ [NC]
RewriteRule ^ https://%1%{REQUEST_URI} [L,R=301]
```
For non-www to www redirects, use this code:
```apache
RewriteEngine On
RewriteCond %{HTTP_HOST} ^yourdomain\.com$ [NC]
RewriteRule ^ https://www.yourdomain.com%{REQUEST_URI} [L,R=301]
```
#### Force HTTPS Redirect
After using free SSL from Levamo (or a third-party [SSL certificate](/blog/fix-ssl-certificate-error/)), you must include the following code in the .htaccess file for proper [HTTPS redirection](/blog/redirect-http-to-https/):
```apache
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
```
#### Handling 404 Errors
Error 404 basically indicates a non-existing URL. To properly handle 404 errors, you should create a dedicated 404 page and redirect traffic there. To redirect 404 errors, you can use this code:
```apache
ErrorDocument 404 /404-page
```
#### Redirect Specific Pages (Using Regex)
You can also use regular expressions to handle redirects with more complex patterns. For example, if you want to redirect any URL that starts with /product/ to a new base URL:
```apache
RewriteEngine On
RewriteRule ^product/(.*)$ https://www.yoursite.com/new-product/$1 [L,R=301]
```
## How to Protect Your .htaccess File
Protecting your .htaccess file is absolutely critical because it serves as a powerful configuration gateway to your web server. This small but mighty file can control server behavior, URL redirects, password protection, and security policies for your entire website.
If left unsecured, malicious actors could gain access to it, potentially exposing sensitive server paths and authentication credentials or modifying server rules to create backdoors. A compromised .htaccess file could lead to a complete website takeover, data breaches, or defacement without leaving obvious traces of intrusion.
Put the following code in the .htaccess file to deny access:
```apache
# Deny access to hidden files - files that start with a dot (.)
Order allow,deny
Deny from all
```
## Fixing Common .htaccess Related Issues
Because the .htaccess file controls such critical behavior, even a small error can cause major issues. Here’s a deeper look at the most frequent problems and how to resolve them.
### 1. **[500 Internal Server Error](/blog/fix-the-500-internal-server-error/)**
- This typically happens due to incorrect syntax, such as a missing character or miswritten directive in the .htaccess file.
- **Fix:** Restore the default WordPress .htaccess content or upload a working backup. If the issue persists, temporarily disable plugins to rule out conflicts.
#### 2. **Permalinks Not Working**
- If your links return 404 errors, it’s often because the .htaccess file is missing or doesn’t contain the proper rewrite rules.
- **Fix:** Go to **Settings > Permalinks** in your WordPress dashboard and click **Save Changes**. This will regenerate a fresh .htaccess file.
#### 3. **Redirect Loops**
- Conflicting or duplicate redirect rules - especially involving www, non-www, or HTTPS - can lead to endless loops.
- **Fix:** Review your .htaccess file and remove redundant redirects. Also, check your plugin settings (like SSL or SEO plugins) for overlapping rules.
#### 4. **403 Forbidden Error**
- Overly strict access restrictions or incorrect file permissions can prevent users from accessing certain pages.
- **Fix:** Review IP restriction rules in .htaccess and ensure your IP is allowed. Also, verify that file permissions are correctly set (typically 644 for files, 755 for directories).
#### 5. **Unable to Access Admin Dashboard**
- If access is blocked to **/wp-admin** or **wp-login.php**, it’s likely due to IP filtering or misconfigured security rules in .htaccess.
**Quick Tip:** Always create a backup of your .htaccess file before making changes. One wrong character can take your whole site down - backups make recovery painless.
## The Ultimate Optimization Powerhouse
Offering a wide range of benefits from performance optimization to enhanced security, the .htaccess is a powerful tool for any WordPress webmaster. Proper understanding and usage of this file can save you from installing too many plugins. However, due to its configurable nature, the file should be hardened with added security and multiple off-site copies.
## Frequently Asked Questions

### How to access WordPress .htaccess file?
There are two ways through which you can access the .htaccess file in WordPress:
Use a dedicated WordPress .htaccess (or in some cases, SEO) plugin.
Use an FTP/STP client (like FileZilla)
### How to redirect http to https in WordPress using .htaccess?
Use the following code in the .htaccess file:
```apache
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
```
### How to add a 301 redirect in WordPress .htaccess?
Edit your .htaccess file with this code:
```apache
Redirect 301 /old-page https://www.yoursite.com/new-page
```
### Is WordPress .htaccess necessary?
The .htaccess file significantly enhances the capabilities of a WordPress site. It is essential for enabling pretty permalinks, which improve URL readability, and can also bolster security and performance through various configurations. While a basic WordPress installation can run without it, utilizing .htaccess is highly beneficial for optimizing site management and user experience.
### How to redirect HTTP to HTTPS in WordPress without a plugin?
Yes. You can do it without using a plugin. You will have to edit the .htaccess file with the following code:
```apache
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
```
---
## How to Build a WordPress Website using Levamo
- URL: https://levamo.com/blog/build-a-wordpress-website/
- Category: website-development
- Author: Faisal Sarker
- Published: 2025-03-11
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Build a WordPress website easily with Levamo. Follow our step-by-step guide.
Launching a site is a huge undertaking, especially when you’re juggling a gazillion other things: from customer service to growing your brand and anything in between.
To make matters worse, setting off to build a WordPress website often means wrestling with complicated hosting control panels. In a flash, initial excitement can give way to frustration.
That's why [Levamo](/) exists - to shorten the learning curve needed to build a WordPress website and simplify the entire [web development](https://blackthorn-vision.com/web-development/) process - from setup to launch.
That’s also why this article exists. By the time you finish it, you'll know all there is to know on how to build a website with WordPress that is professional, secure, and ready to welcome visitors from every corner of the world.
## Step-by-Step Guide to Build a WordPress Website

### 1. Registering Your Domain
It all starts with a domain name, which is basically your online address - aka. the name people put in their browsers to find you. But it just can’t be any name - no sir/mam. You have to put your thinking cap on and carefully pick it.
**Key considerations when choosing a domain name:**
- **Simplicity:** Shorter names are generally remembered better.
- **Relevance:** Ideally, your domain should reflect what you do and who you are.
- **Extension:** The .com one is most common, though you could certainly use a regional or niche extension if it fits your business.
Now that we got your creative juices flowing, here’s how you can register your domain in a few quick steps:
- **Choose a Domain Name Registrar:** This is the company that handles the reservation of domain names and assigns IP addresses to them. GoDaddy, Namecheap, and Cloudflare Registrar are good options.
- **Search for Availability:** Check with the registrar's search tool if your desired domain is available. If so, consider variations or look for another extension.
- **Purchase and Complete Registration:** Provide your details, add domain privacy if you want to keep your personal info hidden in WHOIS databases, and make payment.
With a fresh domain secured, the next thing you need to build a WordPress website is hosting.
### 2. Signing Up for Levamo
You’d think that with so many hosting providers available, picking one would be quite a task. Luckily for you, Levamo is one of the easiest to use out there, and WordPress installation is a breeze.
**Why Levamo,** you ask? Here are just a few reasons:
- **Simple Onboarding:** You can start a WordPress site without figuring out complex server settings.
- **Powerful Server Infrastructure:** High-performance LiteSpeed servers designed for top-notch efficiency so you can grow your website to its full potential.
- **Intelligent Caching:** Advanced caching with Redis and Object Cache Pro that speeds up your website.
- **Free CDN:** No-cost Levamo CDN ensures high performance to all visitors, regardless of where they are.
- **Security Features:** Built-in support for SSL and automatic backups (with or without plans) that keep your site safe.
- **Auto-scalable Plans:** You don't have to upgrade your plan just to deal with a sudden traffic growth; Levamo auto-scaling eases the load for you.
- **Rapid Support:** 24/7 assistance with an average first response time of just under 46 seconds (personal best!).
Convinced Levamo is the right choice? Then here’s how you kickstart the relationship with your new best friend:
- Login to the [Levamo account](https://my.levamo.com/).
- Head over to the Levamo website.
- Choose between the three offered plans (we have plenty of discounts!).
### 3. Creating a New WordPress Site
This is where things get serious, as you can now create a new WordPress-ready site with a few clicks.
To do that, go to the Levamo dashboard and click Sites.
- Click on **Add Site.**

- A modal will pop up, where you’ll be asked to select the plan you purchased and want to build your site on. Click Continue after choosing the plan.

**Quick note**: In case all of your existing plans are linked to active sites or you don’t have a plan, an alternate pop-up will prompt you to buy a new plan.
- After that, you will be asked to provide specific information about your new site: site name and domain, location of your target audience, and the desired PHP version of your website. There’s also a checkbox you can tick if you need the mighty WooCommerce on your site.
The site domain name inserted here is only a placeholder for finding your website and won’t be connected to it. As for the PHP version, choosing 8+ is highly recommended.d.

Once you’ve duly filled the necessary details, click on **Add Site**. You’ll have to wait a few minutes, as it usually takes a little bit of time to create the website at this stage.

### 4. Connecting Your Custom Domain to Levamo
At this point, your site will be accessible through a default Levamo subdomain or an IP address. For the ultimate professional look, though, you want to use the custom domain you registered already. Follow these steps:
- From the Levamo dashboard, click on **Domains**.
A list of associated domains will appear. For your first domain setup, the page will be empty.

- 2. Click **Add domain** at the top right. In the popup, enter your domain name (example.com) and click on the **Add domain** button.

If all goes well (it should), you'll be taken to the domain activation page with instructions for the next step.
You'll see a management page for that domain when it gets added to the system.
3. For activation, update the nameservers through your domain registrar (e.g., GoDaddy, Namecheap, whichever you chose). You’ll have to go to your registrar account and find the domain's DNS settings.
Replace the current servers with those provided by Levamo and save your changes. Note that nameserver updates may take 10 minutes to several hours to propagate worldwide.

4. When you’re done, return to the Levamo dashboard and click **Check again** on the domain activation page.
If verification is successful, your domain will become **Active**.
Once active, you can manage all DNS records directly in Levamo and use services like CDN and WAF (web application firewall).
### 5. Maintaining Site Security
Security is paramount, especially if you collect user data, offer e-commerce functionality, or simply want to appear online as a responsible business entity. The good news is that with Levamo, you don’t have much to worry about in that regard, as we provide features like free SSL, WAF, and built-in malware protection on all sites. We’ve also partnered with Monarx and PatchStack to up the level of protection against malware and WordPress vulnerabilities.
**Also Read:** [A Simple Look at SSL Certificate Errors and How to Fix Them](/blog/fix-ssl-certificate-error/)
All of these security measures are then coupled with our first line of defense, Levamo CDN, which also protects you from DDoS and cyber attacks.
However, if you decide to turn off any of our security features (which we urge you not to do), at least be a good sport and install a prominent security plugin like Wordfence or Security to keep your website somewhat protected.
### 6. Designing Your WordPress Website
WordPress has a functional but not so flashy default theme. If you have a few bucks to spare, try a paid theme, but if the budget is tight, you can also go for cool freemium themes like Astra, Blocksy, or Neve.
For this purpose, we’ll show you how to design a site using the popular [Astra theme](/blog/astra-wordpress-theme-review/).
- Log in to the Levamo dashboard and click on the WP Admin button to access the WordPress admin backend.
From the menu, click on **Appearance > Themes.**

2. You have a few options here as you can use default WordPress themes, a third-party theme from the WordPress.org repository, or maybe upload a premium theme. For now, we will use the Astra theme from the WordPress.org repository.
For starters, click on **Add New Theme**.

3. Now search for the theme you want to install (Astra). Click on **Install**, then **Activate**.

4. You can either design your entire website with a block editor from scratch or simply use one of the starter templates to get started. We’ll go for the latter option, so be sure to click on the **Let’s Get Started with Starter Templates** button.

5. After activating the starter templates extension, you will have to choose between using the AI Web Builder or the Classic Starter Templates. Not that we’re old school, but we’ll go with Classics in this case.

6. Next, you’ll have to decide if you want a page builder like [Elementor](/blog/elementor-review/) or Beaver, or to build a Block Editor-based website. We chose the Block Editor here (maybe we are a bit old school).

7. The following screen will show a complete list of starter templates. Take a few moments and pick the one you like the most, then click **Continue**.

8. Fill in the relevant details and click on **Submit & Build My Website. Again, you’ll have to exercise some patience as it will take some time to build your website**. Once built, you can click on **View Your Website** to check how it looks.

**That’s it - your website is ready!**
But wait, there’s more. You can click on **Customize** from the toolbar and further tweak each aspect of your website until everything is just right.

### 7. Finalizing and Launching
Nearly there!
All that is left is to do your homework before you go live so that everything is primed for prime time.
By that, we mean making sure all content is proofread and responsive, running a speed test, and checking SEO settings before you publish, share, and index your site to search engines and the world.
### 8. Shape Your Online Presence With Ease
Hopefully, we did a good job in showing that building a WordPress website on Levamo is an incredibly straightforward process - even for complete novices who are about to be first-time website owners. From the registration of domain names and [DNS records](/blog/dns-records-explained/) configuration to installing WordPress, every step is simplified so you can focus on what matters most: your website.
Now, the time has come to launch your website.
We wish your new site to be more than a digital address - may it be your foundation and voice to connect with a global audience.
Godspeed!
## Frequently Asked Questions

### How long does it take for my website to go live?
DNS changes can take up to 48 hours to spread over the internet. But usually, it is done within 10 minutes or so.
### Do I need to buy an SSL certificate separately?
No, the free SSL certificate offered by Levamo will be automatically activated.
### What DNS records do I need to update for my domain?
Usually, you change a record to point to the Levamo with our nameservers, which will be shown on the instructions after you add your domain.
### Can I migrate an existing WordPress website to Levamo?
Absolutely. Levamo offers free migrations.
### What if my site doesn’t load properly after updating DNS?
- **Check Propagation:** Check if the DNS records have changed globally using tools like WhatsMyDNS.net.
- **Verify Records:** Type the IP address or CNAME correctly.
- **Wait a Bit:** Change can take a while, though, so wait for a bit.
**Also Read:** [TLS vs SSL: What’s the Difference?](/blog/fix-ssl-certificate-error/)
## Conclusion
Hope you understand till now that building a WordPress website on Levamo's [managed WordPress cloud hosting](/managed-wordpress-hosting/) is an incredibly simple process - even for complete novices in online publishing. From the registration of domain names and DNS records configuration to installing WordPress, every step is simplified so you can focus on what matters most: your website! How you shape your online presence.
If you've read this guide, and now it's time to launch your website.
We wish your new site be more than a digital address. May this be your foundation, your voice, and a way to connect with a global audience.
---
## WordPress Page Speed Optimization: 21 Performance Tips
- URL: https://levamo.com/blog/wordpress-speed-optimization/
- Category: website-performance
- Author: Shahzeb Ahmed
- Published: 2025-03-10
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Speed up WordPress! 21 performance tips to boost your site's speed today.
WordPress speed optimization is critical if you want to survive in 2025 and beyond. Why? Because the faster your page speed, the higher you'll convert. The slower your web page speed, the more users bounce and leave your business
So, how can you speed up your WordPress site?
You start by measuring your website’s performance on [Google Page Insights](https://pagespeed.web.dev/), a tool that has more or less standardized how site performance is measured. Any time above 2.9 seconds on the Page Insights tool is bad news. Use this guide like a checklist and go through one thing at a time to understand what is (and isn’t) making a real difference.
## Why Is WordPress Page Speed So Important?
If there’s one thing every WordPress site owner needs to take seriously, it’s speed. Your visitors expect fast, seamless experiences, and so does Google. A slow-loading website doesn’t just frustrate users, it also sabotages your visibility, engagement, and ultimately, your revenue. This is why WordPress page speed optimization is so crucial, but let's understand why it's so important.
### Faster Web Page = Online Visibility
Let’s start with SEO. Google now uses *[Core Web Vitals](/blog/core-web-vitals-and-seo/)*, which is a set of user experience signals, to help decide how well your pages rank. These include:
- **Largest Contentful Paint (LCP)** - how quickly your main content loads.
- **Cumulative Layout Shift (CLS)** - how stable your page elements are while loading.
- **Interaction to Next Paint (INP)** - how fast your site responds to user actions.
The faster and smoother your site feels, the better your chances of climbing up the rankings. A sluggish page, on the other hand, is like telling Google: “Maybe try the site next door.”
### Crawlers Ignore Slow Websites
Search engines don’t have unlimited bandwidth. When your site loads slowly, crawlers may not bother indexing everything, meaning some of your content might never even show up in search results. Speed helps ensure your entire site gets seen.
### Faster WordPress Page Speed = Less Bounce Rate
Ever landed on a site, waited, sighed, and clicked away? So have your visitors. If your competitors are just one click away (which they are), site speed becomes a direct factor in whether someone stays or bounces. Fast sites make strong first impressions and keep people around long enough to make a difference.
### Faster WordPress Page Speed = Higher Conversions
People don’t wait around. Whether you're running a course, selling products, or building a membership community, every second counts. A fast site keeps users engaged and drives them toward your goal, whether that's signing up, checking out, or sharing your content. Just a one-second delay can slash conversion rates dramatically, and that's the ultimate goal you want to take a hit on.
#### Tools to Test (and Improve) Your WordPress Page Speed
So if you're thinking, "how to check my website speed?" it's the right question to tackle. The following WordPress speed optimization services or tools help you test performance and pinpoint what’s slowing things down in your mission of speed optimization in WordPress:
- [PageSpeed Insights](https://pagespeed.web.dev/)
- **[Search Console](https://search.google.com/search-console/about)**
- **[Chrome UX Report](https://cruxvis.withgoogle.com/#/)**
- **[Chrome DevTools](https://developer.chrome.com/docs/devtools)**
- **[Lighthouse](https://chromewebstore.google.com/detail/lighthouse/blipmdconlkpinefehnmjammfjpmpbjk)**
## 1. Choose a Fast Hosting Provider
If your website is not performing well, one of the most common reasons is a poor hosting choice. While all hosting providers tend to support WordPress, not all are optimized to deliver reliable uptime and speed.
In all fairness, your budget drives the decision when choosing the [fastest WordPress hosting](/blog/fastest-wordpress-hosting/) partner for your WordPress site.
That said, it’s always smart to sign up with a [managed WordPress hosting](/managed-wordpress-hosting/) platform like Levamo since those are specially created for WordPress websites. From hosting stack to caching and backups, every aspect is fine-tuned to deliver the best results.
With cutting-edge features like [LiteSpeed servers](/blog/lite-speed-hosting-benefits/), MariaDB databases, and KeyDB caching, Levamo, in particular, is a great choice for reliable and lightning-fast WordPress hosting that will deliver impressive load times.

Plus, you get free SSL and a Content Delivery Network (CDN), along with after-sales 24x7 support from WordPress experts.
## 2. Use a Caching Plugin to Improve Performance
A caching plugin ups your site’s performance by creating static HTML versions of your pages and storing them on the server. When a user visits your website, the plugin serves the pre-generated HTML file that loads faster instead of running complex PHP scripts.
This process reduces the time it takes to display content to visitors. However, constantly reloading static files like images and JavaScript with every request can slow down the site’s speed.
Levamo has an efficient caching mechanism where LScache, Redis, and Memcached are used at different levels to deliver insanely fast page load times. Plus, you get [free WordPress CDN](/cloudflare-cdn/) (on all plans) and free Object Pro Cache (on Startup and Performance plans) to speed up WordPress.
## 3. Deploy a CDN
A Content Delivery Network (CDN) is a network of servers distributed across the world that caches your site’s static content (images, CSS, and JavaScript files) and delivers it to users from the server closest to their geographic location. This proximity lowers latency, improving website speed and providing a better user experience.
Integrating a CDN with your WordPress site offers several benefits:
- **Enhanced performance:** CDNs reduce the distance data travels by serving content from multiple locations, resulting in quicker page loads.
- **Reduced server load:** Offloading static content delivery to the CDN lets your origin server handle dynamic requests more efficiently.
- **Improved security:** Many CDNs provide additional security features, such as [DDoS protection](/blog/preventing-ddos-attacks/) and SSL encryption, protecting your site against malicious attacks.
Levamo’s [Enterprise Cloudflare CDN](/cloudflare-cdn/) delivers your content from Cloudflare’s global network of 300+ data centers, with full page caching, static assets cached at the edge, and enterprise-grade security including an advanced Web Application Firewall.

Activating it is straightforward. Add your domain in the Levamo dashboard, select Cloudflare as your DNS provider, and delivery switches to the edge with no extra plugins or complex configuration.
## 4. Optimize Background Processes
In WordPress, many critical tasks are carried out behind the scenes for smooth operation. These are known as background processes, and they often run automatically without requiring your attention. When it comes to WordPress performance optimization, always keep an eye on your background processes to understand what your website is running.
Examples of common background operations on a WordPress site include:
- Backups triggered by WordPress backup plugins
- Cron jobs scheduling future posts
- Cron jobs checking for plugin or WordPress updates
- Crawlers from search engines retrieving content
While scheduled tasks like post publishing or update checks generally have little impact on performance, other processes like frequent backups or constant search engine crawling can slow your site down.
To ensure your backup plugin doesn’t negatively affect your site’s performance, it’s wise to schedule backups during off-peak hours when traffic is low. In addition, consider tweaking the backup frequency and the specific data you’re backing up.
For instance, if you’re performing a full backup daily but only adding new content a couple of times a week, it’s best to scale back the frequency of backups. Most hosting providers (good ones, anyway) allow you to create a policy according to your website’s needs.
For those needing more frequent backups, such as real-time ones, a SaaS service like BlogVault is a neat option. This allows you to avoid overloading your server while making certain your data is consistently protected.
On the crawling side, regularly monitor your crawl statistics in Google Search Console. Excessive crawling, especially if it leads to errors, can significantly hinder your website’s performance, potentially causing slowdowns or even crashes.
## 5. Optimize Your WordPress Site’s Homepage
Apart from search engines and social media, a website’s homepage receives a lot of direct traffic. Hence, it’s important to keep it in good shape. Start by removing unnecessary elements such as cluttered content, excessive widgets, and tools that add little to no value.
Instead of displaying full-length posts, opt to show just the introduction or a brief excerpt. This helps reduce the amount of content being loaded at once. Avoid showcasing too many posts on a single page, which can slow down the site’s loading time.
A cleaner, more streamlined homepage will significantly boost your site’s load speed.
## 6. Optimize Your WordPress Site’s Size
Thinking about why you should reduce your site’s overall size? Well, if you set a good impression by creating a speedy homepage, the same expectation will be there for other pages. Therefore, it is important to refine everything.
Large files, including images, videos, and plugins, are the main slowdown offenders. Utilizing a plugin like [EWWW Image Optimizer](https://wordpress.org/plugins/ewww-image-optimizer/) can help to speed up your site with compressed images and converting to better optimized image formats like WebP.
Start by compressing images and removing needless media files. You can also deactivate or remove unused plugins. Moreover, consider optimizing your theme and scripts by minimizing their size.
Using tools like [FeedTheBot Gzip Test](https://www.feedthebot.org/tools/gzip/) can help you verify that compression is working correctly across your entire site
By keeping your site’s size in check and using GZIP compression, you can ensure faster load times and a smoother user experience.
## 7. Pick a Lightweight Theme
Designed with clean, minimal code, a lightweight theme avoids redundant features, delivering faster load times and smoother functionality. Unlike heavy, feature-packed themes that bloat your site with excessive scripts and styles, lightweight themes prioritize speed and efficiency, directly improving user experience and SEO rankings.
That way, you reduce server response times and minimize resource consumption, which is crucial for users on slower internet connections or mobile devices.
Lightweight themes also provide a solid foundation for scalability, allowing you to add only the plugins and customizations you need without compromising performance.
The thing is, in most cases, you don’t need a fancy theme. The default themes inside WordPress are good enough for most websites. Of course, you can always opt for a third-party solution whenever required.
Themes like [Astra](https://wpastra.com/), [GeneratePress](https://generatepress.com/), or [Neve](https://wordpress.org/themes/neve/) are excellent examples of lightweight options that balance aesthetics and functionality. Remember, a visually appealing site is important but not at the cost of speed.
## 8. Using the Same Data Center for Website and Database
When your WordPress site and database are geographically close to each other, latency is reduced, which is the delay before a data transfer begins following instructions for its transfer. Lower latency means faster data retrieval and smoother interactions with the database, ultimately leading to a more efficient and responsive website.
Let’s say your WordPress site is hosted in a data center in New York City, and the database is in another data center in California. The time it takes for your site to fetch posts or process user requests will be longer due to the physical distance between them. This can result in slower page load times and a less-than-optimal user experience.
On the other hand, when both the site and the database are in the same data center, the communication between them happens almost instantaneously, providing a seamless browsing experience for your visitors.
To find out where your server is located, contact your hosting provider directly. They can provide you with detailed information about the specific data center hosting your site. In some cases, vendors may disclose this information during the sign-up process or on their website.
## 9. Keep Media File Sizes Small
Large media files are a major culprit behind slow-loading WordPress sites. Images, videos, and other media consume significant bandwidth and increase page load times. Compress images using tools like [TinyPNG](https://tinypng.com/) or WordPress plugins such as [Smush](https://wordpress.org/plugins/wp-smushit/) or [EWWW Image Optimizer](https://wordpress.org/plugins/ewww-image-optimizer/) to optimize performance.
Reducing file sizes without sacrificing quality ensures faster delivery to users. Furthermore, you should adopt modern formats like WebP, which offers superior compression compared to JPEG or PNG.
For videos, consider embedding from platforms like YouTube instead of self-hosting. Smaller media files lead to quicker load times, improved SEO, and a smoother browsing experience for visitors.
## 10. Update Your WordPress Frequently
To speed up WordPress, one of the most low-hanging fruits is ensuring you keep the WordPress site updated. Regular updates include WordPress performance optimizations and bug fixes that can considerably lower loading times. Newer versions often come with streamlined code, reducing the load on servers and speeding up page delivery.
Here are a few refinements the WordPress core received in 2024:
- **Faster template loading:** [WordPress 6.6 reduced](https://make.wordpress.org/core/2024/07/29/wordpress-6-6-performance-improvements/) template loading times by 40%, enhancing site responsiveness.
- **Improved lazy loading for Embeds:** Enhanced lazy loading for oEmbed iframes in WordPress 6.6 boosts page performance, more so for content-rich sites.
- **Auto-sizing for lazy-loaded images:** [WordPress 6.7](https://make.wordpress.org/core/2024/12/10/wordpress-6-7-performance-improvements/#:~:text=This%20release%20delivers%20important%20performance%20updates%2C%20including%20faster,more%20efficient%20tag%20processing%20in%20the%20HTML%20API.) introduced auto-sizing for lazy-loaded images, optimizing load times and user experience.
- **Optimized AVIF image generation:** WordPress 6.7 boosted AVIF image generation speed by up to 20%, reducing image load times.
- **Enhanced PHP 8+ Support:** WordPress 6.7 improved compatibility with PHP 8+, ensuring faster execution and better performance.
Additionally, updated plugins and themes are optimized for the latest WordPress version, ensuring compatibility and efficiency. Of course, you remain protected against different types of attacks too.
Outdated sites may struggle with modern web standards, leading to slower performance. By staying current, you benefit from the latest caching techniques and database optimizations.
This not only boosts user experience but also improves search engine rankings, as Google favors faster sites. In short, keeping WordPress updated is a simple yet effective way to maintain a fast, secure, and streamlined website.
## 11. Disable Hotlinking
Imagine this: you’ve spent countless hours crafting a stunning website, only to discover that other sites are slyly using your images and videos without permission. This sneaky practice is known as hotlinking and can be a real drain on your resources.
When outsiders directly link to your media files, they’re essentially stealing your bandwidth, causing your server to work overtime and potentially slowing down your site’s performance. It’s like having freeloaders at a party who eat all the food but don’t contribute anything.
By disabling hotlinking, you protect your website’s precious resources, ensuring it runs as it should.
To prevent hotlinking, open the .htaccess file and add the following code:
RewriteEngine on
RewriteCond %{HTTP_REFERER} !^$
RewriteCond %{HTTP_REFERER} !^http(s)?://(www\.)?yourdomain\.com [NC]
RewriteRule \.(jpg|jpeg|png|gif|mp4)$ - [NC,F,L]
Naturally, replace “yourdomain.com” with your actual domain name. This code checks the referrer and blocks requests from domains other than yours for specified file types.
## 12. Minimize JavaScript and CSS Files
Running a WordPress site through tools like Google PageSpeed Insights or ySlow often highlights a common issue: the need to minify JavaScript and CSS files.
When left unchecked, these files can bloat your site with superfluous code, leading to slower loads and higher bandwidth usage.
The good news? Minifying them is a game-changer. By stripping out extra spaces, comments, and redundant characters, you’ll shrink file sizes and reduce the number of server requests.
The result? A faster, leaner website that feels snappier for visitors.
The best part is you don’t need to be a coding expert to make this happen. If you’re comfortable editing code, you can minify manually. But if you’d rather take the easy route, plugins like [Autoptimize](https://wordpress.org/plugins/autoptimize/) or [W3 Total Cache](https://wordpress.org/plugins/w3-total-cache/) will do the heavy lifting for you.
Either way, optimizing these files boosts speed and saves bandwidth, giving your site the performance edge it truly deserves.
## 13. Focus on Database Caching and Optimization
Each time a page loads, WordPress checks the database for content, settings, and other data. Excessive queries can slow down your site, particularly during high-traffic periods.
Database caching circumvents this problem by storing frequently accessed data in memory, eliminating the need to query the database repeatedly. Tools like Redis, Memcached, or WordPress plugins like WP Rocket and W3 Total Cache make this process seamless. Caching not only reduces server strain but also ensures faster content delivery to users.
Together, these strategies create a more efficient and scalable website. Visitors experience quicker load times, improved reliability, and a more polished browsing experience. For growing websites, reducing database calls and leveraging caching is a proven way to maintain speed and performance while effortlessly handling increased traffic.
One of the ways Levamo optimizes WordPress performance is by utilizing MariaDB, an open-source database management system known for its speed, security, and scalability. It retrieves data faster and handles large data sets, easing the burden when traffic peaks.
## 14. Limit Post Revisions
The idea here is to reduce database bloat. Each revision creates a full copy of your content, leading to increased database size and potentially slower queries.
By limiting the number of revisions WordPress retains, you can maintain a leaner database, resulting in faster loads and improved overall performance. To implement this, add the following line to your ‘wp-config.php’ file:
``` php
define('WP_POST_REVISIONS', 5);
```
This configuration keeps only the last five revisions for each post, ensuring efficient database management.
## 15. Host Your Fonts
Third-party font services like Google Fonts or Adobe Fonts often track user data, risking compliance with GDPR or other regional privacy laws. By hosting fonts locally, you eliminate external dependencies, reduce latency, and avoid downtime if third-party services fail.
You gain complete control over caching strategies, optimizing load times for your audience. Self-hosting also future-proofs your design - external font libraries can deprecate or alter fonts, disrupting your site’s aesthetics. Additionally, self-hosting allows font subsetting (trimming unused characters), which reduces file sizes for faster performance.
For businesses, this approach reinforces consistency. Some externally hosted fonts may face regional blocks or slow speeds in certain areas, compromising user experience. Self-hosting ensures fonts load reliably, maintaining visual identity across all touchpoints.
Pair self-hosted fonts with a CDN to boost global delivery. An [EWWW Image Optimizer](https://wordpress.org/plugins/ewww-image-optimizer/) premium subscription provides an option to self-host your fonts, or a CDN that can host them to mask visitor information from Google for better privacy. This combination delivers the control of self-hosting with the scalability and speed of a CDN, resulting in fast, reliable font rendering worldwide - even during traffic spikes.
## 16. Use Asynchronous Loading for Long-Form Content
For long-form content on WordPress, asynchronous loading is ideal because it balances speed and user experience. By loading non-critical scripts (e.g., fonts, analytics) at different times, your page renders content faster, keeping visitors engaged without delays. Attributes like *async *or *defer *prevent render-blocking, ensuring text and images display swiftly while scripts load in the background.
*Why prioritize async?*
- Retains visitor attention with faster perceived performance.
- Aligns with Core Web Vitals metrics (e.g., Largest Contentful Paint).
- Simplifies SEO, as search engines crawl single-page content more effectively.
*Isn’t pagination better?*
Pagination splits lengthy posts into smaller pages, reducing initial load times and server strain. However, it risks frustrating users who prefer seamless scrolling. Reserve pagination for extremely long content (e.g., multi-chapter guides) where navigation clarity outweighs continuity.
WordPress usually handles pagination well, but just the same, make sure your theme or plugin is correctly set up. You can check this by viewing the source of a paginated page and ensuring it has proper “next” and “prev” links, along with any necessary canonical tags.
Here are the best practices to paginate content if necessary:
- Use canonical tags to point paginated pages to a “View All” version.
- Implement rel=” next/prev” (though less critical now; Google deprioritized it).
- Avoid paginating critical content; opt for lazy-loading or accordions for long-form text.
- Strengthen internal linking to consolidate authority.
Strike a balance! Optimize heavy assets asynchronously and paginate only when content structure demands it.
## 17. Paginate or Disable Comments as Required
Did you know that comments can impact your WordPress site’s speed and, by proxy, user experience? Each comment adds to the database load, and more of them can slow down the site. While fostering engagement is valuable, an overloaded comments section may become a detriment at some point.
Here’s what you can do:
- **Pagination for large comment threads:** If your posts attract hundreds of comments, pagination splits them into manageable pages. This reduces server load, speeds up initial page rendering, and keeps navigation smooth. Use WordPress’s built-in settings (Settings > Discussion) or plugins like WP-PageNavi for customization.
- **Disable comments strategically:** For low-engagement sites or static pages (e.g. portfolios, service pages), consider disabling comments entirely. This eliminates unnecessary database queries and streamlines code. Use plugins like Disable Comments or adjust settings per post.
- **Reduce plugins and scripts:** Comment sections often rely on third-party scripts (e.g. Gravatar) or plugins (e.g. Akismet), which add HTTP requests. Minimize these or switch to lightweight alternatives.
## 18. Use Lazy Loading on Images
By loading images only when they enter the user’s viewport, you reduce initial page load times, ultimately conserving bandwidth and improving user experience. This technique is particularly beneficial for image-heavy pages as it ensures that only the images visible to the user are loaded, leading to faster page rendering.
Additionally, lazy loading can positively impact your site’s SEO since search engines favor faster-loading pages. To implement lazy loading, you can utilize WordPress’s built-in functionality or install a plugin like WP Rocket, which offers advanced lazy loading features.
You can also use the loading = “lazy” attribute inside the image tag for native WordPress support.
## 19. Use Third-Party Platforms for Videos and Interactive Content
Hosting large media files like videos on external platforms such as YouTube, Vimeo, or Wistia reduces server load, freeing up resources and speeding up your WordPress site. These platforms also use their own CDNs to deliver fast loading times globally, enhancing user experience without straining your server.
Interactive content tools like H5P or Playbuzz can be embedded seamlessly, keeping your site lightweight. By offloading resource-heavy elements to third-party services, you lessen the need for plugins or custom coding, which tend to slow down sites.
Moreover, these platforms often provide optimized code for embedding, ensuring efficient loading. This approach both raises website performance and enhances scalability and reliability, leaving you to focus on creating engaging content while maintaining a fast, responsive WordPress site.
## 20. Uninstall Inactive or Faulty Plugins
WordPress speed optimization does not need to be overly complicated. It can be something as easy as regularly checking your plugins to identify and remove non-essential and broken ones. Faulty plugins can cause errors or conflicts, leading to sluggish load times or even crashes. Always test plugins for compatibility and performance before fully integrating them. A neat trick is to create a staging site and tinker around without worry.
By uninstalling unnecessary or problematic plugins, you build a leaner plugin library that streamlines your site’s operations, reduces server load, and improves speed.
## 21. Build with the Block Editor Over Third-Party Page Builders
Provided you don’t have specific design or functionality needs, use Gutenberg Block Editor to build your WordPress website for the ultimate WordPress performance optimization boost. Gutenberg is a lightweight, native WordPress editor that eliminates the need for heavy page builders, reducing bloat and improving loading times. Its clean code structure provides efficient rendering, contributing to faster page speeds and better performance.
Additionally, Gutenberg integrates seamlessly with WordPress core, ensuring compatibility and regular updates. For advanced needs, you can still use lightweight plugins or custom code.
However, if you have distinct needs, such as highly customized layouts or advanced functionality, third-party page builders like Elementor or Divi will likely be better options. They offer greater flexibility and design control but may introduce additional scripts and plugins that can impact speed. To mitigate this, optimize their usage by limiting unnecessary features, enabling caching, and using a CDN.
## Optimization Should Be A Routine
Some techniques listed here are light and simple tasks, like deleting unused and faulty plugins and setting up a favorable backup policy. Others, like selecting a theme or choosing a suitable WordPress host, might be more challenging and time-consuming.
What’s important to remember is that WordPress speed optimization should never be a “set it and forget it” thing. Always treat your website like a running machine: regular checks and maintenance will keep performance consistent.
## Frequently Asked Questions

### Why is my WordPress website so slow?
There can be multiple reasons behind the slow performance of your WordPress website. You might have outgrown the type of hosting you are using or have picked a poorly coded theme. Perhaps you have a faulty plugin that is messing up everything. Use this article to get started with your WordPress performance optimization journey.
### How can I check my website's speed and performance?
Simply visit Google Page Insights to check your website's speed and performance. Its report is based on Core Web Vitals, a set of metrics Google uses to measure and improve user experience.
### What are the main factors that slow down a WordPress site?
First, check the results screen from the Google Page Insights tool. You will get a lot of good recommendations, like minifying your CSS and JS, optimizing your images and videos, and so on.
Once you have corrected these issues, proceed to auditing your plugin library. Bad plugins are one of the main factors of slowing down a WordPress site. Test out different themes if things did not improve significantly after the plugin audit. Implement a CDN to make content delivery faster.
If all this goes in vain, try deploying asynchronous loading to speed up your WordPress site. More advanced stuff, like modifying your caching mechanism and fine-tuning your background processes should be done when all the basics are checked and covered.
### Does my hosting provider affect my website speed?
Yes. If your WordPress website doesn’t get enough computing resources or is treated like any other HTML website, then you’re in for a rough ride. Always choose a fully managed WordPress hosting like Levamo to get the most bang for your buck.
### Can a CDN improve my WordPress speed?
Yes, since it offloads content delivery from the host and distributes files and scripts using its global network. Due to a CDN’s worldwide access, website visitors receive data quicker as it gets from the nearest location instead of the origin server.
### How to increase WordPress website speed in 2025?
You can increase your WordPress website’s speed in 2025 by measuring your web pages on Google Page Insights, minifying CSS and JS files, fine-tuning background processes, deploying a CDN, reducing reliance on third-party fonts and page builders, resolving any plugin- and theme-related issues, reducing media file sizes, improving database and caching capabilities, and moving to a fully managed WordPress hosting platform.
### How to improve the speed index in WordPress?
Improving your WordPress website’s speed in 2025 involves several key steps:
- Migrate to a fully managed WordPress hosting platform for superior speed and reliability.
- Use Google Page Insights to identify performance bottlenecks.
- Minify CSS and JavaScript files to reduce load times.
- Optimize background processes, including backup policies, to minimize resource usage.
- Deploy a CDN for faster content delivery.
- Reduce dependency on third-party fonts and page builders.
- Resolve plugin and theme conflicts to ensure smooth functionality.
- Compress media files to decrease page size.
- Enhance database efficiency and implement advanced caching mechanisms.
---
## What Is A DNS Record? Understanding the Basics
- URL: https://levamo.com/blog/dns-records-explained/
- Category: website-development
- Author: Salman
- Published: 2025-03-05
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Demystifying DNS records! Understand how they work and why they're important.
Ever wondered how your browser magically knows where to take you when you type in a simple domain name like example.com? Behind the scenes, there’s a system translating that user-friendly text into a server address so your computer lands on the right website. That entire process revolves around DNS (Domain Name System), and the key pieces of information that make DNS work are known as **DNS records**.
We’re about to take a fun, understandable stroll through DNS land - no complicated lingo required. By the end, you’ll understand how to **create a DNS entry**, what each record is for, and how services like **Levamo** can ease your DNS headaches. Buckle up - here we go!
### 1. Why DNS Exists: A Shortcut for Our Brains
Let’s set the stage. Every website on the internet sits at a specific IP address, which is basically a series of numbers (like 192.168.1.10 or a more complex IPv6 address). If we had to memorize those strings just to watch a video or read a blog, we’d lose our minds. DNS steps in, letting us type in “google.com” or “mycoolblog.net” instead of some random numeric code.
- **Think of DNS like a phone book**: You search by name (the domain), and DNS finds the matching “phone number” (the IP address).
- This is how your email, websites, and subdomains all neatly connect to the services that power them - courtesy of **DNS records**.
Also Read: [Nameserver vs DNS](/blog/nameserver-vs-dns/)
### 2. DNS Records 101: The Core Player in the Game
So, **what is a DNS record**? You can think of it as a tiny instruction that helps direct traffic or handle domain-specific tasks. Let’s walk through a few favorites:
**A Record**
- Likely the one you’ll deal with most. It pairs a domain (like example.com) with an IPv4 address (such as 192.168.4.56).
- Whenever someone visits example.com, the A record basically says, “Hey, the server you want is at IP X.”
**AAAA Record**
- The twin sibling of the A record but for IPv6 addresses.
- As more of the web shifts to IPv6, you might find yourself setting these up to handle modern traffic.
**CNAME Record**
- Essentially an alias. Tells DNS that one domain or subdomain is just another domain’s nickname.
- A common scenario is making www.example.com a CNAME pointing to example.com, so you only have one IP address to manage.
**MX Record**
- Stands for “Mail Exchange.” Guides all incoming email for a domain to the right mail server.
- If you use an external email service (like Google Workspace), you’ll add their MX entries so your messages reach the correct inbox.
**TXT Record**
- A flexible record that’s often used for verification or security details, such as SPF (to help with email deliverability) or domain ownership.
- You might also store short notes or other meta-information in these text fields.
**NS Record**
- Points out which name servers are authoritative for your domain. If you register “mybrand.com” at a domain registrar, you typically set the NS records to your hosting or DNS provider so the entire system knows where your domain’s “zone file” lives.
**SOA Record**
- Stands for “Start of Authority.” Typically the first record in a zone, containing info like the primary name server and some housekeeping timers.
Sure, there are other advanced entries - like SRV (for specific services) or CAA (to control who can issue SSL certificates) - but the ones above cover the bulk of everyday tasks.
### 3. The Anatomy of a DNS Zone: Where Records Live
When you look at a domain’s DNS settings (often called a “zone file”), you’ll see a collection of these records stacked together. Each line or entry typically has:
- **Type** (A, CNAME, MX, etc.)
- **Name/Host** (like example.com, mail.example.com, or www.example.com)
- **Value** (could be an IP address, a domain name, or a text string)
- **TTL (Time to Live)** - tells servers how long to cache that record before checking back for an update.
If you’re new to domain management and want to **create a DNS entry**, remember you’ll add one record per line in your DNS management tool, specifying each of those elements. Easy, right?
### 4. The “How-To” of Creating a DNS Record
Let’s imagine you just bought “mygreatsite.com” and you want to direct it to your web server. Here’s the typical process:
**Find Your DNS Host**
- Sometimes it’s the same place you registered your domain. Other times, you might use a third-party service or your hosting provider’s control panel.
- Confirm your NS records at the domain registrar are pointing to wherever you’re managing DNS.
**Add an A Record**
- Inside your DNS management area, pick “Add Record,” select “A” from the type dropdown.
- Under “Host” or “Name,” you might type “@” (meaning the root of your domain) or specify the domain itself.
- The “Value” or “Points To” field is your server’s IP address.
- Choose a TTL - perhaps something like 3600 seconds (one hour) - and save.
**Wait for Propagation**
- Once you hit save, it can take a few minutes or up to 48 hours for the rest of the internet to see your changes.
- You can use a “DNS checker” website or a tool like dig in Terminal to confirm the record is live globally.
**Check Everything**
- Type your domain in your browser - hopefully, you see your site! If not, give it more time or double-check you typed the IP correctly.
### 5. Everyday DNS Scenarios
#### Scenario A: Website Migration
You’re moving from Host A to Host B. You’ll likely have a new IP address for your domain. So you update the A record to the new IP. Maybe your subdomain’s A record also needs changing. If your mail hosting stays the same, you can leave the MX record alone.
#### Scenario B: Setting “www” to Alias Your Root Domain
Some people prefer “example.com” as their main site, while others like “[www.example.com.”](http://www.example.com.xn--ivg/) Using a CNAME from “www” to the root domain means you only maintain one IP address or server setting.
#### Scenario C: Email with an External Provider
If you decide to let Google or Microsoft handle your email, you’ll add or edit your MX records so that inbound messages go to their mail servers. Don’t forget any SPF or DKIM TXT records they recommend, or your messages might end up flagged as spam.
### 6. Why DNS Performance and Security Matter
We often think of DNS as a “set it and forget it” thing. But a slow or unreliable DNS host can lengthen page load times, frustrate visitors, and cause sporadic downtime. Meanwhile, insecure DNS accounts with weak passwords are prime targets for hackers wanting to redirect your traffic elsewhere.
- **Performance**: Some DNS hosts are geographically distributed and use load balancing to ensure quick responses. This can slightly speed up your site’s first-time load.
- **Security**: Consider enabling two-factor authentication on your registrar and DNS provider accounts. For an extra layer, DNSSEC can help validate that the DNS data you’re getting hasn’t been tampered with.
### 7. Overcoming DNS Anxiety: Tips & Best Practices
- **Triple-Check Before Saving**: A simple typo in an IP address can knock you offline. When in doubt, copy-paste carefully.
- **Back Up Your Old Records**: Some hosting dashboards let you export a zone file so you can revert if you make a mistake.
- **Keep TTL Reasonable**: For stable records, a longer TTL (like 4 or 12 hours) is fine. If you plan to move your site soon, set a shorter TTL (like 300 seconds) so changes take effect faster.
- **Verify Domain Services**: If your site uses separate providers for email, subdomains, or special services, ensure you keep relevant records intact whenever you do an update.
### 8. Extra Goodies: SRV, DKIM, and CAA
- **SRV Records** help direct specialized services (like _minecraft._tcp.) to the correct server and port.
- **DKIM** is a TXT record that helps authenticate your emails, proving they came from your domain. A must-have if you’re serious about deliverability.
- **CAA** locks down which certificate authorities can issue [SSL certificates](/blog/fix-ssl-certificate-error/) for your domain. This can prevent unauthorized cert issuance if an attacker tries to impersonate your domain.
Not every site needs these advanced records, but it’s nice to know they exist if you’re building out a more complex setup.
### 9. Wrapping Up the DNS Basics
Let’s be honest - DNS can feel intimidating. One small mix-up can break your site or email. But with the fundamentals in your toolkit, you’re already miles ahead:
- You know DNS’s core purpose (matching names to IPs so we can surf easily).
- You understand the big record types (A, CNAME, MX, TXT, etc.).
- You grasp how to **create a dns entry**: pick the type, add the name, provide the correct value, and set a TTL.
- You realize that sometimes you need to wait out the dreaded “DNS propagation” period.
Once you see how it all fits together, “**dns records explained**” stops sounding like techno-babble and starts feeling like a puzzle you can solve.
### 10. Why Levamo Makes It Easier
By now, you might be thinking: “Okay, I get DNS in theory, but I’m not dying to juggle it day in and day out.” That’s where **Levamo** can step in:
**All-in-One Dashboard**
- Levamo offers a streamlined interface for domain management, hosting, and security. This means you can handle all your **dns entries for domain** in the same place you manage your site or app.
**Smart Defaults**
- Unsure how to set your MX or CNAME records? Levamo provides sensible defaults for typical domain configurations, saving you time and stress.
**Performance and Reliability**
- With Levamo, you’re tapping into a robust, globally distributed infrastructure. That translates to speedy DNS lookups and fewer downtime surprises.
**Friendly Support**
- Stuck on a DNS question or worried about messing up your subdomains? Levamo’s support team can guide you step by step, ensuring you don’t break your site by accident.
In short, if you’re ready to ditch the guesswork, give Levamo a try. Let them handle the underlying complexities so you can stay focused on building an awesome website - without losing sleep over arcane IP addresses or cryptic DNS records.
## Final Takeaway
DNS might seem arcane at first, but it’s really just an elegant system mapping human-friendly domains to the behind-the-scenes addresses that run the internet. From simple tasks like adding an A record for your new website, to advanced features like DKIM or SRV entries, you’ve got a lot of power at your fingertips. And with the help of a platform like **Levamo**, you can navigate all those DNS tasks confidently - knowing your domain, site, and email setups are in safe hands.
So go forth, pick your domain, set up those records with care, and watch your site flourish on the net. After all, the internet would be a lot scarier if we had to memorize hundreds of IP addresses!
---
## Elementor Review 2025: The Ultimate WordPress Builder, or Performance Nightmare?
- URL: https://levamo.com/blog/elementor-review/
- Category: website-development
- Author: Sunyyan Junaid
- Published: 2025-03-04
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Elementor in 2025: Still the ultimate WordPress builder, or a performance nightmare?
Building a website used to mean either learning to code or paying someone who did, both of which could leave you questioning your life choices. Then came page builders, and suddenly, anyone with a mouse and an internet connection could design websites.
And leading the charge? **Elementor. 🚀**
But the web design world moves fast, so the question now is: **Is Elementor still worth using in 2025?** Or has it been overtaken by faster, more optimized solutions?
As someone who has used Elementor extensively both for personal projects and client websites, I’m here to give you an honest, no-nonsense Elementor review, with a breakdown of what it does well, where it still struggles, and why it **performs significantly better on [Levamo](/)** than any other hosting provider (seriously, if you use Elementor, this is a game-changer).
Let’s dive in.
**Note**: If you’re looking for a guide on how to install Elementor in WordPress, we’ll be publishing the guide soon!
## What is Elementor?
Before we answer the question, here’s another question that users commonly ask: are WordPress and Elementor the same? Or, what is Elementor WordPress? To answer briefly, no! They’re not the same. WordPress is a CMS you can build your websites on, while…
[Elementor](https://elementor.com/) is a **drag-and-drop page builder** for WordPress that lets you create fully designed websites without writing code. It comes with a visual editor, pre-built templates, and tons of widgets for everything from buttons and forms to pricing tables and animations.
So is Elementor for WordPress free? Technically, yes.
There are two versions:
- **Elementor Free** - A basic version with limited widgets and design options.
- **Elementor Pro** - The premium version ($59/year for a single site) that unlocks advanced features like the *Theme Builder, WooCommerce integration, Popup Builder, and more*.
It has been a lifesaver for *freelancers*, *agencies*, and *business* *owners* who don’t want to mess around with complex code but still want professional-looking websites.
That said, Elementor is not without its flaws, and some developers absolutely hate it.
So, where does it stand today?
## What Elementor Does Well
### 1. Ridiculously Easy to Use (Especially for Non-Developers)
One of Elementor’s biggest strengths has always been its ease of use.
Instead of dealing with WordPress’s sometimes clunky block editor (Gutenberg), Elementor gives you a fully visual interface. You simply drag elements onto the page and adjust them in real time - no need to constantly preview or refresh.
As one Reddit user put it:
*“Elementor is a breath of fresh air compared to the block editor. The UI makes sense, and I don’t need to hunt around to change a font size.”*
For anyone who isn’t a developer, this is a huge deal. You can build complex layouts, add animations, and fine-tune every part of your site without ever opening the WordPress backend.
### 2. Feature-Rich (You Can Build Almost Anything)
Elementor Pro, in particular, is stacked with features:
- **Theme Builder** - Design custom headers, footers, blog layouts, and even WooCommerce pages.

- **Popup Builder** - Create popups without needing an extra plugin.

- **Motion Effects & Animations** - Parallax scrolling, hover effects, entrance animations, etc.

- **Dynamic Content** - Pull in data from custom fields (ACF, MetaBox) for more dynamic pages.

- **Huge Template Library** - Pre-built designs that speed up site creation.

Essentially, Elementor makes web design accessible to anyone, and that’s why it’s still one of the most popular builders in 2025.
### 3. Massive Community & Ecosystem
Since Elementor is so widely used, there’s **a massive community** around it. You’ll find:
- Countless YouTube tutorials and blog posts.
- Thousands of third-party add-ons that expand Elementor’s functionality.
- A dedicated Facebook group and Reddit community where users help each other.
If you ever get stuck, chances are someone else has already found a solution.
## Where Elementor Still Falls Short
This is where things get a little interesting. While Elementor is extremely popular and used by millions, some things bother users on a level that leaves them frustrated with the plugin. So, before we sum up the issues with Elementor, let's take a look at some real feedback from users.
*Note: The following feedback is not the views of the author or Levamo.*
### Unfiltered Feedback from Redditors
To dig deeper into the frustrations of users, I created a thread in the unofficial subreddit for Elementor: [What are your biggest frustrations with Elementor?](https://www.reddit.com/r/elementor/comments/1jqc4dc/what_are_your_biggest_frustrations_with_elementor/)
And to say the least, over 50 Redditors chimed in to voice their frustrations.
[u/thomisawesome](https://www.reddit.com/user/Thomisawesome/) "There are quite a few things, but one of the dumbest and most annoying things is with any of the areas where you can adjust top/bottom/right/left, like padding or margin.
If I had a left margin of 10px, when I come back to it later and want to change just that number, the "adjust all" mark is automatically checked. When I uncheck it, everything zeroes out, and I lose my previous number.
I don't know why that option is automatically selected, or why it zeroes out when I uncheck it. Minor, but extremely annoying. A productivity speedbump."
Another user ([u/slimpuffs](https://www.reddit.com/user/SlimPuffs/)) laid down an entire list of his issues with the plugin:
"These sound minor at first glance, but it adds up.
- This is already the top voted comment but I'll say it again - padding/margins resetting when going into a different reponsive mode. Dumbest ever, and has been there for years. Even Divi doesn't do this.
- Automatically adding 20 pixels at the bottom of a text element (specifically paragraphs, headlines are excluded from this)
- Image/Icon box styling - it seems if you adjust something, it'll only actually show if you switch back and forth between the Content and Style tab. Custom SVGs don't even show up at all unless you do the tab dance.
- Overlays sometimes lie. An opacity of 0.5 might look way too light while in edit mode, but on the live page it's considerably darker. Doesn't always happen though, not sure what causes the discrepancy.
- The sliders are very basic. The Plus Elements has a nice 'slider anything' widget which I'd like to see added to Elementor.
- Media Carousel - you can have either images or videos within the carousel - cool. *But you can't use self-hosted videos because...why?*
- I'd like to have the option of completely hiding elements that are hidden due to responsive mode settings, instead of just being greyed out and affecting the layout while editing. I get why they do it that way, but it's annoying.
- Global widgets - Stop making me unlink a global widget just because I want to delete it from the page. It's literally impossible to delete a global widget once it's placed on the page unless you unlink it.
- I much prefer the way Divi handles global sections. Elementor doesn't really have that kind of system, other than using template shortcodes I guess. Divi does it better though.
- Contact Forms - If you create a basic form using the Form widget, and want to set the Reply-To field to the Email field, you usually have to refresh the page before that option appears in the dropdown. Minor, but annoying running into it every time.
- If I set a text element to use a global font/typography, but want to adjust the font-size in this particular instance, I have to fuck with the unit dropdown before I can get what I want. For instance, lets say I apply a global style to a text element and it's at 1.2rem (the global default). If I want to make it 1.8rem or something, the unit automatically defaults to px. Clicking the unit dropdown and selecting rem doesn't actually change it. I have to first choose a completely different option like vw, *then* I can select rem, *then* I can actually change the size."
[u/Miserable_Doughnut_9](https://www.reddit.com/user/Miserable_Doughnut_9/) (not sure what reason a donut has for being miserable) laid this down:
"The fact that they keep adding features when things like the loop grid or global style still are very unstable. Things shouldn’t brake as soon as your add wordfence or a more complicated theme.
And I understand that its difficult to make software 100% fool proof and compatibel with other plugins. But I run into the same frustrating issues with Elementor too often, and when i go look for a solution online I see that i’m not the only one. Meanwhile Elementor announce a new groundbreaking feature while their Loop grid feature still break 6 out of 10 times.
Anyway, I wish they did a bit more stress testing and hardening of their base features and that they include other popular plugins that might cause issues. "
There are tons of other comments as well, but to sum things up, there are the biggest frustrations users face with Elementor:
### **1. Performance** and Bloat
Let’s address the elephant in the room: Elementor has long been criticized for being “bloated” and slowing down websites.
Why?
- It generates a lot of extra HTML and CSS, making pages heavier.
- It loads multiple JavaScript files, which can slow things down.
- Complex pages with lots of widgets can feel sluggish, especially on cheap hosting.
As one Redditor put it:
*“Elementor is great… until you realize your pages are loading at a snail’s pace.”*
That said, Elementor has been improving performance with updates like **Flexbox Containers**, which reduce unnecessary nested elements and improve loading speed. But out-of-the-box, it’s still heavier than pure Gutenberg or lightweight builders like Bricks.
However, if you run Elementor on Levamo, performance issues are nonexistent (more on that in a second).
### 2. Updates Can Be Buggy
Elementor rolls out frequent updates, but sometimes, these updates break things.
A common complaint among users is that new versions occasionally cause compatibility issues with themes, plugins, or even Elementor’s own widgets.
One frustrated user on Reddit shared:
*“Every time I update Elementor, I hold my breath, hoping nothing breaks. It’s like playing Russian roulette.”*
The safest approach? Always test Elementor updates on a staging site before applying them to a live website.
### 3. Official Support Could Be Better
While Elementor has a massive user community, its official support team has been criticized for slow response times.
A Redditor vented:
*“I pay for Elementor Pro, but getting support feels like waiting for a snail to cross the road.”*
That’s why many users rely on community forums and Facebook groups instead of Elementor’s official support.
### 4. Complex and Has a Learning Curve
Some users find Elementor's interface to be unintuitive and complex, especially for beginners. The plethora of options and settings can be overwhelming, leading to a steep learning curve and potential misconfigurations.
So while we can't do much about the official support or the learning curve of Elementor, at Levamo, we DO have a solution for Elementor's performance woes!
## Elementor on Levamo: The Best Performance You Can Get

The solution: [Levamo](/).
On cheap shared hosting, the Elementor builder can feel slow and clunky. But on a highly optimized platform that's built for speed and performance even under peak traffic, Elementor websites can perform significantly faster.
### Why?
Levamo was built for performance even under heavy traffic loads, with:
✅ **Advanced caching & auto-scaling** - Elementor pages load instantly.
✅ **[Free WordPress CDN](/cloudflare-cdn/) (Levamo CDN)** - Global delivery for ultra-fast speeds.
✅ **Modern infrastructure** - NVMe storage, optimized PHP, and LiteSpeed servers.
✅ **[24/7 managed WordPress hosting support](/support/)** - No more waiting days for answers.
✅ **Advanced security** - Keeping Elementor sites safe from attacks.
This means no lag, no slow editors, and no random crashes, just buttery smooth performance, even on large, complex Elementor sites.
But don't take our word for it. Read the reviews of actual users who are using Levamo: [Levamo Truspilot](https://www.trustpilot.com/review/rapyd.cloud) & [G2 reviews](https://www.g2.com/sellers/rapyd-cloud).
If you love Elementor but hate performance issues, Levamo is the answer.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
### Elementor vs. Gutenberg: Which One Should You Use?
We’re only comparing Elementor vs. Gutenberg here because Gutenberg is the default WordPress editor, meaning it’s what you get out-of-the-box without installing any extra plugins. If you want comparisons with other page builders (like Divi, Bricks, or Oxygen), let us know, and we’ll cover those as well!
So, how does Elementor stack up against WordPress’s native Block Editor?
### 1. Ease of Use & Design Flexibility
Elementor wins when it comes to design control and ease of use.
With Elementor, you get:
✅ **A true drag-and-drop builder** where you can see your edits in real time.
✅ **Complete control over layouts,** spacing, and responsiveness without coding.
✅ **A huge widget library** (buttons, forms, popups, sliders, etc.).
With Gutenberg, you get:
✔️ A **block-based editor** that is simpler and faster but less visually intuitive.
✔️ A **cleaner interface** but **limited design flexibility** unless you use custom CSS or third-party block plugins.
✔️ A system that feels more like editing a document than designing a page.
A Reddit user summed it up well:
“*Gutenberg is fine for writing blog posts, but for page layouts? Elementor all day.*”
If you’re building simple content pages or blog posts, Gutenberg might be enough. But if you want custom layouts, advanced styling, and interactive elements, Elementor is the clear winner.
### 2. Performance & Speed
Gutenberg **wins** on performance.
Because it’s built directly into WordPress, Gutenberg is faster and more lightweight than Elementor. A site built with Gutenberg (and a well-optimized theme) generally:
✅ **Loads faster** because there’s no extra page builder code.
✅ **Uses fewer resources** (less CSS/JavaScript).
✅ Has better out-of-the-box performance on budget hosting.
On the other hand, Elementor adds extra code and scripts, which can slow down pages if not optimized properly.
One Redditor put it bluntly:
“If performance is your #1 priority, Gutenberg is the way to go. But if you need to actually design a website, Elementor wins.”
That being said, performance isn’t an issue if you’re hosting your Elementor site on Levamo. Thanks to advanced caching, auto-scaling, and a free Levamo CDN, Elementor runs just as fast as Gutenberg but without the design limitations.
### 3. Workflow & Customization
- **Gutenberg is great for content-focused websites.** If your site is mainly blog posts, news articles, or simple pages, Gutenberg is leaner and integrates more naturally with WordPress.
- **Elementor is better for business websites,** portfolios, landing pages, and sales funnels. It lets you build pages visually without needing to write code or worry about layout limitations.
One user described the difference like this:
“Gutenberg is the ‘official’ way, but Elementor is the better way if you want full creative control.”
### So, Which One Should You Use?
✔️ **Use Gutenberg if:**
- You want a lightweight site with maximum performance.
- You’re fine with basic layouts and minimal design flexibility.
- You don’t mind using CSS or extra plugins to get more design options.
✔️ **Use Elementor if:**
- You want full control over your design without coding.
- You need advanced layouts, animations, or interactive elements.
- You want to work faster with a true drag-and-drop interface.
The bottom line? Gutenberg is great for speed, but Elementor is better for design.
And if you’re worried about Elementor’s performance, hosting on Levamo's [best managed WordPress hosting](/managed-wordpress-hosting/) eliminates that problem entirely. 🚀
## Final Verdict: Is Elementor Still Worth It in 2025?
So while this Elementor review covers the most important aspects of this feature-rich plugin, it all boils down to what you want from your website. So, Elementor for WordPress is a:
✅ **YES**, if you want an easy, powerful way to build WordPress websites without coding.
❌ **NO**, if you’re obsessed with performance and want a leaner, more minimal approach.
For freelancers, agencies, and designers who value creative freedom and speed of development, Elementor is still one of the best page builders available.
And if you’re using Elementor, switching to [Levamo](/performance/) will completely change your experience by eliminating performance issues and giving you the smoothest Elementor experience possible.
So, is Elementor still the king of page builders?
It depends on your needs, but with the right hosting (👀 Levamo), it’s still a great choice in 2025. 🚀
---
## How to Redirect HTTP to HTTPS: Top 4 Methods
- URL: https://levamo.com/blog/redirect-http-to-https/
- Category: website-development
- Author: Salman
- Published: 2025-02-26
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Secure your site! 4 easy methods to redirect HTTP traffic to HTTPS.
Picture this: You’ve just gone through the trouble of installing an SSL certificate on your website. You’re ready to boast that little padlock icon in the browser address bar - only to discover that half of your visitors still see the old **HTTP** version of your site. Frustrating, right? This is why and where the question **"how to redirect HTTP to HTTPS"** comes into play.
Below, we’ll take a deep dive into why HTTPS is crucial, how to make sure your site can handle secure connections, and exactly how to **redirect http to https all links** so nobody slips through the cracks. We’ll cover different hosting environments, common pitfalls, and the finishing touches that ensure you pull off a smooth, and permanent, transition to HTTPS.
## Why Bother Switching to HTTPS?

Let’s start with the basics - HyperText Transfer Protocol Secure [a.k.a **HTTPS**] is the encrypted version of HTTP. It uses SSL/TLS encryption technology to keep users’ data safe in transit - think of it as turning a website’s communication into a coded language. This offers big benefits:
- **Security**: Sensitive information (like passwords, payment details, or personal data) stays hidden from prying eyes.
- **SEO Love**: Google has repeatedly confirmed that HTTPS is a ranking signal. Sites with HTTPS can enjoy a slight boost in search visibility.
- **Trust Factor**: Modern browsers flag non-HTTPS sites as “not secure,” which can scare off potential visitors or customers.
- **Future-Proofing**: Many new features in web development - like certain browser APIs - require HTTPS to function fully.
Long story short: going fully secure is not just for banks and e-commerce giants. Bloggers, small businesses, and personal portfolios can all benefit from that extra layer of trust and encryption.
## First Things First: How to Make Your Website Support HTTPS

Before you can **redirect both http and https** URLs to the secure version, you need a valid **SSL/TLS certificate** installed. Here’s the gist of how to make your website support HTTPS:
**Get an SSL Certificate**:
- Some hosting providers offer free certificates via Let’s Encrypt. If not, it is quite easy to purchase one from a certificate authority like Sectigo, DigiCert, or GlobalSign.
- For personal sites, Let’s Encrypt is usually enough. E-commerce or enterprise projects might prefer a paid cert with extended validation.
**Install and Configure the Certificate**:
- Many hosting dashboards have an option to install your SSL certificate.
- Most users have to paste the certificate code, private key, and intermediate certificates into their respective fields.
**Check the Installation**:
- Tools like SSL Labs let you verify if everything is set up correctly and if your server is delivering the right chain of trust.
- Visit your site using https://yourdomain.com to confirm that no glaring browser warnings pop up.
Once your certificate is in place, your site can handle secure connections, but visitors might still be reaching the old HTTP version. That’s where the redirect step comes in.
**Also Read:** [TLS vs SSL](/blog/tls-vs-ssl/)
## Approaches to Redirect HTTP to HTTPS
There isn’t a one-size-fits-all method to **redirect http to https all links**, mainly because different hosting environments handle this differently. Let’s look at a few common scenarios:
### 1. Using .htaccess on Apache
If you're on an Apache web server (common with many shared hosts), you can place rewrite rules in a file named .htaccess at the root of your site. Here's a simple snippet:
```apache
RewriteEngine On
RewriteCond %{HTTPS} !=on
RewriteRule ^(.*)$ https://%{HTTP_HOST}/$1 [R=301,L]
```
**Explanation**:
- RewriteEngine On : Turns on Apache’s rewriting engine.
- RewriteCond %{HTTPS} !=on : Checks if HTTPS is off.
- RewriteRule ^(.*)$ https://%{HTTP_HOST}/$1 [R=301,L] : Redirects the user to the same domain and request URI, but forces HTTPS. The R=301 signals a permanent redirect.
If your hosting environment uses a special control panel (like cPanel), you might find a “Force HTTPS Redirection” toggle button. This does basically the same thing under the hood, but in a few clicks rather than manual code editing.
### 2. Using Nginx
Nginx, another popular server, doesn't use .htaccess. Instead, you'll typically edit your server's config file directly. The snippet might look like this:
```nginx
server {
listen 80;
server_name yourdomain.com www.yourdomain.com;
return 301 https://yourdomain.com$request_uri;
}
```
**Explanation**:
- listen 80; means the server is listening on port 80 for HTTP traffic.
- server_name clarifies which domains this config applies to.
- return 301 https://yourdomain.com$request_uri; forces the visitor to the HTTPS version, carrying over the path/query string.
After editing, you’d reload or restart Nginx, typically with a command like sudo service nginx reload.
### 3. Using Cloudflare or Other CDNs

If you’re using a known service like Cloudflare, set up “Always Use HTTPS” or “SSL/TLS” rules in the dashboard, thus removing the need for custom server config. Also, make sure the origin server also has a valid certificate - otherwise, create a “Flexible SSL” scenario, which only encrypts traffic from the user to Cloudflare, not from Cloudflare to your server. That’s suboptimal from a security standpoint.
### 4. CMS-Specific Plugins
For example, with WordPress, a plugin like “Really Simple SSL” can handle the necessary changes. Or set “WordPress Address (URL)” and “Site Address (URL)” to use https:// in the general settings. Just note that you may still want a server-level redirect to catch any direct requests to the old HTTP version.
## Checking If Your Redirect Actually Works
Once a method is configured, how to ensure the website **redirects both http and https** to the correct version?
- **Manual Testing**: Simply type http://mysite.com or http://www.mysite.com in your browser. Did the browser land at https://yoursite.com? If yes, success!
- **Multiple Endpoints**: Don’t forget to test subpages or blog posts. For instance, if you have http://yoursite.com/blog, see if it automatically loads https://yoursite.com/blog.
- **Online Redirect Checkers**: Tools like “Redirect Checker” or “HTTP Status Code Checker” can verify that each request triggers a 301 status code.
- **Search Engine Tools**: Check Google Search Console or Bing Webmaster Tools. If they see consistent HTTPS indexing, you’re in the clear.
**Pro Tip**: Use a “301 Moved Permanently” redirect. This tells browsers and search engines your site has permanently changed its protocol to HTTPS, preserving SEO juice, ensuring a clean search engine index, and making sure you don't face an error like "[the requested url was not found on this server](/blog/the-requested-url-was-not-found-on-this-server/)".
## Common Pitfalls and How to Avoid Them
### 1. Mixed Content Warnings
You might have done everything right for your domain. However, if your pages embed images, scripts, or stylesheets using http://, modern browsers will show a “[mixed content](/blog/how-to-fix-mixed-content-issue-wordpress/)” warning or block them entirely. That’s definitely not the user experience you want.
**Solution**:
- Update your site’s URLs (images, CSS, JavaScript, etc.) to use https:// or relative links (//example.com).
- WordPress users can do a quick search-and-replace in the database or use a plugin like “Better Search Replace.”
### 2. Inconsistent Domain Coverage
Another snag is forcing https://example.com but forgetting about https://www.example.com. Some site owners prefer the “www” version, others don’t. The key is to pick one canonical version and redirect the other to it. This helps your site’s SEO by avoiding content duplication.
**Solution**:
- Use your config or .htaccess to direct every single variation (http://, http://www, https://www) to your chosen primary domain with https://.
### 3. Missing or Incorrect SSL Installation
If your certificate chain is incomplete, users might still see errors, and you might need to [fix SSL certificate error,](/blog/fix-ssl-certificate-error/) even if you’re forcibly redirecting them. The dreaded “NET::ERR_CERT_AUTHORITY_INVALID” can appear if you’ve missed an intermediate certificate. Or maybe you forgot to install the certificate for www.example.com, so users typed in “www” and got an invalid certificate.
**Solution**:
- Double-check your SSL installation. Tools like SSL Labs confirm if your chain is valid and all domains are covered.
### 4. Overlooked Hard-Coded Links
Even if you set up the best redirect rules, some old forum posts or third-party sites might link to your old http:// addresses. The good news is that a well-configured redirect will still route those links to HTTPS. But if your own site is peppered with manual http:// references, it’s better to update them for a consistent experience.
## Performance Considerations
While HTTPS encrypts data, it used to have a slight performance overhead. These days, however, that overhead is minimal, thanks to modern hardware and protocols like HTTP/2 or HTTP/3, which actually require or strongly recommend TLS encryption. In many cases, sites actually become faster over HTTPS if HTTP/2 is enabled because it supports features like multiplexing and header compression.
**Actions to Consider**:
- **Enable HTTP/2**: If your server supports it, you’ll see performance gains once you switch to HTTPS.
- **Use Caching and Compression**: Tools like Gzip compression or a caching plugin can ensure your new secure site still loads fast.
- **CDN Integration**: A Content Delivery Network can reduce the load on your server and speed up global access - just make sure it’s configured to handle HTTPS properly.
## Telling Search Engines You’ve Moved to HTTPS
When you **redirect http to https all links**, search engines eventually pick up on the changes, but it’s good practice to give them a heads-up:
- **Update Google Search Console**: Add the HTTPS version of your site as a new property and submit a fresh sitemap.
- **Update Your Sitemaps**: Make sure your sitemaps list the https:// URLs. This helps crawlers discover the new links faster.
- **Monitor Indexing**: Keep an eye on your analytics and Search Console coverage reports. If Google sees 301 redirects, it will gradually shift its index to the new protocol.
**Important**: Don’t just flip everything overnight and expect a perfect transition. Google might take a couple of weeks to fully re-index your site as HTTPS. That’s normal - just ensure your 301 redirects remain in place long-term.
## Ongoing Maintenance and Best Practices
- **SSL Certificate Renewal**: Make sure you renew your certificate before it expires. If you’re using Let’s Encrypt, set up auto-renew. If you’re using a paid cert, mark your calendar well before the expiry date.
- **Keep an Eye on Mixed Content**: If a new image is added or content embedded from external sites, ensure it's served via HTTPS.
- **Review Security Headers**: If the website is on HTTPS, consider adding HTTP Strict Transport Security [a.k.a HSTS] too and other security headers to further protect visitors.
- **Educate Team**: If there are multiple people updating content or working on dev, ensure they always use HTTPS links.
- **Monitor Logs and Analytics**: Keep an eye out for 404 errors or unexpected traffic drops. They might indicate an issue with your redirect rules.
## Conclusion
Switching from HTTP to HTTPS feels like a big leap, but it doesn’t have to be stressful. The crucial steps are:
- **Install a valid SSL/TLS certificate** to make your website support https.
- **Set up the appropriate redirect** at a server or CMS level, ensuring visitors (and search HTTPengines) land on the secure version.
- **Check for mixed content** and domain consistency to avoid partial security warnings or SEO confusion.
- **Verify everything** using online tools and keep an eye on your site’s performance and search rankings.
Yes, it’s a bit of housekeeping. But once you do it, you’ll enjoy a more professional, trusted, and future-proof online presence. Not to mention, seeing that reassuring padlock icon in the browser feels great - like locking your house’s front door and knowing everything’s safe.
Not in the mood to juggle the complexities yourself? Levamo can streamline the entire process by offering built-in SSL support, one-click redirects, and top-tier [fully managed ](/managed-wordpress-hosting/)[WordPress ](/managed-wordpress-hosting/)[hosting](/managed-wordpress-hosting/) features to keep your site both secure and speedy.
When all’s said and done, you’ll be rewarded with that reassuring padlock icon in the browser - letting the world know your site values visitor privacy and data protection. It’s a small touch that can make a big difference in user confidence.
**In short**, if you’re looking to **redirect both http and https** or want to handle “HTTP to HTTPS all links” meticulously, just follow the steps above. It’s a one-time (or occasional) chore that pays off in trust, SEO benefits, and overall site security.
Now go forth, set up your secure environment, and watch your visitors (and Google) smile at that oh-so-lovely padlock.
## Frequently Asked Questions

### How do I automatically redirect HTTP to HTTPS?
You can automatically redirect HTTP to HTTPS by editing your server configuration. Here's how you do it for different servers:
**Apache (.htaccess file):**
```apache
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
```
**Nginx:**
```nginx
server {
listen 80;
server_name yourdomain.com www.yourdomain.com;
return 301 https://$host$request_uri;
}
```
### How to redirect HTTP to HTTPS using URL rewrite?
If you're using **IIS** (Internet Information Services), you can use **URL Rewrite Module**:
- Redirect type: `Permanent (301)`
- Open IIS Manager.
- Select your website.
- Go to **URL Rewrite**.
- Add **Inbound Rule** → **Blank Rule**.
Set the condition:
- Condition input: `{HTTPS}`
- Check if input string: `Matches the Pattern`
- Pattern: `^OFF$`
Action:
- Action type: `Redirect`
- Redirect URL: `https://{HTTP_HOST}/{R:1}`
- Redirect type: `Permanent (301)`
### How do I force HTTPS traffic?
Forcing HTTPS traffic means ensuring all traffic uses HTTPS. This can be done via:
- **.htaccess file** (Apache)
- **Nginx redirect rules**
- **IIS URL Rewrite Module**
- Using **HSTS headers** to instruct browsers to always use HTTPS.
Example HSTS header:
`Header always set Strict-Transport-Security "max-age=31536000; includeSubDomains" env=HTTPS`
### How do I change all links from HTTP to HTTPS in WordPress?
There are a few ways.
**1. Update Site URL:**
- Go to **Settings > General**
- Change both "WordPress Address (URL)" and "Site Address (URL)" to `https://`
**2. Use a Plugin:**
- Install a plugin like **Better Search Replace** or **Really Simple SSL**
- Use it to find and replace `http://yourdomain.com` with `https://yourdomain.com`
**3. Update Database Manually:**
- Via phpMyAdmin or CLI, run SQL queries to replace all occurrences.
---
## What is an SSL Certificate and How to Fix SSL Errors?
- URL: https://levamo.com/blog/fix-ssl-certificate-error/
- Category: website-development
- Author: Sunyyan Junaid
- Published: 2025-02-24
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix SSL errors! Understand certificates and keep your browsing secure.
Ever hopped onto a website, ready to browse new gadgets or read a juicy blog post, only to be blindsided by a giant security warning splashed across your screen? It’s unnerving, right? Usually, those alerts revolve around **SSL certificate errors**, and they can appear under names like “ssl certificate cannot be trusted,” “invalid ssl certificate,” “outdated security certificate,” or even the puzzling “err ssl version or cipher mismatch.”
Truth is, you don’t need to panic; these warnings don’t automatically mean you’ve landed on some sketchy, underworld corner of the internet.
In fact, many SSL hiccups boil down to small oversights that you (or a site owner) can fix with a little detective work.
In the sections below, we’ll demystify why SSL certificate errors show up, clarify the role SSL plays in your online safety, and offer some down-to-earth tips for preventing (or resolving) these issues, whether you’re the site owner or just a casual visitor.
So, if you're already asking, "What is SSL?" let's start with that. If you'd rather watch that read, here's a video on what an SSL certificate is:
https://www.youtube.com/watch?v=b8rX7sSupO8
## What Is an SSL Certificate And Why Do They Matter?
Think of **SSL (Secure Sockets Layer)** and its newer cousin, TLS (Transport Layer Security), as digital bodyguards for any data flowing between your device and a website’s server. They have three big jobs:
- **Encryption**: They scramble your info (like passwords or credit card numbers) so snoops can’t intercept it in readable form.
- **Authentication**: They confirm that the site you’re on is legit, not a shady impersonator.
- **Building Trust**: When a site’s SSL certificate is good to go, browsers show that comforting padlock icon in the address bar. People see it and think, “Okay, I’m safe to shop or sign up here.”
When something’s off, like maybe the certificate has expired or doesn’t match the domain, your browser throws up a big red flag, also known as an SSL certificate error. Even if you personally believe the site is safe, your browser is programmed to protect you first and ask questions later.
**Also Read:** [TLS vs SSL](/blog/tls-vs-ssl/)
## Common SSL Errors/Warnings
Let’s be real: SSL warnings can look a little scary, especially if you’re not familiar with the lingo. But most revolve around a few recurring scenarios:
### A. “SSL Certificate Cannot Be Trusted”
This message pops up when your browser doesn’t recognize the authority that issued the certificate. Maybe it’s a self-signed certificate or from a less-known provider. Essentially, your browser’s saying, “I don’t see this certificate in my trusted database - proceed with caution.”
### B. “Invalid SSL Certificate”
“Invalid” is a broad label for when a certificate doesn’t line up with what the browser expects. Some typical culprits:
- **Domain Mismatch**: Maybe the certificate says www.example.com, but you’re loading example.com.
- **Corrupted or Incomplete Certificate**: If installation wasn’t done properly, the certificate might appear broken.
### C. “Outdated Security Certificate”
A super-common error: all SSL certificates expire after a certain period (often 90 days if it’s Let’s Encrypt, or up to two years for longer-term certificates). If the site owner forgets to renew, visitors get a dreaded expiration warning stating that the certificate isn’t valid anymore.
### D. “ERR SSL Version or Cipher Mismatch”
Despite sounding super technical, this basically means the server is using old encryption protocols (like SSL 2.0, SSL 3.0, or old versions of TLS) that modern browsers have deemed unsafe. The browser responds by blocking the connection.
## **Core Reasons Why Browser Shows SSL Error Warnings**
- **Expired Certificate**: If a site’s SSL certificate crosses its expiration date, browsers freak out because that typically indicates someone’s not actively maintaining security.
- **Missing or Incorrect Configuration**: Installing an SSL cert sometimes involves multiple files (including intermediates). Skip a step, and your browser raises an eyebrow.
- **Domain Differences**: If the certificate says it’s for one domain but you’re visiting another, your browser spots the mismatch and complains.
- **Server or Hosting Setup**: A server that insists on using ancient TLS versions can lead to “err ssl version or cipher mismatch” alerts.
## How to Fix SSL Certificate Error if You're the Site Owner
Good news is that most SSL certificate errors are easy to correct once you know what to do. Let's take a look at some of the methods:
- **Renew an Expired Certificate**: If your certificate has lapsed, renew it immediately. Many hosts or services (like Let’s Encrypt) can auto-renew to prevent future lapses.
- **Install the Full Certificate Chain**: Reputable SSL issuers provide both a main certificate and one or more intermediates. If you don’t install those middle links, browsers say, “ssl certificate cannot be trusted.”
- **Ensure the Domain Matches**: If your cert covers www.example.com, but your site is also accessible at example.com (no “www”), you might need a Subject Alternative Name (SAN) or wildcard certificate to cover all variations.
- **Upgrade Outdated TLS Versions**: For “err ssl version or cipher mismatch,” configure your server to use modern TLS (at least TLS 1.2 or 1.3). Your hosting provider often has a guide on how to do this.
- **Use an SSL Checker**: Tools like SSL Labs are free and let you test your domain. They’ll point out missing intermediate certs, weak ciphers, or domain mismatch issues in plain English.
## Fix SSL Error as a Website Visitor
If you’re not the site owner, but a site you generally trust is throwing an “invalid ssl certificate” or something that says “ssl certificate cannot be trusted,” here’s how to proceed:
- **Double-Check the URL**: Typos are more common than you think! Scammers also use look-alike domains to fool you.
- **Update Your Browser**: Running an outdated Chrome, Firefox, or Safari can cause random SSL warnings if the browser doesn’t recognize a newer certificate authority.
- **Check Your OS or Device Date**: Weird but true: if your computer’s date/time is off by a large margin, certificates can appear invalid. Sync your device’s clock and refresh.
- **Temporarily Disable Antivirus SSL Scans**: Some antivirus tools meddle with encrypted connections, occasionally causing false alerts about an “invalid ssl certificate.” Only do this if you genuinely trust the site, and remember to switch the feature back on afterward.
- **When in Doubt, Don’t Proceed**: If you have a gut feeling the site might be dangerous (like a random email link or suspicious content), err on the side of caution. SSL warnings serve as that neon caution sign for a reason.
## Tips to Avoid SSL Errors in the Future
- **Opt for Auto-Renew**: Services like Let’s Encrypt or commercial SSL providers let you set up auto-renew so you never wake up to an expired certificate again.
- **Keep Your Server/Hosting Updated**: Old server software often defaults to outdated protocols, leading to that “err ssl version or cipher mismatch” fiasco.
- **Use Reputable SSL Authorities**: If you’re going for a free SSL, Let’s Encrypt is widely trusted. For paid options, stick to recognized names that browsers trust by default.
- **Test Changes in Staging**: If you maintain a mission-critical site, test certificate updates or domain changes on a staging version before flipping the switch on your main site.
- **Confirm Domain Variations**: Decide whether your site should appear with or without “www,” or whether subdomains like blog.example.com or shop.example.com exist. Make sure your certificate covers them all.
- **Use Managed hosting providers**: [Managed WordPress cloud hosting](/managed-wordpress-hosting/) providers usually take care of these issues for you, so you can stay worry-free.
### Wrapping Up
SSL certificate errors can seem like the internet is waving a huge red flag in your face. But in reality, these messages usually boil down to simple oversights: an expired cert, a domain mismatch, missing intermediate files, or archaic encryption protocols.
If you’re the site owner, renewing or properly configuring your certificate is often all it takes to banish those warnings. If you’re a user, double-check everything from the URL to your own device settings before ignoring the pop-up.
At its core, an SSL warning is just your browser or system trying to shield you. Embrace that extra layer of caution. Keep your certificates current, ensure your domain settings line up, and upgrade your server’s TLS protocol if you need to.
With those steps, you’ll be well on your way to ensuring that visitors see the friendly little padlock rather than an ominous caution sign every time they land on your site.
---
## How to Access WordPress Admin with a Fatal Error Warning
- URL: https://levamo.com/blog/wordpress-fatal-error-warning/
- Category: website-development
- Author: Sunyyan Junaid
- Published: 2025-02-20
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix a fatal WordPress error! Get back into your admin dashboard quickly.
When you're browsing through your WordPress site and you're met with a fatal error message, it could be due to a plugin conflict, or your theme decided to throw a tantrum. Either way, you probably can’t even open the WordPress dashboard to fix the problem, and you're panicking...
Don’t worry. This is a straightforward guide on **how to access WordPress admin with a fatal error warning** and restore your site.
## What is a WordPress Fatal Error Warning?
A WordPress fatal error is the moment your site slams into a wall and refuses to move. Under the hood, WordPress is powered by PHP. Every theme, plugin, and core file leans on PHP to load the features your visitors rely on. When a PHP script blows up, WordPress cannot finish its start-up routine. The result is a white screen, a scary “There has been a critical error on this website” notice, or a login page that goes nowhere.
#WordPress Fatal error warning
Sounds final, but it is not. WordPress ships with a built-in safety net called **Recovery Mode**. This tool pauses the offending code, lets you back into the admin area, and lets you deactivate the broken theme or plugin before your audience even notices something was wrong.
So let’s turn that “critical error” screen into a quick pit stop instead of a full-blown crisis.
## 1. Take a Deep Breath and Gather Your Tools
Do not try to solve the problem before you have the following access rights:
- **Web Hosting Credentials**: You may require File Transfer Protocol (FTP) or File Manager access from your hosting control panel (cPanel or similar).
- **Backup or Staging Option**: In an ideal world, you’d have a recent backup. If not, proceed carefully to avoid losing data.
**Goal**: The idea is to bypass or fix whatever’s causing the fatal error so you can open the WordPress admin area again.
## 2. Identify the Usual Suspects
A typical reason you can’t access WordPress admin with a fatal error warning is a code conflict, often from a plugin or theme. If you recall installing or updating something right before the error, that might be your culprit.
- **Plugins**: Maybe you activated a brand-new plugin that isn’t playing nicely with your theme.
- **Themes**: Sometimes, a theme update or a custom code snippet can break your site.
- **PHP Version**: Outdated PHP or mismatch with your plugin requirements.
## 3. Disable Plugins (Without the Admin Panel)
If you suspect a plugin is behind the meltdown, you’ll need to disable it manually.
### Using FTP or File Manager
- **Sign in** to your hosting control panel or FTP client.
- **Go to** /wp-content/plugins/ folder.
- **Rename** the plugin folder you suspect, e.g., change wp-content/plugins/conflicting-plugin/ to wp-content/plugins/conflicting-plugin-disabled/.
- **Check Your Site**: Try logging into your WordPress admin again. If the error vanishes, you’ve found the culprit.
**Pro Tip**: If you’re not sure which plugin caused the error, temporarily rename the entire plugins folder to plugins-disabled. This deactivates all plugins. Then restore them one by one until you find the bad apple.
## 4. Switch to a Default Theme (If the Theme Is the Problem)
In some cases, your theme might be throwing a fatal error:
- **Open File Manager or FTP**: Head over to /wp-content/themes/.
- **Rename the Active Theme Folder**: For example, awesome-theme becomes awesome-theme-off.
- **WordPress Defaults to a Core Theme**: Something like Twenty Twenty-Three will load automatically.
- **Log in** to your admin to confirm the error is gone.
## 5. Check Your PHP Version
If you are using an older PHP version and your theme or plugin needs a higher version, then you will get the fatal error message. You may be able to resolve the issue by changing your PHP settings:
- **Log into Hosting Panel**: Look for a “PHP Settings” or “Select PHP Version” tool.
- **Upgrade to a Stable PHP Version**: Typically, 7.4 or higher (depending on current WordPress recommendations).
- **Save & Test**: Refresh your site to see if the error disappears.
## 6. Increase Your Memory Limit
Sometimes, WordPress runs out of memory, causing a fatal error. To boost it:
- **Edit wp-config.php**: Using FTP or File Manager, open wp-config.php.
`define( 'WP_MEMORY_LIMIT', '256M' );`
- **Save and Check**: If a lack of memory was the issue, you should now be able to access WordPress admin with a fatal error warning a thing of the past.
## 7. Activate Debugging to Get Clues
If you still can’t figure out the root cause, turn on [WordPress debugging](/blog/debug-in-wordpress/):
- **Open wp-config.php**
define( 'WP_DEBUG', true );
define( 'WP_DEBUG_LOG', true );
define( 'WP_DEBUG_DISPLAY', false );
- **Check the Debug Log**: Inside wp-content, a new file called debug.log will show error messages that might point you to the culprit.
## 8. Contact Your Host or Developer
If all else fails and you’re still locked out:
- **Contact Support**: Your web hosting might spot server-level issues causing the fatal error.
- **Hire a Developer**: If it’s complex custom code or a persistent error, a professional can sort it out faster than you can say “[white screen of death](/blog/wordpress-white-screen-of-death/).”
## 9. Tips to Prevent Future Fatal Errors
- **Test Updates in a Staging Environment**: Before you click “Update Plugin” or “Update Theme,” try it on a test site.
- **Use Reputable Plugins/Themes**: Check reviews, active installs, and last update date to avoid shady or abandoned code.
- **Keep WordPress & PHP Up to Date**: Outdated software is a recipe for trouble.
**Also Read:** [Common Server Problems](/blog/fastest-wordpress-hosting/)
## Conclusion
No one likes the “fatal error” roadblock, especially when you’re locked out of your own admin panel. But tackling **how to access WordPress admin with a fatal error warning** doesn’t have to be a nightmare. By disabling troublesome plugins or themes, checking your PHP setup, and upping your memory limit if necessary, you’ll be back in business in no time. Keep backups, test changes, and stay on top of updates to ensure these errors remain rare guests on your site.
Remember: a little precaution today can save a major headache tomorrow. Good luck, and happy WordPressing!
---
## The Fastest WordPress Hosting Provider in 2025
- URL: https://levamo.com/blog/fastest-wordpress-hosting/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2025-02-20
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find the fastest WordPress hosting for 2025 based on rigorous testing.
Website speed is no longer a luxury but a necessity. A slow-loading site can impact everything from user experience to SEO rankings and conversion rates. That's where the need for the fastest WordPress hosting comes into play.
If you're looking for a fast web hosting provider, you need data-driven insights rather than marketing claims. That’s why we analyzed the 2025 [fully managed WordPress hosting](/managed-wordpress-hosting/) Industry and rigorously tested multiple hosting providers to uncover the best-performing platforms.
We'll break down the fastest WordPress hosting providers in this article based on real test data. We’ll compare their server response times, query execution speeds, load handling, and caching technologies to help you make an informed decision.
But before you jump into that, let's take a quick look at why anyone would need the fastest WordPress hosting in the first place.
## Why Do You Need the Fastest WordPress Hosting?
The reason is simple: Slow websites lose traffic, trust, and money. High-performance hosting does the opposite: it gets you more traffic, more trust, and higher revenue.
Here’s why speed should be non-negotiable:
- **Fast hosting saves you money**: Faster load times mean higher conversions. That ad spend? It works harder when your site loads instantly.
- **Visitors bounce fast**: If your site takes more than 3 seconds to load, nearly half of your visitors are gone. Poof. No clicks, no conversions, just lost opportunities.
- **Speed affects your SEO**: Google ranks faster sites higher. If your hosting slows you down, you're basically telling search engines, *“Please ignore me.”*
- **Your backend deserves better**: Tired of a sluggish WordPress dashboard? Fast hosting makes publishing, editing, and even plugin updates feel smooth.
- **Mobile users won’t wait**: On mobile, every millisecond counts. The slower your site is, the faster they hit the back button.
- **First impressions matter**: Your site speed is your handshake. If it’s slow and sloppy, that visitor is already halfway to your competitor.
So, while these are the reasons why you need fast WordPress hosting for your online business, how do you know which among the hundreds of choices out there are actually fast? Good question.
Let's break it down.
## Features of the High-Traffic WordPress Hosting
To determine the fastest hosting for WordPress or any other hosting, there are some key features that they must have to ensure that they provide you with the most reliable hosting.
**[Performance-First Infrastructure](/performance/)**: The Fastest WordPress hosting will always be engineered for peak performance and will provide unmatched performance for even the most dynamic websites.
**Reliability**: The Fastest WordPress hosting will always boast a reliable and stable infrastructure with at least 99.99% uptime.
**Autoscalability**: Any fast cloud hosting will offer limitless scalability, which allows users to grow without limits and handle traffic peaks effectively during the busiest sales seasons.
**[Iron Clad Security](/managed-security/)**: Malware scanning, DDoS protection, firewalls, and all the security bells and whistles must be a part of any good web hosting solution.
**[24/7 Expert Support](/support/)**: Any fast web hosting worth its salt will back you up with 24/7 real engineers' support, not scripted replies. Top hosts have people who’ve been there and* debugged that.*
Other critical features: **[Global CDN](/cloudflare-cdn/)**, Built-in Caching, [Ease of Use](/easy-to-use-platform/), Cost-effectiveness, etc.
While these are the most critical aspects you should be looking at while choosing the Fastest WordPress hosting, you should also look at actual user reviews and feedback, which are even more important than just raw numbers. For example, always take a look at [Trustpilot](https://www.trustpilot.com/review/rapyd.cloud?) or [G2 reviews](https://www.g2.com/products/rapyd-cloud/reviews#reviews) of a fast cloud hosting service to ensure users are happy.
## Why Is Levamo the Fastest WordPress Hosting?

What sets Levamo apart as a top choice for the Fastest WordPress hosting? Let's take a closer look!
### Levamo Stack
WordPress recommends a hosting setup that includes **LiteSpeed**, **Apache**, or **NGINX**, along with the latest stable PHP versions (8.0 or greater) and MariaDB (version 10.4 or greater) for optimal performance.
Levamo’s hosting stack is built on high-performance technologies:
- **[LiteSpeed Web Server](/blog/lite-speed-hosting-benefits/)**
- **Latest PHP** and **MariaDB versions**
- **AWS-backed cloud infrastructure**.
Levamo's optimized LiteSpeed stack enhances WordPress performance with the lowest server response times, allowing websites to handle more traffic effortlessly.
Additionally, you get powerful performance boosters like:
- Object Cache Pro (Redis with Rely)
- Advanced CDN integration
- Enterprise-level caching mechanisms
All this ensures the fastest load times and seamless scalability.
### Levamo **Server Technology**
The server software you choose plays a critical role in your website’s performance.
While Nginx offers a noticeable improvement, making it a better choice for efficiency. However, LiteSpeed Web Servers takes it a step further with even superior performance.
LiteSpeed Web Servers excel in server response times. They handles more requests per second with superior resource management and faster data transfer, ensuring your site operates at peak efficiency.
Hence, Levamo employs LiteSpeed Web Servers, renowned for their swift response times and ability to handle high traffic efficiently, up to ten times faster than Apache. This server software excels in environments that demand high concurrency, making it ideal for dynamic and resource-intensive WordPress sites.
### Boosting Speed with Object Caching
Object caching is a technique that stores data from database queries in memory, so when the same piece of data is needed again, it can be served from the cache rather than querying the database a second time. This is particularly important for Dynamic WordPress site performance because they rely heavily on database queries to serve content.
Levamo integrates Redis for object caching, significantly enhancing database query responses and page load times. With WordPress 6.4's native optimization for Redis, Levamo ensures superior caching efficiency, crucial for sites with heavy dynamic content.
Additionally, Levamo includes the Object Cache Pro plugin and Relay for free, which further optimize caching operations and ensure even faster performance for high-demand WordPress sites.
### Redis Cache (via Relay) and Object Cache Pro
Another superior caching system that we provide for our dynamic website hosting is Relay, a special type of Redis client.
Relay is so good for dynamic sites because of a feature called active invalidation. Active cache invalidation ensures that any time a piece of information changes on an interactive site, the old cached version of that data is invalidated, and the new version is then immediately re-cached.
And that is exactly what dynamic sites need: the “active” elimination of stale cache content so users always see timely, accurate updates.
We also provide free usage of Object Cache Pro, the premium version of Redis Object Cache. Object Cache Pro helps reduce a server's workload by storing database queries as objects that can be cached and quickly executed from RAM.
It's highly recommended to help speed up your site by lowering the workload on your database and, thus, the CPU.
### Global Reach with Content Delivery Networks
A Content Delivery Network (CDN) is a network of servers distributed geographically, working together to provide fast delivery of Internet content. By caching content closer to website visitors, CDNs reduce loading times, improve website speed and performance, and decrease bandwidth costs.
With Levamo, you get a [free WordPress CDN](/cloudflare-cdn/) called Levamo CDN, making it really easy to install a powerful CDN and take full advantage of it.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## Levamo Compared to Other WordPress Hosting Providers
Is Levamo truly the best-managed hosting solution for LMS websites, E-commerce, and media publications websites, or do these claims fall short? Let’s compare Levamo with other leading hosting providers.
### Levamo vs. WP Engine

Levamo is the best [WP Engine alternative](/wpengine-alternative/) for site owners who want fast, high-performance, managed hosting with Top-tier security and [24/7 managed WordPress hosting support](/support/) at a fair price.
Let's see how.
#### Server Technology: The Backbone of Performance
The server software you choose directly impacts website performance. While Apache struggles with dynamic WordPress environments, NGINX improves efficiency to offer improved concurrency.
LiteSpeed Web Servers extend this further with superior response times, handling more requests with optimal resource management. Modern servers further enhance speed, and performance depends on more than just clock speed; newer models can outperform older ones even at lower frequencies.
**WP Engine**
Utilizes Apache servers, which are traditional but less efficient for handling dynamic WordPress sites. Suitable for basic blogs or static pages that struggle under a heavy load.
**Levamo**
Employs LiteSpeed Web Servers, renowned for their swift response times and ability to handle high traffic efficiently up to ten times faster than Apache. This server software excels in environments that demand high concurrency, making it ideal for dynamic and resource-intensive WordPress sites.
#### Boosting Speed with Object Caching
As of WordPress 6.4, WordPress is now natively optimized for Redis. So this is our preferred option.
**WP Engine**
Offers object caching capabilities, but its performance may vary depending on the plan, and it may not include advanced features without additional costs.
**Levamo**
Integrates Redis for object caching, significantly enhancing database query responses and page load times. With WordPress 6.4’s native optimization for Redis, Levamo ensures superior caching efficiency, which is crucial for sites with heavy dynamic content.
Additionally, Levamo includes the Object Cache Pro plugin and Relay for free, which further optimize caching operations and ensure even faster performance for high-demand WordPress sites.
#### Enhancing PHP Efficiency with OPcache
**WP Engine**
Does not enable OPcache by default, which may affect the performance of dynamic sites.
**Levamo**
Levamo provides OPcache out of the box, storing precompiled script bytecode in memory to speed up PHP execution. This feature is essential for reducing load times and improving the performance of WordPress sites.
#### Global Reach with Content Delivery Networks
**WP Engine & Levamo**
Both providers offer free CDN services to distribute content close to the user’s location, reducing latency and speeding up content delivery across global locations.
#### Load Testing & Concurrency Handling
K6 Load testing simulates a number of users performing the same task on your website at the same time. This helps identify performance bottlenecks and the ability of the website to keep up during a traffic spike.
| **Category** | **Levamo** | **WP Engine** |
|---|---|---|
| Plan Name | Levamo Startup 1 | WP Engine Growth Plan |
| Pricing | $26 | $74 |
#### Results
Levamo performed notably better and proved to be the fastest WordPress hosting compared to WP Engine in this test, processing significantly more requests with fewer errors (except for Site F), indicating its strength in high-traffic scenarios and dynamic environments.
However, WP Engine is less than ideal for handling dynamic sites like ecommerce or elearning that usually see occasional high-traffic situations.
### Levamo vs. Kinsta

Levamo is the best [Kinsta alternative](/kinsta-alternative/) for site owners seeking a fast, high-performance, managed-to-host with top-tier security, reliable customer support, and a fair price.
Let's take a closer look.
#### Server Technology: The Backbone of Performance
The top contender, LiteSpeed Web Server, excels in server response times, handling more requests per second with superior resource management and faster data transfer, ensuring your site operates at peak efficiency.
**Kinsta**
Kinsta uses Nginx servers, which tend to be slower and are more suitable for blogs or brochure-type sites. This choice limits the performance capabilities for high-traffic or dynamic sites.
**Levamo**
Employs LiteSpeed Web Servers, renowned for their swift response times and ability to handle high traffic efficiently, up to ten times faster than Apache. This server software excels in environments that demand high concurrency, making it ideal for dynamic and resource-intensive WordPress sites.
#### Boosting Speed with Object Caching
As of WordPress 6.4, WordPress is now natively optimized for Redis. So this is our preferred option.
**Kinsta**
Kinsta offers Object Cache as a premium add-on, which means additional costs for users. This essential feature is not included by default.
**Levamo**
Integrates Redis for object caching, significantly enhancing database query responses and page load times. With WordPress 6.4’s native optimization for Redis, Levamo ensures superior caching efficiency, which is crucial for sites with heavy dynamic content.
Additionally, Levamo includes the Object Cache Pro plugin and Relay for free, which further optimize caching operations and ensure even faster performance for high-demand WordPress sites.
#### Enhancing PHP Efficiency with OPcache
Both provide OPcache out-of-the-box, which stores precompiled script bytecode in memory to speed up PHP execution. This feature is essential for reducing load times and improving the performance of WordPress sites.
#### Global Reach with Content Delivery Networks
Both providers offer free CDN services, which distribute content close to the user’s location, reducing latency and speeding up content delivery across global locations.
#### Load Testing & Concurrency Handling
K6 Load testing simulates a number of users performing the same task on your website at the same time. This helps identify performance bottlenecks and the ability of the website to keep up during a traffic spike.
| Category | Levamo | Kinsta |
|---|---|---|
| Plan Name | Levamo Startup 1 | Kinsta Business 1 |
| Pricing | $26 | $74 |
#### Results
In this test, Levamo performed notably better and again proved to be the fastest WordPress host compared to Kinsta across all load-testing parameters, normalizing over 14 times more requests with no errors except for Site F. This indicates that Levamo is better equipped to manage high-traffic peaks with greater stability and efficiency. Kinsta’s early error rate indicates that it is less than ideal for handling dynamic sites like eCommerce or eLearning that usually see occasional high-traffic situations.
### Levamo vs. Cloudways (AWS)

Levamo is the best [Cloudways alternative](/cloudways-alternative/) for site owners seeking a fast, high-performance, managed-to-host with top-tier security, reliable customer support, and a fair price.
Let's take a closer look.
#### Server Technology: The Backbone of Performance
**Cloudways**
Cloudways (AWS) uses Apache servers, which tend to be slower and are more suitable for blogs or brochure-type sites. This choice limits the performance capabilities for high-traffic or dynamic sites.
Levamo
Employs LiteSpeed Web Servers, renowned for their swift response times and ability to handle high traffic efficiently - up to ten times faster than Apache. This server software excels in environments that demand high concurrency, making it ideal for dynamic and resource-intensive WordPress sites.
#### Boosting Speed with Object Caching
As of WordPress 6.4, WordPress is now natively optimized for Redis. So this is our preferred option.
Both integrate Redis for object caching, significantly enhancing database query responses and page load times. With WordPress 6.4’s native optimization for Redis, Levamo & Cloudways ensures superior caching efficiency, which is crucial for sites with heavy dynamic content.
Additionally, Levamo includes the Object Cache Pro plugin and Relay for free, which further optimize caching operations and ensure even faster performance for high-demand WordPress sites.
#### Global Reach with Content Delivery Networks
Both providers offer free CDN services, which distribute content close to the user’s location, reducing latency and speeding up content delivery across global locations.
#### Load Testing & Concurrency Handling
K6 Load testing simulates a number of users performing the same task on your website at the same time. This helps identify performance bottlenecks and the ability of the website to keep up during a traffic spike.
| Category | Levamo | Cloudways (AWS) |
|---|---|---|
| Plan Name | Levamo Startup 1 | Cloudways AWS Medium |
| Pricing | $26 | $74 |
#### Result
In this test, Levamo performed better than Cloudways (AWS) across all load-testing parameters. Both hosts encountered no errors except for Site F errors on Levamo. Nonetheless, Levamo handled 31 times more normalized requests than Cloudways (AWS).
This suggests Cloudways (AWS) sites would usually not crash under increasing traffic load, even if they act a bit slower. Levamo sites, on the other hand, should be faster. Both hostings should be able to handle dynamic sites well.
So there we go. After all the testing and benchmarking, we can easily conclude that Levamo is the high traffic WordPress hosting out there, especially for dynamic WordPress websites that handle peak traffics all the time and still want to perform at the highest levels.
But before we conclude, let's take a quick look at who'd actually need the Fastest WordPress hosting, because not everyone needs to have the most robust hosting solution for their websites.
For example, if you have a blog or a portfolio website, you don't have to [migrate](/free-website-migrations/) to fast-managed and high traffic WordPress hosting solution like Levamo unless your online business grows quickly. So, who are the people who need the fastest hosting solution? Let's take a look.
## Who Needs Fast WordPress Hosting?

Businesses and websites that require high performance, smooth user experiences, and traffic surges need fast and reliable hosting. The following are the most critical types of websites that benefit from the fastest web hosting for WordPress:
**🛒 E-commerce Business Owners**: Ecommerce shops depend on fast web hosting. Quick page loads, smooth checkouts, and stable transactions build customer trust and drive sales.
**📚 Online Course Creators (LMS) & Membership Websites**: Platforms hosting online courses, training programs, and membership content require fast performance to handle video streaming, interactive learning, and real-time engagement.
**🎨 Design, Development & Marketing Agencies**: Agencies with multiple client websites need high-speed hosting to improve workflows & deliver projects on time. Sluggish or unreliable hosting can cause delays, frustrated clients, and extra work for developers.
**📰 Media Publications & Content-Rich Websites**: Online media outlets, blogs, and content-heavy websites reach large audiences daily, hence, speed and uptime are critical.
## Final Thoughts
Choosing the right WordPress hosting isn’t just about picking a name, it’s about performance, reliability, and value. Levamo stands out as the fastest managed hosting for WordPress, delivering LiteSpeed Web servers, KeyDB Object Caching, OPcache optimization, and a global CDN, along with horizontal autoscalability, all designed to maximize speed and scalability.
As you can see from the benchmarking tests, the results look impressive! Levamo outperforms WP Engine and Kinsta, handling traffic surges with faster load times and greater stability. Whether you run an eCommerce store, LMS, agency, or media site, Levamo is the ultimate WordPress hosting solution you need at a fair price.
We have conducted benchmarking with multiple providers, including Rocket.net, Pagely, and Pressable. The [benchmarking report](/benchmark-methodology/) provides more in-depth analysis and additional testing beyond this blog.
## Frequently Asked Questions
### Which is the fastest WordPress hosting?
According to our [hosting benchmarks](/benchmark-methodology/), Levamo is the fastest hosting for WordPress, constantly achieving better performance under pressure compared to other top WordPress hosting providers. It is the best hosting for website speed thanks to robust caching technology, built-in CDN services, and intelligent resource allocation. It also has the best balance between speed and affordability, offering competitive [pricing](/pricing/) for the features it offers, making it the best combination of speed and budget-friendliness.
### How does a fast WordPress hosting help with website performance?
Fast WordPress hosting isn’t just about quick load times (though we’ve got those too - under 200ms globally). With a good host, your site runs smoother, stays online with 99.99% uptime, and scales effortlessly when traffic spikes. Built-in security protects you from DDoS attacks and malware, with no extra plugins or add-ons needed.
Faster hosting means better SEO, lower bounce rates, and happier users.
### What is the advantage of opting for the fastest hosting for WordPress?
Choosing the fastest hosting for WordPress has many advantages:
- Fast hosting saves you money
- Visitors don't bounce and improve your average engagement time
- Faster web page speed improves SEO
- Your backend performance is a lot better and faster
- Mobile users also spend more time on your website
- Improves user trust and reliability
---
## WP Job Manager Review: The Ultimate Plugin for WordPress Job Boards?
- URL: https://levamo.com/blog/wp-job-manager-reviews/
- Category: online-business
- Author: Sunyyan Junaid
- Published: 2025-02-19
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is WP Job Manager the ultimate WP plugin for job boards? Find out here.
Recruiting the right talent is not an easy task. While companies shortlist and hire professionals in many ways, using your website as a talent hunter is the most convenient.
That’s where [WP Job Manager](https://wordpress.org/plugins/wp-job-manager/) comes in. It allows you to post a job and let candidates contact you without requiring any coding or technical assistance on your part. It is a simple and easy process to start finding the best candidates in no time.
In our detailed WP Job Manager review, we wanted to take a closer look at the plugin’s core functionalities and features, show you how to install it, and offer our two cents on the overall experience.
## What is WP Job Manager? An Overview
WP Job Manager
 is a **lightweight yet powerful** job listing plugin for WordPress. It allows website owners to **easily add, manage, and display job listings**. Originally developed by Mike Jolley (also the creator of WooCommerce), WP Job Manager is now maintained by Automattic. It’s a great solution for businesses, job boards, and niche websites offering job listings without a complex setup.
**Rating**: 4.4/5
**Active Installations**: 90,000+
**Pricing**: Free with options for Paid add-ons
## Core Features of WP Job Manager
So, what makes WP Job Manager one of the most popular options for creating job sites on WordPress? Well, it's the plethora of features that empowers the users. Here's a list of the things you can do with the WordPress plugin:
- Easy Job Submissions
- Customizable Job Listings
- Different Job Categories and Types
- Google Job Schema
- Job Listing Pages
- RSS Feeds
- Jobs Dashboard
Let’s explore these features one by one.
### Easy Job Submission
WP Job Manager offers both front-end and back-end job submission forms, making it easy for you to post jobs. The front-end submission process is particularly user-friendly, allowing you to create listings without access to the WordPress dashboard.
### Customizable Job Listings
Customizing job listing fields allows you to capture specific information relevant to your industry. This includes fields for job title, description, location, company, application URL, and more.
### Job Categories and Types
You can organize job listings using categories and types, making it easy for job seekers to filter and find relevant opportunities based on the parameters they set. This is particularly useful if you are running a global firm with offices in multiple physical locations.
### Google Job Schema
Over the last few years, Google has been displaying jobs in search results, which means that searches can now feature a job description and list it accordingly. WP Job Manager comes with a Google Job Schema, making it easy for Google to read job posts and include them in searches.
### Job Listing pages
Every job gets its unique listing page, making it indexable and SEO-friendly. Recruiters can then share these links with prospective candidates through social media applications or email and have interested applicants apply.
### RSS Feeds
You can have your blog readers subscribe to your job board and get notified with new job alerts, making it super simple to apply. Every time a new job is posted, it gets automatically delivered to their RSS feeds.
### Jobs Dashboard
Without access to the site admin, you can easily add a page on your website to manage the job applications. This removes the hassle of logging in to the WP dashboard and making changes from the backend.
**Quick note:** WP Job Manager is extensible through add-ons.
Rest assured, the free version does most of the job for you, but if you need more, you get it through paid extensions. These can greatly extend the plugin’s functionality to include resume submissions, application tracking, and more.
Now, before we go on to see how to install WP Job Manager on WordPress, let's take a quick look at the plugin vs. other available options.
## WP Job Manager vs. Other Job Board Plugins
| Feature | WP Job Manager | Simple Job Board | WP Job Openings |
|---|---|---|---|
| **Free Version Available** | ✅ Yes | ✅ Yes | ✅ Yes |
| **Frontend Job Submission** | ✅ Yes | ❌ No | ✅ Yes |
| **Paid Listings Option** | ✅ Yes (via add-on) | ✅ Yes | ✅ Yes (Pro) |
| **Job Alerts & Notifications** | ✅ Yes (via add-on) | ❌ No | ✅ Yes (Pro) |
| **Resume Submissions** | ✅ Yes (via add-on) | ✅ Yes | ✅ Yes (Pro) |
| **Customization & Themes** | ✅ Works with any theme | ⚠️ Limited | ✅ Works with any theme |
## Step-by-Step Installation Guide
Installing the WP Job Manager plugin is simple. Just follow these steps, and you’ll be all set to post jobs left and right.
- Go to your WordPress admin dashboard and head over to **Plugins** > **Add New Plugin**. Search for WP Job Manager in the upper right corner, then click **Install**.

- After the installation is done, click **Activate.**

- Once activated, you will see a notification. There are two ways to create job listings: setup wizard and manual.
If you click **Run Setup Wizard**, the plugin will create all the necessary pages so that it can work without any issues. You can choose the **Skip Setup** option, but then you’ll need to manually create all the pages. We recommend running the setup wizard and letting it do the job for you.

- Next, click **Start setup**.

- In this step, you can specify titles for the three essential pages the plugin will create, alongside the shortcodes shown on the right for each one. Click **Create selected pages.**

- And that’s it! The necessary pages have been created, and you can start using the plugin.

- There is one more thing you need to do before posting a new job - ensure they are correctly set in the plugin.
Go to **Job Manager > Job Listings > Settings > Pages**. From here, you can manually verify the pages that will show for each of the four titles. You can change the page name or title, but always verify that you have specified the correct page for each functionality.

### How to Post a Job?
Now that you have installed and set up WPJM, it’s time to start posting jobs.
There are two ways of doing this.
One is through the backend WP admin, and the other is via the frontend. Both are undemanding processes, but we recommend using the latter method.
To post a new job through the front end, you’ll first need to be logged in to your WP admin dashboard.
Head over to your **Post a Job** page. Here, you will see multiple options to add a new job listing:
- **Job Title:** Specify a job title.
- **Location (optional):** Specify a location if required.
- **Remote position (optional**): Check this box if remote work is included.
- **Job Type:** Select from the drop-down menu the job type, such as **Freelance, Full Time, Internship, Temporary**, or **Part Time.**
- **Description:** Provide details on what the position entails.
- **Application email/URL:** Specify the email address or the URL where you want the candidates to reach you.
- **Company name:** Enter the name of your company.
- **Website (optional):** Specify the company website
- **Tagline (optional):** Provide a tagline if you have one.
- **Video (optional):** A video works great to explain more about your company.
- **Twitter username (optional):** Specify the company’s X handle.
- **Logo (optional):** If you have a logo, this is a great opportunity to use it!

- Click on **Preview** to see what the job post looks like on your website. If everything is alright, click on **Submit Listing**. If not, you can click on **Edit Listing** to make further changes.

- You now need to go back to the WordPress admin dashboard and manually approve the job listing to be visible.

- Once approved, here is what the actual job listing will look like on the website:

## Pricing Structure
WP Job Manager is a free plugin, but there are paid add-ons that you can use to extend its functionalities. As of February 2025, these are the pricing plans:
- **Free**: Great for starting out and posting multiple jobs.
**Single Site License ($159/year)**: Get all of the following paid add-ons inclusive with a single-site license:
- Resume Manager ($49/year) - A widget built on top of WP Job Manager that adds a resume submission form to your site and resume listings, all manageable from your admin dashboard.
- Job Alerts ($49/year) - Allow registered users to save their job searches and create alerts that send new jobs via email daily, weekly, fortnightly, or monthly.
- Job Tags ($29/year) - Improve job listings by adding Job Tags, which can include skills, interests, technologies, and more. Display job listings based on their corresponding tags and use them to search for relevant job opportunities.
- Simple Paid Listings ($29/year) - Add paid listing functionality. Set a price per listing and take payment via Stripe or PayPal before the listing is published.
- WC Paid Listings ($49/year) - Powered by WooCommerce, you can create custom job packages that can be purchased or redeemed during job submission. Requires the WooCommerce plugin.
- Application Deadline ($29/year) - Enables job listers to specify a closing date for applications by adding a new field on the job submission form.
- Bookmarks ($29/year) - Allow logged-in candidates to bookmark jobs and resumes along with an added note.
- Applications ($79/year) - Allows candidates to apply to jobs using a form, while you can view and manage the applications from the job dashboard.
- Embeddable Job Widget ($29/year) - Shows job listings from your site by generating an embeddable widget.
- **Developer ($329/year)**: Run WP Job Manager with paid add-ons on unlimited websites.
All purchases come with a 14-day money-back guarantee.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## Verdict: Manage Your Listing with Ease
In our WP Job Managed reviews from multiple fronts (from features to usability and pricing), we went in-depth into this popular plugin. To summarize, WP Job Manager offers a user-friendly and powerful solution for creating and managing job boards directly within your WordPress website at no cost (except for your time and effort, of course). Its core functionality, combined with a range of helpful add-ons that provide more value, makes it a **versatile option** for small to medium businesses.
However, the performance of any WordPress website handling a significant number of job listings and visitor traffic hinges on its hosting environment. You want a provider that takes the hassle out of website management, allowing you to focus on what matters the most: connecting talent with opportunity.
At Levamo, we’ve dedicated our work to handling such dynamic and feature-rich WordPress websites since our [managed WordPress cloud hosting](/) is specifically engineered to optimize performance and ensure your job board runs smoothly and efficiently.
We make sure that your reputation doesn’t take a hit even in extreme scenarios (e.g., if a thousand candidates apply to your posting), as dealing with high traffic is our forte. So, you can rest assured that your site will always be up and running for potential employees - and clients, too.
## Frequently Asked Questions

### What is WP Job Manager?
WP Job Manager is a free WordPress plugin that allows you to easily create and manage a job board website on WordPress. It simplifies the process of posting, categorizing, and displaying job listings, making it a popular choice for companies looking to hire the right talent.
### Is WP Job Manager free to use?
Yes, the core WP Job Manager plugin is free to use. However, there are paid add-ons available that extend its functionality with features like applications, resumes, and more.
### Can WordPress WP Job Manager handle multiple job listings efficiently?
Yes, WP Job Manager can handle multiple job listings. That's what it's made for!
### What are the best add-ons for WP Job Manager?
Some popular and highly recommended add-ons for WP Job Manager include:
- **Applications:** Enables job seekers to apply for jobs directly through your website.
- **Resumes:** Allows candidates to upload their resumes.
- **WooCommerce Paid Listings:** This lets you charge for job postings if someone wants to advertise jobs on your site.
- **Simple Listings:** This plugin simplifies the listing process for basic job boards.
Each add-on comes with a specific price tag, so if you want to get the most out of this plugin, we recommend buying its single-site license that covers all paid add-ons.
### How does hosting affect the WordPress WP Job Manager’s performance?
Hosting plays a critical role in WP Job Manager's performance. A hosting plan with sufficient resources (CPU, RAM, storage) is essential, especially as the number of job listings and website traffic increases. Levamo’s managed WP hosting is highly suited for a job board website.
### Is WP Job Manager suitable for enterprise-level job boards?
While WP Job Manager is a great starting point, it may not be the best solution for large, enterprise-level job boards with complex requirements. For such scenarios, dedicated job board platforms or highly customized solutions built on Javascript or closed-source frameworks might be more appropriate.
WP Job Manager can be scaled with add-ons and customizations, but at a certain point, a more specialized platform will likely be necessary.
---
## Sensei LMS Review: The Best WordPress Plugin for Selling Courses?
- URL: https://levamo.com/blog/sensei-lms-review/
- Category: lms
- Author: Sunyyan Junaid
- Published: 2025-02-18
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is Sensei LMS the best WP plugin for selling courses? Find out in our review.
By WordPress, for WordPress. This sentence perfectly sums up the definition of [Sensei LMS](https://senseilms.com/), a learning management plugin developed by Automattic (the team behind WP).
With e-learning booming and making it ever more profitable to build an online course business, Sensei LMS represents an option worth considering thanks to its many capabilities, and so we decided to take it for a spin in this Sensei LMS review to find out if it's one of the best WordPress plugins for selling courses online, or does it get beat by the likes of TutorLMS or LearnDash, etc.
In the next 10 minutes or so, we’ll explore what the plugin has to offer, its strengths and weaknesses, and see how it can help you unlock your potential as an educator.
Let’s dive in.
## Key Features
The core offering of Sensei LMS revolves around the following:
### Course Creation and Management
Build structured courses with modules, lessons, and quizzes. Adding multimedia content like videos, images, and documents is not only seamless but allows your students to get the most out of your courses.
### Quiz and Assessment Tools
Create engaging quizzes to assess student understanding. Sensei LMS supports various question types and options for grading and feedback. These include multiple-choice and fill-in-the-blank questions, matching types, and more.
### Content Dripping and Conditional Release
Control the pace of your course by releasing content gradually. The conditional release allows you to unlock content based on student progress, adding flexibility to the process and ensuring that your students complete one lesson/module at a time.
### WooCommerce Integration
Seamlessly integrate with WooCommerce to monetize your courses. Set pricing, offer discounts, and manage transactions with ease. All popular LMS plugins integrate with WooCommerce to enable course monetization, and Sensei LMS is no different.
## Pros & Cons of Sensei LMS
Not every LMS plugin will fit your needs, which is why it’s paramount to first study the pros and cons of a specific solution - that’s the only way to know you’ll be getting one that aligns with your strategic goals.
Here’s what Sensei LMS does well and some of its drawbacks:
| **Pros** | **Cons** |
|---|---|
| Easy to install and use for existing WordPress users | Limited features in the free version |
| Intuitive course builder with drag-and-drop functionality | Need to purchase the Pro version to sell courses and access advanced quizzes |
| Solid quiz and assessment tools | Design customization can be challenging for first-time users |
| Excellent WooCommerce integration for monetization | Doesn’t have assignment options |
| Backed by Automattic | Not a very user-friendly interface |
| Affordable monthly plans to get started | Developers are slow in adding new features |
| | Some advanced functionalities demand a developer for proper integration |
## Comparison with Other LMS Plugins
Thanks to its intuitive nature, Sensei LMS is a strong contender for an online learning platform, but it's worth considering alternatives like [LearnDash](https://www.learndash.com/) and [TutorLMS](https://tutorlms.com/).
Sensei's strength lies in its simplicity and an affordable monthly payment plan of just $15, which is rather wallet-friendly for those just getting started.
That said, Sensei LMS is not very easy to learn right out of the box. You will need some time to figure out where the course options are located because the plugin comes with a bit of a learning curve.
What’s more, you can’t sell using the free plan, so you’ll have to upgrade to the Pro option to integrate WooCommerce and enable monetization.
In case you want an LMS with better customization and advanced features, LearnDash LMS and Tutor LMS are great alternatives. Both come at $199 per year for a single-site license and have far more installations than Sensei LMS.
Tutor LMS has over 100,000 active WP installations and also comes with a free version.

On the other hand, LearnDash doesn’t provide a free version and is only available for download once you buy it from the official website. Builtwith.com puts the estimate at around 67,000+ active installations, which is still a pretty impressive number:

## Step-by-Step Guide to Installing and Setting Up Sensei LMS
This step-by-step guide allows you to easily install and set up Sensei LMS to start creating quality courses.
- Open your WordPress dashboard admin and navigate to **Plugins > Add New Plugin.**
- Search for Sensei LMS, then install and activate the plugin.

- Once you activate it, you will be greeted with a new welcome screen. You can either **Skip onboarding** or click **Get Started** to, well, get started.We strongly recommend not skipping this section as Sensei LMS does a good job guiding you through the entire course creation and setup process.

- Next, choose the purpose of your website and check one that suits your requirements. Click **Continue** to proceed.

- In this step, you will be prompted to explore the theme options, with the options being using your current theme or the Course theme that comes for free. This choice entirely depends upon you. Since we don’t have a theme installed at the moment, we will go with **Get the Course Theme**.

### Create your First Course
Once you have completed the installation of the plugin and the theme, you will now be taken to the plugin’s settings. This is where you get to work on your first course:
- Click **Create your first course.**

- In a new window, enter the **Course Title** and **Course Description**, then click **Continue.**

- Since we are using the free version, there is a prompt to buy the paid version at $179. We’re only learning the course creation process for now, so click **Continue with Sensei Free**.

- In this step, you can either proceed with a layout from the pre-made collection or click **Start with default layout.** We are going with the **Course Default** option.

- Here you can start creating your course by adding descriptions, lessons, and other multimedia content. To use the **Generate with AI** feature, you need to purchase the Sensei LMS Pro plan. For now, let’s click **Start with blank.**

- To edit a lesson, click **Edit lesson.**

- Add a title for your lesson and click **Continue**.

- To add a quiz, click the **+** icon, then search for **Quiz** and add the block.

Click the question type and from the list of drop-down menu, select any one of the following:
- Multiple Choice
- True/False
- Gap Fill
- Single Line
- Multi Line
- File Upload

- For example, if you pick the True/False type, you can specify the correct and incorrect options on the right side.

In a similar manner, you can also insert multimedia content and enrich the course with more information.
Also Read: [BuddyPress Review](/blog/buddypress-review/)
## Levamo Hosting and Sensei LMS - A Match Made in Heaven
Your hosting environment is crucial for [LMS performance](/blog/lms-performance-optimization/). As the number of enrolled students increases, so does the toll on your hosting server. This is where Levamo differs from other hosting providers.
With us, you get benefits ideally suitable for LMS users:
- **High-Performance Infrastructure:** Our optimized servers deliver your course content quickly, ensuring a smooth learning experience. Whether you have two or 1000 students viewing multimedia content, your site will always be up with no glitches.
- **Scalability:** More students mean more income but also an additional burden on the server. With integrated CDN and SSD-powered servers, computing resources scale as you grow.
- **Robust Security:** Thanks to advanced security measures, our team of experts works around the clock to keep your site safe from malware, SQL injection, and other cybersecurity attacks. You also get automated backups at regular intervals to ensure seamless interruption.
If you're looking to build a successful online course business, Sensei LMS and Levamo are as good of a foundation as you’ll find.
## Why Go For Sensei?
Sensei LMS is a cost-effective solution for creating and selling online courses with WordPress. While it may require extensions for advanced features, its core functionalities and WooCommerce integration make it a great choice for many course creators.
It’s also affordable and built by the highly credible Automattic, the creators of WordPress. Hence, you won’t go wrong with this choice.
By pairing Sensei LMS with the speed, security, and scalability of Levamo [LMS hosting](/managed-lms-hosting/), you can create a powerful online learning platform that will be ready to handle anything you throw at it.
## Frequently Asked Questions

### What is Sensei LMS, and how does it integrate with WordPress?
Sensei LMS is a WordPress plugin that transforms your website into a fully functional learning management system (LMS) by allowing you to build, manage, and sell online courses from your WordPress site. It is developed by Automattic, the creator of WordPress.
### Is Sensei LMS suitable for non-developers?
Yes, but do note that you need more time to learn Sensei LMS as it has somewhat of a learning curve. With that being said, it is good enough for those without coding experience as you can create courses, lessons, and quizzes using a drag-and-drop interface and visual editors. There is a front-end and back-end course creator that any novice can use with minimum coding to create and launch engaging courses.
### Can I sell courses directly using Sensei LMS?
Yes. Sensei LMS integrates with WooCommerce, a popular e-commerce plugin for WordPress. This integration allows you to easily sell your courses, manage payments, and track sales. You can set pricing, offer discounts, and create various purchase options for your students.
### How does Sensei LMS compare to other WordPress LMS plugins?
In our review, Sensei LMS performs almost flawlessly when compared to Tutor LMS and LearnDash, two of the most popular LMS plugins at the moment. However, Sensei LMS may have a slightly steeper learning curve for certain advanced features, though its simplicity for core LMS tasks makes it a competitive option. Tutor LMS and LearnDash LMS offer a $199 per year single-site license, whereas Sensei provides it for $179 or $15 per month.
### What hosting requirements are recommended for running Sensei LMS efficiently?
Running an LMS with numerous courses and students requires scalable hosting that grows with your business. For Sensei LMS, we recommend a hosting environment optimized for WordPress, like Levamo's managed WordPress hosting. Every plan comes with an integrated CDN, SSD storage, and enough system resources to ensure your website is always reliable when it’s needed by your students.
### Are there any additional costs associated with using Sensei LMS?
The core Sensei LMS plugin is free. Nonetheless, like many plugins, there are premium extensions and add-ons available that can enhance its functionality. You can only sell courses via the Sensei LMS Pro plan, which costs $15 per month or $179 per year, whichever works best for you.
---
## Improved WAF Controls: Temporary Whitelisting for Admin Access
- URL: https://levamo.com/blog/improved-waf-controls-temporary-whitelisting-for-admin-access/
- Category: news
- Author: The Levamo Team
- Published: 2025-02-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
New WAF setting lets you temporarily whitelist your browser for WP Admin access.
## What's New
A new Web Application Firewall (WAF) setting has been added to facilitate access to protected site areas, such as WordPress admin panels, when both CDN and WAF are enabled. This addresses common access issues customers experienced after enabling the WAF.
## How It Works
- **Available When CDN is Enabled**: This setting only appears if your site has both the CDN and WAF enabled. If the CDN is disabled, this option will not be available.
- **Whitelist Browser for WP Admin Access**: A new option under Security allows you to temporarily whitelist your browser, bypassing the WAF for your current session. This ensures you can access WP Admin and other restricted areas without firewall interference.
- **Session-Based Whitelisting**: The whitelist applies only to your current browser session. The WAF will be re-enabled once you close and reopen your browser.
- **Clearer Messaging**: If your site does not have the CDN enabled, the dashboard will now indicate that this setting requires both the CDN and WAF to function. Additional improvements are planned to make this even clearer.
We continue refining CDN settings to improve security controls and address customer concerns.
---
## How to Install MySQL Community Server for Local Development
- URL: https://levamo.com/blog/mysql-community-server/
- Category: database
- Author: Salman
- Published: 2025-02-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Set up MySQL for local dev! Our guide covers install, security, and optimization.
Setting up a robust local database environment can be the key to testing new features, learning database management, or simply experimenting without touching live production systems.
In this guide, we will discuss how to install MySQL Community Server on Windows, macOS, and Linux. Once you’re up and running, we’ll touch on how to secure your new setup and keep it [optimized](/blog/mysql-performance-tuning/) for ongoing development.
### What Is MySQL Community Server?
MySQL Community Server is basically the free, open-source version of MySQL, a relational database management system that underpins countless websites, applications, and services. It's packed with all the tools dev need to build, test, and fine-tune their projects.
## Before You Begin
- **Check System Requirements**: Ensure your machine meets any minimum specifications your operating system or MySQL documentation recommends.
- **Look for Existing Database Services**: If you already have a database installed, double-check that there are no port conflicts or overlapping services.
- **Back Up Any Previous MySQL Data**: If you’ve used MySQL in the past, export your databases or store important files to avoid overwriting them.
## How to Install MySQL Community Server by Operating System
### How to Install MySQL on Windows
**Download the Installer**
- Head to the official MySQL site and find the **MySQL Community Server** installer for Windows.
**Launch the Installer**
- Choose “MySQL Server” and proceed through the setup wizard.
- When prompted, set a strong root password.
**Complete Configuration**
- Follow the on-screen steps to configure default settings.
- Once finished, confirm the service is running by checking the MySQL icon in your system tray or using services.msc.
### How to Install MySQL on Mac
**Get the DMG Archive**
- Download the MySQL package for macOS from MySQL’s official site.
**Install & Configure**
- Double-click the DMG and run the installer.
- Set a secure root password when prompted.
**Verify Startup**
- MySQL often starts automatically. You can verify by opening System Preferences > MySQL and checking its status.
### How to Install MySQL on Linux
- **Use Your Package Manager**
On Ubuntu/Debian-based systems, run
sudo apt-get update
sudo apt-get install mysql-server
**Secure the Setup**
- During installation, you’ll set a root password.
Complete additional security steps by running:
`sudo mysql_secure_installation`
- **Start the Service**
Confirm MySQL is active with:
`sudo systemctl start mysql`
## Basic Configuration After Installation
**Secure the Installation**
- Use mysql_secure_installation (Linux) or the equivalent method (Windows/macOS) to remove test databases and enforce strong passwords.
**Test Connectivity**
- Log in via the command line (mysql -u root -p) or through a GUI like MySQL Workbench.
- **Create Databases**
If you’re new to SQL, try creating a simple test database:
`CREATE DATABASE test_db;`
## Keeping Your Setup Secure & Efficient
- **Update Regularly**: Apply new patches to address bugs and security vulnerabilities.
- **Use Strong Credentials**: Choose complex passwords and avoid using the root for day-to-day operations.
- **Firewall Rules**: Limit remote access or bind MySQL to localhost if you only need local development.
- **Regular Backups**: Even for development environments, it’s wise to back up your data before major changes.
## Conclusion
By installing **MySQL Community Server** on your local machine, you’re granting yourself a safe sandbox for learning, experimenting, and building. Whether you’re developing a small-scale application or honing your database skills, having a locally hosted environment speeds up iteration and reduces the risk of harming any live production setup. With just a bit of configuration and attention to security best practices, you’ll be set to start exploring all that MySQL has to offer.
## Frequently Asked Questions
### How to install MySQL?
Choose the installer based on your OS (Windows, macOS, or Linux), follow the guided setup, set a root password, and run security configuration steps to finalize the installation.
### How to install MySQL on Mac?
Download the MySQL DMG package from the official site, run the installer, set a secure root password, and verify it's running via System Preferences > MySQL.
### How to install MySQL on Ubuntu?
If you want to know how to install MySQL in Ubuntu, then first use the following commands:
sudo apt-get update
sudo apt-get install mysql-server
Then secure it with:
`sudo mysql_secure_installation `
### How to install MySQL in Windows?
Download the installer from the MySQL website, choose "MySQL Server" during setup, set a root password, complete the configuration, and confirm it’s running via the system tray or `services.msc`.
---
## How to Manage the Maximum PHP Memory Limit (and Other Key Settings) in WordPress
- URL: https://levamo.com/blog/maximum-php-memory-limit/
- Category: hosting
- Author: Salman
- Published: 2025-02-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix WordPress memory issues! Tweak PHP settings for a faster site.
Keeping your WordPress site running smoothly often comes down to how well you manage your server resources - especially **server memory limit. If you’ve encountered [“white screen of death”](/blog/wordpress-white-screen-of-death/) or a “Fatal error: Allowed memory size exhausted,” that’s your cue to check your memory and max execution settings**. In this guide, we’re discussing what the memory limit for PHP Server is, why it’s an important factor, and how you can tweak your PHP configurations without any headaches.
## What Exactly Is the Maximum PHP Memory Limit?
Your WordPress site is powered by PHP scripts that handle everything from loading themes to running plugins. The **maximum PHP memory limit** sets the upper boundary for how much memory these PHP processes can use before the server says, “Enough!” If your site demands more memory than the limit allows, you’ll likely see errors or a sluggish experience for visitors.
It’s kind of like setting a maximum water level in a tank - if your WordPress “tank” runs dry, tasks stall out and you’ll notice slow page loads or outright crashes.
## Why the Maximum PHP Memory Limit Matters
- **Prevents Crashes**
**When your site’s processes exceed the **memory limit**, they can’t complete their tasks - leading to error messages or blank pages**.
- **Ensures Stability**
**A well-allocated memory limit helps WordPress carry out operations (like loading heavy plugins, media-rich pages, or complex queries) without draining server resources**.
- **Improves Performance**
**The right balance keeps your site speedy**. Too low a setting can choke your site, while going too high might deprive other processes on the server.
## Increasing the Maximum PHP Memory Limit in WordPress
Before you start editing files, it’s wise to back up your site. If anything goes wrong, you’ll have a safety net to restore your previous configuration.
### 1. Edit **wp-config.php**
**Locate Your WordPress Files**
- Use your hosting control panel or FTP to open your WordPress installation directory (often named public_html).
**Open** wp-config.php
- Look for a file called wp-config.php in the root folder. Right-click (or equivalent) to edit it.
**Set Your Memory Limit**
- Find the comment that says `/* That's all, stop editing! Happy publishing. */`.
Just above that line, insert:
`define( 'WP_MEMORY_LIMIT', '256M' );`
- This line tells WordPress the **maximum PHP memory limit** is 256 MB. Adjust as you see fit - for instance, 128M or 512M.
**Save and Upload**
- Once saved, your site should start using the new memory limit instantly.
## Adjusting the Max Execution Time
While you’re revisiting your PHP settings, you might as well look at your max execution time, another factor that influences your site’s stability and speed. If a script runs too long, it could stall out or hog server resources.
**Find .htaccess**
- In your WordPress root directory, locate the hidden file named .htaccess. You may need to enable “Show Hidden Files” in your file manager.
- **Edit the File**
Add a line at the bottom, such as:
`php_value max_execution_time 60`
- This grants a 60-second window for PHP scripts to run. Adjust the number for your needs (but be mindful not to set it too high).
**Save and Test**
- After saving, load your site to ensure everything is still functional.
## Common Pitfalls to Avoid
- **Over-Allocating Memory**: While setting a high **memory limit for PHP server** might seem like a quick fix, it can deprive other processes on your server if your hosting environment is limited. Strike a balance.
- **Forgetting to Back Up**: Editing WordPress core files or config files without a backup is risky. Always keep a recent backup handy.
- **Plugin Conflicts**: Sometimes the real culprit isn’t your memory limit, but a poorly coded plugin. If you keep running out of memory, audit your plugins to find any resource hogs.
## Final Thoughts
Managing your **memory limit** and other PHP settings (like max execution time) is an essential step in optimizing your WordPress site. By allocating enough memory and capping how long scripts can run, you’ll avoid errors, improve performance, and create a smoother experience for visitors.
Keep in mind that every WordPress site is unique - what works for one might be overkill for another. Regularly check your server resource usage, monitor site health, and adjust the **memory limit** as your content or traffic evolves. With a well-tuned environment, you’ll keep your WordPress site humming along without those pesky crashes or slowdowns.
---
## Maximizing Course Completion Rates: 8 Proven Strategies
- URL: https://levamo.com/blog/maximize-course-completion-rates/
- Category: lms
- Author: Faisal Sarker
- Published: 2025-02-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Boost course completion! Use 8 strategies to engage learners and grow revenue.
According to Global Market Insights, the online learning industry has experienced remarkable growth, expanding by **900% since 2000. With projections showing user numbers reaching 958.4 million by 2028, the potential for online education is immense. However, a significant challenge remains: course completion rates typically hover between 12% and 15%**.
For owners of Learning Management System (LMS) platforms like [LifterLMS](/blog/lifterlms-review/), TutorLMS, or any other LMS, these statistics present both a challenge and an opportunity. When students don't complete courses, they miss out on valuable education, and course creators lose potential revenue and reputation.
## Understanding Course Abandonment
The journey from course enrollment to completion often gets derailed, but understanding why it happens is the first step toward addressing them effectively.
Picture a typical online learner, Sarah, who enrolls in a web development course with enthusiasm. Initially excited about learning to code, she begins to struggle when the course jumps from basic HTML to complex JavaScript without adequate bridging content. The lack of clear progression leads to frustration, and eventually, she stops logging in altogether.
But let’s take a look at the most common factors that lead to course abandonments:
- **Mismatched Difficulty**: Courses that are either too basic or too challenging fail to maintain student engagement
- **Content Delivery**: Monotonous presentation methods and lack of varied learning materials
- **Knowledge Gaps**: Insufficient prerequisite knowledge leading to frustration
- **Time Management**: The absence of structured schedules makes procrastination easier
- **Technical Issues**: Poor platform usability or performance problems
- **Practical Application**: Lack of clear real-world implementation examples
- **Commitment Level**: Courses requiring unexpected time investments
- **Course Hoarding**: Students collecting multiple courses without committed focus
- **Misleading Marketing**: Course content not aligning with promotional material
Now that you understand the key challenges, let’s explore proven strategies to boost course completion rates on your LMS.
## Strategy 1: Crafting Clear and Actionable Learning Objectives
The foundation of any successful course lies in its learning objectives. Rather than presenting these as dry bullet points, frame them as achievable milestones in your students' journey.
Consider this example structure:
**“Module 1: WordPress Plugin Development Fundamentals**
*By the end of this module, you'll be able to:*
- Create a basic plugin structure that follows WordPress coding standards
- Implement secure user authentication methods
- Deploy your first plugin to a live WordPress site
**Real-world application:** You'll build a working contact form plugin that you can use in your portfolio.
This approach shows students not just what they'll learn, but how it connects to their goals as well.
## Strategy 2: Designing an Intuitive Course Structure
Think of your course structure as a roadmap guiding students to their destination. In LifterLMS, you get a drag-and-drop curriculum builder that makes it easy to create a logical progression through your content. For example:
- Opening Hook (2-3 minutes) Connect the topic to real-world applications
- Core Content (10-15 minutes) Present key concepts with examples
- Practice Activity (5-10 minutes) Apply the learning immediately
- Quick Win (2-3 minutes) End with an achievable task that builds confidence

Credits: [LifterLMS - Using Course Builder](https://lifterlms.com/docs/using-course-builder/)
## Strategy 3: Leverage Multimedia Content
Transform your content from flat text into an engaging multimedia experience.
This can be done easily with the help of [Word to PPT AI](https://plusai.com/free-tools/word-to-ppt), which converts text-based content into visually appealing presentations.
Here's how different content types serve different learning needs:
**Video Lessons:** Perfect for demonstrations and visual concepts
Best Practices for videos:
- Keep videos under 10 minutes
- Include captions for accessibility
- Provide downloadable transcripts
- Use [AI dubbing](https://www.veed.io/tools/voice-dubber/ai-dubbing) for better audio quality
**Interactive Elements:** Engage students through active participation:
- Clickable diagrams
- Drag-and-drop exercises
- Interactive code editors
## Strategy 4: Engaging Assessments and Quizzes
Transform traditional quizzes into engaging checkpoints in your student's learning journey. Think of assessments not as tests, but as opportunities for reinforcement and celebration.
For example, you can follow the “Achievement Pathway”:
**Level 1: Foundation Builder:** Complete basic concept checks > Earn the "Getting Started" badge > Unlock practical exercises
**Level 2: Skill Developer:** Apply concepts in real scenarios > Earn the "Practitioner" badge > Access advanced content
**Level 3: Master Craftsman:** Create original solutions > Earn the "Expert" badge > Join mentor program
Remember: Each assessment should serve as a stepping stone, not a barrier. Include immediate feedback that guides students toward improvement.
**Strategy 5: Personalizing the Learning Experience**
Imagine your course as a responsive mentor that adapts to each student's needs. Everyone already wants more personalized experiences that cater to their particular problems, and using LifterLMS's conditional logic makes this possible through sophisticated learning paths.
**For example:** If a student scores above 90% on the basic assessment, they can skip the introductory material and move directly to more advanced challenges, ensuring they stay engaged and appropriately challenged.
For those scoring between 70% and 89%, the standard learning path is recommended, with optional support resources available to reinforce key concepts. However, if a student scores below 70%, it is beneficial to guide them through prerequisite modules and provide additional examples to strengthen their foundational understanding before progressing further.
This systematic approach ensures every student receives the right level of challenge and support.
**Strategy 6: Optimization for Mobile Learning**
In today's on-the-go world, mobile optimization isn't optional - it's essential.
"Mobile users complete courses 27% faster when content is properly optimized for their devices." - eLearning Industry Report, 2023
Here's how to create a seamless mobile experience:
**The Mobile-First Checklist:**
- Content Adaptation Text that's readable without zooming > Videos that play smoothly on mobile networks > Touch-friendly navigation elements
- Performance Optimization Fast-loading pages > Efficient image compression > Minimal bandwidth usage
- User Experience Simple, intuitive interfaces > Easy progress tracking > Quick access to key features
**Strategy 7: Collecting and Acting on Feedback**
Your student’s feedback is critical in helping you improve and get better with time. Create a continuous dialogue with your students through strategic feedback collection and implementation.
The Feedback Loop
*Collect*
- Short, focused surveys at key milestones
- Regular progress check-ins
- Optional detailed reviews
*Analyze*
- Identify common patterns
- Track completion rates
- Monitor engagement metrics
**Strategy 8: Continuous Improvement**
Think of your course as a living document that grows and evolves with your student's needs. So how to ensure that you’re continuously improving your courses?
**Monthly Tasks:** Review completion rates and update any outdated content. Additionally, keep adding new industry developments so the courses are always up to date with times.
**Quarterly Tasks:** Analyze student feedback and update assessment questions. Keep further enhancing multimedia content to keep engagement high.
**Annual Tasks:** Keep performing major content revisions and most importantly, keep your platform updated so it performs optimally at all times.
## Technical Considerations
Your course content is only as good as the technical infrastructure supporting it. "Technical issues account for 28% of course abandonment rates. A reliable technical foundation is crucial for success." - LMS Research Group
Here's what you need to ensure:
**Essential Technical Elements**
**Performance**
- [Page load times under 3 seconds](/performance/)
- Smooth video playback
- Reliable assessment submission
**Security**
- Regular backups
- [Secure student data](/managed-security/)
- Protected course content
**Support**
- [Quick technical help](/support/)
- Clear documentation
- Regular maintenance
## Conclusion
Using the above strategies can help you improve your course completion rates. Remember: clear objectives, intuitive design, engaging content, and continuous improvement are the pillars of a successful course that students and learners tend to finish.
## Frequently Asked Questions

### What features in LifterLMS can help improve course completion?
The following features can help improve your LifterLMS course completion rate:
**Membership Integration:** Offer exclusive content for increased user commitment.
**Gamification:** Use certificates, badges, and leaderboards to motivate learners.
**Drag-and-drop Course Builder:** Create an engaging and intuitive course structure.
**Quizzes and Assessments:** Reinforce learning while maintaining engagement.
**Conditional logic:** Personalize learning path for users based on progress or quiz results.
### How can gamification boost learner engagement?
Gamification helps to make the learning process interactive, fun, and rewarding. Some gamification features include certificates, badges, and leaderboards to help track progress and create a sense of achievement.
### What hosting features should I look for when running an LMS?
When running an LMS, look for the following hosting features:
[LMS Optimization](/blog/lms-performance-optimization/)
Faster load times
Scalability
Reliability
Security
Smooth video playback
Backup solutions
### How can I track and analyze course completion rates?
You can use LifterLMS’ inbuilt analytics to track course completion rate or:
Monitor engagement metrics by analyzing the time spent on lessons and interaction with course content
Track quiz performances
Survey learners to understand why they complete or quit halfway
### What are the common reasons students drop out of online courses?
Here’s a quick overview of common reasons why users drop out of online courses:
Technical issues (such as slow load times, glitches, or poor mobile optimization)
Lack of motivation
Poor time management
Overwhelming content
Lack of clarity
Boring delivery of content
---
## All About WordPress Code Snippets & How to Customize Your Site [Without Breaking It]
- URL: https://levamo.com/blog/add-code-snippets-in-wordpress/
- Category: wordpress
- Author: Salman
- Published: 2025-02-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Customize WordPress easily! Use code snippets to enhance your site today.
Have you ever wanted to add a new feature to your WordPress site without installing another bulky plugin? This guide will show how a few lines of custom code - these little snippets - can give your website a boost. We’ll cover what these snippets are, how to add them safely, and I’ll share some practical examples you might actually use. Let’s get started!
## What Are WordPress Code Snippets?
WordPress code snippets are small building blocks of a website's functionality. They’re short pieces of code - usually written in PHP, JavaScript, CSS, or HTML - that let you tweak or enhance your site without overcomplicating things. Want a custom login page or a neat automatic redirect after login? Instead of adding a whole plugin just for that one feature, you can simply insert a snippet that does the job.
Typically, WordPress code snippets live in:
- Your theme’s functions.php file
- A child theme (for code changes that survive theme updates)
- A custom plugin
- A dedicated code snippet plugin (like “Code Snippets”)
Which method you choose depends on your comfort level and how frequently you plan to update or change your theme.
## Four Ways to Add WordPress Code Snippets
**Editing Theme Files Directly**
- You can open your theme’s functions.php (for PHP code) or header.php/footer.php (for HTML/JavaScript).
- **Be cautious**: A single typo can break your site. Always back up before making direct edits.
**Using a Child Theme**
- A child theme inherits styles and functionality from its parent theme but keeps your custom code separate.
- This is one of the safest ways to store **WordPress code snippets** if you’re comfortable creating a child theme.
**Creating a Custom Plugin**
- By placing snippets in a custom plugin, you avoid messing with theme files altogether.
- Perfect if you switch themes often or want a portable set of custom functions.
**Employing a Code Snippets Plugin**
- Tools like “Code Snippets” give you an easy interface to add, manage, and deactivate snippets.
- Great for those not comfortable editing PHP directly or who prefer an organized dashboard for their code.
## Step-by-Step: Adding Snippets via a Child Theme
**Create (or Install) a Child Theme**
- If you’re using a theme named “MyTheme,” you’d create “MyTheme Child” with its own style.css and functions.php.
- This ensures your custom code remains intact even when you update the parent theme.
**Open Your Child Theme's functions.php**
- Go to **Appearance** > **Theme File Editor** in WordPress, then pick your child theme from the dropdown.
- Find Theme Functions (functions.php) in the file list.
**Paste Your Code Snippet**
- Place your snippet just before the closing ?> tag (if it exists). If there’s no closing tag, simply paste the snippet at the end of the file.
**Save and Test**
- After you hit “Update File,” check your site to ensure everything still works.
- If you see an error, revert your changes or restore from a backup.
## Step-by-Step: Adding Snippets via the Code Snippets Plugin
**Install and Activate “Code Snippets”**
- In the WordPress admin, go to **Plugins** > **Add New**, search for “Code Snippets,” then click **Install** and **Activate**.
**Access the Snippets Dashboard**
- On the left-hand menu, click **Snippets**. You’ll see a list of active and inactive snippets.
**Add a New Snippet**
- Click **Add New**. Give your snippet a descriptive title.
- In the code editor, paste your snippet. Optionally, add a description or tags.
**Save and Activate**
- Click **Save Changes and Activate**. The snippet now runs on your site.
- If you run into problems, you can easily deactivate it from the same dashboard - no file editing needed.
## 5 Common WordPress Code Snippets (With Examples)
```php
// Makes the login page logo link to a custom URL
add_filter('login_headerurl','custom_login_link');
function custom_login_link() {
return "https://your-site.com/";
}
```
- *Changes the default WordPress logo link on the login screen to your preferred site.*
**Separate Homepages for Logged In vs. Logged Out Users**
```php
if( is_user_logged_in() ) {
$page = get_page_by_path( 'private-home' );
update_option( 'page_on_front', $page->ID );
update_option( 'show_on_front', 'page' );
} else {
$page = get_page_by_path( 'public-home' );
update_option( 'page_on_front', $page->ID );
update_option( 'show_on_front', 'page' );
}
```
- *Requires you to set the "public-home" or "private-home" slug. Then, it automatically shows a different homepage based on the user's login status.*
**Redirect Users to Their Profile Upon Login**
```php
function redirect_to_profile( $redirect_to_calculated, $redirect_url_specified, $user ) {
if ( ! $user || is_wp_error( $user ) ) {
return $redirect_to_calculated;
}
if ( empty( $redirect_to_calculated ) ) {
$redirect_to_calculated = admin_url();
}
if ( function_exists( 'bp_core_get_user_domain' ) && ! is_super_admin( $user->ID ) ) {
return "https://your-site.com/user-profile/";
}
return $redirect_to_calculated;
}
add_filter( 'login_redirect', 'redirect_to_profile', 100, 3 );
```
- *Non-admin users go straight to their profile page instead of the WordPress dashboard.*
**Restrict Admin Area to Admins Only**
```php
function restrict_admin_area() {
if ( ! current_user_can( 'manage_options' ) && ! wp_doing_ajax() ) {
wp_safe_redirect( site_url() );
exit;
}
}
add_action( 'admin_init', 'restrict_admin_area', 1 );
```
- *Boots out non-admin users who try to access the WP admin, redirecting them back to the homepage.*
**Enable Automatic User Registration**
```php
function disable_validation( $user_id ) {
global $wpdb;
$wpdb->query( $wpdb->prepare( "UPDATE $wpdb->users SET user_status = 0 WHERE ID = %d", $user_id ) );
}
add_action( 'bp_core_signup_user', 'disable_validation' );
function fix_signup_form_validation_text() {
return false;
}
add_filter( 'bp_registration_needs_activation', 'fix_signup_form_validation_text');
```
- *Lets new users start using their accounts right away, bypassing the usual activation link or manual approval.*
## Best Practices When Working with WordPress Code Snippets
- **Backup First**: Always create a backup before you add or modify WordPress code snippets. A single misplaced semicolon can take your site down.
- **Understand the Code**: Don’t paste random snippets if you’re unsure what they do. Unfamiliar or outdated snippets can introduce security holes.
- **Use a Test Environment**: If you can, spin up a [staging site or local environment](/blog/how-wordpress-sandboxes-help-developers-test/) to verify your code changes before pushing them live.
- **Comment Everything**: Leaving notes (// your comment here) ensures you - and anyone else - know the snippet’s purpose months from now.
- **Stay Theme-Agnostic**: If you use a child theme or custom plugin, you won’t lose your changes when the theme updates.
- **Follow Coding Standards**: WordPress has coding guidelines for consistency and security. Sticking to them helps avoid weird conflicts.
- **Keep It Minimal**: The fewer WordPress code snippets you run, the fewer potential conflicts and performance issues. Only add what you actually need.
- **Stay Updated**: Check occasionally if your code snippet remains compatible with the latest WordPress release. If something breaks, see if you need to adjust or remove it.
- **Use Plugins as Needed**: If editing code isn’t your style, or you prefer a simpler management interface, code snippet plugins exist for a reason. They make it easier to turn certain snippets on or off quickly.
**Also Read:** [Common Server Problems](/blog/common-server-problems/)
## Conclusion
Well-chosen **WordPress code snippets** can transform your site’s functionality without burying it under dozens of plugins. Whether you’re customizing your login page, restricting admin access, or automatically directing users to specific pages, these small bits of code can make a big impact. Just remember to back up your site, understand what you’re adding, and ideally test in a safe environment first.
By following best practices and using methods like child themes or snippet management plugins, you’ll keep your customizations manageable, secure, and ready for future WordPress updates. So go ahead - experiment with WordPress code snippets and watch your site evolve in all the right ways. If you’re ever unsure, consulting a pro or using a test site can help you avoid any major hiccups. Happy coding!
---
## Security Best Practices for Membership Websites (and How Hosting Plays a Role)
- URL: https://levamo.com/blog/membership-websites-security/
- Category: website-security
- Author: Faisal Sarker
- Published: 2025-02-11
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Harden your membership site! Security tips & how hosting helps protect you.
If you own a membership website, you already know all kinds of threats constantly threaten it. The last thing you want is for your website to be compromised, which in turn will greatly hurt your brand reputation and, most importantly, your business model. Consider how I[BM reported that a data breach costs $4.88 million globally](https://www.ibm.com/reports/data-breach), which should give you more than enough reason to take membership websites security seriously.
Since you cannot afford to lose your membership website’s credibility, you will need to adopt several membership websites security measures to protect sensitive data like financial records, user emails, and so on. Keeping this in mind, this guide will cover the best security practices for membership websites and how you can solve all your problems by simply switching to a reliable hosting provider.
## Best Practices for Secure Membership Websites
Without wasting any time, let’s look at some of the best practices you need to adopt to secure your membership website.
### 1. Use SSL Certificates to Encrypt Data Transmission
Studies have shown that more than [84% of users exit a website without SSL](https://www.bluecorona.com/blog/googles-call-http-sites-https-sol/#:~:text=According%20to%20a%20GlobalSign%20survey,between%20HTTP%20and%20HTTPS%20sites.), so if you want users to stick around, you must have the required [SSL certificates](/blog/ssl-website-security/) in place. SSL certificates ensure there is an encrypted tunnel between your website and users, thus securing any and all data that is exchanged, like payment details and login credentials.
To get an SSL certificate, here is what you need to do:
- Verify the ownership of your domain.
- Choose an authority for the SSL certificate.
- Put in a certificate signing request.
- Send the certificate signing request to the certificate authority.
- Await validation.
- Once received, install the certificate.
**Quick Tip**: How about you choose a hosting provider that provides SSL certificates by default?
**Also Read:** [Best Hosting for MemberPress Websites](/memberpress-hosting/)
### 2. Implement Strong Password Policies for Members and Admins
[Reports indicate that 81% of data breaches result from stolen or weak passwords](https://www.getastra.com/blog/security-audit/password-statistics/#:~:text=Poor%20passwords%20contributed%20to%2081%25%20of%20corporate%20data%20breaches&text=62%25%20of%20organizations%20think%20they,and%2076%25%20of%20targeted%20attacks.). As absurd as it may sound, many users still use passwords like 12345 or their date of birth, and so on. To avoid data breaches due to stolen or weak passwords, make it mandatory for users to create complex and strong passwords. Additionally, administrators should enforce periodic password updates to eliminate the risks originating from compromised credentials.
**Quick Tip**: If you are using weak passwords for your management website, how about you change them pronto?
### 3. Keep WordPress, Themes, and Plugins Up-to-Date
Interestingly, [61% of hacked WordPress websites had outdated software](https://www.getastra.com/blog/security-audit/hacking-statistics/#:~:text=Hacking%20Statistics%20in%20WordPress&text=Nearly%208%25%20of%20WordPress%20websites,vulnerabilities%20arise%20from%20outdated%20plugins.), which tells everything you need to know about the importance of ensuring your WordPress, WordPress themes, and plugins are up-to-date. Make it a habit to update all relevant software to eliminate potential risks that could do considerable harm to your membership website.
**Quick Tip:** How about you enable automatic updates to avoid the hassle of doing everything manually?
### 4. Use Two-Factor Authentication (2FA) for an Additional Security Layer
[Research shows that two-factor authentication can block up to 100% of attacks](https://eftsure.com/statistics/two-factor-authentication-statistics/), which solidifies the importance of using this preventive measure as an extra layer of protection for your membership website.
How two-factor authentication works is that it requires users to submit a code that is normally sent to a mobile device. This extra step may seem frustrating, but it is worth it considering the fact that will reduce any chances of unauthorized access, even if your passwords have been compromised.
**Quick Tip:** How about you set up Google Authenticator to secure your membership website rather than relying on SMS codes?
### 5. Install Security Plugins for Comprehensive Site Security
Many membership website owners do not know they can install various [security plugins](/blog/best-wordpress-security-plugins/) to monitor, detect, and eliminate risks. You can install plugins like Succuri and Wordfence to benefit from firewall protection, malware scanning, etc.
For the [buddyboss hosting](/buddyboss-hosting/) and [memberpress hosting](/memberpress-hosting/), choose platforms that support these tools, and if they don’t, understand that something is wrong. Chances are you will not be able to protect your membership website, which should explain why they were dirt cheap in the first place.
### 6. Set Up Firewalls and Monitor for DDoS Attacks
[Considering the number of DDoS attacks rose by 118% in 2024](https://stormwall.network/resources/blog/ddos-report-q3-2024#:~:text=In%20Q3%202024%2C%20DDoS%20attacks,to%20write%20better%20code%20faster.), you must set up firewalls and monitor traffic to [prevent DDoS attacks](/blog/preventing-ddos-attacks/).
A firewall will act as a barrier between your website and all potential threats, essentially blocking malicious traffic before it can do any harm. Moreover, you must monitor your traffic for DDoS attacks, which may not seem like much at first but will overwhelm your server with traffic. If your server is overloaded, your membership website will be out for the count.
### 7. **Regularly Back Up Your Website**
If you do not want to lose your membership website for good, how about you start backing it up regularly? Consider setting up automated daily backups to quickly restore your website in case of a technical failure or breach. With this approach, you can minimize downtime and preserve vital data for smooth operations.
**Quick Tip:** Opt for secure hosting for membership sites that offer automated backups from the get-go.
### 8. Limit User Roles and Permissions
If you are determined about protecting member data, there is no better way to do so than by restricting user roles to their essential functions. This simple strategy will reduce the risk of accidental or malicious actions. Of course, you will need to assign permissions carefully, which will be time-consuming, but it will ensure users have access to the features they need and nothing more.
### 9. Monitor Logs for Suspicious Activity
Since prevention is better than cure, how about you take a bit of time to monitor logs for suspicious activity? While cumbersome, reviewing activity logs regularly will allow you to identify and deal with unusual behavior, such as unauthorized changes to your website or repeated login attempts.
### 10. Educate Users About Security Best Practices
According to a report from Verizon, phishing accounts for 36% of data breaches. If you want to secure your membership website, you must empower your users and educate them to identify phishing attempts. Give your users easy-to-digest information, such as how to navigate your website safely and create strong passwords. When your users are informed, this in itself will act as a line of defense against all kinds of cyber threats.
**Quick Tip:** Consider sending out a newsletter to educate your users about securing themselves online, just don’t spam them, though.
## How Hosting Providers Can Strengthen Security?
While you can implement the best practices mentioned above to secure your membership website, another solution can nip the problem in the bud: opt for a reliable hosting provider.
A reliable hosting provider will protect your website from all kinds of security threats, curbing potential risks by delivering exceptional infrastructure and preventive measures against cyberattacks.
*Speaking of a reliable hosting provider, if you do not know how to pick the best one, how about you check out Levamo, the [best managed WordPress hosting](/managed-wordpress-hosting/)? *
Levamo takes security seriously, offering a secure hosting environment where it eliminates the need for manually adopting the best practices mentioned earlier. They are a **[WordPress hosting with SSL certificate](/managed-security/)**, virtual patching, automatic malware detection, free malware insurance. Let’s take a look at them more in-depth:
- Built-in SSL encryption.
- Advanced security systems, including automated brute-force attack prevention and strong password enforcement policies by default.
- Automated updates and vulnerability patching.
- Built-in support for two-factor encryption.
- Comprehensive security plugins that come pre-configured and more.
Securing your membership website should not be a daunting task, which is why you will find Levamo to be right up your alley. Levamo is an all-in-one hosting solution provider that eliminates the burden of securing your website manually and allows you to focus on things that are really important, like driving traffic, increasing sales, growing your online community, etc.
## Conclusion
When it comes to membership websites security, you will need to adopt multiple strategies. You must introduce strong password policies, choose the right hosting provider, and implement SSL certificates. You must also focus on educating your users, ensuring regular updates, etc., to stop potential threats dead in their tracks.
If you do not want the hassle of securing your website, your best bet would be to opt for Levamo. You will be able to rest easy knowing your membership website is in safe hands, and you can focus on things that matter.
## Frequently Asked Questions

### What Are the Most Common Security Threats to Membership Websites?
Some common security threats include data breaches, phishing schemes, malware, and brute-force attacks.
### How Can I Secure My Membership Website on WordPress?
You can secure your membership website on WordPress by keeping your software up-to-date, enabling two-factor authentication, using SSL certificates, etc. Additionally, you must educate your users on how to enhance WordPress membership security.
### Why Is Hosting Important for Website Security?
Hosting providers offer essential features like automated backups, DDoS protection, and active monitoring. Essentially, a reliable hosting solution will ensure your website remains operational and secure at all times.
### How Often Should I Update Plugins and Themes for My Membership Site?
Update plugins and themes as soon as updates become available. Regular updates patch security vulnerabilities and improve functionality.
### Can Hosting Providers Help Prevent Brute-Force Attacks?
Yes, hosting providers, like Levamo, with active monitoring and firewalls, can detect and block brute-force attacks, ensuring unauthorized users cannot gain access to your website.
###
---
## Top White-Label WordPress Agencies to Consider in 2025
- URL: https://levamo.com/blog/white-label-wordpress-agency/
- Category: website-development
- Author: Sunyyan Junaid
- Published: 2025-02-10
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find the perfect white-label WordPress partner for your agency in 2025.
Let’s be real: running a top WordPress agency is a juggling act. Between managing client expectations, keeping up with endless projects, and trying to grow your business, it’s easy to feel stretched thin. But what if you could offer more services without the hassle of hiring and training a full-time team?
That’s where partnering with a white-label WordPress agency can make a difference. These companies take care of everything behind the scenes, from custom WordPress development and Figma-to-WordPress conversions to plugin development, SEO, and maintenance, so you can focus on building client relationships and scaling your agency. It’s like having an expert development team without the long-term commitment.
From affordable hourly rates to dedicated developer hiring models, we’ll compare pricing, key services, and who they’re best suited for, so you can find the top white label WordPress agency for your needs.
Oh, and if you're looking for the fastest WordPress hosting to back up your incredible WordPress agency services, take a look at [Levamo](/), a managed hosting solution that your clients' sites run at blazing fast speeds and stay online 99.99% year-round.
Now, let's dive into the best white label WordPress services to consider for yourself.
## Top-Rated White-Label WordPress Agencies in 2025
Choosing the top white label WordPress agency can be a game-changer for your agency’s success. Below, we’ve compiled a list of the best white-label WordPress agencies, highlighting their services, pricing, and what makes them stand out.
### 1. Seahawk

[Seahawk ](https://seahawkmedia.com "nofollow")is a globally recognized top [white label WordPress](https://seahawkmedia.com/services/wordpress-white-label/ "nofollow") agency, trusted by 1,000+ brands, including Alibaba. The company specializes in helping agencies scale their WordPress services effortlessly while maintaining high-quality development standards. With a strong presence in the WordPress ecosystem, Seahawk offers comprehensive solutions that cover every aspect of WordPress management.
Seahawk’s team of experts delivers high-performance websites, security solutions, and maintenance services tailored to agencies' needs. Their self-service marketplace, QuickSite, and custom WordPress development services make them a go-to partner for businesses looking to streamline operations without expanding their in-house teams.
**Key Services:**
- **White-label development** - Custom WordPress themes, plugins, and eCommerce solutions.
- **Maintenance and support** - Ongoing updates, security checks, and site optimizations.
- **Custom web design** - Tailored solutions to create unique, high-converting websites.
- **Site speed optimization** - Enhancing website performance and user experience.
- **Migration and rebuilds** - Seamless transitions to modern WordPress sites.
- **SEO and content services** - Boosting website visibility and engagement.
**Pricing:**
$59 per hour - Simple and transparent pricing for custom WordPress services.
### 2. WP Tasks

[WP Tasks](https://wptasks.com "nofollow") is a specialized white-label WordPress service provider offering unlimited support hours. Their solutions cater to agencies looking for reliable task assistance, from minor website tweaks to complex customizations. Their dedicated team ensures that every website project meets industry standards and exceeds expectations.
With a flexible pricing structure, WP Tasks helps agencies scale their services efficiently without increasing operational overhead. Their commitment to quality and timeliness makes them a preferred choice for agencies handling multiple WordPress projects.
**Key Services:**
- **WordPress Builds** - Custom WordPress website development from scratch.
- **Task Assistance** - Handling minor and major website improvements.
- **Tweaks and Adjustments** - Quick fixes and modifications for WordPress websites.
- **Fixing Issues** - Resolving bugs, performance issues, and security threats.
- **Unlimited WordPress Support** - Dedicated development assistance for agencies.
- **Custom Development** - Tailor-made WordPress solutions based on client requirements.
**Pricing:**
- Intenso Plan: $2,999/month (6-8 hours daily)
- Growth Plan: $1,499/month (3-4 hours daily)
- Lite Plan: $749/month (1-2 hours daily)
### 3. Wbcom Designs
[Wbcom Designs](https://wbcomdesigns.com/ "nofollow") runs white-label development for WordPress and Laravel agencies that have hit a capacity ceiling that has nothing to do with sales. The pipeline is full, but hiring senior engineers takes months, and junior subcontractors tend to leave technical debt for someone else to clean up later. Wbcom operates as a second engineering team inside the agency's own brand: NDA-backed, capped monthly retainers, and the client never sees a Wbcom email, invoice, or domain.
The team doing the white-label work is the same one that builds and maintains Wbcom's own product line (BuddyX Pro, BuddyPress Moderation Pro, and the BuddyNext community ecosystem), so there is no hand-off to an offshore junior team after the sales call closes. Code, GitHub access, and hosting credentials stay in the partner agency's own accounts throughout the engagement, so there is no lock-in if the partnership ends.
**Key Services:**
- **White-label WordPress & Laravel development** - Custom builds, plugin development, and LMS and community-platform engineering, delivered under the partner agency's brand end to end.
- **Capped retainers with rollover** - Monthly hour caps (up to 50% rollover) or fixed-price scope blocks, so margin is locked in before the client is ever quoted.
- **Full agency stack, one vendor** - WordPress, BuddyPress, LearnDash, and WooCommerce, plus Laravel SaaS engineering, Astro static sites, and AI/MCP development, replacing a subcontractor matrix with a single partner.
- **Co-branded reporting** - Weekly status in whatever format the partner's clients expect (PDF, Loom, Slack, Basecamp), translated to outcomes instead of commit messages, ready to forward without a rewrite.
**Pricing:**
Not publicly listed - partner pricing tiers are shared after a free scoped discovery call.
### 4. WP White Label

[WP White Label](https://wpwhitelabel.io "nofollow") is another top white label WordPress agency offering seamless white-label development, maintenance, and customization services. Their focus on delivering high-quality WordPress solutions allows agencies and freelancers to expand their services under their own branding.
With expertise in WordPress plugin development and conversion services, WP White Label ensures that agencies can meet their client demands efficiently. Their structured workflow and transparent pricing make them a dependable white-label partner.
**Key Services:**
- **WordPress Development** - Custom-built websites and themes.
- **Website Design** - High-quality, responsive website design solutions.
- **WordPress Maintenance** - Ensuring website security, updates, and performance.
- **WordPress Support** - Ongoing technical assistance for businesses.
- **Figma to WordPress** - Converting Figma designs into functional WordPress sites.
- **Custom Plugin Development** - Building and modifying plugins for unique functionalities.
- **Site Migration** - Seamless migration from other platforms to WordPress.
- **SEO Services** - Enhancing search visibility and rankings.
**Pricing:**
$99 per hour - Fixed hourly pricing for WordPress services.
### 5. FigtoWP

[FigtoWP](https://figtowp.com "nofollow") is a white-label agency specializing in high-quality Figma to WordPress conversion services. Their streamlined design-to-development process ensures pixel-perfect results, making them an ideal partner for agencies focusing on UI/UX-centric web projects.
From Elementor to Gutenberg, FigtoWP ensures seamless WordPress integration, offering agencies a reliable way to bring their creative designs to life. Their expertise allows agencies to scale their services while maintaining top-notch website aesthetics.
**Key Services:**
- **Figma to [Elementor](/blog/elementor-review/)** - Smooth conversion for Elementor-based WordPress sites.
- **Figma to Divi** - Building websites with Divi’s powerful framework.
- **PSD to Figma** - Transforming Photoshop designs into web-ready Figma files.
- **Figma to SeedProd** - Converting Figma layouts into high-performance landing pages.
- **Figma to Gutenberg** - Ensuring compatibility with WordPress’s native block editor.
**Pricing:**
**Starts at $200 per page - Pricing depends on design complexity**.
### 6. WPBeginner Pro Services

[WPBeginner Pro](https://www.wpbeginner.com/services/ "nofollow") Services is a well-known white-label WordPress agency leveraging WPBeginner’s extensive knowledge and resources. They specialize in helping agencies provide advanced WordPress solutions without building an in-house team.
With a team of WordPress experts, WPBeginner Pro Services offers website development, maintenance, and optimization services tailored to agency needs. Their industry reputation ensures agencies can rely on their expertise for high-quality deliverables.
**Key Services:**
- **Custom WordPress Development** - Fully tailored website solutions.
- **Website Maintenance** - Security updates, backups, and optimizations.
- **SEO Services** - Enhancing website visibility through targeted strategies.
- **Speed Optimization** - Improving website performance and loading times.
- **Security Solutions** - Protecting sites from malware and cyber threats.
**Pricing:**
**Custom Pricing - Contact WPBeginner for service details**.
### 7. The White Label Agency

[The White Label Agency](https://thewhitelabelagency.com "nofollow") is a prominent, top white label WordPress agency service provider based in the USA with a strong presence in Europe. They have over a decade of experience managing thousands of WordPress projects for agencies worldwide.
Their structured development workflow ensures agencies can scale their services seamlessly without hiring additional in-house developers. The White Label Agency specializes in providing dedicated WordPress developers at a fixed monthly rate.
**Key Services:**
- **Custom WordPress Websites** - Fully customized builds with ACF and CPT.
- **Project-Based WordPress Development** - Fixed-price quotes for individual projects.
- **WordPress Migration & Conversion** - Moving sites from other platforms.
- **Dedicated Developer Hiring** - Hiring dedicated developers on a monthly basis.
**Pricing:**
- Junior Developer: $2,900/month
- Middle Developer: $3,900/month
- Senior Developer: $5,000/month
### 8. GetDevDone

[GetDevDone](https://getdevdone.com "nofollow") is a white-label web development agency with over 15 years of experience, delivering custom digital solutions to enhance brands and accelerate business growth. They specialize in high-performance web applications, WordPress development, and scalable eCommerce solutions.
With an in-house team of experts, GetDevDone ensures that agencies receive seamless development services that align with their specific goals and industry needs. Their strong technical capabilities make them a trusted partner for businesses looking for tailored WordPress solutions.
**Key Services:**
- **WordPress Development** - Custom themes, plugins, and website builds.
- **Shopify Development** - Shopify store setup, customization, and maintenance.
- **PSD to HTML Conversion** - Converting designs into high-quality HTML code.
- **Drupal Development** - Building and managing Drupal-based websites.
- **Webflow Development** - Designing and developing responsive Webflow sites.
- **Low-Code Development** - Implementing modern low-code/no-code solutions.
- **Web App Development** - Custom applications to enhance business workflows.
**Pricing:**
**Not publicly available - Please contact GetDevDone for a detailed quote**.
### 9. ZoomAgency

[ZoomAgency](https://www.zoomagency.co "nofollow") is a well-established white-label digital marketing and development firm with over 10 years of experience. They focus on providing scalable web solutions to agencies, allowing them to deliver high-quality services without expanding their in-house teams.
From WordPress development to SEO and PPC management, ZoomAgency offers full-spectrum digital marketing services to enhance client acquisition and brand visibility. Their Hyper Prospecting Program is a unique feature that helps agencies grow their clientele efficiently.
**Key Services:**
- **Custom WordPress Development** - Fully customized WordPress websites.
- **Website Performance Optimization** - Improving site speed and responsiveness.
- **SEO and Google Ads Management** - White-label digital marketing services.
- **Client Acquisition Assistance** - Connecting agencies with potential clients.
- **Duda Development** - White-label website development using Duda.
**Pricing:**
**Not publicly available - Contact Zoom Agency directly for a custom quote**.
### 10. Monocubed

[Monocubed](https://www.monocubed.com "nofollow") is a Canada-based white-label web development agency specializing in business-first digital transformation. They focus on creating high-performing, brand-aligned web solutions that help agencies streamline their operations while delivering outstanding results.
By emphasizing partner goals and technical excellence, Monocubed ensures that agencies receive innovative web solutions tailored to meet modern business demands. Their deep understanding of web technologies makes them a reliable choice for agencies looking to expand their service offerings.
**Key Services:**
- **Python Development** - Custom applications using Python for business automation.
- **WordPress Development** - High-quality themes, plugins, and website builds.
- **Full Stack Web Development** - Comprehensive solutions using the latest frameworks.
- **Web Portal Development** - Secure and scalable portals for businesses.
- **White Label Web Development** - Fully white-labeled solutions for agencies.
- **Web Development Consulting** - Strategic consulting for digital projects.
**Pricing:**
**Not publicly available - Reach out to Monocubed for tailored quotes**.
### 11. Pronto Marketing

[Pronto Marketing](https://www.prontomarketing.com "nofollow") is a Bangkok-based white-label digital marketing agency with over 15 years of expertise in WordPress development and online marketing. They specialize in providing seamless support for agencies, ensuring effortless scaling without operational burdens.
Their solutions focus on website design, SEO, PPC management, and GMB optimization, helping agencies improve their clients' digital presence. With a predictable fixed-cost model and a dedicated team, Pronto Marketing ensures quality execution while agencies focus on business growth.
**Key Services:**
- **WordPress Development** - Building and maintaining high-performing WordPress sites.
- **SEO Services** - Enhancing online visibility through strategic SEO.
- **PPC Management** - Running effective paid ad campaigns.
- **GMB Optimization** - Improving local search rankings.
- **Digital Marketing Solutions** - Tailored strategies for business growth.
**Pricing:**
**Their white-label WordPress support starts at $25 USD/hour**.
## How to Partner with the Best White-Label WordPress Agency?
Finding the right white-label WordPress partner isn’t just about outsourcing work - it’s about building a reliable collaboration that helps your agency scale seamlessly. Here’s what to consider when choosing the best agency to work with:
### 1. Define Your Needs and Expectations
- Identify the services you need, whether it’s development, maintenance, SEO, or full-scale project management.
- Determine your budget and pricing structure that aligns with your business model.
- Set clear quality expectations and deadlines to ensure smooth delivery.
### 2. Evaluate Their Portfolio and Expertise
- Check their previous work and case studies to assess their experience.
- Look at the industries they have worked in; do they align with your clients’ needs?
- Ensure they follow best coding practices and offer scalable solutions.
### 3. Assess Their Communication and Support
- A good white-label partnership requires seamless communication.
- Do they offer dedicated account managers or project managers?
- Test their response time and support structure - you want a team that’s available when you need them.
### 4. Understand Their White-Label Process
- Find out how they manage projects, revisions, and approvals.
- Do they allow full branding under your agency’s name?
- Check their workflow and tools - do they use platforms like Slack, Trello, or Asana for smooth collaboration?
### 5. Request a Trial Project
- Before committing to a long-term partnership, test their services with a small project.
- Evaluate their timeliness, quality, and ability to meet expectations.
- See how flexible they are with feedback and changes.
## Comparison of Top White-Label WordPress Agencies
We have prepared a table to compare pricing, key services, and best use cases for each agency.
| **Agency Name** | **Key Services** | **Pricing** | **Best For** |
|---|---|---|---|
| **Seahawk Media** | Full-scale white-label WordPress solutions | $59/hr | Agencies & businesses |
| **WP Tasks** | Unlimited WP support & maintenance | From $749/month | Agencies needing ongoing support |
| **Wbcom Designs** | White-label WordPress & Laravel dev, capped retainers, zero lock-in | Contact for quote | Agencies needing senior dev capacity without hiring |
| **WP White Label** | Custom WP builds, plugins, and migration | $99/hr | Developers & agencies |
| **FigtoWP** | Figma-to-WordPress conversion | From $200/page | Design-focused agencies |
| **WPBeginner Pro Services** | WP development & SEO optimization | Custom pricing | Small to large agencies |
| **The White Label Agency** | Dedicated WP development teams | From $2,900/month | Agencies needing full-time devs |
| **GetDevDone** | WP, Shopify, Webflow & custom builds | Contact for pricing | Multi-platform solutions |
| **ZoomAgency** | SEO, PPC, & WP performance | Not available | Agencies needing marketing + WP services |
## Final Thoughts: Which White-Label Agency Should You Choose?
The top white label WordPress agency for your business depends on your specific needs. If you’re looking for affordable ongoing support, **WP Tasks** offers budget-friendly plans. For custom development and scalability, **Seahawk Media** and **The White Label Agency** are excellent choices. If design precision is your priority, **FigtoWP** specializes in pixel-perfect Figma-to-WordPress conversions, while **WPBeginner Pro Services** and **ZoomAgency** focus more on SEO and performance optimization.
The key is to start with a small project, test their responsiveness and quality, and ensure they align with your agency’s workflow. A great white-label partner should feel like an extension of your team, helping you scale without adding unnecessary complexity. Choose wisely, and you’ll have a long-term ally in growing your agency effortlessly.
---
## TLS vs SSL: What's the Difference?
- URL: https://levamo.com/blog/tls-vs-ssl/
- Category: website-development
- Author: Salman
- Published: 2025-02-10
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Uncover the key differences between TLS and SSL for secure online communication.
What’s the difference between TLS vs SSL? And is it something you need to worry about?
When it comes to securing online communications, including websites, ecommerce stores, and financial transactions using websites, SSL (Secure Sockets Layer) and TLS (Transport Layer Security) are two terms that often come up.
Many people use them interchangeably, but there are key differences between these protocols. In this blog, you’ll learn the key differences between TLS vs SSL, and why TLS is now the preferred standard.
## What Are TLS and SSL?
SSL and TLS are cryptographic protocols designed to secure communication over the Internet. They encrypt data between a user's browser and a web server, ensuring that sensitive information like passwords, credit card details, and personal messages remains private.
- **SSL (Secure Sockets Layer):** The first widely adopted encryption protocol for the web.
- **TLS (Transport Layer Security):** The successor to SSL, offering enhanced security and efficiency.
## The Evolution of SSL and TLS: A Brief History
### Transition to TLS: TLS 1.0 and TLS 1.1
In 1999, TLS 1.0 was introduced as the successor to SSL 3.0, improving encryption and authentication. However, it was later found vulnerable to attacks like BEAST.
TLS 1.1 was released in 2006, enhancing security against CBC attacks. Despite improvements, both versions were deprecated in 2020 due to outdated encryption methods.
### The Rise of Stronger Encryption: TLS 1.2
Launched in 2008, TLS 1.2 introduced SHA-256 hashing and removed weaker encryption algorithms, becoming the widely accepted standard for secure communication. It remains in use today across many websites and services.
### The Future of Web Security: TLS 1.3
Released in 2018, TLS 1.3 removed outdated cryptographic methods, improved connection speeds, and strengthened security. It is now the most secure and recommended encryption protocol for modern web applications.
## Evolution of SSL to TLS
SSL has gone through multiple versions, with SSL 3.0 being the most notable. However, due to security vulnerabilities, SSL was replaced by TLS.
- **TLS 1.0 & 1.1:** Built on SSL but now considered outdated.
- **TLS 1.2 & 1.3:** The most secure and widely used versions today.
## How HTTPS, SSL, and TLS Work Together
When you visit a website using **HTTPS**, here’s what happens behind the scenes:
- **Your browser requests a secure connection.**
- **A secure handshake occurs,** where encryption keys are exchanged.
- **The website's server responds with an SSL/TLS certificate**, verifying its identity.
- **Data is encrypted and transmitted safely** between the browser and the server.
This process ensures **privacy, integrity, and authenticity**, preventing attackers from stealing or modifying your data.
## Key Similarities Between TLS and SSL
Despite differences in TLS vs SSL, they share some common features:
- **Handshake Process:** Both use a client-server handshake to establish a secure connection.
- **Encryption:** They encrypt data to prevent unauthorized access.
- **Certificates:** The terms "SSL certificate" and "TLS certificate" refer to the same thing in practice.
## SSL VS TLS
| **Feature** | **SSL (Secure Sockets Layer)** | **TLS (Transport Layer Security)** |
|---|---|---|
| **Security Level** | Strong encryption, but older standards | Enhanced security with updated encryption methods |
| **Encryption** | Provides solid encryption for secure connections | Uses stronger encryption algorithms like AES and SHA-256 |
| **Speed** | Reliable but slightly slower due to extra processing | Optimized for faster performance and efficiency |
| **Vulnerabilities** | Secure but older versions had some known exploits | Eliminates outdated cryptographic methods for better protection |
| **Handshake Process** | Secure handshake process with authentication | More efficient handshake, reducing connection delays |
| **Deprecation Status** | SSL certificates are still widely recognized and used | TLS is the recommended protocol, but SSL certificates remain industry-standard |
| **Usage Today** | Still used and supported across many platforms | TLS 1.2 is the industry standard, with TLS 1.3 being the latest version |
| **Certificate Naming** | SSL certificates are the industry norm | Technically, they are TLS certificates, but often still referred to as SSL |
## How to Install an SSL/TLS Certificate on Levamo
As soon as you add your custom domain, an SSL certificate is automatically installed - no extra steps are needed! 🎉 Yes, Levamo understands the imperative need for SSL in today's online ecosystem.
That’s why every website hosted with Levamo comes equipped with an SSL certificate, helping your site rank better in search results while ensuring a secure experience for your visitors.
Read More: [SSL Certificate Errors](/blog/fix-ssl-certificate-error/)
Just make sure your domain is correctly pointed to your server's IP, and once the system confirms the connection, your site will be secured with SSL in no time! 🚀
## Final Thoughts
In today’s digital world, security isn’t just a technical requirement - it’s a fundamental expectation. Whether you’re running a personal blog, an online store, or a business website, ensuring that your visitors’ data is protected is essential.
At the end of the day, web security should be simple and seamless. That’s why Levamo takes the hassle out of SSL management - your site gets a free, automatically installed SSL certificate the moment you connect your domain.
There are no manual configurations and no hidden fees, just secure, fast, and reliable hosting so you can focus on what truly matters: growing your online presence with confidence.
Security shouldn’t be an afterthought - it should be built in. And with Levamo, it is. 🚀
---
## What are the top 8 WordPress Mistakes [Community Comments]
- URL: https://levamo.com/blog/worst-wordpress-mistake/
- Category: wordpress
- Author: Salman
- Published: 2025-02-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Avoid common WordPress errors! See top community-voted mistakes.
You know that panicky feeling when your WordPress site starts loading at a snail’s pace, or worse, gets hit with unexpected downtime? Often, the root cause can be traced back to well-intentioned but terrible advice. Over the years, users and developers alike have shared stories of crippling plugin overloads, questionable hosting decisions, and security blunders - each one wrapped in seemingly harmless tips.
A recent wordpress community thread posed the question: **“What’s the worst WordPress advice you’ve ever heard?”** The community came back with a flurry of responses - from piling on plugins to hosting nightmares. Below, we’ve gathered some of the standout “worst advice” and explained why you might want to avoid it. Let’s dive in.
## 1. “****[Just Install More Plugins to Add Features](https://www.reddit.com/r/Wordpress/comments/1igukpt/whats_the_worst_wordpress_advice_youve_ever_heard/)****”

### Why It’s #1 WordPress Mistake?
Plugins are a hallmark of WordPress. They make it easy to add everything from contact forms to security features without writing a line of code. So it’s natural to think, “Why not just keep installing plugins for every new feature I want?”
### Why It’s Bad
- **Performance Drain**: Each plugin adds extra scripts, styles, or queries. Multiply that by 20, and you’ve got a bloated site that crawls.
- **Security Risks**: More plugins = more potential vulnerabilities, especially if you’re not updating them regularly.
- **Compatibility Woes**: Plugin conflicts can send your site into a tailspin, often resulting in [500 errors](/blog/fix-the-500-internal-server-error/) or broken layouts.
**Better Advice**: Be selective. If you need advanced functionality, consider custom code (in a child theme) or a reliable all-in-one plugin. Fewer, well-maintained plugins generally lead to fewer headaches.
## 2. “****[Host It on Shared Hosting](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/marxtrg/)****”

### Why It’s #2 WordPress Mistake
Major Famous Hosting Brands have massive name recognition. They often run flashy ads promising unlimited everything for pocket change.
### Why It’s Bad
- **Performance Complaints**: Community threads frequently mention slow load times and server timeouts.
- **High Upsells & Renewal Costs**: Those cheap intro deals sometimes skyrocket when it’s time to renew.
- **Aggressive Sales Tactics**: Users often complain about constant upselling calls or promotions.
**Better Advice**: Search for a host known for WordPress-optimized stacks (like **Levamo**, of course). Look for speed benchmarks, top-tier support, and transparent pricing that won’t leave you blindsided at renewal time.
## 3. “****[Just Hook Everything Into functions.php](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/marvudl/)****”

### Why It’s #3 WordPress Mistake
If you’re new to WordPress, you might stumble upon tutorials telling you to stuff custom code directly into functions.php. It’s a quick fix, right?
### Why It’s Bad
- **Theme Dependency**: The moment you change your theme, say goodbye to all that custom functionality.
- **Clutter & Confusion**: A single error in your functions.php can break your entire site. Debugging becomes a nightmare.
- **No Toggle Switch**: If something stops working, you can’t just deactivate a plugin. You’re sifting through code.
**Better Advice**: Create a **child theme** for theme-specific tweaks, or develop a **simple custom plugin** for site functionality. That way, you’re not tying critical code to a single theme choice.
## 4. “****[Use Nulled (Pirated) Plugins; They’re Free!](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/marqnxs/)****”

### Why It’s huge WordPress Mistake
Paying for premium plugins can get pricey, so stumbling onto “free” versions of big-name plugins might seem like a bargain.
### Why It’s Bad
- **Malware & Backdoors**: Many nulled plugins have hidden code that can hijack your site for spam or worse.
- **No Updates or Support**: Even if the code is initially clean, you’ll miss out on security patches and new features.
- **Ethical & Legal Gray Areas**: WordPress is open-source, but reselling or redistributing premium plugins can violate licensing (and the trust of developers).
**Better Advice**: Pay for the plugins you need or find reputable free alternatives. Supporting developers means you’ll get proper updates, security patches, and customer support.
## 5. “****[Never Use a Security Plugin - WordPress Is Already Secure!](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/mat1gxa)****”

### Why It’s Tempting
WordPress core has decent security baked in, and if you’re just running a small blog, you might think no one’s going to bother hacking you.
### Why It’s Bad
- **Common Target**: WordPress is used by over 40% of the web. That makes it a massive bullseye for botnets and brute-force attacks.
- **Plugin & Theme Vulnerabilities**: Even if WordPress core is secure, third-party themes and plugins can open loopholes.
- **Server Config Matters**: Few site owners truly have “properly configured servers” that block every threat by default.
**Better Advice**: Security is a layered approach. Install a [reputable security plugin](/blog/best-wordpress-security-plugins/) (Wordfence, iThemes Security, etc.), keep your hosting up to date, and consider a firewall or CDN with DDoS protection - like **Levamo’s** solutions.
## 6. “****[Don’t Bother Updating Core, Themes, or Plugins](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/mau6cno/)****”

### Why It’s Tempting
If it ain’t broke, don’t fix it - right? Some folks worry updates might break their site, so they shy away from regular maintenance.
### Why It’s Bad
- **Security Risks**: Outdated software is a magnet for exploits.
- **Compatibility Issues**: Web tech evolves; ignoring updates might lead to conflicts with your hosting environment or other tools.
- **Missed Features & Fixes**: You won’t get the new goodies plugin developers release, nor bug fixes that might improve performance.
**Better Advice**: Update regularly, but do it wisely. Make backups first (or use a [staging environment](/blog/how-wordpress-sandboxes-help-developers-test/)). If something goes awry, you can easily roll back.
## 7. “****[Elementor/Gutenberg/Any Page Builder Slows You Down - Don’t Use It Ever](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/masd9p1/)****”

### Why It’s Tempting
Page builders can be known resource hogs, especially if misused. A bare-bones website will almost always outpace a site loaded with builder scripts.
### Why It’s Bad
- **Overgeneralization**: Not all page builders are created equal. Some are more efficient than others, and with the right optimization, your site can still be quick.
- **Ease vs. Speed Trade-Off**: For many site owners, the convenience of drag-and-drop design outweighs a small performance hit.
- **Plugin & Hosting Quality**: A well-chosen hosting plan, caching plugin, and image optimization can mitigate a lot of builder-related slowdown.
**Better Advice**: If you love a certain builder, optimize it. Choose a lightweight theme. Use caching and good hosting. Test performance regularly - tools like GTmetrix or Google PageSpeed Insights can guide you.
## 8. “****[Go With a Custom Theme - Updates Don’t Matter](https://www.reddit.com/r/Wordpress/comments/1igukpt/comment/marv7hl/)****”

### Why It’s Tempting
A custom theme designed from scratch can be lightning-fast and totally unique. Who doesn’t want that?
### Why It’s Bad
- **Abandoned Updates**: If your developer disappears, you’re stuck with old code that might break down the line.
- **Hidden Bloat**: A poorly written custom theme can be just as bloated as any mega theme - if not worse.
- **Limited Support**: You can’t rely on a community forum for help, since the code is one-of-a-kind.
**Better Advice**: If you go custom, ensure you have a reliable developer who updates the theme as WordPress evolves. Alternatively, use a reputable framework or lightweight theme that’s actively maintained.
Also Read: [LMS hosting](/managed-lms-hosting/)
## Final Thoughts: Trust, But Verify
There’s a common thread in most of this advice: a little bit of knowledge can be dangerous. WordPress is powerful and flexible, but that flexibility opens the door to questionable shortcuts, shady plugins, or poor hosting choices.
If you’re uncertain about a recommendation, do a quick search - or ask the WordPress community. You’ll often find a nuanced answer that weighs pros and cons, rather than a blanket “yes” or “no.”
And remember: **Levamo** as the best [Kinsta alternative](/kinsta-alternative/) is here to help if you need hosting tailored for WordPress. We handle the behind-the-scenes optimizations so you can focus on building your site without wading through shady advice.
**So, what’s the worst WordPress tip you’ve encountered?** If it didn’t make this list, let us know! Chances are, someone out there has heard it, tried it, and learned an unforgettable lesson. Stay safe, stay curious, and keep building on WordPress - the right way.
---
## Meet Levamo at WordCamp Asia 2025!
- URL: https://levamo.com/blog/wordcamp-asia-2025/
- Category: news
- Author: Faisal Sarker
- Published: 2025-02-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo sponsors WordCamp Asia 2025! See what to expect in Manila.
We are thrilled to announce that Levamo will be joining WordCamp Asia 2025 as an **Author-level Sponsor**!
WordCamp Asia is one of the flagship conferences for WordPress on the continent of Asia. This year, the stage is set for a grand union in the city of Manila, the bustling capital of the Philippines. The conference will take place at the Philippine International Convention Center (PICC) from February 20-22, 2025.
Let’s take a quick look at what you can expect from this conference from Levamo and the WordPress community!
## What to Expect from WordCamp Asia 2025?
Like every year, WordCamp Asia 2025 is filled with insightful sessions, workshops, parties, and more! Here’s what is happening at this year’s grand event.
### Key Events
WordCamp Asia 2025 will happen for three consecutive days, starting from February 20 to February 22.
- February 20: Contributor Day
- February 21: Conference Day 1
- February 22: Conference Day 2 and After Party
You can find the [detailed schedule and speaker lineup](https://asia.wordcamp.org/2025/schedule/) on the official WordCamp Asia 2025 website.
## Meet Team Levamo at WordCamp Asia
As a proud sponsor, we will bring our passion for WordPress and high-performance hosting to the WordCamp. We want to empower businesses, developers, and creators by offering the fastest WordPress hosting possible.
**Here’s a glimpse of who you can meet from our team:**
| | Name | Title |
|---|---|---|
|  | **Michael Eisenwasser** | Co-founder, President & CPO |
|  | **Tom Cheddadi** | Co-founder & CEO |
|  | **Wes Tatters** | Managing Director & Infrastructure Architect |
|  | **Shelby Fernandes** | Chief Operating Officer |
And of course, **Fleet**, our fun-loving mascot!
Fleet, the fun loving mascot
### Our Booth & What to Expect
During this WordCamp Asia, the Levamo booth is the place to have fun and learn expert insights to take your WordPress site to the next level. Whether you’re looking to boost page speeds, handle surging traffic, or simply sharpen your WordPress skills, our friendly team is here to offer practical suggestions for you.
And while you’re there, don’t forget to grab some exclusive swag and take part in our special giveaway.
Here’s a quick look at what you can expect:
- **Product Walkthroughs**
**See how our managed WordPress hosting platform effortlessly handles dynamic websites and peak traffic**.
- **Performance Upgrades**
**Want to experience a faster site firsthand? You can take advantage of the Levamo free trial on the spot**. Experience your WordPress site performance boost-up, instantly.
- **Expert Advice**
**Meet our founders and WordPress hosting experts and get personalized recommendations to speed up your website**.
- **Swag & Surprises**
**But it’s not always all about serious talk**. You can also drop by to score some fun swag - and don’t miss our **exclusive giveaway**, where you could win a special gift! 👀
We can’t wait to meet you in person, talk shop about WordPress performance, and share a few goodies along the way.
## See you there!
That’s it for now! We can’t wait to meet you in person at **WordCamp Asia 2025**.
Whether you’re a WordPress newbie, a seasoned developer, or a business owner, please come and say hello to our friendly team.
And if you want to discuss your hosting needs in detail or talk about a partnership, let's have a meeting.
**[Schedule a Meeting with Team Levamo](https://calendly.com/community-rapyd/wordcamp-asia)**
Can’t attend the event physically this time around? No worries! We’ll be sharing the highlights throughout the conference. We will also share a full recap of the three-day event shortly after WordCamp Asia concludes.
If you have any questions before the event, please feel free to reach out to us.
---
## What Is the scp Command in Linux? [Examples Provided]
- URL: https://levamo.com/blog/scp-command-in-linux/
- Category: hosting
- Author: Salman
- Published: 2025-02-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Use scp in Linux to securely transfer files. Examples included.
Moving files securely between systems isn’t always easy - especially when you’re dealing with sensitive data and can’t afford any slip-ups.. That’s where the **scp** command in Linux comes into play. Short for “secure copy,” scp encrypts your files during transit (thanks to the SSH protocol) so that nosy third parties can’t snoop on your data. Whether you’re migrating server configs, sending scripts to colleagues, or just moving a folder of cat memes to your VPS, scp has you covered. Below, we’ll walk through how scp works, why it’s useful, and some handy examples to kickstart your learning.
## Why Use scp Instead of Other Methods?
- **Encryption Built-In**: Unlike plain copy commands, scp automatically safeguards your files with SSH encryption.
- **Remote to Remote**: You can shuffle files between two remote servers without downloading them to your local machine first.
- **User-Friendly**: The syntax feels familiar if you’ve ever used cp for local copies - just add your SSH credentials and paths.
## Basic scp Syntax
The general format looks like this:
scp [options] [source] [destination]
- **options**: Special flags you can enable for debugging, limiting speed, recursive copying, etc.
- **source**: Where your file currently lives (either locally or on a remote server).
- **destination**: Where you want the file to end up (again, can be local or remote).
## 1. Copying a Local File to a Remote Server
So you’ve got a file named notes.txt on your local machine, and you want to upload it to a remote server. Here’s how:
`scp /path/to/local/notes.txt username@remote_host:/remote/path/`
- Replace username with your actual username on the remote server.
- remote_host can be an IP address or a domain name.
- If the file is small, this will happen almost instantly; for larger files, you’ll see a progress bar.
## 2. Copying a Remote File to Your Local System
Sometimes you need to grab something from a server - maybe logs or a config file. Reverse the direction:
`scp username@remote_host:/path/to/remote/backup.tar.gz /local/path/`
Now scp will fetch backup.tar.gz from the remote server and plop it into your local /local/path/.
## 3. Copying a Directory (Recursively)
Transferring one file is fine, but what if you’ve got an entire directory of files you need to move? Just tack on the **-r** flag for recursion:
`scp -r /local/directory/ username@remote_host:/remote/directory/`
- This grabs every file, folder, and subfolder nested inside /local/directory/.
- Make sure you include the trailing slash / so that scp copies the contents instead of creating an extra subdirectory.
## 4. Copying Between Two Remote Systems
A lesser-known trick: you can move files between two remote hosts without touching your local machine:
`scp username1@remote_host1:/path/to/file.txt username2@remote_host2:/path/to/destination/`
Think of it like telling one server to pass your file directly to another. Handy if your local bandwidth is limited.
## Extra Options You Should Know
**Custom SSH Port with -P**
If your server runs on, say, port **2222** instead of the standard **22**, you can specify that like so
`scp -P 2222 /local/file.txt username@remote_host:/remote/path/`
**Limit Bandwidth with -l**
**On a slow or shared connection? Avoid hogging all the bandwidth**
`scp -l 200 /local/file.txt username@remote_host:/remote/path/`
The 200 here means 200 Kbps - enough to get the job done without saturating the network.
**Verbose Output with -v**
**Having trouble diagnosing a stalled transfer? Verbose mode spills all the behind-the-scenes details**
`scp -v /local/file.txt username@remote_host:/remote/path/`
This prints out each step, which can be a lifesaver for debugging.
## Common Pitfalls and Pro Tips
- **Check Your Paths**: Typos in file paths can lead to errors like “No such file or directory.” Always verify you’ve spelled everything correctly.
- **Permissions**: Make sure your user account on the remote server has write permissions in the target folder.
- **SSH Keys**: Setting up public key authentication (instead of password auth) makes scp both more secure and more convenient.
- **Security**: Even though scp uses SSH, always keep an eye on which users have access to your server. A strong SSH setup plus consistent updates is a must for safe file transfers.
## Why System Administrators Love **scp**
- **Reliability**: It rarely fails if your SSH credentials are in order and your network is stable.
- **No Third-Party Tools**: No need to install separate clients; scp comes standard on most Linux distros (and macOS).
- **Automation**: You can script scp commands (with SSH keys) for automated backups, deployments, or log transfers.
## Wrapping Up
When it comes to moving files around safely and easily, the **scp** command in Linux is a real MVP. It’s simple, gets the job done, and leans on SSH to protect your data in transit. Whether you’re archiving log files, distributing scripts, or just tinkering around with personal projects, scp is a staple tool you’ll want in your arsenal.
**Ready to try it out?** The next time you need to shuffle files between machines, open your terminal and give scp a spin. The secure, efficient transfer might just become your new go-to method - no extra steps, no third-party apps, just a single command that does it all. Happy copying!
---
## Academy LMS Review - A Powerful eLearning Plugin for Your WordPress Website
- URL: https://levamo.com/blog/academy-lms-review/
- Category: lms
- Author: Faisal Sarker
- Published: 2025-02-05
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is Academy LMS right for you? See our in-depth review now.
There is no shortage of WordPress LMS plugins such as Tutor LMS, LearnDash, and LearnPress that offer amazing features for building dynamic eLearning platforms. However, one platform gaining traction and popularity is [Academy LMS](https://academylms.net/).
In the next 10 minutes or so, we will take a closer look at its features and pricing, and share in detail what you can get out of using it. When we’re done, you’ll have a pretty good idea of how to create a fully functional LMS website using Academy LMS and the ever-important (but often underestimated) role of hosting in making it run smoothly.
**Quick tip**: to make the reading of this article more interactive, we suggest you give the [demo version](https://test.academylms.net/?_gl=1%2A14afevq%2A_gcl_au%2AMTQ2MDYzOTA0OC4xNzM4NzUxMjMx%2A_ga%2ANTk4ODE3MzAuMTczODc1MTIzMQ..%2A_ga_58FWH2EV94%2AMTczODc1MTIzMC4xLjEuMTczODc1MTI4MC4wLjAuMA..%2A_ga_NPQ6YPPJTP%2AMTczODc1MTIzMC4xLjEuMTczODc1MTI4MC4wLjAuMA..) a try and experiment with its multiple features as we go through the paces.
Here are all the points we will be covering in our Academy LMS review:
- How to install and set up Academy LMS
- How to use the frontend course builder and the backend analytics
- How to create quizzes, assignments, and exams using Drip Content Builder
- Pros and cons of Academy LMS
- Quick comparison of Academy LMS with other platforms
Before we start, we need to quickly sort out a couple of things first.
## Why Academy LMS?
Academy LMS is a new entrant in the highly competitive world of LMS plugins that doesn’t disappoint in terms of price and performance. Compared with other plugins that cost around $199 per year for a single-site license, Academy LMS provides the same features at only $119.
In our humble opinion, this is the most economical option to get started with your course website right away.
## What Do You Need To Build A Great LMS?
To get the most out of your LMS, you need a few things:
- Reliable web host provider
- Reputable LMS such as Academy LMS
- Responsive WordPress theme that suits your needs
The great thing about WordPress is that you don’t have to code anything to create an LMS, as the plugins offer everything for a beginner to get started.
For hosting, you want to go with cloud, such as [Levamo’s managed WordPress hosting](/), where you get 24/7 proactive security, integrated CDN, and resources that scale as you grow.
## Who is Academy LMS Best For?
Let's start this Academy LMS review with what it is particularly well-suited for:
- **Solopreneurs and small businesses** looking to create and sell online courses with minimal technical expertise.
- **Educators and trainers** who want a user-friendly platform to deliver their educational content.
- **Businesses incorporating training programs** such as employee onboarding or customer education.
- **Anyone prioritizing marketing and sales** with an option to monetize with multiple payment gateways via WooCommerce.
## Academy LMS Key Features At A Glance
Let’s take a quick look at the main features of this platform and how you can use them to create engaging online learning experiences:
- **Sandbox environment** - Test the platform without downloading or installing it on your server. The official website allows you to try the demo version, which is a great way to check if it is suitable for your needs before making a purchase.
- **Frontend Course Creation** - Create courses just the way you like via an easy-to-use user interface.
- **Drip Content** - Schedule when the course content is released to the students.
- **Course Progress and Tracking** - Let the students track their progress as they enroll in any course.
- **Awards and Certificates** - With a Certificate Builder, instructors can craft customized certificates for students who successfully complete their courses.
- **Quiz Builder** - Create quizzes and assignments that become a part of the student's progress for each course.
- **Live Classes** - Provide live sessions through Google Meet integration.
- **Course Monetization Options With Payment Gateway Integration** - Monetize your work by integrating multiple payment gateways such as Stripe and PayPal.

### Sandbox environment
Since you’re likely not ready to purchase a license at this point, you can leverage the live demo option to create new classes and quizzes and test the platform’s frontend and backend. To use the sandbox environment, go to the Academy LMS website and click **Try Admin Demo**.

The default username and password is “demo”. Once you log in, you will see the following screen with a dashboard that shows the number of enrolled courses, completed courses, total students, total lessons, total quizzes, and other options. In other words, this is where you get all the important statistics for courses.

To access the backend, click **Dashboard** by hovering the mouse on the ALMS Testing tab.

This will take you to the WP Admin area. Here you can see further statistics in more detail.

### Frontend Course Creation
Not everyone using WordPress is tech-savvy. Academy LMS understands this limitation and provides a front-end course creation feature that is easy to use for anyone with basic WordPress knowledge.

You can quickly create new courses by going to **Academy LMS > Courses > All Courses > Add New Course.** Add your **Course Title** and **Course Description**.
You can also set your course to **Free**, **Paid**, or **Public.** Once you are done with the setup, click **Publish** to launch the course on your website.
### Quiz Builder and Assessment Functionalities
What’s the point of using an LMS if it doesn’t come with a built-in quiz builder? Academy LMS’s quiz creator allows you to design unlimited quizzes of varying lengths, difficulties, and question types. To create quizzes, simply click **Quizzes > Add New Quiz.**

In a new pop-up window, there will be three steps for quiz creation. First, add the **Quiz Title** and **Description**. Click **Save & Continue**.

In the next step, click on **Add Questions+.**

Add the **Question Title** and select the **Question Type** from the drop-down list.

You can select from **True/False, Single Choice, Multiple Choice, Short Answer**, and **Image Answer**. In our case, we chose the **Single Choice** option, which requires the student to decide on the right answer for the question.

Once you are done, click on **Add Question.** In the third step, you will be shown the quiz settings. You can choose to hide or enable the question number, quiz time, time limit, and **Quiz Feedback Mode**. Once done with all the changes, click **Finish**.

To access a course from the student’s point of view, open up the course in a new window and click **Start Course**.

### Integration with WooCommerce for Monetization
Just like with every WordPress-based LMS, you can easily integrate WooCommerce with Academy LMS to enable monetization features. You can set a price for your courses and sell them by enabling payment gateways such as Stripe and Paypal. To do this, head over to **Settings > Payments, then** turn on WooCommerce next to **Select eCommerce Engine**.

### Content Drip and Scheduling Options
As a course creator, you need to have complete freedom on how you want the content to be published for the enrolled students. You can either make all the lessons and quizzes available if someone signs up for your course or schedule it with drip content.
The latter is an excellent option to make sure that students only reach a certain part of the course when they have completed specific prerequisites. To enable this feature, access course settings through the **Course Edit** option and then scroll down where you can see the following options:

Under the **Content Drip Types,** you can specify how you want to schedule your content:
- **Schedule course content according to the date** - Specify an exact date.
- **Content Accessible after X days from enrollment** - Specify the number of days after enrollment when lesson plans start becoming accessible.
- **Course content available sequentially** - Once the previous lesson plan is completed, the next one gets automatically visible.
- **Course content available after completing prerequisites** - Specify prerequisites to access content.
- **Content accessible after x days from topic completed** - Specify the number of days for content to be available once a topic is completed.
These options allow you to fully customize how you schedule and publish the course content.
### Certificate Creation and Gamification Elements
Did you know that you can assign certificates at the end of course completion for each student? Not only that, but you can change the look and feel of certificates by scrolling down under each Course through the main WP Dashboard until you get to the following:

Click **Change Certificate**.

In a new pop-up window, you can select a certificate style you like the most and then customize it accordingly.
## Value for Money
We have to talk about the price tag, even for a little bit.
One of the strongest aspects of Academy LMS is that it offers a good balance of features and affordability. Its pricing is competitive, considering the scope of marketing and sales tools it brings into the mix.
For just $119, you can get started with a 1-site license. The WooCommerce integration adds significant value for those already using or planning to use WooCommerce for e-commerce. So, if you’re not looking to splash out big bucks but still get the features you need, Academy LMS will be more than a fine choice.
## Benefits and Limitations of Academy LMS
Just like with every other LMS, there are good and bad things about Academy LMS that you need to consider before buying its license.
### Pros
- One of the most economical options for anyone starting as a course creator
- Lightweight and user-friendly interface
- Frontend course creator and quiz builder
- Ability to duplicate courses and quizzes to save time
- Optimized for faster load times
- Automatic and manual enrollments
- Ability to create unlimited courses with multiple instructors
- Course difficulty indicators assist students in deciding the right one based on their needs
- Seamless integration with Zoom for live classes and WooCommerce for payments
### Cons
- Free version has limited support and functionalities
- Tutor LMS has additional types of questions such as Matching Types that Academy LMS doesn’t offer
- Limited options as compared to other LMS platforms
## How Levamo Helps Get the Most Out of Your LMS
Running a dynamic LMS website using Academy LMS (or any other similar plugin) demands a powerful and reliable hosting environment to keep everything running like clockwork. Levamo’s [best managed WordPress hosting](/managed-wordpress-hosting/) is ideally suited for this task for several reasons, including:
### Blazing-Fast Speeds
With its dynamic content and user interactions, Academy LMS tends to get resource-intensive. This will be more apparent as your audience grows.
Levamo's optimized infrastructure, including SSD storage and advanced caching mechanisms, ensures lightning-fast loading times, providing an engaging learning experience for your students. This is crucial for reducing bounce rates and improving student satisfaction.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
### Integrated CDN
Serving course content including videos and large files tends to consume a lot of bandwidth. Levamo's integrated [free WordPress CDN](/cloudflare-cdn/) distributes your content across a global network of servers, resulting in fast delivery to students regardless of their locations.
### Guaranteed Uptime
Uptime is paramount for educational platforms where consistent access is a must. Levamo’s team of WordPress experts proactively monitors your site leading to maximum uptime. We handle the technical complexities, allowing you to focus solely on creating and delivering valuable content.
### Great Fit for Dynamic Websites
LMS platforms are dynamic by nature, constantly generating and updating content based on user interactions. Levamo's infrastructure is designed to handle such websites, providing the stability and performance needed for a seamless LMS experience.
By hosting your Academy LMS platform on Levamo, you can be confident that your courses will be accessible, fast, and reliable, providing an optimal learning environment for your students.
Also Read: [Managed Hosting for BuddyPress](/blog/buddypress-review/)
## Alternatives and Short Comparisons
- **[LearnDash](https://www.learndash.com/learndash-lms/)**: Powerful WordPress LMS plugin with advanced features like drip-fed content and gamification, but requires more technical knowledge to manage effectively.
- **[Tutor LMS](https://wordpress.org/plugins/tutor/)**: User-friendly and feature-rich LMS plugin that offers a good balance between ease of use and functionality.
- **[LifterLMS](https://wordpress.org/plugins/lifterlms/)**: Comprehensive LMS plugin that focuses on memberships and community building. It offers robust membership features, content protection, and integrations with popular membership plugins.
## Sell Your Expertise With This All-in-One WordPress LMS Plugin
If you’re just starting your LMS adventure (so to speak), we recommend going with Academy LMS to build and monetize online courses. While the plugin may have some limitations in advanced features compared to more complex platforms, its overall ease of use, wallet-friendly price, and focus on course sales make it a choice you won’t regret.
We hope this Academy LMS review was helpful and do let us know if you have any questions about it.
## Frequently Asked Questions

### What is Academy LMS, and how does it work?
Academy LMS is a platform for creating, managing, and selling online courses. Instructors upload content, organize lessons, and deliver them to students who can track progress and earn certificates. It's a web-based system accessed through any browser.
### Is Academy LMS free to use?
Yes. Academy LMS has a free version but with limited features and options. Start with the free version to get a feel of the platform, then opt for one of the paid plans to get the most out of this platform.
### How does Academy LMS compare to Tutor LMS?
Academy LMS is more affordable than Tutor LMS but the latter offers better customization options. The best choice depends on your specific needs.
### Can I integrate Academy LMS with WooCommerce?
Yes. Academy LMS integrates with WooCommerce, allowing you to use its e-commerce features for course sales, payments, and discounts.
### Does Academy LMS support multiple instructors?
It does, allowing different individuals to create and manage their own courses within the platform.
### What kind of support does Academy LMS offer?
Academy LMS provides support through documentation, email, live chat, and community forums.
### Does Levamo Offer Specialized Academy LMS Hosting?
Yes, Levamo offers specialized [LMS hosting services](/managed-lms-hosting/). It offers Academy LMS hosting, [Tutor LMS Hosting](/tutorlms-hosting/), just to name a few.
---
## Preventing DDoS Attacks: How Levamo Protects Your Website
- URL: https://levamo.com/blog/preventing-ddos-attacks/
- Category: website-security
- Author: Faisal Sarker
- Published: 2025-02-04
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
DDoS attacks are rising; see how Levamo protects your website from them.
The [number of ](https://blog.cloudflare.com/ddos-threat-report-for-2024-q4/)Distributed Denial-of-Service (DDoS)[ attacks grew by 53% in 2024](https://www.techmonitor.ai/technology/cybersecurity/cloudflare-blocks-21-3-million-ddos-attacks-2024-53-yoy-surge) compared to 2023, emphasizing the importance of preventing DDoS attacks to safeguard online infrastructure and ensure uninterrupted service.
If you are a website owner, this stat can sound horrifying.
The rise in DDoS attacks is not just concerning for corporations but also for small to medium-sized businesses, with e-commerce, LMS, and community sites among those targeted more often.
Unfortunately, the consequences of these attacks are immediate and very severe.
But that’s not the case if you use Levamo to host your website. Our hosting platform uses some of the most advanced techniques to save you from DDoS attacks.
In this post, we’ll dive into how DDoS attacks happen and how Levamo’s advanced protective measures ensure your site remains online and secure.
## Understanding DDoS Attacks
A DDoS attack aims to disrupt the normal operation of a website, server, or network. It does so by overwhelming the target with a flood of internet traffic at once. DDoS attacks use numerous compromised computers or devices, which then hit your website at the same time. These devices are controlled by the attacker, who directs traffic to the website.
When the amount of traffic reaches the capacity of the target website server, it simply stops working. This results in slow loading, unresponsiveness, and oftentimes downtime.
### Common Ways DDoS Attacks Happen
Here are some of the common methods of DDoS attacks, so you can get an idea of how exactly these hostile actions come about.
- **Large Volume of Attacks:** This is the most common DDoS attack in which the attacker targets the website with a sizable amount of traffic to consume the bandwidth. Once the bandwidth usage has peaked, legitimate traffic can no longer access the website or it becomes really slow or unresponsive.
- **Protocol Attacks:** These usually target specific network protocols or servers. This is dangerous because the requests can saturate the server’s connection tables, and as a result, legitimate traffic can’t make a connection with the server.
- **Application Layer Attacks:** The way it works is that the attacker mimics the behaviors of genuine users. However, they repeatedly hit the most resource-intensive pages of the website or make continued database requests, so your server resource gets exhausted.
### Consequences of a Successful DDoS Attack
The result of a DDoS attack can be quite devastating, depending on its intensity. In fact, for a successful application-layer DDoS attack, the [average cost of downtime is approximately $6,130 per minute](https://www.radware.com/multi-cloud-report-2023/). Let’s look in-depth at what can happen if your website is hit with a successful DDoS attack.
- **[Downtime](/blog/minimizing-website-downtime/):** The most direct result of a successful DDoS attack, downtime can last from a few hours to days. You will likely have to reach out to your hosting service provider and explain the issue, and they might charge you additional fines for their help (talk about adding insult to injury).
- **Lost Revenue:** In what is a natural turn of events, you lose out on potential revenue when you fail to deliver the usual user experience to your customers. This is particularly hurtful and scary for small businesses that simply can’t afford such a scenario to occur.
- **Reputational Damage:** Losing out on temporary sales is one thing, but getting a reputational hit is a whole other story. Facing downtime or having a slow or unresponsive website can damage your brand reputation beyond repair - to the point it permanently decreases your customers' trust in you.
## How Levamo Can Protect You From DDoS Attacks
Levamo is not just a [best managed WordPress hosting](/managed-wordpress-hosting/), but it is also a secure WordPress hosting. We understand just how disastrous DDoS attacks can be for your business. That’s why we employ a whole lot of features dedicated to preventing DDoS attacks from taking place.
Here are some of the measures we have taken to tackle DDoS attacks on our customers’ websites.
### 1. Advanced Traffic Filtering
Levamo provides a multi-level traffic-filtering solution that separates harmful requests from legal traffic. It is powered by a Web Application Firewall (WAF) and easily integrated with our state-of-the-art cloud infrastructure.
The filtering solution monitors the way users interact with your website in real time. It flags and segregates the traffic for further examination in case it identifies unusual activity, such as an abnormal number of requests coming from a single IP address or atypical header attributes.
**Why It Matters**
**This preventive approach ensures there is no possibility of downtimes or performance degradation as the traffic is filtered out before it can reach your website**. Hence, genuine visitors can always smoothly access your memberships, courses, or subscription services.
### 2. Real-Time Monitoring
Cyberattacks are not one-time events, as attackers change or amplify their tactics frequently. Levamo's DDoS protection package includes 24x7 monitoring of application-layer requests, bandwidth usage, and traffic patterns for DDoS prevention. Its two key elements are:
- **Anomaly Detection:** The automated anomaly detection systems scan for activity in incoming communications that doesn’t correlate to normal usage. This could be surges in requests to certain endpoints or spikes in failed logins.
- **Geo-Filtering:** Certain geographic regions can sometimes produce disproportionate levels of traffic. Levamo’s real-time monitoring identifies such trends, which could then apply geo-blocking or stricter rate limits as necessary to use and stop an in-flight attack dead in its tracks.
#### Why It Matters
Levamo’s real-time monitoring sees to it that your response time is quick whenever your website comes under a DDoS attack. That means our systems are scanning and ready to respond if a cyber attack starts in the middle of the night or on a holiday weekend. That early detection is often what separates a small, manageable problem from a major outage.
### 3. Rapid Response Mechanisms
You don’t want your website to suffer one second. Thankfully, with Levamo, it won’t since protection starts almost immediately against an ongoing DDoS attack. It includes:
- **Immediate Traffic Rerouting:** The traffic analysis result is automatically sent to our DDoS mitigation server to confirm if an attack is happening.
- **Auto-Scaling Resources:** If you think an attack can only be tackled by simply increasing bandwidth for some time or you don’t want any potential downtime at all, there is the option of [auto-scaling](/blog/cloud-auto-scaling/). Turning it on will immediately increase the bandwidth.
#### Why It Matters
By making the mitigation process as swift as possible, Levamo makes sure that your website is always active. Even if it faces downtime, it would be practically unnoticeable to your customers.
## Levamo: The Security-first WordPress Hosting
With Levamo at the hosting helm, you get a full suite of security features for battling menacing DDoS attacks, from fast response mitigation to advanced traffic filtering and real-time monitoring. As a [WordPress hosting with DDoS protection](/managed-security/), we deliver a complete set of future-ready tools and strategies to protect your WordPress website in every way possible.
**[Try Levamo’s secure WordPress Hosting today!](/managed-security)**
## Frequently Asked Questions

### 1. What is a DDoS attack, and how does it affect my website?
A DDoS attack is a way to make your website unavailable by redirecting a lot of traffic to it at once. It can cause downtime, slowness, and unresponsiveness.
### 2. How does Levamo detect DDoS attacks?
Levamo has real-time monitoring in place to detect any DDoS attacks.
### 3. Is DDoS protection included in all Levamo hosting plans?
Yes! All of Levamo's hosting services, including managed WordPress hosting, have DDoS protection. To make use of these security measures, you don't need to buy any add-ons.
### 4. Can DDoS attacks lead to data breaches?
DDoS attacks don’t directly lead to data breaches. However, they can be a distraction to a much larger attack to access the data.
### 5. How can I monitor my website for potential DDoS attacks?
With Levamo, you can monitor your website traffic straight from our intuitive dashboard. This way, you can keep an eye on any sudden traffic discrepancies and take measures if they seem malicious.
### 6. Can Levamo also protect MemberPress or BuddyPress sites from DDoS?
Whether you use Levamo as your [BuddyPress hosting](/buddypress-hosting/) or [MemberPress hosting](/memberpress-hosting/), it has the necessary mechanisms in place to protect your site from DDoS attacks.
---
## An In-Depth Review of Easy Digital Downloads (EDD) in 2025
- URL: https://levamo.com/blog/easy-digital-downloads-review/
- Category: ecommerce
- Author: Sunyyan Junaid
- Published: 2025-02-03
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Our 2025 EDD review helps you build a thriving digital product marketplace.
If you are considering creating an e-commerce website for digital goods, this Easy Digital Downloads review will teach you everything you need to know to maximize this valuable and versatile plugin.
There are plenty of plugins for creating e-commerce sites on WordPress, offering different ways of doing so. One standout choice for a budding online business is Easy Digital Downloads (EDD).
Designed to simplify the process of selling digital products (and physical ones, if need be), Easy Digital Downloads plugin comes with an intuitive design and purpose-driven features that will enable you to build a thriving marketplace.
## Why Do Digital Product Sellers Prefer EDD?
Unlike other e-commerce tools that try to balance physical and digital product sales, EDD is laser-focused on those selling e-goods, offering clarity, efficiency, and adaptability.
Sellers of e-books, software, music, and design templates appreciate its unrivaled simplicity. Unlike all-purpose solutions, EDD addresses all aspects of selling digital goods, including licenses and subscriptions.
The plugin comes with dozens of essential and optional features, and in most cases, you will be just fine with the Lite (Free) version. That said, the plugin’s functionality can be enhanced with integrations and extensions.
### Advantages Over Competitors
Here are three reasons why EDD is better than its competitors:
- **Purpose-Built Simplicity:** EDD specializes in the sale of digital goods. It basically works on the “set it and forget it” motto. Other plugins are more complex considering they cover all types of sales activity. You can learn more about this issue under “Comparison With Alternatives” heading.
- **Rich Customization:** Its robust ecosystem of extensions allows sellers to shape their stores exactly as they envision.
- **Community Connection:** EDD is backed by a community that supports and nurtures new ideas and approaches to digital commerce.
## Who Should Use Easy Digital Downloads?
While compiling this Easy Digital Downloads review, one of the biggest concerns we saw from the business owners while trying to sell anything online was the technical side of e-commerce.
EDD offers a powerful, secure, and customizable platform that does its best to empower users to efficiently manage their digital storefronts and deliver exceptional customer experiences. Plus, it’s **no code**. This means you can create automated processes without any coding (for the most part).
All of this makes EDD a great choice for anyone looking to sell digital products online. And when we say anyone, we really mean it.
Developers and SaaS providers use EDD for software licenses, plugins, and subscriptions, leveraging its licensing management and automatic updates.
Authors distribute e-books and digital publications securely, avoiding restrictions from mainstream retailers. Graphic designers market digital art, templates, and fonts using EDD’s file management and licensing features.
Content creators sell courses and educational materials through [LMS hosting](/managed-lms-hosting/) integrations, drip content, and recurring payments. Musicians and audio producers distribute tracks and podcasts with flexible pricing and bundling options.
Entrepreneurs and small businesses enjoy EDD’s customizable storefronts for selling consultations, resources, and exclusive content, while membership sites use them to create premium member areas.
Developers and agencies sell templates and plugins utilizing EDD’s APIs. Nonprofits and educational institutions share reports and materials securely, while publishers and filmmakers monetize subscriptions, articles, and video content efficiently.
All in all, building your own store with EDD instead of distributing goods on popular marketplaces like Amazon, Gumroad, and the like is a great and rather feasible idea, as it allows you to operate without being bound by the rules of these platforms.
Also Read: [CDN for eCommerce](/blog/cdn-for-ecommerce/)
## Key Features of Easy Digital Downloads

Just as architects rely on their toolkit, EDD equips sellers with everything they need to succeed. The plugin operates on a freemium revenue model, which means that the basic features are available for free, but advanced features are paid.
### Comprehensive Shopping Cart
Easy Digital Downloads offers a complete shopping cart system tailored for digital products. It supports both Stripe and PayPal payment gateways at no additional cost, enabling secure transactions for your customers. You can change the “call to action” button to fit your business needs.
Moreover, EDD has a fantastic built-in feature for reducing cart abandonment. It can “save” a shopper cart with a unique and temporary link, allowing potential customers to save and revisit their carts at their convenience. The system handles both registered users and guest checkouts, catering to diverse customer preferences.
Additionally, EDD protects business owners by requiring customers to agree to terms before finalizing their purchases. Collectively, these features make EDD a robust solution for efficiently managing digital product sales.
### Detailed Reporting
EDD stores every data point inside a sales funnel for you to see and act on. First up, you can export data in CSV for record-keeping and in-depth study.
Next, you can filter reports by specific dates and products, leading to a detailed analysis of sales performance over chosen periods. EDD also has a built-in tracking mechanism, giving you control over churn rates and helping to identify areas for improvement.
### Order & Customer Management
Through the intuitive dashboard, you can manage order statuses, ensuring accurate tracking of each purchase from initiation to completion. You can also create role-based control access and assign different roles to different team members, thus making certain that every member has the appropriate access level for managing orders and other store operations.
Sometimes, customers may ask you to modify details, and with EDD, you can do it with just a few clicks. The plugin also has advanced refund management capabilities, allowing your customers to receive their money back. The system records the transaction dutifully for transparent financial bookkeeping.
When it comes to customer management features, EDD assigns a unique profile containing a detailed record of their transactions and activities, along with a customized “Account” page. As a store owner, you can view, modify, or delete any customer profile.
### API Access
For most users, EDD is a delightfully easy, no-code solution for creating a store for digital products and services. However, the plugin does not lock store owners in if they have a technical need. The RESTful API facilitates the retrieval of information on products, customers, sales, and earnings, supporting both JSON and XML formats.
## Step-by-Step Guide to Setting Up EDD
Stepping into the world of EDD requires nothing more than an open mind and a clear focus. Here’s a step-by-step guide to setting up your first EDD store:
### 1. Installation
Begin your EDD experience within WordPress. Log in to your WordPress admin. From the dashboard, Navigate to **Plugins > Add New**, then search for ‘Easy Digital Downloads’ and activate it with one click. Alternatively, install [EDD through the official WordPress](https://wordpress.org/plugins/easy-digital-downloads/) plugin repo.
### 2. Configuring General Settings
It’s advisable to spend some time exploring the settings. Define your currency, configure payment gateways, and set download email templates that resonate with your brand’s voice.
### 3. Creating Your First Product
Head to **Downloads > Add New** and showcase your inner writer for the product description. Upload your digital file and set a suitable price.
### 4. Customising Your Store
Ideally, you want to create a storefront that resonates with your business’ identity. Choose from clean, modern layouts that offer ease of navigation (and a little bit of eye candy) for your customers.
### 5. Setting Up Extensions
Enhance your store’s abilities by incorporating extensions like recurring payments or email marketing integrations.
### 6. Launch and Reflect
With the setup complete, it’s time to launch. Pay attention to customer feedback - it’s a mirror reflecting your store’s vibe and potential for growth.
## Pricing

EDD offers flexible pricing, allowing you to start small and scale as you grow:
- **Free**: A generous option for new sellers exploring possibilities.
- **Personal Pass ($99.50/year)**: Great for small stores that need more commercial options.
- **Extended Pass ($199.50/year)**: Unlocks more advanced features, like Subscriptions, Advanced Marketing Tools, Advanced Payment Tools, etc.
- **Professional Pass ($299.50/year)**: Ideal for thriving businesses seeking unlimited possibilities.
- **All Access Pass ($499.50/year)**: Best for creating multi-faceted marketplaces with advanced automation.
## Extensions
There are two types of EDD extensions: Free and Paid. If you are looking to extend the functionality of your store with a free extension, just use the [‘Free’ filter](https://easydigitaldownloads.com/downloads/category/free/) on the [Extension Downloads](https://easydigitaldownloads.com/downloads/) page. Notable options include [Hide Downloads](https://easydigitaldownloads.com/downloads/hide-download/), [Terms per Product](https://easydigitaldownloads.com/downloads/terms-per-product/), and [Lock Download to IP](https://easydigitaldownloads.com/downloads/lock-downloads-to-ip/). A few themes are also included at no extra cost.
In case you are looking for a real boost, then investing in a few paid extensions might be the way to go. There are dozens of them, though you might want to check these out:
- **Recurring Payments**: Stay connected with your customers through [subscriptions](https://easydigitaldownloads.com/downloads/recurring-payments/).
- **All Access Pass**: Invite your customers to explore your [entire catalog for one fee](https://easydigitaldownloads.com/downloads/all-access/).
- **Email Marketing Integration**: Build [insightful connections with your community](https://easydigitaldownloads.com/downloads/category/extensions/email/) via tools like [Mailchimp](https://easydigitaldownloads.com/downloads/mailchimp/).
- **Zapier Automation**: [Automate your store](https://easydigitaldownloads.com/downloads/?download_s=zapier&action=download_search) with 5,000+ third-party web services for the ultimate power-up.
- **AffiliateWP**: Make your store grow by offering an [affiliate program with management](https://easydigitaldownloads.com/downloads/affiliatewp/) directly from your WordPress dashboard.
## Comparison with Alternatives
In the next few minutes, we’ll assess how EDD stacks up against two of the most popular e-commerce platforms: [WooCommerce and Shopify](/blog/woocommerce-vs-shopify/).
### EDD vs. WooCommerce
EDD is tailored specifically for selling digital products, such as software and e-books, while WooCommerce is a more “open-ended” e-commerce solution that supports both physical and digital products.
- **Setup and Usability:** EDD offers a more straightforward and intuitive setup for digital sales, making it easier for users who primarily sell digital goods. In contrast, WooCommerce tends to be more complex due to its extensive features and options.
- **Built-in Features:** EDD includes essential features for digital product management, like file access control and download limits, which are specifically designed for digital sales. While versatile, WooCommerce may require additional plugins to achieve similar functionality.
- **Customization and Extensions:** There are a lot of extensions and plugins for WooCommerce that can be used to make it more customizable and add extra features like inventory management and shipping choices. EDD has similar options, but its main goal is to boost sales of digital products.
- **Payment Processing:** Both platforms support various payment gateways, ensuring secure transactions. However, WooCommerce provides a broader selection of payment options, accommodating a wider range of business models.
- **Market Share and Community:** WooCommerce has a significantly larger user base, with over 61 million installations, making it one of the most popular e-commerce platforms globally. EDD, while smaller with around 2 million installations, has a dedicated community focused on digital products and specialized support.
### EDD vs. Shopify
EDD is primarily geared toward digital goods, while Shopify is a more encompassing e-commerce platform that caters to both physical and digital products.
- **Ease of Use:** EDD provides a straightforward setup for digital sales, making it user-friendly for those focused on online goods. Shopify is also rather user-friendly but offers a more extensive setup process due to its wide range of features and customization options. Also, Shopify is a “hosted” e-commerce platform with an “Acceptable Use” policy which controls what can be sold or not. On the other hand, EDD doesn’t have such restrictions, except as required by the hosting company or local laws.
- **Customization and Themes:** Shopify offers a variety of professional themes and a robust app store for additional functionalities, allowing for extensive customization of online stores. EDD has fewer themes and extensions due to its primary focus on digital product sales.
- **Payment Processing:** Both platforms support multiple payment gateways, but Shopify has built-in support for a broader range of payment options, including its payment processor, Shopify Payments - albeit with processing charges.
- **Inventory Management:** Shopify excels in inventory management for physical products, providing tools for tracking stock levels and managing orders. EDD focuses on digital product management, offering features like download limits and file access control.
- **Cost Structure:** EDD typically costs less for businesses focused solely on digital products, with fewer associated fees. Shopify, while offering a comprehensive package, can become more expensive due to monthly subscription fees and transaction fees based on the chosen payment gateway.
## EDD Websites Perform Best on Levamo Hosting
The foundation of digital success largely lies in the speed and reliability of your web host, as well as trust - all the qualities embodied by Levamo. If you are looking for [best managed WordPress hosting](/managed-wordpress-hosting/) for your EDD site, here are four good reasons why Levamo should be your EDD hosting partner:
- **LiteSpeed Caching**: Ensures a seamless purchasing experience, no matter how many customers visit.
- **Uptime Reliability**: Your store remains open 24/7, ensuring a stable user experience every time.
- **Auto-Scaling**: Fluid scalability that goes hand in hand with your store’s growth.
- **Global Reach**: Geographic limitations dissolve with Levamo CDN, which is available for free with all plans.
Although we have a dedicated [WooCommerce managed hosting](/managed-woocommerce-hosting/), that performs equally well with EDD Sites. Your site will be hosted on an optimized and managed WordPress environment with LightSpeed Enterprise, Object Cache Pro, and [free WordPress CDN](/cloudflare-cdn/). You’ll also benefit from powerful protection with services like Patchstack, Monarx, and free SSL.
If you need more convincing, how about a quick testimonial?
[The Happy Pear](/blog/the-happy-pear-customer-stories/), a health and wellness membership website built on WordPress, saw a monumental **performance improvement of 400% with Levamo. While it’s not a 100% apple-to-apple comparison, an [optimized WordPress hosting](/managed-wordpress-hosting/) environment makes a big difference in the performance of a plugin-based e-commerce site**.
That’s not all, as the Happy Pear experienced a second benefit: savings. ***Thanks to optimizations by Levamo, the hosting bill was reduced by 40%***!
Like what you see? Then give Levamo a go!
## Conclusion
The Best WordPress Plugin for Digital Downloads.
For those of you thinking of starting a business with online goods, EDD is the optimal WordPress plugin as the cost to get started is very low. The Core version (also known as ‘Lite’ or ‘Free’) is good enough to get the ball rolling. Once you get traction (fingers crossed), you can always level up to a paid plan.
We hope this Easy Digital Downloads review was helpful to you. And you can always let us know if you still have any questions.
## Frequently Asked Questions

### What types of products can I sell with Easy Digital Downloads?
Easy Digital Downloads is perfect for digital products, like e-books, courses, music, design templates, and so on. You can also sell subscriptions with recurring payments and licensable software with automatic updates.
### How does EDD compare to WooCommerce for digital sales?
WooCommerce is built for retail e-commerce, where store owners sell physical products. While it can be used for digital goods, it’s too complex. EDD is much easier, as it is purpose-built to serve e-commerce sites with digital assets.
### Is Easy Digital Downloads free?
Yes, Easy Digital Downloads is a free plugin that can be installed directly from the WordPress Plugin directory. However, EDD has paid plans with advanced features, like duplicate products, lead magnets, multi-currency support, multi-vendor marketplace, etc.
### What hosting requirements are needed for EDD?
If you have a WordPress website with EDD that generates income, then performance-optimized WordPress hosting with a LightSpeed server and advanced caching will be a great investment. Digital goods stores should be good at concurrency, stability, and scalability. Levamo is a great option if your store is facing any performance bottlenecks.
### Can I use EDD with payment gateways like PayPal or Stripe?
EDD has built-in support for Stripe and PayPal, even for the free version. The EDD Pro (paid) provides you with more options.
---
## Top 5 Bottlenecks and LMS Performance Optimization Techniques to Fix Them
- URL: https://levamo.com/blog/lms-performance-optimization/
- Category: lms
- Author: Faisal Sarker
- Published: 2025-01-31
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix slow LMS! Top 5 bottlenecks & optimization techniques revealed inside.
Learning never stops, but it certainly pauses when a learning management system (LMS) malfunctions. Since interactivity is at the core of these platforms, you should pick your LMS hosting carefully.
Similar to traditional schools, online courses need classrooms, and group assignments require active participation. Therefore, any LMS, big or small, should be powerful enough to host dozens (or hundreds) of users simultaneously.
Much like an e-commerce website, an online learning website is like a machine with many moving parts. All modules need to be in harmony to deliver the best results for both students and the teaching staff.
But that is not always the case. Fret not, as we’ll show you the 5 most common performance shortfalls that affect your website speed and LMS performance optimization techniques to fix them.
## Performance Bottleneck #1: Slow Page Load Times

Page load times indicate how long it takes for a web page to load and render all its elements in a visitor’s web browser. Any time exceeding the optimal threshold of 2-3 seconds is considered as “slow”.
Waiting is not a lot of fun, more so considering that LMS websites are generally subscription-based. Hence, paying and then waiting for the content to load can be frustrating for students.
So what’s causing the problem?
Unsupported themes, plugins, or page builders, for starters. Large media files without a good delivery system can also be the reason behind an LMS website’s slow performance.
### How to fix the slow page time issue
This is one of the most important ways for LMS performance optimization. Start by testing your website using the [Google PageSpeed Insights tool](https://pagespeed.web.dev/). The tool may seem technical at first, but Google has done a great job explaining performance issues on the results screen.
After the test is complete, you need to check for the following three vital insights:
- Largest Contentful Paint (LCP),
- Interaction to Next Paint (INP)
- Cumulative Layer Shift (CLS)
The LCP part is directly related to a webpage’s loading time. If it’s higher than 2.5 seconds, then you have some work to do.
To improve the delivery of media such as images, videos, JavaScript files, and HTML pages, use a Content Delivery Network (CDN) with clusters of servers spread over different geographical locations. Due to their global spread, CDNs reduce latency and boost delivery times, resulting in a better experience.
The size of your media files also matters. This is a separate topic that we cover in great detail under #3, so we’ll save it for later.
Suppose things do not improve after CDN implementation and content optimization. In that case, you need to check your theme, page builders, and plugins for any conflicts, preferably one by one. Every LMS platform provides a set of recommendations, especially for which themes work best. Use that as a guiding principle to enhance performance.
## Performance Bottleneck #2: Inefficient Database Queries
One of the most critical capabilities of an online learning website is its ability to serve concurrent users. If the database is not set up correctly, performance is hindered due to limited computing resources.
Inefficient querying is a significant contributor to database performance issues. Poorly written queries can cause the database to perform excessive work to retrieve data, which can increase I/O load and CPU usage.
Then, there is caching. Many LMS admins do not use the cache properly, and even when the cache is deployed, it’s not configured efficiently. Without a caching mechanism, the database is forced to fetch data from the disk repeatedly, which can lead to increased latency and decreased throughput, particularly under high load conditions.
### How to fix inefficient database issues
There are three solutions for better database efficiency:
- Object Caching
- Database Indexing
- Query Optimization
Object Caching temporarily stores crucial information for quick delivery. This practice reduces the load on the database and speeds up your LMS website. Without it, the server will keep asking the database for the latest content. When object cache is used, the server “stores” crucial information for a defined period and “recalls” when needed.
You can further improve things through Database Indexing.
By indexing the database, the search for required information is quicker. Database indexing is organized in a defined manner to enable quick retrieval.
Lastly, Query Optimization is all about creating efficient “routes” to retrieve or modify data. This requires improving the efficiency of SQL queries executed by a database management system. Simply put, if the database is a library with thousands of books, then the data index is the book catalog, and Query Optimization tells how to find a particular book.
By working on your database, you can minimize the processing time and effort required for data retrieval and modification. This optimizes your website for better concurrency.
It is always a great idea to invest in a load-testing tool to check how concurrent your website is. The insights from the load test will inform you on the right steps for your LMS.
## Performance Bottleneck #3: Media-Heavy Content Delivery

[Some studies suggest](https://www.insivia.com/2023-saas-marketing-report/) viewers retain 95% of the information from a video, while only 10% is retained from a text version. Consequently, success-focused online learning websites frequently opt for video content to enhance their users’ educational journey.
However, there is a risk of slowing down the page load time.
### How to fix the media-heavy content delivery issue
Being media-heavy should not be a hurdle for an online education website. The latest compression standards for videos and images allow LMS platforms to stay “lean”.
At the moment, H.264 works great for video and supports screen resolutions from standard definition (SD) to 4K and beyond. It is widely supported for nearly all types of devices and browsers. Newer standards like H.265 (HEVC) or AV1 are also available.
WebP performs exceptionally well for images and produces up to 30% smaller file sizes without any compromise on image quality. It supports both lossy and lossless compression, as well as transparency (like PNG) and animations (like GIF). Most modern devices display WebP files without any issues. Due to smaller sizes, WebP indirectly contributes to lower energy consumption, which means using it is better for the planet.
Of course, when you are using heavy media on your LMS, you should implement a CDN to reduce latency and support concurrency. Levamo has free Levamo CDN available with all of its hosting plans. Furthermore, you are free to integrate popular CDN solutions through an intuitive dashboard.
## Performance Bottleneck #4: Scalability During Traffic Spikes
A traffic spike is a sudden event with increased user activity, though planned campaigns can also cause traffic spikes. For an online education website, the ability to handle such upticks is essential. That said, most academies plan only for scheduled events and often overlook sudden occurrences.
During a traffic spike, a site’s performance slows down if the infrastructure is not adequately planned or lacks load-balancing capabilities. Single-server setups are bound to go down due to infrastructural limitations, whereas multi-server setups can break down if the load is not distributed evenly.
### How to fix traffic spike issues
In situations where your platform encounters an abrupt surge in user activity, such as during a live webinar or the launch of a popular course, managing traffic flow becomes a priority to maintain functionality and user satisfaction.
Due to its dynamic nature, an LMS always benefits from an [auto-scaling setup](/blog/cloud-auto-scaling/), preferably on multiple servers with a load balancer. Auto-scaling ensures that your website keeps on going by scaling up server resources or adding more servers. In the same manner, an auto-scaling environment scales down when the flow of traffic decreases.
If your LMS is on a multi-server configuration, a load balancer ensures that the traffic is distributed so that no servers are overloaded.
Consider Levamo’s fully [LMS hosting services](/managed-lms-hosting/) for creating impactful learning environments. We understand what it takes to create a successful LMS website since we prioritize high availability. With auto-scaling and load-balancing features included in every plan for seamless operations, your site will keep running even during high-traffic times.
## Performance Bottleneck #5: Security-Related Matters

Wherever there is ample traffic, there is a chance of a cyber attack. When online academies cheap out on their hosting environment, they are open to different types of online threats, like [DDoS attacks](/blog/preventing-ddos-attacks/).
While SSL integration is now universally available with hosting providers, some online schools fail to set up their SSL certificates correctly. In doing so, they also risk reputational damage.
### How to fix security-related matters?
When picking a reliable hosting provider for your LMS, always check the platform’s security features. For instance, Levamo has robust defenses against online threats, including free built-in SSL certificates and management, powerful DDoS prevention, and automatic backups.
In addition, having a sound backup policy is like a good insurance package. In case of any untoward event, your backups will save you from many embarrassments.
## How Levamo can improve the performance of your LMS website

At Levamo, we aim for top grades when it comes to managed hosting. This is why we go above and beyond for all our clients. Online education is an area of our expertise.
By leveraging the power of LiteSpeed Enterprise (a high-performing web server with robust security and scaling) with AWS-powered scalable infrastructure and advanced caching, learning websites see dramatic results when they work with us.
**Case in point:** English Pro Tips achieved a 300% improvement in page load time. With more than 35,000 students from every corner of the world, the BossBuddy-powered learning community takes advantage of all the LMS website speed features of Levamo to deliver courses with interactive quizzes, video lessons, expert strategies, and model answers.
*“I wanted to be with a hosting provider that understood dynamic membership and eLearning websites,”* expressed Eli Hardie, founder of English Pro Tips.
Want more proof? After moving to Levamo, TCM not only saw significant improvements in BossBuddy and LearnDash performance, but they also got customer complaints down to ZERO!
*“All the caching features set specifically for dynamic sites (OP Cache, Object Cache, Redis, Litespeed Cache) really improve performance,” *shared Dr. Yair Maimon, renowned clinician and Managing Director of TCM Academy.
## Level Up Your LMS Experience
It does not matter if you are looking to improve LearnDash performance or seeking guidance for Tutor LMS speed optimization; the issues and solutions provided in this article apply to all LMS platforms.
And it all begins with a good hosting partner. From an optimized hosting stack to advanced caching and [free WordPress CDN](/cloudflare-cdn/), your LMS will be set up for success in the academic world with Levamo.
[Start a free trial now ](https://my.levamo.com/start)to experience up to 10X faster LMS hosting!
## Frequently Asked Questions

### What are common LMS performance issues?
Slow performance, inadequate handling of concurrent users, inefficient database management, lack of caching, and absence of CDN and load balancing are common LMS performance issues.
### How can I optimize my LMS website for speed?
Start by testing your web pages using the Google PageSpeed Insights tool. Focus on resolving LCP issues to optimize LMS performance and boost speed by implementing CDN, caching, auto-scaling, load balancing, content and database optimizations, and security enhancements.
### What hosting features are essential for LMS platforms?
When choosing a hosting partner for your LMS, make sure they offer caching mechanisms, CDN availability, auto-scaling with load-balancing, robust security practices with regular offsite backups, and exceptional after-sales support.
### How does a CDN improve LMS performance?
CDNs, or Content Delivery Networks, are interconnected networks of servers spread across the world that deliver content based on a visitor’s location. Delegating content delivery to a CDN significantly improves performance. Latency and server load are reduced, and users access content faster, which boosts satisfaction.
### What is Object Caching, and how does it benefit LMS platforms?
Object Caching is a practice of storing frequently required data in memory instead of fetching it from the disk every time. When it’s in use, the system first checks if the data is available in the cache before contacting the database. Object Caching has a positive effect on LMS performance optimization as data is retrieved or modified more quickly with less computing resource usage.
### How can I ensure scalability for my LMS during peak usage?
To ensure scalability, you should deploy your LMS on an auto-scaling setup with a load balancer.
---
## How To Avoid Common Server Problems and Errors?
- URL: https://levamo.com/blog/common-server-problems/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2025-01-31
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix server errors! Learn to avoid 500, 404, & other common problems.
Imagine getting up to check your website analytics and seeing that half of your pages won't load. Frustrating right? Server problems might feel like digital barriers that impede both your workflow and your visitors' experience. Fortunately, most of these issues are easier to fix than you may think, especially if you have a bit of know-how and a dependable hosting solution like Levamo.
## So, What Counts as a “Server Error” Anyway?
A **server error** means the server hosting your site ran into an issue and couldn’t load the page your visitor wanted to see. These mishaps often come with various status codes like **500**, **404**, **503**, and so forth that can leave you puzzled. The silver lining? Each code offers a clue about what went wrong.
Below, we’ll highlight some of the usual culprits, explain why they happen, and suggest a few ways to steer clear of them in the future. You’ll be back to smooth sailing in no time.
### 1. The Dreaded 500 Internal Server Error
**What Is It?**
**A [500 error](/blog/fix-the-500-internal-server-error/) is the classic “oops, something went wrong” message that websites occasionally cough up**. It’s a general-purpose alert telling you the server encountered an unexpected problem.
**Why It Happens**
- Misconfigured permissions or software bugs
- Insufficient memory or disk space on the server
- Faulty plugins (in the WordPress realm) or mismatched themes
**Quick Fixes**
- First, take a peek at your site’s error logs. They might point directly to the glitch.
- If you’re using WordPress, try deactivating any recently installed (or suspicious) plugins.
- Contact your hosting provider if the error persists. Sometimes, they’ll discover deeper server-side issues that need a tech guru’s attention.
### 2. The Infamous 404 Not Found
**What Is It?**
When a user clicks on a link and the server returns a “404,” it basically means, “That page you’re looking for? It doesn’t exist here,” or ‘[The Requested URL Was Not Found on This Server](/blog/the-requested-url-was-not-found-on-this-server/)’
**Why It Happens**
- Typos in the URL
- Pages that were moved or deleted without proper redirects
- Outdated internal links within your own site
**Quick Fixes**
- Double-check for spelling errors (seriously, it happens more often than you might think).
- Update or remove broken links, and use 301 redirects for any pages you’ve recently re-homed.
- If you keep running into the same 404 on a page that definitely exists, try clearing your browser cache or visiting from an incognito window.
### 3. 503 Service Unavailable (a.k.a. “Server’s Taking a Break”)
**What Is It?**
**A 503 means the server couldn’t handle your request at that moment - maybe it’s overloaded, or maybe it’s down for maintenance**.
**Why It Happens**
- Surge in traffic (hey, maybe that viral post is paying off!)
- Routine server maintenance or updates
- Limited server resources, like CPU and RAM
- [Distributed Denial of Service (DDoS)](/blog/preventing-ddos-attacks/) attacks overwhelm your site
**Quick Fixes**
- Wait a few minutes and refresh. If it’s a temporary traffic spike, it might fix itself.
- Check your hosting provider’s status page for maintenance announcements.
- Scale up your hosting resources if you regularly see heavy traffic. **Levamo** can help you manage surges more gracefully with load-balancing options.
### 4. 403 Forbidden: When Access Is Off-Limits
**What Is It?**
**A 403 error occurs when the server recognizes your request but won’t let you in**. Think of it like a locked door you don’t have the key for.
**Why It Happens**
- Improper file or folder permissions
- Security settings or firewall rules that block certain IP addresses
- Missing authentication credentials for restricted areas
**Quick Fixes**
- If you’re the site owner, verify file and directory permissions (e.g., 755 for folders and 644 for most files).
- Ensure any required login credentials are correct and up to date.
- Occasionally, server-level firewalls might need tweaking; your hosting provider can guide you here.
### 5. 502 Bad Gateway: The Relay Race Fumble
**What Is It?**
**When one server acts as a gateway or proxy and receives a confusing response from an upstream server, you get a [502](/blog/502-bad-gateway-error/)**.
**Why It Happens**
- The upstream server is down or overloaded
- Misconfigured proxies, load balancers, or DNS settings
- Network connectivity issues between servers
**Quick Fixes**
- Refresh the page to see if it’s just a momentary hiccup.
- Check DNS and proxy configurations; typos or outdated IP addresses can lead to a 502.
- If you’re using a load balancer, make sure it’s distributing traffic correctly. Simple restarts can sometimes solve a world of problems.
## How to Keep Server Errors at Bay
While it’s impossible to guarantee a completely error-free existence, you can reduce the odds with these habits:
- **Regular Updates:** Keep your WordPress core, themes, and plugins updated. Outdated code is a magnet for compatibility issues and security risks.
- **Resource Monitoring:** Watch your hosting dashboard for memory usage, CPU spikes, or disk space shortages. Spotting a problem early is half the battle.
- **Security First:** Employ strong passwords, two-factor authentication, and firewall rules. A major chunk of server issues stems from malicious attacks or vulnerabilities.
- **Backups, Backups, Backups:** Mistakes happen. When you have a recent backup, you can roll back to a stable version with far less stress.
- **Scalable Hosting:** If you notice regular slowdowns or frequent 503 errors, it might be time to upgrade your hosting plan. **Levamo** offers flexible solutions to handle those busy days without missing a beat.
## Final Word
Server errors can be exhausting, but they don’t have to ruin your life or your website’s reputation. By understanding the basic causes behind each error code and following a handful of best practices, you’ll be ready to handle common issues like a pro. Plus, if you’re hosting with **[Levamo](/)**, you’ve got a built-in safety net: a dependable infrastructure paired with a support team that has your back.
Ultimately, no one likes encountering roadblocks online, least of all your visitors. A little proactive maintenance goes a long way toward preventing headaches for you and ensuring a pleasant browsing experience for everyone else. If you ever feel stuck or suspect a deeper server problem, remember you’re not alone. Reach out to us at **Levamo** anytime, and we’ll help you get things sorted faster than you can say “error code.” Good luck, and keep on building that awesome web presence!
---
## Understanding SSL Certificates and Their Role in Website Security
- URL: https://levamo.com/blog/ssl-website-security/
- Category: website-security
- Author: Faisal Sarker
- Published: 2025-01-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
SSL certificates protect your website and user data. Read on to learn how.
The internet is a dog-eat-dog world, which means all kinds of predators constantly threaten your website. You will have to deal with hackers trying to steal data and probing your website for vulnerabilities. Fortunately, you can solve this problem with the following three magical letters: SSL. Investing in SSL website security ensures your site remains protected against hackers and cyber threats.
As a website owner, you do not want sensitive information like payment details and passwords to be accessible to everyone. To secure sensitive information, you must take advantage of SSL certificates. If you do not know about SSL certificates and how they are important for securing your website, this blog will be right up your alley.
## What are SSL Certificates? The TLDR
SSL stands for Secure Sockets Layer, but what does this term mean? Don’t let the fancy term intimidate you, as it simply acts as a bodyguard for your website.
When users visit your website, an SSL certificate will create an encrypted connection between the web server and your website. This is a fundamental part of SSL website security, ensuring private and sensitive data remains safe from cybercriminals.
For the nerds out there, SSL encrypts data using private and public keys.
Here is some interesting and relevant data regarding SSL certificates to consider regarding its importance:
- [Over 317 million SSL certificates](https://sslinsights.com/ssl-certificates-statistics/) are being used around the globe at this time, highlighting its increased adoption rate over the years.
- An estimated **82.9% of websites now use valid SSL certificates**, an increase of 18.5% from five years ago, showcasing the growing importance of secure web connections.
- Interestingly, out of all browsers, **93.2% of Chrome users** spend their browsing time on HTTPS-secure websites, indicating widespread reliance on SSL for secure browsing.
- The global SSL certificate market was valued at $187 million in 2023 and is projected to **grow by 12% every year until 2030**, reaching a value of $413 million.
- The **United States leads in SSL adoption**, with an astounding 34 million certificates, followed by Germany with 14 million certificates.
## Why are SSL Certificates Necessary for your Website?
Understanding SSL certificate importance is crucial if you want to build a secure and trustworthy website. If your website is your castle, SSL website security acts as your military, defending against cyber threats and unauthorized access. SSL certificates are a must-have feature if you are serious about website security.
SSL certificates play a crucial role in things like [eCommerce site optimization](/blog/ecommerce-site-optimization/), directly impacting user trust and conversion rates. Online shoppers are more likely to complete purchases on secure websites, and the following stats highlight why SSL is essential:
- **84% of online shoppers abandon purchases** if data is not sent over secured connections.
- 85% of online shoppers stay clear of unsecured websites.
- 79% of consumers would not go through with a purchase if they were met with a “*Not Secure*” warning.
If you are still unconvinced about the importance of SSL certificates, here are a couple of factors to consider:
- SSL certificates are an indication that your website is trustworthy and reliable with immediate visual cues, i.e., **https://** instead of **http://** in the URL. According to a GlobalSign survey, **28.9% of users look for the green address bar** as a sign of security.
- Google loves secure websites and uses **HTTPS as a ranking factor**, meaning if you have better security, your SEO will benefit, too.
- If your website handles sensitive information, an SSL certificate is mandatory for meeting **data protection laws like GDPR**.
Fun Fact: **[Over 95% of web traffic is encrypted on Google since 2020](https://www.researchgate.net/figure/Trend-of-encrypted-traffic-across-google-2_fig1_359309522)**, and if you are not a part of this percentage, you are practically living in the Stone Age.
## Why Choose Hosting with SSL Certificates
Your SSL certificates are worthless if your hosting provider does not support them. For this reason, it is important to find hosting that supports SSL certificates out of the box.
When choosing the [best managed WordPress hosting](/managed-wordpress-hosting/) with SSL certificate, like Levamo, you ensure your website is automatically secured with SSL without any manual setup. This means you do not have to worry about setting up SSL or renewing it every year manually. Your hosting provider will take care of all the technical stuff, allowing you to focus on things that matter.
### How to Ensure SSL is Set Up on Your Website Properly?
Wondering how to make your website SSL secure?
- After buying hosting, you can check if the SSL certificate is installed using an SSL checker tool.
- Once your SSL certificate is live, your site should automatically [redirect users from HTTP to HTTPS](/blog/redirect-http-to-https/).
## The Role of SSL in WordPress Malware Protection
It is no secret that WordPress websites are easy targets for hackers and cybercriminals, despite adopting a [WordPress website security checklist](/blog/wordpress-best-security-practices/). Third-party integrations, themes, and plugins are easy to exploit, but an SSL certificate can do wonders in protecting your website from the most common types of attacks.
### Phishing Protection
SSL makes it difficult for phishers to copy and replicate your website. The padlock icon on the browser will be a clear indicator for your users that they are in the right place.
### Protection against Man-in-the-Middle Attacks
SSL encrypts all data between the server and the user, preventing anyone from listening in. Even if an attacker is stalking your website, they can’t read any of the information that is being exchanged.
### Stronger Security against Malware
SSL certificates prevent hackers from gaining access to your website, and when used with other malware protection plugins, your website will be impenetrable. This ensures you do not have to go through the hassle of adopting and implementing a website security checklist, after which you would need to update regularly, too.
### Brute Force Attack Prevention
Combine SSL with two-factor authentication or plugins like Sucuri or Wordfence to benefit from multi-layered protection, bolstering brute force attack prevention and preventing hackers from using automated tools to guess your passwords.
**Also related**: [TLS vs. SSL](/blog/tls-vs-ssl/)
## Tips and Tricks to Make the Most of SSL Certificates

Now that your SSL certificate is up and running, you may wonder what comes next. The good news is you can take a few additional steps to make the most of this handy feature. If you do not know where to begin, check out the following tips and tricks:
### Check SSL Certificate Regularly
If you want to check website SSL security, don’t assume your SSL certificate is always active. Just because your SSL certificate is installed does not mean you can kick back and relax. SSL certificates have expiration dates, and if you do not want to risk your [website flashing “Not Secure” to visitors](/blog/how-to-fix-https-not-secure-message-in-chrome/), you must use tools like SSL Test to check the health of your SSL certificate.
### Redirect All Traffic to HTTPS
Installing SSL is not going to be enough; you must ensure every page is encrypted. For this reason, you will need to set up a 301 redirect to send visitors to HTTPS versions of pages automatically.
This little trick will ensure every bit of your traffic is secure, and reliable managed hosting providers, like Levamo, make this job easier with built-in tools that handle redirects for you.
### Optimize SSL Performance
SSL encryption can take a toll on your website’s performance, but you can solve this by enabling HTTP/2. This newer version of the HTTP protocol speeds up SSL connections, and since most modern servers and browsers support it, there is no reason why you should not enable it.
SSL is a powerful tool, yes, but it is not the only solution for all your security needs. You will need to use it in collaboration with other practices for website protection like:
- Regularly update WordPress, WordPress themes, and plugins.
- Use stronger passwords and advise your users to do the same.
- Enable two-factor authentication for your admin login page.
## Why Choose Levamo for your Website’s Security?
By now, you have a better understanding of **SSL website security** and how it plays a vital role in WordPress malware protection. But let’s talk about something more exciting - your cloud hosting platform. Many website owners fail to realize the importance of choosing a reliable and dependable managed hosting solution provider, thus doing more harm than good in the long run.
If you opt for a top-tier cloud hosting provider like Levamo, here is how you will benefit:
- You will not have to install SSL certificates on your own, as it will be taken care of for you.
- Slow websites are intolerable; visitors hate them, Google hates them, and they will affect your conversion rates. Levamo offers blazing-fast speeds, allowing you to keep your visitors and Google happy.
- Features like built-in malware scanning, automated backups, etc., ensure your website is secure from all kinds of threats.
- Levamo offers continuous secure monitoring, meaning their team will keep their eyes peeled for vulnerabilities. If a threat is detected, you will get the latest patches sooner rather than later.
- As your website grows, your security needs will evolve as well. Whether you are expanding your business or adding new features, Levamo will keep up with your pace. Levamo has a robust infrastructure that can handle high traffic, offers extra security measures, and much more.
If you are serious about your website and its security, you should opt for Levamo, the [secure WordPress hosting](/managed-security/). Levamo offers features like automated features, built-in SSL certificates, etc., essentially taking care of the nitty gritty so that you can pay attention to things like growing sales, improving customer support, and working on your digital marketing efforts. So what are you waiting for, Christmas?
[Try Levamo Today for Free](https://my.levamo.com/start)
---
## What is DNS vs. Nameserver ? An Indepth Guide for Beginners
- URL: https://levamo.com/blog/nameserver-vs-dns/
- Category: hosting
- Author: Salman
- Published: 2025-01-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Demystifying DNS & nameservers! Grasp key concepts for web navigation.
Have you ever wondered what’s actually happening behind the scenes when anyone type a domain name into your browser? The answer lies in two key players that power the internet’s “phonebook” system: **DNS (Domain Name System)** and **Nameservers**. Although they work together, each one has a unique role. Think of DNS as the big-picture framework for translating domain names to IP addresses, while Nameservers operate at a more focused level, storing and serving those DNS records for each domain.
## What Is Domain Name System (DNS)?
The Domain Name System, [DNS], is the backbone of online navigation. When anyone enter a domain name like www.example.com into your browser, DNS goes into action, converting that human-friendly domain name into a numerical IP address (like 192.0.2.1) that servers and networks use to locate each other.
**How DNS Works**
**DNS operates like a massive, distributed phonebook spread across servers worldwide**. It includes:
- **Root DNS Servers**: The top of the DNS hierarchy, directing queries to the correct top-level domain (TLD) servers (like .com, .net, etc.).
- **TLD Servers**: These store information for domains within that specific TLD and point you toward the server that holds the final DNS records.
- **Authoritative DNS Servers**: Contain the actual, definitive [DNS records](/blog/dns-records-explained/) for your domain (A records, MX records, etc.). When a DNS resolver (often your ISP or a third-party DNS provider) queries your domain, these authoritative servers provide the IP address or other relevant data.
### Why DNS Matters
You don’t have to memorize IP addresses. It’s a worldwide system that ensures domain names remain unique and consistent across the internet. DNS supports A, MX, TXT, CNAME, SPF, DKIM, and more. Each record type serves a specific purpose, from directing web traffic to email routing and security validations.
**Common DNS Record Types (Quick Overview)**
- **A Record**: Points a domain to an IPv4 address (the “street address” for your website).
- **MX Record**: Specifies mail servers responsible for receiving emails on behalf of your domain.
- **TXT Record**: Stores text-based data (often for verification or security like SPF, DKIM).
- **[CNAME Record](/blog/multiple-cname-records/)**: Creates an alias from one domain to another.
- **SPF Record**: Part of email authentication to specify which servers can send emails from your domain.
- **DKIM Record**: A cryptographic signature verifying the authenticity of your emails.
## What Is a Nameserver?
A **nameserver** is a specialized server responsible for storing and serving the DNS records specific to one or more domains. When someone types in a domain name, the DNS resolver checks the domain’s associated nameservers to find the correct IP address.
**How Nameservers Operate**
- **Authoritative vs. Recursive**
An **authoritative Nameserver** has the definitive DNS data for a domain, while a **recursive Nameserver** searches other servers if it doesn’t have the information on hand.
- **Zone Files**
Each Nameserver stores a “zone file” for the domains it governs, detailing all DNS records (like A, MX, CNAME). These files tell the internet how to handle requests for those domain names.
### Why Nameservers Matter
Every domain has at least two Nameservers to provide redundancy and ensure uptime. You can switch your domain’s Nameservers if you prefer a specific DNS hosting provider, which can be beneficial for performance, security, or advanced features.When you purchase hosting - like **Levamo’s managed WordPress** solution - your hosting provider will often direct you to point your domain to their Nameservers so everything is configured correctly.
## Key Differences Between DNS and Nameservers
Although they’re closely related, DNS and Nameservers have distinct roles in the domain name resolution process.
**Role and Function**
- **DNS**: Serves as the global framework that translates human-readable domain names to IP addresses.
- **Nameserver**: Functions as the “custodian” of DNS records for a particular domain, responding with the IP address or other DNS data when queried.
**Level of Operation**
- **DNS**: Operates at a macro level across the internet, maintaining a vast, hierarchical system of domain-to-IP mappings.
- **Nameserver**: Works at a micro level, hosting the specific records for individual domains or subdomains.
**Hierarchy and Interdependence**
- **DNS**: A globally distributed system that includes root servers, TLD servers, and authoritative servers.
- **Nameserver**: Exists within the DNS hierarchy, typically designated as authoritative for the domain(s) it manages.
**User Interaction**
- **DNS**: End users interact with DNS every time they navigate the web, but this happens behind the scenes.
- **Nameserver**: Users might see or edit their Nameserver details when setting up a new domain or changing hosting providers.
**Impact of Failure**
- **DNS System Failure**: Can cause widespread internet disruptions because domain names will fail to resolve globally.
- **Nameserver Failure**: Usually impacts only the domains tied to that specific Nameserver, leaving the rest of the internet unaffected.
**Redundancy and Backup**
- **DNS**: Inherently distributed and robust; multiple servers hold copies of DNS data.
- **Nameservers**: Domains typically have at least two. If one fails, the secondary Nameserver ensures continued domain resolution.
**Security Considerations**
- **DNS**: Vulnerable to spoofing or cache poisoning attacks if not protected.
- **Nameservers**: Can be targeted by [DDoS attacks](/blog/preventing-ddos-attacks/) or unauthorized access attempts. Techniques like DNSSEC help secure both DNS and Nameservers against tampering.
## Why This Matters for Levamo (WordPress Hosting)
If you’re hosting your WordPress site on **Levamo**, these distinctions matter for a few reasons:
- **Site Reliability** → Pointing your domain to the correct Nameservers ensures traffic is routed to Levamo’s servers. If Nameservers are misconfigured, visitors might see error pages or land on old hosts.
- **Performance Optimization** → DNS response times can affect initial connection speed. A well-optimized DNS setup can slightly reduce page load times, which is crucial for a smooth WordPress experience.
- **Email and Security** → Proper DNS records (like SPF, DKIM, and DMARC) help authenticate email sending, preventing spam issues. Levamo can guide you through these record configurations to keep your domain’s reputation clean.
## Common Questions About DNS and Nameservers
- **Do I Need to Change My Nameservers When I Switch Hosting?**
**Yes, typically. If you move your website to Levamo, you’ll update your domain’s Nameservers to those provided by Levamo. This ensures all DNS records (A, MX, etc.** ) point to the new hosting environment.
- **Can I Use Third-Party DNS While Still Hosting on Levamo?**
**Absolutely. Some users prefer services like Cloudflare or a premium DNS provider**. You’d simply update your DNS records on that platform to reference Levamo’s server IP.
- **What Happens If I Don’t Set Up the Right DNS Records?**
**Your site could be unreachable, or your emails might bounce**. The correct DNS configuration is essential for every aspect of site functionality, from domain resolution to email deliverability.
- **How Do I Check My DNS or Nameserver Settings?**
**Tools like[ WhatsMyDNS](https://www.whatsmydns.net/) or command-line queries (dig, nslookup) can show you which IP addresses or Nameservers your domain is pointing to**.
## Mini Glossary
- **Resolver**: The “middleman” between your computer and DNS servers, finding the IP address for the domain you type in.
- **Zone File**: A text file on a Nameserver that contains DNS records for a domain.
- **Apex Domain**: Your main domain (e.g., example.com), as opposed to a subdomain (blog.example.com).
- **DNS Propagation**: The time it takes for DNS changes to spread globally, often up to 48 hours.
## Final Thoughts
DNS and Nameservers might seem interchangeable, but they aren't. DNS is the overall system that translates domain names into IP addresses all over the internet. Nameservers hold and serve the DNS records for individual domains. These two systems working together keep your website (and the entire internet) functioning like a well-oiled machine.
For a managed WordPress hosting service like **Levamo**, a solid understanding of DNS vs. Nameservers helps you troubleshoot domain issues, set up email authentication, and ensure your site remains accessible worldwide. By configuring your DNS records accurately and pointing your domain to the correct Nameservers, you’ll minimize downtime, deliver a smoother experience for your visitors, and protect your brand’s reputation.
Still have questions about domain setup or how to optimize your DNS for better performance? Feel free to explore more guides on[ Levamo’s Support Page](https://support.levamo.com/) or reach out to our team. We’re here to help you navigate the nuts and bolts of running a successful WordPress site - no matter your level of technical expertise.
---
## Faster Speeds & Better Security: Levamo CDN is Finally Here
- URL: https://levamo.com/blog/faster-speeds-and-better-security-rapyd-cdn-is-finally-here/
- Category: news
- Author: The Levamo Team
- Published: 2025-01-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo CDN brings global caching, lower server load, and optional WAF protection.
> *Note: This post was originally published January 2025 as "Faster Speeds & Better Security: Rapyd CDN is Finally Here" when our platform was called Rapyd Cloud. We've since rebranded to Levamo. The product details below remain accurate - only the brand name has changed.*
From day one, we promised a built-in content delivery network to speed up and protect your sites. Now, it's here, bringing global caching, reduced server load, and an optional Web Application Firewall (WAF) for even stronger security.
## What's New?
- **Faster Load Times**: The Levamo CDN caches your site's static assets and delivers them from servers closer to your visitors, reducing latency and improving performance.
- **Stronger Security**: The optional Web Application Firewall (WAF) helps protect your site against malicious attacks, including DDoS, SQL injection, and cross-site scripting (XSS).
- **Lower Server Load**: Offloading static content to the CDN reduces bandwidth usage and keeps your origin server free to handle more complex operations.
## How It Works
1. The Levamo CDN is available for managed primary domains and can be enabled directly from your dashboard.
2. Navigate to **Settings > Domains** in your Levamo dashboard.
3. Find your Primary Domain, click the three-dot menu, and select **Turn on Levamo CDN**.
4. (Optional) Enable WAF protection for added security.
5. Click **Activate CDN** and wait for setup to complete.
## Learn More
To learn more about the Levamo CDN and domain management with Levamo, check out our [Levamo CDN Guide](https://support.levamo.com) and our [Domains & CDN help collection](https://support.levamo.com).
It's been a long time coming, and we appreciate your patience. Now, you can finally experience the performance and security boost of the Levamo CDN!
---
## How to WooCommerce Get Orders Completed for This Year
- URL: https://levamo.com/blog/woocommerce-get-orders/
- Category: ecommerce
- Author: Salman
- Published: 2025-01-29
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Get your WooCommerce completed orders for this year, the easy way.
Managing a WooCommerce store Business can sometimes feel like a hassle, especially when trying to keep up with orders. One common challenge is figuring out woocommerce get completed orders of this year for analysis, reporting, or even just to see how your store is doing.
Having that information at your fingertips goes a long way toward understanding what’s selling best, how your promotions are performing, and where you might want to fine-tune your strategy.
The year's completed order data is crucial for spotting trends, automating processes, and improving your store's overall performance and this guide will walk you through how to woocommerce get orders for the current year in WooCommerce programmatically.
## Why Should You Track Completed Orders?
Imagine this: You’re running a WooCommerce store, and it’s December. The holiday rush is over, and you’re gearing up for next year. You want to see how many orders you fulfilled this year so you can:
- **Evaluate Performance**: Did you process more orders than last year? Which months were the busiest?
- **Plan Ahead**: If February was a slow month, maybe you should run a promotion next year.
- **File Taxes**: Completed orders are directly tied to revenue, so having this data ready is a lifesaver for bookkeeping.
And here’s an interesting stat: [WooCommerce powers **over 28% of all online stores globally**](https://blogonyourown.com/woocommerce-statistics/), and many store owners process thousands of orders every year. So, if you’ve ever felt overwhelmed managing your orders, you’re not alone!
## How to Woocommerce Get Completed Orders of This Year
WooCommerce provides a powerful API that lets you query order data with ease. Here’s how you can use it to get all completed orders for the current year.
### Step 1: Define the Date Range
First, set up the start and end dates for the current year. This helps you filter only the orders completed within this timeframe:
```php
$start_date = date('Y-01-01 00:00:00'); // Start of the year
$end_date = date('Y-12-31 23:59:59'); // End of the year
```
### Step 2: Query WooCommerce for Completed Orders
Use WooCommerce's wc_get_orders() function to fetch the data. Here's the code:
```php
$args = array(
'status' => 'completed',
'date_completed' => array(
'after' => $start_date,
'before' => $end_date,
),
);
$orders = wc_get_orders($args);
```
### Step 3: Display the Orders
Once you've got the data, you can loop through it to display details like the order ID, customer name, and completion date:
```php
foreach ( $orders as $order ) {
echo 'Order ID: ' . $order->get_id() . '
';
echo 'Customer Name: ' . $order->get_billing_first_name() . ' ' . $order->get_billing_last_name() . '
';
echo 'Completed on: ' . $order->get_date_completed()->date('Y-m-d H:i:s') . '
';
}
```
## Real-Life Scenarios: Why This Data Matters
Let’s put this into perspective with some real-world examples:
### 1. Tracking Growth Over the Year
Imagine you run an online store selling handmade candles. In January, you only completed 50 orders, but by November, you’re processing 500 orders a month. By fetching completed orders for the year, you can easily visualize this growth and use it to motivate your team - or yourself!
### 2. Preparing for Tax Season
If you’ve ever scrambled to calculate your annual revenue during tax season, you know the stress it can bring. By querying completed orders, you can instantly get the data you need for accurate tax filings.
### 3. Identifying Seasonal Trends
Let’s say you notice that most of your orders are completed in the last quarter of the year. This insight could lead you to ramp up marketing efforts in October or stock up on inventory earlier to meet demand.
## Fun WooCommerce Order Stats
Did you know:
- The average WooCommerce store processes **1,200 orders annually**?
- Around **15% of online orders are completed within the first hour** of being placed?
- Stores offering faster fulfillment see a **67% increase in customer satisfaction**?
These stats highlight just how important it is to track and analyze your completed orders.
## Advanced Example: Exporting Completed Orders for Analysis
Want to take this a step further? Here's how you can prepare your completed orders for export (e.g., to a CSV file for reporting):
```php
function export_completed_orders_this_year() {
$start_date = date('Y-01-01 00:00:00');
$end_date = date('Y-12-31 23:59:59');
$args = array(
'status' => 'completed',
'date_completed' => array(
'after' => $start_date,
'before' => $end_date,
),
);
$orders = wc_get_orders($args);
if ( empty($orders) ) {
echo 'No completed orders found for this year.';
return;
}
foreach ( $orders as $order ) {
echo 'Order ID: ' . $order->get_id() . '
';
echo 'Customer Name: ' . $order->get_billing_first_name() . ' ' . $order->get_billing_last_name() . '
';
echo 'Completed on: ' . $order->get_date_completed()->date('Y-m-d H:i:s') . '
';
echo 'Total: $' . $order->get_total() . '
';
}
}
```
## Conclusion:
By leveraging wc_get_orders() in WooCommerce provides store owners and developers with an efficient way to filter and retrieve woocommerce get orders. This functionality is crucial for monitoring sales trends, generating financial reports, and refining marketing strategies based on real transaction data and see what actually works at your store.
For businesses seeking robust and scalable solutions, hosting WooCommerce on high-performance platforms like Levamo ensures seamless order processing, superior site speed, and uninterrupted eCommerce operations.
---
## The Best Plugins for WooCommerce in 2026
- URL: https://levamo.com/blog/best-plugins-for-woocommerce/
- Category: ecommerce
- Author: Shahzeb Ahmed
- Published: 2025-01-29
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find top WooCommerce plugins to boost sales and streamline your store in 2026.
In this article, we have listed the best plugins for WooCommerce stores. From coupons to payments and compliance, these plugins help you maintain and scale up your store for maximum output.
The eCommerce industry is thriving day by day, and so is the competition. To stay competitive in the long run, you’ll need some advanced tools and solutions.
Without further ado, let’s get started.
## 1. WebToffee WooCommerce Smart Coupons

[WooCommerce Smart Coupons](https://www.webtoffee.com/product/smart-coupons-for-woocommerce/ "nofollow") by WebToffee is an advanced coupon plugin. It enables the creation of different types of coupons and [discount rules](https://www.webtoffee.com/woo-discount-rules/ "nofollow") for your WooCommerce store. Using this plugin, you may create offers of all kinds. This includes BOGO offers, fixed and percentage-based discounts. Moreover, to also includes quantity and price-based discounts, gift cards, store credits, etc.
This plugin lets you set condition-based discounts and advanced coupon usage restrictions. For instance, you can create special offers, like discounts for customers who have spent $100 or more. This flexibility will enable you to customize promotions to fit your store's needs.
The plugin will provide cart abandonment coupons. These will give customers exclusive offers to finish their purchases. Other targeted promotions will include sign-up discounts for new customers. It can help you run offers based on purchase history and free shipping coupons.
**Pricing:** The [WooCommerce Coupons](https://wordpress.org/plugins/wt-smart-coupons-for-woocommerce/ "nofollow") plugin is available for both free and paid versions. You can access the paid version at $89 per year for a single site license.
## 2. WC Vendors
[WC Vendors](https://www.wcvendors.com/ "nofollow") is the plugin to reach for when you want to turn your WooCommerce store into a full multi-vendor marketplace. Once it's active, independent sellers can register, list their own products, and manage their own orders from a dedicated dashboard, while you set commission rates and approve who joins. It handles all the marketplace essentials - vendor storefronts, automated commissions, and payouts - without locking you into a hosted platform or charging per-sale fees. That makes it a strong fit for anyone building a marketplace on WordPress who wants to keep full control of their store.
**Pricing:** The core WC Vendors Marketplace plugin is free. Paid plans with advanced features start at $99.
## 3. Bit CRM
[Bit CRM](https://bit-crm.com/ "nofollow") is a complete sales CRM that runs inside your WordPress website. With it, you can manage leads, contacts, companies, deals, products, and invoices from one dashboard, along with tasks, meetings, calls, and notes. There is no external tool to log into and no per-seat monthly fee.
Native WooCommerce sync makes Bit CRM a strong choice for store owners. Once you connect your store, every buyer is added to your Contacts automatically, and each new order keeps that contact updated. Your WooCommerce products flow into the CRM too, so you can add them as line items in any deal or invoice without manual entry. When a client pays through a Bit CRM invoice, the WooCommerce order is updated on its own.
Bit CRM also has native integrations with Bit Integrations, Bit Flows, and Bit Form. That means you can use CRM records as a trigger or action, connect them to hundreds of outside platforms, and turn any form submission on your site into a lead automatically.
You also get a Kanban deal pipeline, a visual workflow builder for automating follow-ups, a branded client portal where customers view their own invoices and meetings, IMAP email tracking, role-based access, and multi-currency support. It runs only in the WordPress admin, so it does not affect your front end or conflict with your theme or page builder. This makes it a strong option for WooCommerce stores that want to track customers and close deals without paying for a separate CRM platform.
**Pricing:** Bit CRM plans start at $149 one-time for a single site, $299 one-time for 5 sites, and $299 one-time for unlimited sites.
## 4. WP Sell Services
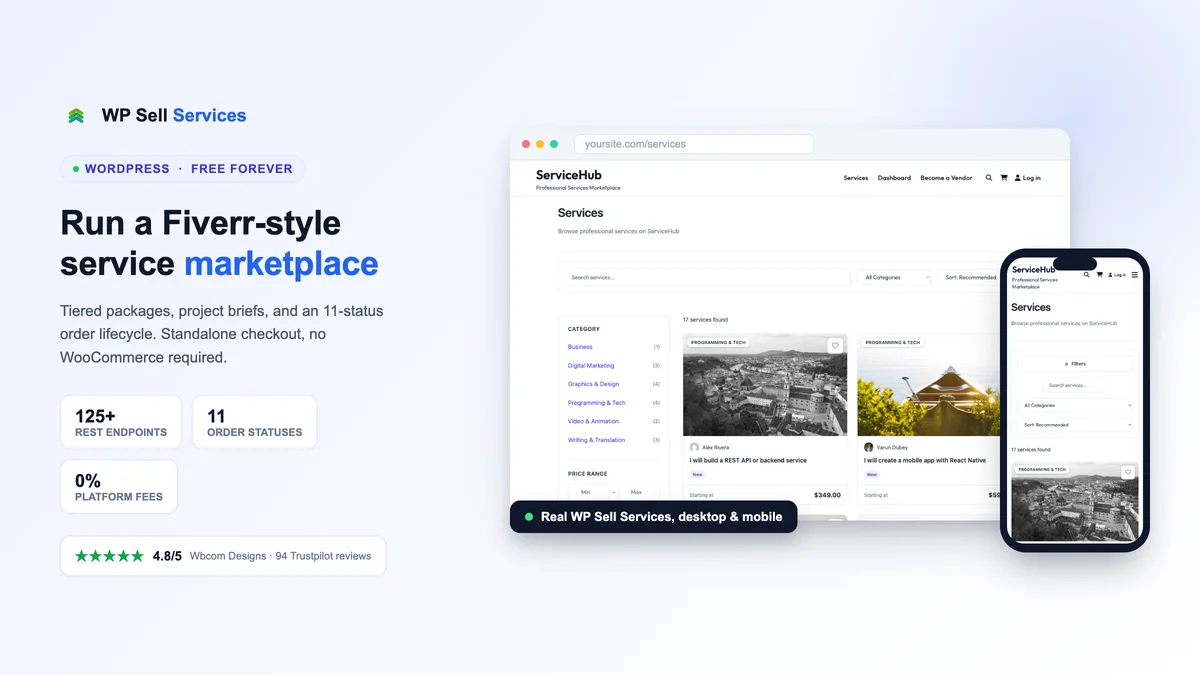
[WP Sell Services](https://wpsellservices.com/ "nofollow") turns WordPress into a Fiverr- and Upwork-style service marketplace, and it does it on its own, with no WooCommerce required. It ships its own cart and checkout (Stripe, PayPal, and offline payments), so you can run a complete service marketplace with zero WooCommerce installed. Vendors list tiered packages (Basic, Standard, Premium) for buyers to browse and purchase directly, or buyers can post a project brief and collect proposals from vendors instead. Both modes ship free and can run side by side.
Because a service sale needs more than a standard product page, WP Sell Services includes a full order lifecycle: requirements collection, delivery, revisions, and dispute resolution. That is the part marketplace plugins built for physical products first (Dokan, WCFM, WC Vendors) tend to feel retrofitted around when you bend them toward services. If you are already running WooCommerce and want to fold a service marketplace into the same storefront, the Pro version adds WooCommerce as an optional checkout path with 100+ payment gateways, alongside the plugin's own standalone Stripe and PayPal checkout.
**Pricing:** WP Sell Services is free forever for the core marketplace (both marketplace modes, the full order lifecycle, standalone checkout, disputes, and commissions). Pro (WooCommerce integration, vendor analytics, automated payouts, and white-label) starts at $99 per year for a single site.
## 5. CartCue

[CartCue](https://www.userelements.com/cartcue-woocommerce-automation/ "nofollow") is a WooCommerce automation plugin built to recover lost sales and follow up with customers automatically. It handles the repetitive marketing tasks that store owners rarely have time for, like abandoned cart reminders, post-purchase follow-ups, and win-back sequences for lapsed buyers, all running quietly in the background.
What sets CartCue apart is how readable its automations are. Every workflow follows a plain-language structure: When something happens, And certain conditions are met, Wait a set amount of time, Then take an action. So instead of wrestling with abstract nodes and connectors, you simply describe the customer journey the way you'd say it out loud. For example, when a cart is abandoned, and the order value is over $50, wait one hour, then send a reminder email.
This approach makes CartCue especially friendly for store owners who aren't developers, while still being powerful enough to chain multi-step campaigns. It comes with a built-in email builder with a live audience preview, so you can see exactly who a campaign will reach before it sends. A guided setup wizard gets your first automation running quickly, and related workflows can be grouped together to keep your store organized as your automations grow.
For WooCommerce stores that want focused, store-specific automation without the bloat of a general-purpose platform, CartCue is a lightweight and intuitive option.
**Pricing:** CartCue is available in free and paid versions. The premium version starts at $59 per year for a single site.
## 6. Wholesale Suite
[Wholesale Suite](https://wholesalesuiteplugin.com/ "nofollow") adds a complete B2B and wholesale sales channel to your WooCommerce store. With it active, you can set wholesale-only pricing, create tiered price levels for different customer roles, and require minimum order quantities - all running alongside your normal retail store. It also includes wholesale order forms, tax handling, and a dedicated registration page, so approved buyers get a checkout built for bulk purchasing. This makes it a great option for stores that want to sell to both retail shoppers and business customers from a single site.
**Pricing:** Wholesale Suite offers a free plugin (Wholesale Prices Lite), with paid plans for the full B2B feature set starting at $299.
## 7. Popup Builder by OptinMonster

Using [OptinMonster](https://wordpress.org/plugins/optinmonster/ "nofollow"), you can create countless varieties of popups on your WordPress eCommerce site, including floating bars and gamified spin-a-wheel popups.
These popups work well on mobile devices and desktops. What sets OptinMonster apart from other pop-up builders is its ability to create subtle popups. This design enhances user experience without being intrusive.
**Pricing:** OptinMonster is free to use, however, it also comes in a paid version. The paid version will cost you $7 per month.
## 8. **Gift Cards for WooCommerce Pro**
[](https://wpswings.com/product/gift-cards-for-woocommerce-pro/ "nofollow")
[Gift Cards for WooCommerce Pro](https://wpswings.com/product/gift-cards-for-woocommerce-pro/ "nofollow") offers customizable templates. You can design gift cards to match your brand. QR codes and barcodes make redemption simple, both online and in-store. Users can also personalise their gift cards by adding text messages or images, making each one special for the recipient.
Delivering gift cards is easy. Customers can send them by email, WhatsApp, SMS, or as a downloadable PDF. So, for birthdays, holidays, or special occasions, this plugin makes gifting simple and fun. It helps boost sales and build customer loyalty.
**Pricing:** Gift Cards for WooCommerce Pro offers three plans to fit your needs: **$89** for a single site, **$169** for up to 5 sites, and **$329** for up to 10 sites. If you want a free option, try the Gift Cards for WooCommerce Lite plugin. It has basic features to help you get started. You can upgrade to the Pro version for advanced options, multiple delivery methods, and better management tools to boost your sales.
## 9. WooCommerce Gift Cards

The [WooCommerce Gift Cards](https://www.webtoffee.com/product/woocommerce-gift-cards/ "nofollow") plugin allows you to create attractive gift cards and vouchers on your WooCommerce store. You can create an unlimited number of gift cards on your store and allow your customers to purchase, redeem, and share with their loved ones. This can help facilitate customers sending out gift cards as gifts to others in celebration of birthdays, anniversaries, and similar special occasions.
In addition, your customers can even schedule gift cards and add personalized messages for delivery on any given date.
The plugin has more than twenty pre-designed templates that ensure a hassle-free and enjoyable gifting experience. You can offer instant refunds in the form of store credits for returned products.
**Pricing:** The [Gift Cards for WooCommerce plugin](https://wordpress.org/plugins/wt-gift-cards-woocommerce/ "nofollow") is available for free on WordPress. However, for advanced features, custom templates, as well as an unlimited number of gift cards, the premium version has to be purchased, starting at $99 for one site.
## 10. WPForms - Easy Form Builder for WordPress

[WPForms](https://wordpress.org/plugins/wpforms-lite/ "nofollow") is a great choice for a reliable form builder on your WordPress eCommerce site. This easy-to-use tool lets you create and add different forms. You can make contact forms, payment forms, donation forms, and booking forms.
It allows you to build forms with the drag-and-drop form builder. So, it is possible to make changes in forms by customizing without any code. It simply lets you drag elements into place to create forms.
WPForms offers over 2000 ready-made templates. These help you create mobile-friendly and SEO-optimised forms quickly. The forms are well-protected against spam. This is thanks to integrations with hCaptcha, Google reCAPTCHA, and Cloudflare Turnstile.
This plugin also integrates with the most famous platforms, like Google Sheets, Zapier, HubSpot, and PayPal Commerce, which ensures seamless functionality on your website.
**Pricing:** WPForms is available for free. However, there's also a paid version, which you can attain at $49.50 per year.
## 11. GDPR Cookie Consent Plugin

The [GDPR Cookie Consent](https://www.webtoffee.com/product/gdpr-cookie-consent/ "nofollow") plugin helps you meet key privacy laws like GDPR, CPRA, and LGPD. It creates a custom cookie banner on your WordPress site. This lets visitors choose to accept or reject cookies.
This plugin disables all third-party cookies and scripts unless users approve them. It also lets visitors choose specific cookie categories based on their purposes.
An integrated cookie scanner finds and counts cookies on your site. This plugin supports Google Consent Mode v2. It lets you use Google Ads and analytics services smoothly while staying compliant with regulations. It also works with IAB TCF and other consent standards from Google for sites with third-party ads.
**Pricing:** The plugin is priced at $69 per year for a single site.
## 12. Mailchimp for WooCommerce

One good choice for setting up email marketing for your online shop is [MailChimp](https://wordpress.org/plugins/mailchimp-for-woocommerce/ "nofollow"). Among the top-rated WordPress email marketing tools, this one allows specific emails to be sent to customers.
This tool also impacts how you handle abandoned carts. It can send automated emails based on what users do, such as reminders about stuff left in their carts. That reduces cart abandonment and increases sales on your website.
You can track results and segment your audience to make running your email campaigns easier. As a result, you can create beautiful pages to promote store items, sales, or contests.
**Pricing:** Mailchimp for WooCommerce has a free version and a paid version, which vary depending on the plan.
## 13. WooCommerce PayPal Payments

With the WooCommerce [PayPal Express](https://www.webtoffee.com/product/paypal-express-checkout-gateway-for-woocommerce/ "nofollow") plugin, you can link the PayPal payment gateway to your WooCommerce store. This lets you accept payments through PayPal, Venmo, SEPA payments, and major debit and credit cards.
Your store will follow PayPal's security standards. This includes encryption and multi-factor authentication for payments. This add-on lets customers check out directly from a product page. They can also enjoy express checkout with PayPal.
You can authorise payments from your customers at the time of purchase. Then, you can capture the payment when the products are delivered. The WooCommerce PayPal Payments plugin lets you issue full and partial refunds to customers. It also allows credit card payments from non-PayPal users.
**Pricing:** This [WooCommerce Paypal](https://wordpress.org/plugins/express-checkout-paypal-payment-gateway-for-woocommerce/ "nofollow") plugin is available in free and paid versions. The paid version has a price tag of $59 for a license issued on a single site.
## 14. Customer Reviews for WooCommerce

One of the best tools to attract new customers to your eCommerce store is social proof. Customer reviews are a strong form of social proof. The [Customer Reviews for WooCommerce](https://wordpress.org/plugins/customer-reviews-woocommerce/ "nofollow") plugin lets you send automated, personalized emails to customers. This aims to encourage reviews for their recent purchases.
This would bring more reviews and ratings on the products offered in your store. Some features added with the review plug-in include images, voting systems, and Q&A on the product pages.
It provides a 'click to chat' integration through which you can send review reminders on WhatsApp manually. It offers an on-site review form so that customers may drop reviews easily. You can give exclusive discounts to your customers to encourage them to drop reviews. It also allows importing and exporting reviews on your website.
**Pricing:** Customer Reviews for WooCommerce is a free plugin.
## 15. WooCommerce Product Feed

The [WooCommerce Google Product Feed](https://www.webtoffee.com/product/woocommerce-product-feed/ "nofollow") is a leading plugin for WooCommerce. It helps you create optimised product feed files for popular sales channels. These include Google Shop, Facebook Shop, Instagram Shop, TikTok, Pinterest, Bing, Idealo, and more. You can set the plugin to update the feed data automatically. This keeps your product listings accurate and up to date across all sales channels.
This plugin provides extra filtering options. You can create category-specific feeds or choose to add or exclude certain products based on your needs.
It also lets you make customizable data feed files for any sales channel. The plugin has both free and paid versions. The premium version offers advanced features for better control over filtering and scheduling.
**Pricing:** The [product feed plugin](https://wordpress.org/plugins/webtoffee-product-feed/ "nofollow") for WooCommerce is available in free and paid versions. The pricing for the paid version starts at $89 per year for a single site.
## 16. SaveTo Wishlist
[SaveTo Wishlist](https://wordpress.org/plugins/saveto-wishlist-lite-for-woocommerce/ "nofollow") adds fast, friendly wishlist functionality to your WooCommerce store. Once it's active, shoppers can save the products they love and come back to buy them later, which is one of the simplest ways to turn browsers into repeat customers.
It works for logged-in customers and guests alike, so no one has to create an account just to build a wishlist. Shoppers can keep multiple wishlists, revisit their saved items across visits, and pick up right where they left off. For store owners, that means more returning visitors and more recovered sales without any extra day-to-day work.
**Price:** SaveTo Wishlist is a free plugin.
## 17. WooCommerce Product Recommendations

Want to offer product suggestions to your customers and hence increase sales? Make use of the [Product Recommendations](https://www.webtoffee.com/product/woocommerce-product-recommendations/ "nofollow") for WooCommerce plugin. It increases the average order value through suggestions relevant to the customer.
This product recommendations plugin will work well with any product type. Whether it is simple or grouped, variable, or even subscription-based. All of them are guaranteed to be actionable as they remove the out-of-stock products.
You can choose which products to recommend and decide when and where to show them. It offers pre-built recommendation templates. Such as upsells, cross-sells, frequently bought together, top-rated, etc.
The pricing will start at $89 per year for the premium version, considering the added advanced options. Still, the free version of the [WooCommerce Product Recommendations](https://wordpress.org/plugins/wt-woocommerce-related-products/ "nofollow") should offer all the necessary features.
## 18. Google Analytics for WooCommerce

The [Google Analytics for WooCommerce](https://woocommerce.com/products/woocommerce-google-analytics/ "nofollow") plugin is an advanced solution to understand the performance of your store. It tells you which channels bring in the most traffic, such as search, social, or email. You can then change your marketing strategies based on this data.
It tracks customer behaviour and offers detailed info on transactions, traffic, and revenue for each product. It also connects with enhanced eCommerce analytics. This link provides insights into product views and actions in the cart. This data can boost your store's performance, even if changes are necessary.
**Pricing:** Google Analytics for WooCommerce is available for free to use.
## 19. Checkout Field Editor (Checkout Manager) for WooCommerce

[Checkout Field Editor](https://wordpress.org/plugins/woo-checkout-field-editor-pro/ "nofollow") is one of the top WooCommerce plugins for a WooCommerce store owner because it allows you to customize and streamline your checkout process.
It allows you to add up to 20 types of custom checkout fields and to add validation, thus ensuring that you collect all the information you need from the customers.
**Pricing:** Checkout Field Editor comes in a free version and a paid version. It can be purchased at $49 per year as a paid version.
## 20. Advanced Shipment Tracking for WooCommerce

[Advanced Shipment Tracking](https://www.zorem.com/ast-pro/ "nofollow") for WooCommerce plugin makes order fulfillment and shipping management easy. Compatible with ShipStation, WooCommerce Shipping, Ordoro, Royal Mail Click & Drop, Dear Inventory, Ali2Woo, Printful, and many other similar platforms.
It tracks shipments by item and shows all tracking numbers on one dashboard. This plugin also offers customizable email templates and responsive tracking widgets. You can create a custom shipping workflow based on different order statuses.
This plugin also comes with a Shipment Tracking API. You can also add third-party services for managing shipments.
**Pricing:** A paid version is offered at $129 per year.
## 21. Discount Rules and Dynamic Pricing for WooCommerce

The [WooCommerce Dynamic Pricing & Discounts](https://wordpress.org/plugins/easy-woocommerce-discounts/ "nofollow") plugin is one of the top free WooCommerce plugins. It gives you a competitive grounding concerning sales in your store because you can add any options in your store for discount purposes.
These include store-wide volume as well as quantity discounts. It also has automated rules, which automatically trigger the discounts for a better shopping experience. Additionally, this plugin offers promotions such as BOGO offers, category deals, and percentage-off deals. It even has price tables for items by quantity, bringing the buyer to order more.
Furthermore, weight-based shipping and scheduled shipping are supported, along with customizable discount rules with cart weight, item count, or specific date ranges.
**Pricing:** The WooCommerce Dynamic Pricing and Discounts plugin is free at the WordPress repository.
## 22. Gift Cards for WooCommerce Pro

[Gift Cards for WooCommerce Pro](https://wpswings.com/product/gift-cards-for-woocommerce-pro/ "nofollow") comes with customizable templates, so you can design gift cards accordingly that match your brand. The QR codes and barcodes ensure easy redemption online or in-store. Users can personalize their gift cards by adding text messages or images, making each one truly special for someone.
Delivering gift cards is simple - customers can send them via email, WhatsApp, SMS, or as a downloadable PDF. Whether for birthdays, holidays, or special occasions, this plugin makes gifting convenient and engaging, helping you drive more sales and customer loyalty.
**Pricing:** Gift Cards for WooCommerce Pro are available in three pricing plans to suit different business needs. It is **$89** for a **single site**, **$169** for up to **5 sites**, and **$329** for up to **10 sites.** However, if you're looking for a free option, you can try the Gift Cards for WooCommerce Lite plugin. It offers essential features to get you started. Pro version for advanced customization, multiple delivery options, and enhanced management tools to maximize your sales potential.
## 23. CrawlWP SEO

Using the [CrawlWP WordPress SEO Plugin](https://crawlwp.com/ "nofollow"), WooCommerce store owners can ensure their products, categories, and pages are discovered by search engines faster and more reliably.
Getting your products indexed quickly can be the difference between making a sale and losing it to a competitor. CrawlWP automates the process of notifying major search engines like Google and Bing whenever a product is added or updated, so you never have to wait days or weeks for your listings to appear in search results.
What makes CrawlWP especially valuable for WooCommerce websites is its built-in [SEO performance dashboard](https://crawlwp.com/article/overview-of-seo-stats-feature/ "nofollow") powered by Google Search Console. It provides real-time insights into how your products and pages perform in search, including total impressions, clicks, average rankings, and keyword CTRs. This data is shown directly in your WordPress dashboard, allowing store owners to optimize titles, descriptions, and product content based on actual search behavior.
Another powerful feature for WooCommerce users is the [index status checker](https://crawlwp.com/article/understanding-seo-indexing-feature/ "nofollow"). CrawlWP shows you which of your products and pages are indexed by Google, and which aren’t. This is critical for store owners who want to ensure their most profitable or seasonal products are searchable. With one click, you can request indexing for any missing pages, ensuring your full product catalog is visible to potential buyers.
**Pricing:** [CrawlWP](https://crawlwp.com/pricing/ "nofollow") offers a free version with essential indexing features. For full SEO stats, bulk indexing, and premium support, plans start at $49 per year for a single site.
## Conclusion
There you have it. Our list of the best plugins for WooCommerce!
We hope this list will help you enhance your store’s functionality and improve your sales and revenue. However, some plugins in this list may require a premium subscription to access all the features mentioned.
While these plugins may help you manage and scale your WooCommerce store, you need a capable WooCommerce-optimized host to support that growth. That’s where Levamo comes in. Our [woocommerce managed hosting](/managed-woocommerce-hosting/) makes sure your eCommerce site is always performing at the top level, no matter where your visitors are from.
[Try Levamo for Free](https://my.levamo.com/start)
---
## 20 WordPress Best Security Practices to Secure Your Website
- URL: https://levamo.com/blog/wordpress-best-security-practices/
- Category: website-security
- Author: Sunyyan Junaid
- Published: 2025-01-28
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Harden your WordPress site! Follow these 20 security best practices today.
Looking for an all-in-one guide with actionable tips to optimize the security of your WordPress website? Here’s a 20-point WordPress best security practices that you can easily follow.
As a proud owner of multiple online businesses, I have learned with experience that ignoring my own WordPress security was a costly mistake. I got hacked and lost my data because of outdated plugins, themes, and WP core releases.
That was enough to teach me multiple lessons I will be sharing (which I learned the hard way) with you through an actionable checklist so that you don’t have to endure the same pain that I did.
Even if you’re a total newbie, WordPress website security is no different than taking care of your home, car, office, and other personal assets.
Always remember that hackers are constantly attacking websites, always targeting the most vulnerable ones with little to no basic security.
We’ll start off with the most basic WordPress security practices and then proceed with slightly advanced ones.
## But First, Is WordPress Really Secure?
Despite being a top target of hackers, the WordPress platform is inherently secure.
But just like any other platform, risks are not completely off the table, specifically if you are not careful. The same risks apply to leaving your doors unlocked at night or not having a security system at your premises.
Don’t blame the intruders. You just made it easy for them to get in and inflict damage.
## Why is Website Security Critical for WordPress?
Did you know that over [half of all WordPress websites](https://wpmayor.com/wordpress-security-based-on-facts-and-statistics/) were attacked due to outdated plugins and delayed core updates? Delaying updates can make your website extremely insecure and highly vulnerable to intrusions and threats.
Years of hard work can wipe out right before your eyes if you don’t take your WordPress website’s security seriously - just like it happened to me.
In my case, I also had to deal with devastating consequences, such as loss of business revenue, getting back and forth with the hosting support, and buying premium themes and plugins.
And that’s when I realized: It’s all about the basics that I never followed in the first place!
I was wrong the whole time.
Imagine you visit a website, and Google warns you that it is not safe. Would you still continue?
That’s a scenario for more than 15 million website visitors daily. In addition, Google also regularly blacklists more than 10,000 websites every single day. You really don’t want to be in the bad books of Google, do you?
Let’s start with understanding the root causes of these attacks and the WordPress best security practices to stop them.
## Understanding WordPress Vulnerabilities - Why Do WordPress Websites Get Attacked?
Let’s first understand the basic ecosystem of a WordPress website:
- **WordPress Core** - the WordPress open-source software provided by hosting companies and downloaded from WordPress.org
- **Themes** - The overall design and layout of your website, including fonts, colors, and images. These can be free or purchased from a reputable marketplace (Themeforest) or the theme developer’s website. These can be free or paid.
- **Plugins** - These are software add-ons that enhance the functionality of your WordPress website. By default, WordPress comes with multiple features, but to get the most out of this platform, you have to rely on plugins. Some are built by WordPress, whereas most of them are developed by third-party developers. Similar to themes, plugins are both free and paid.
Together, all 3 elements combine to give a powerful end-user experience. If any one of the elements breaks, it could potentially increase the risk of your site getting hacked.
Common entry points for attackers include:
- **Cracked themes and plugins:** Many website owners will not invest in installing paid plugins and themes. Instead, they download cracked versions. Hackers can easily inject malicious code into your website to take control if you’re using nulled or pirated versions.
- **Outdated Software**: Running outdated WordPress core, themes, or plugins is like leaving a window open for hackers.
- **Weak Passwords:** Weak passwords are still one of the most common causes of WP attacks! Use strong passwords with capital, lowercase letters, numbers, and a symbol. Consider using a reliable [password manager](https://psono.com/) to securely store and generate complex passwords that are difficult to crack.
Never use easily guessable words such as your name, website name, year of birth, etc.
- **Brute Force Attacks:** An old but effective method that hackers still use to date. This involves using multiple variations of usernames and passwords until one works correctly.
- **Phishing:** Derived from “fishing”, hackers use fraudulent techniques of sending emails and tricking you into entering your username and passwords onto reputable-looking websites.
- **Vulnerable Plugins and Themes**: Not all plugins and themes are created equal. Some may contain security flaws that attackers can exploit. Thoroughly review and vet each plugin and theme before purchasing one.
- **SQL Injection:** Hackers can inject malicious SQL code into your website if they find a vulnerability in your themes or plugins.
- **[DDoS Attacks](/blog/preventing-ddos-attacks/):** When more traffic is sent to the website than its servers can handle, resulting in frequent crashes.
- **Installing non-tested plugins:** Always read the plugin review thoroughly before installing it. Not all plugins work as expected.
Now let's go over to our list of WordPress best security practices.
## WordPress Best Security Practices: Your Actionable Checklist
So, how to make WordPress website secure? Based on my personal experience and vetted by our experts at Levamo, this actionable list of WordPress best security practices is the only solution you ever need to keep your site safe from hackers.
### Part 1: The Basics
- **Get a Reliable Web Hosting**
This should not come as a surprise. One of the top WordPress best security practices to follow is having good hosting. Before you can decide about the aesthetics of your WordPress website, you need to find a [reliable hosting service provider](/). Many site owners fail to do their due diligence and opt for the most economical one.
The problem with this approach is that not every web host is equal, and most of the shared plans are not optimized for WordPress websites. At the end, they all face the same fate: malware infections and lost rankings!
And since most of you may not have the time or resources to do all the hard lifting, Levamo’s managed hosting for WordPress does the job for you. With world-class security, integrated CDN, site monitoring, malware detection, and automated backups, a good host acts as a first line of defense against attacks.
- **Install an SSL Certificate on Your Website**
You see this padlock?

This indicates that the website is secure and uses an SSL certificate.
By default, almost all hosting service providers, including Levamo, now provide a free [SSL certificate](/blog/ssl-website-security/) with their hosting services.
Once SSL is activated, also set an [HTTPS redirect](/blog/redirect-http-to-https/) so that anyone visiting the non-secure (HTTP) version of your website is automatically redirected to its secure version (HTTPS).
- **Keep Everything Updated - WordPress Core, Themes, and Plugins**
I was one of the unlucky owners who never updated the core theme and plugins and faced the dire consequences of it!
Ignorance isn’t bliss anymore. The cost of planned downtimes for server maintenance and updates is nothing compared to recovering from a hack.
Think of updates as security patches that close potential loopholes. To check for updates, click **Updates** under **Dashboard** and you will see a list of themes, plugins, and WP core that require updates.

Make sure that everything shows as **“up to date.”** That’s one tip down.
- **Regularly Back Up Your WordPress Website**
This point relates to the previous one. Every time you make an update to your website, perform a backup of the last operating version of your website. If anything breaks up, you can safely restore it with no hiccups.
You seriously don’t want to be in a situation with a broken website and no backups to fix it.
You also need to understand that in the worst possible scenarios, if your website gets hacked, having a safe and secure backup will ensure you are up and running in no time.
You can use any free or premium backup plugins. Alternatively, if you are hosted with us, your website, our platform will perform daily automatic backups.
Here’s how you can [initiate backups at Levamo](https://support.levamo.com/articles/8484102-creating-and-managing-backups). Here are some popular plugins to perform a one-click backup of your website:
- UpdraftPlus WP
- JetPack
- Duplicator
- All-in-one WP Migration and Backup
- Backup - WordPress Backup & Plugin

- **Also, Keep Your Backups Separate**
While backups are important, keeping them in the same location as your current website is not going to help either.
What if the server malfunctions? Your data and backups could be erased. With Levamo, you get automated daily backups, stored at separate servers from your current website, ensuring continuity in case your website goes down.
- **Choose Plugins and Themes Wisely:**
Before installing any plugin or theme, do your research. Check reviews, ratings, and the developer's reputation.
I wish I had done the same while mindlessly installing plugins without looking at the reviews. At the end, I had a site bloated with so many plugins, I didn’t even know what to do with them.
Only install plugins from reputable sources like the official WordPress.org repository. Check if the plugins are tested with the latest WP core version and the last time an update was made.
If there are no regular updates by the developer, pass them on. Better safe than sorry.
- **Remove Unused Plugins**
If you're not using a plugin or theme, delete it.
“But what harm is it posing to my website? I am not using it!” You aren’t, but your database is.
Inactive plugins are the silent killers. Hackers can still use them to inject malicious code into your website.
Head to **Plugins**>**Installed Plugins** and browse for deactivated plugins. Then find the **Delete** link underneath to delete that plugin, permanently closing any possible loopholes in the future:
Do the same for themes and delete all unused ones.
- **Install a Security Plugin**
Not installing a security plugin was another costly mistake! It wasn’t until I installed it for my clients that I noticed the way it worked in blocking hacking attempts.
A security plugin is like hiring a 24-hour guard right at your website’s doorstep, ensuring only people with authorized access enter the system. One of the most popular security plugins for WordPress is Wordfence Security.
Tight on budget?
Go with its free version, which provides the same level of security as the paid version ($149 per year). The only difference is that the former has a delay of 30 days in patching for new vulnerabilities, whereas the latter provides real-time protection.
There are many [reputable plugins](/blog/best-wordpress-security-plugins/) that you can use, such as Sucuri, Wordfence, Solid Security, and Security Ninja. Out of these, I am personally using Wordfence Security, and so far, it’s going great.
You get login & firewall protection, malware scanning, and active monitoring of your website to track user activity and suspicious behavior.
Wordfence Security has more than 5 million installs with an average rating of 4.7 on the WordPress.org repository. Here is a live demo of its functions inside a WordPress website dashboard:
This is equivalent to installing a security camera outside your home.
### Part 2: Advanced Settings
- **Set up a Firewall**
Securing WordPress website means performing multiple actions to keep it safe from any malicious activity. Relating to the previous point, a good plugin provides a basic level of firewall protection,
A firewall, explained in simplest terms, is a network security device through which all incoming and outgoing traffic to your website is monitored. When a malicious activity is detected, the firewall blocks it immediately.
A basic Web Application Firewall (WAF) is now a standard offering among many reliable hosting providers, including Levamo.
With security plugins like Wordfence, you can easily set up and monitor incoming/outgoing traffic rules.
- **Use Strong Credentials - Complex Passwords and Unique Usernames**
Would you lock your door and place its key under the doormat outside of your house?
How about using a strong lock with a complex key combination and keeping it safe with you?
Which option sounds more reasonable? If you’re like me, the second one reduces the risk of intruders breaking in.
The same goes for your WordPress website.
Use strong and unique passwords for all your WordPress accounts. Avoid easily guessable information like birthdays or pet names. Moreover, do not use the same password across all your accounts.
We also do not recommend using any password manager. In fact, password managers should be avoided at all costs.
In 2022, LastPass, one of the most popular password managers, suffered [two massive data breaches](https://blog.lastpass.com/posts/notice-of-recent-security-incident), resulting in hackers stealing encrypted password vaults and personally identifiable information.
Who suffered? The customers who relied on this tool to do the very thing it failed.
Here are some examples of weak passwords:
- Short passwords less than 8 characters - 123456a
- Passwords with recognizable keyboard patterns - qwerty12345
- Common names - Michael
Here are some examples of strong passwords:
- Lengthy with random characters - Mich@elsLapt0p88!!
- Long recognizable words with multiple characters - Walk2miles3achDay!
Always focus on using a strong password because the chances of it getting cracked are exponentially higher than those of a weak password.
- **Use 2-Factor Authentication**
A two-factor (2FA) authentication method adds an additional layer of protection to your site. It ensures that the person accessing the website is the one who he/she really are.
Even though using a strong password is important, it isn’t secure enough for your website.
What if someone gets access to your credentials and you haven't enabled 2FA?
With 2FA enabled, every time you log in, a code is sent via SMS or email that you need to enter for authorization. I personally use the Google Authenticator app on my phone, and every time I have to log in, I would then simply enter the authorization code for verification.
By default, WordPress does not come with 2FA. You can use any of the following plugins:
- Google Authenticator
- Wordfence Login Security
- 2FA
- Loginizer
- Solid Security
These plugins further make it nearly impossible for cybercriminals to hack your website.
- **Change the Default Admin URL and Username**
By default, the admin URL for any WordPress website is:
[https://yourwebsite.com/wp-admin](https://yourwebsite.com/wp-admin)
This URL is a part of every standard WordPress installation because every time you install WordPress, you hardly bother to change the admin URL. That’s also another blunder I made.
“Why does it even matter?”
It does. While the link is easy for you to remember, it is also just as easy for hackers to launch brute-force attacks.
Just changing the default admin URL can significantly reduce hacking attempts, such as:
[https://yourwebsite.com/site-login-panel](https://yourwebsite.com/site-login-panel)
[https://yourwebsite.com/we-can-login-in-here](https://yourwebsite.com/we-can-login-in-here)
The same goes for the admin login. Many website owners (even me before my website got hacked) had “admin” as the username. Changing it can make it much more difficult for hackers to guess the right username.
- **Limit Login Attempts**
We all forget passwords once in a while. With so many websites to manage, I find it intimidating to memorize every login credential.
I even have to retype my passwords multiple times to figure out the correct one until I am in.
And that is exactly what hackers do. They continue multiple attempts with various combinations of passwords and usernames until they are successful. This is called a “brute-force attack.”
As a website owner, there is no harm in multiple attempts to log in to your WP dashboard. But you definitely want to limit this access to any unknown person who might be trying to get in.
With a security plugin like Wordfence Security, you can limit login attempts, making it difficult and time-consuming for hackers to break in.
To enable this feature, head over to **Wordfence > Firewall > Global Firewall Options**
Scroll down and you can define a number against **Lock out after how many login failures**. That’s it.
Let the plugin do its job and thank me later.
- **Turn Off File Editing**
WordPress has a built-in code editor, making it easy for admins to edit themes, plugins, and other files. Anyone with malicious intent can change the contents of your files and inject malicious code.
To avoid this situation, disable the file editing feature. To do this, head over to Appearance>Theme File Editor, locate the WP-Config.php file, and insert the following code.
// Disallow file edit
define( 'DISALLOW_FILE_EDIT', true );
If you need assistance, better hire a WordPress professional or let your hosting company do this for you. Alternatively, you can also use a plugin to get this job done safely, such as All In One Security, Wordfence, or MalCare.
- **Disable PHP File Execution**
Hackers have many ways to compromise your digital assets, and one of these methods is by uploading malicious files to your WordPress website. Here’s how to further harden your website security.
You need to disable PHP file execution, which stops all malicious code from running on your website. It is a fairly simple and easy way to do it.
Open up Notepad or any text editor on your system and enter the following code:
deny from all
Now save this file as .htaccess.txt and upload it to your /wp-content/uploads and /wp-includes directories. You can upload using any FTP uploader or via the website admin panel provided by your hosting service company.
- **Change the Default Database Prefix**
The default prefix for all WordPress websites is *wp_*, which is why it is the most common prefix name for all databases. When you get something by default, make it difficult for hackers to guess it by changing its name.
And that’s what you have to do here. You need to first change the database prefix in the **wp-config.php** file, which should have a line that looks like this:
`$table_prefix = 'wp_';`
Now use phpMyAdmin to update the table names:
`RENAME table `wp_options` TO `wp_awesomesite_options`;`
You can use this query structure and change what comes after the “TO” to match the table name with the updated prefix.
- **Disable Directory Indexing and Browsing**
The directory indexing and browsing feature for my websites is disabled, and if someone tries to access it, they will see this error:
Directory browsing gives hackers a way to know where the files are located on your server and which one of them could potentially have vulnerabilities.
Remember the .htaccess file we created earlier? Head over to this file on your server and add the following code:
Options All -Indexes
There you go, another security measure making it much more difficult for hackers to break in!
- **Use SFTP instead of FTP**
SFTP means Secure File Transfer Protocol, and as the name suggests, it’s a secure version of the FTP protocol. Some hosting providers, such as we at Levamo, use the more advanced and safer version, the SFTP, while transferring files and data to and from your website.
SFTP is secure because it encrypts the transmitted data.
If your hosting provider only uses FTP, ask them to provide you with SFTP. If they do not have this option, it is time to think about migration to a secure host.
- **Regularly Update PHP Versions**
PHP is a programming language used to build WordPress, and to run WordPress on the server, you need to have the latest version of PHP.
Head over to **Tools > Site Health > Info > Server** to check the version of your PHP. As of writing this blog, the latest PHP version is 8.3, released on November 23, 2023.
If your version is not the latest, better to update it. I also strongly suggest you leave this part to either a WordPress professional or the experts at your hosting company, because if not done right, it could potentially break your website.
- **Hide Your WordPress Version Number**
Many WordPress themes show the WP core version to the public, however, it is never required in the first place.
No visitor should know the version number of your CMS because hackers can easily guess potential security flaws with your website.
There is nothing to worry about if you are using a security plugin like Sucuri or Wordfence, as they automatically hide the WP version number.
If you don’t have a plugin or want to do it manually, add the following line of code to the **functions.php** file in **Theme File Editor**.
`remove_action('wp_head', 'wp_generator');`
So, there you go! The top WordPress security tips to securing WordPress website.
## Role of Hosting in WordPress Web Security
While these practices are important to follow, the first thing that plays a crucial role in your website’s security is hosting. Most of the attacks begin from having a weak and unreliable service provider. Server-side security is the first line of defense against many threats. This means that if a hosting provider does not take security seriously, all websites on those servers could potentially be vulnerable to external threats.
At Levamo, that’s not the case. Our Managed Hosting for WordPress is built with security in mind. Our experts work around the clock to provide advanced security features, including:
- **DDoS Prevention:** Protection against distributed denial-of-service attacks.
- **SSL Encryption:** Secure communication between your website and visitors.
- **Server-Level Firewalls:** Robust firewalls to block malicious traffic.
- **Automated Backups:** Regular backups to ensure you can quickly restore your site in case of an incident.
- **Integrated CDN:** Ensuring your site loads at blazing-fast speeds.
## Conclusion: Taking Control of Your WordPress Security
This list of 20 best practices will significantly strengthen the security of your WordPress website. Even following the most basic tips can go a long way in providing the necessary protection you need.
I also encourage you to regularly audit your website for vulnerabilities and take proactive steps to improve your security posture. Train your employees to monitor suspicious user behavior, as human error is a big cause of security breaches.
Ready to experience the peace of mind that comes with secure, managed WordPress hosting? Explore Levamo’s solutions today!
## Frequently Asked Questions

### How do I secure my WordPress login page?
Change the default login URL and admin name, implement 2FA, and limit login attempts. You can achieve this all by using a security plugin.
### What are the best tools for WordPress malware detection?
Sucuri, Wordfence, and MalCare are all popular options.
### Can I protect WordPress without a plugin?
Yes, but plugins often provide convenient and effective solutions for many security tasks. You cannot solely rely on manual protection.
### How does managed hosting improve WordPress security?
Managed hosting providers handle server-side security, updates, and other technical aspects, freeing you to focus on your website. It’s like having your own experts without the hefty price tag.
### What should I do if my WordPress website is hacked?
Immediately change all passwords, scan for malware, restore from a clean backup, and contact your hosting provider for assistance.
### What are some common signs that a WordPress site has been compromised?
Unexpected changes to your website, suspicious redirects, new user accounts you didn't create, and malware warnings from your browser.
---
## The Importance of Minimizing Website Downtime for Your Online Business
- URL: https://levamo.com/blog/minimizing-website-downtime/
- Category: ecommerce
- Author: Faisal Sarker
- Published: 2025-01-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Uptime matters! Keep your site online, customers happy, and sales flowing.
Let’s begin our class on what uptime really is (in case you stumbled across this article and don’t know what you’re doing here) and what measures you can take to improve your website reliability and minimizing website downtime.
Downtimes suck. There, we said it.
Uptimes rock. In fact, 100% uptime rocks even more than 99% uptime. But then we’re living in reality, and 99% sure beats 90%, so we’ll take that as well.
The point is, for you to have a reliable online business, uptime and overall website reliability are absolutely critical. The best way to ensure your website never faces downtimes - especially during critical periods like sales season or campaigns - is to opt for an optimized platform. But more on that later.
## What Is Uptime, and Why Does It Matter?

Uptime refers to the amount of time your website is accessible and operational. In simple terms, it’s the opposite of downtime, which occurs when your website is unavailable to users. [Reliable hosting providers](/) typically guarantee uptime percentages of 99.9% or higher. While 0.1% downtime might seem negligible, consider this:
- **99.9% uptime** means about **8.76 hours of downtime annually**
- **99.5% uptime** translates to **43.8 hours of downtime annually**
And in case you’re wondering why this matters, here’s a fun fact: **Gartner says the average cost of IT downtime is $5,600 per minute.** That’s more than most of us spend on rent in a month - heck, maybe even two!
Still think your website can afford to take a nap? Let’s see how that pans out in real-life scenarios for LMS and eCommerce businesses.
## Impact of Downtime on LMS Websites
As an LMS website owner, you should know that downtime can be a real arch nemesis to your students’ learning path. Why? Because:
- **Interrupted Learning Experiences:** Learners expect uninterrupted access to their courses. A sudden crash during an exam or lecture can erode trust and lead to complaints.
- **Loss of Revenue:** Many LMS platforms operate on subscription or pay-per-course models. If users can’t access the platform, they’re less likely to renew subscriptions.
- **Damaged Reputation:** In a crowded market, downtime can set you apart - but not in the way you’d want. Negative reviews and poor word-of-mouth can tarnish your brand’s credibility.
And these are just a few of the ways downtimes can impact your LMS business negatively.
Now let’s take a look at the impact on eCommerce businesses.
## Why Uptime Is Critical for eCommerce Owners
For eCommerce businesses, uptime and reliability can make or break your success, just like any other industry, but the financial impact can be even greater depending on the size of your business. Here’s why:
- **Lost Sales Opportunities:** Amazon once reported losing $220,000 per minute during a site outage. While smaller businesses may not operate at Amazon’s scale, even minor outages can result in significant revenue loss, especially during peak sales periods like [Black Friday](/blog/black-friday-hosting-preparation/).
- **Customer Trust:** When customers encounter an error page or a slow-loading website, they’re likely to leave and shop elsewhere. Studies show that **53% of users abandon a site that takes longer than 3 seconds to load.**
- **Search Engine Rankings:** Google prioritizes reliable websites in its rankings. Frequent downtime can hurt your SEO, making it harder for potential customers to find you.
Okay, so hopefully these two examples illustrate clearly why uptime is absolutely critical for your business. So how do you ensure that your business doesn’t face any downtime?
Over the years, we’ve picked up the best methods to ensure that our own website along with our users’s websites never have to face downtimes that affect their businesses, and this is how we do it:
## Tips for Measure and Maintaining Your Website’s Uptime

- **Use Monitoring Tools:** Website uptime monitoring tools like UptimeRobot and Pingdom are essential to track your site's performance and catch downtime before it impacts users.
- **Invest in High-Quality Hosting:** Avoid shared hosting environments that can lead to bottlenecks and server overloads. For mission-critical websites, it’s important to invest in a [managed WooCommerce hosting](/managed-woocommerce-hosting/) environment that truly delivers on its promise (more on this below).
- **Optimize Your Website:** Minimize heavy plugins and use a [Content Delivery Network (CDN)](/cloudflare-cdn/) to improve speed and reliability.
- **Regular Maintenance:** Keep your site’s software updated to prevent vulnerabilities that could lead to downtime.
- **Focus on Website Reliability:** Regularly test your site’s performance under different conditions to ensure consistent reliability.
While these tips will help you with maintaining your website’s reliability, the single most important factor that can ensure all of the above is your hosting provider.
In fact, your choice of hosting may be even more important than your cup of morning coffee. If you go with a shared hosting service or one that cannot deliver the kind of performance your particular website needs, not only will it cost you time and resources, but it’ll lose you money on both business and expense fronts.
This is why Levamo is the go-to choice for hosting for people who have dynamic websites and who need a high-performance hosting service.
Also Read: [CDN for eCommerce](/blog/cdn-for-ecommerce/)
## How Levamo Ensures Unmatched Uptime and Reliability
At Levamo, we understand the importance of [lms hosting services](/managed-lms-hosting/) and eCommerce websites that is high-availability. Here’s how we deliver peace of mind to our customers:
- **99.99% Uptime Guarantee:** Our hosting infrastructure is designed to keep your website online, no matter the demand.
- **Auto-Scaling Technology:** We handle sudden traffic surges with ease, ensuring your website performs flawlessly during high-demand periods.
- **Blazing Fast Speeds:** Powered by cutting-edge technologies and [free WordPress CDN](/cloudflare-cdn/), Levamo optimizes performance for platforms like WooCommerce and LearnDash, reducing page load times to keep users engaged.
- **24/7 Managed Hosting for WordPress Support:** Our team is always on hand to resolve issues quickly and effectively, minimizing potential downtime.
- **Incremental Backups:** Regular backups ensure you can recover data swiftly in case of unexpected disruptions.
In fact, our users are not just happy; they rave about our service.
[Levamo User Review on TrustPilot](https://www.trustpilot.com/review/rapyd.cloud?search=downtime)
In short, minimizing website downtimes is easy with Levamo. Get Started for Free today with a 7-day free trial!
## In Conclusion: Uptime Isn’t Optional
Your website’s uptime and reliability are the cornerstones of your online success. Whether you’re educating learners or selling products, one thing’s for sure: downtime is the enemy.
With Levamo, you get a hosting platform that understands your needs, tackles your challenges, and keeps your website running like a dream.
---
## Boosting E-commerce Sales with a CDN: Faster Loading Times, Higher Conversions
- URL: https://levamo.com/blog/cdn-for-ecommerce/
- Category: ecommerce
- Author: Faisal Sarker
- Published: 2025-01-22
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Speed up your e-commerce site with a CDN for higher conversions now.
This blog explores what a CDN is the benefits of CDN for eCommerce, and how it helps turn the lost opportunities into revenue. We'll also introduce Levamo CDN, a powerful solution built on top of Levamo hosting, designed to optimize your online shopping experience and improve eCommerce conversion.
Imagine a customer visits your shop and just as they’re about to make a purchase, the power goes out. By the time you figure out what happened and restore electricity, the customer’s gone, as if disappearing into the abyss.
That's exactly what happens every time your online store takes too long to load. While everyone deserves a second chance, that’s not the case in the world of e-commerce because customers have near-to-zero patience.
Here’s an interesting fact you got to know:
*A staggering 70% of consumers admit that page speed impacts their willingness to buy from an online retailer.*
Lost customers translate to lost revenue, and a missed opportunity to grow your business.
So what’s the solution? How can we turn lost customers into profitable streams of income?
**A Content Delivery Network (CDN).**
## What is a CDN and Why Does it Even Matter?

A CDN is a geographically distributed network of servers that caches static website content, such as images, videos, and HTML files.
When a user visits your website, the CDN delivers the content from the server closest to their location, significantly reducing latency and improving loading times. For your e-commerce store, you know that every second counts.
Let’s put it this way:
Having a CDN on your website is like launching multiple physical locations of your business, making it easy for your customers to make a purchase from the one closest to their location.
The same goes for your website. If your website’s hosted in the US, and your customers are landing in from Australia, your site will automatically show content from the nearest servers in their geographic location.
## What is The Impact of Slow Websites on E-commerce Sales?
Slow websites are the equivalent of trying to use a family sedan as a sports car. It just doesn’t work.
In different studies on the impact of slow websites on eCommerce sales, here are some facts and figures you need to know:
- **Increased Bounce Rates:** A mere one-second delay in page load time can increase bounce rates by up to 32%. This means potential customers are leaving your site before even seeing your products.
- **Decreased Conversions:** Slow loading times directly correlate with lower conversion rates. Customers are less likely to complete a purchase if the checkout process is slow, has multiple steps, or is not user-friendly.
- **Negative SEO Impact**: Search engines now prioritize fast-loading websites in their rankings. Why? Because search engines now translate the user experience on your website directly into rankings. Happy customers, happy search engines, and vice versa. A slow site will negatively impact your search engine optimization efforts, making it harder for customers to find you.
- **Damaged Brand Reputation**: A slow and unreliable website can damage your brand's credibility and deter customers from returning. That’s no different than the example we shared at the start of this blog.
## Here Are 7 Benefits of CDN for eCommerce Sales

A CDN offers numerous benefits that directly translate to increased e-commerce sales. Here’s how:
- **Accelerates Page Load Times**
By delivering content from geographically closer servers, a CDN drastically reduces loading times. This leads to lower bounce rates, increased engagement, and more completed purchases.
This is by far the biggest and the most obvious advantage of having a CDN for your online store. The time you save results in higher conversions and sales revenue.
- **Increases Mobile Conversions**
Let’s be honest. Nobody has the time to sit on their home or office laptop, scrolling for those favorite brands. Everyone’s busy and mobile shopping is now the go-to way for boosting eCommerce sales.
You have to be where your customers are.
This means having your website super optimized for mobile devices. A CDN optimizes site speed for mobile users, ensuring a smooth and enjoyable experience, even on slower mobile connections. This is crucial for maximizing mobile conversions.
- **Improves Checkout Experiences**
A seamless and quick checkout process is essential for minimizing cart abandonment. A CDN ensures a fast and reliable checkout experience, encouraging customers to complete their purchases with reliability and satisfaction.
Abandoned carts are a big problem for online stores, and most often than not, the primary reason for them is due to slow loading websites. Customers neither have the time nor the energy to purchase from slow websites anymore.
- **Handles Flash Sales and Traffic Surges**
During peak sales events or marketing campaigns, website traffic usually surges, and thatá a good thing for your business, but not if you aren’t ready for these spikes!
A CDN for eCommerce can handle these spikes in traffic without compromising performance, ensuring a smooth experience for all customers.
- **Boosts Search Engine Rankings**
As mentioned earlier, website speed is a ranking factor for search engines. By improving site speed, a CDN for eCommerce can help you rank higher in search results, driving more organic traffic to your store.
Remember, you’re competing with thousands, if not hundreds of thousands of other stores in your geographical location. So why compromise and settle for slow speeds?
- **Delivers High-Quality Media Quickly**
High-quality images and videos of your products are essential for a long-lasting first impression. How would customers buy from you if they don’t get to visually see what you sell?
However, the problem with high-quality media is that it often takes up a lot of storage space. For example, a high-res image can exceed 1 MB in file size. Despite high-speed internet connections, loading this file size is a disaster for your website.
This is where CDN does its magic. Levamo CDN ensures that these media files load quickly by compressing and caching them, creating a visually appealing and engaging shopping experience.
- **Enhances Personalized Shopping**
CDNs can efficiently deliver dynamic content, allowing you to personalize the shopping experience for each customer. This can lead to increased customer satisfaction and higher conversion rates.
Our fully [managed Woocommerce hosting](/managed-woocommerce-hosting/) has a built-in Levamo CDN that allows your eCommerce stores to run like a sports car.
## Why Choose Levamo for Your CDN Needs?

We have recently [launched Levamo CDN](/blog/introducing-rapyd-cdn/), our in-built [free WordPress CDN](/cloudflare-cdn/) specifically designed for dynamic websites on Levamo’s hosting servers.
With Levamo’s [best managed WordPress hosting](/managed-wordpress-hosting/) and the power of Levamo CDN, you get:
- **Superior Speed and Performance:** Leveraging a global network of servers and advanced caching techniques, Levamo CDN delivers exceptional speed and performance, ensuring your website loads quickly for users anywhere in the world.
- **Enhanced Reliability and Uptime:** Levamo CDN's robust infrastructure and redundant systems ensure high availability and minimal downtime, keeping your online store accessible to customers 24/7.
- **Scalability for Growth:** As your business grows, Levamo CDN can scale seamlessly to handle increasing traffic and data demands, ensuring consistent performance.
- **Round-the-clock Support:** Ran into some problems? Or just confused about how it all adds up for better site speed? Let our experts know and they’ll take care of everything.
## Here’s a Customer Success Spotlight
[Veteran Hundo Club](/blog/veteran-hundo-club-customer-stories/) is a social platform that used to struggle with slow load times, to the tune of up to 60 seconds. Prolonged loading of websites will eventually tarnish brand reputation eventually driving it out of business.
That’s the threat Veteran Hundo Club was facing. While they were already using Namehero’s cloud solution, the services offered were no match to the price that they paid.
To top it off, they were already using BuddyBoss, a WP plugin that converts your website to a dynamic social platform. But running a site like this requires scalable cloud resources, which they didn’t get through their previous hosting provider.
**Enter Levamo.**
When they learned about our powerful, scalable and reliable cloud hosting service, they immediately made the decision to take a leap of faith and migrate to us.
While hesitant at first, the migration was a smooth process, ensuring zero downtime. By the time you read this paragraph, their website was already migrated, showing great improvements in speed.
The best part? They didn’t face any downtime, nor technical glitches like they did with their previous hosting provider.
## The Road Ahead..
If you’re launching or have already launched an online store, a membership site or an LMS-based course website, now is the best time to integrate our 1-click Levamo CDN!
We are also working to add in new features in our Levamo CDN and one of them is Rule Set Manager, with which, you’ll be able to set custom rules for caching, redirecting, and more.
While the one-click CDN feature will still do its job, if you’re an advanced user, you’ll soon be able to optimize CDN rules for unique site requirements.
For us, the sky's the limit and we will continue delivering exceptional performance upgrades to ensure that your websites load blazing fast, and your customers keep on returning back to your store!
We’re in the business of growing your business.
The road ahead in 2025 and beyond is exciting for us and we’re sure it’ll be the same for you too.
We can’t be any more excited than seeing our clients getting the most out of their investment into reliable hosting services by Levamo.
Ready to experience the power of Levamo CDN? Explore our solutions today and unlock the potential of your online business.
[Try Levamo for Free](https://my.levamo.com/start)
## Frequently Asked Questions

### What is a CDN, and how does it improve website performance?
A CDN is a network of servers that caches website content closer to users, reducing latency and improving loading times.
### How does website speed affect e-commerce sales?
Slow websites lead to higher bounce rates, lower conversions, and negative SEO impact, all of which negatively affect sales.
### What are the advantages of using a CDN for my online store?
A CDN improves site speed, handles traffic surges, enhances mobile performance, and boosts SEO, all leading to increased sales.
### How do I integrate a CDN into my e-commerce platform?
Levamo CDN offers easy integration with various platforms, including WordPress and WooCommerce. Our support team can assist with the process.
### How does Levamo’s CDN differ from others?
Levamo CDN offers superior speed, reliability, scalability, and expert support, tailored for the demands of e-commerce businesses.
---
## Why Do Course Creators Need Fast and Reliable Hosting?
- URL: https://levamo.com/blog/hosting-platform-for-online-courses/
- Category: hosting
- Author: Faisal Sarker
- Published: 2025-01-21
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Reliable hosting boosts online course engagement. Learn why it matters now.
In this blog, we will explore how hosting platform for online courses directly impacts user engagement and why it matters for your online business.
In your opinion, what is the most valuable currency in the world? The US Dollar? Kuwaiti Dinar? Omanis Riyal? No. None of that even comes close.
In today’s fast-paced digital world, the most valuable currency is ATTENTION.
From Super Bowl ads to the social media campaigns, marketers are competing for YOUR attention. They want YOU to engage with their brands.
But why?
Attention leads to engagement. Have you ever paused a video and then commented on it because it was highly relatable? This is exactly the type of engagement that brands want from you.
Let’s put it this way.
As you walk down the aisle at a grocery store, you look at a number of different products on the shelves. In that same aisle, there are brands with similar products competing for your attention, which could be in the form of discounts, coupons, buy one/get one free offers, unique ad copies, or different colors.
The moment you pick up a product, read its labels and inquire about its price with the storekeeper, the marketers have done their job. They have compelled you to engage with the product.
Now let’s take that example to an online business.
Whether you're managing a bustling online community, delivering engaging online courses, or providing exclusive content to subscribers, the foundation of a thriving membership platform lies in delivering a seamless and enjoyable user experience.
A YouTuber would want more likes, shares and comments on their video. Similarly, a course creator would want more attention, interest and motivation from their subscribers.
And at the heart of this experience lies the often-overlooked yet critical factor: hosting.
## How Does Fast Hosting Help Increase User Engagement?

Think of your website's hosting as the engine that powers your membership platform. Just as a powerful engine ensures a smooth and efficient journey, the same goes for fast and reliable hosting and here is why it matters:
### Fast Loading Speeds
Browsing slow-loading websites is now a thing of the past. Frustrated members will abandon your platform before they even get a chance to explore your offerings.
Fast loading speeds, facilitated by advanced caching and Content Delivery Networks (CDNs) are essential for keeping members engaged and exploring your platform's depths.
Here’s something to ponder upon:
40% of visitors will abandon your website if it takes 3 seconds or more to load.
And why shouldn’t they when there are an abundance of options available online?
To be considered a priority and not an option, your website needs to load up fast.
### Uninterrupted Uptime
Nothing disrupts the member experience more than unexpected downtime.
When your platform goes offline, members are left stranded, unable to access valuable content, participate in community discussions, or connect with fellow members.
Consistent uptime is crucial for building trust and fostering a sense of reliability.
### Seamless User Experience
A sluggish platform can lead to a frustrating user experience, hindering member interaction and exploration, thereby negatively impacting user engagement.
Reliable hosting platform for online courses ensures that your platform can handle traffic spikes, ensuring a smooth and responsive experience even during peak usage periods.
### Scalable Resources
For a course creator, nothing's more irritating to see your business grow only to face limited system resources. With fast and reliable hosting, you are essentially trusting the hosting provider to scale up in resources with you as your number of subscribers and members grow.
With today’s average shared hosting solutions, scalability is a rare luxury that comes with additional charges.
However, with Levamo, as your numbers grow, so do the resources required to facilitate this growth, and none of that comes at an extra cost. We are able to deliver a seamless experience because of our cloud server technology that distributes data across multiple servers. This ensures your platform can meet[ infrastructure scalability requirements](https://www.servers.com/news/blog/infrastructure-scalability-needs) without compromising performance.
## The Challenges Faced by Course Creators

Many platforms grapple with common hosting-related challenges. Here are some of these:
- Frequent Downtime: Unexpected outages can lead to lost revenue, frustrated members, and damage to your brand reputation.
- Slow Loading Pages: Slow-loading pages can result in high bounce rates, hindering member engagement.
- Scalability Issues: The inability to handle sudden traffic surges during peak usage or special events can lead to a poor user experience and potential downtime.
We have come across a number of course creators and membership platform owners that say they lost a good amount of revenue because they were unable to scale with their previous hosting service providers.
## Choosing the Right Hosting Partner: Key Considerations

To overcome these challenges and create a truly engaging membership platform, it's essential to choose a reliable hosting platform for online courses. Here is a list of all the features that you need to look for in a web hosting service:
### Speed:
Look for reviews of website owners that praise a hosting service for how quick it loads your website. Speed is also one of the most important elements for SEO and user engagement.
Go with a hosting provider that utilizes Content Delivery Networks, or CDNs. These CDNs distribute your website's content across multiple servers globally, ensuring faster delivery to visitors regardless of their location.
With Levamo, we ensure that your site never lets you down because of our Hyperspeed hosting.
### Reliability:
Reliability simply means that the service is available whenever you need it. Cloud services are targeted for course creators, online community developers and digital services providers.
Hence, it is imperative that our services are available when you need them.
### Scalability:
The ability to automatically adjust resources based on traffic, ensures your platform can handle sudden surges without compromising performance.
This is what we at Levamo do for you. We adjust our cloud server resources as your site grows in traffic and user registrations at no additional costs to you.
# Levamo: The Ideal Hosting Platform for Online Courses

Don't compare Levamo with other [LMS hosting services](/managed-lms-hosting/), but think of it as your long-term partner in success. We are your ideal hosting platform for online courses.
Why? Because we are optimized for dynamic websites like LMS. Every website hosted with us has blazing-fast speeds, ensuring your students enjoy a seamless and responsive experience.
Built on the robust and scalable infrastructure, free Wordpress CDN, we offer unparalleled reliability and uptime. Our [24/7 managed WordPress hosting support](/support/) is always available, even during the weekends and national holidays to ensure your website always remains online.
With auto-scaling capabilities, Levamo effortlessly adapts to changing traffic demands, ensuring your platform can handle any surge in activity.
## A Case Study in Success
[TCM Academy](/blog/the-tcm-academy-customer-stories/), the Traditional Chinese Medicine Academy, is hosted on Levamo. Before hosting with us, they were paying $170 each month for a 16 GB cloud server with another service provider. Despite this, their website would often slow down and unable to load when it consumed more resources than allocated.
Levamo was quite new at the time when TCM Medicine migrated to us. Initially they were skeptical due to our brand new launch, but eventually they took a leap of faith and migrated their website to our servers.
Within days, their customer complaints fell by a whopping 100%, page loading speed dramatically improved and the website automatically scaled as the user base grew.
Faster loading speeds, coupled with consistent uptime, led to increased member engagement, higher course completion rates, and ultimately, a significant boost in revenue.
Want to join the likes of TCM and grow your membership site engagement?
[Try Levamo](/pricing)
## Conclusion
In the competitive world of online membership platforms, simply relying on a hosting provider isn’t enough.
By choosing the reliable and [fastest WordPress hosting](/blog/fastest-wordpress-hosting/) provider Levamo, you can create a seamless and engaging experience for your members, fostering a thriving online community.
Ready to elevate your membership platform to new heights? Explore Levamo's hosting solutions and discover how we can help you build a truly exceptional online community.
## Frequently Asked Questions

### What is the connection between hosting speed and user engagement?
Hosting speed is directly linked with user engagement. Slow-loading and bloated websites will often turn away the visitors. You need engagement in the form of community discussions, subscriptions and more. This is only possible when the website loads at blazing fast speeds.
### How can I ensure my hosting solution can scale with my platform's growth?
Based on the key considerations above, go with a cloud hosting provider that automatically scales up the resources as you do. This ensures uninterrupted community engagement without incurring astronomical hosting costs.
### What types of platforms benefit most from Levamo hosting?
Levamo is ideal for a wide range of membership platforms, including online courses, subscriptions, exclusive communities, and SaaS platforms.
Other than this, you don’t really have to be a course seller to use our hosting. Even if you are into blogging such as news, entertainment, fashion or any other niche, you can rely on us for speed and reliability.
### Can I migrate my LMS site to Levamo without downtime?
Yes, Levamo offers free migration services to minimize disruption to your members.
First, we will create a backup copy of your entire website onto our servers and then migrate with the change in domain nameservers.
Our experts do this on a daily basis without any downtime. Your website will be transferred without hurting your overall experience.
### Can fast hosting improve my website's search engine optimization (SEO)?
One of Google’s [Core Web Vitals](/blog/core-web-vitals-and-seo/) factors is the website loading speed. Fast loading websites provide a positive user experience, signalling Google and other search engines to push your site into organic rankings. Hence, it is imperative to have reliable hosting services for better SEO and visibility.
---
## The Top Web Hosting Trends to Look Out for in 2025
- URL: https://levamo.com/blog/web-hosting-trends/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2025-01-20
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Future-proof your site! See 2025's top web hosting trends now.
The digital landscape is constantly changing, and with it, the very foundation upon which our online experiences are built: web hosting.
As 2025 is just around the corner, the demands on hosting infrastructure are evolving at an unprecedented pace, driven by emerging technologies, shifting user expectations, and a growing emphasis on sustainability.
Simply maintaining the status quo is no longer an option; businesses must adapt to innovation or get ready to be eliminated from the competition.
This isn't just about faster loading times; it's about harnessing the power of cutting-edge hosting solutions to unlock new possibilities for growth, engagement, and operational efficiency.
This exploration of web hosting trends offers crucial and actionable insights into the technologies that will define the future of online presence.
From the rise of AI-powered performance to the inevitable green hosting and serverless architectures, let’s explore what web hosting trends 2025 brings for us.
## Trend #1: AI-Powered Solutions

Just like AI was part of web hosting market trends in 2024, the trend will not only continue but also exceed adoption rates in 2025. This means that hosting service providers will be switching to AI and automation to better serve their customers.
**Impact:** AI will improve efficiency by predicting the maintenance of servers, thereby directly reducing downtime. This will lead to a reliable hosting service whilst maintaining lower costs at the same time. The automated customer support will enable customers to find the solution to their problems using a chatbot that directs them to the video and/or an article in the knowledge base.
## Trend #2: Green Hosting Will Gain Momentum
According to a [Harvard Business Review](https://hbr.org/2024/07/the-uneven-distribution-of-ais-environmental-impacts#:~:text=The%20escalating%20and%20localized%20environmental,hundreds%20of%20tons%20of%20carbon.), training just one single Large Language Model (LLM) of AI requires thousands of megawatts of hours of electricity. This carbon footprint is estimated to be the equivalent of several hundred American households in a year. Plus, it can also lead to the evaporation of fresh water, most of which is needed to keep the equipment cool.
These environmental concerns are driving innovation among web hosting companies to look for alternatives and reduce their carbon footprint, hence the need for eco-friendly solutions.
**Impact:** In web hosting trends 2025, it is estimated that a number of hosting solutions will shift to renewable energy sources like solar and wind to lower costs. optimize server efficiency, and minimize waste. A direct impact of this decision is most likely to result in the conservation of freshwater.
## Trend #3: Increased Adoption of Cloud Hosting

For a typical website, shared hosting has sufficient resources to work fine with minimum downtime. However, for a dynamic website with an increasing amount of traffic, shared servers just cannot cope.
**Impact:** [Cloud hosting solutions](/) are highly scalable, allowing website owners to adjust server usage as their website grows in numbers. This means that even during peak holiday seasons, websites will not face downtime or speed issues. Businesses will be adopting hybrid and multi-cloud strategies, and web hosting companies need to adjust to this trend. Levamo offers the most affordable and unbeaten cloud hosting services that scale with you!
## Trend #4: Managed Hosting for WordPress for Everyone
Up till now, managed hosting for WordPress was considered a luxury reserved only for those who could afford it. In 2025 web hosting trends, we can witness the surge in managed hosting for WordPress, making it easy and affordable for technical and non-technical WP enthusiasts to get the most out of their investments. Regular updates and bug fixes are critical to ensure optimum performance for a WP website.
Powering more than 40% of the web, WordPress is the king of CMS. [Managed hosting for WordPress](/managed-wordpress-hosting/) takes care of security, regular backups, and critical security vulnerabilities. 2025 will see the improved sophistication of these services with better performance and higher adoption rates by consumers who will be increasingly looking for reliable hosting solutions for their complex WP websites.
**Impact:** With all of the technical aspects taken care of by the hosting company, businesses will only need to focus on their content and marketing, leading to cost savings in the long run. This also eliminates the need to hire an expert team of WP developers in-house as the hosting team manages everything, and hence named “Managed hosting for WordPress.”
Our experts at Levamo’s Managed Hosting for WordPress ensure regular backups, site configurations, periodic server maintenance, and a distributed network of cloud servers to manage your traffic. Businesses will also see a reduction in the time spent resolving website server queries in 2025.
## Trend #5: Decentralized Hosting for Enhanced Privacy Measures

2025 and beyond will see a dramatic shift toward decentralized hosting. Instead of hosting all files on one server, web hosting platforms will leverage the power of blockchain technology to distribute data across a network of nodes.
**Impact:** By distributing data across a network of nodes, businesses will witness improvements in security, privacy, and reduced vulnerability to censorship. Since there will be no centralized server, the chances of failures drop significantly, with better resilience to security attacks.
It is also important to note that decentralized hosting will take time for mass adoption because it may not serve as an ideal use case for every client.
Despite this, the centralized cloud hosting that we at Levamo offer is designed to meet the needs of complex websites and online businesses.
## Trend #6: Edge Computing and CDN
Rather than storing in a centralized server, edge computing and CDNs store data closer to the user’s geographical location to load content faster and reduce latency. This will be an important trend to keep an eye out for in 2025 web hosting trends.
**Impact:** The immediate impact of edge computing is the dramatic reduction of latency and improvement in performance. This benefits not only the end user but also the business in terms of revenue and profitability.
Edge computing and Content Delivery Networks (CDNs) minimize the distance for information to travel between the server and the end user. This leads to not only faster load times, but refined streaming experiences and responsive applications, specifically IoT devices.
In case if one edge server fails, others can seamlessly take over the workload without disrupting the business. By 2025 and beyond, edge computing will become an integral part of the web hosting landscape, making service providers more competitive than others.
## Trend #7: Serverless Hosting

Serverless hosting is a type of cloud-hosting model that works as a Function-as-a-Service (Faas). The developers write the code and deploy it in a container without worrying about the server.
The rest is managed by the hosting company, which charges the developers based on resources utilized. Apps built on the serverless infrastructure will scale automatically to accommodate a growing user base.
The servers will often start up, run, and end as and when they are needed without piling up astronomical hosting costs to the client. In 2025 and beyond, serverless architectures will gain momentum because businesses can run and stop the services they need and pay only for the resources they have utilized.
**Impact**: Serverless architecture allows developers the necessary freedom they need to write and execute code without acquiring a new server.
Businesses can scale with a faster-to-market time, all whilst managing their hosting expenses. By eliminating the need for server maintenance and management, businesses can save up on these costs and focus on revenue growth.
AWS Lambda, Google Cloud, and Microsoft Azure all provide these functionalities.
A real-life example is Netflix harnessing the power of serverless architecture to provide uninterrupted streaming services throughout the world.
## Trend #8: Implementation of Zero Trust and Enhanced Cybersecurity Measures

Research indicates that approximately [11.5 cybersecurity attacks](https://www.nu.edu/blog/cybersecurity-statistics/) occur every minute worldwide. Moreover, 40% of successful cyberattacks result in data breaches.
However, the attack itself is not the sole source of devastation; the ensuing consequences - such as reputational damage, revenue loss, and even bankruptcy - are the most damaging.
Fast-loading sites won’t be the only metric that clients will see in 2025 web hosting trends. In fact, they also want to ensure that the hosting companies will safeguard and protect their data.
In 2025, clients and hosting service providers will focus more on implementing enhanced cybersecurity measures with the implementation of Zero Trust.
Zero Trust is a network security model that hosting companies will implement to prevent unauthorized access to client data by enforcing multiple layers of security. Hosting firms will also implement AI-driven measures such as automated patch management, threat detection, and powerful encryption.
**Impact:** With hardened network security, implementation of the Zero Trust model, and AI-driven cybersecurity policies in place, businesses will see an uptick in data security, directly impacting their bottom line. Automated malware scans, regular backups, and quick restoration of data in the event of a catastrophe further ensure that clients can trust hosting companies focused on keeping the data safe and secure.
With our cloud hosting plans, you get to have an offsite cybersecurity team working round the clock to keep your data safe. We ensure data confidentiality and business continuity by keeping your data safe and secure from hackers.
## Trend #9: Increased Spending in Cloud Hosting
2025 will witness a surge in cloud computing in web hosting trends because of the reliability, scalability, and flexibility of the services, catering to millions of businesses worldwide.
In a 2024 article, Gartner projected that global spending on cloud infrastructure is poised to grow from $561 billion in 2023 to more than $671 billion by the end of 2024. This is a mind-boggling [20.4% increase](https://www.gartner.com/en/newsroom/press-releases/2024-05-20-gartner-forecasts-worldwide-public-cloud-end-user-spending-to-surpass-675-billion-in-2024#:~:text=Worldwide%20end%2Duser%20spending%20on,(GenAI)%20and%20application%20modernization.) on a Y-o-Y basis.
But this uptick in investment has many reasons behind it such as higher adoption rates of AI and machine learning, cybersecurity concerns, and a rise in remote working.
A lot of spending has to do with regulatory compliance to protect and safeguard confidential and sensitive data for millions of businesses and their clients. For example, to ensure data confidentiality for European citizens, Europe demands all businesses remain compliant with GDPR. This is why in 2025, investment in cloud computing will likely surge to ensure stringent regulatory compliance.
**Also Read:** [Best Managed Hosting for Ultimate Member](/ultimatemember-hosting/)
## Summary of Key Trends for 2025
Every business is unique and so are its requirements. It is imperative that hosting companies keep up with these trends to stay competitive or risk getting eliminated. Hosting companies need to provide quick, reliable, and scalable solutions for their clients to ensure better user experiences.
High-performance [secure WordPress hosting](/managed-security/) like Levamo provides you with complete peace of mind knowing that your site can easily scale without draining your budget. The future of web hosting is a lot more than just faster load times, clients also expect to keep their data safe when they choose you as the service provider.
Enhanced website security measures, increased spending in cloud hosting, stringent regulatory compliance, and scalability are all shaping up the hosting landscape in 2025.
Experts predict a rise in cloud adoption, more AI-driven solutions, and enhanced website security.
It is time to keep yourself updated with the web hosting industry trends.
Check out our **[benchmark methodology](/benchmark-methodology/)** to see how we measure hosting performance, and keep yourself updated on the performance trend for [fast WordPress hosting](/managed-wordpress-hosting/).
## Frequently Asked Questions

### What is edge computing, and how does it enhance performance?
Edge computing minimizes the distance it takes for the data to travel between the end user and the server, thereby directly leading to faster load times and improved user experience.
Edge servers work with CDNs, a distributed network of nodes across the globe. If a visitor in France is accessing a website with its server hosted in New York, this would cause delays for the data to load as it has to travel across the continent. With edge computing, a local edge server in London can cache content and handle requests, significantly speeding things up.
Levamo’s infrastructure is designed with performance in mind, and leveraging edge computing principles is the key to delivering a consistently fast experience for WordPress sites hosted on our platform.
### Is serverless hosting suitable for my WordPress site?
It depends entirely on your needs. A typical WordPress blog or a WooCommerce site may not need serverless hosting. However, if you want to build and deploy custom apps without worrying about hosting them, then this could be a viable option.
### How can I ensure my hosting provider is secure?
Always read reviews and inquire from the hosting company about the following security measures:
**CDN Support**
**Firewalls and Intrusion Detection/Prevention Systems (IDS/IPS)**
**Malware scanning and removal**
**[DDoS protection](/blog/preventing-ddos-attacks/)**
**Regular security audits and patching**
**Free [SSL certificates](/blog/fix-ssl-certificate-error/)**
**Regular and automatic updates of themes, plugins, and WP versions**
**Automatic backups and restoration**
### What is modular hosting, and how can it improve flexibility for developers?
Modular hosting allows developers to select and combine specific services and resources as needed, allowing for greater flexibility and control.
Levamo’s platform is built with modularity in mind, allowing us to tailor solutions to specific WordPress needs and provide developers with the flexibility they require.
### How does global CDN integration impact user experience and site speed?
A Content Delivery Network (CDN) stores copies of your website's static content (images, CSS, JavaScript) on servers distributed across various continents in the world. When a user visits your site, the CDN serves the content from the server closest to them, reducing latency and improving loading times.
While this may not be necessary for a website serving its country’s residents, as your site grows, it will only help in improving speed for the international audience. Levamo provides CDNs to ensure your website loads fast regardless of your visitors’ geographical locations.
### What is the difference between traditional and serverless hosting?
You manage the server, including operating system updates, security patches, and resource allocation. This is the typical and traditional server hosting model, one that incurred enormous costs and human resources.
In serverless hosting, the cloud provider handles all of this. You only focus on your business and leave the rest to your service provider.
### What role does AI play in web hosting support and optimization?
AI is transforming web hosting by automating tasks, improving performance, and enhancing security. AI-powered systems can:
**Fast customer support turnaround times**
**Monitor server performance and predict potential issues**
**Optimize resource allocation**
**Detecting and mitigating security threats**
---
## Levamo CDN: The Next-Gen of Global Website Speeds!
- URL: https://levamo.com/blog/introducing-rapyd-cdn/
- Category: news
- Author: Faisal Sarker
- Published: 2025-01-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Unlock blazing-fast WordPress speeds with Levamo CDN. It's free for our users!
> *Note: This post was originally published January 2025 as "Rapyd CDN: The Next-Gen of Global Website Speeds!" when our platform was called Rapyd Cloud. We've since rebranded to Levamo. The product details below remain accurate - only the brand name has changed.*
Imagine your website loading so quickly that your audience hardly has time to think. In 2025, that’s the standard every user demands and search engines reward.
At Levamo, we’ve been pushing the boundaries of WordPress hosting performance. In this article, we talk about one of our most popular features that is crucial to our focus on speed.
**Levamo CDN! 🎉**It’s our next-gen [free WordPress CDN](/cloudflare-cdn/) that has been redefining how your WordPress site performs globally!
And the best part? It’s **completely free** for our users!
[Levamo CDN](/cloudflare-cdn/) comes integrated into our platform and works seamlessly to cater to all your CDN needs. All you need to do is sit back and watch your pages load faster, because it’s engineered to deliver content at remarkable speeds across the globe, giving your WordPress site the edge it needs to outperform the competition.
## Why Levamo CDN & What Does It Do?

It’s simple. Our job is to make our users’ lives easier. So when you demand a simpler solution to a CDN, our engineers put their heads together to give you a better experience and improve your website’s performance right out of the box. No extra plugins, no more juggling third-party services.
Powered by NOC, Levamo CDN serves your website content from multiple servers, located in several edge locations around the world. The servers cache your static files and optimize images to reduce page load times so that no matter where your visitors are from, they always get the best, most reliable performance.
Additionally, since it operates as a reverse proxy, not only does it speed up the website performance globally, but it also provides essential security benefits like **DDoS mitigation**, improvements to **security certificates**, and other optimizations.
## Key Features of Levamo CDN
Levamo CDN is packed with innovative features and tailored for our users. It packs the features of a couple of website optimization tools alone. Let’s take a look at what makes Levamo CDN so great, and how it will help optimize your website speed even further:
### 1. Caching Static & Dynamic Pages & Resources
Levamo CDN caches static pages and resources to our physical servers specifically placed around the world. So no matter what part of the world your visitors are from, they get the same fast experience while browsing your website.
### 2. Image Optimization
Images are an important part of our website. But at the same time, they are also heavy and slow down your pages. Levamo CDN will be a game changer for images because it intelligently handles:
- **Image Conversion:** Compressing the images to load faster while keeping their quality optimal.
- **Format Conversion:** Conversion of images from other heavy formats to next-gen formats like **WebP** and reduce the size even more.
### 3. Distributed Infrastructure
As we already discussed above, Levamo CDN utilizes globally distributed PoP servers (also known as edge locations) and caches your website on these servers. We have world-class PoPs in all major regions. Especially in the USA and Europe, your users will enjoy the fastest loading time possible.
As a result of our global PoP servers, your site’s assets - images, JavaScript, and CSS - are served from a server that is closest to each visitor. The result is significantly faster load times, reduced latency, and a smoother user experience.
### 4. Enhanced Security
Your website security is of utmost importance to Levamo. We already have industry-leading security features in place, in partnership with **Monarx** and **Patchstack**. With Levamo CDN, you’ll fortify your security even further now.
Here’s how:
- **DDoS protection**: Levamo CDN will be your first line of defense against DDoS attacks.
- **Secure TLS/SSL**: The CDN will ensure all the data that you transfer is encrypted, keeping your website data secure.
### 5. Seamless Integration
The Levamo CDN is a CDN for WordPress, and it serves its purpose efficiently. Usually, connecting a website to a CDN is a multi-step process. It involves changing domain records, installing plugins, or manually configuring caching rules.
With Levamo CDN, the process is simple, because it’s directly integrated into Levamo hosting. If you use Levamo for your WordPress hosting, then you can turn on Levamo CDN with just one click and start delivering your content quickly.
## Levamo CDN Truly Enhances Your Website Performance
Activating Levamo CDN is super simple on the platform.
All you have to do is navigate to the **Domains Page**, locate your **custom domain**, and select **Turn On Levamo CDN.**
Once done, simply complete the setup in the Modal and wait for activation.
Here’s a guide to help you with everything related to Levamo CDN: [The Complete Levamo CDN Guide](https://support.levamo.com/articles/10189152-the-complete-rapyd-cdn-guide)
Once activated, your WordPress websites can see significant performance improvement like:
- **Up to a 2x improvement** in website performance.
- **Improved Time to First Byte (TTFB)** due to fetching data from our closest servers around the globe.
- **Better stability** during traffic spikes.
If you’re running WooCommerce stores, LMS sites, or membership sites, these improvements can lead to improved user satisfaction, better search engine rankings, and increased conversions.
More business, more satisfaction, more peace of mind! That’s you in a nutshell when you host your websites on Levamo.
## Going Forward
Levamo CDN is available to all Levamo users, and with this, you can offer a superior website experience to your users.
Levamo is already regarded as one of the best [managed WooCommerce hosting](/managed-wordpress-hosting/) and [LMS hosting services](/managed-lms-hosting/), but we’re constantly on the edge to keep improving our products for you.
So while Levamo CDN adds another layer of convenience and better performance for your websites, we’ll keep adding further capabilities and advanced features to further enhance
If you are not already a Levamo user and are looking for WordPress hosting with an integrated CDN for enhanced and powerful performance, you can [try Levamo for free](https://my.levamo.com/free-trial).
Join the most innovative managed WordPress hosting today and experience the difference in performance so many others are enjoying!
Try Levamo Today
## Frequently Asked Questions

### What is Levamo CDN?
Rapid CDN caches and serves content from servers all over the world to speed up website loads, no matter where the user is browsing from.
### How does Levamo CDN improve website speed?
Levamo CDN caches and serves static content on our strategically distributed global edge servers to reduce latency and accelerate website speed.
### Does Levamo CDN offer image optimization?
Yes, Rapid CDN compresses images and converts them to modern formats like WebP to reduce file sizes while maintaining visual quality for faster website performance.
### Is Levamo CDN integrated with Levamo hosting?
Definitely, Levamo CDN works in conjunction with Levamo hosting, and users can activate it with a click without any additional setup or plugins required.
### Is Levamo CDN free for Levamo users?
Yes, Levamo CDN is available for free to all Levamo users, regardless of hosting plan.
---
## Understanding Core Web Vitals and Their Impact on Website Performance
- URL: https://levamo.com/blog/core-web-vitals-and-seo/
- Category: website-performance
- Author: Faisal Sarker
- Published: 2025-01-16
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Improve site speed! Core Web Vitals explained for better SEO and user experience.
Gone are those days when website performance was not a necessity, but just another “nice-to-have”. With the average customer span going lower and lower, website performance is now a critical factor. It can make or break user engagement, conversions, and overall brand perception.
*In light of this trend, Google introduced a set of metrics called “Core Web Vitals” to measure and reward websites offering quality user experience.*
These metrics do not focus on the quality of content itself. Instead, they reflect user-centric performance benchmarks - like page loading speed, interactivity, and visual stability. And now, all of a sudden, your website no longer just depends on content and SEO optimization. A website that scores well on Core Web Vitals metrics is not just more likely to satisfy users and retain their attention longer, but also rank higher in search results. On the contrary, underperforming websites now risk losing out on organic traffic.
And this is just the summary. In this blog, we will go in-depth into the metrics and let you know the Core Web Vitals SEO impact. And finally, we will also share the website speed optimization techniques to get a higher score.
Let’s get started!
## What Are Core Web Vitals - The Metrics

At its core, Core Web Vitals consists of three key performance metrics. They are **Largest Contentful Paint (LCP)**, **First Input Delay (FID)**, and **Cumulative Layout Shift (CLS)**.
These metrics give us universal benchmarks of how quickly a website should load and respond to user inputs.
### Largest Contentful Paint (LCP)
LCP measures how quickly the largest piece of visible content on the webpage appears on the screen. This content is often an image, video, or large text block.
**Benchmark:** You should aim for the LCP to appear on the screen within 2.5 seconds of when the page first starts loading.
**How Does it Impact Website Experience:** Slow loading of LCP means the largest chunk of content is taking time to load. Users will perceive your website to be sluggish and may leave prematurely.
### First Input Delay (FID)
FID measures the time it takes for your web page to respond when a user interacts with it. The interaction can be just clicking a link, tapping a button, or entering data in a form field.
**Benchmark:** You should aim for an FID of less than 100 milliseconds.
**How Does it Impact Website Experience:** A first input delay means that there is a lag between a user’s action and the response from the website. This delay can frustrate the user and may discourage them from taking further action or engagement on your website.
### Cumulative Layout Shift (CLS)
CLS doesn’t measure speed, but rather the change in layout that occurs while your webpage is loading. Most of the time, it is the media content or ads that shift the layout during loading, which can be an eyesore for users.
**Benchmark:** You should aim for a CLS score of less than 0.1 for optimal performance,
**How Does it Impact Website Experience:** Unexpected layout shifts can cause accidental clicks or disrupt the reading experience for the user. If users try to click somewhere on the webpage and find out the next second that it’s not there anymore, it’s normal to create a bad experience for them.
## Tools to Measure Core Web Vitals
Google made it easy to evaluate your website’s performance on Core Web Vitals metrics. They offer [PageSpeed Insights](https://pagespeed.web.dev/) and [Lighthouse](https://developer.chrome.com/docs/lighthouse/overview), both accessible free of charge.
Besides these tools, you can also use the popular third-party [Web Vitals](https://chromewebstore.google.com/detail/web-vitals/ahfhijdlegdabablpippeagghigmibma?hl=en) browser extension or the Core Web Vitals report from Google Search Console for more insights.
- **Google PageSpeed Insights**: It is the most popular way to check the Core Web Vitals score of a webpage. It offers both lab and field data for a webpage, and also reports on the user experience of a page on both mobile and desktop devices and provides suggestions on how that page may be improved
- **Lighthouse**: Lighthouse is an automated tool on Google Chrome, that you can run on any web page, from the Developer Tools option, command line, or as a Node module. It provides a detailed diagnosis of performance issues, plus accessibility and best practices audits.
- **Web Vitals Extension (Chrome)**: An easy way to get a Core Web Vitals score for any website. Just click on the Chrome extension while browsing a website and it will share the real-time metrics for LCP, FID, and CLS as you browse.
- **Search Console’s Core Web Vitals Report**: This is an actionable Core Web Vitals report that you can find on Google Search Console. It helps you see how real-world users experience your site and group pages that are not performing well.
## Why Do Core Web Vitals Matter?
We already shared the importance of Core Web Vitals for your website briefly in the introduction. Now let’s talk more in detail about the two major reasons that it matters for your website.
### User Behavior and Engagement
It’s not that your website will have poor user engagement due to a low Core Web Vitals score. Rather it’s the opposite. The factors that make your bounce rates high, keep your session durations low, and your conversions limited, are the same factor that makes your website perform poorly on Core Web Vitals metrics.
According to various business impact [case studies on web.dev](https://web.dev/case-studies/vitals-business-impact), improving load times and interactivity as suggested by the Core Web Vitals metrics, leads to increased user satisfaction, sales, and readership.
So, Core Web Vitals are proven to be a good way to learn how your users will perceive your website and their potential engagement.
- **For e-commerce**: Website speed can make a difference in whether the user purchases or abandons their cart.
- **For media and content websites**: Slower loading times mean that the users spend less time reading or watching.
- **For SaaS platforms**: Quick response times directly lead to improved trial sign-ups and user retention.
### SEO and Google’s Ranking Factors
The [SEO landscape](/blog/changing-seo-lanscape/) has evolved. There is definitely a Core Web Vitals SEO impact, as these scores are now a central part of Google’s [Page Experience signals](https://developers.google.com/search/docs/appearance/page-experience).
While content relevance still remains key, performance can now influence the scales when two pages have equally relevant content. If you are outperforming competitors in terms of Core Web Vitals score, you will gain a competitive edge for ranking higher and getting more visibility.
## Common Issues That Impact Core Web Vitals Score and their Solutions
Now that we know how Core Web Vitals impacts your website, let’s share exactly the issues that cause the problem and how to improve Core Web Vitals for WordPress sites.
### Optimizing Largest Contentful Paint (LCP)
#### Common Issues Affecting LCP:
- **Slow Server Response Times**: Unoptimized hostings or server configurations are often the reason for high Time to First Bite or TTFB.
- **Render-Blocking Resources**: If your CSS and JavaScript files aren’t well-optimized and minified, or not delivered efficiently, that can block the rendering of the main or large content piece.
- **Large Images**: Using large or uncompressed images can also cause slow LCP.
#### How to Fix Them:
- **Use a Fast Web Hosting Provider**: Choose a hosting provider that prioritizes performance, and offers optimized server configurations. [Levamo](/) can be an excellent choice in this regard.
- **Optimize and Defer Resources**: Minimize or minify CSS and JavaScript bloat. It can be done using third-party plugins or tools if you are not too technologically skilled.
- **Image Optimization**: Compress and resize images that you upload on your website., Try to use modern image formats like WebP.
- **Implement a CDN**: Try to use Content Delivery Networks (CDNs). They cache content across worldwide servers, which reduces the latency and improves LCP for global audiences. If you are a Levamo user, you can enjoy our Levamo CDN for free.
### Improving First Input Delay (FID)
#### Common Issues Affecting FID:
- **Heavy JavaScript Execution**: Large JavaScript bundles often block the server thread. They can create delays when users try to interact.
- **Inefficient Code**: If there are too many functions or scripts, they can occupy the CPU resource. It can lead to the disruption of immediate interaction.
- **Third-Party Scripts**: Too many widgets, analytics, or ads on a webpage can also block main-thread tasks.
#### How to Fix Them:
- **Minimize JavaScript**: You can implement code-splitting and remove unused libraries to avoid heavy JavaScript execution.
- **Defer Non-Critical Scripts**: Load only essential scripts first and defer non-critical scripts until after the main content renders.
- **Optimize Third-Party Scripts**: Third-party plugins or scripts can have a big impact on increasing FID. So if they don’t provide any value, remove them. Or load them asynchronously if they are not very important.
- **Use a Modern JavaScript Framework**: Opt for using modern frameworks like **React**, **Vue**, or **Svelte.** They are known to manage code more efficiently and mitigate main-thread blocking.
### Reducing Cumulative Layout Shift (CLS)
#### Common Issues Affecting CLS:
- **No Dimensions for Media**: If you place images or ads without setting their height and width, the layout adjusts as they appear on the screen while loading.
- **Dynamically Injected Content**: Popups, banners, or chat widgets can also shift the layout.
#### How to Fix Them:
- **Reserve Space for Images and Ads**: Always specify image height and width in the HTML. Or you can use CSS aspect-ratio properties for image placeholders.
- **Avoid Inserting DOM Elements Above Existing Content**: Place dynamic elements at the bottom of the code.
- **Preload Key Fonts**: Preloading fonts to reduce the reflow caused by late font rendering.
- **Use CSS Transformations Carefully**: Don’t use too many elements with CSS transformations. They should only be used strategically.
## How Levamo Hosting Enhances Core Web Vitals
As you can see from the section above, a big part of improving your pages for a great Core Web Vitals score goes back to server-side optimization. And your hosting provider can play a very important role in that.
Choosing [fully managed WordPress hosting](/managed-wordpress-hosting/) can drastically improve your Core Web Vitals scores.
That is where Levamo can help. It is a high-performing web hosting, that impacts multiple performance factors at the same time. By using Levamo with its [WordPress speed secrets](/blog/speed-up-wordpress/), you can significantly enhance your website’s Core Web Vitals. Here’s how Levamo can help you score higher on Core Web Vitals:
### Advanced Caching
Caching plays an important role in reducing server response time and page load speed. With the help of Redis caching and Object Cache Pro, Levamo offers advanced caching features.
When a user requests a page from their browser, the caching ensures that the page loads instantly. Delivering pre-loaded pages instantly improves the LCP score greatly.
### LiteSpeed Web Server Technology
Levamo is powered by the [LiteSpeed Web Server](/blog/lite-speed-hosting-benefits/), known for its optimized architecture and ability to handle large traffic with minimal resource usage. It often outperforms traditional Apache or Nginx setups due to its built-in caching engine, optimized HTTP/3 Support, and ability to power high concurrency.
These features directly impact FID, as scripts and resources are delivered faster and more efficiently.
### CDN Integration
To serve content to a global audience, content should travel shorter distances to users from the physical server. That is what CDN ensures. Levamo CDN’s globally spread-out servers ensure that users face very little latency, no matter where they are.
This fast delivery of resources improves the LCP dramatically while also reducing the chance for CLS issues, as Levamo CDN also compresses images.
## Conclusion
Core Web Vitals is a great way to understand how users perceive your website. Besides Core Web Vitals SEO impact is now real because of it being a part of Page Experience Signals. Whether you manage an eCommerce website, an LMS, or a blog, optimizing your website with LCP, FID, and CLS ensures you get the most out of it.
However, apart from manual configuration, server-side optimization is also crucial for a great Core Web Vitals score. That’s why you should power your website with performance-driven hosting.
Levamo offers you that and more, with advanced caching, LiteSpeed web server technology, and seamless CDN integration. These help you deal with server-side bottlenecks that most people experience from other hosting providers.
Want to explore how much of a difference our hosting can make? [Move to Levamo](/pricing) and get a [Managed WordPress Migration](/free-website-migrations/) for free.
## Frequently Asked Questions

### What are Core Web Vitals, and why are they important for my website?
Core Web Vitals is a set of performance metrics, that includes Largest Contentful Paint (LCP), First Input Delay (FID), and Cumulative Layout Shift (CLS). Introduced by Google, they help to measure different aspects of user experiences on a website like loading speed, interactivity, and visual stability.
### How do Core Web Vitals affect SEO and user engagement?
Google uses Core Web Vitals as part of its Page Experience signals. Thus, Core Web Vitals SEO impact is now confirmed as it is one of the recognized search engine ranking factors. While it doesn’t directly impact user engagement, a website that underperforms in Core Web Vitals is likely to have visible issues hindering user engagement.
### What tools can I use to measure Core Web Vitals?
There are several tools that you can use to measure Core Web Vitals. These include PageSpeed Insights, Lighthouse, the Web Vitals browser extension, or the Core Web Vitals report from Google Search Console.
### How does hosting influence Core Web Vitals?
Hosting directly influences the server response time (TTFB). Apart from high-performing hosting servers, they also ensure that your website's FID and CIS are always optimized by offering optimal loading times using caching and CDN services.
### How can Levamo improve my website's core Web Vitals?
Levamo is a performance-driven, [fast managed WordPress hosting](/managed-wordpress-hosting/) service that helps you improve your website’s Core Web Vitals. Its high-performing server, advanced caching, and Levamo CDN directly improve your Core Web Vitals score. If you are a WooCommerce user, you can also choose their [managed WooCommerce hosting](/managed-woocommerce-hosting/) to achieve a great Core Web Vitals score.
---
## How to Integrate WordPress with CRM & Email Marketing Software
- URL: https://levamo.com/blog/wordpress-crm-email-marketing-integrations/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2025-01-15
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
CRM & WordPress integration streamlines marketing. Click to learn how!
Do you want to integrate WordPress with your CRM? Are you tired of manually exporting and importing leads?
Communication is an essential aspect of business ownership. You need to communicate and build good relationships with your customers to build a lasting brand.
Over the years, communication with customers or website subscribers has become easier with the advent of email marketing integrations for WordPress and CRMs. Most CRM offers all the tools you will need to maintain a database of customer contacts and send them periodic emails based on your preference.
Upgrading your business or website with WordPress CRM integration and email marketing features is important to take advantage of automation, which can save you time and keep your data synchronized.
The [FuseWP WordPress automation plugin](https://fusewp.com/) integrates WordPress with various email marketing integrations for WordPress and CRMs.
## Why Integrate WordPress with Your CRM & Email Marketing Platform
Connecting your WordPress site to your email marketing software or CRM can provide numerous benefits, but we will quickly mention some.
### Improved Data Management
If you do not have a WordPress CRM integration, you will have to perform extensive manual data management and synchronization. To streamline this process, you can also consider using [CDC software](https://hevodata.com/learn/7-best-cdc-tools/) to capture real-time data changes and maintain accurate, up-to-date information across your systems
However, when your systems are connected, you can automate the data synchronization, simplifying your data management process and ensuring updated records across various platforms. This becomes even more critical when using **[best managed WordPress hosting](/managed-wordpress-hosting/)** services that prioritize seamless integrations and platform optimizations, ensuring your data is always synchronized effectively.
### Targeted Marketing Campaigns
One of the biggest benefits of CRM and email marketing integrations for WordPress is “Personalization”.
Personalization enables you to create highly targeted emails and marketing campaigns by leveraging the data from your WordPress site, CRM, and email marketing platform. To boost email deliverability, use an [SPF record generator](https://easydmarc.com/tools/spf-record-generator) to authenticate your domain and avoid spam filters.
When you use WordPress CRM integration, you can access up-to-date data such as purchase history, membership status, demographics, and more.
If you're running an e-commerce site with **[managed WooCommerce hosting](/managed-woocommerce-hosting/)**, integrating these platforms ensures accurate, real-time insights into customer behaviors. This enables you to create list segments, craft targeted campaigns, and send personalized emails that resonate with each user, improving your conversions and engagement.
### Improved Customer Insights
Connecting your WordPress website with your email marketing platform or CRM can provide better insight into customer behaviors, interactions, and preferences. These data points can help you create better-personalized offers and targeted marketing campaigns that resonate with your customers.
If needed, an [email marketing agency](https://impressive.com.au/email-marketing/) can support you in analyzing this data and executing campaigns more effectively.
## Introducing FuseWP?
[FuseWP](https://fusewp.com/) is a marketing automation plugin that synchronizes your WordPress users, forms data, eCommerce data, membership details, and other information between your WordPress site and your favorite CRM.
With FuseWP, any changes to a user’s data on your WordPress site are automatically synced to your WordPress CRM integration and email marketing integrations. There is no longer a need for manual reconciliation or checks. It ensures that all your users' data are updated across all marketing platforms.
FuseWP supports various platforms, including popular ones like Mailchimp, Brevo, Constant Contact, Hubspot, Zoho, Sendy, Campaign Monitor, AWeber, Zoho CRM, Zoho Campaigns, Kit (ConvertKit), Drip, Brevo, HubSpot, MailerLite, Klaviyo, and more.
### Installing And Activating FuseWP
To install FuseWP, go to the [FuseWP website](https://fusewp.com/) to purchase a suitable license. After purchasing a license, you will receive an email with your license key and the plugin download link. Download the plugin to your computer.
Next, log in to your WordPress dashboard, navigate to **Plugins >> Add New**, and click “**Upload Plugin**”.
Upload the FuseWP plugin you downloaded earlier and click the “**Activate Plugin**” button to activate the plugin.
With this done, you have enabled FuseWP, and are ready for CRM and email marketing integrations for WordPress.
## How To Sync WordPress Users to a CRM (MailChimp)
FuseWP integrates with all the popular CRM and Email marketing platforms, but we will use Mailchimp for this article. The process is similar to that of other platforms; just follow the intuitive user interface of FuseWP.
To integrate FuseWP with Mailchimp, navigate to **FuseWP >> Settings**. Scroll to the Integrations section and click the “**Configure**” button under the MailChimp logo to open the popup box.
In the popup box, click the “Connect MailChimp” button.
Once you click the button, you will be taken to the MailChimp website to log in and authorize the connection with FuseWP.
After authorizing the connection, you will be redirected to the FuseWP settings page. A green checkmark should indicate that Mailchimp has been successfully connected to your WordPress website.
### Syncing WordPress Users to Your Email List
Now that you have integrated your WordPress site with Mailchimp, you need to set up the syncing process so that WordPress leads and users are automatically synced.
Navigate to **FuseWP >> User Sync** and click the ‘**Add New**’ button.
On the next page, you must choose a source and a destination. Select the “**User Roles**” as your source.
Next, click the “**+ Add Destination**” button and choose the user role you want to sync. For this article, we will select the “**Any Roles**” option and choose MailChimp as our Integration.
In the “Select Audience” dropdown, select your desired Mailchimp list to which the users will be added.
In the image above, we are syncing all users belonging to any role on our WordPress site to our MailChimp mailing list and sending their First Name and Last Name data to MailChimp. FuseWP also supports syncing custom fields mapped to merge fields in Mailchimp.
In the image below, we are syncing all users with the “**Subscriber**” role to the “**Test List**” audience on MailChimp.
FuseWP can sync all the various user roles available on your WordPress site. To synchronize multiple roles, repeat the above steps to add more destinations with different User Roles.
*For CRMs and Email marketing platforms that support custom field mappings and tagging, you can map or tag your user data to these fields from this synchronization setup page.*
We have successfully configured synchronization between our WordPress users and MailChimp email lists. When someone signs up for our WordPress site, they will be automatically added to our MailChimp list. If they update their information on our WordPress site, the data will also be updated in our MailChimp list.
## Syncing Form Submissions to CRM and Email Marketing Software
FuseWP also synchronizes WordPress form data with your email marketing platforms or CRM. It supports popular WordPress form plugins such as Gravity Forms and WPForms.
This section will focus on syncing data from WPForms entries to a MailChimp email list. We will automatically add users who submit our WPForms form to our MailChimp email list, a process similar to other supported WordPress forms plugins.
Navigate to **FuseWP >> User Sync** and click the “**Add New**” button.
On the next page, you will need to choose a Source and a Destination. For the source, select “**WPForms,**” for the Source Item, select an existing Form you want to sync.
**Note:** You need to have created at least one WPForms form before you can choose a ‘source item”.
Next, click the “**+ Add Destination**” button to select the event that triggers the data sync.
Next, select your Audience and map your custom fields to your MailChimp fields.
In the image above, all users who fill out and submit the contact form powered by WPForms will be added to our “Test List” mailing list on MailChimp and tagged with ‘wp’ and ‘form’.
FuseWP can also add users after they sign up via a form powered by WPForms. In this case, the “**Event**” in our Destination setup will be “**After User Registration**” as shown below.
Once you have completed this setup, you have successfully connected WPForms to Mailchimp and established a reliable WordPress CRM integration and email marketing integrations for WordPress.
Note that FuseWP also integrates various ecommerce, LMS, and [WordPress membership plugins](https://profilepress.com/) like WooCommerce, Paid Memberships Pro, and [MemberPress](/blog/memberpress-review/), Easy Digital Downloads, ProfilePress, [LearnDash](/blog/learndash-review/), [LifterLMS](/blog/lifterlms-review/), so you can use FuseWP to sync your customers and membership data with any CRM and email marketing platform.
And if you're running a membership site with [MemberPress hosting](/memberpress-hosting/), FuseWP ensures your membership data is accurately synchronized, enhancing customer management and marketing automation. Similarly, course creators leveraging [LifterLMS hosting](/lifterlms-hosting/) can take advantage of FuseWP to streamline student data and optimize engagement strategies, all while maintaining a smooth and reliable platform.
## Wrapping Up
The FuseWP plugin offers a simple solution for integrating and syncing your WordPress data with your favorite email marketing solution. It integrates with [email newsletter signup forms](https://mailoptin.io/) to capture and save leads to your CRM.
Keeping in touch with customers is an important aspect of business, and integrating your WordPress website with your CRM or email marketing software can make it easier.
---
## PeepSo Review: A BuddyBoss Alternative to Build Communities on WordPress
- URL: https://levamo.com/blog/peepso-review/
- Category: lms
- Author: Sunyyan Junaid
- Published: 2025-01-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is PeepSo a good BuddyBoss alternative for WordPress communities? Find out here.
Creating an online community today is one of the best ways to build a long-term and sustainable business. Regardless of your skills and knowledge, if you want to monetize your content, now is the perfect time to do it.
When it comes to building a community or social networking websites on WordPress, people usually turn to BuddyPress or [BuddyBoss](/blog/buddyboss-review/). But Peepso plugin is a great alternative that helps you convert an existing audience into loyal buyers and long-time users.
In this **PeepSo review**, we'll dive into its features, performance, and how it stacks up against other community-building solutions, helping you decide if it's the right fit for your website.
Without further ado, let’s jump right into it.
## What is PeepSo?
PeepSo is a powerful WordPress plugin designed to transform any website into a fully functional social networking platform. Whether you're building a private community, a niche social network, or an interactive membership site, PeepSo provides an intuitive, feature-rich solution that integrates seamlessly with WordPress.
With robust tools for user profiles, activity streams, messaging, and group interactions, it rivals major social platforms while giving you full control over your community.
## Should You Choose Peepso?
Peepso is one of the most popular community plugins on WordPress. With over 5,000 active installations, Peepso is an ideal choice for entrepreneurs looking to develop thriving digital communities.
It is important to note that Peepso comes with premium add-ons because the free version has limitations. To enhance the functionalities, you can always choose the add-ons and features to purchase.
## Core Features of Peepso
Peepso has a user-friendly interface and comes with amazing features allowing WP website owners to make custom online communities to their own likings.
Some of the core features are what you’d expect from any good social networking plugin. Here are these in more details:
- Create and manage user profiles with images, avatars, and cover photos.
- Activity streams similar to the likes of Facebook and X Feeds lead to dynamic engagement
- Customizable member directories such as unique groups and communities.
- Support for a number of language options making it truly accessible for your global audience.
- Private messaging allows users to communicate one-on-one.
- User mentions such as a tagging function similar to other social media platforms.
- Push notifications.
Peepso also allows third-party integrations, elevating its functionalities.
## Pros and Cons of PeepSo:
Just like with any other plugin, Peepso has its own set of benefits and limitations. Here are these in more detail:
### Pros (The Good):
- **Feature-Rich:** Offers a comprehensive suite of social networking tools making it easier than ever to build an online community.
- **Customizable:** Change the color, layout and other features according to your own requirements making it highly customizable.
- **Extensible:** Supports add-ons and integrations to expand functionality.
- **Active Development:** Regularly updated with new features and improvements with round-the-clock support, priority maintenance, and more.
### Cons (The Limitations):
Even though Peepso has amazing features to build your online community, you still need some time to figure out how it works:
- **Resource-Intensive:** Peepso does not work best with shared hosting plans. While cloud hosting plans may drive the cost upward, hosting with Levamo provides peace of mind with scalable cloud solutions.
- **Learning Curve:** While generally user-friendly, setting up and configuring all features can take time. Expect to spend anywhere between a few days up to a few weeks to learn how the features work.
- **Premium Add-ons:** Many features are paid and if you are not willing to upgrade such as the ability to send and receive private messages among users, then this may not be the best option for you.
Also Read: [Managed Hosting for BuddyPress](/blog/buddypress-review/)
## Step-by-Step Guide to Setting Up a Social Networking Community with PeepSo
Downloading and setting up Peepso is not difficult, however, the plugin is not available from the WordPress plugin store. You need to visit Peepso's official website to download and install the plugin. Here is how it works:
- **Download the plugin from the website:** Visit Peepso's official website and click **Click here to download**. This will download the plugin in a zip file.
- **Install and Activate:** Head over to your WordPress plugins and click **Add New Plugin. Now browse for the downloaded zip file and install it. You will see the following screen as the plugin is being installed**. Once installed, click **Activate Plugin.**

- **Configuration:** Configure the basic settings, including registration options, email notifications, and privacy settings. You can also see this **Your website might be in danger** notification. If this is the case, then you need to update the PHP version of your website.

- **Customize Appearance:** Customize the look and feel of your community using PeepSo's customization options. You can see that the premium add-ons require an upgrade as this is the free version of the plugin:

- **Change Appearance -** To change the appearance of your online community, head over to **Configuration**>**Appearance,** and on the right you will see the following options. You can change how the name is displayed for the user profiles, the color scheme, avatars, and much more. Feel free to play around with these options to customize and adjust the settings to match your requirements.

- **Create Groups:** Set up initial groups and categories to organize your community. Every group resembles a Facebook feed or a subreddit in Reddit for a true community interaction experience. To check your community participation by user type, head over to Dashboard, and on the right you will see the interaction by demographics:

7. You can also change the settings for Blog Posts. You can customize how the blogs should show up for each user. You can have them shown in the activity feed and right next to the user profile under the **Author Profiles** section. Change the layout of the posts with a two-column layout and assign a limit of text as an excerpt for each blog post.

## PeepSo Pricing Plans
PeepSo offers a free core plugin with optional premium add-ons for enhanced functionality. These add-ons are typically sold as bundles or individual purchases, offering various pricing tiers based on the number of sites you want to use them on. This allows you to scale your investment with your community’s growth.

As of now, Peepso is providing an ultimate sale bundle with an annual 1-site license at just $199. A 5-site license will cost you only $249, averaging $50 per site.
Also Read: [BuddyPress Review](/blog/buddypress-review/)
## Why Choose Levamo with PeepSo?
This is where the power of cloud hosting becomes crucial. PeepSo, with its dynamic content and user interactions, can be demanding on server resources. Shared hosting struggles to provide the necessary performance, leading to slow loading times and a poor user experience.
[Levamo](/), with its high-performance infrastructure, offers several key advantages for PeepSo-powered communities:
- **Scalability:** Easily scale your server resources as your community grows, ensuring consistent performance even during peak traffic. All of this comes at no additional costs.
- **[Speed](/performance/):** SSD storage, optimized servers, and content delivery networks (CDNs) ensure lightning-fast loading times, keeping users engaged.
- **[Security](/managed-security/):** Robust security measures, including firewalls, intrusion detection systems, [DDoS Protection](/blog/preventing-ddos-attacks/), and regular backups, protect your community from threats.
- **Reliability:** We are always here whenever you need. You can count on us to keep your communities online with a 99.99% uptime.
Imagine a surge of new members joining your community after a successful marketing campaign.
On shared hosting, this could lead to server overload and site crashes, eventually turning your members away for good, but not with Levamo. With us, your site will always be ready to manage the sudden peak in traffic.
## The Future of Online Communities and Cloud Hosting
The future of online communities is intertwined with cloud hosting.
There was a time when websites used to be simple and load static content such as blog posts of company pages. For these websites, shared hosting can offer a good value for money.
But with the passage of time, communities started getting developed online. As these communities grew larger and more complex, the need for scalable, reliable, and secure infrastructure became paramount.
This is the gap that cloud hosting fills, with the flexibility and performance needed to support these evolving needs. It has empowered community owners to focus on building engagement, rather than worrying about server management.
## Conclusion
PeepSo is a powerful tool for building engaging online communities within WordPress. However, to truly unlock its potential, pairing it with high-performance cloud hosting like Levamo is essential.
This combination provides the scalability, speed, and security needed to create a thriving and sustainable online community.
## Frequently Asked Questions

### What is PeepSo, and how does it work?
PeepSo is a WordPress plugin that turns your website into a social network. It adds features like profiles, activity streams, friends, groups, and messaging. It allows people to interact with each other, making your website similar to Facebook or Reddit.
### Is PeepSo free to use?
The core PeepSo plugin is free, but premium add-ons are available for additional features. As of now, the minimum option is a 1-site annual license that costs $199.
### How does PeepSo compare to BuddyBoss?
Both are popular social networking plugins for WordPress. PeepSo is generally considered more lightweight, while BuddyBoss offers deeper integration with LearnDash for learning communities. Choosing between them depends on your specific needs. Peepso also offers to migrate your community from BuddyPress and BuddyBoss.
### Can PeepSo handle large communities?
Peepso is designed for community interaction, large or small. However, it requires adequate server resources. Cloud hosting is highly recommended for large communities to ensure optimal performance.
### What hosting requirements does PeepSo need for optimal performance?
While it can technically run on shared hosting, a VPS or cloud hosting solution with sufficient RAM, CPU, and SSD storage is recommended. Levamo provides this ideal environment for hosting small to large dynamic community-driven websites.
---
## Ecommerce Store Not Selling Enough? Here's How To Ensure It Does
- URL: https://levamo.com/blog/ecommerce-site-optimization/
- Category: ecommerce
- Author: Faisal Sarker
- Published: 2025-01-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Boost sales! Optimize your eCommerce store with these overlooked strategies.
As a business owner, one question will always linger in your mind: “Why is my ecommerce store not selling enough?”
This performance-focused mindset is always a great thing to have. It shows drive and ambition. This very question has helped many become category-leading multi-millionaires.
It doesn’t matter whether you’re running a small made-to-order fashion boutique or operating a dropshipping venture - you must always keep an eye on your online store's performance.
## How Can You Improve the Sales of Your eCommerce Store?
When you search online for advice on this topic, most articles will encourage you to review your marketing practices, sales funnels, and site’s user experience. All of these are crucial factors to consider - and you will learn more about them in the following paragraphs.
However, one of the most overlooked aspects of improving sales is eCommerce site optimization.
Now, the question arises:* What is eCommerce site optimization?*
It can be defined as “the art and science of improving content delivery, simplifying purchase actions, and enhancing the checkout process to increase the likelihood of converting visitors into customers.”
Simply put, you need to figure out how your website can help a customer buy a product faster than your competitors.
Ecommerce site optimization is all about boosting the conversion rate.
## 7 Ways To Improve Conversion Rate of Your Ecommerce Site

A conversion rate measures the portion of website visitors who complete specific actions, such as placing an order, subscribing to a mailing list, or filling out a form. It is a fundamental metric for assessing how well a site owner has succeeded in converting visitors into customers.
There are no quick solutions for improving disappointing sales performance. However, if you want a plan, you have come to the right place.
Here is a seven-point checklist that you can use to improve the performance of your online store, technically and financially:
- Improve Your Website's Core Web Vitals
- Choose a Great Hosting Service
- Optimize Your Content (and SEO)
- Test The Sales Funnel
- Check Your Marketing Campaigns
- Use Social Proof and Sales Enhancement Tools
- Invest In Customer Engagement and Support
### 1. Improve Your Website's Core Web Vitals
[Core Web Vitals (CWVs)](/blog/core-web-vitals-and-seo/) are a set of performance metrics, primarily created by Google, that measure how users experience the speed and responsiveness of a website. You can check the CWVs of a web page by using the[ Google PageSpeed Insights tool](https://pagespeed.web.dev/).
The tool assesses a web page for three main things:
1. **Largest Contentful Paint (LCP):** This measures how long it takes for the most significant piece of content on the page to load. The goal is to have this happen within 2.5 seconds.
2. **Interaction to Next Paint (INP):** This measures the responsiveness to user interaction on the page.
3. **Cumulative Layout Shift (CLS):** This measures how much the page layout shifts or moves around as the page loads. The goal is to keep this under 0.1.
These metrics are important because they directly impact how users experience a website. If a page is slow to load, hard to interact with, or keeps shifting around, users will get frustrated and likely leave the site.
For eCommerce sites, having good Core Web Vitals is especially important. Online shoppers expect fast, smooth, and responsive experiences. If an eCommerce site performs poorly on these metrics, it can lead to:
- Higher bounce rates as users get impatient and leave
- Lower conversion rates as users struggle to navigate and complete purchases
- Worse search engine rankings since Google now uses Core Web Vitals as a ranking factor
By optimizing their sites to meet the CWVs targets, eCommerce businesses can provide a better shopping experience, keep more visitors on the site, and ultimately drive more sales. It's a win-win for both the company and its customers.
The key is continuously monitoring these metrics and making the necessary technical optimizations to the site's code, images, and other assets. Over time, improving CWVs can have a big impact on the overall success of an ecommerce operation.
It also **improves SEO performance**, which you can read about in the content optimization section.
### 2. Choose a Great Hosting Platform
You can hire the best coding talent in the world to improve your eCommerce site's performance. However, if your site is deployed on a [fully managed WordPress hosting](/managed-wordpress-hosting/) platform that does not prioritize speed, all your efforts might go to waste.
Most eCommerce business owners do not understand the importance of choosing the correct type of hosting.
Some may rely on out-of-the-box solutions like Shopify, which limit you to cosmetic changes. Others may opt for directly hosting their sites on Amazon or Google Cloud without understanding the complexities of SysAdmin and DevOps. Many might start with a generic shared hosting setup, leading to frequent downtimes and malfunctions.
Hosting can make or break your business. Therefore, always pick a [managed WooCommerce hosting](/managed-wordpress-hosting/) platform that clearly defines what they are delivering. To ensure optimal eCommerce hosting performance, pay close attention to these key hardware metrics:
- **CPU:** Consider it the brain, as it is responsible for running the code (mainly written in PHP) and the OS (mainly some form of Linux). A powerful CPU ensures your web processes and pages run smoothly.
- **RAM:** Imagine RAM as your server's active workspace - it must comfortably fit your entire operating system, web server software (such as LiteSpeed), databases (like MariaDB), and running processes. Higher traffic volumes, especially simultaneous visitors, demand more RAM to ensure your CPU can efficiently process all incoming requests without bottlenecks.
- **Storage:** High-performing web hosts prefer SSD drives for storage. These drives are great for storing all your data, but there is an added benefit. SSD drives allow you to create swap space. When a server reaches peak traffic, there is a risk of RAM maxing out. Once maxed out, the website goes down. To prevent this issue, a swap space gives a bit of buffer for smooth operations.
- **CDN:** A Content Delivery Network (or CDN) is a network of distributed servers that deliver images, videos, and other web assets based on a user’s geographical location. This reduces latency and improves load times. Most hosting companies now offer the option to use CDN (either built-in or third-party) for ecommerce site optimization.
At levamo.com, performance is always a priority. Our hosting plans are built with speed in mind.
### 3. Optimize Your Content (and SEO)
You have already learned about CDNs, and using one is a very good practice. However, if your website attracts traffic but can't convert visitors into customers, the issue might be with its content.
Typically, an eCommerce site has the following types of content:
- **Visuals:** According to an[ eye-tracking study by NN Group](https://www.nngroup.com/articles/how-people-read-online/), visitors scan web pages in a "lawnmower" pattern where eyes go from one side to the other. In the real world, we naturally focus more on objects and stimuli in motion than on static text. This makes visuals - such as images and videos - crucial for engaging visitors and driving sales.
- **Text:** Do not sleep on the importance of getting your text right. From titles to descriptions, each word should help customers make purchase decisions. Try to incorporate SEO keywords creatively. Write for your visitors (and not for the search engines). Use alt text to explain images. Use tables wherever necessary. If you think most of your customers will have similar questions about your products, create an FAQ (frequently asked questions) section on the product pages.
- **Call-to-Actions:** The "Buy" button is the most important piece of text on any ecommerce website. Therefore, it is important to create one that catches attention. Use icons (preferably with text) for CTAs like "Tracking", "Search", "Help", etc. to conserve space and improve content consumption. If there are special offers, highlight them with a CTA that does not clash with the "Buy" button.
- **Navigations:** Many do not consider site navigation a part of a website's content. However, it is as important as images and videos. You need to plan your site navigation properly to avoid losing out on sales. Menus tell customers where they can find something. By putting your products in categories, you can train visitors to make repeated purchases. If you are clueless about creating navigation, just copy your closest competitor.
- **Policies:** Customers will trust you with their money if you are clear about your business practices regarding delivery, returns, and refunds. Do not hide these pages in your navigation. Instead, provide a link to them from every customer-facing web page.
Now, let’s discuss SEO (aka Search Engine Optimization). When you combine user-centric content with speedy hosting and excellent CWVs scores, you slowly and surely start to rank higher on Google and other search engines. Why?
Because SEO is now more focused on site and content optimization than just keyword optimization.
### 4. Test The Sales Funnel
As an eCommerce business owner, you might already be regularly testing the sales funnel. A standard sales funnel begins with your website's home page, proceeds to a category page, then to a product page, and finally ends with the checkout process.
If you use digital ads, the sales funnel can sometimes be really short, like starting on a product page and concluding with the checkout process.
Page load times are usually checked individually, but the overall buying process is rarely checked. While checking and optimizing individual instances is a good practice, the checkout process seldom gets attention. According to a[ 2024 study by Baymard Institute](https://baymard.com/lists/cart-abandonment-rate), 22% of visitors abandoned their carts due to checkout issues.
Due to the nature of the page, the checkout cannot be tested on publicly available tools like Google PageSpeed Insights. This is where you will need on-stack tools like New Relic or Solarwinds. These tools track every event closely and indicate where the problems lie.
For other pages, it is always a good idea to use heat mapping tools like Microsoft Clarity or Hotjar to know how customers engage with your content.
### 5. Check and Measure Your Marketing Campaigns
Marketing campaigns are where you might find a lot of things to fix. If your eCommerce site is new, it's best to start with a "failing fast" mindset. However, you need to understand that marketing takes time to produce results.
Social media ads are a popular marketing strategy that works for all kinds of businesses. However, every social media platform has its own set of best practices. So, it's a good idea to partner with [social media marketing agencies](https://www.sortlist.com/social-media/dubai-ae) to ensure your content is optimized for each platform and stay ahead of ever-changing algorithms. If you are not hiring a specialist, you should study the documentation on creating and managing ads.
Remember to fail fast. Here are some recommendations:
- If a marketing campaign does not provide a return on ad spend (RoAS) of 4 or more after 2 weeks, then the campaign is not yielding good results.
- If you are a new business, do not sit on a failing campaign thinking, "People will come." Change it after a week if the RoAS is less than 3.
- Whether you are new or old, create a long-term awareness marketing campaign. You do not need to check the RoAS of this campaign, as it is created to remind your social media audience about your business.
If you are running search engine ads, here are some recommendations:
- Search engine ads can be costly. Therefore, hire a specialist to run such ads. Work with them to finalize your keywords.
- Google Ads are preferred due to their market share in online search. However, Bing Ads can provide good results.
### 6. Use Social Proof and Sales Enhancement Tools
Building trust and guiding customers through their buying journey is essential in today's competitive online marketplace. One powerful way to achieve this is by using *social proof* - the psychological phenomenon where people are influenced by the actions and opinions of others. Showcasing reviews, ratings, testimonials, or user-generated content on your site helps build credibility and makes potential buyers feel more confident in their purchasing decisions.
But social proof alone isn't enough. Sales enhancement tools - like live chat, exit-intent popups, and personalized recommendations - can boost your conversion rates and reduce cart abandonment. Live chat, for instance, allows real-time communication, addressing customer concerns instantly, while exit-intent popups can offer timely discounts or incentives to prevent cart abandonment.
When customers feel as if others have had a positive buying experience, they are more likely to spend their hard-earned cash. Integrating social proof with other features of your ecommerce site streamlines the buying process and encourages customers to spend. It is an effective approach to increasing interaction and driving sales too!
### 7. Invest In Customer Engagement and Support
Never underestimate the power of human connection. While artificial intelligence (AI) is all the buzz, a[ 2024 Gartner study](https://www.gartner.com/en/newsroom/press-releases/2024-07-09-gartner-survey-finds-64-percent-of-customers-would-prefer-that-companies-didnt-use-ai-for-customer-service) observed that a whopping 64% of the participants did not want companies to use AI for customer service. Therefore, you should have a person if you are considering using live chat for customer support.
However, you can always use the same software for customer engagement. According to [a blog post by customer engagement solution Tidio](https://www.tidio.com/blog/live-chat-statistics/), there are multiple benefits of having a live chat channel on your website:
- Websites with live chat can increase their chances of conversion, with over 63% of customers more likely to make a purchase.
- 38% of customers report being ready to make a purchase immediately after a positive chat session.
- Visitors to online stores who engage with live chat are 513% more likely to convert into customers.
The best part is most live chat solutions have a free plan. Therefore, your starting cost is only the talent you hire and train.
Also Read: [CDN for eCommerce](/blog/cdn-for-ecommerce/)
## Conclusion
Ecommerce site optimization is not a sprint; it’s a marathon. There are no shortcuts to improve eCommerce site performance. It is a multifaceted process with many moving parts. In this post, we have discussed a detailed roadmap of how to speed up eCommerce sites, optimize eCommerce checkout process, and reducing cart abandonment. It’s always a good idea to take a procedural approach to eCommerce site optimization. Always finish one step before starting work on another. This way, you’ll be able to better understand what’s working.
---
## Ultimate Member Review in 2025: Features, Advantages, and Use Cases
- URL: https://levamo.com/blog/ultimate-member-review/
- Category: lms
- Author: Faisal Sarker
- Published: 2025-01-09
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Ultimate Member reviewed! See if it's right for your membership site.
Thinking about building a membership or community website that truly connects with your audience? Membership sites are a fantastic way to grow your online presence, engage users, and even monetize your content. They are perfect for businesses, educators, and developers who want to create value and build lasting communities.
Now one of the top tools for this is the **Ultimate Member plugin**. And why so? Well, it simplifies user registration, profiles, and membership features, all while offering a clean interface and robust options. No wonder it's a favorite among website creators!
In this review, we will go deeper into what makes the **Ultimate Member Plugin** stand out. We will explore its features, benefits, and how it can help you build a fantastic membership site without breaking a sweat.
## Who Should Use Ultimate Member? Our Ultimate Member Review Answers it for You

[The Ultimate Member](https://ultimatemember.com/) Plugin is ideal for anyone creating membership websites. It's user-friendly, lightweight, and doesn't need any coding skills. With its customizable design and a mix of free and premium extensions, you can easily create advanced online communities tailored to your needs. Whether it is user profiles, payment options, or private messaging - this plugin has you covered.
**If you are looking for a powerful solution, we highly recommend giving Ultimate Member a try!**
It is mainly designed for:
- **Businesses** that want to earn money through memberships.
- **Community managers** who build subscription-based groups.
- **Educators and course creators** offer exclusive content.
- **Developers and agencies** create custom membership sites for clients.
*Ultimate Member is a popular WordPress Plugin and the [below details](https://wordpress.org/plugins/ultimate-member/) prove that also:*
- **200,000+** active installations
- **4.5**-star rating
- Supports **PHP 5.6** and higher
- Available in **25+** languages
- Versatile & reliable
## What People Say About Ultimate Member
The Ultimate Member plugin for [WordPress has mixed reviews](https://wordpress.org/support/plugin/ultimate-member/reviews/). Many users like its features, especially how it handles membership management and works seamlessly with WooCommerce and bbPress. It’s clear this plugin can add a lot of value to membership sites.
That said, not everyone finds it smooth sailing. Some users mention setup challenges and feel the interface could be more user-friendly. We also have heard about occasional bugs and plugin conflicts. So it is worth considering both the pros and cons before deciding if it is the right fit for your site.

## 

## Key Features of Ultimate Member
Curious about what makes Ultimate Member stand out? We have explored its features, and here is why we think it is a fantastic choice for creating membership websites. Let’s look into what it offers and how it can simplify your site-building journey!
- **Front-End User Profiles:** Users can create and manage their profiles directly on your websites - no backend access required. These profiles look clean, are easy to update, and are designed to make things simple and user-friendly! It is all about creating a seamless experience.
- **Front End User Registration & Login:** Let visitors sign up and login effortlessly with clean and customized forms. You can adjust these forms to collect the exact information you need. It makes the sign-up and login process smooth and professional.
- **Custom Form Fields:** Build forms that suit your audience by adding custom fields. You can gather all the important details you need whether it is for registration or profiles.
- **Conditional Logic for Form Fields:** Make your forms smarter by showing or hiding certain fields based on what users select. This keeps forms clean and relevant for each person filling them out.
- **Drag-and-drop Form Builder:** Creating forms is a breeze with the drag-and-drop builder menu. No coding skills are required, allowing you to design professional and functional forms in just a few minutes.
- **User Account Page:** Give each user their own account page where they can manage their details, view updates, and handle everything in one place. It is simple, efficient, and user-friendly.
- **Custom User Roles:** Create roles with specific permissions for your members. This feature makes managing users straightforward whether you need it for free or premium tiers.
- **Member Directories:** Showcase your members in searchable and filterable directories. It is a great way to help users find and connect with others in your community.
- **User Emails:** Automate communication by sending customized emails for things like registrations, password reset, and updates. This simple feature helps keep your members informed and engaged without any extra effort on your part.
- **Content Restriction:** Protect specific pages or posts, ensuring only certain members can see them. You can control this access based on user roles or membership levels.
- **Conditional Navigation Menus:** Show different menu options depending on whether users are logged in or what role they have. This keeps making the site experience more personal.
- **Developer-Friendly Tools:** The plugin offers plenty of actions and filters, giving advanced users the flexibility to customize and extend its functionality to meet specific needs. It is perfect for developers who want to take things further.
Ultimate Member is a simple, flexible solution that we believe is perfect for anyone looking to build a membership website. It combines ease of use with powerful features, making it ideal for both beginners and experienced developers.
## Ultimate Member: Pros & Cons
Like any plugin, Ultimate Member comes with its strengths and weaknesses. After testing it ourselves, we have put together a list of the key pros and cons to give you a clear picture of what to expect. Here is what we found:
### Pros:
- It offers everything you need to create a membership site easily.
- The drag-and-drop form builder makes creating forms super simple.
- You can control user access, restrict content, and manage login and restriction pages.
### Cons:
- The response time from the support team could be faster.
- The interface could have some more improvement for a better user experience.
## Ultimate Member Pricing Plans

Ultimate Member provides a range of [pricing options. ](https://ultimatemember.com/pricing/)From a free plan to a more advanced paid option - you will find everything. Here is a simple breakdown of each plan and the features you can expect:
### Core Plugin: Free
The **Ultimate Member WordPress plugin** is free and gives you the basics to build your membership site. With this plan, you will get:
- Basic user profiles
- Simple users’ registration and login forms
- Member directories to help find each other.
- Content restriction options to protect certain pages or posts.
This plan is ideal if you are just starting with this or only need the basic features for your site.
### Extensions Pass: $249/Year
**The Extensions Pass** offers you all the premium features. You will get more flexibility and customization options. This plan includes:
- Full access to all premium extensions.
- 1 Year of email support to assist with any issues or questions
- Unlimited licenses, so you can use the plugin on as many websites as you want.
- 1 year of updates. It keeps your plugin up-to-date with the latest features and functionality.
This plan is perfect if you want to enhance your membership site with additional features.
### Extensions + Theme Pass: $299/year
**The Extensions + Theme Pass** includes everything in the Extension Pass. Plus, it gives you access to the Ultimate Member Theme. It is designed specifically to work seamlessly with the plugin.
- Full access to all premium extensions
- Unlimited licenses for use on any number of sites.
- 1 year of email support to help you with any issues.
- The Ultimate Member Theme helps you design a professional and stylish site with ease.
This plan is the best value if you need a complete package with a theme and all the features.
## Comparison of Features Across Plans
| **Feature** | **Free** | **Extensions Pass** | **Extensions + Theme Pass** |
|---|---|---|---|
| User Profiles | Yes | Yes | Yes |
| User Registration & Login | Yes | Yes | Yes |
| Content Restriction | Yes | Yes | Yes |
| Member Directories | Yes | Yes | Yes |
| Access to Premium Extensions | No | Yes | Yes |
| Unlimited Site Licenses | No | Yes | Yes |
| Email Support | No | Yes (1 Year) | Yes (1 Year) |
| Updates for 1 year | No | Yes | Yes |
| Ultimate Member Theme | No | No | Yes |
### 30-Day Money Back Guarantee
All paid plans come with a **30-day money-back guarantee**. You can just let them know within 30 days if you are not happy with the purchase. They will give you a full refund. Yes, it is that simple!
Each plan is designed to meet different needs. The **Core Plugin** offers basic features to get started. While the **Extensions Pass and Extensions + Theme Pass** give you more advanced tools to create a fully customizable membership site.
## Step-by-Step Guide to Setting Up Ultimate Member
Our **Ultimate Member Plugin review** will walk you through all the steps you need to get started. From installation to setup, we will show you the simple process of getting Ultimate Member up and running smoothly on your site.
### Step 1: Install & Activate

Go to your WordPress admin area. Search for the Ultimate Member Plugin from the plugin directory. Now, you just need to install and activate it. Find the **Ultimate Member > Settings** option in the left menu of your WordPress dashboard.
This opens up the main setup area. Here you can configure all the features of the plugin. You will find the tabs mentioned below:

- General
- Access
- Email
- Appearance
- Advanced
- System Info
Now let us review this tap one by one. Remember there are many options to explore. How you set them up depends on what you want to show, offer, and achieve with your WordPress membership site.
**Tip:** Always click the **"save changes" button in each section to ensure your settings are saved**.
### Step 2: General Settings

- **Pages:** Decide which pages will serve as membership-related pages (ex, profiles, login, and registration). The plugin can automatically create these pages, or you can assign existing ones by selecting them from a dropdown menu.
- **Users:** Customise how users are displayed on the front end. Review each setting and adjust them based on your preferences. If you are ever unsure about a particular setting, simply hover over the question mark icons for helpful explanations.
- **Account:** Configure user account settings to control how accounts appear and function. You can easily add or remove the features as needed, giving you complete flexibility in managing user experiences.
- **Uploads:** Manage uploads and user profile pictures with ease. You can customize image settings and set rules for account users to ensure smooth profile management.
### Step 3: Access Settings

This section lets you control who can access specific content. You can:
- Restrict access to posts, pages, categories, or taxonomies.
- Customize a message shown to users who attempt to access restricted content.
Additionally, under the **"other"** section, you can manage password-related settings and additional restrictions.
### Step 4: Email Settings

Here, you can manage all the email-related functions. A detailed list of email types is provided for you to customize. Tailor each template to suit your needs, adjusting both the layout and content to align with your site’s branding.
### Step 5: Appearance Settings

Control the look and feel of essential plugin elements:
- **Profiles:** Set how user profiles appear.
- **Menus:** Customise navigation menus for users.
- **Registration & login forms:** Style these forms to match your website’s theme.
Test your changes live, refine them as needed, and save them when satisfied.
### Step 6: Advanced Settings

The advanced section offers tools for refining your website and adding extra functionality. You can learn more about the advanced settings [from here](https://docs.ultimatemember.com/article/1902-advanced-tab).
- **General:** Adjust advanced settings to enhance your site or enable new features. This area is for fine-tuning and optimization.
- **Features:** Access and test new tools being introduced to improve user management.
- **Security:** Protect your site by detecting suspicious accounts. Restricting admin capabilities for regular users and enforcing password resets for added safety.
- **Developers:** Contains settings for developers to customize and modify. Non-developers should be cautious when making any changes here.
### Step 7: System Info

This page gives you all the key details about your WordPress site’s setup. It helps you identify areas where you can make improvements.
Also Read: [Managed Hosting for BuddyPress](/blog/buddypress-review/)
## Other Settings in Ultimate Member Plugin
You can explore additional options for forms, roles, and the member directory once you finish setting up the plugin. Simply click on these links in the left menu to start editing and customizing them as needed.
### Set up Forms & User Roles
To manage **"Forms"** and **"User Roles"** in Ultimate Member - go to your WordPress dashboard. Click **"Ultimate Member > Forms"** to edit or create forms and **"Ultimate > User Role"** to manage user permissions.
**Forms:**

- Customise registration and profile forms by adding or editing fields.
- Create unique forms, like member contact forms.
- Link forms to specific user roles for controlled access.
**User Roles:**

- Create custom roles beyond default ones like “Subscriber”
- Adjust permissions for existing roles.
- Set access levels for features and content based on roles.
**Member Directories:**

- Go to the **Ultimate Member > Member Directories** to create a new member directory in the Ultimate Member. You will find only one member directory. However, you can edit it by clicking on the **"edit"** button if you want to add more.
Creating a WordPress membership site is not too hard. While it may take some time, using the Ultimate Member plugin makes the process much easier. It streamlines everything and makes your site more manageable.
## What’s the Best Way to Choose a Platform for Ultimate Member Hosting?
Now, when it comes to hosting a site that has intensive integrations like the **Ultimate Member WordPress plugin**, you will need a platform that’s robust, scalable, and fast.
Membership sites have a lot going on behind the scenes. They handle sign-ups, secure payments, and access to exclusive content. A slow or unresponsive site can make members leave and damage your reputation.
There are a few other considerations here. For one, does the **Ultimate Member hosting platform** offer Content Delivery Networks (CDNs) and caching for faster content retrieval? Next, do we have a **managed WordPress hosting** service that offers a staging demo feature - to test the changes before making them live? Easy access to file manager and database management? Firewall protection? The list can go on - but they are all important.
You don’t want to compromise on your user's data, so you need an **Ultimate Member hosting provider** that does it all - from caching, website hosting, and speed optimization to security and easy access to the database when you need it.
## Why Go For Ultimate Member Performance with Levamo Hosting?
Levamo’s powerful **managed WordPress hosting service** is designed to make your life easier. We take care of all the technical aspects of hosting - ensuring your membership site runs smoothly with fast load speeds and no downtime.
From server maintenance and security updates to automatic backups, we handle it all. In short, you can focus on growing your site while Levamo takes care of everything behind the scenes.
### Why choose Levamo Hosting
Levamo is a great WordPress hosting solution for websites using the **Ultimate Member plugin for WordPress**. Here is why you can try it once for your membership sites:
- **Best for dynamic sites:** Membership websites rely on complex workflows like user registrations, and content restrictions. Levamo is designed to handle [these dynamic sites](/managed-wordpress-hosting/) with ease. It ensures a smooth experience for both users and admins.
- **Scale with your growth:** More people will visit and interact with a site when it grows. This can slow down other hosting solutions. But Levamo uses advanced [servers like Amazon m7a instances](https://support.levamo.com/articles/8890310-comparing-rapyd-plans?). It adjusts resources automatically in real time to handle the extra traffic. In short, your site will always stay fast and reliable whether you are launching a new product or running a big company.
- **Lighting speed for better performance:** Slow loading speeds frustrated users. They might even cancel their memberships. Levamo ensures your pages load quickly. It optimizes hosting settings so members can access your content without waiting. Faster times mean happier users and better performance.
- **Strong security for member data:** Membership sites often deal with sensitive user data, including payment information, and other personal details. That’s why [Levamo](/managed-security/) takes security seriously. It provides free SSL certificates, advanced firewalls, and [DDoS protection](/blog/preventing-ddos-attacks/). This ensures that your site is secure and your members can trust you with their information.
### Here Are Some case studies that showcase Levamo’s success rates
- **Take Back Your Temple:** This wellness platform struggled with slow loading times and that ultimately hurts member engagement. However, they saw a [94% improvement in page speed ](/blog/take-back-your-temple-customer-stories/)after moving to Levamo. This made users stay longer and interact more with the content.
- **E-learning Platform:** An educational platform with 35,000 students faced frequent slowdowns during course launches. However, [Levamo boosted its speed by 300%](/blog/english-pro-tips-case-study/), allowing the platform to support more users - even during pick times.
By pairing Levamo with a membership plugin like Ultimate Member, you will get all the tools and performance you need. It is like a winning combination that ensures your site’s success.
## Conclusion
Ultimate Member is a powerful tool for creating membership and community websites effortlessly. Its flexibility, and user-friendly interface make it a top choice for a variety of use cases. Combining it with Levamo hosting ensures your site runs fast, stays secure, and grows with your needs.
Ready to build your ideal membership site? Start using Ultimate Member today and power it with Levamo hosting for the best performance. Your users will thank you later!
## Frequently Asked Questions

### 1. Is there a free plan for Ultimate Member?
Yes, there is a free core **Ultimate Member plugin** for WordPress. It includes essential features like user registration, login, and content creation. This makes it a great option for starting out without any cost. You can later upgrade to premium plans if you need advanced features and extensions.
### 2. How does Ultimate Member compare to other WordPress membership plugins?
Ultimate Member is known for its simplicity and flexibility. Unlike many plugins, it offers a drag-and-drop form builder and detailed customization options. Its focus on front-end user experience makes it stand out. Additionally, it gets regular updates and has strong strong support that ensures reliability.
### 3. Can I customize member profiles with Ultimate Member?
Yes, customization is one of Ultimate Member’s strengths. You can add custom fields, adjust layouts, and even show user-specific content. This flexibility allows you to create profiles that match your website’s style and your audience’s needs.
### 4. What types of websites benefit from using Ultimate Member?
The plugin is perfect for membership websites, online learning platforms, and community forums. It is also great for any website needing user interactions such as networking or subscription-based platforms.
### 5. How does hosting affect the performance of Ultimate Member websites?
Hosting plays a critical role in your website’s speed and reliability. A hosting service like Levamo ensures fast load times, and scalability for growing user bases and high security. This ensures a smooth experience for your members and reduces downtime.
---
## Dokan Review - Is it the Best Multivendor Marketplace in 2025?
- URL: https://levamo.com/blog/dokan-review/
- Category: ecommerce
- Author: Faisal Sarker
- Published: 2025-01-09
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Dokan review: Build your own Amazon/Etsy in 2025? See if it's the best platform.
Have you ever thought of building your online marketplace similar to the likes of Amazon and Etsy, but didn’t have the financial resources and the expertise? If your answer to this question is a yes, then read on. In this Dokan review, we’ll explore how you can create your own multi-vendor marketplace effortlessly and cost-effectively. We’ve got something great for you in store!
In today’s blog, we’ll be reviewing Dokan, a multivendor marketplace plugin that easily transforms your Woocommerce site into a powerful marketplace.
You can easily create and manage your own online store using Woocommerce. Let’s learn more about the plugin and understand the step-by-step process of installing, setting up and creating your first online marketplace.
**Fun Fact**: Dokan is a word derived from languages commonly spoken in the Middle East and South Asia, which means a shop.*

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## But First, What Is An Online Marketplace?
Before we jump on reviewing the plugin, it is important to first understand what exactly is a marketplace.
Imagine a traditional marketplace such as a flea market. Every seller would sell different types of secondhand goods with each having their own stalls. Buyers would come to this market to browse and buy, easily comparing prices and finding the best deals from multiple sellers under one roof.
Now, let's bring that online.
An ecommerce marketplace is just like that market square, but online. Instead of physical stalls, you have online "shops" or "stores" on a website with a potential to add multiple products. Sellers can open their own online stores on this single platform and sell digital and physical products, subscriptions and downloadable items.
Buyers can easily browse and purchase from multiple sellers without having to visit separate websites for each one.
Excellent examples of multi vendor marketplaces are Amazon, Etsy and Ebay. In classified marketplaces, you can also find OLX and Craigslist.
## What is Dokan, and How Does It Help?

Dokan is an ecommerce plugin for WordPress that easily transforms your websites into a fully-fledged online marketplace. With over **70,000 active installations**, it is the most popular marketplace plugin available WordPress.
Dokan helps you to build a website where you can generate passive income by allowing sellers to set up their own stores and earning a commission everytime they generate a sale.
## Quick Guide to Setup Multi Vendor Marketplace using Dokan
Dokan is compatible only with Woocommerce. If you do not have Woocommerce installed on your WP site, you need to install it first from the plugin section and then install Dokan.
- To install the plugin, head over to **Plugins>Add New** and then search for **Dokan**.

- Once you successfully install the plugin, it will start with a simple 3-minute set up process as follows. Click **Let’s Go** to start.

- Here you can assign basic details about your store. Name your store right next to the **Vendor Store URL.** You can also choose whether you want the Vendor or the Admin to be the Shipping Fee, Product Tax Fee, and Shipping Tax Fee recipients. You can also select Map API keys if you have them and once completed, click **Continue.**

- You can enable or disable the option to allow **New Vendor Enable Selling** and **Order Status Change**. Click **Continue.**

- In this step, you can choose if you want commissions to be based on a fixed percentage of sale, or category based. Choose **Fixed** or **Category Based** from the dropdown menu and specify the percentages for your commission.

- Under the **Withdraw Setup** options, you can enable or disable the option to allow vendors to make withdrawals using Paypal and Bank Transfer. You can also set a **minimum withdrawal limit** and the **Order Status for Withdraw.** Now click **Continue**.

- At this step, you can check or uncheck the recommended features for Dokan marketplace.

- At this step, click **Visit Dokan Dashboard** as Dokan readies your store.

### Visit Your Dashboard
Once you are done setting up, this is how the WP dashboard will look like:

Under the **At a Glance** option, you can see how many vendors you have, the products available for sale, withdrawals made and the overall sales generated by day, month or year. On the right side under the **Overview** category, you can see **Total Sales**, **Number of Orders** and **Commission** generated. You can also use the filters to get your desired information.
### How to Add a Vendor
- To add a vendor, click **Vendors** and on the new page, click on **Add New**.

- In a new popup window, you will see a 3-step process starting from **Account Info** to **Address** and **Payment Options. Start by filling out the basic details for the vendor such as their Full Name, Vendor Picture, Banner, Store Name, Store URL and a Phone Number. All of this information is required to create a store**. Once you have entered in all the details, click **Next**.

- In this step, enter the address of your vendor and click **Next.**

In this final stage, you need to specify the payment options for the vendor. At the end you will also see the following options. Once completed, click **Next**.
- **Enable Selling** - Toggle this on/off to enable vendor to sell on your marketplace
- **Publish Product Directly** - Toggle this on/off to enable vendor to publish products directly to their store.
- **Make Vendor Featured** - Got a vendor that you can feature on the store page? Toggle this option on.

- You will now see a popup confirming successful creation of a new vendor.

## Pricing Plans and Value
The following table highlights a comparison between free and all paid plans for Dokan.
### What’s the Difference Between Free and Paid Plans?
The main difference is that all modules that enhance the functionalities of Dokan are not available in the free version. If you click **Modules** under **Dokan** in the Plugin section, on your right, you will see a list of modules or integrations.

All of these modules are only available in the pro versions. As of now there are nearly 28 Dokan modules that limit the plugin’s performance in the free version. Here are these:
- **WooCommerce Booking Integrations**
- **Color Scheme Customizer**
- **Vendor Product Importer and Exporter**
- **Elementor**
- **Wirecard**
- **Product Enquiry**
- **Product Addon**
- **Shipstation Integration**
- **Single Product Multiple Vendor**
- **Auction Integration**
- **Stripe Connect**
- **Store Reviews**
- **Vendor Analytics**
- **Wholesale**
- **Vendor Subscription Product**
- **Vendor Subscription**
- **Vendor Staff Manager**
- **Store Support**
- **Follow Store**
- **Geolocations**
- **Report Abuse**
- **Return and Warranty Request**
- **Live Chat**
- **Live Search**
- **Paypal Adaptive Payment**
- **ShipStation Integration**
- **Seller Vacation**
There are 4 plans for Dokan Pro, other than the free plan. Among all plans, there are two additional categories; Annual and Lifetime. Annual plans seem a great fit as you can get started without a major upfront investment.
Here are the prices for Annual plans, which are currently at a discounted rate:
- Starter: $127/year (1 site license)
- Professional: $199/year (3-site licenses and 23 premium modules)
- Business: $374/year (5-site license and 39 premium modules)
- Enterprise: $699/year (Talk with the chat support for more information)
Here are the prices for their Lifetime plans:
- Starter: $596
- Professional: $934
- Business: $1,747
- Enterprise: $3,247
### How Does the Competition Stack Up?
There are many multivendor plugins for WordPress that compete with Dokan. While it isn’t technically possible to study them all, let’s review another prominent plugin, WCFM Marketplace.
WCFM Marketplace was launched in 2018 and has 30,000+ active installations, making it the second most popular plugin just after Dokan. It also offers a range of features similar to the top contender.
Both plugins have an easy-to-use interface with the necessary features for admins, buyers and sellers.
While Dokan has over 40 modules for integration, WCFM provides anywhere between 16 to 20 based on the plan that you purchase.
Customer Support for both plugins is also great, providing email and ticket support, knowledge base and forum discussions. Dokan however, takes the lead here with a live chat option that you can use to talk with their team.
Also Read: [CDN for eCommerce](/blog/cdn-for-ecommerce/)
## Who Should Use Dokan?
Whether you’re selling online courses, memberships or physical/digital products, Dokan empowers you to become an entrepreneur.
Dokan has both free and paid versions. For starters, you can easily download, install and integrate Dokan into your Woocommerce website in no more than 15 minutes. Since it is all plug and play, no technical or coding skills are required.
In short, if you are someone passionate to build a brand with long-term returns and profitability, then Dokan is for you.
## What Are the Core Features of Dokan?
A successful marketplace requires customers, buyers and administrators to run and manage it. Dokan has features for all three of them.
Vendors are the backbone of your marketplace because in order to gain traffic and retain customers, there needs to be a variety of vendors selling successfully on your platform.
Listed below are the core features of Dokan:
## Vendor Management
As the website admin/owner, you need to be able to manage all your vendors from the WP dashboard. You can look at all the stores and the products that they are selling.

As discussed earlier, Dokan offers three types of commission structures and these are flat, percentage, and combined with the option of customizing to vendors, categories or products.
### Independent Store
Just like setting up their own stalls or shops, every vendor will have an independent store that can be customized with branding, colors and products. Dokan Multivendor provides a comprehensive frontend order management system for vendors where they can view all orders, statuses, and other relevant information.
They can also see customer details such as name, address, phone number, email address, and the products that were bought.

### Bulk Edit Products
Editing a product or two is not that hard. But when a vendor has multiple products, it gets time consuming to edit them manually. To save this time, Dokan allows each vendor to edit multiple products in bulk such as coupons, price and product status.
### Multiple Product Variations and Shipping Methods
The backend interface can get complicated for a non-technical person despite WordPress having an easy interface. That’s why the frontend product creation feature is a breeze for vendors. Adding to this, vendors can also manage multiple shipping methods and choose one that suits according to their needs.
### Social Login and registration
Allowing your users to sign up and login using their social media platforms is a feature that immediately elevates their trust levels. This simply bypasses a hectic process of signing up with their email addresses, and gives instant access to your platform.
### Access to Financial Statements
The financial dashboard provides important and accurate details of the earnings and expenses for each vendor. They can also see the amounts that can be withdrawn.
### Email notifications
Everytime your customers purchase a product, they receive email notifications with details including the product name, price, date and time.
### Ajax search
Search has become one of the most important functionalities of an ecommerce store. This saves time and allows your customers to search for the product that they are looking for. Taking it one step further, Dokan integrates Ajax live search option, which means that every time your customers search, the search results fetch instantly without reloading the page.
Customers also have the option to search for vendors and products by selecting a location. This further filters out the right vendor that they are looking for.
In an ecommerce market, every second counts and the Ajax search option ensures your customers do not bounce back off.
### Store follow
Just like you can follow any social media profile of your favorite influencer, brand, celebrity or business, your customers can do the same with vendors. So everytime there is a new product launch, news or discounts, customers will receive an email notification.
## Why Choose Levamo for Hosting Your Marketplace Site?
Imagine the frustration of not being able to make a purchase during peak days like Christmas, Easter, Black Friday and New Year’s eve. Multiple timeout sessions and website crashes are all too familiar during peak hours.
You don’t want that to happen to your store, do you?
When many users try to browse products, add items to their carts and complete purchases concurrently, it puts an extra strain on the server. If the infrastructure isn't designed to handle this load, it can lead to slow loading times, frequent website crashes and multiple errors.
Levamo addresses this challenge with a robust and scalable infrastructure. As your site grows, so does your infrastructure, automatically allocating more resources. We distribute traffic across multiple servers, which further ensures consistent performance.
Levamo is designed to handle these abrupt surges in traffic efficiently and often regarded as the [best hosting provider for WooCommerce](/managed-woocommerce-hosting/).
## Customer Success Stories and Testimonials
Although we stand by our offering and claims, the best way to find out is by reading actual customer reviews and testimonials. One of our customers who runs an online school using our [LMS hosting services](/managed-lms-hosting/), witnessed an amazing speed boost of 300% for 35,000 students!
Here is his [testimonial](/blog/english-pro-tips-case-study/).
## Wrapping It Up
That was a wrap!
After going through a thorough review, by now, we’re sure that you’d be able to build your own thriving online dynamic marketplace without any hiccups.
Once only available to investors and tech giants, Dokan now enables anyone with a little upfront investment to make their own dynamic marketplaces.
But operating a robust marketplace requires more than just having an excellent plugin; it demands a solid foundation. This is where Levamo becomes your partner in success.
By providing a scalable hosting environment, your marketplace can handle peak traffic, deliver seamless user experiences, and avoid costly downtime.
Together, Dokan and Levamo offer a compelling solution for anyone looking to launch a successful online marketplace, turning entrepreneurial visions into successful realities.
### What is the best hosting solution for Dokan-based marketplaces?
For large Dokan marketplaces, Levamo’s managed cloud WordPress hosting is the best option to handle peak traffic. You get allocated with powerful server resources, caching, and [free WordPress CDN](/cloudflare-cdn/) to ensure your website loads fast.
## Frequently Asked Questions

### Does Dokan support multiple payment gateways?
Yes, Dokan supports multiple payment gateways, allowing vendors to choose their preferred payment methods. These include MangoPay, Stripe, Paypal, WireCard, RazorPay and Skrill. Dokan’s payment gateways allow you to split the payment so that the vendor gets their revenue minus the commissions that will be paid to the site admin.
### Can Dokan vendors customize their stores?
Yes, Dokan provides vendors with customization options, allowing them to personalize their store's appearance with banners, logos and individual product pages for maximum organic reach.
### Is Dokan suitable for non-technical users?
Dokan is designed to be relatively user-friendly, making it suitable for non-technical users, though some basic WordPress knowledge is helpful. With some workaround, you would be able to set up your own marketplace in no time.
### Is Dokan free to use?
Dokan offers both free and premium versions. The free version provides basic functionality, while premium versions unlock advanced features and integration of dozens of modules that enhance the functionality of your store.
### Can Dokan handle a marketplace with thousands of vendors?
Yes, Dokan can handle marketplaces with thousands of vendors, but proper hosting and optimization are crucial for optimal performance. That’s where Levamo comes in.
---
## BuddyPress Review 2025: Build Powerful Communities on WordPress Easily
- URL: https://levamo.com/blog/buddypress-review/
- Category: lms
- Author: Faisal Sarker
- Published: 2025-01-09
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
BuddyPress 2025: Community building on WordPress made easy! See if it's right for.
Looking to create an online community or social network on your WordPress site? BuddyPress is a popular plugin that makes it easy for us to add social features - helping people connect effortlessly. Whether you want a niche community, a discussion forum, or a private social network, BuddyPres simplifies the overall process. In this **BuddyPress review**, we’ll discuss how it has earned praise for its user-friendly interface, flexibility, and seamless integration with WordPress.
What sets BuddyPress apart is its versatility. It offers essential features like user profiles, activity streams, and private messaging, making it perfect for interactive communities.
BuddyPress has remained a favorite because it’s customizable and works smoothly with WordPress. Developers value its flexibility, while non-technical users appreciate the easy setup. In this review, we will discuss its features and strengths to understand why it’s such a popular choice among many.
## Is BuddyPress Right For Your Site?
If you are looking to add community features to your WordPress site, BuddyPress can be a great option! It has a strong theme compatibility API that ensures BuddyPress pages work smoothly with most WordPress themes. With just a few tweaks to the styling, you can make everything look just the way you want.
But what if you are not happy with the available themes? No worries. You can easily create your own theme or pick from a wide range of options available on WordPress.org or from third-party sites.
Plus, many BuddyPress users rave about how easy it is to integrate bbPress for forums and Akismet for spam protection. Both tools can be easily customized to fit your specific needs, making it even easier to build a secure and engaging community.
*BuddyPress has earned its popularity among *[*WordPress*](https://wordpress.org/plugins/buddypress/)* users and the following details highlight that:*
- **100,000+** active installations
- **4.1**-star rating
- Supports PHP **5.6** and higher
- Available in **48+** languages
- Supports over **8.1 Million** user profiles on WordPress.
## Should you choose BuddyPress? Our BuddyPress Review Answers it For You

*Thinking about adding social networking features to your WordPress site?* BuddyPress might just be the perfect fit. It is designed to create online communities that bring people together. Whether it is a nice network, a forum, or a group hub, BuddyPress gives us all the tools to make it happen effortlessly!
Here are the reasons you should consider it once:
- **Easy to use:** This plugin is designed with simplicity in mind, making it incredibly easy to set up. Even if you don’t have much technical skills, you will still find the process straightforward.
- **Official and trusted:** BuddyPress is an official WordPress Plugin. It powers over 8.1 million user profiles on WordPress.org. That includes well-known profiles like [djpaul](https://profiles.wordpress.org/djpaul) and [boonebgorges](https://profiles.wordpress.org/boonebgorges).
- **Theme compatibility:** BuddyPress works seamlessly with almost all WordPress themes, ensuring smooth integration. Plus, it provides a compatibility layer, making customization effortless and tailored to your needs.
- **Engaging tools:** You can create profiles, post in groups, make friends, and do a lot more using BuddyPress. These features make your site interactive and fun for users.
- **Extensive Add-ons:** With over 1200 BuddyPress plugins available - it gives you endless options to expand its features and tailor it perfectly to your community’s needs.
This plugin is worth considering if you want to build an active online community. It is flexible and has strong support from its users.
### Case Study: Total Wellness Challenge with BuddyPress
[The Total Wellness Challenge (TWC)](https://buddypress.org/2017/05/total-wellness-challenge-fitness-with-buddypress/), created by Ginny Wright, moved from a paper-based system to an online platform using BuddyPress. This shift helped TWC to provide private subtitles and member-only access. Plus, features like daily point logging, leaderboards, and group reflections took member engagement to a whole new level.
**It is a great example that shows us how BuddyPress can transform a community into something much more interactive and dynamic.**
BuddyPress helped TWC in several ways,
- **Increased engagement:** Interactive tools helped community participation and keep members engaged.
- **Easy Scaling:** Managing multiple challenges, including corporate programs, became simple and efficient.
- **Simplified Management:** Automated tracking significantly reduced admin workload, making engagement a breeze.
This change made TWC more user-friendly and effective for participants in their wellness journeys.
## Key Features of BuddyPress
When it comes to creating social networks and online communities, we think BuddyPress truly shines. But why is it so effective? It’s all thanks to its amazing features that have already helped countless websites grow. Curious about how it can transform your site? You can take a quick look at what BuddyPress can do to help you create vibrant, interactive spaces.
### 1. User Profile
BuddyPress lets users make detailed profiles with personal info and photos. You can tweak these profiles to match what your community needs and give each member their own unique space.
### 2. Activity Streams
BuddyPress features an activity stream where members can post updates and share content, much like a social media feed. This keeps everyone engaged about what's happening in the community.
### 3. User Groups
You can set up groups for members to join with this plugin. These groups can be open to all, private, or hidden. They also give people a place to chat and share things with others who have the same interests.
### 4. Private messages
BuddyPress lets users send direct messages to each other. This feature makes the experience more personal and interactive for members.
### 5. Friendship System
BuddyPress includes a built-in friendship system. Members can send friend requests, accept or decline them, and manage their connections. This makes it easy for members to build and maintain relationships within the community.
### 6. Notifications
BuddyPress sends notifications to users when they have new messages, friend requests, or group updates. This keeps the members informed about the important events and interactions within the community.
### 7. Extended Profile Fields
BuddyPress lets you add custom fields to user profiles to collect specific information like interests, skills, or other details. This helps create a profile that fits your community's needs.
### 8. Activity Filters
BuddyPress provides filters that let members sort posts by type. This makes it easier to find relevant content and engage in meaningful interactions.
### 9. Multilingual support
This plugin also supports multiple languages, making it a great choice for building global communities. You can translate your site’s content into different languages to reach a wider audience.
## Drawbacks of BuddyPress Compared to BuddyBoss & PeepSo
When you compare BuddyPress to BuddyBoss and PeepSo, there are a few things to keep in mind. While BuddyPress is a solid choice for building online communities, it does have some drawbacks when compared to these other options. Let’s take a closer look at how BuddyPress stacks up.
### 1. Design & User Experience
- **BuddyPress**: The design is a bit outdated and not user-friendly.
- **BuddyBoss:** It offers a modern and visually appealing design.
- **PeepSo:** Offers users a sleek and modern interface that is similar to any popular social media platform.
### 2. Features & Functionality
- **BuddyPress:** It offers basic features but requires plugins for advanced functionality.
- **BuddyBoss:** You will get comprehensive features built in.
- **PeepSo:** Essential features are free, but advanced ones need paying add-ons.
### 3. Support & Updates
- **BuddyPress:** Community-driven support, less frequent updates.
- **BuddyBoss:** Dedicated support with regular updates.
- **PeepSo:** Good support but updates may disrupt customizations.
### 4. Cost
- **BuddyPress:** Free to use but additional plugins will cost you money.
- **BuddyBoss:** Requires a paid license that includes support and updates.
- **PeepSo:** Free version with paid add-ons for advanced features.
### 5. Compatibility & Integration
- **BuddyPress:** Works well with most WordPress plugins but compatibility can vary.
- **BuddyBoss:** Smaller but more cohesive ecosystem.
- **PeepSo:** Growing community that focuses on social networking.
We found a few drawbacks when comparing **BuddyPress with BuddyBoss and PeepSo. Indeed BuddyPress is a solid choice for building online communities. However, it lacks some advanced features and customization options that BuddyBoss and PeepSo offer**.
These alternatives come with **more out-of-the-box solutions** and better user experience, especially those looking for more polished and feature-rich platforms.
## BuddyPress Pricing Plans
BuddyPress is a free plugin that you can easily install and use on your WordPress site without spending a dime. However, you might come across some costs if you decide to explore certain add-ons or themes. These extras are optional. But they can help enhance your features and the overall experience of your BuddyPress-powered community.
### 1. Free Version
The core BuddyPress plugin is free to use. It offers all the basic features needed to create a community. That includes user profiles, activity streams, and messaging.
### 2. Premium Add-ons
You may want to purchase premium add-ons for advanced functionality. These add-ons enhance BuddyPress with additional features such as
- **BuddyPress Profile Builder:** Customise member profiles with more fields and options.
- **BuddyPress Member Types:** Organize members into custom types to make it easier to manage and display user groups.
- **BuddyPress Private Community:** Creating a fully private community for registered members only to get access to content.
- **BuddyPress Member Review:** It lets users leave reviews and ratings for other members, creating a more interactive community experience.
### 3. Themes
BuddyPress works with most WordPress themes. However, there are premium themes designed specifically for BuddyPress as well. These themes may come with a cost but are designed to work seamlessly with BuddyPress features. In simple words, BuddyPress itself is free. But you can choose to pay for additional add-ons, and themes to enhance your site.
## Step-by-Step Guide to Setting Up BuddyPress
In this BuddyPress review, we will tell you in detail how to get started with the BuddyPress Plugin in WordPress. Setting the BuddyPress plugin is pretty straightforward. Make sure you have the latest version of WordPress on your site before installing BuddyPress. There are two ways to install **BuddyPress: Automatic and Manual**. We will discuss them both in the section below:
### 1. Installing and Activation (Automatic)
- Log in to your WordPress admin panel
- Navigate to your dashboard.
- Select **Plugins > Add New** from the menu
- Now search for “BuddyPress” in the search bar
- Click **Install** and hit **Activate**
- A Welcome screen will appear once activated.

### 2. Installing and Activation (Manual)
Installing BuddyPress manually is simple. Here is how to do it:
1. [Download the BuddyPress plugin](https://wordpress.org/plugins/buddypress/) from the official website.
2. Use an FTP program to upload the plugin file to the **wp plugin/plugins** folder on your server.
Not familiar with FTP? No problem! You can install it directly through WordPress instead.
3. Log in to your WordPress admin dashboard.
4. Go to **Plugins > Add New** and Click on **Upload plugin.**
5. Click **Choose File** to locate the BuddyPress file you downloaded.
6. Select the file and click **Install Now.**

Just click the **Activate plugin** once the installation is complete. That’s it. Your BuddyPress plugin is ready to use.
### 3. Enabling BuddyPress Components
BuddyPress includes ten optional components you can turn on or off based on your needs. You don’t have to activate everything - just choose the ones that you find relevant to your site. Simply follow these steps to activate the components you require.
- Head to **Settings > BuddyPress** in your WordPress dashboard.
- Click on the Components tab.
- You will see a list of all available components.
- Check the boxes for the components you want to activate or uncheck to deactivate.
- Click on the **Save Settings** button to apply changes once done.
Now your BuddyPress components are ready to use.

### 4. Configuring the BuddyPress Plugin
It is time to configure BuddyPress settings once you have set up the components.
- Navigate to WordPress **Settings > BuddyPress**
- Open the Options tab to access the configuration settings.
You will find various features with enable or disable options in the Options tab. Choose the ones according to your needs and then click on **Save Settings** to apply the changes. You will find the following features under this tab:
- Account Settings
- Community Members
- Extended Profiles
- User Groups
- Activity Streams

Setting up BuddyPress is quick and easy. You can create a dynamic community platform with the right components, pages, and settings. It helps you engage users and grow your sites effortlessly.
## Why BuddyPress Sites Need Managed Hosting for WordPress
Ever thought about what makes [BuddyPress hosting](/buddypress-hosting/) unique? Well, it needs a hosting provider that can handle dynamic content, user interactions, and growing online communities. They offer features like activity streams, private messaging, and user groups. Now, these need a hosting service that can handle constant database queries and sudden traffic spikes.
And **[BuddyPress hosting](/buddypress-hosting/) reviews** suggest that many get it wrong.
Now your site might become slow, crash under pressure, or face security risks without good hosting. That is why choosing a reliable and [best managed WordPress hosting](/managed-wordpress-hosting/) is important. It ensures your site runs smoothly and gives users a great experience every time.
## Levamo: The Best Hosting Solution for BuddyPress
**[Levamo](/)** is a managed WordPress hosting service for high-performance websites. It offers speed, reliability, and user-friendly features. For BuddyPress site owners - Levamo offers everything you need to keep your site running smoothly.
### Top features of Levamo for Hosting BuddyPress
**BuddyPress hosting requirements** can seem significant, but Levamo has done all the groundwork for you. Here is why you will love us as a **BuddyPress hosting** provider.
- **Litespeed Web Servers:** Levamo utilizes [LiteSpeed Web Server](/blog/lite-speed-hosting-benefits/) - known for exceptional speed and efficiency. These servers are basically designed to handle high-traffic situations with ease. This ensures your website remains fast and responsive even during high-traffic surges. LiteSpeed servers are designed to deliver optimal performance when you host large community sites - like one powered by BuddyPress.
- **Object Caching**: Object caching stores frequently accessed data in memory for quick retrieval. This reduces server load and speeds up your site. It is perfect for active community sites like BuddyPress, which ensures a smooth experience even when many users are online.
- **Free Levamo CDN:** Levamo [free WordPress CDN](/cloudflare-cdn/) helps your website load faster by quickly delivering content to visitors - no matter where they are in the world. It reduces the time it takes for your page to load, saves bandwidth, and makes browsing your site smoother for all.
- **Built for Media-rich sites:** BuddyPress sites often have lots of photos, videos, and interactive elements. Levamo ensures the smooth handling of media-heavy pages seamlessly.
- **Optimized for WordPress:** Levamo is designed specifically for WordPress websites. It takes care of hosting tasks like updates and backups so you can focus easily on our site growth.
### Why Levamo is perfect for high-traffic sites
At Levamo, we understand that BuddyPress sites can grow rapidly and attract large numbers of users. That’s why we have Java designed our platform to handle these challenges seamlessly.
- Levamo grows with you as your user base grows. Its scalable infrastructure adapts to your needs no matter the size of your community.
- Levamo delivers fast loading times with the LiteSpeed Web Server and built-in CDN. This keeps users happy and engaged.
- Member privacy is crucial for high-traffic sites. Levamo offers [top-tier security](/managed-security/) to protect sensitive information and keep your community safe.
## Customer Success Stories
### 1. GetAConnect:
[GetAConnect](/blog/getaconnect-customer-stories/) moved to Levamo for better performance. The transition resulted in faster page loading time and improved satisfaction. Their BuddyBoss site now can handle thousands of users seamlessly.
*“Levamo cloud hosting was a very important decision for our business” stated Chanakya Joshi, the Founder of GetAConnect.*
### 2. Mind the Grad:
[This educational platform](/blog/mind-the-grad-customer-stories/) uses Levamo to support its media-rich pages. They saw dramatic speed improvements and had critical bugs fixed after switching.
*“My customers said that it feels like a new website. Customer feedback improved, and so did the time spent on the platform,” stated Valeria Loureva the founder of Mind The Grad.*
These case studies show that with Levamo, you are not just getting hosting - you are getting an upgraded experience for your entire site.
## Conclusion
BuddyPress is a powerful tool for creating online communities on WordPress. It offers features that make building a social network easy and customizable.
And BuddyPress works even better when paired with Levamo. Levamo’s fast and reliable hosting ensures your BuddyPress site runs smoothly even as your community grows.
The combination of BuddyPress and Levamo provides the perfect foundation for a seamless and high-performing community experience. Together they make managing and growing your community easier and more efficient.
## Frequently Asked Questions

### Is BuddyPress free to use?
Yes, BuddyPress is completely free to use. You can install and set it up on your WordPress site at no cost.
### What kind of websites can I create with BuddyPress?
BuddyPress lets you create social networks, community forums, or any site that needs interactive user features like profiles, activity streams, and messaging.
### Can BuddyPress handle larger user bases or communities?
Yes, BuddyPress can handle large communities. It can scale to support thousands of users and active interactions when you use a good hosting service like Levamo.
### How does BuddyPress integrate other WordPress plugins?
BuddyPress integrates smoothly with many other WordPress plugins. It works well with plugins for SEO, security, content management, and more. That ultimately helps to enhance your community features.
### Are top WordPress themes compatible with BuddyPress?
Yes, most top WordPress themes are compatible with BuddyPress. Some themes are specially designed for BuddyPress which ensures better integration and appearance.
---
## MemberPress Review: Build Great WordPress Membership Websites
- URL: https://levamo.com/blog/memberpress-review/
- Category: membership
- Author: Faisal Sarker
- Published: 2025-01-07
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is MemberPress the right WordPress membership plugin for your site? Read on.
Thinking about starting a membership site? This MemberPress review will help you uncover whether this plugin is the ultimate solution for your needs. It is such a fantastic way to share what you know - and connect with people who love the same things you do. Plus, it is an excellent way to earn a steady income. You can turn your skills into paid content - whether it is blogs, videos, or courses.
Now let’s be real - it can feel overwhelming to maintain the entire thing on your own. You need the right tools to make it all work smoothly. Something that handles payments, content, and all the little details.
That is where **MemberPress comes in.** It is like your secret weapon for building a membership site on WordPress. Easy to use and perfect for beginners. It is designed to grow with you and offer you tools to scale your platform as your audience grows. Now let us break down why MemberPress might be the perfect fit for you in the review below.
## Who is MemberPress For? Our MemberPress Review Answers it All.
[MemberPress](https://memberpress.com/) is for those who want to create a membership site and share their content. It caters to creators, businesses, and educators - aiming to transform their passion into a steady income.
The MemberPress WordPress plugin allows you to manage memberships and deliver content without hassle. Whether you’re a blogger sharing premium content, a teacher creating engaging courses, or a business owner building a loyal community, MemberPress will empower your journey.
The statistics also show that **[MemberPress has earned the trust](https://6sense.com/tech/wordpress-plugins/memberpress-market-share?)** of many,
- **Current Customers:** 8,057 businesses use MemberPress.
- **Global Ranking:** MemberPress ranks #25 among WordPress plugins.
- **Market Share:** It holds an estimated 0.12% of the market.
- **Growth in 2024:** Over 7,455 companies adopted MemberPress this year.
- **Top Industries:** Education (139), Training (110), and Marketing (105) lead in using MemberPress.

Here are also some cool facts that you should know. Thousands of creators are using MemberPress and **[have earned over $1 billion in revenue!](https://memberpress.com/blog/memberpress-customers-pass-the-1-billion-benchmark/)**. [Pilatesology](https://pilatesology.com/), for one, has relied on MemberPress for years and has become a leading platform for at-home Pilates videos.
**Founders Jack Coble and Alisa Wyatt** say their success comes from MemberPress’s easy settings, ready-made pages, reminders, and key integrations. It is also called “the gold standard for online Pilates” by [CBS News](https://www.cbsnews.com/pictures/the-best-online-fitness-classes-for-slim-budgets/).
**Chris Lema** also stated *“MemberPress is killing it! They are moving and progressing better and faster than anyone out there in this space. It’s impressive.”* These success stories are proof of how powerful this plugin can be!
And the membership industry is growing really fast. Subscription services in the US alone saw a rise from 182 million users in early 2020 to 205 million. So if you're mulling over starting your own membership site now is an excellent time to do it with MemberPress.
## Key Features of MemberPress
So yes, MemberPress is great. The community around it is testament to that. But the question is, what makes it great? And the answer is in the features. It’s a solid one stop solution for all your membership website needs and here’s what it gives you:
- **Quick & easy setup:** No tech skills? No problem. MemberPress is super easy to install. You can create membership plans and set prices. You can even lock your content with just a few clicks. It is all designed to get you started fast.
- **Content Control:** Want certain pages or posts to be for members only? MemberPress lets you decide who sees what. You can restrict content based on pages, posts, and even files. You will be in full control of what your audience can access.
- **Easy Payment Options:** Handling payments is super simple with MemberPress. It works with major payment platforms like **[Stripe,](https://stripe.com/in)** and **[PayPal](https://www.paypal.com/in/home)**.You can also set up recurring payments for subscriptions. So there will be no extra hassle for you or your members.
- **Built-in Course Builder:** MemberPress makes it simple when you are offering online courses. Its built-in course builder is easy to use and does not need any extra tools. You can create lessons and even track your progress right within your MemberPress courses LMS platform.
- **Drip Content:** You can keep members coming back more with timed content releases. MemberPress lets you drip content over time. So it keeps your members engaged and excited for the next piece of your course or content.
- **Flexible Membership Plans:** You can create membership levels according to your needs. It offers free trials, limited discounts, and exclusive plans. It is all customizable to fit your business needs.
- **Email marketing made easy:** Staying in touch with members is key. MemberPress integrates with email tools like **Mailchimp** and **[Kit](https://kit.com/?gad_source=1)**. You can send welcome pages, promotions, or updates without any extra work.
- **Detailed Reports:** You can know how your site is doing with this plugin. MemberPress gives you clear reports on your memberships, revenue, and user activity. It helps you understand what is working and where you can grow.
- **Customizable coupons:** Boost your sales with special offers. MemberPress lets you create customizable coupons with set expiration dates and usage limits. This keeps your members coming back for more!
### MemberPress: Pros
- Easy to set up
- Handles taxes automatically
- Provides detailed reports to track performance
- Offers many customizable email templates
- Flexible content dripping and expiration options
- Allow membership segmentation with groups
- Responsive and helpful customer support
### MemberPress: Cons
- Costs increase with advanced features
- Limited customization options for branding
- Forums and other bumps are only in the higher-priced plans
## MemberPress Pricing Plans
MemberPress has three [pricing plans](/pricing/) for different needs. Whether you are just starting, running a small business, or a pro - there is a plan for everyone. Here is a quick look at each plan offers:

- **Basic Plan:** The basic plan is great for beginners starting their first membership plans. It gives you all the tools you need. You will have unlimited courses, lessons, and members. It is simple and affordable. And it gets your job done without any unnecessary complexity.
- **Plus Plan:** It is ideal for small businesses, freelancers, and entrepreneurs looking to expand. It comes with advanced marketing integrations. You will get unlimited quizzes and certificates in the LMS features. And will also get tools like Zapier and HelpScout. This plan helps you grow your membership site while offering more customization and functionality.
- **Pro Plan:** It is basically for professionals and advanced users managing multiple membership sites. This plan gives you tools like corporate account sales, order bumps, and assignment grade books. It comes with premium features and offers you top-notch support. So you call it your ultimate choice for achieving big results.
## Comparison of Features Across Plans
| **Feature** | **Basic** | **Plus** | **Pro** |
|---|---|---|---|
| Price | $179.50/year (save $179.50) | $299.50/year (save $299.50) | $399.50/year (Save $399.50) |
| Best for | It is for beginners | For entrepreneurs & freelancers | Pros & advanced users |
| Sites Allowed | One Only | Offer up to two | Offers upto three |
| Courses & Lessons | Unlimited | Unlimited | Unlimited |
| Quizzes & Certificates | Basic | Unlimited | Unlimited |
| Gradebook for Assignments | No | No | Yes |
| Advanced Integrations | Basic Integrations | Zapier, HelpScout, podcast memberships | Corporate accounts, gifted memberships |
| Payment tools | Stripe & PayPal | All basic + advanced order tools | TaxJar and Authorize.net integrations |
| Marketing Features | Drip content, email automation | Forums, communities, advanced customizations | All Plus+order bumps at checkout |
| Extra | ReadyLaunch™ Page Maker | 3 months TrustPulse & OptinMonster | All Plus+ Exclusive OptinMonster access |
| Support | Standard | Priority | Premium |
The basic plans are great for those starting their first site. The Plus plan is for users looking to grow their business with more integrations and tools. The Pro plan delivers premium features and support to manage multiple sites. Pick the one that fits your needs and start your membership journey today!
## Step-by-Step Guide: How to Set Up MemberPress
In this MemberPress review, we’ve also covered how to get started with the Memberpress Plugin in WordPress. This guide will take you through every step. From installing the plugin to setting up memberships - we will discuss everything here.
**Step 1: Install & Activate the Plugin**
- Download the plugin zip file from your user dashboard after you sign up for MemberPress.
- Log in to your WordPress admin area and go to the Plugin menu.
- Click **Add New** and then select the **Upload Plugin** option at the top.
- Use the **Choose File** button to locate the MemberPress zip file you downloaded.
- Click **Install Now** to start the installation process once you selected it.
- Now click the blue Activate Plugin button after the installation.
To ensure the plugin works correctly and receives updates:
- Navigate to the **Settings** menu in MemberPress and open the License Tab.
- Enter your license key which you can find in your MemberPress dashboard.
**Step 2: Set Up a Payment Method**
It is essential to know how payments can be handled before adding the memberships.
- Go to the payments tab in the MemberPress **Settings** menu.
- Click the Add Payment Method button (indicated by a “+” sign)
- Select a payment option you can choose from:
- Stripe
- F
- Authorize.net
- Offline Payments
- Add a name for the payment method (used internally) and fill in the required details.
**For example, if you select Stripe:**
- You need to enter a name for that method. Now click on **Connect with Stripe** to link your website with your Stripe account. Follow the wizard that guides you through the connection process. Click Update to save the payment method once it is completed.
Additional options in the **Settings** menu:
- **General Tab:** Configure currency defaults and SEO settings.
- **Taxes Tab:** Enable features like Stripe Tax to automatically calculate taxes for Stripe payments.
**Step 3: Create Membership Levels**
Membership levels allow you to offer different plans to your users. To set them up:
- Go to the **Memberships** menu in the left-hand sidebar and click **Add New.**
- Use the editor to add a title and description for your membership level.
- You can set the price and billing type in the **Membership Term** section. Choose between a **one-time payment** or a **recurring payment.**
You will see the following options for recurring payments:
- **Interval:** You can set payment intervals (ex, weekly, monthly, and yearly)
- **Trial Period:** Specify the duration, price (or keep it free), and whether to allow only one trial.
- **Limit Payment Cycles:** Specify how many payments a member can make before their subscription expires. Or if they will have lifetime access.
Next, customize the membership settings in the Membership Options window. This includes four tabs:
- **Registration:** Edit the signup button text and welcome email
- **Permission:** Control who can sign up.
- **Price Box:** Customise how the price will be displayed.
- **Advanced:** Manage URLs like the login redirects and membership access.
You can also add a featured image from the sidebar. Click **Publish** to make the membership level live when everything is ready.
**Step 4: Create Rules for Memberships**
Rules let you manage how members access your content. Here is how to create them:
- Go to the Rules menu in the sidebar and click **Add New.**
- You will see three main sections there:
- **Content & Access:** Select the type of content you want to protect (ex, posts, pages, categories, tags) and set access to these conditions.
- **Drip/Expiration:** Schedule when content becomes available and when it expires.
- **Unauthorized access:** Override global settings to customize what non-members see like a teaser or redirect.
Save your rule when everything is set up.
**Step 5: Add-ons and Integrations**
MemberPress supports many add-ons and third-party integrations to expand its functionality.
**For example:**
- Use a China Payments Plugin add-on and third-party integrations to expand its functionality.
- The Importer Tool helps you transfer your existing members if you are switching from another platform.
**To install an add-on:** Go to the Add-ons page and find the add-on you need. And then click Install Add-on within its widget.
You can quickly set up the MemberPress plugin by following these simple steps. And you can start offering memberships on your WordPress site. The plugin will offer you everything you need to manage a successful membership website!
## Levamo: The Ideal MemberPress Hosting Partner
Running a membership site smoothly needs reliable managed WordPress hosting. Without a robust hosting solution, your website will be slow and can frustrate your members. That is where Levamo shines, and is one of the [best web hosting for membership websites](/memberpress-hosting/). It truly delivers as the best [MemberPress Hostin](/memberpress-hosting/)g option you can get out there.
This means it will handle all the technical details for you. That includes updates, security, and performance. You do not have to worry about the server or troubleshooting issues. It ensures your WordPress site runs smoothly and performs at its best. That ultimately helps you focus on growing your membership site.
### What makes Levamo so great?
Levamo’s managed WordPress hosting service offers free Object Cache Pro to offer blazing fast site speeds, but that’s not the only reason to get the hosting for your membership website. Here is a look at why Levamo can be a top choice.
- **Optimized for dynamic sites:** [Levamo](/) is built for websites that can handle a lot of features like MemberPress. It keeps your site [fast and responsive](/managed-wordpress-hosting/) even when many members are online. No slow load times or crashing during peak hours.
- **Scalability:** Levamo is [designed on Amazon m7a instances](https://support.levamo.com/articles/8890310-comparing-rapyd-plans?). This means your site gets a reserved number of vCPUs to handle traffic. But it does not stop here. Levamo can adjust in real time if your platform suddenly gets more visitors. It adds more resources when needed to keep your site running smoothly. Your site will not slow down whether you have 100 visitors or 10,000.
- **Super-fast speeds:** Speed is everything for membership sites. Levamo uses high-performance servers and advanced caching for seamless high-traffic WordPress hosting. You get access to free Levamo CDN, and Redis caching to optimize site speeds further, with unmatched speed and efficiency. This keeps your pages loading in seconds even with heavy content. Fast sites make users happy and keep them coming back.
- **Strong security:** Membership sites deal with sensitive information. Levamo offers multi-layered security to protect your data and your member’s data. It will give you peace of mind from proactive monitoring to advanced resources. You get easy database management and access to quick backups - should anything go wrong.
### Success Stories with Levamo
Many businesses have experienced real success with Levamo.
- [TCM Academy shared](/blog/the-tcm-academy-customer-stories/) that customer complaints about site performance were reduced to zero after switching to Levamo. Their site becomes faster and easier to use.
- [Mingle Grove](/blog/mingle-grove-customer-stories/) - a busy online community also reported instant page loads after moving to Levamo. This improved user satisfaction and engagement.
These case studies show how Levamo does not just host your site - it improves your entire experience.
In simple words, you will get a powerful setup when you combine MemberPress and Levamo. MemberPress provides advanced membership tools. Levamo ensures those tools work smoothly. No matter how complex or active your site becomes. This pairing makes your membership site fast, scalable, and secure. It is the foundation you need to succeed.
## Conclusion
Building and managing a successful membership site requires the right tools and reliable hosting. MemberPress gives you the power to create and grow. While Levamo ensures your site stays fast, secure, and scalable. Together they can create a seamless experience for both you and your members.
It is the time to try MemberPress with Levamo if you want your business to thrive. Take the first step toward building a stronger and smarter site today. Start your journey now and see the difference for yourself!
## Frequently Asked Questions

### Is MemberPress the best membership plugin?
MemberPress is one of the leading membership plugins offering powerful tools to manage memberships, sell courses, and restrict content. It is easy to use and works for both beginners and advanced users.
### Is MemberPress free?
No, MemberPress is a premium plugin and does not offer a free version. However, its pricing plans offer features that provide excellent value for money. The plugin is an investment for anyone serious about creating and managing a membership site.
### Can I use MemberPress for e-learning platforms?
Yes, MemberPress is perfect for e-learning platforms. It has a built-in Learning Management System (LMS) called courses. This lets you add multimedia content, quizzes, and certificates. This makes it ideal for educators, coaches, and businesses offering training programs.
### How much does MemberPress cost?
MemberPress offers three pricing plans to suit different needs. The Basic Plan is $359 per year. The Plus Plan is $599 per year. Also, the Pro Plan is $799 per year. Each plan includes core features like unlimited memberships, content protection, and payment integrations. So you can choose based on your requirements.
### Do I need advanced hosting for a MemberPress site?
Yes, LearnDash includes powerful reporting and analytics tools that allow you to monitor student progress, track course completion rates, and identify areas where learners may need additional support.
---
## LearnDash Review in 2025: How to Launch Your Own Website Using the LMS Plugin
- URL: https://levamo.com/blog/learndash-review/
- Category: lms
- Author: Sunyyan Junaid
- Published: 2024-12-26
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Launch your online courses with LearnDash! Our 2025 review shows you how.
Ready to transform your knowledge into a thriving online business? LearnDash, the industry-leading LMS plugin, empowers you to create and sell stunning online courses with ease. In this hands-on LearnDash review, we’ll dive deep to help you determine if this plugin is the right fit for your needs.
Whether you're an entrepreneur, educator, or course creator, LearnDash provides the tools you need to captivate your audience, deliver exceptional learning experiences, and generate significant revenue. Discover how to harness the power of [LearnDash hosting](/learndash-hosting/) and launch your own successful online learning platform today!
The reason why LearnDash is so popular with course creators is that it has robust features that convert your WordPress website into a cash-making machine.
In this blog, we will discuss the LearnDash LMS plugin in detail, its working, installation, and how it allows anyone to be a course creator.
## 1. What is LearnDash LMS?
LearnDash is a powerful WordPress LMS plugin with features such as a quiz builder, assignment maker, lessons, drip content and more. According to Builtwith, there are currently 75,000+ active websites that have installed this LMS.
### 1.1. Overview and Statistics

While there is no free version available, you can always try it out in a sandbox environment, which is the one we’ll use to demonstrate how it works. To take it out for a spin, head over to LearnDash website, enter in your email address, and receive the username/password in your inbox, which you can then use to sign in and test out the system.
### LearnDash LMS Pricing
Once you are completely satisfied with it, you can go ahead and make a purchase at an annual price of just $199, which provides licenses for use on 1 site.
If you are a total newbie and want to skip the queue by purchasing a self-hosted solution, then their cloud hosting option is something you can consider which provides you with WordPress CMS, the Learndash LMS, and website hosting, starting at $29 a month.

LearnDash Cloud is a new feature that differentiates it from other top LMS plugins like Tutor LMS and Lifter LMS.
This means, you get a managed WordPress hosting solution with LearnDash, at a monthly price of $29 instead of $199 upfront. Other LMS platforms do not provide such an option, which makes LearnDash to be a lucrative option.
## Step-by-Step Guide to installing LearnDash LMS on WordPress
LearnDash LMS comes with a host of powerful course creation features such as drip content, quiz maker, front-end course maker, assignment builder and many more. Let’s understand the step-by-step LearnDash setup process.
The following tutorial highlights all steps in detail for you to set up, install and configure LearnDash LMS on your website. We will be demonstrating everything based on the sandbox environment as it contains all the features that you’d get otherwise with a paid license.
### Step 1. Choose a Hosting Solution
To launch your own website using LearnDash, you need to have reliable and powerful [LMS hosting services](/managed-lms-hosting/). While shared hosting is great for beginners, you’d ideally want to set yourself up for success. This is why we strongly recommend to opt for [Levamo’s hosting](/), which provides DDoS protection, NVME storage, and turbo fast servers for hosting.

### Step 2. Install and Configure the LearnDash LMS plugin
Head over to the LearnDash LMS website, and click **Demo** at the top right corner.

Now in a new popup window, enter your email address to receive the demo link.

Check your inbox and you should receive an email that provides you with a username, password and login access to your personal sandbox environment. Click **Click Here to Login** link to log in the WordPress Dashboard with your credentials.

### Step 3. WP Dashboard for Course Creation
You will be immediately logged in to the WordPress admin area where you can see the plugin already installed. Click on **Courses** on your left, and one the right side, you will see a list of pre-built courses that you can explore.

### Step 4. Create a Course, Add Topic, Lesson and Quizzes
The fun part begins here. You can start creating courses, adding topics and developing dynamic and highly engaging quizzes. To create a new course, click **Courses>Add New via Frontend Course Creator**.

You will be taken to the frontend section, with multiple options:
- **Course Page** - This is where you enter the title, description and the featured image of the course.
- **Builder** - Add in lessons, topics and quizzes.
- **Settings** - Decide if you want to show content as drip or all at once, and many other settings that you can tweak for the course.
- **Extend Access** - Provide access to the course either for a set duration or have an expiry date.
- **Groups** - You can define groups with inclusions or exclusions from this specific course.
Once we have built some foundations of the course, you can see it populated in the image above. We have just created a new course on Cybersecurity by adding in the details to show you how it is done easily.
### Step 5. Add in Lessons and Topics
To create new lessons click **Builder** and here you will see the following options:
- **Add a new lesson** - Lesson is the main heading or unit of the module.
- **Add a new topic** - Topic is added underneath each lesson.
- **Add a new quiz** - To enhance learning, add a quiz of various types.

To add in a new lesson, click on **Add New Lesson. In a new popup window, add in your lesson details**. Here is the list of options that you get:
- **Content** - You add in course content here.
- **Material** - If you want to add additional content such as PDFs, you can attach here.
- **Settings** - Specify quiz appearance, time and other options for each test.

Head over to **Material** where you can add PDFs and other course content to make it more interactive and rich in media.

Now click **Settings** where you can adjust how you want people to view the contents of the lesson. You can set it as a free sample lesson or set a publishing schedule.

Once you are done making changes, click **Publish** and you can see the lesson.

To add in topics, you need to click **Add a Topic** under each lesson and in a new popup window you can provide details for the topic. The options that you see here are no different than the ones seen in **Lesson**. Once you click **Publish**, you will be able to see the topic underneath the lesson.

This is how the topics appear beneath lessons.

To add a quick, click on **Add New Quiz** and in a new popup window, you need to specify the **Quiz Title**, **Quiz Description.**

To add new questions, click **Builder>Add new question**.

There are multiple options for quizzes. These are:
- Single Choice
- Multiple Choice
- Free Choice
- Matrix Sorting Choice
- Sorting Choice
- Fill in the Blanks
- Assessment
- Essay/Open Answer
Select any one from the drop down and give a title and description to the answer. Next, click the **Answer** tab and fill out the possible answers based on your question type. Don’t forget to check the **Mark as correct answer** option or else your question won’t be saved. Once you are done adding answers, click **Publish**.

This is how the questions will appear once created in the Frontend.

To make any changes to how the quiz appears, such as quiz time, access settings and progression, click the **Settings** option at the top next to **Builder** and feel free to play around with the options to suit your liking.

Once the page refreshes, go to the course page and you can see the lessons, topics and the quiz added as follows. The sections are on the left, and the contents for each section on the right.

Click **Start Quiz** to start the quiz that you just created.

We chose the option of showing all questions on just one page. This is how the quiz is beautifully displayed to the user attempting it:

You can also see the main courses page of the website where all courses are beautifully displayed. This is the main page with the /courses link generated by default to make it easier for your audience to pay and enroll in a course of their choice.

### Step 5. How to integrate Stripe/Paypal
The entire purpose of creating a course website is to monetize your knowledge by setting a price for each course. This is an exclusive option that is provided by LearnDash LMS. This step shows you how to integrate payment gateway methods, mostly Stripe and Paypal, so that your students can confidently make a purchase using SSL encryption on your website.
The method of setting up Stripe is the same for Paypal. To set up, head to the main page, and click **Connect Stripe**, under the payment options.

You will now be redirected to the Stripe page where you can enter your Stripe credentials to integrate your account with your website and LearnDash LMS portal.

Once you enter your Stripe details, it will ask you to connect the account associated with your username.

Once connected, you will be redirected back to LearnDash LMS portal and then see a message at the top **You are connected! Please configure your Stripe webhook to finalize the setup.**

Once you set up an endpoint, you can now visit the **Settings** page of your course and set a price that you want to sell it for. **Open** means that the course is openly available to anyone without registration. **Free** means that even though the course is free, the user still needs to sign up and enroll with their email address to access the course. **Buy now** means you can set the **Course Price** to your liking. Next to **Course Enrollment URL,** specify the link address where you want people to redirect to once they make a successful purchase of your course. **Recurring** means that the fee will be deducted on a monthly basis from each user enrolled in the course. Once you are done with all the changes, click on **Update**.

You can now see that the course has a set price of $97 which you specified earlier under the settings.

## 2. Who Should Use LearnDash?
If you have the knowledge and are willing to share it with others, there is someone out there ready to pay for it.
This statement may sound like a cliche, but if you think deeply, it efficiently sumps up the motivation you need to start your own digital product.
Whether you’re a teacher sharing your love and passion for Physics, Chemistry or any other academic subject, or an online entrepreneur who wants to just share premium knowledge with the world, LearnDash LMS is here to help you in achieving your dreams.
It enables you to set up your own course website and start selling your online courses by integrating with Stripe and PayPal in a matter of minutes.
## 3. Pros and Cons of LearnDash
Every LMS plugin has its own learning curve, and for LearnDash LMS, this is no different. You need to invest some time and energy before you can make the best use out of it.
Since the only way to install LearnDash LMS on your website is after purchasing its site license, we strongly recommend testing out and learning all of its features in the sandbox environment. This will dramatically reduce the time you need to build your own online courses without having to worry about making a significant investment.
Here are all the pros and cons highlighted:
Pros
- Complete control over course contents, price, and audience metrics.
- Create unlimited courses any way you want.
- Buy a self-hosted solution or a one-time annual fee to set up the LMS.
- You retain your customers.
- You do not pay a cut to LearnDash LMS for any sales you generate.
Cons
- Not easy to set up as it comes with a learning curve.
- You are responsible for branding and marketing
- Regardless of the sales or free content, you are also responsible for timely payments (monthly or annually as per your contract)
- Some question options are limited compared with Tutor LMS Pro.
## 4. Comparison with Tutor LMS Pro
LearnDash LMS and Tutor LMS both are comparable to each other. They offer robust features, enhanced security, stripe/paypal integration and have frontend course creation options. Tutor LMS also comes with a free version that you can use on your website but you have limited options of creating lessons, topics and quizzes.
In contrast, LearnDash LMS does not provide a free option, rather you can try out all features for free using their sandbox environment before making a purchase.
LearnDash provides monthly self-hosted plans and annual site-wide license, whereas Tutor LMS does not offer any self-posted plan. You can read our detailed [Tutor LMS ](/blog/build-lms-website-with-tutor-lms/)review here to know more about using this plugin.
## 4. Conclusion and Final Verdict
Learndash LMS offers outstanding features and the best in class for course creation, allowing you to build visually stunning courses, course pages, and a wholesome online learning environment.
Using LearnDash LMS and Levamo hosting is a perfect match because the hosting solutions offered are in line with the demands of hosting your own course website. Go ahead and build an online learning empire with the likes of Coursera and Udemy, whereas we cover your hosting needs.
## Frequently Asked Questions

### What is LearnDash LMS?
LearnDash is a powerful WordPress plugin that transforms your website into an online learning platform. You can create courses, quizzes, and publish drip content. It is an excellent tool for marketers, educators and entrepreneurs looking to share their knowledge and build a community online.
### How much does LearnDash cost?
A single-site license costs 199 a year, 355 for 5 sites, and 799 for 10 sites, respectively. If you want to avoid this upfront investment and get a ready-made solution with hosting, then the learndash cloud hosting plan is a better option for you. It starts at 29 a month, and goes upward based on the features you need.
### Is LearnDash easy to use?
While LearnDash offers a wide range of features, it's designed with user-friendliness in mind. But for anyone trying out for the first time, we strongly recommend taking a demo version and using all of its features before making a purchase. The detailed documentation makes it relatively easy to set up and manage your online courses.
### Does LearnDash offer support?
Yes, LearnDash provides comprehensive support to its users. You can access their extensive documentation, knowledge base, and community forums for assistance. Additionally, they offer premium support plans for more in-depth help.
### Can I track my students' progress with LearnDash?
Yes, LearnDash includes powerful reporting and analytics tools that allow you to monitor student progress, track [course completion rates](/blog/maximize-course-completion-rates/), and identify areas where learners may need additional support.
### Is LearnDash suitable for beginners?
A: While LearnDash offers a range of advanced features, it's also accessible to entrepreneurs who have never created a course. The user-friendly interface and helpful resources make it a good choice for those new to online course creation.
### Why should I choose Levamo for my LearnDash LMS site?
Levamo is specifically designed to handle the demands of resource-intensive platforms like LearnDash. It offers optimized performance, fast load times, ironclad security, scalability and expert Support.
---
## BuddyBoss Review & How to Launch Your Own Website Using the #1 Course Plugin
- URL: https://levamo.com/blog/buddyboss-review/
- Category: lms
- Author: Sunyyan Junaid
- Published: 2024-12-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
BuddyBoss review: Launch your course website & turn passion into profit today.
If you've ever dreamed of becoming your own boss, now is the perfect time to do it! There is a reason why [BuddyBoss](/buddyboss-hosting/) has the word “boss” in it. It truly allows you to be your own boss by launching a course or a membership website where you can turn your passion into profit.
BuddyBoss theme, together with its free and powerful BuddyBoss plugin, allows you to convert your WordPress website to a social networking platform, akin to Facebook.
**Key Takeaways from the BuddyBoss Review**:
1. All-in-one platform for building online communities.
2. Seamless LMS integrations for courses and memberships.
3. Monetization, scalability, and mobile app options.
4. Trusted by 25,000+ websites and growing.
5. Requires high-performance LMS hosting services like Levamo.
It also comes with private and open discussion groups, messaging, and integration with leading LMS platforms such as [Tutor LMS](/blog/build-lms-website-with-tutor-lms/) and LearnDash. Combined, these platforms have hosted over 10 million courses, 15 million+ lessons, and 450,000 certificates awarded to recognize students’ achievements.

With a 4.6 rating based on 500+ glowing reviews on Trustpilot, you cannot go wrong with this platform!
As per the usage statistics generated from BuiltWith, BuddyBoss is steadily increasing and has currently over 25,000 active websites. So far, there are roughly 50,000+ websites using BuddyBoss.

In this BuddyBoss review, we will explore its features, benefits, and unique selling points for course creators and digital entrepreneurs. We will also understand how to build and launch your own course website using the [fastest hosting for BuddyBoss websites](/buddyboss-hosting/).
Also Read: [Managed Hosting for BuddyPress](/blog/buddypress-review/)
## What is BuddyBoss and Why Choose it?
The vast majority of WordPress themes (paid or free) are not suited for a membership website, because the needs of a community platform extend beyond those of other regular blogs. A membership website requires multiple plugins to function properly on WordPress.
And that’s why BuddyBoss was created. It replaces the need to install many different plugins to get the same functionality you can have with one theme and one platform. But before Buddyboss, there was another platform named BuddyPress.
The same WordPress enthusiasts who developed BuddyBoss also created BuddyPress. But BuddyPress came with a multitude of limitations, and it was not possible to create a forum without an additional plugin.
That’s when BuddyPress was rebranded to develop into one single BuddyBoss theme.
## What is the Difference Between BuddyBoss Theme and Platform?
Notably, you may get confused between the BuddyBoss theme and its platform. Let's remove this confusion.
The BuddyBoss platform allows you to build and manage online communities. In simple words, it is a WordPress plugin that adds extra functionalities to your website.
The BuddyBoss theme, like the name suggests, is the theme that syncs perfectly with the platform. It’s like iOS (the operating system for iPhones) and iPhone (the devices that run iOS) and how seamlessly they run together.
Similarly, while you can use any theme with the BuddyBoss Platform, the BuddyBoss theme is built to work seamlessly with the platform, so you're better off using their native theme.
Now that we’re done with the confusion, let’s just mention both as simply as BuddyBoss.
## Key Features of BuddyBoss
- **Sandbox in Demo -** Although BuddyBoss is paid, you get to try their demo version for free in a sandbox environment. Test out new features and make changes before buying it.
- **Community-Driven Design -** BuddyBoss enables you to create private or public online communities, complete with discussion forums, group creation, and activity feeds, having amazing interaction between students and educators.
- **Powerful LMS Integration -** Integrate LearnDash, Membership Pro, and Tutor LMS Pro to access amazing features like quizzes, certificates, and course progress tracking.
- **Customizable Memberships -** Offer tiered memberships, manage subscriptions, and provide exclusive access to premium content.
- **Highly responsive -** Its responsive design ensures a seamless user experience across multiple devices. With additional monthly charges, you can even launch branded mobile apps for your students.
- **Monetization Features -** Integrated payment gateways and subscription options make it easy to monetize your courses.
- **Cost-Effective Solution -** Pay annual fees and retain complete control of your website and content, unlike third-party platforms.
- **Scalability -** Scale and grow your membership site as BuddyBoss is configured to grow with you.
## BuddyBoss Pricing
Unlike other plugins and platforms, BuddyBoss does not provide a free trial or a free-tier version. First year, and for one site, you pay $299 fee, with the renewals at $399. While this may seem to cost a fortune, you get amazing features to build a community that you can grow online.
You get the best of a membership site, including communities, public and private groups, and other social features, with a complete pre-built solution.
However, if you have more than 1 site, then the 5-site option is a steal. You are charged an average of just $70 per website per year.

But other than this, you also get a feature where you can build a branded, white-labelled mobile app:

Priced at $99 monthly, you get a native app that can extend the functionalities of your website without having to build one from scratch. This saves you thousands of dollars and countless hours of developing your own solution.
## How to Install BuddyBoss and Integrate it into your Website?
Once you download and install the theme, this is how it will look in your dashboard:

The current version of the site is using [LearnDash LMS](/blog/learndash-review/), which shows that it is easily integrated with the theme and the platform.
- BuddyBoss comes with numerous features. To access these, click **BuddyBoss,** and you will see them. Here is a description for each one of these:
- **Member Profiles:** Every user has his/her own profile.
- **Profile Fields:** Fully editable profile fields allow members to share details about themselves.
- **Account Settings:** Allow members to modify their account and notification settings from within their profiles.
- **Notifications:** With a toolbar bubble and/or via email, you can allow notifications to be sent to your members.
- **Social Groups:** Allow members to organize themselves into public, private or hidden social groups.
- **Forum Discussions:** Allow members to have discussions using Q&A style message boards.
- **Activity Feeds:** Global, personal, and group activity feeds with threaded commenting, direct posting, and @mentions, with email notification support.
- **Media Uploading:** Allow members to upload photos, documents, emojis and animated GIFs, and to organize photos into albums.
- **Private Messaging:** Allow members to send private messages. Messages can be sent to one member or a group of members.
- **Member Connections:** Allow members to make connections with one another and focus on those they care about most.
- **Email Invites:** Allow members to send email invitations to non-members to join the network.
- **Network Search:** Allow members to search the entire network, along with custom post types of your choice.

- To check which platforms it can integrate with, head over to **BuddyBoss>Components>Integration**.

For building a course website, you either need LearnDash LMS, or Tutor LMS Pro, both of which cost $199 per year, and are equally good for a smooth user experience.
- The individual profile option looks something like this, with the likes of Facebook. You can share an update, upload media, and even edit posts after they are published, just like we did here:

- Job Posting Section - This feature extends beyond just selling online courses. You can build your own job board, complete with all the details of the company, job description, wage, and contact details. The backend of the job portal can be accessed by going to **Job Manager>Job Listings**

The dashboard is intuitive and user-friendly, similar to publishing a new blog post. You can add a new job by clicking the **Add Job** button. Once you add in the details of the new job post and publish it, here is how it will show in the job board:

When someone applies for the job position, you can see it in the backend by going to **Job Applications**

## Does BuddyBoss Come with a Pre-installed LMS?
The primary reason for purchasing BuddyBoss is to build your own community where you can sell courses and coaching through membership-based websites. While BuddyBoss has powerful features, it doesn’t come with an LMS.
There are many LMS plugins that you can download and install to sell courses. BuddyBoss has seamless integrations with all of the following:
- LearnDash: $199/yr.
- Tutor LMS: $199/yr. (free plan comes with limited options)
Hence, you’re typically factoring around $500+ only for the premium theme, platform, and the LMS plugin. Hosting plans are separate from this investment.
Let’s discuss both.
## Integration with LearnDash
The sandbox environment already has Learndash LMS installed and integrated with the theme. The courses page looks like this:

The outlook, user interface, and experience are great. You can easily customize the main page through the customization options within the LMS. Learndash LMS comes with a number of features such as course creation, quizzes, assignments, video/audio lessons, topics, and student progress.
Develop advanced quizzes and integrate in BuddyBoss to get an ultimate membership-based website. You can also determine the order in which the course will be completed and whether or not you want content to be visible in a drip format.
## Integration with Tutor LMS
Tutor LMS is yet another powerful plugin that rivals LearnDash LMS. Both plugins offer premium functionalities, quizzes, assignments, and other features that dynamically power your website into a membership-based platform. The features and functionalities do not fall short of your expectations, and which LMS you end up using is purely your own decision.
Here is the interface of Tutor LMS, where you can see the option of adding a new course through the WP Dashboard:

## [BuddyBoss Hosting](/buddyboss-hosting/) Options
When you’re hosting a blog or static website, any shared hosting would work well, but not with Buddyboss.
Since you’re building a thriving community, you need a hosting solution that can do all the heavy lifting, such as handling traffic and data loads and scaling when required to match the demand. Hence, choosing the right hosting provider that prioritizes scalability and performance is important.
This is where [Levamo hosting](/buddyboss-hosting/) comes in.
Here are the top reasons why Levamo is the best managed hosting for BuddyBoss websites:
- **Purpose-Built for BuddyBoss**: Created by the founders of BuddyBoss to solve sluggish performance issues for dynamic websites. In fact, it's the top [BuddyBoss recommended hosting](https://www.buddyboss.com/hosting-recommendations-for-buddyboss-platform/) solution.
- **Unmatched Performance**: Optimized for BuddyBoss and WordPress, ensuring lightning-fast load times and smooth functionality.
- **Scalability**: Handles heavy traffic spikes and growing user bases effortlessly.
- **Reliable Security**: Offers robust, multi-layered security to protect your community.
- **24/7 Expert Support**: Dedicated assistance to resolve issues anytime, ensuring uptime.
Levamo is not just another hosting solution - it’s the definitive choice for BuddyBoss users, purpose-built to help your community thrive.
## Support Options
You can get access to their vast knowledge base, email, and ticketing. Support is available 24/7, and the average response time is less than 1 hour. While the live chat option is not yet available, their support is pretty fast and the support staff is also knowledgeable in resolving your issues.
## Final Verdict
For less than $1,000, you have your own membership-based website that comes with the theme, platform, LMS, and hosting.
In the end, if you want a platform that powers up your website as a social network, then look no further than BuddyBoss. This platform is also the best option when you want your website to resemble a web application with interactivity and social discussion.
There is a learning curve when working with this platform as the features and functionalities are not the same as other WordPress websites. You will need some time to understand how this platform works.
While the platform comes with robust features, you still need to account for an LMS to be able to sell courses. In the future, the BuddyBoss theme may offer a built-in course creation process. But for now, a supported LMS platform is mandatory to sell online courses and digital products.
Hopefully, this BuddyBoss review has answered all your pressing questions and you've made up your mind about the taking things to the next level!
## Frequently Asked Questions

### 1. Can I create an online course or membership site without BuddyBoss?
Yes, but it will be very difficult. BuddyBoss provides a premium theme and platform designed for building vibrant online communities and membership sites. Not all platforms have these many features without the need of installing multiple WordPress plugins.
### 2. Is BuddyBoss free?
No, BuddyBoss is a paid platform. There's no free tier, but they offer a free sandbox demo to try out its features before you buy. Their basic plan starts at $299 per year for one site. As you scale, you can easily go for a 5-site plan for just $349.
### 3. What Learning Management Systems (LMS) does BuddyBoss integrate with?
BuddyBoss integrates seamlessly with popular LMS platforms like LearnDash, Tutor LMS, and Lifter LMS. These plugins cost extra (almost $199 per year) but allow you to create and sell courses within your membership site.
### 4. What kind of hosting do I need for BuddyBoss?
BuddyBoss has a robust setup compared to normal WordPress websites and so it requires a hosting that can fulfill the demands of such a dynamic setup. For this, BuddyBoss itself recommends using Levamo hosting because of [auto scalable server](/blog/cloud-auto-scaling/) and high performance even when there's peak traffic.
### 5. Does BuddyBoss have good customer support?
Yes, BuddyBoss offers 24/7 support via email and ticketing with an average response time of less than 1 hour. Live chat isn't currently available, but their support staff is known for being knowledgeable and helpful.
### 6. Is there a learning curve to using BuddyBoss?
Yes, BuddyBoss has more features and functionalities than a typical WordPress site and you'll need some time to learn, specifically if you haven't built a membership site before.
### 7. Is BuddyBoss worth the investment?
For under $1,000 (including theme, platform, LMS, and basic hosting), you can have a powerful membership site with social networking features. If you want a user-friendly, interactive online community, BuddyBoss could be a great choice. Starting any business requires investment, but for an online membership site under $1,000 is a reasonable option.
---
## WordPress Year-In-Review 2024: The Good, the Bad, and the Unexpected!
- URL: https://levamo.com/blog/wordpress-in-2024/
- Category: wordpress
- Author: Sunyyan Junaid
- Published: 2024-12-20
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WordPress in 2024: Key updates, stats, and community buzz you need to know.
What a year it’s been! And the world of WordPress has seen its share of excitement and ups and downs, and throughout it all, it inspired people to decorate the web with their creativity.
2024 was yet another year of dynamic updates, releases, strategic acquisitions and even heated debates in the WordPress community.
Whether you’re a developer, an entrepreneur, a blogger or just someone who constantly screams “*Why is my website not fast enough?,*” this recap will take you through the major milestones and happenings from the world of WordPress.
Let’s roll.
## WordPress in Numbers
As of November 2024, there are more than 1.1 billion websites out there in the wild, out of which around 488 million are hosted on WordPress, maintaining its position as the leading CMS globally.
But let’s take a look at things in numbers:
**Global Usage**: 488.6 millions websites run on WordPress, which is approximately [43.7% of all websites](https://www.wpzoom.com/blog/wordpress-statistics/?utm_source=chatgpt.com).
**CMS Market Share**: Holds a dominant 62.2% CMS market share, which is significantly ahead of other key players like Shopify (6.6%) and Wix (4.5).
**Themes**: There are 30,000+ available, out of which 13,000 are free.
**Plugins**: There are 70,000+ plugins available to enhance and augment your website’s functionality.
**WooCommerce**: The ecommerce plugin for WordPress boasts a 36.3% share of the ecommerce platform market, trumping significant rival Shopify.
**Version Adoption**: Over 86% of WP websites are [running version 6](https://w3techs.com/technologies/details/cm-wordpress?utm_source=chatgpt.com), which means there’s widespread adoption of the latest features and enhancements.
**Language Support**: The CMS supports over 200 languages, with English taking the lead with 71% usage.
These are just some figures that tell you about the dominance of WordPress as a CMS. And it seems that with passing years, the WordPress ecosystem is only growing.
But let’s take a look at the highlights of 2024, the good, the bad, the unexpected, and what to possibly expect in the year to follow.
## WordPress vs WP Engine Drama - The Unexpected Highlight of 2024
Before we move on with the exciting updates and major happenings, it is important to highlight the biggest event surrounding the WordPress community in 2024; the **WordPress drama**.
On 20th September 2024, Matt Mullenweg criticized WP Engine pointing that despite being a huge corporation, it wasn’t doing enough to contribute to the open-source community. WP Engine, in contrast, denied this claim stating that they have been contributing as much as any other company would.
Things escalated quickly to Cease and Desist Letters from both companies, and now there is a litigation battle going on in the US courts.
Also Read: [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
### What exactly is open-source contribution and why does it even matter?
Even though WordPress provides its CMS platform for free, it doesn’t happen out of thin air.
The entire premise behind an open-source platform is for a loyal global community to contribute to it. Since the code is publicly accessible, anyone can [use, modify and distribute it.](https://learn.wordpress.org/lesson-plan/what-is-open-source/) This is what the hosting companies do when they provide shared or managed WP hosting services.
To operate a healthy ecosystem, there is a sustained level of contribution to it, by:
- Writing new codes, testing and fixing bugs.
- Helping other users to get the most out of the platform in forums, blogs and on social media.
- Developing educational material such as API docs.
The reason why WordPress is an immensely successful platform is the tireless global contribution of volunteers every single day. It is no wonder to see WordPress evolving from a simple blog to a versatile platform powering 43% of the web.
This criticism by Matt on WP Engine centered on whether their level of contribution was proportional to their commercial success derived from WordPress.
### So what is next?
The WordPress community has had its mixed share of responses. Some are siding with WP, whereas others believe that WP Engine was doing their job.
[Comment by user reddit user u/deadweights](https://www.reddit.com/r/webhosting/comments/1fmtdtk/wordpress_founder_calls_wpengine_a_cancer/) who thinks Matt Mullenweg is doing the right thing.

[Comment by Reddit user u/screendrain](https://www.reddit.com/r/Wordpress/comments/1fpkek6/wp_engine_must_win/) who thinks it’s unfair to WP Engine.
So while the opinions are polarizing, in the grand scheme of things, none of this is impacting our clients. In fact, most of the small and medium businesses relying on WordPress hardly know or are impacted by this controversy.
Companies would often engage in legal battles due to trademark and branding disputes. And in this case, it doesn’t spell the end of WordPress. This is a dispute between two companies, and as long as you are currently not using WP Engine, there isn’t anything you need to be concerned about.
Even though the judge ruled that [WordPress parent company must stop blocking WP Engine](https://www.theverge.com/2024/12/10/24318350/automattic-restore-wp-engine-access-wordpress), we believe there’s still a long way to go before the dust settles on this entire WordPress drama.
Now, let’s continue with all the other major updates from the world of WordPress in 2024:
## Major WordPress Releases and Updates
In 2024, similar to what WordPress does every year, there were major updates to the WP open-source platform. These updates are critical for over 488 million websites to ensure they remain functional with no hiccups.
WordPress kicked off 2024 with a trio of game-changing updates, each introducing enhancements that beefed up the platform’s content management capabilities.
But beyond just adding new features, these updates were vital for maintaining the platform’s security, compatibility and performance. Every update came with patches for addressing critical vulnerabilities and making major performance updates.
The platform also has a tradition of naming each major update after a Jazz musician, which sets it apart from other open-source platforms. Naming releases after artists gives each update a distinct identity making it more engaging than simply using numerical version numbers.
Here are the 2024 updates:
### WordPress 6.5 “Regina” (April 2)
Released on 12th April, Regina focused on improving accessibility. It also added ARIA landmark support, making it a step forward for inclusivity.
It refined site-building experience, providing you with greater control on your website with the ability to add and manage fonts in the new Font Library without coding.
Key improvements also included extensive revision tracking and significant updates to the Site Editor, all while boosting overall site performance for a faster and more efficient workflow.
### WordPress 6.6 “Dorsey” (July 16)
Dorsey was released on 16th July, introducing asynchronous block saving and significantly speeding up content workflows.
A crucial feature was automatic plugin updates, including a rollback feature. This meant that in any unlikely event of the updates causing errors, you can now safely rollback the website to its last known working condition.
This provided a safety net for developers and site owners, making maintenance headaches a thing of the past.
Another highlight was the 58 website accessibility fixes and enhancements in accordance with the WCAG guidelines improving the overall user experience (UI) of your website.
### WordPress 6.7 “Rollins” (November 12)
WordPress is known for releasing a brand new theme every year, named after that year.
Similarly, alongside Rollins update on 12th November, the CMS also released the sleek **Twenty Twenty-Five Theme (2025)**, which emphasized design flexibility and cutting-edge typography. It also included 16 bug fixes throughout the Core and Block editor.
Building upon 6.6, the release focused on stabilizing and optimizing the Site Editor, enhancing performance, and addressing bugs.
The main highlight around the Site Editor was the “Zoom-Out” feature, which enabled site owners to literally zoom out and view every section to get a better understanding of content blocks.
WordPress 6.7 also came with faster load times, optimized previews in the data views component, better PHP 8+ support and efficient tag processing in the HTML API.
In addition to this, the update further addressed 65+ accessibility fixes and enhancements including a refined user interface and better keyboard navigation in the Editor.
## WordCamp Highlights
Each year, thousands of developers, designers, editors and enthusiasts come together under one roof as part of the ecosystem.
These are organized by the local community put together by users like you. Everyone gets a chance to contribute to the open-source world of innovation.
WordCamps have long been a cornerstone of the WordPress community for learning, networking, and collaboration.
From hosting the first WordCamp back in August 2006 in San Francisco by Matt, WordCamps have now transformed into defining the very definition of giving back to the community by encouraging open source contributions.
With a total of 78 events held in 2024, here are the ones that stole the limelight:
- **WordCamp Asia 2024**: March 7–9, 2024 at the Taipei International Convention Center in Taipei, Taiwan.
- **WordCamp Europe 2024**: June 13–15, 2024 in Torino, Italy.
- **WordCamp US 2024**: September 17–20, 2024 in Portland, Oregon. The spiciest one yet where Matt’s comments triggered the whole WP Engine drama.
## Acquisitions Shaping the WP Ecosystem
2024 saw an unprecedented wave of acquisitions that reshaped the WordPress landscape. Automattic, the company behind the open-source solution, also gained a strong foothold by acquiring new companies.
But acquisitions are much more than just buying out another company. Every company specialises in a specific set of services, such as themes, plugins, hosting solutions and more. Every acquisition brings a diverse pool of talent to work on solving problems and eventually creating something even bigger for the WP ecosystem.
Here are the highlights for 2024:
### Automattic acquired WPAI (December 10)
For an undisclosed sum, Automattic acquired WPAI, a startup that offers AI solutions for WordPress, just before the year end.
These include CodeWP, which uses AI to develop WP Plugins; AgentWP, an AI assistant; and WP Chat, a chatbot for WordPress-related questions.
Automattic’s acquisition of WPAI also meant that the year 2025 will bring exciting updates in terms of integrating AI into the WP platform. We see it as a major milestone as AI keeps on getting a bigger role in website development.
### Awesome Motive acquired BuddyBoss (July 9)
Awesome Motive announced acquisition of BuddyBoss, one of the leading community-building platforms on WordPress.
Pst, we also did a [BuddyBoss Review](/blog/buddyboss-rapyd-journey-podcast/) here that you can read to find out its amazing features.
### WP Engine acquired Nitropack (July 18)
WP Engine acquired Nitropack, a SaaS solution for improving site speed, [Google’s core web vitals](/blog/changing-seo-lanscape/), and performance metrics among other things.
### CaseProof acquired AccessAlly (April 30)
Caseproof acquired AccessAlly on 30th July, expanding its learning management and membership platforms-based services.
## Notable Security Incidents and Swift Patch Updates:
While every major WP release comes with security fixes and patches, the open-source contributors also play a vital role in keeping the platforms safe and secure.
Many cybersecurity incidents and data breaches were noticed by independent contributors that highlighted them on different forums and encouraged plugin and theme developers to come up with fixes.
The following were the most notable ones that took place in 2024:
### Hunk Plugin Security Breach (December 12)
There’s a reason why we always say to keep your themes, WordPress CMS and all the plugins updated. Just recently this month, the Hunk Companion plugin got compromised and malicious actors took advantage of this situation.
Affecting more than 10,000 websites, malicious actors were able to get backdoor access to vulnerable websites. Tracked as CVE‑2024‑9707, the bug allowed “unauthenticated attackers to install and activate plugins and execute remote code execution”, a [NIST advisory](https://nvd.nist.gov/vuln/detail/CVE-2024-9707) stated.
Version 1.8.5 came with the security patch, but later reports found out that even the 1.8.7 version was vulnerable.
On December 10, Hunk Companion rolled out a new patch with the latest 1.9.0 version update. Thankfully, no major compromises were reported.
### Really Simple SSL Security Vulnerability (November 06)
WordFence stated that more than 4,000,000 websites using the Really Simply Security SSL plugin got affected by a critical authentication bypass.
Really Simple SSL is a plugin that installs and activates SSL on WordPress websites. The critical vulnerability allowed fully remote access to the websites, completely locking out the site owners.
As a security provider for WordPress, this discovery was by far one of the most serious vulnerabilities that WordFence reported in more than its 12 years of history.
The Really Simple Plugins released patches for the Pro plugins on November 12, 2024, and for the Free plugin on November 14, 2024, which effectively meant that the vulnerability was addressed within 8 days of discovery.
Also Read: [LMS hosting](/managed-lms-hosting/)
### WPML Remote Code Execution Threat (August 26):
WPML is a popular WordPress plugin with more than 1,000,000 active installations, which allows users to translate their websites into multiple languages.
WordFence stepped in to protect 1 million sites from potential exploitation after one of its contributors reported Remote Code Execution via Twig Server-Side Template Injection vulnerability in [WPML](https://www.wpml.org/).
The vulnerability, tracked as [CVE-2024-6386, impacted](https://www.wordfence.com/blog/2024/08/1000000-wordpress-sites-protected-against-unique-remote-code-execution-vulnerability-in-wpml-wordpress-plugin/) all versions of the plugin before 4.6.13. OnTheGoSystems, the team behind WPML, released 4.6.13 with a patch to address the critical vulnerability.
## New Launches in the WordPress Ecosystem
If you thought this was it, hang on, there’s a LOT more exciting things happening as we speak. The year 2024 was marked as full of important launches and here are a few of them:
### Levamo - Jan, 2024
Yes, Levamo will turn 1 in early 2025!
Back in January 2024 cofounders Tom Cheddadi and Michael Eisenwasser along with Wes Tatters launched Levamo which was born out of a necessity rather than a business idea.
Why? Because BuddyBoss users were constantly complaining about how their hosting platforms couldn’t handle the robust nature of websites, and so they needed a better solution.
And so Levamo was a [custom made WordPress hosting solution](/blog/buddyboss-rapyd-journey-podcast/) for website owners with dynamic needs.
With 500+ satisfied users now, Levamo is fast becoming the [fully managed WordPress hosting ](/managed-wordpress-hosting/)for users with high demand WordPress websites. With Levamo, your [websites get a hyperspeed hosting environment](/performance/), are incredibly secure, and you get 24/7 expert support that goes out of their way to help you.
[Give it a try for free](/) and see for yourself why it’s such an incredible solution.
### MonsterInsights launched Conversation AI - July, 2024
Reimagining the concept of website analytics and data, MonsterInsights launched a new AI tool on 29th July, 2024, which allowed users to type and ask anything about their website analytics and the tool will share those specific details.
This means that in 2025, there will be more updates on how people can interact naturally with website management tools to understand site analytics in an even easier way.
## WooCommerce Updates: Empowering E-commerce
Just like WordPress, WooCommerce also is an essential cornerstone of the open-source contribution. It enables anyone with even limited technical skills to build and run a successful online store. From launch of [WooCommerce managed hosting](/managed-wordpress-hosting/) to features launched by WooCommerce, let’s see what was in the store for us in 2024.
WooCommerce rolled out the premium Brands feature to all of its users on 21st October.
Similar to Categories, website owners can assign brands to stores using the Brand feature by creating as many dedicated brand pages as you like with no additional charges.
In December, WooCommerce also rolled out a much-awaited feature, named COGS, or Cost of Goods Sold function. Without the need of additional plugins, you can now calculate the exact profit margins and make data-driven decisions.
These two features enhanced the e-commerce functionalities of WooCommerce store owners to provide a rich online shopping experience.
## Looking Ahead - What to Expect in 2025?
With all the exciting updates in 2024, the future is bright for WordPress enthusiasts. Here are key milestones that you need to keep an eye on:
- **WordPress 6.8 - Beta 1 on March 4:** Stable release on April 15
- **[WordPress 6.8](/blog/wordpress-6-8-cecil-now-available/) (April 15):** Promises enhanced speed and block editor improvements.
- **WordPress 6.9:** Beta 1 on June 24, stable release on August 5
- **WordPress 6.9 (August 5):** Expected to introduce groundbreaking e-commerce features.
- **WordPress 7.0:** Beta 1 on September 30, stable release on November 11
- **WordPress 7.0 (November 11):** A milestone release to redefine the platform’s capabilities.
- **[WordCamp Asia 2025](/blog/wordcamp-asia-2025/):** February 20-22
- **WordCamp Europe 2025:** Basel, Switzerland, 5 - 7 June
- **WordCamp US 2025:** August 26th - 29th
- **Back in Stock Notifications & Shipment Tracking** [to release in WooCommerce](https://developer.woocommerce.com/2024/12/12/woocommerce-in-2025/)
## Here’s to 2025
As we approach 2025 in the coming days, the WP landscape promises to bring even continued evolution built on the 2024 updates.
We will witness better and more refined digital experiences through the integration of AI and bringing automation features related to content creation, website management and UX personalization.
This means that you would be able to generate content based on current trends through the development and integration of new AI-powered plugins.
As we move into 2025, headless WordPress will gain traction due to its ability to unlink front end and back end user interface, allowing for customized website development.
The potential is enormous and the possibilities are endless.
Here’s to a successful 2025!
---
## LifterLMS Review: A Powerful WordPress LMS Plugin For Online Courses
- URL: https://levamo.com/blog/lifterlms-review/
- Category: lms
- Author: Sunyyan Junaid
- Published: 2024-12-19
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is LifterLMS the right WordPress LMS plugin for your online courses? Find out now.
If you're on the hunt for a Learning Management System (LMS) for your online course business, then LifterLMS is a name you will find everywhere. It's one of the most popular options for WordPress LMS plugins, but if you're not sure whether it's good for you or not, you'll get the answer to all your questions and doubts in this LifterLMS review.
Considering there are so many [WordPress LMS plugins](/blog/best-wordpress-lms-plugins/) out there, I'll make it easy for you to decide if the plugin in question is the right fit for your business in this LifterLMS review.
Let's get into it.
## Lifter LMS Review: An Overview of the LMS Plugin
The global e-learning market is expanding like never before! *It was worth USD 305.97 billion in 2023, and by 2033, it is set to hit a staggering USD 1515.97 billion.* This presents an incredible opportunity for aspiring course creators. But you need the right tools and support to succeed in this industry.
**Enter LifterLMS.** Chris Badgett started [LifterLMS](https://lifterlms.com/) in 2014, and it has continued to expand since then. The mission was simple: “To lift up others through education,” and the numbers prove that Chris's mission has been pretty successful and is still ongoing.
**The statistics also show that LifterLMS has earned the trust of many,**
- **8.3+ million** courses enrolled in courses through LifterLMS
- More than **12.5 million** lessons and courses completed successfully.
- **310,000+** certificates awarded to recognise students' achievements.
- Trusted by **10,000+** active websites worldwide.
- Rated highly with [308 five-star](https://wordpress.org/support/plugin/lifterlms/reviews/?filter=5) reviews from satisfied users.

Now, let's take a look at the features of LifterLMS that may be of importance to you.
### LifterLMS Features we love:
This [WordPress LMS](/managed-lms-hosting/) plugin comes with tools that simplify course creation and make managing students so much easier. Here is what you should know about this plugin:
- **Drag and Drop Builder:** It has a drag-and-drop builder that helps you create courses. You don’t need any coding skills to create the course. Just drag and drop lessons, quizzes or sections into place. It feels intuitive even for beginners.
- **Quizzes and assignments:** You can create engaging tests to keep students interested. Setting up quizzes is simple, and the variety of question types adds a fun twist.
- **Student dashboards:** [These dashboards](https://lifterlms.com/docs/student-dashboard/) are clean and professional. They help students track their progress, see achievements and stay motivated.
- **Integration:** LifterLMS works beautifully with tools like Stripe, PayPal, and email marketing platforms like Mailchimp. This flexibility makes it easy to manage payments and communications in one place.
- **Easy memberships & payments:** You can offer courses and site access through [memberships with LifterLMS. ](https://lifterlms.com/docs/getting-started-with-creating-memberships/)It lets you set up automatic enrollments, special membership pricing, and more. Payments are flexible too! Students can pay with credit cards and set up recurring payments. They can even choose custom pricing plans. It is simple and adaptable to everyone.
### Benefits you get using LifterLMS
Here are the reasons we believe LifterLMS will work best for you:
- **It fits any budget:** The core plugin is totally free of cost. You can start small and later add premium features when needed. You can give it a try even before committing to it. Explore the full features on a [demo site for just $1](https://lifterlms.com/try/). It gives you 30 days to test it out risk-free.
- **It is scalable:** LifterLMS simply grows with you whether you are just starting with a single course or managing a full academy. Adding courses or upgrading features is seamless.
- **Deep WordPress Integration:** This plugin is specially built for WordPress. The main goal here is to let you customize your site to look and function exactly how you want. We simply loved how much control it gives its customers over the design and functionality.
- **Content protection:** Protecting your content is vital - especially when you offer it exclusively to paying students. LifterLMS makes it easy with strong content restriction features. You have complete control over who can access your lessons. This ensures only the right people can see your work. The protection is reliable and gives you peace of mind that your valuable material stays secure.
- **Student engagement:** Keeping students engaged is key to helping them enjoy learning and succeed in their courses. LifterLMS makes it easy with features like achievement badges, social learning tools, or private coaching. These options keep learning interactive and encourage students to perform their best.
- **Supportive community:** [Chris and his team](https://lifterlms.com/start-in-style/) genuinely care about helping creators succeed. Their tutorials and support sources are incredibly helpful when you are stuck. We also appreciate their active online community for advice and tips.
### Challenges You Should Know
Not every tool is perfect, and LifterLMS is no exception. Here is what we have noticed about this WordPress LMS plugin:
- **Add-on Costs:** The free version is simply great. But to unlock other features like LifterLMS Advanced coupons, custom fields or private areas, you need to pay for [add-ons](https://lifterlms.com/store/). This can get a bit pricy if you get multiple ones.
- **Learning curve:** The number of options makes you feel overwhelmed at first if you are a beginner. But things get easier with some practice. And their helpful guidance is simply great when you go for an online course creation with WordPress using this plugin.
## Who Should You Use LifterLMS?
From our experience with this LifterLMS review, this WordPress plugin is best suited for:
- **Course creators and educators:** This tool will give you everything you need to build professional courses if you teach online.
- **Businesses:** Companies can use it to create employee training programs or onboarding materials.
- **Schools and institutions:** It is perfect for organizations looking to expand into e-learning.
- **WordPress users:** LifterLMS feels like a natural fit if you are already comfortable with WordPress.
## How to Start An Online Course with LifterLMS: A Step-by-step Guide
Creating an online course takes time and effort. Especially with so many details to manage. You need to think about your curriculum, study materials, quizzes, and even how everything looks and flows.
LifterLMS simplifies this whole process with its drag-and-drop course builder. This tool lets you easily map out the overall structure of your course. And once it’s done, you can add specific details and fine-tune the section. It is basically designed to save your time and make the course creation more straightforward.
### 1. Install and Set the LifterLMS on a WordPress Site
LifterLMS is available for free in the WordPress.org plugin repository. You can install it directly from your WordPress dashboard. And you would not require any license or upgrades for that.
**Step 1:** First, you can simply log in to your WordPress site and go to the **Plugins** section. Then click on the **Add New** to start.

**Step 2:** You will find the **Search plugins** at the top of the screen.

**Step 3:** Now Type “LifterLMS” into the search bar.
**Step 4:** Locate LifterLMS and click on **Install Now** when the search results appear.

**Step 5:** Click on the **Activate** button. It will enable the plugin after the installation finishes.

**Step 6:** The activation step will automatically take you to the **Setup Wizard**. If this is your first time using LifterLMS, you can follow the steps in the wizard to configure your LMS.
And don’t worry if the Setup Wizard doesn't appear. You can still manually access it by following the instructions in the [official documentation](https://lifterlms.com/docs/rerun-lifterlms-setup-wizard/).
**Step 7:** You will be directed to the Welcome Page of the Setup Wizard after activation. This is your first time installing the LifterLMS. Now simply click on the **Get Started** button to begin.

**Step 8:** The setup wizard will guide you through the initial configuration of LifterLMS. Completing this is essential to set up your LMS. At the very least, you need to finish the Page Setup step.

This step automatically creates all the essential [LifterLMS pages](https://lifterlms.com/docs/lifterlms-required-pages/) your platform needs, including:
- Course Catalog
- Membership Catalog
- Checkout page
- Student dashboard
They will not be recreated if any of these pages are already on your site. Click on **Save & Continue** to move forward once you have reviewed everything.
### 2. Configure payment gateway options & membership options

**Step 1: You can configure your default settings on the payments screen:**
- Select your site’s **default country** and **currency.**
- Now optionally activate the built-in [manual payment gateway ](https://lifterlms.com/docs/using-lifterlms-manual-payment-gateway/)for basic payment handling.
Settings are not final. You can adjust them anytime by navigating to **LifterLMS > Settings > Checkout.**
You need to install one of the [LifterLMS E-commerce add-ons](https://lifterlms.com/product-category/e-commerce/) when processing payments, such as Credit Cards, Stripe or PayPal. These add-ons expand your payment options. And make it easier to manage transactions directly through your site.
**Step 2: Membership access**
LifterLMS adds a Membership Access feature that appears as a meta box on your WordPress posts and images. This handy tool lets you restrict access to certain posts. So that only students with specific membership can view them. You can create exclusive content for your members with this feature and easily manage who gets access to what.
### 3. Creating your first course
**Step 1: Start building your course**
It is time to create your first course once LifterLMS is installed. Go to your WordPress dashboard **(wp-admin)** and navigate the **courses.** And click on the **Add New** to get started with it.

**Step 2: Customize your course settings**
Every course comes with essential settings that you need to configure:
- **Course Title:** Name your course so it is clear and engaging.
- **Course information:** Provide details about what the course offers.
- **Access plans:** Set up the pricing or enrollment options.
You can also refer to the [LifterLMS QuickStart](https://academy.lifterlms.com/course/how-to-build-a-learning-management-system-with-lifterlms/?_gl=1*1qkqmlm*_ga*NzM1MjQ5OTMxLjE3MzIyNjMwNTg.*_ga_2P21QXXHNZ*MTczMjMzOTE1NC4zLjEuMTczMjM0NjA4MC4wLjAuMA..) guide for advanced options like content restrictions. But these settings will get you up and running.

**Step 3: Add lessons to your course**
To build your course structure - activate the **LifterLMS Course Builder** from the right-hand sidebar on the course editing page. You can also **add sections and lessons** to organize your content in the builder.

Click on the WordPress icon next to the lesson title to edit a specific lesson. This will take you directly to the lesson editor.

**Step 4: Course quizzes**
You can also add quizzes to your course lessons using the **LifterLMS Quiz Builder.** The core plugin includes basic question types to make testing students' knowledge simple. You can even explore the [LifterLMS Advanced Quizzes add-ons](https://lifterlms.com/product/advanced-quizzes/) for additional question types or deeper customisation. This option expands your quiz-building capabilities. It provides a more robust assessment experience for your learners as well.

### 4. Customize your student experience and enable analytics
LifterLMS goes beyond just hosting courses - it lets you tailor the student experience. You can even track progress through detailed analytics. Their built-in analytics provide you insights into students’ performance. That ultimately helps you refine your content and improve engagement.
**1. You can create a certificate**
LifterLMS lets you create certificates to reward students for completing courses. You can design certificates using the WordPress block editor. Simply go to the **wp-admin > Engagements > Certificates. Now build your certificate and click publish when finished**.

**2. You can create an engagement**
You can trigger engagement to create awards, certificates, or emails automatically. Go to **wp-admin > Engagements > Add New.** Don’t forget to click on the Publish button to save your certificates.

**3: Downloading students’ reports to track progress**
- Go to the LifterLMS **> Reporting**.
- Click the export button under the Students tab.
- The CSV files will be downloaded to your computer.
This makes it easy to analyse [your data and track students’](https://lifterlms.com/docs/download-reports-reporting-data-lifterlms/) progress seamlessly!
### 5. Review, publish & promote your course
Preview your course to see how it looks to students once you have added the lessons. Publish it if everything looks great! Do not forget to add the course page to your website menu so learners can easily find it.
You can offer free course enrollments or use the manual payments option with LifterLMS. You can even activate a [payment gateway add-on](https://lifterlms.com/docs/what-payment-gateways-can-i-use-with-lifterlms/) to streamline transactions and grow your revenue - when you look to sell courses and memberships efficiently.
## Power Your LifterLMS Site With Levamo
You know how important it is for your site to perform well if you are using LifterLMS. A slow site and unexpected downtime do not just frustrate you, they can also hurt your business. This is where **Levamo** shines! This [LMS hosting](/managed-lms-hosting/) solution is built to keep your e-learning site running smoothly, no matter what.
### Fast and Reliable Even During Peak Traffic
Levamo ensures your site remains [lightning-fast](/performance/) - even during peak traffic. It is built to handle the heavy demands of dynamic platforms like LifterLMS. Whether it is streaming video, taking quizzes or earning certificates, all of it demands top-notch performance.
Now, with Levamo, you don't have to wait for lessons to load or pages to open - even when you teach hundreds of students online at once. This platform uses advanced caching and optimized server configuration. It also offers proactive monitoring to guarantee smooth and responsive interactions. Don’t believe it? [You can check out this case study!](/blog/english-pro-tips-case-study/)
### Why Fast Loading Times Are Crucial
Picture this: A student logs in and is excited to learn. But their course takes forever to load. Annoying right? A slow site is not just a bad experience, it leads to low engagement and fewer returning learners.
**Levamo’s fast-loading speed helps:**
- Keep learners engaged by eliminating delays.
- Enhanced your credibility by offering a professional experience.
- Boost interaction because students stay focused on the content - not on waiting for it long.
### Reliable uptime every time
No students want to see a “site unavailable” message when they are ready to study. Levamo guarantees near-perfect uptime with the advanced infrastructure they have.
**This reliability means:**
- Learners can access their courses anytime, hassle-free.
- You can avoid interruptions that could damage your reputation.
- Your focus will stay on business - not troubleshooting downtime.
### Customised for LifterLMS
What sets Levamo apart is its compatibility with LifterLMS. It is optimised to meet the unique demands of e-learning sites.
- **Content protection:** Your course material stays secure with [multi-layer security protocols.](/managed-security/)
- **Scalable performance:** Whether you are managing 50 students or 1000 students, Levamo adjusts to your needs effortlessly.
- **Third-party integration:** Levamo supports seamless connections with payment gateways, analytics tools and many more.
### Proactive support, so you don’t worry
Running an LMS is complex. But you are never alone with Levamo. [Their 24/7 expert support team](/support/) acts as an extension of your own - ready to solve issues quickly. They also handle routine backups, updates and monitoring. So you can focus on creating content while they hold the technical side.
## Why Levamo is a Game-changer
Levamo is not just hosting - it is a performance booster for your LMS. It is fast, reliable and secure. Levamo helps you deliver an exceptional learning experience to your students while scaling your business stress-free.
Are you ready to see the difference? You can try **Levamo today** and give your students the experience they deserve!
**[Try Levamo For Free](/pricing/)**
## Conclusion
LifterLMS simplifies online course creation with powerful tools like a course builder, quizzes and student engagement features. It will help you manage progress and deliver a professional learning experience. And the best part about this?
You can simply pair LifterLMS with Levamo hosting to take your online courses to the next level. Levamo ensures your platform runs smoothly with fast load times, reliable uptime, and robust security. Together, they provide an excellent and seamless solution for creating and delivering courses. So what are you waiting for? Start building your dream e-learning site today with this winning combination.
---
## Save Time at Checkout with Saved Payment Methods
- URL: https://levamo.com/blog/save-time-at-checkout-with-saved-payment-methods/
- Category: news
- Author: The Levamo Team
- Published: 2024-12-08
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Use saved payment methods for faster checkout when purchasing or upgrading.
You no longer need to enter your payment details every time you make a purchase. Now, you can use saved payment methods when buying a new subscription or upgrading a support plan, making checkout faster and easier.
## What's New
- When purchasing a **new subscription** or **upgrading a support plan**, you can select from payment methods already saved in your account.
- If you prefer to use a new payment method, you can still select **"Pay another way"** during checkout.
- Payment methods are securely stored through **Paddle's payment system** (our merchant of record).
This update streamlines the checkout experience, reducing friction when making purchases. With saved payment methods, upgrading or adding new services is now quicker and more convenient.
---
## The Changing SEO Landscape in 2025: How Website Speed, Core Web Vitals & Other Factors Now Impact Your Rankings
- URL: https://levamo.com/blog/changing-seo-lanscape/
- Category: seo
- Author: Faisal Sarker
- Published: 2024-11-21
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
SEO in 2025: Website speed, vitals, & more impact rankings. Find out how!
Did you know that Google uses over 200 factors for ranking websites? While it is not humanly possible to work on all 200 of these, there are a few really important ones we will be discussing herein.
In this guide, we will be exploring how the rise of AI, core web vitals, [website speed test](https://www.dotcom-tools.com/website-speed-test), content relevancy and voice search are all going to change the SEO landscape in 2025.
Key takeaways:
- Core Web Vitals are now a part of Google’s ranking factors.
- Writing structured content only for rankings, may lead to penalties.
- Focus on generating quality content on search intent to fill the information gap.
- Google now prioritizes page speed and user experience.
- High-quality, original content is still the king that dominates search results.
## What are Core Web Vitals and Why Are They Really Important?
According to the Google Search Central Developer Documentation, Core Web Vitals is:
**A set of metrics that measure real-world user experience for loading performance, interactivity, and visual stability of the page.**
The three Core Web Vitals are:
- **Largest Contentful Paint (LCP)**- This metric measures how quickly your website starts loading and displaying the main content. Ideally, this should not exceed 2.5 seconds.
- **Interaction to Next Paint (INP)**- This metric measures how responsive your site is to the actions that a user takes. In short, it measures interactivity. If you have a well-optimized and responsive site, this time should not exceed 200 milliseconds.
- **Cumulative Layout Shift (CLS)**- This metric measures visual stability, which points out to the unexpected shifts in user interactions. This should be less than 0.1.
Here’s how you can check your website’s Core Web Vitals through Google Search Console:

## How Do Core Web Vitals Impact Rankings?
How well your website responds to the end users is what Google considers now to be an important ranking factor.
Visitors are more likely to spend time and convert to customers if your page is well-optimized, fast, and fulfills Google’s core web vital metrics. By focusing on [effective local SEO strategies](https://gorilladesk.com/learn/marketing-a-landscaping-business/), you can increase your visibility in specific geographic areas where your target audience is located.
So let’s understand how each of these metrics impact page ranking.
### Largest Contentful Paint
LCP shows how quickly your page’s main content loads up. The following elements comprise of the loading time for LCP:
- Images
- Image tags
- CSS
- Large blocks of text
You can use [Google PageSpeed Insights](https://pagespeed.web.dev/) to test core web vitals and diagnose performance issues.
If your LCP is:
- Less than 2.5 seconds - Your page has a fast loading time. (Green)
- 2.5 to 4 seconds - Page needs further optimization. (Orange)
- More than 4 seconds - Page load time is extremely poor and needs immediate attention. (Red)
Google also shows LCP data for all of your web pages, so that you can focus and start improving them one by one.
### Cumulative Layout Shift
CLS measures any unexpected or sudden movements when your page loads. Visitors will get confused when the order of elements on your web page keeps changing. A healthy score to target is less than 0.1.
If your CLS score is:
- Less than 0.1 - No sudden changes in layout.
- In between 0.1 and 0.25 - Website visitors are able to notice a significant amount of shifting in the page content once it loads.
- Over 0.25 - You need to redesign or fix the entire layout as there are far too many sudden movements in the content, such as big texts and buttons appearing out of nowhere. This deteriorates user experience and severely affects your rankings.
### Interaction to Next Paint (INP)
INP is the latest Core Web Vitals metric to replace First Input Delay (FID) on 12th march, 2024.
It measures how quick your website is in responding to the interactive elements. INP tracks, measures and then assigns a score in terms of user interaction. This number is in milliseconds.
So let’s suppose a visitor lands on your page, zooms in on a map, submits a form, and clicks a button. INP measures the time from the first interaction (zooming on a map) up to the last interaction (clicking a button).
If your INP score is:
- 200 milliseconds or less - All interactive elements are responsive.
- In between 200 and 500 milliseconds - Improve the interactive elements.
- Over 500 milliseconds - There are multiple glitches and lags when users interact with your site. Fix them to improve user experience
That’s why it is critical to have a reliable web host that exceeds all [benchmark tests for core web vitals](/benchmark-methodology/).
## So What Can You Do To Improve Your Core Web Vitals?
Streamline the code by removing unnecessary third-party scripts. Third party scripts put extra load on the web server. Do not have more than the required scripts to run your page smoothly.
Migrate to a [reliable and faster web host](/managed-wordpress-hosting/). Better hosting leads to faster load times, boosting the overall user experience, thereby positively impacting your core web vitals.
CSS, JS and uncompressed images will easily choke up your website, and before you even know it, visitors will bounce off as if they never arrived. Make sure to use services like [Minifier](https://www.minifier.org/) and [TindyPanda](https://tinypng.com/) to compress the code and multimedia content to reduce page load time.
These suggestions will help you to dramatically boost your site speed for all three metrics of [core web vitals](/blog/core-web-vitals-and-seo/).
## So Is Having Excellent Page Experience Enough?
Yes, and no. Yes, because you need to provide the best possible user experience. No, because it isn't the only ranking factor. There are hundreds of factors that Google takes into account for ranking a website, and page experience is just one of them.
Needless to say, if your well-optimized website is neither helpful nor relevant to your users, you will struggle in organic rankings.
That’s why quality content remains vital. Whether you run a [WordPress](/managed-woocommerce-hosting/) blog or an ecommerce website, you can never achieve your targeted ranking without consistently publishing quality content that is helpful for your audience.
So instead of writing well-structured content for search engines, it is time to write for your visitors. This was the target of the mid-2022 Helpful Content Update by Google, which has now become a part of the March 2024 Core Web Vitals.
Write helpful, authoritative and informational content that puts you in the limelight. Develop topical authority so that Google considers you an expert in your field and rewards you with better rankings and traffic.
Write content that shows Google you have EEAT (Experience, Expertise, Authoritativeness and Trustworthiness). For example, we want our resources such as blogs, case studies and white papers to be an ultimate representation of our experience and trustworthiness in the cloud hosting industry. When a visitor reads our content, we would ultimately want them to trust us as experts in our field.
Similarly, you have to build this trust with your audience in your field by constantly publishing textual and video content that demonstrates your excellence in the industry.
Remember that whatever you do has to eventually help your target audience, not search engines.
## Why Site Speed Matters More Than Ever?
The digital landscape has everyone racing for views, clicks and leads, resulting in revenue for their business. But all of this boils down to one thing; how quickly does your site open up to your users. That’s because users' patience is waning. In an age of high-speed internet, slow sites will have no room to compete in 2025 and beyond.
A 2023 study found that websites loading in under 3 seconds [experienced 32% lower bounce rates](https://www.outerboxdesign.com/digital-marketing/page-speed-conversion-statistics/#:~:text=Page%20speed%20continues%20to%20be%20a%20crucial%20factor%20for%20SEO,website%20page%20speed%E2%80%8B%E2%80%8B.) than slower sites. What’s worse? You lose 90% of the traffic when this load time shoots up to 5 seconds.
For e-commerce websites, a delay of even [1 second can lead to a 7%](https://www.bigcommerce.com/glossary/page-load/) reduction in conversions.
Levamo provides a reliable foundation by offering advanced caching, CDN integration, and quick-loading server infrastructure. This minimizes server response time, ensuring your website stays competitive in Google’s speed-driven algorithm.
But it isn’t just limited to Google. People shouldn’t suffer with slow page loading speed when they already have great options. The quality of your hosting provider is no longer just a convenience - it’s a necessity. Hosting affects load time, uptime, and user experience, all of which play a vital role in SEO.
Faster server response times directly improve LCP and user satisfaction leading to better user experience. While downtime can severely impact rankings and user trust, at Levamo, we provide an iron-clad [99.99% uptime guarantee](/blog/choosing-reliable-hosting-provider/).
## Why Go For a Mobile-First Index?
With over **60% of searches** conducted on mobile devices, Google’s mobile-first indexing has made mobile performance a priority. Gone were the days when a website was designed for desktop, and then redeveloped for smartphones. Today, it is the exact opposite.
If a website isn’t responsive, you may lose a big chunk of your audience. Always ensure the website layout adjusts seamlessly to different screen sizes.
## How AI Tools and Algorithms Are Reshaping the Landscape?
Artificial intelligence (AI) is transforming SEO by enhancing search engine algorithms and automating data analysis.
Google and Bing now leverage the power of AI in their search results. Let’s say if you were to do a quick Google Search on “**What are core web vitals**?”, here is how the search results will appear:
And here are the search results for the same query on Bing:
You can see how both search engines are using AI to generate meaningful summaries and content, which will immediately help the users with the right information.
This means that **keyword stuffing** and **over-optimization** have already become obsolete. Instead, AI favors content that matches user intent with high relevance and natural language flow.
For that reason, effective [local keyword research](https://pwd.com.au/blog/local-keyword-research/) is needed to ensure the content resonates with the specific needs of target audiences in different geographic areas.
According to a [Hubspot survey](https://offers.hubspot.com/ai-marketing), digital marketing professionals use a number of AI tools for content creation, with most of them utilizing chatbots (53%).
Search engines and brands have already started taking the help of Generative AI, and it is time you do the same too.
### SSL, Security, and SEO in 2024
Cybersecurity is becoming a nightmare for website owners. According to a report, there are [97 victims](https://aag-it.com/the-latest-cyber-crime-statistics/#:~:text=With%20an%20average%20of%2097,their%20data%20leaked%20every%20second.) of a cyber crime every hour. Security has always been a ranking factor, but Google’s emphasis on SSL certificates and HTTPS in 2024 highlights its importance.
Sites lacking SSL certificates are labeled “Not Secure,” which impacts both user trust and ranking potential.
All of our hosting plans come with a host of [security features](/managed-security/), which include:
- Free SSL Certificates
- Advanced DDoS Protection
- Vulnerability Scanning
- Bot Protection
- Malware Removal
- 24/7 Real-Time monitoring and mitigation of threats
[SSL certificates](/blog/ssl-website-security/) also help in protecting confidential user information such as bank details, credit card numbers, name, DOB and residential address.
**Read More:** [TLS vs SSL](/blog/tls-vs-ssl/)
## What Are The Technical SEO Trends to Watch in 2025?
Alongside Core Web Vitals and hosting, a few key technical SEO trends stand out in 2025:
**Structured Data**
Google’s AI relies on structured data to understand website content. Implementing schema markup for products, reviews, and events helps search engines accurately interpret and display content.
You should also structure your content in headings, embedded videos, infographics and images to make it more appealing and engaging for your audience.
**Server-Side Rendering (SSR)**
SSR enhances SEO by delivering fully rendered pages to search engine crawlers. This setup is ideal for websites with heavy JavaScript usage.
**Content Delivery Networks (CDNs)**
CDNs reduce load times by delivering content from the server closest to the user. Using a CDN can improve both speed and reliability, making it a key investment for any site focused on SEO.
We have designed our [managed WordPress hosting solutions](/managed-wordpress-hosting/) for your peace of mind.
## Wrapping it all up
In 2025, SEO will no longer be just about backlinks and keywords. Instead, it will be a complex mixture of user experience, content quality, relevancy and speed. AI-based search results, mobile-first indexing and the Core Web Vitals are all shaping up the SEO landscape. It is time that you stay ahead of the market trends and consider your website more like a digital asset.
Remember, your goal should be to provide the best possible user experience while delivering quality content that solves real-world problems.
---
## E-commerce Trends & Black Friday 2026: A Comprehensive Analysis of Trends & Opportunities
- URL: https://levamo.com/blog/e-commerce-black-friday-trends/
- Category: ecommerce
- Author: Faisal Sarker
- Published: 2024-11-19
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
BF 2026 e-commerce trends: Exploit holiday sales with our analysis.
E-commerce is booming. Last year, online sales reached an [astounding $5.8 trillion](https://www.statista.com/statistics/379046/worldwide-retail-e-commerce-sales/), with projections indicating further expansion to over $8 trillion by 2027.
This rapid growth has redefined the competitive landscape, particularly among the industry giants Alibaba and Amazon. And while Alibaba holds a significant lead with nearly a quarter of the market share, Amazon isn’t trailing too far behind with projected sales expected to reach $1.2 trillion in the near future.
So, as we head into Black Friday & Cyber Monday 2024, the stakes have never been higher. For many brands, this could be a critical opportunity to excel - or risk falling behind. The question is: Are you prepared to capitalise on this moment? What e-commerce strategies do you have that will differentiate your brand and ensure success during this pivotal holiday season? What’s the next viral product to sell, and in which market?
These and a lot more questions are critical to answer as you step into the thick of the holiday sales season. And at [Levamo](/), we’re not just about providing a Hyperspeed hosting for dynamic websites; we also provide in-depth insights to help our users and readers understand what truly matters for their success.
So here’s a comprehensive look into the E-commerce trends and predictions for Black Friday 2024 and other insights that will help you create a strong holiday strategy.
## Key Takeaways
- E-commerce sales are surging - and are projected to reach over $8 trillion by 2027.
- Smartphones are expected to account for 62% of e-commerce sales - and social platforms like Instagram and TikTok are driving significant sales growth.
- Direct-to-consumer (DTC) models and eco-friendly products are increasingly popular.
- AI personalisation, BNPL options, and chatbot support are enhancing customer experience and conversions.
- Black Friday 2024 will see more businesses using strategies like personalized marketing, loyalty programs, and robust mobile optimisation, essential for capturing seasonal sales growth.
## E-commerce Overview: 2019 - 2024
The global eCommerce market really took off from 2019 to 2024, and different regions are playing big roles in this growth.
- **E-commerce Trends in North America, Europe and Asia Pacific**

Things are looking bright in North America. The e-commerce market is projected to reach $1327 billion in 2024. And it is not stopping here. It will continue to grow at a 9.09% annual increase over the next few years - reaching $2050 billion by 2029.

Europe is also seeing [immense growth in eCommerce](https://www.statista.com/outlook/emo/ecommerce/europe). The market is expected to reach $632.66 billion, and by 2029, it will hit $977 billion. And that is a solid 54.48% growth. So we can say countries like the UK, Germany and France are leading the way as more people embrace online shopping.

Asia Pacific is also leading the way, with China at the forefront. China is expected to bring in [about $1,469 billion in eCommerce revenue](https://www.statista.com/outlook/emo/ecommerce/china) in 2024. These numbers are something that all entrepreneurs should watch closely, especially if they are looking to increase sales this Black Friday!
- **From Desktop to Mobile: The Shift in Online Shopping**
Our research indicates that **mobile shopping trends** will continue to have a major impact.
**That’s because mobile e-commerce has reached a massive $2.2 trillion, making mobile shopping set to account for 62% of e-commerce, with sales hitting $3.4 trillion.**

So, what’s driving this chance? It is simple: ***convenience***. People love the ability to shop whenever they want - whether on the move or relaxing at home. This shift is something every e-commerce store owner, marketer, and tech professional needs to take seriously.
- **Social Commerce on The Rise**
Social media is no longer just for scrolling with platforms like Instagram and TikTok making it easier than ever to shop online and turning into something more than just consuming media.

In 2023, social commerce brought in [$571 billion USD worldwide](https://www.statista.com/statistics/1231944/social-commerce-global-market-size/), and it is only going up! Experts think it could double and hit $1 trillion by 2028.

This shift is too big for eCommerce store owners and marketers to ignore.

- **The Direct-to-Consumer (DTC) Trend**
*Think about this:* you are a shopper who gets to buy straight from your favourite brand, with no middlemen and no extra steps. That’s the magic of DTC - it is a more personal experience. You feel more connected, and the brand feels like it really gets you.

DTC brands are totally transforming eCommerce by connecting directly with their customers. It’s kind of the rage right now, and I get why. It helps bring the brand closer to your audience - and gives you more control over how others perceive the product.
- **Total e-commerce market size (USD) in 2019 vs. 2024**

Let’s take a look at how massive the e-commerce market is becoming. Back in 2019, the was already impressive. But fast forward to 2024, and we are talking about $8.8 trillion globally. And it is not stopping there. According to many, it will hit $18.81 trillion by 2029. That’s nearly doubled in just five years - growing at a 15.8% annual rate.
- **Percentage of retail sales done online across major countries**
Online retail sales, as expected, [have increased](https://www.emarketer.com/content/worldwide-ecommerce-sales-break-6-trillion). Now, the post-pandemic years of 2021 and 2022 saw a stagnancy in sales - with online sales around 18.9% of the total.

However, this year, we expect online retail sales to make up over 20.1% of the total retail sales and worth over $6.334 trillion USD. That figure will go up to 23% by 2027.
We can see similar rise in US retail eCommerce holiday season sales from 2018 to 2024.

- **Mobile vs. Desktop During Sales Trend**
Did you know mobile shopping officially took the lead over desktop shopping during Cyber Week? Even a few years ago, mobile conversations barely inched past desktop at 49%. But mobile surged to 53% last year - a solid 8% lead.

With more shoppers checking out on their phones than ever, retailers need to make sure their websites are mobile-ready. A seamless experience could be key to capturing those valuable Cyber Week Sales.
## Shifting Consumer Preferences and Emerging Trends
We also see users interacting with businesses differently. For instance, here are three things we are noticing.
- **Subscription models are changing the e-commerce market**
Subscription models are growing fast, especially in SaaS and curated products.

The U.S. subscription hit over $23 billion in 2020 and, by 2023, had generated over [$38 billion](https://www.statista.com/statistics/452764/subscription-e-commerce-sales-united-states/) in year sales - more than double from just a few years ago.

Consumers love convenience and personalisation.
- **More people are now more into eco-friendly brands** *
Sustainability is no longer just a buzzword - it is becoming a top priority for consumers. In fact, products with ESG (Environmental, Social, Governance) claims saw an impressive [28% cumulative growth from 2018 to 2023](https://www.mckinsey.com/industries/consumer-packaged-goods/our-insights/consumers-care-about-sustainability-and-back-it-up-with-their-wallets), outpacing the 20% growth of products without these claims.
More and more shoppers want to support brands that align with their values, ones that are eco-friendly and socially responsible. And if you are not considering sustainability in your business, it is time to rethink your strategy. Consumers are making their choices, and they are leaning toward green!
- **Same-day delivery is reshaping consumers' expectations**
Speed is everything these days. Imagine placing an order and expecting it to show up the same day. Well, that’s exactly what more and more customers want.
The global same-day delivery market is only increasing. Three years ago, in 2021, it was valued at around $8.4 billion. And by the end of 2027, it is expected to go up to [$26.4 billion](https://www.statista.com/statistics/1255427/same-day-delivery-market-size-worldwide/) USD.

While you can implement tons of strategies to build brand loyalty and customer trust, you need to do what your competitors are doing first. And I think many are focusing on how they can achieve quicker deliveries.
## Top eCommerce Strategies Businesses Can Use This Holiday Season
Now that we know the top general e-commerce trends, what can you expect this Black Friday? Levamo took a look at the top strategies businesses are using this festive season, and compiled them for you.
Here are my e-commerce predictions for Black Friday 2024 that businesses are using - and what I believe can power your business ahead.
- **AI-powered personalisation**
AI is transforming how we shop online. Imagine getting product recommendations tailored just for you - this is AI at work! Half of the decision-makers in customer experience are already using AI to analyse feedback and even predict trends and [shopping habits by 2024](https://www.statista.com/statistics/1490150/ai-customer-experience-adoption/).

Personalized shopping is no longer a bonus - it is becoming essential. Using AI can mean happier customers who find exactly what they need for eCommerce businesses. More businesses are adopting AI this Black Friday to woo more customers.
- **BNPL (Buy Now, Pay Later)**
“Buy Now, Pay Later” changes how people pay. In [countries like Sweden and Germany](https://www.statista.com/statistics/1233850/online-bnpl-penetration-country/), BNPL has now become one of the top payment options. Shoppers love the flexibility - spreading payments over time without using a credit card.

And for retailers? BNPL means more conversions and bigger orders. As customers are more likely to purchase when they don’t need to pay all at once. If you know people are interested in your product, Black Friday presents a great opportunity to increase conversions with BNPL.
- **Loyalty programs & their effect on consumer retention**
Loyalty programs are not just about points. They are about building connections. 79% of consumers said they bought more often from brands with loyalty programs, according to data in 2022. And that works - [70% of U.S. consumers](https://statista.com/statistics/1375145/top-ways-loyalty-programs-influenced-consumer-behavior-us/) in loyalty programs keep customers engaged, spending more and coming back. For e-commerce, a [good loyalty program](/blog/woocommerce-loyalty-program/) can turn one-time buyers into lifelong fans.

If you’re still in two minds about whether your business should target customers on Black Friday, read on. We are answering a few of the common questions you may have,
### *Is BFCM’s sales impact growing every year?*
Black Friday and Cyber Monday keep setting records! For 2024, online sales during “Cyber Five” (Thanksgiving to Cyber Monday) are expected to hit over $39 billion and $2 billion more than last year.

Despite a slow start on [Black Friday 2023](https://www.statista.com/statistics/283409/cyber-five-e-commerce-sales-united-states/), European sales also grew 7% over 2022. In short: across North America, Asia Pacific and Europe - BFCM is now a major revenue driver. It has become a powerhouse that retailers can count on every year.
### *How much of annual sales come from the holiday season?*
How much money do you think the average shopper spends during the holiday season? In the U.S. we will see people spending between $957 to $967 Billion USD in the last two months of the year. That’s, on average, a good [$875 per customer](https://www.statista.com/chart/11979/holiday-season-retail-sales/)!

For some shops like toy and hobby stores, the last few months make up over a third of their yearly sales. In fact, for many retailers, holiday sales account for at least a quarter of their total revenue.
This shows us just how essential this season is for e-commerce businesses.
### *Why does conversion rate matter so much during BFCM?*
During Black Friday and Cyber Monday, getting conversions right is everything. Google Ads saw an average [conversion rate of 3.75% this year](https://convert.bouncex.com/rs/445-FJV-353/images/Wunderkind-BFCM-Insights-Guide.pdf), and Facebook Ads did better at 7.75%. Traditional methods like SMS and email really stand out. SMS had a solid 5.5% conversion rate, while email reached 19%.

So, to make the most of BFCM, focusing on email and SMS could make a big difference in keeping shoppers engaged. Plus, **hiring a [web hosting site](/blog/black-friday-hosting-preparation/)** will also help you have fast and secure websites to handle traffic and prevent cart abandonment during peak times like BFCM!
## Black Friday Cyber Monday BFCM 2024: What to Expect

So here we are with the exciting news about BFCM - indeed, things are looking great! And we expect the holiday season to see a 3.0% growth overall, with a huge 9.5% increase in non-store sales, including eCommerce and mail orders.
If you are in the UK, Black Friday is set to bring in £800 million more than last year, a 27% jump! Yes, it is time to prepare for a busy and rewarding season.
### Retailers are Going All in at BFCM Deals
From 2020 to 2023, [global BFCM sales](https://www.salesforce.com/news/press-releases/2020/12/01/salesforce-reveals-2020-cyber-week-digital-sales/) have increased from $270 Billion USD to $298 Billion USD.
Retailers are getting smarter each year with their strategies for Black Friday and Cyber Monday.
- Early discounts and exclusive offers are the go-to moves for grabbing shopper’s attention early on.
- Personalised marketing and targeted promotions are gaining more success.
- Omni-channel marketing strategies like ‘**Buy Now, Pay Later’** are getting more popular.
- Influencer collaborations and a better mobile UX
- Better cybersecurity and fraud prevention measures.
These strategies are paying off big time - especially when you look at how BFCM sales have grown over the last few years! And that’s why, we see:
- The [average global order value](https://www.syte.ai/blog/bfcm-resources/bfcm-2023-top-trends-and-takeaways/) increased from $121 in 2022 to $127.6 in 2023.

- Home decor and jewelry continues to outperform, with an [average order value](https://www.syte.ai/blog/bfcm-resources/bfcm-2023-top-trends-and-takeaways/) of $511.7 and $285.5
- We are looking at an even higher average holiday spend of around $1,778, which is an [8% increase](https://www2.deloitte.com/content/dam/insights/articles/us187581_cic-holiday-retail/2024-Deloitte-holiday-retail-survey_Protected.pdf) year-over-year.
However, we do see a strategic shift in consumer behavior, with customers trading loyalty with more affordable choices. That’s perhaps more because of inflationary pressures, as we will talk about below.
## Technological Innovation Is Driving Continued E-commerce Success
So, what are companies doing to enhance customer experience and streamline operations? We talked about personalisation and innovation in e-commerce. It all depends on how you make customers know about you or want to know more about you. You can do that in different ways, like with a Black Friday campaign or creating a customer-centric experience.
- **Customer Service Automation**
Bots help with everything, from instant answers to better engagement. More Americans are adopting chatbot usage when shopping online, with The New York Post reporting that over 47% use it when shopping online and over 35% when setting up deal alerts.

Like last year, during the holiday season, we saw a 10% year-over-year increase in AI-powered chatbot sessions. We don’t believe that should be your only go-to strategy for customer engagement, but customer service automation through chatbots does seem to help brands meet customer needs efficiently.
- **E-commerce Platforms and Adoption Rates**
Many businesses start with platforms like Shopify, WooCommerce and BigCommerce for their online store. Some of them you can create right on WordPress - like many levamo.com customers do. They use the [WooCommerce WordPress plugin](https://en-ca.wordpress.org/plugins/woocommerce/) to set up their own store.

That’s also in part because you don’t need to invest in a separate Shopify plan - your managed WordPress or WooCommerce hosting plan with us has it all covered. Levamo WooCommerce hosting plan, for instance, features everything you need for a smooth user experience. We have got everything from CDN, free SSL, Object Cache Pro to backups and more - all included in one single plan price.
- **AI in E-commerce Sales**
Now, my favourite part. Customers can engage with bots, but they need to feel that you deliver something that they need. And that’s where personalisation comes into play. Fortunately, using A.I. can help you do that - ensuring you show up products and customer flows that can keep them engaged.
They put a brush on the cart but didn’t check out? Have an email sent to them about an offer on their cart item. Did someone browse some coffee cups on your site? The A.I. can check their interests and suggest more relevant ones to them. The possibilities are endless.

Research by McKinsey, for instance, indicates that **businesses investing in AI are seeing a revenue uplift of 3-15% and a sales ROI uplift of 10-20%**.
- **Market Size of SaaS Tools in E-commerce**
Since last year, companies have been adopting SaaS tools much more significantly. I see more businesses looking to use SaaS tools to improve operational efficiency.
And that’s what we have - while the e-commerce SaaS market is expected to reach around[ $9.4 billion USD](https://www.businessresearchinsights.com/market-reports/e-commerce-saas-market-102571) by the end of this year, we are looking at an industry size of over [$26 billion USD](https://www.verifiedmarketreports.com/product/e-commerce-saas-market/) by the end of 2030.
So, when I say we are seeing an increased adoption rate for SaaS tools, I mean it!
## Challenges and Risks for E-commerce in the Near Term
The first major challenge would be that we have to be prepared for a dot-com-level bust.
Everyone’s using A.I. - and two things can happen.
- For one, with the increased competition, if you don’t adapt, you go out of the game.
- The other is that the number of SaaS tools in the market will change - not all will survive, especially given changing market conditions.
For your business, it means relying on tools that are effective and reliable and do their job. Additionally, here are some of the other things we need to look for.
- **Economic Pressures: Inflation and Recessionary Concerns**
Less demand can mean fewer sales. And with inflation surging in the last couple of years, businesses have had it challenging to make sales. In fact, we don’t have to go far back to see this. When [inflation surged in 2022](https://gripsintelligence.com/articles/cost-of-living-crisis-impact-on-ecommerce-in-uk), the **Average Order Value (AOV) rose by 12.1%** compared to 2021.
Some categories were affected far more than others. Health, for instance, saw a **10.3% increase**, and grocery grew by **12.1%.**
That means a few things:
- Your cost of producing goods is increasing.
- Customers do not want to spend more on the product
- They are, in fact, trying to reduce their spending.
So, the catch-22 for you? You can’t increase prices because of falling demand, while you’re seeing more input costs to your products.
Now, thankfully, inflation is on a downward trend, but you still need competitive pricing to stay afloat. And you can only do that with value-driven strategies.
- **Supply Chain Disruptions and Impact on Delivery Times**
You want to meet your customer demand - at all times. And while you can have reliable suppliers, you can’t control outside variables - like wars and political disruptions. In 2023, we had a fair bit of that, which created supply chain issues at the peak of the holiday season. This caused the composite rate to [surge beyond 200%](https://www.ft.com/content/17bb8aef-9ce2-437c-a450-16deb4d92880). That’s not all - spot freight prices tripled during that time.
- For your business, it might mean higher global shipping costs and longer delivery times.
- Customers won’t like their delivery to be late - and this can lead to falling brand loyalty and satisfaction.
- For your business, it might mean the need to diversify and invest in efficient logistics solutions.
- Increasing Competition and Rising Customer Acquisition Costs (CAC)
The number one challenge for your business is to get more customers. And today, we are looking at increasing customer acquisition costs across industries.
Shopify [states that these costs](https://www.shopify.com/uk/blog/customer-acquisition-cost-by-industry) can be as low as $21 if you’re in the arts and entertainment industry, or as high as $377 for the electronics niche.
## Growing Importance of Cybersecurity
With everything being said about strategies and trends, we have to tell one important thing. If you’ve an online business, you need a robust platform. And I will tell you why - online frauds have been increasing. Every year. From 2020 to 2023, the value of online fraud increased from $17.5 billion to over $48 billion.
As we collect more customer data, protecting customer information is crucial. With Levamo, it’s easy to secure your site with our industry-grade malware security, and advanced DDoS protection, WAF and Bot protection.
## Future of e-Commerce Beyond 2026: Predictions and Projections
Our **eCommerce strategies for the holiday season** are simple - future proof your business. And adapt - as needed.
Personalisation will continue to grow - because the use of AI alone will not cut it.
Personalisation is just one lever, though, the stores that keep climbing after the Black Friday spike fades are the ones running a year-round plan for acquisition, retention, and average order value. If you want that momentum to outlast the holiday season, it’s worth [building a strategy around it now](https://wholesalesuiteplugin.com/top-wholesale-holiday-promotions/ "nofollow").
While brands will use A.I. to cut costs and streamline operations, it’s about connecting to customers and their needs. As businesses access newer markets, especially across Asia Pacific and Europe, they will also look at newer ways to engage customers.
- Some of them can be done through the metaverse.
- More widely used AR and VR strategies can help customers try on products virtually and experience what it’s like to ‘own’ them first.
- Some businesses may also experiment with drone deliveries in order to reach customers quicker. Dominos, in the U.S., has [already started experimenting](https://dronedj.com/2022/01/27/dominos-pizza-drone-delivery-new-zealand/) with it.
- Some believe that drone delivery could become a standard offering for quick, cost-effective shipments in the next few years.
There is another aspect to the mass adoption of A.I. We will see more voice commerce - or where people are buying new products directly with the help of Alexa or Siri. Your business’ integration with smart devices may pave the way for more online sales, as you can continue to build up on customer satisfaction with immersive user experiences.
As Black Friday 2024 approaches, we can see that businesses are looking at refined strategies and innovative technologies. From mobile optimisation to AI-driven personalisation, businesses have multiple avenues to reach and engage their audiences effectively.
If you want to survive, you need to prioritize customer experience, security, and efficient logistics to stay competitive. At Levamo, we have some of the best tools for you to achieve that. *And this Black Friday, we have our own exclusive deal that you might just want to look again at!*
---
## Build Your Online Learning Platform with Tutor LMS: A step-by-step Guide
- URL: https://levamo.com/blog/build-lms-website-with-tutor-lms/
- Category: lms
- Author: Sunyyan Junaid
- Published: 2024-11-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Create your own online learning platform using Tutor LMS. Start now!
In 2023, the e-learning market hit a staggering $307.5 billion, and it's projected to exceed $1.50 trillion by 2033. For aspiring course creators like you, this translates into immense earning potential. But to succeed, you need the right guidance and tools.
This guide will show you how to create an efficient and scalable **Learning Management System (LMS)** with [Tutor LMS](https://tutorlms.com/) in WordPress. Tutor LMS, one of the best LMS plugins for WordPress, empowers you to design and monetize an interactive learning experience, similar to Coursera and Udemy. And if you are also ready to convert your skills and passion into profit, then creating and selling online courses on [WordPress using Tutor LMS](/managed-lms-hosting/) is the way to go.
With zero coding knowledge and a low upfront investment, you can build your own digital asset within days.
### Key Takeaways:
- Create a fully-functional LMS website on WordPress using Tutor LMS.
- Set up your online course website using [Levamo hosting](/managed-lms-hosting/).
- Highly cost-efficient method of starting your own e-learning platform.
- Installing and setting up Tutor LMS on your WordPress website
**Ready to create your own LMS? Let’s get started.**
## What is a Learning Management System?
A learning management system, short for LMS, is a web app that allows you to publish courses with all the bells and whistles that you’d expect from an actual classroom. These include quizzes, assignments, video lessons, student progress reports, grade sheets, full-length practice tests, live classes, etc.
In short, it’s a robust solution for anyone who wants to create an online learning platform.
## What Do You Need to Build a Great LMS?
To build a robust LMS website, there are three essentials that you need:
- A responsive and fast WordPress theme
- A powerful cloud hosting solution
- An industry-leading LMS
Let’s understand them one by one.
### 1. Why Tutor LMS?
Tutor LMS
Built by Themeum, a premium WordPress design agency, Tutor LMS is an all-in-one powerhouse that converts your simple WordPress website into a dynamic online learning resource. It checks all the essentials and more:
☑️ Create, manage, and sell online courses from your WordPress website.
☑️ Develop engaging quizzes, practice tests, and assignments to engage students.
☑️ Have multi-instructor support with numerous teachers publishing their own courses.
☑️ Host multimedia content, including audio, video, and documents.
[Tutor LMS Pro](https://tutorlms.com/pricing/) is the premium version of the course builder and is top-rated on Trustpilot. It only costs $199 a year to create unlimited courses and comes with advanced features such as import/export quizzes, course content protection, drip course content, and more. The UI/UX is also super easy to build your own LMS.
But that's not even the best part. We have our clients using Tutor LMS for selling all sorts of courses and learning materials across multiple niches like **language teaching** (IELTS, TOEFL, PTE, any other language), **health and fitness coaching**, **digital marketing training**, and **productivity tutorials**, to name a few.
Whatever you can think of, you can indeed sell online using Tutor LMS.
### 2. Why WordPress?
You can’t be wrong going with an open-source platform that hosts nearly 42% of the websites. With a truly global community, you will join a massive community with support at every step of the way.
Here are some reasons why WordPress is the ideal choice for LMS creation:
- Economical solution that doesn’t take a toll on your budget
- Complete control over your LMS
- Multiple customization options
- Scale your business as your traffic grows by adding new courses and upgrading to a more premium hosting services.
### 3. Why Levamo for your Online Course Website?
[Levamo](/) and Tutor LMS is a match made in heaven. Why?
Because Levamo is custom-built for dynamic websites and delivers performance that blows every other [LMS hosting service](/managed-lms-hosting/) out of the water. You can read the benchmarks linked above, but choosing Levamo gives you hyperspeed hosting that doesn’t just perform incredibly well when you have high traffic and concurrent users, but scales seamlessly when your server capacity is full.
But here’s an overview of why Levamo is the best choice for anyone building a Tutor LMS website:
Truly fast performance: Most hosting providers claim they are fast. But when it really comes down to it, most hosts fail when there’s high traffic and concurrent users. But Levamo is built to [handle dynamic websites](/managed-wordpress-hosting/) with high traffic. Read this [case study](/blog/english-pro-tips-case-study/) to find out more.
**Seamless Scalability**: Levamo boasts vertically dynamic servers, meaning that when traffic spikes hit, your server simply scales to handle the load seamlessly, and your website keeps performing as smoothly as ever.
**Top-Tier Security**: Levamo has a proactive multi-layered defense strategy, complete with firewall protection, proactive vulnerability detection, and many more [security measures](/managed-security/) to ensure your online business and customers are completely safe from attacks.
**Simple Platform**: No one likes complexity, which is why the Levamo Platform was built with [simplicity in mind](/easy-to-use-platform/). You can accomplish all tasks in a few clicks, enabling you to focus on growing your business instead of managing your servers.
**24/7 Expert Support**: While we hope for a seamless hosting experience for you, in case you are stuck and need a helping hand, our 24/7 expert support is available round the clock to ensure you’re in good hands.
While there’s a lot more to talk about Levamo and why it should be the number one choice for anyone building a Tutor LMS website, we need to bring our focus back to creating a Tutor LMS website.
Let’s get on with it.
## Step-by-Step Guide to Installing Tutor LMS on WordPress
### Step 1: Choose a Hosting Solution
To host your online content, you need a reliable hosting provider that not only handles all the bandwidth you need to stream audio and video content but also scales as you grow. With levamo.com, you don’t have to worry about powerful hosting features, website security, and speed. Its cloud infrastructure supports quick content loading and handles high traffic levels, useful for streaming multimedia content.
- **Sign up** for a [plan on Levamo](/pricing/) based on your expected traffic and storage needs.
- **Install WordPress**: All Levamo cloud hosting for LMS plans comes with WordPress pre-installed.
### Step 2: Install and Configure Tutor LMS Plugin
To get started with Tutor LMS, you’ll need to install the plugin on your WordPress site. Tutor LMS offers a free version, but upgrading to Tutor LMS Pro unlocks additional features that are particularly useful for course creators.
- **Install Tutor LMS**: Go to your WordPress dashboard, navigate to Plugins > Add New, and search for **Tutor LMS**. Click on **Install Now**.

- **Activate Tutor LMS:** Click on the Activate button to activate, follow the on-screen instructions, and set up the LMS plugin

- **Basic configuration**: After activation, you will be taken through the initial setup process. Once the plugin is set up, you can see it in the left menu of your WP dashboard. Once you click on courses, you will be taken to the following screen.

### Step 3: Create and Organize Your Courses, Add Topics, Lessons, and Quizzes
Now that you are all set up, you need to click on **Add New** at the top left or simply head over to **Tutor LMS > Courses > Add New Course**:

Enter the course title, description, and thumbnail image just like you would write and publish a blog post. The interface and publishing format of the Tutor LMS course is no different than that of a blog, which makes it super easy for anyone to create and launch their online courses.
- **Add lessons and quizzes**: Add video lessons, PDF files, assignments, quizzes, and full-length mock tests for each course. To do this, scroll down, and you will see the option to add a **new topic**.

- Click the **Add new topic**, and in a new pop-up window, write the **Topic Name** and **Summary** for the new lesson. Once done writing, click on **Add Topic**.

- You can now see the new topic added to the course curriculum. Once you have added a topic, you can unlock additional options such as Lesson, Quiz, and Assignments. To integrate Meet Live Lesson, you need to integrate the Google OAuth API and connect your Gmail account. However, in most cases, that is not required.

- To add a new Lesson, click on the **Lesson** button on the left side, and you will see a new pop-up window similar to this. Add in the **Lesson Name**, **Lesson Content**, and once completed, click on **Update Lesson**.

To add a quiz, simply click the **Quiz** option next to **Lesson** and in a new pop-up window, you will be taken to create a new quiz. Provide some quiz info and click on **Save & Next**. Here you will have the option to add in as many of the following question types as you want:
- True/False
- Single Choice
- Multiple Choice
- Open Ended
- Short Answer
- Fill In the Blanks
- Matching
- Image Matching
- Image Answering
- Ordering
You can select any one of these options from the drop-down menu:

Once you click on **Add to Questions**, you can then make changes in **Settings** as you like and click **Save & Next** to publish your quizzes.

*Pro Tip: If you’re handling multiple instructors or collaborators, Tutor LMS Pro’s multi-instructor feature will be highly beneficial.*
Under **Course Settings,** you can see the following options:
- **Maximum Students**: Set it to 0 if you do not want to put a limit on the number of students you want enrolled. Or specify a number, after which Tutor LMS will now allow additional students to enroll.
- **Difficulty Level**: You select the difficulty level of each course from **All Levels**, **Beginner**, **Intermediate**, or **Expert**.
- **Public Course:** When someone signs up on your website, you can either make this course public for them to enroll or keep it private with a manual enrollment option.
- **Q&A:** You can enable the questions and answers feature to allow your students to contact you or your instructors.
- **Content Drip**: This is an LMS Pro addon, which comes with a yearly $199 fee. It allows you to publish content based on a set of criteria, such as dates or prerequisites of lesson completion.

A fully-fledged course with all the bells and whistles will look like this. You can see how everything is neatly structured. The following screenshot is of a live website that teaches language content. It has lessons and quizzes that are clearly structured.

### Step 5: Optimize Media and Content with Cloud Hosting
As an LMS creator, you’ll likely upload videos, documents, and quizzes, which can consume a lot of storage and bandwidth. Levamo allows you to store large media files without compromising your site’s speed.
- **Use your website storage**: Upload videos directly onto your LMS website and make them private, accessible only to your paid students. Here, one of the lessons has an audio file directly embedded on the hosting server.
### Step 6: Set Up Payment Gateways
If you’re monetizing your courses, setting up a secure, efficient payment process is essential. Tutor LMS integrates with popular gateways like PayPal, Stripe, and WooCommerce.
- **Configure payment settings**: Go to **Tutor LMS > Settings > Monetization**, and choose your preferred gateway.

Many [online education platforms](/blog/kc360-customer-stories/) rely on Tutor LMS and Levamo to deliver a seamless learning experience. By embedding multimedia content on the website, you can also provide students with uninterrupted access to resources, even during high bandwidth consumption.
- You can also set up email configurations, but before doing that, make sure you let our team know to set up a webmail server so that your emails can go through. The email setting is one of the most powerful options for LMS, as every time a new student is enrolled, completes a quiz, and submits an assignment, the instructors and the students both get email notifications.

### Step 7: Tutor LMS Import/Export Plugin
But what if you already have your course content created in another LMS? Would you manually update Tutor LMS with all the course materials? No. The best solution is to install the LMS Migration Plugin that allows you to easily migrate all course content from any other WP-based LMS to Tutor LMS.

### Step 8: Test and Launch
With everything set up, it’s time to test your LMS website before the official launch.
- First, let’s look at how your students can log in and see their dashboards. On the left side, your students can view profile options, the courses they have enrolled in, reviews, quiz attempts, settings, and calendar. On the right side, they get detailed options.

- Click on the **Enrolled courses,** and the students can see the courses that they have enrolled in. Once they click that course link, they will be taken to a new page as shown below:

## Free vs. Pro LMS Comparison
To know more about the free vs. Pro versions, have a look at the following comparison below:

## Important Tips:
- **Regularly update plugins**: Keep Tutor LMS and all other plugins updated for security and performance enhancements. With Levamo, leave that to us. We’ll automatically update your theme and plugins.
- **Monitor traffic and resource usage**: Levamo provides analytics to help you track and manage server resources. Should there be an anomaly, our team will handle it.
## Conclusion
Building a high-quality LMS website with Tutor LMS demands dedication, but the results are truly rewarding. With Tutor LMS’s robust features combined with [Levamo’s optimized](/managed-lms-hosting/), high-performance infrastructure, you can focus on what truly matters - creating impactful courses and driving revenue. Let us handle the technical challenges, so you can bring your educational vision to life smoothly and confidently. Whether you're an educator, entrepreneur, or institution, Levamo is the ideal partner for launching a scalable, efficient LMS that captivates learners and fuels growth. Ready to take the leap and launch your own online courses?
---
## How to Handle Sales Season Traffic with Auto-scaling Servers
- URL: https://levamo.com/blog/how-to-handle-sales-season-traffic-with-auto-scaling-servers/
- Category: hosting
- Author: Faisal Sarker
- Published: 2024-11-04
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Scale servers automatically & ace sales season traffic. Read how!
The holiday sales season is here, and your marketing budget has played its part. But what if your website can’t keep up with the incoming traffic?
Yep! **Slowdowns. Crashes. Lost customers**.
Your hosting now forces you to upgrade or you lose customers. Not the ideal scenario to face when you’re busy on the business front.
But here’s the good news: there’s a smarter way to avoid all that hassle.
Enter **Auto scaling servers**!
Intrigued?
Let’s dive deep into why you need hosting with auto-scaling servers for the holiday season to tackle all the extra surge in traffic and ensure not a single customer leaves frustrated!
## Key Takeaways
- How holiday traffic spikes can lead to website slowdowns or crashes.
- Auto-scaling can help tackle the traffic surge.
- The behind-the-scenes look at how auto-scaling servers adjust resources.
- Auto-scaling’s impacts on customer satisfaction and conversions.
## Auto-scaling to Handle Traffic Surges
Auto-scaling is the process in which your server infrastructure adjusts the allocation of resources dynamically based on real-time traffic demand.

So when the holiday season hits the peak and traffic grows beyond your regular server capacity, auto-scaling servers will dynamically boost capacity to make sure that your website doesn’t go down.
Let’s give you a more detailed look at how auto-scaling works.
### Example Typical Server Resource Usage
Suppose, under normal conditions, your website might run efficiently on a server setup with:
- **4GB of RAM**: Adequate for handling your daily visitor traffic.
- **2 CPU cores**: Sufficient for processing user requests and site functionalities.
- **10Mbps bandwidth**: Enough to serve your website content to users without delays.
### How The Traffic Surge is Handled
During a holiday sale or a promotional event, traffic to your website can increase significantly, potentially overwhelming your server's current capabilities.
The same thing happens outside the holidays, too. A single print-on-demand design going viral can send a flood of visitors to your store overnight, with no warning and no marketing spend behind it. That kind of unpredictable spike is exactly why a [print-on-demand marketplace](https://www.wcvendors.com/print-on-demand-marketplace/ "nofollow") needs infrastructure that scales on demand.
Here’s how auto-scaling responds to this challenge:
- **Increased Traffic Detection**: The system monitors traffic in real time. Upon detecting a spike, it triggers the scaling mechanisms.
**Resource Scaling**:
- **RAM Scaling**: From 4GB to 8GB or as much more as needed to handle more simultaneous user sessions and data interactions.
- **CPU Scaling**: From 2 cores to 4 cores or more, allowing for more concurrent processes and faster execution of user requests.
- **Bandwidth Scaling**: From 10Mbps to 20Mbps or even higher, ensuring that the increased data flow doesn’t bottleneck your server’s connection, thus maintaining smooth user experiences.
- **Predictive Scaling:** As of now, we have talked about auto-scaling as reactive to a certain situation. But in reality, auto-scaling can also be proactive. Using historical data, the system can predict and scale up resources before peak periods begin. What this can do is ensure that your website is prepared for the surge, just before the storm hits.
- **Easy Implementation:** Setting up auto-scaling is typically very easy. They involve enabling the feature in one click in most hosting services. Once you enable it, this feature automatically manages resource allocation. This lets you focus on running your business without worrying about server capacity.
## Key Benefits of Auto-scaling for eCommerce Sites

Now let’s take a look at the key benefits of auto-scaling servers on a hosting site and how it impacts your online business during the holiday season.
- **Maintaining Fast Loading Times During High Traffic**
One of the biggest challenges during traffic spikes is keeping load times fast. Slow websites can seriously hurt conversions. When shoppers are eager to grab deals during the holidays, just a few extra seconds of load time can mean the difference between making a sale and losing a customer.
With auto-scaling, servers can automatically allocate more resources as demand increases, ensuring that your site remains quick, regardless of how many people are browsing. The quicker your site loads, the more likely a customer is to complete their purchase.
- **Ensuring that the Site Doesn’t Go Down Even Under Heavy Traffic**
While slow-loading can hamper the user experience, a site that is down is the worst thing that can happen to your website. Because customers are no longer able to access your site.
Auto-scaling ensures that your site always has the resources and bandwidth you need to cope with increasing demand, so it never shuts off. And you know what more uptime means during the holiday season, more sales,
- **Seamless Customer Experiences**
Overall, auto-scaling ensures a seamless customer experience. No hurdle in browsing the website, checking out the offers, taking the orders to the cart, or ordering them.
## Levamo's “Performance Boost” Feature: A Game-Changer

Auto-scaling is great, but can you get that on affordable WordPress hosting? Well, you can. Whether you take the lowest plan or the highest one from Levamo, you can enjoy the Levamo’s version of auto-scaling, which we call “**Performance Boost**”.
You can just enable a performance boost before a campaign or the holiday offer begins. And you only pay for the extra resource that you use at that time, not year-round!
Levamo is here to support you so that your holiday season campaign goes just the way you planned, without breaking the bank.
That’s how [The Happy Pear](/blog/the-happy-pear-customer-stories/) saw a jaw-dropping **400% performance boost** and **40% cost reduction** for the Happy Pear.
[Try Levamo for Free](/)
## Conclusion
The holiday season comes with its own set of challenges. And none of them are bigger than the sudden traffic surges. Luckily, as I shared in this article, with auto-scaling hosting for holiday season traffic, you don’t have to worry about your site slowing down or crashing.
**[Levamo’s Performance Boost](/managed-wordpress-hosting/)** solution makes it easy to handle short-term traffic surges and makes it more cost-effective than ever. So invest in the right auto-scaling cloud servers and ensure that your website delivers a fast, seamless experience to your users. Even during the peak shopping days like [Black Friday, Cyber Monday](/blog/black-friday-hosting-preparation/), and beyond.
## Frequently Asked Questions

### What is auto-scaling in cloud hosting?
[Auto-scaling in cloud hosting](/blog/cloud-auto-scaling/) allows servers to adjust their resources as traffic demand changes. This helps websites cope with busy times such as the holiday season, without slowing down or crashing.
### What are the benefits of using auto-scaling for eCommerce websites?
Auto-scaling offers a cost-effective scalability solution, making sure that websites load without delay and keep running just as well during busy times. It helps online business websites stay fast and deal with high traffic times easily.
### How can auto-scaling servers help during holiday season traffic surges?
When holiday traffic spikes, auto-scaling servers boost their capacity to handle more visitors. This keeps load times quick and stops sites from crashing, giving customers a hassle-free shopping experience.
### How does Levamo’s Performance Boost feature work for traffic spikes?
Levamo’s Performance Boost is a feature that allows eCommerce sites to temporarily increase their server capacity during traffic spikes, such as during holiday sales. It offers real-time scalability without requiring a permanent server upgrade, making it a flexible and cost-effective solution.
### Do I need to upgrade my hosting plan to handle holiday traffic?
Auto-scaling hosting can help you avoid upgrading your hosting plan for short-term traffic increases. This feature lets you increase capacity for short periods without spending on pricey upgrades you'd pay for all year.
---
## Enhanced Security Insights: New Patchstack Dashboard
- URL: https://levamo.com/blog/enhanced-security-insights-new-patchstack-dashboard/
- Category: news
- Author: The Levamo Team
- Published: 2024-11-04
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
View threats blocked and vulnerable software directly from your dashboard.
## What's New?
You can now access detailed Patchstack insights directly from your dashboard. The new Patchstack dashboard shows an overview of threats blocked and highlights any vulnerable or outdated software, including plugins, themes, PHP, and WordPress versions.
## How It Works
Clicking **"Open Patchstack"** in the Security section opens a new tab, providing a full breakdown of your site's security status. At a glance, you'll see vulnerable software, outdated components, and recent threats blocked. The software table also includes component details such as name, type, version, and security status. You can even update individual components directly from this view for streamlined management.
This improved security feature will help you stay ahead of threats and provide you with the peace of mind knowing that your site is safe with Levamo.
You can learn more about Patchstack on Levamo in [our knowledge base guide](https://support.levamo.com/en/articles/8999895-security-features-on-the-rapyd-dashbord#h_6be5dd471c).
---
## Best Web Hosting Practices to Prepare for Black Friday/Cyber Monday Traffic
- URL: https://levamo.com/blog/black-friday-hosting-preparation/
- Category: hosting
- Author: Faisal Sarker
- Published: 2024-10-28
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
BFCM traffic spikes? Prep your web hosting now for peak performance.
A 1-second delay in page load time can result in a 7% drop in conversions.
During the all-important Black Friday/Cyber Monday period, the impact can be even deadly. You might have the best deals, but if your website can’t handle the surge in traffic and slows down, you’ll lose those precious sales that your business deserves.
The same shouldn’t happen to your business.
Hence, I’ve put together this article to help you with your Black Friday hosting preparation, so you don’t face the same website slowdowns, server crashes, and eventual loss of sales that most unprepared businesses face during the Black Friday traffic surge.
So without further ado, let’s get started!
## Key Takeaways
- A slow website during Black Friday can lead to lost sales.
- How to optimize speed and scalability to handle traffic surges.
- How using caching tools like Object Cache Pro and a CDN for faster content delivery.
- How to implement dynamic scaling to prevent crashes during peak traffic times.
- Why and how to prioritize security during peak-sales period.
- Scheduling frequent backups during Black Friday and monitoring your site 24/7.
- Collaborating with your hosting provider to ensure best Black Friday preparation.
## Understanding the Impact of Black Friday Traffic Surges
Black Friday drives a massive surge in online traffic. With major e-commerce giants such as Amazon and Walmart attracting millions of visitors, smaller businesses often face the challenge of balancing heavy traffic loads without the same infrastructure.
Black Friday Sales Compared to Average October Day Sales in 2023
Statistics show that in 2023, e-commerce sites saw almost **[2x traffic during Black Friday](https://queue-it.com/blog/2023-online-holiday-shopping-statistics/#6-black-friday-sees-traffic-almost-2x-that-of-average-october-day:~:text=5.%20Black%20Friday%20remains%20biggest%20day%20despite%20early%20access%20surge)** compared to an average October day. While this surge is excellent for sales, it’s a disaster waiting to happen for unprepared websites.
So how do you avoid such a disaster? Following the best hosting practices mentioned in the next section of this article. 👇
## Best Hosting Practices for Peak Traffic
Now let’s take a look at the best hosting practices to handle peak Black Friday traffic.
### 1. Optimize Website Speed for Black Friday
Website speed is critical for converting visitors into customers during Black Friday. Here are the key steps to optimize your site for peak traffic.
- **Implement Caching Tools Like Object Cache Pro**
Object Cache Pro
Caching stores frequently requested data in a way that reduces the load on your server. [Object Cache Pro](https://objectcache.pro/) is a perfect tool to speed up database queries and ensure faster load times.
It is available as a paid plugin, that you can use to improve the performance of your web stores dramatically.
- **Use a CDN for Faster Global Content Delivery**
A **Content Delivery Network (CDN)** reduces the distance between your server and your users, ensuring faster content delivery.
- **Benefits**: A CDN can reduce load times by serving cached versions of your site from servers around the world.
- **Best CDN Options**: Consider using **[Cloudflare](https://www.cloudflare.com/application-services/products/cdn/)** for robust global coverage and protection. Or choose a hosting provider that takes care of that for you.
- **Compress Content and Optimize Media**
Large image files and uncompressed content can severely slow down your site.
You can use a plugin like [WP Rocket](https://wp-rocket.me/) to reduce the size of your CSS, HTML, and JavaScript files.
WP Rocket
You can also optimize images to further speed up your website. You can do that by using formats like **WebP** and ensuring that images are properly compressed. If your uploaded images are not already WebP, you can still use plugins like **[Imagify](https://imagify.io/)** to convert and optimize them automatically after uploading.
### 2. Scale Resources Dynamically to Prevent Site Crashes on Black Friday
When traffic surges, your hosting needs to scale accordingly. That’s where [auto-scaling](/blog/how-to-handle-sales-season-traffic-with-auto-scaling-servers/) comes into action. Auto-scaling allows your website to automatically adjust server resources based on demand. During a traffic spike, the system will allocate more resources to maintain performance.
**How to Integrate Auto-Scaling**:
- Check if your hosting provider offers **auto-scaling. Very few cloud hosting providers offer this feature (like Levamo). So choose a hosting provider that offers this feature**.
- Test auto-scaling under simulated traffic conditions to ensure seamless operation during Black Friday.
If you’re running on shared hosting or an entry-level VPS, consider upgrading to a higher-tier plan for Black Friday. Or move to a [cloud hosting provider that offers dynamic auto-scaling](/) features.
### 3. Implement Robust Security Measures
The surge in Black Friday traffic also increases the risk of cyberattacks. Robust security is vital to protecting your business.
- **Advanced DDoS Protection**
A **[Distributed Denial of Service (DDoS)](/blog/preventing-ddos-attacks/)** attack can bring down your site by overwhelming it with malicious traffic. To deal with such malicious attacks, you can:
- Implement **DNS protection** through your hosting provider.
- You can also use a third-party security service or plugin like **[Cloudflare](https://www.cloudflare.com/security/)** or **[Sucuri](https://wordpress.org/plugins/sucuri-scanner/)**.
DDoS Protection
- **Update Plugins & Themes**
Outdated plugins and themes can leave your site vulnerable to security threats. They often miss the critical security patches or updates needed to keep your website secured, and out of harms way.
- Regularly update your plugins and themes to ensure that your site is secure and running efficiently.
- Choose a hosting provider that offers automatic theme and plugin updates along with security checks before the update.
- Turn on the automatic update feature from WordPress.
- **Secure Payment Gateways**
Ensure your payment gateways are secure and reliable to maintain customer trust.
- Make sure your payment system complies with **PCI DSS** standards to protect sensitive information.
- Implement 3D Secure 2.
- Enable multi or Two-Factor authentication.
### 4. Ensure Frequent Backups and 24/7 Monitoring
**Fleet Monitoring Traffic**
- **Importance of Regular Backups**
If something goes wrong, you need a quick way to restore your website. That is especially true during the Black Friday sale, as you don’t want your site to be out of order for long even if something goes wrong.
- Schedule automated backups to occur daily, especially in the lead-up to Black Friday.
- Make sure your hosting offers cloud-based solutions to store backups offsite, ensuring they’re safe from server issues.
- **Monitoring Tools and Services**
Real-time monitoring will help you identify and resolve issues immediately, even if any downtime occurs.
- Use services like **[Pingdom](https://www.pingdom.com/)**, **[New Relic](https://newrelic.com/)**, or your hosting provider’s built-in monitoring tools.
Pingdom Website Monitoring Tool
- Set up **alerts** for any critical issues such as high server load or security breaches.
### 5. Collaborate with Your Hosting Provider
Working with your hosting provider is essential for successful Black Friday hosting preparation.
- **Pro Tip**: Send a detailed email to your provider outlining expected traffic spikes, so they can allocate resources as needed.*
- **Get Support for Scaling Resources**
Your provider likely offers consultative support to help you scale server resources effectively. Some hosting providers will offer customized solutions if you communicate your needs well in advance.
Fleet Providing Support
- **Choose a Hosting with Auto-Scaling**
With top cloud hosting like [Levamo](/), you don’t even need to contact support, as your website will automatically be allocated more resources as demand grows. Levamo features like **Dynamic Performance Boost** for auto-scaling ensure your website remains as fast and smooth during peak traffic times as it is during regular days.
### 6. Load Testing and Stress Testing
Testing your site’s performance is crucial before Black Friday. Let’s take a look at how you can do that.
#### Simulate Peak Traffic
Use load-testing tools like **[K6.io](http://k6.io)** or **[Blazemeter](https://www.blazemeter.com/)** to simulate high-traffic conditions on your site.
K6 Load Test
After testing, use the results to fix any performance bottlenecks.
- Common issues that can happen include database overload, poorly optimized media, and slow third-party scripts.
## Additional Tips for Black Friday Hosting Preparation
Now let’s take a look at some additional tips to prepare for the Black Friday sale even better.
- **Optimize Database Performance**
Clean up your database by removing old entries and indexing tables for faster access. Use plugins like **[WP-Optimize](https://wordpress.org/plugins/wp-optimize/)** to handle this.
- **Ensure Mobile Responsiveness**
Ensure your site is optimized for mobile users, as mobile traffic spikes during Black Friday. Use tools like **[Bing’s Mobile-Friendly Test](https://www.bing.com/webmaster/tools/mobile-friendliness)** to judge the mobile-friendliness of your website.
Microsoft Bing Mobile Friendliness Test Tool
- **Prepare Customer Support for Increased Volume**
Black Friday can increase the number of queries on your website significantly. Scale your support team for this time, or integrate chatbots to handle a large number of customer inquiries.
## Levamo Hosting: Your Best Bet to Handle Peak Traffic
Levamo vs Regular Hosting Provider
If you’re looking for a hosting provider that’s built for peak performance, look no further than Levamo Hosting. It offers the most bleeding-edge technology to ensure your website stays up and running smoothly not just at regular times but also during peak traffic times.
It offers:
- **Performance Optimization**: Ensuring server-level caching with **LiteSpeed** and **Redis Cache** ensures fast load times.
- **Dynamic Resource Scaling**: To get on-demand performance boosts without costly long-term upgrades.
- **Robust Security**: To enjoy advanced DDoS protection and proactive security measures.
- **Automated Backups and 24/7 Monitoring**: So you can stay online with regular backups and real-time monitoring.
Levamo is powering thousands of resource-heavy websites and has already proven to be the perfect hosting for demanding websites.
Just take a look at how Michal P describes how [Droga Odważnych](/blog/droga-odwaznych-customer-stories/) has achieved a stunning soar in page speed using Levamo!
**[Try Levamo for Free](https://my.levamo.com/free-trial)**
## Conclusion
It goes without saying that if your site crashes or slows down on Black Friday, you lose a lot of sales. But with the right hosting preparation, you can avoid those risks entirely.
In this article, I’ve outlined the essential steps to optimize your site for speed, scalability, and security, but none of that matters if your hosting provider can’t handle the traffic.
That’s where **Levamo Hosting** comes in. With advanced caching, DDoS protection, and dynamic scaling, Levamo ensures your site stays fast, secure, and online during the busiest times. Automated backups and real-time monitoring give you peace of mind, so you can focus on maximizing sales without worrying about downtime.
Don’t leave your Black Friday success to chance. **[Try Levamo Hosting](/)** today and ensure your website is ready to handle the busiest shopping day of the year with confidence.
## Frequently Asked Questions

### When should you start preparing for Black Friday?
It's best to start preparing at least two months before Black Friday to give yourself ample time for testing, optimizing, and upgrading your hosting setup. Early preparation helps avoid last-minute issues that could impact your site's performance.
### How do I get my business ready for Black Friday?
To get ready, optimize your website for speed, security, and scalability while planning your marketing strategy in advance. Make sure your customer support is prepared to handle increased inquiries and sales traffic.
### How do you attract customers on Black Friday?
Use email marketing, social media campaigns, and paid ads to build excitement and promote your deals. Offering limited-time discounts and exclusive promotions can help create urgency and drive more traffic to your site.
### When should I start promoting Black Friday?
Start promoting your deals in early November to build anticipation and ensure your audience is aware of your offers. Gradual teasers and early access deals can help boost engagement before the big day.
### How to sell more on Black Friday?
To increase sales, create irresistible offers like bundled deals or tiered discounts, and ensure a seamless shopping experience. Fast checkout and secure payment options will help maximize conversions during peak traffic.
### How do you retain customers after Black Friday?
Follow up with post-purchase emails and exclusive discounts to encourage repeat business. Offering loyalty programs or special promotions can help turn one-time buyers into long-term customers.
---
## More Security, More Control: Add Extra Backup Storage to Your Plan
- URL: https://levamo.com/blog/more-security-more-control-add-extra-backup-storage-to-your/
- Category: news
- Author: The Levamo Team
- Published: 2024-10-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Expand your backup storage in 100GB increments for just $3 per month.
We're excited to introduce a new feature that lets you expand your backup storage, giving you more control over how you manage your site's data.
## What's New?
You can now increase your backup storage in 100GB increments, making it easier to ensure your site is always backed up without worrying about running out of space. Each block of 100GB has a price of just $3 per month.
## How It Works
You can quickly select the amount of additional backup storage you need from the **Edit plan** option in the **Billing** area of the dashboard. The total cost, prorated to your next billing date (whether monthly or yearly), will be displayed before confirming your choice.
You can always see how much you're paying for extras like backup storage in the Extras section of your billing page.
For more details on adding backup storage, check out our [knowledge base](https://support.levamo.com).
---
## The Big Reveal: 2026’s Best Managed WordPress Hosts Ranked
- URL: https://levamo.com/blog/best-managed-wordpress-hosts-2025/
- Category: website-performance
- Author: Tom Cheddadi
- Published: 2024-10-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See 2026's top managed WordPress hosts ranked! Find your perfect provider.
In the ever-evolving landscape of web hosting, the choice of a WordPress hosting provider can significantly impact a website's success.
As we step into 2026, the demands on hosting infrastructure have never been greater, especially for dynamic WordPress sites that require robust performance to deliver seamless user experiences.
The 2026 Managed Hosting for WordPress Performance Industry Report offers an unprecedented, data-driven analysis of leading hosting providers, with a laser focus on their ability to handle the complexities of modern, dynamic WordPress installations.
## Executive Summary: The Heartbeat of Our Findings
The report begins with a comprehensive executive summary, distilling months of rigorous testing and analysis into key insights that web professionals and business owners need to know. This section provides a bird's-eye view of the hosting landscape, highlighting standout performers and identifying [web hosting trends](/blog/web-hosting-trends/) that are shaping the industry.
Our executive summary reveals significant variations in performance across providers, with some excelling in handling high-concurrency scenarios while others shine in database operations or static content delivery. We've uncovered that the top performers consistently deliver sub-second response times even under heavy loads, a crucial factor for user experience and search engine rankings.
## What is a Dynamic WordPress Site?
Before diving into the technical details, it's crucial to understand what we mean by a "dynamic WordPress site." This section of the report defines and explores the characteristics that set dynamic sites apart from their static counterparts.
Dynamic WordPress sites go beyond simple blogs or brochure-style websites. They often include e-commerce functionality, membership areas, learning management systems, or complex custom applications built on top of WordPress. These sites typically:
- Rely heavily on database queries to generate personalized content
- Utilize advanced caching mechanisms to maintain performance
- Employ numerous plugins and custom code to extend functionality
- Handle frequent content updates and user-generated content
- Manage concurrent users and sessions
Understanding these characteristics is crucial because they directly impact hosting requirements. A host that performs well for a static site might crumble under the demands of a dynamic WordPress installation.
Also Read: [Managed Hosting for BuddyPress](/blog/buddypress-review/)
## Detailed Methodology: The Foundation of Credibility
Our methodology section is the bedrock of the report's credibility. We believe in full transparency, allowing readers to understand exactly how we arrived at our conclusions. This section is broken down into several key areas:
### Website Demos and Configurations
We created a diverse array of website demos to simulate real-world scenarios. These ranged from:
- Basic WordPress installations with minimal plugins
- E-commerce setups using [WooCommerce](https://wordpress.org/plugins/woocommerce/) with varying product counts
- Membership sites utilizing [BuddyPress review](/blog/buddypress-review/) or [MemberPress review](/blog/memberpress-review/) thrive with optimized hosting.** [MemberPress hosting](/memberpress-hosting/)**ensures fast performance for managing subscriptions and gated content, while **[BuddyPress hosting](/buddypress-hosting/)**supports interactive communities with scalable speed and security. Reliable hosting is key to an exceptional user experience.
- Learning Management System (LMS) configurations with [LearnDash](https://www.learndash.com/) or [LifterLMS](https://lifterlms.com/)
- High-traffic news or media sites with frequent content updates
Each configuration was meticulously documented, including the exact plugin list, theme, and content volume. This approach ensures that our tests cover the spectrum of WordPress use cases, from simple to highly complex.
### Hosting Plan Selection and Price Brackets
To ensure fair comparisons across different providers, we categorized hosting plans into eight distinct price brackets:
- Level 1: $25 to $74 - Entry-level plans
- Level 2: $75 to $149 - Advanced entry-level and small business plans
- Level 3: $150 to $299 - Mid-range plans for growing websites
- Level 4: $300 to $399 - High-performance plans for established sites
- Level 5: $400 to $499 - Premium plans for high-traffic websites
- Level 6: $500 to $999 - Enterprise-grade solutions
- Level 7: $1,000 to $1,499 - Advanced enterprise solutions
- Level 8: $1,499 to $2,000 - Top-tier, fully managed enterprise hosting
This bracketing allows for apples-to-apples comparisons, ensuring that we're evaluating plans with similar resource allocations and price points across different providers.
### Selection Criteria for WordPress Hosting Providers
Our report focuses on well-established [fully managed WordPress hosting](/managed-wordpress-hosting/) providers known for their performance and reliability. The selection includes:
- Levamo
- WP Engine
- Kinsta ([Kinsta Alternative](/kinsta-alternative/))
- Rocket.net
- Pressable
- Pagely
- Cloudways AWS
- Cloudways DigitalOcean
Each provider was chosen based on market presence, reputation, and the unique technologies they bring to the table. We explain our rationale for including each host, highlighting their specialties and target markets.
### Testing Environments
For each provider, we detail the specific plans tested, including:
- Plan names and pricing
- Server locations (where this information is available)
- Resource allocations (CPU, RAM, storage)
- Any special features included in each plan
This granular level of detail allows readers to understand exactly what they're getting at each price point and how it compares across providers.
### Third-Party Testing Plugins and Tools
To ensure objectivity and reproducibility, we relied on industry-standard testing tools. This section of the report details each tool used and explains how it contributes to our overall analysis:
#### A. WordPress Hosting Benchmark Tool Plugin
[WordPress Hosting Benchmark Tool](https://wordpress.org/plugins/wpbenchmark/) allows us to measure:
- PHP execution speed
- MySQL query performance
- Filesystem operations
- Server response times under various conditions
We explain how each metric is calculated and what it means for real-world performance.
#### B. WPPerformanceTester Plugin
The [WPPerformanceTester](https://wordpress.org/plugins/wpperformancetester/) plugin stress-tests the hosting environment by:
- Performing complex mathematical operations
- Executing string manipulation tasks
- Running intensive loop and conditional statement tests
- Conducting database insertion and query tests
Our report breaks down how these tests correlate to everyday WordPress operations and why they matter for dynamic sites.
#### C. K6 Tool
[K6](https://k6.io/) is our chosen solution for advanced load testing. This section of the report is particularly detailed, covering:
##### TESTING OVERVIEW
We explain the K6 script used for testing, which simulates increasing user loads over a set period. This script is designed to push hosting environments to their limits, revealing how they handle traffic spikes and sustained high loads.
##### CONCURRENCY
Understanding concurrency is crucial for dynamic WordPress sites. We delve into how we measure true concurrency versus what we term "platform concurrency," accounting for the complex nature of modern WordPress setups with multiple AJAX calls and background processes.
##### READING THE TESTS
This subsection provides a guide on interpreting the K6 test results, including:
- How to understand the graphs produced
- What different metrics (like request rate and error percentage) mean in practical terms
- How to identify the point at which a hosting environment begins to struggle
##### METRICS COMPARISONS
We compare the K6 results across different hosts, highlighting:
- Maximum sustained request rates
- Error onset points
- Recovery capabilities after high-stress periods
## Server and Software Analysis
The underlying technology stack of a hosting provider plays a crucial role in its performance. Our analysis covers:
### Web Server Software
We compare the pros and cons of different web server software used by hosts, including:
- [Apache](https://httpd.apache.org/)
- [Nginx](https://nginx.org/en/)
- [LiteSpeed](https://www.litespeedtech.com/)
- [OpenLiteSpeed](https://openlitespeed.org/)
### PHP Versions and Configurations
This section examines:
- The PHP versions offered by each host
- Custom PHP configurations and their impact on performance
- PHP-FPM vs. other PHP handlers
CPU Specifications We detail the CPU models and specifications used by each host, explaining how differences in CPU architecture can affect WordPress performance.
### OPcache and Object Cache Technologies
Our analysis covers:
- The implementation of OPcache across different hosts
- Object caching solutions (like Redis or Memcached) and their configurations
- The impact of these caching technologies on dynamic WordPress sites
### Database Software and Versions
We examine:
- [MySQL](https://www.mysql.com/) vs. [MariaDB](https://mariadb.org/) implementations
- Database version differences and their performance implications
- Custom database optimizations offered by each host
## Analysis of Results
### Making Sense of the Data
This crucial section ties together all the data points collected, providing insights that go beyond raw numbers:
#### Emphasis on Dynamic WordPress Site Requirements
We interpret the results with a focus on how each host performs for dynamic sites, considering factors like:
- Ability to handle concurrent users
- Performance under heavy database loads
- Caching effectiveness for frequently changing content
#### Uniform Testing Across Hosts
We explain our approach to ensuring test consistency, including:
- How we accounted for geographical differences in server locations
- Methods for normalizing results across different hardware configurations
- Strategies for eliminating variables that could skew results
#### Analysis Methodology
This subsection details how we weighted different performance factors, explaining our rationale for prioritizing certain metrics over others based on their relevance to dynamic WordPress sites.
#### Interpretation of Results
Here, we provide a nuanced interpretation of the data, going beyond simple rankings to explain:
- Why certain hosts excel in specific scenarios
- How different architectural choices impact various performance metrics
- The trade-offs between performance, features, and pricing
#### Implications for Users
We translate our technical findings into practical advice for different user types, such as:
- E-commerce site owners
- Community or membership site managers
- High-traffic blog operators
- Enterprise WordPress users
### Transparency and Reproducibility
In the interest of scientific rigor, we provide:
- Detailed testing schedules
- Raw data sets for all tests conducted
- Instructions for replicating our testing environment
This level of transparency allows for peer review and ensures that our findings can be independently verified.
### Quality Control and Reporting
Our quality control measures include:
- Multiple test runs to account for variability
- Statistical analysis to identify and explain outliers
- Peer review process for interpreting results
We also detail our reporting methodology, explaining how we distilled vast amounts of data into actionable insights.
## Where Levamo Fits: Plans and Pricing
Levamo is one of the [fully managed WordPress hosting](/managed-wordpress-hosting/) providers built for the dynamic, high-concurrency sites this report focuses on. Every plan runs on LiteSpeed with an Enterprise Cloudflare CDN, automated backups, free migration, and 24/7 expert live chat. Here is where the current plans start:
| Plan | Built for | Starts at (billed annually) |
|---|---|---|
| Starter | Entrepreneurs and small business websites | $29/mo |
| Business | Stores, communities, and courses that need scalable performance | $99/mo |
| Performance | High-traffic dynamic websites and apps | $299/mo |
| Enterprise | Mission-critical sites needing dedicated resources and priority support | $649/mo |
Each tier scales up through multiple levels as your traffic and resource needs grow. For the full breakdown, monthly pricing, and everything included at each level, see the [Levamo pricing page](/pricing/).
## Conclusion
The 2026 Managed Hosting for WordPress Performance report is more than just a comparison of hosting providers; it's a deep dive into the state of WordPress hosting technology. By thoroughly examining each aspect of hosting performance, from server software to database efficiency, we provide a comprehensive resource for anyone looking to make an informed decision about WordPress hosting.
Whether you're a small business owner looking for a [managed WooCommerce hosting](/managed-woocommerce-hosting/), a developer managing multiple client websites, or an enterprise-level organization running complex WordPress applications, this report offers the insights you need to choose the right hosting solution for your specific needs.
Hosting is only one line in the budget, though. If you’re pricing out a marketplace specifically, it pays to map every recurring cost - hosting, plugins, payment fees, and vendor payouts. Before you commit to a platform, know first the [cost of running a WooCommerce marketplace](https://www.wcvendors.com/cost-of-running-woocommerce-marketplace/ "nofollow").
As we move further into 2026 and beyond, the demands on WordPress hosting will only increase. Dynamic content, real-time interactions, and complex integrations are becoming the norm rather than the exception. By understanding the nuances of hosting performance outlined in this report, you'll be well-equipped to make a choice that not only meets your current needs but also positions you for future growth and success in the digital landscape.
---
## Enhanced Control and Improved Invitations for Your Team
- URL: https://levamo.com/blog/enhanced-control-and-improved-invitations-for-your-team/
- Category: news
- Author: The Levamo Team
- Published: 2024-10-03
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
New team permissions and a streamlined invitation flow for your dashboard.
New features have been introduced to provide greater control over team permissions and streamline the invitation process for the Levamo dashboard.
## What's New?
### Domain Management Permissions
Team members can now have access to domain management granted or revoked. This permission adds flexibility to controlling access to sensitive settings. The permission can be assigned when inviting new team members or modified later through the Teams section of the dashboard.
### Improved Invitation Flow
The invitation process includes an added confirmation step for better clarity and control. Before sending an invitation, users see a summary displaying the recipient and their assigned permissions. This step prevents access management mistakes.
## Learn More
For additional information about Teams functionality, refer to these resources:
- **Team Roles & Permissions**: Understand the available roles and what each can access
- **Navigating the Team Section**: Learn how to manage your team from the Levamo Dashboard
---
## Simplify Your Login with Google Sign In
- URL: https://levamo.com/blog/simplify-your-login-with-google-sign-in/
- Category: news
- Author: The Levamo Team
- Published: 2024-10-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Log in to your Levamo dashboard faster using your Google account.
We're excited to introduce **Sign in with Google**, making it even easier for you to access your Levamo dashboard.
- You can now log in using your Google email address, saving you time and reducing the need to remember extra login credentials.
- Simply click the **Sign in with Google** button on [the login page](https://my.levamo.com).
- For first-time users, you'll just need to complete a quick authentication step to grant permission to [levamo.com](/).
**What this means for you**: Faster, hassle-free logins and seamless access to your dashboard. By using your Google account, you enhance security and simplify the sign-in process, letting you focus more on what matters.
---
## More Space, More Flexibility: Add Local SSD Storage to Your Plan
- URL: https://levamo.com/blog/more-space-more-flexibility-add-local-ssd-storage-to-your/
- Category: news
- Author: The Levamo Team
- Published: 2024-09-21
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Expand your local SSD storage in 50GB increments as your sites grow.
Levamo has introduced the ability to expand local SSD storage in 50GB increments, providing scaling flexibility as your sites grow.
## Key Features
- **Flexible SSD Storage**: Increase storage in 50GB blocks at USD $7 per month.
- **Easy to Add**: The edit plan modal displays total costs prorated to the next billing date before confirming changes.
- **Plan Upgrades**: When upgrading to higher-tier plans with more included storage, existing add-ons are automatically absorbed, eliminating additional charges.
- **Annual Plans**: For yearly subscriptions, storage add-ons are charged upfront and prorated accordingly.
## How It Works
1. Navigate to Billing > View subscription > Edit plan (pencil icon)
2. Under Local Storage, select desired additional space
3. Review total cost and confirm via "Change plan" button
4. Receive updated subscription receipt with prorated charges
## Important Notes
Storage cannot be removed while connected to a site but can be removed if the plan is empty.
For additional details, the knowledge base article on adding local storage is available.
---
## Introducing Our Status Page: Enhanced Transparency and Real-Time Updates
- URL: https://levamo.com/blog/introducing-our-status-page-enhanced-transparency-and-real-time-updates/
- Category: news
- Author: The Levamo Team
- Published: 2024-08-22
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Track real-time operational status of Levamo infrastructure and services.
Stay informed and in control with our new Status Page. This feature empowers you to track real-time updates on the operational status of our infrastructure, including hosting services and the user dashboard.
You can access our status page here: [status.levamo.com](https://status.levamo.com/)
## How It Works
You can also always access the status page either from the Levamo dashboard or from our homepage.
- **Dashboard**: Click **Get help** in the main nav
- **Homepage**: In the **Resources** menu item, then Product > System Status
On the status page you'll see real-time status of:
- The User Dashboard
- Levamo Infrastructure
- Hosting Services for each region (DNS resolvers and cluster server)
With our new status page, you'll be able to stay on top of any critical infrastructure issues and act accordingly.
---
## Your WooCommerce Store Just Got Faster: Introducing Elasticsearch and Litespeed Cache Enhancements
- URL: https://levamo.com/blog/your-woocommerce-store-just-got-faster-introducing-elasticsearch-and-litespeed/
- Category: news
- Author: The Levamo Team
- Published: 2024-06-21
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Major WooCommerce performance upgrades with Elasticsearch and LiteSpeed Cache.
We've made some major performance enhancements to WooCommerce, making your online store faster and more efficient for both you and your customers.
## What's New?
We've supercharged WooCommerce performance on the Levamo platform through two key enhancements:
- **Elasticsearch Integration**: By integrating the ElasticPress plugin and a local Elasticsearch server, we've dramatically improved the speed and efficiency of your product searches. This means your customers can find what they're looking for faster, resulting in a smoother shopping experience.
- **LiteSpeed Cache for WooCommerce**: This advanced caching solution, featuring "smart purge" technology, ensures that your cache remains up-to-date, keeping your pages loading incredibly quickly. Additionally, Live Cart provides each customer with a dedicated private cart cache using LiteSpeed Edge Side Includes (ESIs), which means each user's cart is stored in their own private cache for an exceptionally smooth shopping experience.
## How It Works
These new features can be managed from the WooCommerce tab in the site management area, which is visible for any site that has WooCommerce installed.
- **New WooCommerce Sites**: These enhancements are automatically enabled for new WooCommerce installations. Simply check the "Add WooCommerce to this site" checkbox during the Add Site flow.
- **Existing WooCommerce Sites**: For sites that already have WooCommerce installed, you can activate these new features by navigating to the WooCommerce tab in your Levamo dashboard and turning them on.
**Important Note**: These performance enhancements are available for Developer plans and above. If you're on a Lite plan, we encourage you to consider upgrading to unlock the full potential of your online store.
## Learn More
For detailed instructions and additional information, please visit our knowledge base guide on Getting Started with WooCommerce on Levamo.
---
## File Management Just Got Easier: Introducing Duplicate & Move in Your Dashboard
- URL: https://levamo.com/blog/file-management-just-got-easier-introducing-duplicate-and-move-in/
- Category: news
- Author: The Levamo Team
- Published: 2024-06-10
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Duplicate and move files directly in your Levamo dashboard file manager.
We've made significant enhancements to the dashboard file manager designed to streamline your workflows and boost productivity.
## What's New?
### Duplicate Files and Folders
You can now quickly duplicate files right in the Levamo file manager. This feature accelerates troubleshooting without requiring FTP clients. Duplicated files receive a "-1" suffix appended to their names.
### Move Files and Folders
The file manager now enables moving files and folders throughout the file tree structure. This works especially well alongside the duplication feature, giving you full control over your site's file organization.
## How It Works
The file manager enhancement is located in the Settings section of the left-hand menu. To use these features:
1. Navigate to the file manager in Settings
2. Click the three-dot menu icon next to a file or directory name
3. Select either "Duplicate" or "Move" from the action menu
4. Complete your desired action
## Learn More
For additional details about using the file manager in the Levamo dashboard, consult the knowledge base guide: "Introduction to File Manager on the Levamo Dashboard" available at [support.levamo.com](https://support.levamo.com).
---
## How Veteran Hundo Club Went From 60-Second Lag to Lightning Speed
- URL: https://levamo.com/blog/veteran-hundo-club-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how Veteran Hundo Club achieved lightning speed with better hosting.
[Veteran Hundo Club](https://www.veteranhundoclub.com/) is a veteran social platform that struggled with **slow loading times** on its previous hosting plan. This also threatened the entire platform's viability. Levamo hosting's performance and seamless migration process saved the day for their business. Now, VHC boasts a **lightning-fast website** and **exceptional ongoing support.**
## Customer Introduction
Veteran Hundo Club is a veteran-owned organization that empowers veterans to thrive after service. Founded by Christopher K. Raymond, a highly respected advocate for veterans with a proven track record in both business and veteran affairs, VHC offers a comprehensive suite of services designed to meet the unique needs of this community.
VHC builds upon Mr. Raymond's expertise by offering a wide range of services, including VA claims coaching, business coaching, website development, and business development support. They also address legal issues and connect veterans with valuable Veteran Service Officers (VSOs).
## Problem
Due to the Veteran Hundo Club social platform's dynamic nature, its previous hosting provider plagued it with slow loading times. They were using NameHero’s Business Cloud solution, which could not cope with their website’s dynamic nature. This significantly impacted user experience and frustrated visitors.
“**The performance is exceptional for static websites and blogs without many moving parts, but with our use of our social platform, we could not find a working solution no matter how many plugins we tried or upgrading to higher packages such as enterprising or other,”** he added, “They just lacked the delicate need to provide for our dynamic social platform.”
These slow loading times hindered their ability to connect with veterans and deliver valuable services. Christopher further emphasized the seriousness of the issue, stating, ***"...People were saying our server was slow and just not functioning. They spend upwards of 45-60 seconds loading things on the page. It was horrible..."***
Even when they decided to migrate to a new hosting, they were not sure if it would actually solve the problem. ***“Our biggest doubt, of course, was how well the new server was going to perform. We had no way to actually see the difference compared to another service provider,”*** he shared.
## Solution
Veteran Hundo Club was already using BuddyBoss to power their community. Thus, they learned about Levamo hosting through promotional content from BuddyBoss. They were impressed by Levamo's commitment to performance and their user-friendly migration process.
***"We knew our previous provider just wasn't designed for a dynamic website with so many moving parts. They lacked the ability to address the specific needs of our social platform,"*** Christopher shared. So when they learned about [Levamo], they immediately got on board. ***“We choose to go with Performance Level 1 for [www.hundoclub.net](http://www.hundoclub.net/).”***
He also appreciated the migration service, saying, “We used the amazing migration service. No improvements to be found. Absolutely amazing. Nearly flawless experience."

## Results
The Veteran Hundo Club website migration to Levamo was a smooth and efficient process with minimal downtime.
***“In our first interaction of purchasing the new managed hosting we were astonished how they personalized our problems as literally their own,”*** Christopher shared.
As a result of migrating, VHC experienced a dramatic improvement in website performance. Christopher described the new server's speed as follows:

He also loves the support of the [Levamo] team, saying, ***“The continued support and fast turnaround time is also amazing. They take every single issue and break it down to the smallest detail to ensure our problems no longer exist.”***
He then went on to say, *“As it turns out, we are more than happy about their service.”*
## Conclusion
Veteran Hundo Club's sluggish website, which threatened their entire platform, is now a lightning-fast hub for veterans. This newfound speed and stability have allowed VHC to refocus its energy on its core mission: empowering veterans.
The founder of Christopher Raymond shared how vigilant and adaptive they were in keeping their program afloat. ***“We would have completely shut down our program because the server before going to [Levamo] was just not working no matter the package deal we went higher on.”***
He finished by praising [Levamo], ***"This is the type of service we can see our organization staying and becoming decades-long members of."***


###### Challenges
- 45-60 Seconds Load Time
- Couldn’t Handle High Traffic
- Consistently Sluggish Performance
- Steep Learning Curve
###### Outcome
- Dramatically Improved Speed
- Efficient Issue Resolution
- Ongoing Personalized Support
- Free Migration by Levamo

---
## Jaw-dropping 400% Performance Boost and 40% Cost Reduction for the Happy Pear
- URL: https://levamo.com/blog/the-happy-pear-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how The Happy Pear got a 400% performance boost and cut costs.
[The Happy Pear](https://thehappypear.ie/), a leading health and wellness company, struggled with **downtime and resource limitations** on their dedicated server. Levamo Hosting's reliable infrastructure and exceptional support solved these issues. Now, they offer **a seamless online experience** for their growing community at a lower cost.
## Customer Introduction
The Happy Pear, founded by twin brothers David and Steve Flynn, is a dynamic company that promotes health, happiness, and sustainability. Their multifaceted enterprise encompasses a thriving 4-acre organic farm, a bustling café, and a range of health-focused products. They've also cultivated a vibrant online community of over 2 million followers across social media platforms and newsletters. Furthermore, they have a dedicated BuddyBoss app with 4,000 to 12,000 members.
This online presence proved crucial for connecting with their audience and fostering a supportive community. However, maintaining a robust online platform became challenging. Their previous hosting solution, a dedicated server, struggled to handle the intense resource demands of their membership site. Frequent crashes disrupted their operations and frustrated their community members.
## Problem
"We were having lots of issues with our old server crashing under the intense resource requirements that a membership site demands," explained David Flynn, Founder & CEO of The Happy Pear. Their dedicated hosting server simply couldn't handle the demands of their growing online community.
David elaborated on the problems with the previous hosting, ***"We run a private dedicated server and even with that it was considered by them (the previous hosting) to be a lot of resources."***
The combination of downtime, resource limitations, and potential revenue loss made finding a more reliable and scalable hosting solution a top priority for The Happy Pear.
## Solution
The Happy Pear team uses BuddyBoss, so they immediately got interested when Levamo hosting was released from the same company.
***“It (the previous hosting) still couldn't handle the demand. You ([Levamo]) promised to solve our downtime and resource issues, simple as that.”***
Levamo's robust infrastructure eliminated downtime. It also provided the resources needed to support The Happy Pear's thriving online community.
At the same time, with [Levamo], the cost is also less than the previous hosting for the Happy Pear team. ***“Really our monthly costs with [Levamo] are 40% less than what we were paying with previous hosts,”*** shared David.

## Results
Since switching to Levamo Hosting, The Happy Pear has reaped great benefits.
[Levamo] provides significantly more resources than the previous hosting, which have boosted the website and app performance by up to 400%. David shared, ***“[Levamo] provides so much more resources for that lower price.”***

Apart from solving the performance issues, the Levamo support team has also been very helpful to David and the Happy Pear team.

By providing a reliable, scalable, and cost-effective hosting solution, Levamo Hosting has empowered The Happy Pear to connect with its audience on a deeper level and continue its mission of promoting health and happiness through its online community.
## Conclusion
The Happy Pear's recipe for success combines fresh ideas, a commitment to well-being, and a supportive online community. With Levamo Hosting as their trusted partner, they can continue to inspire and empower their audience on their journeys to healthier, happier lives.
***"It ([Levamo]) really really is good value,"*** David concludes. The reliable hosting, cost-effective plans, and exceptional support have allowed them to focus on what they do best - promoting health and happiness through their online community. With a secure and scalable platform, [Levamo] Hosting empowers The Happy Pear to connect with its audience on a more personal level.

###### Challenges
- **Server Couldn’t Handle Demand**
- **Regular Crashes During Peak Times**
- **High Costs for Insufficient Resources**
###### Outcome
- **400% Increase in Performance**
- **40% Reduction in Monthly Expenses**
- **Free Access to Security and Caching Tools**
- **Hands-on Support from Levamo's Team**

---
## How Bulletproof Musician Achieved 90% Faster Site Speed
- URL: https://levamo.com/blog/the-bulletproof-musician-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how Bulletproof Musician sped up their site by 90% with new hosting.
[The Bulletproof Musician](https://bulletproofmusician.com/), a platform that blends music performance with sports psychology, faced **frustratingly slow website performance** despite seemingly powerful hosting. Switching to Levamo hosting with less raw power on paper (but focusing on optimized performance) resulted in a **dramatic improvement**. Group activity feeds in their app went from a sluggish 20-30 seconds to load down to a snappy 2-3 seconds - a 90% reduction! This boost in speed translated to a happier and more engaged community of musicians.
## Customer Introduction
The Bulletproof Musician, founded by Dr. Noa Kageyama, is a unique platform that goes beyond simply teaching music. They combine traditional music instruction with the principles of sports psychology, empowering musicians to overcome performance anxiety and achieve peak onstage presence. The platform offers many resources, including online courses, articles, and a vibrant online community where musicians can connect and support each other.
## Problem
Despite their success in helping musicians unlock their full potential, The Bulletproof Musician faced a challenge - their website performance lagged behind. ***" I would often get complaints from community members about the slowness of the group activity feeds and forums,"*** says Noa.
Their previous hosting plan offered seemingly robust resources (8GB RAM/4-core CPU), but the reality was sluggish loading times. *“When clicking on a group’s activity feed in the app, it would typically take 20-30 seconds for any content to appear - no exaggeration,”* Noa Shared, *“even my sales pages were taking 5-7+ seconds to load, which was also concerning.”*
He tried every trick in the book to cut down the loading time. “**And this is even after using object caching and the WP Offload Media plugin to offload user-submitted videos and photos and serve these via a CDN,” shared Noa**.
Even when he started considering Levamo, he wasn’t sure it would be much better. Especially since it looked inferior on paper. “**But I wasn't sure how much faster they would load, especially when I was on a Levamo plan that, on paper, offered only half of the power/resources of my previous plan with my prior host,” said Noa**.
## Solution
While looking for a new hosting for the Bulletproof Musician, Noa discovered Levamo early as he is a BuddyBoss user. **“I started hearing rumblings about Levamo in the BuddyBoss Facebook group. But I also got emails as a BuddyBoss customer,”** he said.
It caught his attention, and he wanted to try it because of his positive experience with BuddyBoss. ***"I went with the Starter plan,"*** Noa shared. He also shared that he used the free migration service [Levamo] offers.

***"I was worried about signing up for a new service like [Levamo], which didn't have much of a track record,*** "Noa admits.
## Results
The switch to Levamo hosting brought about a dramatic improvement in the performance of the Bulletproof Musician.
For starters, the Group Activity Feed became much faster than before. ***“Group activity feeds in the app, the previous bottleneck taking 20-30 seconds to load. Now take only 2-3 seconds - a staggering 90% improvement,”*** Noa shared.

Website responsiveness also saw a significant boost. Pages across the entire site, from sales pages to course materials, now load significantly faster. Noa mentions, ***"Instead of waiting 3, 4, 5 seconds for each page to load on the WordPress backend, each page loaded in less than 2 seconds.”***
He further added, “And the same difference in speed was noticeable on the site’s front-end as well. With everything from sales pages and checkout pages and course pages and forums and group activity feed loading up so faster than I’d ever seen."

## Conclusion
Now, The Bulletproof Musician website performs at the level their community deserves. Gone are the days of sluggish loading times and frustrated users. With a lightning-fast experience, musicians can access resources, connect with peers, and focus on achieving peak performance.

The positive impact is clear - complaints have vanished, and Noa is excited about the future.
Noa concluded by praising [Levamo] and sharing, ***“I had never seen my site load so quickly,”***
With a seamless platform supporting their mission, The Bulletproof Musician is poised to empower even more musicians. So they can conquer performance anxiety and reach their full potential.

###### Challenges
- Slow Group Activity Feeds
- Slow Sales Pages
- Regular Member Complaint
- Persistent Performance Issues
###### Outcome
- 90% Faster Group Activity Feed
- Improved Overall Performance
- Zero Customer Complaints
- Free & Seamless Migration

---
## ‘Take Back Your Temple’ Cuts Page Loading Time by 94%
- URL: https://levamo.com/blog/take-back-your-temple-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how one site slashed loading time by 94% and saved money.
[Take Back Your Temple](https://takebackyourtemple.com/), a faith-based weight loss program with over 7,500 users, struggled with its previous slow and expensive hosting provider. After switching to Levamo hosting, they achieved **blazing-fast website speeds**, **significant cost savings**, and **exceptional customer support.** This led to a more positive user experience for their members.
## Customer Introduction
Kimberly Taylor's story is one of remarkable personal transformation and a deep commitment to helping others achieve the same. Once struggling with emotional eating and a size 22 frame, a profound experience at a Christian women's conference marked a turning point. Kimberly recognised that emotional wounds often lie at the root of weight struggles. So, Se dedicated herself to a program centred on seeking God's love and strength. This shift led to a remarkable weight loss of 85 pounds, dropping to a size 8, and a lasting commitment to maintaining a healthy lifestyle.
Driven by her success and a desire to empower others, Kimberly built a thriving online community around Take Back Your Temple. With over 7,500 members, the program has become a beacon of hope and support for those seeking sustainable weight loss through spiritual growth and practical tools.
## Problem
As Take Back Your Temple's online community flourished, exceeding 7,500 members, its website began to experience growing pains. Once sufficient, its previous hosting provider, Kinsta, needed help to keep up with the increasing traffic. This led to a critical challenge: slow website performance.
***“Our old hosting company couldn’t handle increased traffic because it was (already) struggling to keep up with our current traffic!”*** shared Kimberly Taylor, founder of Take Back Your Temple. "This resulted in sluggish loading times, particularly for our BuddyBoss community features, which are essential for fostering interaction and engagement among our members."
Beyond the performance issues, Take Back Your Temple also grappled with Kinsta's high costs.
"Kinsta was woefully slow and expensive. It did not provide the excellent experience we felt our members deserved.”
## Solution
Already facing performance and cost challenges, Kimberly and her team got to know about Levamo through a BuddyBoss email.

They opted for different plans for their membership and main website, confident that this combination would provide the necessary resources.
**“We have the Startup plan for our Membership site, plus Developer (plan) for our main website.”**
## Results
The switch to Levamo hosting has delivered a transformative experience for Take Back Your Temple.
One of the most significant improvements has been the dramatic increase in website speed.
She shared, *“Our Membership site news-feed load time is ONE SECOND on several devices, compared to 16 seconds in times past.”*
But at the same time, Levamo was also much cheaper than their previous hosting.
Kimberly added, ***"We pay $500 less with [Levamo] for our yearly subscription, and it provides 4 times the PHP workers. We love getting more resources for less money.”***
In addition, Take Back Your Temple has been particularly impressed by the exceptional support provided by the Levamo team.

Take Back Your Temple has a reliable team to rely on as they navigate the ongoing growth of their membership website.
## Conclusion
Kimberly Taylor and her team have overcome the challenges of slow website speeds and high costs and gained a valuable partner invested in their success.
Their website now delivers lightning-fast performance while being on a cost-effective hosting plan. The dramatic improvement in loading times has increased engagement and satisfaction among their members.
***“We highly recommend other dynamic websites get "[Levamo]-cated" and move their website hosting to [Levamo] too!”*** Kimberly concluded.


###### Challenges
- Struggled with High Traffic
- Slow and Expensive Hosting
- Lack of Speed and Reliability
###### Outcome
- 16x Improved Loading Time
- $500/Year Savings
- Rapid and Friendly Support

---
## Sudhir Shivaram Photography Cuts Response Time by 70%
- URL: https://levamo.com/blog/sudhir-shivaram-photography-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how photography courses cut response time by 70% with new hosting.
[Sudhir Shivaram Photography](https://www.sudhirshivaramphotography.com/), a leader in wildlife photography education, faced limitations with their existing hosting solution. Migrating their BuddyBoss-powered course platform to Levamo hosting resulted in a **significant boost in performance**, **scalability**, and **value**. They now effortlessly handle thousands of users with blazing-fast response times, while enjoying exceptional support and bundled features.
## Customer Introduction
Sudhir Shivaram Photography ignites a passion for wildlife conservation through captivating photography courses and tours. Led by the renowned wildlife photographer Sudhir Shivaram, the organization empowers students with a comprehensive learning experience. Their online courses have garnered a loyal following, exceeding 10,000 subscribers. Sudhir Shivaram wanted to cater to this growing community by delivering exceptional online education. However, they needed a robust and scalable hosting solution.
## Problem
The initial hosting setup of Sudhir Shivaram Photography included twelve virtual CPUs and 48GB RAM. Even though the server was powerful on paper and physically close to most of its users, it was performing terribly.
***“The Vultr high-frequency server was based out of Mumbai,”*** Sudhir shared.
Performance bottlenecks emerged as user traffic increased, causing a dip in website performance. :
***"What we did is like we ran a test of 50 virtual users... So when we used 50 virtual users and the load for five minutes, the server did start noticing the kind of traffic that we were getting. And now what we did is like we went up to 350 virtual users. So when we went to 350 virtual users, the cpu usage went to like 100% for the PHP workers. And that was the maximum load that the virtual high-frequency server could take."***
They wanted to continue delivering a high-quality online learning experience for their wildlife photography students. The need for a scalable and performant hosting solution became paramount for Sudhir Shivaram Photography.
## Solution
Sudhir Shivaram discovered Levamo hosting through the BuddyBoss Facebook group.

He added that the cost of the previous hosting was also a factor in deciding on [Levamo] for Sudhir Shivaram Photography. ***"The previous Vultr HF and the RunCloud that I was using, the overall cost was more than $400 per month. In fact, probably around 450 plus dollars per month is what I was paying over there.”***
He then explained why Levamo is much more cost-friendly for him, especially with the premium tools that come with the package.

Sudhir also shared his experience with Levamo’s free migration for Sudhir Shivaram Photography. He said, *“I logged into my servers, checked everything, and it was absolutely fine, and then I requested for the complete migration, changing the DNS, everything was very nicely taken care of.”*
## Results
Sudhir Shivaram Photography's migration to Levamo hosting was a huge success. Their website performance and scalability are much better now.
Sudhir Shivaram shares the impressive results:

Even though the server is based in Ireland, his performance is now better than before. ***“The server is based out of Ireland. So with that, what we did was a load test varying, from 50 virtual users to 700 virtual users. So, with the previous hosting, it basically topped up at 350. Now here, even with 700 virtual users, the overall response time went down from say 1 second compared to previous to just 200 to 300 milliseconds.”***
So, Sudhir Shivaram Photography can now comfortably handle a larger user base with exceptional performance, all at a cost-effective price point. The exceptional level of support from the [Levamo] team is another big advantage for him. As Sudhir shared, ***“What I get now, each time, whatever issues or whatever support I needed using my [Levamo] dashboard, I just went onto the chat and at any point of time, always a support person was available to take me through all the issues, whatever queries, anything I had, they used to get it resolved.”***

**“The support is one thing which we always look for, and in this case, I think it's absolutely top-notch,” he added**.
## Conclusion
Sudhir Shivaram Photography's investment in a robust hosting solution has yielded impressive results. Their website can now comfortably handle a significantly larger user base with blazing-fast response times, creating a noticeably smoother and more responsive learning experience for their students.
***“Since it's (BuddyBoss) their own platform, they know what they have designed,"*** Sudhir expressed his opinion on why he thinks [Levamo] has such a big impact on his website.
With a solid foundation in place, Sudhir Shivaram Photography is poised for continued growth and success in fostering a love for wildlife photography through exceptional online education. He credited this transformation to [Levamo] Hosting, saying ***“What you folks are giving me, the specific experience. The whole migration process, I should say, was very smooth. And even after migrating, the follow-up support, everything, absolutely flawless. So a big kudos to your support team.”***


###### Challenges
- High CPU Usage for Less Users
- Cost Over $400/Month
- Limited Technical Support
###### Outcome
- Performs Same at High Traffic
- Reduced Server Response Time
- Over $400 Monthly Savings

---
## Secrets to Reiki Time Academy’s Astonishing GTMetrix Results
- URL: https://levamo.com/blog/reiki-time-academy-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See Reiki Time Academy's secrets to boosting site speed and user experience.
[Reiki Time Academy](https://reikitimeacademy.com/), a BuddyBoss-powered platform empowering women in Reiki, faced **frequent crashes** and **slow loading times**. After switching to Levamo hosting, they saw **significant improvement in website performance**. Their GTmetrix score leaped from an "F" to "A"s. So users can now enjoy a more stable and responsive user experience. This empowers Reiki Time Academy to focus on its mission of fostering a thriving community of female Reiki practitioners.
## Customer Introduction
Reiki Time Academy is a unique online platform dedicated to empowering women through the transformative practice of Reiki and integrative therapies. It offers diverse programs, including personalized mentoring, comprehensive courses, and immersive experiences. Its focus extends beyond teaching Reiki. It also cultivates a supportive community where aspiring female practitioners and therapists can seek guidance and turn their passion into fulfilling careers.
## Problem
Reiki Time Academy's journey wasn't smooth sailing. They faced significant challenges with their previous hosting provider. They used two different HostGator plans, and while support was good on one plan, it wasn’t so on the other. But two things were common in both plans: frustratingly slow loading times and frequent site crashes.
***"We had complaints of slow loading times, site/app crashing especially when we sent out notifications on the app or when we had a live event on the site,"*** shared Gabriel, CEO of the Reiki Time Academy.
They were in search of a more reliable and performant solution. A hosting provider specifically designed for BuddyBoss platforms like theirs. They knew a platform optimized for their specific needs was crucial to overcome these challenges.
In Gabriel’s words, they were looking for ***“Faster loading times, less crashes especially when sending out notifications on the app or when we had a live event on the site.”***
## Solution
Gabriel learned about [Levamo] through a BuddyBoss support ticket, ***"I believe the first time I heard about [Levamo] was through a BuddyBoss ticket, where I was asking about server options,"*** he shared.
He immediately found Levamo perfectly aligned with the needs of Reiki Time Academy.

As they had a small community, he chose the basic plan. ***“I went with the Foundation plan. I just have over 500 users and not a very active community at this stage,”***
Ultimately, the transition to Levamo was even smoother thanks to the free migration service offered. This ensured a hassle-free experience. With no downtime or disruption for the Academy and its students.
When asked about the free migration service from [Levamo], Gabriel shared, ***"Yes, I did use the free migration service, and it was great, smooth, and easy, the tech team did a great job."***

## Results
The switch to Levamo hosting has been a game-changer for Reiki Time Academy. Website performance has seen a dramatic improvement, with GTmetrix scores jumping from an "F" to a consistent "B" and occasional "A." This translates to a significantly faster and more responsive user experience for students and visitors.

The improved performance isn't just reflected in technical benchmarks; it's also translating into positive user experiences. While some existing users, primarily older individuals, haven't explicitly commented on the improvements, there's been a shift in feedback from new users.
***"My customers are older people, and they don’t share a lot of the positives, but the new customers that are coming in are comparing our app with other apps and saying that it is great and it is quick and other things related more to BuddyBoss, like design and ease of use,"*** the founder explained.
## Conclusion
Today, Reiki Time Academy's frustrating slow loading times and website crashes are a distant memory. It has been replaced by a stable and responsive user experience.
***"The new customers that are coming in are comparing our app with other apps and saying that is great and quick,"*** shared the Academy's founder. This is a significant testament to the improvements achieved. Thus, Reiki Time Academy can now confidently focus on expanding its course offerings. They now have a reliable foundation in place for that.
Gabriel concluded by praising [Levamo], ***“I have an amazing journey with [Levamo]. No more site crashes, no more slow loading times. Support is always quick.”***

As a result of Levamo's backing, Reiki Time Academy is confident that it can empower a new generation of female Reiki practitioners.

###### Challenges
- Slow Loading and Crashes
- Inadequate Support
- User Performance Complaints
###### Outcome
- Improved Loading Times
- GTmetrix Score F to A
- Smooth and Efficient Migration

---
## How MingleGrove Achieved Instant Page Load Times
- URL: https://levamo.com/blog/mingle-grove-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See MingleGrove's instant speed boost with Levamo & improve user experience.
[Mingle Grove](http://MingleGrove.com) is a community-focused dating platform powered by BuddyBoss. Its WordPress website is plugin-heavy, **which slowed the site admin** and **significantly decreased user experience. To solve these problems,** it sought a high-performance hosting solution.
Seeking a solution optimized for website performance, they discovered Levamo Hosting. Impressed by its capabilities and the free migration service, they decided to use Levamo. Even before launch, Mingle Grove witnessed **instant page load times**, exceeded expectations, and laid a strong foundation for a smooth user experience. They anticipate a seamless transition to high user volumes while maintaining top-notch performance.
## Customer Introduction
MingleGrove.com is a dating platform founded by seasoned online professional George Allen. The website has a distinct mission of fostering genuine connections within local communities. It started as an alternative to the impersonal nature of larger platforms. However, with time, the platform grew and expanded its function. Mingle Grove is now a space where users not only find a romantic partner but also build meaningful relationships with people in their neighbourhoods.
This focus on community and local connections sets Mingle Grove apart and necessitates a unique approach to website design. The platform boasts a plugin-heavy WordPress architecture, rich with features designed to facilitate genuine interactions and connections. While this intricate design offers a wealth of functionality, it also presents a challenge when choosing a hosting solution.
## Problem
While the website is more feature-rich than ever, as it scaled, MingleGrove.com started facing performance challenges with its previous VPS hosting solution. The plugin-heavy design significantly slowed down the admin and user experience, hindering the platform's potential for smooth operation and user engagement.
***"MingleGrove.com was previously hosted on the very capable Hostwinds VPS during development,"*** said George. ***"My plugin-heavy design slowed the site admin and user experience significantly."***
## Solution
Seeking a performance-driven hosting solution, George discovered Levamo Hosting. Impressed by its WordPress optimisation focus and free migration service, he chose Levamo as his hosting partner.
He was using BuddyBoss to power his community and felt the combination of BuddyBoss and Levamo would be the best solution for him compared to big cloud services.
"I was sold on Buddyboss as the platform for our connections website, MingleGrove.com," George explained. ***"I watched some of the videos previewing [Levamo] and decided it was a better match than the large, cloud services like Google and Amazon."***

He also took the free migration service from [Levamo]. ***"[Levamo]'s migration service took care of the transition with flying colours. Thank you, [Levamo]!"*** Mr. Allen added, commending the seamless migration process facilitated by [Levamo].
## Results
Even before launch, Mingle Grove witnessed significant improvements in performance on its development site, despite the plugin-heavy design. ***“We have yet to launch, but the page load performance has remained 'instant'",*** he said.
While the platform is yet to experience high user traffic, George's experience with similar plugin-heavy WordPress sites on VPS hosting leads him to believe that Levamo's infrastructure will prevent potential performance issues as Mingle Grove scales.
***"Being a startup, we have yet to see [Levamo]'s advantages under large use, but I keep adding plugins and it doesn't blink,"*** shared George. ***"I am positive from building many WordPress sites that my VPS hosting would have crashed some time ago."***

## Conclusion
MingleGrove.com's mission of fostering real connections within local communities hinges on a website that delivers a seamless user experience. With its plugin-heavy WordPress design, finding a hosting solution that could handle the complexity without compromising performance was crucial.
***"Their ([Levamo]’s) focus on WordPress website performance handles the code quickly and efficiently,"*** adds George Allen, the founder. ***"I transferred my plugin-heavy, BuddyBoss-based website, MingleGrove.com, to [Levamo].cloud hosting and never looked back"***.

[Mingle Grove ](https://minglegrove.com)is a community-focused dating platform powered by BuddyBoss. Their WordPress website is plugin-heavy, **which slowed the site admin** and **decreased user experience significantly. To solve these problems,** they sought a high-performance hosting solution.
Seeking a solution optimized for website performance, they discovered Levamo Hosting. Impressed by its capabilities and the free migration service, they decided to use Levamo. Even before launch, Mingle Grove has witnessed **instant page load times**, exceeding expectations and laying a strong foundation for a smooth user experience. They anticipate a seamless transition to high user volumes while maintaining top-notch performance.

###### Challenges
- Slow Admin and User Experience
- Site Crashes with High Resource Use
###### Outcome
- Instant Page Load
- Smooth Admin Panel
- Free Migration Service

---
## Mind The Grad Sees Dramatic Increase in User Session Time
- URL: https://levamo.com/blog/mind-the-grad-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how hosting boosted Mind The Grad's user session time dramatically.
[Mind The Grad](https://mindthegrad.com/), a career and education consultancy empowering international students, faced a **crippling website slowdown** while hosted on Bluehost. This sluggish performance significantly hampered the user experience for Valeria, the founder, and her website visitors.
The search for a solution led them to Levamo hosting, a game-changer that completely transformed their website's performance. The **dramatic speed improvement** resulted in a significantly more positive user experience, propelling Mind The Grad towards tremendous success.
## Customer Introduction
Valeria Loureva is the founder of Mind The Grad. She is a passionate advocate for international students. For years, she has helped countless individuals achieve their career aspirations and secure skilled worker visas through her career and education consultancy. Today, Valeria leads a dedicated team that continues this mission, guiding ambitious professionals towards their dream jobs in the UK.
Recognising the need for a supportive and empowering environment specifically designed for international students, Valeria established Mind the Grad. This innovative online platform offers valuable resources, group career coaching, exclusive events, and insights from career experts and former international students. They also have an insider community called GradCircle. Powered by BuddyBoss, this community is a space where international students can communicate, learn, and get all the help they need to excel in their job search journey in the UK.
## Problem
Before discovering Levamo, Mind The Grad suffered from severe performance issues while hosted on Bluehost. This persistent slowness significantly impacted the user experience, causing frustration for both Valeria and her website visitors.
"Bluehost made my website super slow... nothing could fix it," Valeria stated, highlighting her helplessness with the previous hosting solution.
She tried many things to solve the sluggishness, but nothing worked. *“I have tried 1000 things to improve the performance of the community website, endless plugins, optimisation of pages, and hiring various people on Upwork and Fiverr.” *she shares*.*

With that kind of experience, she had the same worry in her mind during her initial consideration of Levamo. When asked what her most significant doubt was when signing up for Levamo, she answered, “**I was hoping to improve the speed and performance, but I was worried that it would not change things too much.** ”
## Solution
Valeria's search for a solution led her to Levamo hosting through social media channels, particularly YouTube and email marketing. Impressed by what she discovered, she decided to give Levamo a try for Mind the Grad.
"I heard about it by following the BuddyBoss on social media, especially YouTube and email,"Valeria explained.
Two key factors that solidified her decision were Levamo's free migration service and the early bird discount.

***"I think it is a very good deal for such pricing; I am lucky to be one of the first people to take on [Levamo] and get the concierge service”,*** Valeria shared, emphasising the positive experience and personalised support she received during the transition.
## Results
The switch to [Levamo] hosting dramatically improved Mind the Grad's website speed. Valeria enthusiastically described the performance boost: ***"the website flies like a rocket now!"*** This significant change led to a more positive user experience for her customers.
***"My customers said that it feels like a new website. Customer feedback improved, and so did the time spent on the platform,"*** Valeria shared, highlighting the positive impact the improved website performance had on her audience.

Since she has no technical background, migrating the website to a new hosting was another hurdle for her. However, Levamo’s free and seamless migration service made it all easier for her.
***“The team also migrated everything for me for free; as I am not a developer, this was an amazing perk,”*** Valeria added.
## Conclusion
***“I just needed [Levamo], and now all the bugs and speed issues are fixed,”*** Valeria told us. With the dramatic speed improvement by [Levamo] hosting, Mind The Grad has transformed its online presence. No longer plagued by the frustrations of a sluggish website, Valeria can now focus on what she does best: empowering ambitious professionals and international students.
Looking towards the future, Mind The Grad is confident in its continued growth and success. With a reliable and high-performing hosting solution, they can confidently expand their reach and impact the lives of even more individuals seeking to achieve their career goals. As Valeria herself stated, ***"I only wish I had [Levamo] when I started building my community website... it would have saved me hours of time and a lot of tears and sweat!"*** This sentiment perfectly encapsulates the significant value [Levamo] hosting has brought to Mind The Grad's online journey.

[Mind The Grad](https://mindthegrad.com/), a career and education consultancy empowering international students, faced a **crippling website slowdown** while hosted on Bluehost. This sluggish performance significantly hampered the user experience for both Valeria, the founder, and her website visitors.
The search for a solution led them to Levamo hosting, a game-changer that completely transformed their website's performance. The **dramatic speed improvement** resulted in a significantly more positive user experience, propelling Mind The Grad towards greater success.

###### Challenges
- Extremely Slow Site
- Ineffective Performance Fixes
- Constant Customer Complaints
###### Outcome
- Rocket-Like Website Speed
- Increased User Session Time
- Smooth Migration Service

---
## How KC360 Achieved a 100%+ Performance Boost
- URL: https://levamo.com/blog/kc360-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
KC360 boosted performance 100%+. See how they did it with Levamo hosting!
[KC360](https://kc360.co/), a leading international higher education consultancy supporting Third Culture Kids (TCKs), was facing a **downward performance** using their hosting, coupled with **ineffective support response**. To overcome these issues, they migrated to Levamo. They now enjoy **faster loading times**, **enhanced security**, and **exceptional support**, solidifying their decision to switch.
## Customer Introduction
KC360 supports Third Culture Kids (TCKs) through the college search and admission process. It is the brainchild of Kristi Steele, a TCK and former college recruiter. KC360 offers invaluable resources and online communities specifically designed for their unique needs.
David Hare, Chief Operation Officer at KC360, brings a wealth of experience to the team. He has extensive practical experience in various sectors of the field of social enterprise. And that helps KC360 provide solutions that make a tangible difference.
## Problem
Prior to [Levamo], KC360 hosted their website on multiple platforms before. ***“We were previously hosted at Cloudways on Digital Ocean servers, for about three years, having moved on from Godaddy hosting”,*** David shared with us.
They initially experienced a significant performance boost after moving to Cloudways. However, they faced declining effectiveness in service and support over time. Due to decreased performance, their BuddyBoss-powered community app began experiencing increasing load times.
In his words, *“With a decrease in the effectiveness of Cloudways services, the ability for their support remains effective, and we noticed Buddyboss' APP was slowly getting longer load times even after we added expensive increases in applied hosting services.”*
"*As our customers rely entirely on our expertise and have 100% belief in our relationship, we were the only ones who were becoming frustrated with the hosting platform,*" David shared.
## Solution
KC360 was already a BuddyBoss customer. They immediately jumped in when they knew that the team behind BuddyBoss was launching a cloud hosting service. *“There were no doubts”,"* David told us.
David believed that Levamo’s compatibility with BuddyBoss could technically upgrade his platform. *“I knew we were about to get a serious technology boost after a great deal of comparative match-making was done over a few weeks between what was being offered and what we were using at Cloudways”,"* he shared.
With good faith in mind, they decided to migrate their website. KC360.CO opted for Performance Level 1 and Start Level 1 packages with the Enhanced Support Plan. The free migration service, facilitated by Levamo, was remarkably smooth and successful.

**"Breathtakingly successful!! Breathtaking!! The most exhilarating way to start 2024,"** David exclaimed, reflecting on the seamless migration experience.
## Results
The switch to Levamo resulted in a dramatic performance improvement. While they could not asses exact numbers, KC360 experienced a significant increase in performance, leading to faster loading times and a more seamless user experience for their clients.
*“I don't know the numbers - but it must be 100's of percentages increased in performance metrics”,"* David shared.
Furthermore, the WAF (Web Application Firewall) included in Levamo's solution allowed KC360 to drop their previous security service, leading to cost savings. This came on top of exceptional technical support provided by Levamo.

## Conclusion
Since migrating to Levamo hosting, KC360 has significantly improved its website performance and user experience. With newfound confidence in its hosting infrastructure and exceptional support, KC360 is optimistic about continued growth and delivering the best possible service to its clients.
*"Our clients haven't noticed, because the service we provide through KC360's LMS and our clients' online communities powered by Buddyboss are targeted at unique market sectors who have never had access to these sorts of services: any performance would have been ok - but we only want the best for our clients, so it matter more to us","* David emphasized.


###### Challenges
- Slow Load Times with Cloudways
- Unresolved Performance Issues
- Costly Security Solutions
###### Outcome
- Speed Boost with Levamo
- Better Overall Performance
- Cost Savings with WAF

---
## How HumanDesign.ai Increased Member Engagement by 300%
- URL: https://levamo.com/blog/humandesign-ai-customer-stories/
- Category: customer-stories
- Author: Shahzeb Ahmed
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how HumanDesign.ai boosted engagement 300% and cut costs.
[HumanDesign.ai](http://humandesign.ai/), a revolutionary platform offering personalized Human Design insights and resources, faced a significant hurdle: **a sluggish website experience** that stifled its online community.
After migrating to [Levamo](/), it witnessed a remarkable turnaround: User engagement skyrocketed by 300%, and its hosting costs dipped by a significant 30%.
**Overview of the Results:**

###### Challenges
- Faced Performance Issues
- Generic Configurations
- High Cost vs. Performance
###### Outcome
- 300% Increase in Engagement
- 30% Reduced Hosting Costs
- Enhanced Community Traction
## Customer Introduction
Kyle Hi’s passion for web development began to blossom in the early days of dial-up internet, and over the years, it morphed into a deep understanding of the intricate world of websites. But in 2021, he started towards a new vision: Human Design. This complex yet insightful system resonated deeply with Kyle, and he envisioned a platform that would empower anyone to explore its fascinating depths. Thus, HumanDesign.ai was born.
HumanDesign.ai is a one-stop shop for individuals seeking to unlock the secrets encoded in their unique Human Design blueprint. Their platform leverages artificial intelligence to analyze human design charts and generate personalized reports, guides, and resources. Users gain valuable insights into their personality traits, potential career paths, and strategies for personal growth.
## Problem
The initial journey of HumanDesign.ai was challenging. They experimented with various hosting providers.
**“We tried multiple hosts, WPMU & Kinsta,” shared Kyle**.
While these solutions offered decent customer support, a crucial issue was that they both had generic configurations. These generic setups, designed for a broad range of websites, needed to be optimized for HumanDesign.ai's specific needs.
**"Customer support was great on both, but their generic configurations meant we were paying a huge amount for slow applications,"** explains Kyle. **"We wanted a smoother experience for our users. We didn't know if it was actually possible to ever achieve the speed we have now."**
## Solution
Kyle, a dedicated member of the BuddyBoss community, stumbled upon a potential solution: Levamo hosting.
**“(I am) already a BuddyBoss customer, watching the BuddyBoss for many years, watching the updates as they happen,”** he shared.
Due to his previous positive experience with BuddyBoss, he was immediately excited about a specialised hosting solution for the BuddyBoss platform that could offer the optimization that previous providers lacked. Ultimately, he decided to migrate HumanDesign.ai to Levamo hosting, which proved to be a turning point for his community.
## Results
The impact of switching to Levamo hosting was nothing short of transformative.

He further shared the positive influence of [Levamo] on his website: ***“Since moving to [Levamo], our community has gained traction, our members are more active than ever, and we have the foundations of an epic online community that actually works.”***
When asked if his website's performance improved since switching to Levamo, he shared, “*(We had an increase of) 300% member engagement”*.

But that’s not all. [Levamo] also offered a more cost-effective solution. HumanDesign.ai saw a significant reduction in monthly expenses compared to their previous hosting providers. When asked about his monthly cost compared to the previous host, he shared, ***“(We have) reduced costs by 30%”.***
## Conclusion
HumanDesign.ai's story is a compelling testament to the transformative power of optimised hosting for online communities. Their experience highlights the limitations of generic hosting solutions for dynamic websites. It also underscores the significant benefits of leveraging a hosting service specifically designed for the chosen technology stack.
"Highly recommend working with Levamo if you are an active Buddyboss community," says Kyle Hi, founder of HumanDesign.ai.


---
## GetAConnect Boosts User Experience with Massive Performance Increase
- URL: https://levamo.com/blog/getaconnect-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how GetAConnect boosted user experience and grew with cloud hosting.
[GetAConnect](https://getaconnectglobal.com/), a content funnel company, faced website slowdowns and lost B2B customers due to a poor user experience with its previous host. Levamo cloud hosting's smooth migration, blazing fast speeds, and seamless rebranding helped it overcome these challenges and achieve significant growth.
## Customer Introduction
Chanakya Joshi, an alumnus of the prestigious IIM Indore, brings a wealth of experience. Over the past two decades, he has gone through the same pain points businesses face in stakeholder engagement. His entrepreneurial spirit led him to found GetAConnect, a company dedicated to revolutionising how businesses connect with their partners, employees, and customers through strategic content funnels.
GetAConnect operates on the fundamental belief that a company's success hinges on its customers and the strength of its relationships with partners and employees. Their innovative approach leverages learning and marketing technologies to achieve this.
## Problem
Before migrating to Levamo, GetAConnect's website used HostGator to host their website.
***“My website was previously hosted on Hostgator. It was a shared hosting (a Baby Cloud plan). The challenge was website was very slow both at the backend as well as front end”***, Chanakya Shared.
Moreover, sudden spikes in website usage lead to significant slowdowns, negatively affecting the trial experience for potential B2B customers and even leading to lost business opportunities.

***"The website used to completely become slow once the resources were utilized due to sudden spike in usage,"*** Joshi explained. ***"I lost a couple of B2B customers because of the backend trial experience was not good with them."***
Beyond the performance issues, Joshi's other concern was migration to a new hosting, even if he decides to change it.
***“The first apprehension of course was about the Migration. The migration has to be smooth as it was a big change for us,”*** he added.
## Solution
Joshi discovered [Levamo] cloud hosting through his involvement with the BuddyBoss community. He already knew BuddyBoss for its high-quality products and support, as he has been using BuddyBoss to power the GetAConnect community website. ***“I am an ardent fan of BuddyBoss and especially Michael Eisenwasser (for his really well built product and, even better, the videos about the product) and Tom Cheddadi for his extremely high level of energy and awesome culture he has set up at BuddyBoss.”***, Joshi shared. ***“So when [Levamo] Beta was announced in BuddyBoss Facebook Group, it was a no-brainer for me to register for the Beta.”***

He opted for the Levamo Startup Level 1 plan and took advantage of the free migration service from Levamo.
***"The migration experience was really smooth for me,"*** Joshi said. ***"When the migration actually went live, I was at a hospital due to a personal emergency. I got time during the night when I got time for a chat with your support team and give the 'Go Ahead'. In next 5 minutes the site was migrated. I could not believe that I could do it with all the personal challenges I faced at the hospital."***
## Results
Since migrating to Levamo cloud hosting, GetAConnect has experienced significant performance improvements in its website. Apart from the speed improvement, they had a great experience with the domain transfer of their website.
***“The major challenges [Levamo] solved for us are 1) SPEED of the website (both at front end and back end), 2) SMOOTH REBRANDING (easy 301 redirects from https://getaconnect.in to [https://getaconnectglobal.com](https://getaconnectglobal.com/)),”*** Chanakya shared.

## Conclusion
GetAConnect now has a website blazing fast and responsive, fostering a more positive user journey and potentially leading to increased customer satisfaction.
Their decision to partner with [Levamo] cloud hosting played a critical role in this success story, providing the foundation for a high-performance website and a seamless rebranding experience. As Joshi emphasised, ***"[Levamo] cloud hosting was a very important decision for our business.”***

He further added, *“It is extremely comforting when your developer himself is looking at hosting in a way. I think this is their inherent differentiator (of BuddyBoss) which almost no one can beat.”*
[GetAConnect](https://getaconnectglobal.com/), a content funnel company, faced website slowdowns and lost B2B customers due to **poor user experience with their previous host.** Levamo cloud hosting's **smooth migration**, **blazing fast speeds**, and **seamless rebranding** helped them overcome these challenges and achieve significant growth.

###### Challenges
- Slow Performance on Front & Backend
- Loss of B2B Customers
- Slowdown During Peak Times
###### Outcome
- Improved Speed
- Better Value for Money
- Effective Support

---
## How Levamo Helped English Pro Tips Achieve 300% Speed Boost
- URL: https://levamo.com/blog/english-pro-tips-case-study/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how Levamo boosted English Pro Tips' site speed by 300%!
[English Pro Tips](https://englishprotips.com/), a BuddyBoss-powered eLearning platform for IELTS exam preparation with over 35,000 students and a combined +1 million social media followers, sought *a hosting solution to keep pace with their comprehensive learning resources and growing student community.*
Founder Eli Hardie Howes chose Levamo to host the website. Levamo's optimization for BuddyBoss helped them ***achieve significant improvements in website speed***, which delivered a smoother and more engaging learning experience to English Pro Tips' students.

**Challenges**
- Slow performance
- Inadequate for eLearning needs
- Inadequate customer support
**Outcome**
- 300% increase in site speed
- Tailored for eLearning sites
- 24/7 quick and effective support
## Customer Introduction
Eli Hardie Howes founded English Pro Tips to help students get better scores on the IELTS exam through a comprehensive online learning platform. English Pro Tips offered a well-rounded approach to exam preparation, with interactive quizzes, video lessons, expert strategies, and model answers to help students score better.
## Problem
Before discovering Levamo, Eli used Cloudways to host English Pro Tips. However, he recognized the limitations this posed for his dynamic e-learning platform.
- **Slow page loading speed, poor user experience.**
- **Slow website performance leads to higher dropout rates.**
- **Platform inefficiencies stifle growth potential.**
There was no particular optimisation for a dynamic course and membership website.
"*I was previously with CloudWays,*" Eli added. *“I wanted to be with a hosting provider that understood dynamic membership and eLearning websites*"
## Solution
Eli was looking for a hosting provider more suited for his unique and dynamic website. So when Levamo Early Bird launched, recognizing the potential of Levamo hosting for English Pro Tips, Eli decided to make the switch. "*I decided to buy their early bird deal (of Levamo),*" Eli said.

While initially apprehensive about the level of support compared to his previous host's larger team, Eli's concerns were quickly alleviated:
"When I started with Levamo, I was worried about their ability to reply quickly to my support needs," Eli admitted.
***"However, I was pleasantly surprised by [Levamo]'s support and responsiveness. I even had Wes (the architect) help me delete some unnecessary files that were slowing my site down,"*** he went on to share his amazement at Levamo's support.

## Results
After migrating to Levamo hosting, English Pro Tips reaped numerous benefits.
- **🚀 300% faster load times than with the previous hosting solution.**
- **📎 Retention rates improved, with fewer complaints about platform speed.**
- **🏆 Increased platform scalability to accommodate future growth.**
As Eli elaborated, ***"In a world of decreased patience and distractions left, right, and center, it's essential that your site is as fast as it can be,"*** Eli emphasized. ***"There is no doubt that my site is much faster now that it's on [Levamo]."***
Eli further elaborated on his experience with Levamo's personalised support:
***"I even had Wes, who I guess is the grand architect of [Levamo], go into my site specifically and help me discover a file in my WP config file that was slowing my website down. And since removing that, I've noticed sizable increases in my speed. "***

Overall, he expressed his joy about how fast his website had become after moving to Levamo from Cloudways with an estimated performance increase of +300%.
***"I've been very happy with how fast my website has been since switching to [Levamo].***"
## Conclusion
Eli Hardie Howes had transformed English Pro Tips into a powerful resource for IELTS exam preparation. When he recognised the limitations of his previous hosting solution, he was seeking a platform tailored for dynamic websites and social communities. Eli found that fit in Levamo hosting.
The switch to Levamo delivered significant benefits, most notably a substantial boost in website speed. That translated directly to a smoother user experience for Eli's students and a higher income.
***”The BuddyBoss + [Levamo] combo has allowed me to leave my full-time job as an English teacher and work entirely for myself. And with a much higher income than I ever anticipated!”*** Eli shared.

With the secure and optimized foundation that Levamo provided, Eli was able to focus on delivering exceptional learning experiences to his students.
---
## Reasons Behind Droga Odważnych’s Stunning Soar in Page Speed
- URL: https://levamo.com/blog/droga-odwaznych-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how Droga Odważnych boosted site speed and user engagement.
[Droga Odważnych](https://aplikacja.odwazni.pl/), a Catholic community for men's development, saw its website performance suffer due to **frequent downtime** and **slow loading times**. Levamo's robust infrastructure and expert migration services provided the right solution. This led to a **66% improvement in page loading time** and a **150% improvement in response times**. As a result, they saw a **30% increase in user engagement**.
## Customer Introduction
Founded in 2010, Droga Odważnych is a Polish Catholic community that helps nurture leadership and spiritual development for men. Their BuddyBoss-powered online community platform serves as a cornerstone for their mission, offering formation groups, retreats, workshops, and other programs. This virtual space fosters connection and growth for men seeking to enrich their lives.
## Problem
The Droga Odważnych website faced sluggish loading times and frequent downtime, especially during periods of high traffic. These issues frustrated users and threatened to limit the community's growth potential.
"Our platform struggled with frequent downtime and performance bottlenecks, especially under high traffic conditions," explains Michał Paczula, Director of the Droga Odważnych Foundation.
These performance issues significantly impacted user experience. Downtime resulted in complete inaccessibility, hindering engagement and preventing users from accessing valuable resources.
They have a dynamic community site powered by BuddyBoss. So, they needed a solution to support the site and keep the member experience top-class. ***"This was particularly problematic since we rely heavily on BuddyBoss to manage our online community and membership functionalities."***
He added, ***"We aimed to eliminate the recurring downtime issues and improve overall system responsiveness to ensure a seamless user experience for our growing community."***
## Solution
Michał and his team discovered Levamo through a recommendation. They found it impressive because of its reputation for scalability and reliability.
***"Their positive feedback, especially regarding the reliability and scalability, encouraged us to consider [Levamo] as a potential solution for our own challenges,"*** Michał shared.
He also explained the reasons behind Choosing Levamo for Droga Odważnych.

After exploring their options, they opted for [Levamo]'s "Business" plan. Michał explained, ***"(The Business plan) was well-suited to meet our needs for higher processing power and storage capacity. This plan also included advanced security features and priority support, which were critical for us given the sensitive nature of our community interactions and data."***
They also took advantage of Levamo's free migration service.

## Results
Since migrating to Levamo, Droga Odważnych has dramatically improved website performance. Downtime is non-existent, and response time has increased significantly.

Their page loading times decreased, leading to user satisfaction and a greater likelihood of users returning and engaging with the platform.
***"Our page load times have decreased from an average of 6 seconds to around 2 seconds,"*** Michał explained the current performance.
Ultimately, this translates to community growth, attracting new members and fostering stronger connections among existing ones.
The impact is visible on user engagement on the site as well. ***"Our user engagement metrics, such as time spent on site and pages per session, have also seen improvements of around 30%,"*** Michał shared.
## Conclusion
The story of Droga Odważnych is an example of the transformative power of investing in the right hosting solution. They've created a platform that is not only reliable and accessible but also delivers a fast and engaging user experience.
This translates directly to a more satisfied and engaged community. As one of the customers on their platform said, ***"The site now loads so much faster and without the annoying timeouts I used to face during busy hours."*** This sentiment is echoed by many users who now benefit from a seamless online experience.
Droga Odważnych is now ready for long-term growth thanks to these improvements. Michał concluded by saying, ***"We are now more confident than ever in our platform's ability to handle growth and deliver exceptional user experiences, thanks to [Levamo]."***


###### Challenges
- Frequent Downtime
- Crashes Under High Traffic
- Slow Load Times
###### Outcome
- Virtually Zero Downtime
- 150% Faster Load Times
- 30% Enhanced User Engagement

---
## Secrets to Balanced Veterans’ Unbelievably Better Website Speed
- URL: https://levamo.com/blog/balanced-veterans-network-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how Balanced Veterans boosted website speed and community engagement.
[Balanced Veterans Network](https://balancedveterans.org/), a non-profit dedicated to veteran wellness, struggled with a slow website and limited community features that hindered its ability to serve veterans effectively. Levamo hosting came to the rescue, providing BVN with the speed, robust community functionalities, and exceptional customer service needed to create a thriving online community for veterans.
## Customer Introduction
Balanced Veterans Network (BVN) is a non-profit organization with a mission to empower veterans and their families through education, community, and alternative wellness practices. Melissa Tew, COO and a Navy veteran herself, understands veterans' unique challenges and is passionate about providing them with the resources they need to thrive. BVN offers various initiatives like Community, Mental Wellness, Movement, Operation 1620, and Project Triangle. They all help veterans achieve holistic well-being and a renewed sense of purpose.
## Problem
BVN's previous hosting provider presented significant challenges that hindered their ability to serve veterans effectively online. The website was slow, impacting user experience and also making it difficult for veterans to access resources efficiently.
***"Our previous host was slow,"*** said Melissa Tew, COO of Balanced Veterans Network. ***"It didn't have the community integration options we wanted, and their customer support was lacking."*** These hurdles meant that Veterans relied on Facebook to interact because of these hurdles. And didn’t always feel secure for the members.
BVN emphasizes fostering a safe and supportive online environment. So, forcing members to rely on an external platform wasn't ideal. ***“Our customers had to use Facebook to interact which doesn't always feel safe,”*** Mellissa shared.
These limitations posed a significant obstacle to BVN's mission.
## Solution
After repeatedly experiencing frustration with their previous provider, the Balanced Veterans Network team discovered Levamo [BuddyBoss hosting](/buddyboss-hosting/), the platform powering their website.
***"BuddyBoss (team) told us about [Levamo] after we complained many times about how slow their platform made our website,"*** said Melissa. [Levamo]'s commitment to speed directly addressed BVN's primary concern.
BVN was impressed by Levamo's dedication to customer service.

As a result of this dedicated support, BVN can now focus on its mission without technical roadblocks.
## Results
The switch to [Levamo] hosting has been transformative for Balanced Veterans Network. Website speed has increased significantly. “***While we struggled to succeed with our platform speed and performance, everything changed once we found [Levamo],”*** shared Mellissa.

It also provided veterans with a much smoother user experience. ***"Immediately, we found our customers were happier with the speed of their experience,"*** said Melissa.
***"Now, our veterans feel they can express themselves more freely on our website,*** "Melissa added.
## Conclusion
The success story of Balanced Veterans Network exemplifies the transformative power of reliable, feature-rich hosting. With a faster website and responsive hosting, BVN can continue providing essential resources and fostering a sense of belonging for veterans.
By leveraging Levamo hosting, BVN is not a slow website anymore. Thus, Veterans now have a faster, more secure platform to connect, share experiences, and access resources that can improve their well-being.
Melissa concluded, ***"If BuddyBoss did anything right, it was bringing [Levamo] into the picture."***


###### Challenges
- Slow Website
- Insufficient Customer Support
- Poor User Experience
###### Outcome
- Seamless Community Integration
- Significantly Faster Speeds
- Effective Customer Service

---
## Accessible Japan Takes Their Website From Slow to Amazingly Fast
- URL: https://levamo.com/blog/accessible-japan-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
See how Accessible Japan boosted site speed for accessible travel info.
[Accessible Japan](https://www.accessible-japan.com/) and its BuddyBoss-powered community, [TabiFolk](https://www.tabifolk.com/activity/), saw their websites hampered by slow loading times on shared hosting. The website is dedicated to empower disabled travelers to explore Japan. However, the website was frustrating for users because of a lagging TTFB (Time To First Byte) that hindered their ability to provide a smooth and inclusive travel experience. Switching to Levamo hosting **dramatically improved website speed**, boosting user engagement and allowing Accessible Japan to serve its community of globetrotters better.
## Customer Introduction
Barry Joshua Grisdale is a Canadian-born Japanese citizen who advocates for accessible travel. He uses his platform, Accessible Japan, to empower disabled travelers to explore the beauty of Japan. Born from his own travel experiences using a wheelchair, Accessible Japan tackles the frequent lack of accessible information, providing detailed reviews of accommodations, attractions, and accessible tours. His website also features a blog with travel stories and tips, facilitates equipment rentals, and has published a guide to accessible Tokyo. Accessible Japan actively engages with its community through groups and forums, encouraging users to continually share updates and reviews to enhance travel experiences for all.
## Problem
Accessible Japan initially resided on a shared hosting on Siteground. When asked what challenges he faced with his previous host, he shared, ***"Caching issues, slow speeds, "special" version of PHP"*** The slowness directly contradicted Accessible Japan's mission: to ensure a smooth and inclusive travel experience for all. As Barry said, ***"I started off on shared hosting and constantly struggled with slow loading times and frustration."***
So when he was considering migrating Accessible Japan to [Levamo], he was still doubtful about it. In Barry’s words, ***"I was worried it wouldn't live up to the hype but far surpassed it."***
## Solution
Josh learned about Levamo hosting through the BuddyBoss Facebook group. The promise of superior speed and user reviews of Levamo was intriguing.
Thus, despite his concerns that a new platform would not live up to the hype, Josh decided to try it on Accessible Japan during the beta phase.
***“After I heard about [Levamo], I signed up for the beta and stayed up to 2 am local time waiting for my reservation to open up,”*** Josh shared.
***“Even in beta,”*** Josh recalls, ***“it was fast, and the user interface was easy to use.”*** His doubts were quickly dispelling.

He then moved to [Levamo] and bought separate packages for his static and community sites. ***“My site is still small, so it is on Startup 1. My static site is on the Developer package.”***
Josh also highlighted the ease of use of Levamo's platform, mentioning a user-friendly interface that simplifies migration. Levamo also offers a free migration service, further streamlining the customer transition.
## Results
The switch to [Levamo] has been a game-changer for Accessible Japan. ***"The cost is actually lower despite getting much more,"*** says Josh.

He highlights the significant improvement in website speed, specifically mentioning a dramatic decrease in TTFB.

Faster loading times improved user experience and contributed to better search engine ranking possibilities, potentially bringing Accessible Japan's valuable resources to a broader audience.
## Conclusion
Accessible Japan's story is a testament to the power of prioritizing user experience. By overcoming the hurdle of slow loading times, they've created a platform that empowers disabled travelers to explore Japan with confidence.
The improved website speed translates to a more engaged audience, allowing visitors to delve deeper into Accessible Japan's resources and connect with a supportive travel community.
He was impressed with the performance after moving to [Levamo]. ***“I could not be happier with everything and even moved my other site here soon after,”*** shared Barry.

Their story is an inspiration, demonstrating how dedication and the right tools can positively impact a global scale.

###### Challenges
- Caching Issues
- Older PHP Version
- Slow Loading Times
###### Outcome
- Significantly Faster Speeds
- Drastic TTFB Improvement
- Lower Costs with More Features

---
## How TCM Academy Slashed Their Customer Complaints by 100%
- URL: https://levamo.com/blog/the-tcm-academy-customer-stories/
- Category: customer-stories
- Author: Faisal Sarker
- Published: 2024-05-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
TCM Academy eliminated all customer complaints. Find out how they did it.
The TCM Academy is a leading online platform for continuing Traditional Chinese Medicine (TCM) education. It faced frequent website performance issues that hindered its ability to deliver a seamless learning experience.
After switching to Levamo hosting, they achieved a **significant performance boost.** They also **eliminated customer complaints to zero** and **gained valuable security features.** All while **enjoying cost savings** compared to their previous provider.
## About TCM Academy
[TCM Academy](https://www.tcm.ac/) was founded by the visionary Dr. Yair Maimon, a renowned clinician and teacher with over 30 years of experience in TCM and oncology research. It offers a unique online learning environment powered by tools like BuddyBoss and LearnDash. The academy's in-depth programs and advanced courses are led by the world's leading TCM and conventional medicine experts. They provide students with a comprehensive understanding of Eastern and Western medical practices.
The TCM Academy needed to ensure the quality of its content and the user experience for its students. This is mainly because their students learn remotely from the comfort of their homes or offices. Recognizing the crucial role of website performance in ensuring a smooth learning journey, Dr. Maimon sought a reliable hosting solution that could guarantee optimal speed and stability.
## The Challenge
Prior to Levamo, the TCM Academy hosted its website on a 16GB Digital Ocean server for a $170 per month fee. However, it still experienced frequent performance issues, which resulted in slow page loading, gateway timeouts, and frequent customer complaints.
"The site was very slow even though we scaled it to this level, especially when running events with multiple people online at once," shared Dr. Maimon.
## The **Solution**
Learning about [Levamo] through their developer, [Paul Brian](https://www.paulbrian.co.uk/), the TCM Academy opted for the Startup Level 4 plan, hoping to increase their website performance. When asked, D. Maimon shared that he initially had doubts about choosing [Levamo], ***“Had doubts due to the recent launch (of [Levamo]),”*** shared Dr. Maimon.

However, his doubts soon started getting cleared, especially after utilizing the free migration service offered by Levamo, which ensured a smooth transition.
## The Outcome
Since switching to Levamo, the TCM Academy has witnessed a dramatic improvement in website performance. Customer complaints regarding slow loading times and timeouts have completely vanished.
***"Performance has increased considerably,"*** Dr. Maimon confirms.

Beyond performance, [Levamo] provided the TCM Academy with significant cost-to-value ratio and security benefits. ***“We are paying slightly less now and getting so much more value with all the security features such as Patchstack,”*** he added.
They also loved that [Levamo] has top-class caching solutions specifically designed for dynamic websites. ***“All the caching features set specifically for dynamic sites (OP Cache, Object Cache, Redis, Litespeed Cache) really improve performance,”*** he shared.
The TCM Academy's experience with Levamo hosting is a testament to the platform's ability to deliver exceptional performance, user experience, and security at a competitive price point. Dr. Maimon praises the positive impact on their operations Levamo:


###### Challenges
- Slow Website
- Couldn’t Handle High Traffic
- Frequent Customer Complaints
###### Outcome
- Much Faster and Reliable Website
- Zero Customer Complaints
- Zero downtime

---
## Building a Passive Income Stream with WordPress: Plugins, Themes, and More
- URL: https://levamo.com/blog/making-passive-income-with-wordpress/
- Category: wordpress
- Author: Tom Cheddadi
- Published: 2024-05-08
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Monetize your WordPress site! Get passive income tips using themes and plugins.
WordPress has become one of the go-to platforms for [website creation](https://wordpress.org/40-percent-of-web/) and management, powering almost 40% of all websites on the internet. With around [2.7 million searches](https://www.sixthcitymarketing.com/wordpress-stats/) every month, this platform provides opportunities for those looking to leverage its popularity.
With [WordPress](https://wordpress.com/), there are multiple tools and resources for creating a passive income. Its diverse themes, plugins, and integrations also make it easy for anyone. In this article, discover the best strategies to build a passive income stream. Ready to start earning? Let's get started!
Image source: Unsplash.com
## Understanding Passive Income in the WordPress Ecosystem
Passive income is the money you earn that only requires a little time or effort to maintain. That's not to say passive income is easy money. Most ways to generate a passive income require an upfront investment of either money, time, or both.
Many people share the dream of generating a steady stream of income with minimal daily effort. For WordPress professionals, having a passive income means they can keep earning from anywhere, even when not actively working.
Passive income is a shift from the traditional time-for-money trade to earning potential that's not directly tied to the hours you work. It takes pressure off having just one income stream and opens possibilities of financial independence.
Here are ways to build a passive income using your WordPress website.
## Developing and Selling WordPress Themes
There is always a demand for new and innovative themes; and WordPress themes are some of the most in-demand products on the internet, which has led to a thriving market. Therefore, it becomes easy to build a passive income if you can develop well-crafted and user-friendly WordPress themes.
According to [ThemesBazaar](https://www.wpthemeschecker.com/how-much-can-you-make-selling-wordpress-themes/#:~:text=According%20to%20ThemesBazaar%2C%20the%20average,theme%20and%20the%20features%20included.), the average price for a WordPress theme is $49, and you can make more depending on your theme's quality and features included.
Of the 28,644 templates and themes on Envato's [ThemeForest](https://themeforest.net/), 7,986 (or 28%) are WordPress themes. Since 2008, ThemeForest has processed a total of transactions worth $355,617,997. Out of those transactions, $286,355,625 is exclusively for WordPress themes.
Knowing the factors that contribute to the success of one theme over another can be difficult. However, here are a few principles that can significantly impact your theme’s overall sales.
### Design and Development Tips for Themes
Image source: Unsplash.com
**1. Start with a Good Design**
Remember the fundamentals of a good design. Look closely at your typography, layouts, image sizes, color choices, etc., and have a quality concept to build on. Your target audience is users who want a simple solution to set up a professional-looking website that works flawlessly.
**2. Design High-Quality Themes**
High-quality themes control so much of a website's overall feel and design. Your goal should always be to create performing themes - ones that do not leave your target audience with an excessive amount of work to do on their own.
**3. Follow WordPress Best Practices**
When developing your theme, consider these elements that will set it apart from others:
- Include custom widgets and shortcodes. This way, users can customize their sites with ease
- Install a dedicated plugin
- Pay attention to responsive design principles
- Choose styles that will serve mobile users more effectively, etc.
### Best Practices for Selling Themes to Build a Passive Income stream
Every WordPress site uses a theme, which means there's a huge market to sell WordPress themes. You may sell your themes at [ThemeForest](https://themeforest.net/), [TemplateMonster](https://www.templatemonster.com/marketplace/?aff=aoclarkejr), or [Creative Market](https://creativemarket.com/templates-themes), or you can sell them from your website. Some tips for successful sales are:
1. Using your website as the platform to sell themes is the optimal strategy for maximizing profits. This approach gives you control over all aspects, from your pricing structure to managing customer communications.
2. Having a great "sales" page or demo site is necessary for generating sales. It is the place for you to showcase all the amazing styles. Live demos allow users experience your theme's features and functionality first-hand.
3. Use SEO tips to get your theme discovered in Google searches. Write informative and authentic blog posts relevant to your target audience and attach a link to your theme.
4. Leverage existing online communities to promote your theme. Social media platforms are excellent ways to achieve a wider audience. Examples are Twitter, Facebook, and Instagram
## Creating Profitable WordPress Plugins
There are a lot of WordPress plugins to build a passive income stream. Plugins help to upgrade and strengthen the WordPress website. They can thoroughly change your website's user experience. This is by adding new layouts, and features, and presenting new ways for users to interact with it.
[WordPress plugins ](https://wordpress.org/plugins/)also help enhance performance, and gain higher search engine rankings. They optimize many other aspects of the everyday workflow. Additionally, they come with tools to make websites less vulnerable to data breaches and malware.
An example of a powerful tool for plugin development is **[Crocoblock](/blog/crocoblock-review/)**, an extensive suite of tools and plugins designed for building dynamic websites without coding. Crocoblock’s plugins, especially its JetPlugins set, empower WordPress users to create advanced functionality and custom layouts that appeal to both developers and non-developers.”
### Developing Plugins WordPress Users Want
Successful plugins often solve specific problems or provide unique functionality that users find valuable. Understanding the target audience, their pain points, and the features they desire is crucial when developing your plugins if you wish to build a passive income.
To avoid unnecessary plugins, research only specific website recommended types. For example, a particular plugin offering multiple payment methods will not hold the same significance for a blog as it does for an eCommerce site.
### Monetization Strategies for WordPress Plugins
Image source: Unsplash.com
Once your plugin is up and running, various methods can be used to monetize and achieve a sustainable income stream. They are:
**1. Premium App:** This provides a free, basic version of the plugin with limited features alongside a paid premium version that includes advanced features, customization options, and priority support. Every time a user chooses to install your plugin, you'll boost your earnings through download fees.
2. **Subscription-based Model:** This offers subscription-based access to the plugin, offering high-quality support, providing ongoing updates, and granting access to premium features for a recurring fee.
3. **License Keys and Activation:** This prevents unauthorized use of premium features and ensures compliance with licensing terms.
4. **Premium Addons or Extensions:** This creates a marketplace for addons or extensions that enhance the functionality of the core plugin, allowing users to purchase individual addons as needed.
## Offering Maintenance and Support Services
Similar to [WordPress support services,](https://www.elegantthemes.com/blog/wordpress/best-wordpress-maintenance-support-services) a huge opportunity to generate ongoing income is with maintenance and support services. Website owners want their sites to run smoothly without disruptions. However, they also don't want to take time away from regular business matters to deal with the day-to-day tasks of running a website.
Maintenance can entail managing WordPress updates, monitoring for security breaches, theme and plugin updates, hosting management, CDN setup, and offering other types of support, giving you a reliable way to generate income with WordPress.
A successful website requires consistent maintenance. Have you tried any of these maintenance services, and what was your experience like?
### Setting up
For ease, you'll want to use a site management plugin like [InfiniteWP](https://www.wpexplorer.com/out/infinitewp), [MainWP](https://www.wpexplorer.com/out/mainwp), and [ManageWP](https://www.wpexplorer.com/out/managewp). These plugins authorize you to handle core, plugin, and theme updates. They also monitor site speed, SEO, comments, and even backups, all from one single dashboard. This streamlines maintenance service to your clients without the need to monitor each site individually.
### Automating WordPress Updates and Maintenance Tasks
By automating tasks such as updating core files, making backups, scheduling posts, and optimizing images, you can free up valuable time and reduce the stress and energy involved in manual maintenance.
The best part? There are plugins like [Uncanny Automator](https://automatorplugin.com/) that make the process seamless and efficient.
### Pricing
When creating your service page, consider including multiple price offerings and increasing levels of service. For instance, you could have a basic support service for $100. This package could include uploading a theme and adding the theme's demo content.
Then, you can offer a specific website plugin setup as a $20 upsell. You can also include as a part of a premium setup service bundled with a few other features (like homepage setup, etc.).
## Utilizing Affiliate Marketing within WordPress
Image source: Unsplash.com
Affiliate marketing stands as a proven strategy to build a passive income from a blog. [According to Business Insider](https://www.businessinsider.com/the-affiliate-marketing-report-how-mainstream-publishers-are-turning-performance-based-marketing-into-a-fine-art-2015-11), affiliate programs contribute to 15% of digital marketing revenue. Basically, you include promotional links to products on your website. This will fetch you a commission whenever someone's click-through leads to a sale.
As your network of affiliates grows, so will your earnings potential. However, it would help if you had a reliable and robust plan, such as themes, plugins, and hosting, to truly use affiliate marketing capabilities.
### Theme
Choosing the right WordPress theme is crucial for the success of your affiliate marketing website.
1. [Astra](/blog/astra-wordpress-theme-review/)'s affiliate marketing templates are lightweight and extremely configurable, making them ideal for promoting products and services.
2. [Divi](https://www.elegantthemes.com/gallery/divi/)'s templates make it simple to create landing pages and execute advertising campaigns on Facebook and Google without the need for a page builder.
3. [Neve](https://themeisle.com/themes/neve/) offers ready-to-import website designs for a number of business fields. It is performance-optimized, resulting in fast speeds and a pleasant browsing experience.
4. [OceanWP](https://wordpress.org/themes/oceanwp/) features a 1-click demo content importer and dozens of pre-designed demo sites. It seamlessly integrates with drag-and-drop page builders like [Elementor](https://www.wpbeginner.com/refer/elementor-pro/). This means you can tailor any demo site to your exact specifications.
### Plugin
1. [YITH WooCommerce Affiliates](https://wordpress.org/plugins/yith-woocommerce-affiliates/): this plugin is great for eCommerce businesses, offering a user-friendly yet powerful affiliate management tool.
2. [Ultimate Affiliate Pro](https://codecanyon.net/item/ultimate-affiliate-pro-wordpress-plugin/16527729): has advanced features - like custom rewards and affiliate slugs - that give users a personalized experience.
### Hosting
1. [Siteground](https://world.siteground.com/) is a standard option among affiliates. With Siteground, you'll be getting updated SuperCacher, PHP, and other innovative protocols like HTTP/2 and QUIC to guarantee a fast loading time for your affiliate website.
2. [WPX](https://kb.wpx.net/) has a great Content Delivery Network (CDN) with 26 Global Edge Locations, ensuring quick load times for your affiliate site. Additionally, WPX allows you to evaluate or test your website before its launch.
3. [Hostinger](https://www.hostinger.com/) has great features, such as unlimited bandwidth, that help your site thrive. With servers and data centers located in Asia, the United States, and the UK, they ensure stable and swift loading times for your affiliate site. Swift load times are keys to success in affiliate programs.
### Tips for Successful Affiliate Marketing to Build a Passive Income Stream
Here are some tips for getting started with affiliate marketing on WordPress.
1. Like display ads, you won't profit from an affiliate program if you lack an audience. Build out your readership with excellent content before placing affiliate links.
2. Promote products within your niche expertise. You don't need to alter your content to fit your monetization plan - there's likely an affiliate marketing program within your blogging topic.
3. It's essential to track how visitors engage with your site to know which affiliate products generate the most clicks. This data helps you make improvements to your website that result in more revenue. You can also use the metrics to negotiate higher payouts with partner companies.
4. Follow the rules for your affiliate programs. Always disclose in your posts when your links are affiliate links.
## Building Memberships and Subscription Sites
To build a passive income on a month-to-month basis, running a membership site is one of the most promising ways. It offers members access to gated content, which gives you a unique edge - it allows you to appeal to a specific subset of your audience.
Interested in building a membership site but not sure where to begin? Here are a few indispensable tools you can use to make your membership site into a money-making machine.
Image source: Unsplash.com
### The Best Tools and plugins for Creating Membership Sites
**1. [MemberPress](/blog/memberpress-review/)**: This plugin tracks and manages your site's members and subscriptions and offers digital downloads or a content gateway for posts, tags, categories, forums, and more. To get the most out of MemberPress, it's essential to pair it with [best web hosting for membership websites](/memberpress-hosting/). [MemberPress hosting](/memberpress-hosting/) ensures fast loading times, enhanced security, and seamless performance, providing your members with an exceptional user experience.
**2.** [Restrict Content Pro](https://restrictcontentpro.com/): This premium plugin provides a full content management tool. With it, you can create an unlimited number of membership levels, track payments, and offer discounts, all from within the WordPress dashboard.
**3.** [Paid Memberships Pro: ](https://www.paidmembershipspro.com/)This is a plugin for managing professional organizations that have a lot of members. It allows for customizing the registration process, setting up recurring dues, and providing extra value to members of your community. It can also be used to manage an e-learning experience, downloadables, forums, and more.
**4.** [SureMembers](https://suremembers.com/): This is a WordPress plugin that turns any website into a fully functioning membership community. It makes it easy to create membership tiers, charge or offer free access, lock content to specific tiers, and manage every aspect of your membership website.
**5.** [Memberful](https://memberful.com/): This is designed as a membership site software that integrates with all types of websites, like WordPress and Squarespace. You can employ it for content charging, selling subscriptions, and setting up members-only community spaces.
### Strategies for Retaining Members
While there's no one-size-fits-all solution that works in every case, following these tips will make the most of your membership sites, and build a passive income stream successfully.
**Get familiar with your members**.
According to [Copyblogger](http://www.copyblogger.com/membership-site-basics/), it's a good idea to keep tabs on where your members are at regularly. This means holding webinars where you can interact one-on-one with your members. You could even set up a special chatroom with live hours when members can get in touch with you for immediate feedback.
**Include a Forum**
They offer an excellent way for you to find out what your members. This allows members to interact with one another on a regular basis. It builds an environment of collaboration and working together toward a common goal - both of which encourage members to come back time and time again.
**Give Your Members a Challenge**
This applies particularly to membership sites that include an online course component. Many online courses can be completed at your own pace, which is great for those with hectic schedules.
**Solicit (and Use) Feedback**
Ask your members regularly for what they'd like to see more of and pay attention to what they want. If you provide content that resonates with them, your member base can stay on track.
## Content Creation and Monetization
A common monetization strategy is creating and offering premium content. Premium content offers insights beyond standard blog posts. By charging a fee for access to this premium content, you can significantly boost your earnings while rewarding your most dedicated followers.
Image source: Unsplash.com
If you're wondering what content would provide value to readers, consider one of many possible content types:
**1. Exclusive blogs or posts:** These provide extra value in addition to your free posts. They can be entirely new pieces, or they could expand or augment existing posts. Whether they're for other blogs, digital magazines, or content platforms, your expertise can command a premium price.
**2. Printable blog posts:** Another option is converting your longest posts into printable PDFs that users can purchase.
**3. Ebooks:** They require less time and effort to produce compared to other forms of content. They're typically affordable, and you can even repurpose old blog content to create them.
**4. Courses and webinars:** Share your knowledge on a specific topic and use your WordPress site to host and sell these courses.
### Best Practices for Content Monetization to build a Passive Income stream
1. Conduct thorough market research to gain insights into your [target audience](https://aicontentfy.com/en/blog/utilizing-interactive-quizzes-to-engage-target-audience)'s preferences and pain points.
2. Understand Your Metrics. Have a deeper mastery of your industry - what other creators are doing, what brands seek in partnerships, and identify your unique value proposition. This relies heavily on being able to interprete your metrics.
Image source: Unsplash.com
3. Performing a content audit provides insight into the performance of all your content, from your website to your online courses, blog posts, videos, and more. By identifying weak areas, you can improve them.
4. Growing an audience requires some strategy. You might rely on:
- an opt-in and email list to effectively communicate with your members.
- using a content platform that benefits from search engines (e.g., a blog, YouTube channel, Pinterest) to ensure continued discovery.
- forging partnerships with creators or influencers who have different audiences.
## Marketing Your WordPress Passive Income Streams
Having [better rankings](https://www.luigisbox.com/blog/what-is-product-ranking/) for your products and services will get more organic traffic to your website, and possibly more organic sales. So, here are some SEO tips to help.
SEO Tips for Ranking Your Products and Services
**1. Format your content for readers (and search engines)**
Your content's format can make or break your SEO efforts. Formatting affects readability and the user experience, and these influence the time users spend on your page, the engagement levels, and whether they share your content with others.
**2. Utilize internal links**
Using internal links smartly is like laying down a map inside your website that guides your visitors and search engines through your content, creating a network that boosts your SEO while enhancing the user experience. This will distribute your site's authority across different pages and keep your audience engaged with your best content.
Image source: Unsplash.com
**3. Get quality backlinks**
The idea behind backlinks is simple: If many high-authority websites link to your page, it signals to search engines that your page is also a reliable, high-quality source.
It's crucial to ensure that all your important pages have the best chance of being discovered and indexed. Tools like [XML Sitemaps Generator](https://www.xml-sitemaps.com/), [RankMath](https://wordpress.org/plugins/seo-by-rank-math/), or [Yoast](https://yoast.com/) are perfect for creating a sitemap without diving into the technical details.
**4. Improve site load time**
This will keep visitors engaged and reduce bounce rates, positively affecting your SEO rankings. The journey to a faster website begins with optimizing your images.
### Utilizing Social Media to Amplify Your Reach
Social media platforms provide a powerful avenue for content monetization. By engaging with your target audience through platforms like Instagram, Facebook, and Twitter, you can promote your content and drive traffic to your monetization channel. This is how you leverage social media using the following tools and tactics.
**1. Hashtags and Keywords:** Consider incorporating hashtags into your content that are relevant to your product and target audience. However, overusing or using irrelevant hashtags can actually have a negative impact on the discoverability and credibility of your content.
**2. Staying on Top of Algorithm Changes:** Understand the factors that influence the algorithms, such as engagement metrics (comments, likes, shares), which play a big role in deciding your content's visibility. However, it's important to be flexible and adapt to changes as they occur. For example, if a platform changes its algorithm to prioritize longer videos, you may need to adjust your content strategy to include longer-form videos.
**3. Cross-Promoting Across Different Platforms:** This can be effectively done by capitalizing on the unique strengths of each platform. For example, using Instagram, you'll want to focus on visually appealing content, such as images and videos, while short, snappy text updates may be more effective on Twitter.
Image source: Unsplash.com
## Case Studies of Successful WordPress Passive Income Strategies
Numerous businesses built on the WordPress platform have successfully generated revenue in various ways. Here are some real-world examples and insights from WordPress professionals on Passive Income Strategies:
**1. Content Creation and Monetization**: By blogging about programming or software development, *creators* can document their progress, share challenges and solutions, and gather an audience. Through monetization methods with affiliate products, eBooks, courses, and contextual ads, they can turn their expertise into a profitable online business through WordPress. Like the case of [WPBeginner](https://veppa.com/wpbeginner-business-model-growth-story/), earning 100k $ per year.
**2. Developing Plugins:** From creating and monetizing small plugins while enhancing them with additional features, creators can diversify their income streams. Vipin Sahu, founder of [Webkul Software](https://store.webkul.com/), started by selling small social plugins for Joomla and then progressed to providing plugins for several e-commerce platforms. When you build plugin projects, offer paid versions for those that are popular and include features that can be monetized.
**3. Developing and Selling WordPress Themes:** [Selling themes](https://mixergy.com/interviews/andy-miller-rockettheme-interview/) can be a way to build a passive income for developers or grow bigger and turn into a profitable business. [Rocket Theme](https://rockettheme.com/) offered themes for WordPress and other platforms. They grew successfully by utilizing various strategies like Google AdWords and affiliate systems. In addition, they were also generating tutorials and related content, dedicated web pages for demos, and documentation for themes. They have blog content and some plugin reviews also.
## Conclusion
To build a passive income stream with WordPress, it is important to figure out what your targeted audience truly wants. With this, you can utilize WordPress' many ecosystems of plugins, themes, and tools to create multiple revenue streams.
By implementing these strategies and continually refining your approach, you can make an income stream that gets better over time. Do you have any more strategies to earn money online using WordPress?
---
## A More Streamlined Support Experience for Faster Fixes
- URL: https://levamo.com/blog/a-more-streamlined-support-experience-for-faster-fixes/
- Category: news
- Author: The Levamo Team
- Published: 2024-05-08
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Grant temporary dashboard access to support for faster issue resolution.
Say goodbye to lengthy troubleshooting! We've introduced a feature that allows you to grant temporary access to your dashboard directly to our support team. This enables faster issue diagnosis and resolution for problems affecting your websites or dashboard.
## Key Benefits
- **Faster Resolutions**: Our support team can diagnose issues directly, leading to quicker fixes.
- **Improved Accuracy**: Access to relevant information enables more precise diagnosis.
- **Simplified Communication**: No need to explain technical details. The team can observe the issue themselves.
## How It Works
To grant our support team access to your Levamo dashboard:
1. Log in to your Levamo dashboard and click the "Get Help" button.
2. From the dropdown menu, select "Support Access."
3. Click "Approve Levamo access" to grant temporary access.
## Built-in Security Limitations
- The support team can only view your dashboard, not perform sensitive actions like adding users or modifying billing.
- Access expires automatically after 14 days.
- You can revoke access anytime through the "Support Access" menu.
## Learn More
For detailed instructions, visit the Knowledge Base article: "How to Give Dashboard Access to Levamo's Support Team" at [support.levamo.com](https://support.levamo.com).
---
## WordPress Development Hacks: Speed Up Your Workflow in 2025
- URL: https://levamo.com/blog/wordpress-development-hacks/
- Category: wordpress
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Speed up WordPress development in 2025 with these workflow hacks.
WordPress continues to dominate as *the* CMS to craft diverse online experiences, from online stores and hobby blogs to scalable enterprise websites.
Launched over two decades ago, WordPress still holds its crown as the top content management system. This is largely thanks to its flexible, open-source nature. It allows for the creation of custom websites built on its foundation.
Despite its robustness, WordPress can sometimes pose challenges, primarily due to its complex and continuously evolving codebase, shaped by numerous updates and iterations over the years.
However, this complexity doesn't have to make your WordPress development process chaotic. Instead, it presents a unique opportunity to streamline your approach and distinguish yourself by organizing and optimizing your workflow.
Keep reading to arm yourself with practical tips and essential tools for developing WordPress sites more efficiently. But first, let's delve into why it's crucial to invest in speeding up your development process.
## The Value of Streamlining Development Workflow
Streamlining your WordPress development workflow goes beyond just saving time. It enhances the quality and consistency of your work while reducing stress and redundancy in your processes.
Efficient coding practices enable WordPress developers to manage more projects of greater complexity without sacrificing quality. This is especially crucial for businesses, big or small, whose operational success depends heavily on their website presence. Examples include online marketplaces, large-scale publishers, educational platforms, and community-driven sites.
Moreover, by refining your workflow with these techniques, you will also set up your coding environment to quickly adapt to changes in project requirements, WordPress updates, or emerging [security](/blog/how-to-fix-https-not-secure-message-in-chrome/) challenges.
Take a look at the tangible benefits of a streamlined workflow for you and your organization:
- **Increased Productivity:** Streamlined workflows minimize repetitive tasks and reduce time spent on project setup, enabling you to focus more on unique aspects of each project.
- **Enhanced Quality:** With more efficient workflows, you can allocate additional time to refine and test your work, improving the overall quality and performance of the code.
- **Reduced Overhead:** Efficient workflows incorporate automation tools and templates, which decrease the amount of manual work and lower the likelihood of human errors. This, in turn, saves costs related to debugging and lengthy problem-solving sessions.
- **Faster Time to Market:** By reducing the cycle time from development to deployment, you can launch features faster.
- **Better Adaptability:** Streamlined processes make it easier to integrate new tools or practices, allowing you to stay up-to-date with the latest industry standards.
Together, these benefits make for a more agile, responsive, and efficient WordPress development environment that fosters high performance and reliability in any project.
Now, let’s dive right into the expert hacks that will help you with your [WordPress Speed Optimization](/blog/wordpress-speed-optimization/) development workflow.
**Also Read:** [Fastest WordPress Hosting](/blog/fastest-wordpress-hosting/)
## Pro Hacks for Speeding Up WordPress Development
Optimizing your WordPress development workflow essentially boils down to selecting the right tools and tactics to minimize redundant effort and maximize efficiency.
Here are the top seven hacks that will enable you to speed up your development process.
### 1. Choosing the Right Tools and Environment
Selecting the appropriate tools and setting up the right environment are foundational steps in optimizing your WordPress development workflow. Let’s take a detailed look at these components.
#### Local Development Environments
Tools like Docker and Vagrant are great for creating isolated, reproducible development environments. Docker containers package up code and dependencies together. This makes it straightforward to share among team members or deploy into different stages of development.
Vagrant offers a more traditional virtual machine environment. However, it includes configuration scripts that automate the setup of your operating system and software.
Local development environment workflow
#### Integrated Development Environments (IDEs)
A good IDE can significantly enhance your productivity. As you likely know, Visual Studio Code (VS Code) is widely favored for its lightweight nature, extensive library of extensions, and strong community support.
It features extensions specifically for WordPress development, like IntelliSense for PHP, which boosts productivity by allowing smart completions. On the other hand, PHPStorm offers deep code analysis and error prevention. It also provides coding assistance and supports all PHP tools and major UI frameworks.
#### Version Control Systems
Integrating a version control system like Git is crucial not just for collaboration but also for maintaining a clear history of changes. It enables the safe exploration of new features through branching.
Git allows teams to work concurrently on different features without interference, merge changes smoothly, and revert to previous states if something goes wrong. We'll talk more about version control in the last tip.
#### Configuration Management Tools
Tools like Ansible, Chef, and Puppet can automate the setup of your development environments, ensuring consistency across multiple setups and reducing manual setup errors. This is particularly valuable in larger teams where environment parity is crucial.
Overall, these tools and environments not only streamline the development process but also ensure that the applications you build are robust and reliable from the start, reflecting the high standards expected in professional WordPress development.
### 2. Leveraging Code Generators and Starter Themes
A powerful strategy to accelerate WordPress development is having a solid foundation from which to build. WordPress offers a variety of starter themes that serve as a great starting point for kickstarting development.
In essence, a starter theme serves as a base template for creating your own themes. Underscores (_s), for instance, is a popular choice that provides clean, well-commented, and minimalistic HTML5 templates that are ready to be extended. Another example is Sage, which includes a modern build system and a structured approach to theme development using contemporary tools like webpack, Babel, and Bootstrap.
Leveraging frameworks within these themes can dramatically speed up development. For example, themes built on the Genesis framework come with built-in SEO settings and security features, and are highly customizable, reducing the need for extensive coding.
WordPress Genesis Framework
Furthermore, tools like WP-CLI or Yeoman offer generator capabilities that can scaffold out a new theme or plugin. They provide basic structures and files that adhere to WordPress standards. This automates the mundane initial setup process, allowing developers to move directly to feature development.
Ideally, both code generators and starter themes should allow for easy customization and scalability. The idea is to use these tools to create a base that is both versatile and adaptable. This base should be capable of evolving as project requirements grow.
These themes are invaluable for both novice and expert developers. They simplify the initial stages of development and ensure that projects start with a codebase that is optimized, secure, and aligned with the best practices of WordPress development.
### 3. Mastering Keyboard Shortcuts
Keyboard shortcuts are quite literally shortcuts to a faster development process. By reducing reliance on mouse clicks, you can execute commands and navigate files much faster, significantly cutting down on coding time.
Here are some essential shortcuts you should know:
- **General IDE Shortcuts:** Familiarize yourself with shortcuts for common IDE functions like opening, closing, and switching between files (Ctrl + Tab), searching within files (Ctrl + F), and saving files (Ctrl + S). These are universally helpful across most text editors and IDEs.
- **Code Navigation and Manipulation:** Learn shortcuts for quickly moving through code (Ctrl + Arrow Keys), selecting blocks of code (Shift + Arrow Keys), and duplicating or deleting lines (Ctrl + D for duplicate, Ctrl + X for cut).
- **Refactoring and Code Formatting:** Utilize shortcuts for refactoring code like renaming variables (Shift + F6 in many IDEs) and reformatting code to adhere to standards (Ctrl + Alt + L in PHPStorm).
- **Debugging:** Debugging shortcuts, such as setting breakpoints (Ctrl + F8) or stepping through code (F10 for step over and F11 for step into), can drastically improve efficiency when diagnosing issues.
- **Custom Shortcuts:** Most IDEs allow customization of shortcuts. Tailor them to fit your workflow for the functions you use most frequently.
Incorporating these shortcuts into daily practice not only enhances productivity but also fosters a more fluid development experience.
### 4. Using Development Plugins
WordPress being WordPress, you can’t miss enhancing your development process through various plugins with useful capabilities that aid in things like debugging, testing, and optimizing performance.
Consider these plugins:
- **Debugging Plugins:** Plugins like Query Monitor or Debug Bar are useful for debugging. They provide insights into database queries, PHP errors, hooks and actions, conditionals, HTTP requests, redirects, etc., allowing you to pinpoint issues quickly.
- **Performance Testing Plugins:** Tools such as P3 (Plugin Performance Profiler) analyze the impact of each plugin on the website’s performance, helping you as a developer to make informed decisions about which plugins to keep.
- **Security Plugins:** Never treat security as an afterthought. Plugins like Wordfence or Solid Security provide robust out-of-the-box security features to protect your site from attacks and vulnerabilities.
- **SEO Plugins:** [Search engine optimization (SEO)](/blog/lite-speed-hosting-benefits/) is vital for any site's visibility to its audiences. Plugins like Yoast SEO offer comprehensive tools to optimize your site, from generating sitemaps to providing real-time content analysis.
Yoast SEO plugin real-time content analysis
Adopting these plugins not only streamlines development but also ensures a higher standard of quality and security in the final product.
### 5. Automating Repetitive Tasks
Automation almost always has a pivotal role to play when making any workflow (from development to marketing) more efficient.
Speaking of WordPress development, here are a few effective ways to automate repetitive tasks:
- **Task Runners:** Use Gulp or Grunt for task automation. These tools can automate many routine tasks such as minifying CSS and JavaScript, compiling SCSS or LESS, and optimizing images, which are essential for production-ready websites.
- **Build Tools:** Webpack can be used to bundle JavaScript files and other assets. It compiles all resources, including images and fonts, ensuring that everything is minified and optimized.
- **CSS Preprocessors:** Tools like Sass or Less help in writing maintainable and scalable CSS. By using these preprocessors, you can automate the generation of CSS files from more functional and feature-rich syntaxes.
- **Code Linters and Formatters:** Automate code quality checks with tools like ESLint for JavaScript or PHP_CodeSniffer for PHP. These tools can automatically flag syntax errors, enforce coding standards, and even fix code style issues on the fly.
- **Automated Testing:** Implement automated testing with plugins like PHPUnit for PHP unit tests or WP Mock for mocking WordPress functions in tests. These tests run automatically and validate that your code works as expected before deployment.
Integrating these automation tools into your development workflow will reduce manual effort and increase the consistency of your code.
### 6. Making Use of Code Snippets
[Code snippets](/blog/add-code-snippets-in-wordpress/) are reusable pieces of code that can significantly speed up development by reducing redundancy and enhancing consistency across projects. Here’s how you can effectively utilize code snippets in WordPress development:
- **Snippet Management Tools:** Utilize tools like GitHub Gist or Bitbucket Snippets to store and manage your snippets. These platforms allow you to categorize, share, and maintain snippets, making them accessible from anywhere.
- **Integrated Snippet Features in IDEs:** Most modern IDEs like Visual Studio Code or PHPStorm have built-in snippet management features. You can create, store, and insert frequently used code snippets with keyboard shortcuts, streamlining your coding process.
- **Custom Snippet Libraries:** Build your own snippet libraries tailored to the specific needs of your projects. This can include custom WordPress hooks, theme-specific functions, or frequently used CSS patterns.
- **Community Resources:** Dig up community-contributed snippets from forums, developer communities, and [dedicated snippet websites](https://skillcrush.com/blog/find-free-pre-written-code-snippets/). These resources can be invaluable for solving common problems or learning new techniques.
Put simply, by using reusable snippets, you can shift your focus to the unique aspects of your projects rather than rewriting common code.
### 7. Version Control
You’re familiar with Git, and as touched upon in the first tip, version control systems (VCS) like Git play a critical role in every phase of the development process:
- **Tracking Changes:** VCS like Git allow developers to keep a complete history of all changes made to the codebase. This makes it easier to identify when and where changes were made, facilitating troubleshooting and version tracking.
- **Collaboration:** With VCS, multiple developers can work on the same project simultaneously without overwriting each other's work. Branching features enable developers to experiment with new features without affecting the main codebase.
- **Deployment and Rollback:** Version control systems streamline the deployment process to staging and production environments. If issues arise, developers can quickly roll back to a previous version, ensuring stability and continuous service availability.
- **Integration and Automation:** VCS can integrate with other tools like continuous integration/continuous deployment (CI/CD) systems, automating testing and deployment tasks, further enhancing workflow efficiency.
Continuous integration and continuous deployment systems
And so, using Version Control Systems (VCS) is not just a best practice. It is a crucial element in reducing errors, streamlining teamwork, and maintaining a high-quality codebase in WordPress development projects.
Also Read: [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
## Staying Up-to-Date with Latest Development Practices
Working in tech is living life in the fast lane. Tools and best practices can become obsolete in a matter of months. Thus, as a WordPress professional, keeping tabs on the [WordPress codex](https://codex.wordpress.org/Main_Page) and ever-evolving developer resources is crucial to staying competitive.
Here are a few ways to keep abreast of the latest in WordPress development:
- **Follow WordPress Core Updates:** Regularly updating your knowledge with the latest WordPress core updates ensures that you are utilizing new features and improvements effectively.
- **Engage with the Community:** Participate in WordPress forums, attend WordCamps, and engage with other developers through social media or Slack/Discord channels dedicated to WordPress development.
- **Educational Resources:** Use online learning platforms like Coursera or LinkedIn Learning, which offer short courses on the latest WordPress development techniques.
- **Read Developer Blogs and News:** Follow blogs by prominent WordPress developers and platforms like WPBeginner, Smashing Magazine, and the official WordPress.org [blog](/blog/how-to-start-a-successful-blog/) to stay informed about new tools, plugins, and coding standards.
Understandably, doing all this means going the extra mile. But that’s how you continually refine your skills and ensure your dev practices are aligned with industry standards and the latest technologies.
## Common Challenges and How to Overcome Them
Implementing all these workflow acceleration hacks and plugins comes with a few hiccups. Here’s how to tackle some common hurdles:
- **Dependency Management:** Ensure all tools and plugins are compatible with each other to avoid conflicts. Use dependency management solutions like Composer for PHP.
- **Overhead from Tools:** Evaluate the performance impact of each tool. Disable or optimize tools that slow down the development environment.
- **Learning Curve:** Allocate time for team training on new tools to ensure everyone is proficient and can fully leverage their capabilities.
- **Plugin and Theme Conflicts:** Test new plugins and themes in a [staging environment](/blog/how-wordpress-sandboxes-help-developers-test/) before going live. Keep backups and use version control to revert changes if needed.
- **Keeping Up with Updates:** Automate updates where possible and use management tools like ManageWP to handle multiple sites.
- **Continuous Integration/Continuous Deployment (CI/CD):** Establish CI/CD pipelines to automate the building, testing, and deployment processes, significantly reducing manual intervention and speeding up development cycles.
- **Streamlined Code Reviews:** Use tools like GitHub for efficient code reviews, which help in identifying issues early and speeding up the development process by incorporating feedback quickly.
- **Effective Project Management:** Adopt agile methodologies and use [project management tools](https://thedigitalprojectmanager.com/tools/best-project-management-tools-for-software-development/) to keep track of tasks and deadlines, ensuring efficient workflow and timely project completion.
By proactively addressing these challenges, you can set your project workflows up for speed and efficacy.
## Parting Thoughts and Next Steps
The need for speed in high-stakes WordPress development cycles is undeniable. By following this structured guide, you can achieve a leaner and more professional development process.
Efficiency in WordPress development isn't just about speed. It's about creating a workflow that is both scalable and sustainable. This approach minimizes errors and maximizes resource utilization.
Integrating these nifty tools, practices, and hacks into your development process significantly enhances your productivity and project turnaround times. This ensures that your WordPress sites are not only shipped faster but are also fully functional and secure.
Are you looking for the [best managed WordPress hosting](/managed-wordpress-hosting/) or [WooCommerce managed hosting](/managed-woocommerce-hosting/)? A service that takes care of your website’s updates, backups, security, and various other aspects, thereby speeding up your development workflow.
---
## WooCommerce Fortress: The 2025 Security Checklist
- URL: https://levamo.com/blog/woocommerce-security-checklist/
- Category: ecommerce
- Author: Ochai Emmanuel
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Lock down your WooCommerce store! Use this 2025 security checklist.
Managing a WooCommerce store can be challenging. While you must perform tasks like adding and promoting your products, security is also paramount. Because WooCommerce stores are among the most popular in the industry, they regularly face these risks.
These sites face brute force attacks, malware, cross-site scripting, and [phishing](/blog/phishing-campaign-targeting-woocommerce-stores/). However, since WooCommerce has taken measures to protect websites, store owners must also do their part. This way, they can protect their information and their customers.
This post explores the importance of maintaining safety in your WooCommerce store. It also covers the common risks that these sites face and ways of dealing with them in 2024. Read on to understand how to improve and secure your store.
A person uses a smartphone to browse an e-commerce store.
## Understanding WooCommerce and its Vulnerabilities
WooCommerce is an open-source platform powering over 3.9 million stores. It is one of the most customizable e-commerce platforms you’ll find. While it is built on WordPress, it helps businesses sell their products online how they want to.
The platform initially sold commercial themes before turning to full-time commerce. At that point, it became the largest commerce platform on the Internet in terms of growth. While the platform has continued to grow, there are also increasing risks and dangers, most of which relate to safety.
This online commerce platform faces serious safety issues. These issues sometimes result in breaches and forced access, which could cause the loss of information and affect your company’s reputation.
So, here are the most common vulnerabilities affecting the platform in 2024:
### Vulnerable Themes and Plugins
Compatibility issues come up when you use unsupported or outdated themes and plugins on your store. This problem sometimes results in a bad user experience. Using these outdated components could really be a big problem since it affects your site’s functionality.
Other problems include errors and slower load, which may frustrate site visitors. As a result, fewer people will visit your store, which could affect your business in the long term. Serious risk management helps to deal with these issues.
### Brute Force Attacks
In the case of brute force attacks, hackers typically attempt to get unauthorized access to your account, network, or system. The most common method they use is trying multiple username and password combinations until they find one that gives them access.
These types of attacks mostly capitalize on easy, weak, and guessable passwords. If the hacker succeeds, they could steal your data, disrupt your system, mess with your finances, and damage your brand’s reputation.
### Out-of-Date WordPress and WooCommerce Versions
Using out-of-date WooCommerce and WordPress versions can cause serious problems for your store. For instance, it can cause the site to load slowly, affecting user experience and sometimes making it incompatible with other themes and plugins.
While this affects how your site runs, it damages your reputation and causes you to lose potential customers. Using these versions exposes your store’s and customers’ information to hackers.
A box on a laptop computer with the inscription “Online shopping.”
### SQL Injections
Structured Query Language (SQL) injections happen when hackers target weaknesses in web applications to make changes in the databases. In this case, hackers intentionally add dangerous SQL code to your site’s database.
This code then allows hackers to see, change, or remove sensitive information. To stop these types of attacks, you’ll need to use safe codes and limited queries to differentiate SQL commands from user inputs. This is one of the most common problems in 2024.
### Cross-Site Scripting (XSS)
For [cross-site scripting (XSS)](https://portswigger.net/web-security/cross-site-scripting), hackers add dangerous scripts to your online store’s pages. When users view these pages, the scripts hijack their accounts or collect their data. There are three types of XSS.
Stored XSS attacks happen when the hacker places the dangerous script on your site permanently. They usually add these scripts to forum comments, and they execute as soon as a user views them.
Reflected XSS is another type of cross-site scripting. The script is usually plated in an email, a URL, or other temporary information on the site. Once a user clicks the link, they will execute the script.
### Distributed Denial of Service (DDoS) Attacks
In this case, hackers or bots send tons of fake requests to your site, overwhelm your server, and push it to full capacity. The goal of these [attacks](/blog/preventing-ddos-attacks/) is to stop your server from responding to authentic requests and break down your site in extreme cases.
Sometimes, it may only temporarily disrupt your activities or make your site inaccessible. Filtering incoming traffic is an excellent way to prevent these attacks. Alternatively, you can use a [content delivery network (CDN)](/blog/cdn-for-ecommerce/) to avoid server congestion.
## WooCommerce Security Checklist Explained
After understanding the type of risks your WooCommerce store is exposed to, it is time to secure it. Well, several safety measures can help protect your site. We’ve added them to a checklist to help you implement them better.
### 1. Choose a Safe E-Commerce Platform and Web Host
Before you start a store, you must make the right decisions, like choosing a safe e-commerce platform and [fully managed WordPress hosting](/managed-wordpress-hosting/). These platforms offer everything you need to run an online business, such as product listings and checkouts. On the other hand, web hosts store your database, site files, and content, making them available to users when they visit.
WooCommerce remains one of the most popular and secure e-commerce platforms. You can start your journey by installing the plugin on your WordPress website. Alternatively, some web hosts install the plugin beforehand to make your site a fortress.
A smartphone displays a padlock icon with the word “Security” and a toggle button.
### 2. Get a Valid SSL Certificate
If your website accepts payments online, a [Secure Sockets Layer (SSL) certificate](/blog/ssl-website-security/) is one of the first things you should install. This certificate encrypts the information your customers send to your website and also authenticates your site’s information.
Essentially, it protects sensitive information like credit card info as well as addresses, making it hard for hackers to steal. An SSL also switches your URL from HTTP to HTTPS. Not to worry, web hosts usually add these certificates to their hosting plans but you can always buy another to turn your site into a fortress.
### 3. Get Secure and Safe Versions of Plugins and Themes
Sometimes, people go for nulled versions of plugins and themes. Since these versions are usually cheaper or free, many store owners install them on their sites. However, there are big disadvantages to using these pirated copies.
First, they are not always supported by the site and do not even get regularly updated. As a result, they are not compatible with WordPress as well as other plugins. If you’re not careful, they also carry malware, which is dangerous to your site. That is why you must use original plugins and themes.
### 4. Create a Secure Gateway for Payment
Websites that accept online payments must have gateways that enable and authorize transactions. For sites like WooCommerce stores, top payment gateways provide excellent security and support a smooth transaction process for customers.
When choosing payment gateways, always pay attention to how they deal with important information like credit card information. For example, some options offer extra safety features like advanced protection against fraud. [WooPayments](https://woocommerce.com/payments) is an incredible choice to consider.
### 5. Go for the Latest PHP Version
Most of the WordPress core is written in PHP. Therefore, you must install the latest PHP version to protect your site adequately. This is quite similar to updating your themes and plugins for the latest features.
You can update your version of PHP in the host settings. Alternatively, you can request an update from your hosting provider. But overall, this keeps your site safe from bugs and other vulnerabilities.
### 6. Keep Everything Updated on Your Site
WordPress, themes, and plugin updates do not always include newer features. Sometimes, they only fix some bugs and other issues that hackers may exploit. That is why you must always keep everything on your site up-to-date.
Luckily, some plugins like [Jetpack](https://jetpack.com/) help with automatic updates to secure your website.
A person registers their fingerprint while the word “Security” floats ahead.
### 7. Prevent Spam on Your Site
Usually, the most common type of spam you’ll find in your online stores is spam comments and contact form entries. These typically contain links to harmful software and sites that may pose further risks. Sometimes, spammers also use these contact forms to carry out SQL injections.
This is a big problem because customers may consider your store fraudulent when there is massive spam content. To deal with this, you may review all forms and comments by yourself. But this can be a lot of work, so some [anti-spam plugins like Akismet](https://www.wpwebify.com/wordpress-plugins/anti-spam-plugins-for-wordpress/) help with risk management to deal with such problems.
### 8. Install an Application Firewall
One of the most efficient ways to secure your site is by installing a web application firewall (WAF). The WAF keeps track of all incoming web traffic, blocking any suspicious IP addresses from accessing it. It is generally a great way to provide protection against threats.
You can sometimes get a web application firewall from your web host. Besides that, you can use other third-party options. An excellent firewall can turn your site into a fortress. So, this is important in the checklist.
### 9. Prevent Brute Force Attacks
Brute force attacks happen when hackers break into your site. In most cases, hackers try out different combinations of usernames and passwords until they get access to your site. So, you must also protect your store against these kinds of attacks.
These attacks mainly involve hackers guessing your passwords and usernames. The most effective way to prevent these attacks is to use strong passwords. You can also install plugins that protect your site against brute-force attacks.
### 10. Use Activity Logs
While activity logs do not necessarily protect your WooCommerce store against threats, they help in some regard. For instance, it can help you watch out for certain actions on your site. As a result, you can use them to identify suspicious activity and the causes of vulnerabilities.
Tools like Jetpack offer logs that record your activity for specific periods. Through this, you can view any kind of activity that takes place on your site. You can also identify the people who perform each action. So, it is an excellent item on the checklist.
A white computer keyboard with a cart button and order button beside it.
## Top Recommended Security Plugins for WooCommerce
Are you looking for the best security plugins for your WooCommerce store? You’re in the right direction because these plugins are one of the most effective ways of securing your store. They offer multiple features such as malware scans, backups, firewalls, etc.
So, here are the top options for your store:
### 1. Jetpack
[Jetpack](https://wordpress.org/plugins/jetpack/) is arguably the best security plugin for your WooCommerce store. Being integrated with the e-commerce platform, this resource allows you to secure your site from threats. It scans your site every day and reports back on any activity.
It also has a real-time backup feature that allows you to restore your site info in the case of data loss. The plugin pays much attention to your site’s performance to enhance the experience for your customers.
Its features include:
- Constant site monitoring to determine downtimes when they happen.
- Blocking malicious IP addresses automatically.
- Every day, scanning for suspicious activities and effective threat prevention.
- Two-factor authentication to improve safety.
- Turning on and off automatic updates of other plugins.
- Real-time backing up of site data as well as effective restoring.
### 2. Defender Security
While [Defender Security](https://wordpress.org/plugins/defender-security/) is a pretty new plugin for WooCommerce stores, it has gotten popular recently. You can easily install and configure this on your site with a few clicks. It provides protection by scanning for malicious threats, providing a firewall, and securing your login feature.
Besides that, it protects your store against brute force attacks, SQL injections, and cross-site scripting. This plugin offers several important features for free. Since it pays attention to simplicity, you will not need to go through complex settings to protect your site.
Here are the most essential features of this plugin:
- Brute-force attack prevention.
- Frequent scans for harmful material and other threats.
- Two-factor authentication.
- Login screen masking.
- Firewall and IP manager.
- Recommendations for core and server updates.
- Antivirus scans.
### 3. Wordfence
[Wordfence](https://wordpress.org/plugins/wordfence/) is one of the most efficient security plugins for WooCommerce stores and other WordPress sites. It secures your site with a malware-scanning feature and an endpoint firewall. All these help to protect all the aspects of your store.
One feature that makes Wordfence so effective is its ability to scan WordPress core files, themes, and other plugins. This way, it easily picks out any threats that may be present.
Here are the features you’ll find most interesting on Wordfence:
- A web application firewall that runs at the endpoint and integrates well with your store.
- The standard scanner that secures your content.
- Frequent monitoring that identifies possible problems.
- A two-factor authentication feature for brute-force entry prevention.
- It quickly recovers and repairs files after a hack.
- Blocking specific suspicious IP addresses.

### 4. All-In-One Security
This is a popular WordPress plugin you can use on your WooCommerce store. [All-In-One Security](https://wordpress.org/plugins/all-in-one-wp-security-and-firewall/) protects your site from multiple vulnerabilities, including brute-force attacks, bots, and malicious material.
Its firewall also adds an additional defense layer to your store, while the plugin also secures your login feature. So, here are the plugin’s features you should note:
- The login lockdown feature protects your site against brute-force attacks.
- Its powerful firewall provides extra defense for your store.
- Filters suspicious IP addresses.
- You can use it to pick out unauthorized file changes.
- Allows you to back up your files and restore them conveniently.
- You can use it to enable or disable auto-updates on other plugins.
## Quick Tips and Tricks for Better WooCommerce Security
Besides following the ideas in the security checklist, there are several other important ways you can secure your store effectively. For example, you may find a few cybersecurity tips helpful. While you may find them simple, they help protect your site to a high degree.
So, here are some quick tips and tricks to improve your WooCommerce defense and make it a fortress:
### 1. Use Strong Passwords
Simple and basic passwords are the reasons for many safety breaches. Therefore, to secure your site, you must always use strong passwords. Besides offering protection from phishing, strong passwords also secure you from brute-force attacks.
Although you may sometimes assume that your passwords are not easily accessible, some complex hacking systems can override them. WooCommerce [provides some password requirements](https://woocommerce.com/document/password-protected-categories-store/) that you’d find useful.
### 2. Backup Your Data Regularly
Even after securing your WooCommerce store using different features, backups are sometimes a lifesaver. In fact, consider creating multiple backups of your information. You cannot always tell when newer issues that threaten your data come up, and you wouldn’t want to be unprepared if this happens.
### 3. Place Limits on Login Attempts
Hackers are getting better at brute-force hacks in 2024. These hacks usually involve the hacker or bot testing multiple word or number combinations to find the password and access an account. With artificial intelligence and machine learning, they can break weaker passwords in no time.
That is why you must limit login attempts from specific IP addresses on your site. This way, you can deal with this issue. You can also add an authentication feature to back it up as well.
### 4. Geoblocking Is Sometimes Helpful
Bots and hackers sometimes come from one location. So, you should consider blocking traffic from those locations entirely. Of course, your analytics should show where your expected traffic comes from.
If you notice dramatic traffic levels from a suspicious location, that may be the work of bots. In this case, you can block entire countries from accessing your store. Many security plugins offer geoblocking in 2024, so that should not be a problem.

### 5. Mandate Strong Passwords for Users
Accounts on WooCommerce stores are sometimes complex. In some cases, it becomes necessary for you to provide admin access to others. That is why you must mandate strong passwords for anyone with access. You can use a strong password generator to help with risk management.
### 6. Disable Trackbacks and Pingbacks
Trackbacks and pingbacks allow other websites to receive notifications when you publish a new post. While this appears like a pretty helpful feature, it has its disadvantages. For instance, spammers can use this feature to send a lot of spam to your site. Disabling this feature is usually helpful in this case.
## Continuously Securing WooCommerce Sites
Securing your WooCommerce site is not a one-time activity. You’ll need continuous work due to the changing and evolving threats your sites face every day. This is why you must remain alert and add new measures to secure your site more regularly to make it a fortress.
For example, hackers are discovering new ways to break through to your websites each day using threats like brute-force attacks and SQL injections. For this reason, you must also remain on top of the game by putting helpful strategies in place.
Also, there are more security risks to WooCommerce sites through machine learning and artificial intelligence. So, you should also regularly update your site, themes, plugins, and other features. You can also use modern firewalls and strong backup options at all times.

## Conclusion
To run a WooCommerce store successfully, you must pay attention to security. Since these sites are quite popular, they face several risks and threats. Common problems you may face include vulnerable plugins and themes, SQL injections, and brute-force attacks.
However, you can still prevent or deal with these risks by choosing secure web hosts, using application firewalls, and securing your payment gateway. You should also consider going for stronger passwords, data backups, geoblocking, and activity limits.
Having gone through this comprehensive guide, why don’t you go ahead and secure your store? These solid risk management tips will help you make your site a fortress in 2024. Also, learn more about Levamo [managed WooCommerce Hosting](/managed-woocommerce-hosting/).
## FAQ
Do you have more questions? Here are the common answers you need:
### Can Someone hack a WooCommerce website?
Like other websites, WooCommerce sites can be hacked. However, WooCommerce and WordPress have added features that protect your site, data, and content. Also, you can put measures in place to secure the site better.
### Is an SSL necessary for a WooCommerce site?
It is recommended that you secure your WooCommerce site with an SSL to protect the information on your site from unauthorized parties. This is necessary because your WooCommerce site collects sensitive data during transactions, and this data must be protected.
### Is WooCommerce safer than Shopify?
Unlike WooCommerce, Shopify takes care of your defense by itself. Although this practice has advantages, it limits your control over your security. However, deciding which is safer is quite tricky since hackers do not typically discriminate when it comes to the sites to attack. Overall, your setups all matter in this case.
## Frequently Asked Questions

### Can Someone hack a WooCommerce website?
Like other websites, WooCommerce sites can be hacked. However, WooCommerce and WordPress have added features that protect your site, data, and content. Also, you can put measures in place to secure the site better.
### Is an SSL necessary for a WooCommerce site?
It is recommended that you secure your WooCommerce site with an SSL to protect the information on your site from unauthorized parties. This is necessary because your WooCommerce site collects sensitive data during transactions, and this data must be protected.
### Is WooCommerce safer than Shopify?
Unlike WooCommerce, Shopify takes care of your defense by itself. Although this practice has advantages, it limits your control over your security. However, deciding which is safer is quite tricky since hackers do not typically discriminate when it comes to the sites to attack. Overall, your setups all matter in this case.
**References**
- [https://digitalradium.com/wordpress-security-checklist-2024/](https://digitalradium.com/wordpress-security-checklist-2024/)
- [https://www.linkedin.com/pulse/woocomerce-seo-optimization-checklist-2024-muhammad-ansar-iaspf/](https://www.linkedin.com/pulse/woocommerce-seo-optimization-checklist-2024-muhammad-ansar-iaspf/)
- [https://woocomerce.com/posts/woocomerce-security/](https://woocommerce.com/posts/woocommerce-security/)
- [https://woocomerce.com/posts/ecommerce-security/](https://woocommerce.com/posts/ecommerce-security/)
---
## Scaling Success: How Top WooCommerce Stores Stay Fast Under Pressure
- URL: https://levamo.com/blog/woocommerce-scaling-speed-strategies/
- Category: wordpress
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WooCommerce speed secrets revealed: Keep your store fast and boost conversions.
Speed, as the saying goes, kills, but not always, especially for WooCommerce stores, where slow hosting speeds can be deadly to customer traffic. A lack of speed can also be fatal to the bottom line. In its *[Online Retail Performance Report](https://www.akamai.com/newsroom/press-release/akamai-releases-spring-2017-state-of-online-retail-performance-report)*, Akamai found, "A 100-millisecond delay in website load time can hurt conversion rates by 7%." They also found a two-second delay in web page load time increases bounce rates by 103%. Conversely, increasing an "e-commerce website speed by just 0.1 seconds improved conversion rates by 8.4%," says [Adquadrant](https://www.adquadrant.com/why-website-speed-matters-conversions-loyalty-and-google-search-ranking/). So, a barely perceptible difference in time can lead to a substantial change in conversion rates. In terms of website e-commerce speed, every millisecond counts.
Speed is crucial to online shoppers as it significantly impacts their shopping experience. It can also play a vital role in building brand loyalty. Consumers are more likely to be loyal to a site with quick page loads; [Tribes](http://tribes.no/2013/10/28/how-website-speeds-affects-online-sales/) reports that 52% claim that a fast page load is essential for their website loyalty. On a macro level, speed affects search engine rankings, particularly on Google, which emphasizes the importance of speed for visibility and search ranking success. Every customer wants a high-octane shopping experience when buying something online. E-commerce purchases are often impulse buys. The longer someone has to wait for a webpage to load, the more likely their rational brain overrides their impulse buying desire.
WooCommerce sites improve their speed and performance by optimizing their product handling capabilities and selecting the right hosting solution. No one likes to wait for product pages to download. The longer the wait, the higher the chance a customer or potential customer moves onto a competitor's website. Top WooCommerce stores stay fast under pressure by following the methodologies listed below.
## Evaluating Your WooCommerce Store Performance

WooCommerce provides a set of metrics that track order count, average order value, product discounts, top-performing coupons, order status, and customer refunds. These metrics reveal a store's performance, customer behavior, and any underlying marketing strategies that affect on-site customer behavior.
In addition to tracking all these metrics, users must monitor their store's performance during high-traffic periods. Tools like New Relic and Google Analytics can reveal performance bottlenecks and highlight areas primed for improvement.
Data is the backbone of an e-commerce website. Optimizing a site's database queries can improve performance, which enables full-page caching and site speed analysis. Above all else, selecting an exemplary hosting service is paramount. A [fully managed WordPress hosting](/managed-wordpress-hosting/) or specialized WooCommerce hosting service ensures a store's foundations reside on capable servers that can scale as necessary. Plugins like WP-Optimize, which automate the data cleansing process, can ensure database optimization. Diminishing dependencies on external resources, such as scripts and style sheets, helps expedite load times and limits any potential surprises arising from data conflicts.
## Strategic Infrastructure: Hosting & Technologies
WooCommerce sites improve their speed and performance by making smart hosting choices. These fall into two categories: general-purpose web hosting and WooCommerce-specific hosting. The former is suitable for most websites. However, online store owners must consider server performance for things like uptime, fast loading times, and the always-important search engine rankings.
Although many WordPress hosts provide WooCommerce-specific hosting, most only provide some WooCommerce-specific features. They also lack hosting performance and the ability to scale.
This inadequacy stems from the fact that most hosting solutions are traditionally engineered for simpler WordPress sites such as blogs or brochure sites, which can be fully cached to minimize server load and enhance speed - even on less capable servers.
Unlike these static sites, a WooCommerce store cannot cache all its pages due to the dynamic nature of shopping carts and user accounts. Implementing full-page caching could lead to serious issues like users seeing incorrect products in their carts or accessing others' account details due to cached data. This highlights the need for a hosting environment designed specifically for dynamic sites that require robust performance to manage high traffic volumes and simultaneous transactions effectively.
For WooCommerce stores, it is crucial to choose a hosting platform that excels in handling high concurrency and provides optimized caching solutions tailored for e-commerce. Levamo's hosting service addresses these challenges with innovative technologies such as smart purge caching. Our system intelligently purges cached content, such as product pages when stock levels change - whether through customer transactions or updates in the admin dashboard.
Additionally, when a product page is purged, related categories and tag pages are automatically refreshed to ensure your site consistently displays up-to-date product information. This capability leverages LiteSpeed Cache's advanced cache tagging system, which is available exclusively on LiteSpeed Enterprise servers - our server software of choice for Levamo's dynamic plans. This system significantly outperforms other plugins in maintaining the relevance and freshness of related content, offering your customers a seamless and up-to-date browsing experience.
### Well-designed Tech Stacks Ensure Optimal Performance
Beyond hosting, a good tech stack that ensures optimal performance, tight security, and easy scalability should include the following:
- Web Hosting: a WooCommerce-specific hosting provider suitable for dynamic sites, should ensure your store has the resources and support for full eCommerce functionality.
- WordPress: the most recent version provides a strong foundation for WooCommerce.
- WooCommerce: WooCommerce provides the core eCommerce functionality for your store.
- PHP: A recent version of WordPress and WooCommerce server-side programming language will provide optimal performance and security.
- Database: A reliable database management system, such as MySQL, MariaDB, or Percona, will allow your site to store and manage its data.
- Caching: Implementing multiple levels of caching solutions will improve page load times, reduce server load, and help with load balance. But be careful not to fully cache your pages. Use
- Security: Websites should take vigilant cyber security measures, like using SSL certificates, setting up firewalls, and screening for malware.
- SEO: Customers must discover your site through search engines. Optimizing a site for search engines using SEO plugins improves visibility.
- Payment Gateways: Integrate reliable payment gateways to ensure secure and convenient payment options for your customers.
- Shipping Integration: Integrate reliable shipping providers to ensure accurate and efficient shipping options for your customers.
- Email marketing automation: Utilize email marketing tools to automate marketing campaigns and engage with customers.
Combining all these components into a well-designed tech stack will ensure WooCommerce sites improve their speed and performance, which should help them provide their customers with a seamless shopping experience.
### Guides and Checklists
[CRAZY FAST WooCommerce Sites Guide & Checklist](https://drive.google.com/file/d/1T08uHOUPmEGQcJD3nspNw502d66rXPa0/view) contains relevant tips and tools that help you measure your site and server’s performance. The [WordPress Performance Tester](https://wordpress.org/plugins/wpperformancetester/) plugin evaluates your WordPress site's performance by testing server response times and database operational efficiency. It will help you identify areas of potential improvement. The [WordPress Hosting Benchmark tool](https://wordpress.org/plugins/wpbenchmark/) evaluates the performance of your WordPress hosting environment. It conducts a series of tests to measure the response time and capacity of your server, providing insights into how well your hosting handles WordPress-specific tasks. The [Grafana K6 tool](https://k6.io/) simulates real-world website traffic scenarios and specific user behaviors, revealing whether the websites can function properly during traffic spikes.
These tools can uncover performance issues, helping top WooCommerce stores prepare for traffic spikes. They are well suited for dynamic WordPress sites because they provide a thorough evaluation of a site’s performance. One of the highest-performing managed WordPress Hosting services available is [Levamo’s hosting package](/).
## Database Optimization for Peak Performance

Optimizing a database for peak performance can be like a trip to the dentist, something unpleasant at the time but, ultimately, something necessary for long-term health. Although somewhat irritating at the time, that trip has the potential to pay big dividends down the line. So, it is with database optimization. To optimize for peak performance, users should:
- Rewrite complex queries to simplify logic and improve efficiency.
- Avoid N+1 query problems to minimize roundtrips to the database by using joins and batch fetching.
- Evaluate and rearrange the join order to enhance query performance.
- Employ index hints to guide the database engine in selecting appropriate indexes for queries.
- Store frequently run query results in memory to reduce processing overhead.
- Implement efficient locking mechanisms and adjust isolation levels to balance consistency and performance.
- Regularly monitor query performance metrics as well as analyze query plans, and then fine-tune based on collected data.
- Raise index efficiency to speed up data retrieval and reduce disk I/O operations.
- Analyze query patterns to uncover performance bottlenecks.
You significantly enhance a database's performance by following these techniques during peak usage periods. They can go a long way to tackling the rising volume of transactions one can expect from growing websites.
## Robust Caching Solutions
Caching is the process of temporarily storing frequently accessed data in computer memory. It reduces the time and resources necessary to access and process data, improving a system's overall performance and efficiency. A copy of all the web page's components, such as images, text descriptions, or even code scripts, will be stored in the cache. When users browse a webpage they've seen before, the local cached version appears. Proper caching is also essential for WooCommerce sites.
Something similar happens in a database system. Frequently accessed data resides in memory, reducing the need to query the database repeatedly, and substantially reducing data response times.
### WooCommerce’s Caching Systems and Plugins
WooCommerce's caching systems and plugins, OPcache, LiteSpeed Cache, Redis Cache with Object Cache, and Relay Cache, help ensure websites load as quickly as possible. OPcache, built into PHP and storing precompiled script bytecode in shared memory, eliminates the need for PHP to load and parse scripts upon each request, significantly improving performance. LiteSpeed Cache, or LSCache, is a built-in, high-performance dynamic content acceleration feature of the LiteSpeed Web Server. It is like Apache mod_cache but implemented more efficiently.
[Redis Cache with Object Cache Pro and Relay Cache](/blog/key-db-and-redis/) are robust caching solutions. The former uses Redis, a high-performance, in-memory data store with fast reading and writing speeds; the latter is a client-side cache that associates each piece of data with a unique identifier and compares the data on the server with the data in the cache. Both come free of charge in Levamo's Dynamic Plan.
#### Increasing Speed with Smart Purge Technology
Temporarily storing frequently accessed data in a cache can result in the cache getting too large and somewhat unwieldy, which will require constant housekeeping. However, if WooCommerce manages your stock, WooCommerce's "smart purge" technology can keep your listing clean. It removes product pages, related categories, and tag pages from the cache whenever a stock change occurs. This keeps the site's product information consistently updated, reducing the need for constant manual changes. This is one of LiteSpeed's significant advantages. Other plugins need help with this type of purge because they need a similar cache tagging system. [Levamo's ](/)hosting includes Smart Purge technology.
Whenever product details update, Levamo's LScache integration automatically refreshes your content across all platforms, ensuring the site always displays the latest product information. The WooCommerce shop cache keeps all information as fresh as possible. Your customers will always see the most up-to-date product and category information. This mitigates customers' frustration when discovering something they want is out-of-stock. An added benefit: it improves a WooCommerce site's speed and performance.
## Engaging the Power of ElasticSearch

Elasticsearch uses generative AI, specifically Generative AI Retrieval-Augmented Generation (RAG) models that tailor responses to a customer's preferences and needs to enhance its search capabilities, allowing a more personalized and intuitive buying experience. Elasticsearch uses vector search technology that transforms unstructured data into a numeric format. This allows for faster, more relevant search results when compared with traditional keyword searches. It also utilizes semantic search, identifying the query's meaning and context. RAG models are a cutting-edge approach in generative AI that enhances the accuracy and reliability of models by incorporating external knowledge sources to improve the relevance of search results by supplementing the original knowledge base with new information from various sources. RAGs should ensure users receive more accurate and more contextually aware responses.
## Content Delivery Network (CDN) Integration
A [content delivery network (CDN)](/blog/cdn-for-ecommerce/), a network of geographically distributed servers that work in concert to deliver web content to users as quickly and optimally as possible, stores cached copies of content in data centers worldwide. They allow users to access internet content from a server that is physically nearer them. By reducing the distance data and content need to travel, CDNs decrease latency, improving user experiences. They also reduce the stress on origin servers by distributing the traffic load geographically across multiple servers. CDNs play a crucial role in improving website performance. They deliver online content and enhance user experiences by providing faster loading times, reducing bandwidth consumption, and better responding to traffic spikes. The Levamo hosting service comes with a free CDN.
## Efficient Asset Delivery
Efficient asset delivery for websites, the process of optimizing the presentation of digital assets, is another tool that will improve a WooCommerce site's speed and performance. A digital asset management (DAM) system can help store, organize, manage, and deliver these digital assets to customers. This speeds up delivery and reduces the load on a server. For example, CDNs can distribute assets across multiple servers, compress images and videos to reduce their file size, and cache assets to reduce the number of server requests.
## Other Performance Techniques Affecting Speed
According to [Queue-it](https://queue-it.com/blog/ecommerce-website-speed-statistics/), a tenth of a second improvement in mobile site speed increases retail conversions by 8.4%. Speed is a significant factor for eCommerce sites, impacting user experience, conversion rates, brand loyalty, and search engine rankings. Optimizing website speed is essential for eCommerce businesses to remain competitive and achieve their sales goals.
Lazy loading can also help optimize e-commerce websites. It delays the loading of non-critical resources until the site needs them. Images only upload when required in the user's viewport. This significantly reduces the initial page load time, particularly with image-rich product pages.
Insight into AJAX for dynamic content without the wait helps optimize the communication path, which can enhance a user's experience by reducing wait times and improving application responsiveness.
By leveraging techniques such as caching, intelligent caching, asynchronous requests, and traffic management, developers can address challenges related to AJAX-based applications. These strategies help distribute requests efficiently. They prioritize critical requests while also preventing conflicts and managing high request rates. These performance techniques will help WooCommerce sites improve their speed and performance.
## Scalability Testing
Stress testing, which involves testing a website's performance under extreme conditions, is crucial to website maintenance and optimization. Sudden spikes in website traffic could be due to many factors. Regular stress tests can identify any hosting or website weaknesses that impact the all-important user experience. By regularly stress testing a website, e-commerce sites can ensure any unexpected traffic spikes don't derail business and website scaling goes as planned.
Stress testing is essential for eCommerce sites and other websites that experience planned and unplanned spikes in traffic. By determining the projected number of visits and requests made during busy periods, e-commerce sites can anticipate potential loads and make any necessary improvements to prevent performance issues.
By regularly testing a website's performance under extreme conditions, e-commerce sites can ensure that their website can handle any expected traffic that comes their way. Armed with this information, a user can make improvements to prevent any issues from occurring because of unexpected high-traffic periods. Regularly scheduled scalability testing should help improve a WooCommerce site's speed and performance.
### Grafana

Grafana K6, an open-source load testing tool, makes performance testing easy and productive for engineering teams. Optimized for minimal resource consumption, it runs high-load tests like spike, stress, and soak tests. It supports multiple protocols and has a large extension ecosystem.
### WP Performance Tester

WP Performance Tester measures the speed and efficiency of a WordPress website by running a series of tests, such as the time it takes to generate a page, the number of queries per page, and the database size. The tool can compare the performance of different WordPress installations, identify bottlenecks, and reveal areas for optimization. It can track the performance of a website over time. It is a valuable tool for website owners, developers, and administrators who want to ensure their WordPress sites are running at an optimal performance level.
### WordPress Hosting Benchmark

The WordPress Hosting Benchmark performance testing tool measures the performance of different WordPress-specialized hosting services. Originally published in March 2014, the benchmark aimed to perform unbiased, data-driven performance tests to reveal how well a hosting company could handle traffic spikes. The benchmark tests performance on six measurements: price range and plans from different hosting providers, measuring peak performance and consistency over two months. The benchmarks report judges the performance of different WordPress hosting providers, allowing users to choose a web hosting service based on real-world performance information. Benchmarking will also give WooCommerce sites a roadmap that reveals exactly how to improve their speed and performance.
## Conclusion
Every customer wants a high-octane shopping experience when purchasing something online. E-commerce purchases are often impulse purchases, and the longer someone has to wait for a webpage to load, the more likely their rational brain overrides their impulse buying.
Implementing lazy loading, leveraging browser caching, using a lightweight WooCommerce theme, minimizing JavaScript and CSS files, optimizing your database, implementing a content delivery network, optimizing your product pages, enabling ElasticSearch, adding a [managed WooCommerce hosting](/managed-woocommerce-hosting/) solution, and regularly monitoring your site's speed will go a long way toward optimizing the user experience so you can realistically expect a rise in sales.
Speed is essential for e-commerce sites, impacting the user experience, potential conversion rates, brand loyalty, and search engine rankings. Optimizing a website's upload and download speed is essential for eCommerce businesses to remain competitive and achieve their sales goals.
Overall, website speed can provide seamless customer experiences, raise conversion rates, foster customer loyalty, and improve search engine visibility in the highly competitive online marketplace. As previously noted, a delay of just one second in a page's response can result in a 7% decrease in sales, while increasing e-commerce website speed by 0.1 seconds can improve conversion rates by 8.4%. Speed is a critical factor in online shopping, affecting customer satisfaction, sales, brand loyalty, Google search rankings, bounce rates, session depth, shopper experience, and product detail page performance. Improving website speed can increase sales and search rankings, producing happier customers. There is no single way to become a top WooCommerce store, but following the methodologies above should ensure a WooCommerce site improves its speed and performance, which should go a long way to increasing customer satisfaction and loyalty.
These speed gains matter even more once your store grows into a multi-vendor marketplace, where every extra vendor, product, and order multiplies the load your site has to handle. At that point the platform you build on decides how far these scaling strategies can actually take you. Learn what to look for in [choosing a multi-vendor ecommerce platform](https://www.wcvendors.com/multi-vendor-ecommerce-platform/ "nofollow").
---
## Unlock Customer Loyalty: Turn WooCommerce Shoppers to Lifelong Fans
- URL: https://levamo.com/blog/woocommerce-loyalty-program/
- Category: ecommerce
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Boost WooCommerce sales! Build customer loyalty for long-term success.
A 3D image of the WooCommerce logo printed on a slanted white cube. (Source: Unsplash.com)
While the quality of a product or service is a significant factor in business success, the role of loyal customers cannot be understated. Customers with positive experiences with your brand become repeat buyers and advocates, driving business growth. Hence the importance of implementing a Customer Loyalty program for your WooCommerce store.
Today, millions of e-commerce sites on the internet provide several alternatives for customers. Nevertheless, building customer loyalty can significantly impact the success of your WooCommerce store, even making you an industry leader.
Today, there are more than 26 million e-commerce websites worldwide, and new sites continue to launch daily (Doofinder). Of these, close to 6 million are using WooCommerce for their store.
Screenshot from Builtwith.com showing WooCommerce Usage Statistics. (Source: BuiltWith.com)
This article explores customer behaviors and recommends strategies, tools, and software for building brand loyalty and achieving business success. Read on to learn how to get loyal customers and lifelong fans to grow your e-commerce store!
## Understanding Customer Behavior
Customers influence a market or business much more than product owners do. That is why customer satisfaction is at **the heart of every successful business model. This customer satisfaction breeds loyalty, which, in turn, promotes business success**.
Contemporary research, recurring customer experience, and reports show that certain factors influence customer behaviors, especially brand loyalty. Here are five of these factors and why they are important to you.
### How Product and Service Quality Affects Customer Loyalty
Good-quality products or services can automatically instill loyalty, and vice versa with poor-quality products. With many alternatives at their disposal, consumers only want to invest in products that give them the best bang for their buck.
However, the modern customer dislikes shopping, even on e-commerce platforms. So, when they find a brand that gives optimum value for their money, they tend to stick with it. Thus, a product’s quality is the most basic factor influencing customer loyalty and continuous engagement.
### How Your Company Reputation Affects Customer Loyalty
Today’s customers don’t just want to buy good products, but they also want to buy from good people. So, shoppers give their loyalty to brands they perceive as good, not just in production, but good to people, the environment, and the planet.
Customers are more loyal to brands that support a cause they also support. The same is true for brands and companies involved in the community and honoring their corporate social responsibility. Those who treat their partners and employees better earn stronger loyalty bonds with repeat customers.
### How Good Customer Experience Affects Customer Loyalty
A satisfying customer experience is one of the most effective ways to unlock consumer loyalty in e-commerce. When you give your customers a satisfying experience, you keep them yearning for more and returning for more. Customer satisfaction triumphs over many others because customers readily ignore other brands and even pay more for the best experience.
Providing a good experience for your customers in an e-commerce Store is not difficult. You can do this by making shopping convenient and improving communication and feedback between you and your customers. This way, you’ll bolster a loyalty bond that keeps them returning as lifelong fans.
### How Brand-Person Attachment Affects Customer Loyalty
Customers can activate a sense of loyalty to your brand when they feel a deep personal attachment to it. This attachment can evolve from various cues. Some customers develop this attachment with your marketing collaterals and what they represent. Others get attached to your organizational structure or service delivery systems like personalization.
Whatever the cue, you develop a loyal customer when your brand can reach a customer and resonate with them. If those cues remain with your brand, you can rest assured that such customers will remain loyal. So, seek out these cues in your brand and advertise them vigorously in your marketing campaign.
### Customer Loyalty and Reward Programs
Some people view loyalty and reward programs as candy given to adults. However, discerning customers look beyond the rewards to see the rationale behind it. They understand the company’s effort to appreciate their continuous patronage. Acknowledging this appreciation fosters brand loyalty from many customers, attracting lifelong fans.
Additionally, the long-run benefits of these programs create a loyalty loop for many other customers. They learn to return naturally without considering other options as they seek more benefits and reduced costs from continuous engagement.
A red “Thank You” card placed on a ceramic table next to a fountain pen. (Source: Unsplash.com)
## Strategies To Build Customer Loyalty
You can create effective strategies to build consumer loyalty based on the factors influencing their loyalty. This section highlights three strategies you can adopt in your e-commerce store to unlock loyalty through improved customer satisfaction.
### Create Personalized Experiences for Your Customers
Personalizing your customers’ experiences is a great way to ensure a satisfying experience and earn lifelong fans. A simple personalization feature on your e-store endears customers to your brand. It reveals your effort to build an interpersonal relationship with your customers, not just a business relationship.
Here are four simple personalization features you can try on your e-commerce store:
#### Use Personalized Messages
You can improve customer experience through personalized messages bearing customers’ names. This can be welcome messages when they log into their accounts or goodbye messages when exiting the store. Personalized prompts during and after successful purchases also thrill customers, giving them a feel of interpersonal communication over an online store.
When you use personalization for on-platform messages and email, you **show personal interest in your customers. Repeat customers respond with their loyalty and continuous engagement, sticking to your brand as lifelong fans**.
#### Create Personalized Homepages
Rather than repeating a bland homepage for all your customers, you can encourage personalization of their account homepage to improve satisfaction. Allow users to choose their preferred theme and [profile picture maker](https://www.adobe.com/express/create/profile-picture) tools to create a custom picture.Then, personalize the page with their name, picture, and favorite products.
Shoppers feel unique and important when they help design their distinctive homepage. Loyalty comes naturally when you offer premium customer satisfaction through an improved personal experience with your brand.
#### Provide Personalized Suggestions
You can leverage data collection to provide personalized assistance to your customers. From their previous purchase, you can learn their preferences and make personalized suggestions for their next purchase. With suggestions matching their preferences and budgets, you’ll help promote a seamless shopping experience for your customers.
You can also extend this personalization to marketing emails to share marketing or product updates they may like. Customers are loyal to brands who love and care about them. You show these qualities when you seek the best for them through these services.
#### Personalize Product Pages
Another excellent way to earn loyalty through a good customer experience is to ensure purchase convenience. When customers can conveniently access good products and services from a brand, they will loyally stick to that brand.
You can ensure this convenience in your e-commerce store through personalized product pages. Part of your data collected from customers' accounts reveals their location. Use this data to automatically convert prices to their local currency and estimate shipping fees. This feature will improve shopping convenience, unlocking brand loyalty to earn lifelong fans.
### Introduce Post-Purchase Tactics To Build Customer Loyalty
Personalization and other purchase tactics that promote customer satisfaction can spark loyalty in your shoppers. However, you must nurture these flames to establish unwavering loyalty for your brand.
Nowhere does that nurturing pay off more than in wholesale, where a single loyal account can reorder every month for years, dwarfing the lifetime value of a one-off retail sale. It takes a deliberate [retention system for recurring customers](https://wholesalesuiteplugin.com/recurring-customers/ "nofollow"), not just good products.
An effective way to do this is through post-purchase loyalty tactics.
These tactics extend a continuous thread of loyalty cues for your customers. Below are four post-purchase tactics to adopt for your brand:
#### Use Branded Confirmation
A branded purchase confirmation, though simple, re-exposes your customers to your marketing collaterals, reminding them why they chose your brand. So, don’t sell yourself short with bland notifications. Your purchase confirmation should be as appealing as your ad notification. That way, buyers will look forward to them, creating repeat customers.
#### Request Post-Purchase Customer Feedback
Don’t just let your customers go with a confirmation notification; request feedback about their purchase experience. This simple gesture demonstrates interest in shoppers and a desire to please them better, unlocking their loyalty.
You can simplify this feedback request by using survey-like questions to receive their feedback. When customers submit such feedback, they look forward to their implementation, attracting them to repeat purchases and continuous engagement.
#### Invite Customers to Your Loyalty and Reward Program
Reports show that customer loyalty programs convert about 81% of one-time shoppers to repeat customers ([Bond Loyalty Report](https://info.bondbrandloyalty.com/2016-loyalty-report-canada)). However, this can only work when customers know about your loyalty and reward programs. You can easily create this awareness by advertising the program and inviting customers to participate after every purchase. Your loyal customers will increase as you cultivate more interest and participation in these programs.
#### Upsell Related Products
You upsell when you identify a customer’s need from their current purchase and offer a product to fill it. This post-purchasing tactic has dual main benefits: increased sales and brand loyalty. When you offer customers their next need after each purchase, it deepens their experience and relationship with the brand, unlocking loyalty.
A person holds a phone showing the dollar sign on a white screen. (Source: Unsplash.com)
## Gain Lifelong Fans With a Customer Loyalty and Rewards Program
You can not overemphasize the influence of a rewards program and incentives in cultivating loyalty toward a brand. Any brand can introduce simple customer loyalty programs to reward shoppers and convert them into repeat customers.
However, there are several types of customer loyalty programs, and determining the best fit for your brand determines the program's effectiveness. Consider four types of customer loyalty programs you can explore:
### Point-Based Programs
Under this program, consumers earn redeemable points with purchases. They can redeem these points for exclusive products, discounts, or other special incentives. This program type is the best for growing businesses that prioritize increasing purchases per customer.
### Value-Based Programs
This program is similar to the points-based program, as it also allows consumers to earn points. However, in this rewards program, customers earn points from purchases and other non-purchase engagements with the brand. For example, some brands may offer points for downloading apps or following and engaging their handles on social media. Brands requiring high visibility for their products benefit most from this program type.
### Partnered Loyalty Programs
Two or more businesses team up to offer a loyalty program that benefits their mutual customers. Points or rewards earned with one partner can be used with any partner.
An example would be Airline partnerships where miles earned on one airline can be redeemed for flights on another.
### Paid Loyalty Programs
Customers pay a fee to join the loyalty program in exchange for benefits. These can include enhanced services like free shipping, exclusive product access, or special discounts.
For example, Amazon Prime offers free two-day shipping, streaming video/music services, and exclusive shopping deals for an annual fee.
### Subscription-Based Programs
In this program type, customers pay for access to perks and privileges. Nevertheless, the brands offer significant benefits that offset the customers' subscriptions. This program type is usually best for a brand that sells seldom-purchased products.
### Game-Based Loyalty Programs
These programs incorporate gamification elements such as challenges and badges to make the shopping experience more engaging and fun. For example, customers earn badges or levels for completing activities like reviewing products or trying a new service, which can be exchanged for rewards.
### Cash Back Loyalty Programs
Customers receive a percentage of their purchases as cash rewards, which can be applied to future purchases. For example, customers earn a 5% cash back on all purchases, which can be used towards the next purchase or accumulated for a bigger purchase.
### Tiered Loyalty Programs
The tiered customer loyalty program involves various membership levels with increasing benefits and incentives based on customer purchases and engagement. Such rewards programs are best for luxury and high-end products where the buyers chase exclusivity delivered by the luxury status of these products.
### Hybrid Loyalty Programs
Combining two or more of the above types creates a complex but flexible program catering to a diverse customer base. An example is a points-based system with tiers offering occasional cash-back events or partner rewards.
An image of a WordPress site showing the plugin tab. (Source: Unsplash.com)
## Tools and Software for Building Your WooCommerce Customer Loyalty Program
You need effective and efficient tools and software to implement the abovementioned strategies to build consumer loyalty. Fortunately, you don’t need to look elsewhere; WooCommerce provides several extension tools and software for unlocking and implementing whichever loyalty and rewards program you desire.
Here are four examples you’ll find in the reward and loyalty extensions section:
### WooCommerce Points and Reward Extension
This extension helps you reward your customer for purchase and non-purchase actions. It also manages these points in their accounts to redeem them as discounts for future purchases. The points and reward extension is easy to use.
With the [Points and Reward Extension](https://woocommerce.com/products/woocommerce-points-and-rewards/), you set the number of points earned per purchase or action and predetermine the maximum discounts customers can enjoy with accrued points. This tool effectively builds customer loyalty because it applies points earned to all previous orders for immediate redemption. The tool also offers smooth point management for customers and admins.
As an admin, you can change what you call points on your e-commerce store. You could call them “tokens” or “coins.” Customers also experience smooth point management on their accounts through swift updates to the points balance display on their account page. This reward tool will help nurture loyal and repeat customers for your brand.
### [AutomateWoo](https://woocommerce.com/products/automatewoo-birthdays/) - Birthdays Add-on
*AutomateWoo Birthdays Add-On plugin featured image (Source: WooCommerce.com)*
Build stronger relationships with your customers with branded birthday wishes before, on, or after their special day. You don’t have to worry about learning and tracking customers’ birthdays; AutomateWoo does the rest after you collect birthday details at checkout.
[AutomateWoo - Birthday Add-on](https://woocommerce.com/products/automatewoo-birthdays/) sends your customers customized birthday wishes and special offers on their special day. You can program the extension to send this email some days before the birthday to get them to purchase something special before that special day.
Everyone loves receiving birthday wishes, but kind wishes and thoughtful offers from a brand impress more in customers’ hearts. That fosters deep personal relationships with the brand and unwavering loyalty.
### [Cashback](https://woocommerce.com/products/cashback-for-woocommerce/) for WooCommerce
[](https://woocommerce.com/products/cashback-for-woocommerce/)Featured image of the Cashback for WooCommerce add-on. (Source: WooCommerce.com)
You can always give back to your customers to earn their trust and loyalty. The Cashback extension allows you to offer cashback rewards for orders, purchases, payment options, and shipping. This tool automates sending reciprocatory incentives and rewards to loyal shoppers.
[This plugin](https://woocommerce.com/products/cashback-for-woocommerce/) lets users see the cashback they can earn from certain actions and immediately adds it to their account after the action. As the product owner, **you set the criteria and eligibility statutes** for enjoying these incentives. Each time customers receive cashback, even at decimal levels, they feel rewarded and are encouraged to keep shopping with your brand as lifelong fans.
### [Next Order Reward](https://woocommerce.com/products/next-order-reward-for-woocommerce/) for WooCommerce
Build loyal repeat customers by upselling your products with discount coupons and incentives. Building a new e-commerce store helps to invest in repeat purchases from returning customers. The [Next Order Reward plugin](https://woocommerce.com/products/next-order-reward-for-woocommerce/) helps you achieve this by advertising discount coupons for customers' next purchase.
You can program this coupon to display on the confirmation or thank you page. It may even advertise incentives through a pop-up at checkout or an upsell email. When you offer customers their next need at discounted rates, you leave them no reason to look elsewhere.
### [Gratisfaction](https://wordpress.org/plugins/gratisfaction-all-in-one-loyalty-contests-referral-program-for-woocommerce/) for WooCommerce
[](https://wordpress.org/plugins/gratisfaction-all-in-one-loyalty-contests-referral-program-for-woocommerce/)Gratisfaction for WooCommerce plugin screenshot on the WordPress plugin repository. (Source: WordPress.org)
As a highly regarded loyalty plugin for WooCommerce, Gratisfaction stands out for its extensive customization capabilities. You can tailor your rewards programs extensively, setting up everything from giveaways and referral programs to purchase rewards. The tool provides detailed controls over its features, allowing users to activate comprehensive functionalities or select specific features to implement. For instance, in referral rewards, options include providing benefits to the referrer or both the referrer and the referred customer.
Gratisfaction's free tier supports up to 100 loyalty members. Upgrading to the premium version is necessary for expanded features and higher user limits, with prices varying based on the desired cap on loyalty program members.
Pricing for larger memberships scales up to $349 per month (when billed annually) for up to 25,000 users. Businesses exceeding 25,000 users should reach out directly for tailored pricing solutions. Opting for an annual subscription also secures a 30% discount on all plans.
### [Sumo Reward Points](https://codecanyon.net/item/sumo-reward-points-woocommerce-reward-system/7791451) for WooCommerce
[](https://codecanyon.net/item/sumo-reward-points-woocommerce-reward-system/7791451) *Screenshot of the Sumo Reward Points plugin on CodeCanyon (source: Codecanyon.net)*
The SUMO Reward Points plugin allows you to assign varying point values for activities such as purchases and referrals. These points can either be redeemed for cash or transferred between users. Additionally, the system supports unlimited email subscribers, and all design elements are fully customizable to fit your brand's aesthetics.
SUMO Reward Points is part of a comprehensive plugin suite that enhances customer loyalty through various tools. These include functionalities for managing coupons, subscriptions, membership programs, and setting up flexible payment plans.
The SUMO Reward Points admin dashboard makes overseeing customer interactions and point allocations easy. It provides extensive options to set up referral links, cap maximum point balances, and define point expiration parameters, among other features. This plugin is renowned for its robust capabilities and popularity within the e-commerce community.
In contrast to the other solutions listed, SUMO does not offer a free trial. Instead, prospective users can explore its features through a live demo. A license purchase is required to fully implement the plugin.
### [MyCred](https://mycred.me/) for WooCommerce
Screenshot of the hero section of MyCred’s website. (Source: mycred.me)
In the quest to elevate customer loyalty within your WooCommerce storefront, myCred emerges as a beacon of gamification and engagement. This versatile plugin is designed to infuse your e-commerce experience with excitement, rewarding users through a clever system of points, badges, and ranks. With myCred, every click brings your customers closer to you, fostering a community swathed in loyalty and mutual appreciation.
Starting as a free service, myCred offers a foundation brimming with potential. Its true prowess, however, is unlocked through tailor-made add-ons, allowing you to sculpt the perfect loyalty program to suit your agenda. Whether it's rewarding daily visits or celebrating community milestones, myCred adapts to your needs, ensuring that your rewards system is as unique as your business. Joining the myCred Membership Club further enhances this experience, bundling up your favorite add-ons at an irresistible price.
### [WPLoyalty ](https://wordpress.org/plugins/wployalty/)for WooCommerce
[](https://wordpress.org/plugins/wployalty/)WPLoyalty plugin page screenshot on the WordPress plugin repository. (Source: WordPress.org)
WPLoyalty empowers you to craft a loyalty program that rewards customers for their purchases and engaging actions such as account sign-ups, referrals, product reviews, and social shares. It's a toolkit for magnetizing and retaining customers by embedding rewarding experiences into every interaction with your brand.
WPLoyalty is versatile; it allows you to create custom loyalty tiers and badges, awarding your most dedicated customers exclusive rewards and recognition. Celebrations are in order, too, with birthday rewards to make your customers feel valued on their special day. WPLoyalty features point expiry notifications to keep the interest alive, gently nudging customers to engage and redeem their points.
Offering flexibility in rewards - be it coupons, free shipping, or free products - and integrating with multi-currency and multi-lingual setups, WPLoyalty ensures your rewards program is accessible and engaging to a global audience. The plugin simplifies customer relationship management through a clean, intuitive dashboard, ensuring you're always on top of your loyalty game.
## Best Practices for Successful Implementation of Your WooCommerce Customer Loyalty Program
You now have the appropriate tools and strategies to build consumer loyalty for your brand effectively. However, your implementation process is also key to unlocking success. Thus, this section shares three tips for successfully implementing a brand loyalty and retention strategy.
### Choose a Strategy That Fits Your Brand
The success of a loyalty and retention strategy for one brand does not ensure its success for another, even in the same industry. Several other considerations are necessary to determine the success of a retention strategy for your business before engagement.
You should consider the size and nature of your business. Its structure and the types of customers you attract also factor in significantly. The nature of your products and their demand patterns are other essential considerations you must factor in.
Explore each loyalty strategy and tool's features and discern which best fits your brand to impact your customers more. Use a rewards program and incentives when you’re sure of a good ROI.
### Use Woocommerce Loyalty Tools and Software
A good loyalty and retention strategy with poor implementation tools results in wasted efforts. Your tools for implementing a loyalty strategy must be convenient and reliable. That is why veteran e-commerce shops recommend WooCommerce, which powers about 29% of all e-commerce sites (source: [Tooltester.com](https://www.tooltester.com/en/blog/wocommerce-market-share/)) over the Internet.
Loyalty and reward tools are convenient and easy to use. Any e-commerce shop owner, even without technical and programming experience, can use these tools seamlessly. Additionally, the tools are reliable for automation and accurate recording and data analysis. These tools ensure the smooth implementation of any retention strategy for unlocking brand loyalty with repeat customers.
### Gather and Use Feedback About Your Loyalty and Rewards Program
Users are always happy to share feedback about a product or service, commend good products, and seek improvement where necessary. It helps to leverage this customer behavior to learn about their perception of your loyalty-building efforts.
Send emails and on-app prompts to survey your customers' feelings about your loyalty-building strategies. Ask whether they participate in your rewards program and how they feel about it. You could also leave room for suggestions for further improvements. After a data analysis of your results, you’ll learn where to improve to ensure higher efficiency of your loyalty and retention strategy.
A digital illustration of a shop on a green background. (Source: Unsplash.com)
## Case Studies: Real-Life Success Stories From Brodo and Nutribullet
Many brands are already partnering with WooCommerce to implement these loyalty-building strategies. Their experiences show the benefits of the tools and strategies discussed above. See what you can learn from the success stories of Brodo and Nutibullet, two brands that sought loyalty through improved customer experience with them.
### Expanding [Brodo](https://www.brodo.com/) to a Nationwide Brand
How far can a bone broth brand really go? With the right tool, Brodo went from a brand sold at a takeout window to being shipped nationwide through e-commerce stores. Here’s their story:
Seeking expansion through e-commerce, Brodo explored WordPress and WooCommerce. Although the initial ride was bumpy, the team quickly identified the need for a better, more responsive website to meet emerging customer experience needs.
The approach to improving customer experience began with better UX and CX design for mobile web users. Then, they introduced a self-service subscription and an information homepage to delight their customers.
Brodo also used tools like [WooCommerce Emails](https://woocommerce.com/products/mailpoet/) and [AutomateWoo](https://woocommerce.com/products/automatewoo/) for upselling and referral programs to build brand loyalty. This simple partnership and proper loyalty and retention strategy implementation have grown a local brand into a big business with customers nationwide.
[Read more about Brodo’s WooCommerce Case Study >](https://woocommerce.com/posts/brodo-broth-ecommerce-case-study-takeout-to-nationwide/)
### Nutribullet Improves Conversions & Customer Loyalty With Woopayments
The Nutribullet case shows how convenience and reliability impact customer satisfaction, influencing loyalty. Their case shows how a simple tweak and one appropriate strategy can influence the desired results.
Nutribullet is not new to e-commerce; it has always been a strong brand with a good online presence that just needed optimization. As a retail company selling small kitchen appliances, Nutribullet depends on ad conversions and repeat customers to thrive online.
However, despite using Apple Pay, PayPal, and Google Pay, many customers were dissatisfied with their checkout experience. After a thorough audit, they sought to improve customer satisfaction on their e-commerce platform site through an improved checkout experience.
Then, they chose [WooPayments](https://woocommerce.com/products/woocommerce-payments/), seeking a payment gateway with advanced functionality, like accepting payment plans, gift cards, and continuity subscription billing. Since [Nutribullet adopted this payment gateway](https://woocommerce.com/posts/nutribullet-woopayments/#:~:text=Nutribullet%20improves%20conversion%20rate%20by%2035%25%20with%20WooPayments), conversion has increased by 35%, and reports show that the numbers continue to rise.
With WooPayments delivering improved customer service at checkout, Nutribullet has improved conversion and positive customer experience. This case study is your cue to pick a loyalty tool to build your e-commerce store today!
## Conclusion
This article has highlighted the importance of customer loyalty as a key driver for business growth and expansion. Despite its pivotal effect, brand loyalty is easy to achieve with the right tools and strategies. Here, you’ve seen examples of simple yet effective tools and strategies to adopt and how to do it.
Lastly, did you know that website performance has a major impact on customer loyalty? A mere [one-second delay in page load time](/blog/speed-up-woocommerce/) can lead to a 16% decrease in customer satisfaction. This is crucial, as satisfied customers are more likely to develop a sense of loyalty to a brand. Furthermore, 40% of users will abandon a website that takes more than three seconds to load, showcasing the thin line eCommerce sites tread between retaining potential loyal customers and driving them away through poor performance.
Want to improve your WooCommerce site’s performance? Try Levamo [managed WooCommerce hosting](/managed-woocommerce-hosting/) and optimize your website by [Downloading the CRAZY FAST WooCommerce Sites guide and checklist](/) to discover the secret strategies for a fast, highly scalable WooCommerce site.
---
## 30 Stunning Web Developer Portfolios for the Ultimate Inspiration
- URL: https://levamo.com/blog/web-developer-portfolios-inspiration/
- Category: website-development
- Author: Shahzeb Ahmed
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Get inspired! View 30 stunning web developer portfolios and cool design tips.
A strong Web Developer Portfolio is more than just a resume. It's a powerful showcase of your expertise, experience, and reliability as a web programmer, helping you attract high-value clients and accelerate your professional growth.
However, creating a standout Web Developer Portfolio can be challenging, especially in today’s highly competitive development landscape, which is why it’s smart to draw inspiration from industry experts and top-performing portfolios.
Looking at an expertly designed web developer website portfolio may just be the nudge you need to create one that works for you. So, I've shortlisted the top 30 best portfolio websites for web developers to give you some ideas on how to design your own.
At the end of the list, I've also shared some cool tips on creating your web dev portfolio on top of [Levamo](/), a [high traffic WordPress hosting](/blog/fastest-wordpress-hosting/) that gives you the most powerful platform to impress your clients. But we'll talk about that later.
Let's quickly understand why a good web dev portfolio is so important.
## The Importance of a Good Web Developer Portfolio
Let's face it - if you want to make it as a web developer, you need a killer portfolio. Beginner or pro, it doesn't matter. Your portfolio is your ticket to getting noticed in this industry, so trust me, it's worth the effort for the following reasons:
### 1. A Web Developer Portfolio Showcases Your Skills
Your dev portfolio allows you to showcase your skills and expertise as a web developer. It goes beyond simply listing your skills and qualifications and provides strong evidence that you understand the craft.
### 2. A Web Developer's Portfolio Enhances Your Credibility
Your developer portfolio isn't just a collection of projects. It helps build trust with potential customers, increasing your credibility in multiple ways, like displaying your range and types of projects you've already accomplished.
### 3. Attracts Employers and Web Development Clients
While an expertly designed web portfolio is aesthetically great, it's really helpful in attracting excellent opportunities for future work. You can use it as a strong marketing tool if you’re a freelancer, since potential clients typically like to go through any web developer's work before hiring them.
### 4. Web Developer Portfolios Aid Your Growth
Your portfolio offers an excellent opportunity to grow as a web developer. Since you’ll continuously add newer projects to the catalog, it shows clearly how you've grown as a developer and can take on more serious projects now.
Now let's dive into the top web developer website portfolios that will inspire you to start your own!
## Top 30 Stunning Web Developer Portfolios to Inspire You
Now that you know that having a web developer portfolio is critical for your career, the next step is to set one up for yourself. We've laid down the basics of how to create your own portfolio as a web developer, but before we get into that, let's take a look at the best web developer portfolio websites to help you get some inspiration.
### 1. Charles Bruyerre

[Charles Bruyerre](https://www.itssharl.ee/), a French web developer, graphic designer, and UI/UX designer, portrays a unique design in this portfolio. While the site interacts with you as you browse the project catalog, you can still observe the playful but modern look. Besides the listed branding, portrait, and gaming projects, you can also see the developer’s Instagram and Behance profiles.
### 2. Brittany Chiang

While [Brittany’s portfolio](https://brittanychiang.com/) describes her incredible expertise, its brilliant color choices and makeup make it an excellent model to consider. It has a modern design and highlights her vast experience working with brands of different sizes, including Apple Music. So, if you’d prefer a calm and smooth portfolio design, check this out.
### 3. Bruno Simon

If you’re trying to over-impress with your web developer catalog, look at [Bruno Simon’s portfolio](https://bruno-simon.com/). This developer has designed a 3D navigation system that takes you through a collection of projects using a car. Thus, you can actively interact with the projects and social media links in the portfolio; it is quite impressive.
### 4. Cassie Codes

If you’re trying to design a fun and interactive portfolio as a web developer, [Cassie Codes](https://www.cassie.codes/) shows you how to do it. First, you’ll trigger some pop-ups by hovering over several characters on a screen. Then, you can also turn on light and dark mode. Scrolling through the sections on the site takes you through some excellent UX designs.
### 5. Ian Dunkerly

[Ian Dunkerly](https://dunks1980.com/), a UK-based front-end developer, specializes in UI/UX designs. His web developer portfolio excellently represents his projects, which include disc jockey apps and e-commerce platforms. One of this portfolio’s most beautiful features is the single-page layout that flips to show all the information you need.
### 6. Patrick David

Once you open [Patrick David’s portfolio](https://bepatrickdavid.com/), a well-packed screen with an outstanding background photo greets you. As a result, it is a helpful idea if you’re looking to showcase your creativity with a touch of innovation. While there is a lot to digest on the site, going to the **works** section provides a seamless view of the entire project catalog.
### 7. Monica Dinculescu

[Monica’s portfolio](https://meowni.ca/) has a comprehensive list of projects she’s worked on. After opening the portfolio, you’ll see artwork you can regenerate with one click. Besides that, the top menu can check past posts, projects, talks, and the shop. Are you looking for a simple yet effective style? Go for this.
### 8. Keita Yamada

A designer and a developer, [Keita Yamada](https://p5aholic.me/), has designed one of the simplest yet effective web developer portfolios you’ll find. As you open the site, you’ll immediately notice the bio on the bottom right corner and the menu redirecting you to the projects, info, contact, and FAQ. You can also change the moving background’s theme from light to dark.
### 9. Matt Farley

[Matt Farley](https://mattfarley.ca/) uses a consistently simple design as well as basic fonts, images, and figures in his portfolio. The result is a well-placed design with a great interface. You can scroll down the page to view the project catalog. Surely, consider this type of design if you’re targeting simplicity.
### 10. Lauren Waller

[Lauren Waller's portfolio](https://www.lauren-waller.com/) contains large-font text that directs you to the **work**, **about**, **contact**, and **shop** pages. In this case, clicking the **work** option takes you to the project catalog. Since this design is simple and easy to use, you should take some ideas if you need something similar.
### 11. Kaleb McKelvey

[McKelvey’s portfolio](https://kalebmckelvey.com/) is a bit more comprehensive than your usual design. Besides a well-written **about** section, there is also a blog discussing various related issues. On opening the site, a silhouette of the author and the bio greet you coolly. So, if you’re integrating blogs in your web developer portfolios, take a look at this.
### 12. Lars Olson

Olson has expertly designed a single-page [web developer portfolio](https://www.lars-olson.com/). While the external links connect to his social pages and resume, you can learn about him and view the projects as you scroll down. An excellent mix of colors and beautiful fonts shows you how to design a clean-cut portfolio. We recommend it.
### 13. Eric Van Holtz

A deep blue background and large menu options greet you as you open [Eric Van Holtz’s portfolio](https://vanholtz.co/). He does a great job of emphasizing his past projects at the expense of other elements on the site. For instance, the social media links and other details appear in tiny fonts, and you know why.
### 14. Lynn Fisher

You can easily toggle between light and dark modes while browsing [Lynn Fisher’s portfolio](https://lynnandtonic.com/). The background is plain white in the light mode and black in the dark version. In this version, clicking **work** takes you to the project's catalog, where the instruction is to “waste time here.” Simplistic and effective.
### 15. Olaolu Olawuyi

Olaolu uses an exquisite color mix in [his web developer portfolio](https://olaolu.dev/) to create a standard design. Scrolling the homepage takes you through his skills, experience, and contact page. Also, you can click the **my work** option on the menu to view his projects. While simple, web developer portfolios designed this way usually contain all the relevant info.
### 16. Neal

Neal has designed a [tiny website](https://neal.fun/) that also functions as a portfolio. It is quite basic: the homepage has a plain white background containing a cascade of the developer’s past projects. Honestly, you can find some pretty impressive items there. You can also find a couple of social media links down the page.
### 17. Adenekan Wonderful

When you first open [Adenekan’s portfolio](https://www.codewonders.dev/#!), the glitching effect directs your attention to the developer’s name. While you can also switch between light and dark modes, the **Projects** option takes you to an impressive, wonderful catalog. This concept is quite outstanding; you should pick some ideas here.
### 18. Adham Dannaway

[Adham Dannaway](https://www.adhamdannaway.com/), a web developer, has created a pretty classy portfolio that will blow your mind. The homepage has an effect that switches between a photo and a painting of him. In this case, clicking the **portfolio** button on the menu takes you to his projects. It is a pretty impressive idea to model.
### 19. Dejan Markovic

[Dejan Markovic’s portfolio](https://www.dejan.works/) features a simple but well-placed design. The site immediately showcases the developer’s projects as soon as you open the homepage. The plain white visuals carry a cleanly arranged catalog. This is another idea for a simplistic design. Also, note the tiny **About** option on the screen’s top right corner.
### 20. Ram Maheshwari

[Ram Maheshwari](https://www.rammaheshwari.com/) has created a pretty formal and straightforward portfolio. With simple fonts, backgrounds, and colors, he effectively showcases his skills and projects. He has placed this information on one page, boosting the user experience. His catalog has some excellent items, like the **Dopefolio**. Furthermore, the web developer portfolios that follow this format usually follow a more formal approach.
### 21. Rafael Caferati

[Rafael Caferati’s portfolio](https://caferati.me/) first asks you to “destroy this homepage.” After clicking that button, the site presents a shooting game between a specific character and the developer’s bio. That aside, the menu has several options, including the portfolio, showing the developer’s past projects. With its creativity and efficiency, this is an excellent portfolio idea.
### 22. Adeola Adeoti

[Adeola Adeoti](https://www.adeolaadeoti.site/) displays his incredible works and accomplishments in his uniquely designed portfolio. Besides the dark visuals and interactive design, you’ll first notice the rotating bar that follows your cursor on the screen. Then, scrolling down the screen takes you to the projects section. This is an excellent inspiration if you’re considering an interactive layout.
### 23. Pierre Nel

[Pierre Nel’s ](https://pierre.io/)Interstellar Design is one of the most effective web developer portfolios. The dark-themed site offers an interactive user experience with dancing characters that welcome you to the site. By scrolling down the site, you’ll see the developer’s bio and the recent and previous projects.
### 24. Denise Chandler

Another interactive design with an obvious pink theme characterizes [Denise Chandler’s portfolio](https://denisechandler.com/). Besides the rotating clock, the blooming flowers on the homepage boost the visuals. Since the site has a single-page layout, you can either scroll to the portfolio or use the menu. So, this is a great idea if you wish to showcase your inner creativity.
### 25. Edewor Onyedika

Onyedika uses several animated elements in his [web portfolio](https://www.onyedika.xyz/). With a predominantly green and dark-themed design, this developer effectively creates a stunning multi-page layout that may be just the inspiration you need. A quick visit to the **work** page shows you all the projects he’s worked on. Despite the multiple animated features, the user experience is top-notch.
### 26. Seán Halpin

[Seán’s portfolio](https://www.seanhalpin.xyz/) describes his eye for color, providing the ultimate inspiration for developers who wish to create catchy designs and visuals. Once you open the site, you’ll see his completed projects and those in progress below the bio. He also adds reflections, thoughts, and tips for other web development enthusiasts.
### 27. Ben Adam

Are you looking for a minimalist design idea? [Ben Adam’s portfolio](https://benadam.me/) will give you the perfect inspiration. With just a plain white background, this developer records his projects. You can find these projects under the **experiments** section. Besides that, the dev posts helpful thoughts and tips quite regularly.
### 28. Edward Hinrichsen

Once you open [Edward Hinrichsen’s portfolio](https://www.edwardh.io/), an illustration of a vintage computer set welcomes you. You can scroll or type “help” to access his full catalog of fascinating projects. It is an excellent idea to create an interactive site to save your web development projects.
### 29. Jhey Tompkins

Jhey’s Twitter/X profile- sorry, [Jhey’s portfolio](https://jhey.dev/) is quite interesting. The outside-the-box layout looks like a Twitter profile but contains his info and articles. In addition, the site lets you switch between dark and light modes. Although he plays around with CSS, this is an unconventional idea for your portfolio.
### 30. Robb Owen

[Robb Owen’s portfolio](https://robbowen.digital/) has a characteristic light theme with some animation. Well, the site also contains some writing on tech and language. However, you can access the developer’s projects by scrolling down the homepage. This simple interface with excellent navigation offers good pointers if you need some inspiration.
### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## The Common Traits Among Successful Web Developer Portfolios
What makes a successful web developer portfolio? What are the things to look out for when designing one for yourself? If you’re unsure what to add to your portfolio, this section highlights them. Remember that these factors interlock and do not function separately.
That said, here are the common traits among successful web developer portfolios:
Also Read: [MemberPress Review](/blog/memberpress-review/)
### 1. Excellent Display of Projects
Your projects are the most important parts of your portfolio. For this reason, you must display them excellently. For each product, you must add details, photos, and links to the work. Also, grouping your projects into separate categories helps ease the navigation process.
### 2. A Good Touch of Personal Branding
Most successful portfolios are characterized by consistent branding. While this includes the site’s overall outlook, colors, and fonts, a style and logo also count. You must also capture your professional identity and the type of web development you enjoy the most. Overall, everything should fit consistently and smoothly.
### 3. An Excellent Collection of Projects
To create a portfolio that wins contracts, you must first understand which projects to show the world. Pay attention to showing the quantity rather than quantity when adding projects to your catalog. Also, ensure you capture your skills in the portfolio to show your strengths and versatility. Include your personal, open-source, and freelance projects for better effect.
### 4. Display of Key Skills
Besides choosing your best projects, you must focus on your most important skills. First, your homepage should highlight your biggest strengths in web development. Also, consider using headers and different sections to make your skills obvious. You can also create sections that capture skills like back-end and front-end development, user interface, and [web development ](https://webisoft.com/enterprise-software)in general etc.
### 5. User-Friendly Designs
Your portfolio must have a user-friendly interface that supports seamless navigation. In this case, you must stick to a consistently organized layout and avoid stuffing the pages with excessive information. You should also create a simple navigation menu pointing to your site's different sections.
You must also create a mobile-friendly, responsive makeup since most visitors browse with their mobile devices. Adding beautiful visuals to your projects makes the web pages more engaging. Finally, standard color schemes and typography polish the appearance and produce a more professional look and feel.
### 6. Included Testimonials and Recommendations
Although your projects show your strengths in web development, testimonials and recommendations improve your credibility. In fact, clients are more likely to hire when they see good reviews from past clients. You should add these testimonials where people can find them in your portfolio. Placing them with descriptions could also add to the effect.
## How to Launch Your Web Portfolio on WordPress
[WordPress](/managed-wordpress-hosting/) is still the go-to choice for developers who want full control, flexibility, and speed, especially when paired with a high-performance host like [Levamo](/). Here’s a quick-start guide to get your web programmer portfolio online without the headaches.
### 🎨 Choose a Lightweight, Portfolio-Friendly Theme
You don’t need a bloated theme with a million features you’ll never use. Here are a few developer-loved themes that strike the right balance between flexibility and speed:
- **[Astra](/blog/astra-wordpress-theme-review/)** - Fast, minimal, and works great with page builders.
- **[JetPlugins](https://crocoblock.com/plugins/)** – For creating custom post types, portfolio listing, filtering or searching among your works or skills.
- **GeneratePress** - Lightweight, clean codebase, and perfect for custom work.
- **Blocksy** - Gutenberg-first, responsive, and visually impressive.
- **Kadence** - Ideal if you want pre-built templates without compromising speed.
All of these work flawlessly on Levamo and are optimized for peak performance.
### 🔌 Must-Have Plugins to Power Up Your Portfolio
Keep it lean. These are powerful without dragging your site down:
- **WPForms** - For a contact form that actually works (and doesn’t look outdated).
- **Perfmatters** - Disable bloat, control scripts, and boost speed.
- **Rank Math or Yoast SEO** - So your portfolio shows up where it should: in search results.
- **MonsterInsights Lite** - Simple Google Analytics integration.
- **WP Rocket or FlyingPress** - Page speed optimization made easy ([Levamo is already blazing fast](/performance/), but this adds that extra edge).
### 💡 Pro Tip:
Always test your site’s speed after you build. Levamo already gives you server-level caching and optimized performance for WordPress, so you’re starting strong. But a fast theme + lean plugins = *chef’s kiss*.
## Conclusion
Web development is an ever-expanding field. There are newer ideas, trends, and styles emerging every day. As a result, you must keep up with these ideas and [web hosting trends](/blog/web-hosting-trends/) in the industry to remain relevant as a developer. Also, you must maintain a steady learning streak to build the needed creativity.
You’ll sometimes need to draw inspiration from other professionals and creatives to do this. That is why this article has highlighted 30 stunning web developer portfolios to stir that creative element in you. The post also covers the items you must add to your catalog to boost your chances of attracting and securing clients and contracts.
Now that you’ve gone through this post, what are you waiting for? Apply these ideas to your own project for the best results.
---
## Freelancer's Growth Manual: 18 Strategies for Client Attraction & Loyalty
- URL: https://levamo.com/blog/strategies-client-attraction-retention/
- Category: online-business
- Author: Ochai Emmanuel
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Grow your freelance biz! 18 client attraction & loyalty strategies inside.
Since the COVID-19 pandemic, the freelance business industry has received tremendous positive attention, fostering its growth and expansion. Additionally, starting and running a freelance job is easy - a home office provides almost all you need. Unfortunately, these factors have created a disproportionate industry, with many more freelancers than clients.
Therefore, you must learn how to attract and retain clients to [build a successful freelance business](/blog/build-successful-wordpress-freelance-career/). Veteran freelancers agree that a good and sustainable client base is the foundation for a successful and sustainable freelance career.

However, with such intense competition for limited clients in every niche, you can’t rely on luck for client attraction. Proven methods exist to help you find and keep your client to build sustainable business growth. Therefore, this article discusses 18 strategies to attract and retain your clients and grow your business. Keep reading to learn the ropes!
## Understanding the Freelance Business Landscape
The freelance marketing landscape is dynamic yet easy to understand and master. Basically, this industry operates on a performance-based model instead of the loyalty-based model of traditional businesses. That means clients will only hire and keep you for what you can do.
As a result, this encourages a feeble relationship between employers and employees. [Freelance employees expect more autonomy and flexibility](https://codecontrol.io/en/blog/why-top-talents-become-freelancers#:~:text=the%20desire%20for%20more%20autonomy%20is%20a%20key%20factor.%20Top%20talents%20in%20particular%20want%20to%20choose%20their%20own%20clients%20and%20projects%2C%20because%20that%20way%20they%20can%20ensure%20they%20can%20make%20the%20best%20use%20of%20their%20skills.), while employers want faster and more cost-effective results. Moreover, both parties are usually bound by time-bound contracts, with renewal dependent on the satisfaction of both parties.
Additionally, freelancing is an open-entry industry where anyone can participate freely. Further, freelancing models, like the interim and fractional models, allow traditional employees to participate in the industry.
Therefore, with loyalty gone and more freelancers available than clients, freelancing is now one of the most competitive industries. Nevertheless, you can still succeed, even if you’re just starting your freelance journey. The client attraction and retention strategies discussed in this article will help you build a successful freelance business.
## Strategies To Help Freelancers Attract New Clients
Attracting clients is not a passive activity but an active one. You can’t wait for clients to contact you in the competitive freelance industry. Instead, you must make them contact you. There are several ways to make your freelance business attractive and win clients. Let’s explore eight marketing strategies in this section.
### 1. Leverage Your Network of Personal and Professional Contacts
Charity begins at home, and sometimes, so does business. Your next client can come from your current contact, personal or professional. So, discuss your freelance business and advertise your brand to your physical or online contacts.
Also, quickly offer your service to anyone you think will benefit from it. Even if they don’t require your service now, implore them to reach out when needed and recommend your business to their friends and contacts.
Consider collaborating with an [event agency](https://www.ch3.agency/) to expand your network further through industry events and professional gatherings.
### 2. Optimize Your Online Presence To Improve Your Visibility
You can only attract clients who can see you, so it is important to improve your visibility. One way to achieve this is by optimizing your online presence. If your business has a website, observe SEO rules and guidelines to stay at the top of all search results.
You can also optimize your online presence with your social networking handles. Create a professional profile on all social platforms and engage with potential clients. Then, advertise your business while promoting your skills and expertise. If you leverage social media properly, it can become a source of client lead generation.

### 3. Win Freelance Business Clients With Persuasive Proposals
You’ll encounter many opportunities to pitch your service when searching for freelance clients, especially on job boards and freelance markets. You can leverage these opportunities to attract clients with a persuasive pitch or proposal.
A persuasive pitch details the service you offer and why it is unique. Convince the potential client that you’re the best fit for his project. A rich, confident, and detailed proposal can convince any client to partner with your freelance business.
### 4. Use Cold Emails To Attract New Clients
Sometimes, people who need your services are outside your contact list. However, you can reach them via mail and introduce your service to them. While this may seem like a bold move, it is an effective way to attract new clients when done right.
Your cold email will more likely produce the desired result when you personalize your message. Additionally, highlight the needs of the individual or business and demonstrate how your business can satisfy that need.
### 5. Publish Social Proof To Promote Your Freelance Business
When seeking freelancers to partner with, clients always look for the best. Sometimes, it’s insufficient to sell yourself as the best; you need others to back up your claim. That is where [social proof](https://sproutsocial.com/glossary/social-proof/#:~:text=Social%20proof%20is%20the%20psychological%20concept%20that%20people%20are%20influenced%20in%20their%20decision%20making%20by%20others%2C%20compelling%20them%20to%20act%20within%20societal%20norms%20or%20expectations) comes in.
Positive reviews and recognition from previous clients count towards your social proof. This proof attracts new clients to your business to enjoy the same positive experience. So, keep gathering social proof from social media and freelance platforms. Publish them on your professional profiles and use them in proposals to attract new clients.

### 6. Offer Competitive Pricing for Client Attraction
All clients want the best value for their money. Plus, the freelance pool is flooded with several alternatives to choose from. So, when offering your service, offer competitive pricing, especially at the beginning.
A competitive price for your service must be balanced. It should not be too low to suggest inferiority, and it should not be too high to discourage potential clients. Therefore, set a price range that instills confidence in potential clients and encourages them to hire you. Where appropriate, publish your price on your profile or in proposals to accompany your service offering.
### 7. Sell Your Service on Freelance Platforms
Freelance platforms constitute the highest buyer base for freelancers today. These platforms unite clients and freelancers and ensure smooth transactions for both parties. Freelance platform eliminates the stress of finding clients, allowing you to focus on attracting and impressing the delivered client.
With many platforms and markets to enjoy, you’ll benefit most from an [industry-specific platform](/blog/best-freelance-websites/). So, create a profile on a good platform and attract clients today!
### 8. Promote Your Freelance Business With a Unique Selling Proposition
Clients should see what you offer from a distance, which should not be common. Find something that sets you apart and puts you ahead of other freelancers in your niche. Then, publish this on your profile or website portfolio.
In this increasingly competitive freelance industry, it helps to develop specialized skills and expertise. Such skills will strengthen your unique selling proposition and branding, attracting clients at first glance. Utilizing [AI logos](https://www.brandcrowd.com/ai-logo-generator) can be a cutting-edge way to showcase your specialization and unique selling proposition to potential clients.
## Client Retention Strategies for Your Freelance Business
Attracting clients to partner with is insufficient to ensure success and sustainability for a freelance business. Freelance contracts encourage satisfaction-based relationships that could dissolve at any time. Therefore, it depends wholly on you to ensure client retention after attracting a desirable client. Fortunately, this section shares ten strategies to help you achieve this.
A computer screen shows an analytics page revealing increased business conversions.
### 9. Always Deliver Beyond Expectation
Freelance clients will only renew their contracts with you when you deliver good quality work. However, considering industry competition, it helps to even exceed the expectations where possible. Your delivery should show commitment not just to the contract but to your client’s business.
This exceptional delivery will foster loyalty in your clients, ensuring client retention. However, this commitment level should not end with your first task. Instead, consider every project a new opportunity to impress your client and reinforce their loyalty.
### 10. Communicate Clearly and Regularly To Build Trust
Clear and frequent communication is a key strategy that ensures customer loyalty. When you communicate clearly and regularly, you build your client’s confidence and trust. In the beginning, outline your deliverable and set a reasonable timeline.
During the project, send regular updates, however simple. Such frequent communication reveals your dedication and commitment to the project, endearing your client to you. Most clients reciprocate such dedication with loyalty as they grow to trust you.
### 11. Request and Act on Clients’ Feedback
Invite your clients to criticize your work and share feedback for improvement during and after the project. Many clients appreciate a willingness to be taught and corrected. That will convince them of your humility and flexibility in working together to achieve the target goals.
You’ll immediately earn their trust when you implement shared feedback. Such an attitude can encourage a client to convert a one-off contract into a permanent one.
### 12. Build a Freelance Business That Offers a Positive Client Experience
When considering retention, clients don’t just look at the end product but factor in the entire process. That includes your communication, attitudes, and availability, all contributing to their experience with your business.
So, you can ensure client retention by providing a satisfactory experience for them. Clients will more readily keep working with you when you offer them a smooth, rich, and exciting experience.
### 13. Develop Personal Relationships With Your Clients
Where accepted, build a personal relationship with your client. Try to learn about their interests and preferences. Further, ask about their personal life and discuss topics of interest outside the project.
Showing personal interest endears many clients and builds strong bonds beyond a business relationship. If you balance your display of personal interest with outstanding project delivery, clients will consider you an efficient work friend.
### 14. Provide Value-Added Services for Your Clients
You’ll impress all clients when you deliver what your contract stipulates. However, try to provide more for client satisfaction and retention. [Value-added services](https://www.afreelanceworker.co.uk/freelance-workers-value-added-services.html#:~:text=Value%20added%20services%20are%20things%20that%20freelancers%20can%20offer%20to%20their%20clients%20to%20help%20make%20projects%20more%20successful%20without%20any%20extra%20monetary%20cost.) are simple extra tasks beyond a project’s scope. It could even be as simple as suggesting alternative solutions or providing more insight.
These tasks showcase your expertise and commitment to the project and your client’s business. Consistently delivering more value impresses clients and encourages them to retain freelancers.

### 15. Upsell and Cross-Sell Your Freelance Business Services
Some freelance clients genuinely need your service for a one-time project. However, you can retain them by cross-selling other services you offer that they need. For example, if you’re a content writer with SEO expertise, you can recommend optimization for your client and offer your services.
With proven quality and timeliness records, clients will not hesitate to retain you for other projects within your expertise.
### 16. Respect and Adhere to Deadlines
Always remember that many other freelancers can do the job, maybe even as well as you. However, it is the little details, like your timeliness, that encourage client retention. The client will reward you with trust and loyalty if you consistently meet the assigned deadlines.
### 17. Offer Loyalty Packages to Your Clients
Clients are to freelancers, what customers are to commercial businesses. To retain customers, businesses offer loyalty packages to reward them for choosing their brand. This strategy also works with freelance clients.
To encourage retention, you can offer loyalty packages to your clients. Your package can include a free task, an exclusive offer, or a discount for a project. Some clients are more impressed with your thoughtfulness than your offer and will reward you with loyalty.
### 18. Improve Your Availability to Your Client
Many clients prioritize reliability and dependability during a project. You can show that you possess these qualities by improving your availability. Ensure your client can reach you anytime to communicate new instructions and adjustments. If they can rely on you, they’ll be encouraged to keep working with you on more projects.
## Tools and Resources To Support These Strategies for Your Freelance Business
The 18 methods discussed above are proven strategies for ensuring client attraction and retention. It helps to apply as many of these as possible, if not all. Nevertheless, some tools help facilitate their implementation. This section lists some examples for you under three categories.

### 7 Best Customer Relationship Management Tools for a Freelance Business
Below are seven CRM tools to implement the client satisfaction and retention strategies above:
- Zoho CRM
- FreelanceMate CRM
- HubSpot CRM
- SoloFlow CRM
- Agile CRM
- HoneyBook
- OnePage CRM
### 5 Exciting Project Management Tools for Freelancers
Here are five project management tools you can use to improve your work and client relationships as a freelancer:
- Asana
- ClickUp
- Hive
- Teamwork
- Trello
### Top 5 Communication Tools for Every Freelance Business
The following are five popular tools freelance businesses and clients use for effective communication:
- Slack
- Google Meet
- Microsoft Teams
- Zoom
- Skype
## Common Challenges to Customer Attraction and Retention and Possible Solutions
The freelance industry has a reputation for being difficult. New or old freelancers sometimes find it difficult to succeed in the industry. If you’re in this category, do not fret. This section discusses some common challenges impeding client attraction and retention. You’ll also find plausible solutions to overcome these challenges.
### 3 Common Obstacles Against Client Attraction
If you’ve been struggling to attract new clients to your freelance business without success, you’re facing one of the three challenges discussed below. Read on to find possible solutions to help overcome your obstacle to client attraction.
#### 1. Low Visibility Due to High Industry Competition
High competition is a primary characteristic and challenge of the freelance industry. There are so many freelancers offering the same services as you do. So, it can be difficult for clients to see and even consider you, especially on freelance platforms and markets.
**Solution:** Optimize your online presence to improve your visibility. It also helps to earn badges and ranks on freelance platforms to increase your qualifications and appear in more searches.
#### 2. Lack of Consideration for Beginners
In the freelance industry, the rich keep getting richer. That is because clients focus on hiring talents with proven records of excellence as freelancers. Consequently, you may find it hard to attract clients as a beginner, however talented you are.
**Solution:** Publish your unique value proposition for potential clients. You can also start working for an agency to build a portfolio and receive exposure to the freelance landscape. Then, publish your portfolio and social proof as you gain strength in the industry.
#### 3. Unresponsive Clients
In trying to attract clients, you sometimes send proposals and pitch to clients. Unfortunately, many of these become unresponsive, even those who earlier sought your service, especially on freelance platforms. These unfruitful attempts could discourage you from attracting new clients.
**Solutions:** Research potential clients before sending proposals to ensure you pitch to someone who needs your service. Additionally, only apply for jobs that match your qualifications to increase your chances for success.

### 3 Common Challenges to Client Retention
Learning how to keep clients is important even after finding them. However, some obstacles challenge this important action. Consider three of these challenges below and find some solutions you can explore.
#### 1. Working With Perpetually Dissatisfied Clients
You simply can’t satisfy some clients, however hard you try. Such clients find fault with whatever you do. It is a real challenge working with such clients. So, what can you do?
**Solution:** Always research a client before working with them. Freelance platforms allow you to read reviews from other freelancers who have worked for them. Leverage this feature to learn about clients before agreeing to work with them.
#### 2. Clients Keep Changing the Contract Details
Working with a client who keeps changing your contract details and terms is usually challenging and discouraging. Without saying, you know that working with such a client will be short-lived. Again, this challenges client satisfaction and retention for you, so what’s the solution?
**Solution:** It’ll help clearly state your working principles before commencing a contract. You could even provide a limited number of changes you’ll accept during a project.
#### 3. Poor Communication
Some clients will frustrate you by communicating poorly. They’ll either rely slowly or delay your instructions. Ultimately, they record an unsatisfactory experience, and you’ll lose out on retention even though it's not your fault. Still, you can do something to overcome this challenge.
**Solution:** Find a more convenient communication tool or platform to interact with your client. That will greatly improve their communication and eliminate this challenge.

## Learning From Dakota Robertson: A Case Study of a Successful Freelancer
On a straight line, [Dakota Robertson](https://twitter.com/WrongsToWrite) started as a freelance ghostwriter but is now a content marketing expert with hundreds of clients. He also runs a personal brand and earns over $250,000 monthly! While many factors helped Dakota succeed, applying most of the client attraction and retention strategies discussed above contributed greatly. This section shows you how.
First, Dakota prioritized optimizing his online presence. He manages an SEO-optimized business [website](https://www.dakotarobertson.net/) you can easily find on any search engine. Next, he successfully manages social media accounts across several platforms, such as X and LinkedIn.
He publishes social proof on these platforms and uses his unique value proposition to attract new clients. This branding approach earns him several new clients. Today, his freelance business boasts hundreds of satisfied clients. What’s more? Dakota continues to attract new clients by leveraging his online network.
Dakota maintains his large client base with effective client satisfaction retention strategies, most of which we have discussed. For example, he always delivers beyond expectations. Today, Dakota has trained [over 117 successful content marketers](https://www.dakotarobertson.net/#:~:text=I%27ve%20used%20to%20help%20117%2B%20creators).
As evident on his X page, Dakota frequently receives and applies feedback from his client. He also cross-sells his skills as a ghostwriter and content marketing expert to his clients. His clients also report that Dakota is always available to meet their needs.
The lesson here is simple - the client attraction and retention strategies discussed in this article are effective. Just as they worked for Dakota Robertson, they’ll also work for you if applied meticulously!
## Conclusion
Running a successful and sustainable freelance business depends mainly on the sustainability of your client base. However, the freelance industry is highly competitive, with more freelancers than clients. Therefore, you need effective marketing strategies to attract and retain clients for sustainable business growth.
Fortunately, this article discussed 18 client attraction and retention strategies, from leveraging your network to offering loyalty packages to clients. It also outlined some communication and management tools for client satisfaction and retention. You’ve also seen the solutions to some common client attraction and retention challenges. Finally, Dakota’s success story with these strategies undoubtedly inspires you as a freelancer.
Therefore, why wait to get there? Evaluate your current strategy and start implementing these strategies today to win and keep clients and boost your freelance business! Follow these strategies systematically as outlined: first, attract, then keep your clients to ensure sustainable business growth.
---
## The Only Guide You'll Need to Speed Up WordPress Site
- URL: https://levamo.com/blog/speed-up-wordpress/
- Category: wordpress
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Get a faster WordPress site! This guide reveals essential speed secrets.
While web development trends may come and go, one thing is certain: websites will always have a need for speed.
In this guide, we are going to share with you a treasure trove of WordPress speed secrets you can (and should) use to keep your visitors happily clicking around and interacting with your site.
We launched Levamo for just this reason: speedy WordPress hosting specifically for dynamic WordPress sites where users frequently interact.
We won’t focus only on dynamic sites here, though, but rather all kinds of WordPress sites.
After all, speed isn’t a bonus for websites, it’s the entire point - letting people connect instantly over the internet.
## Speed Up WordPress Site - Why is it a Necessity?

The ideal page load speed for any website is anything less than 3 seconds. Longer than that, and the visitor staring at your loading icon starts to get annoyed.
Imagine it yourself: Count 1… 2… 3… **Gone,** and never to return, right? It’s funny how that works, when before the internet people would happily wait a week or longer for a letter to arrive in the post.
But like it or not, that’s what we as web maestros are working with. If your site doesn’t load in a flash, you might as well pack it up or content yourself with a tiny fraction of your site’s potential.
This number isn’t just a hunch; it was studied by Google and [presented in 2016](https://www.marketingdive.com/news/google-53-of-mobile-users-abandon-sites-that-take-over-3-seconds-to-load/426070/). And ask yourself, with all the misery that exists in this world, do you *really *want to add to it by launching a clunky website that makes people frustrated or angry?
Here are more reasons why your WordPress website speed is so important:
- **User experience:** Slow sites don’t just suck. They really ought to be considered “broken”, like a tap that merely drips. Poor load time is one of the top contributing factors to high bounce rates, second only to having a downright ugly website.
- **SEO ranking:** Google added [site speed as a ranking factor](https://searchengineland.com/google-now-counts-site-speed-as-ranking-factor-39708) back in 2010 and other search engines like Bing also use load time as a key ranking signal.
- **Increased sales conversions:** The quicker your site, the more likely people are to become customers of whatever products or services you might be selling.
- **Higher traffic potential:** A well-optimized site is able to handle higher workloads and, thus, serve more traffic.
- **Accessibility:** Mobile users and those in rural areas don’t always have fast internet, so a quick site ensures wide accessibility.
Now that you know the reason why you need a fast WordPress site, let's take a detailed look at how to speed up WordPress site effortlessly.
## WordPress speed secrets: revealed!
Optimizing for site speed has been a problem that many have worked on since the beginning of the web. With evolving HTTP versions such as HTTP/2 and HTTP/3 (HTTP over QUIC), this work continues at the upper echelons. However designing an internet protocol is outside many ordinary webmasters’ hands.
Regardless, there are many things that you *are* in control of. That’s what you’re here for, so let’s get started with speed up WordPress site, step by step.
### 1. Choose high-performance hosting
Most hosting companies are general-purpose providers. Not optimized for any one platform, but overall good enough for anything you can throw at them. That’s okay if you are running a simple blog or online store. But for anything more demanding there is *massive* potential for optimization.
Hosting: how it all comes together.
Here are the crucial hardware specs to look for in a high-performing web host:
- **CPU:** Responsible for the processing of code such as PHP (and much more, as it is the brain of the entire operating system). Generally, the more CPU/vCPU cores, the faster your site will be able to process and show pages to users.
- **RAM:** The OS, web server software (e.g. LiteSpeed), related programs (e.g. MariaDB), and other data all need to fit inside RAM to run properly. The more traffic (esp. concurrent traffic) you get, the more RAM you need to keep the CPU fed with data for processing all those requests.
- **Storage:** A good web host will provide fast SSD drives to fit all your website files and media, with swap space to spare. When a server reaches peak traffic it always risks running out of RAM. That’s when a server really slows down and bad things happen, system-wise, if no swap space is available.
- **Networking:** The best hosting hardware is nothing without a fast network. Beyond offering high bandwidth rates, high-performance hosting often relies on CDN technology where servers are distributed worldwide to serve visitors with the lowest possible latency.
Did we mention that Levamo’s [cloud hosting plans](/pricing/) tick all these boxes? That’s because we are bucking the trend of providing just-good-enough hosting services. Our new way? Putting speed first, no matter what.
### 2. Adopt a lightweight theme
Before going into all the major [WordPress speed optimization](/blog/wordpress-speed-optimization/) techniques, the type of theme you start off with is very important. You might find a theme with a style that you love, but it comes with dozens of features that you will never need.
Consider all those features as bloat that may ruin your WordPress speed. After all, the appearance of any theme can be easily changed to your liking with custom CSS or third-party page builders like Elementor or Beaver Builder.
GeneratePress, a lightweight theme for WordPress.
Check out these five of the fastest, most lightweight WordPress themes in 2024, according to WP Rocket:
- [Hello](https://wordpress.org/themes/hello-elementor/)
- [Astra](https://wordpress.org/themes/astra/)
- [OceanWP](https://wordpress.org/themes/oceanwp/)
- [GeneratePress](https://wordpress.org/themes/generatepress/)
- [Kadence](https://wordpress.org/themes/kadence/)
The same advice goes for plugins. If you need a specific feature that a simple plugin offers, always choose the simple plugin over an all-in-one plugin that has what you need, but also lots that you don’t. Unless the simple plugin is badly coded, it won’t put as much load on the server as a complex one.
### 3. Leverage caching plugins
Caching means to save the results of some processing (e.g. the output of PHP code) on the hard disk or in RAM so that they can be called upon later without having to reprocess the same code or data over and over.
The cumulative benefits are enormous. Not only does caching greatly reduce the loading time of the web page being shown to a visitor, but it also reduces the workload of the CPU and frees up RAM (even when you are storing cached data in RAM itself).
With caching, sites that would ordinarily need a hefty server now only need a fraction of the hardware resources to handle the same amount of traffic.
Here we will explain the common types of caching for WordPress.
#### Page caching
When a visitor loads a web page, the server needs to look at all the PHP code for that page, interpret it, and execute it. Finally, it spits out the result to the browser as viewable HTML.
Instead of doing this every time for every visit, you can store the result (the processed web page) in a page cache.
Now, the web server only needs to pull in the cached page from RAM as a static (i.e. fixed and readily-available) resource instead of having to compute it again and again from disk for every visitor. Once the page cache has stored all your website pages (a process called building the cache), page load times are dramatically reduced and everyone is happy.
#### Object caching
Object caching is a method of caching that stores the results of database queries in RAM. These results can then be called from RAM the next time they are needed without having to continually query the database.
A caveat of object caching is that it can lead to excessive memory usage, so caution is advised when setting it up. On the other hand, it reduces CPU workload since the CPU doesn’t have to keep processing database queries; it already has the data ready in RAM.
Scientists believe this is how caching works at the subatomic level.
One of the top ways to cut your WordPress speed in half all on its own, caching should generally be tackled last when setting up a new site. This is especially true for sites that are being modified and updated live (instead of on a separate staging site, which some amateur WordPress admins tend not to bother with).
Setting up caching is notorious for giving webmasters of even the simplest sites much pain and suffering. For one, you will have to keep flushing the cache each time you make new changes. Luckily, many caching solutions handle this automatically.
Further, a single caching misconfiguration can bring down the whole site. Other times, half your site content is stuck in some kind of limbo, while the rest is fine. Figuring out how to fix it isn’t a matter of just clicking around; you usually have to go and read the user manual at some point.
Caching is a complex topic, but true to form, WordPress caching plugins can help save you much time.
#### WordPress performance plugins with caching
Here are the top WordPress plugins that offer caching functionality (in no particular order):
- [W3 Total Cache](https://wordpress.org/plugins/w3-total-cache/)
- [WP Super Cache](https://wordpress.org/plugins/wp-super-cache/)
- [Hummingbird](https://wordpress.org/plugins/hummingbird-performance/)
- [WP Fastest Cache](https://wordpress.org/plugins/wp-fastest-cache/)
- [Comet Cache](https://wordpress.org/plugins/comet-cache/)
- [WP-Optimize](https://wordpress.org/plugins/wp-optimize/)
- [Autoptimize](https://wordpress.org/plugins/autoptimize/)
- [WP Rocket](https://wp-rocket.me/)
- [LiteSpeed Cache](https://wordpress.org/plugins/litespeed-cache/)
- [Cache Enabler](https://wordpress.org/plugins/cache-enabler/)
- [Speed Optimizer](https://wordpress.org/plugins/sg-cachepress/)
- [Perfmatters](https://perfmatters.io/)
- [WPSpeed](https://wordpress.org/plugins/wpspeed/)
- [PageSpeed Ninja](https://wordpress.org/plugins/psn-pagespeed-ninja/)
Many of these caching plugins also let you do other neat things to increase your WordPress speed such as lazy loading images and minifying JS/CSS. We will cover these extra optimization features separately in this guide so you know how to get the most out of the plugins above.
But first, let’s cover the specific caching solutions that work best for our customers, especially those with lots of dynamic content that is often difficult to cache correctly and efficiently.
#### Opcode caching (OPcache)
Other than page caching and object caching, there is another important type of caching called opcode caching, which is performed by a PHP extension called OPcache.
Any time a PHP script is executed for the first time, the OPcache engine compiles the script as bytecode in RAM. When the same script is called in the future, the cached bytecode is loaded from RAM without the script needing to be read and interpreted from scratch from the hard disk.
Like page caching, OPcache increases the page load speed and reduces disk I/O, which can also prevent wear-and-tear on the server’s SSD.
#### OPcache vs. page caching
However, OPcache is not identical to page caching since page caching stores the actual output of a PHP script (like the final HTML of a page written in PHP) as a static file that can be instantly loaded from RAM, whereas OPcache only stores the script code itself in its cache in RAM, in a machine-friendly form (bytecode) that makes it quicker to execute as needed. In OPcache, only the script code itself is cached, not the final output.
For dynamic and highly interactive WordPress sites that change a lot in terms of the updating of small pieces of data (e.g. real-time notifications/messages/profile updates/page interactions such as ‘likes’ or ‘votes’, etc.), OPcache makes a lot more sense than page caching because page caching isn’t designed to handle these events. OPcache, on the other hand, doesn’t care about the actual content and simply speeds up the processing of scripts at the server level in general.
In the BuddyBoss podcast, “Wes Tatters on Levamo: The Journey Towards an Optimized [BuddyBoss Hosting](/buddyboss-hosting/)”, Levamo’s Managing Director, Wes Tatters, touches on how OPcache works, why it’s so crucial for performance, and why so many other providers have failed to get it right. Watch the episode here:
https://youtu.be/VX22ANhY1WI?si=dmdaVBhVpWDlrokd
Meanwhile, WP Rocket have written a great [guide on how OPcache works](https://wp-rocket.me/blog/best-php-accelerators/) and how to configure it. Check it out.
#### LSCache
LSCache is a bespoke page caching system developed by LiteSpeed, the web server that Levamo uses for its excellent ability to handle high-concurrency traffic. Enabling server support for LSCache for our customers is just one of the ways we take the pain out of caching for you.
#### Redis Cache (via Relay) and Object Cache Pro
Another superior caching system that we provide for our dynamic website hosting is Relay, a special type of Redis client.
The reason why Relay is so good for dynamic sites is a feature called active invalidation. Active cache invalidation ensures that any time a piece of information changes on an interactive site, the old cached version of that data is invalidated and the new version is then immediately re-cached. And that is exactly what dynamic sites need: the “active” elimination of stale cache content, so users always see timely, accurate updates.
What’s more, we also provide free usage of [Object Cache Pro](/blog/key-db-and-redis/), which is the premium version of Redis Object Cache. Object Cache Pro helps reduce a server’s workload by storing database queries as objects that can be cached and quickly executed from RAM. It’s highly recommended to help speed up your site by lowering the workload on your database, and thus, the CPU.
### 4. Optimizing images for speed
According to [The HTTP Archive](https://almanac.httparchive.org/en/2022/page-weight), as of 2022 the average page weight (size of a page in bytes) for most web pages in the world is 2,315 KB on desktop and 2,020 KB on mobile.
In other words, that’s an average page size of **~2 MB** for all web pages on Earth.
From the same study, out of that 2 MB page size, images are the largest content type with 1,026 KB taken up by images on desktop and 811 KB on mobile.
Simplified again, that means roughly half of the total file size of every web page, on average, is taken up by images. Now that’s a fact we can work with, confirming that image optimization should never be just an afterthought.
Image optimization for WordPress is all about keeping image file sizes as small as possible. There are a few ways you can do this, explained below.
Image optimization.
#### Choose the appropriate format
Though not widely adopted as yet, [WebP](https://developers.google.com/speed/webp) is touted as the new image format standard for the web. It is more efficient at compressing images down to web-friendly file sizes than both PNG and JPEG, and that’s about all you need to know, at least according to Google.
If you prefer to keep using JPEG/PNG for technical (or other) reasons for the moment, then here’s what you need to know about these older file types.
PNG retains the best image quality for drawn or computer-generated images (illustrations, art, etc.) while JPEG is best for real-life photographic images because you can better compress JPEG photos without as much image degradation compared to PNG.
In summary, choose WebP format by default for all images unless you have a good reason not to. For photographic images, use JPEG, otherwise go for PNG.
#### Resize and compress images
There’s no point providing large, super high-resolution images if they are only for screen display purposes (as opposed to print publishing).
Either downscale and compress your images in a tool such as Photoshop or GIMP, or let an image optimization plugin like [Smush](https://wordpress.org/plugins/wp-smushit/) help you do all this automatically.
Tip: [TinyPNG](https://tinypng.com/) is a free online image compression tool that does an amazing job of compressing images while retaining quality. It is useful if you don’t want to add an extra plugin for this and aren’t familiar with image editing software.
This screenshot of TinyPNG.com was 617 KB. After TinyPNG’ing it, it’s now 178 KB.
#### Enforce image upload limits
For user-generated content sites like social networks and forums, ensure that image uploads are restricted to a certain max file size and/or resolution.
Note that an appropriate limit depends on the type of site; a photography forum might have much larger limits than other sites.
Tip: You can enforce upload file size limits at a server-wide level by editing the *upload_max_filesize* option in your “php.ini” config file.
#### Set all images to 72 DPI
The optimal DPI (Dots Per Inch) for images displayed on any device screen is 72. 300 DPI, the standard for print publishing, results in a much larger image file size than 72 DPI for no noticeable difference in quality.
There is never a good reason to provide 300 DPI images unless your site handles images for print publishing (e.g. book covers, print magazines, advertising billboards, T-shirts). Think of print-on-demand sites like Etsy or Zazzle.
#### Use “srcset” for responsive images
In HTML, the *srcset *attribute lets you specify different sizes of images to be served to visitors depending on the device they are using or the actual viewport. This lets you provide just the right image size for the right device.
You can also do other sensible things with srcset such as type-switching. Type-switching is where you can specify whether images should be served as the new WebP format, falling back to PNG or JPEG if the browser doesn’t support WebP.
### 5. Reducing HTTP requests
When a visitor loads a page, all the different files that make up your website (*.html, *.css, *.js, *.webp, etc.) need to be fetched individually from the web server.
This is usually fine and dandy for files that are hosted locally on the server, but web pages often also need to fetch external resources such as JavaScript libraries and other scripts.
The key concept here in terms of website speed is **Round-Trip Time (RTT). For every external HTTP request that a browser makes while loading your website, the browser has to wait for that other server to: 1) receive the request, and for the server to, 2) acknowledge the request and send a response**.
Naturally, too many HTTP requests can introduce a lot of unnecessary latency and impact your overall WordPress speed score.
#### A word on HTTP requests from ad networks
One of the worst offenders for adding lots (and lots) of HTTP requests is advertising networks. Not only do these HTTP requests all add up, but you also have no control over the latency of each source, which may have their own ungainly Round-Trip Times.
As a rule, if you are monetizing your website with display/text ads on an ad network such as Google AdSense or Mediavine, your page speeds are going to suffer.
There’s not much to be done about ad network overhead in terms of HTTP requests, which is why it’s so important to keep the ads you show to a minimum. But even so, ad networks often add a dozen third-party trackers to a page despite only showing one or two ads.
If this is a deal-breaker, consider alternative monetization methods such as affiliate marketing, where you are more in control over how ad slots are displayed and tracked. Another idea is to use an ad manager plugin such as [AdRotate](https://wordpress.org/plugins/adrotate/), but this may not totally solve the problem.
#### Suggestions for reducing HTTP requests:
Here are some suggestions on how to minimize your total HTTP requests:
- Combine multiple CSS and/or JS files into one file for each file type. For instance, all your different CSS style files can be lumped into a single large styles.css file.
- Host as many resources (images, fonts, CSS, JS) as possible locally on your hosting server itself. Note that popular libraries such as JQuery are now provided within WordPress core so you don’t need to request them from a third-party.
- Minimize the amount of plugins your site uses, or swap out a plugin that makes unnecessarily many HTTP requests for one that doesn’t.
Ultimately, every time the browser has to wait for an HTTP request to be received, it can potentially block the loading of the rest of the page. To avoid this without reducing any HTTP requests, you should learn about [how to eliminate render-blocking resources](https://jetpack.com/blog/wordpress-eliminate-render-blocking-resources/) such as by deferring scripts and optimizing the loading of CSS.
### 6. Database optimization
Not many WordPress webmasters tend to treat their MySQL/MariaDB database as an area for optimization. This isn’t surprising, since messing with the database is always risky. It’s where all your website data is stored, after all, and one mistake can be very costly.
As such, we recommend you back up your database at least two times over, preferably with two different plugins or methods, before doing anything at all with it.
Optimizing a database mainly involves cleaning up old data that doesn’t need to be there anymore. This data may include:
- Inactive users: admins, editors, authors, subscribers, and so on.
- Post revisions, which have a habit of piling up over time.
- Spam and other possibly useless comments such as pingbacks and trackbacks.
- Trashed items (posts, comments, etc.).
Some reliable plugins that can help you with your database maintenance are:
- [WP-Optimize](https://wordpress.org/plugins/wp-optimize/)
- [WP-Sweep](https://wordpress.org/plugins/wp-sweep/)
- [Advanced Database Cleaner](https://wordpress.org/plugins/advanced-database-cleaner/)
- [Optimize Database after Deleting Revisions](https://wordpress.org/plugins/rvg-optimize-database/)
### 7. Using a Content Delivery Network (CDN)
A Content Delivery Network is what it sounds like, a network of servers that helps to deliver content to users.
It’s a pretty simple concept, really.
These servers are distributed around the world for one main reason: to improve the latency from the server to the visitor. The closer a server is to a visitor, geographically, the faster the data can be received. This helps reduce Round-Trip Time in many scenarios, especially relevant when your website makes a lot of HTTP requests.
A CDN consists of multiple Points of Presence (POP), which is a fancy way of saying they have servers in different locations. CDNs typically use techniques like load-balancing and anycast to ensure that visitors get served by the closest server that also has enough resources to handle the traffic without breaking a sweat.
At Levamo, we focus on doing everything possible to get your website data to your users in no time at all, no matter where they are. As part of this mission we offer a [free WordPress CDN](/cloudflare-cdn/) for all our WordPress hosting plans, so your content can be distributed not just from one international server, but locally from servers all over the world.
### 8. Ensure mobile responsiveness
Mobile responsiveness has been a best practice in web design for quite some time. Not only does it make good design sense, but it also lets your website provide smaller, faster-loading images on the mobile version as compared to the desktop version.
Responsive design.
Thankfully, almost all modern WordPress themes are built with mobile responsiveness in mind, so this is more of a reminder than anything else. You are welcome. Oh, and don’t forget to do the dishes.
### 9. Minify JS, CSS, and HTML files
Minification is a very common speed-boosting technique, and easy to implement on any site.
It is simply the process of removing all non-essential characters from the source code of your JS, CSS, or HTML files. This includes white space and newline characters as well as code comments. While these characters are helpful to humans reading the source code, computers don’t care about them at all.
Stripping them out of your source code with a WordPress performance plugin or other method can reduce their file size by a good amount. There are 35 white space characters in this paragraph of text alone.
### 10. Lazy loading media
Lazy loading is a super simple concept to increase your WordPress speed: images and other bulky media are not all loaded immediately when the page loads. Instead, the images are held back until the visitor scrolls down to where the image would be shown. At this point, the browser loads the image from the server and it pops into view.
This has a double-sided benefit. For the visitor, the page initially loads very quickly, as if there were no images to begin with. Meanwhile, you can save a lot of bandwidth over time because not every visitor will actually scroll all the way through a page. Awesome!
Lazy loading comes as a feature you can enable in several WordPress performance plugins such as W3 Total Cache. There are also standalone lazy load plugins such as [a3 Lazy Load](https://wordpress.org/plugins/a3-lazy-load/) and the aptly named [Lazy Load Plugin](https://wordpress.org/plugins/rocket-lazy-load/).
Also Read: [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
### Going further
Beyond all the above, there are many other optimizations that webmasters aren’t currently using to their benefit, since they require deep knowledge of Linux computing and how to properly configure operating systems and web server software (e.g. Apache/ nginx/LiteSpeed, MySQL/MariaDB, load-balancers, reverse-proxies, [PHP workers](/blog/php-workers/), etc.).
From an engineering standpoint, that’s simply another reason why we encourage WordPress website owners of all kinds to take advantage of managed dynamic WordPress hosting like us.
We’re biased, we know, but we also know your passion is your website and your community; not the toil and slog of system administration. Check out our high-performance managed WordPress and [managed WooCommerce hosting](/managed-woocommerce-hosting/) plans to find out how we can help host you.
## How to measure your WordPress speed?
Now if you did all those stuffs to speed up WordPress, how do you know that your website speed is now improved?
### WordPress speed testing tools
The easiest way to figure out what the above metrics mean in practice is to hop onto a website speed test website that tracks them for you.
These excellent performance testing tools help you see what’s going on with each metric as they pertain to your site in action:
- [PageSpeed Insights](https://pagespeed.web.dev/) (Free)
- [WebPageTest](https://www.webpagetest.org/) (Free)
- [Pingdom Website Speed Test](https://tools.pingdom.com/) (Free)
- [GTmetrix](https://gtmetrix.com/) (Free/Paid)
- [DebugBear](https://www.debugbear.com/) (Free/Paid)
- [Request Metrics](https://requestmetrics.com/) (Free/Paid)
- [PageVitals](https://pagevitals.com/) (Trial/Paid)
A neat benefit of using a tool as above, rather than running tests from your own PC, is that they can test your site speed from multiple different countries. If your server is located in the U.S. but also serves a European audience, you can find out what kind of latency is involved for those far-flung reaches of the world.
Some of these website performance tools can also simulate your site with different browsers and device models, helping you ensure top speed no matter how your site is accessed.
Also, don’t forget about [Google Search Console](https://search.google.com/search-console/about), which can tell you much about your website performance according to real users on its Core Web Vitals page.
### Inspect with developer tools
You can also gain a lot of info about your website’s performance and networking by using the developer tools that are built into all web browsers. To access these tools, simply right-click anywhere on your website and select “**Inspect**”.
Next, head to the “Network” tab and refresh the page. Now you will see a list of all the network requests that your browser makes and exactly how long it takes to receive them individually.
Hey, that’s us!
If you are a new developer, designer, or webmaster, you will learn to love these developer tools as they are mostly intuitive and make web development and debugging processes a breeze.
Simply, no site speed issue can remain a mystery for long with the power of “Inspect”!
### Load testing tools
One of the final tasks you should do is load testing. With performance monitoring tools, you know your website loads instantly for any given visitor, but what about when thousands or more reach the site at the same time? Can your site actually handle all those concurrent users?
Here are some great load testing tools you can use to test your site’s resilience to high traffic:
- [Grafana k6](https://k6.io/)
- [Loader.io](https://loader.io/)
- [LoadForge](https://loadforge.com/)
- [LoadView](https://www.loadview-testing.com/)
- [WebLOAD](https://www.radview.com/webload-download/)
- [Loadero](https://loadero.com/)
*Warning: *Some load testing tools are capable of sending enormous amounts of traffic to your website all at once. This may incur unwanted bandwidth costs, so be careful.
### Query Monitoring
Just as important as server and site monitoring, however, is keeping your finger on the pulse of how your community is experiencing your site. You can’t fix or improve what you don’t know about, so listening to your actual users and asking for feedback will be your best defense against the pitfalls of complacency.
Oh, and, one last hearty recommendation: install the [Query Monitor](https://wordpress.org/plugins/query-monitor/) plugin. It sits in your admin dashboard and gives you a ton of useful information about how your site is performing on any page you have open in the browser.
### What should be your target speed?
The problem is, how do you know what level of website speed is expected, at a minimum, by most website visitors? Other than the 3-second rule, of course.
With well-studied industry metrics and benchmarks, of course. And the benchmark that is now the standard in the industry is combined on Google's [Core Web Vitals](/blog/core-web-vitals-and-seo/).
Not even Reddit gets a perfect score on PageSpeed Insights.
Here are the metrics for measuring the speed of a WordPress website, or any site at all:
- **Latency:** How long it takes for a website to respond when a visitor sends a request. Latency is mostly dependent on location: the closer the hosting server is to the visitor, the lower the latency.
- **TTFB (Time To First Byte):** Similar to latency, this is how long it takes for the server to respond to any request, measured by the time it takes a browser to receive the first byte of data.
- **FCP (First Contentful Paint):** How long it takes for a website to show something (anything!) while loading. This is a measure of perceived load speed, in that a fast FCP time can quickly tell the user whether the site is actually loading or has become stuck on a blank page.
- **LCP (Largest Contentful Paint):** Another measure of perceived load speed, this is how long it takes for the visitor to see that the main content of a page has been loaded. It is defined as the point at which, during page load, the largest text or image block becomes visible to the visitor.
- **CLS (Cumulative Layout Shift):** Web pages might delay the loading of certain visual elements (such as popups, menu panels, etc.), gradually shifting around the layout of the content. The sooner your webpage settles on a final layout while loading, the better.
- **INP (Interaction to Next Paint):** How long it takes for the website to visually respond after a visitor takes some action (e.g. clicking a link or button). When you snap your fingers, the site must dance!
These metrics may have awkward acronyms but they are quite self-descriptive. You can check on [Google PageSpeed insights](https://pagespeed.web.dev/) to track each of these metrics.
## Wrapping up
Phew, you made it to the end? On behalf of all your future visitors and web users everywhere, thank you for recognizing the need to speed up WordPress website as fast as possible!
We know it’s not always easy, but by following the advice provided in this comprehensive WordPress speed guide, you are helping make the web a better, more joyful technology for everyone. Nothing could be more commendable.
In summary, here’s a recap of the main points we have covered:
- Why WordPress speed matters.
- How to measure the speed of a WordPress website.
- The top 10 WordPress speed secrets, including choosing a high-performance, [fully managed WordPress hosting](/managed-wordpress-hosting/), leveraging caching, optimizing your images, reducing HTTP requests, minifying files, and more.
- Potential pitfalls of optimizing for speed in various ways, how to monitor website performance over time, and how to load test your website to check your optimizations at scale.
Do you know of any other tips or tricks to improve the performance of WordPress?
Please let us know - once you’ve shared this guide on social media, of course!
## Frequently Asked Questions

### Why is my WordPress so slow?
[WordPress can be slow](/blog/why-is-my-wordpress-site-so-slow/) due to too many plugins, unoptimized images, poor-quality hosting, no caching, or using a heavy theme.
### How do I increase my WordPress speed?
Install good caching plugin, optimize images, limit plugins, update everything, use lightweight themes and use reliable hosting.
### How to speed up WordPress search?
Use a hosting like Levamo that offers ElasticSearch by default to speed up WordPress site search functionality.
### How do I clear the cache in WordPress?
In the settings of your caching plugin (W3 Total Cache, WP Rocket), click [Clear Cache/Purge All Caches](/blog/wordpress-clear-cache/). Alternatively you can do that from your hosting backend, if they have that feature.
### How do I make WordPress load faster?
Couple that with caching, image optimization, a fast theme, CDN integration, and fewer plugins for low load time and high performance.
---
## Maximize Your Earnings: Pricing Strategies for WordPress Projects
- URL: https://levamo.com/blog/pricing-strategies-for-wordpress/
- Category: website-development
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Price WordPress projects right & boost earnings. Get practical strategies now.
WordPress
The pricing strategy for your WordPress work can sometimes feel like a guessing game. What if you could crack the code and know exactly what to charge? Most developers working with WordPress typically take home earnings of anywhere between [$10,000 to $100,000](https://www.ziprecruiter.com/Salaries/Wordpress-Developer-Salary).
This is the kind that pays the bills and lets you enjoy the extra things in life. To get there, you need to play the pricing game smart.
We will walk through the nuts and bolts of pricing strategies for WordPress projects. By the time you are done with this article, you will be ready to price your [WordPress projects with confidence](/blog/best-online-business-ideas/).
## Insights Into the WordPress Development Market
The WordPress platform is constantly alive with opportunity. For those in the know, it's the go-to place for creating websites that click with users and tick all the right boxes for functionality. However, with opportunity comes competition, and to stand out, you need a strategy.
The market for [WordPress development](/blog/hosting-for-business/) is as diverse as the people who use the internet. Some clients need a simple blog to share their thoughts, while others are on the lookout for a robust online store to sell thousands of products.
Your neighbor might want a personal portfolio, and a local business down the street, a snappy landing page. The point? Every project is unique, and so should your pricing.
Most WordPress developers are pulling in impressive figures, but those who truly understand their market can earn even more. They know the price tags that hang off the different types of WordPress projects, and they use that knowledge to their advantage.
It's about recognizing that a one-size-fits-all pricing model is a relic of the past. The modern [WordPress freelancer](/blog/wordpress-freelance-success-guide/) or agency is nimble and adjusts its sails to the wind of market demand and client budgets.
It's not just about what others are charging, though. It's about the value you deliver.
Seasoned pros often command higher fees, because they've honed the art of translating that experience into tangible benefits for their clients. Newcomers shouldn't count themselves out, either. What you lack in years, you can make up for with:
- Passion
- The latest know-how
- A keenness to please
## Hourly, Fixed Fee, and Value-Based Model

When you're in the world of WordPress development, figuring out the best way to charge for your services can make all the difference. There are three main pricing models most developers dance with:
- Hourly rates
- Fixed fees
- Value-based pricing
Let's break down the beat of each one so you can find your rhythm.
### Hourly Rates: Counting Time as Money
Charging by the hour is straightforward. You can set a rate, clock your hours, and invoice for the time spent. It's great for projects that are hard to predict or when you're just starting out and learning the ropes of how long tasks can take.
The upside? Every minute you're working, you're earning. But there's a catch: if you become quicker and more efficient, you'll actually earn less for doing the same job.
Plus, clients can get antsy about open-ended budgets where the ticking clock is the meter running up their bill.
### Fixed Fees: The One-Price Hat Trick
A fixed fee means you quote a price upfront for the entire project. Clients love it because it's predictable, and you can love it too because it rewards efficiency. If you can do the job faster while maintaining quality, you're effectively giving yourself a raise.
But beware, underestimating the work can lead to long hours for not enough pay. Nail the estimate, though, and it's smooth sailing.
### Value-Based Pricing: The Game Changer
This one flips the script. Instead of pricing based on what you do, value-based pricing looks at the worth of the work to the client. If the new website is going to be a major money-maker for them, your cut reflects that potential.
It requires a deep dive into understanding the client's business and the impact your work will have. If you align the price with the perceived value, it can lead to higher earnings for you without the client feeling overcharged.
Now, which pricing strategy do you choose? It might be a bit of each. Some projects might call for a meter of hourly rates; others for the simplicity of a fixed fee.
When you can, go for the win-win of value-based pricing. The trick is to know your project, know your client, and, above all, know your worth. Keep these in mind, and you are set to compose pricing that plays the right tune for your WordPress business.
## Factors That Dictate WordPress Project Costs
When pricing your WordPress projects, it is important to look at the bigger picture. Each aspect represents a factor that will affect overall costs. While your time is valuable, there are unique elements that you bring to your projects.
Take each factor of your projects into consideration so that you can price your services fairly for yourself and your client.
### Scope Complexity: Features and Functionality
Every website is a world unto itself, with some as straightforward as a small town and others as complex as a bustling metropolis. The more features and custom functionalities a project requires, the higher the cost.
Think:
- eCommerce integrations
- Membership systems
- Interactive user interfaces
### Timeframe: The Fast-Track Premium
Sometimes a client needs things done yesterday. When projects come with a rush tag, they also carry a premium price.
Time is a commodity, and like any express service, speed can come at a premium so that you can prioritize someone's work over other projects.
### Client Type: Understanding Who You're Dancing With
Who's asking for the website?
- A solo entrepreneur?
- A non-profit?
- A big company?
The size and type of the client can influence the project's cost. Larger organizations often have more complex needs and deeper pockets, while smaller clients might be working with a tighter budget but offer more creative freedom.
### Your Experience: The Price of Wisdom
Your track record and skills play a big part in pricing. If you've been building WordPress sites that wow for years, you can, and should, charge for that expertise.
Clients are just not paying for your time but can reap the benefits of the years of learning and projects that got you to where you are, and your prices should reflect that.
### Maintenance and Updates: The Road Ahead
Websites, like gardens, need tending to grow. Ongoing maintenance and updates are all part of the post-launch package you can offer.
Clients may not know they need these services yet, but including them can ensure a website's longevity and your continued relationship with the client.
## Align Market Rates With Your Business Goals

The sweet spot of pricing doesn't only boost your profit; it accelerates it faster than chasing after more projects ever could. It's the difference between keeping afloat and sailing the high seas of success.
But many shy away from pricing adjustments, worried about walking the plank and losing clients.
A [slight improvement](https://www.investopedia.com/terms/o/operating_profit.asp) in your pricing strategy, as little as 1%, can increase your operating profit by over 11%. That's a significant boost to your bottom line.
On the other hand, a small misstep in pricing, such as undervaluing your service by 1%, could wash away the same amount of profit. This seesaw effect shows the power of pricing in the WordPress sea of opportunities.
In the WordPress realm, it's crucial to manage not the price you put on your invoice but the real transaction price. That's the price that truly sails into your bank account after all the discounts and negotiations.
It's what you really earn after the haggling is done. This transaction price is where many developers leave money on the table, and with it, the chance to make their business more profitable.
Here's how you can navigate these waters:
### Understand the Currents of Supply and Demand
Grasp the ebbs and flows of the WordPress market. When [demand is high](https://fastercapital.com/content/Demand-based-pricing--Maximizing-Profits-with-Peak-Pricing-Techniques.html), and your type of work is in short supply, you can set sail with higher prices.
But if there's a storm of competition, you might need to offer more competitive rates.
### Map Out Your Product Market Strategy
Know the value you're bringing to your clients. If your WordPress site is the flagship that's bringing in the big catches for your clients, your prices should reflect that. Use tools like market research to understand what features clients treasure the most and set your prices accordingly.
### Manage Each Transaction With a Spyglass
Zoom in on each deal. Whether it's the base price, the terms, or the discounts, every piece counts. Align your pricing decisions with the strategic positioning of your services in the market.
So, as you set your compass to navigate the pricing strategies of your WordPress projects, remember that even the most seasoned professionals in the industry adjust their sails to catch the best wind.
Charge too little, and you will have trouble paying the bills. Charge too much, and you might find potential clients passing you up. But get it just right, and you'll be sailing towards the horizon of [success with satisfied clients](/blog/importance-of-a-web-host/).
## Techniques to Assess and Set Project Prices
It is always a bad idea to pull numbers out of thin air. For each project, it is absolutely crucial that you understand each project's unique circumstances.
While you can't predict the future and each situation, you can form a basic formula to refer to when needed. Take a look at how you approach each project with confidence.
In[ web design and development](/blog/website-design-in-wordpress/), a utopian scenario where clients present you with a neatly packaged scope of work is rare. The reality is that clients don't live and breathe web design or WordPress. They're masters of their own trades and look to you for this particular project.
As a WordPress expert, your role extends beyond coding and designing; you're an educator and guide. Your clients depend on you to:
- Show the path through the web design process
- Share insights on content strategy and website strategy
- Place their [business objectives](/blog/fast-server-speed-tools/) at the forefront
- Provide honest and transparent cost estimates upfront
During this discovery, each layer reveals more about the client's needs and goals, which helps map the terrain of the project.
However, the course isn't always clear, and unknowns are common.
Often, the full scope of a WordPress project isn't clear at the outset. Skipping the due diligence phase is risky and potentially costly. Make the discovery phase as integral to your process as the design or development itself.
Beyond initial interviews, schedule deep-dive sessions with your client to extract every detail about what the project needs to achieve.
### Accounting for Every Aspect of the Project
It's easy to focus solely on the time you'll spend coding or designing when estimating project costs. However, this narrow view can lead to underpricing, as it often fails to account for the myriad of other tasks that are critical to the project's success, such as:
- Client communication
- Project management
- Unforeseen challenges
Adopt a holistic approach to your pricing strategy. Develop a comprehensive pricing model that includes all facets of project execution.
### Base Your Price on Value, Not Fear
The temptation to lower your prices to match or undercut the competition is common, especially when you're eager to secure a new project. However, this 'should be' pricing strategy, driven by fear rather than data, can lead to significant underestimations that undermine your business's financial health.
Let the distinct value and expertise you bring to each project guide your pricing decisions. Compete on the quality and [unique solutions you provide](/blog/monarx-security/), not just on cost.
Educate your clients about the benefits and value of your work and how these justify your pricing. When clients understand the rationale behind your fees, they're more likely to perceive the cost as a reflection of your worth and the tangible benefits they will gain, rather than just a number.
## How Pricing Influences Client Choices and Expectations

Your pricing often gives the first impression of your quality and service level. High prices might suggest top-quality service and attract clients who don't mind paying more for better results.
On the other hand, lower prices may appeal to those on a budget but could also make some people wonder if the quality might be lower.
It's important that your price matches what you offer. If there's a mismatch, clients might feel let down, and this can hurt your reputation.
Be clear about what each price level includes to avoid confusion and make sure clients know what they're getting. If your services are priced higher, explain why this is and what extra benefits you provide, like faster service or more personalized work.
How you set your prices can make clients think differently about the quality of your services. If prices are too low, people might doubt the quality; if they're too high, they might expect more than you can deliver.
To manage expectations, use real examples like client feedback and project outcomes to show the value you bring.
As your skills and business grow, your prices will likely need to change. Review and adjust your prices to keep up with your experience, changes in market demand, or your costs. Be open with your clients about any price changes and why they are needed.
## How to Enhance Your WordPress Offerings
If you are looking to find ways to increase your earnings, a good way to make your services stand out is by adding more value for your clients.
Clients usually need more than just a basic website. They're looking for solutions that tackle their specific problems and help them meet their goals.
For example, you can help their sites show up better in search results with SEO optimization, or make sure their sites are safe with enhanced security features. Another big help is making sure their website loads quickly and runs smoothly, which is essential for keeping visitors happy and improving the site's rank on search engines.
Each client is unique, and customizing your services to address their specific challenges can really make you stand out. If you specialize in certain areas, like creating online stores for retailers or crafting portfolios for artists, you can offer solutions that are specifically designed for those fields.
You can also design custom plugins or themes that add special features or styles they don't have with standard options.
Clients really appreciate it when you help them get better at managing their own website. You can offer training sessions on how to use WordPress and how to handle their content and understand their site analytics.
## Identify Opportunities to Elevate Your Pricing
As time moves on, you will see the need to increase your pricing. There are a number of reasons why this might be the case, but not all of them will sit well with your clients.
It is a delicate act to balance, but the "when" and "how" can make all the difference.
### Know When to Raise Your Rates
One key to deciding when to raise your rates is looking at your own growth and changes in the market. If you've been adding new skills or services that help your clients get more visitors or make their sites easier to use, that's adding value. Your prices should reflect that.
Also, if other developers with your skills are charging more, it might be time to think about your own rates. This keeps you competitive and ensures you're not selling yourself short.
Another thing to consider is how your clients see your work. Are they thrilled with what you're delivering? If you consistently get feedback that your work is top-notch, that's a sign that your clients see value in what you do, which might mean you can afford to ask for more.
### How to Talk About Price Increases With Your Clients
Telling your clients about a price increase is all about preparation and transparency.
Start by giving your clients plenty of heads-up before the new prices kick in. This respects their need to budget and shows you're thoughtful about their business needs.
Be clear and honest about why your rates are going up. Maybe it's because you've learned new technologies that make your sites better, or perhaps the costs of running your business have increased. Whatever the reason, explain it plainly. This helps your clients understand that the price increase is fair and based on real changes in what you offer.
It's also good to talk about what your clients will gain from the new pricing. The higher rates may come with:
- Faster turnaround times
- Additional features
- More personalized service
## Success Stories for Effective Pricing Strategies

There are many examples we can pull to see which pricing strategy works best for you. However, each situation is unique, so look at them with an open mind and don't be afraid to mix and match.
For example, [Apple is famous](https://fourweekmba.com/apple-pricing-strategy/) for its value-based pricing. While priced higher than their competitors, they market their brand on a guarantee of superior design and quality.
Another example is [Uber's demand-based pricing](https://www.cbsnews.com/news/dynamic-pricing-uber-restaurants/). During rush hour and other busy times of the day, they increase their price.
## The Right Tools for Efficient Pricing and Management
Having the right tools is half the job. It is a sentiment often used in construction, but it rings true in WordPress development as well.
These tools can lighten the load, but do not underestimate the value of your personal knowledge and skills. Use these tools to track your data and automate some of your admin work. However, remain diligent in every aspect of your business to decrease the likelihood of errors.
## WordPress Projects: Elevate Your Earnings Today
The first step to choosing the right strategy is to understand the value of your WordPress projects. As soon as you know that crucial factor, you can set fair prices for both you and your client.
Are you looking for specialized [fully managed wordpress hosting](/managed-wordpress-hosting/)? Levamo offers the speed, scalability, and support necessary to elevate your digital presence. We understand that each site is unique and we cater to our services as such.
---
## Mastering Metrics: Unlocking Growth with WooCommerce Analytics
- URL: https://levamo.com/blog/growth-with-woocommerce-analytics/
- Category: ecommerce
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Grow your store! Use WooCommerce analytics like a pro to boost sales.
The WooCoommerce platform powers the majority ([about 39%](https://www.statista.com/statistics/710207/worldwide-ecommerce-platforms-market-share/#:~:text=WooCommerce%20was%20the%20worldwide%20leading,14.95%20and%2014.67%20percent%2C%20respectively)) of all e-commerce websites globally. This means that most online store owners can rely on WooCoommerce Analytics to get actionable insights to grow their business.
However, analytics looks different for different e-commerce businesses. The nature of insights you seek, the metrics you track, etc., all depend on various factors that are unique to each online store.
This makes navigating the complexities of WooCommerce Analytics a daunting task. This is more true for budding e-commerce businesses. New businesses might still be figuring out certain things such as what dashboards they need and who should have access to the numbers.
As a result, the chances of human errors can increase leading to delays in setting up a robust analytics workflow for the e-commerce store.
In this article, let’s look at the relevant features, understand how they work, and learn about common pitfalls you need to watch out for to begin your analytics journey on the right foot to unlock growth for your e-commerce business.
## Understanding WooCommerce Analytics
WooCommerce Analytics provides users with comprehensive insights through its suite of new reports, advanced filtering and segmenting capabilities, and a [customizable dashboard](https://support.levamo.com/articles/8312213-the-wordpress-dashboard-explained). The dashboard allows users to monitor key metrics effectively and efficiently by serving as a single source of truth.
WooCommerce Analytics dashboard (source: woocommerce.com)
Consequently, e-commerce teams can always be on the same page while finalizing strategies, setting goals, etc.
Here’s a brief overview of some of the key features and functionalities of WooCommerce Analytics:
- **Reports**: WooCommerce Analytics offers nine new reports with tools that allow users to customize and delve deeper into their store's data. This includes revenue, orders, items sold, average order value, net sales, and more.
- **Advanced Filtering and Segmenting**: Users can refine their data view using advanced filters and segmenting tools, making it easier to target specific audience groups for enhancing learning.
- **Data Export**: All data can be downloaded to CSV format, facilitating further analysis or record-keeping outside the WooCommerce platform or even running more analyses on BI reporting tools.
**Customizable Dashboard**: Only focus on the metrics that are relevant to your decision-making process. Furthermore, WooCommerce Analytics dashboard widgets help you look at recent activities on your website and secondary stores if any.
### What WooCommerce Analytics Brings to the Table
Integrating WooCommerce Analytics into decision-making processes can benefit e-commerce businesses by enabling:
- **Enhanced Understanding of Sales Trends**: By tracking and analyzing sales data, businesses can identify trends, peak selling periods, and customer preferences, which can be leveraged to optimize sales strategies.
- **Improved Customer Insights**: Purchase patterns, pain points that need to be addressed, expectations they might have, etc., are some of the insights you can get with advanced analytics.
- **Optimized Conversion Rates**: Through detailed metrics on customer interactions on various touchpoints and conversions, businesses can fine-tune their marketing and sales approaches such as emails and push notifications to boost conversion rates.
- **Strategic Inventory Management**: Data on item sales and order values assists in managing inventory more effectively, ensuring that stock levels are aligned with customer demand.
By harnessing the power of WooCommerce Analytics, e-commerce businesses can make data-backed decisions that drive growth, improve operational efficiency, and enhance customer satisfaction.
**Read More: [WooCommerce Get Completed Order for This Year](/blog/woocommerce-get-orders/)**
## Why You Need Advanced Analytics for Your WooCommerce Store
Basic analytics tools usually provide the numbers on vanity metrics such as page views and impressions. These indicators, although can be useful at certain circumstances, often fall short when it comes to guiding your marketing and sales strategies.
Additionally, as the scale of the WooCoommerce store increases along with the needs of the customers and the number of products on the catalog, these vanity metrics offer little to no direction to the teams looking to improve performance.
This level of analysis does not support deep dives into user behavior, conversion pathways, or customer lifecycle management. These are the areas that are essential for [making strategic businesses decisions](/blog/hosting-for-business/) for the growth of an online store.
WooCommerce Analytics addresses these challenges by providing e-commerce stores with more in-depth data on their customers. Furthermore, the intuitive interface of the tool empowers even non-technical stakeholders to stay on top of things without the need for data scientists.
Moreover, since it is the native analytics solution, the data is always real-time and often reliable. This is because the information is not transferred from an external source through API.
### The Advantages with WooCommerce Analytics
Consequently, e-commerce stores hosted on WooCoommerce can:
- **Track detailed customer interactions**: A buyer, from being aware of your store or a product, connects with you at various touch points. Understanding this can help for more precise segmentation and target marketing.
- **Improved conversion rate optimization (CRO)**: When you know how a visitor browses your online store, you can discover areas of friction that slow or confuse them. WooCoommerce analytics can help you identify these areas to aid in creating a seamless purchase experience.
- **Optimize marketing spend**: As teams can know where their buyers come from and what kind of messaging they respond to, they can invest in the right campaigns. Allocating the marketing budget effectively can contribute to a reduction in customer acquisition costs.
- **Sales prediction and demand forecasting**: WooCoommerce Analytics helps e-commerce businesses learn about their customers and industry trends. As a result, they can predict how many units they will roughly sell in the coming months with more accuracy. This can play a pivotal role in streamlining everything between logistics and online experience.
Tools such as customizable dashboards and comprehensive reporting are made easily available and accessible to technical and non-technical stakeholders of e-commerce businesses. Consequently, teams can extract actionable insights without juggling through multiple tabs and windows.
WooCommerce Analytics interface displaying sales performance
Access to valuable data-backed insights with such efficiency sets WooCommerce stores up for growth by improving various aspects of business like customer satisfaction and user experience.
Throughout this article so far, we have mentioned the importance of making decisions based on real-time customer data. This data consists of various metrics or KPIs that give you a pulse into the market and your audience.
Let’s dive into these numbers.
## Key Metrics to Track for Growth
As we touched upon earlier, every e-commerce business is unique. Due to this reason, their dashboards and reports look different from each other. This depends on various factors such as the nature of the business, kinds of products, target demography, etc.
For instance, if an e-commerce store sells supplements, they might focus on metrics such as long-term retention of their buyers whereas a shop selling furniture could look at average order value more closely.
At the same time, there are [some fundamental metrics](/blog/fast-server-speed-tools/) that can be useful for most WooCoommerce online stores:
### Sales and Revenue
The total income generated from goods sold before any expenses. It helps assess financial health, revenue trends, and seasonal patterns.
Tracking gross revenue is only the start. The real growth lever is what’s left after costs, and margins are where wholesale sellers usually have the most room to improve. Once your analytics show where money is leaking, you can act on it with [smarter pricing](https://wholesalesuiteplugin.com/wholesale-price/ "nofollow") and buying.
### Customer Acquisition Cost (CAC)
The total cost of acquiring a new customer, which includes all marketing and sales expenses. It reflects how well you know your audience and how effectively you can direct them to your store. E-commerce businesses should always strive for the lowest CAC possible.
### Customer Lifetime Value (CLV)
The total amount a customer may spend between their first and last purchase from your store. This value is crucial to the structure of your business. A good rule of thumb is to aim for the highest CLV possible. WooCoommerce analytics, as we explained earlier, enhances the understanding of your audience and customers to which can help you retain them for longer.
### Product performance
How each of the products are faring in the market? This is essential for giving direction to your development (or procurement) efforts, inventory management, and marketing strategy. It looks at product reviews and feedback along with sales data.
### Website traffic and user behavior
This will tell you how popular are within the audience of your niche and how the visitors to your WooCoommerce store interact with your business. These metrics can tell you whether you need to invest in brand awareness or user experience.
### Conversion rate
The number of visitors, out of a hundred, that make a purchase from your e-commerce site. Keep in mind that a person may not make a purchase the first time they land in your store as the consideration phase could take between weeks and months.
### Average order value (AOV)
The monetary value of a cart that gets checked out. This can be pivotal for building effective upselling and cross-selling strategies to increase spending per visit.
### Cart abandonment rate
It is the percentage of shoppers who drop off at the checkout after adding things to their shopping cart. Monitoring this will help you uncover areas of improvement in the purchase experience such as the availability of enough payment options.
The above commonly focused metrics are essential in giving an idea of the overall health of your e-commerce store. You can consider creating a custom dashboard with WooCoommerce analytics with only the fundamental KPIs that are central to your business.
## Actionable Insights from WooCommerce Data
Now that we’ve got the fundamentals out of the way, the next question is: does WooCoommerce Analytics actually help e-commerce businesses grow sustainably?
A great way to know that, on a tangible level, is to look at case studies of a couple of businesses that have successfully grown their ecommerce businesses. It can give a thorough understanding of how WooCoommerce analytics can direct strategic actions effectively.
### [The Barrington Coffee Company](https://www.metrilo.com/blog/woocommerce-analytics-case-study-barrington-coffee)
[The Barrington Coffee Company](https://www.metrilo.com/blog/woocommerce-analytics-case-study-barrington-coffee), based out of Massachusetts, USA, often relied on advertising channels like Facebook and Google to get the word out about their offerings. WooCoommerce analytics helped their team discover that most of the traffic is dropping off without making a purchase.
The Barrington Coffee Company storefront
In other words, the conversion rates needed to improve.
Realizing the inefficacy of programmatic advertising campaigns, the marketers of the Barrington Coffee Company allocated their marketing budget towards other strategies. They focused on niche review websites, which to their own surprise, gave quite high returns.
Simply put, the insights gained with the help of WooCoommerce analytics allowed Barrington to optimize their marketing budget, focusing solely on high-return channels. This enhanced the overall conversion rates and ultimately achieved a more efficient acquisition strategy.
### [Yumi](https://www.metrilo.com/blog/woocommerce-analytics-case-study-yumi-on-a-growing-quest)
Similarly, another e-commerce brand [Yumi](https://www.metrilo.com/blog/woocommerce-analytics-case-study-yumi-on-a-growing-quest), specializing in fresh vegetable juice, faced two challenges. Optimizing customer acquisition costs and understanding the customer lifetime value (CLTV).
a bottle of Yumi vegetable juice
By integrating WooCommerce Analytics, Yumi was able to set precise Key Performance Indicators (KPIs). Monitoring them for various channels consistently helped them understand their audience well. This enabled them to maintain control over acquisition costs.
As a result, the profitability grew.
Analytics also helped them segment customers based on their behaviors and acquisition sources. Consequently, the marketing efforts got a lot more personalized. This strategic use of data helped Yumi manage immediate ROI.
Moreover, the team could make better marketing strategies with such insights.
The case studies above signify that when integrated properly, WooCommerce Analytics can help e-commerce businesses drive measurable outcomes. These outcomes could be increasing conversion rates, targeting the right audience, and understanding the long-term needs of the buyers.
## Common Pitfalls and How to Avoid Them
Understanding these common issues can help e-commerce businesses better utilize their analytics tools. This can help drive growth and steer clear of costly mistakes.
- **Accumulating vast amounts of data without clear objectives** can lead to confusion and analysis paralysis. Prioritizing key metrics that align with your business goals is the first step to deal with this challenge. WooCommerce Analytics allows you to customize dashboards to display only the most relevant data, helping you focus on what truly matters.

- **Misreading data can lead to misguided strategies. For instance, a spike in website traffic could be misinterpreted as a successful marketing campaign, ignoring that the traffic did not convert to sales. To avoid oversights related to this, use WooCommerce Analytics to dive deeper into data correlations and context**. Employing segment analysis and conversion funnels can clarify the real impact of observed changes.
- **Collecting and analyzing data without implementing changes** based on those insights is a common issue that negates the benefits of having analytics in the first place. Establish a routine for regular review of analytics reports and set up action plans based on those insights.
- While quantitative data is valuable, **ignoring qualitative data like customer feedback** can lead to a lack of understanding of the customer experience. Integrate customer feedback mechanisms such as feedback forms and review them alongside quantitative analytics.
It is advisable to revisit your e-commerce analytics workflow regularly and get feedback from various teams to remain vigilant towards such potential roadblocks and proactively address them before they start affecting your progress.
By recognizing and addressing these pitfalls, e-commerce businesses can effectively leverage WooCommerce Analytics to enhance decision-making, optimize strategies, and drive sustainable growth.
## Conclusion
Keeping an eye on the right e-commerce metrics is a necessity for making informed decisions that drive growth and improve profitability. The KPIs provide a snapshot of where your business stands and a roadmap of where it needs to go.
Utilizing a robust analytics tool like WooCommerce Analytics can significantly enhance this process by offering deep insights into sales trends, customer behaviors, and operational efficiencies.
To further empower your WooCommerce store, considering high-performance [fullly managed WordPress hosting](/managed-wordpress-hosting/) can enhance the reliability, scalability, and overall performance of your analytics operations.
Managed hosting solutions like Levamo [WooCommerce Hosting](/managed-woocommerce-hosting/) provide a secure, high-speed environment designed to handle the complexities of large-scale e-commerce operations, ensuring that your store and its data are always accessible and performing at peak levels.
[Get started today with Levamo WooCommerce Hosting](/).
---
## Remote Work: Build a Successful Freelance Career You Love
- URL: https://levamo.com/blog/build-successful-wordpress-freelance-career/
- Category: wordpress
- Author: Tom Cheddadi
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Freelance freedom is yours! Build a WordPress career you'll love.
Are you looking to enter the World of WordPress Freelancing? WordPress was conceived on 27 May 2003, humbly birthing what would later become the world’s most-loved virtual printing press. By 2006, it had surpassed 1 million downloads, despite being in its infancy with barely a plugin to speak of.
It’s now 2024, and with more than 20 years for competitors to catch up, there’s still no contender. WordPress is the de facto ruling party in the Congress of Content Management Platforms. From the beginning, it’s been the platform of choice. Not only for individuals but also for companies, newspapers, official institutions, and large international organizations.
## WordPress Freelancers are in High Demand
Like with the good old-fashioned printing press, one still needs to know how to use WordPress, maintain it, and get the most from it. That’s where the WordPress specialist steps in. Not everyone has the skills, time, or interest to manage their own website platform or the technology behind it.

## Remote Work is Standard
Being a freelance WordPress professional in a world with hundreds of millions of existing WordPress websites means that there will never be a day when you’ll say, “Gosh, I wish there was more work available.” It’s a career path with endless avenues for success. And the best part is that it’s an online business that you can run from home with practically no overhead.

While it’s true that many WordPress experts are still employed in traditional office-based roles, such as in a digital agency, it is not expected for those with skills in WordPress to be bound to any specific location, nor to be associated with a traditional company.
A great part of this is thanks to the global Work From Home (WFH) initiatives that emerged in 2020. These led to broad societal acceptance of the concept of remote work in general, which can be summed up as the slogan:
> **Work is what we do, not where we are.**
But even so, the WordPress developer culture at large has always embraced the idea of digital nomadism. The core WordPress software has been built and continuously refined by a diverse group of creators worldwide. And everything is coordinated over the Internet. So, in a way, you could say that freelancing goes with the territory when it comes to WordPress.
Are you an aspiring WordPress freelancer? Then read on to discover what it takes to thrive as a freelance WordPress services provider, whether designing themes, developing plugins, offering technical support, or assisting with day-to-day WordPress publishing tasks.
## Why working with WordPress rocks as a freelancer
Working with WordPress in any capacity (e.g. design, development, support, consulting, or publishing) lends itself extremely well to the style of work known as freelancing.

### What is Freelancing?
To be clear, when we say “freelancing”, we don’t necessarily mean “remote working”. The two concepts are quite different, even if there is a conceptual overlap.
In contrast with remote work, which is when an employee of a single company may choose to work from wherever they like, freelancing is a form of entrepreneurship where a person is self-employed and takes on work from one or more clients as an independent contractor.
### The Freelancer's Freedom: Commanding Your Career and Comfort in Pajamas
As a freelancer, you’re the boss - literally. This can be daunting at first, but it’s also incredibly liberating since you not only get to choose your own rates but also who you work for. Oh, and you get to work in your pajamas (even though that’s no longer a perk exclusive to freelancers thanks to the rise of remote working).
### Embracing the Challenges: Navigating Business Management as a Freelancer
On the other hand, as the boss of your own company, you will have to deal with everything else that goes into running a business, such as marketing, accounting, sales, and customer service. You’ll also be responsible for your time management, which is crucial in maintaining a healthy work-life balance.
Thankfully, all this isn’t as hard as it sounds, and just because you are a freelancer doesn’t mean you can’t pay for help with these aspects of business management. We will get into these a bit later in this guide.
### Flexibility and Demand: Why WordPress Specialists Thrive in the Freelance Economy?
The freelancing business model is a great fit for WordPress specialists in particular for many reasons, including:
#### Project-Based Engagements: The Freelancer's Advantage
Many WordPress website owners don’t need a full-time employee to fulfill the various tasks they need to do. Once a website has been created and tested to be working, the content might not change much over time, which is especially true of many local business websites. Thus, offering your services to multiple clients makes sense, serving each as and when they need you.
#### Virtual Collaboration: Maximizing Remote Communication Tools
With all the instant messaging options available (voice, video, email, text chat), being present in person is no longer necessary to have productive meetings. A conference call with a client over the Internet can be as effective as face-to-face. And in many cases, it is preferred because neither party needs to be anywhere in particular.
#### A Market in Demand: WordPress Skills Wanted
It’s an in-demand specialty in the overall freelance marketplace, with thousands of work opportunities constantly posted on freelance job marketplaces like Upwork.
#### Industry-Independent Stability
It doesn’t depend on the economics of any one industry. Companies in all industries have a need for website services in some form.
#### Brand Recognition: The WordPress Advantage
WordPress is a well-known brand with instant recognition among clients the world over. If WordPress is good enough for Microsoft and Reuters, it’s good enough for most people.
#### WordPress: A Tool for All Trades
It’s incredibly versatile and can be used to create websites, blogs, magazines, online stores, community forums, directories, and many more types of websites.
#### Global Opportunities: Overcoming Geographical Limits
It’s easy to go global. For example, what happens when all the businesses in your area dry up, or the local economy goes south, and no one has the budget for your services? For a WordPress freelancer with an online presence, geographical distance poses no barrier to business.
#### Self-Led Learning and Growth in WordPress Expertise
It’s very possible to teach yourself WordPress and everything that goes into becoming an expert in it. This can make up for the lack of mentorship one might receive as a company employee, and it means that you can keep upskilling and earning higher rates as you go along.
However, if you ever feel the urge for guidance, [mentoring software](https://www.qooper.io/mentoring-software) can offer the support you need, providing tailored guidance and growth opportunities that help you sharpen your skills and increase your earning potential over time.
### An Open Source Platform with Infinite Possibilities
A beautiful fact about working with WordPress from a career perspective is that it’s both a simple and a complex tool. A basic WordPress site is super easy to create, but that doesn’t mean you can’t do more advanced things with it.
Quite the contrary: the power of WordPress is that because it is open source, its functionality, and appearance can be extended not only with themes or plugins but even its source code can be changed to accommodate any custom change a client might desire. As you can imagine, this situation creates many opportunities for freelancers of different strengths and experience levels.

#### From Novice to Expert: Growing Your WordPress Freelance Career
In other words, because WordPress is essentially an out-of-the-box solution for creating and managing websites, you don’t need a lot of experience to get started as a WordPress freelancer. Yet at the same time, there is always something new that you can learn and add to your professional repertoire over time, thereby increasing your demand and overall earning potential.
For instance, you might be a total beginner at WordPress now, knowing only how to use the admin dashboard, create posts, and upload media. Who would pay for that, right? Wrong! Companies do pay for this type of work, and you certainly need not be an expert at programming in PHP to get a paying gig, even if it’s simply to help a company upload a photo gallery or publish a series of blog posts.
#### Exploring WordPress Freelance Roles
Depending on your specialty, knowing WordPress deeply isn’t just about knowing WordPress. Here are some common freelance roles with a simplified breakdown of each:
**WordPress Designer**
- **Responsibilities:** Designing themes and page layouts, choosing color schemes and typography, and generally making things look nice.
- **Required skills:** An eye for aesthetics and modern web design with basic knowledge of HTML and CSS (optionally: JavaScript and/or PHP).
**WordPress Developer**
- **Responsibilities:** Developing plugins, extending theme functionalities, adding new features, fixing bugs, and hosting/server administration.
- **Required skills:** Good knowledge of HTML, CSS, JavaScript, and PHP, as well as web hosting and Linux system administration (including a typical WordPress tech stack such as LAMP: Linux, Apache, MySQL, and PHP).
**WordPress Virtual Assistant**
- **Responsibilities:** Using the WordPress dashboard to upload/crop/resize images, edit and publish posts and pages, and perform other manual tasks.
- **Required skills:** Basic communication skills, data entry, image editing, and attention to detail.
Of course, these are only a few typical roles in theory. In practice, there are many other niche services that can be offered by a WordPress freelancer (say, content moderation on a WordPress-based forum), and sometimes a developer might also do design (and vice versa). Overall, there’s something for everyone depending on whether you’re more creative or logical.
## Essentials of success as a WordPress freelancer
So you’ve decided to become a freelancer specializing in WordPress. Great decision - you may now pat yourself on the back. Truly.
In the following sections, we will cover some of the key elements of success that many new freelancers tend to overlook, much to their detriment.
Specifically, we will talk about how to:
- Boost your productivity in a remote work or freelancing environment.
- Find gigs in the competitive freelance job market.
- Stand out as the freelancer who’s the perfect fit for the job.
- Find networking opportunities in the WordPress space.
- Expand your set of services by improving your skill set.
- Manage your finances for a sustainable career.
Let’s get on with it, then.
### Boosting your productivity
One of the biggest mistakes many freelancers make is wasting time. Often, it’s not that obvious that you are even doing so, as procrastination can take on a million subtle forms.

Here are a few tips on how to make the best use of your time:
#### Track your time
If you’re charging hourly for your work, a time-tracking tool can be essential to ensure you bill your clients accurately. And if you’re charging per project (or deliverable), time-tracking is just as important as it helps you stick to the actual scope of the project.
#### Create templates for client management
Although you want to treat each client individually, the use of templates can help save a lot of time. One example is a proposal template, where you outline how you will approach a commonly encountered problem, how long it will take, and how much it will cost. You can then save the template and customize it for each new client.
#### Use plugins where appropriate
WordPress plugins are all about increasing productivity by not having to reinvent the wheel every time. For example, rather than coding your own photo gallery, use one of the dozens already available in WordPress’s plugin collection. It’s a no-brainer, really.
#### Work on your communication skills
No matter how well you talk the talk, you can always do better. As they say, people do business with people they like, so spend time understanding how clients respond to your proposals and communications and constantly refine your approach.
### Finding gigs
You might have all the skills in the world, but if you don’t know how to find a market for them, all your efforts will be in vain.
The success of your freelancing business relies on how well you market yourself, so here are a few avenues to pursue:
#### Online freelance platforms
The top [freelance marketplace](/blog/best-freelance-websites/) that everybody knows is Upwork, but there are other good opportunities for WordPress experts on other marketplaces such as Post Status (for exclusively WordPress jobs), Freelancer, Toptal, People Per Hour, and Fiverr.
Screenshot of Upwork’s website home page where many WordPress Freelancers find work.
#### Paid advertising
If you have the budget to invest in advertising, this is a surefire way to acquire clients quickly. Make sure that your ads lead to an attractive, persuasive landing page that explains what you offer and shows your best pieces of past work in a neat portfolio.
#### Word of mouth
Sometimes it only takes one client to get the ball rolling. If you do good work for them, they’ll be naturally inclined to refer you to others.
#### Volunteer work
Not to suggest that you do all your work for free, but contributing code or other efforts within the WordPress community can easily lead to paying contracts later, as it’s free advertising that puts you in front of the people who may need exactly the solutions you can offer.
#### Cold calling/door-to-door
Once you’ve become established, most of your clients might come from referrals or from people who contact you first. Until then, however, you might have to put in some extra legwork. Directly soliciting work by approaching businesses who might need your services is an age-old tactic. Just make sure you don’t cross the line into spam, especially if you are sending out many emails, for instance.
### Standing out from the crowd
Let’s be real: There’s a lot of competition out there. Since this fact cannot be ignored, it’s a good idea to learn how other freelance WordPress experts managed to stand out. There are hundreds of such case studies online, so settle in and get reading.
Screenshot of a Portfolio demo of the Uncode WordPress Theme.
One common thread in many freelancer case studies is the need to niche down and specialize in some aspect of WordPress that isn’t being serviced as well as the others. Beyond specializing in a high-demand service, here are some other ways to get ahead of the pack:
#### Build a portfolio website
Your portfolio website is a place to showcase your best work, and as a bonus, the website itself can act as its own portfolio piece. Don’t bother displaying mediocre projects or those you’re not that proud of; instead, even if you only have a small sample of projects to showcase, it’s important to pick only the best to show to potential clients.
#### Write your own case studies
A portfolio piece is typically displayed on its own, with little explanation of the processes that went into it. What clients really want to know, however, is how you actually approach the problems that they pose. Presenting a case study can help you walk clients through the story of a certain portfolio piece from proposal to completion. This helps build immediate trust and makes you much more memorable.
#### Gather testimonials
Social proof is one of the most effective ways to persuade clients to hire you. Once you have finished a project, don’t be shy to ask the client for a testimonial. Even a single glowing testimonial displayed on your portfolio site can greatly increase your chances of being hired.
#### Contribute to WordPress.org
For WordPress developers especially, clients are looking for whether you have any existing reputation they can check on. Making public contributions to WordPress.org, whether helping to build a free plugin or creating a new theme can be a brilliant way to make a name for yourself. Find out more on the [Make WordPress](https://make.wordpress.org/) website.
#### Always go the extra mile
This is classic wisdom that never fails. Don’t overpromise and underdeliver; instead, aim for over-delivery on every project. This is not to say that you should work for free, but if an opportunity presents itself for you to add a little extra value that your client wasn’t expecting, then you’re far more likely to gain happy, long-term clients.
### Networking
This isn’t just what you do when you connect a new server to the Web! Networking, as in meeting, socializing, and collaborating with others in the WordPress industry, is the key to unlocking opportunities you never imagined were possible.
Photo from WordCamp Europe Berlin 2019
As a freelancer, much of your work will be done in physical isolation from other people since you’re likely to be running a home office and meeting clients virtually instead of in person. Dedicating time for local networking is not only essential to your sanity but also has many other benefits, including the ability to gain new business from event attendees and the prospect of potential collaboration with other freelancers.
WordPress.org is very involved in organizing meetups and other networking events. For more information, visit [events.wordpress.org](https://events.wordpress.org). You can also find local meetup groups in your area on the [WordPress page at Meetup.com](https://www.meetup.com/pro/wordpress/). If nothing is listed for you there, browse the [WordPress topic page](https://www.meetup.com/topics/wordpress/) for events nearby.
Another great website for WordPress networking is [Post Status](https://poststatus.com/), a membership site with a WordPress-focused job board where you can connect with clients directly. In addition to these areas, don’t forget to join any of the thousands of WordPress networking groups on Facebook, Slack, Discord, and so on.
### Expanding your WordPress skillset
Being a freelancer of any kind requires that you keep up to date with industry trends, lest your services become outdated. Now, being a *WordPress* freelancer can be even tougher in this sense because of the rate at which WordPress is constantly evolving. Needless to say, staying in the loop with new features and version updates is essential to staying relevant.
Going further, the point of any career is based on progression - whether it’s progressing in your own self-development or simply earning higher rates than the year before. And while you might be comfortable with the skills you already possess at the moment, the time will come when you feel the need to extend your horizons.
The best freelancers are always learning and improving because they know that others are doing the same. Don’t be the one who gets left behind; instead, factor in the time you need to work on learning new skills and get to it.
One of WordPress's wonders is that it’s easy to learn new skills and deepen your technical knowledge. The WordPress code base is open source and well documented, so making an effort to read through it will make a huge difference in how you present yourself to clients and how you develop solutions.
Learning as much as you can about how WordPress works, including how plugins mesh with the core software and how themes are built from scratch, can make you an incredibly versatile, and thus valuable, freelancer.
Here is a collection of resources to keep you informed about the latest news, trends, and skills.
#### Podcasts
- [WP The Podcast](https://wpgears.com/podcast/)
- [WP Watercooler](https://www.wpwatercooler.com/shows/wpwatercooler/)
- [The WPMRR](https://wpmrr.com/podcast/)
- [WP Coffee Talk](https://wpcoffeetalk.com/)
- [Kitchen Sink WP](https://kitchensinkwp.com/category/podcast/)
- [WordPress Plugins from A to Z](https://wppluginsatoz.com/)
#### YouTube Channels
- [WPLearningLab](https://m.youtube.com/@wplearninglab/videos)
- [WPCrafter](https://m.youtube.com/channel/UCjDuxPEhNQ2qn_qAdjRG4YQ)
- [WebTegrity](https://m.youtube.com/user/webtegrity)
- [WPTuts](https://m.youtube.com/user/ipixeltutorials)
- [WPBeginner](https://m.youtube.com/user/wpbeginner)
- [Ferdy Korpershoek](https://m.youtube.com/@ferdykorpershoek/videos)
- [Josh Hall](https://m.youtube.com/@JoshHallco/videos)
#### Blogs
- [WordPress.org News](https://wordpress.org/news/)
- [Torque](https://torquemag.io/)
- [WPBeginner](https://www.wpbeginner.com/)
- [WPTavern](https://wptavern.com/)
- [IsItWP](https://www.isitwp.com/blog/)
- [codeinwp](https://www.codeinwp.com/blog/category/wordpress-tutorials/)
- [WPShout](https://wpshout.com/)
- [Smashing Magazine](https://www.smashingmagazine.com/category/wordpress/)
- [Colorlib](https://colorlib.com/wp/)
- [Yoast](https://yoast.com/seo-blog/)
- [AISEO](https://aioseo.com/blog/)
### Managing your finances
Finally, let’s talk about finances. As mentioned, freelancers are responsible for all their own pricing, bookkeeping, and taxes. This includes [calculating your rates](/blog/pricing-strategies-for-wordpress/) in such a way as to be sustainable, keeping track of expenses vs. income, as well as a handful of other financial management tasks common to all businesses.
If you opt to work exclusively through a freelance job marketplace like Upwork, then, fortunately, you won’t have to deal with creating your own invoices or keeping track of all payments in one place since the system keeps a record of all your financial activities for you. It’s a great perk, but not everyone goes all in on a single freelance job site, and you might have a mixture of clients from various channels.
On the other hand, if you are working for clients directly you will likely need help keeping all your financial records organized. Unless you are also an accounting whiz, it would be wise to invest in financial management software such as:
- [FreshBooks](https://www.freshbooks.com/)
- [Zoho Books](https://www.zoho.com/us/books/)
- [Paymo](https://www.paymoapp.com/)
- [Wave](https://www.waveapps.com/)
- [Xero](https://www.xero.com/us/)
## Wrapping up
Only five years ago, freelancing was seen as a somewhat fringe business model, reserved for all but the most exclusive professionals. Since 2020, however, all that has changed.
With the rise of remote work, where physical location no longer matters to many businesses, freelancing has become a highly promising career path that holds a huge earning potential and a host of other benefits for those who can adapt to this style of work.
Hopefully, the insights offered here have given you a kickstart in the right direction. Thanks to the ease with which freelancers can now connect, collaborate, and do business with clients worldwide, isn’t it about time you got started? Your future of financial freedom awaits!
---
## How To Automate Your WordPress Site Maintenance: Tools & Tips
- URL: https://levamo.com/blog/automate-wordpress-maintenance-guide/
- Category: wordpress
- Author: Pratik Dholakiya
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Automate WordPress maintenance! Tools & tips for an efficient, secure site.
Just like a physical office space needs regular upkeep, your WordPress website - your business's virtual estate - requires ongoing maintenance too.
Maintaining your WordPress site is essential not only for its security and performance but also for ensuring a continually seamless user experience.
However, as your business grows, the tasks needed to manage your WordPress site can become daunting, particularly if your daily operations depend heavily on your website.
Automating WordPress maintenance can streamline a good chunk of these tasks, reduce human error, and free up valuable time for strategic work such as audience research and content creation.
In this article, let’s learn how to automate various aspects of your WordPress website’s maintenance with the right tools, plugins, and tactics. Let's make sure your site remains efficient, secure, and consistently up-to-date.
## The Benefits of Automating WordPress Maintenance
Have you thought about the benefits of automating your WordPress site's maintenance? Investing a bit of time upfront to automate can yield big rewards.
Here are three compelling reasons to get started with automation for your WordPress maintenance:
### 1. Time Savings
Automation transforms how your team handles routine maintenance tasks. By implementing plugins that automatically manage updates, backups, and security checks, you eliminate hours of administrative work and manual upkeep.
Instead, you can focus on more exciting stuff like crafting killer content, boosting customer engagement, and scaling your business.
### 2. Reliability
Manual updates and backups can mean more slip-ups. Automated tools perform tasks with consistent precision, reducing the likelihood of human error.
You can rely on these tools to execute updates, security measures, and backups correctly and on schedule, keeping your site’s integrity intact. And so, everything runs on schedule and your site functions smoothly, keeping the digital gears of your site well-oiled and operational.
### 3. Improved Website Uptime
Manual updates and backups often cause unexpected site downtime, especially if not managed correctly.
Automation allows for these tasks to be scheduled during off-peak traffic hours. This means less disruption for your visitors and more uptime for your site. Keeping your site available around the clock is crucial for user satisfaction and maintaining a slick, professional online presence.
These are just a few of the many benefits of automating your WordPress maintenance.
Now, the question is: how do you realize these benefits for your WordPress website?
Well, it’s WordPress: there’s a plugin or solution for everything. Next, let's explore some tools that can help automate the various aspects of WordPress maintenance.
## Tools to Automate WordPress Maintenance
Now that you know the *what* and *why* of automating your WordPress website maintenance, let’s look at the *how*. Here are the best tools that do the heavy lifting for your website, freeing up your time.
### 1. Backup Tools
Imagine waking up one fine day and seeing years of investment in creating high-quality, SEO-friendly content gone from your site due to malware. This isn’t uncommon: a [report](https://sucuri.net/reports/2021-hacked-website-report/) suggests 72.7% of WordPress site infections are due to malware. Additionally, unauthorized backdoor access and SEO spam are significant threats, accounting for 69.6% and 46.7% of all WordPress hacks, respectively.
When your site gets infected by malware, hit by a bad update, or accidentally deleted, a backup saves the day, ensuring your valuable data and content can be securely recovered.
Admittedly, regularly backing up and updating WordPress core, themes, and plugins is one of the most tedious tasks, but it’s essential. With major core updates handled automatically by WordPress, it's the minor updates and backups for themes and plugins that demand significant time.
Here are a couple of great plugin options for automated site backups scheduled regularly:
- **UpdraftPlus:** Automates backups and stores them in the cloud (e.g., Google Drive, Dropbox). It supports scheduled and on-demand backups and can restore your site directly from the WordPress admin panel.
- **BackupBuddy:** Provides scheduled backups, off-site storage options, and full-site restores. It also includes features for migrating WordPress sites to different [servers](/blog/fast-server-speed-tools/) or domains.
UpdraftPlus Backup and Restore
### 2. Update Management Tools
Just like backups, frequent updates to your themes, plugins, and WordPress core protect your website from vulnerabilities in your tech stack. Updates also ensure you get the most out of your installations.
Here are a couple of great plugin options for automated site backups scheduled regularly:
- **ManageWP:** Offers centralized management for multiple WordPress sites, automating updates for plugins, themes, and the WordPress core. Updates can be set to low-traffic periods to minimize disruption, ensuring your site benefits from the latest security patches and features without requiring manual intervention.
- **Easy Updates Manager:** Allows you to manage all updates from a single dashboard, with options to enable or disable automatic updates for plugins, themes, and WordPress core.
ManageWP for update management
### 3. Security Scanning Tools
Your WordPress website can be a breeding ground for malware for months before you detect it. While an automated security scan doesn't fix issues directly, it does highlight potential vulnerabilities. With periodic security scans, you can take proactive steps to strengthen any weaknesses and enhance your website's security.
Security plugins such as Patchstack and Monarx, which are included for free with [Levamo](/) hosting, provide comprehensive security monitoring:
- **Patchstack:** Focuses on security vulnerabilities in plugins and themes, offering automated security scans and real-time alerts.
- **Monarx:** Provides proactive malware protection by monitoring files for changes and detecting malware patterns.
Integrated into Levamo hosting, these tools offer an additional security layer at no extra cost. These tools regularly scan your site for vulnerabilities and malware, and even automatically address common security issues.
Patchstack for automated security scans
### 4. Performance Tools
Similar to malware issues, performance issues tend to accumulate and grow over time and aren’t always obvious at first. If slow page loading times go unnoticed, they can damage your website in more ways than one.
Your website visitors won’t wait around for a slow page to load, they will simply bounce away. In fact, the odds of bounce increase [32%](https://www.thinkwithgoogle.com/marketing-strategies/app-and-mobile/page-load-time-statistics/) as page load time goes from 1 second to 3 seconds. Furthermore, poor website performance also hurts your search engine rankings, as page speed and user experience metrics are [crucial ranking signals](https://www.searchenginejournal.com/ranking-factors/page-speed/) for search engines like Google.
So, by periodically reviewing your site’s performance, you can pinpoint problems before they seriously hurt its UX and SEO. Automated performance tools help keep an eye on issues and tackle the optimization tasks, requiring little-to-no manual intervention from your end.
Here are a couple of tried-and-true plugins that help you monitor and improve your site’s performance:
- **WP Rocket:** Automatically applies a range of performance optimizations, including caching, database optimization, minifying CSS and JavaScript, and lazy loading images, which can significantly speed up WordPress sites.
- **Perfmatters:** Improves site performance by disabling unnecessary WordPress features, optimizing database interactions, and reducing HTTP requests.
WP Rocket dashboard for performance optimizations
### 5. Miscellaneous Tools
Besides the above four aspects, you can also consider using automation tools for other areas of website upkeep.
For example, here are a couple of plugins for fixing broken links and automating redirects:
- **Broken Link Checker:** A popular plugin that automatically monitors and fixes dead links across your site, which can degrade SEO performance and user experience if left unchecked. Automating this process helps maintain the health and credibility of your site.
- **Redirection:** A plugin that you can configure to monitor when post or page permalinks are changed and automatically create a redirect to the new URL. Helps manage and fix 301 redirects and track 404 errors without requiring knowledge of Apache or Nginx. This ensure users don't face errors like "[the requested url was not found on this server](/blog/the-requested-url-was-not-found-on-this-server/)".
All in all, each of the above tools lets you automate the various time-consuming areas of WordPress website maintenance, ensuring it remains secure, efficient, and user-friendly with minimal manual oversight.
Broken Link Checker plugin
## Setting Up Automation Tools
To successfully implement automation in your WordPress maintenance routine, you need to set up these tools correctly. Here’s a primer on configuring some commonly used WordPress automation plugins and services mentioned above.
**1. UpdraftPlus for Backups:**
- Navigate to the [WordPress dashboard](https://support.levamo.com/articles/8312213-the-wordpress-dashboard-explained) and install the UpdraftPlus plugin.
- Go to Settings → UpdraftPlus Backups and configure your backup schedule.
- Choose your remote storage option and authenticate it to ensure backups are safely stored off-site.
**2. ManageWP for Update Management:**
- Sign up and add your site to the ManageWP dashboard from its official website.
- Configure settings to automate updates for themes, plugins, and WordPress core, as well as manage other aspects like uptime monitoring and SEO performance.
**3. Patchstack for Security Scanning:**
- Install Patchstack from your WordPress plugin repository.
- Activate and go to its dashboard to set up automated security audits, real-time monitoring, and receive alerts for any vulnerabilities.
**4. WP Rocket for Performance Optimization:**
- Install WP Rocket from your WordPress dashboard.
- Once activated, most of the default settings will automatically optimize your site. However, you can customize settings like caching levels, file optimization, and preloading according to your site’s needs.
**5. Broken Link Checker for Link Maintenance:**
- Install and activate the Broken Link Checker plugin.
- It automatically starts scanning your posts, pages, and comments for broken links.
- You can set up notifications and choose whether to display broken links differently or prevent search engines from following them.
Note that these are just the initial steps. Proper further configuration of these tools is necessary to maximize their efficacy and ensure they serve your precise automation needs.
Also Read: [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
## Best Practices for Automated Maintenance
You have the tools. Now, take a look at these tips to make sure they are working as intended:
- **Review Automation Logs:** Regularly check the logs produced by your automation tools to ensure they are running as expected and to catch any issues that may not trigger automatic alerts.
- **Keep Automation Tools Updated:** Just as you keep your WordPress themes and plugins updated, ensure your automation tools are also up to date to benefit from the latest features and security improvements.
- **Test Restore Processes:** Periodically test the restore process for your backups to ensure that you can quickly and reliably restore your site in case of an emergency.
- **Monitor and Adjust Settings:** Track the performance impacts of your automation tools and adjust settings as needed. This ensures that your site remains optimized without sacrificing user experience.
- **Use Multifactor Authentication:** Secure the interfaces of your automated tools with multifactor authentication to prevent unauthorized access.
Multi-factor authentication
Also, if automation fails, it's crucial to have a plan in place to address issues promptly:
- **Immediate Notification Setup:** Whenever possible, configure your automation tools to send immediate notifications if a task fails. This can be via email, SMS, or a dedicated monitoring dashboard.
- **Manual Intervention Plan:** Have a clear manual intervention plan. Know who is responsible for what actions when automation fails, ensuring that team members are trained to handle common issues.
- **Backup Systems:** For mission-critical aspects of your website, such as customer data, set up second-level backup systems. This can mean having secondary tools or manual processes ready to go.
So, while automation is incredibly helpful in managing WordPress site maintenance, it's important to maintain a balance between automated systems and manual oversight.
## Frequent Challenges and Solutions in Automated WordPress Maintenance
Automating WordPress maintenance simplifies many tasks but also brings in some challenges. Here's how to address some of the most common issues:
- **Plugin Conflicts:** Regularly [test plugins in a staging environment](/blog/how-wordpress-sandboxes-help-developers-test/) before updating them on your live site. This can help identify conflicts in a controlled setting.
- **Failed Updates:** Set your system to alert you immediately if an update fails. Ensure you have a rollback plan to revert to previous versions if necessary.
- **Backup Failures:** Monitor backup processes closely and verify the integrity of backup files periodically. Use reliable storage solutions to minimize the risk of data loss.
- **Security Oversights:** Combine automated security tools with regular manual security audits to catch any issues that automated scans might miss. This ensures that automation complements rather than replaces human oversight.
Addressing these challenges proactively ensures that your automation tools work effectively, keeping your WordPress site secure, up-to-date, and performing well.
## Looking Ahead: WordPress Maintenance in 2025 and Beyond
As we look towards the latter half of 2025 and beyond, WordPress maintenance is likely to become more sophisticated with advancements in automation technologies.
Here are some emerging trends and what we might expect moving forward:
- **Increased Use of AI:** Expect Artificial Intelligence and machine learning to play a bigger role in predictive maintenance. These technologies are becoming adept at identifying potential issues before they escalate, ensuring your site remains in peak condition.
- **Integration of More Advanced Analytics:** As analytics tools become more sophisticated, they will offer deeper insights into website performance and user behavior. This advancement will enable more precise and targeted maintenance efforts, enhancing site efficiency and user experience.
- **Rise of Decentralized Hosting Solutions:** With the growth of blockchain and decentralized technologies, we might see innovative approaches to automating, maintaining, and [hosting WordPress](/blog/hosting-for-business/) sites. These technologies could enhance security and data integrity, offering robust alternatives to traditional hosting methods.
- **Enhanced Security Protocols:** As cybersecurity threats evolve, expect to see more advanced automated security measures integrated into WordPress maintenance tools.
- **Sustainability in Web Operations:** There will be a greater focus on sustainability. Look for tools designed to optimize energy consumption and reduce the carbon footprint of running a WordPress site.
Staying in the know with these trends will help you make your WordPress website increasingly efficient and secure.
## Conclusion
If you prioritize efficiency, security, and performance, automating WordPress maintenance is crucial. You're now familiar with various tools and strategies that simplify site maintenance tasks, including backups, updates, security enhancements, and performance optimizations. By integrating these automation solutions, you ensure that your WordPress site runs smoothly, freeing you up to focus on expanding your brand and boosting user engagement.
However, remember that while automation significantly aids in routine tasks, maintaining a balance with periodic manual checks is essential to catch issues that automated systems might overlook.
Are you seeking a high-performance [fully managed WordPress hosting](/managed-wordpress-hosting/) that automatically handles your website’s updates, backups, and security defenses? You’re in the right place.
---
## Mobile Magic: 9 Quick Wins for Your WooCommerce Store
- URL: https://levamo.com/blog/9-quick-wins-for-your-woocommerce-store/
- Category: ecommerce
- Author: Nick Badot
- Published: 2024-05-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Boost sales! Get 9 quick WooCommerce mobile optimization wins now.
## Mobile Optimization: An Overview
Mobile optimization for WooCommerce and other e-commerce stores provides a positive user experience and boosts conversion rates. With an [estimated 60% of E-commerce purchases](https://www.statista.com/chart/13139/estimated-worldwide-mobile-e-commerce-sales/) made on mobile phones in 2024, an optimized mobile storefront is crucial for the survival of modern businesses. In this article, we will discuss the importance of mobile optimization and give you some tips to ensure your storefront provides a mobile-friendly interface that will convert customers.
Mobile Optimization can be tricky. But we are here to help.
## Why Mobile Optimization Matters in E-Commerce
Good mobile optimization is like skin: vital, and you don’t really think about it when it’s there. But when you take it away, the results are as obvious as they are painful. We have all experienced what a non-optimized landing page looks like. Web elements that fail to resize to the screen. Pop-ups that devour the entire display and make it impossible to do anything. Visual elements that distort or otherwise fail to load. You probably immediately abandoned the website after running into these errors. If so, you’re not alone - even small customer-side frictions have a significant impact on bounce rates. Google Insights found that [53% of visits are abandoned if a mobile site takes longer than 3 seconds to load](https://www.thinkwithgoogle.com/consumer-insights/consumer-trends/mobile-site-load-time-statistics/). The same source states that 79% of users are more likely to return or recommend a mobile site if they deem it easy to use.
With[ three out of five dollars](https://www.oberlo.com/statistics/mobile-commerce-sales) spent on e-commerce spent via mobile, losing mobile web traffic can severely curtail total conversions and sales. In fact, being mobile-ready can improve engagement by as much as [85%](https://blog.kissmetrics.com/wp-content/uploads/2011/09/mobile-mania.pdf). Moreover, [page load speed and mobile friendliness](https://developers.google.com/search/blog/2020/05/evaluating-page-experience) are factors Google uses when generating its search rankings. In short: mobile optimization is a necessity, not a luxury.
When mobile optimization is bad, customers will notice.
## 9 Quick Wins for Mobile Optimization on WooCommerce
At Levamo, our mission is to help you build successful, scalable web storefronts and make big wins in your e-commerce business. Here are nine of our top recommendations to optimize your WooCommerce site and maximize conversion rates:
### 1. Measure and Accelerate your Load Times
Keeping your load times low - especially on landing pages - is crucial for engaging customers at the top of the funnel and driving conversions; every second of an increase in load times[ can reduce conversion rates by 17%](https://www.bidnamic.com/resources/how-website-speed-affects-your-conversion-rates). Load speed is a key metric for mobile shopping, and should be measured and optimized for regularly. Open source tools like [Google’s Lighthouse](https://developer.chrome.com/docs/lighthouse/overview/) (formerly Google Friendly Mobile Test) can analyze page loads and run site audits. Lighthouse also offers a number of implementation options - from simple web and command line tools where a URL can be entered for a quick assessment, to Chrome Dev Tool and Node implementations that can be embedded into your development cycle.
[Choosing the right web host](/blog/importance-of-a-web-host/) for your site is also vital to keeping load speeds low and stable - consider using hosts that offer dynamic resources and can scale with increases in traffic. Load times can also be improved by reducing the number of CSS and JavaScript files acting on a page, removing unnecessary plug-ins, optimizing images (see item 3), and using the appropriate caching techniques and [Content Delivery Networks (CDNs)](/blog/cdn-for-ecommerce/) for your site.
### 2. Streamline your Website’s Design
Aside from the technical implementation of your e-commerce site, the overall design and user flow are key. Actions that customers are likely to perform (or that you want them to perform) should require as little effort as possible and be intuitive. Some storefronts like to add technically complex bells and whistles, or devote themselves too much to a certain gimmick, and thus make mobile navigation more convoluted and confusing for the customer.
To build a seamless web experience consider keeping pop-ups to a minimum, or making existing pop-ups less ‘loud’; use simple, complementary colors that make the text legible - colored text may look good to you but not to all of your customers, not to mention the risk of driving away color blind users; implement ‘dark mode’ compatibility and other accessibility tools like screen reader support; make important buttons visible but not overbearing; and - most importantly - map out the number of actions a user has to complete to achieve a task and reduce this number wherever possible.
### 3. Optimize Images for Fast Loading
Humans tend to respond strongly to visual stimuli. That's why images and videos are essential in online sales - both as a means to draw in customers and to help them visualize the product and make the decision to buy. But images, especially the high quality images used in modern e-commerce, take some effort to load, and image-heavy pages lead to slower loading speeds and errors if they are not optimized for mobile users.
Thankfully, modern compression techniques allow you to reduce image size without affecting quality. Tools such as [TinyPNG](https://tinypng.com/) can be used for this purpose. Larger storefronts with thousands of products, or those that allow users to upload their own images, must consider automated image compression in their pipelines. Other techniques such as [lazy loading](https://web.dev/articles/lazy-loading) - in which images are not fully resolved until they are needed - can also help keep loading times manageable.
### 4. Embrace Responsive Design
Nothing is more frustrating to mobile users than a website that won’t display correctly on a mobile screen or that isn't configured for touch input. For example, [67%](https://www.tidio.com/blog/mobile-commerce-statistics/) of mobile users in 2023 stated that pages and links being too small to click were significant barriers to their online shopping.
Responsive design principles are ideally implemented during the design phase and followed through to development and testing. Mobile-friendly sites generally use flexible grids of content that can stretch or contract to different screen sizes and orientations. For example to handle landscape vs portrait. While developing web content, relative values (e.g. % of screen) rather than absolute values (number of pixels) are a must. Dynamic fonts that change based on hardware are also useful. This allows your content to stay not only legible but pleasant to read on all manner of devices.
### 5. Simplify the Checkout Process
How many clicks does it take a user on your WooCommerce site to buy your product? This is another invaluable metric, and one that you should take every step to reduce. There should be no walls between your user and their ability to buy a product on your site. Amazon, the champion of e-commerce, introduced the 1-click system in 1997 which has been replicated countless times since. In fact, sites with a one-click checkout option tend to have a conversion rate of [10%, versus the average of 2-3%](https://markerly.com/pulse/echoes-of-efficiency-how-amazons-one-click-checkout-resonates-with-consumers/) for those which don’t.
Ways to simplify the Checkout process on your WooCommerce site include:
- Integrate payment services such as PayPal, Google Pay, and Apple Pay.
- Reduce the amount of form fields (phone, address, etc.) a user has to fill out.
- Ensure there are clear error messages in your form to help users correct input typos etc.
- Save customer information for repeat purchases.
### 6. Leverage Mobile Friendly Plug-Ins for WooCommerce
Plug-ins offer simple ways to make the job of running an e-commerce site much easier and save you hours of development time.
The right plugin can also unlock an entirely new revenue stream: selling wholesale. Adding a B2B channel, with role-based pricing, minimum orders, and tax handling, is one of the highest-ROI quick wins a growing store can make. A dedicated plugin does the heavy lifting for you. Start by picking the [best wholesale plugin for WooCommerce](https://wholesalesuiteplugin.com/ "nofollow").
WooCommerce supports a wide variety of plug-ins that can help you make your site more mobile-friendly and improve the overall user experience. Installing plug-ins is relatively easy, and many are free or offer free trials, so you can shop around and test different options to find the one that’s right for you.
Here are some of our favorite WooCommerce plug-ins for mobile optimization:
- [WPtouch](https://wordpress.org/plugins/wptouch/): A popular plug-in that immediately converts desktop websites to make them more mobile-friendly, without altering the desktop view. This plug-in offers a free tier and directly targets your Google Mobile Friendliness score.
- [Jetpack](https://wordpress.org/plugins/jetpack/): A high-level mobile plug-in developed by WordPress.com. It has a wide array of site management tools designed to cater to broad use cases and boasts solid security credentials.
- [WP Mobile Menu](https://wordpress.org/plugins/mobile-menu/): A more specific plug-in designed to improve menus and menu interaction on your site. Ideal for sites that already have some level of responsive design and want to improve their menus and navigation.
### 7. Utilize Mobile Data Analytics for Insights
An estimated [330 million terabytes](https://www.statista.com/statistics/871513/worldwide-data-created/) of data is created on a daily basis, and this number is projected to continue increasing. Modern businesses need to use data and generate actionable insights to remain competitive in almost all sectors. In e-commerce this fact is especially salient.
Collecting data is easy and more or less automatic with a wide variety of tools available, such as [Google Analytics](https://marketingplatform.google.com/about/analytics/) and [Matomo](https://matomo.org/). It’s knowing what to do with it that can prove more challenging. The first step is to decide which metrics are valuable for your WooCommerce site. (We have already suggested a few in this article, such as load time and clicks-to-checkout.) Once you identify these, the next step is to implement processes that generate and regularly audit your metrics. No single metric can accurately predict your future performance. We suggest keeping a broad selection that targets diverse, non-dependent components of your WooCommerce site.
### 8. Implement Click-to-Call Buttons on your E-Commerce Portal
Click-to-call buttons do exactly what they say on the tin - they allow mobile customers to call with a single touch. Making it easier for customers to get in touch, especially on mobile storefronts, provides an edge over competitors that don’t. It allows users to quickly overcome issues or pull further down the sales funnel. In fact, Forrester Research reported a [143%](https://www.builtinla.com/articles/what-click-call-forrester-research-reported-roi-increase-143-25-million-extra-revenue) average return in ROI for businesses who implemented click-to-call functionality.
The feature is [relatively easy](https://www.callrail.com/blog/add-click-to-call-button-website-html) to implement. But you should prepared for an increase in calls from potential customers and train staff accordingly.
### 9. Test and Refine your Mobile Site Regularly
Quality Assurance (QA) is essential for all software ventures, and WooCommerce sites are no exception. Regular testing of your site allows for the quick detection of bugs and sources of potential friction. This allows fixes and improvements to be deployed quickly and maintain a high standard of mobile performance and UX.
A wide variety of testing tools, methodologies, and philosophies exist - enough for several full articles on the topic. We’ve collated some of our best advice about web testing here:
- Test core components of your site after every deployment. If possible, have safeguards in place to prevent deployments that break everything.
- Run tests on multiple devices, operating systems and form factors. That includes desktop, tablets, mobiles and different browsers on the same device.
- Automated front-end testing with tools such as Appium and Selenium can save on long-term costs, provided the component being tested is stable.
- Do not skip user acceptance testing. This is end-to-end testing by people who do not know the mechanics of the implementations, i.e. getting as close to the actual customer as possible. If you only have the budget for one type of testing, do this.
## Tools and Resources
We’ve mentioned a few resources for mobile optimization throughout the article, and we’ve gathered them all here for easy access, along with a few we didn’t mention:
- [Google’s Lighthouse](https://developer.chrome.com/docs/lighthouse/overview/): Open-Source tool to measure loading speeds
- [TinyPNG](https://tinypng.com/): Simple tool for image compression.
- [Canva](https://www.canva.com/colors/color-wheel/): A color wheel to help choose complementary colors for your site.
- Our recommended plug-ins, [WPtouch](https://wordpress.org/plugins/wptouch/), [Jetpack](https://wordpress.org/plugins/jetpack/), and [WP Mobile Menu](https://wordpress.org/plugins/mobile-menu/).
- [Appium ](http://appium.io/docs/en/latest/)and [Selenium WebDriver](https://www.selenium.dev/documentation/webdriver/) for automated in-browser testing.
- [Google Analytics](https://marketingplatform.google.com/about/analytics/) and [Matomo ](https://matomo.org/)for analysis of web traffic on your site.
Make your WooCommerce site into a winner and boost conversion rates.
## Conclusion
We’ve looked at the importance of mobile optimization for your WooCommerce site, and at a selection of methods to turn your website into a winner, securing a great user experience and driving up conversion rates. Whether it’s increasing load speeds, responsive design, improving mobile navigation or applying best practices in data analytics and testing, we’re confident that there is something in this article that can help you.
Do you want to do more to boost your WooCommerce site’s performance? At Levamo we make it our mission to launch secure, high-performing websites. [Click here](/#dynamic) to learn more about how Levamo can help you boost your site’s performance.
---
## Unlock Your WordPress Freelancing Potential: Profit Like a Pro
- URL: https://levamo.com/blog/wordpress-freelance-success-guide/
- Category: wordpress
- Author: Tom Cheddadi
- Published: 2024-05-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WordPress freelancing can be lucrative. Start profiting like a pro today.
For a WordPress freelancer, the only barrier to entry into the world of business up till now has been mindset. Before the rise of remote work in 2020, many viewed freelancing as little more than a side hustle. Meanwhile, parents worldwide would constantly urge their freelancer offspring to “get a real job.”
Of course, this is far from the truth. For almost all types of knowledge work, there is no need to be anywhere specific to get work done. And if it brings in money, it’s a real job by definition. Take that, ma!
In this guide, we aim to help new WordPress freelancers navigate the freelance landscape and kickstart their own freelance business, whether they sell design services, theme/plugin development, SEO, security audits, hosting support, or anything related to WordPress.
Read on to find out how to become the freelancer you always knew you wanted to be.

## An opportunity of a lifetime, and a lifetime’s worth of opportunity
Why is freelancing, or even remote working, such a good deal for those with skills in WordPress? For one, all you need is a computer with internet, a head on your shoulders, and time on your hands.
That goes for a lot of other types of jobs, too, though. So take a look at these stats and you will understand why WordPress represents a lifetime of opportunity for those with the skills to wrangle it:
- An estimated 800 million websites use a Content Management System, of which about 43% rely on WordPress. This is an enormous potential client base, no matter how high the competition.
- According to Search Engine Journal, the number of websites using WordPress increased by 227% between 2011 and 2022.
- There are over 30,000 WordPress themes and 50,000 free plugins in the WordPress plugin catalog. It is Murphy’s Law that every single one has a hidden bug or plugin conflict issue that *someone *is going to have to figure out and fix at some point. If you are into plugin development, that person could be you… for a reasonable fee, of course.
- According to WordPress.org, only 49.9% of WordPress websites are updated to the latest version (WordPress v6.5) at the time of writing. Guess who will be called to help update the other 51.1% of (some horribly) outdated WordPress installations? Very likely a skilled freelance WordPress developer who can ensure that the updates go smoothly without breaking the site. This kind of service is vital to many bigger website owners who can’t risk downtime, and the same goes for security, optimization, maintenance, and more.
### Why become a WordPress freelancer?
Not yet convinced by the above stats? Here are some more of the top reasons to get started as a WordPress freelancer:
- **No investment needed:** WordPress is free to download, use, and modify for any number of websites you can create. Thus, your time and effort will be the only meaningful expense for most of your freelance services. The rest is essentially profit.
- **Unlimited earning potential:** Want to charge an arm and a leg because you know your work is that good? No one’s going to stop you (although clients might not hire you altogether). Just ensure you can deliver that level of service and quality or you will be back to the 9 to 5 in no time.
- **Do things your way:** Your business means your rules, putting you in control of your equipment, workflow, tools, and processes that you use to get things done. You also decide your working hours so you can work away at your most productive times (night owls, anyone?).
- **It just makes sense:** Many companies prefer hiring a WordPress freelancer for different WordPress jobs and tasks rather than a full-time employee. In many cases, it wouldn’t be viable to have an employee. Big digital agencies and development studios also sometimes need WordPress freelancers to help with client overflow work, so that is yet another addition to your potential client base.
### And… the drawbacks of being a WordPress freelancer
To be fair, there are also some drawbacks to making a life for yourself as a WordPress freelancer, such as:
- **You’re on your own:** If you are an extrovert who feels the isolation of freelancing more than most, it might be wise to seek traditional employment. On the other hand, the WordPress community has a strong history of socializing, sharing, and networking. This gives you plenty of opportunity to collaborate with others in the real world, and not just behind a screen.
- **Less job security:** A client can vanish at any time and there is nothing you can do about it. As long as they have paid their dues, of course. You will need to develop good client retention and time management strategies to prevent this from seriously affecting your income stability.
- **No employee benefits:** Being self-employed, freelancers don’t receive employee benefits from any company, as they are both the employee and the employer. On the other hand, you are surely a kind and generous boss. Buy yourself a chocolate or something nice once in a while (or any time you want) and call it the benefit of being a freelancer.
- **Your work-life balance can get weird:** Don’t be surprised if you find yourself deep in thought about your latest plugin customization project instead of focusing on a romantic dinner with your date. Try not to do that, okay?
## Building your foundation as a WordPress freelancer
The problem for most new freelancers is that they don’t know exactly what kind of work is available, or where to begin looking for it.
They might know their way around WordPress quite well from a technical perspective, with good knowledge of all the moving parts behind it. But still, they struggle to convey what it is they can offer a client.
Considering that there are hundreds of niches within niches a WordPress freelancer can pursue, this is no surprise. Want to be the expert at setting up Contact Form 7 integration with MailChimp? Well, if there is a market for it, why not, right?
### Example niches for a WordPress freelancer
To help you gain a bird's-eye view of some of the more popular niches you can delve into, here are a few typical WordPress skills and service offerings with examples.
**Theme development and design**
- Example niche: Specializing in the creation of new WordPress themes or the customization of existing ones.
**Page layout design**
- Example niche: Specializing in using Elementor to design attractive landing page layouts.
**Custom plugin development**
- Example niche: Specializing in the creation of custom plugins developed to client specifications.
**Security and networking**
- Example niche: Specializing in the configuration of security and network settings to ensure protection from hackers, malware, and spam.
**System Administration**
- Example niche: Specializing in the installation, troubleshooting, and maintenance of server operating systems and system software optimized for high-volume, WordPress-based e-commerce sites.
**SEO**
- Example niche: Specializing in technical SEO audits for blogs, magazines, newspapers, and other publications.
**Accessibility**
- Example niche: Specializing in ensuring adherence to WCAG accessibility standards for WordPress.
**Publishing**
- Example niche: Specializing in creating blog posts, website content, copywriting, and other professional writing and article design services for WordPress websites.
Depending on your experience level, you may offer freelance services in many or all of the above areas. However, each niche has its unique system of tradecraft. Try not to overwhelm yourself by offering everything under the sun, even if it means casting a smaller net for clients until you are more ready to branch out.
The fantastic thing about open-source software is that everyone can get involved in some small way. That’s another reason it’s so easy to get started with WordPress as a freelancing platform; even if you can only do one thing well, start there.
## Setting up shop as a professional WordPress freelancer
A completely accurate depiction of how freelancers get paid.
Say after me: “I am a freelance WordPress specialist.” Congratulations, you are now a professional freelancer!
No, seriously, that’s all there is to it - everything else is a formality (although yes, the formalities are still important). You might not have any clients yet, but that doesn’t matter. Anyone can be a freelancer at any time, even if they already have a full-time job.
### Formalities
In legal and administrative terms, a freelancer is, by default, a sole proprietor. This is the simplest type of business structure in which an individual is self-employed and takes on all liabilities and potential debts. Sole proprietors don’t register a business name but instead use their personal name for trading, marketing, invoicing, and tax purposes.
The next simplest business structure is a **partnership**, which is similar to a sole proprietorship in that both you and your partner are personally responsible for debts and liabilities.
If you want to trade and market yourself under a registered company name rather than your personal name, you can register your freelance business as a company such as an **LLC** (Limited Liability Company). With this, all income, expenses, debt, liability, etc. are attributed to the company rather than you, which helps protect you against risk.
### Tax deductions
Regardless of your business structure, you will need to keep track of all income earned and the expenses incurred in earning that income for tax purposes. When submitting your tax return you can deduct various expenses, including:
- Internet costs and software products.
- Marketing, accounting, and bookkeeping.
- Equipment (e.g. PC/laptop) and maintenance.
- Rent and utility bills for your designated home office or workspace.
- Business travel.
Please note that company registration and tax laws differ around the world, so it is always best to consult with a local accountant and/or tax advisor about how to structure your freelance business.
Here are some other questions you will need to ask yourself:
- What needs to be in your client contracts to ensure you are covered from all angles?
- How are you going to accept payments? For example, bank transfers, credit/debit cards, PayPal, Stripe, or Payoneer.
- Will you use your personal bank account or open a separate account for your business?
- Are you going to do all your bookkeeping and taxes yourself, or will you need to hire a professional?
### Personal branding
With freelancing, your name is your brand.
If, like many freelancers, you are going ahead as the sole proprietor of your freelance business, you will be trading under your own name. This means that all your marketing efforts will be focused on you as both a person and a professional.
Here are some tips to help you develop your personal branding:
- **Write a strong bio:** Who are you? What skills and services do you offer? What is your experience, and do you have any projects you are particularly proud of? Is there anything that makes you different from other freelancers offering similar services? You get the picture.
- **Register on freelance sites:** Fill out the required profile overviews with a well-crafted bio for each and a description of your services, and don’t forget to add your portfolio pieces. Being visible on these sites can help you get your name out there, even if you aren’t yet getting any work from them.
- **Create a portfolio website:** Having your freelance profile on a marketplace site is great, but you have little control over its look and feel. Luckily, you know WordPress, so create yourself a nice portfolio website that will wow potential clients the moment they land on it.
- **Advertise yourself:** Whether you run ads to your freelance profile on a site like Upwork, or to your portfolio website, this is a quick way to get in front of people who will pay for your services. You might also want to create ads in local or online classifieds. Additionally, consider using a [logo maker](https://www.design.com/logo-maker) to design a standout logo that you can include in your ads, creating a professional look for your brand.
- **Build a reputation in the WordPress community:** Whether it’s contributing code to WordPress itself (or themes and plugins), or simply volunteering support and helpful comments to people in need on forums, get yourself out there!
Also Read: [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
## Finding clients and winning contracts
Don’t think that just because you have a professional profile on various freelance sites and a beautiful personal portfolio site, clients will just start flooding in. That’s all necessary groundwork, sure. But to win actual contracts you will have to be proactive.
Here we will cover strategies for finding and approaching clients, crafting proposals, and [pricing your services](/blog/pricing-strategies-for-wordpress/).
### Engaging with clients
Beyond setting up your freelance profile on freelance sites and having a website where clients can find you, there is already a vibrant community environment for you to begin networking within. This community, whether on the official [WordPress support forums](https://wordpress.org/support/forums/) or elsewhere on the Web, will be your go-to not only for finding potential clients but also for learning about common problems that people need solutions to.
But your search for clients doesn’t have to stop there.
Get creative and act like a detective: start local and scope out the WordPress websites of businesses in your area. Local is best for starters, as it is easier to win contracts if you can get to the decision maker (usually the owner) in person and present your services much like a sales rep does.
### Getting your foot in the door
An excellent starter sales tactic is to do a free site audit for your potential client. For example, are they offering an online store with WooCommerce, but their product images are all blurry, their checkout page is broken, or their email form isn’t sending emails?
Type up a report with all your findings and hand it over to the company with a description of how you will fix each issue, and how much they can expect to pay.
“Ma’am, this is no website. This is a crime scene.”
Of course, not everyone who wants to freelance is prepared or able to do this (after all, you want to work from home, not roam the streets looking for business), but this isn’t necessarily an ongoing activity. It is simply a kickstart to get you:
- Earning money (the number one priority).
- Winning clients who can refer you to other clients and give you testimonials.
- Gaining professional experience and making a name for yourself.
### Consulting as a WordPress freelancer
Later on, once you know your WordPress niche extremely well, you can also do consulting, which doesn’t involve any hands-on work but simply entails guiding a client to find the right solution.
Consulting is a great opportunity because there are so many moving parts in WordPress that clients can easily get overwhelmed. They may simply need someone to tell them if it makes sense to go with a certain plugin for the use case they have in mind.
Then, of course, you can upsell them regarding your proposed solutions by offering to do the work as well. For instance, if they ask you to recommend someone, tell them: “I might know a guy/gal”, and wink. Referring to yourself, of course.
If you’ve created any WordPress products (themes/plugins/productivity tools) that you can sell, you can align your freelancing services with these products by offering personalized support and custom development, priced at your standard freelance rates.
Often a client wants something that is mostly covered by a plugin, but it needs just one or two tweaks to the code. Be the person who can help with that, and you may easily unlock further business with them down the road.
### Billing hourly vs. per project:
The two main ways to charge for your services are hourly and per project (or deliverable). It’s up to you to decide when it makes sense to go with either billing type.
**Hourly billing:** You charge an hourly rate (e.g. $45/hour) by tracking your time and invoicing the client based on how long it took you to complete the job. Different types of jobs might have different hourly rates depending on complexity. Use an hourly rate calculator such as the one by [Clockify](https://clockify.me/hourly-rate-calculator) for help with this.
**Per project billing:** You charge a fixed price based on the value of what you can deliver. This makes sense for well-defined tasks with a clear scope and can be more lucrative than hourly billing in cases where the work can be done at a fast rate. For example, you may charge a fixed price of between $500 and $3,000 to install, configure, and design a basic WordPress website.
A note on competitor pricing: Some regular companies and agencies charge a premium for simple services that a freelancer would gladly do for a fraction of the cost. This isn’t because the companies are greedy, per se, but is more about having to offset the expenses of paying full-time staff, renting office space, etc.
When you are pricing your services to be competitive in the market, pay attention to what other freelancers are charging, and not only what companies charge.
### Proposal tips to win contracts
Check out these tips to help you write proposals that won’t be overlooked.
**Show relevant work only:** Imagine yourself as a client needing a WordPress security audit - would you hire someone who can only show you portfolio samples of work that have nothing to do with security? Of course not. Yet, many freelancers make this mistake, thinking that their experience in creating a nice-looking website should be enough to convince the client of some overall broader skill set. Rather be specific and always show work that the client will instantly recognize as relevant to their needs.
**Leverage your non-WordPress skills and experiences:** For example, if you’ve previously worked retail at a high-end luxury store, you can use this to your advantage when approaching clients in the jewelry or luxury fashion industry who need help with their company’s WordPress site. Clients are more inclined to hire freelancers who can not only design a great website but also understand the client’s industry at a deeper level.
**Strike a balance between broadness and specificity:** You want to let your client know exactly how you can provide a solution… but don’t box yourself in. Make it known that your proposal is only tentative, and may be subject to changes as you become more informed about the scope and requirements. Try to remain flexible from the very beginning, as client needs can and do evolve.
**Leave room for negotiation:** State your pricing upfront in your proposal, but don’t dig in your heels if the client tells you they don’t have the budget for you. Instead, enquire further to negotiate within their actual budget. You might not win the whole contract, but instead, only a certain part of it that the client can afford, and that’s good, too.
## Project management mastery
The blue lines are for planned nap time, of course.
An intrinsic part of being a WordPress freelancer is juggling multiple client projects at once. Naturally, this demands a certain level of planning.
Fortunately, as a one-person business, you won’t need to take a lengthy course on project management, for instance, as these are more relevant to large teams within organizations than single freelancers.
Your project management strategies need not be too complex and might involve:
- **Determining project scope:** What all needs to be done? Get it all in writing, itemizing each separate aspect (e.g. design mockups, installation, custom development, etc.).
- **Estimating time to completion:** How long will each milestone take? What’s the priority or urgency of this project compared to the others in your pipeline?
- **Tracking your time:** So you spent 3-6 hours writing code for a new plugin? Well, which is it? 3 hours or 6? If you don’t know, you can’t bill your clients fairly or accurately.
- **Remembering that you are human:** Sleeping, eating, household chores, a social life; all these things must be taken into account. You’re not just a freelancer, you’re human, too!
As much as you might like to wing it, planning out the basic outline of your projects is crucial to staying on track and keeping clients happy. Always set aside enough time to organize your project workflows for each new client. And if you can’t deliver to your client’s desired deadline, let them know immediately, not later.
### Productivity tools for WordPress freelancers
Here are some powerful tools that can help you manage clients and execute your projects like a well-made machine, especially if you’re not the only freelancer working on a large WordPress website project:
- [Trello](https://trello.com/)
- [Asana](https://asana.com/)
- [Basecamp](https://basecamp.com/)
- [Monday.com](http://monday.com/)
- [Jira](https://www.atlassian.com/software/jira)
- [Calendly](https://calendly.com/)
If you need help with creating invoices and keeping them organized, see these solutions that are ideal for freelancers and small businesses:
- [Wave](https://www.waveapps.com/)
- [FreshBooks](https://www.freshbooks.com/)
- [Zoho Books](https://www.zoho.com/books/)
- [Paymo](https://www.paymoapp.com/)
- [Xero](https://www.xero.com/)
- [Moxie](https://www.withmoxie.com/)
And don’t forget to check out some of the [project management plugins](https://wordpress.com/plugins/browse/projectmanagement) made specifically for WordPress that you can easily integrate with your portfolio website.
## Growing towards sustainability
There’s a bit of a catch-22 for freelancers who haven’t quit their day job just yet: they want to grow their freelance business to a full-time venture, but they aren’t sure they can make it sustainable enough to live on.
They might have already seen some freelance success, but they were small jobs and only to be considered a bonus on top of their existing salary. The big catch is that they won’t ever know if they can pull it off until they dive in, and that can be risky.
If this sounds like you, you’ll want to work on your [client retention strategies](/blog/strategies-client-attraction-retention/) so that you can build up a steady, stable stream of work, gradually working toward a minimum of sustainability. In other words, maybe don’t quit your day job just yet, but instead, aim to test how well the freelance market can sustain you over time.
Your ideal goal is just the right mixture of projects from one or several clients to keep you earning at a comfortable, consistent rate.
### Client retention strategies
Consider these client retention tips that apply to all types of WordPress freelancers:
- Deliver impeccable customer service by meaningfully communicating with your clients. Freelance work isn’t just about business transactions, but also about fostering relationships and making clients feel special.
- Offer reasonable rates. A desperate client might pay good money for a project now, but if you want them to keep spending, your pricing needs to match their long-term budget.
- Create solutions tailored to your clients so that they won’t ever want to go elsewhere. Ensure you do your homework on both the client’s needs and their overall industry.
- Don’t be shy to ask for feedback. If a client’s satisfaction with your services dwindles, they might not even tell you before deciding to move on. Elicit these concerns and address them.
- Apply cross-selling and upselling tactics to keep the client on board with you even when they no longer need the service they came to you for. For example, if you’re contracted for a one-off website creation job, consider offering the client ongoing support to handle plugin updates and other maintenance tasks.
### Scaling up as a WordPress freelancer
If you find that you can’t do it alone and need some help with various matters like marketing or accounting to free up your time, that’s perfectly reasonable.
As it happens (surprise!), there are freelance professionals out there who can help with any tasks you don’t want to be burdened with yourself. If it makes sense and eases your workload while helping you grow, use them.
Doing the work of 5 people all by yourself? Not advised.
Meanwhile, you can also delegate some of your non-critical work (or non-specialized tasks that only you do best) to another WordPress freelancer in your field. For example, hiring someone to manage basic admin tasks from within the WordPress dashboard can help free you up for more lucrative tasks that make better use of your skills, such as coding or design.
Pretty soon you might just have a bustling full-service freelance agency on your hands.
### Expanding your services
Let’s say you’ve done everything right and you are assured that the income from your existing freelance business can sustain you. Why rest on your laurels when adding to your skills is so easy in the world of WordPress?
Here are some ideas on how to expand your horizons:
- [Get certified](https://www.tealhq.com/certifications/wordpress-developer).
- Take online courses on popular learning websites such as [Coursera](https://www.coursera.org/courses?query=wordpress), [Udemy](https://www.udemy.com/topic/wordpress/), [WP101](https://wp101.com/), [WPSessions](https://wpsessions.com/), and [WP Apprentice](https://wpapprentice.com/).
- Attend [WordPress events](https://events.wordpress.org/) and conferences like [WordCamp](https://central.wordcamp.org/) for networking and partnership opportunities.
- Work on your soft skills and learn about how to lead and manage a team that can boost your growth, productivity, and profits.
- Stay on top of new developments in WordPress so you can constantly add the latest and greatest solutions to your arsenal.
- Be affiliate partner with relevant tools like [](/managed-wordpress-hosting/)[fully managed WordPress hosting](/managed-wordpress-hosting/) or WooCommerce managed hosting providers and earn extra revenue recommending that.
## WordPress freelancer success stories
This guide wouldn’t be complete without a few examples of noteworthy freelancers who have used their WordPress skills to build thriving businesses.
The first inspirational example is Erik Karkovak, a highly successful WordPress developer and designer who first began working with WordPress in 2005. He details his falling in love with WordPress as a freelancer and how it helped him pursue his dreams in this [short essay at HeroPress](https://heropress.com/essays/broadening-my-horizons-through-wordpress/).
Next up is Chris Misterek at SelfMadeWebDesigner.com, a former pastor who doubled his previous full-time employment income in only 18 months by working as a freelance WordPress web designer. Chris tells his story of how he became successful by always putting clients first, in the article: [From $500 to $4500 for WordPress Websites in No Time At All: My Story](https://selfmadewebdesigner.com/from-500-to-4500-for-wordpress-websites-in-no-time-at-all-my-story/).
Then we have the uplifting story of Mohammad Kasim, a freelance UX/UI/Product Designer who started freelancing on Fiverr in 2016 and later moved to Upwork, where he has so far earned upwards of $100K. Read about his journey and advice for new freelancers here: [Success Story: $100K On Upwork and 500 Orders Completed On Fiverr](https://www.linkedin.com/pulse/success-story-100k-upwork-500-orders-completed-fiverr-muhammad-qasim).
These are great stories, but they’re certainly not the only ones. Millions of ordinary people have made a life for themselves, with full financial freedom, all thanks to their skills in WordPress. And some have become rather wealthy, indeed. Why not you, too?
## Wrapping up
Well done, you’ve reached the end of this guide to building a successful freelance business with WordPress! You are now equipped with all the basic knowledge you need to:
- Start on a strong foundation by identifying your WordPress skills and suitable niches.
- Set up your freelance business the right way, understanding what is involved from a legal and admin perspective.
- Find and engage with clients, win contracts, and retain business for the long term.
- Increase your productivity with powerful project management tools.
- Grow your business further by expanding your team, skills, and professional services.
What’s next? Well, that’s up to you, of course, but we recommend taking a deep breath, opening up your notepad, and gifting yourself a fresh new freelance bio that you can use to get started on any number of [freelance marketplaces](/blog/best-freelance-websites/)… right now.

---
## Skyrocket WooCommerce Sales Instantly with these 10 Quick Wins
- URL: https://levamo.com/blog/woocommerce-conversion-optimization/
- Category: ecommerce
- Author: Ochai Emmanuel
- Published: 2024-05-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Boost WooCommerce sales! 10 quick wins for instant e-commerce conversion.
Many e-commerce businesses perform poorly and fail because they focus on promoting visibility while neglecting conversion. However, experts agree that business growth depends not on who sees you but on who buys. So, if you have good traffic on your WooCommerce store without sufficient purchases, you must optimize your e-commerce shop for increased conversion.
This conversion rate optimization helps your business to grow economically, providing sufficient returns even for your SEO investments. While many consider this a long, slow, and steady process, it doesn’t have to be so. With proper guidance, you can optimize your WooCommerce conversion rate to maximize impact instantly with minimal effort.
Therefore, this article details the WooCommerce Conversion Rate Optimization (CRO) concept. It further provides ten expert tips and quick wins for optimizing your WooCommerce shop for increased conversion and revenue generation.
[](https://unsplash.com/photos/a-computer-screen-with-a-line-graph-on-it-_Lnid7JAWFQ)A closeup view of a desktop screen showing an analytics page of a website overview.
## Understanding WooCommerce Conversion Rate Optimization (CRO)
From a broad perspective, conversion rates describe the percentage of your e-commerce shop **visitors who carry out the desired shop action. These actions are not limited to purchases; conversion occurs when visitors subscribe to your email, add to their carts, or submit forms. Provided any of these actions were a desired target of the shop owner, their occurrence constitutes a conversion**.
However, since most WooCommerce stores primarily target product purchases, this article focuses on purchase actions in discussing conversions. Now, what is conversion rate optimization?
CRO describes how you increase the percentage of your e-store visitors who perform the desired actions on your e-commerce shop. Note that this does not necessarily mean gaining more viewers. Instead, it focuses on how to get more out of the existing traffic on your shop.
Many e-commerce shop owners believe leads or conversions only increase when visitors increase. So, they continuously spend on promotions to attract more visitors. Conversely, the nature, structure, and operation of your e-commerce shop more significantly influence your conversion rates.
These features can encourage customers to purchase or visit another e-store. Thus, optimizing these features in your shop can directly convert more existing visitors to paying customers.
## 10 Quick Conversion Wins To Improve Your WooCommerce Conversion Rates
Your conversion increases when you please and satisfy more customers. But how can you achieve this over an e-commerce store? Although you cannot see your customers physically, you know the factors influencing customer behaviors that promote customer loyalty. Many of these factors revolve around your sales process and their customer experience.
Therefore, you can improve these factors to enhance satisfaction and improve conversions. This section outlines ten quick wins and expert tips for instant customer rate improvement in your e-commerce shop.
[](https://unsplash.com/photos/person-holding-black-samsung-android-smartphone-rocEacp5Y6c)A person holds a black iPhone with the screen displaying the Internet speed-check page.
### 1. Use Speed Optimization for Higher Conversion
Your website speed describes how quickly browsers can load pages from your site. It is an important factor that directly impacts user experience. Shoppers have limited patience and expect all sites to load fast. So, when your site loads slowly, they will likely leave it for alternative e-commerce stores.
A report shows that sites with a one-second load time curate [three to five times higher conversion rates](https://www.portent.com/blog/analytics/research-site-speed-hurting-everyones-revenue.htm) than those who load in about five to ten seconds. Thus, you can massively and instantly boost your conversion rates by simply [enhancing your website speed](/blog/speed-up-woocommerce/). Choose a [fully managed WooCommerce hosting](/managed-woocommerce-hosting/) to optimize your eCommerce website.
#### How To Measure Speed Optimization
There are many ways to measure your site speed, including the first-byte time, load time, and start render time.
The first-byte time measures the duration between a browser requesting a page from your website and receiving the first information byte for the server. Load time describes how long it takes for the entire page to be viewed after submitting a URL. Similarly, the start render time measures the duration between sending a request and the page loading enough for users to interact with.
These are only some basic metrics that help measure your website speed. Several tools exist to help you measure these and other essential metrics. Some of these include;
- [Page Speed Insights](https://pagespeed.web.dev/)
- [GTMetrix](https://gtmetrix.com/)
- [WebPageTest](https://www.webpagetest.org/)
#### Tips for Improving Your Website Speed
[Users are more likely to complete desired actions](https://www.cloudflare.com/learning/performance/more/website-performance-conversion-rates/) when a website loads faster. However, it doesn’t take much to optimize your website to boost its speed massively; a few common tweaks are all you need. Here are seven tips to help you improve your website speed:
- Minify your JavaScript, HTML, or CSS files by removing white spaces and redundant characters. Then, compress the files using compression algorithms.
- Optimize your image through resizing and compression, and use the correct format for each image.
- Use content delivery networks to share your content across multiple servers for faster loading.
- Optimize your server queries to reduce your server response time.
- Use browser caching to store accessed files on the users’ devices to eliminate re-downloading needs.
- Apply responsive designs to enforce mobile optimization.
- Use a optimized [fully managed WordPress hosting](/managed-wordpress-hosting/).
### 2. Ensure Audience Targeting and Factor in Your Website Goals
Targeting your audience helps ensure positive customer experiences, directly impacting your conversion rate. Conversation only happens when you keep visitors in your e-commerce shop and impress them enough to do what's needed.
That is only possible when you use a tone for your content and a site structure that appeals to your target audience. However, you'll need to know your audience to target them.
Every WooCommerce shop has a specific target audience for its products. Therefore, your target audiences are the **people who are most likely to purchase your products. Some products target teenagers, some mothers, while others target elite socialites**.
[](https://unsplash.com/photos/person-writing-on-white-paper-U33fHryBYBU)A person draws arrows toward the word “AUDIENCE” on a whiteboard.
It helps to direct your marketing effort on the shop to your specific audience class. Doing this helps you to create a more personalized and engaging experience for your shoppers. It also increases the relevance and value of your content and products to this audience.
Your website goals complement audience targeting to help increase your conversion rates. After you identify your audience, you can set goals for them that you want to achieve through your website. Defining your website goals also helps you streamline your shop features and operations to achieve them.
These goals also help you create key performance indicators (KPIs) to measure your campaign success. Below are five examples of website goals you can set for your target audience:
- Increasing purchases
- Increasing social engagements
- More subscriptions
- Increasing customers’ cart size
- More successful upsells
### 3. Take Steps Towards Improving Website Performance
Website performance generally describes website speed - how quickly a site loads and renders. Your site performance is the first event your shoppers experience, and it can cause them to stay long enough for conversion or leave for alternative shops.
Many features, including hosting and page weight, affect a website's speed and performance. Optimizing these features can improve your site’s performance. Though simple and familiar, these tweaks make a world of difference.
Consider some strategies you can adopt to improve your website’s performance for increased conversion rates:
#### Pay Attention to User Experience
Your website's user experience (UX) design does not necessarily impact its speed. However, it directly impacts its performance through the sentiment and response of the users. Experts believe a good user experience on your site encourages more purchases and conversions. An **excellent UX design can increase brand value** massively, attracting loyal customers.
When your site is easy to navigate, with attractive buttons, product display, and simplified processes, shoppers will readily purchase and return for more. That rates your e-commerce shop as a high-performing website.
Below are some quick wins that can help improve the UX design of your website:
- Use images properly
- Leave sufficient white space for skimmers
- Implement simple and straightforward navigation
- Differentiate hyperlinks
- Use good and easy-to-read typography
- Use attractive CTA buttons placed on hotspots
- Limit ads and place them appropriately
- Use an exciting and attractive color scheme
#### Invest in Mobile Responsiveness and Friendliness
Many web developers ignore mobile optimization because of its heavy demands. It requires updating font size, positions, shapes, and patterns according to screen size. But while this is laborious, it’s worth the investment.
Statistics show that [over 50% of every website’s traffic today comes from mobile devices](https://happyaddons.com/how-to-improve-website-user-experience/#secrets-on-how-to-improve-website-user-experience:~:text=over%2050%25%20of%20traffic%20for%20any%20website%20today%20is%20generated%20from%20mobile%20devices). The convenience of mobile devices for internet users makes it the primary channel for accessing e-commerce stores.
So, if your website is not mobile-friendly and responsive, you’ll lose out on many customers. Conversely, if shoppers can easily access and navigate your WooCommerce store, they’ll readily purchase your products, increasing your conversion rate.
[](https://unsplash.com/photos/monitor-showing-java-programming-OqtafYT5kTw)A closeup image of a part desktop screen showing lines of code for a web page.
#### Review and Reduce Your Page Weight
Page weight is the sum of the size of all the resources on a webpage, including images, code files, embeds, etc. This weight directly impacts your website speed and load time. The heavier a page, the slower it loads.
Most of the time, all the resources on a page are essential, and you cannot remove them. You can lighten the page weight by compressing images and codes in this case. Review your code lines to remove redundant characters. Then, compression tools are used to compress images while maintaining their quality.
Doing this lightens the page for faster request retrieval and a shorter load time.
### 4. Work on WooCommerce Product Page Optimization
Optimizing your product page for conversion means improving its content, functionality, and design to encourage purchases. It involves optimizing the page’s features, including the CTA buttons, reviews, price, product description, and images.
The goal is to create a personalized shopping experience for each shopper on that page and to boost their confidence in the product and brand. Let’s discuss three quick wins for optimizing your product page using key page features:
#### Use Compelling and Functional Images
In commerce, people judge the book by its cover. So, create a compelling cover using good product images to advertise your product. While many shoppers may only skim through product descriptions, they spend time on the product images. So, use images that allow them to see or even feel the product’s details and long to have it.
Your images on this page must also be functional. It helps to upload images of product variants. It allows shoppers to choose their products based on color, style, packing, and delivery techniques. Such functional images may compel a speculative visitor to purchase your product immediately!
#### Keep the Call to Action Clearly in Sight
The primary purpose of your product page is to compel shoppers to buy the product. That happens when they click the “Buy” or “Add to Cart” buttons. Therefore, always keep this button in sight on the page. The typography, text, and highlights must stand out so that it’s the first thing buyers notice when they land on this page.
Mobile optimization is crucial to ensuring you reach mobile shoppers this way. Keep this button central on your product page so it remains visible and accessible wherever the shopper navigates.
[](https://unsplash.com/photos/a-person-holding-a-black-book-with-the-word-buy-written-on-it-Uh5GWNUGgGY)A person holds a black card with the word “BUY” printed in gold.
#### Use a Rich but Concise Product Description
Customers don’t want to read much on a product page, but you must convince them to part with their bucks. An extended product description may discourage them from reading and buying your product. So, **write a rich and concise description** that captures all they need to make a satisfying purchase decision.
If you need to use many for your product description, create sections like warranty information, size, features, purpose, etc. Then, you can hide more information in these sections beneath drop-down menus to keep your product page clutter-free.
### 5. Intensify Checkout Process Simplification
Shoppers are more likely to complete the purchase process when the checkout process is simple and requires less effort.
This is doubly true for B2B and wholesale buyers, who often order dozens of SKUs at once and will abandon fast if they’re pushed through a slow, retail-style checkout. A [purpose-built order form](https://wholesalesuiteplugin.com/creating-winning-customer-order-forms/ "nofollow") lets them enter quantities in bulk and check out in a fraction of the clicks.
In contrast, they readily abandon a product mid-purchase at even the slightest friction they experience at checkout.
Therefore, it helps streamline your store's checkout process to encourage smoother purchases and increased conversion. It is one of the most common yet effective conversation rate optimization techniques all WooCommerce stores can adopt.
Below are two quick wins for simplifying and improving the checkout process on your e-store:
#### Allow Guest Checkout
Guest checkout allows a buyer to check out of an e-store without logging in or creating an account. The traditional approach of requesting account creation when checking out is reasonable. This allows you to collect information to build a database for continuous engagement. While the rationale is excellent, the enforcement is not so much.
These simple pop-ups that request login and account creation discourage many buyers from completing their purchases. So, you can improve your checkout process by offering guest checkout. A more straightforward process means more sales and conversion. In time, return customers will willingly create accounts and queue products in their carts.
You could also modify your checkout system to present the pop-up with purchase confirmation. This way, you offer account opening without causing friction in the checkout process.
#### Use a Simple Payment System Allowing Multiple Payment Options
The modern customer expects convenience at every stage of their journey with an e-store, even at checkout. Whenever this is lacking, it could hinder conversion even from willing customers. Therefore, you can optimize conversion on your e-store by using an effective payment system that ensures convenience.
**A convenient payment system supports multiple payment options**, such as credit and debit cards, gift cards, and other digital currencies. It should also support payment plans and continuity billing for subscriptions. Choose a payment system like [WooPayments](https://woocommerce.com/products/woocommerce-payments/), which supports all these features to simplify payments on your WooCommerce shop and optimize conversions.
[](https://unsplash.com/photos/woman-holding-silver-iphone-6-SpVHcbuKi6E)A woman with her phone, laptop, and bank token device checking out of an e-store.
### 6. Implement Testing and Analytics
A/B testing, or split testing, is a popular comparison method for evaluating two web page versions to determine which provides higher returns. The A/B test elements could be the CTA buttons, images, web page layout, or color scheme. However, only the tested element changes; all other features remain the same during the test. The goal is to extract empirical analytics data that highlights the better method.
Before a split test, you must set clear objectives for your text. These objectives will inform the KPIs that you monitor during the test. By testing an existing design (control group) against a variation with a specific element change, you learn how much a specific element impacts your conversion.
Most importantly, the analytics data show which version yields better conversion, allowing you to choose the most effective approach to conversion rate optimization on your e-store.
### 7. Publish Social Proof and Trust Signals
Trust signals and social proof are visible elements on your website that highlight your authority, credibility, and value to visitors. These include case studies, ratings, reviews, endorsements, badges, certifications, awards, and social media follower count.
Social proof and trust signals are not bragging elements; they help build credibility and trust with your audience. When you achieve this, you eliminate anxiety and objections from prospective customers, increasing your conversion rates.
Trust signals are especially important because they assure your visitors of security, reliability, and professionalism. Visible security badges on your page ensure that visitors can stay on your website without compromising their data. They also convince them to use your payment channel confidently without fear of data breach.
Publishing social proof and trust signals on your e-store are excellent conversion rate optimization strategies for instant improvements.
[](https://unsplash.com/photos/graphs-of-performance-analytics-on-a-laptop-screen-JKUTrJ4vK00)A website analytics page showing some performance metrics measurements.
### 8. Improve Product Search on Your WooCommerce Store
Speed is the primary factor influencing convenience for many shoppers. However, it’s not always about the web page and load time but also the time it takes to find the desired product on your WooCommerce store. Too much time and effort to find desired products can discourage potential conversions.
SEO will not always lead shoppers to your product page, so when they visit your website, help them find the right product quickly. You can do this by improving your website navigation and correctly categorizing products.
Another effective way to improve product search is to introduce an on-site search function. Place this function on a visible part of your page for easy accessibility. Buyers can use this to search for product keywords. The search function should also return fast and accurate results. You can improve the function with filters and indexing.
Although [only 15% of buyers use the search bar](https://www.addsearch.com/blog/site-search-statistics/), it contributes about 45% of revenue on e-commerce websites!
### 9. Sell With a Sense of Urgency
If left to most customers, they’ll only purchase products when convenient - a period that does not exist. So, they’ll readily fill out their wishlist and carts but never check out. This situation causes increased visits but low conversion.
You can fix this and optimize your conversion rate by creating a sense of urgency for your customers. **Give them a reason to want to buy now!** Many e-store owners sell urgently through limited-time discount sales; you can also adopt this method.
You can use promotional keywords to provoke fear of missing out on your juicy but limited offers in your customers. Limit offers by time and number of early buyers, and this approach will encourage buyers to check out faster and boost your conversion rates.
Shoppers always want to enjoy the advantage. Even a decimal percentage off gives them an advantage, mainly when limited. You can leverage this customer behavior to massively boost your conversions.
### 10. Prevent and Recover Lost Conversions
Recall that conversion rate optimization deals with increasing conversion percentage from the existing traffic. What better way to do this than to recover lost conversions?
All visits to your e-store move towards conversion, but most get lost, and many close to checkout. Studies show that about [98% of shoppers won’t buy a product on their first visit](https://blog.kissmetrics.com/why-visitors-arent-signing-up/). However, their visit shows interest in the products, hence their classification as lost conversions.
Luckily, a few quick wins, tips, and tricks can help you prevent conversion loss and recover lost conversions. Let’s discuss two, one for each category.
[](https://unsplash.com/photos/blue-and-white-logo-guessing-game-LPZy4da9aRo)A closeup image of the mail icon on a phone screen shows two unread emails.
#### Prevent Conversion Loss With Wishlists and Carts
No matter how exciting your product offer is, you’ll not always reach buyers at the right time. At such times, they’ll leave your product page without purchasing the product. However, with the Wishlist and Cart features, you can reel them back at the right time.
Allowing them to add their desired products to this list keeps their attention on the products until they’re genuinely ready to get them. Without these features, a customer journey may terminate abruptly. However, these features ensure that such visits reach conversion, however long it takes!
This is exactly where the right tool earns its keep. The easier a store makes it to save an item, the more shoppers actually do it instead of drifting off. A free, lightweight plugin like [SaveTo Wishlist](https://savetowishlist.com/free-woocommerce-wishlist-plugin/ "nofollow") lets visitors save products in a single click (guests included), then return to buy when they’re ready, turning a "not right now" into a recovered sale.
#### Recover Lost Conversions With Abandoned Cart Emails
Some shoppers add items to their e-store carts but remove them from their hearts. This leads to many abandoned carts in an e-store, increasing lost conversion from website visits. You can recover the conversion from such ones through warm reminders via email.
[Abandoned cart emails](https://www.virfice.com/recover-abandoned-carts-on-woocommerce-stores/) gently remind buyers of their unfinished business in your store. Those who genuinely forget will appreciate this reminder and follow up immediately. On the other hand, the reminder encourages those not yet ready to prioritize their purchase or review their cart. This common approach helps to clear out several conversions to increase your conversion rate.
## Recap and Actionable Steps
All the traffic on the internet and no conversion on your WooCommerce shop is a waste of your time and marketing efforts. To grow your e-commerce brand, you must optimize conversation rates to get the most out of your visits. You don’t need to break rocks or wait ages to achieve this. Some common, practical steps can massively boost your conversion rates almost instantly.
This article has considered ten practical and expert tips you can apply to your e-store. It ranges from A/B testing for elements to speed and performance optimization, audience targeting, checkout simplification, and trust signal publication. Thus far, you’ve seen how to apply these and other quick wins for swift conversion rate improvement.
To implement any of the tips discussed in the article, follow the steps outlined below:
- First, split-test the element you desire to improve.
- Next, acquire the tools and software needed for implementation. Many WooCommerce [extensions and plugins](https://woocommerce.com/product-category/woocommerce-extensions/?categoryIds=28698&collections=product&page=1) can help with your implementation.
- Further, hire experts for front and back-end development tweaks where necessary.
- Finally, monitoring tools should be used for successful evaluation.
---
## 10 Easy Ways to Speed Up WooCommerce Sites in 2025
- URL: https://levamo.com/blog/speed-up-woocommerce/
- Category: ecommerce
- Author: Tom Cheddadi
- Published: 2024-05-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Boost your WooCommerce store's speed! Get 10 optimization tips for 2025.
“Move fast. Speed is one of your main advantages over large competitors,” recommends Sam Altman, the CEO of OpenAI, an executive who knows a thing or two about facing strong competition.
This is great advice, especially for e-tailers who are trying to get their products noticed in a world filled with fierce competitors. Speed can be the differentiator between making or losing a sale.
Fast-loading websites ensure a smooth user experience, making it more likely the user sticks around, browses for what they are looking for, and then makes a purchase.
Now this brings the question, how to speed up WooCommerce sites, then?
Well, in this article, we will explore the answers to that question. We will show you how to speed up WooCommerce sites with 10 instant WooCommerce speed optimization techniques.
Let's get started!
## Why Speed Matters for Your WooCommerce Site
Speed is not just critical for e-commerce success; sometimes, it directly correlates to revenue. Studies have shown that even a slight delay in page load time can significantly impact a website’s conversion rates.
Fast-loading websites can enhance the user experience while slow-loading ones can frustrate potential buyers and send them to a competitor.
> According to [Webfx.com](https://www.webfx.com/blog/seo/site-speed-statistics), 83% of people expect websites to load in three seconds or less; 40% will leave if they don’t.
The king of search, Google, uses website speed as a ranking indicator for their SEO algorithm. Fast-loading sites usually rank higher in search results, which can lead to increased organic traffic, the preferred type of website traffic you want.
A fast-loading website also contributes to building brand loyalty. Consumers are more likely to return to a site that provides a good user experience, substantially increasing profits and overall business growth. According to [Queue-it](https://queue-it.com/blog/ecommerce-website-speed-statistics/), a tenth of a second improvement in a mobile site’s speed increases retail conversions by 8.4%. This can add up to thousands or even tens of thousands of dollars of additional sales per year.
Mobile has become an increasingly important sales channel and ensuring fast load times on mobile devices is crucial. Google rewards websites that prioritize mobile-first design and fast load times.
The advantages are obvious, but what can an e-tailer do to ensure his or her website is as fast as it can be? To ensure your WooCommerce site loads as fast as possible, follow the top ten fixes below.
## The Top 10 Instant Fixes to Speed up WooCommerce
### 1. Implement Lazy Loading & Optimize Your Images
**Lazy Loading**

/blog/wordpress-speed-optimization-plugins/
Lazy loading delays the loading of non-critical resources until they are needed on the site. Images are delayed until they are in the user's viewport, which can significantly reduce the initial page load time, particularly with image-rich pages. Lazy loading can be executed using the “loading” attribute on images and iframes, which allows authors to control when the browser starts loading resources.
Lazy loading can also be used for related data in databases. By enabling lazy loading, your website can load related data as needed rather than immediately. This reduces the initial data load, improving performance and reducing bounce rates. As an added bonus, it helps with SEO.
**Image Optimization**

While high-quality images are essential in user engagement and effectively conveying product information, incorporating them without considering their impact on a website’s performance can hinder the user experience and hurt SEO. Large image files can significantly slow a website's loading time, frustrating visitors and high bounce rates.
A picture might be worth a thousand words, but not when it comes to your website if the image load takes too long. Images load significantly slower than words do, but images can be instrumental in making a sale. While the human brain might process images 6 to 600 times faster than text, computers don’t work that way. Images take much longer to load because they contain so much more data and information than text descriptions.
That is why image optimization is vital for websites as it considerably improves page download speeds. Optimized images can reduce file sizes without compromising visual quality, resulting in faster page load times and smoother browsing experiences.
Website owners need to strike a balance between visual appeal and optimized page loading. Optimized images are easier for search engines to find and index, and this will give a website a clear advantage in search engine rankings. It can also lead to improved loading speeds and better website visibility, which should result in better SEO performance.
Optimizing images for different devices is also essential in today's digital landscape. Delivering appropriately sized visuals that match the screen resolution of a buyer’s device will enhance the user experience across a multitude of mobile platforms. This also prevents unnecessary data transfers while ensuring the correct display of images.
### 2. Leverage Browser Caching
Caching refers to storing frequently accessed data in a temporary storage location, allowing for faster access and lower retrieval times. Web browsers store certain files locally in the user's cache to reduce the need for repeated downloads, which improves load times for frequently visited websites. Caching can significantly enhance a website's performance and scalability by reducing latency, network traffic, and server load. Proper caching is essential for websites because it improves their speed and efficiency and enhances the user experience.
**LiteSpeed Cache**
[](https://wordpress.org/plugins/litespeed-cache/)LiteSpeed Cache Plugin in the WordPress Repository
If you use [LiteSpeed Cache](https://wordpress.org/plugins/litespeed-cache/) for WordPress and your host uses LiteSpeed WebServers, that’s great news: It works beautifully to speed up WooCommerce websites. LSCache has built-in logic that handles everything WooCommerce determines to be cacheable. If WooCommerce recognizes something as cacheable, LSCache will cache it.
**Automated Cache Purging**
If WooCommerce manages your stock, product pages will be purged from the cache whenever stock changes occur. Additionally, with WooCommerce’s “**smart purge**” technology, the related category and tag pages will also be removed when a product page is purged from the cache. This keeps your site’s product information consistently updated, reducing the need for constant manual changes when products are purged.
This is one of LiteSpeed’s big advantages. Other plugins struggle with this type of purge because they don’t have a cache tagging system like LiteSpeed’s. If you host with Levamo, smart purge technology is built in. Our hosting service can be found [here](/).
Levamo’s LScache integration automatically refreshes your content across all platforms whenever a product's details are updated, ensuring your site always displays the latest product information. WooCommerce shop cache keeps everything as fresh as possible.
Your customers will always see the most up-to-date product and category information, which should reduce customers trying to buy out-of-stock products.
### 3. Use a Lightweight WooCommerce Theme
A lightweight WooCommerce theme can significantly speed up your WooCommerce website's loading speed, but it is important to consider factors such as compatibility with your content, your unique website goals, your performance optimization features, and the ease of content customization. A lightweight theme will provide a better user experience as well as enhance your website's SEO performance.
**Storefront**
[](https://wordpress.org/themes/storefront/)Storefront Theme on the WordPress Repo
One popular lightweight WooCommerce theme choice is [Storefront](https://wordpress.org/themes/storefront/) by Automattic. It is lightweight, fast-loading, and has a minimal design built and maintained by the team responsible for WooCommerce. It provides an uncluttered user experience and has a library of child themes for quickly transforming a store’s look.
**Astra**
[](https://wpastra.com/)Astra Theme Website
Another lightweight and fast-loading design option is the [Astra theme](/blog/astra-wordpress-theme-review/) by Brainstorm Force. It has over 5,000 five-star ratings on the [WordPress repository](https://wordpress.org/themes/astra/), making it a popular choice among WooCommerce customers. The theme is highly customizable and offers several starter sites that can be edited with Elementor.
**Neve Theme**
[](https://wordpress.org/themes/neve/)Neve Theme on the WordPress Repo
The [Neve theme](https://themeisle.com/themes/neve/) is another lightweight and fast-loading WooCommerce theme that provides several built-in features to improve the shopping experience. It has a distraction-free checkout, built-in code minification for improved performance, and conversion optimization features like trust badges and microcopy.
**Evaluating WooCommerce Themes**
Every e-commerce store is unique, though, so you should evaluate a potential WooCommerce theme for performance before purchase. Website speed-testing tools like Google PageSpeed Insights, Pingdom, GTMetrix, and WebPageTest can be used to test the theme’s speed. These tools don’t just measure the theme's speed; they also provide recommendations for improving it.
- Lightweight Themes
Neve Theme on the WordPress Repll worth stating - lightweight themes with a well-structured codebase will load faster than a heavy theme with a poorly structured one. Look for themes that are optimized for speed, with minimal HTTP requests and small file sizes.
As mentioned above, some themes have built-in performance features, like lazy loading, image optimization, and minification. These features can help improve your website's speed and reduce its load time.
- Mobile Support
Responsiveness is also important. Themes that adjust to different screen sizes and devices will improve the user experience and reduce load time. Themes optimized for mobile devices will have a high mobile responsiveness score, which will also positively affect SEO.
- Customer Support
Even with the most robust and error-free themes, there will probably come a time when you need support. Good WooCommerce themes should have a responsive and helpful support team and regularly scheduled updates for bug fixes and security patches. Cyber-attacks are becoming increasingly common, and security vulnerabilities are growing, so you should look for themes that get frequent updates and have a solid security history.
### 4. Minimize JavaScript and CSS Files
Minifying JavaScript and CSS files is an important best practice for improving a website’s performance. Minification involves removing unnecessary characters, such as whitespace and comments, from code to reduce its size, which, in turn, will improve load times.
There are several tools available for minifying JavaScript and CSS files, such as [LiteSpeed Cache](https://wordpress.org/plugins/litespeed-cache/), [WP-Optimize](https://wordpress.org/plugins/wp-optimize/), [W3 Total Cache](https://wordpress.org/plugins/w3-total-cache/), and more. Choosing a reputable tool and following its documentation for proper usage is important. And if you’re already using LiteSpeed Cache, there's no need to add more plugins; keep it simple and use their minify feature. Additionally, it is crucial to minify files in the correct order to maintain dependencies between files and to thoroughly test a website's functionality across different browsers and devices after minification.
Minifying HTML, CSS, and JavaScript files can lead to faster loading times, improved SEO rankings, network bandwidth savings, and an enhanced user experience. However, following standard best practices is imperative; create backups of original files and regularly update minified files as the codebase changes. Monitoring and measuring the impact of minification on website performance is also essential to ensure optimal performance.
### 5. Database Optimization
As with all IT systems, databases should be regularly optimized for performance. Plugins like WP-Optimize can automate the database cleaning and optimization process. Removing unnecessary data, such as old revisions, expired transients, and other digital clutter, will improve query performance and speed up WooCommerce. Database tables should also be optimized to improve query performance. This can be done manually from phpMyAdmin or with a plugin like [WP-Optimize](https://wordpress.org/plugins/wp-optimize/).
**Caching Plugins**
Caching plugins like the free [Redis Object Cache](https://wordpress.org/plugins/redis-cache/) or [Object Cache Pro](https://objectcache.pro/) can significantly reduce the load on the WordPress database. If you’re hosting with Levamo, you’ll get free access to [Object Cache Pro](https://objectcache.pro/) with your [Levamo dynamic plan](/pricing/). The Pro version performs around twice as fast and normally costs $95/month.
Object Cache Pro website screenshot.
**Backups**
Database backups should be scheduled regularly to protect data and prevent it from being lost in a crash. The database’s size should also be monitored regularly to prevent it from becoming too large and unwieldy. If you’re hosting with Levamo, we provide a Backups feature that takes care of handling backups automatically.
**Avoid Too Many Plugins**
Although plugins can be powerful assets, you can have too much of a good thing. An overabundance of them can lead to performance issues. Each plugin added to a site introduces additional code and functionality, which can increase server load and HTTP requests during page loading. So try to use plugins that combine multiple related features whenever possible.
**PHP Version & Caching**
Keep your PHP current. PHP is the main programming language of WooCommerce and WordPress and using the latest version of PHP can help improve a website’s performance as well as keep the site as secure as possible.
You can also cache your PHP using Redis and a Redis client like phpRedis, Predis, or RELAY. RELAY is the premium option here and can be as much as 20 times faster than other Redis clients. While [RELAY](https://relay.so/) starts at $147/month, if you’re hosting with Levamo, you’ll get free access to it with your [Levamo dynamic plan](/pricing/). If you’re using a different host, check with their support if they can enable Redis for you and find out which Redis client they use.
The website’s performance should be monitored regularly with tools like Google PageSpeed Insights, GTmetrix, and Pingdom. These can help identify bottlenecks before they become problematic and point out areas to improve.
### 6. Use a Content Delivery Network (CDN)
A Content Delivery Network (CDN) is a network of geographically distributed servers that work in concert to deliver web content, such as webpages, images, videos, and other media, to users more quickly and efficiently. CDNs store cached copies of content in data centers around the world, allowing users to access internet content from a physically closer server.
By reducing the distance that data and content need to travel, CDNs help decrease latency, improve user experiences, and reduce the stress on origin servers by distributing the load geographically across multiple servers.
CDNs play a crucial role in improving website performance, delivering online content, and enhancing user experiences by speeding up WooCommerce loading times, reducing bandwidth consumption, and providing better responses to traffic spikes.
If you’re hosting with Levamo, a [free WordPress CDN](/cloudflare-cdn/) (Levamo CDN) is included for free in your plan.
### 7. Optimize Product Pages
- **Product Page Design**: Keep your design simple. A cluttered product page can impact loading times and distract from the main conversion goal.
- **Use Efficient Widgets**: If you're using widgets on your product pages, ensure they are optimized for performance. Some widgets can make a lot of unnecessary requests or load extra files that can slow down your page.
- **Optimize for Mobile**: Ensure your product pages are responsive and optimized for mobile devices. Mobile users often have less bandwidth, making speed optimization even more critical.
### 8. Enable ElasticSearch
Elasticsearch can greatly speed up WooCommerce sites, especially when it comes to managing search queries and retrieving product information. Here's how it works;
**Speedier Search Results**
Elasticsearch is built for lightning search capabilities. It organizes your WooCommerce product data to enable retrieval and display of search results with sizable product collections.
**Enhanced Search Precision**
Elasticsearch search results are typically more relevant than the default WooCommerce search function. It employs algorithms to comprehend and rank the suitable results, making it easier for customers to find what they're looking for quickly.
**Scalability**
Elasticsearch efficiently handles scaling operations. As your WooCommerce store expands, Elasticsearch can effectively manage increasing data volumes without compromising on performance, ensuring that search functionality remains speedy and dependable.
**Handling Complex Queries**
Elasticsearch can manage search queries, including matching, synonyms, and partial matches, without a notable impact on performance. This feature is particularly beneficial for stores with inventories and product ranges.
**Reduced Database Load**
By delegating the search process to Elasticsearch, you lessen the burden on your WooCommerce database. The database no longer needs to execute SQL queries, for searches, which can be demanding on resources - during periods of high user traffic.
**Auto-Complete & Instant Search**
Elasticsearch supports autocomplete and instant search, which suggests searches as they are being typed, leading to faster product findings and more intuitive presentation.
**Handling Traffic Spikes**
When sales or promotion events happen and the traffic suddenly increases, Elasticsearch can handle it without any problem. As a result, search functionality does not become slow but rather a bottleneck.
By leveraging Elasticsearch with WooCommerce, you can totally enhance your customer shopping experience and increase your sales by improving search performance precision.
If you’re hosting with us at Levamo, we provide Elastic Search with [ElasticPress](https://wordpress.org/plugins/elasticpress/) and Levamo’s search hosting. Alternatively, if you’re hosting elsewhere and your host doesn’t support Elastic Search, then you can use [ElasticPress’s search hosting](https://www.elasticpress.io/plans-pricing/), although it can get quite costly.
[](https://wordpress.org/plugins/elasticpress/)ElasticPress plugin in the WordPress Repo
### 9. Enable WooCommerce Hosting Solutions
Web hosting significantly impacts website speed, which in turn affects the user experience, SEO, and conversion rates. Choosing the [fastest WordPress hosting](/blog/fastest-wordpress-hosting/) service is crucial for ensuring optimal website performance.
Cloud hosting, in particular, offers several benefits for website performance. It uses virtual servers rather than physical servers, allowing for resource allocation based on real-time activity. This flexibility results in faster load times and improved performance, even during spikes in traffic. Cloud hosting can provide data security through multiple remote data storage locations and fast backups, ensuring quick recovery in case of a website crash.
A well-optimized web hosting service can ensure that websites load quickly, provide consistent uptime, and be accessible 24/7. Security is always crucial, and good hosting services provide robust security features, such as DDoS protection, regular security updates, and SSL certificates, protecting websites from potential threats.
In addition to these factors, the choice of web hosting can also impact SEO. Cloud hosting, for example, can boost website speed and performance, ensuring greater reliability, uptime, and security, all of which enhance website SEO.
The advantages of cloud hosting are many and measuring a cloud host's performance can be done by using tools like:
**WordPress Performance Tester plugin**
Your WordPress website’s performance can be measured using the WordPress Performance Tester plugin. It has a number of tests that are designed to assess the speed and efficiency of your WordPress environment, some of which include checking server response times and database operations so as to identify areas where performance can be enhanced.
**WordPress Hosting Benchmark Tool**
This plugin enables you to gauge how well your [fully managed WordPress hosting](/managed-wordpress-hosting/) environment is performing. By performing several tests, it measures the response time and capacity of your server, thereby giving an idea about how well your hosting handles tasks specific to WordPress.
**Grafana K6**
Use Grafana K6 to load test your site by simulating traffic characteristics from real-world situations and behaviors of particular users. However, you will need a developer to assist you in creating JavaScript-based test scripts that mimic actual user experiences on websites. Following their development, we conduct load tests that simulate hundreds or thousands of users undertaking the same task simultaneously on your website. This will help us identify performance bottlenecks, peak user loads and whether the website can withstand traffic spikes or not.
**Explore Further**
- For more in-depth information on WooCommerce Performance Optimization, download our free eBook: [Crazy Fast WooCommerce Sites](https://drive.google.com/file/d/1T08uHOUPmEGQcJD3nspNw502d66rXPa0/view).
- Download our [2024 Dynamic Managed Hosting for WordPress Industry Report](https://drive.google.com/file/d/1qKnXt9OK7uT1fdEqqsEZlNtixZWvfyNR/view?usp=drive_link) to compare various hosts' performance.
### 10. Regularly Monitor Your Site’s Speed
It is important to regularly monitor your WooCommerce site’s speed because it directly impacts your users’ experience. Slow page loads can lead to frustration, high bounce rates as well as lower engagement and a decrease in conversion rates. On the other hand, fast-loading websites can enhance user satisfaction and lead to increased customer engagement and higher conversion rates. Therefore, website owners should prioritize optimizing their website speed to provide a positive user experience.
Website speed is a critical factor in SEO. Search engines consider website speed one of the top-ranking factors in their algorithms. Faster-loading websites are more likely to rank higher on search engine results pages (SERPs), which can lead to increased website visibility and more organic traffic. To improve website speed, website owners should optimize their images and videos, reduce server requests, and use a content delivery network (CDN), as mentioned above.
By regularly monitoring website speed, website owners can identify any issues that may arise and take prompt action to address them, ensuring that their website remains fast, efficient, and user-friendly.
Tools like Google PageSpeed Insights, GTmetrix, Pingdom, WebPageTest, and Datadog can monitor website performance from different devices and browsers. They also offer actionable insights and tips for improving website performance, such as compressing images, reducing unused JavaScript, and optimizing server response times. These tools help speed up WooCommerce sites and correct while providing alerts when performance issues arise.
## Conclusion: The Need for Speed
According to [Queue-it](https://queue-it.com/blog/ecommerce-website-speed-statistics/), a tenth of a second improvement in mobile site speed increases retail conversions by 8.4%. Speed is an incredibly important factor for eCommerce sites, impacting user experience, conversion rates, brand loyalty, and search engine rankings. Optimizing website speed is essential for eCommerce businesses to remain competitive and achieve their sales goals. Speed matters. Speed is revenue.
[WordPress Speed Optimization](/blog/wordpress-speed-optimization/) techniques like lazy loading, leveraging browser caching, using a lightweight WooCommerce theme, minimizing JavaScript and CSS files, optimizing your database, implementing a content delivery network, optimizing your product pages, enabling ElasticSearch, adding a [managed WooCommerce hosting](/managed-woocommerce-hosting/) solution, and regularly monitoring your site’s speed will go a long way to optimizing the user experience so you can, realistically, expect a rise in sales.
Of course, there are surely other ways to speed up WooCommerce websites, but these will be a great start. By following the steps above, you should be able to create a fast and well-optimized website that will motivate your customers to purchase rather than drive them away in frustration. The renowned social psychologist David W. Johnson once said, “There are no speed limits on the road to success.”
So, what are you waiting for? It’s time to join the race.
## Frequently Asked Questions

### Why is my WooCommerce so slow?
WooCommerce is slow because of big themes, too many plugins, images that are not optimized or poor hosting. Hostile server response time and database bloat can also affect performance.
### Can WooCommerce be fast?
WooCommerce is fast if optimized properly and hosted correctly. Lean setups combining caching, CDN and performance-focused themes can achieve lightning-fast loads.
### How do I speed up my WooCommerce site?
Optimize images, use a fast theme, enable caching & reduce plugin bloat for performance gains. Upgrades to high-performance hosting and content delivery network (CDN) can also dramatically improve speed.
### What is the best speed plugin for WooCommerce?
WP Rocket, LiteSpeed Cache, and FlyingPress are popular speed plugins for WooCommerce stores. They improve caching, script loading, and database cleanup.
### Best hosting for fast WooCommerce website
Dedicated [managed hosting for WooCommerce](/managed-wordpress-hosting/) from Levamo is fast and scalable. Choose a hosting with SSD storage, caching built-in, and server-level optimizations.
---
## 13 Best WordPress Security Plugins to Safeguard Your Site In 2025
- URL: https://levamo.com/blog/best-wordpress-security-plugins/
- Category: website-security
- Author: Sunyyan Junaid
- Published: 2024-05-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Lock down your site! See 2025's top WordPress security plugins now.

Finding the best WordPress security plugins to safeguard your websites is a great way to ensure your online business stays safe. And while your choice of [web hosting is the first line of defense](/managed-security/), a good security plugin further enhances and provides extra layers of security every WordPress website should have.
With over *90,000 hacking attempts* occurring on WordPress websites per minute, it only makes sense to use the best WordPress security plugins to add more safety walls against those hackers. If you don't, you're simply letting hackers steal your data and majorly impact your business by tanking your SEO rankings. As a business owner, such malware or hacking attempts can mean huge losses, and no one wants that.
But there are many WordPress security plugins out there, and each seems to have some advantage or disadvantage, making it difficult to choose the right one.
Hence, we've compiled a list of the best security plugins for WordPress for you to keep your WordPress secure and safe from any threats.
And while we're diving straight into the list of our top 11 plugins to keep your WordPress secure, we're also going to touch on what makes a good security plugin and what drives our choice. You can skip to that part if you want conviction on this list, but for now, let's dive into what you came for.
## Our Pick of the Top 13 WordPress Security Plugins
## 1. Wordfence

[Wordfence](https://www.wordfence.com/products/pricing/) is one of the most popular WordPress security plugins that provides safety scanning and a firewall. It helps lock down your websites and provides a wide array of features to help identify and block malicious traffic. First, it provides real-time firewall protection and IP blocking.
This top WordPress security plugin protects websites at the endpoint and integrates excellently with WordPress. It also provides a site scanner and login defense, which includes CAPTCHA and two-factor authentication. It is often regarded as arguably the best security plugin for WordPress.
**Top Features:**
- Firewall with both endpoint (plugin-based) and cloud-based rules
- Malware scanner that compares core files, themes, and plugins against WordPress.org repository versions
- Live traffic monitoring for real-time threat detection
- Login security (limit login attempts, 2FA available in premium)
- Country blocking (premium feature)
**User Comments:** “One of the most comprehensive solutions. Just works." However, some users mention heavier resource usage on smaller hosting plans.
**Rating**: 4.8/5 stars
**Active Installs**: 4+ million
**Pricing**: Free version available; premium plans start around $119/year for a single site (discounts often apply for multiple sites).
## 2. Malcare

[Malcare](https://www.malcare.com/pricing/) is easily one of the most reputable security plugins for WordPress websites' security. Ideal for high-performance websites, it gives you automatic malware scans, on-click malware removal, and other essential security features to keep your mind at peace.
**Top Features:**
- Ability to manage multiple sites from one dashboard
- One-click malware removal for effortless cleanup
- Cloud-based scanning that doesn’t burden your server resources
- Real-time threat detection and automatic scanning
- Integrated backup solution (in premium tiers)
**User Comments**: “Their cloud-based scanning is a performance win.”
**Rating**: 4.4/5 stars
**Active Installs**: 100k+
**Pricing**: Free version for basic scans; premium starts around $99/year (includes malware removal)
## 3. Jetpack

[Jetpack](https://jetpack.com/features/security/) offers growth, performance, and safety tools for these websites. This feature of this plugin is relatively easy to use, provides comprehensive site protection, and provides real-time backups. The tool offers common spam protection, malware scanning, and a web application firewall.
It is one of the popular security plugin options for securing your websites. Jetpack helps you create better content while offering high-level defense and related features. It offers 24/7 support for as low as $9.95 per month.
**Top Features:**
- Automated daily backups and one-click restore (premium)
- Malware scanning and brute force attack protection
- Downtime monitoring alerts
- Spam filtering for comments (premium with Akismet integration)
- Performance enhancements (CDN for images and static files)
**Community Insight**: "Well-maintained by Automattic with frequent updates"
**Rating**: 4.3/5 stars
**Active Installs**: 5+ million
**Pricing**: Free core plugin; security plans start around $10/month
## 4. Monarx

Although [Monarx](https://www.monarx.com/) is not technically a website security Plugin, it is worth mentioning due to its related nature. It is an effective defense solution for Linux web hosting in 2025. This tool detects and prevents malicious activity at the server level, helping to ensure its safety.
The expert tool offers advanced cleaning, first involving priority and advanced threat analysis. This involves identifying and removing threats from your website. Then, it provides notifications and reports regarding the problem.
**Top Features:**
- **Continuous Updates**: Monarx continuously updates its detection rules to keep pace with new threats.
- **Server-Level Threat Detection**: Uses behavioral and AI-based analysis to spot malicious code before it can run.
- **Automatic Malware Blocking**: Intercepts and quarantines attacks in real time, often without manual cleanup needed.
- **Lightweight for End Users**: Because it runs on the server level, it doesn’t rely on your WordPress site’s resources.
- **Host Integration**: Typically integrated with cPanel, Plesk, or other hosting control panels, offering global protection for multiple sites.
**Rating**: Not applicable (no official WP.org listing)
**Active Installs**: Not applicable for the same reason above
**Pricing**: Geared toward hosting companies (e.g., [Monarx security comes free with Levamo](/managed-security/) hosting) and agencies. Pricing details aren’t publicly listed on a monthly “per-site” basis in the same way as typical security plugins.
## 5. Shield Security

[Shield Security](https://getshieldsecurity.com/features/) offers expert bot protection for websites in 2025. It is one of the best WordPress security plugins for tackling bots. Since bots account for many of the common safety issues on these websites, this plugin tackles them. It helps to lock down your sites and protect them from attacks, injections, malware, and vulnerability exploitation.
**Top Features**:
- Firewall and brute force protection
- Two-factor authentication and IP auto-blocking
- Automatic bot detection
- Audit trails for admin and user actions
- Advanced scanning for file changes
**User Comments**: “A lighter-weight alternative to Wordfence.”
**Rating**: 4.8/5 stars
**Active Installs**: 50k+
**Pricing**: Free version; paid plans start around $24/month, scales with features
## 6. Sucuri Security

[Sucuri Security plugin](https://sucuri.net/website-security-platform/) is another expert defense suite for websites in 2025. It offers a wide array of features that scan for malware on your website, removing it on time. While it helps to lock down your site, this tool also cleans hacked sites.
**Top Features:**
- Integrates with Sucuri’s CDN for performance and extra security (premium)
- Website application firewall (premium)
- Malware scanner that checks files and notifies you of potential threats
- Security activity auditing, including file integrity monitoring
- Post-hack security actions for quick cleanup and recovery
**User Comments**: “Their free malware scanning is a lifesaver.”
**Rating**: 4.4/5 stars
**Active Installs**: 800k+
**Pricing**: Free malware and security checker; premium starts around $229.99/year (includes advanced firewall and CDN)
## 7. Patchstack

[Patchstack](https://patchstack.com/wordpress-security/) is one of the best WordPress security plugins that lets you identify vulnerabilities and weak points within a website's plugin choices and related themes. Also, it picks out vulnerabilities in the WordPress core, helping to lock down your website.
This tool is powered by one of the most active communities of ethical hackers. It has three versions: the community, developer, and business versions. Fortunately, these allow users to stay ahead of safety issues, receive alerts, and prevent costly clean-up measures.
**Top Features:**
- **Virtual Patching / Firewall**: Blocks known vulnerability exploits in themes and plugins even before you update them.
- **Vulnerability Database**: Patchstack actively monitors and discloses plugin and theme vulnerabilities so you can see if your site is exposed.
- **Security Monitoring and Alerts**: Real-time alerts when vulnerabilities or attacks are detected.
- **File Integrity and Malware Scanning**: Flags suspicious changes in your WordPress file structure.
- **Multi-Site and Agency Tools**: The higher tiers provide dashboards that let you manage multiple sites’ security in one place.
**Rating**: 4.7/5 stars (approx.)
**Active Installs**: 10k+ (approx.)
**Pricing**: Free version on WordPress.org with basic security scanning. Pro and Business plans start around $8–$12/month per site (billed annually), with higher-tier packages for agencies and enterprises.
## 8. Defender Security

[Defender Security](https://wpmudev.com/project/wp-defender/), from WPMU DEV, offers a comprehensive suite of tools to harden your WordPress website's defenses. It simplifies security management with a clean, modern, user-friendly interface.
Automated scanning can easily detect any vulnerabilities, including malware and viruses. Defender focuses on proactive measures, addressing potential vulnerabilities before they can be exploited. The plugin does not offer any cleanups.
**Top Features:**
- Security scanning for core files, plugins, and themes.
- IP lockout and login masking to prevent brute-force attacks.
- Security recommendations and vulnerability patching.
- Security logging and audit trails.
- File change detection.
- Geoblocking and bot protection.
- Web application firewall scanning for proactive security.
**Rating**: 4.8/5 stars
**Active Installs**: 90,000+
Pricing: Free version available; premium plans are part of WPMU DEV membership ($49/month, includes access to all their plugins). For Defender Pro, plans start at $36 per year for a single-site license.
## 9. All In One Security (AIOS)

Talking about security plugins and not mentioning [All In One Security (AIOS)](https://wordpress.org/plugins/all-in-one-wp-security-and-firewall/) would be an injustice. AIOS is an extremely popular plugin that provides a free and robust security plugin that packs a punch.
The plugin offers a wide range of security features, categorized for ease of use. AIOS focuses on a strong security foundation, with options to fine-tune settings to your specific needs. It does not offer malware scanning and cleanup options, and sometimes the plugin can also interfere with indexing.
**Top Features:**
- Blacklisting functionality.
- Firewall functionality.
- Brute-force login protection.
- Database security.
- File system security.
- User account security.
**Rating**: 4.7/5 stars
**Active Installs:** 1+ million
**Pricing**: Free. Premium plans start at $70 per annum for a single-site license.
## 10. Astra Security Suite

[Astra Security Suite](https://www.getastra.com/) is a comprehensive web security solution that goes beyond basic plugin functionality. The primary focus of this plugin is to provide a range of pentesting and vulnerability management solutions for websites, APIs, and the cloud.
It provides a cloud-based firewall, malware scanning, and ongoing security audits. Astra security is designed to protect your website proactively from a wide range of threats. One of the main features that WP users buy is due to the extensive firewall protection, something that not every security plugin offers. But its hefty price tag does not justify its usage for normal WP websites.
**Top Features:**
- Cloud-based firewall protection.
- Malware scanning and removal.
- Real-time IP blocking.
- Security audits and vulnerability assessments.
- 24/7 security monitoring.
- Bot protection.
**Rating**: 4.0/5 stars
**Active installs**: 1,000
**Pricing**: Starts at $69/month, no free plan.
## 11. Bulletproof Security

[Bulletproof Security](https://wordpress.org/plugins/bulletproof-security/) is a plugin focused on a set of powerful security measures, particularly file and database protection. It offers a comprehensive set of tools to harden your WordPress site against various threats. The interface is designed for advanced users, which may not prove to be the best option for amateurs.
According to its official plugin page at WordPress.org, the plugin fixes more than 100 known issues with other plugins. It also offers some of the best security features at an extremely low one-time cost, making it more cost-effective than other plugins.
**Top Features:**
- .htaccess security.
- Database security.
- Login security.
- File system security.
- Malware scanning.
- Security logging.
**Rating**: 4.8/5 stars
**Active installs**: 60,000+, inclusive of free and premium purchases
**Pricing**: Free version available; premium version is a one-time purchase of $69.95.
## 12. CleanTalk Security
[CleanTalk Security](https://cleantalk.org/) focuses on preventing spam and malicious activity, with a strong emphasis on real-time protection. While other plugins offer multiple types of protection, its specialty and focus on spam make it a great choice for WP website owners looking to get rid of spam.
It leverages a cloud-based service to block spam registrations, comments, and other threats.
**Top Features:**
- Spam protection for registrations, comments, and forms.
- Real-time IP blocking.
- Security firewall.
- Malware scanning.
- Traffic control.
**Rating:** 4.8/5 stars
**Active installs:** 200,000+
**Pricing:** There is no free option available. Starts at $12/year for a single site license.
## 13. **Security Ninja**
[Security Ninja](https://wpsecurityninja.com/) is one of the best WordPress security plugins that takes a proactive approach to safeguarding your website. It doesn't just block threats; it systematically tests your site for vulnerabilities, providing you with detailed reports and actionable insights.
It also comes with a malware scanner, which is identical to Wordfence’s own system. This makes Security Ninja a highly reliable plugin. However, unless the database is updated with new malware types, any new malware affecting your website may not be detected.
**Top Features:**
- Security tests for various aspects of your WordPress site.
- Malware scanning.
- Core code checks.
- Brute-force test.
- Database security test.
**Rating:** 4.8/5 stars
**Active installs:** 10,000+
**Pricing:** Free version available; premium plans start at $8.99/year for a single-site license.
## Why Choose the Right Security Plugin for Your WordPress
### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
To ensure your website’s safety, you must choose the best security plugin for WordPress. First, determine what you need and what you’re looking for in a security plugin. Then, choose one that integrates well with your hosting provider.
Also, consider options that offer effective protection and ease of usage. There are several advantages to choosing the appropriate plugin for your site. Here is why this topic is important:
### Best WordPress Security Plugins Provide Regular Updates
The internet is ever-changing. As a result, there are new threats to your website almost daily. So, when choosing a plugin to lock down your site, go for an actively maintained one.
These expert tools provide helpful updates that keep your website safe from the latest threats. The entire reason for installing these defense platforms is to keep your site safe. Therefore, they should be able to protect it against even newer dangers.
### They Will Be Compatible With Your Site
Compatibility is a significant issue when choosing the right plugin. So, you must make sure that your chosen plugin fits your WordPress version. It must also fit other installed resources on your site.
Problems with compatibility can affect your site’s functionality, also affecting its overall safety. To avoid this, consider testing reputable options that have good reviews on a staging site before buying a plan.
### Good Security Plugins Support Scalability
When choosing a plugin for your website, you must consider how it can scale. Then, pay attention to your website's growth potential before picking a plugin that can scale. This way, you can still protect your website as its traffic and content increase.
Plugins that do not scale your site create risks when traffic and content begin to grow. In these situations, they can crash easily, affecting your site’s safety in the future.
### They Offer Effective Redundancy Measures
Top security plugins provide effective redundancy measures to protect websites. Additionally, they provide multiple defense layers, triggering another if one fails. In these situations, the plugin can better maintain your site’s safety.
This feature does not reduce the safety of these top options. It is even more effective since new risks come out every day. Therefore, these extra features deal with new threats such as phishing attacks, hacks, etc.
### They Provide Alerts and Notifications
Fast and timely alerts can be a lifesaver in the case of a security issue. That is why the best websites provide variable alert and notification options. These allow you to keep up with potential issues and threats that may be present.
Fast notifications are usually helpful for real-time safety and related problems. While they notify you about live issues, these alerts also provide a definitive guide on fixing them and preventing further problems.
### You Can Get Extra Features Besides Security
As expected, these security plugins are meant to maintain your website’s safety. However, many modern ones offer more than that. They offer additional features that are pretty useful, although not precisely safety-related.
One important feature provided by these modern plugin choices is the backup feature. While dedicated backup options also exist, you can never have too many backups for your site. So, choosing an option with this additional feature is always a good idea.
### You’ll Enjoy Two-Factor Authentication (2FA)
The login page is one of the most vulnerable pages on websites. This problem is significant on sites where the default login link has not been changed. In this case, you may notice bots trying brute entries into your website using typical logins.
So, many effective ones usually add two-factor authentication (2FA) to secure website logins. Some also move the login page, changing the URL to prevent bot attacks. They ensure that people use verification codes to access the website.
### High Levels of Customization
Good security plugins for websites offer users multiple customization options. They allow users to set them up based on their needs. So, consider the more flexible options when looking for a customizable option to secure your website.
This way, you can better set up the available measures to fit your requirements. This feature is quite crucial since different websites have different safety requirements.
### An Excellent Cost-to-Benefit Ratio
When paying for a plugin to secure your website, the cost is an essential factor besides the benefits. As a result, you must compare the cost of the resource with its premium features. This will help you decide whether to go with one resource or not.
While many have free and premium versions, the free versions only provide essential protection. On the other hand, premium versions provide advanced features and enjoy priority customer support.
## How to Install and Setup Security Plugins on WordPress
Now that you know which are the best WordPress security plugins in 2025, it’s time to install one on your website. While relatively easy to do due to WordPress’s popularity, you may still need some help. It takes the same process to install all of them. So, here is a definitive guide on how to install and set up this resource:
- Log in to your WordPress dashboard.
- Move to the “Plugins” section.
- Click the “Add New”, button, then search the appropriate keywords to draw the options.
- Choose the appropriate plugin and hit the “Install Now” button next to it:
- After you’ve installed it, click the “Activate” button next to it.
- Set up the plugin settings to fit your preferences and requirements.
Besides installing and setting up these security plugins, it is also necessary to update them frequently. These updates usually carry newer features and address newer issues and vulnerabilities. Also, it should be configured to perform regular scans to ensure continued safety.
## Enhance Your WordPress Security Now
There you go, you now know the best WordPress security plugins. It's up to you now to choose the best one that matches your budget and workflow.
But security plugins are not the only thing you need to choose for a secure WordPress site. Since your website’s safety is of the utmost importance, you shouldn't overlook choosing the right defense tools, and of course, the most robust security starts with your choice of managed cloud hosting.
In order to keep your website secure from the server side, there's no alternative to having a secured [fully managed WordPress hosting](/managed-wordpress-hosting/). To equip your website with the most secure WordPress hosting today that empowers your security plugin, host your website on Levamo.
## Frequently Asked Questions

### Is WordPress good for security?
Yes, WordPress is secure at its core and is updated regularly for vulnerabilities. But its security depends largely on how well it’s maintained and the quality of themes and plugins used.
### How to make WordPress more secure?
Keep your core, themes, and plugins updated, use strong passwords, and enable two-factor authentication to improve WordPress security. A good security plugin and a firewall will also protect you.
### What is a security plugin in WordPress?
Security plugin blocks malware, blocks brute force attacks, and scans for vulnerabilities on your WordPress site. It’s a defense against common threats and for monitoring suspicious activity.
### What is the best security plugin for WordPress?
WordPress Security plugins to consider include Wordfence, Sucuri Security, and iThemes Security. Each has malware scanners, login protection, and firewalls.
### Do I really need a security plugin for WordPress?
Yes, especially if your site handles user data or gets a lot of traffic, security plugins provide defense against hacks and malware. While good practices help, plugins give automation and real-time protection that manual efforts miss.
### Is Wordfence the best security plugin?
Wordfence is one of the best WordPress security plugins, if not the best security plugin for WordPress. It is used by more than 4 million people, and that speaks for its usefulness.
### Is Wordfence a firewall?
Yes, Wordfence provides dedicated firewall protection for your WordPress site. However, it offers more than just a firewall, with security checking, activity log and [DDoS protection](/blog/preventing-ddos-attacks/), it is an all-round security plugin for WordPress.
### Is Sucuri free?
Yes, it is a freemium plugin, meaning that the highly popular Sucuri plugin for WordPress security is available for free, and you can also upgrade to premium for extra features.
---
## The 23 Best Freelance Websites Of 2025 To Boost Your Earnings
- URL: https://levamo.com/blog/best-freelance-websites/
- Category: online-business
- Author: Sunyyan Junaid
- Published: 2024-05-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find 23 top freelance sites for 2025 and boost your earnings now.
You’ve got the skills, the passion, and the drive. Now all you need is the right platform to connect with clients, score exciting projects, and kickstart your dream freelance career. That’s where the **top freelance websites** come in, giving you the perfect launchpad to make it happen.
The freelance economy is booming, and we've seen a surge of platforms where you can showcase your skills and land gigs that help you make good money. Now, nearly 9 out of every 20 workers are proudly self-employed. But here’s the catch: not all platforms make the cut. To succeed, you need to know which ones rank among the **best freelance websites**.
Thus, choosing the right freelancing platform can mean the difference between snagging high-paying projects that make you excited or endlessly scrolling through irrelevant jobs.
Hence, I've shortlisted the top 23 platforms of 2025 that will help your freelance career take off!
Rather watch a video?
[Watch the video on YouTube](https://www.youtube.com/watch?v=_dfpUVoJgJ4)
## Why Choose the Right Freelance Websites?
Freelance websites are like online storefronts. You want yours to attract the right kind of customers. Choosing platforms that match your skills and the type of work you love doing is key to a successful freelance experience. Here is why it matters:

### Attract Your Ideal Clients
Imagine being a [web developer](/blog/web-developer-portfolios-inspiration/) who is great at [building e-commerce stores](/managed-woocommerce-hosting/). You would not want to spend your time on a platform filled with clients looking for simple logo designs, right? Freelance websites specializing in your niche help you connect with clients who need those specific e-commerce skills.
Also, as a [freelance web developer](/blog/build-successful-wordpress-freelance-career/), you'd want to deliver the fastest websites to your clients once you find the right freelance platform and the right clients. For that, you need a robust [high traffic WordPress hosting](/blog/fastest-wordpress-hosting/) solution like [Levamo](/). Make sure to check it out and discover hyperspeed hosting that truly delivers on the performance promise.
But, let's not digress...
### Showcase Your Best Work
If you're a graphic designer, you want a platform that lets you showcase your stunning works, not just a boring text description. Therefore, freelance websites tailored to your discipline often have features for beautiful portfolio displays, helping your work truly shine.
### Get Paid What You Are Worth
Let's be real: freelancing is about making a living! Moreover, niche freelance websites tend to attract clients who understand the value of specialized skills and are willing to pay a fair price for your expertise. Did you know 60% of freelancers in the world earn more than they did in their past jobs? Thus, no more fighting for low-paying gigs against a massive pool of generalists.
Also, if you're an agency, you can always join Levamo's [Agency Partnership Program](/web-hosting-affiliate-program/) to earn even more through referral and recurring commissions.
### Less Competition, More Focus
Scrolling through hundreds of irrelevant jobs is a drag. Focusing on the right freelance websites means less noise and more opportunities that fit your skill set. Additionally, this frees up your time to land the good stuff!
### Enjoy the Work
Freelancing is great when you are doing what you love. Finding projects that genuinely excite you makes the whole experience way more fun and rewarding. The right freelance websites help you locate those hidden gems that make you eager to get started.
84% of all freelancers admit that their nature of work lets them live the kind of lifestyle they want. However, wading through endless job postings that are not a good fit is a major time-suck and can be super discouraging. Therefore, selecting the right freelance websites helps you focus your energy where it counts- landing good projects, building a thriving freelance business, and living how you have always wanted to.
## **Overview of the Freelance Landscape in 202**5

The way we work is changing, and freelancing is at the forefront of that shift. Besides, more businesses than ever are embracing the flexibility and access to specialized talent that freelancers offer. Technology is breaking down geographical barriers and opening up a global marketplace for freelancers to connect with clients from anywhere.
Next, we are seeing an explosion in demand for skills like web development, digital marketing, content creation, and [marketplace hosting](/managed-marketplace-hosting/), where freelancers help businesses build, manage, and scale their online stores or service platforms.
Besides, businesses are not just looking for someone to do the task; they want creative partners who understand how to engage audiences and drive results in an online world. It makes sense that a whopping 47% of the global workforce consists of freelancers.
This shift has exciting implications for freelancers. Specialization is becoming even more valuable. If you have a specialization, like social media strategy or UI/UX design, you are in a great position. The competition is out there, but honing your niche and showcasing your unique perspective can set you apart from the crowd.
In short, the freelance landscape in 2025 is dynamic and full of opportunities for those who are adaptable and eager to learn. Taking on these trends puts you ahead of the game as the digital sector continues to boom!
## **The 23 Best Freelance Websites of 202**5
Now let's get into the actual meat of the matter. If you're a freelancer looking for a gig platform to get a steady stream of income, the following top freelancing platforms are exactly where you should be looking.
### Freelance Websites for Developers
If you are a developer, these websites can help you land regular and well-paying gigs. Let’s look:
#### [1. Working Nomads](https://www.workingnomads.com/jobs)

[Working Nomads](https://www.workingnomads.com/jobs) curates remote job listings with a focus on digital nomads and location-independent professionals. It connects developers, designers, and other creatives with companies that consider remote work the norm. Moreover, this makes it a great resource for finding opportunities that prioritize flexibility and global collaboration.
**Specialty:** Remote work across various disciplines, with a strong presence of developer positions
**Pros:**
- Emphasis on location-independent jobs
- Community features and resources tailored to remote workers
- Potential to find exciting projects with companies that embrace a remote-first culture
**Cons:**
- May require more self-filtering compared to niche developer platforms
- Not ideal if you are strictly seeking local in-person opportunities
**Ideal Demographic:** Developers seeking fully remote work, especially those who value location independence and a strong remote-work community.
#### [2. Stack Overflow Jobs](https://stackoverflow.com/jobs/companies)

This one is a well-established job board connected to the massively popular [Stack Overflow](https://stackoverflow.com/jobs/companies) developer community. It features a mix of traditional listings alongside niche and unique project opportunities.
**Specialty:** Software development across various technologies and experience levels
**Pros:**
- Huge reach due to the active Stack Overflow community
- Potential to find niche projects alongside standard listings
- Free to use for job seekers
**Cons:**
- Can be competitive, especially for entry-level positions
- Job quality can vary depending on the company's posting
**Ideal Demographic:** Developers of all levels seeking a wide range of opportunities. Particularly recommended if you are active in the Stack Overflow community.
#### [3. GitHub Careers](https://www.github.careers/careers-home)

This is a job board directly integrated with the world’s largest developer community platform, [GitHub](https://www.github.careers/careers-home). While it features a range of tech-related roles, it stands out as a natural fit for software developers to showcase their open-source work and discover opportunities at top companies.
**Specialty:** Software development, with an emphasis on open-source technologies and projects
**Pros:**
- Ability to highlight open-source contributions directly on your profile
- Potential for finding companies actively seeking developers with specific open-source experience
- Access to a vast developer network
**Cons:**
- Might be less diverse in non-developer tech roles compared to broader job boards
- Emphasis on open-source work could be less relevant for those without that experience
**Ideal Demographic:** Software developers with a strong open-source portfolio or those seeking companies that understand and value those contributions.
#### [4. Gigster](https://gigster.com/)

[Gigster](https://gigster.com/) matches vetted developers with teams requiring experts on their team. Its focus is largely on collaboration and long-term engagements. Thus, if that is what you are looking for, this platform is for you.
**Specialty:** Full-stack development, mobile development, product management
**Pros:**
- First, opportunities to work on large-scale projects as part of a team
- Second, the potential for long-term or recurring work
- Finally, Gigster handles project management and client communication
**Cons:**
- Might not be ideal if you prefer short-term freelance gigs
- Requires a strong portfolio and experience working in a team setting
**Ideal Demographic:** Developers comfortable with collaborative environments and seeking ongoing project work.
#### [5. Hirable](https://hirable.fyi/)

[Hirable](https://hirable.fyi/) is a curated marketplace where companies proactively reach out to pre-vetted freelance developers. However, the unique selling point for Hirable is its insistence on quality over quantity. If you take pride in your work, consider this one.
**Specialty:** Software development with in-demand skills
**Pros:**
- First, less competition as clients initiate the contact
- Next, streamlined application and communication process
- Finally, a high potential for well-paying projects
**Cons:**
- Requires a strong track record to attract invitations
- Might not be the best fit for those who enjoy actively pitching
**Ideal Demographic:** Experienced developers with in-demand skill sets seeking a less self-promotional approach.
#### [6. Turing](https://www.turing.com/)

This platform matches elite software developers with remote opportunities at primarily US-based companies. Moreover, they use a rigorous vetting process, including algorithms and human evaluation, to ensure top-tier talent. Thus, developers accepted into [Turing’s](https://www.turing.com/) pool gain access to long-term, high-paying remote projects.
**Specialty:** Long-term, full-time equivalent remote software development roles
**Pros:**
- Potential for highly competitive pay and stable work
- Streamlined matching process for vetted developers
- Access to projects that might be difficult to get independently
**Cons:**
- Acceptance into the program is highly selective due to its rigorous standards
- Focus on long-term placements might not suit those seeking shorter gigs
**Ideal Demographic:** Experienced developers with proven skills, seeking stable, well-paid remote work with a greater possibility of full-time hours.
#### [7. Gun.io](http://gun.io/)

This is a premium freelance platform that focuses on matching developers with well-established companies and teams working on challenging projects. Therefore, if you have a proven track record of success in software development, [Gun.io](http://gun.io/) offers access to some of the best-paying freelance gigs.
**Specialty:** Software development across various specializations and experience levels, with a focus on mid-senior-level talent
**Pros:**
- High-quality projects from reputable companies
- Potential for long-term or ongoing placements
- Streamlined matching process and support from Gun.io
**Cons:**
- Highly selective due to its focus on elite talent
- Primarily for developers comfortable communicating in English
**Ideal Demographic:** Experienced software developers with a strong portfolio and track record, looking for challenging but high-paying freelance projects.
#### [8. LHH Recruitment Solutions](https://hired.com/join)

LHH Recruitment Solutions (formerly Hired) is a curated marketplace where companies proactively reach out to pre-approved tech talent, including software developers. Their unique model streamlines the hiring process and reduces the need for constant self-promotion. To succeed on [Hired](https://hired.com/join), a strong profile and sought-after expertise are key factors.
**Specialty:** High-demand tech roles, with an emphasis on software development.
**Pros:**
- Companies initiate contact, reducing the time spent on pitching
- Transparent salary information for many listings
- Potential for competitive offers from interested companies
**Cons:**
- Requires a strong profile to attract quality leads
- Might involve a waiting period before receiving invitations
**Ideal Demographic:** Developers with in-demand skills and a proven track record. Particularly well-suited to those who prefer a less self-promotional approach.
#### [9. CodementorX](https://www.codementor.io/)

This freelance platform connects software developers with project work, offers on-demand mentorship, and provides resources for professional development. Moreover, [CodementorX’s](https://www.codementor.io/) dual focus on project matching and mentorship makes it a great resource for developers of various experience levels.
**Specialty:** Software development projects, with a strong focus on mentorship opportunities
**Pros:**
- First, opportunity to both find project work and offer your expertise as a mentor
- Second, flexible working options, from short-term gigs to longer engagements
- Thir, built-in resources for learning and skill development
**Cons:**
- Competition can vary depending on your specific skill set
- May require more active portfolio building compared to curated platforms
**Ideal Demographic:** Developers looking for flexibility, both in the types of projects and the option to mentor. Benefits both those seeking freelance work and those wanting to share their knowledge.
### Freelance Websites for Designers
Are you an expert designer looking for freelance gigs? We have listed some of the top websites for you. Let us have a look:
#### [10. Toptal](https://www.toptal.com/)

Web design is statistically the most popular and in-demand freelance service. Toptal, as a premium platform, offers extensive opportunities in this flourishing field. Additionally, they have a strict qualifying process to keep track of the quality of their talent network. Besides, [Toptal](https://www.toptal.com/) prioritizes matching top-tier freelancers with challenging projects at reputable companies and offers access to high-paying opportunities.
**Specialty:** Various design disciplines- graphic design, UX/UI, web design, product design, and more
**Pros:**
- Potential for high-paying projects from established clients
- Access to long-term or ongoing placements for those seeking stability
- Toptal handles client communication and project management
**Cons:**
- Highly competitive due to its emphasis on top talent
- May not be ideal for entry-level designers still building their portfolios
**Ideal Demographic:** Experienced designers with strong portfolios and a proven track record, looking for challenging and well-compensated projects.
#### [11. Dribbble](https://dribbble.com/)

This multi-faceted freelance website functions as a portfolio showcase, a designer community hub, and a job board. [Dribbble](https://dribbble.com/) is known for attracting visually-driven clients and encouraging a collaborative environment with features like design feedback and networking opportunities.
**Specialty:** Primarily focused on visual design disciplines - graphic, UI/UX, web, illustration, and more
**Pros:**
- Great platform for showcasing your work to a design-savvy audience
- Active community for networking and receiving feedback
- Integrated job board for landing freelance gigs
**Cons:**
- Can be competitive due to its popularity
- Building a strong following and exposure takes time and effort
**Ideal Demographic:** Designers looking to showcase their visual work, build a network, and discover project opportunities through organic exposure.
#### [12. 99designs](https://99designs.com/)

This one is a contest-based platform where clients post design briefs and multiple designers compete by submitting concepts. Clients choose a winning design, and the winning designer is paid a predetermined fee. [99designs](https://99designs.com/) offers a way to gain experience and build a portfolio, especially for those new to freelance design.
**Specialty:** Primarily graphic design projects- logos, branding, web design elements, and more
**Pros:**
- To begin with, a wide range of project opportunities at various budget levels
- Next, a good starting point for new designers to build experience
- Finally, it can be a fun way to try out different design styles
**Cons:**
- Highly competitive, requiring frequent submissions to increase chances of winning
- Pricing can be less lucrative than direct client work
**Ideal Demographic:** New designers looking to build a portfolio and gain experience, or those comfortable with a competitive and fast-paced contest format.
#### [13. Behance](https://www.behance.net/)

Behance is a creative portfolio platform owned by Adobe, integrated with the Adobe Creative Cloud. Its primary focus is on showcasing visual work and building a professional network within the design community. [Behance](https://www.behance.net/) also features a built-in job board, making it a valuable resource for freelance designers to both display their best work and find potential projects.
**Specialty:** Wide array of design disciplines, with a strong focus on graphic design, illustration, web design, and UX/UI
**Pros:**
- Integration with Adobe Creative Cloud provides added visibility
- Great platform for attracting clients drawn to visually-driven portfolios
- Opportunities for networking and collaboration within the creative community
**Cons:**
- Building a significant following can take time and dedicated effort
- The job board can be competitive depending on your specialization
**Ideal Demographic:** Designers of all levels seeking a visually impactful platform to showcase their work, connect with other creatives, and find freelance opportunities
#### [14. Fiverr](https://www.fiverr.com/)

Fiverr is a large, gig-based marketplace with numerous freelance services, including design. It is one of the best Upwork alternatives (more on Upwork later) and is known for its wide range of price points and varying levels of project complexity. [Fiverr’s](https://www.fiverr.com/) structure prioritizes pre-packaged gigs with clear deliverables, making it a good option for specific design services or well-defined projects.
**Specialty:** Offers a broad range of design services, with graphic design being of particular interest
**Pros:**
- Potential to attract clients with diverse budget needs
- A streamlined system for offering and purchasing pre-defined design services
- Good starting point for new designers offering specific, deliverable-focused gigs
**Cons:**
- Can be highly competitive, especially in lower price brackets
- May be less suited for complex projects requiring extensive back-and-forth
**Ideal Demographic:** Designers offering clearly defined services (logo design, social media graphics, or more), especially those comfortable with competitive pricing.
#### [15. DesignHill](https://www.designhill.com/)

DesignHill is another contest-based platform similar to 99designs. Clients launch design competitions, designers submit entries, and the client chooses a winner. [DesignHill](https://www.designhill.com/) also offers one-on-one project opportunities, providing a mix of formats for landing freelance work within their marketplace.
**Specialty:** Primarily focuses on graphic design projects such as logos, branding, and such
**Pros:**
- First, provides the opportunity to participate in both contests and direct projects
- Next, it can be a way to gain experience and potentially build a client base
- Furthermore, offers varying budget levels for design contests
**Cons:**
- Contests involve speculative work, with no guarantee of payment
- Pricing for direct projects can still be competitive
**Ideal Demographic:** Designers comfortable with a contest-based model or those looking to expand into the one-on-one project side of their platform.
#### [16. Smashing Jobs](https://www.smashingmagazine.com/jobs/)

[Smashing Jobs](https://www.smashingmagazine.com/jobs/) is a job board offshoot of Smashing Magazine, a well-known publication within the web development and design community. Their job board attracts top design-focused companies and agencies. It is a great resource for finding quality listings with an emphasis on thoughtful design and user experience.
**Specialty:** Design roles with a strong focus on web design, UX, UI, and front-end development
**Pros:**
- Curated listings with an emphasis on design-conscious companies
- Less likely to find low-quality or irrelevant listings
- Potential to discover unique opportunities within the design community
**Cons:**
- Job listings may be more niche compared to larger, generalist platforms
- Can be competitive, especially for sought-after roles
**Ideal Demographic:** Designers focused on web and digital product design, seeking roles at companies that prioritize design excellence.
### Freelance Websites for Digital Creatives
We have a list of gig websites for digital creative freelancers. So, let’s get started!
#### [17. Upwork](https://www.upwork.com/)
[](http://upwork/)
[Upwork](https://www.upwork.com/) is one of the largest and most well-known marketplaces with 12 million freelancers. They help to connect businesses with gig seekers across multiple disciplines, including design, writing, editing, marketing, and more. Besides, it offers a mix of short-term and long-term project opportunities, making it a very versatile platform for freelancers of all levels.
**Specialty:** Wide range of digital creative services, including writing, editing, content creation, graphic design, and web design and development
**Pros:**
- A massive pool of potential clients and projects
- Features to accommodate both hourly and fixed-price work
- Caters to various experience levels, from beginners to seasoned professionals
**Cons:**
- Can be highly competitive, especially for lower-priced projects
- Finding the right clients may require careful filtering and proactive pitching
**Ideal Demographic:** Digital creatives with diverse skill sets, looking for a platform with a vast array of projects and the potential to build long-term client relationships.
#### [18. Guru](https://www.guru.com/)

[Guru](https://www.guru.com/) is another large freelance marketplace offering services in a variety of creative fields. Similar to Upwork, its breadth of categories makes it a potential fit for digital creatives with diverse expertise. Moreover, it features tools for managing projects, invoicing, and secure payments, streamlining the freelance workflow.
**Specialty:** Offers a broad range of digital creative categories, including content writing, editing, graphic design, and marketing services.
**Pros:**
- Firstly, a large selection of potential projects
- Next, there are safeguards in place for payments and work agreements
- Finally, it features different work arrangements (hourly, project-based, recurring, etc.)
**Cons:**
- Competition can be high, requiring strong profile building and active pitching
- Platform fees can influence earning potential
**Ideal Demographic:** Digital creatives open to a variety of project types, seeking a large marketplace with established payment and work management infrastructure.
#### [19. Freelancer.com](http://freelancer.com/)

[Freelancer.com](http://freelancer.com/) is the most popular freelancing website with upwards of [31 million users](https://www.websiteplanet.com/blog/freelance-stats/). As a top freelance website, it offers a vast array of projects across various disciplines. This makes it a potential option for digital creatives with diverse skill sets. Besides, its focus on affordability means it attracts clients with a range of budgets.
**Specialty:** Wide variety of digital creative services, including writing, editing, graphic design, video, and marketing.
**Pros:**
- Massive pool of potential clients and projects
- Option for both contest-style and direct client projects
- Can be a good starting point for new freelancers
**Cons:**
- High competition, especially in the lower price brackets
- Quality of jobs can vary significantly
**Ideal Demographic:** Digital creatives open to a competitive environment with a wide range of project types and budgets, or those hoping to gain some entry-level freelance experience.
#### [20. Flexjobs](https://www.flexjobs.com/lp/remote-jobs1?utm_source=google&utm_medium=sem&utm_campaign=19937444305&utm_term=flexjobs&network=g&device=c&adposition=&adgroupid=148245362856&placement=&adid=664704106764&gad_source=1&gclid=CjwKCAjw26KxBhBDEiwAu6KXt-Y7F3vGQcNkZWBIRFakwfND00dwumHk9F1ZmhVZO9Q2C5lim2ARuhoCzvMQAvD_BwE)
[](https://jooble.org/)
Flexjobs offers high-quality freelance, remote, and flexible work opportunities across multiple disciplines. Their listings go through a screening process to reduce the number of scams or low-paying gigs. Moreover, this emphasis on quality makes [Flexjobs](https://www.flexjobs.com/lp/remote-jobs1?utm_source=google&utm_medium=sem&utm_campaign=19937444305&utm_term=flexjobs&network=g&device=c&adposition=&adgroupid=148245362856&placement=&adid=664704106764&gad_source=1&gclid=CjwKCAjw26KxBhBDEiwAu6KXt-Y7F3vGQcNkZWBIRFakwfND00dwumHk9F1ZmhVZO9Q2C5lim2ARuhoCzvMQAvD_BwE) a valuable resource, especially for those seeking credible and professional clients.
**Specialty:** Various digital creative roles, including writing, editing, content marketing, social media, and some design positions.
**Pros:**
- Pre-vetted listings for quality and legitimacy
- Prioritizes remote and flexible work arrangements
- Resources and tools for freelancers on their platform
**Cons:**
- Requires a paid subscription to access their job board
- Might have slightly fewer listings compared to massive free marketplaces
**Ideal Demographic:** Digital creatives searching for a curated experience, with a focus on reliable clients and flexible work opportunities, and who are willing to invest in a paid platform
#### [21. ServiceScape](https://www.servicescape.com/)

This is a freelance platform focused on writing, translation, and editing projects. It works on a client-friendly process with features like curated matches and an emphasis on quality work. Although primarily for writing and language-related services, [ServiceScape](https://www.servicescape.com/) may offer opportunities for content specialists with strong writing skills.
**Specialty:** Primarily focused on writing, editing, and translation services
**Pros:**
- Potential for less competition in niche writing/editing areas
- Focus on quality work and curated client matching
- Can be a good fit for experienced writers seeking higher-paying projects
**Cons:**
- Fewer project types compared to broader marketplaces
- May require a strong writing portfolio to attract clients
**Ideal Demographic:** Experienced writers, editors, and translators looking for a platform that prioritizes quality work and potential for direct client relationships.
#### [22. Jooble](https://in.jooble.org/)

Jooble is a job aggregator that sources listings from multiple job boards and company websites. It functions as a search engine for job seekers, offering a convenient way to scan multiple sources in one place. [Jooble](https://in.jooble.org/) can be useful for a broad job search, but it is not a dedicated freelance platform.
**Specialty:** Aggregates a wide variety of jobs, including freelance, remote, and full-time positions across various industries
**Pros:**
- Centralizes the job search process across multiple websites
- Can help you discover opportunities you might not have found on individual job boards
- Offers a broad range of listings, including freelance, remote, and full-time positions
**Cons:**
- Might not have as many freelance-specific listings compared to dedicated freelance platforms
- The quality and reliability of listings can vary since they are pulled from external sources
**Ideal Demographic:** Job seekers with a broad search who want to maximize their exposure to potential opportunities, including those considering a mix of freelance and traditional employment.
#### [23. PeoplePerHour](https://www.peopleperhour.com/)

[PeoplePerHour](https://www.peopleperhour.com/) is a UK-based freelance marketplace focusing on short-term projects and hourly work. Clients post projects, freelancers submit proposals, and chosen freelancers are paid hourly through the platform. It offers a good entry point for those new to freelance work.
**Specialty:** Offers short-term projects and hourly work across various creative, technical, and business services
**Pros:**
- User-friendly interface and project posting process for clients
- Emphasizes short-term projects and hourly work for flexibility
- Potential for new freelancers to gain experience and build their portfolio
**Cons:**
- High competition, particularly in lower-paying categories
- Platform fees can impact earning potential
**Ideal Demographic:** Freelancers, especially those less experienced, seeking short-term, hourly projects, and those comfortable with a competitive environment.
### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
**How to Make the Most of the Top Freelance Websites?**
You have found some great freelance platforms that are a great fit. Now what? It is time to make the most of them! 87% of traditional workers with jobs see freelancing as a lucrative option in the coming years. But the trick is in knowing where to redirect your efforts. Here are a few key tips to help you stand out, land those dream projects, and increase your earnings:
### Let Your Profile Represent Yourself
Treat your profile like your most important marketing asset. Make sure it showcases your very best work, using visuals and case studies where possible. Clearly outline your core skills and areas of expertise. A touch of personality can also help you connect with potential clients. Remember, people hire people they like and trust!
### Always Settle on a Niche
The temptation to market yourself as a “jack-of-all-trades” is real, but resist it! Specialization is your friend. Focus on the types of projects you both excel at and enjoy doing. This makes it easier for your ideal clients to find you and increases your chances of landing projects that genuinely excite you.
### Do Not Take First Impressions Lightly
Avoid generic copy-and-paste proposals. Take the time to research the client and tailor your pitch to their specific project. Highlight how your unique skills and experience can contribute to their success. Showing genuine interest and enthusiasm goes a long way.
### Be Confident About the Worth of Your Work
It is natural to feel unsure about pricing, especially as a new freelancer. Do your research! Explore industry standards, factor in your experience level, and do not be afraid to [charge fair rates](https://www.rapyd.net/solutions/industries/gig-economy-payments/) for your time and expertise. Underselling yourself hurts not only you but the freelance community as a whole.
### Prioritize Building Long-Term Relationships
Freelancing is about more than just completing one-off projects. Foster positive relationships with clients by providing excellent work, communicating clearly, and going the extra mile. Happy clients often lead to repeat business, referrals, and glowing testimonials, all of which boost your reputation.
### Never Stop Adapting and Learning
The best freelancers never stop growing. Invest in online courses, workshops, or conferences to deepen your skills and stay on top of [web hosting trends](/blog/web-hosting-trends/) in your industry. This constant improvement will show in your work and make you an even more attractive candidate for those exciting projects.
Do not get discouraged. Finding the perfect fit takes time and persistence. Keep refining your profile, pitching for projects, and building your portfolio. Your dream gig is out there!
## Conclusion
The freelance world is full of possibilities. Finding the right freelance websites is a very important step in taking those opportunities head-on. Remember, the best websites for you are the ones that align with your skills, your preferred types of projects, and the way you like to work.
Do not be afraid to experiment! Moreover, explore a few different freelance websites, refine your profile, and start putting yourself out there. The perfect freelance gig is waiting for you, and with these resources at your fingertips, you are well on your way to finding it.
Choose one of the top 23 freelancing websites we have discussed above and start building your freelancer profile today. It is never too late to be a thriving freelancer!
## Frequently Asked Questions About Gig Economy

Now, we will address a few of the most commonly asked questions about freelancing. If you are a fresher in this industry, don’t forget to read this section!
### 1. How do I find my first clients?
Finding those initial clients can feel like the biggest hurdle. Start by leveraging your existing network (friends, former colleagues, etc.). Next, join relevant online communities and social media groups, and do not be afraid to put yourself out there. Additionally, even offering a few smaller projects to build your portfolio and gain testimonials can make a huge difference.
### 2. What if I experience a “feast or famine” cycle with projects?
The inconsistent flow of work is a reality for many freelancers. Thus, proactive marketing during slower periods is key. Use that time to network, update your portfolio, and perhaps pitch for recurring “retainer” style projects with ongoing clients to provide some baseline stability.
### 3. How do I handle difficult clients?
Even the best freelancers encounter the occasional tricky client. Clear communication, well-defined contracts, and setting boundaries from the start are essential. Do not be afraid to respectfully walk away from a situation if it becomes unreasonable or compromises your well-being.
### 4. Should I incorporate as a freelancer?
Whether or not to incorporate is a complex decision based on your individual circumstances. Factors like your income level, liability risks in your field, and the tax laws in your location all come into play. Therefore, consulting with an accountant or business advisor can help you make the best choice for your freelance venture.
### 5. How do I stay motivated as a freelancer?
Working for yourself requires self-discipline and a strong support system. Begin by setting clear goals. Next, connect with other freelancers (in person or online). Additionally, do not underestimate the importance of breaks and self-care for avoiding burnout. Finally, celebrate your wins, big and small, to keep yourself feeling energized.
### 6. Which is the best freelancer platform for beginners?
All the websites listed above are good for both pros and beginners alike. All you need to do is start looking for a client who's willing to hire beginners at a lower rate, and then you start climbing up from there.
### 7. I'm a freelance WordPress developer. Is your hosting platform a good choice for me?
Yes, our Managed Cloud Hosting platform was built with developers and creators in mind and has all the tools you need to create a website with zero hassles and ease, and manage as many sites and clients as possible. For more info, head over to [levamo.com](/) for more details.
### 8. I'm a freelance web developer. Does your platform have the right tools for me to manage all my clients?
Levamo was built with web developers in mind and has all the right tools and features that give you complete control over all your projects and websites. It's also the fastest WordPress hosting platform, which means your clients won't just be happy with your services; they'll also be singing praises about the website's performance!
---
## Our Feedback Portal is Now Live and Getting Help is Easier Than Ever
- URL: https://levamo.com/blog/our-feedback-portal-is-now-live-and-getting-help-is/
- Category: news
- Author: The Levamo Team
- Published: 2024-04-29
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Introducing the Levamo Feedback Center and a new Get Help button.
> **Update:** The feedback portal described in this post is no longer in service. The Get Help button in your dashboard still works for live chat and support, but it no longer links to a public feedback site. If you'd like to share feedback or request a feature, please [contact us](/contact/) - we'd love to hear from you.
We're excited to announce two major features designed to enhance your support experience and give you a voice in product development: the **Get Help button** and the **Levamo Feedback Center**.
## What's New
### Get Help Button
The Levamo dashboard now includes a "Get Help" button in the main menu containing four sections:
- **Resources**: Links to the Getting Started Guide, Knowledge Base, and Levamo Blog
- **Product**: Access to feedback submission, product roadmap, and changelog
- **Support**: Live chat option and ticket viewing for existing support cases
- **Account Support Plan**: Information about your support plan with management options
### Levamo Feedback Center
You can access the feedback portal at [contact us](/contact/) with three main tabs:
- **Feedback**: An interactive board for posting and viewing community feedback
- **Roadmap**: Displays planned development features so you can see what's coming
- **Changelog**: A running log of updates with context and implementation details
## How It Works
Log into your Levamo account and click the Get Help button to submit feedback directly through a popup interface. Your feedback automatically posts to the feedback center. Alternatively, visit [contact us](/contact/) directly using your Levamo Dashboard credentials to access all three tabs.
---
## You Have the Control with the Restore Backup Feature
- URL: https://levamo.com/blog/you-have-the-control-with-the-restore-backups-feature/
- Category: news
- Author: The Levamo Team
- Published: 2024-04-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Restore site backups directly from your dashboard without contacting support.
Say goodbye to contacting our support team whenever you want to restore a backup of your site. You can now restore site backups directly from the dashboard.
## What's New?
We've finished building and testing the restore backups feature, and now it's all yours. From the **Backups** area of the dashboard, select the backup version that you wish to restore and click **Restore**.
The process usually takes about 5-10 minutes, but if your site is very large, it may take longer. While your backup is being restored, we switch your site into WordPress maintenance mode, but this will disappear automatically when the restore is complete.
## Important Notes
- **Recent backup required**: To restore a backup, you must have taken a backup within the past hour. If you haven't, the dashboard will prompt you to do so. This ensures there is a reliable rollback version just in case something goes wrong during the recovery process. We plan to automate this in the future.
- **Recovery stalls**: If a backup recovery stalls, contact our support team. We've got a process in place to fix it.
- **Email notifications**: You'll receive emails during the recovery process, once when the recovery begins and another when it is complete.
- **Full restore**: Restoring a site backup includes both web files and the database.
## Learn More
You can learn more about restoring backups in the dashboard in the following knowledge base article: [How to Restore a Backup](https://support.levamo.com/en/articles/8484134-how-to-restore-a-backup).
---
## How to Choose Best Hosting for Your Business Purpose
- URL: https://levamo.com/blog/hosting-for-business/
- Category: hosting
- Author: Faisal Sarker
- Published: 2024-04-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find perfect hosting! Match your business needs with our expert advice.
Are you navigating the vast ocean of web hosting options, wondering, How to Choose Best Hosting for Your Business Purpose?
[With over 330,000 Web Hosting Companies Worldwide](https://www.hostingadvice.com/how-to/how-many-web-hosting-companies-are-there/#:~:text=There%20Are%20More%20Than%20330%2C000,exact%20number%20is%20unknown1.), each offering a unique blend of services, features, and pricing, the quest to find the perfect fit for your business can feel like searching for a needle in a digital haystack.
Choosing the right web hosting isn't just about what you prefer; it's crucial to find a service that's reliable, scalable, and secure for your website's needs. This guide is here to help, offering straightforward advice and important factors to consider so you can make a well-informed choice.
Before we delve into selecting the best hosting for your business, let's first understand your website needs.
## Pinpointing What Your Website Demands
To find the ideal web host, it's essential to clearly define your website's demands. Here's a reshuffled list of considerations:
### Budgeting for Web Hosting
Start by setting a clear budget for your web hosting needs. The cost of hosting services varies, so establishing a budget early on will help you manage expenses effectively and choose a service within your financial reach.
### Security Priorities
Determine the level of [security necessary for your website](/blog/how-to-fix-https-not-secure-message-in-chrome/). For instance, sites that handle sensitive customer information, like online stores, need top-notch security measures to protect data.
### Expected Visitor Traffic
Assess the amount of traffic you anticipate your website will receive. This foresight is crucial for selecting a hosting plan that can smoothly accommodate your expected traffic volume.
### Website Creation Tools
Choose between using a self-hosted platform or a hosting service that comes with website-building capabilities. Opt for a web host that supports the platform or tools you prefer for building your site.
### Website Objectives
Clarify your site's main objectives. Whether it’s for personal use, such as a blog or portfolio, or for business purposes like a company landing page, your goals will dictate the hosting resources required.
### Storage and Feature Needs
Consider the bandwidth and storage your website will need to operate efficiently. Also, think about the potential for growth and scalability offered by the hosting provider to ensure your site has room to expand.
## How Do I Choose a Website Host for My Business?

When it comes to finding the [best hosting provider for WooCommerce](/managed-woocommerce-hosting/), identifying what your website aims to achieve is the first crucial step. Different websites serve different purposes; a blog, for example, won't have the same requirements for [LMS hosting services](/managed-lms-hosting/). The nature of your site dictates the type of hosting service you should look for, especially in terms of features like e-commerce capabilities and content management systems.
### Comparing Hosting Providers with a Critical Eye
Embarking on the journey to find the right hosting provider means diving into research and comparisons. It's essential to evaluate the credibility of each potential host. Using reliable review sites and checking for trial offers or money-back guarantees can provide insights into the quality of service.
Moreover, ensuring they offer responsive customer support across multiple channels can save you from potential future headaches.
### Delving into the Technical Aspects
The backbone of any hosting service is its technology. Providers that leverage advanced server technologies, such as [LiteSpeed Web Servers](/blog/lite-speed-hosting-benefits/), can offer better security and performance. Consider the location of the provider's data centers for optimal site speed and check if they facilitate easy website migration, which is especially important if you're looking to switch hosts.
Additionally, the availability of domain registration and custom email addresses through your hosting provider can significantly enhance your business's professionalism.
### Securing Reliable Support
A web host that stands by 24/7 ready to assist is invaluable. Beyond the availability of support, the quality matters - having access to a detailed knowledge base, engaging tutorials, and diverse communication channels like live chat, email, and phone support can dramatically improve your experience. This dedicated support system ensures your website remains operational, addressing any issues promptly and efficiently.
### Selecting the Right Type of Hosting Service
Finally, understanding the spectrum of hosting services available is vital. From dedicated to shared and VPS to cloud and WordPress specialized hosting, each has its advantages and best use cases. The choice should reflect your website’s traffic expectations, security requirements, and growth prospects.
Evaluating the balance between cost, features, and the level of management offered (self-managed vs. managed hosting) will guide you to the hosting plan that best fits your business goals.
There are also different types of hosting services available, and each one has its own benefits and downsides. To help identify which option will suit your website best, let’s take a closer look at each web hosting type below.
## What Are the 5 Types of Hosting?

### Shared Hosting: The Gateway to Going Online
Shared hosting is where your website lives on a server shared with other websites, making it the most cost-effective option for many. It's particularly suited for sites with low to medium traffic, such as blogs, personal portfolios, and small business websites.
The appeal of shared hosting lies in its simplicity and user-friendliness, with many providers offering intuitive control panels for easy site management. However, the shared nature of the resources means that your site's performance could be affected by other sites on the same server.
### Virtual Private Server (VPS) Hosting: The Middle Ground
VPS hosting offers a step up from shared hosting, providing dedicated resources on a shared server through virtualization technology. This option strikes a balance between cost and performance, offering more stability and resources than shared hosting without the price tag of dedicated hosting.
VPS hosting is ideal for medium-sized businesses that require more control and resources but are not ready to invest in a dedicated server. Although it requires more technical knowledge, many providers, such as Hostinger, simplify the process with user-friendly management tools and support for various operating systems.
### Cloud Hosting: For Scalability and Reliability
Cloud hosting represents a significant leap in hosting technology, offering high scalability and reliability. Your website is hosted across a network of virtual servers, ensuring that it remains operational even if one [server goes down](/blog/the-requested-url-was-not-found-on-this-server/). This type of hosting is perfect for businesses expecting fluctuating traffic or those in need of high availability.
Cloud hosting combines the ease of shared hosting with the performance and resources closer to that of VPS hosting, making it suitable for a wide range of business sizes and types.
### Dedicated Hosting: The Pinnacle of Performance
Dedicated hosting provides the ultimate control and resources, offering an entire server for your website. This option is best suited for large-scale businesses and high-traffic sites requiring top-tier performance, security, and customization.
While dedicated hosting comes with a higher price point and demands significant technical expertise, the investment is well justified for businesses that cannot afford any compromise on performance and reliability.
### WordPress Hosting: Tailored for the World’s Favorite CMS
WordPress hosting is specifically designed to optimize the performance and security of websites powered by WordPress, the world’s most popular content management system. This type of hosting can range from shared to dedicated environments but is fine-tuned for WordPress. Features often include one-click installations, automatic updates, and specialized support, making it an attractive option for users at all technical levels.
Providers like levamo.com dedicatedly design their WordPress hosting plans with performance-boosting features and security measures to ensure your site runs smoothly.
## Things to Be Considered to Choose Best Hosting for Your Business Purpose

Selecting the perfect hosting for your business website is a multifaceted process that involves more than just comparing prices. To ensure your website performs optimally, supports your business growth, and provides a secure environment for your customers, several critical factors must be considered:
### Platform Compatibility: CMS vs. Website Builder
Understanding whether your site will run on a Content Management System (CMS) or if you’ll utilize a website builder is crucial. CMS platforms like WordPress, Joomla, and Drupal offer flexibility and the ability to customize your site extensively but often require a bit more technical knowledge to manage.
On the other hand, website builders offer a more straightforward, less technical route to getting your site up and running, ideal for those seeking simplicity and ease of use. Your choice will influence the hosting services you consider, as some are better suited to specific platforms.
### Storage and Bandwidth Needs
The amount of storage and bandwidth your website requires is dictated by its size and the volume of traffic it receives. Storage is necessary for all your website's files, while bandwidth affects how quickly your site can serve those files to visitors.
Evaluating your needs in these areas is essential for choosing a hosting package that ensures your site runs smoothly without unnecessary expense for unneeded capacity.
### Speed and Performance Optimization
A fast-loading website is vital for user experience and SEO ranking. Opt for hosting services that offer performance-enhancing features like caching, the use of a Content Delivery Network (CDN), and data centers located near your primary audience to minimize load times. These features can significantly impact your website’s accessibility and visitor satisfaction.
### Security Measures
Protecting your website from cyber threats is non-negotiable. Look for hosting providers that offer robust security features such as [SSL certificates](/blog/fix-ssl-certificate-error/), firewalls, and regular backups. Ensuring your website is secure not only protects your business but also builds trust with your visitors.
### Reliability and Uptime
Your website’s availability is critical; even small amounts of [downtime can lead to lost revenue](/blog/wordpress-site-down-common-issues-and-fixes/) and diminished trust in your brand. Seek out hosting services with [high uptime guarantees](/blog/choosing-reliable-hosting-provider/) and reliable customer support to address any issues promptly.
### Customer Support Availability
When issues arise, having access to responsive, knowledgeable support can make a significant difference in resolving problems quickly. Evaluate potential hosting providers based on the support channels they offer - such as live chat, email, and phone support - and their reputation for customer service.
### Ease of Management
For many business owners, managing a website is just one of many responsibilities. A hosting provider that offers an intuitive control panel and easy-to-use tools for site management can save you time and frustration. Additionally, resources like tutorials and a comprehensive knowledge base can be invaluable for troubleshooting and learning.
### Scalability
As your business grows, so too might your website. Consider how easy it is to upgrade your hosting plan or add resources. The ability to scale quickly and efficiently is crucial for supporting business expansion without the need for a complete overhaul of your hosting arrangement.
### Price vs. Value
While cost is always a consideration, the cheapest option is not always the best when it comes to hosting. Assess the value each hosting provider offers, considering their reliability, feature set, and support, to find the best fit for your budget and business needs.
## FAQs
**Can I switch hosting providers if I'm not satisfied?**
Yes, most websites can migrate to a new hosting provider. Look for hosts offering migration services to ease the transition.
**Do I need technical knowledge to manage a hosting service?**
While some hosting types (like VPS or dedicated hosting) may require technical skills, many providers offer managed services and user-friendly control panels that minimize the need for technical management.
**What are some red flags when choosing a web hosting provider?**
Beware of providers with no clear uptime guarantees, negative reviews, limited customer support options, and a lack of transparency about pricing and renewal fees.
**How do CMS and website builders affect my hosting choice?**
Your choice between a CMS and a website builder can influence your hosting decision. Some hosts specialize in certain CMS platforms (like WordPress) with optimized performance and support, while others might offer integrated website builders for ease of use.
**What's the difference between shared, VPS, cloud, and dedicated hosting?**
**Shared Hosting:** Multiple websites share the same server resources. Ideal for small to medium sites.
**VPS (Virtual Private Server) Hosting:** A shared server, but with dedicated resources for each site. Suits medium-sized businesses.
**Cloud Hosting:** Utilizes multiple servers for high reliability and scalability. Good for businesses with fluctuating traffic.
**Dedicated Hosting:** Offers an entire server for one website, providing maximum control and resources. Best for large businesses.
## Conclusion
Selecting the ideal web hosting is crucial for your business's success, requiring a thoughtful balance of needs, security, and budget. By prioritizing scalability, reliability, and support, you can secure a hosting solution that not only meets your current demands but also supports future growth.
The right hosting ensures a flawless online experience for your customers, positioning your business for success in the ever-evolving digital world. Make an informed choice to lay a strong foundation for your digital journey.
## Frequently Asked Questions

### Can I switch hosting providers if I'm not satisfied?
Yes, most websites can migrate to a new hosting provider. Look for hosts offering migration services to ease the transition.
### Do I need technical knowledge to manage a hosting service?
While some hosting types (like VPS or dedicated hosting) may require technical skills, many providers offer managed services and user-friendly control panels that minimize the need for technical management.
### What are some red flags when choosing a web hosting provider?
Beware of providers with no clear uptime guarantees, negative reviews, limited customer support options, and a lack of transparency about pricing and renewal fees.
### How do CMS and website builders affect my hosting choice?
Your choice between a CMS and a website builder can influence your hosting decision. Some hosts specialize in certain CMS platforms (like WordPress) with optimized performance and support, while others might offer integrated website builders for ease of use.
### What's the difference between shared, VPS, cloud, and dedicated hosting?
- **Shared Hosting:** Multiple websites share the same server resources. Ideal for small to medium sites.
- **VPS (Virtual Private Server) Hosting:** A shared server, but with dedicated resources for each site. Suits medium-sized businesses.
- **Cloud Hosting:** Utilizes multiple servers for high reliability and scalability. Good for businesses with fluctuating traffic.
- **Dedicated Hosting:** Offers an entire server for one website, providing maximum control and resources. Best for large businesses.
---
## See the Progress When Creating Downloads for Backups
- URL: https://levamo.com/blog/show-the-percent-progress-when-downloading-a-backup/
- Category: news
- Author: The Levamo Team
- Published: 2024-03-16
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Track backup download progress with a new percentage indicator.
We've introduced a feature that displays the backup download link creation status as a percentage. This enhancement helps you manage your time more effectively while waiting for download links to be prepared, as the process can range from minutes to several hours depending on backup size.
## How It Works
You can download backups through the dashboard as usual. The system then checks the download link creation status every minute and displays the progress percentage in the backups section of the dashboard. No more guessing how long you'll need to wait.
## Learn More
For additional information on downloading site backups from the dashboard, consult the support documentation: [How to Download a Site Backup](https://support.levamo.com) available in the Levamo Knowledge Base.
---
## Add Lite Plans to Your Order During Checkout
- URL: https://levamo.com/blog/allow-purchasing-lite-plans-during-checkout/
- Category: news
- Author: The Levamo Team
- Published: 2024-03-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
You can now add Lite plans to your cart during signup checkout.
Our Lite plan lets you host your low-traffic and static websites on Levamo alongside your dynamic and resource-hungry sites. Now you can add this plan to your order before you checkout.
## What's New?
Previously, customers could only purchase Lite plans through the Levamo dashboard after their initial account setup. This required making an initial purchase, then returning separately to buy additional Lite plans.
The updated process simplifies this workflow. During signup, users can now add Lite plans directly to their shopping cart. These can be purchased simultaneously with other plan tiers, eliminating the need for a second transaction.
## Learn More
For additional information about Lite plan features and differences, see our [Comparing Levamo Plans](https://support.levamo.com/en/articles/8484102-comparing-rapyd-plans) knowledge base article.
---
## It's Easier to Find the Right Levamo Plan for Your Site
- URL: https://levamo.com/blog/new-and-improved-plan-details-popover/
- Category: news
- Author: The Levamo Team
- Published: 2024-03-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
A new plan details popover shows key info when you hover.
As we continue to listen to customer feedback and roll out new features, we've needed to rethink how we present plan information before purchase. We think we did a pretty alright job!
## What's New?
You'll now see a handy window that shows important information about the plan that you've selected. All you have to do is hover over the question mark icon and the window will appear.
## Learn More
For detailed breakdowns of all available Levamo service tiers, see our [Comparing Levamo Plans](https://support.levamo.com/en/articles/11886518-technical-specifications-of-rapyd-cloud-plans) knowledge base article.
---
## The Impact of LiteSpeed on Web Hosting and SEO
- URL: https://levamo.com/blog/lite-speed-hosting-benefits/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2024-03-11
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
LiteSpeed hosting boosts SEO! See how it speeds up your site and improves rankings.
In the fast-paced digital landscape of today, selecting the right web hosting is crucial for a website's success. LiteSpeed hosting benefits, particularly its influence on SEO, distinguish it as a premier web server option.
According to data from [W3Techs](https://w3techs.com/technologies/overview/web_server),
"LiteSpeed now claims the fourth spot in the web server market, boasting a 14.6% share among websites whose web server is known"
In this detailed exploration, we'll dive deep into the significant impact of LiteSpeed on web hosting and SEO. We aim to uncover what sets LiteSpeed apart from its competitors, showcasing its unique features and the various editions of LiteSpeed Web Server available.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## What is a Web Server and How does it Work?

A web server can be defined either as a computer program or device that delivers web pages to users upon request. Think of it as a waiter in a restaurant: when you as a user ask for a dish (in this case, a web page), the waiter goes to the kitchen (the server) to get it for you.
When you type a website address into your browser or click on a link, your browser sends a request to the web server hosting that site. The web server then processes this request and sends back the requested web page to your browser, allowing you to view the website.
If the address you request exists and there are no issues, the server retrieves the page and sends it back to your browser in a form that you can read and interact with. If the page doesn't exist or there's an error, the [server will send an error message instead.](/blog/the-requested-url-was-not-found-on-this-server/) This entire process is usually so fast that you get your results in just a few seconds, making web servers a crucial backbone of the internet, enabling the swift flow of information across the world.
## What is a LiteSpeed Web Server

LiteSpeed Web Server, from [LiteSpeed Technologies](https://www.litespeedtech.com/products/litespeed-web-server), exemplifies the LiteSpeed hosting benefits as a top-tier, highly scalable solution designed to effortlessly enhance your web hosting experience. It seamlessly integrates in place of an existing Apache server, without the need for modifications to other software or the operating system. This smooth transition to LiteSpeed Web Server eliminates potential bottlenecks in your current hosting setup without disruptions.
With its array of features and user-friendly web administration console, LiteSpeed Web Server makes setting up and managing a robust web hosting infrastructure simpler. Its efficiency and ease of adoption position it as a smart choice for the [fully managed WordPress hosting](/managed-wordpress-hosting/).
### Understanding the Range of LiteSpeed Web Server Options
#### OpenLiteSpeed Edition:
Engineered for large, high-traffic sites, this open-source version stands out for its cost-free availability for both personal and commercial use. However, it does not support integration with hosting control panels.
#### Standard Edition:
Ideal for smaller, less busy websites, the Standard Edition is compatible with popular hosting control panels like [WHM/cPanel](https://cpanel.net/products/cpanel-whm-features/) and DirectAdmin. This edition is also free for personal and commercial applications, making it a versatile choice for a broad range of users.
#### Enterprise Edition:
Designed for high-traffic sites and boasting compatibility with several hosting control panels, the Enterprise Edition is the go-to choice for top web hosting companies aiming to deliver an exceptional hosting experience. Known for its supreme stability and cPanel support, it also works seamlessly with DirectAdmin, making it a premium option for serious hosting requirements.
### Distinguishing Features of LiteSpeed Web Server
LiteSpeed Performance Features distinguishes itself uniquely positioning it as a premier choice for web hosting and SEO optimization, especially for WordPress platforms. Here’s a closer look at its standout attributes:
#### Pioneering HTTP/2 and HTTP/3 Support:
Image instruction: Use the below image as inspiration for the image

LiteSpeed introduces the industry with the first commercial server to fully embrace HTTP/2, enhancing web communication through features like binary protocol and header compression. It extends this [innovation to HTTP/3](https://medium.com/@maryanngitonga/evolution-of-http-http-3-deep-dive-469e5e13ae70), leveraging QUIC for encrypted, faster, and more reliable connections.
#### Comprehensive Scripting Language Support:
Unlike many of its competitors, LiteSpeed excels in handling dynamic content across a broad spectrum of scripting languages, including PHP, Perl, Ruby, Python, and Java, through its efficient LiteSpeed SAPI (LSAPI).
#### Advanced Security and Compatibility:

With support for modern encryption standards like SSL/TLS and compatibility with IPv6, LiteSpeed ensures websites are secure and future-proof. Its Apache compatibility allows for a seamless transition, utilizing existing Apache configurations and .htaccess files without reconfiguration.
#### Efficient Resource Management:
The event-driven architecture of LiteSpeed significantly reduces memory footprint and increases the ability to handle concurrent connections without additional hardware resources. This leads to better scalability and performance, particularly for high-traffic WordPress sites.
#### Performance Optimization Features:
LiteSpeed includes built-in support for cutting-edge technologies like Brotli and GZIP compression, SPDY, and WebSocket proxying. These features collectively enhance website speed and performance, directly benefiting SEO by improving page load times and user experience.
#### Seamless Integration with Control Panels:

LiteSpeed works effortlessly with all major hosting control panels, including cPanel, Plesk, and DirectAdmin. This ensures webmasters can easily manage their sites and benefit from LiteSpeed's performance without changing their workflow.
#### Superior Caching Capabilities with LSCache:
LiteSpeed's integrated caching solution, [LSCache](https://lscache.io/), rivals other caching technologies like Varnish but with added flexibility and customization through rewrite rules. This feature significantly speeds up content delivery for dynamic websites such as WordPress, directly contributing to better SEO rankings.
#### CloudLinux Compatibility:
A close partnership with CloudLinux ensures LiteSpeed is fully compatible with CloudLinux's security and stability features, like CageFS and PHP Selector. This compatibility enhances the hosting environment's security and flexibility, making it ideal for shared hosting providers.
#### High Availability and Ease of Use:
Features like zero downtime for configuration changes, instant recovery from service failures, and user-friendly control panel plugins make LiteSpeed an accessible and reliable web server choice for businesses of all sizes.
## Why Choose LiteSpeed Over Other Web Servers for Hosting and SEO

LiteSpeed Web Server stands out as the premier choice for web hosting and SEO due to its unmatched performance, security, and compatibility with WordPress. Its efficiency in resource management and ability to seamlessly handle high traffic volumes make it an ideal solution for websites aiming for top SEO rankings.
Whether compared with Apache, Nginx, IIS, or Caddy for Web hosting or SEO, LiteSpeed consistently proves to be the [superior web server technology ](/blog/web-host-vs-web-server/)for modern web hosting demands.
Also Read: [LMS Hosting](/managed-lms-hosting/) and [MemberPress Review](/blog/memberpress-review/)
### LiteSpeed vs. Apache
**Optimal Output:**
LiteSpeed offers a significant performance boost over Apache, handling more requests per second while consuming fewer resources. This translates into faster loading times for WordPress sites, a crucial factor for SEO.
**Secure Shield:**
While Apache is known for its robustness, LiteSpeed provides enhanced security features and easier management of SSL certificates, offering better protection against web attacks.
**Resource Efficiency:**
LiteSpeed's efficient use of server resources means that WordPress sites can handle higher traffic without requiring server upgrades, unlike Apache which may struggle under heavy load.
**CMS Compatibility:**
When it comes to compatibility, LiteSpeed is the best choice for popular CMS platforms like WordPress. It offers specific optimizations such as LiteSpeed Cache that significantly improve website performance, an area where Apache lacks specific integrations.
### LiteSpeed vs. Nginx
**Peak Efficiency:**
Both LiteSpeed and Nginx are known for their high performance, but LiteSpeed often edges out with its ability to serve dynamic content faster, thanks to its built-in caching solutions for WordPress.
**Security Features:**
Nginx offers marvelous security, but LiteSpeed includes additional protection features like mod_security compatibility and [DDoS protection](/blog/preventing-ddos-attacks/), providing a safer [environment for WordPress hosting.](/blog/importance-of-a-web-host/)
**Growth Potential:**
While Nginx is scalable, LiteSpeed's unique architecture allows for more efficient scaling in shared hosting environments, making it easier to manage sudden traffic spikes.
**Affordable Option:**
LiteSpeed offers a free tier with LiteSpeed Cache for WordPress, making it a cost-effective solution for improving SEO and website performance compared to Nginx's more complex pricing for advanced features.
### LiteSpeed vs. IIS (Internet Information Services)
**Quick Access:**
LiteSpeed significantly surpasses IIS in serving static and dynamic content, which is crucial for fast WordPress site performance and SEO.
**SafeGuard:**
In the case of providing high-class security LiteSpeed provides comparable, if not superior, features to IIS. LiteSpeed offers easier management and integration of SSL certificates and comprehensive protection against web attacks.
**Windows Server Environments:**
While IIS is built for Windows, LiteSpeed offers compatibility with Windows server environments, providing a high-performance alternative for WordPress sites hosted on Windows servers.
### LiteSpeed vs. Caddy
**Automatic HTTPS:**
Both LiteSpeed and Caddy offer automatic HTTPS, but LiteSpeed's implementation is designed to maximize performance and SEO for WordPress sites.
**Performance Metrics:**
LiteSpeed provides detailed performance metrics and easier optimization tools for WordPress, outperforming Caddy in resource-intensive scenarios.
**User-Friendly:**
While Caddy is praised for its simplicity, LiteSpeed combines ease of use with advanced features, making it more suitable for WordPress hosting needs and achieving better SEO results.
## The Impact of LiteSpeed Web Server on Website Hosting and SEO Rankings
LiteSpeed Web Server stands at the forefront of enhancing website performance, playing an instrumental role in the success of SEO strategies. This is particularly evident for WordPress-based websites, where selecting an optimized hosting provider like Levamo can drastically improve search engine visibility and user experience.
Below are seven key ways LiteSpeed Web Server elevates website hosting and SEO rankings:
### Gear up Site Speed and Boost Performance

LiteSpeed Web Server's ability to swiftly deliver web pages is crucial for enhancing a website's loading speed. LiteSpeed powers some of the [fastest WordPress hosting](/blog/fastest-wordpress-hosting/) service providers by significantly boosting content delivery speeds.
The rapid loading of sites not only enhances the user experience but also contributes to higher search engine rankings, emphasizing the critical role of speed in SEO.
### Confirming Peak Uptime and Unmatched Reliability
The reliability of LiteSpeed Web Server is showcased through its exceptional [uptime, ensuring that websites are consistently accessible](/blog/choosing-reliable-hosting-provider/) to both users and search engines. For WordPress sites looking to maintain online visibility, the uptime guaranteed by LiteSpeed-based hosting solutions is vital.
Such reliability supports improved SEO outcomes by keeping websites available and performant at all times.
### Topnotch Security and Trust
With multiple security features, the LiteSpeed Web Server plays a proper role in safeguarding WordPress sites from cyber threats. Enhanced security measures provided by LiteSpeed-compatible hosting services not only protect websites from attacks but also positively influence SEO rankings by ensuring a safe browsing experience.
The importance of secure sites is highlighted by search engines' preference for them, underlining the significance of stringent security in SEO strategies.
### Facilitating Scalability and Growth
The scalability of resources according to traffic demands is a critical feature of LiteSpeed Web Server for WordPress sites experiencing growth. Dedicated WordPress hosting provider like [levamo.com](/) offers scalable LiteSpeed-based hosting solutions that adjust to evolving needs, ensuring sites remain quick and responsive.
Such scalability is crucial for sustaining and enhancing SEO rankings, as it directly affects site performance and user satisfaction.
### Improve Mobile Responsiveness

LiteSpeed Web Server ensures content is efficiently served and optimized for mobile devices. LiteSpeed ensures that WordPress sites get more mobile-friendly, improving both loading times and layout responsiveness.
Mobile responsiveness is a key search engine ranking factor, making it an essential component of SEO for any website.
### Supporting Content Delivery Network (CDN) Integration
Integrating a CDN with LiteSpeed Web Server can significantly enhance website loading times by caching content across a global network. Seamless CDN integration for WordPress sites, minimize latency and boost site speed.
This worldwide approach to content delivery is invaluable for SEO, as it improves the user experience for visitors from any location.
## Final Words
Web Hosting with LiteSpeed web server can be a wiser choice as it stands out as a key player in the world of web hosting and SEO. Thanks to its cutting-edge design, WordPress compatibility, and a range of standout features like HTTP/2 and HTTP/3 support, strong security, and easy [free WordPress CDN](/cloudflare-cdn/) integration. It's an ideal option for anyone running a website, from small blogs to large, high-traffic sites, offering better performance, dependability, and safety.
LiteSpeed SEO Optimization on the other hand is also something worth mentioning. As the internet keeps growing and changing, LiteSpeed is equipped to handle the demands of modern web hosting includng [WooCommerce managed hosting](/managed-woocommerce-hosting/), making sites quicker, safer, and more SEO-friendly. Choosing LiteSpeed might just be the turning point your website needs to stand out in the crowded online space.
## Frequently Asked Questions

### What is LiteSpeed Web Server?
LiteSpeed Web Server is a high-performance, scalable web server from LiteSpeed Technologies, offering a significant boost in web hosting and SEO capabilities compared to traditional web servers.
### Can LiteSpeed Web Server replace Apache?
Yes, LiteSpeed can seamlessly replace Apache without requiring changes to other software or operating systems, utilizing existing Apache configurations and .htaccess files efficiently.
### Is LiteSpeed compatible with WordPress?
Absolutely. LiteSpeed offers specific optimizations for WordPress, including the LiteSpeed Cache plugin, significantly improving website performance and SEO.
### Is LiteSpeed Web Server free?
OpenLiteSpeed and the Standard Edition of LiteSpeed Web Server are free. The Enterprise Edition, offering advanced features and support, requires a license.
### Can LiteSpeed handle high traffic websites?
Yes, thanks to its efficient resource management and ability to handle concurrent connections, LiteSpeed is ideally suited for high-traffic websites, ensuring stability and responsiveness.
---
## Save Time by Automatically Starting the Backup Download Link Creation Process
- URL: https://levamo.com/blog/new-feature-to-download-this-backup-immediately/
- Category: news
- Author: The Levamo Team
- Published: 2024-03-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Start backup download link generation right from the creation modal.
The backup download link generation process can take some time, so we've made it possible to start the process right from the backup creation modal.
## What's New?
We've added the option to begin the backup download link generation process immediately when you create a new backup.
Previously, you had to create the site backup, then generate the download link. Each of these steps required you to interact with the dashboard. The problem was that both steps can take anywhere from a few minutes to a few hours. So, if you wanted to download a backup, you had to just hang around and wait for the backup to finish, then click "Download backup" to begin creating the download link.
This improvement means that you can simply check the box before creating your backup, then our system will take care of the rest. You can go enjoy a coffee and you'll be notified when the download link is ready.
## Learn More
See our [Creating and Managing Backups](https://support.levamo.com/en/articles/8484102-creating-and-managing-backups) knowledge base article to learn more.
---
## Schedule Your Backups Using Your Local Timezone
- URL: https://levamo.com/blog/backup-timezone-can-be-set-to-your-local-timezone/
- Category: news
- Author: The Levamo Team
- Published: 2024-03-01
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Set your preferred timezone when scheduling site backups.
We've made backup scheduling simpler by eliminating the need to work exclusively with multiple time zones.
## What's New?
You can now specify your preferred timezone when scheduling backups, rather than being limited to UTC. This makes it easier to plan backups during off-peak hours specific to your location.
Here's what changed:
- **Timezone selection**: Now available in the backup scheduling interface
- **Display**: The selected timezone displays in the backups management area
- **Execution**: Backups execute at the specified local time
- **Completed backups**: Details remain shown in UTC format
## Learn More
See our [Creating and Managing Backups](https://support.levamo.com/en/articles/8484102-creating-and-managing-backups) knowledge base article for additional information on backup management features.
---
## Six Ways to Fix 'Error 404: The Requested URL Was Not Found On This Server'
- URL: https://levamo.com/blog/the-requested-url-was-not-found-on-this-server/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2024-02-26
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix Error 404! Six proven ways to troubleshoot this frustrating server error.
When you enter a webpage address and see the message '**Error 404: The Requested URL Was Not Found On This Server**,' it can be a bit frustrating. From the site owner and developer's perspective, it's even worse because you must address the issue immediately.
But don't worry. This guide will help you understand the reasons behind the "Error 404: The Requested URL Was Not Found On This Server" error and outline many strategies for resolving it.
Addressing error 404 is crucial not only from a technical standpoint but also for a good user experience.
By the way, in case you'd rather watch a step-by-step video guide on solving the 404 not found error, here it is:
https://www.youtube.com/watch?v=oAhKtIipmOI
But if you're more of a reader, let's continue. Now let's first understand what is a 404 error.
## What does “Error 404: The Requested URL Was Not Found On This Server” Mean?

So, what is a **404 error**?
"The Requested URL Was Not Found On This Server" error is also known as a **404 error**, which is an HTTP status code that says that the server is operational and accessible, but a specific page or resource you're attempting to reach cannot be found based on the URL provided.
This is a common HTTP status code that most users encounter at some point during web browsing. In eCommerce environments like those powered by [Magento Hosting](https://www.mgt-commerce.com/), ensuring proper URL structure and server configuration is key to avoiding such errors.
This type of situation can occur for many reasons, such as the resource doesn't exist at the specified location, possibly because it was moved, deleted, or never existed. It could also be due to a typo or error in the URL or an issue with the website's configuration that prevents the server from correctly identifying and serving the requested resource.
Understanding the error is important for both web developers and users. Here, we will discuss some common causes of the error first.
**Also Read:** [Common Server Problems](/blog/common-server-problems/)
## Why You're Seeing 'The Requested URL Was Not Found on This Server'
### 1. Incorrect or Typo in URL

The most common issue for this error is simply an incorrectly typed URL. This encompasses human errors such as typos, misplaced characters, or incorrect spellings, which can all lead to the problem.
A customized error 404 page - [Levamo](/)
In the screenshot above, you can see that I just added an extra 's' in the URL of this same article you're reading, and Levamo's server returned with the 404 error.
Mistakes like the one above, with an additional symbol, space, or incorrect case sensitivity in the URL, could direct you to a non-existent resource. So check the URL for discrepancies, including the protocol ([http or https](/blog/redirect-http-to-https/)), domain name, path, and specific file names or extensions, in case you see this error.
### 2. Missing Page or Resource
The absence of the requested page or resource on the server can also cause this error, which can happen if the content has been relocated to a new URL or removed from the server.
As websites evolve through redesigns or updates, pages may be shifted without proper redirection, or outdated content might be eliminated, potentially leading to dead links.
### 3. Server Misconfigurations
Server misconfigurations are a more technical cause of this error. Servers are configured to handle URLs in specific ways, and any changes or errors in these settings can block access to the intended resources.
Misconfigurations can arise from errors in the .htaccess file on Apache servers, issues in server software settings, or problems with how [Content Management Systems (CMS)](https://wordpress.com/go/tutorials/what-is-a-cms/) create URLs.
### 4. DNS Issues

DNS (Domain Name System) issues can also lead to a 404 error code. Indirectly, if a domain's DNS settings are configured incorrectly or have not fully propagated, it leads to an incorrect server where the desired resource is unavailable.
Also Read: [Code snippets for wordpress](https://support.levamo.com/articles/8316789-code-snippets-in-wordpress-usage-and-best-practices)
This is especially common following recent updates to a domain’s [DNS records](/blog/dns-records-explained/), such as during a change in hosting providers or after modifying [DNS configurations](/blog/nameserver-vs-dns/). DNS propagation delays, which can last up to 48 hours, might necessitate waiting or clearing the DNS cache for resolution.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
### 5. Content Restriction and Permissions
Sometimes, the resource or page exists but is inaccessible due to restrictions based on user permissions or geographic location, leading to the 'The Requested URL Was Not Found On this Server' error.
Servers configured to restrict access to specific resources based on criteria such as the user's IP address or login status might return this error to prevent unauthorized access, even if the denial is not explicitly stated.
### 6. Case Sensitivity in URLs
On some servers, particularly Unix and Linux-based servers, URLs are case-sensitive. In such environments, a resource identified by a URL with uppercase letters is considered distinct from another with the same name in lowercase.
The lack of awareness regarding this case sensitivity could result in 'The Requested URL Was Not Found On this Server' errors for users who enter a URL with the incorrect case.
### 7. Incorrect **File permissions**
**7. Incorrect File Permissions**
Sometimes, the page or resource you're trying to access does exist on the server, but due to improper file or directory permissions, the server can't access it. This can result in a 'The Requested URL Was Not Found on This Server' error.
Web servers like Apache or Nginx rely on specific permission settings to read files and traverse directories. If these permissions are misconfigured, and to give an example, if directories are set to `744` instead of the recommended `755`, or files are set to `600` instead of `644`, the server may be blocked from accessing the necessary resources. In such cases, instead of returning a 403 Forbidden error, some servers are configured to respond with a 404 Not Found error to avoid revealing the existence of restricted resources.
The seven points mentioned above are the potential causes of the 404 error. Now that you're aware of what can cause this error, let's learn how to resolve it using the solutions given below.
## 6 Ways To Fix “The Requested URL Was Not Found On This Server” Error

## 1. Reload the Webpage
If you encounter the "The Requested URL Was Not Found On This Server" error, a quick and effective first step is to refresh the webpage. Temporary issues with the server or errors in how the page was initially loaded can often be resolved with a simple refresh.
For Windows users, you can refresh the page by pressing **Ctrl + R**, while Mac users would need to press **Cmd + R**. This action prompts your browser to request the page from the server again, which can often bypass temporary glitches or loading errors.
## 2. Check the URL for any Typos

Another crucial step in troubleshooting the error 404 involves checking the URL for any mistakes. Typing errors are a common reason for users seeing 'The Requested URL Was Not Found On this Server ' error message.
Carefully review the URL in your browser's address bar. Look for any incorrect spellings, misplaced characters, or unnecessary punctuation. Ensuring the URL is entered correctly is a simple yet effective way to avoid the 404 page not found error.
## 3. Clear the Browser Cache
If refreshing the webpage doesn't eliminate the error, consider clearing your browser's cache. This action deletes temporary files your browser has stored, which might be contributing to the issue.
For Chrome users, navigate to the settings by clicking on the three dots in the upper-right corner.
After that, click on '**Clear browsing data**' from the drop-down menu.

A new dialog box will appear where you will find the option named “**Cached images and files**”. Check mark it and click on “**Clear data.**”

Once you've cleared the cache, go back to the website to check if the error has been fixed. If you're still encountering "The Requested URL Was Not Found On This Server," it's time to move on to the next step in troubleshooting.
## 4. Update Your Site’s Permalinks
Updating your website's permalinks is often a solution for '404 error: The Requested URL Was Not Found On this Server' errors, which are frequently caused by broken permalinks.
To update the permalink first, log in to your WordPress admin panel. Then, navigate to the **Settings** option on the left-side menu, and click on '**Permalinks**' from the submenu.

Once you're on the next page, review the post name to check for and correct any typing errors in your address bar.

## 5. Configuring 301 Redirects for Moved or Renamed Website Content
As a developer or site owner, if you've recently relocated or modified your web pages, it's crucial to establish a 301 redirect that guides users to the new URL on [your WordPress site](/blog/website-design-in-wordpress/). If it's not redirected properly, then users can see 'The Requested URL Was Not Found On this Server' error.
This step is essential for ensuring search engines can efficiently crawl your site and accurately index your pages. To implement this, you can utilize a redirection plugin within WordPress or manage the redirects through your hosting provider's control panel. If you encounter any difficulties in setting up the redirects, don't hesitate to reach out to your hosting provider for assistance.
## 6. Manually Reset the .htaccess File
This approach involves navigating to the backend of your WordPress site to alter a concealed file located in the root directory named ".htaccess."[There are several methods to access this file](/blog/wordpress-htaccess/), including FTP, cPanel, or a WordPress plugin such as WP File Manager.
Begin by opening the file manager via any of the mentioned tools. For illustration purposes, let's use WP File Manager as an example. Navigate to the Root directory and select the .htaccess file.

Before doing this, take a backup by right-clicking it and selecting “**Duplicate**”.
After that, right-click again and select “**Open.** ”

In the new window, you will see the .htaccess file codes.

Now, remove the previously written codes and paste these fresh rules into it:
# BEGIN WordPress
RewriteEngine On
RewriteBase /
RewriteRule ^index\.php$ - [L]
RewriteCond %{REQUEST_FILENAME} !-f
RewriteCond %{REQUEST_FILENAME} !-d
RewriteRule . /index.php [L]
# END WordPress
After applying these modifications, click the "Save" button. Then, attempt to access the targeted page to check whether the issue has been resolved.
**Note:** If you're uncertain about deleting the .htaccess file, we suggest seeking assistance from [your web hosting provider.](/blog/web-host-vs-web-server/) If you use Levamo and its [free WordPress CDN](/cloudflare-cdn/), just reach out to an expert on Live Chat!
## Never See a "404 Page Not Found" Error Again
‘The Requested URL was not found on this server’ or the 404 Page Not Found error is one of those frustrating crossroads where you’re left scratching your head trying to figure out what’s going on. With the solutions above, though, we're sure your visitors will not see the error 404 again on your website.
To summarize, the causes for HTTP error 404 range from typos to misconfigurations on your server, but the guide above provides the solutions to address URL issues, restore missing pages, and ensure server configurations.
We’ve also highlighted the importance of maintaining well-configured servers and websites through regular audits and diligent health checks.
A well-optimized server and website are your constant companions, providing a great experience for you and your audience. By implementing these practices, you not only solve immediate issues but also protect your online presence from potential pitfalls.
Also Read: [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/)
## Frequently Asked Questions

### What is a 404 error, and what causes the ‘Error 404: the requested url not found’ error on a server?
This error usually occurs due to mistyped URLs, the page has been moved or deleted, DNS issues, content restrictions and permissions, or server configuration issues etc.
### How often should I check my website for broken links to prevent ‘URL Not Found’ errors?
Regularly auditing your site for broken links, at least monthly, can help prevent these errors and improve user experience.
### How to prevent ‘The Requested URL Was Not Found On This Server’ Error?
To prevent the 404 page not found error, ensure correct URL entry, regularly update and check for broken links, correctly configure server settings, implement 301 redirects for moved content, verify DNS settings, and maintain updated plugins or CMS configurations.
Regular website maintenance and monitoring are key to minimizing the occurrence of this error.
### Are there tools to help identify why “Error 404: the Requested URL Was Not Found On This Server” error occurs?
Yes, you can use tools like Google Search Console or Screaming Frog SEO Spider to analyze your website for common issues leading to this error, helping you pinpoint and fix them efficiently.
### Why the requested URL was not found on this server?
While we have answered this question sufficiently in the article above and in the first question of this FAQ, we’ll still go ahead and answer this question for you: it could be due to multiple reasons like: incorrect URL, page removed or moved, broken link, server misconfiguration, permission issues, or DNS or hosting issues.
---
## Stay Ahead of Malware with the Security Area and Our New Monarx Security Dashboard
- URL: https://levamo.com/blog/now-showing-monarx-information-for-each-site/
- Category: news
- Author: The Levamo Team
- Published: 2024-02-24
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
A new Security area in your dashboard shows Monarx malware details.
Sites hosted on Levamo have always enjoyed automatic malware scanning and removal by Monarx. However, there was no security section in our dashboard that showed the details. We've changed that so you can be confident that your site is clean and safe.
## What's New?
We've introduced a new dashboard area called **Security**. In this area, you can see a summary of security tools and features. For now, this includes a section dedicated to Monarx malware protection and insurance.
## How It Works
In the dashboard, go to **Tools > Security**. Here you'll get a short summary of what Monarx is doing. If you have a Startup plan or above, you'll see that Monarx is not just protecting you from malware, but also protecting your site with malware insurance.
If you want to see a detailed breakdown, you can click **Open Monarx**, which will bring you to a dashboard that shows the details of how Monarx is protecting your site.
## Learn More
To learn more about the Security area, see our knowledge base article on [security features in the Levamo Dashboard](https://support.levamo.com).
---
## Web Hosting vs Web Server: What's the Difference and Meaning?
- URL: https://levamo.com/blog/web-host-vs-web-server/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2024-02-19
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Web hosting vs server: Know the difference. Don't buy the wrong thing!
Imagine this scenario: you buy a brand-new car engine and you expect it to drive you to work. No seats, no wheels, no frame, just the engine sitting in your garage. That’s what it’s like confusing a web server with web hosting. One is the guts. The other is the entire vehicle that gets your website from point A to point B on the internet.
People mix hosting vs server all the time. And in the process, they buy the wrong thing, overpay, or worse, blame their tools when their site crashes on launch day. So let's fix that today.
But before you decide which will be the best choice for your online business between web host vs server, let's understand the meaning of both:
## What is the Difference Between Hosting and Server?
At first glance, " web hosting" and " web server" might seem interchangeable, but they refer to different aspects of making a website accessible online.
**Web Server**: This is the physical or virtual machine that stores your website's files and delivers them to users' browsers upon request. Think of it as the engine of the car in our analogy above.
**Web Hosting**: This is the service that provides the infrastructure, maintenance, and support to keep your website running on the web server. Think of it as the car's body and the steering wheel and dashboard etc.
Understanding this distinction helps in making informed decisions about setting up and maintaining a website.
Now, let's dive deeper into both web hosting and web server to understand them more deeply and their types and why it's important for you to know the difference. First, let's dig into web hosting, since that's what most users know and will have to care about while hosting their websites.
## What is a Web Host?

Web hosting is a service that allows individuals and organizations to make their websites accessible via the internet. [Hosting providers](/) offer the technology and support needed to store website files on web servers and ensure they're available to users around the clock.
There are many different types of web hosting providers that cater to different needs of a user. So let's understand the different web hosting types.
### Types of Web Hosting

Shared Web Hosting: Shared web hosting is a service where multiple websites are hosted on a single web server that is connected to the Internet. This is the most cost-effective hosting option as costs are spread out among many users, and the most common hosting type for small website with little to no traffic.
**VPS Hosting**: Virtual Private Server (VPS) hosting splits a server into different virtual servers, where each website is hosted on its own dedicated virtual server environment, offering better performance and customization than shared hosting.
**Dedicated Hosting**: Dedicated hosting provides a dedicated server for a single user or organization, providing maximum performance and control, but costs a lot.
**Cloud Hosting**: Cloud hosting uses a network of virtual servers that tap into an underlying network of interconnected physical web servers. This setup offers scalability and reliability, as resources can be adjusted based on demand.
**Grid Hosting**: Grid hosting involves distributing a website's hosting across a network of interconnected servers, ensuring improved load balancing and reliability.
**Managed Hosting for WordPress**: Managed hosting for WordPress is specifically optimized for WordPress websites, with the hosting company handling technical aspects like security, updates, and backups.
There are very few dedicated WordPress hosting providers out there, with [Levamo](/) as one of the best options which is highly optimized for WordPress websites.
**Cluster Hosting**: Cluster hosting uses multiple servers to host a single website, distributing the load among several machines. Example: Some enterprise-level hosting solutions offer cluster hosting to ensure website availability and scalability.
## Key Factors In Choosing a Fast Web Host Provider
Selecting the right web host is critical for the success of your website, impacting everything from user experience to security. Here are the key factors you must consider before choosing the web host:
### Better Disk Space or Storage Management
Your web host should provide sufficient storage to accommodate your website's content, including text, images, videos, and databases. As your site grows in popularity, its storage needs will increase, especially for media-rich sites.
While most small to medium websites won't exceed 1 GB of storage, it's essential to plan for future growth. Some hosts offer scalable storage options like Levamo, allowing you to increase capacity as needed. For example, a blog might initially require 700-800 MB, but a video-heavy site like YouTube consumes far more, highlighting the need for scalability.
### High Bandwidth Offering
Bandwidth affects your website's load times and its ability to handle traffic spikes. A site with high traffic volumes and heavy content needs more bandwidth to ensure smooth user experiences.
Estimate your bandwidth requirements by considering your daily visitor count, average page views, and average page size. Look for a web host that offers unlimited or high bandwidth limits to accommodate growth and prevent slowdowns during peak times.
### Take Care of Websites Security
With increasing cyber threats, your web host must prioritize security to protect your site from attacks and breaches. This includes safeguarding sensitive data and ensuring your website's integrity.
Search for web hosts offering comprehensive security features, such as [SSL certificates](/blog/fix-ssl-certificate-error/), regular malware scans, firewalls, and more. The best hosts incorporate multiple layers of security measures and are proactive in updating and maintaining their security protocols.
### Dependable Customer Support

Reliable customer support is essential for addressing technical problems and minimizing downtime. Quick and effective support ensures issues are resolved promptly, maintaining your website's performance and availability.
Evaluate the support channels offered (phone, email, chat, chatbots) and their availability (24/7 support is ideal). Assess the host's reputation for customer service through reviews and testimonials. A good support team can be the difference between a minor hiccup and extended downtime.
### Highest Rate of Uptime
Uptime is a measure of reliability, indicating how often your website is accessible to users. [High uptime rates](/blog/choosing-reliable-hosting-provider/) ensure that your site is available to visitors and customers around the clock, essential for maintaining credibility and maximizing engagement.
Aim for a web host that guarantees an uptime of 99% or higher. Some hosts offer uptime guarantees with compensation for downtime beyond agreed levels. Additionally, look for hosts with high-performance hardware and multiple data centers to mitigate the risk of significant outages.
### Automatic Backup
Regular backups protect your website against data loss due to hardware failure, hacking, or human error. An effective backup strategy is crucial for quick recovery after data loss incidents.
Choose a host that offers automatic daily backups, both onsite and offsite, allowing for easy restoration in case of data loss. Verify the ease of accessing and restoring backups, ensuring you can quickly revert to a previous version of your site if necessary.
## Why Choose Web Host over Web Server
Between web host vs web server, you will choose one for sure but on which basis? Let's check the crucial points.

**Cost-Efficiency:** Web hosting services spread their costs across many customers, making it more affordable than maintaining a dedicated web server.
**Technical Support:** Web hosts provide technical support, handling server-related issues, which is invaluable for users without technical expertise.
**Easy Management:** Web hosting companies offer control panels and tools that make website management simpler, even for beginners.
**High Security:** Professional web hosts implement top-notch security measures, including firewalls, malware scanning, and regular updates, to protect your website.
**Smooth Running Assurance:** Hosting providers ensure high uptime for your website, using redundant systems and backup power supplies to keep sites running smoothly.
**Scalability:** Web hosts allow easy scaling of resources (e.g., bandwidth, storage) to accommodate your site's growth, which can be challenging to manage on a personal server.
**Maintenance & Updates:** Web hosting services handle the maintenance and updates of the server hardware and software, reducing the workload on the website owner.
## What is a Web Server?

A web server is a system that delivers content or services to end users over the internet. It consists of both physical hardware that stores website data and software that handles requests via [protocols like HTTP. ](https://www.cloudflare.com/learning/ssl/what-is-https/)
When a user accesses a website, the web server processes the request and sends the relevant content back to the user's browser. This setup enables the hosting and viewing of web pages, images, videos, and other online content. Common web server software includes Apache and Nginx, each facilitating the dynamic delivery of web content to users worldwide.
## Different Types of Web Server
Each of these web servers offers unique advantages, catering to different hosting needs, programming languages, and performance requirements.
### Apache HTTP Server
Apache HTTP Server is a widely used open-source web server software, known for its flexibility and compatibility with various operating systems. It supports a range of modules for enhanced functionality.
- Highly customizable through modules.
- Supports various programming languages.
- Wide community support for troubleshooting.
### Nginx
Nginx is a [high-performance web server](https://www.nginx.com/) that also functions as a reverse proxy and load balancer, known for handling high volumes of concurrent connections with low resource consumption.
- Efficiently manages thousands of simultaneous connections.
- Offers high scalability and performance.
- Functions as a reverse proxy and load balancer.
### Microsoft Internet Information Services (IIS)
Microsoft IIS is a scalable web server software provided by Microsoft, integrated with Windows Server. It supports .NET and other Windows-based technologies, offering robust security features.
- Tight integration with Windows infrastructure.
- Supports .NET framework for web applications.
- Offers advanced security features.
### LiteSpeed Web Server
[LiteSpeed Web Server](/blog/lite-speed-hosting-benefits/) is a lightweight, high-performance web server, known for its speed and efficiency in serving static content, dynamic content, and accelerating data transfer.
- Optimizes speed for both static and dynamic content.
- Compatible with Apache configurations and .htaccess.
- Offers built-in security features.
### Tomcat
Apache Tomcat is an open-source web server and servlet container developed by the Apache Software Foundation. It implements Java Servlet and JavaServer Pages technologies, supporting Java applications.
- Dedicated to Java applications, supporting Servlet and JSP.
- Open-source with strong community support.
- Lightweight and flexible for Java web development.
## Things to Check on a Good Web Server
When evaluating a good web server, there are several key aspects to consider that ensure the server meets your needs for convenience, reliability, and performance. Here's what to look for:
### HTTP Protocol Support
A web server must offer robust support for HTTP/HTTPS protocols for secure and efficient data transfer between the server and clients. This foundational feature ensures your web content is accessible and securely delivered to users' browsers.
### Content Delivery

Look for a server capable of delivering a wide range of content types (HTML, images, videos, scripts) efficiently. It should also support dynamic content generation, seamlessly integrating with databases and application servers to serve personalized web pages.
### Security Features
A top-notch web server provides strong security measures, including SSL/TLS encryption for secure connections and configurations to safeguard against web vulnerabilities (SQL injection, XSS). Access control and authentication mechanisms are crucial for protecting sensitive areas of your website.
### Customization and Extensibility
The ability to customize server settings via configuration files and extend functionality through modules or plugins is vital. This flexibility allows for tailored server behavior, including custom error pages, URL rewrites, and enhanced performance or security features.
### Performance Optimization

Features that boost server and website performance, such as content caching, compression, and persistent connections, are key. These optimizations reduce load times and bandwidth usage, improving the user experience.
### Scalability and Load Balancing
For websites expecting high traffic volumes, the server's scalability and load-balancing capabilities are essential. They ensure the server infrastructure can distribute load effectively, preventing downtime and maintaining smooth performance during peak times.
## Why Choose a Web Server over a Web Host
In computation between web host vs web server, choosing a web server over a web hosting service can offer specific advantages. Particularly for businesses with unique or demanding online needs:
**Complete Control:** Operating your own web server provides full control over the server environment, allowing for custom configurations and installations tailored to your specific requirements.
**Custom Security Measures:** You can implement bespoke security protocols, firewalls, and encryption standards to meet your organization's security policies, offering a higher level of data protection.
**Optimized Performance:** By managing your own server, you can optimize hardware and software configurations for the best possible performance, ensuring faster load times and a smoother user experience for your website visitors.
**Reduced Costs Over Time:** For large-scale operations, investing in your own hardware and software might result in lower costs over time compared to recurring hosting fees, especially if you have the in-house expertise to manage the server environment.
**Exclusive Resource Use:** Unlike shared hosting environments, a dedicated web server ensures that your operations do not compete for resources with other users, leading to consistent performance and reliability.
## Which One Is Better for Your Online Business and Why?

Determining whether a web server (managing your own server) or a web host provided service is better for your online business depends on several factors, including your business's size, technical expertise, and specific needs. Here's a breakdown to guide your decision:
### Web Hosting Service: Ideal for Small to Medium-sized Businesses
**User-friendly Interface:** Web hosting services offer user-friendly control panels, making it easy to manage your website without deep technical knowledge.
**Cost-Effectiveness:** With a web hosting service, you avoid the upfront costs of hardware and software, making it a more affordable option for smaller businesses.
**Maintenance and Support:** Hosting providers handle server maintenance and offer support, reducing the need for a dedicated IT team.
### Web Server: Suited for Large Businesses or Those with Specialized Needs
**Customization and Control:** Operating your own web server offers unmatched control over your server environment, allowing for custom configurations that meet your specific requirements.
**Performance Optimization:** You can modify your server's hardware and software to optimize the performance of your websites and applications.
**Security:** With your own server, you can implement advanced security measures tailored to your business's needs, offering a higher level of protection for your data.
If your business lacks the IT expertise to manage a server or if you're looking to minimize costs while getting your online presence off the ground, a web hosting service is likely the better choice. It offers simplicity, cost savings, and adequate resources for most small to medium-sized businesses.
## Conclusion
Conversely, if your business has unique technical requirements, demands maximum control over its online environment, or experiences high traffic levels, investing in your own web server could be more beneficial. This option is best suited for larger businesses or those with the capability to manage the technical aspects of a server.
Ultimately, the decision hinges on balancing your business's specific needs, technical capabilities, and budgetary constraints. It's about choosing the path that aligns with your strategic objectives and offers the best platform for growth and success in the digital space.
## Frequently Asked Questions

### Can I host my website without a web hosting service?
Yes, it's possible by setting up your own web server, provided you have the necessary hardware, software, and technical expertise. However, this requires significant investment in resources and ongoing maintenance.
### What is the typical lifespan of a server?
The average lifespan of a physical server is about 3-5 years. Beyond this period, the risk of hardware failure increases, and it may become less cost-effective due to advances in technology and energy efficiency.
### How do you determine the best hosting providers for your needs?
To select top hosting providers, assess factors like uptime guarantees, customer support quality, scalability options, security measures, and the cost-to-feature ratio. Reading user reviews and testing their customer service can also provide valuable insights.
### Does web hosting mean having a server?
Yes, web hosting involves a server where your website's files are stored and accessed. However, the term "web hosting" usually refers to a service provided by a company that manages these servers, offering varying levels of access, maintenance, and support.
---
## Addressing Security Warnings: How to Fix 'Not Secure' Website in Chrome
- URL: https://levamo.com/blog/how-to-fix-https-not-secure-message-in-chrome/
- Category: website-security
- Author: Faisal Sarker
- Published: 2024-02-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Fix the Chrome "Not Secure" warning! Secure your site and protect visitors.
Have you ever opened your own site in Google Chrome only to see the unsettling "Not Secure" label appear? You certainly are not alone. That website not secure warning sign may feel like a red flag to anyone who visits your site; visitors may ask whether their private information is at risk or if they should continue.
But the good news is, getting rid of that warning isn't hard.
In this article, I'll discuss how to fix not secure website in Chrome, how that label affects you and your visitors, and how you can fix that problem.
Are you ready to tackle "the site you are trying to visit is not secure", and show your visitors that your website is safe and secure? Let's get started.
## What is 'Not Secure' Website in Chrome?
So, what does a "not secure" website mean? In Google Chrome, "Not Secure" means that the website you're visiting is not using the secure HTTPS protocol.
This HTTPS warning came about in July 2018 as part of Google's initiative to promote a more secure web. So in essence, "Chrome connection not secure" is a step to alert users that the website is without an HTTPS connection and warn them about potential security risks of the website. At the same time, it encourages site owners to adopt HTTPS encryption.
Learn how to [redirect HTTP to HTTPS here](/blog/redirect-http-to-https/).
In short, the **your connection to this site is not secure** Chrome error is primarily intended for non-HTTPS websites, especially those handling sensitive information, to warn users that the site you're trying to visit is not secure. It indicates that these sites lack encryption, potentially enabling unauthorized access, tampering, or data interception.

Secure HTTPS sites are identified by a lock icon on the left side of the web address to ensure encrypted communication. The "Not Secure" warning on websites doesn't mean there's malware, but it signals an unsafe connection.
It's like a caution sign when sharing sensitive information because it could be intercepted or altered by hackers, ISPs, or governments. This exact warning can lead to user confusion and negatively impact a website's bounce rate.
## Why Websites Show Chrome "Connection Not Secure" Error

The primary reason behind this error is the absence of an [SSL certificate](/blog/ssl-website-security/), but there are a few more.
### Missing SSL Certificate
One of the most common and primary reasons a website shows a "Not Secure" warning is the absence of an SSL (Secure Sockets Layer) certificate. This type of certificate encrypts the data exchanged between the user's browser and the website server to ensure the confidentiality of information. Without an SSL certificate, the connection is considered insecure, leading to a warning.
**Also Read:** [TLS vs SSL](/blog/tls-vs-ssl/)
### Presence of Mixed Content
When your website contains both secure (HTTPS) and non-secure (HTTP) elements, Chrome may display a "Not Secure" warning. It can happen when some resources like images, scripts, or style sheets are loaded over HTTP instead of HTTPS, potentially compromising the security of the page.
### Expired SSL Certificate
Even if a website initially had an SSL certificate, but it expired, the connection becomes insecure. The moment Chrome security identifies this, it will start displaying this warning to inform users of the potential risk.
### Insecure Password Fields
A website may have portions where it asks users to input sensitive information, such as passwords or credit card details, on an unsecured page (HTTP), which can trigger the "Not Secure" website warning.

### Insecure Third-party Content:
If a website includes content from third-party sources that is not secure, the warning can be triggered. It can happen from the embedded content, like ads and widgets, which are not served securely.
### Mixed Information Forms:
If a webpage with an HTTPS connection contains forms that submit data over HTTP, it can also start ringing a bell with this particular warning. Even if the home page and the primary focused page are in HTTPS, if user data submission is directed to an insecure page, the warning will appear.
## How to Fix Not Secure Website in Chrome
Now that you understand why the "Not Secure" warning appears on websites, it's essential to explore solutions to fix it. This "Not Secure" warning in Chrome actually indicates the absence of a secure HTTPS connection, which potentially risks users' security. Both website owners and end users can play a role in addressing this issue.

### Solutions for Website Owners to Fix 'Not Secure' Websites in Chrome
Website owners need to implement HTTPS, involving TLS/SSL certificates and server configuration.
So how to make your website support HTTPS? Here are some actionable solutions for you:
#### Solution 1: Use Hosting Providers that Offer SSL

Most of the top hosting providers like [Levamo](/) offer free SSL certificates. They also take care of the installation and renewal process. Transitioning to a hosting service that provides free SSL and assists with configuration can quickly make your website SSL-ready. When you get SSL on your website, the "Not Secure" warning of Chrome will be removed.
#### Solution 2: Use Free SSL from Let's Encrypt
[Let's Encrypt ](https://letsencrypt.org/)provides an easy and cost-free method to secure your website with HTTPS. This Certificate Authority offers automated SSL certificate issuance, supported by prominent organizations like Google, Mozilla, Facebook, and WordPress.com. Many WordPress-specialized hosting companies support Let's Encrypt, enabling you to obtain an SSL certificate instantly.
#### Solution 3: Consider Paid SSL Certificates
While free options are accessible, paid SSL certificates offer additional features, such as enhanced security guarantees and security seals. However, it's advisable to opt for paid SSL certificates only if your website requires these extra features. E-commerce sites, in particular, should consider paid SSL solutions like Organization Validation or Extended Validation to meet industry security standards. Some reputable paid SSL providers include Positive SSL, Rapid SSL, Symantec, GeoTrust, and EV SSL.
These are the focused solutions to get and implement SSL on your website as a site owner. After successfully [installing an SSL certificate](/blog/fix-ssl-certificate-error/), ensure that your website URLs are updated to reflect the new HTTPS address. This typically involves a search-and-replace operation for existing HTTP URLs. Additionally, consider implementing 301 redirects if URL changes occur. It's worth noting that Google has confirmed that 301 or 302 redirects from HTTP to HTTPS do not result in page rank loss, addressing potential SEO concerns.
Other than only SSL implementation, there are a few more fixes that you can check if your site shows 'Not Secure' from Chrome.
#### Solution 4: Regularly Update Content Management System (CMS) and Plugins

Always keep your Content Management System (CMS), such as [WordPress](https://wordpress.com/), Joomla, or Drupal, and all associated plugins and themes up to date. This is essential because security vulnerabilities are often discovered in older versions of software. For this particular issue, your site can show a ‘Not Secure' sign. Regular updates and patches close these vulnerabilities, making your site less susceptible to attacks and ensuring a secure environment for your users.
#### Solution 5: Enable HTTP Strict Transport Security (HSTS)
Add HTTP Strict Transport Security (HSTS) to your website. This server configuration enhancement forces all user connections to your site through HTTPS. It prevents users from accessing your site via an insecure HTTP connection. HSTS headers instruct browsers to automatically use HTTPS for all communications, enhancing the security of data in transit.
#### Solution 6: Use Content Delivery Networks (CDNs) with HTTPS Support
Employing [Content Delivery Networks](https://www.markuptrend.com/the-benefits-of-using-a-content-delivery-network/) (CDNs) that offer HTTPS support can make your site more secure in serving content. CDNs not only improve a website's loading times globally by serving content from locations closer to the user but also enhance security. If you enable CDN support it means that the content is encrypted, and it secures data transfer between your users and the CDN servers.
#### Solution 7: Implement Two-Factor Authentication (2FA)
The websites that manage user accounts must implement Two-Factor Authentication (2FA) to add an extra layer of security and also not get suspicious on Google's list, which may result in your site getting a Not Secure warning. 2FA requires users to provide two different authentication factors to verify themselves. This way, even if a user's credentials are compromised, unauthorized access to the account is significantly more challenging. 2FA acts as a deterrent against common cyber threats like phishing attacks and credential stuffing.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## What You Can Do as an End User About 'Not Secure' Websites in Chrome

### Avoid Doing Any Kind of Transactions on Unsecured Sites
Do not enter personal, financial, or sensitive information on websites that display the "Not Secure" warning. This includes logging in, filling out forms, or making payments.
### Check for “HTTPS” Manually
Sometimes, a website may support HTTPS but not default to it. Try changing the URL from "http://" to "https://" manually in the Chrome browser's address bar. If the site loads securely, then it's good to go.
Note that this doesn't guarantee security, as the site might still have vulnerabilities or improperly configured SSL certificates.
### Install Browser Extensions
Consider installing browser extensions that enhance security. For example, [HTTPS Everywhere](https://chrome.google.com/webstore/detail/https-somewhere/dapfmaempgppekcneleonmpoebhkfaol) can force your browser to use HTTPS when available, even if you've typed or clicked an HTTP link.
### Enable Enhanced Security Features
Chrome offers settings to increase security, including warnings about potentially risky sites or downloads. Check your browser's security settings to ensure they are set to a level you're comfortable with.

### Contact the Website Owner or Organization
If you need to use a website that is showing a “Not Secure” warning, consider contacting the site's owner or support team to inform them of the issue. Encourage them to adopt HTTPS by obtaining an SSL certificate.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## It's Your Time to Solve the ‘Not Secure’ Issue in Chrome
You already know how critical it is to respond to the "Not Secure" warning, both to protect your visitors' data and to keep your site okay with search engines. And by now, you also know how to fix not secure website in chrome.
From getting an SSL certificate to changing all your site links to HTTPS, every little thing you do puts that padlock in the address bar instead of that scary security alert.
For a hosting solution that takes the guesswork out of these steps, check out Levamo's [secure WordPress hosting](/managed-security/). It includes a built-in SSL certificate, automated security updates, and robust performance features. Overall, Levamo takes the hassle out of securing your site so you can focus on what matters most: providing an excellent experience for your users. Check our [cloud hosting prices](/blog/how-much-does-cloud-hosting-cost-2/).
**Also Read:** [Common Server Problems](/blog/common-server-problems/)
## Frequently Asked Questions

### What does the 'Not Secure' warning in Chrome mean?
This Chrome connection not secure warning appears when a website is accessed over an HTTP connection instead of HTTPS, indicating that the connection between the browser and the website is not encrypted.
### How can I switch my website from HTTP to HTTPS?
To switch to HTTPS, you need to obtain an SSL (Secure Socket Layer) certificate for your website, install it on your server, and update your website to use HTTPS URLs.
### How can end users protect themselves when browsing 'Not Secure' websites?
Users should avoid entering personal or sensitive information on non-HTTPS sites, use secure networks, and consider browser extensions that force HTTPS connections where possible.
### What should I do if my website shows a 'Not Secure' warning despite having an SSL certificate?
Ensure the SSL certificate is correctly installed and fully functional. Check for [mixed content](/blog/how-to-fix-mixed-content-issue-wordpress/) (HTTP resources on an HTTPS page), as it can also trigger the warning. You may need to update resource URLs to HTTPS or remove insecure links.
### Why is HTTPS important for my website?
HTTPS encrypts data between the visitor's browser and an owner's website, protecting sensitive information from being intercepted by attackers. It also boosts user trust and may contribute to higher search engine rankings.
### Can you fix your connection to this site is not secure Chrome error?
Absolutely, it's pretty easy to fix "your connection to this site is not secure chrome" error by just moving to HTTPS instead of HTTP.
---
## Say Hello to the Lite Plan
- URL: https://levamo.com/blog/lite-plans-are-now-available-to-purchase/
- Category: news
- Author: The Levamo Team
- Published: 2024-02-09
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo introduces the Lite plan for blogs, portfolios, and low-traffic sites.
## What's New?
We've introduced a scaled-back hosting option designed for those running promotional sites, blogs, portfolios, and low-traffic WordPress installations who don't require dynamic scaling capabilities.
## Key Features
- **Monthly Visits**: 200,000 estimated monthly visits capacity
- **Resources**: 1 vCPU, 2GB RAM, and up to 18 PHP workers
- **Security**: Firewall with DDoS protection
- **Malware Protection**: Automatic malware scanning and protection by Monarx
**Note**: Dynamic scaling is not available on Lite plans.
## How It Works
To purchase a Lite plan, you must maintain an active subscription at the Developer, Startup, Performance, or Enterprise tier. The Lite plan functions as an add-on to your existing subscription.
## Pricing
The Lite plan costs $35/month paid monthly or $29/month paid yearly (total of $348/year).
For more details, check out our support documentation for plan comparisons and subscription management instructions.
---
## Maximizing Site Success: Why is it Important to Use a Web Host
- URL: https://levamo.com/blog/importance-of-a-web-host/
- Category: hosting
- Author: Faisal Sarker
- Published: 2024-02-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
A great web host is key to site success. See why it matters for your website.
Have you ever wondered why selecting a web host is such a pivotal decision in the journey of creating a website? It might seem like just another step in the checklist of creating your dream website, but the truth is, your choice of web hosting service is fundamental to the success and reliability of your website.
Whether it's a vibrant blog, a sleek portfolio, or a bustling online store, the web host you choose not only houses your digital creation but also ensures it's accessible, secure, and fast for anyone who visits. The web hosting industry is scaling fast, and here’s a striking example of that:
> *[The global web hosting industry hit a staggering $108.54 billion in 2023.](https://www.fortunebusinessinsights.com/industry-reports/web-hosting-services-market-100863)*
Let's explore the crucial role a web host plays in the life and performance of your website, setting the stage for a deeper understanding of its indispensable value.
## Understanding What is Web Hosting?

When a website is created a lot of files need to be stored “somewhere” from where everyone can access those files. When you purchase certain space from website hosting providers, they will “host” your website's files on their servers. The amount you have to pay these hosting providers can be paid in monthly or yearly installments.
Let's make it clear with an example -
Imagine website hosting as an automobile fair. The whole area allotted for this fair is the web server maintained by the web hosting providers. Normal people have access to this fair as the route is created by the hosting companies. Each of the automobile display pavilions are websites that are full of various types of automobiles or in this case, pages and files of the website.
So in general to sell automobiles, you need to reserve a pavilion first, and when it comes to a website, you have to host it via a reliable hosting provider.
Now that you know how websites are hosted, you get an idea about why it is important to use one, but you also need to have a basic idea of the types of hosting services.
## Different Types of Website Hosting

Web hosting can be categorized into various categories and subcategories. Four of the main hosting types are -
### Shared Hosting:
One of the most common and inexpensive types of hosting is shared hosting. As you know, websites need to be hosted on a web server, when multiple websites get hosted on the same server it's called shared hosting.
Shared website hosting is most suitable for personal websites, small businesses and start-ups, etc.
### Dedicated Hosting:
Dedicated hosting is just an alternative to shared hosting. From the name, you understand here that each website has its own hosting server. Dedicated hosting definitely has more options and benefits than shared hosting. But it's more expensive too.
Mostly medium to larger businesses, e-commerce sites and professional support-type websites are suitable for dedicated hosting.
### VPS (Virtual Private Server) Hosting:
VPS (Virtual Private Server) is a hybrid hosting service that stands in the middle point between shared web hosting and dedicated web hosting. In this type of hosting facility, all the hosted websites share the same physical server space, but each of them has their own independent virtual space.
In a more simplified way, VPS website hosting virtually represents the environment of a dedicated server within a shared server.
### Cloud Hosting:
In the era of [cloud-based services hosting](/blog/how-much-does-cloud-hosting-cost-2/) providers also scaled up from the traditional concept of renting space from one physical server. A cloud server hosts a website via a network of connected virtual and physical cloud servers. These types of servers are not only providing greater reliability for the hosted server. This type of web server is also renowned for better flexibility, scalability, and security.
With the right setup, businesses can also [optimize cloud costs](https://cloudchipr.com/blog/cloud-cost-optimization) while maintaining performance and reliability.
## What Qualities You Need to Check on a Web Host?

When venturing into the vast digital landscape, your choice of a web host can significantly influence your website's performance, reliability, and user experience. Here are some essential qualities and factors to consider when choosing a web hosting provider:
Here, we will discuss some [essential features of web hosts ](/#dynamic)that you must look for if you want to boost your site's potential.
### Search for “Real” Bandwidth Limit
Bandwidth means the capacity of your website to accommodate traffic and the number of page views each month. You can choose specific bandwidth from your hosting providers as the charge varies based on that. But it's important to note that in cases of sudden, significant traffic spikes for example, during holiday sales or if a blog post becomes highly popular - your site could face slowdowns or even go offline if it does not have proper bandwidth.
So before selecting a website hosting provider, especially shared hosting, look for the packages properly. It may mention unlimited bandwidth, but this 'unlimited' may have its limits. Typically, a website on a basic shared hosting plan can manage around 30,000 visitors per month before experiencing slower loading times and reduced performance. If your site reaches this level of traffic, it's high time to consider upgrading to a more advanced hosting package.
To gain a deeper understanding of these SEO factors and related terminology, it can also be useful to familiarize yourself with an [SEO glossary](https://saynine.ai/seo-glossary/).
**You can also read -** **[WordPress Speed Optimization](/blog/fast-server-speed-tools/)**
### Estimate Your Desired Storage
Storage limits differ among hosting packages, but they are generally less complicated than bandwidth limits. Unless you intend to store numerous high-resolution videos, store a large volume of user information, or operate a large-scale e-commerce site, a modest storage plan from your hosting provider should suffice.
Your site should operate smoothly within your chosen storage capacity provided by the web hosts unless you excessively increase the content on your website.
### Look for a Proper Site Management Dashboard
When choosing a hosting provider, it's crucial to think about both your current needs and future growth. To boost your site's potential, proper site management is essential. You may start with hosting for a single site, but in the future, you might need to register multiple domains or set up subdomains under a main site. These tasks require a dashboard that facilitates easy management of your websites.
Therefore, before committing to any web host, ensure that their service allows the inclusion of [multiple domains in a single hosting account.](https://hostadvice.com/blog/domains/multiple-domains-on-one-server/) Often, hosting packages may restrict you to using a single domain. It's advisable to select a hosting provider that offers the ability to add multiple domains and provides a website management tool with a user-friendly interface.
### Make Sure about the offering of Professional Email Addresses
Web hosting companies often offer an email hosting feature, allowing you to create professional email addresses using your own domain name, such as info@yourwebsitename.com.
Having such a professional email address enhances your brand image and lends a unique credibility to your business. Therefore, when selecting a web host that can boost your site's potential, ensure that they also offer email services.
### Evaluate Average Uptime and Response Rate if the Site Gets Down
One of the least desirable scenarios for any [website is unexpected downtime](/blog/wordpress-site-down-common-issues-and-fixes/), making the site inaccessible to users. This not only disrupts user experience but also negatively impacts the site's SEO. No duration of downtime is acceptable. In a reliable web hosting provider, you should seek an [average uptime ](/blog/choosing-reliable-hosting-provider/)of at least 99%.
Additionally, it's important to consider their response services. When your site goes down for any reason, how quickly the hosting provider can restore it to live status is a crucial factor to evaluate.
### Find Who Offers Accurate Price with No Hidden Charges
The cost of hosting can naturally increase over time, especially if you don't purchase multi-year packages upfront. However, renewal or installment charges can sometimes be unexpectedly high due to hidden fees. It's important to sign up with hosting providers who offer clear pricing and transparent terms.
This way, you can make informed decisions about which package to choose and anticipate any potential price increases.
### Keep the Option to Scale Up
As your site grows with time and attracts more traffic, your needs from a web host service provider will change. You might find yourself needing to migrate from a shared hosting plan to a specialized WordPress hosting or a cloud hosting service.
So while choosing a website host, ensure they offer scalable packages. This means they provide options for users to upgrade from one hosting plan to another. As a paid user you always have the option to switch hosting providers, it's much more convenient to select a host that can accommodate your long-term needs.
### Get Sure About Customer Support
Before settling on a hosting provider, it's wise to test their support system. You can do this by submitting a question or two and assessing whether their support process meets your expectations. For instance, some web hosting companies provide support exclusively through email or ticketing systems, while others offer live chat or phone support.
It's crucial to ensure that the company you're considering for your website's hosting can deliver the level of support you need when you need it.
## How Choosing the Right Web Host Can Boost Your Site’s Potential?
Just choosing a website host does not make your website become recognized, but choosing the right one can help you boost your site’s potential.
### Boost Site Performance and SEO:

A website’s loading speeds and search engine rankings and interrelated. Slow-loading sites can result in high bounce rates and poor user experience, adversely affecting SEO. While factors like site design or excessive plugins can contribute to sluggish performance, the hosting service often plays a significant role. If your optimized site still underperforms, it might indicate the need to switch to a more capable host or upgrade your hosting package.
### Remain Trustworthy with High-Class Security:

Imagine being a web development course owner and your website faces security issues becuase of not using great [LMS hosting services](/managed-lms-hosting/). How would students trust you? That's why it's always important to pick a hosting with good security measures in place.
Strong security provided by web hosts is crucial for preventing data breaches and hacking. Affordable hosting plans should still offer key security features like malware protection, [SSL certificates](/blog/fix-ssl-certificate-error/), and effective firewalls. There's no perfect security solution, but combining these hosting features with actions like regular updates and using security plugins greatly strengthens your website's defenses.
This approach not only keeps your site safe but also boosts its credibility and trustworthiness with users, which is essential for its potential. The host's commitment to high-quality security is like having a thorough, easy-to-use security system for your online presence, creating a secure and dependable environment for your website's growth and success.
### Minimize the Loss of Sales:

The uninterrupted uptime of your website is intrinsically linked to the success of your online business, especially in generating leads or sales. The right web hosting provider should guarantee an [uptime of 99.9%](https://uptime.is/), ensuring that your website is consistently available to users. Frequent downtime, unless caused by factors within the site owner's control, is a clear indicator that a more robust hosting package or a switch to a more dependable host is necessary.
This aspect is particularly crucial for e-commerce websites, where every minute of downtime can result in significant revenue loss. Choosing the [best hosting provider for WooCommerce](/managed-woocommerce-hosting/) minimizes these disruptions, directly contributing to the website's potential to attract and retain customers. Moreover, consistent uptime is vital for maintaining customer trust and satisfaction, which are key drivers of repeat business and positive word-of-mouth.
## Web Hosting Selection Tips for New Users

### Sort out Your Website's Specific Needs
Take time to evaluate what your website truly requires in terms of traffic handling, storage capacity, software compatibility, and security measures. This will help you zero in on a hosting plan that fits perfectly.
### Search and Analyze Hosting Providers
Dive into user reviews, weigh up the different features, and ponder the overall standing and trustworthiness of various hosting providers. This due diligence is key in making an informed choice.
### Get Proper Knowledge of the Types of Hosting Available
Make an effort to understand the array of hosting solutions out there, ranging from shared to cloud hosting, and pick one that suits both your current requirements and potential future expansion.
### Focus on Support Quality and User Feedback
Place a high emphasis on accessible and efficient customer support. Seek out and consider feedback from current users to get a sense of their experiences and level of satisfaction.
### Try Out Some Hosting Service First
Many hosting services provide a trial run or a refund policy. Use these opportunities to thoroughly test the hosting service, paying special attention to its performance and the quality of support provided.
## Final Words
Deciding on the right web hosting is a vital step for your website. Instead of just picking the cheapest option, take the time to research and find the best fit for your needs. While you can always switch hosts later, choosing wisely the first time is easier and helps you make the most of your website's potential. This careful choice sets the foundation for your site's success.
## Frequently Asked Questions

### What is web hosting and why is it essential for a website?
Web hosting is a service that allows your website to be stored and accessible on the internet. It's essential because, without it, you cannot store your website data somewhere everyone can access it.
### How does choosing the right web host impact my site's performance?
The right web host can improve site speed, ensure high uptime, and enhance the overall user experience.
### Is it worth paying more for premium hosting services?
Premium hosting often offers better performance, security, and features, which can be worth the extra cost, especially for larger sites.
### How often should I review and potentially change my web hosting?
Regularly review your hosting needs, especially when your site grows or changes, to determine if a switch is necessary.
---
## Levamo Beta: Mission Accomplished and Ready for Launch
- URL: https://levamo.com/blog/rapyd-is-officially-out-of-beta/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo exits beta after months of user feedback and real-world testing.
> *Note: This post was originally published January 2024 as "Rapyd Beta: Mission Accomplished and Ready for Launch" when our platform was called Rapyd Cloud. We've since rebranded to Levamo. The product details below remain accurate - only the brand name has changed.*
## The Levamo Beta Journey
Levamo originated from real challenges BuddyBoss users faced. They were caught in three difficult situations:
1. **The DIY Dilemma**: Building and managing complex server infrastructure required significant technical expertise, or outsourcing proved costly.
2. **Expensive Hosting**: Available hosts offered marginally better performance for BuddyBoss sites but remained inadequate and overpriced.
3. **Live with a Slow Site**: Users often accepted slow speeds, negatively impacting user experience and growth.
Levamo was built specifically for performance-demanding platforms. While initially designed for BuddyBoss, the team recognized similar challenges across e-commerce, e-learning, and membership sites. The product tackles traditional hosting limitations to deliver consistently fast experiences.
## You Spoke, We Listened: How the Beta Shaped Levamo
Beta feedback proved instrumental across multiple areas:
- **Internal Processes**: Streamlined for faster customer communication
- **Dashboard Design**: Revamped for a more intuitive experience
- **Feature Prioritization**: Based on actual user needs rather than assumptions
- **Support Team**: Strengthened through diverse customer interactions
## What Testers Are Saying About Levamo
The platform's core strength lies in infrastructure that dynamically scales and adjusts to your site's needs in real time. This enables sites to handle traffic spikes seamlessly.
Additional features like Object Cache Pro and Relay optimize WordPress performance further. The support team actively resolves issues to maximize platform value.
## Ready to Take Your Site to the Next Level?
Our roadmap includes enhanced backup management, the Levamo CDN, and transactional email add-ons. Visit [levamo.com](/) to sign up and take advantage of our Early Bird Sale with exclusive benefits while availability lasts.
---
## We've Just Made Managing Your Levamo Subscription Almost Too Easy
- URL: https://levamo.com/blog/manage-your-subscription-from-the-dashboard/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Pause and cancel subscriptions directly from the Levamo dashboard.
Say goodbye to reaching out to our support team every time you want to make a change to your Levamo subscriptions. Now *you* have the power.
## What's New
We've added the ability for billing managers to pause and cancel subscriptions directly from the dashboard.
### Pause Subscription
You can pause your subscription for up to 6 months. When you restart, your billing date resets based on the pause duration. Multiple pauses are permitted as long as your total pause time remains under 6 months. This applies to both monthly and yearly subscriptions.
### Cancel Subscription
We understand cancellations happen. If you do decide to cancel, we'd love to hear your feedback at success@levamo.com.
## How It Works
1. Navigate to the **Billing** area of the dashboard
2. Select the subscription you want to manage
3. Click the **Manage** button at the top left
This opens a modal that guides you through the process.
**Important**: Subscriptions cannot have active sites to be paused or cancelled.
## Helpful Resources
- How to Download a Site Backup
- How to Delete a Site
- How to Pause a Subscription
- How to Cancel a Subscription
---
## Our Support Plans Are Live and Ready to Help You Reach True Peace of Mind
- URL: https://levamo.com/blog/manage-support-plans-from-the-dashboard/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-30
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Premium support plan add-ons are now available in the Levamo dashboard.
## What's New?
Support plan add-ons are now available for purchase. The Enhanced and Elite support plans offer premium benefits including:
- Improved SLAs
- Deeper levels of troubleshooting
- Dedicated account manager
- Dedicated Slack Channel (Elite only)
These features enable deeper support access for managing your website, though the team remains committed to providing excellent support at all levels.
## How It Works
The support add-on can be purchased in the **Billing** area of the dashboard. Navigate to **Billing > Support plan > Upgrade** to get started.
**Foundation Support** is included for free with every Levamo account.
**Enhanced Support** ($100/month) is offered free of charge for:
- All Performance Plans
- Enterprise Level 1 and 2
**Elite Support** ($500/month) is offered free of charge for:
- Enterprise Level 3, 4, and 5
Support plans require a minimum 6-month commitment. For questions about which plan is right for you, contact success@levamo.com.
## Learn More
See our knowledge base article "Understanding Levamo's Support Plans" for additional information.
---
## Remove Unwanted Plans Quickly and Easily
- URL: https://levamo.com/blog/new-feature-to-remove-plans-from-the-dashboard/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-26
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
You can now remove plans from subscriptions directly in the dashboard.
We've added a new feature that simplifies subscription management. You can now remove plans from your subscriptions directly in the Levamo dashboard, without contacting support.
## What's New?
Plan removal is now available directly within the Billing section of the Levamo dashboard.
## How It Works
Before removing a plan, make sure it has no active site associations. To remove a plan:
1. Navigate to **Billing > View subscription**
2. Review which plans have sites assigned
3. Click the **Remove plan** icon on the far right to proceed with removal
## Learn More
Check out our knowledge base article "How to Remove a Plan from a Levamo Subscription" for step-by-step instructions.
---
## Take Complete Control Over Your Backups with Our Dashboard's New Backups Area
- URL: https://levamo.com/blog/backup-management-is-now-live/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-26
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Manage backup schedules, create manual backups, and download from the dashboard.
We're excited to introduce a dedicated Backups section in the Levamo dashboard. Previously, the platform provided daily backups automatically but lacked user controls for scheduling, manual creation, downloads, and restoration. The new Backups area addresses all of those gaps and puts you in the driver's seat.
## What's New?
### Backup Schedule
You can now adjust the timing of your automatic daily backups. Schedule your site's backups during off-peak times to reduce load on your server and ensure they run when traffic is lowest.
### Last Performed
The interface now displays when the most recent site backup was completed, so you always know the state of your latest backup at a glance.
### Backup Storage
Backups are stored off-site without impacting your disk space. The system uses incremental backups: the initial backup stores a copy of your entire site, then each subsequent backup only records changes. This keeps storage efficient while maintaining full restore capability.
### Create Manual Backups
You can now generate backups on-demand whenever you need them. Creating a manual backup before making any major changes to your website is a best practice that gives you a reliable rollback point.
### Download Backups
Need a local copy? You can now generate download links for your off-site backups. Download links remain active for 24 hours, giving you plenty of time to save a copy to your own storage.
### Restore Backup
The restore option is visible in the interface and will be fully enabled soon. In the meantime, if you need to restore a backup, please reach out to our support team and we'll handle it for you.
## Learn More
For additional details on how the backup system works, check out our knowledge base article in the support portal.
---
## Upgrade and Downgrade Your Plans with Our New Edit Plan Feature
- URL: https://levamo.com/blog/you-can-now-edit-plans-from-the-dashboard/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-17
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Edit your hosting plan directly from the dashboard. No support needed.
We're thrilled to introduce the new "Edit plan" feature, giving you enhanced flexibility to upgrade and downgrade your plans directly from the dashboard, without needing to contact our support team.
## What's New?
The dashboard now lets you edit your plan whenever you need to. Whether you're upgrading to a larger tier before a big launch, scaling back down afterward, or simply transitioning between plan levels, you can manage it all independently through the dashboard.
## How It Works
To get started, navigate to **Billing > View subscription** and click the pen icon to begin editing. A modal window will appear where you can select your new plan tier and level, along with descriptions of each option to help you decide.
The same modal also displays add-on details. While add-ons aren't yet available for selection, they will be enabled soon.
## Important Downgrade Limitation
**Cross-tier downgrades are not permitted.** You cannot downgrade between different plan tiers (for example, from Startup to Developer or Performance to Startup) due to disk space technical constraints. If you need a cross-tier downgrade, please contact our support team for assistance.
## Learn More
For additional information, check out our knowledge base article on upgrading and downgrading plans.
---
## We've Released Updates to Team Management: Guest User Roles and Team Visibility
- URL: https://levamo.com/blog/new-guest-user-role-added-in-teams/
- Category: news
- Author: The Levamo Team
- Published: 2024-01-05
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
New Guest role and team visibility controls for better access management.
We've introduced more granular control when inviting team members to your Levamo account. This update brings a new Guest user role and improved team visibility for Admins and Billing managers.
## What's New?
### Guest User Role
A new Guest access level provides the most restricted account access. Guests cannot view the Team tab in the main menu and can only see sites they've been specifically granted access to. As an administrator, you can also decide whether guests receive access to the Levamo support widget.
### See Team Members
Administrator and Billing Manager roles can now view all team members within the Team section of the dashboard. This gives managers a complete picture of who has access to the account and at what level.
## How It Works
Administrators can invite Guests by navigating to **Team > Invite people** and selecting the Guest role. Guest permissions regarding site access and support access are configurable during the invitation process. You can also adjust these settings later by selecting the three-dot menu next to a Guest user and choosing "Edit role."
## Learn More
For additional information about team management, check out our support documentation article on navigating the Team section on the Levamo Dashboard.
---
## Billing Boost: Enhanced Layout, Multiple Subscriptions, and Clear Plans
- URL: https://levamo.com/blog/new-feature-to-purchase-multiple-subscriptions/
- Category: news
- Author: The Levamo Team
- Published: 2023-12-20
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Redesigned billing with multiple subscriptions and clearer plan details.
We've made a number of improvements to viewing billing information in the dashboard. From a refreshed layout to the ability to manage multiple subscriptions, these changes make it easier than ever to stay on top of your account.
## What's New?
### New Billing Layout
The billing section has received a redesigned interface to streamline access to key financial data. You'll now see improved account balance visibility, next invoice due dates, and a cleaner subscription management view.
### Multiple Subscriptions
You can now purchase and manage multiple subscriptions within a single Levamo account. This is especially useful if you operate multiple client websites on the platform, as it enables better organizational flexibility. Each subscription supports its own payment method, giving you enhanced control over how your sites are managed and billed.
### Rename Subscriptions
Subscription names are now customizable. Simply click on any subscription name to modify it according to your preferences. This makes it easy to keep things organized when managing several subscriptions at once.
### Site Plan on Overview Page
A new billing plan line item now appears on the site overview section. This eliminates the need to navigate between different areas just to confirm which plan a site is associated with.
## Learn More
For additional guidance, check out the Subscription Management knowledge base collection for everything you need to know about managing subscriptions within Levamo.
---
## Save Time and Clicks with Our Rebuild Staging Feature
- URL: https://levamo.com/blog/new-feature-to-quickly-redeploy-your-staging-environment/
- Category: news
- Author: The Levamo Team
- Published: 2023-12-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Rebuild your staging site from production with a single click.
We've released the Rebuild Staging tool, designed to streamline the process of updating your staging site with the most recent copy of your production site.
## What's New?
You can now rebuild a staging site with a single click. Located at the bottom of the overview section of your staging site, the **Rebuild** button copies the latest version of your production site into your staging environment.
This makes it simple to test plugins, edits, and new content before deploying anything to your live environment. Instead of manually recreating your staging site each time you need a fresh copy, just hit Rebuild and you're ready to go.
---
## Test Updates, Content Edits, and Design Changes in a Safe Place with Our New Staging Feature
- URL: https://levamo.com/blog/new-feature-to-add-staging-sites/
- Category: news
- Author: The Levamo Team
- Published: 2023-11-23
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Safely test site changes before going live with our new staging feature.
Levamo has launched its first version of a staging feature, enabling developers to test site edits before making them on your live site.
## What's New
The staging feature allows creation of a dedicated staging site to safely test any site updates before implementing changes on the production environment.
## How It Works
### Creating a Staging Site
- Access the dashboard and click the **Production** tab dropdown
- Select **Create staging** option
- Build process takes approximately 10 minutes
- Once built, test edits and updates before deploying to live site
### Staging Site Specifications
- Same specs as Developer plan: 1 vCPU, 2GB RAM, 18 PHP workers
- Disk space matches the production site plan (e.g., 150GB for Performance plan)
### Current Limitations
- Cannot pull from production to staging with one click
- To refresh staging, delete the site and rebuild following the creation process
- Quick rebuild tool coming soon to replace manual process
- Custom domains not supported on staging sites
- Staging sites lack dedicated IP addresses
## Additional Resources
For detailed instructions, see the support article: [How to Add and Use Staging Sites Using Levamo](https://support.levamo.com/en/articles/8650798-how-to-add-and-use-staging-sites-using-rapyd).
---
## For Those Fans of Google Pay, Levamo Now Supports It
- URL: https://levamo.com/blog/added-support-for-google-pay/
- Category: news
- Author: The Levamo Team
- Published: 2023-11-22
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Google Pay is now a supported payment method for Levamo subscriptions.
We'll keep this update short and sweet.
Google Pay is now a supported payment method for purchasing subscriptions and plans.
To use Google Pay, you must be using the Chrome browser and Google Pay needs to be configured as a payment method in your browser. If you're unsure about how to do that, check out the [Google Pay website](https://pay.google.com/about/) for more information.
---
## Introducing Two Big Billing Features: Apple Pay and Edit Payment Method
- URL: https://levamo.com/blog/added-support-for-apple-pay/
- Category: news
- Author: The Levamo Team
- Published: 2023-11-16
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo now supports Apple Pay and lets you edit your payment method.
Levamo now supports Apple Pay for monthly and yearly subscriptions, and you can now edit your payment method from the **Billing** area of the Levamo dashboard.
## What's New?
### Apple Pay
You can now pay for Levamo services with Apple Pay. At this time, this feature only works in Safari, and it cannot be used in a private window.
### Edit Your Payment Method
You can now edit the payment method for a subscription in the Levamo dashboard. Go to the **Billing** section of the dashboard and click on the pencil icon. This will open a modal window that allows you to update your payment details.
---
## How To Do Website Design in WordPress
- URL: https://levamo.com/blog/website-design-in-wordpress/
- Category: website-design
- Author: Faisal Sarker
- Published: 2023-11-14
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Make amazing websites! Design tips and WordPress insights await you.
WordPress is a favorite tool for many to create websites due to its easy-to-use features and lots of design options. As of 2022, WordPress is the engine behind a huge 43.2% of all websites on the internet, showing a big jump from 39.5% just a year before[1](https://blog.hubspot.com/website/wordpress-stats#:~:text=According%20to%20data%20from%20W3Techs%2C,%28W3Techs%2C%202022).
In this guide, we'll explore how to create great web designs in WordPress, understand the important relationship between web design and reliable web hosting, and learn how to make your WordPress site shine among others. Stay with us as we unveil how you can create attractive, easy-to-use, and well-hosted WordPress websites, and why these three elements are a must in today’s digital world!
## Importance of Web Design in WordPress
Web design is like dressing up your website. It's about choosing the right colors, layout, and features that make your website not only look good but also easy to move around. WordPress is a place that gives you tons of options to play dress-up with your website. Imagine having a wardrobe full of outfits and accessories; WordPress is that wardrobe for your website. And the way you dress up your website can make visitors want to stay and explore or leave and never return.
## Connection between Web Design and Reliable Web Hosting
Now, no matter how well you dress up, if the party venue isn’t good, it’s a buzzkill, right? That’s what web hosting is - the venue for your website party. Reliable web hosting ensures that your website is always ready to welcome visitors, runs smoothly, and loads pages quickly. So, the design attracts visitors, and the hosting makes sure they have a good time.
## Choosing the Right Web Hosting for WordPress
### Evaluating Web Hosting on WordPress
When looking for a good neighborhood, you check for safety, amenities, and how well-maintained it is, right? Similarly, evaluating web hosting for WordPress is about checking how fast pages load, how often the hosting service is available (you don’t want a ‘closed’ sign hanging on your website), and how secure it is from online threats. It's about making sure the hosting service can handle the traffic to your website, especially on days when there are a lot of visitors. You should also consider using a purpose-built hosting, like a [WooCommerce managed hosting](/managed-woocommerce-hosting/) if you plan to build WooCommerce sites.
### Benefits of Reliable Web Hosting for Web Design
A good web hosting service is like having a reliable power supply. It ensures that all the design elements on your website are displayed correctly and promptly. When your website loads fast and is available whenever needed, visitors have a better experience. They can easily move around and explore what you have to offer. Moreover, a reliable hosting service also means that you can make updates or changes to your website design without a hitch, keeping your online space fresh and up-to-date.
Through these sections, we'll understand why choosing the [best managed WordPress hosting](/managed-wordpress-hosting/) service is crucial for your site and how it complements your web design efforts. It’s about making sure that the pretty dress (web design) you put on your website shines brightly at the party (the internet) and doesn’t get ruined because of a bad venue (poor web hosting).
## Getting Started with Web Design in WordPress
### Setting up WordPress

Setting up WordPress is like assembling a new toy; you follow some instructions, and in a few steps, you have something ready to play with. First, you'll need a name for your website (this is called a domain name, like yourhouse.com) and a place on the internet to keep your website (this is called hosting, think of it as renting a plot of land). Once you have these, you [install WordPress](https://wordpress.org/download/), which is free and straightforward. It's like setting up a new phone; you press a few buttons, wait for it to install, and voila, you have a fresh new WordPress website ready to be designed.
### Selection of a Suitable WordPress Theme

Now that you have your WordPress set up, it's time to make it look nice. WordPress has something called themes, which are like different styles or outfits for your website. Selecting a suitable theme is like choosing the right outfit for an occasion. You want something that looks good and fits well with what you want to do with your website. For instance, if you're going to have a blog, you'd choose a theme that displays your posts in an appealing way. Or if you're setting up an online store, you'd pick a theme that showcases your products nicely. There are thousands of themes available, both free and paid, so you can browse, try on different themes, and pick the one that suits your website the best.
Through these steps, you're laying down the first bricks of your website's structure and appearance. It's all about making a solid start with a clean WordPress setup and a theme that resonates with your website’s purpose. So, it's a blend of technical setup and creative selection to kickstart your website-building journey on WordPress.
## Web Design Fundamentals for WordPress
Web design in WordPress is like painting a picture, but instead of a canvas, you have a webpage. It's about arranging various elements like buttons, images, and text in a way that's both good-looking and easy for visitors to use.
### Understanding WordPress Interface

The WordPress interface is like the control room for your website. It’s where you can create new pages, write posts, change how your website looks, and much more. It's like having a dashboard in your car with different buttons to control various features. Getting to know this interface is the first step toward making your website look the way you want.
### Front-End WordPress Basics
The front end is what people see when they visit your website. It’s like the front of a store, where all the products are displayed. In WordPress, you control the front end by choosing themes and customizing them to your liking. It's about making your website look neat, attractive, and easy for visitors to find what they’re looking for.
### Website Design Questions to Consider
Before diving into designing your website, it's good to ask some questions. What do you want your website to do? Who will visit your website? What should they feel when they land on your website? It's like planning a party; you need to know the occasion, who’s coming, and the vibe you want to create. Answering these questions helps you make better design choices, ensuring your website does what you want it to do and appeals to your visitors. Plus, when diving into designing your website, considering professional [web design services](https://www.chromatix.com.au/services/wordpress/) can streamline the process and elevate your online presence.
Through these sections, you'll get a good grasp of how to navigate WordPress and start shaping your website. It’s about understanding the workspace, getting the basics right, and having a clear idea of what you want to achieve with your website design. This foundation will help you as you move forward in creating a website that not only looks good but also functions well.
## Theme Customization and Creation
Themes are like the outfits of your website. They determine how your site looks to the visitors. Just like you might tweak a dress or a suit to fit you better, you can tweak themes to fit your website’s style and needs.
### Customizing Existing WordPress Themes

WordPress has a bunch of pre-made themes, kind of like ready-to-wear outfits. You can choose one that you like and then tweak it to fit your style. You might change the colors, the fonts, or how the menus look. It’s like adding your personal touch to make it just right.
### WordPress Theme Creation from Scratch
Creating a theme from scratch in WordPress is like sewing your own outfit. It’s for those who have specific ideas and the skills to bring them to life. You start with a blank slate and build up, choosing every color, font, and layout. It’s a bit more advanced but gives you total control over how your website looks.
### Enhancing Web Design with Plugins and Widgets
Think of your website as a smartphone. Just like you can download apps to add new features to your phone, in WordPress, you can use plugins and widgets to add new features to your website. They help in making your site more useful and easier to navigate.
### Essential Plugins for Web Design in WordPress
Plugins are like magic tools for your website. They can help you do almost anything, from making your site look good, to adding new features like a contact form or a photo gallery. It's like having a toolbox where each tool helps you do something different on your site. Some essential plugins help with designing your site, like ones that help you build beautiful pages or ensure your site looks good on mobile phones.
The image below shows the Elementor plugin that allows you to design your WordPress website. But you can consider using other plugins such as Happy Addons, Essential Addons, and so on.

### Utilizing Widgets for Enhanced Functionality
Widgets are small blocks that perform specific functions on your site, like showing your latest posts or a search bar. It's like having mini-apps that you can place in different parts of your site. They help in adding handy features without needing to know how to code. You just drag and drop them where you want, and voila, your site has new features! You will be able to make widgets when you add a web design plugin such as [Elementor review](/blog/elementor-review/).
Below is an example of the Elementor page with widgets to design your WordPress website without writing a single line of code.

Through these additions, you can make your website more functional and user-friendly. It's about picking the right plugins and widgets that align with your site’s design and what you want to offer to your visitors. They are like the extra toppings that make a good site great!
## Advanced Web Development on WordPress
As you get more comfortable with WordPress, you might want to do more advanced stuff on your website, kind of like going from riding a bike to driving a car. Advanced web development lets you do more complex things to make your website fit your vision perfectly.
### Introduction to Custom Coding in WordPress
Custom coding is like knowing how to cook from scratch instead of using pre-made ingredients. It allows you to add your own special touch to the website. You can write lines of code to change how things look or work on your site. It’s a bit technical, but once you get the hang of it, you can make your website do pretty much anything you want.
### Exploring Advanced Plugins and Page Builders
Advanced plugins and page builders are like having a set of power tools for your website. They let you create complex layouts and add cool features without needing to know a lot of coding. It's about using special tools that make designing pages easier and more creative. You can drag and drop different elements, arrange them how you want, and create beautiful, professional-looking pages.
Through these advanced steps, you'll be diving deeper into what you can do with WordPress. It's about moving beyond the basics, getting a bit technical, and making your website look and work exactly how you want. It's a journey into the heart of WordPress, discovering the powerful tools and options waiting for you.
## Responsive and Mobile Design in WordPress

### Importance of Responsive Web Design
Responsive design is like having clothes that fit you well, whether you're standing up or sitting down. Similarly, a responsive design ensures your website looks good and is easy to use, no matter what device someone is viewing it on. It adjusts to the screen size, so everything remains readable and clickable. Simply, it makes your website friendly for both computer and mobile users.
### Implementing Mobile-First Design in WordPress

Mobile-first design is about creating your website with mobile users in mind from the get-go. It's like designing a park with enough pathways for both walkers and bikers. Since a lot of people use their phones to browse the web, a mobile-first design ensures your site looks great and works well on smaller screens. In WordPress, you can choose themes and use tools that help you create a mobile-friendly site easily.
With these steps, you’re ensuring that anyone can access and enjoy your website, whether they’re on a computer or a phone. It’s all about making your online space welcoming and usable for everyone, no matter how they choose to visit.
## SEO and Performance Optimization
SEO is about making your website easy to find when people search for stuff online. Performance Optimization ensures your website works fast and without any hitches. Both of these help more people find and enjoy your website.
### SEO Best Practices in Web Design
SEO is like the signs on a shop that tell people what’s inside. In web design, SEO means using the right words and organizing things well so search engines like Google can understand what’s on your page. This way, when someone searches for something you have on your website, they can find you easily. It's like making sure the signs on your shop are clear and tell people exactly what they can find inside.
### Performance Optimization Techniques
Performance optimization is like cleaning and organizing your shop so customers can move around easily and find what they need quickly. For your website, it’s about making sure everything loads fast and works right. There are ways to do this, like making sure pictures aren’t too big and slow to load and cleaning up any unnecessary stuff that could slow down your site.
By following these steps, you help ensure that people can not only find your website but also enjoy using it because it’s fast and works well.
## Troubleshooting and Maintenance
Websites, like cars, need a little upkeep now and then to keep them running smoothly. Troubleshooting is about fixing problems when they pop up, and maintenance is about doing small regular check-ups to keep bigger problems at bay.
### Common Web Design Issues and Solutions
Sometimes, your website might act a bit funny. Maybe the pictures are not showing right, or things are looking a bit jumbled. It's like when a drawer gets stuck and you need to figure out why and fix it. There are common issues many website owners bump into, like slow-loading pages or things looking out of place, but luckily, there are also known solutions to get things back to normal.
### Regular Website Maintenance for Optimal Performance
Just like you take your car for regular check-ups to keep it running well, your website also needs some routine care. This can include updating it with the latest software, checking for any issues that might cause problems later, and making sure it's safe from online troublemakers. By doing regular maintenance, you're making sure your website stays in good shape and continues to work well for everyone who stops by.
Through these steps of troubleshooting and regular maintenance, you can keep your website running smoothly and ensure it remains a welcoming place for your visitors. It's about nipping problems in the bud and keeping things in tip-top shape!
Conclusion
Now, it's your turn to play around and get creative with your website on WordPress. Don't be afraid to try new things, experiment with different designs, and see what works best for you. There are so many tools, themes, and plugins in WordPress to explore. It's like having a big playground where you can learn and create. So, go ahead, try new things, learn a little, and have fun making your website awesome!
With this conclusion, we wrap up our guide, hoping you've gained a good understanding and are now excited to jump into the world of web design in WordPress. Remember, every expert was once a beginner, so take your first steps, keep learning, and enjoy the creative journey!
## Frequently Asked Questions

### What language is used for web design in WordPress?
WordPress is built upon four core languages: HTML, CSS, JavaScript, and PHP. Among these, HTML, CSS, and JavaScript are executed within the browser, enabling the structuring, styling, and interactive elements of a webpage, respectively. On the other hand, PHP operates on the web server, playing a pivotal role in generating and delivering the HTML, CSS, and JavaScript code that the browser will utilize.
### How do I keep my WordPress website secure?
[Keeping your WordPress site secure](/blog/wordpress-best-security-practices/) involves regularly updating the WordPress core, themes, and plugins, using strong passwords, and installing reputable security plugins. Implementing a two-factor authentication process and conducting regular site backups are also crucial steps for maintaining security.
### What are some common tools used in WordPress web design?
WordPress has its own set of tools to design a website. This is called Page Builders. An example of a page builder is Elementor. It is a popular drag-and-drop page builder that allows for live editing and offers a variety of pre-designed templates.
Bootstrap is a popular Theme Development Tool. It is a framework that can be used to create responsive and mobile-first themes. You will also need coding and IDE Tools such as Sublime Text or Visual Studio Code. These text editors/IDEs are useful for coding custom themes or plugins.
Another tool is PHPStorm, A powerful IDE for PHP development. There are other tools in web design but these are the most common tools to get to know.
### Which is the best Web Hosting for WordPress Web Design?
There are several hosting platforms to choose from. HostGator, Google Cloud, Amazon AWS, and so on. But if you are looking for an affordable solution where you can host your WordPress site along with your mobile application can start with Levamo. If you would like to know[ **How Much Cloud Hosting Costs**](/blog/how-much-does-cloud-hosting-cost-2/) for your WordPress site be sure to check out the link.
###
---
## Help! My Website is Down - 23 Common Fixes for WordPress
- URL: https://levamo.com/blog/wordpress-site-down-common-issues-and-fixes/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2023-11-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Website down? Get 23 quick WordPress fixes to get your site back online now.
If you've ever found yourself panicking and thinking, "Why my website is down?" you're not alone. According to a study by [Hosting Facts](https://smallbiztrends.com/2019/02/web-hosting-uptime-statistics.html) shows,
> *An average website is down 3 hours per month due to web hosting outages*
Not being able to access your website can be nerve-wracking, especially when you don't know the reason behind it. Whether it's because your website is not properly functioning or you're wondering why is my website going down, you need immediate solutions to get back on track.
In this guide, we'll walk you through 23 common fixes for WordPress sites to ensure you're well-equipped to handle any website downtime. So the next time your site is inaccessible, you'll know exactly what steps to take.

## Why is My Website Down?
The phrase "my website is down" strikes fear into the hearts of website owners and administrators. But the good news is that the majority of issues causing your website to go down are fixable.
These issues can range from server overloads to DNS issues, to simple WordPress plugin conflicts. Understanding the root cause is crucial for applying the correct fix. This blog post will act as a troubleshooter, guiding you through the maze of potential problems and their solutions.

**Also Read:** [Common Server Problems](/blog/common-server-problems/)
## How to Check Why Your Website is Down
First things first. Before you start tampering with code or deactivating plugins, it's essential to ascertain the scope of the problem. Is the issue just for you, or is it a more extensive outage affecting all visitors?
To check “why my website is down”, you can use various online tools and resources. Websites like "[Down for Everyone or Just Me](https://downforeveryoneorjustme.com/)" and "[Is It Down Right Now](https://www.isitdownrightnow.com/)" can give you a quick answer. These tools work by attempting to access your website from different locations, providing a more comprehensive view.
You can also conduct a DNS propagation check or even use command-line tools like ping or traceroute to check the reachability of your website.

## 23 Common Fixes When Your Website is Down
Before jumping to the problems of “my website is down” and solution, you need to have ideas about some common files that we’ll mention repeatedly. So let’s get you acquainted with the files and how to find them, before going on with fixes.
### Where to Find .htaccess File
The .htaccess file is typically located in the root directory of your WordPress installation. You can access it by connecting to your web server using an **FTP client** like FileZilla or directly via your **web hosting control panel** under the '**File Manager**' section. The file might be hidden; in that case, you'll need to enable the 'Show Hidden Files' option.
### Where to Find wp-config.php File
The wp-config.php file is also located in the root directory of your WordPress installation, alongside the .htaccess file. You can access it in the same manner, either using an **FTP client** or through your web hosting control panel.
### Where to Find function.php File
The functions.php file is located in your WordPress theme folder. You can access it by going to your [WordPress Dashboard](https://www.google.com/aclk?sa=l&ai=DChcSEwjogcu_1s6BAxX5pWYCHXrDBvcYABABGgJzbQ&gclid=CjwKCAjwyNSoBhA9EiwA5aYlb3aTflwTpEwk0ed7G5VcPh1u7w8mTLPkaA2dAQ4uXFgq6yuGWhqfNhoCEJwQAvD_BwE&sig=AOD64_0SuGg-vxo-Ss6ObwJOh09pzBX7Hg&q&adurl&ved=2ahUKEwjd8cS_1s6BAxX7yTgGHdQhAC8Q0Qx6BAgMEAE) and then navigating to Appearance > Theme Editor. From there, you'll see the functions.php file listed on the right-hand side under the "Theme Files" section.
Now let's start exploring the errors and the common solutions of them.
### 1. Internal Server Error

The Internal Server Error, often labeled as a **"[500 Internal Server Error](/blog/fix-the-500-internal-server-error/),"** is a particularly perplexing issue. It appears when there's something amiss, but the server is unable to pinpoint the problem. This leaves users scratching their heads, wondering, "Why is my website is down?"
#### How to Fix It
To resolve this, start by checking your .htaccess file, as it may be corrupted. Increasing your site's PHP memory limit in the **wp-config.php** file can also be a quick fix. Plugin issues are another common culprit; try deactivating all plugins and then reactivate them one by one. You will be able to do it from the Levamos Dashboard Easily. Lastly, consult your server's error logs for more specific insights.
If you still find that my website is not working, it may be wise to seek professional help.
### 2. WordPress White Screen of Death
Often referred to as WSoD, the [WordPress White Screen of Death](/blog/wordpress-white-screen-of-death/) appears as a blank, white screen with no error message displayed. This often makes users question if their website is down for maintenance or if there is a issue.
#### How to Fix It:
To resolve the WSoD, start by deactivating all of your WordPress plugins. If the issue gets resolved, reactivate them one at a time to identify the culprit. Next, check your theme by reverting to a default WordPress theme. If these steps don't work, look into your website's error logs for clues, or visit this[ helpful guide](https://wordpress.org/support/article/common-wordpress-errors/) for more in-depth solutions.
### 3. Error Establishing a Database Connection
This error occurs when your WordPress site can't connect to the database, leaving users wondering, "Why is my website is down?" It can be due to various factors, such as incorrect database credentials or issues on the server's end.

#### How to Fix It:
The first step is to verify the database credentials in your **wp-config.php** file. Make sure that the database name, username, and password match what's in your hosting account. If the problem persists, you might want to check if the website is down due to server-related issues by getting in touch with your hosting provider. If you're still stuck, visit this[ comprehensive guide](https://wordpress.org/support/article/debugging-a-wordpress-network/) for more advanced solutions.
### 4. This Site is Experiencing Technical Difficulties
When you see the message, "**This Site is Experiencing Technical Difficulties**," it usually indicates a fatal PHP error on your website. If you find yourself wondering, "**Why my website is down,**" this could be one reason.
#### How to Fix It
One of the first steps to take is to check why the website is down by examining the **error logs**. You can usually find these logs in the hosting control panel. Additionally, you can also enable WP_DEBUG (Levamo dashboard WP Debug blogs link will be here) in your **wp-config.php** file to diagnose the issue.
### 5. WordPress Login Page Refreshing and Redirecting Issue
When you attempt to log in, you get stuck in a loop, always finding yourself back at the login page. It's frustrating because, to the visitor, it seems like the website is not working.
#### How to Fix It:
This issue often arises due to[ incorrect URL](https://www.seo.com/blog/3-common-url-problems-and-how-to-fix-them) settings. To resolve it, you may need to edit your **wp-config.php** file. Locate the **WP_HOME** and **WP_SITEURL** settings. Make sure they correspond with your website's correct URL. Additionally, you may want to clear your browser cache and cookies, as these could contribute to the issue. If the problem persists, deactivate all plugins to check for any conflict. Reactivate them one by one to pinpoint the culprit.
### 6. Syntax Error in WordPress
A Syntax Error occurs when there is a mistake in your code, causing your site to display a specific line of code and a description of the error. This can lead to my website not loading properly.

#### How to Fix It
First, identify the line of code mentioned in the error message. You can [use FTP](https://filezilla-project.org/) to edit the relevant file, most commonly **functions.php**, and correct the error.
### 7. WordPress Memory Exhausted Error
This error occurs when a WordPress script or a query requires more memory than the default allocated memory size, usually indicated by a message like "Fatal error: Allowed memory size of X bytes exhausted."
#### How to Fix It:
Increase your [PHP memory limit](/blog/maximum-php-memory-limit/) by editing the **wp-config.php** file. Add the line define('WP_MEMORY_LIMIT', '256M');.
### 8. White Text and Missing Buttons in WordPress Visual Editor
In this issue, the visual editor shows white text or missing buttons, making it challenging to edit content. Users might assume that the website is down for maintenance or malfunctioning.
#### How to Fix It:
[Clearing your browser cache](https://support.google.com/accounts/answer/32050?hl=en&co=GENIE.Platform%3DDesktop) is usually the first step. If that doesn't solve the issue, try deactivating all plugins and switching to a default theme to see if the issue is theme or plugin-related.
### 9. WordPress Posts Returning 404 Error
A 404 error typically means that the server couldn't find the requested page. Visitors might think your website is not loading properly and may be unsure if the website is down or up.

#### How to Fix It:
The most common solution is to re-save your WordPress permalinks. Go to **Settings** -> **Permalinks** and simply click "Save Changes. " If the issue persists, check your .htaccess file to ensure it's properly configured.
### 10. Locked Out of WordPress Admin
You find that you can't access your WordPress admin dashboard. Users may wonder, "Is my website not working?"
#### How to Fix It:
The reasons for being locked out could vary from lost passwords to hacked accounts. Start by using the [password recovery](https://wordpress.com/support/account-recovery/) options. If that fails, you might need to manually reset your password through the database.
### 11. Sidebar Below Content Error
Instead of appearing beside your content, the sidebar displays below it. This layout issue could lead users to wonder why is my website going down or why its not working as it should.
#### How to Fix It:
This is often a [CSS](https://www.w3schools.com/css/css_intro.asp) or HTML issue. Make sure your theme files are correctly coded and check if any recently installed plugins are causing the issue. Deactivate them one by one to find the culprit.
### 12. Common Image Issues in WordPress
Images on your website may appear broken or don't display at all. This often leads users to think that your website is not properly functioning.

#### How to Fix It:
Broken images are often the result of incorrect paths or URLs. The quickest way to fix this is to correct these paths. This can be done manually by editing each post or image setting or by running an[ SQL](https://www.w3schools.com/sql/) query to replace the old URLs.
### 13. Briefly Unavailable for Scheduled Maintenance Error
During updates, your site displays a message that it's [unavailable due to scheduled maintenance](/blog/wordpress-stuck-in-maintenance-mode/). This might make visitors wonder why my website is down for an extended period.
#### How to Fix It:
This usually occurs during an update that failed to complete. To resolve this, access your website's root directory using FTP and locate the .maintenance file. Deleting this file should remove the maintenance status from your website.
### 14. “This Site Ahead Contains Harmful Programs” Error
Users are warned by their browsers that your site might contain harmful programs, which could severely damage your site’s reputation and make users wonder why my website is down or compromised.

#### How to Fix It:
This is often due to malware or hacked content on your website. Immediate action is required: scan your website for malware and remove any compromised files. Once cleaned, you can request [Google ](https://www.google.com/)to review your site.
### 15. Image Upload Issue in WordPress
You can't upload images, or you encounter an error while doing so. This often gives the impression that your website is not working as it should, leading to user frustration.
#### How to Fix It:
Start by checking file permissions in your WordPress installation. Navigate to the **wp-content** folder and see if permissions are set correctly. They should be set to **744** or **755**. If the problem persists, you can switch to the browser uploader within WordPress. To do this, go to **Media** -> **Add New**, and click on “**Browser Uploade** r.”
### 16. Fatal Error: Maximum Execution Time Exceeded
Certain processes on your website are taking too long to complete, [leading to timeouts.](https://www.lifewire.com/408-request-timeout-2622937) This can make users think your website is down.

#### How to Fix It:
To turn off PHP errors, you can add ini_set('display_errors','Off'); in your wp-config.php file. This will ensure that any PHP errors are logged but not displayed to the end users, thereby improving your site's security profile. If you aren't comfortable editing these files, consider seeking professional help as an incorrect modification can render your website inaccessible.
### 17. WordPress Not Sending Email Issue
Emails from your WordPress site (like password reset emails, notifications, etc.) aren't reaching their intended recipients. This creates a feeling that the website is down or dysfunctional in its operations.
#### How to Fix It:
First, make sure that the issue is not with your email service provider. Use plugins like [WP Mail SMTP ](https://wordpress.org/plugins/wp-mail-smtp/)to configure SMTP settings. If the issue persists, you may need to check your server's mail logs for errors. Your hosting provider can help with this.
### 18. Too Many Redirects Issue
Your website keeps redirecting between different URLs, making it impossible for visitors to access the content. This might make them think your website is down.
#### How to Fix It:
The common culprits are incorrect WordPress URL settings and problematic plugins. Start by going to "Settings" > "General" and check your WordPress Address and Site Address. Make sure they are correct. If that doesn't resolve the issue, it could be due to a plugin. You can deactivate all plugins and reactivate them one by one to find the problematic one. Check your .htaccess file as well, as incorrect configuration here can also cause this issue.
### 19. “Are You Sure You Want to Do This” Error
While working on your WordPress admin, a prompt appears asking, "Are You Sure You Want to Do This?" It causes doubts and worries in users' heads by keeps rotating “why my website is down”.

#### How to Fix It:
This issue is typically related to [nonce failure](https://blog.hubspot.com/website/nonce-error), which is a security feature in WordPress. The first step in resolving this is to refresh the webpage. If that doesn't work, the issue may be a theme or plugin conflict. Deactivate all your plugins and reactivate them one by one to identify which one is causing the problem.
### 20. 403 Forbidden Error
Users are prevented from accessing certain pages on your website, leading them to think that the website is down or not fully operational.
#### How to Fix It:
This usually occurs because of incorrect file permissions or server rules. Review your .htaccess file for any irregularities, and make sure your file permissions are set correctly (typically 755 for folders and 644 for files).
### 21. “Upload: Failed to Write File to Disk” Error
You can't upload files via the WordPress dashboard. This could lead users to think that your website is down or experiencing difficulties.
#### How to Fix It:
This error typically arises because of incorrect folder permissions in your WordPress installation. You can use an FTP client to connect to your server and change the permissions for the "wp-content" directory to "755." Additionally, ensure that the "Uploads" folder, within "wp-content," has the correct permissions. If the problem persists, check your PHP settings for file upload size limits, and modify them if necessary.
### 22. WordPress RSS Feed Errors
Your website’s RSS feed is not updating, or it shows broken XML code. This can cause subscribers to believe that the website is not working or has been abandoned.
#### How to Fix It:
The most common cause for RSS feed errors is poor formatting. WordPress is quite strict with [XML structure](https://www.w3schools.com/xml/xml_tree.asp), and a small error can break the feed. Use a feed validator tool to find errors and then fix them by editing the corresponding posts or pages.
### 23. Missed Schedule Post Error
Scheduled posts fail to go live at the set time, leading to gaps in content that might make visitors question if the website is working as it should.

#### How to Fix It:
The first thing you should try is to increase the upload file size limit by editing your WordPress theme's **functions.php file. If that doesn't solve it, you can modify the .htaccess file**, **[php.ini file](https://www.php.net/manual/en/configuration.file.php)**, or even directly in your hosting admin panel, if your host provides such an option. It's crucial to know that tweaking server settings should be done cautiously, and preferably under professional supervision.
## It's a Wrap Up
If your website is down, don't panic.
In this guide, we have covered 23 common WordPress issues and how to resolve them. From server errors, database issues, to errors like **[the requested url was not found on this server](/blog/the-requested-url-was-not-found-on-this-server/)**, most problems have a fix. We hope from this handy guide you'll be easily be able to get your site back online in no time. Thanks for reading!
## Frequently Asked Questions

### What steps can I take to get my WordPress site back online?
To restore your WordPress site, start by identifying the issue, whether it's server-related, a plugin conflict, or a theme issue. Once identified, work on the specific fix to bring your site back online.
### What's the process for resolving a downed website?
To resolve a downed website, first ensure that the issue isn't a server outage. Then look into potential issues with your CMS, plugins, or themes. Debugging tools can also help pinpoint the problem.
### What could be the reason my website isn't accessible?
The inaccessibility of your website could be due to multiple reasons ranging from server outages, DNS issues, to software conflicts. It's crucial to diagnose the exact cause to apply an appropriate solution.
### Is there a way to access my website when it's down?
Accessing a downed website is challenging. However, you can try clearing your browser cache, using a different network, or checking the server status to see if the site is down only for you or for everyone else as well.
---
## How To Know If You Have A Fast Server
- URL: https://levamo.com/blog/fast-server-speed-tools/
- Category: website-performance
- Author: Faisal Sarker
- Published: 2023-11-13
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Is your server fast enough? Find out with our expert tips now.
In today's digital age, having a fast server is more crucial than ever. But how do you know if you actually have a fast web server with top-tier performance and speed? From Fast DNS Server configurations to Speed Measurement Tools, there are various indicators and metrics to look out for. A fast server not only impacts your website's load times but also significantly influences user experience, SEO rankings, and even conversion rates.
According to a study by [Akamai,](https://www.akamai.com/newsroom/press-release/akamai-releases-spring-2017-state-of-online-retail-performance-report) *a 100-millisecond delay in load time can decrease conversion rates by up to 7% *.
Therefore, understanding the importance of server speed and how to measure it effectively can offer a competitive edge in an increasingly crowded digital space. This blog aims to guide you through the essentials of identifying the speed and efficiency of your server. Stay tuned to unlock the secrets behind achieving and maintaining a fast server for your online operations.
## Importance of Server Speed
Server speed is crucial for a multitude of reasons. A fast server ensures that your website loads quickly, leading to a better user experience and higher engagement rates. This is particularly vital as slow load times can result in increased bounce rates and a lower ranking on search engines. Moreover, a fast server is essential for effective data management and running complex tasks swiftly, which could be the backbone of your business operations.

Another angle to consider is fast server internet and [fast server for hosting](/blog/choosing-reliable-hosting-provider/). If you're hosting a website or an application, a fast server can be the difference between a smoothly running platform and one fraught with delays and customer complaints.
Whether you're concerned about fast [DNS server](https://www.cloudflare.com/learning/dns/what-is-a-dns-server/), fast HTTP server, or fast proxy server aspects, the underlying speed of your primary server remains the critical component. So, investing in a fast server should be a top priority for anyone serious about their online presence and performance.
## Fast Server Essentials
Understanding what makes a server fast is essential for optimizing performance. Factors like [RAM,](https://techsourcecanada.ca/blogs/everything-about-random-access-memory/) CPU, SSDs, and the network's speed all contribute to how fast a server can perform tasks and serve data.

### Fast Server Factors
Fast servers generally have several core components optimized for high performance. Let's break down what each of these vital elements does:
- **RAM:** More RAM allows for quicker data access, making your server faster. Enhancing your [data services](https://www.avenga.com/data-services/) infrastructure enables faster response times and improved reliability.
- **CPU:** A powerful CPU can process tasks more rapidly, contributing to a fast server.
- **[SSD Storage:](https://www.teamgroupinc.com/en/blogs/basic-knowledge-ssd)** Compared to traditional HDDs, SSDs are much faster, affecting how quickly data can be read or written.
- **Network Speed:** The fastest server internet options will be significantly affected by how quickly data can be transmitted over the network.
- **Software:** The right server software, be it a fast HTTP server or a fast DNS server, can make a significant difference in speed.
- **Load Balancing:** Distributing network or application traffic across multiple servers can enhance speed and reliability.
All these components contribute to what constitutes a fast server. When looking into fast VPN servers or fast proxy server options, these elements remain constant. Keep these factors in mind, and you will be well on your way to understanding what makes a server genuinely fast.
**Also Read:** [Fastest WordPress Hosting](/blog/fastest-wordpress-hosting/)
### Fast DNS Basics
DNS, or [Domain Name System](https://www.domain.com/blog/what-is-dns/), is often an overlooked component when talking about a fast server, yet it plays a critical role in server speed. A fast DNS server translates domain names into IP addresses, functioning as the internet's directory service. Faster DNS servers mean that this translation happens more quickly, ultimately affecting your server's overall speed and performance.

Understanding DNS performance is vital, especially if you want to achieve the fastest server internet speeds possible. Several elements contribute to the speed of a DNS server:
### Caching:
Effective caching can drastically improve DNS response time.
### Load Distribution:
Similar to load balancing in general servers, a DNS server that can distribute queries efficiently is generally faster.
### Geographical Location:
DNS servers closer to the user will usually provide quicker response times.

### Redundancy:
More DNS servers mean more robust systems, minimizing downtime and improving speed.
### Protocol Optimizations:
Modern DNS servers may support new protocols or extensions that improve query speed.
These are the fundamentals you should know when investigating what goes into a fast DNS server. Understanding these basics will not only help you choose a faster DNS server but also assist in comprehending how the speed of your general server setup can be improved.
### Fast Server VPN Importance
[Virtual Private Networks](https://www.livingsecurity.com/support/blog-virtual-private-network-vpn), or VPNs, have become crucial tools for online privacy and security. However, many overlook the importance of a fast VPN server when considering these services. The speed of your VPN server can significantly impact your online experience, affecting everything from browsing speed to streaming quality.

When you connect to a VPN, your internet traffic is routed through the VPN's servers. The speed of these servers affects how quickly data can be transmitted. Here are a few reasons why a fast VPN server is crucial:
### Latency Reduction:
The higher the VPN speed, the lower the latency, making real-time communications more efficient. This is especially useful for [low latency streaming](https://castr.com/low-latency-streaming/), where smooth delivery of content is crucial for a better user experience.
### Faster Streaming:
A fast VPN server allows for quicker download speeds and uninterrupted streaming, crucial for users who consume a lot of media.
### Better Gaming Experience:
Gamers require low latency and fast speeds for an optimal experience, and a fast VPN server can provide that.
### Seamless Web Browsing:
Fast servers ensure that web pages load quickly, providing a smoother browsing experience.
### Increased Productivity:
For business users, a fast VPN means quicker access to necessary data and applications, resulting in improved efficiency.
Opting for a fast VPN server isn't just about speed but also involves choosing a VPN that offers a balance between speed, security, and privacy. Always consider server speeds when selecting a VPN service; it's a factor that significantly impacts the quality of your online activities.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## The Role of a Fast Proxy Server
A fast [proxy server ](https://www.upguard.com/blog/proxy-server)acts as an intermediary between your device and the internet. While commonly used for anonymity and security, the speed of the proxy server plays a significant role in your online activities. A sluggish proxy can be more of a hindrance than a help, whereas a fast proxy server can offer a range of benefits.

Understanding the role of a fast proxy server can help you make an informed decision when choosing a proxy service. Here's what a fast proxy server can do for you:
### Data Caching:
A fast proxy server often comes with superior data caching capabilities, allowing frequently accessed web pages to load much quicker.
### Improved Security:
While speed is a priority, many fast proxy servers also offer robust security features to protect your data.
### Load Balancing Essentials:
In a corporate environment, a fast proxy can balance the load across multiple servers, ensuring uninterrupted service.
### Access to Restricted Content:
A fast proxy server can bypass geographical restrictions swiftly, granting you access to region-locked content without much waiting.
This experience can be further enhanced with [secure datacenter proxies](https://netnut.io/datacenter-proxies/) for added speed and reliability.
### Reduced Bandwidth Usage:
Due to effective caching and data compression, a fast proxy server can help save on bandwidth costs.
### User Authentication:
Many fast proxy servers come with built-in authentication features, adding an extra layer of security.

### Monitoring and Control:
Administrators can monitor traffic and impose restrictions more efficiently with a fast proxy server.
When selecting a proxy service, speed should be a critical factor in your decision-making process. A fast proxy server not only provides quick access but also offers a better overall user experience. Whether you're an individual user or a business, the benefits of a fast proxy server are manifold and cannot be ignored.
## Fast HTTP Essentials
A fast [HTTP server](https://medium.com/from-the-scratch/http-server-what-do-you-need-to-know-to-build-a-simple-http-server-from-scratch-d1ef8945e4fa) is not just a luxury but a necessity. The speed of your HTTP server directly influences website performance, affecting metrics like page load times, user experience, and even search engine rankings.

To reap the benefits of a fast HTTP server, you need to understand its essential components. Here's what to consider:
### Server Hardware Components:
Top-of-the-line hardware contributes to the server's speed. Look for servers with ample RAM and powerful CPUs.
### Software Optimization:
The right balance of software and hardware can make a noticeable difference. Opt for lightweight server software optimized for speed.
### Content Delivery Network (CDN):
A [free WordPress CDN](/cloudflare-cdn/) can cache your website's static elements, reducing the load on your fast HTTP server and delivering content faster to users.
### Caching Mechanisms:
Effective caching can significantly reduce server load and improve performance. Employ caching tools and mechanisms wisely.
### Load Balancers:
In multi-server environments, load balancers distribute incoming requests across servers, preventing any single server from becoming a bottleneck.
### Compression Algorithms:
Utilize data compression algorithms to reduce the amount of data transferred, making the server faster.
### SSL Accelerators:
These can offload [SSL decryption](https://www.ssl.com/blog/) tasks from the server, improving its speed and allowing it to handle more traffic.

### Database Optimization:
Frequent database calls can slow down a server. Proper database optimization can mitigate this issue, enhancing server speed.
### Monitoring Tools:
Regular monitoring can provide insights into server performance, helping you make necessary adjustments for [WordPress Speed Optimization](/blog/wordpress-speed-optimization/).
By paying attention to these essentials, you can significantly enhance the speed of your fast HTTP server. Remember, the quicker your server, the better the user experience, and the higher the potential for positive engagement and conversion rates.
## How to Measure Server Speed
Knowing how to accurately measure server speed is crucial when you're striving for a fast server. Without proper metrics, you can't diagnose issues or identify areas for improvement. In this section, we'll discuss various methods and speed measurement tools you can use to gauge your [server's performance](https://www.nexcess.net/blog/server-performance-monitoring/) effectively.

Here are some proven methods to measure fast server performance:
### Ping Tests:
This is the most basic test you can perform to measure latency. A lower ping time indicates a faster connection.
### Speed Test Websites:
Websites like Speedtest.net can provide a comprehensive look at your download and upload speeds, contributing to your fast server internet.
### FTP Transfers:
Upload and download files to your server using FTP and measure how long the process takes.
### Web Page Loading Times:
Use browser extensions or web-based tools to analyze how quickly your website pages load. This could be indicative of your fast HTTP server.
### Database Queries:
Measure the time it takes to execute database queries. Faster query execution means you likely have a fast server for hosting especially if you're considering a [Kinsta alternative](/kinsta-alternative/).
### Local Network Speed Tests:
These can help you identify if the bottleneck is with your server or the network.
### Use Monitoring Tools:
There are many server monitoring solutions that can provide real-time analytics on server performance, including fast DNS server, fast server VPN, and fast proxy server metrics.
### Analyze Server Logs:
Server logs can reveal issues that may be affecting speed. Look for errors or bottlenecks that need addressing.
### Third-Party Professional Tests:
Some professional services can perform in-depth server speed tests and provide detailed reports.
### Regular Audits:
Regularly auditing your server's speed can help you keep tabs on its performance over time and make adjustments as necessary.

## Frequently Ask Questions
**Why is server speed important?**
Server speed is crucial for better user experience and SEO rankings. A fast server ensures quicker page load times, reducing bounce rates and improving conversion.
**What is a Fast DNS Server and why does it matter?**
A Fast DNS Server translates domain names to IP addresses more quickly, speeding up how fast pages load. It's a key component for overall server performance.
**What's the role of a Fast Proxy Server?**
A Fast Proxy Server acts as an intermediary, improving security and speed. It can cache data, making repeated requests quicker and reducing latency.
**How can I measure my server speed?**
Use Speed Measurement Tools like ping tests, FTP transfers, or specialized software to measure your server's performance metrics.
## Conclusion
In this blog post, we've navigated through the complex landscape of server speeds, touching on everything from fast DNS servers to fast VPN servers and fast HTTP servers. The speed of your server isn't just a luxury; it's a necessity for optimizing user experience and operational efficiency.
## Frequently Asked Questions

### Why is server speed important?
Server speed is crucial for better user experience and SEO rankings. A fast server ensures quicker page load times, reducing bounce rates and improving conversion.
### What is a Fast DNS Server and why does it matter?
A Fast DNS Server translates domain names to IP addresses more quickly, speeding up how fast pages load. It's a key component for overall server performance.
### What's the role of a Fast Proxy Server?
A Fast Proxy Server acts as an intermediary, improving security and speed. It can cache data, making repeated requests quicker and reducing latency.
### How can I measure my server speed?
Use Speed Measurement Tools like ping tests, FTP transfers, or specialized software to measure your server's performance metrics.
---
## Unleash Your Website's Potential: Introducing the Levamo Beta
- URL: https://levamo.com/blog/rapyd-beta-is-now-available/
- Category: news
- Author: The Levamo Team
- Published: 2023-10-31
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Levamo's beta launch brings managed WordPress hosting built for speed.
> *Note: This post was originally published October 2023 as "Unleash Your Website's Potential: Introducing the Rapyd Beta" when our platform was called Rapyd Cloud. We've since rebranded to Levamo. The product details below remain accurate - only the brand name has changed.*
Is your WordPress website struggling to keep up? Slow loading times and frustrating downtime during traffic spikes can damage your credibility and kill your users' experience. If your site relies on resource-heavy platforms like BuddyBoss, LearnDash, or WooCommerce, you need a hosting solution built for performance.
That's where Levamo comes in. We're thrilled to announce the beta launch of Levamo, a fully managed WordPress hosting solution designed to provide exceptional speed, reliability, and security for mission-critical websites.
## Say Hello to Levamo
Levamo was built to solve the real problems that highly-dynamic sites face everyday with traditional web hosts. Here's what this means for you.
### Supercharge Your WordPress Site
Levamo is engineered to handle the demands of modern WordPress. Our platform dynamically scales to adapt to traffic surges in real-time, ensuring your site stays online and delivers a smooth user experience, even during peak hours. This powerful capability is powered by the Litespeed Enterprise web server and a comprehensive suite of performance features.
If you're a BuddyBoss App customer, you can say goodbye to sluggish performance due to API limitations at your current host. Levamo was conceived as an answer to this problem.
### Security at Every Level
Security is paramount. Levamo utilizes containerized architecture to isolate your website, safeguarding it from threats. Monarx malware scanning with insurance provides an additional layer of protection, and Patchstack virtual patching keeps your plugins up-to-date without downtime or compatibility risks.
### Effortless Management
We understand your time is valuable. Levamo's user-friendly dashboard simplifies site management. Handle tasks like plugin and theme updates with a few clicks, freeing you to focus on what matters most: growing your business.
## Why a Beta?
Your feedback is essential! While our hosting infrastructure is proven and has been battle-tested in production for over a year, we want to ensure our customer dashboard is intuitive and meets your specific needs. The Levamo beta allows us to gather your insights and refine our offering and internal processes before a full launch.
## Join the Levamo Beta Today!
Ready to experience the Levamo difference? Head over to [levamo.com](/) to sign up for the beta. We offer a free managed migration service to get you started quickly, and our 24/7/365 support team is here to answer any questions and address any issues that may arise.
The Levamo beta is just the beginning. We're excited to have you on board and hear your success stories!
*Update: The beta has ended and Levamo is available to everyone! Learn more here: [Levamo is officially out of beta](/blog/rapyd-is-officially-out-of-beta/).*
---
## BuddyBoss Podcast: The Journey Toward Optimizing BuddyBoss Hosting
- URL: https://levamo.com/blog/buddyboss-rapyd-journey-podcast/
- Category: podcast
- Author: Faisal Sarker
- Published: 2023-10-12
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Explore optimized BuddyBoss hosting with Levamo in our latest podcast episode.
In today's episode, we have a captivating chat between our Managing Director Graham Hoffman and the new Managing Director of Levamo, Wes Tatters. They dive into what went behind launching Levamo, a tailored hosting service for dynamic WordPress sites, especially those powered by [BuddyBoss](/buddyboss-hosting/).
Graham and Wes talks about:
- The issues hosting services face with Dynamic WordPress sites and how Levamo comes to the rescue.
- The extra steps needed to manage dynamic community sites and why BuddyBoss users will find Levamo hosting a comfy fit.
- How Levamo handles high concurrency of BuddyBoss-powered community sites.
- Simple and intuitive user experience of Levamo, despite offering state-of-the-art features.
- Levamo's unmatched scalability and the plan to switch to even better CPU technology next year.
- Levamo’s partnerships with Object Cache Pro & Relay to speed up content loading, and with PatchStack and Monarx to keep your site safe from malware and other threats.
- The 24/7 live chat support from Levamo and a special beta launch offer for selected [BuddyBoss hosting](/buddyboss-hosting/) customers.
[Watch the episode on YouTube](https://www.youtube.com/watch?v=VX22ANhY1WI)
RESOURCES
- Subscribe on [Apple Podcasts](https://podcasts.apple.com/us/podcast/the-buddyboss-podcast/id1628557838)
- Subscribe on [Spotify](https://open.spotify.com/show/1vESiPFbSuIieX9fzU4Dtu)
- Subscribe on [Audible](https://www.audible.co.uk/pd?asin=B0B3MSHTL9)
- Subscribe on [Stitcher](https://www.stitcher.com/show/the-buddyboss-podcast)
- Subscribe on [iHeartRadio](https://www.iheart.com/podcast/263-the-buddyboss-podcast-98347438/)
- [Transcript](https://app.trint.com/public/16e230e0-8993-4292-90ef-ab311c82b2a5)
---
## How to Choose Reliable Hosting: Uptime vs. Downtime
- URL: https://levamo.com/blog/choosing-reliable-hosting-provider/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2023-10-03
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Uptime vs. downtime: Get reliable hosting and avoid costly website outages.
Choosing the right web hosting provider isn't just about specs and pricing tables. It's like picking a home for your website. You want something solid, reliable, and dependable. Ideally, a reliable hosting provider does not crash every time there’s a bit of traffic or a hiccup in the server room.
Because when your website goes down, it’s not just annoying. It’s expensive. We're talking **an average of $5,600 for every minute** your site is offline. No, that’s not a typo.
So, whether you're running a personal blog or managing a high-traffic ecommerce store, your hosting provider matters a lot, especially when it comes to uptime vs downtimes.
Why? Let's break it down.
## Understanding the Basics of Web Hosting

Navigating the world of web hosting can be a bit like learning a new language. However, understanding a few key terms can make the journey much easier. Let’s break down some basic concepts.
### What is Web Hosting?
To keep it simple, web hosting is a service that allows individuals and organizations to make their websites accessible via the internet. Hosting providers (like [Levamo](/)) offer the technology and support needed to store website files on web servers and ensure they’re available to users around the clock.
However, many different factors determine whether the web host provider you're choosing is good for you. One of the most important factors is downtime vs uptime.
### What is Uptime in Web Hosting?
Think of uptime as your website’s “open hours.” Just like a physical store that welcomes you during its operating hours, uptime is the amount of time your website is online, functional, and accessible to visitors. The higher the uptime, the more consistently your site is “open for business.”
Most reliable hosting providers aim for **at least 99.99% uptime**, which translates to **less than 5 minutes** of downtime per month. For businesses where every click can turn into a conversion, this consistency isn’t just nice to have; it’s critical.
### What is Downtime in Web Hosting?
Downtime is the opposite. It’s when your site is offline and inaccessible. Like a store that’s closed when someone wants to buy groceries, a website experiencing downtime turns visitors away.
Whether caused by server issues, network failures, or traffic overloads, even short bursts of downtime can be damaging. According to Gartner, the average cost of IT downtime is **$5,600 per minute**, and that number can skyrocket for ecommerce stores and platforms with live users.
## The Impact of Uptime and Downtime on Online Businesses

When it comes to web hosting, uptime and downtime are more than just fancy words. They have real, tangible effects on your website and your business. Let’s explore what these effects are.
### 1. The Direct Impact on Website Accessibility
Visitors expect websites to be available 24/7. If someone clicks a link and gets an error message, their trust in your brand takes a hit. In fact, a **Google survey revealed that 53% of users abandon sites that take more than 3 seconds to load**, so imagine the frustration if the site doesn’t load at all.
On the other hand, consistent uptime builds reliability. Your site becomes a dependable destination, whether it's for customers, students, or community members.
### 2. SEO and Website Ranking
Google doesn’t just rank based on content quality. Site availability plays a major role, too. Frequent or extended downtime can cause search engines to de-prioritize your site in rankings.
If your website is consistently unavailable when crawlers attempt to access it, you risk losing your spot on the front page. Uptime contributes to better crawlability, indexing, and ranking, all things essential for organic traffic.
### User Experience and Customer Satisfaction
Think of your website as your digital storefront. A closed store frustrates customers. Similarly, when users can’t access your site, or it crashes during a key action like checkout or course enrollment, they’re unlikely to return.
**47% of consumers expect a website to load in under 2 seconds**, and if it’s not available at all? They bounce, sometimes straight to your competitors.

### What Do Web Hosting mean by 99.99% Uptime?
Let’s be clear: not all uptime guarantees by different web hosting companies are built the same. Here’s what those percentages actually look like in real-world terms:
- **99.9% uptime** = up to **8.76 hours** of downtime per year
- **99.99% uptime** = just **52.6 minutes** per year
That’s the difference between missing a few sales and losing your entire Black Friday rush.
For industries like **finance, healthcare, e-commerce, or education**, every second your site is down can mean compliance violations, interrupted transactions, or frustrated users abandoning you mid-click. When your website powers your business, uptime isn’t a nice-to-have; it’s your operational baseline.
Choosing a reliable web hosting or exploring a trusted **[Kinsta alternative](/kinsta-alternative/)** means choosing one that guarantees you a high uptime.
This is why [Levamo](/pricing/) is one of the best choices for mission-critical websites. Not only does it perform the fastest in the industry, but it guarantees 99.99% Uptime, which is one of the industry's highest.
### Downtime Impact Analysis: Why Minutes Matter
Downtime doesn’t just show up on a server log. It hits your **revenue**, **reputation**, and **readiness.** Sometimes all at once.
#### 1. The Financial Cost of Downtime
According to **Gartner**, the average cost of IT downtime is $5,600 per minute. That's **$300,000 an hour** in potential losses, a combination of dropped transactions, halted productivity, customer churn, and emergency recovery efforts.
And that’s just the average. For high-traffic WordPress platforms, especially [membership sites](/online-community-managed-hosting/), [LMS platforms](/managed-lms-hosting/), or live [eCommerce stores](/managed-woocommerce-hosting/), the cost can be far greater.
#### 2. Operational Impact
While some downtime is planned (maintenance, updates), the **real damage comes from the unexpected. Unplanned outages can corrupt data, [open the door to security vulnerabilities](https://protostechnologies.com/blog/high-availability/5-steps-analyze-downtime-impact-downtime-impact-cheat-sheet/), and trigger cascading failures across other systems**.
**A single hour of unplanned downtime can take several hours, even days, to fully recover from.**
#### 3. Security and Compliance
Industries with strict regulatory oversight, like healthcare (HIPAA), finance (PCI-DSS), or education (FERPA/GDPR), can’t afford gaps in uptime. Downtime during sensitive operations doesn’t just disrupt service; it can **violate compliance**, **expose data**, and lead to **hefty penalties or lawsuits**.
## How to Choose a Reliable Hosting Provider

Choosing the right hosting provider is more than just picking the cheapest plan or the one with the ads. It’s about finding a partner that can support your website’s performance, security, scalability, and growth. Here’s how you can find the most reliable and [fastest WordPress hosting](/blog/fastest-wordpress-hosting/) for your website:
1. **Uptime Guarantee** - Look for providers that offer a minimum of 99.9% uptime. Anything lower puts your site at risk of frequent unavailability.
2. **Speed & Performance** - Fast page loading times are critical for user experience, SEO, and conversion rates. Server optimization, [free WordPress CDN](/cloudflare-cdn/) integration, and caching technology play a huge role here.
3. **Scalability** - Your hosting should grow with your business. Whether it’s handling sudden traffic spikes or adding more websites, the platform should make scaling seamless.
4. **24/7 Customer Support** - Issues can arise anytime. A reliable host offers round-the-clock support via multiple channels - ideally with real WordPress-savvy experts on standby.
5. **Security Features** - Essential protections include firewalls, malware scanning, [DDoS protection](/blog/preventing-ddos-attacks/), SSL certificates, and regular software updates.
6. **Automatic Backups** - Daily or real-time backups ensure that your data is never lost and can be restored quickly in case of an issue.
7. **Ease of Use** - An intuitive dashboard and user interface make site management easier, especially if you’re managing multiple projects or don’t have a dev team.
8. **Developer-Friendly Tools** - Features like SSH access, staging environments, Git integration, PHP version control, and cron jobs are critical for developers and agencies.
9. **Multiple Site Support** - If you plan to host more than one website, look for plans that offer multiple site or multiple domain support under a single environment.
10. **Pricing & Value** - Transparent pricing with no hidden charges, fair resource limits, and the right balance between cost and capability is key.
11. **Reputation & Reviews** - Check third-party reviews, user testimonials, and Trustpilot scores to get a real sense of customer satisfaction and long-term reliability.
12. **Migration Support** - Moving hosts should be simple and safe. Look for providers that offer free or guided site migration without risking downtime or data loss.
## Why Levamo is The Most Reliable Hosting Provider for WordPress Websites

[Levamo](/) is hands-down the most reliable web hosting service based on real-world performance and data-backed studies. Here are some reasons why:
✅ **99.99% Uptime That You Can Rely On**
Our infrastructure is designed to stay up, no matter what. With automatic failovers, proactive monitoring, and intelligent scaling, we help you stay online and in business, 24/7.
✅ **Blazing Fast Performance, Even Under Pressure**
Levamo is engineered for speed at scale. We use hyperspeed-optimized server stacks, edge caching, and performance-tuned environments, delivering lightning-fast load times even for heavy WordPress setups like [BuddyBoss](/buddyboss-hosting/), LearnDash, WooCommerce, and [LMS plugins](/blog/best-wordpress-lms-plugins/).
✅ **World-Class 24/7 Expert Support**
We don’t do generic scripts or long wait times. Our [support team](/support/) is made up of WordPress-savvy engineers who go above and beyond, including collaborating with plugin developers (like BuddyBoss) to solve complex issues when needed.
✅ **Built-In Security and Peace of Mind**
From [Cloudflare-powered firewalls](/managed-security/) and malware scanning to automatic daily backups and DDoS protection, we take your security seriously, so you don’t have to think twice.
✅ **Developer-Friendly to the Core**
SSH access, staging environments, Git, cron jobs, and PHP version management, all included. We’ve built this for the real builders of the internet.
✅ **Predictable Pricing, No Nasty Surprises**
With Levamo, what you see is what you get. No forced upsells. No charging extra for essentials like backups or staging. Just [powerful hosting at a fair price](/pricing/) that grows with you.
✅ **Loved by WordPress Power Users**
Our customers aren’t shy about sharing their experiences, and they speak volumes. With a [4.8-star rating on Trustpilot](https://www.trustpilot.com/review/rapyd.cloud?) and a growing community of passionate users, Levamo has become the go-to for WordPress professionals who were let down by “big name” hosts.
> Read More: [WordPress Speed Optimization](/blog/wordpress-speed-optimization/)
## Bonus: Tools and Resources to Monitor Website Uptime

When it comes to managing a website, monitoring its uptime and downtime is essential. Here are some tools that can assist you to measure and find reliable hosting providers.
### 1. UptimeRobot

[UptimeRobot](https://uptimerobot.com/) offers 50 monitors with 5-minute checks for free. It allows you to start monitoring in just 30 seconds and currently monitors over 7.5 million monitors for more than 2.1 million users and companies.
**Best for:** Simple, reliable uptime monitoring with generous free limits
- Free plan includes up to 50 monitors
- Checks every 5 minutes (or every 1 minute on paid plans
- Monitors HTTP(s), ping, port, and keywords
- SMS, email, and app alerts
### 2. StatusCake

[StatusCake](https://www.statuscake.com) is built for teams who want to move fast and still catch issues instantly. Their UI is clean, and it’s easy to manage multiple projects.
**Best for:** Fast setup and flexible global monitoring
- Offers SSL monitoring and page speed tracking
- Up to 30-second monitoring intervals
- Integrates with Slack, PagerDuty, and more
### 3. Pingdom

[Pingdom](https://www.pingdom.com/product/uptime-monitoring/) is one of the most trusted names in website monitoring. If you're serious about user experience as well as uptime, this one gives you both.
**Best for:** Visual reports and synthetic transaction monitoring
- Advanced reporting and root cause analysis
- Real-time alerts from over 100 locations worldwide
- Tracks uptime, page speed, and user experience
### 4. Better Uptime

Better Uptime is more than a monitor. It acts like a mini command center for your infrastructure, which is especially useful if you’re a startup or agency managing client sites.
**Best for:** Combining uptime monitoring with incident management
- Native integrations with tools like Notion, Slack, and Zapier
- Uptime checks, screenshots, call alerts, and on-call scheduling
- Beautiful public status pages
## Conclusion
Choosing the right hosting provider is crucial for keeping your website open and working well. This blog walked you through the importance of uptime and downtime, how to measure them, and what to look for in a hosting provider to ensure your website is available when your visitors want to access it. We also discussed tools to monitor uptime and downtime, and resources to find reliable hosting providers. Your website's reliability heavily relies on the hosting provider you choose, so taking the time to make an informed decision is well worth the effort. While there are many good options out there, Levamo stands out as a high-performance managed WordPress hosting provider and [LMS hosting](/managed-lms-hosting/), ensuring your site stays up and runs smoothly.
## Frequently Asked Questions

### What is the best web hosting provider?
The "best" hosting provider largely depends on your specific needs, such as the type of website you're running, your budget, and your technical expertise. However, if you are running a dynamic WordPress site, Levamo is an easy choice. Why? Because of its high-performance infrastructure, 99.99% uptime guarantee, iron-clad security, 24/7 Expert support, and many other factors.
### Who is the fastest and cheapest hosting provider?
The balance between speed, reliability, and cost is vital when choosing a hosting provider. Some providers may offer low prices but compromise on speed or reliability. Levamo, on the other hand, emphasizes delivering top-tier performance and unbeatable uptime, making it a valuable choice for WordPress site owners seeking an optimal balance of speed and cost.
### Which web host is the fastest?
The speed of a web host can be influenced by various factors, including server hardware, network infrastructure, and the optimization of the hosting environment for a specific platform like WordPress. Levamo shines in this aspect with a well-optimized hosting environment that ensures your WordPress site runs swiftly and smoothly, enhancing user satisfaction and SEO positioning.
### How do I find the best web host?
To find the best web host, it's important to identify your needs, research and compare different hosting providers, read user reviews, and consider the technical support and uptime statistics they offer. For example, the best hosting for a static website might not provide the result needed in [LMS hosting services](/managed-lms-hosting/). A high-performance managed WordPress hosting provider like Levamo could be a solid choice, offering a robust infrastructure designed to ensure high uptime and exceptional site performance.
---
## Relay + Object Cache Pro = Amazing WordPress Speed
- URL: https://levamo.com/blog/relay-and-object-cache-pro/
- Category: website-performance
- Author: Sunyyan Junaid
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WordPress speed secrets revealed: Relay + Object Cache Pro for peak performance.
> **Update:** This post is out of date. Levamo no longer uses Relay or Object Cache Pro for caching. Our current setup uses **KeyDB** with Redis object caching to keep dynamic WordPress sites fast under load. For how it works today, read [Faster Dynamic Sites with KeyDB and Object Caching](/blog/key-db-and-redis/).
The modern web demands more than just aesthetics; it demands performance under pressure. Imagine you own a course, community, or membership site, and are hosting a live virtual event. It's a scheduled gathering, and at the set date and time, all your members are attempting to log in and interact in real time. This creates a scenario with hundreds of concurrent users, not just random visitors landing on a page from a link. But soon enough, you find out that your website just can't keep up with such high concurrency.
This could turn a potential success story into a nightmare. However, with Levamo, you're in safe hands. Levamo’s ability to sustain concurrency and scale your website makes sure that every user gets an optimal experience.
Building on that foundation, we're thrilled to announce our collaboration with **Relay and Object Cache Pro**, two top-tier caching tools. These partnerships aren't just about boosting speed; it's about redefining performance standards for WordPress hosting. Let's dive into these exciting collaborations and what they mean for you.
## What is Relay?

[Relay](https://relay.so/) is a next-generation caching layer tailored for PHP, setting it apart from typical Redis™ clients. Designed with the fusion of APCu and PHPRedis' best features, Relay introduces capabilities that redefine caching. It actively manages cache invalidation, ensuring real-time updates, and boasts of resource efficiency that can handle millions of requests seamlessly. Its design is particularly beneficial for hosting services, ensuring that WordPress sites can benefit from unparalleled speed and reduced network communication, enhancing overall performance and user experience.
## What is Object Cache Pro?

[Object Cache Pro](https://objectcache.pro/) is a Redis® object cache backend crafted specifically for WordPress. Prioritizing raw performance, it minimizes unnecessary Redis interactions while maintaining a compact memory footprint. Its design is optimized for popular platforms like WooCommerce, ensuring e-commerce sites run smoothly. Adhering strictly to WordPress’s Object Cache API, it promises stability and compatibility. For Levamo, integrating Object Cache Pro means our users get the advantage of a seamless, high-performance caching solution, ensuring their WordPress sites are both fast and reliable.
## What Do These Partnerships Mean for You?
The integration of Relay and Object Cache Pro into Levamo's managed WordPress hosting service signifies another step in the right direction for performance optimization. Here's what you get from these partnerships.
**Advanced Caching Mechanisms:** The amalgamation of Relay's server-assisted client-side caching and Object Cache Pro's Redis backend optimization introduces a multi-tiered caching mechanism. This ensures that data retrieval is not only swift but also reduces the load on databases, leading to enhanced server response times.
Real-time Data Invalidation: With Relay's active invalidation feature, data consistency is maintained across all cached layers. This means that outdated or stale data is actively purged, ensuring that users always access the most recent version of the content. This is especially important for Levamo's [LMS hosting services](/managed-lms-hosting/).
**Optimized Resource Allocation:** Relay's ability to maintain a partial replica of Redis’ data in the PHP master process's memory, combined with Object Cache Pro's efficient memory footprint, means that server resources are utilized optimally. This leads to reduced overhead costs and maximizes the return on infrastructure investments.
**Free Access to Premium Caching Solutions:** Integrating Relay and Object Cache Pro with Levamo’s service eliminates the need for you to purchase these tools separately, saving $147/m and $95/m respectively. This collaboration brings you premium performance optimization and significant cost savings, allowing more budget for other operational needs.
Enhanced E-commerce Performance: Given Object Cache Pro's extensive optimization for WooCommerce, e-commerce platforms hosted on Levamo can expect faster cart operations, streamlined checkout processes, and overall improved user experiences. This makes us one of the [best hosting providers for WooCommerce](/managed-woocommerce-hosting/).

**Optimized for BuddyBoss Websites & App:** BuddyBoss is also specifically optimized to benefit from these two caching tools. So those who are using BuddyBoss to run their online course, community, and membership can offer customers a smoother experience and better performance on both the website and app.
**Seamless Integration and Scalability:** Both Relay and Object Cache Pro are designed for easy integration with existing systems. This means that current Levamo users can benefit from these enhancements without significant overhauls. Furthermore, as traffic scales, the combined caching solutions can handle increased loads without compromising performance.
In essence, this collaboration is not just a merger of tools but a fusion of visions. With our commitment to delivering unparalleled WordPress hosting performance, we strategically integrated Relay and Object Cache Pro to set new industry benchmarks. This partnership promises a harmonious blend of speed, reliability, and innovation, ensuring that your WordPress sites hosted on Levamo are not just fast but also resilient and future-ready.
---
## Levamo Teams Up with Monarx for Unbeatable WordPress Protection
- URL: https://levamo.com/blog/monarx-security/
- Category: website-security
- Author: Faisal Sarker
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
WordPress security gets easier! See how Levamo & Monarx protect you.
We are thrilled to announce our partnership with **Monarx**, a leading authority in real-time security solutions for web applications.
> **Around 390,000 WordPress websites fall victim to hacking every month**
>
> *Sophos*
This is an alarming statistic that underscores the relentless battle for digital security.
While the precise statistic may send shivers down your spine, the urgency of securing your website remains undeniable.
Our collaboration with Monarx will ensure that your WordPress websites remain fast, responsive, and impenetrable even in the face of the most sophisticated threats.
Let's get to know more about Monarx and how it will help to keep websites hosted on Levamo secure.
## What is Monarx?

> **[Monarx](https://www.monarx.com/)** is a cutting-edge security solution for web hosting. It employs advanced technology to comprehensively understand and prevent malicious activities, offering complete protection for your website.
Unlike traditional security tools, Monarx operates in real-time and employs a signature-less approach. This means it doesn't rely on predefined patterns to identify threats; instead, it comprehensively understands the behavior of files and code on your website. This advanced technology allows Monarx to detect and prevent malicious activities that may have previously gone unnoticed.
The Monarx Agent stays deeply embedded within the PHP engine on the servers, granting it a complete and up-to-the-minute view of web application activity. It can pinpoint precisely what is happening on your site, from code execution to user interactions, allowing it to respond rapidly to emerging threats. Furthermore, Monarx doesn't just react to known issues; it proactively neutralizes payloads from zero-day exploits, offering a level of security that's always one step ahead of cybercriminals.
## What Does This Partnership Mean for You

**Unmatched Security:** With Monarx's signature-less, real-time protection, your WordPress websites hosted with Levamo are now fortified against a wider array of threats than ever before. From known threats to zero-day exploits, Monarx keeps your online presence secure.
**Malware Eradication:** In the unfortunate event that your website falls victim to malware, Monarx's precise removal capabilities ensure that your site is swiftly cleaned, without any data loss or service disruptions.
**Smart Prevention:** Traditional security measures can sometimes lead to false positives or disrupt legitimate user interactions. Monarx's context-aware "smart" prevention minimizes these inconveniences by understanding the context in which threats occur, allowing genuine traffic to flow uninterrupted.
**Global Threat Intelligence:** Levamo's partnership with Monarx connects your website to a global network of threat intelligence. This network, powered by Monarx-enabled servers everywhere, means that emerging threats are identified and neutralized faster than ever, ensuring that your site remains one step ahead of cybercriminals.
**Resource Efficiency:** Monarx's integration directly into the PHP engine is designed to be light on your servers. This means that while providing top-tier security, it won't compromise the performance or resource availability of your website.
Our partnership with Monarx is a game-changer for you. With the integration of Monarx into our managed WordPress hosting services, you no longer need to invest in additional security tools or worry about managing multiple security solutions. Monarx takes care of security seamlessly from behind the scenes, providing comprehensive real-time protection for your websites.
With Levamo and Monarx, your WordPress website is in safe hands, ensuring a secure and seamless online experience for your visitors and customers.
## Why Levamo Chose Monarx
Now let's take a look at the specific reason why we choose to partner with Monarx rather than any other tools on the market.
**Real Time Detection:** Many security providers use patterns or signatures to catch threats. Monarx does better with zero-day exploits detected using behavior analysis.
**Server-Level Integration:** Monarx works within the PHP engine with minimal resource overhead, which is important for high-speed hosting, like on the Levamo.
**Continuous Innovation:** Like us, Monarx is always updating its technologies to stay ahead of new threats. Our commitment to innovation made this partnership easy.
## Looking Ahead
Cybercriminals continue to refine their methods, and security solutions must keep up. With Monarx on board, we've built defenses for today and built defenses for tomorrow too.
The Levamo will continue to:
- Partner with the most advanced security research and tools.
- Maintain world-class speed and low latency performance.
- Offer slick user experiences, from intuitive dashboards to [automated WordPress maintenance](/blog/automate-wordpress-maintenance-guide/).
If you are not yet a Levamo customer, it's time to get hyper-speed performance and real-time security with our [secure WordPress hosting](/managed-security/).
## Frequently Asked Questions

### What is a Monarx?
Monarx is a real-time, signature-less security solution for PHP engines, perfect for WordPress websites. It blocks malicious behavior as it happens, providing proactive protection against known and zero-day threats.
### What is the difference between Monarx and BitNinja?
While BitNinja uses IP reputation and signatures, Monarx uses a behavior-based approach. Monitoring code execution in real-time helps Monarx spot emerging threats faster and reduce false positives more effectively than BitNinja.
### Which is best between Monarx and Imunify360?
Imunify360 provides a firewall and layered defenses. However, Monarx's embedded engine approach provides faster, more accurate zero-day threat detection. Its signatureless method guarantees real-time protection without updates.
### Is Monarx free?
Monarx isn’t usually free. However, we at Levamo partnered with Monarx and included it in our hosting plans at no extra cost.
---
## How To Start A Blog And Make Money - with Checklist
- URL: https://levamo.com/blog/how-to-start-a-successful-blog/
- Category: online-business
- Author: Faisal Sarker
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Start a blog and make money! Use our checklist for a profitable blog.
In today's digital landscape, where online income opportunities abound, blogging for profit emerges as a promising path to financial success. If you've ever wondered how to start a blog and make money, this comprehensive guide is your roadmap to realizing that goal.
According to [productiveblogging](https://www.productiveblogging.com/how-much-do-bloggers-earn/):
> *27% of bloggers start earning money from blogging within 6 months and 38% are making a full-time income within 2 years of starting their blog.*
Let’s explore techniques for maximizing blog earnings through effective monetization strategies and discover affiliate marketing tips and essential tools for successful blogging to enhance your online presence.
Also, we’ll learn methods to boost user engagement on your blog as you embark on your journey toward financial independence
## Why Start Blogging as a Way to Make Money?

If you've been searching for a flexible way to earn income, blogging should be on your radar. Blogging not only allows you to express your creativity and expertise but also offers an array of avenues to make money. From[ affiliate marketing](https://venture.com/domains/affiliatemarketing.com) to sponsored posts and advertisements, the potential to turn a profit is vast.
### Why Should You Consider This?
One of the significant benefits of blogging is its low startup costs. Unlike traditional businesses, which require a substantial initial investment,[ starting a blog](https://www.startablog.com/) is relatively inexpensive. This means that the barrier to entry for aspiring bloggers is quite low, making it an attractive option for many.
### Maximizing Blog Earnings

The versatility of revenue streams is another compelling reason to delve into blogging. You aren't limited to just one way of making money; from blogger-sponsored posts to selling digital products, the opportunities are endless. This flexibility ensures that you can find a revenue model that aligns with your interests and expertise, thereby increasing your chances of making money for blogging sustainably.
**[Image Concept: An Image that showcases a symbolic blogger person sitting on a laptop and different money types surrounding the person]**
### Global Audience Reach
One of the unique aspects of blogging is the potential for a global reach. A well-crafted blog can attract readers from around the world, opening the doors to international opportunities for making money on blogging. Whether it's through affiliate marketing partnerships that have a global appeal or content that resonates with a broad audience, the sky is the limit.
### How Does Blogging Compare to Other Side Hustles?
When compared to other side hustles, blogging offers unparalleled freedom and scalability. You have the creative liberty to produce content you're passionate about and make money with blogging, without the constraints of a 9-to-5 job. As your blog grows, so does your earning potential, making it a scalable venture unlike any other.
### It's a Long-Term Investment
Although blogging isn't a get-rich-quick scheme, it offers sustainable long-term earnings if you are willing to put in the effort. Unlike trendy ways of making money, like viral TikTok videos, a blog is an asset that can provide a stable income for years to come. This is particularly true if you focus on evergreen content that remains relevant over time, thereby maximizing your potential for making money from blogging.
## Tools for Successful Blogging

Starting a blog might seem like a daunting task, but with the right tools and guidance, you can make it happen. In this section, we'll outline the essential elements you need to consider when you're wondering how to start a blog and make money.
### Choosing the Right Niche
Your blog's niche is the foundation upon which you will build your content. Choosing a niche that not only interests you but also has commercial value is crucial for making money on blogging.
#### Why is Niche Important?
Choosing a niche is a crucial first step in figuring out how to start a blog and make money. A focused niche allows you to target a specific audience, making your content more relatable and valuable to them. This increases engagement and the potential to monetize through various avenues like affiliate marketing or sponsored posts. In short, a well-defined niche is the foundation upon which you can build a profitable blog.
### Selecting a Blogging Platform
Once you've identified your niche, selecting the right blogging platform is vital. WordPress is often the go-to choice due to its flexibility and scalability. However, alternatives like Blogger, Wix, and Squarespace have their merits, such as ease of use and design features. Your choice of platform impacts your blog's functionality, its look, and ultimately, your earning potential.
#### WordPress vs. Blogger - What to Choose?
While WordPress offers more customization options, Blogger is user-friendly and easier to set up. You'll need to weigh the pros and cons to decide which platform is best for making money for blogging.

### Investing in Quality Hosting
Investing in quality hosting is a non-negotiable aspect of learning how to start a blog and make money. A reliable host ensures your blog runs smoothly, with minimal downtime and quick loading speeds, both of which significantly impact user experience and SEO rankings. Providers such as [levamo.com](/), [Bluehost](https://www.bluehost.com/), and [HostGator](https://www.hostgator.com/) are top choices in the industry, offering a range of plans to suit different needs and budgets. Selecting a dependable hosting service not only provides a solid foundation for your blog but also contributes to your money-making strategies by optimizing performance and enhancing accessibility.
#### Why Should You Care About Hosting?
Quality hosting not only guarantees round-the-clock website availability but also enhances user experience, boosting your opportunities to make money on blogging. Specifically, hosting solutions tailored for the WordPress industry and blogging-related activities, and that are budget-friendly, can be ideal choices. [Levamo Hosting](/) excels in meeting these criteria and is one of the top contenders in the sector.

### The Importance of a Good Design
When you're contemplating How To Start A Blog And Make Money - with a Checklist, don't overlook the crucial role of good design. A clean, modern layout is more than just eye candy; it's a functional necessity. It sets the stage for user experience and engagement, impacting SEO rankings and, eventually, your revenue stream. The high-quality design invites more interactions and reduces bounce rates, turning casual visitors into loyal readers and, in the long run, contributing to making money with blogging. In essence, a well-designed blog is a pivotal cornerstone in the journey of how to make money from bloggers.
#### What Are the Elements of a Good Design?
Good design includes easy navigation, readable fonts, and color schemes that are easy on the eye. Websites like [BuddyBoss](https://www.buddyboss.com/getting-started-with-the-buddyboss-platform-and-theme/) and [ThemeForest](https://www.themeforest.net/) offer a variety of themes that can help you make money at blogging.
## How Much Does It Cost To Start A Blog?
Understanding the costs involved in starting a blog is crucial for budgeting and financial planning. In this section, we'll break down the potential expenses you can expect when considering how to start a blog and make money.

### Domain Name Costs
When it comes to learning how to start a blog and make money, one of the first steps is securing an impactful domain name. This is more than just a web address; it's the digital identity that your readers will associate with your content. The right domain name not only makes your blog easy to find but also contributes to your credibility, ultimately aiding in how to make money from your blog. Investing wisely in a domain name can set the stage for a profitable blogging journey.
#### Why is a Domain Essential?
A unique domain name adds credibility to your blog and aids in making money on blogging. Domains usually cost around $10 to $15 per year and can be purchased from providers like[ GoDaddy](https://www.godaddy.com/) or[ Namecheap](https://www.namecheap.com/).

### Web Hosting Expenses
We've already touched on the importance of good hosting. The cost can vary depending on the service you choose.
#### Shared Hosting vs. Dedicated Hosting
Shared hosting is cheaper but less reliable, while dedicated hosting offers more stability but is costlier. For those focused on how to make money in a blog, dedicated hosting might be a better investment.
### Additional Costs
Apart from hosting and domain, you may also need to invest in themes, plugins, and potentially even a blog designer.
#### What Additional Tools Might You Need?
If you're serious about how to make money from blogs, investing in premium WordPress plugins and perhaps even a paid theme can set you apart from the competition.
## Effective Blog Monetization Techniques
Content is king when you're figuring out how to start a blog and make money. Let's explore how you can create content that resonates with your audience.
### Understanding Your Audience
In the journey of how to start a blog and make money, understanding your audience is crucial. Knowing your target demographic aids in curating content that resonates with them, contributing positively to how to make money from your blog.
#### Why is Audience Research Important?
Why is audience research important? Well, understanding your readers' needs and preferences is vital for making money with blogging. Utilizing tools like [Google Analytics](https://analytics.google.com/) can offer insights that refine your strategy, further aiding in the blog you create.

### Crafting High-Quality Posts
In the quest of how to start a blog and make money, crafting high-quality posts is non-negotiable. Quality always outweighs quantity; a meticulously researched and well-written article elevates your blog, supporting your goal to make money with blogging.
#### What Does 'High-Quality' Mean?
High-quality posts are those that provide valuable information, are well-researched, and speak directly to the concerns or interests of your readers. This is essential if you're serious about how to make money on a blogger.
## Affiliate Marketing Tips

So you've set up your blog and are producing fantastic content. The next step in how to start a blog and make money is monetization.
### Affiliate Marketing
When exploring how to start a blog and make money, affiliate marketing stands as a popular route. It allows you to promote products or services and earn commissions, serving as an effective strategy for making money on blogging.
#### How Does Affiliate Marketing Work?
In affiliate marketing, you promote products for other companies and earn a commission for each sale made through your unique affiliate link. Websites like[ ClickBank](https://www.clickbank.com/) can help you find products to promote.

### Setting Up a Membership Site
Membership and subscription business market are on the rise and you can leverage it to earn money through your blog. Create one or more membership levels and use content restriction to allow only the paying members to read your exclusive blog content. Herein, you can offer some of the content for free and premium guides, works, or highly professional blogs only for paying members.
#### Using a Plugin to Set Up Member Levels
With an all-rounder WordPress Plugin like [ARMember](/blog/armember-membership-plugin/), you can create different types of membership levels like free, paid (finite & infinite), and recurring subscription. Its powerful content restriction rules lets you keep your content locked away for paying members. The features like drip content and pay per post allows for a wider control over your blogging website. It is an all rounder tool because it offers multiple monetization methods along with email marketing, member community management, and social features.
### Ad Revenue
If you're keen on making money on blogging, consider ad revenue as a viable income stream. Placing ads on your site can bring in consistent revenue over time.
#### Popular Ad Networks
To capitalize on making money from blogging, networks like Google AdSense and [Media.net](https://www.media.net/) are popular choices. They offer various ad types to monetize your content effectively.

## Metrics to Monitor for Blog Success
Monitoring the right metrics can give you great insights into how to make money in a blog.
### Traffic Analysis
Traffic analysis is crucial for evaluating your blog's performance. It provides insights into visitor numbers and behavior, guiding content and SEO strategies to enhance your blog's success
#### Why is Traffic Important?
The more traffic you have, the more opportunities you have to make money with blogging. Tools like[ Google Analytics](https://analytics.google.com/) can provide traffic data.

### Boosting User Engagement on Your Blog
Comments, shares, and the average time spent on your blog are also crucial metrics. Tools like[ BuzzSumo](https://buzzsumo.com/) can help measure user engagement, which is essential for making money from blogging.
### Embarking on Your Blogging Journey
Launching a blog can be an incredibly fulfilling experience, particularly when your eyes are set on how to start a blog and make money. It's not just about writing but also about turning your passion into profit.
### A Recap of Key Steps:
As we've navigated through the essential stages, this summary will act as your **quick guide to making money** from blogging. Make sure you've ticked off each critical component for a successful venture.
### Are You Ready to Launch?
Starting a blog and monetizing it is a fulfilling journey that combines passion with financial gain. The path involves several steps such as choosing a niche, setting up the blog technically, creating engaging content, and leveraging monetization strategies like affiliate marketing or ad networks. Our comprehensive guide and checklist serve as a roadmap, ensuring you navigate through each phase effectively. With persistence, learning, and the right strategies, you can turn your blog into a revenue-generating platform.
So, kickstart your blogging adventure today!
## Frequently Asked Questions

There are a lot of questions that beginners ask about starting a blog and we answered some of the most common ones here.
### What are The Key Steps for A Profitable Blog?
Discover how to choose the right niche, maximize blog earnings, and engage your audience effectively.
### What's The Importance of Niche Selection in Blogging?
Choosing the right niche is crucial for profitable blogging; it aligns with your interests and attracts readers.
### Which Hosting Option is Better for Bloggers, Shared or Dedicated?
Compare shared hosting's affordability with dedicated hosting's stability to make an informed decision.
### How Do I Boost User Engagement on My Blog for Better Earnings?
Implement tools and strategies to enhance user engagement, driving more profit from your blog.
---
## Compare Cloud Hosting Costs: Choosing the Right Web Host
- URL: https://levamo.com/blog/how-much-does-cloud-hosting-cost-2/
- Category: hosting
- Author: Sunyyan Junaid
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Cloud hosting costs decoded! Find the right web host for your budget now.
Cloud hosting is becoming a big deal for anyone wanting to start a website. In 2025, global spending on public cloud services is projected to reach **$723.4 billion**, reflecting a 21.5% increase from the previous year. And Cloud hosting prices differ from company to company and industry to industry, but the real question is: how much do *you* need to invest to get your website up and running?
This guide is here to help you figure out cloud hosting prices. If you were initially looking for GoDaddy hosting prices but then changed your mind and now want to go for [cloud hosting](/) (even if it's low-cost cloud hosting options), that's the best decision you've made, and you'll soon find out why.
Let's dive into cloud hosting costs and start your online adventure on a budget!
## Understanding Cloud Hosting

### What is Cloud Hosting?
Cloud hosting is like having your website live in a big apartment complex instead of a single house. Your website gets its own space, but it shares resources like electricity (which in this case is the server power) with other apartments. This way, if something goes wrong in one server (or one part of the apartment complex), your website can still keep running smoothly because it can use resources from other servers.
### Comparison with Traditional Hosting Solutions
In a traditional webhost, your website lives in a single house (server). If anything goes wrong in this house, like a power outage (server failure), your website goes down. But in cloud hosting, because your website is in an apartment complex with many resources, it stays up and running even if one part has a problem. It's like having a backup plan. Plus, in cloud hosting, you can get more resources whenever you need them, which is harder or not possible with traditional hosting
## Factors Influencing Cloud Hosting Cost
### The Scale of Operations
Imagine you're throwing a party. A bigger party with more guests will cost more money. Similarly, if your website has a lot of visitors or a lot of data, it's like a big party, and you'll need to spend more on cloud hosting to keep everything running smoothly.
### Resources Required (CPU, RAM, Storage, Bandwidth)
These are the different ingredients needed to run your website.
- **CPU (Central Processing Unit):** It's the brain of the computer that handles all the tasks. More complex tasks need a stronger brain, which costs more.
- **RAM (Random Access Memory):** This is like the short-term memory of the computer. The more stuff you need to remember at once, the more RAM you need, which will cost more.
- **Storage:** This is where all your website's data is kept, like photos, videos, and text. If you have a lot of data, you'll need more storage, which will increase the cost.
- **Bandwidth:** This is like the width of the road leading to your website. A wider road allows more visitors to come to your site at the same time, but it also costs more.
### Types of Cloud Hosting
Public, Private, or Hybrid: These are different kinds of cloud hosting, just like there are different kinds of houses.
- **Public Cloud Hosting:** This is like living in an apartment building. It's cheaper because you share the space with others.
- **Private Cloud Hosting:** This is like living in your own house. It's more expensive, but you get all the space and resources to yourself.
- **Hybrid Cloud Hosting:** This is a mix of both. It's like having a house with a shared yard. You get some private space but also share some resources, balancing cost and privacy.
## Dive into Cloud Hosting Cost

### Cloud Hosting Pricing Models
Just like there are different plans for phone bills, there are different pricing models for cloud hosting, too. Some charge you a fixed rate every month, while others charge you based on how much of the resources (like server space and power) you use. We'll go through these two models to help you understand which one might work best for you.
- **Subscription Model:** This is like buying a monthly bus pass. Whether you ride the bus once or twenty times, the cost stays the same. Similarly, with a subscription model, you pay a fixed amount every month, no matter how much or how little you use the hosting services.
- **Pay-as-you-go Model:** This is like paying for a bus ride every time you take one. If you ride a lot, you pay more. If you ride a little, you pay less. In the pay-as-you-go model, you only pay for the cloud hosting resources you use, so if your website gets a lot of visitors one month, you'll pay more, and if it gets fewer visitors another month, you'll pay less.
### Breaking Down Cloud Hosting Cost
Understanding the cloud hosting cost is crucial for anyone looking to start a website. Cloud hosting costs can vary widely depending on several factors. On average, for a small server with **1GB of RAM**, **25GB SSD storage**, and **1 CPU core**, the cost is around $4.55 per month. However, prices can start as low as $2.75 per month or $5 per month for some plans
The prices go up based on how much more storage, bandwidth, and CPU cores you need.
Although cloud hosting tends to be more expensive than traditional hosting, the benefits, such as scalability, flexibility, and better performance, often outweigh the cost difference. There are also some low-cost cloud hosting options, but they often perform worse than standard, so we suggest you not run to the lowest possible offering.
### Hidden Costs to be Aware Of
Now, back to the road trip example, what if your car breaks down or you get a flat tire? Those are unexpected costs that can sneak up on you. In cloud computing, there might be extra costs like additional security or sudden spikes in traffic to your website that can also surprise you. We'll talk about these hidden costs so you can plan better and avoid nasty surprises.
## Cloud Hosting Cost Management Strategies

### Tools and Practices for Managing Cloud Hosting Costs
Think of managing your cloud hosting costs like keeping track of your household bills. There are tools and habits you can use to keep your spending in check. For instance, you might use budgeting software or set reminders for due dates. Similarly, we’ll discuss tools and habits that can help you keep an eye on your cloud computing costs and make sure they don’t spin out of control.
### Cost Optimization Strategies
Now, imagine you find ways to lower your electric bill by using energy-saving bulbs or turning off lights when you leave a room. These are strategies to optimize or reduce your costs. In the same way, we’ll share strategies to help you get the most out of your cloud hosting without spending more than you need to. This could include things like adjusting your hosting plan based on your website’s needs or using built-in tools to monitor and reduce your usage.
## The Economic Advantages: Cloud Hosting Cost Benefits
### Exploring the Financial Benefits of Cloud Hosting
Imagine you decide to buy a bicycle to get to work instead of taking the bus. Initially, it might cost you to buy the bicycle, but over time, you save money on bus fares. Similarly, cloud computing might have some costs upfront, but it can save you money in the long run. For instance, it could lower your costs of keeping your website running smoothly, even when lots of people visit it. We'll explore more financial benefits like this to show you how cloud computing can be a good deal for your wallet.
### Return on Investment (ROI) analysis
Now, back to the bicycle example. If you calculate how much you spent on the bicycle versus how much you saved on bus fares, you can figure out if buying the bicycle was a good investment. Similarly, we'll help you understand how to calculate the Return on Investment (ROI) for cloud computing. By comparing the money you spend on cloud computing to the money you save or earn because your website runs better, you can see if cloud computing is a good investment for you.
## WordPress and Cloud Hosting: A Match Made in Cyberspace

Think of [WordPress](/managed-wordpress-hosting/) as a favorite game you love to play, and cloud hosting as a high-powered gaming console. When you play your game on a high-powered console, it runs smoothly, loads quickly, and rarely crashes. Similarly, when you host your WordPress site on the cloud, it runs faster, handles traffic better, and has fewer problems like site crashes.
Now, you might be wondering about the WordPress cloud hosting cost. Just like different gaming consoles have different prices, hosting WordPress on the cloud can have different costs too. The price can depend on how powerful a “gaming console” (cloud host) you choose for your “game” (WordPress site). A cheap managed WordPress hosting will always perform less than hosting that is priced correctly.
Based on the features on offer, Levamo offers the best value for money when it comes to [WordPress cloud hosting](/managed-wordpress-hosting/). In the following section of our blog, we will get to know more about Levamo.
## Is Levamo the Best Cloud Hosting for WordPress?

Levamo is the [highest-performance managed WordPress hosting](/performance/) on the planet. It is crafted for dynamic, feature-rich WordPress sites that demand high concurrency, even during traffic spikes. With **[LiteSpeed Servers](/blog/lite-speed-hosting-benefits/)** and **MariaDB**, we ensure enhanced query speed and server-level caching alongside complex database query caching.
Levamo also offers an intuitive dashboard for effortless website management. Features like 1-click staging, secure file management, database management, team collaboration tools, site cloning, and integrated domain management are all at your fingertips. The robust web application firewall and high-performance PHP execution engine further ensure that your site runs smoothly and securely.
If you compare the features with the price point that Levamo comes in, considered as the best [Kinsta alternative](/kinsta-alternative/), it is unarguably the best cloud hosting provider for WordPress sites.
## Conclusion
In this blog, we went through some important things like the different types of cloud hosting, what affects the cost, and how to save money.
Choosing the right cloud hosting can be like choosing the right home for your website. It's an important decision that can affect how well your website works and how much money you spend or save. We'll leave you with some tips and ideas on how to evaluate cloud hosting costs wisely as you set out to start your website, so you can make a choice that you'll be happy with in the long run.
---
## AI Website Builder: The Complete Guide in 2025
- URL: https://levamo.com/blog/guide-to-ai-website-builders/
- Category: wordpress
- Author: Faisal Sarker
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Explore AI website builders: features, top 10 tools, and the future of web design.
Feeling tired of manual web development? **AI Website Builders** are here to make the process easier for you.
According to grandviewresearch,
> The global artificial intelligence market size is projected to expand at a compound annual growth rate (CAGR) of 37.3% from 2023 to 2030. It is projected to reach $1,811.8 billion by 2030.
This guide covers all facets of **AI Website Builder**, including their mechanics and impact on web design. You'll learn about what key features you need to consider before using one. Here we'll provide a top 10 list of **AI-powered website builders** for 2024. These tools are not just a trend that will fade out. It's the future of web development, influencing everything from design to SEO optimization.
Stay ahead with this must-read guide.
## Understanding AI Website Builders: An Overview

Artificial intelligence-based website builders simplify website creation process. With their user-friendly interfaces, even beginners can build professional websites without any struggle. These AI builders automate various tasks from layout design to content creation which saves both time and effort.
### Defining AI Website Builders
AI website builders use the power of artificial intelligence to create and manage web pages as per need without implementing any code from the user end. By utilizing algorithms, these high-tech builders automate the website creation process. They eliminate the requirement for technical expertise on each segment creation of a website. AI web builders offer attractive templates and drag-and-drop editors for easy customization. With real-time editing capabilities, AI website builders allow users to personalize their websites without having any kind of programming knowledge.
These platforms increasingly integrate [responsible AI solutions](https://intellias.com/responsible-ai/) to ensure accessibility standards and optimize user experience across different devices
### Future of AI-empowered Web Design
The future of AI-powered Website builders is most promising in every way. AI website builders use advanced AI algorithms to analyze user preferences and requirements for generating personalized website designs. They optimize website layout, color schemes, and font choices using AI. Additionally, they offer various tools for logo design, content creation, and SEO optimization too.
op AI Website Builders for 2024
The top AI website builders for 2024 are equipped with powerful tools and features that simplify website creation. You must read about each of them and then choose the one that fulfills your demands.
### 1. Wix ADI

[Wix ADI](https://users.wix.com/signin), an AI-powered website builder, offers personalized websites based on user preferences. By answering simple questions, users can generate a customized website layout. Wix ADI provides SEO optimization, integration with popular third-party apps, and the ability to add custom domain names for a professional online presence.
### 2. Divi AI

[Divi AI ](https://www.elegantthemes.com/ai/)is an AI website builder that offers a drag-and-drop editor for easy customization. With its pre-designed templates and content modules, users can create stunning websites without any coding or technical knowledge. Divi AI also provides advanced SEO tools and optimization features to improve website visibility.
### 3. 10Web

[10Web ](https://10web.io/ai-website-builder/)is an AI website builder that offers a wide range of templates and layouts catering to various website types. With its intuitive drag-and-drop editor and design elements, users can effortlessly customize their websites according to their preferences.
### 4. Shopify AI

[Shopify AI ](https://www.shopify.com/website/builder)is a specialized AI website builder that focuses on creating online stores. It offers a wide range of professionally designed templates that users can choose from to showcase their products effectively. With powerful tools for inventory management, order processing, and secure payment gateways, Shopify AI makes it easy for businesses to manage their online stores.
### 5. Jimdo AI

[Jimdo AI](https://www.jimdo.com/website/how-to-create/) is an AI-powered website builder that simplifies the process of creating a website. With professionally designed templates and a user-friendly drag-and-drop editor, users can easily customize their websites. Jimdo AI also offers SEO optimization features to improve website visibility on search engines.
### 6. Unbounce AI

[Unbounce AI ](https://unbounce.com/product/landing-pages/)is a powerful AI website builder that focuses on creating high-converting landing pages. With a variety of templates optimized for different marketing campaigns, users can easily customize their landing pages and track conversion rates. The user-friendly interface allows for quick and efficient landing page creation, while integration with popular email marketing platforms enables effective [lead generation](https://www.clodura.ai/blog/lead-generation/).
### 7. Framer AI

[Framer AI](https://www.framer.com/ai) provides powerful tools for creating visually stunning websites, making it an ideal choice for web designers and developers. With Framer AI, you can design web pages without any coding knowledge, thanks to its intuitive and user-friendly interface. The AI-powered platform simplifies the website creation process, allowing you to create your website in minutes. Customize and edit your website effortlessly using Framer AI's AI website builder.
### 8. ClickUp AI

[ClickUp AI](https://clickup.com/features/ai), an AI-powered project management tool, is revolutionizing web development. By utilizing artificial intelligence, ClickUp AI optimizes workflow and enhances productivity. Real-time collaboration and communication features enable efficient web design projects. With automation capabilities, repetitive tasks are streamlined, allowing web developers to focus on more creative aspects.

### All Your Websites.
One Powerful Platform.
With the **Multiple Site Plans**, now you can
**launch 5, 10, or 100+ websites** on a single Hyperspeed platform.
[Get Early Bird Pricing Now](/pricing/)
## Why Use AI Website Builders

AI website builders bring a lot of interesting features that make it easy for you to build a proper website.
### Real-Time Website Editing
An AI website builder is an innovative tool that can help you easily create a professional-looking website. One of the best features of an AI website builder is real-time editing, which allows you to keep your content fresh and up-to-date always! With this extremely important feature, you can change your website's written and visual content, layout, and design in just a few minutes. This makes AI website builder an excellent choice for businesses or individuals looking to create a dynamic and engaging online presence without facing any hassle.
### User-friendly Interface
AI website builders provide a seamless experience with their user-friendly interface. Creating a website becomes effortless, thanks to its drag-and-drop editor and intuitive navigation.
Even without technical expertise, anyone can design a professional website with just a few clicks. The AI tools eliminates the complexities of coding, enabling creators and web developers to focus on the creative aspects.
### Customization Options
These marvelous builders offer a diverse range of customization options to create a unique website. Users have the flexibility to customize various aspects of their site, including the layout, color scheme, and font choices.
Through AI-powered tools, these builders suggest design elements that align with the user's preferences and industry. With an AI website builder, personalizing your website to reflect your brand identity is effortless.
### SEO and Marketing Tools
Using both SEO and marketing tools is essential for a website that needs to come and remain in the spotlight. AI-driven website builders offer a range of SEO and marketing tools to boost online visibility. These tools optimize website structure, meta tags, and keywords for improved search engine rankings. With AI-powered analytics, businesses gain insights into website performance and visitor behavior.
## AI & Future Web Design

AI-empowered web design is the future because it leverages artificial intelligence to create personalized and user-friendly websites. With real-time optimization, AI-powered sites adapt to user behavior and preferences, providing a seamless experience across devices. Automation of repetitive tasks saves time and resources.
### AI's Effect on Web Design

AI has revolutionized web design and [web hosting trends](/blog/web-hosting-trends/) by enabling personalized and dynamic website experiences. Through AI algorithms, user data is analyzed to deliver tailored content and recommendations. Additionally, AI-powered chatbots provide instant assistance, enhancing user engagement on websites. AI-driven design elements, such as color schemes and layouts, optimize user experience and engagement. Integrating a local LLM can further personalize the experience, allowing websites to better understand user intent and offer more accurate, context-aware interactions.
[LLM agents](https://www.superannotate.com/blog/llm-agents) add another layer of intelligence by coordinating multiple tasks behind the scenes, making websites feel more responsive and intuitive.
### Predictions for AI in Web Development
As we look ahead to the future of web development, AI is set to play an even more integral role. With its ability to automate processes and reduce time-to-market, AI will continue to be a game-changer.
Machine learning algorithms will enable AI to create more accurate and personalized website designs, enhancing the user experience. AI will also enhance security measures by detecting and preventing cyber threats in real time.
### Google's Stance on AI Web Design
Google[ ](https://www.google.com/)does not punish websites that are built using AI. AI-powered website builders can help improve your website's performance and user experience, which Google values highly. As long as your website follows Google's guidelines for quality and relevance, using AI to build it will not result in any penalties or negative impact on your search rankings. In fact, the advanced algorithms used by AI technology can help optimize your website for better visibility and ranking on search engine results pages.
### AI Website Builder for WordPress
WordPress[ ](https://www.google.com/aclk?sa=l&ai=DChcSEwimnPXa7s6BAxU5GoMDHdWYAwsYABACGgJzZg&gclid=CjwKCAjwyNSoBhA9EiwA5aYlb1jgFzajgNglEvHZb2b1g5oZzOiIXawQ5oYg3HT72XwMXtjpewMPABoCfw8QAvD_BwE&sig=AOD64_0ZgfmbL3UH0hjfmjAc77QJ5c_XsA&q&adurl&ved=2ahUKEwjXhu3a7s6BAxV9T2wGHX4tBQUQ0Qx6BAgPEAE)is one of the most popular website-building platforms. However, building complex WordPress sites can be time-consuming and challenging, especially for those who are not tech-savvy. This is where [AI website builders](/blog/wordpress-ai-website-builder/) come in. AI-powered website-building features can make the process of creating a complex WordPress website simple and fast.
Right now popular WordPress page builders like [Elementor](/blog/elementor-review/) are already trying to offer new AI-based website-building features for rapid website development.
## Conclusion
AI site builders are like having a personal web designer around the clock, without the cost. This guide explained how those tools harness AI for everything from template selection to content creation. You may be a solo entrepreneur, small business owner, or an experienced developer who needs efficiency, AI website builders will help you create professional-looking websites in an increasingly crowded digital space.
They're convenient and flexible. Most AI-powered tools allow real-time editing, instant previews, and even SEO recommendations to optimize your site for discovery. That means you can work on fine-tuning your brand identity or building your product lineup instead of coding lines of code. Often, AI website builders offer integrated email marketing / eCommerce / social media tools for building an online presence.
Looking forward, AI in web design is practically limitless. Expect more sophisticated features like intelligent analytics, voice-activated design commands, and hyper-personalised template suggestions based on user behavior. As those technologies evolve so will your opportunities to engage online audiences in new, creative ways. If you want to turn your vision into reality without coding for weeks or months, you should look into an AI website builder. So embrace the shift, experiment freely & watch your digital footprint grow.
## Frequently Asked Questions

Now let’s share some common questions regarding AI Website building that we often see on the internet, along with their answers.
### What are AI Website Builders?
AI Website Builders are tools that leverage artificial intelligence to automate and enhance various aspects of website development, from design to SEO optimization.
### How Do AI Website Builders Impact SEO Optimization?
AI Website Builders can automatically analyze data and implement SEO strategies, improving search engine rankings and user engagement.
### What are The Key Features to Consider in an AI Website Builder?
Look for features like intuitive UI, automated design suggestions, and built-in SEO optimization tools when selecting an AI Website Builder.
### How do AI Website Builders Influence Web Design Trends?
AI Website Builders are shaping web design by introducing dynamic, personalized elements and better SEO optimization, setting the trend for modern web development.
---
## 21 Best Online Business Ideas You Can Start Today
- URL: https://levamo.com/blog/best-online-business-ideas/
- Category: online-business
- Author: Faisal Sarker
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Find 21 online business ideas you can start today. Your success awaits!
With the surge of technology and the extensive reach of the internet, starting an online business is easier and more attractive than ever before. More and more aspiring entrepreneurs are exploring the best online business ideas and leveraging the digital world to convert their passions and skills into lucrative ventures.
[As of 2023, the number of online buyers stands at 2.64 billion. Which is a whopping 33.3% of the population worldwide.](https://www.oberlo.com/statistics/how-many-people-shop-online) With such a broad spectrum of potential customers, online businesses can cater to multiple demographics, enhancing their reach and profitability.
However, the multitude of available options can also make it overwhelming to choose the right business idea. You need to assess your strengths, preferences, and market demands meticulously to identify the optimal path to embark on. In this blog, we will share plenty of ideas, so that you can choose the right one for your business.
Without further ado, let’s get started.
## Why Start an Online Business in 2024?

Online businesses have seen a monumental rise in popularity. [The online coaching market is anticipated to grow at a CAGR of 13.4% between 2022–2030](https://growthmarketreports.com/report/online-coaching-market-global-industry-analysis). A prevailing misconception is the dominance of this market by large-scale operators.
However, new entrepreneurs can still carve out their place by focusing on unique, well-researched business ideas that fill a gap in the market. The online space is rich with tools and resources that can help newcomers learn quickly, reach their audience effectively, and adapt to the ever-changing landscape of consumer needs and technological advancements. With the right approach, dedication, and a willingness to learn and adapt, you can still build a brand, connect with your audience, and create value.
So there’s no doubt that it is still feasible to start an online business in 2023.
## The Advantages of Starting Online Businesses

There are plenty of reasons you should consider launching an online business. Here are some of the key reasons to get started with a business over the Internet.
### 1. Flexibility
With an online business, you have the liberty to work from anywhere, anytime, offering avenues to earn passive income, which is one of the online businesses to earn money.
### 2. Global Exposure and Scalability
Being online means your services can be marketed globally without significant investments, breaking geographical barriers.
### 3. Low Overheads
The lack of physical spaces translates to significantly lower overhead costs, making them the best online businesses to start.
### 4. Easy Scaling
Online businesses can add more services or products as they grow, without worrying about physical space constraints.
### 5. Low Startup Costs
Online businesses typically have lower initial costs, making entrepreneurship accessible to a broader audience.
As you can see, online businesses come with loads of advantages over traditional businesses. And when you choose the perfect niche, your chance of becoming successful gets even higher. So let’s explore the the best online business ideas for you to choose from.
## Exploring the Best Online Business Ideas
The good news is that starting an online business is wider than just offering products online. There are numerous business models to choose from - such as offering services, or membership sites.
Here's a list of the best online business ideas to start in 2023:
### 1. E-commerce Store: A Scalable and Best Online Business to Sell Products Globally

Establishing an e-commerce store is a scalable and potentially lucrative online business idea. Selecting a niche, sourcing or creating products, and building a customer base can lead to a successful online store. With platforms like Shopify or WooCommerce, entrepreneurs can create customized online shops, reaching customers globally and selling diverse products, from handmade crafts to tech gadgets.
### 2. Affiliate Marketing: Best Online Business to Earn Money
Affiliate marketing is one of the best online business ideas, allowing you to earn commissions by promoting products relevant to your audience. It is a lucrative path, especially for blog owners and influencers, offering a passive income stream by leveraging platforms like [Amazon Associates](https://affiliate-program.amazon.com/) and integrating seamless product recommendations within your content, thus enhancing user experience and trust.
### 3. Online Course: Top Online Business I Can Start Today
If you have a wealth of knowledge in a particular field, virtual teaching can be one of the most rewarding online businesses to start. Creating online courses or webinars on platforms like Teachable allows for interactive and comprehensive learning experiences. This business model caters to the ever-growing demand for online learning, providing flexibility and accessibility to a global audience.
### 4. Personal Fitness Training: Great Online Business Idea for Health Enthusiasts

With health consciousness on the rise, online personal fitness training is a booming and profitable online business. Offering personalized workout regimes, nutritional guidance, and motivational support can make a substantial impact while also ensuring your economic success.
### 5. Membership Sites: A Best Online Business to Cultivate Community
[Starting a membership site](https://www.buddyboss.com/membership-platform/) is one of the great online business ideas for consistent income. By providing exclusive, high-value content or resources to your members, you foster community and loyalty. This business model is adaptable to various niches, from education to entertainment, and is key to establishing a dedicated follower base eager for premium content and perks.
### 6. Online Marketplaces: An Innovative Online Business to Do in 2023
Developing a specialized online marketplace is a lucrative online business to start. Whether focusing on handmade crafts, digital assets, or unique products, a well-curated platform can attract a dedicated buyer base. This model allows for a diverse range of sellers to showcase their products to a targeted audience, fostering community and commerce around specific interests or industries.
### 7. Dropshipping: A Leading Online Business to Start for E-commerce Aspirants

Among the list of online business ideas, dropshipping offers a low-investment entry into e-commerce. By handling sales while suppliers manage inventory and shipping, entrepreneurs can focus on marketing and customer service. This model, coupled with a well-chosen niche and effective marketing strategies, can lead to a successful online store with substantial profit margins.
### 8. Freelance Writing: A Rewarding Online Business to Earn Money
Freelance writing remains one of the best online businesses to start for individuals with a passion for words. The demand for quality content across industries is ever-present, ranging from blog posts to advertising copy. Utilizing platforms like [Upwork](https://www.upwork.com/) allows for a diverse client base and project variety, ensuring a steady stream of opportunities for earning and skill development.
### 9. Podcasting: A Promising and Profitable Online Business to Start
Podcasting is a fast-growing medium of entertainment, making it one of the great online business ideas. Whether discussing hobbies, academic subjects, or pop culture, creating engaging auditory content can captivate audiences. Monetization through sponsorships, memberships, and merchandise can turn a passion for dialogue into a rewarding online venture.
### 10. App Development: A Best Online Business to Start in the Tech Realm

In the mobile-centric world, app development is a highly profitable online business to do. Identifying needs and creating innovative solutions can lead to successful products, whether utility apps, games, or productivity tools. This field offers the potential for substantial financial success and the opportunity to shape the way people interact with technology daily. Additionally, [enterprise software development services](https://www.intellectsoft.net/services/enterprise-software-development) play a key role in helping businesses build scalable and efficient apps tailored to their specific needs.
### 11. Graphic Designing: Creative Online Business to Earn Money
In this era of visual communication, graphic designing can be a lucrative online business idea to earn money. Creating compelling visuals for brands can significantly impact brand perception and success. From logo designs to marketing collateral, offering high-quality design solutions can lead to a successful freelance career or a thriving design agency.
### 12. Virtual Assistance: Essential Online Business to Start for Administrative Support
Virtual assistance is a versatile online business catering to the diverse administrative needs of businesses and entrepreneurs. From managing emails to scheduling appointments, providing efficient and reliable support can lead to long-term collaborations and a steady income stream. This role is crucial for the smooth operation of many online businesses, highlighting its importance and demand.
### 13. Blogging: A Best Online Business to Provide Informative Content

[Blogging](/blog/how-to-start-a-successful-blog/) is still alive and well. Event in 2023, it is one of the best online business ideas to earn money. With a blog, you create informative and engaging content that can attract a loyal audience. By focusing on a specific niche and offering valuable insights, you can monetize through various channels, including ads, affiliate marketing, and sponsored content, building a sustainable and rewarding online presence.
### 14. SEO Consultancy: A Top Online Business Idea to Optimize Digital Presence
SEO consultancy is a demanding profession in recent times, making it a profitable online business to start. By assisting businesses in optimizing their online presence to rank higher on search engines, SEO consultants drive organic traffic, enhancing brand visibility and credibility. Leveraging SEO tools and strategies, consultants can offer comprehensive solutions, from keyword research to link-building, contributing to the online success of their clients.
### 15. Social Media Management: A Strategic Online Business to Start Today
In the interconnected social era, social media management is a highly sought-after online business idea. Managing and curating brand narratives on platforms like Instagram and Twitter can shape brand identity and community. Effective social media management involves content creation, audience engagement, and analytics review, establishing a coherent and appealing brand presence across diverse platforms. Moreover, understanding [social media reporting](https://reportgarden.com/social-media-reports) metrics is essential for optimizing strategies and identifying growth opportunities.
### 16. E-Book Publishing: Best Online Business to Share Knowledge Digitally

E-book publishing stands out among great online business ideas, allowing for knowledge sharing in accessible digital formats. Whether it’s fiction, non-fiction, or educational material, e-books have a global reach. Authors and publishers can leverage platforms like [Amazon Kindle Direct Publishing](https://kdp.amazon.com/), enabling the sharing of insights and stories to a worldwide audience, while also offering a sustainable income source.
### 17. Web Development: Innovative Online Business to Build Digital Platforms
The internet is evergrowing. And as long as it is growing, web development will remain a great online business idea. Developing sleek, user-friendly websites is essential in the digital economy. Whether running a freelance business or establishing a web development agency, creating websites that meet client specifications and user needs can lead to a successful online venture and a substantial income.
### 18. Event Planning: A Detailed Oriented Online Business to Start
Online event planning is a versatile and creative online business to earn money. Planning and coordinating events, from webinars to online meetups, demands organizational and interpersonal skills. Utilizing online tools for invitations, RSVPs, and live streaming can streamline the process, creating memorable and smooth experiences for clients, and making it a lucrative and fulfilling online venture.
### 19. Digital Marketing Agency: A Profitable Online Business to Enhance Brand Visibility

Starting a digital marketing agency is one of the best online businesses to start in the contemporary commercial landscape. By offering services like content creation, email marketing, and PPC advertising under a single umbrella, you can significantly impact a brand’s online reach and conversion rates. A digital marketing agency can acquire long-term clients and attain substantial growth and revenue by delivering results-driven solutions.
### 20. Photography: A Captivating Online Business to Capture Moments
Selling stock photography is a creative and fulfilling online business that you can start today. You can utilize platforms like Shutterstock for stock photos or offer specialized photography packages that can meet varied client demands, translating your artistic skills into a rewarding online profession.
### 21. Online Consultation: A Profitable Online Business to Start
In recent times, online consultation is among the best online business ideas to earn money. Leveraging your expertise to guide individuals or businesses can help you create a sustainable income stream. From life coaching to business strategy, the opportunities are diverse. Utilizing platforms like [BuddyBoss](http://www.buddyboss.com), you can easily take interactive sessions, while creating a community that can lead to a steady client base, fostering growth and reputation in your chosen niche.
## What is the Best Online Business Nowadays?

Below is the list of the best online business ideas in recent times:
- E-commerce Store
- Affiliate Marketing
- Online Course
- Personal Fitness Training
- Membership Sites
- Online Marketplaces
- Dropshipping
- Freelance Writing
- Podcasting
- App Development
- Graphic Designing
- Virtual Assistance
- Blogging
- SEO Consultancy
- Social Media Management
- E-Book Publishing
- Web Development
- Event Planning
- Digital Marketing Agency
- Photography
- Online Consultation
There is no single answer when it comes to the best online business idea. That’s because it depends on your skill, passion, and capital. While some businesses can be started without any budget (like blogging), they often need certain skills. Other businesses might not need any skill straightaway (like an eCommerce site), but you would need a significant amount of investment upfront. So we suggest you find the best business idea for you, from the list that we shared above.
## Empowering Your Online Business with Levamo Managed Hosting for WordPress
Once you've settled on the best online business ideas that align with your goals and expertise, establishing a solid online presence is the next big step. This is where Levamo Managed Hosting for WordPress becomes invaluable. Whether your venture is into e-commerce, blogging, or consulting, our hosting solutions ensure that your website is secure, fast, and reliable, providing an unparalleled experience for your users.
**Effortless Handling of High Demands:** Designed to effortlessly manage websites with high resource demands, Levamo ensures seamless performance during traffic peaks, pivotal for user experience, conversions, and revenue.
**Dynamic Performance and Automated Scaling:** Levamo’s features include dynamic performance adjustments and automated scaling to ensure resources are always optimized to meet demand, ensuring consistent responsiveness and reliability of your site.
**Enhanced User Experience:** With the superior technology of Levamo Managed Hosting for WordPress, your website provides an optimal user experience, a critical component in building a successful online business.
**Focus on Growth:** Choosing Levamo allows you to concentrate on expanding your brand and reaching a wider audience, without the worry of website management, turning your online business ideas into prosperous realities. Kickstart your journey in the online world with the robust support of [levamo.com](/), and watch your online business idea blossom into a successful venture.
---
## Automate Your WordPress Security with Patchstack on Levamo
- URL: https://levamo.com/blog/automate-with-patchstack/
- Category: news
- Author: Faisal Sarker
- Published: 2023-10-02
- Status: historical
- Freshness note: This article may contain older Rapyd Cloud-era wording or superseded product details. Current product pages are authoritative.
Harden WordPress! Patchstack security now integrates with Levamo. Read more.
According to Patchstack; ***[In 2022, a staggering 26% of WordPress plugins with critical security bugs did not receive a fix](https://patchstack.com/whitepaper/wordpress-security-stats-2022/)***, underscoring the pressing need for robust security solutions.
At Levamo, we take website performance and security seriously. That's why we're thrilled to announce our partnership with **Patchstack**, a leading security solution for WordPress websites.
In this blog post, we'll dive deeper into Patchstack's capabilities and explore how this partnership benefits you as a Levamo customer.
## What is Patchstack?
Patchstack
Founded with a mission to fortify website security, **[Patchstack](https://patchstack.com/)** has been making waves in the cybersecurity landscape. This powerful tool identifies security vulnerabilities within all your WordPress plugins, themes, and the core itself. Patchstack boasts the support of the most active community of ethical hackers within the WordPress ecosystem, ensuring your website is safeguarded against the latest threats.
What sets Patchstack apart is its ability to detect and address new vulnerabilities in WordPress core, plugins, and themes before they become public knowledge. Imagine having a virtual patch and firewall rules in place to thwart potential exploits within plugins, all before the official security update is released. This proactive approach not only keeps your website secure but also alleviates the resource-intensive burden of dealing with security issues.
Patchstack proudly prevents thousands of attacks from happening daily, providing advance protection for your WordPress site.
With this partnership, you can now enjoy seamless and advanced malware protection without the hassle of making code changes yourself.
Also Read: [LMS hosting](/managed-lms-hosting/)
## What Does This Partnership Mean for You?

Here are the game-changing benefits that our partnership with PatchStack brings to your WordPress hosting experience:
**Auto-detect security vulnerabilities across all hosted WordPress applications:** Our collaboration with PatchStack empowers us to perform comprehensive vulnerability scans across all your WordPress applications hosted with Levamo. This means that potential threats are identified before they can even think about compromising your website's security.
**Automated Virtual patching:** Virtual patching is a non-intrusive yet highly effective method to mitigate vulnerabilities on a large scale. It involves the deployment of virtual patches and firewall rules to seal potential security gaps. With Patchstack's virtual patching, you can enjoy peace of mind without making complex code changes or worrying about false positives.
**48-hour early vulnerability detection:** PatchStack's proactive approach ensures that vulnerabilities are pinpointed a full 48 hours ahead of their public disclosure. This time window is crucial in fortifying your website and thwarting potential attacks before they even begin.
**Monitor active exploitation:** In cybersecurity, knowledge is power. This partnership equips us with the tools to monitor active exploitation attempts. By staying ahead of the curve, we can guide you to protect your website more effectively.
**Highly targeted and lightweight:** Patchstack's virtual patching is finely tuned to protect your site from vulnerabilities without bogging down your hosting performance. That means that it will have minimum impact on your website's speed.
**Raise security awareness:** A secure website is a shared responsibility. Levamo and PatchStack are committed to raising security awareness among our customers. We provide valuable insights and best practices to help you maintain a robust online presence.
This partnership between Levamo and Patchstack represents a significant stride towards a more secure online platform for our customers. At Levamo, we're excited to incorporate this cutting-edge security solution into our hosting services, ensuring that your WordPress websites remain not only high-performing but also impervious to the ever-present threat of cyberattacks.
As you embark on your journey with Levamo's managed WordPress hosting, rest assured that our commitment to delivering the best in performance and security remains unwavering.